This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

PING.exe, System Security 2012, Blue Screen On Startup

3 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

Hello everyone. I have been having problems with my computer as of late. I got that System Security 2012 virus thing, and I followed this website to remove it http://deletemalware.blogspot.com/2011/11/…urity-2012.html

Everything worked fine for a couple of weeks, until this week everything has gone back to the crapper. Whenever I start the computer, I get an instant blue screen saying something about memory dumping, it doesn't finish all the way, and then the computer restarts, and the process repeats itself. As I said, I can go into safe mode with networking, which is how I am posting this. Earlier in the week, whenever I would check out task manager, I would see PING.exe taking up a low amount, then in 5 second jump to using all of my processors power, making the computer unusable. I have not installed any software resently or downloaded any torrents, etc. Yet again, I am not the only one that uses this computer.

I think Systems Security 2012 is removed all the way because I followed the guide exactly and deleted the files. I really need my computer working soon for High School projects. Thank you! Here are my reports

Sorry, I know I am not supposed to reply to my own topics, but for some reason whenever I try to post with my reports crashed, my browser says this webpage is not available… Again, sorry..
Extras

OTL Extras logfile created on: 11/15/2011 4:12:42 PM - Run 1
OTL by OldTimer - Version 3.2.31.0 Folder = C:\Users\Charlene\Downloads
Ultimate Edition (Version = 6.1.7600) - Type = NTWorkstation
Internet Explorer (Version = 9.0.8112.16421)
Locale: 00000409 | Country: United States | Language: ENU | Date Format: M/d/yyyy

2.00 Gb Total Physical Memory | 0.58 Gb Available Physical Memory | 28.99% Memory free
4.00 Gb Paging File | 2.68 Gb Available in Paging File | 67.14% Paging File free
Paging file location(s): ?:\pagefile.sys [binary data]

%SystemDrive% = C: | %SystemRoot% = C:\Windows | %ProgramFiles% = C:\Program Files
Drive C: | 287.93 Gb Total Space | 2.70 Gb Free Space | 0.94% Space Free | Partition Type: NTFS
Drive D: | 10.00 Gb Total Space | 3.85 Gb Free Space | 38.53% Space Free | Partition Type: NTFS

Computer Name: MAIN | User Name: Charlene | Logged in as Administrator.
Boot Mode: SafeMode with Networking | Scan Mode: Current user
Company Name Whitelist: Off | Skip Microsoft Files: Off | No Company Name Whitelist: On | File Age = 30 Days

========== Extra Registry (SafeList) ==========


========== File Associations ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\]
.cpl [@ = cplfile] – C:\Windows\System32\control.exe (Microsoft Corporation)
.hlp [@ = hlpfile] – C:\Windows\winhlp32.exe (Microsoft Corporation)

[HKEY_CURRENT_USER\SOFTWARE\Classes\]
.exe [@ = exefile] – Reg Error: Key error. File not found
.html [@ = ChromeHTML] – Reg Error: Key error. File not found

========== Shell Spawning ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\\shell\[command]\command]
batfile [open] – "%1" %*
cmdfile [open] – "%1" %*
comfile [open] – "%1" %*
cplfile [cplopen] – %SystemRoot%\System32\control.exe "%1",%* (Microsoft Corporation)
exefile [open] – "%1" %*
helpfile [open] – Reg Error: Key error.
hlpfile [open] – %SystemRoot%\winhlp32.exe %1 (Microsoft Corporation)
inffile [install] – %SystemRoot%\System32\InfDefaultInstall.exe "%1" (Microsoft Corporation)
piffile [open] – "%1" %*
regfile [merge] – Reg Error: Key error.
scrfile [config] – "%1"
scrfile [install] – rundll32.exe desk.cpl,InstallScreenSaver %l
scrfile [open] – "%1" /S
txtfile – Reg Error: Key error.
Unknown [openas] – %SystemRoot%\system32\rundll32.exe %SystemRoot%\system32\shell32.dll,OpenAs_RunDLL %1
Directory [AddToPlaylistVLC] – "C:\Program Files\VideoLAN\VLC\vlc.exe" –started-from-file –playlist-enqueue "%1" ()
Directory [Bridge] – C:\Program Files\Adobe\Adobe Bridge CS5.1\Bridge.exe "%L" (Adobe Systems, Inc.)
Directory [cmd] – cmd.exe /s /k pushd "%V" (Microsoft Corporation)
Directory [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Directory [PlayWithVLC] – "C:\Program Files\VideoLAN\VLC\vlc.exe" –started-from-file –no-playlist-enqueue "%1" ()
Folder [open] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Folder [explore] – Reg Error: Value error.
Drive [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)

========== Security Center Settings ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center]
"cval" = 0

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Monitoring]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Svc]
"VistaSp1" = Reg Error: Unknown registry data type – File not found
"AntiVirusOverride" = 0
"AntiSpywareOverride" = 0
"FirewallOverride" = 0

========== System Restore Settings ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SystemRestore]
"DisableSR" = 0

========== Firewall Settings ==========

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\DomainProfile]
"DisableNotifications" = 0
"EnableFirewall" = 0

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\StandardProfile]
"DisableNotifications" = 0
"EnableFirewall" = 0
"DoNotAllowExceptions" = 0

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\PublicProfile]
"DisableNotifications" = 0
"EnableFirewall" = 0
"DoNotAllowExceptions" = 0

========== Authorized Applications List ==========

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\StandardProfile\AuthorizedApplications\List]
"Zvpebfbsg Jvaqbjf Ubfgvat Freivpr" = C:\Users\Charlene\AppData\Local\Temp\csrssr.exe – ()


========== HKEY_LOCAL_MACHINE Uninstall List ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall]
"{002D9D5E-29BA-3E6D-9BC4-3D7D6DBC735C}" = Microsoft Visual C++ 2008 ATL Update kb973924 - x86 9.0.30729.4148
"{033E378E-6AD3-4AD5-BDEB-CBD69B31046C}" = Microsoft_VC90_ATL_x86
"{046B525C-FEC6-42A2-A637-53CC2F58100E}_is1" = DroidPad 1.2
"{048298C9-A4D3-490B-9FF9-AB023A9238F3}" = Steam
"{04AF207D-9A77-465A-8B76-991F6AB66245}" = Adobe Help Viewer CS3
"{05308C4E-7285-4066-BAE3-6B50DA6ED755}" = Adobe Update Manager CS4
"{054EFA56-2AC1-48F4-A883-0AB89874B972}" = Adobe Extension Manager CS4
"{08B32819-6EEF-4057-AEDA-5AB681A36A23}" = Adobe Bridge Start Meeting
"{08D2E121-7F6A-43EB-97FD-629B44903403}" = Microsoft_VC90_CRT_x86
"{0A0CADCF-78DA-33C4-A350-CD51849B9702}" = Microsoft .NET Framework 4 Extended
"{0B0F231F-CE6A-483D-AA23-77B364F75917}" = Windows Live Installer
"{0EDBEB2B-7C8D-42E6-8312-0F84394A3223}" = Windows Media Center Add-in for Silverlight
"{0F3647F8-E51D-4FCC-8862-9A8D0C5ACF25}" = Microsoft_VC80_ATL_x86
"{117B6BF6-82C3-420C-B284-9247C8568E53}" = The Sims™ 3 Outdoor Living Stuff
"{12BAA98C-F8DD-4BC9-BBE6-1C8463114197}" = BlackBerry Device Software Updater
"{13A5E785-5197-4EAD-8EE3-D660271E49BC}" = Feedback Tool
"{1618734A-3957-4ADD-8199-F973763109A8}" = Adobe Anchor Service CS4
"{1696C54E-599A-4BA2-9941-BB70C4727887}" = Xtranormal State - Voicepack-English-UK-Daniel
"{16E6D2C1-7C90-4309-8EC4-D2212690AAA4}" = AdobeColorCommonSetRGB
"{184CE391-7E0E-4C63-9935-D7A10EDFD3C6}" = Adobe WinSoft Linguistics Plugin
"{196BB40D-1578-3D01-B289-BEFC77A11A1E}" = Microsoft Visual C++ 2010 x86 Redistributable - 10.0.30319
"{1B7DCBBA-D8C7-4877-967F-C663037353C4}" = BlackBerry Device Software v6.0.0 for the BlackBerry 9700 smartphone
"{1C08A24C-B168-407E-A826-68FAF5F20710}" = Age of Empires III - The WarChiefs
"{1D7CE340-70C3-4848-BCCF-215950328A4C}" = Facebook Video Calling 1.0.0.8953
"{1E99F5D7-4262-4C7C-9135-F066E7485811}" = System Requirements Lab
"{1F1C2DFC-2D24-3E06-BCB8-725134ADF989}" = Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.4148
"{1F77C418-2C90-459C-BD33-B56A4182B9FA}" = System Requirements Lab CYRI
"{200FEC62-3C34-4D60-9CE8-EC372E01C08F}" = Windows Live SOXE Definitions
"{205C6BDD-7B73-42DE-8505-9A093F35A238}" = Windows Live Upload Tool
"{20C11E32-103F-429F-98A4-DA24486D140F}" = MediaBrowser LE
"{26A24AE4-039D-4CA4-87B4-2F83216017FF}" = Java™ 6 Update 26
"{2750B389-A2D2-4953-99CA-27C1F2A8E6FD}" = Microsoft SQL Server 2005 Tools Express Edition
"{29E5EA97-5F74-4A57-B8B2-D4F169117183}" = Adobe Stock Photos CS3
"{29ED20C9-5E15-4969-9279-25BF3727A3DA}" = iTunes
"{2A3FC24C-6EC0-4519-A52B-FDA4EA9B2D24}" = Windows Live Messenger
"{2AFFFDD7-ED85-4A90-8C52-5DA9EBDC9B8F}" = Microsoft SQL Server 2005 Express Edition (BWDATOOLSET)
"{2F4C24E6-CBD4-4AAC-B56F-C9FD44DE5668}" = Roxio Drag-to-Disc
"{3080A282-1DD2-4B3D-80CA-B9E73D182F7B}" = BlackBerry Device Software v5.0.0 for the BlackBerry 9700 smartphone
"{3521BDBD-D453-5D9F-AA55-44B75D214629}" = Adobe Community Help
"{3A4E8896-C2E7-4084-A4A4-B8FD1894E739}" = Adobe XMP Panels CS4
"{3B5C97AB-F523-4C8E-8A0D-A73A57C76F1C}" = AxedMS
"{3C3901C5-3455-3E0A-A214-0B093A5070A6}" = Microsoft .NET Framework 4 Client Profile
"{3D7E3EC9-46CF-4359-9289-39CE01DFB82F}" = Adobe Photoshop CS3
"{3F32058A-343A-4C16-BD1B-BE35E9A42352}" = RZ DVD Creator
"{3FA365DF-2D68-45ED-8F83-8C8A33E65143}" = Apple Application Support
"{411F3ABA-2AB5-4799-AA19-6ADF0A8F7424}" = Adobe Setup
"{41BB38A4-ED84-4682-8329-042FEBD8C30B}" = Mega Manager
"{43509E18-076E-40FE-AF38-CA5ED400A5A9}" = Pixel Bender Toolkit
"{44E240EC-2224-4078-A88B-2CEE0D3016EF}" = Adobe After Effects CS4 Presets
"{45057FCE-5784-48BE-8176-D9D00AF56C3C}" = The Sims™ 3 Late Night
"{45EC816C-0771-4C14-AE6D-72D1B578F4C8}" = Adobe After Effects CS4
"{467A3BF8-4C87-4E68-835C-CE5318C157C2}" = Xtranormal State - Voicepack-English-US-Tom
"{47E16407-05D3-4D2A-B2B9-C30700B7C2AD}" = LogMeIn Hamachi
"{48B3FB4D-CE22-488C-8E9F-24EBB77EAC0F}" = Microsoft Security Essentials
"{49471DB8-7F3C-42DB-89C2-AC50FA0C5290}" = Camtasia Studio 7
"{49EA4128-EF09-4ED1-81FE-45483E9F2770}" = Mushaboom Lite
"{4A03706F-666A-4037-7777-5F2748764D10}" = Java Auto Updater
"{4D6FAB8B-F22B-4272-AA27-9A188E21D047}" = iRip
"{51846830-E7B2-4218-8968-B77F0FF475B8}" = Adobe Color EU Extra Settings
"{53F5C3EE-05ED-4830-994B-50B2F0D50FCE}" = Microsoft SQL Server Setup Support Files (English)
"{54793AA1-5001-42F4-ABB6-C364617C6078}" = Adobe Linguistics CS3
"{56415658-366E-4E28-A6BD-68EC63E560E0}" = Vegas Pro 9.0
"{56B4002F-671C-49F4-984C-C760FE3806B5}" = Microsoft SQL Server VSS Writer
"{579684A4-DDD5-4CA3-9EA8-7BE7D9593DB4}" = Windows Live UX Platform Language Pack
"{59996900-0E6C-45B7-8C39-C64CB98462E4}" = Microsoft Web Platform Installer 2.0
"{5A13987D-55F4-4271-A40E-76AC9B1B38FD}" = OpenOffice.org 3.2
"{5D90E53A-BD7C-8F32-9B82-7733D0F0BC8E}" = Adobe Download Assistant
"{5EE7D259-D137-4438-9A5F-42F432EC0421}" = VC80CRTRedist - 8.0.50727.4053
"{60DB5894-B5A1-4B62-B0F3-669A22C0EE5D}" = Adobe Dynamiclink Support
"{635FED5B-2C6D-49BE-87E6-7A6FCD22BC5A}" = Microsoft_VC90_MFC_x86
"{653F2014-19C5-445A-BF2F-0192D60EBE69}" = PlayOn
"{67A9747A-E1F5-4E9A-81CC-12B5D5B81B6E}" = Adobe After Effects CS4 Third Party Content
"{67F0E67A-8E93-4C2C-B29D-47C48262738A}" = Adobe Device Central CS4
"{682B3E4F-696A-42DE-A41C-4C07EA1678B4}" = Windows Live SOXE
"{69FDFBB6-351D-4B8C-89D8-867DC9D0A2A4}" = Windows Media Player Firefox Plugin
"{6D592E30-11EC-11E0-859C-0013D3D69929}" = Vegas Pro 10.0
"{6FF5DD7A-FE28-4439-B8CF-1E9AF4EA0A61}" = Adobe Asset Services CS3
"{7032B400-11EC-11E0-A9BF-0013D3D69929}" = MSVCRT Redists
"{70F8B183-99EB-4304-BA35-080E2DFFD2A3}" = Age of Empires III
"{71828142-5A24-4BD0-97E7-976DA08CE6CF}" = The Sims™ 3 High-End Loft Stuff
"{72736F5F-520D-472A-88CC-7B02872FD34E}" = ATI Catalyst Registration
"{7299052b-02a4-4627-81f2-1818da5d550d}" = Microsoft Visual C++ 2005 Redistributable
"{75157F34-02C6-4831-BD66-3BC49E7A8394}" = BlackBerry Desktop Software 6.1
"{758C8301-2696-4855-AF45-534B1200980A}" = Samsung Kies
"{770657D0-A123-3C07-8E44-1C83EC895118}" = Microsoft Visual C++ 2005 ATL Update kb973923 - x86 8.0.50727.4053
"{789A5B64-9DD9-4BA5-915A-F0FC0A1B7BFE}" = Apple Software Update
"{79155F2B-9895-49D7-8612-D92580E0DE5B}" = Bonjour
"{7B11296A-F894-449C-8DF6-6AAAA7D4D118}" = The Sims™ 3 Town Life Stuff
"{802771A9-A856-4A41-ACF7-1450E523C923}" = Adobe XMP Panels CS3
"{820D3F45-F6EE-4AAF-81EF-CE21FF21D230}" = Adobe Type Support CS4
"{837b34e3-7c30-493c-8f6a-2b0f04e2912c}" = Microsoft Visual C++ 2005 Redistributable
"{838A22DF-81CA-4452-9BDD-A1745224D960}" = Xtranormal State - Voicepack-English-UK-Serena
"{83C292B7-38A5-440B-A731-07070E81A64F}" = Windows Live PIMT Platform
"{842B4B72-9E8F-4962-B3C1-1C422A5C4434}" = Suite Shared Configuration CS4
"{84713778-D9A9-4130-A811-DF3187827B05}" = LogMeIn
"{84EBDF39-4B33-49D7-A0BD-EB6E2C4E81C1}" = Windows Live Sync
"{86D4B82A-ABED-442A-BE86-96357B70F4FE}" = Ask Toolbar
"{89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}" = Microsoft Silverlight
"{8CFE909D-8F29-4471-B9FD-F7F8E14F272C}" = AIO Vibrant Toolbox
"{8D2BA474-F406-4710-9AE4-D4F22D21F0DD}" = Adobe Device Central CS3
"{8DD46C6A-0056-4FEC-B70A-28BB16A1F11F}" = MSVCRT
"{8E1AB809-F821-4F41-8431-44A11ED1EDBA}" = TVT7Diag
"{8EB8E60B-315D-44EB-A896-10D88602EE46}" = Adobe Setup
"{8EC4F64D-92E4-4274-9495-4C887D49DEC3}" = Xtranormal State
"{8FA53ACE-B718-4FAE-B7BF-95B0FCB320C8}" = SAMSUNG USB Driver for Mobile Phones
"{90120000-0020-0409-0000-0000000FF1CE}" = Compatibility Pack for the 2007 Office system
"{90176341-0A8B-4CCC-A78D-F862228A6B95}" = Adobe Anchor Service CS3
"{901DC58A-5C1B-4315-BA40-5AD3D3A463B9}" = ijji REACTOR
"{9068B2BE-D93A-4C0A-861C-5E35E2C0E09E}" = Intel® Matrix Storage Manager
"{90BC5F99-9172-43B1-805F-77BCC800CAB7}" = Opera 10.60
"{910F4A29-1134-49E0-AD8B-56E4A3152BD1}" = The Sims™ 3 Ambitions
"{912536C4-273C-416F-B42C-BBC5B72114D7}" = Xtranormal State - Voicepack-English-US-Samantha
"{91CA0409-6000-11D3-8CFE-0150048383C9}" = Microsoft Office Small Business Edition 2003
"{92482FB3-C05B-41C6-89E7-75D985602A6E}" = System Requirements Lab
"{92D58719-BBC1-4CC3-A08B-56C9E884CC2C}" = Microsoft_VC80_CRT_x86
"{934528B2-09B3-C6E5-288A-4E554E6DF2B9}" = ATI Catalyst Install Manager
"{94D398EB-D2FD-4FD1-B8C4-592635E8A191}" = Adobe CMaps CS4
"{95120000-00B9-0409-0000-0000000FF1CE}" = Microsoft Application Error Reporting
"{95655ED4-7CA5-46DF-907F-7144877A32E5}" = Adobe Color NA Recommended Settings
"{980A182F-E0A2-4A40-94C1-AE0C1235902E}" = Pando Media Booster
"{9A25302D-30C0-39D9-BD6F-21E6EC160475}" = Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.17
"{9C9824D9-9000-4373-A6A5-D0E5D4831394}" = Adobe Bridge CS3
"{9D318C86-AF4C-409F-A6AC-7183FF4CF424}" = Internet TV for Windows Media Center
"{9F986C21-5D52-49EA-BAE6-23529040A2DC}" = ASPCA Reminder V7F+AU by We-Care.com
"{A00B9A50-3090-4CFF-9CDA-82DA0BEDAA21}" = Apple Mobile Device Support
"{A2D81E70-2A98-4A08-A628-94388B063C5E}" = Adobe Color - Photoshop Specific
"{A371130B-5FA3-4988-9DE3-541A4EE1FE03}_is1" = Diner Dash 5 Boom!
"{A462213D-EED4-42C2-9A60-7BDD4D4B0B17}" = SigmaTel Audio
"{A53A11EA-0095-493F-86FA-A15E8A86A405}" = VMware Player
"{A78FE97A-C0C8-49CE-89D0-EDD524A17392}" = PDF Settings CS5
"{A83279FD-CA4B-4206-9535-90974DE76654}" = Apple Application Support
"{A9BDCA6B-3653-467B-AC83-94367DA3BFE3}" = Windows Live Photo Common
"{AADEA55D-C834-4BCB-98A3-4B8D1C18F4EE}" = Apple Mobile Device Support
"{AC5B0C19-D851-42F4-BDA0-410ECF7F70A5}" = PDF Settings
"{AC76BA86-7AD7-1033-7B44-A94000000001}" = Adobe Reader 9.4.2
"{AC76BA86-7AD7-5464-3428-900000000004}" = Spelling Dictionaries Support For Adobe Reader 9
"{B05DE7B7-0B40-4411-BD4B-222CAE2D8F15}" = Adobe MotionPicture Color Files CS4
"{B15381DD-FF97-4FCD-A881-ED4DB0975500}" = Adobe Color Video Profiles AE CS4
"{B1924580-0C5D-11E0-B655-0013D3D69929}" = MSVCRT Redists
"{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.3DVision" = NVIDIA 3D Vision Driver 275.33
"{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.ControlPanel" = NVIDIA Control Panel 275.33
"{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.Driver" = NVIDIA Graphics Driver 275.33
"{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.NVIRUSB" = NVIDIA 3D Vision Controller Driver 275.33
"{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.PhysX" = NVIDIA PhysX System Software 9.10.0514
"{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.Update" = NVIDIA Update 1.3.5
"{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_installer" = NVIDIA Install Application
"{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_NVIDIA.Update" = NVIDIA Update Components
"{B3BF6689-A81D-40D8-9A86-4AC4ACD9FC1C}" = Adobe Camera Raw 4.0
"{B4346951-3962-4C93-9A49-79A62AD8A632}" = Droid Explorer 0.8.7.2 (x86)
"{B5C314F7-928B-44E3-A8A3-169648B1077D}" = Xtranormal State - SoundPack-Starter Kit
"{B6CF2967-C81E-40C0-9815-C05774FEF120}" = Skype Toolbars
"{B6D38690-755E-4F40-A35A-23F8BC2B86AC}" = Microsoft_VC90_MFCLOC_x86
"{B9DB4C76-01A4-46D5-8910-F7AA6376DBAF}" = NVIDIA PhysX
"{BA1EA42A-B02E-4210-882C-717416D96E65}" = STOPzilla
"{BA26FFA5-6D47-47DB-BE56-34C357B5F8CC}" = The Sims™ 3 World Adventures
"{BB4E33EC-8181-4685-96F7-8554293DEC6A}" = Adobe Output Module
"{BBB7AEE0-AE78-44CC-8CD4-083B0B99EA80}" = Intel® Network Connections [removed]
"{BD68F46D-8A82-4664-8E68-F87C55BDEFD4}" = Microsoft SQL Server Native Client
"{BE9CEAAA-F069-4331-BF2F-8D350F6504F4}" = Adobe Media Encoder CS4 Additional Exporter
"{BEE64C14-BEF1-4610-8A68-A16EAA47B882}" = Futuremark SystemInfo
"{C05D8CDB-417D-4335-A38C-A0659EDFD6B8}" = The Sims™ 3
"{C27BC2A2-30DD-4014-B22E-63EB0DB572F9}" = Logitech Webcam Software
"{C2D69781-F392-4118-A5A7-C7E9C38DBFC2}" = Adobe ExtendScript Toolkit 2
"{C4124E95-5061-4776-8D5D-E3D931C778E1}" = Microsoft VC9 runtime libraries
"{C52E3EC1-048C-45E1-8D53-10B0C6509683}" = Adobe Default Language CS4
"{C6150D8A-86ED-41D3-87BB-F3BB51B0B77F}" = Windows Live ID Sign-in Assistant
"{C9E14402-3631-4182-B377-6B0DFB1C0339}" = QuickTime
"{CC75AB5C-2110-4A7F-AF52-708680D22FE8}" = Photoshop Camera Raw
"{CCA5EAAD-92F4-4B7A-B5EE-14294C66AB61}" = PlayReady PC Runtime x86
"{CE95A79E-E4FC-4FFF-8A75-29F04B942FF2}" = Windows Live UX Platform
"{CFC9F871-7C40-40B6-BE4A-B98A5B309716}" = Adobe Flash Professional CS5
"{D0DFF92A-492E-4C40-B862-A74A173C25C5}" = Adobe Version Cue CS3 Client
"{D1A19B02-817E-4296-A45B-07853FD74D57}" = Microsoft_VC80_MFC_x86
"{D28CB048-A0AB-4F98-909F-69F3F25AA87D}" = Xtranormal State - Showpak-Playgoz-Preview
"{D2C5E510-BE6D-42CC-9F61-E4F939078474}" = Lexmark Printable Web
"{D3742F82-1C1A-4DCC-ABBD-0E7C3C0185CC}" = TuneUp Utilities
"{D436F577-1695-4D2F-8B44-AC76C99E0002}" = Windows Live Photo Common
"{D45240D3-B6B3-4FF9-B243-54ECE3E10066}" = Windows Live Communications Platform
"{D6F879CC-59D6-4D4B-AE9B-D761E48D25ED}" = Skype™ 5.3
"{D92BBB52-82FF-42ED-8A3C-4E062F944AB7}" = Microsoft_VC80_MFCLOC_x86
"{DB6AB705-C9BD-40E3-8929-2EA57F36A4FF}_is1" = ConvertXtoDVD 4.1.19.365
"{DCFD26A8-60A5-4C69-A52D-264D0386FDB3}" = Microsoft Xbox 360 Accessories 1.2
"{DD7DB3C5-6FA3-4FA3-8A71-C2F2940EB029}" = Adobe Color JA Extra Settings
"{DE3A9DC5-9A5D-6485-9662-347162C7E4CA}" = Adobe Media Player
"{DEB90B8E-0DCB-48CE-B90E-8842A2BD643E}" = Adobe Media Encoder CS4
"{E09C4DB7-630C-4F06-A631-8EA7239923AF}" = D3DX10
"{E3E71D07-CD27-46CB-8448-16D4FB29AA13}" = Microsoft WSE 3.0 Runtime
"{E5B21F11-6933-4E0B-A25C-7963E3C07D11}" = Windows Live Messenger
"{E69AE897-9E0B-485C-8552-7841F48D42D8}" = Adobe Update Manager CS3
"{E6B88BD6-E4B2-4701-A648-B6DAC6E491CC}" = The Sims™ 3 Generations
"{E95C1190-3C4A-45B7-B2ED-B49BD1972BB4}" = EasyTether
"{EA2DB6E0-72C5-4ef9-A3A0-E6705F4A6A9E}" = Nexon Game Manager
"{ED436EA8-4145-4703-AE5D-4D09DD24AF5A}" = The Sims™ 3 Fast Lane Stuff
"{EE43894E-FDCF-4A8C-BCD6-3AAA9A48B486}" = Kies mini
"{F1191B7E-84BF-4325-9FFD-80BD8996ED4B}" = MorphVOX Junior
"{F8EF2B3F-C345-4F20-8FE4-791A20333CD5}" = Adobe ExtendScript Toolkit CS4
"{F93C84A6-0DC6-42AF-89FA-776F7C377353}" = Adobe PDF Library Files CS4
"{FCDD51BB-CAD0-4BB1-B7DF-CE86D1032794}" = Adobe Fonts All
"{FDB3B167-F4FA-461D-976F-286304A57B2A}" = Adobe AIR
"{FE044230-9CA5-43F7-9B58-5AC5A28A1F33}" = Windows Live Essentials
"{FE3997D3-6B56-4AC4-A99C-9DDFC45359BF}" = TuneUp Utilities Language Pack (en-US)
"{FF11004C-F42A-4A31-9BCF-7F5C8FDBE53C}" = Adobe Setup
"{FF66E9F6-83E7-3A3E-AF14-8DE9A809A6A4}" = Microsoft Visual C++ 2008 Redistributable - x86 9.0.21022
"1EC636D2DBA2D9924E02E10DA797DEC16306C1A9" = Windows Driver Package - Logitech HIDClass (10/16/2006 1.0)
"7-Zip" = 7-Zip 4.65
"Acoustica Effects Pack" = Acoustica Effects Pack
"Adobe AIR" = Adobe AIR
"Adobe Flash Player ActiveX" = Adobe Flash Player 10 ActiveX
"Adobe Flash Player Plugin" = Adobe Flash Player 11 Plugin
"Adobe_5aab5a491a3a52ae624fd639f6aaa95" = Adobe After Effects CS4 Third Party Content
"Akamai" = Akamai NetSession Interface Service
"ASIO4ALL" = ASIO4ALL
"Audacity 1.3 Beta (Unicode)_is1" = Audacity 1.3.12 (Unicode)
"AviSynth" = AviSynth 2.5
"B076073A-5527-4f4f-B46B-B10692277DA2_is1" = DisplayFusion 3.3.0
"Backyard Baseball 2003" = Backyard Baseball 2003
"BFG-Diner Dash 5 - Boom" = Diner Dash 5: Boom
"BitTorrent" = BitTorrent
"BlackBerry_Desktop" = BlackBerry Desktop Software 6.1
"Bome's Mouse Keyboard_is1" = Bome's Mouse Keyboard 2.00
"chc.4875E02D9FB21EE389F73B8D1702B320485DF8CE.1" = Adobe Community Help
"Cities XL 2011" = Cities XL 2011
"com.adobe.amp.4875E02D9FB21EE389F73B8D1702B320485DF8CE.1" = Adobe Media Player
"com.adobe.downloadassistant.AdobeDownloadAssistant" = Adobe Download Assistant
"Combined Community Codec Pack_is1" = Combined Community Codec Pack 2009-09-09
"CPUID CPU-Z_is1" = CPUID CPU-Z 1.57.1
"Cucusoft iPad/iPhone/iPod to Computer Transfer_is1" = iPad/iPhone/iPod to Computer Transfer 7.5.9
"DAEMON Tools Lite" = DAEMON Tools Lite
"dcmsvc_is1" = dcmsvc 1.0
"Distant Suns 6.0-Special Edition" = Distant Suns 6.0-Special Edition
"DivX Setup.divx.com" = DivX Setup
"Fraps" = Fraps
"Geekbench 2.1" = Geekbench 2.1
"Handbrake" = Handbrake 0.9.4
"ImgBurn" = ImgBurn
"InstallShield_{1C08A24C-B168-407E-A826-68FAF5F20710}" = Age of Empires III - The WarChiefs
"InstallShield_{70F8B183-99EB-4304-BA35-080E2DFFD2A3}" = Age of Empires III
"InstallShield_{758C8301-2696-4855-AF45-534B1200980A}" = Samsung Kies
"InstallShield_{EE43894E-FDCF-4A8C-BCD6-3AAA9A48B486}" = Kies mini
"Intelore - RAR Password Recovery" = RAR Password Recovery v1.1 RC16 (remove only)
"JDownloader" = JDownloader
"Kotor Tool" = Kotor Tool
"LAME for Audacity_is1" = LAME v3.98.2 for Audacity
"LastFM_is1" = Last.fm 1.5.4.27091
"Lexmark 5600-6600 Series" = Lexmark 5600-6600 Series
"Lexmark_HostCD" = Lexmark Software Uninstall
"LibUSB-Win32_is1" = LibUSB-Win32-[removed]
"Logitech Vid" = Logitech Vid HD
"LogMeIn Hamachi" = LogMeIn Hamachi
"lvdrivers_12.10" = Logitech Webcam Software Driver Package
"ManyCam" = ManyCam 2.6.55 (remove only)
"Maxthon3" = Maxthon 3
"Mgeni" = Mgeni Snapshot (10-22-2009)
"Microsoft .NET Framework 4 Client Profile" = Microsoft .NET Framework 4 Client Profile
"Microsoft .NET Framework 4 Extended" = Microsoft .NET Framework 4 Extended
"Microsoft SQL Server 2005" = Microsoft SQL Server 2005
"Mozilla Firefox 7.0.1 (x86 en-US)" = Mozilla Firefox 7.0.1 (x86 en-US)
"Music Liberator 10.2 Release 1_is1" = Music Liberator 10.2 Release 1
"NVIDIA Display Control Panel" = NVIDIA Display Control Panel
"NVIDIA StereoUSB Driver" = NVIDIA 3D Vision Controller Driver
"NVIDIAStereo" = NVIDIA Stereoscopic 3D Driver
"PPJoy Joystick Driver" = PPJoy Joystick Driver 0.8.4.6
"PROSetDX" = Intel® Network Connections [removed]
"Search Toolbar" = Search Toolbar
"SoftwareUpdUtility" = Download Updater (AOL LLC)
"Soulseek2" = SoulSeek 157 NS 13e
"SystemRequirementsLab" = System Requirements Lab
"TeamViewer 6" = TeamViewer 6
"The Sith Lords Restored Content Mod_is1" = TSLRCM 1.7
"TuneUp Utilities" = TuneUp Utilities
"Tweak UI 2.10" = Tweak UI
"Videora Android Converter" = Videora Android Converter 5.04
"VLC media player" = VLC media player 1.1.11
"VMware_Player" = VMware Player
"WinLiveSuite" = Windows Live Essentials
"WinRAR archiver" = WinRAR archiver
"xvid" = Xvid MPEG-4 Video Codec

========== HKEY_CURRENT_USER Uninstall List ==========

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall]
"309a46b1dc89b774" = Dell Driver Download Manager
"Dropbox" = Dropbox
"Google Chrome" = Google Chrome
"Jomic" = Jomic
"JScreenFix" = JScreenFix
"MusicManager" = Music Manager
"Octoshape Streaming Services" = Octoshape Streaming Services
"XBMC" = XBMC

========== Last 10 Event Log Errors ==========

Error reading Event Logs: The Event Service is not operating properly or the Event Logs are corrupt!

< End of report >
OTL logfile created on: 11/15/2011 4:12:42 PM - Run 1
OTL by OldTimer - Version 3.2.31.0 Folder = C:\Users\Charlene\Downloads
Ultimate Edition (Version = 6.1.7600) - Type = NTWorkstation
Internet Explorer (Version = 9.0.8112.16421)
Locale: 00000409 | Country: United States | Language: ENU | Date Format: M/d/yyyy

2.00 Gb Total Physical Memory | 0.58 Gb Available Physical Memory | 28.99% Memory free
4.00 Gb Paging File | 2.68 Gb Available in Paging File | 67.14% Paging File free
Paging file location(s): ?:\pagefile.sys [binary data]

%SystemDrive% = C: | %SystemRoot% = C:\Windows | %ProgramFiles% = C:\Program Files
Drive C: | 287.93 Gb Total Space | 2.70 Gb Free Space | 0.94% Space Free | Partition Type: NTFS
Drive D: | 10.00 Gb Total Space | 3.85 Gb Free Space | 38.53% Space Free | Partition Type: NTFS

Computer Name: MAIN | User Name: Charlene | Logged in as Administrator.
Boot Mode: SafeMode with Networking | Scan Mode: Current user
Company Name Whitelist: Off | Skip Microsoft Files: Off | No Company Name Whitelist: On | File Age = 30 Days

========== Processes (SafeList) ==========

PRC - C:\Users\Charlene\Downloads\OTL.exe (OldTimer Tools)
PRC - C:\Program Files\LogMeIn Hamachi\hamachi-2.exe (LogMeIn Inc.)
PRC - C:\Windows\explorer.exe (Microsoft Corporation)
PRC - C:\Windows\System32\PING.EXE (Microsoft Corporation)
PRC - C:\Windows\System32\conhost.exe (Microsoft Corporation)


========== Modules (No Company Name) ==========

MOD - C:\Windows\System32\DLAAPI_W.DLL ()


========== Win32 Services (SafeList) ==========

SRV - (SwitchBoard) – File not found
SRV - (MSSQL$BWDATOOLSET) SQL Server (BWDATOOLSET) – File not found
SRV - (Akamai) – c:\program files\common files\akamai/netsession_win_dac4cfd.dll ()
SRV - (szserver) – C:\Program Files\Common Files\iS3\Anti-Spyware\SZServer.exe (iS3, Inc.)
SRV - (Hamachi2Svc) – C:\Program Files\LogMeIn Hamachi\hamachi-2.exe (LogMeIn Inc.)
SRV - (nvUpdatusService) – C:\Program Files\NVIDIA Corporation\NVIDIA Updatus\daemonu.exe (NVIDIA Corporation)
SRV - (Stereo Service) – C:\Program Files\NVIDIA Corporation\3D Vision\nvSCPAPISvr.exe (NVIDIA Corporation)
SRV - (MediaMall Server) – C:\Program Files\MediaMall\MediaMallServer.exe (MediaMall Technologies, Inc.)
SRV - (VMnetDHCP) – C:\Windows\System32\vmnetdhcp.exe (VMware, Inc.)
SRV - (VMware NAT Service) – C:\Windows\System32\vmnat.exe (VMware, Inc.)
SRV - (VMAuthdService) – C:\Program Files\VMware\VMware Player\vmware-authd.exe (VMware, Inc.)
SRV - (VMUSBArbService) – C:\Program Files\Common Files\VMware\USB\vmware-usbarbitrator.exe (VMware, Inc.)
SRV - (Futuremark SystemInfo Service) – C:\Program Files\Futuremark\Futuremark SystemInfo\FMSISvc.exe (Futuremark Corporation)
SRV - (TeamViewer6) – C:\Program Files\TeamViewer\Version6\TeamViewer_Service.exe (TeamViewer GmbH)
SRV - (DroidExplorerService) – C:\Program Files\Droid Explorer\DroidExplorer.Service.exe (Ryan Conrad)
SRV - (ufad-ws60) – C:\Program Files\VMware\VMware Player\vmware-ufad.exe (VMware, Inc.)
SRV - (npggsvc) – C:\Windows\System32\GameMon.des (INCA Internet Co., Ltd.)
SRV - (TuneUp.Defrag) – C:\Program Files\TuneUp Utilities 2010\TuneUpDefragService.exe (TuneUp Software)
SRV - (WatAdminSvc) – C:\Windows\System32\Wat\WatAdminSvc.exe ()
SRV - (SbieSvc) – C:\Program Files\Sandboxie\SbieSvc.exe (tzuk)
SRV - (FLEXnet Licensing Service) – C:\Program Files\Common Files\Macrovision Shared\FLEXnet Publisher\FNPLicensingService.exe (Acresso Software Inc.)
SRV - (TuneUp.UtilitiesSvc) – C:\Program Files\TuneUp Utilities 2010\TuneUpUtilitiesService32.exe (TuneUp Software)
SRV - (UxTuneUp) – C:\Windows\System32\uxtuneup.dll (TuneUp Software)
SRV - (LVPrcSrv) – C:\Program Files\Common Files\LogiShrd\LVMVFM\LVPrcSrv.exe (Logitech Inc.)
SRV - (LMIMaint) – C:\Program Files\LogMeIn\x86\RaMaint.exe (LogMeIn, Inc.)
SRV - (Creative Labs Licensing Service) – C:\Program Files\Common Files\Creative Labs Shared\Service\CreativeLicensing.exe (Creative Labs)
SRV - (MvWebServer) – C:\Program Files\Lexmark\MarkVision Server\jre\bin\LexWebService.exe ()
SRV - (MvServer) – C:\Program Files\Lexmark\MarkVision Server\jre\bin\LexMvService.exe ()
SRV - (.1254257635) – C:\Program Files\1254257635\Charlene1254257635L.exe ()
SRV - (lxdu_device) – C:\Windows\System32\lxducoms.exe ( )
SRV - (Steam Client Service) – C:\Program Files\Common Files\Steam\SteamService.exe (Valve Corporation)
SRV - (SensrSvc) – C:\Windows\System32\sensrsvc.dll (Microsoft Corporation)
SRV - (PeerDistSvc) – C:\Windows\System32\PeerDistSvc.dll (Microsoft Corporation)
SRV - (IAANTMON) Intel® – C:\Program Files\Intel\Intel Matrix Storage Manager\IAANTmon.exe (Intel Corporation)
SRV - (StarWindServiceAE) – C:\Program Files\Alcohol Soft\Alcohol 120\StarWind\StarWindServiceAE.exe (Rocket Division Software)


========== Driver Services (SafeList) ==========

DRV - (dtsoftbus01) – C:\Windows\System32\drivers\dtsoftbus01.sys (DT Soft Ltd)
DRV - (szkg5) – C:\Windows\system32\DRIVERS\szkg.sys (iS3 Inc.)
DRV - (is3srv) – C:\Windows\system32\drivers\is3srv.sys (iS3 Inc.)
DRV - (szkgfs) – C:\Windows\system32\drivers\szkgfs.sys (iS3, Inc.)
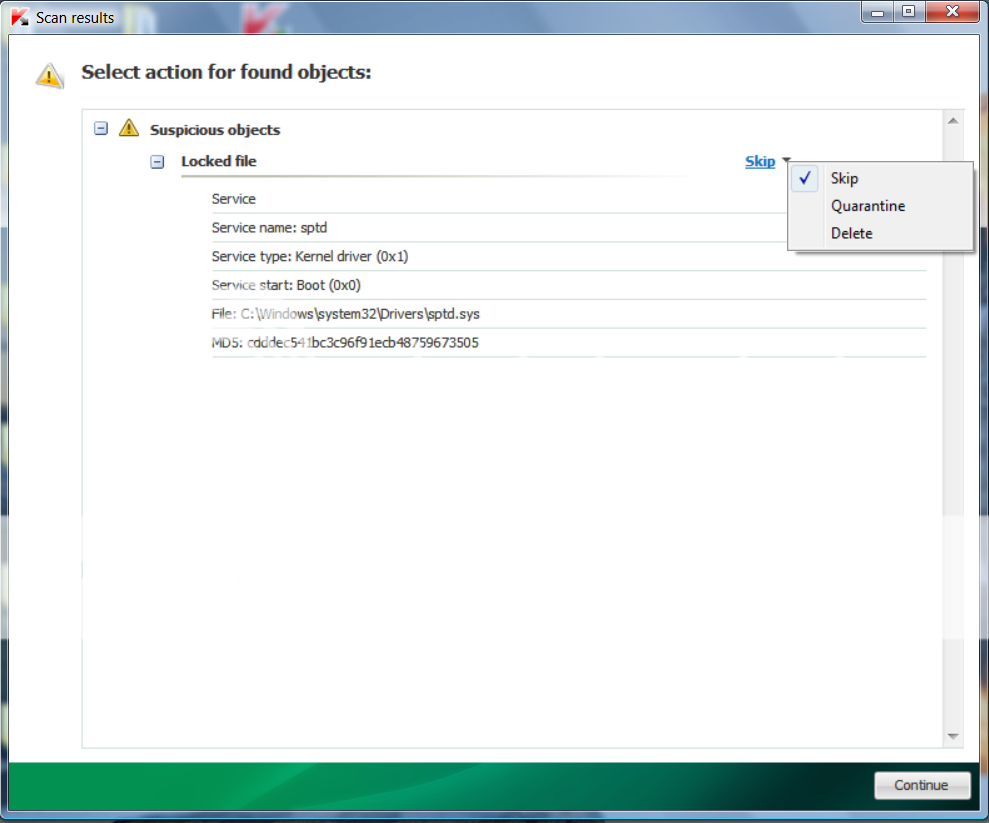
DRV - (sptd) – C:\Windows\System32\Drivers\sptd.sys (Duplex Secure Ltd.)
DRV - (nvlddmkm) – C:\Windows\System32\drivers\nvlddmkm.sys (NVIDIA Corporation)
DRV - (vmx86) – C:\Windows\System32\drivers\vmx86.sys (VMware, Inc.)
DRV - (vmci) – C:\Windows\System32\drivers\vmci.sys (VMware, Inc.)
DRV - (vmkbd) – C:\Windows\System32\drivers\VMkbd.sys (VMware, Inc.)
DRV - (VMnetuserif) – C:\Windows\System32\drivers\vmnetuserif.sys (VMware, Inc.)
DRV - (hcmon) – C:\Windows\System32\drivers\hcmon.sys (VMware, Inc.)
DRV - (VMnetBridge) – C:\Windows\System32\drivers\vmnetbridge.sys (VMware, Inc.)
DRV - (VMnetAdapter) – C:\Windows\System32\drivers\vmnetadapter.sys (VMware, Inc.)
DRV - (msvad_simple) – C:\Windows\System32\drivers\povrtdev.sys (MediaMall Technologies, Inc.)
DRV - (pneteth) – C:\Windows\System32\drivers\pneteth.sys (June Fabrics Technology Inc.)
DRV - (easytether) – C:\Windows\System32\drivers\easytthr.sys (Mobile Stream)
DRV - (vstor2-ws60) – C:\Program Files\VMware\VMware Player\vstor2-ws60.sys (VMware, Inc.)
DRV - (ssadmdm) – C:\Windows\System32\drivers\ssadmdm.sys (MCCI Corporation)
DRV - (ssadbus) SAMSUNG Android USB Composite Device driver (WDM) – C:\Windows\System32\drivers\ssadbus.sys (MCCI Corporation)
DRV - (ssadmdfl) SAMSUNG Android USB Modem (Filter) – C:\Windows\System32\drivers\ssadmdfl.sys (MCCI Corporation)
DRV - (sscdmdm) – C:\Windows\System32\drivers\sscdmdm.sys (MCCI Corporation)
DRV - (sscdbus) SAMSUNG USB Composite Device driver (WDM) – C:\Windows\System32\drivers\sscdbus.sys (MCCI Corporation)
DRV - (sscdmdfl) – C:\Windows\System32\drivers\sscdmdfl.sys (MCCI Corporation)
DRV - (PPortJoystick) – C:\Windows\System32\drivers\PPortJoy.sys (Deon van der Westhuysen)
DRV - (PPJoyBus) – C:\Windows\System32\drivers\PPJoyBus.sys (Deon van der Westhuysen)
DRV - (hamachi) – C:\Windows\System32\drivers\hamachi.sys (LogMeIn, Inc.)
DRV - (SCREAMINGBDRIVER) – C:\Windows\System32\drivers\ScreamingBAudio.sys (Screaming Bee LLC)
DRV - (SbieDrv) – C:\Program Files\Sandboxie\SbieDrv.sys (tzuk)
DRV - (TuneUpUtilitiesDrv) – C:\Program Files\TuneUp Utilities 2010\TuneUpUtilitiesDriver32.sys (TuneUp Software)
DRV - (LVPr2Mon) – C:\Windows\System32\drivers\LVPr2Mon.sys ()
DRV - (IntelDH) – C:\Windows\System32\drivers\IntelDH.sys (Intel Corporation)
DRV - (vmbus) – C:\Windows\system32\DRIVERS\vmbus.sys (Microsoft Corporation)
DRV - (storflt) – C:\Windows\system32\DRIVERS\vmstorfl.sys (Microsoft Corporation)
DRV - (storvsc) – C:\Windows\system32\DRIVERS\storvsc.sys (Microsoft Corporation)
DRV - (msloop) – C:\Windows\System32\drivers\loop.sys (Microsoft Corporation)
DRV - (WinUsb) – C:\Windows\System32\drivers\winusb.sys (Microsoft Corporation)
DRV - (s3cap) – C:\Windows\system32\DRIVERS\vms3cap.sys (Microsoft Corporation)
DRV - (VMBusHID) – C:\Windows\system32\DRIVERS\VMBusHID.sys (Microsoft Corporation)
DRV - (cdrom) – C:\Windows\System32\drivers\cdrom.sys ()
DRV - (VSTHWBS2) – C:\Windows\System32\drivers\VSTBS23.SYS (Conexant Systems, Inc.)
DRV - (e1express) Intel® – C:\Windows\System32\drivers\e1e6232.sys (Intel Corporation)
DRV - (LVRS) – C:\Windows\System32\drivers\lvrs.sys (Logitech Inc.)
DRV - (PID_PEPI) Logitech QuickCam IM(PID_PEPI) – C:\Windows\System32\drivers\LV302V32.SYS (Logitech Inc.)
DRV - (pepifilter) – C:\Windows\System32\drivers\lv302af.sys (Logitech Inc.)
DRV - (LMIRfsDriver) – C:\Windows\System32\drivers\LMIRfsDriver.sys (LogMeIn, Inc.)
DRV - (LMIInfo) – C:\Program Files\LogMeIn\x86\rainfo.sys (LogMeIn, Inc.)
DRV - (ATIAVPCI) – C:\Windows\System32\drivers\atinavrr.sys (ATI Technologies Inc.)
DRV - (ManyCam) – C:\Windows\System32\drivers\ManyCam.sys (ManyCam LLC.)
DRV - (STHDA) – C:\Windows\System32\drivers\stwrt.sys (SigmaTel, Inc.)
DRV - (DLARTL_M) – C:\Windows\System32\drivers\DLARTL_M.SYS (Roxio)
DRV - (DLACDBHM) – C:\Windows\System32\drivers\DLACDBHM.SYS (Roxio)
DRV - (DLADResM) – C:\Windows\System32\DLA\DLADResM.SYS (Roxio)
DRV - (DLAUDFAM) – C:\Windows\System32\DLA\DLAUDFAM.SYS (Roxio)
DRV - (DLABMFSM) – C:\Windows\System32\DLA\DLABMFSM.SYS (Roxio)
DRV - (DLAUDF_M) – C:\Windows\System32\DLA\DLAUDF_M.SYS (Roxio)
DRV - (DLAOPIOM) – C:\Windows\System32\DLA\DLAOPIOM.SYS (Roxio)
DRV - (DLABOIOM) – C:\Windows\System32\DLA\DLABOIOM.SYS (Roxio)
DRV - (DLAPoolM) – C:\Windows\System32\DLA\DLAPoolM.SYS (Roxio)
DRV - (DLAIFS_M) – C:\Windows\System32\DLA\DLAIFS_M.SYS (Roxio)
DRV - (pnetmdm) – C:\Windows\System32\drivers\pnetmdm.sys (June Fabrics Technology)
DRV - (ASPI) – C:\Windows\System32\drivers\ASPI32.SYS (Adaptec)


========== Standard Registry (SafeList) ==========


========== Internet Explorer ==========


IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://www.google.com/
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page Redirect Cache = http://www.msn.com/
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page Redirect Cache AcceptLangs = en-us
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page Redirect Cache_TIMESTAMP = B8 27 1C 4E 62 A0 CA 01 [binary data]
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyEnable" = 0
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyOverride" = *.local

========== FireFox ==========

FF - prefs.js..browser.search.defaultthis.engineName: "Swag Bucks Customized Web Search"
FF - prefs.js..browser.search.defaulturl: "http://search.conduit.com/ResultsExt.aspx?ctid=CT2260173&SearchSource=3&q={searchTerms}"
FF - prefs.js..browser.search.useDBForOrder: true
FF - prefs.js..browser.startup.homepage: "http://en-US.start3.mozilla.com/firefox?client=firefox-a&rls=org.mozilla:en-US:official"
FF - prefs.js..extensions.enabledItems: {d10d0bf8-f5b5-c8b4-a8b2-2b9879e08c5d}:1.3.3
FF - prefs.js..extensions.enabledItems: {ea2b95c2-9be8-48ed-bdd1-5fcd2ad0ff99}:0.3.8.1
FF - prefs.js..extensions.enabledItems: [removed]:1.6.0
FF - prefs.js..extensions.enabledItems: {1cdccf78-1ea9-4f40-b69f-ef7674dbef8c}:0.3.7
FF - prefs.js..extensions.enabledItems: [removed]:3.9.2
FF - prefs.js..extensions.enabledItems: [removed]:[removed]
FF - prefs.js..extensions.enabledItems: {81BF1D23-5F17-408D-AC6B-BD6DF7CAF670}:[removed]
FF - prefs.js..extensions.enabledItems: [removed]:2.8
FF - prefs.js..extensions.enabledItems: {340c2bbc-ce74-4362-90b5-7c26312808ef}:1.6.1
FF - prefs.js..keyword.URL: "http://www.mywebsearch.com/jsp/cfg_redir2.jsp?id=ZJxdm380YTUS&fl=0&ptb=UcGmFtNPvazis6e9w8x4Fw&url=http://search.mywebsearch.com/mywebsearch/GGmain.jhtml&st=kwd&n=77ce7dc5&searchfor="


FF - HKLM\Software\MozillaPlugins\@adobe.com/FlashPlayer: C:\Windows\system32\Macromed\Flash\NPSWF32.dll ()
FF - HKLM\Software\MozillaPlugins\@Apple.com/iTunes,version=: File not found
FF - HKLM\Software\MozillaPlugins\@Apple.com/iTunes,version=1.0: C:\Program Files\iTunes\Mozilla Plugins\npitunes.dll ()
FF - HKLM\Software\MozillaPlugins\@divx.com/DivX Browser Plugin,version=1.0.0: C:\Program Files\DivX\DivX Plus Web Player\npdivx32.dll (DivX, LLC)
FF - HKLM\Software\MozillaPlugins\@divx.com/DivX Player Plugin,version=1.0.0: File not found
FF - HKLM\Software\MozillaPlugins\@divx.com/DivX VOD Helper,version=1.0.0: C:\Program Files\DivX\DivX OVS Helper\npovshelper.dll (DivX, LLC.)
FF - HKLM\Software\MozillaPlugins\@java.com/JavaPlugin: C:\Program Files\Java\jre6\bin\new_plugin\npjp2.dll (Sun Microsystems, Inc.)
FF - HKLM\Software\MozillaPlugins\@microsoft.com/GENUINE: disabled File not found
FF - HKLM\Software\MozillaPlugins\@Microsoft.com/NpCtrl,version=1.0: c:\Program Files\Microsoft Silverlight\4.0.60531.0\npctrl.dll ( Microsoft Corporation)
FF - HKLM\Software\MozillaPlugins\@microsoft.com/WPF,version=3.5: C:\Windows\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\NPWPF.dll (Microsoft Corporation)
FF - HKLM\Software\MozillaPlugins\@microsoft.com/wpi,version=1.0: C:\Program Files\Microsoft\Web Platform Installer\\npwpidetector.dll ()
FF - HKLM\Software\MozillaPlugins\@nexon.net/NxGame: C:\ProgramData\NexonUS\NGM\npNxGameUS.dll (Nexon)
FF - HKLM\Software\MozillaPlugins\@nvidia.com/3DVision: C:\Program Files\NVIDIA Corporation\3D Vision\npnv3dv.dll (NVIDIA Corporation)
FF - HKLM\Software\MozillaPlugins\@nvidia.com/3DVisionStreaming: C:\Program Files\NVIDIA Corporation\3D Vision\npnv3dvstreaming.dll (NVIDIA Corporation)
FF - HKLM\Software\MozillaPlugins\@pandonetworks.com/PandoWebPlugin: C:\Program Files\Pando Networks\Media Booster\npPandoWebPlugin.dll (Pando Networks)
FF - HKLM\Software\MozillaPlugins\@RIM.com/WebSLLauncher,version=1.0: C:\Program Files\Common Files\Research In Motion\BBWebSLLauncher\NPWebSLLauncher.dll ()
FF - HKLM\Software\MozillaPlugins\@soe.sony.com/installer,version=1.0.3: C:\Users\Charlene\AppData\Local\Google\Chrome\User Data\Default\Extensions\dkfjadjghjpjodfhffafagnkbgbpiphf\1.0.3.152_0\npsoe.dll File not found
FF - HKCU\Software\MozillaPlugins\@octoshape.com/Octoshape Streaming Services,version=1.0: C:\Users\Charlene\AppData\Roaming\Octoshape\Octoshape Streaming Services\sua-1103234-0-npoctoshape.dll (Octoshape ApS)
FF - HKCU\Software\MozillaPlugins\@Skype Limited.com/Facebook Video Calling Plugin: C:\Users\Charlene\AppData\Local\Facebook\Video\Skype\npFacebookVideoCalling.dll (Skype Limited)
FF - HKCU\Software\MozillaPlugins\@tools.google.com/Google Update;version=3: C:\Users\Charlene\AppData\Local\Google\Update\1.3.21.79\npGoogleUpdate3.dll (Google Inc.)
FF - HKCU\Software\MozillaPlugins\@tools.google.com/Google Update;version=9: C:\Users\Charlene\AppData\Local\Google\Update\1.3.21.79\npGoogleUpdate3.dll (Google Inc.)
FF - HKCU\Software\MozillaPlugins\pandonetworks.com/PandoWebPlugin: C:\Program Files\Pando Networks\Media Booster\npPandoWebPlugin.dll (Pando Networks)

FF - HKEY_LOCAL_MACHINE\software\mozilla\Firefox\Extensions\\{23fcfd51-4958-4f00-80a3-ae97e717ed8b}: C:\Program Files\DivX\DivX Plus Web Player\firefox\DivXHTML5 [2011/07/05 01:09:25 | 000,000,000 | —D | M]
FF - HKEY_LOCAL_MACHINE\software\mozilla\Mozilla Firefox 3.6.8\extensions\\Components: C:\Program Files\Mozilla Firefox\components [2011/09/22 18:24:19 | 000,000,000 | —D | M]
FF - HKEY_LOCAL_MACHINE\software\mozilla\Mozilla Firefox 3.6.8\extensions\\Plugins: C:\Program Files\Mozilla Firefox\plugins [2011/09/22 18:24:18 | 000,000,000 | —D | M]
FF - HKEY_LOCAL_MACHINE\software\mozilla\Mozilla Firefox 7.0.1\extensions\\Components: C:\ProgramData\Mozilla Firefox\components [2011/10/24 20:21:02 | 000,000,000 | —D | M]
FF - HKEY_LOCAL_MACHINE\software\mozilla\Mozilla Firefox 7.0.1\extensions\\Plugins: C:\ProgramData\Mozilla Firefox\plugins [2011/09/22 18:24:18 | 000,000,000 | —D | M]

[2010/02/27 19:43:03 | 000,000,000 | —D | M] (No name found) – C:\Users\Charlene\AppData\Roaming\mozilla\Extensions
[2011/10/30 11:48:58 | 000,000,000 | —D | M] (No name found) – C:\Users\Charlene\AppData\Roaming\mozilla\Firefox\Profiles\fkl9omt2.default\extensions
[2010/02/27 19:43:13 | 000,000,000 | —D | M] (MegaUpload Time Attack) – C:\Users\Charlene\AppData\Roaming\mozilla\Firefox\Profiles\fkl9omt2.default\extensions\{1cdccf78-1ea9-4f40-b69f-ef7674dbef8c}
[2010/04/27 19:15:07 | 000,000,000 | —D | M] (Microsoft .NET Framework Assistant) – C:\Users\Charlene\AppData\Roaming\mozilla\Firefox\Profiles\fkl9omt2.default\extensions\{20a82645-c095-46ed-80e3-08825760534b}
[2010/02/27 19:43:14 | 000,000,000 | —D | M] (No name found) – C:\Users\Charlene\AppData\Roaming\mozilla\Firefox\Profiles\fkl9omt2.default\extensions\{24d1fe20-76df-11de-8a39-0800200c9a66}
[2010/11/29 19:19:05 | 000,000,000 | —D | M] (iMacros for Firefox) – C:\Users\Charlene\AppData\Roaming\mozilla\Firefox\Profiles\fkl9omt2.default\extensions\{81BF1D23-5F17-408D-AC6B-BD6DF7CAF670}
[2011/10/30 11:48:58 | 000,000,000 | —D | M] (Swag Bucks Community Toolbar) – C:\Users\Charlene\AppData\Roaming\mozilla\Firefox\Profiles\fkl9omt2.default\extensions\{8bdea9d6-6f62-45eb-8ee9-8a81af0d2f94}
[2011/01/01 23:57:06 | 000,000,000 | —D | M] (Adblock Plus) – C:\Users\Charlene\AppData\Roaming\mozilla\Firefox\Profiles\fkl9omt2.default\extensions\{d10d0bf8-f5b5-c8b4-a8b2-2b9879e08c5d}
[2010/03/27 08:49:52 | 000,000,000 | —D | M] (Edit Cookies) – C:\Users\Charlene\AppData\Roaming\mozilla\Firefox\Profiles\fkl9omt2.default\extensions\{ea2b95c2-9be8-48ed-bdd1-5fcd2ad0ff99}
[2010/10/30 09:32:43 | 000,000,000 | —D | M] (InvisibleHand) – C:\Users\Charlene\AppData\Roaming\mozilla\Firefox\Profiles\fkl9omt2.default\extensions\[removed]
[2010/11/29 19:19:14 | 000,000,000 | —D | M] (Firebug) – C:\Users\Charlene\AppData\Roaming\mozilla\Firefox\Profiles\fkl9omt2.default\extensions\[removed]
[2010/09/29 19:41:39 | 000,000,000 | —D | M] ("Xmarks") – C:\Users\Charlene\AppData\Roaming\mozilla\Firefox\Profiles\fkl9omt2.default\extensions\[removed]
[2011/10/30 11:48:58 | 000,000,000 | —D | M] (No name found) – C:\Users\Charlene\AppData\Roaming\mozilla\Firefox\Profiles\fkl9omt2.default\extensions\staged
[2009/11/12 16:37:08 | 000,000,923 | —- | M] () – C:\Users\Charlene\AppData\Roaming\Mozilla\Firefox\Profiles\fkl9omt2.default\searchplugins\conduit.xml
[2009/10/04 15:08:24 | 000,000,921 | —- | M] () – C:\Users\Charlene\AppData\Roaming\Mozilla\Firefox\Profiles\fkl9omt2.default\searchplugins\dictionarycom.xml
[2010/02/13 16:34:48 | 000,009,985 | —- | M] () – C:\Users\Charlene\AppData\Roaming\Mozilla\Firefox\Profiles\fkl9omt2.default\searchplugins\mywebsearch.xml
[2011/02/10 17:38:51 | 000,000,000 | —D | M] (No name found) – C:\Program Files\Mozilla Firefox\extensions
[2010/07/28 20:54:39 | 000,000,000 | —D | M] (Kaspersky Anti-Banner) – C:\Program Files\Mozilla Firefox\extensions\[removed]
[2010/07/28 20:54:40 | 000,000,000 | —D | M] (Kaspersky URL Advisor) – C:\Program Files\Mozilla Firefox\extensions\[removed]
[2010/03/30 11:57:04 | 000,098,304 | —- | M] (NHN USA Inc.) – C:\Program Files\mozilla firefox\plugins\npijjiautoinstallpluginff.dll

========== Chrome ==========

CHR - default_search_provider: Google (Enabled)
CHR - default_search_provider: search_url = {google:baseURL}search?{google:RLZ}{google:acceptedSuggestion}{google:originalQueryForSuggestion}{googl
e:searchFieldtrialParameter}{google:instantFieldTrialGroupParameter}sourceid=chro
me&ie={inputEncoding}&q={searchTerms}
CHR - default_search_provider: suggest_url = {google:baseSuggestURL}search?{google:searchFieldtrialParameter}{google:instantFieldTrialGroupParameter}client
=chrome&hl={language}&q={searchTerms}
CHR - plugin: Shockwave Flash (Enabled) = C:\Users\Charlene\AppData\Local\Google\Chrome\Application\15.0.874.120\gcswf32.dll
CHR - plugin: Shockwave Flash (Enabled) = C:\Windows\system32\Macromed\Flash\NPSWF32.dll
CHR - plugin: QuickTime Plug-in 7.7 (Enabled) = C:\Program Files\QuickTime\plugins\npqtplugin.dll
CHR - plugin: QuickTime Plug-in 7.7 (Enabled) = C:\Program Files\QuickTime\plugins\npqtplugin2.dll
CHR - plugin: QuickTime Plug-in 7.7 (Enabled) = C:\Program Files\QuickTime\plugins\npqtplugin3.dll
CHR - plugin: QuickTime Plug-in 7.7 (Enabled) = C:\Program Files\QuickTime\plugins\npqtplugin4.dll
CHR - plugin: QuickTime Plug-in 7.7 (Enabled) = C:\Program Files\QuickTime\plugins\npqtplugin5.dll
CHR - plugin: QuickTime Plug-in 7.7 (Enabled) = C:\Program Files\QuickTime\plugins\npqtplugin6.dll
CHR - plugin: QuickTime Plug-in 7.7 (Enabled) = C:\Program Files\QuickTime\plugins\npqtplugin7.dll
CHR - plugin: Java Deployment Toolkit 6.0.260.3 (Enabled) = C:\Program Files\Java\jre6\bin\new_plugin\npdeployJava1.dll
CHR - plugin: Java™ Platform SE 6 U26 (Enabled) = C:\Program Files\Java\jre6\bin\new_plugin\npjp2.dll
CHR - plugin: Adobe Acrobat (Disabled) = C:\Program Files\Adobe\Reader 9.0\Reader\Browser\nppdf32.dll
CHR - plugin: Silverlight Plug-In (Enabled) = c:\Program Files\Microsoft Silverlight\4.0.60531.0\npctrl.dll
CHR - plugin: DivX Web Player (Enabled) = C:\Program Files\DivX\DivX Plus Web Player\npdivx32.dll
CHR - plugin: Microsoft\u00AE Windows Media Player Firefox Plugin (Enabled) = C:\ProgramData\Mozilla Firefox\plugins\np-mswmp.dll
CHR - plugin: Remoting Viewer (Enabled) = internal-remoting-viewer
CHR - plugin: Native Client (Enabled) = C:\Users\Charlene\AppData\Local\Google\Chrome\Application\15.0.874.120\ppGoogleNaClPluginChrome.dll
CHR - plugin: Chrome PDF Viewer (Enabled) = C:\Users\Charlene\AppData\Local\Google\Chrome\Application\15.0.874.120\pdf.dll
CHR - plugin: Octoshape Streaming Services (Enabled) = C:\Users\Charlene\AppData\Roaming\Mozilla\plugins\npoctoshape.dll
CHR - plugin: Octoshape Streaming Services (Enabled) = C:\Users\Charlene\AppData\Roaming\Octoshape\Octoshape Streaming Services\sua-1103234-0-npoctoshape.dll
CHR - plugin: RIM Handheld Application Loader (Enabled) = C:\Program Files\Common Files\Research In Motion\BBWebSLLauncher\NPWebSLLauncher.dll
CHR - plugin: DivX VOD Helper Plug-in (Enabled) = C:\Program Files\DivX\DivX OVS Helper\npovshelper.dll
CHR - plugin: WPI Detector 1.1 (Enabled) = C:\Program Files\Microsoft\Web Platform Installer\\npwpidetector.dll
CHR - plugin: NVIDIA 3D Vision (Enabled) = C:\Program Files\NVIDIA Corporation\3D Vision\npnv3dv.dll
CHR - plugin: NVIDIA 3D VISION (Enabled) = C:\Program Files\NVIDIA Corporation\3D Vision\npnv3dvstreaming.dll
CHR - plugin: Pando Web Plugin (Enabled) = C:\Program Files\Pando Networks\Media Booster\npPandoWebPlugin.dll
CHR - plugin: iTunes Application Detector (Enabled) = C:\Program Files\iTunes\Mozilla Plugins\npitunes.dll
CHR - plugin: Nexon Game Controller (Enabled) = C:\ProgramData\NexonUS\NGM\npNxGameUS.dll
CHR - plugin: Google Update (Enabled) = C:\Users\Charlene\AppData\Local\Google\Update\1.3.21.69\npGoogleUpdate3.dll
CHR - plugin: Windows Presentation Foundation (Enabled) = C:\Windows\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\NPWPF.dll
CHR - plugin: Default Plug-in (Enabled) = default_plugin
CHR - Extension: Gizmodo, the Gadget Guide = C:\Users\Charlene\AppData\Local\Google\Chrome\User Data\Default\Extensions\bamognfncfnonmehnncdbgfhdbjjgplp\2011.11.14.12187_0\
CHR - Extension: AdBlock = C:\Users\Charlene\AppData\Local\Google\Chrome\User Data\Default\Extensions\gighmmpiobklfepjocnamgkkbiglidom\2.4.29_0\
CHR - Extension: DivX Plus Web Player HTML5 \u003Cvideo\u003E = C:\Users\Charlene\AppData\Local\Google\Chrome\User Data\Default\Extensions\nneajnkjbffgblleaoojgaacokifdkhm\2.1.2.126_0\

Hosts file not found
O2 - BHO: (DivX Plus Web Player HTML5 ) - {326E768D-4182-46FD-9C16-1449A49795F4} - C:\Program Files\DivX\DivX Plus Web Player\ie\DivXHTML5\DivXHTML5.dll (DivX, LLC)
O2 - BHO: (no name) - {3CA2F312-6F6E-4B53-A66E-4E65E497C8C0} - No CLSID value found.
O2 - BHO: (no name) - {99E00A4C-D35E-11DD-BA95-9B6A56D89593} - No CLSID value found.
O2 - BHO: (Search Toolbar) - {9D425283-D487-4337-BAB6-AB8354A81457} - C:\Program Files\Search Toolbar\SearchToolbar.dll ()
O2 - BHO: (Skype Browser Helper) - {AE805869-2E5C-4ED4-8F7B-F1F7851A4497} - C:\Program Files\Skype\Toolbars\Internet Explorer\skypeieplugin.dll (Skype Technologies S.A.)
O2 - BHO: (Lexmark Printable Web) - {D2C5E510-BE6D-42CC-9F61-E4F939078474} - C:\Program Files\Lexmark Printable Web\bho.dll ()
O2 - BHO: (Ask Toolbar) - {D4027C7F-154A-4066-A1AD-4243D8127440} - C:\Program Files\Ask.com\GenericAskToolbar.dll (Ask)
O2 - BHO: (WeCareReminder Class) - {D824F0DE-3D60-4F57-9EB1-66033ECD8ABB} - C:\ProgramData\WeCareReminder\IEHelperv2.5.0.dll (We-Care.com)
O3 - HKLM\..\Toolbar: (Search Toolbar) - {9D425283-D487-4337-BAB6-AB8354A81457} - C:\Program Files\Search Toolbar\SearchToolbar.dll ()
O3 - HKLM\..\Toolbar: (Ask Toolbar) - {D4027C7F-154A-4066-A1AD-4243D8127440} - C:\Program Files\Ask.com\GenericAskToolbar.dll (Ask)
O3 - HKCU\..\Toolbar\WebBrowser: (no name) - {61539ECD-CC67-4437-A03C-9AACCBD14326} - No CLSID value found.
O3 - HKCU\..\Toolbar\WebBrowser: (Ask Toolbar) - {D4027C7F-154A-4066-A1AD-4243D8127440} - C:\Program Files\Ask.com\GenericAskToolbar.dll (Ask)
O4 - HKLM..\Run: [] File not found
O4 - HKLM..\Run: [056.exe] C:\Program Files\LP\0087\056.exe ()
O4 - HKLM..\Run: [ApnUpdater] C:\Program Files\Ask.com\Updater\Updater.exe (Ask)
O4 - HKLM..\Run: [APSDaemon] C:\Program Files\Common Files\Apple\Apple Application Support\APSDaemon.exe (Apple Inc.)
O4 - HKLM..\Run: [cmmmG5sQJ8234A] C:\Windows\System32\AV Security 2012v121.exe (Корпорация Майкрософт)
O4 - HKLM..\Run: [dcmsvc] C:\Program Files\dcmsvc\dcmsvc.exe ()
O4 - HKLM..\Run: [lxduamon] C:\Program Files\Lexmark 5600-6600 Series\lxduamon.exe ()
O4 - HKLM..\Run: [lxdumon.exe] C:\Program Files\Lexmark 5600-6600 Series\lxdumon.exe ()
O4 - HKLM..\Run: [mswlnsys32] C:\Users\Nathan\AppData\Roaming\AntiSpyware.exe ()
O4 - HKLM..\Run: [MYPROXYREG] C:\Users\Nathan\AppData\Roaming\MYPROXY.exe ()
O4 - HKLM..\Run: [NPPNNyxA1uv] C:\Users\Nathan\AppData\Roaming\dwme.exe ()
O4 - HKLM..\Run: [RIMBBLaunchAgent.exe] C:\Program Files\Common Files\Research In Motion\USB Drivers\RIMBBLaunchAgent.exe (Research In Motion Limited)
O4 - HKLM..\Run: [VMware hqtray] C:\Program Files\VMware\VMware Player\hqtray.exe (VMware, Inc.)
O4 - HKCU..\Run: [DisplayFusion] C:\Program Files\DisplayFusion\DisplayFusion.exe (Binary Fortress Software)
O4 - HKCU..\Run: [Facebook Update] C:\Users\Charlene\AppData\Local\Facebook\Update\FacebookUpdate.exe (Facebook Inc.)
O4 - HKCU..\Run: [Microsoft Windows Hosting Service] C:\Users\Charlene\AppData\Local\Temp\csrssr.exe ()
O4 - HKCU..\Run: [mswlnsys32] C:\Users\Charlene\AppData\Roaming\AntiSpyware.exe ()
O4 - HKCU..\Run: [MusicManager] C:\Users\Charlene\AppData\Local\Programs\Google\MusicManager\MusicManager.exe (Google Inc.)
O4 - HKCU..\Run: [MYPROXYREG] C:\Users\Charlene\AppData\Roaming\MYPROXY.exe ()
O4 - HKCU..\Run: [Octoshape Streaming Services] C:\Users\Charlene\AppData\Roaming\Octoshape\Octoshape Streaming Services\OctoshapeClient.exe (Octoshape ApS)
O4 - HKCU..\Run: [SandboxieControl] C:\Program Files\Sandboxie\SbieCtrl.exe (tzuk)
O4 - Startup: C:\Users\Charlene\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\Warner Bros.lnk = File not found
O6 - HKLM\Software\Policies\Microsoft\Internet Explorer\control panel present
O6 - HKLM\Software\Policies\Microsoft\Internet Explorer\restrictions present
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDriveTypeAutoRun = 255
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: HideSCAHealth = 1
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: ConsentPromptBehaviorUser = 3
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: ConsentPromptBehaviorAdmin = 0
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: EnableLUA = 0
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: PromptOnSecureDesktop = 0
O7 - HKCU\Software\Policies\Microsoft\Internet Explorer\control panel present
O7 - HKCU\Software\Policies\Microsoft\Internet Explorer\restrictions present
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDriveTypeAutoRun = 145
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: DontDisplayLogonHoursWarnings = 1
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: LogonHoursAction = 2
O9 - Extra Button: Skype Plug-In - {898EA8C8-E7FF-479B-8935-AEC46303B9E5} - C:\Program Files\Skype\Toolbars\Internet Explorer\skypeieplugin.dll (Skype Technologies S.A.)
O9 - Extra 'Tools' menuitem : Skype Plug-In - {898EA8C8-E7FF-479B-8935-AEC46303B9E5} - C:\Program Files\Skype\Toolbars\Internet Explorer\skypeieplugin.dll (Skype Technologies S.A.)
O10 - NameSpace_Catalog5\Catalog_Entries\000000000009 [] - C:\Program Files\Bonjour\mdnsNSP.dll (Apple Inc.)
O10 - Protocol_Catalog9\Catalog_Entries\000000000001 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000002 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000003 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000004 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000005 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000006 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000007 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000008 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000009 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000010 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000011 - C:\Program Files\VMware\VMware Player\vsocklib.dll (VMware, Inc.)
O10 - Protocol_Catalog9\Catalog_Entries\000000000012 - C:\Program Files\VMware\VMware Player\vsocklib.dll (VMware, Inc.)
O10 - Protocol_Catalog9\Catalog_Entries\000000000013 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000014 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000015 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000016 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000017 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000018 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000019 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000020 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000021 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000022 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000023 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000024 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000025 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000026 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000027 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000028 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000029 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000030 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000031 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000032 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000033 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000034 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000035 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000036 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000037 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000038 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000039 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000040 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000041 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000042 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000043 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000044 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000045 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000046 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000047 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000048 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000049 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000050 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000051 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000052 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000053 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000054 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000055 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000056 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000057 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000058 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000059 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000060 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000061 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O10 - Protocol_Catalog9\Catalog_Entries\000000000062 - C:\Program Files\Bonjour\mdnsNSP.dll File not found
O15 - HKCU\..Trusted Domains: clonewarsadventures.com ([]* in Trusted sites)
O15 - HKCU\..Trusted Domains: freerealms.com ([]* in Trusted sites)
O15 - HKCU\..Trusted Domains: soe.com ([]* in Trusted sites)
O15 - HKCU\..Trusted Domains: sony.com ([]* in Trusted sites)
O16 - DPF: {140E4DF8-9E14-4A34-9577-C77561ED7883} http://content.systemrequirementslab.com.s…ri_4.1.72.0.cab (SysInfo Class)
O16 - DPF: {1D4DB7D2-6EC9-47A3-BD87-1E41684E07BB} http://ak.exe.imgfarm.com/images/nocache/f…etup1.0.1.1.cab (Reg Error: Key error.)
O16 - DPF: {1E54D648-B804-468d-BC78-4AFFED8E262F} http://www.nvidia.com/content/DriverDownlo…sreqlab_nvd.cab (System Requirements Lab Class)
O16 - DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_26)
O16 - DPF: {CAFEEFAC-0016-0000-0026-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_26)
O16 - DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_26)
O16 - DPF: {D27CDB6E-AE6D-11CF-96B8-444553540000} http://fpdownload2.macromedia.com/get/flas…ent/swflash.cab (Shockwave Flash Object)
O16 - DPF: {E2883E8F-472F-4FB0-9522-AC9BF37916A7} http://platformdl.adobe.com/NOS/getPlusPlus/1.6/gp.cab (Reg Error: Key error.)
O17 - HKLM\System\CCS\Services\Tcpip\Parameters\Interfaces\{264372B7-DA7D-4234-A6D9-7FDCF51120C4}: DhcpNameServer = 192.168.42.129
O17 - HKLM\System\CCS\Services\Tcpip\Parameters\Interfaces\{86F756FD-58DE-4210-A26C-273640AC17BF}: DhcpNameServer = 192.168.1.1
O17 - HKLM\System\CCS\Services\Tcpip\Parameters\Interfaces\{8BBED319-712F-4296-ACF3-319FC1874FAF}: DhcpNameServer = 8.8.8.8 8.8.4.4
O17 - HKLM\System\CCS\Services\Tcpip\Parameters\Interfaces\{9DC2C279-D6C2-4788-93E0-526D048690DE}: DhcpNameServer = 192.168.42.129
O18 - Protocol\Handler\skype-ie-addon-data {91774881-D725-4E58-B298-07617B9B86A8} - C:\Program Files\Skype\Toolbars\Internet Explorer\skypeieplugin.dll (Skype Technologies S.A.)
O20 - HKLM Winlogon: Shell - (explorer.exe) -C:\Windows\explorer.exe (Microsoft Corporation)
O20 - HKLM Winlogon: UserInit - (C:\Windows\system32\userinit.exe) -C:\Windows\System32\userinit.exe (Microsoft Corporation)
O20 - HKLM Winlogon: VMApplet - (SystemPropertiesPerformance.exe) -C:\Windows\System32\SystemPropertiesPerformance.exe (Microsoft Corporation)
O20 - HKLM Winlogon: VMApplet - (/pagefile) - File not found
O21 - SSODL: WebCheck - {E6FB5E20-DE35-11CF-9C87-00AA005127ED} - No CLSID value found.
O22 - SharedTaskScheduler: {1984D045-52CF-49cd-DB77-08F378FEA4DB} - ObjectDockShellExt - No CLSID value found.
O32 - HKLM CDRom: AutoRun - 1
O32 - AutoRun File - [2009/06/10 13:42:20 | 000,000,024 | —- | M] () - C:\autoexec.bat – [ NTFS ]
O33 - MountPoints2\{4e4e3bfb-32ed-11df-9e18-0019d181201d}\Shell - "" = AutoRun
O33 - MountPoints2\{4e4e3bfb-32ed-11df-9e18-0019d181201d}\Shell\AutoRun\command - "" = G:\Autorun.exe
O33 - MountPoints2\{4e4e3bff-32ed-11df-9e18-0019d181201d}\Shell - "" = AutoRun
O33 - MountPoints2\{4e4e3bff-32ed-11df-9e18-0019d181201d}\Shell\AutoRun\command - "" = N:\autorun.exe
O33 - MountPoints2\{cd221640-c26a-11e0-83bc-806e6f6e6963}\Shell - "" = AutoRun
O33 - MountPoints2\{cd221640-c26a-11e0-83bc-806e6f6e6963}\Shell\AutoRun\command - "" = G:\Autorun.exe
O34 - HKLM BootExecute: (autocheck autochk *)
O35 - HKLM\..comfile [open] – "%1" %*
O35 - HKLM\..exefile [open] – "%1" %*
O37 - HKLM\…com [@ = comfile] – "%1" %*
O37 - HKLM\…exe [@ = exefile] – "%1" %*
O37 - HKCU\…exe [@ = exefile] – Reg Error: Key error. File not found

NetSvcs: FastUserSwitchingCompatibility - File not found
NetSvcs: Ias - C:\Windows\System32\ias.dll (Microsoft Corporation)
NetSvcs: Nla - File not found
NetSvcs: Ntmssvc - File not found
NetSvcs: NWCWorkstation - File not found
NetSvcs: Nwsapagent - File not found
NetSvcs: SRService - File not found
NetSvcs: UxTuneUp - C:\Windows\System32\uxtuneup.dll (TuneUp Software)
NetSvcs: WmdmPmSp - File not found
NetSvcs: LogonHours - File not found
NetSvcs: PCAudit - File not found
NetSvcs: helpsvc - File not found
NetSvcs: uploadmgr - File not found

Drivers32: msacm.l3acm - C:\Windows\System32\l3codecp.acm (Fraunhofer Institut Integrierte Schaltungen IIS)
Drivers32: msacm.vorbis - C:\Windows\System32\vorbis.acm (HMS http://hp.vector.co.jp/authors/VA012897/)
Drivers32: MSVideo - C:\Windows\System32\vfwwdm32.dll (Microsoft Corporation)
Drivers32: MSVideo8 - C:\Windows\System32\vfwwdm32.dll (Microsoft Corporation)
Drivers32: vidc.cvid - C:\Windows\System32\iccvid.dll (Radius Inc.)
Drivers32: vidc.DIVX - C:\Windows\System32\DivX.dll (DivX, Inc.)
Drivers32: vidc.ffds - C:\Program Files\Combined Community Codec Pack\Filters\FFDShow\ff_vfw.dll ()
Drivers32: VIDC.FPS1 - C:\Windows\System32\frapsvid.dll (Beepa P/L)
Drivers32: VIDC.I420 - C:\Windows\System32\LVCodec2.dll (Logitech Inc.)
Drivers32: vidc.iv50 - C:\Windows\System32\ir50_32.dll (Intel Corporation)
Drivers32: vidc.tscc - C:\Windows\System32\tsccvid.dll (TechSmith Corporation)
Drivers32: VIDC.VMnc - C:\Windows\System32\vmnc.dll (VMware, Inc.)
Drivers32: vidc.VP60 - C:\Windows\System32\vp6vfw.dll (On2.com)
Drivers32: vidc.VP61 - C:\Windows\System32\vp6vfw.dll (On2.com)
Drivers32: vidc.XVID - C:\Windows\System32\xvidvfw.dll ()
Drivers32: vidc.yv12 - C:\Windows\System32\DivX.dll (DivX, Inc.)

CREATERESTOREPOINT
Error creating restore point.

========== Files/Folders - Created Within 30 Days ==========

[2011/11/15 15:56:31 | 000,518,144 | —- | C] (SteelWerX) – C:\Windows\SWREG.exe
[2011/11/15 15:56:31 | 000,406,528 | —- | C] (SteelWerX) – C:\Windows\SWSC.exe
[2011/11/15 15:56:31 | 000,060,416 | —- | C] (NirSoft) – C:\Windows\NIRCMD.exe
[2011/11/15 15:56:22 | 000,000,000 | –SD | C] – C:\ComboFix
[2011/11/15 15:56:22 | 000,000,000 | —D | C] – C:\Windows\ERDNT
[2011/11/15 15:56:19 | 000,000,000 | —D | C] – C:\Qoobox
[2011/11/15 15:55:59 | 000,000,000 | –SD | C] – C:\32788R22FWJFW
[2011/11/15 10:30:11 | 000,077,824 | —- | C] (TWX Corp.) – C:\Windows\System32\6HWB210E.com
[2011/11/15 10:12:37 | 000,077,824 | —- | C] (TWX Corp.) – C:\Windows\System32\6HWB210E.com_
[2011/11/15 10:03:39 | 000,000,000 | —D | C] – C:\Program Files\1C99B
[2011/11/15 10:02:56 | 000,000,000 | —D | C] – C:\Program Files\LP
[2011/11/15 10:02:30 | 002,784,256 | —- | C] (Корпорация Майкрософт) – C:\Windows\System32\AV Security 2012v121.exe
[2011/11/10 19:52:47 | 000,000,000 | —D | C] – C:\IPS
[2011/11/05 07:54:01 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\STOPzilla
[2011/11/05 07:52:46 | 000,000,000 | —D | C] – C:\Program Files\STOPzilla!
[2011/11/05 07:52:31 | 000,000,000 | —D | C] – C:\Program Files\Common Files\iS3
[2011/11/05 07:52:22 | 000,000,000 | —D | C] – C:\ProgramData\STOPzilla!
[2011/11/05 07:47:45 | 000,000,000 | —D | C] – C:\TDSSKiller_Quarantine
[2011/11/05 07:20:39 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{6DC7570E-2B3A-4C06-A12B-F4F4CB8F4DB2}
[2011/11/05 07:20:25 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{4ECCCD6C-7EE2-4A58-948C-BA2D9DC3EC5F}
[2011/11/05 07:16:54 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\System Security 2012
[2011/11/05 07:16:53 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Roaming\YAA11ivvD2
[2011/11/05 07:16:53 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Roaming\wXwwkkUVelOBzPy
[2011/11/04 23:47:42 | 000,546,256 | R— | C] (iS3, Inc.) – C:\Windows\System32\SZComp5.dll
[2011/11/04 23:47:42 | 000,480,720 | R— | C] (iS3, Inc.) – C:\Windows\System32\SZBase5.dll
[2011/11/04 23:47:42 | 000,132,560 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3HTUI5.dll
[2011/11/04 23:47:42 | 000,022,992 | R— | C] (iS3, Inc.) – C:\Windows\System32\SZIO5.dll
[2011/11/04 23:47:40 | 000,738,768 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3Base5.dll
[2011/11/04 23:47:40 | 000,456,144 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3DBA5.dll
[2011/11/04 23:47:40 | 000,390,608 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3UI5.dll
[2011/11/04 23:47:40 | 000,230,864 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3Win325.dll
[2011/11/04 23:47:40 | 000,103,888 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3Inet5.dll
[2011/11/04 23:47:40 | 000,099,792 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3Svc5.dll
[2011/11/04 23:47:40 | 000,067,024 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3Hks5.dll
[2011/11/04 23:47:40 | 000,028,624 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3XDat5.dll
[2011/11/02 20:23:28 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{0E4EA1E8-C652-492A-B23F-1469C89D91EB}
[2011/11/02 20:23:07 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{59631260-21CC-4C22-8B7D-82C6AC77D9B3}
[2011/11/02 08:22:40 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{16EF2E86-40A0-4E22-83CE-8EC28BE1748F}
[2011/11/01 20:22:03 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{0B00B735-1799-4F9D-B0A9-3ED066E6E4E3}
[2011/11/01 20:21:52 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{FEB5FCDE-02E8-4F32-A3B1-565189DD69FC}
[2011/11/01 07:34:35 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{9472EB8A-7856-4C29-87FB-9D58C09ACD83}
[2011/10/31 19:33:58 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{92992902-AFE7-45F9-8B86-C03D4A54765E}
[2011/10/31 07:33:22 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{D21D86D9-138F-4989-A195-C9E5F12BB149}
[2011/10/30 19:32:40 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{2EDA655C-319D-45E0-AA92-1C3CC65C5DB7}
[2011/10/30 07:32:01 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{C4B44D3E-BAA6-41C3-B59F-D3F1C3457078}
[2011/10/29 19:31:25 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{AD22635F-1CD3-4F5B-8C7A-5229A543334D}
[2011/10/29 07:30:29 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{9DEC7AF9-4A57-4AF4-A11B-02285AAE09C9}
[2011/10/29 07:30:12 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{C13868E2-5F45-4849-BC42-9B2F91372189}
[2011/10/28 15:42:13 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{D5831792-7764-4748-9011-F87FD3572E3D}
[2011/10/28 15:41:51 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{CFAF89E8-3342-45E6-A1ED-724303BC2ECA}
[2011/10/28 03:41:20 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{A225082D-F28D-46A7-BECD-710E9A337DCE}
[2011/10/27 15:40:43 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{A503EAAB-72B5-467D-87DA-E582DFD4DBEC}
[2011/10/27 15:40:33 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{C6FF08F3-4D30-4A3A-8AFB-24D9CA55EE1B}
[2011/10/26 18:18:37 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{C3B002E9-A8F4-4557-A17E-00B7C54AA9F1}
[2011/10/26 18:18:14 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{3444873C-58DF-4F69-8769-0379CF926BA1}
[2011/10/26 06:17:44 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{C5491DA3-6592-4F23-B32A-35B07840AD8A}
[2011/10/26 06:17:32 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{3C6A7CA4-44B8-4DED-94CB-C2EAE398049C}
[2011/10/24 17:37:08 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{FF3E0397-BB32-4726-8BEA-FA2BFEBF1D2A}
[2011/10/24 17:36:53 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{11BD93B8-7757-4680-914A-3D229F174478}
[2011/10/22 20:13:50 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{90483FE8-AE78-4300-A952-EBFB89082D79}
[2011/10/22 20:13:34 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{316CA11D-C16D-4FF7-9471-77ED7452057A}
[2011/10/21 14:29:05 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{F60CB82B-E030-4483-943C-0C7652E4AE89}
[2011/10/21 14:28:54 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{EF93AA2A-EB8E-4D1D-BA3E-1A8C2C69F510}
[2011/10/20 20:38:05 | 000,000,000 | —D | C] – C:\Program Files\Maxis
[2011/10/20 17:59:35 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Focus Home Interactive
[2011/10/20 17:57:44 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\Focus Home Interactive
[2011/10/20 17:47:58 | 000,000,000 | —D | C] – C:\Program Files\Focus Home Interactive
[2011/10/20 17:01:12 | 000,232,512 | —- | C] (DT Soft Ltd) – C:\Windows\System32\drivers\dtsoftbus01.sys
[2011/10/20 16:54:51 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{8D65256F-9329-445D-9CE8-DA4852C239D6}
[2011/10/20 16:54:40 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{7E07CED2-EA01-44D6-9963-00EF92F359EC}
[2011/10/19 22:45:09 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Roaming\vlc
[2011/10/19 22:45:01 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\VideoLAN
[2011/10/19 22:44:37 | 000,000,000 | —D | C] – C:\Program Files\VideoLAN
[2011/10/19 17:07:35 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{2FA2A326-8FDC-4BC1-9D26-AFE7BCC71CB8}
[2011/10/19 17:07:23 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{95842016-CD6E-41EE-B0BE-EB84598EAB43}
[2011/10/17 23:21:31 | 000,000,000 | —D | C] – C:\Users\Charlene\pic
[2011/10/17 17:28:37 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{602DE050-F8F5-4C03-B064-DD48C7E7A2BD}
[2011/10/17 17:28:21 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{512DDC72-13D9-4A76-83C8-7F501F276EE0}
[2011/08/08 15:01:09 | 000,557,056 | —- | C] ( ) – C:\Windows\System32\raac.dll
[2011/08/08 15:01:09 | 000,139,264 | —- | C] ( ) – C:\Windows\System32\sipr.dll
[2011/08/08 15:01:09 | 000,057,344 | —- | C] ( ) – C:\Windows\System32\rv20.dll
[2011/08/08 15:01:09 | 000,053,248 | —- | C] ( ) – C:\Windows\System32\rv30.dll
[2011/08/08 15:01:09 | 000,049,152 | —- | C] ( ) – C:\Windows\System32\rv40.dll
[2011/08/08 15:01:08 | 000,286,720 | —- | C] ( ) – C:\Windows\System32\drvc.dll
[2011/08/08 15:01:08 | 000,180,224 | —- | C] ( ) – C:\Windows\System32\drv2.dll
[2011/08/08 15:01:07 | 000,548,919 | —- | C] ( ) – C:\Windows\System32\colorcvt.dll
[2011/08/08 15:01:07 | 000,090,112 | —- | C] ( ) – C:\Windows\System32\atrc.dll
[2011/08/08 15:01:07 | 000,065,602 | —- | C] ( ) – C:\Windows\System32\cook.dll
[2010/02/18 21:49:29 | 000,446,464 | —- | C] ( ) – C:\Windows\System32\LXDUhcp.dll
[2010/02/18 21:40:29 | 000,368,640 | —- | C] ( ) – C:\Windows\System32\lexlog.dll
[2010/01/19 15:49:48 | 000,047,360 | —- | C] (VSO Software) – C:\Users\Charlene\AppData\Roaming\pcouffin.sys
[2009/10/26 09:10:24 | 001,069,056 | —- | C] ( ) – C:\Windows\System32\lxduserv.dll
[2009/10/26 09:10:23 | 000,651,264 | —- | C] ( ) – C:\Windows\System32\lxdupmui.dll
[2009/10/26 09:10:21 | 000,577,536 | —- | C] ( ) – C:\Windows\System32\lxdulmpm.dll
[2009/10/26 09:10:19 | 000,376,832 | —- | C] ( ) – C:\Windows\System32\lxducomm.dll
[2009/10/26 09:10:18 | 000,364,544 | —- | C] ( ) – C:\Windows\System32\lxduinpa.dll
[2009/10/26 09:10:17 | 000,339,968 | —- | C] ( ) – C:\Windows\System32\lxduiesc.dll
[2009/10/26 09:10:15 | 000,761,856 | —- | C] ( ) – C:\Windows\System32\lxducomc.dll
[2009/10/26 09:10:10 | 000,860,160 | —- | C] ( ) – C:\Windows\System32\lxduusb1.dll
[2009/10/26 09:10:09 | 000,684,032 | —- | C] ( ) – C:\Windows\System32\lxduhbn3.dll
[2009/08/19 20:16:42 | 000,328,360 | —- | C] ( ) – C:\Windows\System32\lxduih.exe
[2009/08/19 20:16:40 | 000,594,600 | —- | C] ( ) – C:\Windows\System32\lxducoms.exe
[2009/08/19 20:16:40 | 000,369,320 | —- | C] ( ) – C:\Windows\System32\lxducfg.exe
[2009/07/10 17:59:32 | 000,409,600 | —- | C] ( ) – C:\Windows\System32\lxducoin.dll
[1 C:\Windows\*.tmp files -> C:\Windows\*.tmp -> ]
[1 C:\ProgramData\*.tmp files -> C:\ProgramData\*.tmp -> ]
[1 C:\ProgramData\*.tmp files -> C:\ProgramData\*.tmp -> ]

========== Files - Modified Within 30 Days ==========

[2055/09/18 22:29:11 | 000,002,012 | —- | M] () – C:\Windows\System32\NAV_75_cltDynam.dat
[2011/11/15 15:38:28 | 000,065,536 | —- | M] () – C:\Windows\System32\Ikeext.etl
[2011/11/15 15:38:16 | 000,067,584 | –S- | M] () – C:\Windows\bootstat.dat
[2011/11/15 10:32:29 | 000,000,352 | —- | M] () – C:\Windows\tasks\At22.job
[2011/11/15 10:30:19 | 000,000,350 | —- | M] () – C:\Windows\tasks\At21.job
[2011/11/15 10:22:05 | 000,000,920 | —- | M] () – C:\Windows\tasks\GoogleUpdateTaskUserS-1-5-21-1842821427-920554174-299800973-1000UA.job
[2011/11/15 10:15:07 | 000,000,112 | —- | M] () – C:\ProgramData\r26fSjfW.dat
[2011/11/15 10:15:00 | 000,000,940 | —- | M] () – C:\Windows\tasks\FacebookUpdateTaskUserS-1-5-21-1842821427-920554174-299800973-1000UA.job
[2011/11/15 10:14:54 | 000,077,824 | —- | M] (TWX Corp.) – C:\Windows\System32\6HWB210E.com_
[2011/11/15 10:14:54 | 000,077,824 | —- | M] (TWX Corp.) – C:\Windows\System32\6HWB210E.com
[2011/11/15 10:12:47 | 000,000,352 | —- | M] () – C:\Windows\tasks\At48.job
[2011/11/15 10:12:47 | 000,000,352 | —- | M] () – C:\Windows\tasks\At46.job
[2011/11/15 10:12:47 | 000,000,350 | —- | M] () – C:\Windows\tasks\At47.job
[2011/11/15 10:12:47 | 000,000,350 | —- | M] () – C:\Windows\tasks\At45.job
[2011/11/15 10:12:46 | 000,000,352 | —- | M] () – C:\Windows\tasks\At44.job
[2011/11/15 10:12:46 | 000,000,352 | —- | M] () – C:\Windows\tasks\At42.job
[2011/11/15 10:12:46 | 000,000,352 | —- | M] () – C:\Windows\tasks\At40.job
[2011/11/15 10:12:46 | 000,000,350 | —- | M] () – C:\Windows\tasks\At43.job
[2011/11/15 10:12:46 | 000,000,350 | —- | M] () – C:\Windows\tasks\At41.job
[2011/11/15 10:12:45 | 000,000,352 | —- | M] () – C:\Windows\tasks\At38.job
[2011/11/15 10:12:45 | 000,000,352 | —- | M] () – C:\Windows\tasks\At36.job
[2011/11/15 10:12:45 | 000,000,352 | —- | M] () – C:\Windows\tasks\At34.job
[2011/11/15 10:12:45 | 000,000,350 | —- | M] () – C:\Windows\tasks\At39.job
[2011/11/15 10:12:45 | 000,000,350 | —- | M] () – C:\Windows\tasks\At37.job
[2011/11/15 10:12:45 | 000,000,350 | —- | M] () – C:\Windows\tasks\At35.job
[2011/11/15 10:12:44 | 000,000,352 | —- | M] () – C:\Windows\tasks\At32.job
[2011/11/15 10:12:44 | 000,000,352 | —- | M] () – C:\Windows\tasks\At30.job
[2011/11/15 10:12:44 | 000,000,352 | —- | M] () – C:\Windows\tasks\At28.job
[2011/11/15 10:12:44 | 000,000,350 | —- | M] () – C:\Windows\tasks\At33.job
[2011/11/15 10:12:44 | 000,000,350 | —- | M] () – C:\Windows\tasks\At31.job
[2011/11/15 10:12:44 | 000,000,350 | —- | M] () – C:\Windows\tasks\At29.job
[2011/11/15 10:12:43 | 000,000,352 | —- | M] () – C:\Windows\tasks\At26.job
[2011/11/15 10:12:43 | 000,000,352 | —- | M] () – C:\Windows\tasks\At24.job
[2011/11/15 10:12:43 | 000,000,350 | —- | M] () – C:\Windows\tasks\At27.job
[2011/11/15 10:12:43 | 000,000,350 | —- | M] () – C:\Windows\tasks\At25.job
[2011/11/15 10:12:43 | 000,000,350 | —- | M] () – C:\Windows\tasks\At23.job
[2011/11/15 10:12:42 | 000,000,352 | —- | M] () – C:\Windows\tasks\At20.job
[2011/11/15 10:12:42 | 000,000,352 | —- | M] () – C:\Windows\tasks\At18.job
[2011/11/15 10:12:42 | 000,000,352 | —- | M] () – C:\Windows\tasks\At16.job
[2011/11/15 10:12:42 | 000,000,350 | —- | M] () – C:\Windows\tasks\At19.job
[2011/11/15 10:12:42 | 000,000,350 | —- | M] () – C:\Windows\tasks\At17.job
[2011/11/15 10:12:41 | 000,000,352 | —- | M] () – C:\Windows\tasks\At14.job
[2011/11/15 10:12:41 | 000,000,352 | —- | M] () – C:\Windows\tasks\At12.job
[2011/11/15 10:12:41 | 000,000,350 | —- | M] () – C:\Windows\tasks\At15.job
[2011/11/15 10:12:41 | 000,000,350 | —- | M] () – C:\Windows\tasks\At13.job
[2011/11/15 10:12:40 | 000,000,352 | —- | M] () – C:\Windows\tasks\At8.job
[2011/11/15 10:12:40 | 000,000,352 | —- | M] () – C:\Windows\tasks\At10.job
[2011/11/15 10:12:40 | 000,000,350 | —- | M] () – C:\Windows\tasks\At9.job
[2011/11/15 10:12:40 | 000,000,350 | —- | M] () – C:\Windows\tasks\At7.job
[2011/11/15 10:12:40 | 000,000,350 | —- | M] () – C:\Windows\tasks\At11.job
[2011/11/15 10:12:39 | 000,000,352 | —- | M] () – C:\Windows\tasks\At6.job
[2011/11/15 10:12:39 | 000,000,350 | —- | M] () – C:\Windows\tasks\At5.job
[2011/11/15 10:12:38 | 000,000,352 | —- | M] () – C:\Windows\tasks\At4.job
[2011/11/15 10:12:38 | 000,000,352 | —- | M] () – C:\Windows\tasks\At2.job
[2011/11/15 10:12:38 | 000,000,350 | —- | M] () – C:\Windows\tasks\At3.job
[2011/11/15 10:12:38 | 000,000,350 | —- | M] () – C:\Windows\tasks\At1.job
[2011/11/15 10:02:30 | 002,784,256 | —- | M] (Корпорация Майкрософт) – C:\Windows\System32\AV Security 2012v121.exe
[2011/11/15 00:54:50 | 000,711,876 | —- | M] () – C:\Windows\System32\perfh009.dat
[2011/11/15 00:54:50 | 000,140,264 | —- | M] () – C:\Windows\System32\perfc009.dat
[2011/11/14 22:15:01 | 000,000,918 | —- | M] () – C:\Windows\tasks\FacebookUpdateTaskUserS-1-5-21-1842821427-920554174-299800973-1000Core.job
[2011/11/14 15:22:00 | 000,000,868 | —- | M] () – C:\Windows\tasks\GoogleUpdateTaskUserS-1-5-21-1842821427-920554174-299800973-1000Core.job
[2011/11/14 13:57:56 | 000,215,201 | —- | M] () – C:\Users\Charlene\Desktop\playing3.jpg
[2011/11/14 13:56:47 | 000,201,852 | —- | M] () – C:\Users\Charlene\Desktop\playing2.jpg
[2011/11/14 13:55:58 | 000,200,271 | —- | M] () – C:\Users\Charlene\Desktop\playing.jpg
[2011/11/10 19:53:38 | 000,007,168 | —- | M] () – C:\Users\Charlene\AppData\Roaming\mswlnsys32.dll
[2011/11/10 19:53:37 | 000,007,168 | —- | M] () – C:\Users\Charlene\AppData\Roaming\MYPROXYDLL.dll
[2011/11/09 07:41:26 | 000,001,069 | —- | M] () – C:\Users\Charlene\Desktop\Videos - Shortcut.lnk
[2011/11/05 07:45:08 | 000,232,512 | —- | M] (DT Soft Ltd) – C:\Windows\System32\drivers\dtsoftbus01.sys
[2011/11/05 07:17:50 | 000,001,213 | —- | M] () – C:\Users\Charlene\AppData\Roaming\ldr.ini
[2011/11/04 23:47:42 | 000,546,256 | R— | M] (iS3, Inc.) – C:\Windows\System32\SZComp5.dll
[2011/11/04 23:47:42 | 000,480,720 | R— | M] (iS3, Inc.) – C:\Windows\System32\SZBase5.dll
[2011/11/04 23:47:42 | 000,132,560 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3HTUI5.dll
[2011/11/04 23:47:42 | 000,022,992 | R— | M] (iS3, Inc.) – C:\Windows\System32\SZIO5.dll
[2011/11/04 23:47:40 | 000,738,768 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3Base5.dll
[2011/11/04 23:47:40 | 000,456,144 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3DBA5.dll
[2011/11/04 23:47:40 | 000,390,608 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3UI5.dll
[2011/11/04 23:47:40 | 000,230,864 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3Win325.dll
[2011/11/04 23:47:40 | 000,103,888 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3Inet5.dll
[2011/11/04 23:47:40 | 000,099,792 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3Svc5.dll
[2011/11/04 23:47:40 | 000,067,024 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3Hks5.dll
[2011/11/04 23:47:40 | 000,028,624 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3XDat5.dll
[2011/11/03 06:33:39 | 000,001,444 | —- | M] () – C:\Windows\Sandboxie.ini
[2011/10/26 06:16:34 | 000,414,368 | —- | M] (Adobe Systems Incorporated) – C:\Windows\System32\FlashPlayerCPLApp.cpl
[2011/10/24 20:21:04 | 000,000,861 | —- | M] () – C:\Users\Public\Desktop\Mozilla Firefox.lnk
[2011/10/23 16:28:40 | 000,273,736 | —- | M] () – C:\Users\Charlene\Desktop\kelly bodybuilder.png
[2011/10/23 16:28:40 | 000,000,132 | —- | M] () – C:\Users\Charlene\AppData\Roaming\Adobe PNG Format CS5 Prefs
[2011/10/23 15:30:30 | 000,065,361 | —- | M] () – C:\Users\Charlene\Desktop\kelly.jpg
[2011/10/20 20:38:11 | 000,000,534 | —- | M] () – C:\Windows\eReg.dat
[2011/10/20 18:02:11 | 000,002,187 | —- | M] () – C:\Users\Public\Desktop\Cities XL 2011.lnk
[1 C:\Windows\*.tmp files -> C:\Windows\*.tmp -> ]
[1 C:\ProgramData\*.tmp files -> C:\ProgramData\*.tmp -> ]
[1 C:\ProgramData\*.tmp files -> C:\ProgramData\*.tmp -> ]

========== Files Created - No Company Name ==========

[2011/11/15 15:56:31 | 000,256,000 | —- | C] () – C:\Windows\PEV.exe
[2011/11/15 15:56:31 | 000,208,896 | —- | C] () – C:\Windows\MBR.exe
[2011/11/15 15:56:31 | 000,098,816 | —- | C] () – C:\Windows\sed.exe
[2011/11/15 15:56:31 | 000,080,412 | —- | C] () – C:\Windows\grep.exe
[2011/11/15 15:56:31 | 000,068,096 | —- | C] () – C:\Windows\zip.exe
[2011/11/15 10:12:49 | 000,000,112 | —- | C] () – C:\ProgramData\r26fSjfW.dat
[2011/11/15 10:12:47 | 000,000,352 | —- | C] () – C:\Windows\tasks\At48.job
[2011/11/15 10:12:47 | 000,000,352 | —- | C] () – C:\Windows\tasks\At46.job
[2011/11/15 10:12:47 | 000,000,350 | —- | C] () – C:\Windows\tasks\At47.job
[2011/11/15 10:12:46 | 000,000,352 | —- | C] () – C:\Windows\tasks\At44.job
[2011/11/15 10:12:46 | 000,000,352 | —- | C] () – C:\Windows\tasks\At42.job
[2011/11/15 10:12:46 | 000,000,350 | —- | C] () – C:\Windows\tasks\At45.job
[2011/11/15 10:12:46 | 000,000,350 | —- | C] () – C:\Windows\tasks\At43.job
[2011/11/15 10:12:46 | 000,000,350 | —- | C] () – C:\Windows\tasks\At41.job
[2011/11/15 10:12:45 | 000,000,352 | —- | C] () – C:\Windows\tasks\At40.job
[2011/11/15 10:12:45 | 000,000,352 | —- | C] () – C:\Windows\tasks\At38.job
[2011/11/15 10:12:45 | 000,000,352 | —- | C] () – C:\Windows\tasks\At36.job
[2011/11/15 10:12:45 | 000,000,350 | —- | C] () – C:\Windows\tasks\At39.job
[2011/11/15 10:12:45 | 000,000,350 | —- | C] () – C:\Windows\tasks\At37.job
[2011/11/15 10:12:45 | 000,000,350 | —- | C] () – C:\Windows\tasks\At35.job
[2011/11/15 10:12:44 | 000,000,352 | —- | C] () – C:\Windows\tasks\At34.job
[2011/11/15 10:12:44 | 000,000,352 | —- | C] () – C:\Windows\tasks\At32.job
[2011/11/15 10:12:44 | 000,000,352 | —- | C] () – C:\Windows\tasks\At30.job
[2011/11/15 10:12:44 | 000,000,350 | —- | C] () – C:\Windows\tasks\At33.job
[2011/11/15 10:12:44 | 000,000,350 | —- | C] () – C:\Windows\tasks\At31.job
[2011/11/15 10:12:44 | 000,000,350 | —- | C] () – C:\Windows\tasks\At29.job
[2011/11/15 10:12:43 | 000,000,352 | —- | C] () – C:\Windows\tasks\At28.job
[2011/11/15 10:12:43 | 000,000,352 | —- | C] () – C:\Windows\tasks\At26.job
[2011/11/15 10:12:43 | 000,000,352 | —- | C] () – C:\Windows\tasks\At24.job
[2011/11/15 10:12:43 | 000,000,352 | —- | C] () – C:\Windows\tasks\At22.job
[2011/11/15 10:12:43 | 000,000,350 | —- | C] () – C:\Windows\tasks\At27.job
[2011/11/15 10:12:43 | 000,000,350 | —- | C] () – C:\Windows\tasks\At25.job
[2011/11/15 10:12:43 | 000,000,350 | —- | C] () – C:\Windows\tasks\At23.job
[2011/11/15 10:12:42 | 000,000,352 | —- | C] () – C:\Windows\tasks\At20.job
[2011/11/15 10:12:42 | 000,000,352 | —- | C] () – C:\Windows\tasks\At18.job
[2011/11/15 10:12:42 | 000,000,350 | —- | C] () – C:\Windows\tasks\At21.job
[2011/11/15 10:12:42 | 000,000,350 | —- | C] () – C:\Windows\tasks\At19.job
[2011/11/15 10:12:42 | 000,000,350 | —- | C] () – C:\Windows\tasks\At17.job
[2011/11/15 10:12:41 | 000,000,352 | —- | C] () – C:\Windows\tasks\At16.job
[2011/11/15 10:12:41 | 000,000,352 | —- | C] () – C:\Windows\tasks\At14.job
[2011/11/15 10:12:41 | 000,000,350 | —- | C] () – C:\Windows\tasks\At15.job
[2011/11/15 10:12:41 | 000,000,350 | —- | C] () – C:\Windows\tasks\At13.job
[2011/11/15 10:12:40 | 000,000,352 | —- | C] () – C:\Windows\tasks\At8.job
[2011/11/15 10:12:40 | 000,000,352 | —- | C] () – C:\Windows\tasks\At12.job
[2011/11/15 10:12:40 | 000,000,352 | —- | C] () – C:\Windows\tasks\At10.job
[2011/11/15 10:12:40 | 000,000,350 | —- | C] () – C:\Windows\tasks\At9.job
[2011/11/15 10:12:40 | 000,000,350 | —- | C] () – C:\Windows\tasks\At11.job
[2011/11/15 10:12:39 | 000,000,352 | —- | C] () – C:\Windows\tasks\At6.job
[2011/11/15 10:12:39 | 000,000,350 | —- | C] () – C:\Windows\tasks\At7.job
[2011/11/15 10:12:38 | 000,000,352 | —- | C] () – C:\Windows\tasks\At4.job
[2011/11/15 10:12:38 | 000,000,352 | —- | C] () – C:\Windows\tasks\At2.job
[2011/11/15 10:12:38 | 000,000,350 | —- | C] () – C:\Windows\tasks\At5.job
[2011/11/15 10:12:38 | 000,000,350 | —- | C] () – C:\Windows\tasks\At3.job
[2011/11/15 10:12:37 | 000,000,350 | —- | C] () – C:\Windows\tasks\At1.job
[2011/11/14 13:57:56 | 000,215,201 | —- | C] () – C:\Users\Charlene\Desktop\playing3.jpg
[2011/11/14 13:56:47 | 000,201,852 | —- | C] () – C:\Users\Charlene\Desktop\playing2.jpg
[2011/11/14 13:55:58 | 000,200,271 | —- | C] () – C:\Users\Charlene\Desktop\playing.jpg
[2011/11/09 07:41:26 | 000,001,069 | —- | C] () – C:\Users\Charlene\Desktop\Videos - Shortcut.lnk
[2011/11/05 07:16:53 | 000,001,213 | —- | C] () – C:\Users\Charlene\AppData\Roaming\ldr.ini
[2011/10/24 20:21:04 | 000,000,861 | —- | C] () – C:\Users\Public\Desktop\Mozilla Firefox.lnk
[2011/10/24 20:21:04 | 000,000,843 | —- | C] () – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Mozilla Firefox.lnk
[2011/10/23 16:28:40 | 000,273,736 | —- | C] () – C:\Users\Charlene\Desktop\kelly bodybuilder.png
[2011/10/23 15:30:46 | 000,065,361 | —- | C] () – C:\Users\Charlene\Desktop\kelly.jpg
[2011/10/20 20:38:11 | 000,000,534 | —- | C] () – C:\Windows\eReg.dat
[2011/10/20 18:02:11 | 000,002,187 | —- | C] () – C:\Users\Public\Desktop\Cities XL 2011.lnk
[2011/08/08 15:01:19 | 000,819,200 | —- | C] () – C:\Windows\System32\xvidcore.dll
[2011/08/08 15:01:19 | 000,180,224 | —- | C] () – C:\Windows\System32\xvidvfw.dll
[2011/08/07 02:31:18 | 000,000,000 | —- | C] () – C:\Windows\PowerReg.dat
[2011/08/07 02:26:49 | 000,000,484 | —- | C] () – C:\Windows\hegames.ini
[2011/08/03 16:55:15 | 000,007,605 | —- | C] () – C:\Users\Charlene\AppData\Local\Resmon.ResmonCfg
[2011/07/25 22:47:48 | 000,043,520 | —- | C] () – C:\Windows\System32\CmdLineExt03.dll
[2011/07/02 01:21:46 | 000,001,456 | —- | C] () – C:\Users\Charlene\AppData\Local\Adobe Save for Web 12.0 Prefs
[2011/05/20 21:35:28 | 000,304,744 | —- | C] () – C:\Windows\System32\nvStreaming.exe
[2011/02/22 07:03:48 | 000,007,168 | —- | C] () – C:\Users\Charlene\AppData\Roaming\MYPROXYDLL.dll
[2011/02/21 04:10:43 | 000,007,168 | —- | C] () – C:\Users\Charlene\AppData\Roaming\mswlnsys32.dll
[2011/02/21 04:10:31 | 000,012,800 | RHS- | C] () – C:\Users\Charlene\AppData\Roaming\AntiSpyware.exe
[2011/02/21 01:43:11 | 000,012,800 | RHS- | C] () – C:\Users\Charlene\AppData\Roaming\MYPROXY.exe
[2011/02/14 22:53:45 | 000,057,344 | —- | C] () – C:\Windows\System32\ff_vfw.dll
[2011/02/14 21:20:53 | 000,000,132 | —- | C] () – C:\Users\Charlene\AppData\Roaming\Adobe PNG Format CS5 Prefs
[2011/01/29 17:00:24 | 000,030,568 | —- | C] () – C:\Windows\MusiccityDownload.exe
[2011/01/29 17:00:22 | 000,974,848 | —- | C] () – C:\Windows\System32\cis-2.4.dll
[2011/01/29 17:00:22 | 000,081,920 | —- | C] () – C:\Windows\System32\issacapi_bs-2.3.dll
[2011/01/29 17:00:22 | 000,065,536 | —- | C] () – C:\Windows\System32\issacapi_pe-2.3.dll
[2011/01/29 17:00:22 | 000,057,344 | —- | C] () – C:\Windows\System32\issacapi_se-2.3.dll
[2011/01/21 18:30:59 | 000,000,029 | —- | C] () – C:\Users\Charlene\AppData\Roaming\RSBot_Accounts.ini
[2010/10/31 10:25:01 | 003,514,368 | —- | C] () – C:\Program Files\INCOMPLETE~208-taylor_swift-the_story_of_us_(us_version).mp3
[2010/10/31 10:22:51 | 007,525,691 | —- | C] () – C:\Program Files\207-taylor_swift-back_to_december_(us_version).mp3
[2010/10/31 10:22:05 | 006,603,340 | —- | C] () – C:\Program Files\102-taylor_swift-sparks_fly.mp3
[2010/10/31 10:21:10 | 007,160,839 | —- | C] () – C:\Program Files\103-taylor_swift-back_to_december.mp3
[2010/10/31 10:20:30 | 005,918,969 | —- | C] () – C:\Program Files\104-taylor_swift-speak_now.mp3
[2010/10/31 10:19:27 | 009,054,846 | —- | C] () – C:\Program Files\105-taylor_swift-dear_john.mp3
[2010/10/31 10:18:46 | 005,531,357 | —- | C] () – C:\Program Files\106-taylor_swift-mean.mp3
[2010/10/31 10:17:56 | 006,915,258 | —- | C] () – C:\Program Files\107-taylor_swift-the_story_of_us.mp3
[2010/10/31 10:17:14 | 006,016,684 | —- | C] () – C:\Program Files\108-taylor_swift-never_grow_up.mp3
[2010/10/31 10:16:08 | 009,129,224 | —- | C] () – C:\Program Files\109-taylor_swift-enchanted.mp3
[2010/10/31 10:15:28 | 005,701,179 | —- | C] () – C:\Program Files\110-taylor_swift-better_than_revenge.mp3
[2010/10/31 10:14:42 | 006,819,869 | —- | C] () – C:\Program Files\111-taylor_swift-innocent.mp3
[2010/10/31 10:13:55 | 006,400,578 | —- | C] () – C:\Program Files\112-taylor_swift-haunted.mp3
[2010/10/31 10:12:53 | 008,773,644 | —- | C] () – C:\Program Files\113-taylor_swift-last_kiss.mp3
[2010/10/31 10:12:01 | 007,517,546 | —- | C] () – C:\Program Files\114-taylor_swift-long_live.mp3
[2010/10/31 10:11:18 | 005,706,399 | —- | C] () – C:\Program Files\201-taylor_swift-ours.mp3
[2010/10/31 10:10:34 | 005,574,290 | —- | C] () – C:\Program Files\202-taylor_swift-if_this_was_a_movie.mp3
[2010/10/31 10:09:33 | 006,869,412 | —- | C] () – C:\Program Files\204-taylor_swift-back_to_december_(acoustic).mp3
[2010/10/31 10:08:29 | 007,124,608 | —- | C] () – C:\Program Files\203-taylor_swift-superman.mp3
[2010/10/31 10:05:46 | 004,878,350 | —- | C] () – C:\Program Files\205-taylor_swift-haunted_(acoustic).mp3
[2010/10/31 10:05:03 | 005,867,918 | —- | C] () – C:\Program Files\206-taylor_swift-mine_(us_version).mp3
[2010/10/31 10:04:20 | 005,609,172 | —- | C] () – C:\Program Files\101-taylor_swift-mine.mp3
[2010/10/27 17:55:22 | 005,219,767 | —- | C] () – C:\Program Files\03 no one's gonna love you.mp3
[2010/10/27 17:55:07 | 005,709,831 | —- | C] () – C:\Program Files\01 the first song.mp3
[2010/10/27 17:53:47 | 005,665,067 | —- | C] () – C:\Program Files\the shins - oh inverted world 05 girl inform me.mp3
[2010/07/20 22:18:32 | 000,082,289 | —- | C] () – C:\Windows\System32\lvcoinst.ini
[2010/07/20 22:09:50 | 000,000,056 | -H– | C] () – C:\Windows\System32\ezsidmv.dat
[2010/06/13 18:45:33 | 000,009,728 | —- | C] () – C:\Windows\System32\uc_karos_launching.dll
[2010/05/21 12:03:13 | 000,000,256 | —- | C] () – C:\Windows\System32\pool.bin
[2010/02/27 19:57:01 | 000,021,316 | —- | C] () – C:\Windows\System32\emptyregdb.dat
[2010/02/18 21:49:29 | 000,389,120 | —- | C] () – C:\Windows\System32\LXDUinst.dll
[2010/01/29 21:53:58 | 000,000,050 | —- | C] () – C:\Windows\MegaManager.INI
[2010/01/19 15:52:40 | 000,001,189 | —- | C] () – C:\Users\Charlene\AppData\Roaming\vso_ts_preview.xml
[2010/01/19 15:49:48 | 000,087,608 | —- | C] () – C:\Users\Charlene\AppData\Roaming\inst.exe
[2010/01/19 15:49:48 | 000,007,887 | —- | C] () – C:\Users\Charlene\AppData\Roaming\pcouffin.cat
[2010/01/19 15:49:48 | 000,001,144 | —- | C] () – C:\Users\Charlene\AppData\Roaming\pcouffin.inf
[2009/12/08 16:19:34 | 000,001,444 | —- | C] () – C:\Windows\Sandboxie.ini
[2009/10/26 09:10:28 | 000,040,960 | —- | C] () – C:\Windows\System32\lxduvs.dll
[2009/10/26 09:09:51 | 000,208,896 | —- | C] () – C:\Windows\System32\lxdugrd.dll
[2009/10/26 09:08:26 | 001,036,288 | —- | C] () – C:\Windows\System32\lxdudrs.dll
[2009/10/26 09:08:26 | 000,081,920 | —- | C] () – C:\Windows\System32\lxducaps.dll
[2009/10/26 09:08:26 | 000,069,632 | —- | C] () – C:\Windows\System32\lxducnv4.dll
[2009/10/18 15:28:12 | 000,000,602 | —- | C] () – C:\Windows\Diamonds.INI
[2009/10/07 12:23:01 | 000,187,612 | -H– | C] () – C:\Windows\System32\mlfcache.dat
[2009/10/07 00:46:36 | 000,025,752 | —- | C] () – C:\Windows\System32\drivers\LVPr2Mon.sys
[2009/10/07 00:23:08 | 000,013,584 | —- | C] () – C:\Windows\System32\drivers\iKeyLFT2.dll
[2009/10/05 17:08:15 | 000,000,208 | —- | C] () – C:\Users\Charlene\AppData\Roaming\iPod Access v4 Prefs
[2009/10/05 16:55:24 | 000,000,047 | -H– | C] () – C:\Users\Charlene\AppData\Roaming\iPodAccessv4_OwnerName
[2009/10/05 16:54:03 | 000,000,011 | -H– | C] () – C:\Users\Charlene\AppData\Roaming\iPodAccess_Time
[2009/10/05 12:10:02 | 000,000,000 | —- | C] () – C:\Windows\nsreg.dat
[2009/09/29 18:05:15 | 000,082,432 | —- | C] () – C:\Windows\System32\ewdll32.dll
[2009/09/29 18:05:15 | 000,077,824 | —- | C] () – C:\Windows\System32\helpmsg32.dll
[2009/09/29 18:05:15 | 000,045,056 | —- | C] () – C:\Windows\System32\avi_util32.dll
[2009/09/29 18:05:15 | 000,000,375 | —- | C] () – C:\Windows\dst_suns.ini
[2009/09/29 16:14:14 | 000,056,056 | —- | C] () – C:\Windows\System32\DLAAPI_W.DLL
[2009/09/29 16:14:14 | 000,000,120 | —- | C] () – C:\Windows\wininit.ini
[2009/09/29 13:09:28 | 000,000,376 | —- | C] () – C:\Windows\ODBC.INI
[2009/09/29 12:58:18 | 000,110,602 | —- | C] () – C:\Windows\System32\xcdsfx32.bin
[2009/09/18 22:00:56 | 000,002,012 | —- | C] () – C:\Windows\System32\NAV_75_cltDynam.dat
[2009/07/13 20:57:37 | 000,067,584 | –S- | C] () – C:\Windows\bootstat.dat
[2009/07/13 20:33:53 | 004,074,120 | —- | C] () – C:\Windows\System32\FNTCACHE.DAT
[2009/07/13 18:05:48 | 000,711,876 | —- | C] () – C:\Windows\System32\perfh009.dat
[2009/07/13 18:05:48 | 000,291,294 | —- | C] () – C:\Windows\System32\perfi009.dat
[2009/07/13 18:05:48 | 000,140,264 | —- | C] () – C:\Windows\System32\perfc009.dat
[2009/07/13 18:05:48 | 000,031,548 | —- | C] () – C:\Windows\System32\perfd009.dat
[2009/07/13 18:05:05 | 000,000,741 | —- | C] () – C:\Windows\System32\NOISE.DAT
[2009/07/13 18:04:11 | 000,215,943 | —- | C] () – C:\Windows\System32\dssec.dat
[2009/07/13 16:19:49 | 000,066,048 | —- | C] () – C:\Windows\System32\PrintBrmUi.exe
[2009/07/13 15:55:01 | 000,043,131 | —- | C] () – C:\Windows\mib.bin
[2009/07/13 15:51:43 | 000,073,728 | —- | C] () – C:\Windows\System32\BthpanContextHandler.dll
[2009/07/13 15:42:10 | 000,064,000 | —- | C] () – C:\Windows\System32\BWContextHandler.dll
[2009/07/13 15:11:26 | 000,108,544 | —- | C] () – C:\Windows\System32\drivers\cdrom.sys
[2009/06/10 13:26:10 | 000,673,088 | —- | C] () – C:\Windows\System32\mlang.dat
[2003/01/07 14:05:08 | 000,002,695 | —- | C] () – C:\Windows\System32\OUTLPERF.INI

========== LOP Check ==========

[2010/10/03 12:31:51 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\.minecraft
[2010/04/06 18:18:59 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\acccore
[2011/05/11 18:32:28 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Acoustica
[2011/09/18 21:35:37 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Applied Acoustics Systems
[2011/09/26 20:58:47 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Audacity
[2011/11/15 09:43:29 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\BitTorrent
[2011/07/02 00:22:48 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\com.adobe.downloadassistant.AdobeDownloadAssistant
[2010/07/05 21:32:56 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\com.warnerbros.DigitalCopyManager.449F66ACC381FDC604DC2AA255FEECEEBBBEE1E5.
1
[2010/02/27 19:42:42 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\DAEMON Tools Lite
[2011/09/18 21:59:45 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\DisplayFusion
[2009/12/27 09:52:29 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\DMCache
[2009/11/09 21:12:24 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Dragon Age Toolset
[2010/12/07 16:53:51 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\DroidExplorer
[2011/07/27 14:12:27 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Dropbox
[2010/02/27 19:42:42 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\FlashGet
[2011/05/19 22:58:40 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\FreeFLVConverter
[2011/02/14 22:53:42 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\GetRightToGo
[2010/12/18 12:51:11 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\HandBrake
[2010/06/13 18:50:27 | 000,000,000 | -H-D | M] – C:\Users\Charlene\AppData\Roaming\ijjigame
[2011/08/12 19:06:34 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\ImgBurn
[2010/02/27 19:42:42 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Lexmark Productivity Studio
[2011/01/08 23:28:20 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\ManyCam
[2011/07/25 21:41:40 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Maxthon3
[2011/08/16 21:57:34 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Octoshape
[2011/04/30 16:21:13 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\OnLive App
[2010/06/07 19:40:53 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\OpenOffice.org
[2010/07/04 13:27:40 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Opera
[2011/08/03 12:12:41 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\PlayFirst
[2011/07/06 18:36:15 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Propellerhead Software
[2011/02/05 19:30:56 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Publish Providers
[2011/04/05 17:18:29 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Research In Motion
[2010/05/23 12:57:20 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\runic games
[2011/03/05 19:12:47 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Samsung
[2011/09/26 20:44:12 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Screaming Bee
[2010/03/21 11:29:39 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\ScummVM
[2011/05/22 16:09:54 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Sony
[2011/05/26 15:14:12 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Stardock
[2011/05/11 18:33:18 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\SynthMaker
[2011/07/02 22:03:54 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\SystemRequirementsLab
[2010/12/30 19:14:55 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\TeamViewer
[2011/01/01 20:01:22 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Thinstall
[2010/03/27 19:38:38 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\TuneUp Software
[2011/10/03 18:31:51 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Vso
[2011/08/10 23:42:29 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\WinFF
[2011/11/05 07:16:53 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\wXwwkkUVelOBzPy
[2011/09/29 20:27:02 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\XBMC
[2011/02/06 18:09:52 | 000,000,000LS\x00\x00\x00\x00
CREATERESTOREPOINT
Error creating restore point.

========== Files/Folders - Created Within 30 Days ==========

[2011/11/15 15:56:31 | 000,518,144 | —- | C] (SteelWerX) – C:\Windows\SWREG.exe
[2011/11/15 15:56:31 | 000,406,528 | —- | C] (SteelWerX) – C:\Windows\SWSC.exe
[2011/11/15 15:56:31 | 000,060,416 | —- | C] (NirSoft) – C:\Windows\NIRCMD.exe
[2011/11/15 15:56:22 | 000,000,000 | –SD | C] – C:\ComboFix
[2011/11/15 15:56:22 | 000,000,000 | —D | C] – C:\Windows\ERDNT
[2011/11/15 15:56:19 | 000,000,000 | —D | C] – C:\Qoobox
[2011/11/15 15:55:59 | 000,000,000 | –SD | C] – C:\32788R22FWJFW
[2011/11/15 10:30:11 | 000,077,824 | —- | C] (TWX Corp.) – C:\Windows\System32\6HWB210E.com
[2011/11/15 10:12:37 | 000,077,824 | —- | C] (TWX Corp.) – C:\Windows\System32\6HWB210E.com_
[2011/11/15 10:03:39 | 000,000,000 | —D | C] – C:\Program Files\1C99B
[2011/11/15 10:02:56 | 000,000,000 | —D | C] – C:\Program Files\LP
[2011/11/15 10:02:30 | 002,784,256 | —- | C] (Корпорация Майкрософт) – C:\Windows\System32\AV Security 2012v121.exe
[2011/11/10 19:52:47 | 000,000,000 | —D | C] – C:\IPS
[2011/11/05 07:54:01 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\STOPzilla
[2011/11/05 07:52:46 | 000,000,000 | —D | C] – C:\Program Files\STOPzilla!
[2011/11/05 07:52:31 | 000,000,000 | —D | C] – C:\Program Files\Common Files\iS3
[2011/11/05 07:52:22 | 000,000,000 | —D | C] – C:\ProgramData\STOPzilla!
[2011/11/05 07:47:45 | 000,000,000 | —D | C] – C:\TDSSKiller_Quarantine
[2011/11/05 07:20:39 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{6DC7570E-2B3A-4C06-A12B-F4F4CB8F4DB2}
[2011/11/05 07:20:25 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{4ECCCD6C-7EE2-4A58-948C-BA2D9DC3EC5F}
[2011/11/05 07:16:54 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\System Security 2012
[2011/11/05 07:16:53 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Roaming\YAA11ivvD2
[2011/11/05 07:16:53 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Roaming\wXwwkkUVelOBzPy
[2011/11/04 23:47:42 | 000,546,256 | R— | C] (iS3, Inc.) – C:\Windows\System32\SZComp5.dll
[2011/11/04 23:47:42 | 000,480,720 | R— | C] (iS3, Inc.) – C:\Windows\System32\SZBase5.dll
[2011/11/04 23:47:42 | 000,132,560 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3HTUI5.dll
[2011/11/04 23:47:42 | 000,022,992 | R— | C] (iS3, Inc.) – C:\Windows\System32\SZIO5.dll
[2011/11/04 23:47:40 | 000,738,768 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3Base5.dll
[2011/11/04 23:47:40 | 000,456,144 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3DBA5.dll
[2011/11/04 23:47:40 | 000,390,608 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3UI5.dll
[2011/11/04 23:47:40 | 000,230,864 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3Win325.dll
[2011/11/04 23:47:40 | 000,103,888 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3Inet5.dll
[2011/11/04 23:47:40 | 000,099,792 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3Svc5.dll
[2011/11/04 23:47:40 | 000,067,024 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3Hks5.dll
[2011/11/04 23:47:40 | 000,028,624 | R— | C] (iS3, Inc.) – C:\Windows\System32\IS3XDat5.dll
[2011/11/02 20:23:28 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{0E4EA1E8-C652-492A-B23F-1469C89D91EB}
[2011/11/02 20:23:07 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{59631260-21CC-4C22-8B7D-82C6AC77D9B3}
[2011/11/02 08:22:40 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{16EF2E86-40A0-4E22-83CE-8EC28BE1748F}
[2011/11/01 20:22:03 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{0B00B735-1799-4F9D-B0A9-3ED066E6E4E3}
[2011/11/01 20:21:52 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{FEB5FCDE-02E8-4F32-A3B1-565189DD69FC}
[2011/11/01 07:34:35 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{9472EB8A-7856-4C29-87FB-9D58C09ACD83}
[2011/10/31 19:33:58 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{92992902-AFE7-45F9-8B86-C03D4A54765E}
[2011/10/31 07:33:22 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{D21D86D9-138F-4989-A195-C9E5F12BB149}
[2011/10/30 19:32:40 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{2EDA655C-319D-45E0-AA92-1C3CC65C5DB7}
[2011/10/30 07:32:01 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{C4B44D3E-BAA6-41C3-B59F-D3F1C3457078}
[2011/10/29 19:31:25 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{AD22635F-1CD3-4F5B-8C7A-5229A543334D}
[2011/10/29 07:30:29 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{9DEC7AF9-4A57-4AF4-A11B-02285AAE09C9}
[2011/10/29 07:30:12 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{C13868E2-5F45-4849-BC42-9B2F91372189}
[2011/10/28 15:42:13 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{D5831792-7764-4748-9011-F87FD3572E3D}
[2011/10/28 15:41:51 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{CFAF89E8-3342-45E6-A1ED-724303BC2ECA}
[2011/10/28 03:41:20 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{A225082D-F28D-46A7-BECD-710E9A337DCE}
[2011/10/27 15:40:43 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{A503EAAB-72B5-467D-87DA-E582DFD4DBEC}
[2011/10/27 15:40:33 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{C6FF08F3-4D30-4A3A-8AFB-24D9CA55EE1B}
[2011/10/26 18:18:37 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{C3B002E9-A8F4-4557-A17E-00B7C54AA9F1}
[2011/10/26 18:18:14 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{3444873C-58DF-4F69-8769-0379CF926BA1}
[2011/10/26 06:17:44 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{C5491DA3-6592-4F23-B32A-35B07840AD8A}
[2011/10/26 06:17:32 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{3C6A7CA4-44B8-4DED-94CB-C2EAE398049C}
[2011/10/24 17:37:08 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{FF3E0397-BB32-4726-8BEA-FA2BFEBF1D2A}
[2011/10/24 17:36:53 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{11BD93B8-7757-4680-914A-3D229F174478}
[2011/10/22 20:13:50 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{90483FE8-AE78-4300-A952-EBFB89082D79}
[2011/10/22 20:13:34 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{316CA11D-C16D-4FF7-9471-77ED7452057A}
[2011/10/21 14:29:05 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{F60CB82B-E030-4483-943C-0C7652E4AE89}
[2011/10/21 14:28:54 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{EF93AA2A-EB8E-4D1D-BA3E-1A8C2C69F510}
[2011/10/20 20:38:05 | 000,000,000 | —D | C] – C:\Program Files\Maxis
[2011/10/20 17:59:35 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Focus Home Interactive
[2011/10/20 17:57:44 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\Focus Home Interactive
[2011/10/20 17:47:58 | 000,000,000 | —D | C] – C:\Program Files\Focus Home Interactive
[2011/10/20 17:01:12 | 000,232,512 | —- | C] (DT Soft Ltd) – C:\Windows\System32\drivers\dtsoftbus01.sys
[2011/10/20 16:54:51 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{8D65256F-9329-445D-9CE8-DA4852C239D6}
[2011/10/20 16:54:40 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{7E07CED2-EA01-44D6-9963-00EF92F359EC}
[2011/10/19 22:45:09 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Roaming\vlc
[2011/10/19 22:45:01 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\VideoLAN
[2011/10/19 22:44:37 | 000,000,000 | —D | C] – C:\Program Files\VideoLAN
[2011/10/19 17:07:35 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{2FA2A326-8FDC-4BC1-9D26-AFE7BCC71CB8}
[2011/10/19 17:07:23 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{95842016-CD6E-41EE-B0BE-EB84598EAB43}
[2011/10/17 23:21:31 | 000,000,000 | —D | C] – C:\Users\Charlene\pic
[2011/10/17 17:28:37 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{602DE050-F8F5-4C03-B064-DD48C7E7A2BD}
[2011/10/17 17:28:21 | 000,000,000 | —D | C] – C:\Users\Charlene\AppData\Local\{512DDC72-13D9-4A76-83C8-7F501F276EE0}
[2011/08/08 15:01:09 | 000,557,056 | —- | C] ( ) – C:\Windows\System32\raac.dll
[2011/08/08 15:01:09 | 000,139,264 | —- | C] ( ) – C:\Windows\System32\sipr.dll
[2011/08/08 15:01:09 | 000,057,344 | —- | C] ( ) – C:\Windows\System32\rv20.dll
[2011/08/08 15:01:09 | 000,053,248 | —- | C] ( ) – C:\Windows\System32\rv30.dll
[2011/08/08 15:01:09 | 000,049,152 | —- | C] ( ) – C:\Windows\System32\rv40.dll
[2011/08/08 15:01:08 | 000,286,720 | —- | C] ( ) – C:\Windows\System32\drvc.dll
[2011/08/08 15:01:08 | 000,180,224 | —- | C] ( ) – C:\Windows\System32\drv2.dll
[2011/08/08 15:01:07 | 000,548,919 | —- | C] ( ) – C:\Windows\System32\colorcvt.dll
[2011/08/08 15:01:07 | 000,090,112 | —- | C] ( ) – C:\Windows\System32\atrc.dll
[2011/08/08 15:01:07 | 000,065,602 | —- | C] ( ) – C:\Windows\System32\cook.dll
[2010/02/18 21:49:29 | 000,446,464 | —- | C] ( ) – C:\Windows\System32\LXDUhcp.dll
[2010/02/18 21:40:29 | 000,368,640 | —- | C] ( ) – C:\Windows\System32\lexlog.dll
[2010/01/19 15:49:48 | 000,047,360 | —- | C] (VSO Software) – C:\Users\Charlene\AppData\Roaming\pcouffin.sys
[2009/10/26 09:10:24 | 001,069,056 | —- | C] ( ) – C:\Windows\System32\lxduserv.dll
[2009/10/26 09:10:23 | 000,651,264 | —- | C] ( ) – C:\Windows\System32\lxdupmui.dll
[2009/10/26 09:10:21 | 000,577,536 | —- | C] ( ) – C:\Windows\System32\lxdulmpm.dll
[2009/10/26 09:10:19 | 000,376,832 | —- | C] ( ) – C:\Windows\System32\lxducomm.dll
[2009/10/26 09:10:18 | 000,364,544 | —- | C] ( ) – C:\Windows\System32\lxduinpa.dll
[2009/10/26 09:10:17 | 000,339,968 | —- | C] ( ) – C:\Windows\System32\lxduiesc.dll
[2009/10/26 09:10:15 | 000,761,856 | —- | C] ( ) – C:\Windows\System32\lxducomc.dll
[2009/10/26 09:10:10 | 000,860,160 | —- | C] ( ) – C:\Windows\System32\lxduusb1.dll
[2009/10/26 09:10:09 | 000,684,032 | —- | C] ( ) – C:\Windows\System32\lxduhbn3.dll
[2009/08/19 20:16:42 | 000,328,360 | —- | C] ( ) – C:\Windows\System32\lxduih.exe
[2009/08/19 20:16:40 | 000,594,600 | —- | C] ( ) – C:\Windows\System32\lxducoms.exe
[2009/08/19 20:16:40 | 000,369,320 | —- | C] ( ) – C:\Windows\System32\lxducfg.exe
[2009/07/10 17:59:32 | 000,409,600 | —- | C] ( ) – C:\Windows\System32\lxducoin.dll
[1 C:\Windows\*.tmp files -> C:\Windows\*.tmp -> ]
[1 C:\ProgramData\*.tmp files -> C:\ProgramData\*.tmp -> ]
[1 C:\ProgramData\*.tmp files -> C:\ProgramData\*.tmp -> ]

========== Files - Modified Within 30 Days ==========

[2055/09/18 22:29:11 | 000,002,012 | —- | M] () – C:\Windows\System32\NAV_75_cltDynam.dat
[2011/11/15 15:38:28 | 000,065,536 | —- | M] () – C:\Windows\System32\Ikeext.etl
[2011/11/15 15:38:16 | 000,067,584 | –S- | M] () – C:\Windows\bootstat.dat
[2011/11/15 10:32:29 | 000,000,352 | —- | M] () – C:\Windows\tasks\At22.job
[2011/11/15 10:30:19 | 000,000,350 | —- | M] () – C:\Windows\tasks\At21.job
[2011/11/15 10:22:05 | 000,000,920 | —- | M] () – C:\Windows\tasks\GoogleUpdateTaskUserS-1-5-21-1842821427-920554174-299800973-1000UA.job
[2011/11/15 10:15:07 | 000,000,112 | —- | M] () – C:\ProgramData\r26fSjfW.dat
[2011/11/15 10:15:00 | 000,000,940 | —- | M] () – C:\Windows\tasks\FacebookUpdateTaskUserS-1-5-21-1842821427-920554174-299800973-1000UA.job
[2011/11/15 10:14:54 | 000,077,824 | —- | M] (TWX Corp.) – C:\Windows\System32\6HWB210E.com_
[2011/11/15 10:14:54 | 000,077,824 | —- | M] (TWX Corp.) – C:\Windows\System32\6HWB210E.com
[2011/11/15 10:12:47 | 000,000,352 | —- | M] () – C:\Windows\tasks\At48.job
[2011/11/15 10:12:47 | 000,000,352 | —- | M] () – C:\Windows\tasks\At46.job
[2011/11/15 10:12:47 | 000,000,350 | —- | M] () – C:\Windows\tasks\At47.job
[2011/11/15 10:12:47 | 000,000,350 | —- | M] () – C:\Windows\tasks\At45.job
[2011/11/15 10:12:46 | 000,000,352 | —- | M] () – C:\Windows\tasks\At44.job
[2011/11/15 10:12:46 | 000,000,352 | —- | M] () – C:\Windows\tasks\At42.job
[2011/11/15 10:12:46 | 000,000,352 | —- | M] () – C:\Windows\tasks\At40.job
[2011/11/15 10:12:46 | 000,000,350 | —- | M] () – C:\Windows\tasks\At43.job
[2011/11/15 10:12:46 | 000,000,350 | —- | M] () – C:\Windows\tasks\At41.job
[2011/11/15 10:12:45 | 000,000,352 | —- | M] () – C:\Windows\tasks\At38.job
[2011/11/15 10:12:45 | 000,000,352 | —- | M] () – C:\Windows\tasks\At36.job
[2011/11/15 10:12:45 | 000,000,352 | —- | M] () – C:\Windows\tasks\At34.job
[2011/11/15 10:12:45 | 000,000,350 | —- | M] () – C:\Windows\tasks\At39.job
[2011/11/15 10:12:45 | 000,000,350 | —- | M] () – C:\Windows\tasks\At37.job
[2011/11/15 10:12:45 | 000,000,350 | —- | M] () – C:\Windows\tasks\At35.job
[2011/11/15 10:12:44 | 000,000,352 | —- | M] () – C:\Windows\tasks\At32.job
[2011/11/15 10:12:44 | 000,000,352 | —- | M] () – C:\Windows\tasks\At30.job
[2011/11/15 10:12:44 | 000,000,352 | —- | M] () – C:\Windows\tasks\At28.job
[2011/11/15 10:12:44 | 000,000,350 | —- | M] () – C:\Windows\tasks\At33.job
[2011/11/15 10:12:44 | 000,000,350 | —- | M] () – C:\Windows\tasks\At31.job
[2011/11/15 10:12:44 | 000,000,350 | —- | M] () – C:\Windows\tasks\At29.job
[2011/11/15 10:12:43 | 000,000,352 | —- | M] () – C:\Windows\tasks\At26.job
[2011/11/15 10:12:43 | 000,000,352 | —- | M] () – C:\Windows\tasks\At24.job
[2011/11/15 10:12:43 | 000,000,350 | —- | M] () – C:\Windows\tasks\At27.job
[2011/11/15 10:12:43 | 000,000,350 | —- | M] () – C:\Windows\tasks\At25.job
[2011/11/15 10:12:43 | 000,000,350 | —- | M] () – C:\Windows\tasks\At23.job
[2011/11/15 10:12:42 | 000,000,352 | —- | M] () – C:\Windows\tasks\At20.job
[2011/11/15 10:12:42 | 000,000,352 | —- | M] () – C:\Windows\tasks\At18.job
[2011/11/15 10:12:42 | 000,000,352 | —- | M] () – C:\Windows\tasks\At16.job
[2011/11/15 10:12:42 | 000,000,350 | —- | M] () – C:\Windows\tasks\At19.job
[2011/11/15 10:12:42 | 000,000,350 | —- | M] () – C:\Windows\tasks\At17.job
[2011/11/15 10:12:41 | 000,000,352 | —- | M] () – C:\Windows\tasks\At14.job
[2011/11/15 10:12:41 | 000,000,352 | —- | M] () – C:\Windows\tasks\At12.job
[2011/11/15 10:12:41 | 000,000,350 | —- | M] () – C:\Windows\tasks\At15.job
[2011/11/15 10:12:41 | 000,000,350 | —- | M] () – C:\Windows\tasks\At13.job
[2011/11/15 10:12:40 | 000,000,352 | —- | M] () – C:\Windows\tasks\At8.job
[2011/11/15 10:12:40 | 000,000,352 | —- | M] () – C:\Windows\tasks\At10.job
[2011/11/15 10:12:40 | 000,000,350 | —- | M] () – C:\Windows\tasks\At9.job
[2011/11/15 10:12:40 | 000,000,350 | —- | M] () – C:\Windows\tasks\At7.job
[2011/11/15 10:12:40 | 000,000,350 | —- | M] () – C:\Windows\tasks\At11.job
[2011/11/15 10:12:39 | 000,000,352 | —- | M] () – C:\Windows\tasks\At6.job
[2011/11/15 10:12:39 | 000,000,350 | —- | M] () – C:\Windows\tasks\At5.job
[2011/11/15 10:12:38 | 000,000,352 | —- | M] () – C:\Windows\tasks\At4.job
[2011/11/15 10:12:38 | 000,000,352 | —- | M] () – C:\Windows\tasks\At2.job
[2011/11/15 10:12:38 | 000,000,350 | —- | M] () – C:\Windows\tasks\At3.job
[2011/11/15 10:12:38 | 000,000,350 | —- | M] () – C:\Windows\tasks\At1.job
[2011/11/15 10:02:30 | 002,784,256 | —- | M] (Корпорация Майкрософт) – C:\Windows\System32\AV Security 2012v121.exe
[2011/11/15 00:54:50 | 000,711,876 | —- | M] () – C:\Windows\System32\perfh009.dat
[2011/11/15 00:54:50 | 000,140,264 | —- | M] () – C:\Windows\System32\perfc009.dat
[2011/11/14 22:15:01 | 000,000,918 | —- | M] () – C:\Windows\tasks\FacebookUpdateTaskUserS-1-5-21-1842821427-920554174-299800973-1000Core.job
[2011/11/14 15:22:00 | 000,000,868 | —- | M] () – C:\Windows\tasks\GoogleUpdateTaskUserS-1-5-21-1842821427-920554174-299800973-1000Core.job
[2011/11/14 13:57:56 | 000,215,201 | —- | M] () – C:\Users\Charlene\Desktop\playing3.jpg
[2011/11/14 13:56:47 | 000,201,852 | —- | M] () – C:\Users\Charlene\Desktop\playing2.jpg
[2011/11/14 13:55:58 | 000,200,271 | —- | M] () – C:\Users\Charlene\Desktop\playing.jpg
[2011/11/10 19:53:38 | 000,007,168 | —- | M] () – C:\Users\Charlene\AppData\Roaming\mswlnsys32.dll
[2011/11/10 19:53:37 | 000,007,168 | —- | M] () – C:\Users\Charlene\AppData\Roaming\MYPROXYDLL.dll
[2011/11/09 07:41:26 | 000,001,069 | —- | M] () – C:\Users\Charlene\Desktop\Videos - Shortcut.lnk
[2011/11/05 07:45:08 | 000,232,512 | —- | M] (DT Soft Ltd) – C:\Windows\System32\drivers\dtsoftbus01.sys
[2011/11/05 07:17:50 | 000,001,213 | —- | M] () – C:\Users\Charlene\AppData\Roaming\ldr.ini
[2011/11/04 23:47:42 | 000,546,256 | R— | M] (iS3, Inc.) – C:\Windows\System32\SZComp5.dll
[2011/11/04 23:47:42 | 000,480,720 | R— | M] (iS3, Inc.) – C:\Windows\System32\SZBase5.dll
[2011/11/04 23:47:42 | 000,132,560 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3HTUI5.dll
[2011/11/04 23:47:42 | 000,022,992 | R— | M] (iS3, Inc.) – C:\Windows\System32\SZIO5.dll
[2011/11/04 23:47:40 | 000,738,768 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3Base5.dll
[2011/11/04 23:47:40 | 000,456,144 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3DBA5.dll
[2011/11/04 23:47:40 | 000,390,608 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3UI5.dll
[2011/11/04 23:47:40 | 000,230,864 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3Win325.dll
[2011/11/04 23:47:40 | 000,103,888 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3Inet5.dll
[2011/11/04 23:47:40 | 000,099,792 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3Svc5.dll
[2011/11/04 23:47:40 | 000,067,024 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3Hks5.dll
[2011/11/04 23:47:40 | 000,028,624 | R— | M] (iS3, Inc.) – C:\Windows\System32\IS3XDat5.dll
[2011/11/03 06:33:39 | 000,001,444 | —- | M] () – C:\Windows\Sandboxie.ini
[2011/10/26 06:16:34 | 000,414,368 | —- | M] (Adobe Systems Incorporated) – C:\Windows\System32\FlashPlayerCPLApp.cpl
[2011/10/24 20:21:04 | 000,000,861 | —- | M] () – C:\Users\Public\Desktop\Mozilla Firefox.lnk
[2011/10/23 16:28:40 | 000,273,736 | —- | M] () – C:\Users\Charlene\Desktop\kelly bodybuilder.png
[2011/10/23 16:28:40 | 000,000,132 | —- | M] () – C:\Users\Charlene\AppData\Roaming\Adobe PNG Format CS5 Prefs
[2011/10/23 15:30:30 | 000,065,361 | —- | M] () – C:\Users\Charlene\Desktop\kelly.jpg
[2011/10/20 20:38:11 | 000,000,534 | —- | M] () – C:\Windows\eReg.dat
[2011/10/20 18:02:11 | 000,002,187 | —- | M] () – C:\Users\Public\Desktop\Cities XL 2011.lnk
[1 C:\Windows\*.tmp files -> C:\Windows\*.tmp -> ]
[1 C:\ProgramData\*.tmp files -> C:\ProgramData\*.tmp -> ]
[1 C:\ProgramData\*.tmp files -> C:\ProgramData\*.tmp -> ]

========== Files Created - No Company Name ==========

[2011/11/15 15:56:31 | 000,256,000 | —- | C] () – C:\Windows\PEV.exe
[2011/11/15 15:56:31 | 000,208,896 | —- | C] () – C:\Windows\MBR.exe
[2011/11/15 15:56:31 | 000,098,816 | —- | C] () – C:\Windows\sed.exe
[2011/11/15 15:56:31 | 000,080,412 | —- | C] () – C:\Windows\grep.exe
[2011/11/15 15:56:31 | 000,068,096 | —- | C] () – C:\Windows\zip.exe
[2011/11/15 10:12:49 | 000,000,112 | —- | C] () – C:\ProgramData\r26fSjfW.dat
[2011/11/15 10:12:47 | 000,000,352 | —- | C] () – C:\Windows\tasks\At48.job
[2011/11/15 10:12:47 | 000,000,352 | —- | C] () – C:\Windows\tasks\At46.job
[2011/11/15 10:12:47 | 000,000,350 | —- | C] () – C:\Windows\tasks\At47.job
[2011/11/15 10:12:46 | 000,000,352 | —- | C] () – C:\Windows\tasks\At44.job
[2011/11/15 10:12:46 | 000,000,352 | —- | C] () – C:\Windows\tasks\At42.job
[2011/11/15 10:12:46 | 000,000,350 | —- | C] () – C:\Windows\tasks\At45.job
[2011/11/15 10:12:46 | 000,000,350 | —- | C] () – C:\Windows\tasks\At43.job
[2011/11/15 10:12:46 | 000,000,350 | —- | C] () – C:\Windows\tasks\At41.job
[2011/11/15 10:12:45 | 000,000,352 | —- | C] () – C:\Windows\tasks\At40.job
[2011/11/15 10:12:45 | 000,000,352 | —- | C] () – C:\Windows\tasks\At38.job
[2011/11/15 10:12:45 | 000,000,352 | —- | C] () – C:\Windows\tasks\At36.job
[2011/11/15 10:12:45 | 000,000,350 | —- | C] () – C:\Windows\tasks\At39.job
[2011/11/15 10:12:45 | 000,000,350 | —- | C] () – C:\Windows\tasks\At37.job
[2011/11/15 10:12:45 | 000,000,350 | —- | C] () – C:\Windows\tasks\At35.job
[2011/11/15 10:12:44 | 000,000,352 | —- | C] () – C:\Windows\tasks\At34.job
[2011/11/15 10:12:44 | 000,000,352 | —- | C] () – C:\Windows\tasks\At32.job
[2011/11/15 10:12:44 | 000,000,352 | —- | C] () – C:\Windows\tasks\At30.job
[2011/11/15 10:12:44 | 000,000,350 | —- | C] () – C:\Windows\tasks\At33.job
[2011/11/15 10:12:44 | 000,000,350 | —- | C] () – C:\Windows\tasks\At31.job
[2011/11/15 10:12:44 | 000,000,350 | —- | C] () – C:\Windows\tasks\At29.job
[2011/11/15 10:12:43 | 000,000,352 | —- | C] () – C:\Windows\tasks\At28.job
[2011/11/15 10:12:43 | 000,000,352 | —- | C] () – C:\Windows\tasks\At26.job
[2011/11/15 10:12:43 | 000,000,352 | —- | C] () – C:\Windows\tasks\At24.job
[2011/11/15 10:12:43 | 000,000,352 | —- | C] () – C:\Windows\tasks\At22.job
[2011/11/15 10:12:43 | 000,000,350 | —- | C] () – C:\Windows\tasks\At27.job
[2011/11/15 10:12:43 | 000,000,350 | —- | C] () – C:\Windows\tasks\At25.job
[2011/11/15 10:12:43 | 000,000,350 | —- | C] () – C:\Windows\tasks\At23.job
[2011/11/15 10:12:42 | 000,000,352 | —- | C] () – C:\Windows\tasks\At20.job
[2011/11/15 10:12:42 | 000,000,352 | —- | C] () – C:\Windows\tasks\At18.job
[2011/11/15 10:12:42 | 000,000,350 | —- | C] () – C:\Windows\tasks\At21.job
[2011/11/15 10:12:42 | 000,000,350 | —- | C] () – C:\Windows\tasks\At19.job
[2011/11/15 10:12:42 | 000,000,350 | —- | C] () – C:\Windows\tasks\At17.job
[2011/11/15 10:12:41 | 000,000,352 | —- | C] () – C:\Windows\tasks\At16.job
[2011/11/15 10:12:41 | 000,000,352 | —- | C] () – C:\Windows\tasks\At14.job
[2011/11/15 10:12:41 | 000,000,350 | —- | C] () – C:\Windows\tasks\At15.job
[2011/11/15 10:12:41 | 000,000,350 | —- | C] () – C:\Windows\tasks\At13.job
[2011/11/15 10:12:40 | 000,000,352 | —- | C] () – C:\Windows\tasks\At8.job
[2011/11/15 10:12:40 | 000,000,352 | —- | C] () – C:\Windows\tasks\At12.job
[2011/11/15 10:12:40 | 000,000,352 | —- | C] () – C:\Windows\tasks\At10.job
[2011/11/15 10:12:40 | 000,000,350 | —- | C] () – C:\Windows\tasks\At9.job
[2011/11/15 10:12:40 | 000,000,350 | —- | C] () – C:\Windows\tasks\At11.job
[2011/11/15 10:12:39 | 000,000,352 | —- | C] () – C:\Windows\tasks\At6.job
[2011/11/15 10:12:39 | 000,000,350 | —- | C] () – C:\Windows\tasks\At7.job
[2011/11/15 10:12:38 | 000,000,352 | —- | C] () – C:\Windows\tasks\At4.job
[2011/11/15 10:12:38 | 000,000,352 | —- | C] () – C:\Windows\tasks\At2.job
[2011/11/15 10:12:38 | 000,000,350 | —- | C] () – C:\Windows\tasks\At5.job
[2011/11/15 10:12:38 | 000,000,350 | —- | C] () – C:\Windows\tasks\At3.job
[2011/11/15 10:12:37 | 000,000,350 | —- | C] () – C:\Windows\tasks\At1.job
[2011/11/14 13:57:56 | 000,215,201 | —- | C] () – C:\Users\Charlene\Desktop\playing3.jpg
[2011/11/14 13:56:47 | 000,201,852 | —- | C] () – C:\Users\Charlene\Desktop\playing2.jpg
[2011/11/14 13:55:58 | 000,200,271 | —- | C] () – C:\Users\Charlene\Desktop\playing.jpg
[2011/11/09 07:41:26 | 000,001,069 | —- | C] () – C:\Users\Charlene\Desktop\Videos - Shortcut.lnk
[2011/11/05 07:16:53 | 000,001,213 | —- | C] () – C:\Users\Charlene\AppData\Roaming\ldr.ini
[2011/10/24 20:21:04 | 000,000,861 | —- | C] () – C:\Users\Public\Desktop\Mozilla Firefox.lnk
[2011/10/24 20:21:04 | 000,000,843 | —- | C] () – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Mozilla Firefox.lnk
[2011/10/23 16:28:40 | 000,273,736 | —- | C] () – C:\Users\Charlene\Desktop\kelly bodybuilder.png
[2011/10/23 15:30:46 | 000,065,361 | —- | C] () – C:\Users\Charlene\Desktop\kelly.jpg
[2011/10/20 20:38:11 | 000,000,534 | —- | C] () – C:\Windows\eReg.dat
[2011/10/20 18:02:11 | 000,002,187 | —- | C] () – C:\Users\Public\Desktop\Cities XL 2011.lnk
[2011/08/08 15:01:19 | 000,819,200 | —- | C] () – C:\Windows\System32\xvidcore.dll
[2011/08/08 15:01:19 | 000,180,224 | —- | C] () – C:\Windows\System32\xvidvfw.dll
[2011/08/07 02:31:18 | 000,000,000 | —- | C] () – C:\Windows\PowerReg.dat
[2011/08/07 02:26:49 | 000,000,484 | —- | C] () – C:\Windows\hegames.ini
[2011/08/03 16:55:15 | 000,007,605 | —- | C] () – C:\Users\Charlene\AppData\Local\Resmon.ResmonCfg
[2011/07/25 22:47:48 | 000,043,520 | —- | C] () – C:\Windows\System32\CmdLineExt03.dll
[2011/07/02 01:21:46 | 000,001,456 | —- | C] () – C:\Users\Charlene\AppData\Local\Adobe Save for Web 12.0 Prefs
[2011/05/20 21:35:28 | 000,304,744 | —- | C] () – C:\Windows\System32\nvStreaming.exe
[2011/02/22 07:03:48 | 000,007,168 | —- | C] () – C:\Users\Charlene\AppData\Roaming\MYPROXYDLL.dll
[2011/02/21 04:10:43 | 000,007,168 | —- | C] () – C:\Users\Charlene\AppData\Roaming\mswlnsys32.dll
[2011/02/21 04:10:31 | 000,012,800 | RHS- | C] () – C:\Users\Charlene\AppData\Roaming\AntiSpyware.exe
[2011/02/21 01:43:11 | 000,012,800 | RHS- | C] () – C:\Users\Charlene\AppData\Roaming\MYPROXY.exe
[2011/02/14 22:53:45 | 000,057,344 | —- | C] () – C:\Windows\System32\ff_vfw.dll
[2011/02/14 21:20:53 | 000,000,132 | —- | C] () – C:\Users\Charlene\AppData\Roaming\Adobe PNG Format CS5 Prefs
[2011/01/29 17:00:24 | 000,030,568 | —- | C] () – C:\Windows\MusiccityDownload.exe
[2011/01/29 17:00:22 | 000,974,848 | —- | C] () – C:\Windows\System32\cis-2.4.dll
[2011/01/29 17:00:22 | 000,081,920 | —- | C] () – C:\Windows\System32\issacapi_bs-2.3.dll
[2011/01/29 17:00:22 | 000,065,536 | —- | C] () – C:\Windows\System32\issacapi_pe-2.3.dll
[2011/01/29 17:00:22 | 000,057,344 | —- | C] () – C:\Windows\System32\issacapi_se-2.3.dll
[2011/01/21 18:30:59 | 000,000,029 | —- | C] () – C:\Users\Charlene\AppData\Roaming\RSBot_Accounts.ini
[2010/10/31 10:25:01 | 003,514,368 | —- | C] () – C:\Program Files\INCOMPLETE~208-taylor_swift-the_story_of_us_(us_version).mp3
[2010/10/31 10:22:51 | 007,525,691 | —- | C] () – C:\Program Files\207-taylor_swift-back_to_december_(us_version).mp3
[2010/10/31 10:22:05 | 006,603,340 | —- | C] () – C:\Program Files\102-taylor_swift-sparks_fly.mp3
[2010/10/31 10:21:10 | 007,160,839 | —- | C] () – C:\Program Files\103-taylor_swift-back_to_december.mp3
[2010/10/31 10:20:30 | 005,918,969 | —- | C] () – C:\Program Files\104-taylor_swift-speak_now.mp3
[2010/10/31 10:19:27 | 009,054,846 | —- | C] () – C:\Program Files\105-taylor_swift-dear_john.mp3
[2010/10/31 10:18:46 | 005,531,357 | —- | C] () – C:\Program Files\106-taylor_swift-mean.mp3
[2010/10/31 10:17:56 | 006,915,258 | —- | C] () – C:\Program Files\107-taylor_swift-the_story_of_us.mp3
[2010/10/31 10:17:14 | 006,016,684 | —- | C] () – C:\Program Files\108-taylor_swift-never_grow_up.mp3
[2010/10/31 10:16:08 | 009,129,224 | —- | C] () – C:\Program Files\109-taylor_swift-enchanted.mp3
[2010/10/31 10:15:28 | 005,701,179 | —- | C] () – C:\Program Files\110-taylor_swift-better_than_revenge.mp3
[2010/10/31 10:14:42 | 006,819,869 | —- | C] () – C:\Program Files\111-taylor_swift-innocent.mp3
[2010/10/31 10:13:55 | 006,400,578 | —- | C] () – C:\Program Files\112-taylor_swift-haunted.mp3
[2010/10/31 10:12:53 | 008,773,644 | —- | C] () – C:\Program Files\113-taylor_swift-last_kiss.mp3
[2010/10/31 10:12:01 | 007,517,546 | —- | C] () – C:\Program Files\114-taylor_swift-long_live.mp3
[2010/10/31 10:11:18 | 005,706,399 | —- | C] () – C:\Program Files\201-taylor_swift-ours.mp3
[2010/10/31 10:10:34 | 005,574,290 | —- | C] () – C:\Program Files\202-taylor_swift-if_this_was_a_movie.mp3
[2010/10/31 10:09:33 | 006,869,412 | —- | C] () – C:\Program Files\204-taylor_swift-back_to_december_(acoustic).mp3
[2010/10/31 10:08:29 | 007,124,608 | —- | C] () – C:\Program Files\203-taylor_swift-superman.mp3
[2010/10/31 10:05:46 | 004,878,350 | —- | C] () – C:\Program Files\205-taylor_swift-haunted_(acoustic).mp3
[2010/10/31 10:05:03 | 005,867,918 | —- | C] () – C:\Program Files\206-taylor_swift-mine_(us_version).mp3
[2010/10/31 10:04:20 | 005,609,172 | —- | C] () – C:\Program Files\101-taylor_swift-mine.mp3
[2010/10/27 17:55:22 | 005,219,767 | —- | C] () – C:\Program Files\03 no one's gonna love you.mp3
[2010/10/27 17:55:07 | 005,709,831 | —- | C] () – C:\Program Files\01 the first song.mp3
[2010/10/27 17:53:47 | 005,665,067 | —- | C] () – C:\Program Files\the shins - oh inverted world 05 girl inform me.mp3
[2010/07/20 22:18:32 | 000,082,289 | —- | C] () – C:\Windows\System32\lvcoinst.ini
[2010/07/20 22:09:50 | 000,000,056 | -H– | C] () – C:\Windows\System32\ezsidmv.dat
[2010/06/13 18:45:33 | 000,009,728 | —- | C] () – C:\Windows\System32\uc_karos_launching.dll
[2010/05/21 12:03:13 | 000,000,256 | —- | C] () – C:\Windows\System32\pool.bin
[2010/02/27 19:57:01 | 000,021,316 | —- | C] () – C:\Windows\System32\emptyregdb.dat
[2010/02/18 21:49:29 | 000,389,120 | —- | C] () – C:\Windows\System32\LXDUinst.dll
[2010/01/29 21:53:58 | 000,000,050 | —- | C] () – C:\Windows\MegaManager.INI
[2010/01/19 15:52:40 | 000,001,189 | —- | C] () – C:\Users\Charlene\AppData\Roaming\vso_ts_preview.xml
[2010/01/19 15:49:48 | 000,087,608 | —- | C] () – C:\Users\Charlene\AppData\Roaming\inst.exe
[2010/01/19 15:49:48 | 000,007,887 | —- | C] () – C:\Users\Charlene\AppData\Roaming\pcouffin.cat
[2010/01/19 15:49:48 | 000,001,144 | —- | C] () – C:\Users\Charlene\AppData\Roaming\pcouffin.inf
[2009/12/08 16:19:34 | 000,001,444 | —- | C] () – C:\Windows\Sandboxie.ini
[2009/10/26 09:10:28 | 000,040,960 | —- | C] () – C:\Windows\System32\lxduvs.dll
[2009/10/26 09:09:51 | 000,208,896 | —- | C] () – C:\Windows\System32\lxdugrd.dll
[2009/10/26 09:08:26 | 001,036,288 | —- | C] () – C:\Windows\System32\lxdudrs.dll
[2009/10/26 09:08:26 | 000,081,920 | —- | C] () – C:\Windows\System32\lxducaps.dll
[2009/10/26 09:08:26 | 000,069,632 | —- | C] () – C:\Windows\System32\lxducnv4.dll
[2009/10/18 15:28:12 | 000,000,602 | —- | C] () – C:\Windows\Diamonds.INI
[2009/10/07 12:23:01 | 000,187,612 | -H– | C] () – C:\Windows\System32\mlfcache.dat
[2009/10/07 00:46:36 | 000,025,752 | —- | C] () – C:\Windows\System32\drivers\LVPr2Mon.sys
[2009/10/07 00:23:08 | 000,013,584 | —- | C] () – C:\Windows\System32\drivers\iKeyLFT2.dll
[2009/10/05 17:08:15 | 000,000,208 | —- | C] () – C:\Users\Charlene\AppData\Roaming\iPod Access v4 Prefs
[2009/10/05 16:55:24 | 000,000,047 | -H– | C] () – C:\Users\Charlene\AppData\Roaming\iPodAccessv4_OwnerName
[2009/10/05 16:54:03 | 000,000,011 | -H– | C] () – C:\Users\Charlene\AppData\Roaming\iPodAccess_Time
[2009/10/05 12:10:02 | 000,000,000 | —- | C] () – C:\Windows\nsreg.dat
[2009/09/29 18:05:15 | 000,082,432 | —- | C] () – C:\Windows\System32\ewdll32.dll
[2009/09/29 18:05:15 | 000,077,824 | —- | C] () – C:\Windows\System32\helpmsg32.dll
[2009/09/29 18:05:15 | 000,045,056 | —- | C] () – C:\Windows\System32\avi_util32.dll
[2009/09/29 18:05:15 | 000,000,375 | —- | C] () – C:\Windows\dst_suns.ini
[2009/09/29 16:14:14 | 000,056,056 | —- | C] () – C:\Windows\System32\DLAAPI_W.DLL
[2009/09/29 16:14:14 | 000,000,120 | —- | C] () – C:\Windows\wininit.ini
[2009/09/29 13:09:28 | 000,000,376 | —- | C] () – C:\Windows\ODBC.INI
[2009/09/29 12:58:18 | 000,110,602 | —- | C] () – C:\Windows\System32\xcdsfx32.bin
[2009/09/18 22:00:56 | 000,002,012 | —- | C] () – C:\Windows\System32\NAV_75_cltDynam.dat
[2009/07/13 20:57:37 | 000,067,584 | –S- | C] () – C:\Windows\bootstat.dat
[2009/07/13 20:33:53 | 004,074,120 | —- | C] () – C:\Windows\System32\FNTCACHE.DAT
[2009/07/13 18:05:48 | 000,711,876 | —- | C] () – C:\Windows\System32\perfh009.dat
[2009/07/13 18:05:48 | 000,291,294 | —- | C] () – C:\Windows\System32\perfi009.dat
[2009/07/13 18:05:48 | 000,140,264 | —- | C] () – C:\Windows\System32\perfc009.dat
[2009/07/13 18:05:48 | 000,031,548 | —- | C] () – C:\Windows\System32\perfd009.dat
[2009/07/13 18:05:05 | 000,000,741 | —- | C] () – C:\Windows\System32\NOISE.DAT
[2009/07/13 18:04:11 | 000,215,943 | —- | C] () – C:\Windows\System32\dssec.dat
[2009/07/13 16:19:49 | 000,066,048 | —- | C] () – C:\Windows\System32\PrintBrmUi.exe
[2009/07/13 15:55:01 | 000,043,131 | —- | C] () – C:\Windows\mib.bin
[2009/07/13 15:51:43 | 000,073,728 | —- | C] () – C:\Windows\System32\BthpanContextHandler.dll
[2009/07/13 15:42:10 | 000,064,000 | —- | C] () – C:\Windows\System32\BWContextHandler.dll
[2009/07/13 15:11:26 | 000,108,544 | —- | C] () – C:\Windows\System32\drivers\cdrom.sys
[2009/06/10 13:26:10 | 000,673,088 | —- | C] () – C:\Windows\System32\mlang.dat
[2003/01/07 14:05:08 | 000,002,695 | —- | C] () – C:\Windows\System32\OUTLPERF.INI
========== LOP Check ==========

[2010/10/03 12:31:51 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\.minecraft
[2010/04/06 18:18:59 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\acccore
[2011/05/11 18:32:28 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Acoustica
[2011/09/18 21:35:37 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Applied Acoustics Systems
[2011/09/26 20:58:47 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Audacity
[2011/11/15 09:43:29 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\BitTorrent
[2011/07/02 00:22:48 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\com.adobe.downloadassistant.AdobeDownloadAssistant
[2010/07/05 21:32:56 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\com.warnerbros.DigitalCopyManager.449F66ACC381FDC604DC2AA255FEECEEBBBEE1E5.
1
[2010/02/27 19:42:42 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\DAEMON Tools Lite
[2011/09/18 21:59:45 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\DisplayFusion
[2009/12/27 09:52:29 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\DMCache
[2009/11/09 21:12:24 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Dragon Age Toolset
[2010/12/07 16:53:51 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\DroidExplorer
[2011/07/27 14:12:27 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Dropbox
[2010/02/27 19:42:42 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\FlashGet
[2011/05/19 22:58:40 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\FreeFLVConverter
[2011/02/14 22:53:42 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\GetRightToGo
[2010/12/18 12:51:11 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\HandBrake
[2010/06/13 18:50:27 | 000,000,000 | -H-D | M] – C:\Users\Charlene\AppData\Roaming\ijjigame
[2011/08/12 19:06:34 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\ImgBurn
[2010/02/27 19:42:42 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Lexmark Productivity Studio
[2011/01/08 23:28:20 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\ManyCam
[2011/07/25 21:41:40 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Maxthon3
[2011/08/16 21:57:34 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Octoshape
[2011/04/30 16:21:13 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\OnLive App
[2010/06/07 19:40:53 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\OpenOffice.org
[2010/07/04 13:27:40 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Opera
[2011/08/03 12:12:41 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\PlayFirst
[2011/07/06 18:36:15 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Propellerhead Software
[2011/02/05 19:30:56 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Publish Providers
[2011/04/05 17:18:29 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Research In Motion
[2010/05/23 12:57:20 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\runic games
[2011/03/05 19:12:47 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Samsung
[2011/09/26 20:44:12 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Screaming Bee
[2010/03/21 11:29:39 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\ScummVM
[2011/05/22 16:09:54 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Sony
[2011/05/26 15:14:12 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Stardock
[2011/05/11 18:33:18 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\SynthMaker
[2011/07/02 22:03:54 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\SystemRequirementsLab
[2010/12/30 19:14:55 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\TeamViewer
[2011/01/01 20:01:22 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Thinstall
[2010/03/27 19:38:38 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\TuneUp Software
[2011/10/03 18:31:51 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Vso
[2011/08/10 23:42:29 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\WinFF
[2011/11/05 07:16:53 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\wXwwkkUVelOBzPy
[2011/09/29 20:27:02 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\XBMC
[2011/02/06 18:09:52 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\Xtranormal
[2011/11/05 07:16:54 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\YAA11ivvD2
[2010/12/21 13:39:07 | 000,000,000 | —D | M] – C:\Users\Charlene\AppData\Roaming\ZeroK
[2011/11/15 10:12:38 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At1.job
[2011/11/15 10:12:40 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At10.job
[2011/11/15 10:12:40 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At11.job
[2011/11/15 10:12:41 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At12.job
[2011/11/15 10:12:41 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At13.job
[2011/11/15 10:12:41 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At14.job
[2011/11/15 10:12:41 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At15.job
[2011/11/15 10:12:42 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At16.job
[2011/11/15 10:12:42 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At17.job
[2011/11/15 10:12:42 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At18.job
[2011/11/15 10:12:42 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At19.job
[2011/11/15 10:12:38 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At2.job
[2011/11/15 10:12:42 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At20.job
[2011/11/15 10:30:19 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At21.job
[2011/11/15 10:32:29 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At22.job
[2011/11/15 10:12:43 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At23.job
[2011/11/15 10:12:43 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At24.job
[2011/11/15 10:12:43 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At25.job
[2011/11/15 10:12:43 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At26.job
[2011/11/15 10:12:43 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At27.job
[2011/11/15 10:12:44 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At28.job
[2011/11/15 10:12:44 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At29.job
[2011/11/15 10:12:38 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At3.job
[2011/11/15 10:12:44 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At30.job
[2011/11/15 10:12:44 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At31.job
[2011/11/15 10:12:44 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At32.job
[2011/11/15 10:12:44 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At33.job
[2011/11/15 10:12:45 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At34.job
[2011/11/15 10:12:45 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At35.job
[2011/11/15 10:12:45 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At36.job
[2011/11/15 10:12:45 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At37.job
[2011/11/15 10:12:45 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At38.job
[2011/11/15 10:12:45 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At39.job
[2011/11/15 10:12:38 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At4.job
[2011/11/15 10:12:46 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At40.job
[2011/11/15 10:12:46 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At41.job
[2011/11/15 10:12:46 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At42.job
[2011/11/15 10:12:46 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At43.job
[2011/11/15 10:12:46 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At44.job
[2011/11/15 10:12:47 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At45.job
[2011/11/15 10:12:47 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At46.job
[2011/11/15 10:12:47 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At47.job
[2011/11/15 10:12:47 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At48.job
[2011/11/15 10:12:39 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At5.job
[2011/11/15 10:12:39 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At6.job
[2011/11/15 10:12:40 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At7.job
[2011/11/15 10:12:40 | 000,000,352 | —- | M] () – C:\Windows\Tasks\At8.job
[2011/11/15 10:12:40 | 000,000,350 | —- | M] () – C:\Windows\Tasks\At9.job
[2011/11/14 22:15:01 | 000,000,918 | —- | M] () – C:\Windows\Tasks\FacebookUpdateTaskUserS-1-5-21-1842821427-920554174-299800973-1000Core.job
[2011/11/15 10:15:00 | 000,000,940 | —- | M] () – C:\Windows\Tasks\FacebookUpdateTaskUserS-1-5-21-1842821427-920554174-299800973-1000UA.job
[2011/05/31 09:46:50 | 000,032,608 | —- | M] () – C:\Windows\Tasks\SCHEDLGU.TXT

========== Purity Check ==========


========== Custom Scans ==========


< %SYSTEMDRIVE%\*.* >
[2011/08/11 13:47:48 | 000,001,024 | —- | M] () – C:\.rnd
[2009/06/10 13:42:20 | 000,000,024 | —- | M] () – C:\autoexec.bat
[2010/10/20 21:20:07 | 000,000,775 | —- | M] () – C:\cleanup.bat
[2009/06/10 13:42:20 | 000,000,010 | —- | M] () – C:\config.sys
[2009/09/29 18:04:50 | 000,000,000 | RHS- | M] () – C:\IO.SYS
[2009/11/20 11:13:44 | 000,000,351 | -H– | M] () – C:\IPH.PH
[2010/02/02 07:31:22 | 000,000,625 | —- | M] () – C:\KF_revLoader.exe.log
[2010/05/16 15:36:00 | 262,323,599 | —- | M] () – C:\KillingFloor.exe.log
[2009/09/29 18:04:50 | 000,000,000 | RHS- | M] () – C:\MSDOS.SYS
[2009/11/12 23:21:05 | 077,998,088 | —- | M] () – C:\none.mpg
[2010/05/16 15:36:10 | 000,003,147 | —- | M] () – C:\Play.exe.log
[2010/12/23 13:53:09 | 000,000,688 | —- | M] () – C:\VMBSettings.ini
[2010/11/15 18:29:13 | 000,001,503 | —- | M] () – C:\VuSettings.ini

< %systemroot%\Fonts\*.com >
[2009/07/13 20:52:25 | 000,026,040 | —- | M] () – C:\Windows\Fonts\GlobalMonospace.CompositeFont
[2009/07/13 20:52:25 | 000,026,489 | —- | M] () – C:\Windows\Fonts\GlobalSansSerif.CompositeFont
[2009/07/13 20:52:25 | 000,029,779 | —- | M] () – C:\Windows\Fonts\GlobalSerif.CompositeFont
[2009/07/13 20:52:25 | 000,043,318 | —- | M] () – C:\Windows\Fonts\GlobalUserInterface.CompositeFont

< %systemroot%\Fonts\*.dll >

< %systemroot%\Fonts\*.ini >
[2009/06/10 13:31:19 | 000,000,065 | —- | M] () – C:\Windows\Fonts\desktop.ini

< %systemroot%\Fonts\*.ini2 >

< %systemroot%\Fonts\*.exe >
< %systemroot%\system32\spool\prtprocs\w32x86\*.* >
[2009/07/13 17:15:35 | 000,022,528 | —- | M] (Microsoft Corporation) – C:\Windows\system32\spool\prtprocs\w32x86\jnwppr.dll
[2009/10/04 12:43:49 | 000,047,416 | —- | M] (LogMeIn, Inc.) – C:\Windows\system32\spool\prtprocs\w32x86\LMIproc.dll
[2009/08/19 19:51:16 | 000,155,648 | —- | M] () – C:\Windows\system32\spool\prtprocs\w32x86\lxdudrpp.dll
[2007/04/09 12:23:54 | 000,028,552 | —- | M] (Microsoft Corporation) – C:\Windows\system32\spool\prtprocs\w32x86\mdippr.dll
[2009/07/13 17:16:19 | 000,029,696 | —- | M] (Microsoft Corporation) – C:\Windows\system32\spool\prtprocs\w32x86\winprint.dll

< %systemroot%\REPAIR\*.bak1 >

< %systemroot%\REPAIR\*.ini >

< %systemroot%\system32\*.jpg >

< %systemroot%\*.jpg >

< %systemroot%\*.png >

< %systemroot%\*.scr >

< %systemroot%\*._sy >

< %APPDATA%\Adobe\Update\*.* >

< %ALLUSERSPROFILE%\Favorites\*.* >

< %APPDATA%\Microsoft\*.* >

< %PROGRAMFILES%\*.* >
[2010/10/27 17:59:32 | 005,709,831 | —- | M] () – C:\Program Files\01 the first song.mp3
[2010/10/27 17:58:20 | 005,219,767 | —- | M] () – C:\Program Files\03 no one's gonna love you.mp3
[2010/10/31 10:04:59 | 005,609,172 | —- | M] () – C:\Program Files\101-taylor_swift-mine.mp3
[2010/10/31 10:22:47 | 006,603,340 | —- | M] () – C:\Program Files\102-taylor_swift-sparks_fly.mp3
[2010/10/31 10:22:05 | 007,160,839 | —- | M] () – C:\Program Files\103-taylor_swift-back_to_december.mp3
[2010/10/31 10:21:07 | 005,918,969 | —- | M] () – C:\Program Files\104-taylor_swift-speak_now.mp3
[2010/10/31 10:20:26 | 009,054,846 | —- | M] () – C:\Program Files\105-taylor_swift-dear_john.mp3
[2010/10/31 10:19:23 | 005,531,357 | —- | M] () – C:\Program Files\106-taylor_swift-mean.mp3
[2010/10/31 10:18:42 | 006,915,258 | —- | M] () – C:\Program Files\107-taylor_swift-the_story_of_us.mp3
[2010/10/31 10:17:53 | 006,016,684 | —- | M] () – C:\Program Files\108-taylor_swift-never_grow_up.mp3
[2010/10/31 10:17:10 | 009,129,224 | —- | M] () – C:\Program Files\109-taylor_swift-enchanted.mp3
[2010/10/31 10:16:05 | 005,701,179 | —- | M] () – C:\Program Files\110-taylor_swift-better_than_revenge.mp3
[2010/10/31 10:15:25 | 006,819,869 | —- | M] () – C:\Program Files\111-taylor_swift-innocent.mp3
[2010/10/31 10:14:38 | 006,400,578 | —- | M] () – C:\Program Files\112-taylor_swift-haunted.mp3
[2010/10/31 10:13:51 | 008,773,644 | —- | M] () – C:\Program Files\113-taylor_swift-last_kiss.mp3
[2010/10/31 10:12:50 | 007,517,546 | —- | M] () – C:\Program Files\114-taylor_swift-long_live.mp3
[2010/10/31 10:11:57 | 005,706,399 | —- | M] () – C:\Program Files\201-taylor_swift-ours.mp3
[2010/10/31 10:11:15 | 005,574,290 | —- | M] () – C:\Program Files\202-taylor_swift-if_this_was_a_movie.mp3
[2010/10/31 10:09:22 | 007,124,608 | —- | M] () – C:\Program Files\203-taylor_swift-superman.mp3
[2010/10/31 10:10:27 | 006,869,412 | —- | M] () – C:\Program Files\204-taylor_swift-back_to_december_(acoustic).mp3
[2010/10/31 10:06:25 | 004,878,350 | —- | M] () – C:\Program Files\205-taylor_swift-haunted_(acoustic).mp3
[2010/10/31 10:05:43 | 005,867,918 | —- | M] () – C:\Program Files\206-taylor_swift-mine_(us_version).mp3
[2010/10/31 10:23:37 | 007,525,691 | —- | M] () – C:\Program Files\207-taylor_swift-back_to_december_(us_version).mp3
[2009/07/13 20:41:57 | 000,000,174 | -HS- | M] () – C:\Program Files\desktop.ini
[2010/10/31 10:25:56 | 003,514,368 | —- | M] () – C:\Program Files\INCOMPLETE~208-taylor_swift-the_story_of_us_(us_version).mp3
[2010/10/27 17:55:16 | 005,665,067 | —- | M] () – C:\Program Files\the shins - oh inverted world 05 girl inform me.mp3

< %APPDATA%\Update\*.* >

< %systemroot%\*. /mp /s >

< %systemroot%\System32\config\*.sav >

< %PROGRAMFILES%\bak. /s >

< %systemroot%\system32\bak. /s >

< %ALLUSERSPROFILE%\Start Menu\*.lnk /x >

< %systemroot%\system32\config\systemprofile\*.dat /x >

< %systemroot%\*.config >

< %systemroot%\system32\*.db >

< %PROGRAMFILES%\Internet Explorer\*.dat >

< %APPDATA%\Microsoft\Internet Explorer\Quick Launch\*.lnk /x >
[2009/09/29 12:55:00 | 000,000,221 | -HS- | M] () – C:\Users\Charlene\AppData\Roaming\Microsoft\Internet Explorer\Quick Launch\desktop (1).ini
[2011/03/20 13:33:54 | 000,000,221 | -HS- | M] () – C:\Users\Charlene\AppData\Roaming\Microsoft\Internet Explorer\Quick Launch\desktop.ini

< %USERPROFILE%\Desktop\*.exe >

< %PROGRAMFILES%\Common Files\*.* >

< %systemroot%\*.src >

< %systemroot%\install\*.* >

< %systemroot%\system32\DLL\*.* >
< %systemroot%\system32\HelpFiles\*.* >

< %systemroot%\system32\rundll\*.* >

< %systemroot%\winn32\*.* >

< %systemroot%\Java\*.* >

< %systemroot%\system32\test\*.* >

< %systemroot%\system32\Rundll32\*.* >

< %systemroot%\AppPatch\Custom\*.* >
========== Hard Links - Junction Points - Mount Points - Symbolic Links ==========
[C:\Windows\$NtUninstallKB28797$] -> Error: Cannot create file handle -> Unknown point type

========== Alternate Data Streams ==========

@Alternate Data Stream - 124 bytes -> C:\ProgramData\TEMP:03D08225

< End of report >
Hello and Posted Image

My name is patndoris. I will be glad to take a look at your log and help you with solving any malware problems. It will be very helpful if you follow these guidelines:
  • Malware logs are often lengthy and can take a lot of time to research and interpret. Please be patient while I review your logs.
  • Please note that there is no "Quick Fix" to modern malware infections and we may need to use several different approaches to get your system clean.
  • Please make sure to carefully read any instruction that I give you. If you're not sure, or if something unexpected happens, do NOT continue! Stop and ask!
  • Please follow my instructions carefully and in the order they are posted. You may also find it helpful to print out the instructions you receive.
  • Please do not run any scans or install/uninstall any applications or delete anything without being directed to do so.
  • Remember, absence of symptoms does not mean the infection is all gone. Please stick with me till you're given the "all clear".
  • Please do not use the Attachment feature for any log file. Do a Copy/Paste of the entire contents of the log file and submit it inside your post.
  • Please reply within 3 days. If I do not hear back from you in that time frame, I will post a reminder for you. Topics with no reply in 4 days are closed!


I can see that you have recently installed Combofix on your machine. If you have already run it (which by the way is highly inadvisable unless your logs have been analyzed and a trained malware helper instructs you to run it) please provide the log produced which will be located at C:\ComboFix.txt


Please read carefully and follow these steps. There is a difference between what you see in one of the images below and what I need you to do.
We are only creating a log - I do NOT want you to "cure" or try to fix anything in this step. It is very important that you don't choose Cure when presented with that option.

  • Download TDSSKiller and save it to your Desktop.
  • Extract its contents to your desktop.
  • Once extracted, open the TDSSKiller folder and doubleclick on TDSSKiller.exe to run the application, then on Start Scan.


    🖼Click to load external image (Posted Image)

  • If an infected file is detected, the default action will be Cure but I want you to choose SKIP instead , click on Continue.


    🖼Click to load external image (Posted Image)

  • If a suspicious file is detected, the default action will be Skip, click on Continue.


    🖼Click to load external image (Posted Image)

  • It may ask you to reboot the computer to complete the process. Click on Reboot Now.


    🖼Click to load external image (Posted Image)

  • If no reboot is require, click on Report. A log file should appear. Please copy and paste the contents of that file here.
  • If a reboot is required, the report can also be found in your root directory, (usually C:\ folder) in the form of "TDSSKiller.[Version]_[Date]_[Time]_log.txt". Please copy and paste the contents of that file here.

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI