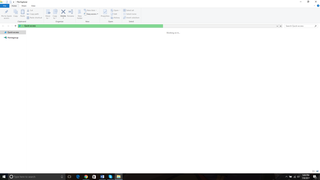
I have a real issue right now with "FILE EXPLORER" not being displayed correctly. I also have graphics not being displayed when viewing files and folders. I think what may of happened is I may have accidentally downloaded some infection and it changed my internal settings of my computer and there may be some slight corruption with my system files. Outside of that, i don't notice any slow downs or usual hick-ups or stutters in the machine. Just file and folders not working correctly.
As you can see i have no access to my hard-drives and the regular "File" Button displays minimal items. I am able to check my files and folders through the "Frequent places" menu. But this is obviously an issue and makes it real hard for me to navigate through all of my files and folders on my computer.
This next image i will show will display the dissapearing graphics of my icons and folder items displayed on the screen
I have no idea what is causing all this but it seemed to have happened a few days ago when i inadvertently when into a website that re-directed me to a site displaying my computer was in danger. Oddly enough Ublock origin didn't block this pop-up.
There are a few other minor changes i have noticed such as the auto spell checker not removing the "RED LINE" under words and some other little things. I am almost these are all the results of some infection. I just don't know the severity of it or if its going to continue to change things on my machine.
[removed]
Platform: Windows 10 Home Version 1607 (X64) Language: English (United States)
Internet Explorer Version 11 (Default browser: Edge)
Boot Mode: Normal
Tutorial for Farbar Recovery Scan Tool: http://www.geekstogo.com/forum/topic/335081-frst-tutorial-how-to-use-farbar-recovery-scan-tool/
==================== Processes (Whitelisted) =================
(If an entry is included in the fixlist, the process will be closed. The file will not be moved.)
(NVIDIA Corporation) C:\Windows\System32\nvvsvc.exe
(AVAST Software) C:\Program Files\AVAST Software\Avast\AvastSvc.exe
(AVAST Software) C:\Program Files\AVAST Software\Avast\afwServ.exe
() C:\Program Files\WinZip Smart Monitor\WinZip Smart Monitor Service.exe
(Apple Inc.) C:\Program Files\Bonjour\mDNSResponder.exe
() C:\Program Files (x86)\Canon\IJPLM\ijplmsvc.exe
(Intel Corporation) C:\Windows\System32\ibtsiva.exe
(Microsoft Corporation) C:\Program Files\Common Files\microsoft shared\ClickToRun\OfficeClickToRun.exe
(Intel(R) Corporation) C:\Program Files\Common Files\Intel\WirelessCommon\RegSrvc.exe
(Intel(R) Corporation) C:\Program Files\Intel\WiFi\bin\EvtEng.exe
(Intel® Corporation) C:\Program Files\Intel\WiFi\bin\ZeroConfigService.exe
(Google Inc.) C:\Program Files (x86)\Google\Update\1.3.33.5\GoogleCrashHandler.exe
(Google Inc.) C:\Program Files (x86)\Google\Update\1.3.33.5\GoogleCrashHandler64.exe
(Microsoft Corporation) C:\Windows\System32\wlanext.exe
(Microsoft Corporation) C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\RemindersServer.exe
(AVAST Software) C:\Program Files\AVAST Software\Avast\AvastUI.exe
(Valve Corporation) C:\Program Files (x86)\Steam\Steam.exe
() C:\Program Files\WindowsApps\Microsoft.SkypeApp_11.18.614.0_x64__kzf8qxf38zg5c\SkypeHost.exe
(Valve Corporation) C:\Program Files (x86)\Common Files\Steam\SteamService.exe
(Microsoft Corporation) C:\Program Files (x86)\Microsoft Office\root\Office16\WINWORD.EXE
(Microsoft Corporation) C:\Windows\System32\dllhost.exe
(Malwarebytes) C:\Program Files\Malwarebytes\Anti-Malware\MBAMService.exe
(Corel Corporation) C:\Program Files\WinZip Smart Monitor\WinZipSmartMonitor.exe
(Valve Corporation) C:\Program Files (x86)\Steam\bin\cef\cef.win7\steamwebhelper.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Skype Technologies S.A.) C:\Program Files (x86)\Skype\Phone\Skype.exe
(Microsoft Corporation) C:\Windows\syswow64\dllhost.exe
() C:\Program Files\WindowsApps\9E2F88E3.Twitter_5.8.1.0_x86__wgeqdkkx372wm\Twitter.Windows.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Skype Technologies) C:\Program Files (x86)\Skype\Browser\SkypeBrowserHost.exe
(Skype Technologies) C:\Program Files (x86)\Skype\Browser\SkypeBrowserHost.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Microsoft Corporation) C:\Windows\System32\mspaint.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Microsoft Corporation) C:\Windows\System32\mspaint.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Microsoft Corporation) C:\Windows\System32\smartscreen.exe
(Microsoft Corporation) C:\Windows\System32\LocationNotificationWindows.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
==================== Registry (Whitelisted) ====================
(If an entry is included in the fixlist, the registry item will be restored to default or removed. The file will not be moved.)
HKLM\…\Run: [ETDCtrl] => C:\Program Files\Elantech\ETDCtrl.exe [3348712 2016-09-07] (ELAN Microelectronics Corp.)
HKLM\…\Run: [AvastUI.exe] => C:\Program Files\AVAST Software\Avast\AvLaunch.exe [213824 2017-05-09] (AVAST Software)
HKLM\…\Run: [WinZip UN] => C:\Program Files\WinZip\WZUpdateNotifier.exe [1878016 2017-04-19] (WinZip)
HKLM\…\Run: [WinZip PreLoader] => C:\Program Files\WinZip\WzPreloader.exe [124360 2017-04-19] (WinZip Computing, S.L.)
HKLM\…\Run: [WinZip FAH] => C:\Program Files\WinZip\FAHConsole.exe [436416 2017-04-19] (WinZip Computing, S.L.)
HKLM\…\Run: [Malwarebytes TrayApp] => C:\PROGRAM FILES\MALWAREBYTES\ANTI-MALWARE\mbamtray.exe [3146704 2017-05-09] (Malwarebytes)
HKLM-x32\…\Run: [PowerDVD15Agent] => C:\Program Files (x86)\CyberLink\PowerDVD15\PowerDVD15Agent.exe [949960 2015-10-18] (CyberLink Corp.)
HKLM-x32\…\Run: [IJNetworkScannerSelectorEX] => C:\Program Files (x86)\Canon\IJ Network Scanner Selector EX\CNMNSST.exe [452272 2012-08-31] (CANON INC.)
HKLM-x32\…\Run: [CanonQuickMenu] => C:\Program Files (x86)\Canon\Quick Menu\CNQMMAIN.EXE [1279120 2012-09-27] (CANON INC.)
HKLM Group Policy restriction on software: %systemroot%\system32\mrt.exe <==== ATTENTION
HKU\S-1-5-21-2880522648-3974542570-3237673942-1001\…\Run: [Lync] => C:\Program Files (x86)\Microsoft Office\root\Office16\lync.exe [23348928 2017-06-16] (Microsoft Corporation)
HKU\S-1-5-21-2880522648-3974542570-3237673942-1001\…\Run: [Mal Updater 2] => C:\Program Files (x86)\Mal Updater 2\MalUpdater.exe [7100928 2017-05-25] (eden.fm)
HKU\S-1-5-21-2880522648-3974542570-3237673942-1001\…\Run: [Steam] => C:\Program Files (x86)\Steam\steam.exe [3042592 2017-06-07] (Valve Corporation)
HKU\S-1-5-21-2880522648-3974542570-3237673942-1001\…\Run: [Skype] => C:\Program Files (x86)\Skype\Phone\Skype.exe [27784672 2017-06-27] (Skype Technologies S.A.)
==================== Internet (Whitelisted) ====================
(If an item is included in the fixlist, if it is a registry item it will be removed or restored to default.)
Tcpip\Parameters: [DhcpNameServer] 192.168.1.1
Tcpip\..\Interfaces\{0f41bf63-5bb8-474d-8459-58f65b76a21f}: [DhcpNameServer] 192.168.1.1
Tcpip\..\Interfaces\{4a451cca-fb3b-42e2-884b-4491dfe30183}: [DhcpNameServer] 192.168.1.1
Tcpip\..\Interfaces\{d6f46e6c-0409-49ec-98a7-7e625be20655}: [DhcpNameServer] 192.168.1.1
Internet Explorer:
==================
HKU\S-1-5-21-2880522648-3974542570-3237673942-1001\Software\Microsoft\Internet Explorer\Main,Start Page =
BHO: Lync Browser Helper -> {31D09BA0-12F5-4CCE-BE8A-2923E76605DA} -> C:\Program Files (x86)\Microsoft Office\root\VFS\ProgramFilesX64\Microsoft Office\Office16\OCHelper.dll [2017-06-16] (Microsoft Corporation)
BHO: Canon Easy-WebPrint EX BHO -> {3785D0AD-BFFF-47F6-BF5B-A587C162FED9} -> C:\Program Files\Canon\Easy-WebPrint EX\ewpexbho.dll [2016-02-23] (CANON INC.)
BHO: Microsoft OneDrive for Business Browser Helper -> {D0498E0A-45B7-42AE-A9AA-ABA463DBD3BF} -> C:\Program Files (x86)\Microsoft Office\root\VFS\ProgramFilesX64\Microsoft Office\Office16\GROOVEEX.DLL [2017-06-16] (Microsoft Corporation)
BHO-x32: Lync Browser Helper -> {31D09BA0-12F5-4CCE-BE8A-2923E76605DA} -> C:\Program Files (x86)\Microsoft Office\root\Office16\OCHelper.dll [2017-06-16] (Microsoft Corporation)
BHO-x32: Canon Easy-WebPrint EX BHO -> {3785D0AD-BFFF-47F6-BF5B-A587C162FED9} -> C:\Program Files (x86)\Canon\Easy-WebPrint EX\ewpexbho.dll [2016-02-23] (CANON INC.)
BHO-x32: Microsoft OneDrive for Business Browser Helper -> {D0498E0A-45B7-42AE-A9AA-ABA463DBD3BF} -> C:\Program Files (x86)\Microsoft Office\root\Office16\GROOVEEX.DLL [2017-06-16] (Microsoft Corporation)
Toolbar: HKLM - Canon Easy-WebPrint EX - {759D9886-0C6F-4498-BAB6-4A5F47C6C72F} - C:\Program Files\Canon\Easy-WebPrint EX\ewpexhlp.dll [2016-02-23] (CANON INC.)
Toolbar: HKLM-x32 - Canon Easy-WebPrint EX - {759D9886-0C6F-4498-BAB6-4A5F47C6C72F} - C:\Program Files (x86)\Canon\Easy-WebPrint EX\ewpexhlp.dll [2016-02-23] (CANON INC.)
Handler-x32: mso-minsb-roaming.16 - {83C25742-A9F7-49FB-9138-434302C88D07} - C:\Program Files (x86)\Microsoft Office\root\Office16\MSOSB.DLL [2017-06-16] (Microsoft Corporation)
Handler-x32: mso-minsb.16 - {42089D2D-912D-4018-9087-2B87803E93FB} - C:\Program Files (x86)\Microsoft Office\root\Office16\MSOSB.DLL [2017-06-16] (Microsoft Corporation)
Handler: osf - {D924BDC6-C83A-4BD5-90D0-095128A113D1} - C:\Program Files\Microsoft Office\Office15\MSOSB.DLL [2016-10-11] (Microsoft Corporation)
Handler-x32: osf-roaming.16 - {42089D2D-912D-4018-9087-2B87803E93FB} - C:\Program Files (x86)\Microsoft Office\root\Office16\MSOSB.DLL [2017-06-16] (Microsoft Corporation)
Handler-x32: osf.16 - {5504BE45-A83B-4808-900A-3A5C36E7F77A} - C:\Program Files (x86)\Microsoft Office\root\Office16\MSOSB.DLL [2017-06-16] (Microsoft Corporation)
FireFox:
========
FF DefaultProfile: ndeblt7j.default
FF ProfilePath: C:\Users\RCMAT\AppData\Roaming\Mozilla\Firefox\Profiles\ndeblt7j.default [2017-07-04]
FF Extension: (Avast SafePrice) - C:\Users\RCMAT\AppData\Roaming\Mozilla\Firefox\Profiles\ndeblt7j.default\Extensions\[removed] [2017-07-07]
FF Extension: (Avast Online Security) - C:\Users\RCMAT\AppData\Roaming\Mozilla\Firefox\Profiles\ndeblt7j.default\Extensions\[removed] [2017-07-07]
FF Plugin: @microsoft.com/SharePoint,version=14.0 -> C:\PROGRA~1\MICROS~2\Office15\NPSPWRAP.DLL [2014-01-23] (Microsoft Corporation)
FF Plugin-x32: @canon.com/EPPEX -> C:\Program Files (x86)\Canon\My Image Garden\AddOn\CIG\npmigfpi.dll [2011-11-30] (CANON INC.)
FF Plugin-x32: @microsoft.com/Lync,version=15.0 -> C:\Program Files (x86)\Microsoft Office\root\VFS\ProgramFilesX86\Mozilla Firefox\plugins\npmeetingjoinpluginoc.dll [2017-05-26] (Microsoft Corporation)
FF Plugin-x32: @microsoft.com/SharePoint,version=14.0 -> C:\Program Files (x86)\Microsoft Office\root\Office16\NPSPWRAP.DLL [2017-05-26] (Microsoft Corporation)
FF Plugin-x32: @tools.google.com/Google Update;version=3 -> C:\Program Files (x86)\Google\Update\1.3.33.5\npGoogleUpdate3.dll [2017-04-27] (Google Inc.)
FF Plugin-x32: @tools.google.com/Google Update;version=9 -> C:\Program Files (x86)\Google\Update\1.3.33.5\npGoogleUpdate3.dll [2017-04-27] (Google Inc.)
FF Plugin-x32: @videolan.org/vlc,version=2.2.4 -> C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll [2017-05-24] (VideoLAN)
FF Plugin-x32: @videolan.org/vlc,version=2.2.6 -> C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll [2017-05-24] (VideoLAN)
FF Plugin-x32: Adobe Reader -> C:\Program Files (x86)\Adobe\Acrobat Reader DC\Reader\AIR\nppdf32.dll [2017-04-04] (Adobe Systems Inc.)
Chrome:
=======
CHR HomePage: Default -> hxxp://www.google.com/ig/redirectdomain?brand=ASUT&bmod=ASUT
CHR Session Restore: Default -> is enabled.
CHR Profile: C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default [2017-07-08]
CHR Extension: (Google Slides) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\aapocclcgogkmnckokdopfmhonfmgoek [2017-03-24]
CHR Extension: (Google Docs) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\aohghmighlieiainnegkcijnfilokake [2017-03-24]
CHR Extension: (Google Drive) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\apdfllckaahabafndbhieahigkjlhalf [2017-03-24]
CHR Extension: (WOT: Web of Trust, Website Reputation Ratings) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\bhmmomiinigofkjcapegjjndpbikblnp [2017-05-30]
CHR Extension: (YouTube) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\blpcfgokakmgnkcojhhkbfbldkacnbeo [2017-03-24]
CHR Extension: (uBlock Origin) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\cjpalhdlnbpafiamejdnhcphjbkeiagm [2017-06-27]
CHR Extension: (Adobe Acrobat) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\efaidnbmnnnibpcajpcglclefindmkaj [2017-04-28]
CHR Extension: (Avast Passwords) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\emhginjpijfggbofeediiojmdlmlkoik [2017-04-07]
CHR Extension: (Google Sheets) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\felcaaldnbdncclmgdcncolpebgiejap [2017-03-24]
CHR Extension: (Google Docs Offline) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\ghbmnnjooekpmoecnnnilnnbdlolhkhi [2017-03-24]
CHR Extension: (Avast Online Security) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\gomekmidlodglbbmalcneegieacbdmki [2017-06-13]
CHR Extension: (Chrome Web Store Payments) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\nmmhkkegccagdldgiimedpiccmgmieda [2017-03-24]
CHR Extension: (Gmail) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\pjkljhegncpnkpknbcohdijeoejaedia [2017-03-24]
CHR Extension: (Chrome Media Router) - C:\Users\RCMAT\AppData\Local\Google\Chrome\User Data\Default\Extensions\pkedcjkdefgpdelpbcmbmeomcjbeemfm [2017-07-06]
CHR HKLM-x32\…\Chrome\Extension: [efaidnbmnnnibpcajpcglclefindmkaj] - hxxps://clients2.google.com/service/update2/crx
CHR HKLM-x32\…\Chrome\Extension: [eofcbnmajmjmplflapaojjnihcjkigck] - hxxps://clients2.google.com/service/update2/crx
CHR HKLM-x32\…\Chrome\Extension: [gomekmidlodglbbmalcneegieacbdmki] - hxxps://clients2.google.com/service/update2/crx
==================== Services (Whitelisted) ====================
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
S3 aswbIDSAgent; C:\Program Files\AVAST Software\Avast\x64\aswidsagenta.exe [7346208 2017-05-09] (AVAST Software s.r.o.)
R2 avast! Antivirus; C:\Program Files\AVAST Software\Avast\AvastSvc.exe [263304 2017-05-09] (AVAST Software)
R2 avast! Firewall; C:\Program Files\AVAST Software\Avast\afwServ.exe [310496 2017-05-09] (AVAST Software)
R2 ClickToRunSvc; C:\Program Files\Common Files\Microsoft Shared\ClickToRun\OfficeClickToRun.exe [4122816 2017-06-10] (Microsoft Corporation)
R2 IJPLMSVC; C:\Program Files (x86)\Canon\IJPLM\IJPLMSVC.EXE [140456 2012-03-28] ()
R2 MBAMService; C:\Program Files\Malwarebytes\Anti-Malware\mbamservice.exe [4470736 2017-05-09] (Malwarebytes)
S3 MyWiFiDHCPDNS; C:\Program Files\Intel\WiFi\bin\PanDhcpDns.exe [268192 2015-06-12] ()
S3 WdNisSvc; C:\Program Files\Windows Defender\NisSrv.exe [347320 2017-04-27] (Microsoft Corporation)
S3 WinDefend; C:\Program Files\Windows Defender\MsMpEng.exe [103712 2017-04-27] (Microsoft Corporation)
R2 WinZip Smart Monitor Service; C:\Program Files\WinZip Smart Monitor\WinZip Smart Monitor Service.exe [495616 2017-04-11] ()
R2 ZeroConfigService; C:\Program Files\Intel\WiFi\bin\ZeroConfigService.exe [3831200 2015-06-12] (Intel® Corporation)
R2 ibtsiva; %SystemRoot%\system32\ibtsiva [X]
===================== Drivers (Whitelisted) ======================
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
R1 aswbidsdriver; C:\WINDOWS\system32\drivers\aswbidsdrivera.sys [319984 2017-07-07] (AVAST Software s.r.o.)
R0 aswbidsh; C:\WINDOWS\system32\drivers\aswbidsha.sys [198944 2017-07-07] (AVAST Software s.r.o.)
R0 aswblog; C:\WINDOWS\system32\drivers\aswbloga.sys [343264 2017-07-07] (AVAST Software s.r.o.)
R0 aswbuniv; C:\WINDOWS\system32\drivers\aswbuniva.sys [57704 2017-07-07] (AVAST Software s.r.o.)
S3 aswHwid; C:\WINDOWS\system32\drivers\aswHwid.sys [46984 2017-07-07] (AVAST Software)
R1 aswKbd; C:\WINDOWS\system32\drivers\aswKbd.sys [41800 2017-07-07] (AVAST Software)
R2 aswMonFlt; C:\WINDOWS\system32\drivers\aswMonFlt.sys [146664 2017-07-07] (AVAST Software)
R1 aswNetSec; C:\WINDOWS\system32\drivers\aswNetSec.sys [554528 2017-07-07] (AVAST Software)
R1 aswRdr; C:\WINDOWS\system32\drivers\aswRdr2.sys [110352 2017-07-07] (AVAST Software)
R0 aswRvrt; C:\WINDOWS\system32\drivers\aswRvrt.sys [84392 2017-07-07] (AVAST Software)
R1 aswSnx; C:\WINDOWS\system32\drivers\aswSnx.sys [1015848 2017-07-07] (AVAST Software)
R1 aswSP; C:\WINDOWS\system32\drivers\aswSP.sys [585608 2017-07-07] (AVAST Software)
S2 aswStm; C:\WINDOWS\system32\drivers\aswStm.sys [198768 2017-07-07] (AVAST Software)
R0 aswVmm; C:\WINDOWS\system32\drivers\aswVmm.sys [361336 2017-07-07] (AVAST Software)
S3 GeneStor; C:\WINDOWS\System32\drivers\GeneStor.sys [107208 2014-01-17] (GenesysLogic)
R3 ibtusb; C:\WINDOWS\system32\DRIVERS\ibtusb.sys [349960 2016-10-11] (Intel Corporation)
R0 IntelHSWPcc; C:\WINDOWS\System32\drivers\IntelPcc.sys [77992 2014-08-03] (Intel Corporation)
R3 kbfiltr; C:\WINDOWS\System32\drivers\kbfiltr.sys [17280 2012-08-05] ( )
U1 lpsport; C:\Windows\System32\Drivers\lpsport.sys [61304 2017-06-06] ()
R2 MBAMChameleon; C:\WINDOWS\system32\drivers\MBAMChameleon.sys [188312 2017-07-04] (Malwarebytes)
R3 MBAMFarflt; C:\WINDOWS\system32\drivers\farflt.sys [113592 2017-07-04] (Malwarebytes)
R3 MBAMProtection; C:\WINDOWS\system32\drivers\mbam.sys [44960 2017-07-04] (Malwarebytes)
R3 MBAMSwissArmy; C:\WINDOWS\system32\drivers\MBAMSwissArmy.sys [252832 2017-07-04] (Malwarebytes)
R3 MBAMWebProtection; C:\WINDOWS\system32\drivers\mwac.sys [93600 2017-07-08] (Malwarebytes)
R3 MEIx64; C:\WINDOWS\System32\drivers\TeeDriverx64.sys [99288 2013-10-23] (Intel Corporation)
S3 NetAdapterCx; C:\WINDOWS\System32\drivers\NetAdapterCx.sys [90624 2016-07-16] ()
R3 NETwNb64; C:\WINDOWS\System32\drivers\Netwbw02.sys [3525896 2016-11-09] (Intel Corporation)
S3 nhi; C:\WINDOWS\System32\drivers\trw81x.sys [59592 2014-05-13] (Intel Corporation)
R3 nvlddmkm; C:\WINDOWS\System32\DriverStore\FileRepository\nvamwu.inf_amd64_d4715679184092a8\nvlddmkm.sys [13754936 2016-10-11] (NVIDIA Corporation)
S3 PXGX112; C:\WINDOWS\system32\drivers\PXGX112.sys [23552 2011-07-29] ( )
S3 WdBoot; C:\WINDOWS\system32\drivers\WdBoot.sys [44056 2016-07-16] (Microsoft Corporation)
S3 WdFilter; C:\WINDOWS\system32\drivers\WdFilter.sys [290144 2016-07-16] (Microsoft Corporation)
S3 WdNisDrv; C:\WINDOWS\System32\Drivers\WdNisDrv.sys [123232 2016-07-16] (Microsoft Corporation)
R3 XtuAcpiDriver; C:\WINDOWS\System32\drivers\XtuAcpiDriver.sys [63840 2016-10-11] (Intel Corporation)
R2 {687703DE-DC6D-4649-892B-B8497854A6AB}; C:\Program Files (x86)\CyberLink\PowerDVD15\Common\NavFilter\000.fcl [29896 2015-10-18] (CyberLink Corp.)
==================== NetSvcs (Whitelisted) ===================
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
==================== One Month Created files and folders ========
(If an entry is included in the fixlist, the file/folder will be moved.)
2017-07-08 17:20 - 2017-07-08 17:21 - 00020207 _____ C:\Users\RCMAT\Desktop\FRST.txt
2017-07-08 17:20 - 2017-07-08 17:20 - 00000000 ____D C:\FRST
2017-07-08 17:19 - 2017-07-08 17:19 - 02437120 _____ (Farbar) C:\Users\RCMAT\Desktop\FRST64.exe
2017-07-07 12:18 - 2017-07-07 12:18 - 00061304 _____ () C:\WINDOWS\system32\Drivers\lpsport.sys.149945512410902
2017-07-07 12:18 - 2017-07-07 12:17 - 00400464 _____ (AVAST Software) C:\WINDOWS\system32\aswBoot.exe
2017-07-04 21:51 - 2017-07-08 12:46 - 00093600 _____ (Malwarebytes) C:\WINDOWS\system32\Drivers\mwac.sys
2017-07-04 21:51 - 2017-07-04 23:54 - 00252832 _____ (Malwarebytes) C:\WINDOWS\system32\Drivers\MBAMSwissArmy.sys
2017-07-04 21:51 - 2017-07-04 23:54 - 00113592 _____ (Malwarebytes) C:\WINDOWS\system32\Drivers\farflt.sys
2017-07-04 21:51 - 2017-07-04 23:54 - 00077376 _____ C:\WINDOWS\system32\Drivers\mbae64.sys
2017-07-04 21:51 - 2017-07-04 23:54 - 00044960 _____ (Malwarebytes) C:\WINDOWS\system32\Drivers\mbam.sys
2017-07-04 21:51 - 2017-07-04 21:51 - 00188312 _____ (Malwarebytes) C:\WINDOWS\system32\Drivers\MBAMChameleon.sys
2017-07-04 21:51 - 2017-07-04 21:51 - 00001914 _____ C:\Users\Public\Desktop\Malwarebytes.lnk
2017-07-04 21:51 - 2017-07-04 21:51 - 00000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Malwarebytes
2017-07-04 21:51 - 2017-07-04 21:51 - 00000000 ____D C:\ProgramData\Malwarebytes
2017-07-04 21:51 - 2017-07-04 21:51 - 00000000 ____D C:\Program Files\Malwarebytes
2017-07-04 21:50 - 2017-07-04 21:50 - 64025992 _____ (Malwarebytes ) C:\Users\RCMAT\Documents\mb3-setup-1878.1878-3.1.2.1733-10139.exe
2017-06-27 19:41 - 2017-06-27 19:42 - 00000000 ____D C:\Users\RCMAT\Documents\Zemuria _ Kiseki Wikia _ Fandom powered by Wikia_files
2017-06-27 19:41 - 2017-06-27 19:41 - 00216241 _____ C:\Users\RCMAT\Documents\Zemuria _ Kiseki Wikia _ Fandom powered by Wikia.html
2017-06-18 13:27 - 2017-06-23 15:40 - 00000000 ____D C:\Users\RCMAT\Desktop\2017 Toll Reunion
2017-06-16 22:26 - 2017-06-16 22:26 - 00000000 ___HD C:\WINDOWS\system32\WLANProfiles
2017-06-16 22:26 - 2017-06-16 22:26 - 00000000 ____D C:\Users\RCMAT\AppData\Roaming\Intel
2017-06-16 22:25 - 2017-06-16 22:25 - 00000000 ____D C:\ProgramData\Intel
2017-06-16 22:25 - 2017-06-16 22:25 - 00000000 ____D C:\Program Files\Intel
2017-06-16 22:25 - 2017-06-16 22:25 - 00000000 ____D C:\Program Files\Common Files\Intel
2017-06-16 22:25 - 2017-06-16 22:25 - 00000000 ____D C:\Program Files (x86)\Intel
2017-06-16 22:25 - 2017-06-16 22:25 - 00000000 ____D C:\Program Files (x86)\Cisco
2017-06-16 22:24 - 2017-06-16 22:24 - 00000000 ____D C:\Users\RCMAT\Documents\WLAN_Intel_Win10_64_VER181212
2017-06-16 22:23 - 2017-06-16 22:24 - 196285356 _____ C:\Users\RCMAT\Documents\WLAN_Intel_Win10_64_VER181212.zip
2017-06-15 01:58 - 2017-06-28 20:53 - 00000000 ____D C:\Users\RCMAT\Documents\Legend of Heroes Translation Video Project
2017-06-13 23:17 - 2017-06-13 23:17 - 00000000 ___SD C:\WINDOWS\UpdateAssistantV2
2017-06-13 20:41 - 2017-06-03 03:50 - 00315744 _____ (Adobe Systems Incorporated) C:\WINDOWS\SysWOW64\atmfd.dll
2017-06-13 20:41 - 2017-06-03 03:16 - 00279904 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\sdbus.sys
2017-06-13 20:41 - 2017-06-03 03:11 - 01706488 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\KernelBase.dll
2017-06-13 20:41 - 2017-06-03 03:09 - 02213760 _____ (Microsoft Corporation) C:\WINDOWS\system32\KernelBase.dll
2017-06-13 20:41 - 2017-06-03 03:06 - 02048496 _____ C:\WINDOWS\SysWOW64\CoreUIComponents.dll
2017-06-13 20:41 - 2017-06-03 02:59 - 01181024 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\ndis.sys
2017-06-13 20:41 - 2017-06-03 02:59 - 00118112 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\tdx.sys
2017-06-13 20:41 - 2017-06-03 02:58 - 00340832 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msv1_0.dll
2017-06-13 20:41 - 2017-06-03 02:55 - 00780640 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WWAHost.exe
2017-06-13 20:41 - 2017-06-03 02:54 - 00187232 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\dumpsd.sys
2017-06-13 20:41 - 2017-06-03 02:52 - 01021784 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\AppxPackaging.dll
2017-06-13 20:41 - 2017-06-03 02:52 - 00607072 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\NetSetupEngine.dll
2017-06-13 20:41 - 2017-06-03 02:52 - 00111968 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\NetSetupApi.dll
2017-06-13 20:41 - 2017-06-03 02:50 - 00857440 _____ (Microsoft Corporation) C:\WINDOWS\system32\WWAHost.exe
2017-06-13 20:41 - 2017-06-03 02:50 - 00381792 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\USBXHCI.SYS
2017-06-13 20:41 - 2017-06-03 02:49 - 20967840 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\shell32.dll
2017-06-13 20:41 - 2017-06-03 02:48 - 00857952 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetSetupEngine.dll
2017-06-13 20:41 - 2017-06-03 02:48 - 00148832 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetSetupApi.dll
2017-06-13 20:41 - 2017-06-03 02:45 - 22220864 _____ (Microsoft Corporation) C:\WINDOWS\system32\shell32.dll
2017-06-13 20:41 - 2017-06-03 02:44 - 01412640 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\gdi32full.dll
2017-06-13 20:41 - 2017-06-03 02:44 - 00545944 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\fontdrvhost.exe
2017-06-13 20:41 - 2017-06-03 02:39 - 05686272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Data.Pdf.dll
2017-06-13 20:41 - 2017-06-03 02:39 - 02532192 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\tcpip.sys
2017-06-13 20:41 - 2017-06-03 02:33 - 00095232 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\UserDataTimeUtil.dll
2017-06-13 20:41 - 2017-06-03 02:32 - 00002560 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\tzres.dll
2017-06-13 20:41 - 2017-06-03 02:31 - 00224256 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ExSMime.dll
2017-06-13 20:41 - 2017-06-03 02:31 - 00037376 _____ (Adobe Systems) C:\WINDOWS\SysWOW64\atmlib.dll
2017-06-13 20:41 - 2017-06-03 02:28 - 00285184 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.BlockedShutdown.dll
2017-06-13 20:41 - 2017-06-03 02:28 - 00232448 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\edputil.dll
2017-06-13 20:41 - 2017-06-03 02:26 - 00231936 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.ApplicationModel.LockScreen.dll
2017-06-13 20:41 - 2017-06-03 02:26 - 00100352 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\AuthBrokerUI.dll
2017-06-13 20:41 - 2017-06-03 02:22 - 00364544 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\NetSetupShim.dll
2017-06-13 20:41 - 2017-06-03 02:22 - 00327168 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\netcorehc.dll
2017-06-13 20:41 - 2017-06-03 02:22 - 00181760 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\tcpipcfg.dll
2017-06-13 20:41 - 2017-06-03 02:20 - 00755712 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\kerberos.dll
2017-06-13 20:41 - 2017-06-03 02:19 - 01164288 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\certutil.exe
2017-06-13 20:41 - 2017-06-03 02:16 - 00709120 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\CPFilters.dll
2017-06-13 20:41 - 2017-06-03 02:16 - 00119808 _____ (Microsoft Corporation) C:\WINDOWS\system32\UserDataTimeUtil.dll
2017-06-13 20:41 - 2017-06-03 02:15 - 00886272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\aadtb.dll
2017-06-13 20:41 - 2017-06-03 02:15 - 00053248 _____ (Microsoft Corporation) C:\WINDOWS\system32\musdialoghandlers.dll
2017-06-13 20:41 - 2017-06-03 02:15 - 00041472 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\BasicRender.sys
2017-06-13 20:41 - 2017-06-03 02:14 - 00238592 _____ (Microsoft Corporation) C:\WINDOWS\system32\MusNotification.exe
2017-06-13 20:41 - 2017-06-03 02:14 - 00124416 _____ (Microsoft Corporation) C:\WINDOWS\system32\mssprxy.dll
2017-06-13 20:41 - 2017-06-03 02:14 - 00098304 _____ (Microsoft Corporation) C:\WINDOWS\system32\MusNotificationUx.exe
2017-06-13 20:41 - 2017-06-03 02:12 - 00027136 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\fdProxy.dll
2017-06-13 20:41 - 2017-06-03 02:08 - 02643968 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\tquery.dll
2017-06-13 20:41 - 2017-06-03 02:08 - 01221120 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Media.Audio.dll
2017-06-13 20:41 - 2017-06-03 02:07 - 00552960 _____ (Microsoft Corporation) C:\WINDOWS\system32\MusUpdateHandlers.dll
2017-06-13 20:41 - 2017-06-03 02:07 - 00456192 _____ (Microsoft Corporation) C:\WINDOWS\system32\puiobj.dll
2017-06-13 20:41 - 2017-06-03 02:05 - 01883648 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Logon.dll
2017-06-13 20:41 - 2017-06-03 02:05 - 00295424 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\hnetcfg.dll
2017-06-13 20:41 - 2017-06-03 02:04 - 02006528 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\DWrite.dll
2017-06-13 20:41 - 2017-06-03 02:04 - 00773120 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SearchIndexer.exe
2017-06-13 20:41 - 2017-06-03 02:03 - 01988096 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mssrch.dll
2017-06-13 20:41 - 2017-06-03 02:02 - 02997760 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\win32kfull.sys
2017-06-13 20:41 - 2017-06-03 01:54 - 01217024 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Media.Audio.dll
2017-06-13 20:41 - 2017-06-03 01:52 - 03403264 _____ (Microsoft Corporation) C:\WINDOWS\system32\tquery.dll
2017-06-13 20:41 - 2017-06-03 01:51 - 00266752 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetSetupSvc.dll
2017-06-13 20:41 - 2017-06-03 01:50 - 02538496 _____ (Microsoft Corporation) C:\WINDOWS\system32\mssrch.dll
2017-06-13 20:41 - 2017-06-03 01:49 - 00903680 _____ (Microsoft Corporation) C:\WINDOWS\system32\SearchIndexer.exe
2017-06-13 20:41 - 2017-06-03 01:48 - 01131008 _____ (Microsoft Corporation) C:\WINDOWS\system32\localspl.dll
2017-06-13 20:41 - 2017-06-03 01:48 - 00834048 _____ (Microsoft Corporation) C:\WINDOWS\system32\win32spl.dll
2017-06-13 20:41 - 2017-06-03 01:48 - 00391168 _____ (Microsoft Corporation) C:\WINDOWS\system32\wuuhext.dll
2017-06-13 20:41 - 2017-06-03 01:40 - 00483840 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\CoreMessaging.dll
2017-06-13 20:41 - 2017-05-24 22:56 - 00038752 _____ (Microsoft Corporation) C:\WINDOWS\system32\OOBEUpdater.exe
2017-06-13 20:41 - 2017-03-03 23:16 - 00368128 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\puiobj.dll
2017-06-13 20:41 - 2017-03-03 23:16 - 00100864 _____ (Microsoft Corporation) C:\WINDOWS\system32\wpninprc.dll
2017-06-13 20:41 - 2016-09-06 21:53 - 00118272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\AppointmentActivation.dll
2017-06-13 20:40 - 2017-06-03 03:50 - 00192856 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\aepic.dll
2017-06-13 20:40 - 2017-06-03 03:14 - 01564512 _____ (Microsoft Corporation) C:\WINDOWS\system32\appraiser.dll
2017-06-13 20:40 - 2017-06-03 03:14 - 01214816 _____ (Microsoft Corporation) C:\WINDOWS\system32\aeinv.dll
2017-06-13 20:40 - 2017-06-03 03:14 - 00629088 _____ (Microsoft Corporation) C:\WINDOWS\system32\generaltel.dll
2017-06-13 20:40 - 2017-06-03 03:14 - 00544096 _____ (Microsoft Corporation) C:\WINDOWS\system32\devinv.dll
2017-06-13 20:40 - 2017-06-03 03:14 - 00379232 _____ (Adobe Systems Incorporated) C:\WINDOWS\system32\atmfd.dll
2017-06-13 20:40 - 2017-06-03 03:14 - 00335712 _____ (Microsoft Corporation) C:\WINDOWS\system32\dcntel.dll
2017-06-13 20:40 - 2017-06-03 03:14 - 00334176 _____ (Microsoft Corporation) C:\WINDOWS\system32\invagent.dll
2017-06-13 20:40 - 2017-06-03 03:14 - 00233824 _____ (Microsoft Corporation) C:\WINDOWS\system32\aepic.dll
2017-06-13 20:40 - 2017-06-03 03:14 - 00136032 _____ (Microsoft Corporation) C:\WINDOWS\system32\acmigration.dll
2017-06-13 20:40 - 2017-06-03 03:14 - 00136024 _____ (Microsoft Corporation) C:\WINDOWS\system32\ImplatSetup.dll
2017-06-13 20:40 - 2017-06-03 03:14 - 00096608 _____ (Microsoft Corporation) C:\WINDOWS\system32\CompatTelRunner.exe
2017-06-13 20:40 - 2017-06-03 03:14 - 00034648 _____ (Microsoft Corporation) C:\WINDOWS\system32\DeviceCensus.exe
2017-06-13 20:40 - 2017-06-03 03:11 - 00128864 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\tm.sys
2017-06-13 20:40 - 2017-06-03 03:08 - 07783256 _____ (Microsoft Corporation) C:\WINDOWS\system32\ntoskrnl.exe
2017-06-13 20:40 - 2017-06-03 03:01 - 02681200 _____ C:\WINDOWS\system32\CoreUIComponents.dll
2017-06-13 20:40 - 2017-06-03 02:59 - 00764392 _____ (Microsoft Corporation) C:\WINDOWS\system32\CoreMessaging.dll
2017-06-13 20:40 - 2017-06-03 02:53 - 00404824 _____ (Microsoft Corporation) C:\WINDOWS\system32\msv1_0.dll
2017-06-13 20:40 - 2017-06-03 02:51 - 02187104 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\dxgkrnl.sys
2017-06-13 20:40 - 2017-06-03 02:51 - 00402272 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\dxgmms1.sys
2017-06-13 20:40 - 2017-06-03 02:49 - 00624048 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\cng.sys
2017-06-13 20:40 - 2017-06-03 02:49 - 00509280 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\storport.sys
2017-06-13 20:40 - 2017-06-03 02:48 - 01112416 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppxPackaging.dll
2017-06-13 20:40 - 2017-06-03 02:48 - 01100128 _____ (Microsoft Corporation) C:\WINDOWS\system32\hvix64.exe
2017-06-13 20:40 - 2017-06-03 02:48 - 00989024 _____ (Microsoft Corporation) C:\WINDOWS\system32\hvax64.exe
2017-06-13 20:40 - 2017-06-03 02:44 - 01600624 _____ (Microsoft Corporation) C:\WINDOWS\system32\sppobjs.dll
2017-06-13 20:40 - 2017-06-03 02:40 - 01566552 _____ (Microsoft Corporation) C:\WINDOWS\system32\gdi32full.dll
2017-06-13 20:40 - 2017-06-03 02:40 - 00628552 _____ (Microsoft Corporation) C:\WINDOWS\system32\fontdrvhost.exe
2017-06-13 20:40 - 2017-06-03 02:39 - 00455520 _____ (Microsoft Corporation) C:\WINDOWS\system32\securekernel.exe
2017-06-13 20:40 - 2017-06-03 02:23 - 00306688 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ieproxy.dll
2017-06-13 20:40 - 2017-06-03 02:22 - 07217152 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Data.Pdf.dll
2017-06-13 20:40 - 2017-06-03 02:18 - 22569984 _____ (Microsoft Corporation) C:\WINDOWS\system32\edgehtml.dll
2017-06-13 20:40 - 2017-06-03 02:16 - 00002560 _____ (Microsoft Corporation) C:\WINDOWS\system32\tzres.dll
2017-06-13 20:40 - 2017-06-03 02:15 - 19414016 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mshtml.dll
2017-06-13 20:40 - 2017-06-03 02:15 - 18364928 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\edgehtml.dll
2017-06-13 20:40 - 2017-06-03 02:14 - 00045056 _____ (Adobe Systems) C:\WINDOWS\system32\atmlib.dll
2017-06-13 20:40 - 2017-06-03 02:11 - 00353792 _____ (Microsoft Corporation) C:\WINDOWS\system32\cloudAP.dll
2017-06-13 20:40 - 2017-06-03 02:10 - 00418304 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.BlockedShutdown.dll
2017-06-13 20:40 - 2017-06-03 02:10 - 00252928 _____ (Microsoft Corporation) C:\WINDOWS\system32\edputil.dll
2017-06-13 20:40 - 2017-06-03 02:10 - 00117760 _____ (Microsoft Corporation) C:\WINDOWS\system32\AuthBrokerUI.dll
2017-06-13 20:40 - 2017-06-03 02:09 - 00489472 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetSetupShim.dll
2017-06-13 20:40 - 2017-06-03 02:09 - 00441344 _____ (Microsoft Corporation) C:\WINDOWS\system32\netcorehc.dll
2017-06-13 20:40 - 2017-06-03 02:09 - 00337408 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetworkBindingEngineMigPlugin.dll
2017-06-13 20:40 - 2017-06-03 02:08 - 12187648 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ieframe.dll
2017-06-13 20:40 - 2017-06-03 02:08 - 00691200 _____ (Microsoft Corporation) C:\WINDOWS\system32\ieproxy.dll
2017-06-13 20:40 - 2017-06-03 02:08 - 00324608 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.ApplicationModel.LockScreen.dll
2017-06-13 20:40 - 2017-06-03 02:08 - 00147456 _____ (Microsoft Corporation) C:\WINDOWS\system32\winsrv.dll
2017-06-13 20:40 - 2017-06-03 02:07 - 00255488 _____ (Microsoft Corporation) C:\WINDOWS\system32\HNetCfgClient.dll
2017-06-13 20:40 - 2017-06-03 02:06 - 03664384 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\jscript9.dll
2017-06-13 20:40 - 2017-06-03 02:06 - 00198144 _____ (Microsoft Corporation) C:\WINDOWS\system32\dpapisrv.dll
2017-06-13 20:40 - 2017-06-03 02:04 - 06042624 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Chakra.dll
2017-06-13 20:40 - 2017-06-03 02:03 - 00932864 _____ (Microsoft Corporation) C:\WINDOWS\system32\kerberos.dll
2017-06-13 20:40 - 2017-06-03 02:01 - 00856064 _____ (Microsoft Corporation) C:\WINDOWS\system32\efscore.dll
2017-06-13 20:40 - 2017-06-03 02:00 - 23677440 _____ (Microsoft Corporation) C:\WINDOWS\system32\mshtml.dll
2017-06-13 20:40 - 2017-06-03 01:58 - 00064512 _____ (Microsoft Corporation) C:\WINDOWS\system32\fdProxy.dll
2017-06-13 20:40 - 2017-06-03 01:56 - 13091840 _____ (Microsoft Corporation) C:\WINDOWS\system32\ieframe.dll
2017-06-13 20:40 - 2017-06-03 01:53 - 08125440 _____ (Microsoft Corporation) C:\WINDOWS\system32\Chakra.dll
2017-06-13 20:40 - 2017-06-03 01:52 - 02510848 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetworkMobileSettings.dll
2017-06-13 20:40 - 2017-06-03 01:52 - 00975872 _____ (Microsoft Corporation) C:\WINDOWS\HelpPane.exe
2017-06-13 20:40 - 2017-06-03 01:52 - 00886784 _____ (Microsoft Corporation) C:\WINDOWS\system32\CPFilters.dll
2017-06-13 20:40 - 2017-06-03 01:51 - 01418240 _____ (Microsoft Corporation) C:\WINDOWS\system32\certutil.exe
2017-06-13 20:40 - 2017-06-03 01:50 - 04744704 _____ (Microsoft Corporation) C:\WINDOWS\system32\jscript9.dll
2017-06-13 20:40 - 2017-06-03 01:49 - 03615744 _____ (Microsoft Corporation) C:\WINDOWS\system32\win32kfull.sys
2017-06-13 20:40 - 2017-06-03 01:49 - 02691072 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Logon.dll
2017-06-13 20:40 - 2017-06-03 01:49 - 02475520 _____ (Microsoft Corporation) C:\WINDOWS\system32\DWrite.dll
2017-06-13 20:40 - 2017-06-03 01:49 - 02318848 _____ (Microsoft Corporation) C:\WINDOWS\system32\wuaueng.dll
2017-06-13 20:40 - 2017-06-03 01:49 - 01845248 _____ (Microsoft Corporation) C:\WINDOWS\system32\FntCache.dll
2017-06-13 20:40 - 2017-06-03 01:49 - 01513472 _____ (Microsoft Corporation) C:\WINDOWS\system32\win32kbase.sys
2017-06-13 20:40 - 2017-06-03 01:49 - 00351744 _____ (Microsoft Corporation) C:\WINDOWS\system32\hnetcfg.dll
2017-06-13 20:40 - 2017-06-03 01:48 - 01490432 _____ (Microsoft Corporation) C:\WINDOWS\system32\lsasrv.dll
2017-06-13 20:40 - 2017-06-03 01:46 - 01121280 _____ (Microsoft Corporation) C:\WINDOWS\system32\aadtb.dll
2017-06-13 20:40 - 2017-06-02 23:08 - 00080078 _____ C:\WINDOWS\system32\normidna.nls
2017-06-13 20:40 - 2017-03-03 23:22 - 00822784 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Chakradiag.dll
2017-06-13 20:40 - 2017-03-03 23:19 - 00635904 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\jscript9diag.dll
2017-06-12 23:39 - 2017-06-12 23:39 - 01393484 _____ C:\Users\RCMAT\Documents\The_Legend_Of_Heroes_Zero_No_Kiseki_English_Patch.xht
2017-06-12 20:52 - 2017-06-12 20:52 - 00155978 _____ C:\Users\RCMAT\Documents\loh zero patch.7z - Google Drive.html
2017-06-12 20:52 - 2017-06-12 20:52 - 00000000 ____D C:\Users\RCMAT\Documents\loh zero patch.7z - Google Drive_files
2017-06-11 03:31 - 2017-06-15 02:25 - 00000000 ____D C:\Users\RCMAT\Documents\Kiseki Translation scripts
==================== One Month Modified files and folders ========
(If an entry is included in the fixlist, the file/folder will be moved.)
2017-07-08 17:21 - 2017-03-24 19:51 - 00000000 ____D C:\Users\RCMAT\AppData\Roaming\Skype
2017-07-08 16:46 - 2017-03-24 20:22 - 00000000 ____D C:\WINDOWS\system32\SleepStudy
2017-07-07 19:42 - 2017-03-24 20:06 - 00000000 ____D C:\WINDOWS\AppReadiness
2017-07-07 14:42 - 2017-03-24 20:06 - 00000000 ___HD C:\Program Files\WindowsApps
2017-07-07 12:18 - 2017-03-24 20:20 - 00361336 _____ (AVAST Software) C:\WINDOWS\system32\Drivers\aswvmm.sys
2017-07-07 12:18 - 2017-03-24 20:20 - 00003994 _____ C:\WINDOWS\System32\Tasks\Avast Emergency Update
2017-07-07 12:17 - 2017-03-24 20:21 - 00041800 _____ (AVAST Software) C:\WINDOWS\system32\Drivers\aswKbd.sys
2017-07-07 12:17 - 2017-03-24 20:20 - 01015848 _____ (AVAST Software) C:\WINDOWS\system32\Drivers\aswSnx.sys
2017-07-07 12:17 - 2017-03-24 20:20 - 00585608 _____ (AVAST Software) C:\WINDOWS\system32\Drivers\aswSP.sys
2017-07-07 12:17 - 2017-03-24 20:20 - 00360792 _____ (AVAST Software) C:\WINDOWS\system32\Drivers\aswvmm.sys.149945512584306
2017-07-07 12:17 - 2017-03-24 20:20 - 00198768 _____ (AVAST Software) C:\WINDOWS\system32\Drivers\aswStm.sys
2017-07-07 12:17 - 2017-03-24 20:20 - 00146664 _____ (AVAST Software) C:\WINDOWS\system32\Drivers\aswMonFlt.sys
2017-07-07 12:17 - 2017-03-24 20:20 - 00110352 _____ (AVAST Software) C:\WINDOWS\system32\Drivers\aswRdr2.sys
2017-07-07 12:17 - 2017-03-24 20:20 - 00084392 _____ (AVAST Software) C:\WINDOWS\system32\Drivers\aswRvrt.sys
2017-07-07 12:17 - 2017-03-24 20:20 - 00046984 _____ (AVAST Software) C:\WINDOWS\system32\Drivers\aswHwid.sys
2017-07-07 12:16 - 2017-03-24 20:22 - 00554528 _____ (AVAST Software) C:\WINDOWS\system32\Drivers\aswNetSec.sys
2017-07-07 12:16 - 2017-03-24 20:20 - 00343264 _____ (AVAST Software s.r.o.) C:\WINDOWS\system32\Drivers\aswbloga.sys
2017-07-07 12:16 - 2017-03-24 20:20 - 00319984 _____ (AVAST Software s.r.o.) C:\WINDOWS\system32\Drivers\aswbidsdrivera.sys
2017-07-07 12:16 - 2017-03-24 20:20 - 00198944 _____ (AVAST Software s.r.o.) C:\WINDOWS\system32\Drivers\aswbidsha.sys
2017-07-07 12:16 - 2017-03-24 20:20 - 00057704 _____ (AVAST Software s.r.o.) C:\WINDOWS\system32\Drivers\aswbuniva.sys
2017-07-07 05:27 - 2017-05-03 15:24 - 00000000 ____D C:\Program Files (x86)\Steam
2017-07-05 23:53 - 2017-03-24 19:51 - 00000000 ___RD C:\Users\RCMAT\OneDrive
2017-07-04 01:24 - 2017-04-30 01:17 - 00000000 ____D C:\Users\RCMAT\AppData\Roaming\Mal Updater
2017-07-04 01:24 - 2017-03-24 19:42 - 00000000 ____D C:\Users\RCMAT
2017-07-04 01:23 - 2017-04-17 15:54 - 00000000 ____D C:\ProgramData\CanonIJPLM
2017-07-03 19:55 - 2017-03-25 03:00 - 00000000 ____D C:\Users\RCMAT\Documents\Ellen
2017-07-03 16:15 - 2017-03-25 02:59 - 00000000 ____D C:\Users\RCMAT\Documents\College
2017-07-03 14:54 - 2017-03-25 13:47 - 00000000 ____D C:\Users\RCMAT\Documents\Word Documents
2017-07-03 05:13 - 2017-03-25 13:10 - 00000000 ____D C:\Users\RCMAT\Documents\X Movies
2017-07-01 01:04 - 2017-05-02 02:06 - 00000000 ____D C:\Users\RCMAT\AppData\Roaming\vlc
2017-07-01 00:27 - 2017-03-24 19:38 - 03069666 _____ C:\WINDOWS\system32\PerfStringBackup.INI
2017-06-30 20:02 - 2017-03-24 19:59 - 00000000 ____D C:\ProgramData\Skype
2017-06-29 12:37 - 2017-05-11 19:37 - 00000000 ____D C:\WINDOWS\system32\UNP
2017-06-29 12:37 - 2017-05-11 19:37 - 00000000 ____D C:\Program Files\UNP
2017-06-28 14:39 - 2017-03-24 19:53 - 00002274 _____ C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Google Chrome.lnk
2017-06-28 14:39 - 2017-03-24 19:53 - 00002262 _____ C:\Users\Public\Desktop\Google Chrome.lnk
2017-06-24 11:15 - 2017-03-24 19:49 - 00000000 ____D C:\Users\RCMAT\AppData\Local\Packages
2017-06-21 03:35 - 2017-04-29 23:58 - 00000000 ____D C:\Users\RCMAT\Documents\Manga
2017-06-20 23:27 - 2017-03-24 19:52 - 00003290 _____ C:\WINDOWS\System32\Tasks\OneDrive Standalone Update Task v2
2017-06-20 23:27 - 2017-03-24 19:51 - 00002369 _____ C:\Users\RCMAT\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\OneDrive.lnk
2017-06-17 22:23 - 2017-04-09 12:00 - 00004600 _____ C:\WINDOWS\System32\Tasks\Adobe Flash Player PPAPI Notifier
2017-06-17 22:23 - 2017-03-24 20:06 - 00000000 ____D C:\WINDOWS\SysWOW64\Macromed
2017-06-17 22:23 - 2017-03-24 20:06 - 00000000 ____D C:\WINDOWS\system32\Macromed
2017-06-16 23:33 - 2017-04-03 11:42 - 00000000 ____D C:\Program Files (x86)\Microsoft Office
2017-06-16 22:35 - 2017-03-24 20:06 - 00000000 ____D C:\WINDOWS\system32\NDF
2017-06-16 22:32 - 2017-03-24 20:22 - 00000006 ____H C:\WINDOWS\Tasks\SA.DAT
2017-06-16 22:32 - 2017-03-24 19:54 - 00524288 _____ C:\WINDOWS\system32\config\BBI
2017-06-16 22:25 - 2017-03-24 20:36 - 00000000 ____D C:\Users\defaultuser0
2017-06-16 22:25 - 2017-03-24 20:05 - 00000000 ____D C:\WINDOWS\INF
2017-06-16 22:25 - 2017-03-24 19:59 - 00000000 ____D C:\ProgramData\Package Cache
2017-06-16 21:06 - 2017-03-24 20:06 - 00000000 ____D C:\ProgramData\regid.1991-06.com.microsoft
2017-06-16 20:42 - 2017-03-24 20:06 - 00000000 ____D C:\WINDOWS\registration
2017-06-16 03:52 - 2017-06-04 19:32 - 00000000 ____D C:\Users\RCMAT\AppData\Roaming\NVIDIA
2017-06-15 00:36 - 2017-03-24 20:06 - 00000000 ____D C:\WINDOWS\rescache
2017-06-13 23:29 - 2017-03-24 19:49 - 00000000 __RHD C:\Users\Public\AccountPictures
2017-06-13 23:18 - 2017-03-24 20:21 - 00344496 _____ C:\WINDOWS\system32\FNTCACHE.DAT
2017-06-13 23:17 - 2017-03-24 20:06 - 00000000 ___RD C:\WINDOWS\ImmersiveControlPanel
2017-06-13 23:17 - 2017-03-24 20:06 - 00000000 ____D C:\WINDOWS\system32\appraiser
2017-06-13 23:17 - 2017-03-24 20:06 - 00000000 ____D C:\WINDOWS\ShellExperiences
2017-06-13 21:00 - 2017-03-24 22:46 - 00000000 ____D C:\WINDOWS\system32\MRT
2017-06-13 20:57 - 2017-03-24 22:46 - 133627792 ____C (Microsoft Corporation) C:\WINDOWS\system32\MRT.exe
2017-06-13 20:57 - 2017-03-24 20:00 - 00000000 ____D C:\WINDOWS\CbsTemp
2017-06-13 16:16 - 2017-03-25 12:56 - 00000000 ____D C:\Users\RCMAT\Documents\Game Directory
2017-06-10 00:56 - 2017-03-25 14:43 - 00000000 ____D C:\Users\RCMAT\Documents\[[Watching Anime]]
2017-06-09 15:15 - 2017-03-24 19:59 - 00000000 ___RD C:\Program Files (x86)\Skype
==================== Files in the root of some directories =======
2017-03-24 20:27 - 2017-03-24 20:27 - 0000000 ____H () C:\ProgramData\DP45977C.lfl
Some files in TEMP:
====================
2017-03-29 22:40 - 2017-03-29 22:40 - 0467968 _____ (Realtek Semiconductor Corp.) C:\Users\RCMAT\AppData\Local\Temp\COMAP.EXE
2017-05-09 21:30 - 2017-05-09 21:30 - 6618052 _____ (Eden.fm ) C:\Users\RCMAT\AppData\Local\Temp\MalUpdater297SetupSSL.exe
2017-04-17 15:54 - 2012-09-27 03:15 - 0865424 ____N (CANON INC.) C:\Users\RCMAT\AppData\Local\Temp\MSETUP4.EXE
2017-04-17 15:57 - 2012-07-27 01:22 - 0353944 ____R (CANON INC.) C:\Users\RCMAT\AppData\Local\Temp\uninstall.exe
2017-05-31 02:24 - 2017-05-31 02:24 - 30950664 _____ () C:\Users\RCMAT\AppData\Local\Temp\vlc-2.2.6-win32.exe
==================== Bamital & volsnap ======================
(There is no automatic fix for files that do not pass verification.)
C:\WINDOWS\system32\winlogon.exe => File is digitally signed
C:\WINDOWS\system32\wininit.exe => File is digitally signed
C:\WINDOWS\explorer.exe => File is digitally signed
C:\WINDOWS\SysWOW64\explorer.exe => File is digitally signed
C:\WINDOWS\system32\svchost.exe => File is digitally signed
C:\WINDOWS\SysWOW64\svchost.exe => File is digitally signed
C:\WINDOWS\system32\services.exe => File is digitally signed
C:\WINDOWS\system32\User32.dll => File is digitally signed
C:\WINDOWS\SysWOW64\User32.dll => File is digitally signed
C:\WINDOWS\system32\userinit.exe => File is digitally signed
C:\WINDOWS\SysWOW64\userinit.exe => File is digitally signed
C:\WINDOWS\system32\rpcss.dll => File is digitally signed
C:\WINDOWS\system32\dnsapi.dll => File is digitally signed
C:\WINDOWS\SysWOW64\dnsapi.dll => File is digitally signed
C:\WINDOWS\system32\Drivers\volsnap.sys => File is digitally signed
LastRegBack: 2017-06-30 21:07
==================== End of FRST.txt ============================