File name:
adlmint_libFNP.dll
Submission date:
2011-04-18 18:19:34 (UTC)
Current status:
finished
Result:
0/ 41 (0.0%)
File name:
adlmint_libFNP.dll
Submission date:
2011-04-18 18:19:34 (UTC)
Current status:
finished
Result:
0/ 41 (0.0%)
File name:
adlmint.dll
Submission date:
2011-04-18 18:28:53 (UTC)
Current status:
finished
Result:
0/ 41 (0.0%)
HI Nightsight,
Yes, thanks for the logs. Please do the following:
Step 1 | ComboFix - CFScript WARNING !This script is for THIS user and computer ONLY! You will not have Internet access when you execute ComboFix. All open windows will need to be closed!
Please open
Notepad and copy/paste all the text below… into the window:
DDS::
uInternet Settings,ProxyOverride = *.local
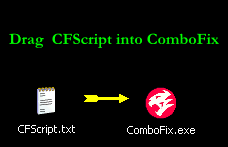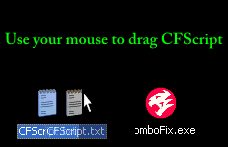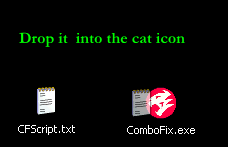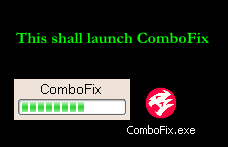
Save it to your desktop as CFScript.txt Please disable any Antivirus or Firewall you have active, as shown in this topic close all open application windows. Drag the CFScript.txt (icon) into the ComboFix.exe icon… as seen in the image below:🖼 Click to load external image (Posted Image)ComboFix to run again.Do Not use your keyboard or mouse click anywhere in the ComboFix window, as this may cause the program to stall or crash. log.txt ". Please copy/paste the contents of log.txt ** Enable your Antivirus and Firewall, before connecting to the Internet again! **
ComboFix 11-04-14.03 - RNS 04/19/2011 14:58:00.2.8 - x86
Microsoft Windows 7 Ultimate 6.1.7600.0.1252.1.1033.18.3062.2217 [GMT -7:00]
Running from: c:\users\[removed]\Desktop\ComboFix.exe
Command switches used :: c:\users\RNS\Desktop\CFScript.txt
AV: Microsoft Security Essentials *Disabled/Updated* {108DAC43-C256-20B7-BB05-914135DA5160}
SP: Microsoft Security Essentials *Disabled/Updated* {ABEC4DA7-E46C-2F39-81B5-AA334E5D1BDD}
SP: Windows Defender *Disabled/Outdated* {D68DDC3A-831F-4fae-9E44-DA132C1ACF46}
.
.
((((((((((((((((((((((((( Files Created from 2011-03-19 to 2011-04-19 )))))))))))))))))))))))))))))))
.
.
2011-04-19 22:02 . 2011-04-19 22:02 ——– d—–w- c:\users\Default\AppData\Local\temp
2011-04-19 20:22 . 2011-04-19 20:22 ——– d—–w- c:\users\RNS\AppData\Local\{83BDAA02-2EFD-4016-BFF4-889713CE6EA7}
2011-04-19 08:49 . 2011-04-11 07:04 7071056 —-a-w- c:\programdata\Microsoft\Microsoft Antimalware\Definition Updates\{6CF9B91C-9FE0-442F-9AD4-4D32E0A8B934}\mpengine.dll
2011-04-19 08:22 . 2011-04-19 08:22 ——– d—–w- c:\users\RNS\AppData\Local\{69DA4B4A-63B6-4258-89D1-8E30EC4B8656}
2011-04-18 20:21 . 2011-04-18 20:22 ——– d—–w- c:\users\RNS\AppData\Local\{25263CAA-CCF9-40AE-A28C-AA65356AF7B5}
2011-04-17 08:36 . 2011-04-17 08:36 ——– d—–w- c:\users\RNS\AppData\Local\{914C0CF0-D860-45D0-80FB-05AE1FCF3329}
2011-04-16 20:36 . 2011-04-16 20:36 ——– d—–w- c:\users\RNS\AppData\Local\{F35C770A-0FE3-423A-B6AF-92D389E14A4C}
2011-04-16 08:35 . 2011-04-16 08:36 ——– d—–w- c:\users\RNS\AppData\Local\{3DE3B02C-B391-4365-988F-E26F8DCB50FB}
2011-04-14 22:07 . 2011-04-14 22:07 ——– d—–w- c:\users\RNS\AppData\Local\{42B4EF6B-CF6D-4A12-B0BB-925F8B63627B}
2011-04-08 23:48 . 2011-04-08 23:48 ——– d—–w- c:\users\RNS\AppData\Local\{F889C204-4786-4501-991B-EE83912B6F7A}
2011-04-08 20:41 . 2011-04-08 20:41 ——– d—–w- c:\users\Default\AppData\Local\Apple Computer
2011-04-08 20:41 . 2011-04-08 20:41 ——– d—–w- c:\users\Default\AppData\Roaming\Apple Computer
2011-04-08 19:38 . 2011-04-08 19:38 ——– d—–w- c:\program files\COMODO
2011-04-08 19:33 . 2010-11-30 18:43 439632 ——w- c:\programdata\Microsoft\Microsoft Antimalware\Definition Updates\NISBackup\gapaengine.dll
2011-04-08 19:33 . 2010-11-30 18:43 439632 ——w- c:\programdata\Microsoft\Microsoft Antimalware\Definition Updates\{B205184F-14BF-40E8-BF9B-FBE57257EB1D}\gapaengine.dll
2011-04-08 19:32 . 2011-03-23 17:11 6792528 —-a-w- c:\programdata\Microsoft\Microsoft Antimalware\Definition Updates\Backup\mpengine.dll
2011-04-05 07:18 . 2011-04-05 07:18 ——– d—–w- c:\users\RNS\AppData\Roaming\SUPERAntiSpyware.com
2011-04-05 07:18 . 2011-04-05 07:18 ——– d—–w- c:\programdata\SUPERAntiSpyware.com
2011-04-05 07:14 . 2011-04-08 19:38 ——– d—–w- c:\program files\SUPERAntiSpyware
2011-04-04 22:00 . 2011-04-04 22:00 ——– d—–w- c:\users\RNS\AppData\Local\{8883D476-BF69-4B53-827D-4FBC02AB6C04}
2011-04-02 05:52 . 2011-04-02 05:52 ——– d—–w- c:\users\RNS\AppData\Roaming\Malwarebytes
2011-04-02 05:52 . 2010-12-21 01:09 38224 —-a-w- c:\windows\system32\drivers\mbamswissarmy.sys
2011-04-02 05:52 . 2011-04-02 05:52 ——– d—–w- c:\programdata\Malwarebytes
2011-04-02 05:52 . 2011-04-02 05:52 ——– d—–w- c:\program files\Malwarebytes' Anti-Malware
2011-04-02 05:52 . 2010-12-21 01:08 20952 —-a-w- c:\windows\system32\drivers\mbam.sys
2011-04-02 01:55 . 2011-04-02 01:55 ——– d—–w- c:\users\RNS\AppData\Roaming\TrojanHunter
2011-04-02 00:37 . 2011-04-02 01:56 ——– d—–w- c:\program files\TrojanHunter 5.3
2011-04-01 23:32 . 2011-04-01 23:47 ——– d—–w- c:\programdata\Spybot - Search & Destroy
2011-04-01 23:32 . 2011-04-01 23:33 ——– d—–w- c:\program files\Spybot - Search & Destroy
2011-04-01 22:31 . 2011-04-01 22:31 ——– d—–w- c:\program files\Microsoft Security Client
2011-04-01 22:31 . 2010-04-09 07:24 1285000 —-a-w- c:\windows\system32\drivers\tcpip.sys
2011-04-01 22:31 . 2010-04-09 07:24 240008 —-a-w- c:\windows\system32\drivers\netio.sys
2011-04-01 22:00 . 2011-04-01 22:00 98392 —-a-w- c:\windows\system32\drivers\SBREDrv.sys
2011-04-01 20:49 . 2011-04-08 19:36 ——– d—–w- c:\programdata\Lavasoft
2011-04-01 20:10 . 2011-04-01 20:10 ——– d—–w- c:\users\RNS\AppData\Local\{8254B4F4-0814-4AA3-A2F4-4DFA97A2F9FD}
2011-04-01 19:35 . 2011-04-01 19:35 ——– d—–w- c:\users\RNS\AppData\Local\{AE5D8B17-DA29-4E35-968B-7EA948EA2BAD}
2011-04-01 19:34 . 2011-04-01 19:56 ——– d—–w- c:\programdata\MFAData
2011-04-01 19:29 . 2011-04-01 19:29 ——– d—–w- c:\users\RNS\AppData\Roaming\Waves Audio
2011-03-30 18:49 . 2011-03-30 18:49 ——– d—–w- c:\users\RNS\AppData\Local\{B1B7536E-0DD8-4439-8E99-70A8E66D1734}
2011-03-30 06:48 . 2011-03-30 06:49 ——– d—–w- c:\users\RNS\AppData\Local\{804B2304-02FC-4948-A8A5-FF3627202746}
2011-03-29 18:48 . 2011-03-29 18:48 ——– d—–w- c:\users\RNS\AppData\Local\{92205DA8-C505-445B-955C-6644972E8B02}
2011-03-29 06:47 . 2011-03-29 06:48 ——– d—–w- c:\users\RNS\AppData\Local\{78C71C97-0A08-4AD9-BEC0-CB5253C6BE8D}
2011-03-28 18:47 . 2011-03-28 18:47 ——– d—–w- c:\users\RNS\AppData\Local\{2BF69A3F-CE2B-49B4-BB7E-0EDE494A3322}
2011-03-23 22:47 . 2011-03-23 22:48 ——– d—–w- c:\users\RNS\AppData\Local\{49DAC749-60EF-4986-B17F-5B51B73AF910}
2011-03-23 10:47 . 2011-03-23 10:47 ——– d—–w- c:\users\RNS\AppData\Local\{3E206A6B-9510-442C-89E9-5877B6F49B3D}
2011-03-22 22:47 . 2011-03-22 22:47 ——– d—–w- c:\users\RNS\AppData\Local\{898B7304-1063-4919-B960-761F25204244}
2011-03-21 22:33 . 2011-03-22 10:34 ——– d—–w- c:\users\RNS\AppData\Local\{1E277148-96B2-4A24-8AA9-A275F171E237}
.
.
.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2011-03-10 01:58 . 2010-06-24 19:33 18328 —-a-w- c:\programdata\Microsoft\IdentityCRL\production\ppcrlconfig600.dll
2011-01-30 08:33 . 2011-01-30 08:33 1228579 —-a-w- c:\windows\LightWave 3D 9 Uninstaller.exe
2011-01-20 04:15 . 2011-01-20 04:16 472808 —-a-w- c:\windows\system32\deployJava1.dll
2009-11-20 05:08 . 2009-11-20 05:08 3749224 —-a-w- c:\program files\Common Files\adlmint_libFNP.dll
2009-11-20 05:08 . 2009-11-20 05:08 2941288 —-a-w- c:\program files\Common Files\adlmint.dll
2011-03-18 17:53 . 2011-04-06 03:05 142296 —-a-w- c:\program files\mozilla firefox\components\browsercomps.dll
.
.
((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4
.
[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"Sony Ericsson PC Companion"="c:\program files\Sony Ericsson\Sony Ericsson PC Companion\PCCompanion.exe" [2009-12-08 774144]
"SpybotSD TeaTimer"="c:\program files\Spybot - Search & Destroy\TeaTimer.exe" [2009-03-05 2260480]
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"StartCCC"="c:\program files\ATI Technologies\ATI.ACE\Core-Static\CLIStart.exe" [2010-10-27 98304]
"RtHDVCpl"="c:\program files\Realtek\Audio\HDA\RtHDVCpl.exe" [2009-03-24 7289376]
"M-Audio Taskbar Icon"="c:\windows\system32\MAFWTray.exe" [2009-07-29 252424]
"Google Desktop Search"="c:\program files\Google\Google Desktop Search\GoogleDesktop.exe" [2010-12-07 30192]
"AdobeCS4ServiceManager"="c:\program files\Common Files\Adobe\CS4ServiceManager\CS4ServiceManager.exe" [2008-08-14 611712]
"Adobe Acrobat Speed Launcher"="c:\program files\Adobe\Acrobat 9.0\Acrobat\Acrobat_sl.exe" [2008-06-12 37232]
"Acrobat Assistant 8.0"="c:\program files\Adobe\Acrobat 9.0\Acrobat\Acrotray.exe" [2008-06-12 640376]
"QuickTime Task"="c:\program files\K-Lite Codec Pack\QuickTime\QTTask.exe" [2010-11-30 421888]
"iTunesHelper"="c:\program files\iTunes\iTunesHelper.exe" [2010-12-14 421160]
"SunJavaUpdateSched"="c:\program files\Common Files\Java\Java Update\jusched.exe" [2010-05-14 248552]
"MSC"="c:\program files\Microsoft Security Client\msseces.exe" [2010-11-30 997408]
.
c:\users\RNS\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\
MagicDisc.lnk - c:\program files\MagicDisc\MagicDisc.exe [2010-12-6 576000]
.
[HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\policies\system]
"ConsentPromptBehaviorAdmin"= 0 (0x0)
"ConsentPromptBehaviorUser"= 3 (0x3)
"EnableLUA"= 0 (0x0)
"EnableUIADesktopToggle"= 0 (0x0)
"PromptOnSecureDesktop"= 0 (0x0)
.
[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\windows]
"AppInit_DLLs"=c:\progra~1\Google\GOOGLE~1\GoogleDesktopNetwork3.dll
.
[HKEY_LOCAL_MACHINE\system\currentcontrolset\control\lsa]
Security Packages REG_MULTI_SZ kerberos msv1_0 schannel wdigest tspkg pku2u livessp
.
[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Lavasoft Ad-Aware Service]
@=""
.
[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\MsMpSvc]
@="Service"
.
R3 A3AB;D-Link AirPro 802.11a/b Wireless Adapter Service(A3AB);c:\windows\system32\DRIVERS\A3AB.sys [2005-03-23 450400]
R3 Adobe Version Cue CS4;Adobe Version Cue CS4;c:\program files\Common Files\Adobe\Adobe Version Cue CS4\Server\bin\VersionCueCS4.exe [2008-08-15 284016]
R3 GoogleDesktopManager-051210-111108;Google Desktop Manager 5.9.1005.12335;c:\program files\Google\Google Desktop Search\GoogleDesktop.exe [2010-12-07 30192]
R3 MpNWMon;Microsoft Malware Protection Network Driver;c:\windows\system32\DRIVERS\MpNWMon.sys [2010-10-25 43392]
R3 NisDrv;Microsoft Network Inspection System;c:\windows\system32\DRIVERS\NisDrvWFP.sys [2010-10-25 54144]
R3 NisSrv;Microsoft Network Inspection;c:\program files\Microsoft Security Client\Antimalware\NisSrv.exe [2010-11-11 206360]
R3 s1018bus;Sony Ericsson Device 1018 driver (WDM);c:\windows\system32\DRIVERS\s1018bus.sys [2009-03-25 86824]
R3 s1018mdfl;Sony Ericsson Device 1018 USB WMC Modem Filter;c:\windows\system32\DRIVERS\s1018mdfl.sys [2009-03-25 15016]
R3 s1018mdm;Sony Ericsson Device 1018 USB WMC Modem Driver;c:\windows\system32\DRIVERS\s1018mdm.sys [2009-03-25 114728]
R3 s1018mgmt;Sony Ericsson Device 1018 USB WMC Device Management Drivers (WDM);c:\windows\system32\DRIVERS\s1018mgmt.sys [2009-03-25 106208]
R3 s1018nd5;Sony Ericsson Device 1018 USB Ethernet Emulation (NDIS);c:\windows\system32\DRIVERS\s1018nd5.sys [2009-03-25 26024]
R3 s1018obex;Sony Ericsson Device 1018 USB WMC OBEX Interface;c:\windows\system32\DRIVERS\s1018obex.sys [2009-03-25 104744]
R3 s1018unic;Sony Ericsson Device 1018 USB Ethernet Emulation (WDM);c:\windows\system32\DRIVERS\s1018unic.sys [2009-03-25 109864]
R3 wacmoumonitor;Wacom Mode Helper;c:\windows\system32\DRIVERS\wacmoumonitor.sys [2010-11-03 10752]
S1 SASDIFSV;SASDIFSV;c:\program files\SUPERAntiSpyware\SASDIFSV.SYS [2010-02-17 12872]
S1 SASKUTIL;SASKUTIL;c:\program files\SUPERAntiSpyware\SASKUTIL.SYS [2010-05-10 67656]
S1 vwififlt;Virtual WiFi Filter Driver;c:\windows\system32\DRIVERS\vwififlt.sys [2009-07-13 48128]
S2 AMD External Events Utility;AMD External Events Utility;c:\windows\system32\atiesrxx.exe [2010-10-27 176128]
S2 SBSDWSCService;SBSD Security Center Service;c:\program files\Spybot - Search & Destroy\SDWinSec.exe [2009-01-26 1153368]
S2 TabletServiceWacom;TabletServiceWacom;c:\program files\Tablet\Wacom\Wacom_Tablet.exe [2010-11-15 4807536]
S3 amdkmdag;amdkmdag;c:\windows\system32\DRIVERS\atikmdag.sys [2010-10-27 6573568]
S3 amdkmdap;amdkmdap;c:\windows\system32\DRIVERS\atikmpag.sys [2010-10-27 229888]
S3 AtiHDAudioService;ATI Function Driver for HD Audio Service;c:\windows\system32\drivers\AtihdW73.sys [2010-09-25 102416]
S3 CLEDX;Team H2O CLEDX service;c:\windows\system32\DRIVERS\cledx.sys [2005-05-10 33792]
S3 MAFW;Service for M-Audio FireWire;c:\windows\system32\DRIVERS\mafw.sys [2009-07-29 192392]
S3 RTL8167;Realtek 8167 NT Driver;c:\windows\system32\DRIVERS\Rt86win7.sys [2009-07-13 139776]
.
.
[HKEY_LOCAL_MACHINE\software\microsoft\active setup\installed components\{10880D85-AAD9-4558-ABDC-2AB1552D831F}]
2009-08-20 21:24 451872 —-a-w- c:\program files\Common Files\LightScribe\LSRunOnce.exe
.
.
——- Supplementary Scan ——-
.
uStart Page = hxxp://www.musicradar.com/computermusic
uSearchURL,(Default) = hxxp://www.google.com/search/?q=%s
IE: Append Link Target to Existing PDF - c:\program files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIEAppendSelLinks.html
IE: Append to Existing PDF - c:\program files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIEAppend.html
IE: Convert Link Target to Adobe PDF - c:\program files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIECaptureSelLinks.html
IE: Convert to Adobe PDF - c:\program files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIECapture.html
FF - ProfilePath - c:\users\RNS\AppData\Roaming\Mozilla\Firefox\Profiles\ehuykxlg.default\
FF - prefs.js: browser.startup.homepage - hxxp://www.musicradar.com/computermusic
.
.
——————— LOCKED REGISTRY KEYS ———————
.
[HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0000\AllUserSettings]
@Denied: (A) (Users)
@Denied: (A) (Everyone)
@Allowed: (B 1 2 3 4 5) (S-1-5-20)
"BlindDial"=dword:00000000
.
[HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0001\AllUserSettings]
@Denied: (A) (Users)
@Denied: (A) (Everyone)
@Allowed: (B 1 2 3 4 5) (S-1-5-20)
"BlindDial"=dword:00000000
.
[HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\PCW\Security]
@Denied: (Full) (Everyone)
.
Completion time: 2011-04-19 15:04:16
ComboFix-quarantined-files.txt 2011-04-19 22:04
ComboFix2.txt 2011-04-16 08:21
.
Pre-Run: 140,668,350,464 bytes free
Post-Run: 140,242,956,288 bytes free
.
- - End Of File - - 6B73576F2D9837FE2F5D585EE882411E
Hey, btw my pc doesn't show any symptoms of infection now
is not redirecting or opening several browsers…
Glad to hear
Please do the following:
Step 1 | Please download
CCleaner (freeware) Step 2 | Please download
Malwarebytes' Anti-Malware to your
desktop.
Double-click mbam-setup.exe and follow the prompts to install the program. At the end, be sure a checkmark is placed next to Update Malwarebytes' Anti-Malware and Launch Malwarebytes' Anti-Malware , then click Finish . If an update is found, it will download and install the latest version. Once the program has loaded, select Perform quick scan , then click Scan . When the scan is complete, click OK , then Show Results to view the results. Be sure that everything is checked, and click Remove Selected . When completed, a log will open in Notepad. Please save it to a convenient location and post the results. Step 3 | Let's perform an ESET Online Scan
Note: You can use either Internet Explorer or Mozilla FireFox for this scan. You will however need to disable your current installed Anti-Virus, how to do so can be read here.
Please go here then click on: [external image: Posted Image] Note: If using Mozilla Firefox you will need to download esetsmartinstaller_enu.exe when prompted then double click on it to install. Select the option YES, I accept the Terms of Use then click on: [external image: Posted Image] When prompted allow the Add-On/Active X to install. Make sure that the option Remove found threats is NOT checked , and the option Scan archives is checked . Now click on Advanced Settings and select the following: Scan for potentially unwanted applications Scan for potentially unsafe applications Enable Anti-Stealth Technology Now click on: [external image: Posted Image] The virus signature database… will begin to download. Be patient this make take some time depending on the speed of your Internet Connection. When completed the Online Scan will begin automatically. Do not touch either the Mouse or keyboard during the scan otherwise it may stall. When completed make sure you first copy the logfile located at C:\Program Files\ESET\EsetOnlineScanner\log.txt Copy and paste that log as a reply to this topic. Now click on: [external image: Posted Image] (Selecting Uninstall application on close if you so wish)
Malwarebytes' Anti-Malware 1.50.1.1100
www.malwarebytes.org
Database version: 6445
Windows 6.1.7600
Internet Explorer 8.0.7600.16385
4/25/2011 11:31:56 PM
mbam-log-2011-04-25 (23-31-56).txt
Scan type: Quick scan
Objects scanned: 178112
Time elapsed: 2 minute(s), 3 second(s)
Memory Processes Infected: 0
Memory Modules Infected: 0
Registry Keys Infected: 2
Registry Values Infected: 0
Registry Data Items Infected: 0
Folders Infected: 0
Files Infected: 0
Memory Processes Infected:
(No malicious items detected)
Memory Modules Infected:
(No malicious items detected)
Registry Keys Infected:
HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Ext\Stats\{B1B220C1-A500-99BD-F110-04B53A2C8952} (Trojan.Ertfor) -> Quarantined and deleted successfully.
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{B1B220C1-A500-99BD-F110-04B53A2C8952} (Trojan.Ertfor) -> Quarantined and deleted successfully.
Registry Values Infected:
(No malicious items detected)
Registry Data Items Infected:
(No malicious items detected)
Folders Infected:
(No malicious items detected)
Files Infected:
(No malicious items detected)
ESETSmartInstaller@High as downloader log:
all ok
# version=7
# OnlineScannerApp.exe=1.0.0.1
# OnlineScanner.ocx=1.0.0.6427
# api_version=3.0.2
# EOSSerial=7e61d2089b772c49841d302bc2a9e535
# end=finished
# remove_checked=false
# archives_checked=true
# unwanted_checked=true
# unsafe_checked=true
# antistealth_checked=true
# utc_time=2011-04-26 08:57:43
# local_time=2011-04-26 01:57:43 (-0800, Pacific Daylight Time)
# country="United States"
# lang=1033
# osver=6.1.7600 NT
# compatibility_mode=512 16777215 100 0 0 0 0 0
# compatibility_mode=3073 16777214 0 5 1422141 1422141 0 0
# compatibility_mode=5893 16776574 100 94 10038033 55344845 0 0
# compatibility_mode=8192 67108863 100 0 0 0 0 0
# scanned=495869
# found=10
# cleaned=0
# scan_time=8209
C:\Program Files\Steinberg\vstplugins\MINDkILLERrev1\SOFTDIST.SEP probably a variant of Win32/PSW.IM.DKZOOVU trojan (unable to clean) 00000000000000000000000000000000 I
C:\Qoobox\Quarantine\C\Users\RNS\AppData\Local\akaxayug.dll.vir a variant of Win32/Cimag.GQ trojan (unable to clean) 00000000000000000000000000000000 I
C:\Windows\System32\config\systemprofile\AppData\LocalLow\Sun\Java\Deployment\cache\6.0\58\4e165e7a-662e5f5a multiple threats (unable to clean) 00000000000000000000000000000000 I
D:\MEDIT8 Files\old computer\New Folder\Sound Forge 7.0 + Keygen\Sonic Foundry Keygen.exe a variant of Win32/Keygen.AQ application (unable to clean) 00000000000000000000000000000000 I
D:\Softwares\Music Software\Rob.Papen.ConcreteFX.Blue.VSTi.v1.7.incl.KeyGen-BEAT.rar probably a variant of Win32/Agent.HEPGPJJ trojan (unable to clean) 00000000000000000000000000000000 I
D:\Softwares\Music Software\Rob.Papen.Predator.VSTi.v1.1.Incl.Keygen-AiR.rar a variant of Win32/Keygen.AD application (unable to clean) 00000000000000000000000000000000 I
D:\Softwares\Music Software\IZotope.Spectron.VST.DX.AS.RTAS.HTDM.v1.12.incl.Keygen-AiR\keygen.exe a variant of Win32/Keygen.AD application (unable to clean) 00000000000000000000000000000000 I
D:\Softwares\Music Software\Native.Instruments.Traktor.DJ.Studio.v2.5.3\Native.Instruments.Traktor.DJ.Studio.v2.5.3-H2O-Pleasuredome101\traktor_keygen.exe a variant of Win32/Keygen.AA application (unable to clean) 00000000000000000000000000000000 I
D:\Softwares\Music Software\SugarBytes.Effectrix.VST.v1.2.Incl.Keygen-AiR\a-sbe120.zip a variant of Win32/Keygen.AD application (unable to clean) 00000000000000000000000000000000 I
D:\Softwares\Nero v9.4.26.0 Reloaded + Working Keymaker\Keymaker.rar probably a variant of Win32/Agent.JMHIEES trojan (unable to clean) 00000000000000000000000000000000 I
Hi Nightsight,
ESET found malware in what appears to be cracks/keygens for music programs. Were you aware of these keygens?
Please do the following:
Step 1 | ESET found some threats in your Java's cache.
Please follow these steps to remove older version Java components and update.
Click on the following link to visit java website: Java Runtime Environment (JRE) 6 Scroll down to where it says "JDK 6 Update 24 (JDK or JRE)" . Click the "Download " button to the right column (JRE). Select the Windows platform from the dropdown menu. Read the License Agreement and then check the box that says: " I agree to the Java SE Runtime Environment 6 with JavaFX License Agreement ". Click on Continue. The page will refresh. Click on the link to download Windows Offline Installation and save the file to your desktop. Close any programs you may have running - especially your web browser. Now go to Start > Settings > Control Panel , double-click on Add/Remove Programs Check (highlight ) any item with Java Runtime Environment (JRE or J2SE or Java™ 6) in the name. Click the Remove or Change/Remove button. Repeat as many times as necessary to remove each Java version. Reboot your computer once all Java components are removed. Then from your desktop double-click on the recently downloaded java installer icon to install the newest version. After the install is complete, go into the Control Panel (using Classic View) and double-click the Java Icon . (looks like a coffee cup)On the General tab, under Temporary Internet Files, click the Settings button. Next, click on the Delete Files button There are two options in the window to clear the cache - Leave BOTH Checked Applications and AppletsTrace and Log Files Click OK on Delete Temporary Files Window Note: This deletes ALL the Downloaded Applications and Applets from the CACHE. Click OK to leave the Temporary Files Window Click OK to leave the Java Control Panel. Step 2 | Run
OTL.exe
Hi Nightsight,
Are you still there?
Yes I'm sorry, my computer suddenly started crashing again, I think the virus are still there I will follow up asap, thx!
Due to inactivity this topic will be closed.
If you need help please start a new thread.
New members follow the instructions here
http://forums.whatthetech.com/you_Infected_t106388.html and start a new topic

 is not redirecting or opening several browsers…