This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

Google redirect Trojan

18 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

Logfile of Trend Micro HijackThis v2.0.4
Scan saved at 5:30:24 PM, on 4/9/2011
Platform: Windows 7 (WinNT 6.00.3504)
MSIE: Internet Explorer v8.00 (8.00.7600.16385)
Boot mode: Normal

Running processes:
C:\Windows\system32\taskhost.exe
C:\Windows\SYSTEM32\WISPTIS.EXE
C:\Program Files\Common Files\microsoft shared\ink\TabTip.exe
C:\Windows\system32\Dwm.exe
C:\Windows\Explorer.EXE
C:\Program Files\Realtek\Audio\HDA\RtHDVCpl.exe
C:\Windows\System32\MAFWTray.exe
C:\Program Files\Google\Google Desktop Search\GoogleDesktop.exe
C:\Program Files\ATI Technologies\ATI.ACE\Core-Static\MOM.exe
C:\Program Files\Tablet\Wacom\Wacom_TabletUser.exe
C:\Program Files\Adobe\Acrobat 9.0\Acrobat\acrotray.exe
C:\Program Files\iTunes\iTunesHelper.exe
C:\Program Files\Common Files\Java\Java Update\jusched.exe
C:\Program Files\Microsoft Security Client\msseces.exe
C:\Program Files\Sony Ericsson\Sony Ericsson PC Companion\PCCompanion.exe
C:\Program Files\ATI Technologies\ATI.ACE\Core-Static\CCC.exe
C:\Program Files\MagicDisc\MagicDisc.exe
C:\Program Files\Common Files\Microsoft Shared\Ink\InputPersonalization.exe
C:\Program Files\Mozilla Firefox\firefox.exe
C:\Windows\system32\DllHost.exe
C:\Program Files\Mozilla Firefox\firefox.exe
C:\Program Files\Mozilla Firefox\plugin-container.exe
C:\Windows\system32\SearchFilterHost.exe
C:\Users\RNS\Desktop\HiJackThis.exe

R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = http://www.musicradar.com/computermusic
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://go.microsoft.com/fwlink/?LinkId=69157
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyOverride = *.local
R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName =
O2 - BHO: Spybot-S&D IE Protection - {53707962-6F74-2D53-2644-206D7942484F} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O2 - BHO: C:\Windows\system32\ma95o12g.dll - {B1B220C1-A500-99BD-F110-04B53A2C8952} - C:\Windows\system32\ma95o12g.dll (file missing)
O3 - Toolbar: Adobe PDF - {47833539-D0C5-4125-9FA8-0819E2EAAC93} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll
O3 - Toolbar: Contribute Toolbar - {517BDDE4-E3A7-4570-B21E-2B52B6139FC7} - C:\Program Files\Adobe\/Adobe Contribute CS4/contributeieplugin.dll
O3 - Toolbar: (no name) - {9D425283-D487-4337-BAB6-AB8354A81457} - (no file)
O4 - HKLM\..\Run: [StartCCC] "C:\Program Files\ATI Technologies\ATI.ACE\Core-Static\CLIStart.exe" MSRun
O4 - HKLM\..\Run: [RtHDVCpl] C:\Program Files\Realtek\Audio\HDA\RtHDVCpl.exe
O4 - HKLM\..\Run: [M-Audio Taskbar Icon] C:\Windows\system32\MAFWTray.exe
O4 - HKLM\..\Run: [Google Desktop Search] "C:\Program Files\Google\Google Desktop Search\GoogleDesktop.exe" /startup
O4 - HKLM\..\Run: [AdobeCS4ServiceManager] "C:\Program Files\Common Files\Adobe\CS4ServiceManager\CS4ServiceManager.exe" -launchedbylogin
O4 - HKLM\..\Run: [Adobe Acrobat Speed Launcher] "C:\Program Files\Adobe\Acrobat 9.0\Acrobat\Acrobat_sl.exe"
O4 - HKLM\..\Run: [Acrobat Assistant 8.0] "C:\Program Files\Adobe\Acrobat 9.0\Acrobat\Acrotray.exe"
O4 - HKLM\..\Run: [Adobe_ID0ENQBO] C:\PROGRA~1\COMMON~1\Adobe\ADOBEV~1\Server\bin\VERSIO~2.EXE
O4 - HKLM\..\Run: [H2O] C:\Program Files\SyncroSoft\Pos\H2O\cledx.exe
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\K-Lite Codec Pack\QuickTime\QTTask.exe" -atboottime
O4 - HKLM\..\Run: [iTunesHelper] "C:\Program Files\iTunes\iTunesHelper.exe"
O4 - HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
O4 - HKLM\..\Run: [LvTfeefnwpc] C:\Users\RNS\AppData\Local\Temp\services.exe
O4 - HKLM\..\Run: [LvTfeefnY] C:\Users\RNS\AppData\Local\Temp\cmd.exe
O4 - HKLM\..\Run: [LvTfeefnZP] C:\Users\RNS\AppData\Local\Temp\gdi32.exe
O4 - HKLM\..\Run: [LvTfeefnb] C:\Users\RNS\AppData\Local\Temp\mdm.exe
O4 - HKLM\..\Run: [LvTfeefnqg] C:\Users\RNS\AppData\Local\Temp\hexdump.exe
O4 - HKLM\..\Run: [LvTfeefnrc] C:\Users\RNS\AppData\Local\Temp\winamp.exe
O4 - HKLM\..\Run: [LvTfeefntpf] C:\Users\RNS\AppData\Local\Temp\iexplarer.exe
O4 - HKLM\..\Run: [LvTfeefneP] C:\Users\RNS\AppData\Local\Temp\avp32.exe
O4 - HKLM\..\Run: [LvTfeefnwg] C:\Users\RNS\AppData\Local\Temp\spoolsv.exe
O4 - HKLM\..\Run: [LvTfeefnZg] C:\Users\RNS\AppData\Local\Temp\al9ax.exe
O4 - HKLM\..\Run: [LvTfeefnz9] C:\Users\RNS\AppData\Local\Temp\nvsvc32.exe
O4 - HKLM\..\Run: [LvTfeefnxb] C:\Users\RNS\AppData\Local\Temp\sysedit.exe
O4 - HKLM\..\Run: [LvTfeefnqe] C:\Users\RNS\AppData\Local\Temp\login.exe
O4 - HKLM\..\Run: [LvTfeefnoc] C:\Users\RNS\AppData\Local\Temp\debug.exe
O4 - HKLM\..\Run: [LvTfeefnsb] C:\Users\RNS\AppData\Local\Temp\drweb.exe
O4 - HKLM\..\Run: [LvTfeefnsd] C:\Users\RNS\AppData\Local\Temp\taskmgr.exe
O4 - HKLM\..\Run: [LvTfeefnvZ] C:\Users\RNS\AppData\Local\Temp\install.exe
O4 - HKLM\..\Run: [LvTfeefnwe] C:\Users\RNS\AppData\Local\Temp\setup.exe
O4 - HKLM\..\Run: [LvTfeefngP] C:\Users\RNS\AppData\Local\Temp\win32.exe
O4 - HKLM\..\Run: [MSC] "C:\Program Files\Microsoft Security Client\msseces.exe" -hide -runkey
O4 - HKCU\..\Run: [Sony Ericsson PC Companion] "C:\Program Files\Sony Ericsson\Sony Ericsson PC Companion\PCCompanion.exe" /systray /nologon
O4 - HKCU\..\Run: [4E3E0230868C0F5D] C:\Calc.Bin\Calc.Bin.exe
O4 - HKCU\..\Run: [LvTfeefnwpc] C:\Users\RNS\AppData\Local\Temp\services.exe
O4 - HKCU\..\Run: [LvTfeefnY] C:\Users\RNS\AppData\Local\Temp\cmd.exe
O4 - HKCU\..\Run: [LvTfeefnZP] C:\Users\RNS\AppData\Local\Temp\gdi32.exe
O4 - HKCU\..\Run: [LvTfeefnb] C:\Users\RNS\AppData\Local\Temp\mdm.exe
O4 - HKCU\..\Run: [LvTfeefnqg] C:\Users\RNS\AppData\Local\Temp\hexdump.exe
O4 - HKCU\..\Run: [LvTfeefnrc] C:\Users\RNS\AppData\Local\Temp\winamp.exe
O4 - HKCU\..\Run: [LvTfeefntpf] C:\Users\RNS\AppData\Local\Temp\iexplarer.exe
O4 - HKCU\..\Run: [LvTfeefneP] C:\Users\RNS\AppData\Local\Temp\avp32.exe
O4 - HKCU\..\Run: [LvTfeefnwg] C:\Users\RNS\AppData\Local\Temp\spoolsv.exe
O4 - HKCU\..\Run: [LvTfeefnZg] C:\Users\RNS\AppData\Local\Temp\al9ax.exe
O4 - HKCU\..\Run: [LvTfeefnz9] C:\Users\RNS\AppData\Local\Temp\nvsvc32.exe
O4 - HKCU\..\Run: [LvTfeefnxb] C:\Users\RNS\AppData\Local\Temp\sysedit.exe
O4 - HKCU\..\Run: [LvTfeefnqe] C:\Users\RNS\AppData\Local\Temp\login.exe
O4 - HKCU\..\Run: [LvTfeefnoc] C:\Users\RNS\AppData\Local\Temp\debug.exe
O4 - HKCU\..\Run: [LvTfeefnsb] C:\Users\RNS\AppData\Local\Temp\drweb.exe
O4 - HKCU\..\Run: [LvTfeefnsd] C:\Users\RNS\AppData\Local\Temp\taskmgr.exe
O4 - HKCU\..\Run: [LvTfeefnvZ] C:\Users\RNS\AppData\Local\Temp\install.exe
O4 - HKCU\..\Run: [LvTfeefnwe] C:\Users\RNS\AppData\Local\Temp\setup.exe
O4 - HKCU\..\Run: [LvTfeefngP] C:\Users\RNS\AppData\Local\Temp\win32.exe
O4 - HKCU\..\Run: [SpybotSD TeaTimer] C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
O4 - HKCU\..\Run: [SUPERAntiSpyware] C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe
O4 - HKUS\S-1-5-19\..\Run: [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun (User 'LOCAL SERVICE')
O4 - HKUS\S-1-5-19\..\RunOnce: [mctadmin] C:\Windows\System32\mctadmin.exe (User 'LOCAL SERVICE')
O4 - HKUS\S-1-5-20\..\Run: [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /autoRun (User 'NETWORK SERVICE')
O4 - HKUS\S-1-5-20\..\RunOnce: [mctadmin] C:\Windows\System32\mctadmin.exe (User 'NETWORK SERVICE')
O4 - Startup: MagicDisc.lnk = C:\Program Files\MagicDisc\MagicDisc.exe
O8 - Extra context menu item: Append Link Target to Existing PDF - res://C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIEAppendSelLinks.html
O8 - Extra context menu item: Append to Existing PDF - res://C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: Convert Link Target to Adobe PDF - res://C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIECaptureSelLinks.html
O8 - Extra context menu item: Convert to Adobe PDF - res://C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIECapture.html
O9 - Extra button: (no name) - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O9 - Extra 'Tools' menuitem: Spybot - Search & Destroy Configuration - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O10 - Unknown file in Winsock LSP: c:\program files\common files\microsoft shared\windows live\wlidnsp.dll
O12 - Plugin for .mdz: C:\Program Files\Internet Explorer\Plugins\npmod32.dll
O20 - AppInit_DLLs: C:\PROGRA~1\Google\GOOGLE~1\GO36F4~1.DLL
O23 - Service: Adobe Version Cue CS4 - Adobe Systems Incorporated - C:\Program Files\Common Files\Adobe\Adobe Version Cue CS4\Server\bin\VersionCueCS4.exe
O23 - Service: AMD External Events Utility - AMD - C:\Windows\system32\atiesrxx.exe
O23 - Service: Apple Mobile Device - Apple Inc. - C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
O23 - Service: Bonjour Service - Apple Inc. - C:\Program Files\Bonjour\mDNSResponder.exe
O23 - Service: FLEXnet Licensing Service - Acresso Software Inc. - C:\Program Files\Common Files\Macrovision Shared\FLEXnet Publisher\FNPLicensingService.exe
O23 - Service: Google Desktop Manager 5.9.1005.12335 (GoogleDesktopManager-051210-111108) - Google - C:\Program Files\Google\Google Desktop Search\GoogleDesktop.exe
O23 - Service: iPod Service - Apple Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: LightScribeService Direct Disc Labeling Service (LightScribeService) - Hewlett-Packard Company - C:\Program Files\Common Files\LightScribe\LSSrvc.exe
O23 - Service: Nero BackItUp Scheduler 4.0 - Nero AG - C:\Program Files\Common Files\Nero\Nero BackItUp 4\NBService.exe
O23 - Service: SBSD Security Center Service (SBSDWSCService) - Safer Networking Ltd. - C:\Program Files\Spybot - Search & Destroy\SDWinSec.exe
O23 - Service: Sentinel Protection Server (SentinelProtectionServer) - SafeNet, Inc - C:\Program Files\Common Files\SafeNet Sentinel\Sentinel Protection Server\WinNT\spnsrvnt.exe
O23 - Service: TabletServiceWacom - Wacom Technology, Corp. - C:\Program Files\Tablet\Wacom\Wacom_Tablet.exe

–
End of file - 10833 bytes

Hi Nightsight,

Welcome to WhattheTech. My name is Blottedisk and I will be helping you with your malware issues. Before we delve into this, please take a look at the following notes:

  • Please subscribe to this topic, if you haven't already. You can subscribe by clicking the Watch Topic button to the right of your topic title and then choosing the notification method ( Recommended: Inmediate Notification)
  • Please avoid installing/uninstalling or updating any programs and attempting any unsupervised fixes or scans. This can make helping you impossible.
  • The forum is busy and we need to have replies as soon as possible. If I haven't had a reply after 3 days I will bump the topic and if you do not reply by the following day after that then the thread will be locked due to inactivity. However, if you will be away, let us know and we will be sure to keep the thread open.
——————————————————-

Ok, let's get started. Please follow the steps below in order:


Step 1 | Download DDS from any of the links below:

Link 1
Link 2
Link 2

——————————————————————–
  • Save it to your desktop.
  • Please disable any anti-malware program that will block scripts from running before running DDS.
  • Double-Click on dds and a command window will appear. This is normal.
  • Shortly after two logs will appear:
    • DDS.txt
    • Attach.txt
  • A window will open instructing you save & post the logs.
  • Save the logs to a convenient place such as your desktop.
  • Post the contents of the DDS.txt report in your next reply.
  • Attach the Attach.txt report to your post by scroling down to the Attachments area and then clicking Browse. Browse to where you saved the file, and click Open and then click UPLOAD.


Step 2 | Please download GMER from one of the following locations and save it to your desktop:

Main Mirror - This version will download a randomly named file (Recommended)
Zipped Mirror - This version will download a zip file you will need to extract first. If you use this mirror, please extract the zip file to your desktop.

——————————————————————–

  • Disconnect from the Internet and close all running programs.
  • Temporarily disable any real-time active protection so your security programs will not conflict with gmer's driver.
  • Right-click on the randomly named GMER file (i.e. n7gmo46c.exe) and choose "Run as administrator" to run it. Allow the gmer.sys driver to load if asked.

Note: If you downloaded the zipped version, extract the file to its own folder such as C:\gmer and then right-click on gmer.exe and choose "Run as administrator".

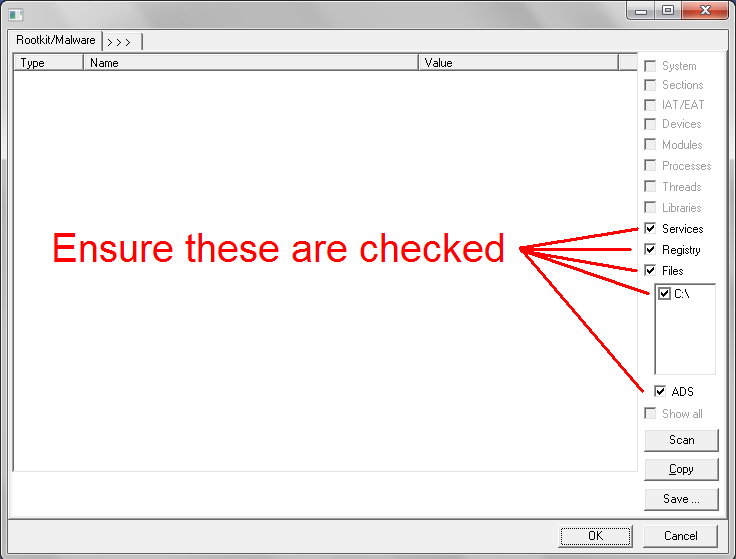
[external image: Posted Image]

  • GMER will open to the Rootkit/Malware tab and perform an automatic quick scan when first run. (do not use the computer while the scan is in progress)
  • If you receive a WARNING!!! about rootkit activity and are asked to fully scan your system…click NO.
  • Make sure these options are all checked:
  • Services
  • Registry
  • Files
  • Systemdrive drive/partition, which is typically C:\
  • ADS

[external image: Posted Image]
Click the image to enlarge it

  • Now click the Scan button. If you see a rootkit warning window, click OK.
  • When the scan is finished, click the Save… button to save the scan results to your Desktop. Save the file as gmer.log.
  • Click the Copy button and paste the results into your next reply.
  • Exit GMER and re-enable all active protection when done.
– If you encounter any problems, try running GMER in Safe Mode.


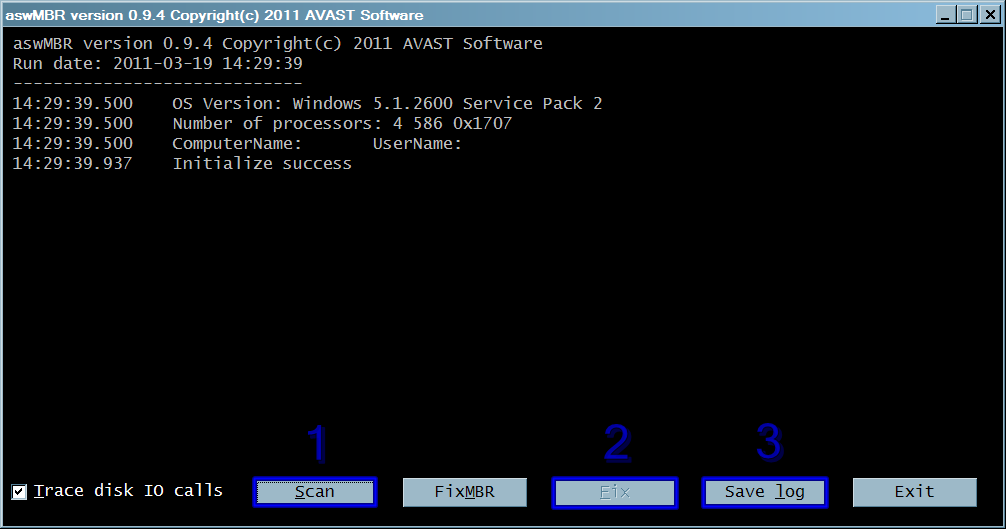
Step 3 | Please download aswMBR to your desktop.

  • Double click the aswMBR icon to run it.
    Vista and Windows 7 users right click the icon and choose "Run as administrator".
  • Click the Scan button to start scan.
  • When it finishes, press the save log button, save the logfile to your desktop and post its contents in your next reply.

[external image: Posted Image]
Click the image to enlarge it
aswMBR version 0.9.4 Copyright© 2011 AVAST Software Run date: 2011-04-11 14:18:42 —————————– 14:18:42.632 OS Version: Windows 6.1.7600 14:18:42.632 Number of processors: 8 586 0x1A05 14:18:42.632 ComputerName: RNS-PC UserName: RNS 14:18:44.125 Initialize success 14:18:56.625 Disk 0 \Device\Harddisk0\DR0 -> \Device\Ide\IdeDeviceP0T0L0-0 14:18:56.627 Disk 0 Vendor: ST31000528AS 0953 Size: 953869MB BusType: 3 14:18:56.630 Disk 1 (boot) \Device\Harddisk1\DR1 -> \Device\Ide\IdePort2 14:18:56.632 Disk 1 Vendor: ST31000528AS CC38 Size: 953869MB BusType: 3 14:18:56.635 Device \Device\Ide\IdeDeviceP2T0L0-3 -> \??\IDE#DiskST31000528AS____________________________CC38____#5&3007a5e1&0&0.0.0#{53f56307-b6bf-11d0-94f2-00a0c91efb8b} not found 14:18:58.639 Disk 1 MBR read successfully 14:18:58.643 Disk 1 MBR scan 14:18:58.647 Disk 1 TDL4@MBR code has been found 14:18:58.651 Disk 1 MBR hidden 14:18:58.655 Disk 1 MBR [TDL4] **ROOTKIT** 14:18:58.660 Disk 1 trace - called modules: 14:18:58.665 ntoskrnl.exe CLASSPNP.SYS disk.sys ACPI.sys halmacpi.dll >>UNKNOWN [0x869a7439]<< 14:18:58.670 1 nt!IofCallDriver -> \Device\Harddisk1\DR1[0x8697f8e8] 14:18:58.676 3 CLASSPNP.SYS[8c67d59e] -> nt!IofCallDriver -> [0x867d6918] 14:18:58.682 5 ACPI.sys[83a3b3b2] -> nt!IofCallDriver -> \IdeDeviceP2T0L0-3[0x867ff030] 14:18:58.688 \Driver\atapi[0x86980510] -> IRP_MJ_CREATE -> 0x869a7439 14:18:58.695 Scan finished successfully
DDS does not support my operating system… so I did the GMER thing first…

GMER 1.0.15.15570 - http://www.gmer.net
Rootkit scan 2011-04-11 14:15:08
Windows 6.1.7600 Harddisk1\DR1 -> \Device\Ide\IdePort2 ST31000528AS rev.CC38
Running: ddli4gnc.exe; Driver: C:\Users\RNS\AppData\Local\Temp\uwldrpow.sys


—- Disk sectors - GMER 1.0.15 —-

Disk \Device\Harddisk1\DR1 TDL4@MBR code has been found <– ROOTKIT !!!
Disk \Device\Harddisk1\DR1 sector 00: rootkit-like behavior

—- EOF - GMER 1.0.15 —-

(I posted this earlier but I guess the internet was down and didn't go trough)
Hi Nightsight, thanks for the logs.


Unfortunately your machine appears to have been infected by the TDSS rootkit/backdoor infection. These kind of malware is very dangerous. Backdoor Trojans provide a means of accessing a computer system that bypasses security mechanisms and steal sensitive information like passwords, personal and financial data which they send back to the hacker. Rootkits can hook into the Windows 32-bit kernel, and patch several APIs to hide new registry keys and files they install. Remote attackers use backdoor Trojans and rootkits as part of an exploit to to gain unauthorized access to a computer and take control of it without your knowledge.


If you use your computer for sensitive purposes such as internet banking then I recommend you take the following steps immediately:

  • Use another, uninfected computer to change all your internet passwords, especially ones with financial implications such as banks,
    paypal, ebay, etc. You should also change the passwords for any other site you use.
  • Call your bank(s), credit card company or any other institution which may be affected and advise them that your login/password or
    credit card information may have been stolen and ask what steps to take with regard to your account.
  • Consider what other private information could possibly have been taken from your computer and take appropriate steps

Please read the following for more information:

How Do I Handle Possible Identify Theft, Internet Fraud and CC Fraud?
What Should I Do If I've Become A Victim Of Identity Theft?
Identity Theft Victims Guide - What to do


Although the TDSS infection can be identified and removed, your PC has likely been compromised and there is no way to be sure the computer can ever be trusted again. It is dangerous and incorrect to assume that if this type of malware has been removed the computer is now secure. In some instances an infection may have caused so much damage to your system that it cannot be completely cleaned or repaired. The malware may leave so many remnants behind that security tools cannot find them. Many experts in the security community believe that once infected with this type of malware, the best course of action is to wipe the drive clean, reformat and reinstall the OS. Please read:

When should I re-format? How should I reinstall?
Where to draw the line? When to recommend a format and reinstall?

Note: Attempting to reinstall Windows (repair install) without first wiping the entire hard drive with a repartition/reformat will not remove the infection. The reinstall will only overwrite the Windows files. Any malware on the system causing problems will still be there afterwards and a Repair will NOT help.


Should you have any questions, please feel free to ask. Please let me know what you have decided to do in your next post. If you decide you want to try and clean your PC then please continue with the following instructions:


Please download OTL from one of the following mirrors:

This is THE Mirror

——————————————————————–

  • Save it to your desktop
  • Double click on the icon to run it. Make sure all other windows are closed and to let it run uninterrupted.
  • Click on Minimal Output at the top
  • Download the following file scan.txt to your Desktop. Click here to download it.
  • Double click inside the Custom Scan box at the bottom.
  • A window will appear saying "Click OK to load a custom scan from a file or Cancel to cancel".
  • Click the OK button and navigate to the file scan.txt which we just saved to your desktop.
  • Select scan.txt and click Open. Writing will now appear under the Custom Scan box.
  • Click the Run Scan button. Do not change any settings unless otherwise told to do so. The scan won't take long.
  • When the scan completes, it will open two notepad windows. OTL.Txt and Extras.Txt. These are saved in the same location as OTL.
  • Please copy (Edit->Select All, Edit->Copy) the contents of these files, one at a time and post them in this topic.
  • You may need two posts to fit them both in.
OTL logfile created on: 4/13/2011 1:24:13 PM - Run 1
OTL by OldTimer - Version 3.2.22.3 Folder = C:\Users\RNS\Desktop
Ultimate Edition (Version = 6.1.7600) - Type = NTWorkstation
Internet Explorer (Version = 8.0.7600.16385)
Locale: 00000409 | Country: United States | Language: ENU | Date Format: M/d/yyyy

3.00 Gb Total Physical Memory | 2.00 Gb Available Physical Memory | 53.00% Memory free
6.00 Gb Paging File | 4.00 Gb Available in Paging File | 73.00% Paging File free
Paging file location(s): ?:\pagefile.sys [binary data]

%SystemDrive% = C: | %SystemRoot% = C:\Windows | %ProgramFiles% = C:\Program Files
Drive C: | 195.31 Gb Total Space | 129.71 Gb Free Space | 66.41% Space Free | Partition Type: NTFS
Drive D: | 736.10 Gb Total Space | 351.60 Gb Free Space | 47.77% Space Free | Partition Type: NTFS
Drive E: | 4.03 Gb Total Space | 0.00 Gb Free Space | 0.00% Space Free | Partition Type: UDF
Drive F: | 931.51 Gb Total Space | 840.03 Gb Free Space | 90.18% Space Free | Partition Type: NTFS

Computer Name: RNS-PC | User Name: RNS | Logged in as Administrator.
Boot Mode: Normal | Scan Mode: Current user
Company Name Whitelist: Off | Skip Microsoft Files: Off | No Company Name Whitelist: On | File Age = 30 Days

========== Processes (SafeList) ==========

PRC - C:\Users\RNS\Desktop\OTL.exe (OldTimer Tools)
PRC - C:\Program Files\Mozilla Firefox\firefox.exe (Mozilla Corporation)
PRC - C:\Program Files\Microsoft Security Client\msseces.exe (Microsoft Corporation)
PRC - C:\Program Files\Tablet\Wacom\Wacom_TabletUser.exe (Wacom Technology, Corp.)
PRC - C:\Program Files\Tablet\Wacom\Wacom_Tablet.exe (Wacom Technology, Corp.)
PRC - C:\Program Files\Microsoft Security Client\Antimalware\MsMpEng.exe (Microsoft Corporation)
PRC - C:\Windows\System32\atieclxx.exe (AMD)
PRC - C:\Windows\System32\atiesrxx.exe (AMD)
PRC - C:\Program Files\Sony Ericsson\Sony Ericsson PC Companion\PCCompanion.exe (Sony Ericsson Mobile Communications AB)
PRC - C:\Program Files\Common Files\Nero\Nero BackItUp 4\NBService.exe (Nero AG)
PRC - C:\Windows\System32\MAFWTray.exe (Avid Technology, Inc.)
PRC - C:\Windows\System32\taskhost.exe (Microsoft Corporation)
PRC - C:\Windows\explorer.exe (Microsoft Corporation)
PRC - C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe (Safer-Networking Ltd.)
PRC - C:\Program Files\Spybot - Search & Destroy\SDWinSec.exe (Safer Networking Ltd.)
PRC - C:\Program Files\Adobe\Acrobat 9.0\Acrobat\acrotray.exe (Adobe Systems Inc.)
PRC - C:\Program Files\Common Files\SafeNet Sentinel\Sentinel Protection Server\WinNT\spnsrvnt.exe (SafeNet, Inc)


========== Modules (SafeList) ==========

MOD - C:\Users\RNS\Desktop\OTL.exe (OldTimer Tools)
MOD - C:\Windows\winsxs\x86_microsoft.windows.common-controls_6595b64144ccf1df_6.0.7600.16385_none_421189da2b7fabfc\comctl32.dll (Microsoft Corporation)
MOD - C:\Windows\winsxs\x86_microsoft.windows.gdiplus_6595b64144ccf1df_1.1.7600.16385_none_72fc7cbf
861225ca\GdiPlus.dll (Microsoft Corporation)


========== Win32 Services (SafeList) ==========

SRV - (FLEXnet Licensing Service) – C:\Program Files\Common Files\Macrovision Shared\FLEXnet Publisher\FNPLicensingService.exe (Acresso Software Inc.)
SRV - (TabletServiceWacom) – C:\Program Files\Tablet\Wacom\Wacom_Tablet.exe (Wacom Technology, Corp.)
SRV - (NisSrv) – C:\Program Files\Microsoft Security Client\Antimalware\NisSrv.exe (Microsoft Corporation)
SRV - (MsMpSvc) – C:\Program Files\Microsoft Security Client\Antimalware\MsMpEng.exe (Microsoft Corporation)
SRV - (AMD External Events Utility) – C:\Windows\System32\atiesrxx.exe (AMD)
SRV - (Nero BackItUp Scheduler 4.0) – C:\Program Files\Common Files\Nero\Nero BackItUp 4\NBService.exe (Nero AG)
SRV - (SensrSvc) – C:\Windows\System32\sensrsvc.dll (Microsoft Corporation)
SRV - (PeerDistSvc) – C:\Windows\System32\PeerDistSvc.dll (Microsoft Corporation)
SRV - (WinDefend) – C:\Program Files\Windows Defender\MpSvc.dll (Microsoft Corporation)
SRV - (SBSDWSCService) – C:\Program Files\Spybot - Search & Destroy\SDWinSec.exe (Safer Networking Ltd.)
SRV - (Adobe Version Cue CS4) – C:\Program Files\Common Files\Adobe\Adobe Version Cue CS4\Server\bin\VersionCueCS4.exe (Adobe Systems Incorporated)
SRV - (SentinelProtectionServer) – C:\Program Files\Common Files\SafeNet Sentinel\Sentinel Protection Server\WinNT\spnsrvnt.exe (SafeNet, Inc)


========== Driver Services (SafeList) ==========

DRV - (MpKsl65a14d5b) – C:\ProgramData\Microsoft\Microsoft Antimalware\Definition Updates\{D8A06A33-9790-4766-A50D-092731E1E543}\MpKsl65a14d5b.sys (Microsoft Corporation)
DRV - (wacmoumonitor) – C:\Windows\System32\drivers\wacmoumonitor.sys (Wacom Technology)
DRV - (amdkmdag) – C:\Windows\System32\drivers\atikmdag.sys (ATI Technologies Inc.)
DRV - (amdkmdap) – C:\Windows\System32\drivers\atikmpag.sys (Advanced Micro Devices, Inc.)
DRV - (wacommousefilter) – C:\Windows\System32\drivers\wacommousefilter.sys (Wacom Technology)
DRV - (wacomvhid) – C:\Windows\System32\drivers\wacomvhid.sys (Wacom Technology)
DRV - (NisDrv) – C:\Windows\System32\drivers\NisDrvWFP.sys (Microsoft Corporation)
DRV - (MpNWMon) – C:\Windows\System32\drivers\MpNWMon.sys (Microsoft Corporation)
DRV - (AtiHDAudioService) – C:\Windows\System32\drivers\AtihdW73.sys (ATI Technologies, Inc.)
DRV - (SASKUTIL) – C:\Program Files\SUPERAntiSpyware\SASKUTIL.SYS (SUPERAdBlocker.com and SUPERAntiSpyware.com)
DRV - (SASDIFSV) – C:\Program Files\SUPERAntiSpyware\sasdifsv.sys (SUPERAdBlocker.com and SUPERAntiSpyware.com)
DRV - (TPkd) – C:\Windows\System32\drivers\TPkd.sys (PACE Anti-Piracy, Inc.)
DRV - (MAFW) – C:\Windows\System32\drivers\mafw.sys (Avid Technology, Inc.)
DRV - (vmbus) – C:\Windows\system32\DRIVERS\vmbus.sys (Microsoft Corporation)
DRV - (storflt) – C:\Windows\system32\DRIVERS\vmstorfl.sys (Microsoft Corporation)
DRV - (storvsc) – C:\Windows\system32\DRIVERS\storvsc.sys (Microsoft Corporation)
DRV - (WinUsb) – C:\Windows\System32\drivers\winusb.sys (Microsoft Corporation)
DRV - (s3cap) – C:\Windows\system32\DRIVERS\vms3cap.sys (Microsoft Corporation)
DRV - (VMBusHID) – C:\Windows\system32\DRIVERS\VMBusHID.sys (Microsoft Corporation)
DRV - (athr) – C:\Windows\System32\drivers\athr.sys (Atheros Communications, Inc.)
DRV - (s1018mdm) – C:\Windows\System32\drivers\s1018mdm.sys (MCCI Corporation)
DRV - (s1018unic) Sony Ericsson Device 1018 USB Ethernet Emulation (WDM) – C:\Windows\System32\drivers\s1018unic.sys (MCCI Corporation)
DRV - (s1018mgmt) Sony Ericsson Device 1018 USB WMC Device Management Drivers (WDM) – C:\Windows\System32\drivers\s1018mgmt.sys (MCCI Corporation)
DRV - (s1018obex) – C:\Windows\System32\drivers\s1018obex.sys (MCCI Corporation)
DRV - (s1018bus) Sony Ericsson Device 1018 driver (WDM) – C:\Windows\System32\drivers\s1018bus.sys (MCCI Corporation)
DRV - (s1018nd5) Sony Ericsson Device 1018 USB Ethernet Emulation (NDIS) – C:\Windows\System32\drivers\s1018nd5.sys (MCCI Corporation)
DRV - (s1018mdfl) – C:\Windows\System32\drivers\s1018mdfl.sys (MCCI Corporation)
DRV - (mcdbus) – C:\Windows\System32\drivers\mcdbus.sys (MagicISO, Inc.)
DRV - (Sentinel) – C:\Windows\System32\Drivers\SENTINEL.SYS (SafeNet, Inc.)
DRV - (CLEDX) – C:\Windows\System32\drivers\cledx.sys (Team H2O)
DRV - (A3AB) D-Link AirPro 802.11a/b Wireless Adapter Service(A3AB) – C:\Windows\System32\drivers\A3AB.sys (D-Link Corporation)


========== Standard Registry (SafeList) ==========


========== Internet Explorer ==========


IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Search Page = http://www.google.com
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://www.musicradar.com/computermusic
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page Redirect Cache = http://www.msn.com/
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page Redirect Cache AcceptLangs = en-us
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page Redirect Cache_TIMESTAMP = FB 35 38 85 AC 95 CB 01 [binary data]
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page Restore = http://g.live.com/1rewlive4startup/home
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyEnable" = 0
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyOverride" = *.local

========== FireFox ==========

FF - prefs.js..browser.startup.homepage: "http://www.musicradar.com/computermusic"

FF - HKLM\software\mozilla\Mozilla Firefox 3.6.16\extensions\\Components: C:\Program Files\Mozilla Firefox\components [2011/04/05 20:05:17 | 000,000,000 | —D | M]
FF - HKLM\software\mozilla\Mozilla Firefox 3.6.16\extensions\\Plugins: C:\Program Files\Mozilla Firefox\plugins
FF - HKLM\software\mozilla\Mozilla Firefox 4.0\extensions\\Components: C:\Program Files\Mozilla Firefox\components [2011/04/05 20:05:17 | 000,000,000 | —D | M]
FF - HKLM\software\mozilla\Mozilla Firefox 4.0\extensions\\Plugins: C:\Program Files\Mozilla Firefox\plugins

[2011/04/05 20:06:11 | 000,000,000 | —D | M] (No name found) – C:\Users\RNS\AppData\Roaming\Mozilla\Extensions
[2011/04/05 20:05:16 | 000,000,000 | —D | M] (No name found) – C:\Program Files\Mozilla Firefox\extensions
File not found (No name found) –
[2011/03/18 10:53:24 | 000,142,296 | —- | M] (Mozilla Foundation) – C:\Program Files\Mozilla Firefox\components\browsercomps.dll
[2010/01/01 01:00:00 | 000,002,252 | —- | M] () – C:\Program Files\Mozilla Firefox\searchplugins\bing.xml

Hosts file not found
O2 - BHO: (Spybot-S&D; IE Protection) - {53707962-6F74-2D53-2644-206D7942484F} - C:\Program Files\Spybot - Search & Destroy\SDHelper.dll (Safer Networking Limited)
O2 - BHO: (C:\Windows\system32\ma95o12g.dll) - {B1B220C1-A500-99BD-F110-04B53A2C8952} - File not found
O3 - HKLM\..\Toolbar: (Adobe PDF) - {47833539-D0C5-4125-9FA8-0819E2EAAC93} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll (Adobe Systems Incorporated)
O3 - HKLM\..\Toolbar: (Contribute Toolbar) - {517BDDE4-E3A7-4570-B21E-2B52B6139FC7} - C:\Program Files\Adobe\/Adobe Contribute CS4/contributeieplugin.dll ()
O3 - HKLM\..\Toolbar: (no name) - {9D425283-D487-4337-BAB6-AB8354A81457} - No CLSID value found.
O3 - HKCU\..\Toolbar\WebBrowser: (Adobe PDF) - {47833539-D0C5-4125-9FA8-0819E2EAAC93} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll (Adobe Systems Incorporated)
O4 - HKLM..\Run: [] File not found
O4 - HKLM..\Run: [Acrobat Assistant 8.0] C:\Program Files\Adobe\Acrobat 9.0\Acrobat\Acrotray.exe (Adobe Systems Inc.)
O4 - HKLM..\Run: [Adobe Acrobat Speed Launcher] C:\Program Files\Adobe\Acrobat 9.0\Acrobat\Acrobat_sl.exe (Adobe Systems Incorporated)
O4 - HKLM..\Run: [Adobe_ID0ENQBO] C:\Program Files\Common Files\Adobe\Adobe Version Cue CS4\Server\bin\VersionCueCS4Tray.exe (Adobe Systems Incorporated)
O4 - HKLM..\Run: [AdobeCS4ServiceManager] C:\Program Files\Common Files\Adobe\CS4ServiceManager\CS4ServiceManager.exe (Adobe Systems Incorporated)
O4 - HKLM..\Run: [H2O] File not found
O4 - HKLM..\Run: [LvTfeefnb] File not found
O4 - HKLM..\Run: [LvTfeefneP] File not found
O4 - HKLM..\Run: [LvTfeefngP] File not found
O4 - HKLM..\Run: [LvTfeefnoc] File not found
O4 - HKLM..\Run: [LvTfeefnqe] File not found
O4 - HKLM..\Run: [LvTfeefnqg] File not found
O4 - HKLM..\Run: [LvTfeefnrc] File not found
O4 - HKLM..\Run: [LvTfeefnsb] File not found
O4 - HKLM..\Run: [LvTfeefnsd] File not found
O4 - HKLM..\Run: [LvTfeefntpf] File not found
O4 - HKLM..\Run: [LvTfeefnvZ] File not found
O4 - HKLM..\Run: [LvTfeefnwe] File not found
O4 - HKLM..\Run: [LvTfeefnwg] File not found
O4 - HKLM..\Run: [LvTfeefnwpc] File not found
O4 - HKLM..\Run: [LvTfeefnxb] File not found
O4 - HKLM..\Run: [LvTfeefnY] File not found
O4 - HKLM..\Run: [LvTfeefnz9] File not found
O4 - HKLM..\Run: [LvTfeefnZg] File not found
O4 - HKLM..\Run: [LvTfeefnZP] File not found
O4 - HKLM..\Run: [M-Audio Taskbar Icon] C:\Windows\System32\MAFWTray.exe (Avid Technology, Inc.)
O4 - HKLM..\Run: [MSC] C:\Program Files\Microsoft Security Client\msseces.exe (Microsoft Corporation)
O4 - HKLM..\Run: [StartCCC] C:\Program Files\ATI Technologies\ATI.ACE\Core-Static\CLIStart.exe (Advanced Micro Devices, Inc.)
O4 - HKCU..\Run: [4E3E0230868C0F5D] File not found
O4 - HKCU..\Run: [LvTfeefnb] File not found
O4 - HKCU..\Run: [LvTfeefneP] File not found
O4 - HKCU..\Run: [LvTfeefngP] File not found
O4 - HKCU..\Run: [LvTfeefnoc] File not found
O4 - HKCU..\Run: [LvTfeefnqe] File not found
O4 - HKCU..\Run: [LvTfeefnqg] File not found
O4 - HKCU..\Run: [LvTfeefnrc] File not found
O4 - HKCU..\Run: [LvTfeefnsb] File not found
O4 - HKCU..\Run: [LvTfeefnsd] File not found
O4 - HKCU..\Run: [LvTfeefntpf] File not found
O4 - HKCU..\Run: [LvTfeefnvZ] File not found
O4 - HKCU..\Run: [LvTfeefnwe] File not found
O4 - HKCU..\Run: [LvTfeefnwg] File not found
O4 - HKCU..\Run: [LvTfeefnwpc] File not found
O4 - HKCU..\Run: [LvTfeefnxb] File not found
O4 - HKCU..\Run: [LvTfeefnY] File not found
O4 - HKCU..\Run: [LvTfeefnz9] File not found
O4 - HKCU..\Run: [LvTfeefnZg] File not found
O4 - HKCU..\Run: [LvTfeefnZP] File not found
O4 - HKCU..\Run: [Sony Ericsson PC Companion] C:\Program Files\Sony Ericsson\Sony Ericsson PC Companion\PCCompanion.exe (Sony Ericsson Mobile Communications AB)
O4 - HKCU..\Run: [SpybotSD TeaTimer] C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe (Safer-Networking Ltd.)
O4 - Startup: C:\Users\RNS\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\MagicDisc.lnk = C:\Program Files\MagicDisc\MagicDisc.exe (MagicISO, Inc.)
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: ConsentPromptBehaviorAdmin = 0
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: ConsentPromptBehaviorUser = 3
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: EnableLUA = 0
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: PromptOnSecureDesktop = 0
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDriveTypeAutoRun = 145
O8 - Extra context menu item: Append Link Target to Existing PDF - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll (Adobe Systems Incorporated)
O8 - Extra context menu item: Append to Existing PDF - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll (Adobe Systems Incorporated)
O8 - Extra context menu item: Convert Link Target to Adobe PDF - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll (Adobe Systems Incorporated)
O8 - Extra context menu item: Convert to Adobe PDF - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll (Adobe Systems Incorporated)
O9 - Extra 'Tools' menuitem : Spybot - Search & Destroy Configuration - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - C:\Program Files\Spybot - Search & Destroy\SDHelper.dll (Safer Networking Limited)
O10 - NameSpace_Catalog5\Catalog_Entries\000000000009 [] - C:\Program Files\Bonjour\mdnsNSP.dll (Apple Inc.)
O12 - Plugin for: .mdz - C:\Program Files\Internet Explorer\Plugins\npmod32.dll (Olivier Lapicque)
O13 - gopher Prefix: missing
O15 - HKCU\..Trusted Domains: localhost ([]http in Local intranet)
O15 - HKCU\..Trusted Ranges: GD ([http] in Local intranet)
O16 - DPF: {CAFEEFAC-0016-0000-0023-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_23)
O16 - DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_23)
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: DhcpNameServer = [removed] [removed] [removed]
O20 - AppInit_DLLs: (C:\PROGRA~1\Google\GOOGLE~1\GO36F4~1.DLL) - C:\Program Files\Google\Google Desktop Search\GoogleDesktopNetwork3.dll (Google)
O20 - HKLM Winlogon: Shell - (explorer.exe) - C:\Windows\explorer.exe (Microsoft Corporation)
O20 - HKLM Winlogon: VMApplet - (SystemPropertiesPerformance.exe) - C:\Windows\System32\SystemPropertiesPerformance.exe (Microsoft Corporation)
O20 - HKLM Winlogon: VMApplet - (/pagefile) - File not found
O21 - SSODL: WebCheck - {E6FB5E20-DE35-11CF-9C87-00AA005127ED} - CLSID or File not found.
O32 - HKLM CDRom: AutoRun - 1
O32 - AutoRun File - [2009/06/10 14:42:20 | 000,000,024 | —- | M] () - C:\autoexec.bat – [ NTFS ]
O33 - MountPoints2\{86fdb943-4e74-11e0-b23c-0024213116bd}\Shell - "" = AutoRun
O33 - MountPoints2\{86fdb943-4e74-11e0-b23c-0024213116bd}\Shell\AutoRun\command - "" = I:\Startme.exe
O34 - HKLM BootExecute: (autocheck autochk *) - File not found
O35 - HKLM\..comfile [open] – "%1" %*
O35 - HKLM\..exefile [open] – "%1" %*
O37 - HKLM\…com [@ = comfile] – "%1" %*
O37 - HKLM\…exe [@ = exefile] – "%1" %*

NetSvcs: FastUserSwitchingCompatibility - File not found
NetSvcs: Ias - File not found
NetSvcs: Nla - File not found
NetSvcs: Ntmssvc - File not found
NetSvcs: NWCWorkstation - File not found
NetSvcs: Nwsapagent - File not found
NetSvcs: SRService - File not found
NetSvcs: WmdmPmSp - File not found
NetSvcs: LogonHours - File not found
NetSvcs: PCAudit - File not found
NetSvcs: helpsvc - File not found
NetSvcs: uploadmgr - File not found

Drivers32: msacm.ac3acm - C:\Windows\System32\ac3acm.acm (fccHandler)
Drivers32: msacm.l3acm - C:\Windows\System32\l3codeca.acm (Fraunhofer Institut Integrierte Schaltungen IIS)
Drivers32: msacm.lameacm - C:\Windows\System32\lameACM.acm (http://www.mp3dev.org/)
Drivers32: vidc.3iv2 - C:\Windows\System32\3ivxVfWCodec.dll (3ivx.com)
Drivers32: vidc.cvid - C:\Windows\System32\iccvid.dll (Radius Inc.)
Drivers32: vidc.DIVX - C:\Windows\System32\divx.dll (DivXNetworks, Inc.)
Drivers32: VIDC.VP31 - C:\Windows\System32\vp31vfw.dll (On2.com)
Drivers32: VIDC.VP60 - C:\Windows\System32\vp6vfw.dll (On2.com)
Drivers32: VIDC.VP61 - C:\Windows\System32\vp6vfw.dll (On2.com)
Drivers32: VIDC.VP62 - C:\Windows\System32\vp6vfw.dll (On2.com)
Drivers32: VIDC.VP70 - C:\Windows\System32\vp7vfw.dll (On2.com)
Drivers32: VIDC.wmv3 - C:\Windows\System32\WMV9VCM.dll (Microsoft Corporation)
Drivers32: vidc.XVID - C:\Windows\System32\xvidvfw.dll ()


SafeBootMin: Base - Driver Group
SafeBootMin: Boot Bus Extender - Driver Group
SafeBootMin: Boot file system - Driver Group
SafeBootMin: File system - Driver Group
SafeBootMin: Filter - Driver Group
SafeBootMin: HelpSvc - Service
SafeBootMin: Lavasoft Ad-Aware Service - Reg Error: Value error.
SafeBootMin: MsMpSvc - C:\Program Files\Microsoft Security Client\Antimalware\MsMpEng.exe (Microsoft Corporation)
SafeBootMin: NTDS - File not found
SafeBootMin: PCI Configuration - Driver Group
SafeBootMin: PNP Filter - Driver Group
SafeBootMin: Primary disk - Driver Group
SafeBootMin: sacsvr - Service
SafeBootMin: SCSI Class - Driver Group
SafeBootMin: System Bus Extender - Driver Group
SafeBootMin: vmms - Service
SafeBootMin: WinDefend - C:\Program Files\Windows Defender\MpSvc.dll (Microsoft Corporation)
SafeBootMin: {36FC9E60-C465-11CF-8056-444553540000} - Universal Serial Bus controllers
SafeBootMin: {4D36E965-E325-11CE-BFC1-08002BE10318} - CD-ROM Drive
SafeBootMin: {4D36E967-E325-11CE-BFC1-08002BE10318} - DiskDrive
SafeBootMin: {4D36E969-E325-11CE-BFC1-08002BE10318} - Standard floppy disk controller
SafeBootMin: {4D36E96A-E325-11CE-BFC1-08002BE10318} - Hdc
SafeBootMin: {4D36E96B-E325-11CE-BFC1-08002BE10318} - Keyboard
SafeBootMin: {4D36E96F-E325-11CE-BFC1-08002BE10318} - Mouse
SafeBootMin: {4D36E977-E325-11CE-BFC1-08002BE10318} - PCMCIA Adapters
SafeBootMin: {4D36E97B-E325-11CE-BFC1-08002BE10318} - SCSIAdapter
SafeBootMin: {4D36E97D-E325-11CE-BFC1-08002BE10318} - System
SafeBootMin: {4D36E980-E325-11CE-BFC1-08002BE10318} - Floppy disk drive
SafeBootMin: {533C5B84-EC70-11D2-9505-00C04F79DEAF} - Volume shadow copy
SafeBootMin: {6BDD1FC1-810F-11D0-BEC7-08002BE2092F} - IEEE 1394 Bus host controllers
SafeBootMin: {71A27CDD-812A-11D0-BEC7-08002BE2092F} - Volume
SafeBootMin: {745A17A0-74D3-11D0-B6FE-00A0C90F57DA} - Human Interface Devices
SafeBootMin: {D48179BE-EC20-11D1-B6B8-00C04FA372A7} - SBP2 IEEE 1394 Devices
SafeBootMin: {D94EE5D8-D189-4994-83D2-F68D7D41B0E6} - SecurityDevices

SafeBootNet: Base - Driver Group
SafeBootNet: Boot Bus Extender - Driver Group
SafeBootNet: Boot file system - Driver Group
SafeBootNet: File system - Driver Group
SafeBootNet: Filter - Driver Group
SafeBootNet: HelpSvc - Service
SafeBootNet: Lavasoft Ad-Aware Service - Reg Error: Value error.
SafeBootNet: Messenger - Service
SafeBootNet: MsMpSvc - C:\Program Files\Microsoft Security Client\Antimalware\MsMpEng.exe (Microsoft Corporation)
SafeBootNet: NDIS Wrapper - Driver Group
SafeBootNet: NetBIOSGroup - Driver Group
SafeBootNet: NetDDEGroup - Driver Group
SafeBootNet: Network - Driver Group
SafeBootNet: NetworkProvider - Driver Group
SafeBootNet: NTDS - File not found
SafeBootNet: PCI Configuration - Driver Group
SafeBootNet: PNP Filter - Driver Group
SafeBootNet: PNP_TDI - Driver Group
SafeBootNet: Primary disk - Driver Group
SafeBootNet: rdsessmgr - Service
SafeBootNet: sacsvr - Service
SafeBootNet: SCSI Class - Driver Group
SafeBootNet: Streams Drivers - Driver Group
SafeBootNet: System Bus Extender - Driver Group
SafeBootNet: TDI - Driver Group
SafeBootNet: vmms - Service
SafeBootNet: WinDefend - C:\Program Files\Windows Defender\MpSvc.dll (Microsoft Corporation)
SafeBootNet: WudfUsbccidDriver - Driver
SafeBootNet: {36FC9E60-C465-11CF-8056-444553540000} - Universal Serial Bus controllers
SafeBootNet: {4D36E965-E325-11CE-BFC1-08002BE10318} - CD-ROM Drive
SafeBootNet: {4D36E967-E325-11CE-BFC1-08002BE10318} - DiskDrive
SafeBootNet: {4D36E969-E325-11CE-BFC1-08002BE10318} - Standard floppy disk controller
SafeBootNet: {4D36E96A-E325-11CE-BFC1-08002BE10318} - Hdc
SafeBootNet: {4D36E96B-E325-11CE-BFC1-08002BE10318} - Keyboard
SafeBootNet: {4D36E96F-E325-11CE-BFC1-08002BE10318} - Mouse
SafeBootNet: {4D36E972-E325-11CE-BFC1-08002BE10318} - Net
SafeBootNet: {4D36E973-E325-11CE-BFC1-08002BE10318} - NetClient
SafeBootNet: {4D36E974-E325-11CE-BFC1-08002BE10318} - NetService
SafeBootNet: {4D36E975-E325-11CE-BFC1-08002BE10318} - NetTrans
SafeBootNet: {4D36E977-E325-11CE-BFC1-08002BE10318} - PCMCIA Adapters
SafeBootNet: {4D36E97B-E325-11CE-BFC1-08002BE10318} - SCSIAdapter
SafeBootNet: {4D36E97D-E325-11CE-BFC1-08002BE10318} - System
SafeBootNet: {4D36E980-E325-11CE-BFC1-08002BE10318} - Floppy disk drive
SafeBootNet: {50DD5230-BA8A-11D1-BF5D-0000F805F530} - Smart card readers
SafeBootNet: {533C5B84-EC70-11D2-9505-00C04F79DEAF} - Volume shadow copy
SafeBootNet: {6BDD1FC1-810F-11D0-BEC7-08002BE2092F} - IEEE 1394 Bus host controllers
SafeBootNet: {71A27CDD-812A-11D0-BEC7-08002BE2092F} - Volume
SafeBootNet: {745A17A0-74D3-11D0-B6FE-00A0C90F57DA} - Human Interface Devices
SafeBootNet: {D48179BE-EC20-11D1-B6B8-00C04FA372A7} - SBP2 IEEE 1394 Devices
SafeBootNet: {D94EE5D8-D189-4994-83D2-F68D7D41B0E6} - SecurityDevices

ActiveX: {08B0E5C0-4FCB-11CF-AAA5-00401C608500} - Java (Sun)
ActiveX: {10880D85-AAD9-4558-ABDC-2AB1552D831F} - "C:\Program Files\Common Files\LightScribe\LSRunOnce.exe"
ActiveX: {22d6f312-b0f6-11d0-94ab-0080c74c7e95} - Microsoft Windows Media Player 12.0
ActiveX: {2C7339CF-2B09-4501-B3F3-F3508C9228ED} - %SystemRoot%\system32\regsvr32.exe /s /n /i:/UserInstall %SystemRoot%\system32\themeui.dll
ActiveX: {3af36230-a269-11d1-b5bf-0000f8051515} - Offline Browsing Pack
ActiveX: {44BBA840-CC51-11CF-AAFA-00AA00B6015C} - "%ProgramFiles%\Windows Mail\WinMail.exe" OCInstallUserConfigOE
ActiveX: {44BBA855-CC51-11CF-AAFA-00AA00B6015F} - DirectDrawEx
ActiveX: {45ea75a0-a269-11d1-b5bf-0000f8051515} - Internet Explorer Help
ActiveX: {4f645220-306d-11d2-995d-00c04f98bbc9} - Microsoft Windows Script 5.6
ActiveX: {5D146993-2BFB-160E-019F-3F7DA85D27A5} - Browser Customizations
ActiveX: {5fd399c0-a70a-11d1-9948-00c04f98bbc9} - Internet Explorer Setup Tools
ActiveX: {630b1da0-b465-11d1-9948-00c04f98bbc9} - Browsing Enhancements
ActiveX: {6BF52A52-394A-11d3-B153-00C04F79FAA6} - Microsoft Windows Media Player
ActiveX: {6fab99d0-bab8-11d1-994a-00c04f98bbc9} - MSN Site Access
ActiveX: {7790769C-0471-11d2-AF11-00C04FA35D02} - Address Book 7
ActiveX: {7C028AF8-F614-47B3-82DA-BA94E41B1089} - .NET Framework
ActiveX: {89820200-ECBD-11cf-8B85-00AA005B4340} - regsvr32.exe /s /n /i:U shell32.dll
ActiveX: {89820200-ECBD-11cf-8B85-00AA005B4383} - C:\Windows\System32\ie4uinit.exe -BaseSettings
ActiveX: {89B4C1CD-B018-4511-B0A1-5476DBF70820} - C:\Windows\system32\Rundll32.exe C:\Windows\system32\mscories.dll,Install
ActiveX: {9381D8F2-0288-11D0-9501-00AA00B911A5} - Dynamic HTML Data Binding
ActiveX: {B57AA43F-22D9-57E0-8CC7-5EB8746E169F} - Microsoft Windows Media Player 12.0
ActiveX: {BD5F616C-0EEE-0E3F-2B58-486EAD260C00} - Java (Sun)
ActiveX: {C9E9A340-D1F1-11D0-821E-444553540600} - Internet Explorer Core Fonts
ActiveX: {D1A7E693-3156-9457-8EB8-FE60490B06C9} - LightScribe Control Panel
ActiveX: {D27CDB6E-AE6D-11CF-96B8-444553540000} - Adobe Flash Player
ActiveX: {DD855E39-EB38-093D-836C-E57873535414} - Browser Customizations
ActiveX: {de5aed00-a4bf-11d1-9948-00c04f98bbc9} - HTML Help
ActiveX: {E92B03AB-B707-11d2-9CBD-0000F87A369E} - Active Directory Service Interface
ActiveX: >{22d6f312-b0f6-11d0-94ab-0080c74c7e95} - %SystemRoot%\system32\unregmp2.exe /ShowWMP
ActiveX: >{26923b43-4d38-484f-9b9e-de460746276c} - C:\Windows\System32\ie4uinit.exe -UserIconConfig
ActiveX: >{60B49E34-C7CC-11D0-8953-00A0C90347FF} - "C:\Windows\System32\rundll32.exe" "C:\Windows\System32\iedkcs32.dll",BrandIEActiveSetup SIGNUP

========== Files/Folders - Created Within 30 Days ==========

[2011/04/13 13:15:44 | 000,580,608 | —- | C] (OldTimer Tools) – C:\Users\RNS\Desktop\OTL.exe
[2011/04/11 14:17:44 | 000,566,272 | —- | C] (AVAST Software) – C:\Users\RNS\Desktop\aswMBR.exe
[2011/04/08 16:48:31 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{F889C204-4786-4501-991B-EE83912B6F7A}
[2011/04/08 16:36:00 | 000,388,608 | —- | C] (Trend Micro Inc.) – C:\Users\RNS\Desktop\HiJackThis.exe
[2011/04/08 12:38:33 | 000,000,000 | —D | C] – C:\Program Files\COMODO
[2011/04/08 12:36:13 | 000,000,000 | -HSD | C] – C:\Config.Msi
[2011/04/08 12:05:38 | 000,000,000 | R–D | C] – C:\Users\RNS\Desktop\MICRO
[2011/04/05 20:05:16 | 000,000,000 | —D | C] – C:\Program Files\Mozilla Firefox
[2011/04/05 00:18:54 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Roaming\SUPERAntiSpyware.com
[2011/04/05 00:18:54 | 000,000,000 | —D | C] – C:\ProgramData\SUPERAntiSpyware.com
[2011/04/05 00:14:12 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\SUPERAntiSpyware
[2011/04/05 00:14:10 | 000,000,000 | —D | C] – C:\Program Files\SUPERAntiSpyware
[2011/04/04 15:00:16 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{8883D476-BF69-4B53-827D-4FBC02AB6C04}
[2011/04/01 22:52:28 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Roaming\Malwarebytes
[2011/04/01 22:52:23 | 000,038,224 | —- | C] (Malwarebytes Corporation) – C:\Windows\System32\drivers\mbamswissarmy.sys
[2011/04/01 22:52:22 | 000,000,000 | —D | C] – C:\ProgramData\Malwarebytes
[2011/04/01 22:52:19 | 000,020,952 | —- | C] (Malwarebytes Corporation) – C:\Windows\System32\drivers\mbam.sys
[2011/04/01 22:52:19 | 000,000,000 | —D | C] – C:\Program Files\Malwarebytes' Anti-Malware
[2011/04/01 18:55:16 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Roaming\TrojanHunter
[2011/04/01 17:37:14 | 000,000,000 | —D | C] – C:\Program Files\TrojanHunter 5.3
[2011/04/01 16:32:12 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Spybot - Search & Destroy
[2011/04/01 16:32:01 | 000,000,000 | —D | C] – C:\ProgramData\Spybot - Search & Destroy
[2011/04/01 16:32:01 | 000,000,000 | —D | C] – C:\Program Files\Spybot - Search & Destroy
[2011/04/01 15:31:34 | 000,000,000 | —D | C] – C:\Program Files\Microsoft Security Client
[2011/04/01 15:31:28 | 000,240,008 | —- | C] (Microsoft Corporation) – C:\Windows\System32\drivers\netio.sys
[2011/04/01 15:00:01 | 000,098,392 | —- | C] (Sunbelt Software) – C:\Windows\System32\drivers\SBREDrv.sys
[2011/04/01 13:49:36 | 000,000,000 | —D | C] – C:\ProgramData\Lavasoft
[2011/04/01 13:10:18 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{8254B4F4-0814-4AA3-A2F4-4DFA97A2F9FD}
[2011/04/01 12:35:15 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{AE5D8B17-DA29-4E35-968B-7EA948EA2BAD}
[2011/04/01 12:34:32 | 000,000,000 | —D | C] – C:\ProgramData\MFAData
[2011/04/01 12:29:09 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Roaming\Waves Audio
[2011/03/30 11:49:04 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{B1B7536E-0DD8-4439-8E99-70A8E66D1734}
[2011/03/29 23:48:41 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{804B2304-02FC-4948-A8A5-FF3627202746}
[2011/03/29 11:48:18 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{92205DA8-C505-445B-955C-6644972E8B02}
[2011/03/28 23:47:54 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{78C71C97-0A08-4AD9-BEC0-CB5253C6BE8D}
[2011/03/28 11:47:41 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{2BF69A3F-CE2B-49B4-BB7E-0EDE494A3322}
[2011/03/23 15:47:47 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{49DAC749-60EF-4986-B17F-5B51B73AF910}
[2011/03/23 03:47:24 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{3E206A6B-9510-442C-89E9-5877B6F49B3D}
[2011/03/22 15:47:13 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{898B7304-1063-4919-B960-761F25204244}
[2011/03/21 15:33:28 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{1E277148-96B2-4A24-8AA9-A275F171E237}
[2011/03/17 22:19:41 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{0E78C31C-32A5-4C9D-B20D-7311E4EF57C4}
[2011/03/16 18:23:50 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\Sony Ericsson
[2011/03/16 18:23:07 | 000,114,728 | —- | C] (MCCI Corporation) – C:\Windows\System32\drivers\s1018mdm.sys
[2011/03/16 18:23:07 | 000,109,864 | —- | C] (MCCI Corporation) – C:\Windows\System32\drivers\s1018unic.sys
[2011/03/16 18:23:07 | 000,106,208 | —- | C] (MCCI Corporation) – C:\Windows\System32\drivers\s1018mgmt.sys
[2011/03/16 18:23:07 | 000,104,744 | —- | C] (MCCI Corporation) – C:\Windows\System32\drivers\s1018obex.sys
[2011/03/16 18:23:07 | 000,086,824 | —- | C] (MCCI Corporation) – C:\Windows\System32\drivers\s1018bus.sys
[2011/03/16 18:23:07 | 000,026,024 | —- | C] (MCCI Corporation) – C:\Windows\System32\drivers\s1018nd5.sys
[2011/03/16 18:23:07 | 000,015,016 | —- | C] (MCCI Corporation) – C:\Windows\System32\drivers\s1018mdfl.sys
[2011/03/16 18:23:07 | 000,012,200 | —- | C] (MCCI Corporation) – C:\Windows\System32\drivers\s1018whnt.sys
[2011/03/16 18:23:07 | 000,012,200 | —- | C] (MCCI Corporation) – C:\Windows\System32\drivers\s1018wh.sys
[2011/03/16 18:23:07 | 000,012,200 | —- | C] (MCCI Corporation) – C:\Windows\System32\drivers\s1018cmnt.sys
[2011/03/16 18:23:07 | 000,012,200 | —- | C] (MCCI Corporation) – C:\Windows\System32\drivers\s1018cm.sys
[2011/03/16 18:23:07 | 000,010,792 | —- | C] (MCCI Corporation) – C:\Windows\System32\drivers\s1018cr.sys
[2011/03/16 18:23:06 | 000,000,000 | —D | C] – C:\ProgramData\Sony Ericsson
[2011/03/16 18:23:06 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Sony Ericsson
[2011/03/16 18:23:06 | 000,000,000 | —D | C] – C:\Program Files\Sony Ericsson
[2011/03/14 21:21:03 | 000,000,000 | —D | C] – C:\Users\RNS\AppData\Local\{3AC1D82F-8220-4F78-B9C3-190D06832C01}
[2009/11/19 22:08:02 | 003,749,224 | —- | C] (Acresso Software Inc.) – C:\Program Files\Common Files\adlmint_libFNP.dll
[2009/11/19 22:08:02 | 002,941,288 | —- | C] (Autodesk, Inc.) – C:\Program Files\Common Files\adlmint.dll
[2009/07/13 16:24:44 | 000,274,432 | —- | C] (Adaptec, Inc.) – C:\Users\RNS\AppData\Local\akaxayug.dll

========== Files - Modified Within 30 Days ==========

[2011/04/13 11:30:22 | 000,010,016 | -H– | M] () – C:\Windows\System32\7B296FB0-376B-497e-B012-9C450E1B7327-5P-1.C7483456-A289-439d-8115-601632D005A0
[2011/04/13 11:30:22 | 000,010,016 | -H– | M] () – C:\Windows\System32\7B296FB0-376B-497e-B012-9C450E1B7327-5P-0.C7483456-A289-439d-8115-601632D005A0
[2011/04/13 11:29:41 | 000,617,222 | —- | M] () – C:\Windows\System32\perfh009.dat
[2011/04/13 11:29:41 | 000,104,496 | —- | M] () – C:\Windows\System32\perfc009.dat
[2011/04/13 11:25:10 | 000,067,584 | –S- | M] () – C:\Windows\bootstat.dat
[2011/04/13 11:25:07 | 312,939,489 | —- | M] () – C:\Windows\MEMORY.DMP
[2011/04/13 11:25:03 | 2408,144,896 | -HS- | M] () – C:\hiberfil.sys
[2011/04/12 22:38:53 | 000,579,267 | —- | M] () – C:\Users\RNS\Desktop\Nomadic21.wav.asd
[2011/04/12 22:29:30 | 086,618,528 | —- | M] () – C:\Users\RNS\Desktop\Nomadic21.wav
[2011/04/11 14:19:17 | 000,000,512 | —- | M] () – C:\Users\RNS\Desktop\MBR.dat
[2011/04/11 14:17:50 | 000,566,272 | —- | M] (AVAST Software) – C:\Users\RNS\Desktop\aswMBR.exe
[2011/04/11 13:31:00 | 000,301,568 | —- | M] () – C:\Users\RNS\Desktop\ddli4gnc.exe
[2011/04/09 13:17:05 | 062,208,044 | —- | M] () – C:\Users\RNS\Desktop\in ur eyes….128.wav
[2011/04/09 13:11:02 | 056,989,484 | —- | M] () – C:\Users\RNS\Desktop\REAL DEAL new.wav
[2011/04/09 13:01:06 | 085,645,288 | —- | M] () – C:\Users\RNS\Desktop\Nomadic20.wav
[2011/04/08 20:28:09 | 069,552,044 | —- | M] () – C:\Users\RNS\Desktop\Innocent Dead 05.wav
[2011/04/08 18:58:33 | 057,824,828 | —- | M] () – C:\Users\RNS\Desktop\Ghetto Life 09.wav
[2011/04/08 16:54:49 | 000,097,360 | —- | M] () – C:\Users\RNS\Desktop\Ambush(Kill).mp3.sfk
[2011/04/08 16:54:42 | 009,340,992 | —- | M] () – C:\Users\RNS\Desktop\Ambush(Kill).mp3
[2011/04/08 16:40:26 | 000,359,929 | —- | M] () – C:\Users\RNS\Desktop\dds.scr
[2011/04/08 16:36:04 | 000,388,608 | —- | M] (Trend Micro Inc.) – C:\Users\RNS\Desktop\HiJackThis.exe
[2011/04/08 16:28:22 | 000,580,608 | —- | M] (OldTimer Tools) – C:\Users\RNS\Desktop\OTL.exe
[2011/04/04 12:22:58 | 000,000,370 | —- | M] () – C:\Windows\tasks\Ad-Aware Update (Weekly).job
[2011/04/02 14:01:56 | 000,000,000 | —- | M] () – C:\Windows\nsreg.dat
[2011/04/01 23:42:12 | 000,000,452 | RHS- | M] () – C:\Users\RNS\ntuser.pol
[2011/04/01 17:37:23 | 000,059,392 | R— | M] () – C:\Windows\System32\streamhlp.dll
[2011/04/01 16:32:13 | 000,001,240 | —- | M] () – C:\Users\RNS\Application Data\Microsoft\Internet Explorer\Quick Launch\Spybot - Search & Destroy.lnk
[2011/04/01 15:29:14 | 000,002,052 | —- | M] () – C:\Windows\epplauncher.mif
[2011/04/01 15:00:01 | 000,098,392 | —- | M] (Sunbelt Software) – C:\Windows\System32\drivers\SBREDrv.sys
[2011/04/01 13:05:00 | 000,003,072 | -HS- | M] () – C:\Windows\57756.exe
[2011/04/01 12:09:57 | 000,000,000 | RHS- | M] () – C:\MSDOS.SYS
[2011/04/01 12:09:57 | 000,000,000 | RHS- | M] () – C:\IO.SYS
[2011/03/24 23:39:24 | 000,111,175 | —- | M] () – C:\Users\RNS\Desktop\ghetto life bass 1.wav.asd
[2011/03/24 23:38:35 | 000,110,559 | —- | M] () – C:\Users\RNS\Desktop\Ghetto life Wah.wav.asd
[2011/03/24 23:34:17 | 000,018,504 | —- | M] () – C:\Users\RNS\Desktop\Ghetto life Wah.sfk
[2011/03/24 23:34:17 | 000,018,504 | —- | M] () – C:\Users\RNS\Desktop\ghetto life bass 1.sfk
[2011/03/24 23:34:10 | 009,442,028 | —- | M] () – C:\Users\RNS\Desktop\ghetto life bass 1.wav
[2011/03/24 23:33:48 | 009,442,028 | —- | M] () – C:\Users\RNS\Desktop\Ghetto life Wah.wav
[2011/03/16 18:23:17 | 000,000,000 | -H– | M] () – C:\Windows\System32\drivers\Msft_User_WpdMtpDr_01_09_00.Wdf
[2011/03/14 22:25:34 | 000,078,160 | —- | M] () – C:\Users\RNS\Desktop\Baionix Nsight INTRO.sfk
[2011/03/14 22:18:19 | 039,984,044 | —- | M] () – C:\Users\RNS\Desktop\Baionix Nsight INTRO.wav

========== Files Created - No Company Name ==========

[2011/04/12 22:38:53 | 000,579,267 | —- | C] () – C:\Users\RNS\Desktop\Nomadic21.wav.asd
[2011/04/12 22:29:29 | 086,618,528 | —- | C] () – C:\Users\RNS\Desktop\Nomadic21.wav
[2011/04/11 14:19:17 | 000,000,512 | —- | C] () – C:\Users\RNS\Desktop\MBR.dat
[2011/04/11 13:30:57 | 000,301,568 | —- | C] () – C:\Users\RNS\Desktop\ddli4gnc.exe
[2011/04/09 15:45:16 | 001,946,528 | —- | C] () – C:\Users\RNS\Desktop\Massive 4.wav
[2011/04/09 15:45:15 | 037,544,208 | —- | C] () – C:\Users\RNS\Desktop\capelton accapella_u tube.wav
[2011/04/09 15:45:15 | 021,967,120 | —- | C] () – C:\Users\RNS\Desktop\erykah badu_on an on.wav
[2011/04/09 15:45:15 | 009,442,028 | —- | C] () – C:\Users\RNS\Desktop\Ghetto life Wah.wav
[2011/04/09 15:45:15 | 009,442,028 | —- | C] () – C:\Users\RNS\Desktop\ghetto life bass 1.wav
[2011/04/09 15:45:15 | 000,112,228 | —- | C] () – C:\Users\RNS\Desktop\capleton_turn it up.wav
[2011/04/09 15:45:14 | 039,984,044 | —- | C] () – C:\Users\RNS\Desktop\Baionix Nsight INTRO.wav
[2011/04/09 15:45:14 | 001,355,664 | —- | C] () – C:\Users\RNS\Desktop\VEC1 BD ReverbFX 16.wav
[2011/04/09 15:45:14 | 000,018,504 | —- | C] () – C:\Users\RNS\Desktop\Ghetto life Wah.sfk
[2011/04/09 15:45:14 | 000,018,504 | —- | C] () – C:\Users\RNS\Desktop\ghetto life bass 1.sfk
[2011/04/09 15:45:14 | 000,003,872 | —- | C] () – C:\Users\RNS\Desktop\Massive 4.sfk
[2011/04/09 15:45:03 | 000,111,175 | —- | C] () – C:\Users\RNS\Desktop\ghetto life bass 1.wav.asd
[2011/04/09 15:45:03 | 000,110,559 | —- | C] () – C:\Users\RNS\Desktop\Ghetto life Wah.wav.asd
[2011/04/09 15:45:03 | 000,078,160 | —- | C] () – C:\Users\RNS\Desktop\Baionix Nsight INTRO.sfk
[2011/04/09 15:45:03 | 000,073,392 | —- | C] () – C:\Users\RNS\Desktop\capelton accapella_u tube.sfk
[2011/04/09 15:45:03 | 000,042,968 | —- | C] () – C:\Users\RNS\Desktop\erykah badu_on an on.sfk
[2011/04/09 15:45:03 | 000,024,951 | —- | C] () – C:\Users\RNS\Desktop\Massive 4.wav.asd
[2011/04/09 15:45:03 | 000,000,284 | —- | C] () – C:\Users\RNS\Desktop\capleton_turn it up.sfk
[2011/04/09 13:16:56 | 062,208,044 | —- | C] () – C:\Users\RNS\Desktop\in ur eyes….128.wav
[2011/04/09 13:09:53 | 056,989,484 | —- | C] () – C:\Users\RNS\Desktop\REAL DEAL new.wav
[2011/04/08 21:58:19 | 085,645,288 | —- | C] () – C:\Users\RNS\Desktop\Nomadic20.wav
[2011/04/08 20:27:50 | 069,552,044 | —- | C] () – C:\Users\RNS\Desktop\Innocent Dead 05.wav
[2011/04/08 18:58:33 | 057,824,828 | —- | C] () – C:\Users\RNS\Desktop\Ghetto Life 09.wav
[2011/04/08 16:50:26 | 000,097,360 | —- | C] () – C:\Users\RNS\Desktop\Ambush(Kill).mp3.sfk
[2011/04/08 16:50:23 | 009,340,992 | —- | C] () – C:\Users\RNS\Desktop\Ambush(Kill).mp3
[2011/04/08 16:40:26 | 000,359,929 | —- | C] () – C:\Users\RNS\Desktop\dds.scr
[2011/04/05 20:05:17 | 000,001,104 | —- | C] () – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Mozilla Firefox.lnk
[2011/04/04 12:20:53 | 000,000,370 | —- | C] () – C:\Windows\tasks\Ad-Aware Update (Weekly).job
[2011/04/02 17:34:50 | 312,939,489 | —- | C] () – C:\Windows\MEMORY.DMP
[2011/04/02 14:01:56 | 000,000,000 | —- | C] () – C:\Windows\nsreg.dat
[2011/04/01 23:42:12 | 000,000,452 | RHS- | C] () – C:\Users\RNS\ntuser.pol
[2011/04/01 17:37:14 | 000,059,392 | R— | C] () – C:\Windows\System32\streamhlp.dll
[2011/04/01 16:32:13 | 000,001,240 | —- | C] () – C:\Users\RNS\Application Data\Microsoft\Internet Explorer\Quick Launch\Spybot - Search & Destroy.lnk
[2011/04/01 15:31:36 | 000,001,897 | —- | C] () – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Microsoft Security Essentials.lnk
[2011/04/01 15:29:14 | 000,002,052 | —- | C] () – C:\Windows\epplauncher.mif
[2011/04/01 12:09:57 | 000,000,000 | RHS- | C] () – C:\MSDOS.SYS
[2011/04/01 12:09:57 | 000,000,000 | RHS- | C] () – C:\IO.SYS
[2011/04/01 12:08:40 | 000,003,072 | -HS- | C] () – C:\Windows\57756.exe
[2011/03/16 18:23:17 | 000,000,000 | -H– | C] () – C:\Windows\System32\drivers\Msft_User_WpdMtpDr_01_09_00.Wdf
[2011/01/30 01:33:19 | 001,228,579 | —- | C] () – C:\Windows\LightWave 3D 9 Uninstaller.exe
[2011/01/03 16:20:05 | 003,300,352 | —- | C] () – C:\Windows\System32\PSP Nitro.dll
[2011/01/02 19:24:28 | 000,000,021 | —- | C] () – C:\Users\RNS\AppData\Roaming\iasna_FB9AEABC-F56E-4c47-A862-8892AA545113.dll
[2011/01/01 22:34:58 | 006,475,776 | —- | C] () – C:\Windows\System32\PSP VintageWarmer2.dll
[2010/12/07 22:56:31 | 000,000,069 | —- | C] () – C:\Windows\NeroDigital.ini
[2010/12/07 20:41:05 | 000,510,976 | —- | C] () – C:\Windows\System32\synsoacc.dll
[2010/12/07 15:54:53 | 000,002,892 | —- | C] () – C:\Windows\System32\audcon.sys
[2010/12/07 15:54:24 | 000,000,045 | —- | C] () – C:\Windows\System32\SYNSOPOS.exe.cfg
[2010/12/07 00:10:55 | 000,380,930 | —- | C] () – C:\Windows\LOOP.exe
[2010/12/06 01:03:31 | 000,679,936 | —- | C] () – C:\Windows\System32\xvidcore.dll
[2010/12/06 01:03:31 | 000,421,888 | —- | C] () – C:\Windows\System32\OpenQuicktimeLib.dll
[2010/12/06 01:03:31 | 000,157,696 | —- | C] () – C:\Windows\System32\unrar.dll
[2010/12/06 01:03:31 | 000,155,648 | —- | C] () – C:\Windows\System32\xvidvfw.dll
[2010/12/06 01:03:31 | 000,019,968 | —- | C] () – C:\Windows\System32\cpuinf32.dll
[2010/12/05 21:24:17 | 000,000,000 | —- | C] () – C:\Windows\ativpsrm.bin
[2010/12/05 21:14:05 | 000,002,888 | —- | C] () – C:\Windows\System32\atipblag.dat
[2010/12/05 21:14:00 | 000,223,990 | —- | C] () – C:\Windows\System32\atiicdxx.dat
[2009/07/13 21:57:37 | 000,067,584 | –S- | C] () – C:\Windows\bootstat.dat
[2009/07/13 21:33:53 | 002,977,160 | —- | C] () – C:\Windows\System32\FNTCACHE.DAT
[2009/07/13 19:05:48 | 000,617,222 | —- | C] () – C:\Windows\System32\perfh009.dat
[2009/07/13 19:05:48 | 000,291,294 | —- | C] () – C:\Windows\System32\perfi009.dat
[2009/07/13 19:05:48 | 000,104,496 | —- | C] () – C:\Windows\System32\perfc009.dat
[2009/07/13 19:05:48 | 000,031,548 | —- | C] () – C:\Windows\System32\perfd009.dat
[2009/07/13 19:05:05 | 000,000,741 | —- | C] () – C:\Windows\System32\NOISE.DAT
[2009/07/13 19:04:11 | 000,215,943 | —- | C] () – C:\Windows\System32\dssec.dat
[2009/07/13 17:19:49 | 000,066,048 | —- | C] () – C:\Windows\System32\PrintBrmUi.exe
[2009/07/13 16:55:01 | 000,043,131 | —- | C] () – C:\Windows\mib.bin
[2009/07/13 16:51:43 | 000,073,728 | —- | C] () – C:\Windows\System32\BthpanContextHandler.dll
[2009/07/13 16:42:10 | 000,064,000 | —- | C] () – C:\Windows\System32\BWContextHandler.dll
[2009/06/10 14:26:10 | 000,673,088 | —- | C] () – C:\Windows\System32\mlang.dat

========== Alternate Data Streams ==========

@Alternate Data Stream - 1381 bytes -> C:\ProgramData\Microsoft:qegwjBXIj1LlXbpm5LacI
@Alternate Data Stream - 1267 bytes -> C:\Program Files\Common Files\System:Hi8VLIassmYB5yhRV8U08ulEw4my
@Alternate Data Stream - 1243 bytes -> C:\ProgramData\Microsoft:WvWIYd3b6bZgZEz0QPkJmohpzf1

< End of report >
OTL Extras logfile created on: 4/13/2011 1:24:13 PM - Run 1
OTL by OldTimer - Version 3.2.22.3 Folder = C:\Users\RNS\Desktop
Ultimate Edition (Version = 6.1.7600) - Type = NTWorkstation
Internet Explorer (Version = 8.0.7600.16385)
Locale: 00000409 | Country: United States | Language: ENU | Date Format: M/d/yyyy

3.00 Gb Total Physical Memory | 2.00 Gb Available Physical Memory | 53.00% Memory free
6.00 Gb Paging File | 4.00 Gb Available in Paging File | 73.00% Paging File free
Paging file location(s): ?:\pagefile.sys [binary data]

%SystemDrive% = C: | %SystemRoot% = C:\Windows | %ProgramFiles% = C:\Program Files
Drive C: | 195.31 Gb Total Space | 129.71 Gb Free Space | 66.41% Space Free | Partition Type: NTFS
Drive D: | 736.10 Gb Total Space | 351.60 Gb Free Space | 47.77% Space Free | Partition Type: NTFS
Drive E: | 4.03 Gb Total Space | 0.00 Gb Free Space | 0.00% Space Free | Partition Type: UDF
Drive F: | 931.51 Gb Total Space | 840.03 Gb Free Space | 90.18% Space Free | Partition Type: NTFS

Computer Name: RNS-PC | User Name: RNS | Logged in as Administrator.
Boot Mode: Normal | Scan Mode: Current user
Company Name Whitelist: Off | Skip Microsoft Files: Off | No Company Name Whitelist: On | File Age = 30 Days

========== Extra Registry (SafeList) ==========


========== File Associations ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\]
.cpl [@ = cplfile] – C:\Windows\System32\control.exe (Microsoft Corporation)
.hlp [@ = hlpfile] – C:\Windows\winhlp32.exe (Microsoft Corporation)

[HKEY_CURRENT_USER\SOFTWARE\Classes\]
.html [@ = FirefoxHTML] – C:\Program Files\Mozilla Firefox\firefox.exe (Mozilla Corporation)

========== Shell Spawning ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\\shell\[command]\command]
batfile [open] – "%1" %*
cmdfile [open] – "%1" %*
comfile [open] – "%1" %*
cplfile [cplopen] – %SystemRoot%\System32\control.exe "%1",%* (Microsoft Corporation)
exefile [open] – "%1" %*
helpfile [open] – Reg Error: Key error.
hlpfile [open] – %SystemRoot%\winhlp32.exe %1 (Microsoft Corporation)
htmlfile – Reg Error: Key error.
htmlfile [print] – rundll32.exe %windir%\system32\mshtml.dll,PrintHTML "%1"
inffile [install] – %SystemRoot%\System32\InfDefaultInstall.exe "%1" (Microsoft Corporation)
piffile [open] – "%1" %*
regfile [merge] – Reg Error: Key error.
scrfile [config] – "%1"
scrfile [install] – rundll32.exe desk.cpl,InstallScreenSaver %l
scrfile [open] – "%1" /S
txtfile – Reg Error: Key error.
Unknown [openas] – %SystemRoot%\system32\rundll32.exe %SystemRoot%\system32\shell32.dll,OpenAs_RunDLL %1
Directory [AddToPlaylistVLC] – "C:\Program Files\VideoLAN\VLC\vlc.exe" –started-from-file –playlist-enqueue "%1" ()
Directory [cmd] – cmd.exe /s /k pushd "%V" (Microsoft Corporation)
Directory [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Directory [PlayWithVLC] – "C:\Program Files\VideoLAN\VLC\vlc.exe" –started-from-file –no-playlist-enqueue "%1" ()
Folder [open] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Folder [explore] – Reg Error: Value error.
Drive [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)

========== Security Center Settings ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center]
"cval" = 1

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Monitoring]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Svc]
"VistaSp1" = Reg Error: Unknown registry data type – File not found
"AntiVirusOverride" = 0
"AntiSpywareOverride" = 0
"FirewallOverride" = 0

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Svc\Vol]

========== System Restore Settings ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows NT\SystemRestore]
"DisableSR" = 0

========== Firewall Settings ==========

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\DomainProfile]
"DisableNotifications" = 0
"EnableFirewall" = 1

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\StandardProfile]
"DisableNotifications" = 0
"EnableFirewall" = 1

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\PublicProfile]
"DisableNotifications" = 0
"EnableFirewall" = 1

========== Authorized Applications List ==========

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\StandardProfile\AuthorizedApplications\List]


========== HKEY_LOCAL_MACHINE Uninstall List ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall]
"{0032D29F-7E8F-40E5-AD12-8857AAB0DBFF}" = Catalyst Control Center - Branding
"{00ADFB20-AE75-46F4-AD2C-F48B15AC3100}" = Adobe Color NA Recommended Settings CS4
"{02627EE5-EACA-4742-A9CC-E687631773E4}" = Nero ShowTime
"{05308C4E-7285-4066-BAE3-6B50DA6ED755}" = Adobe Update Manager CS4
"{054EFA56-2AC1-48F4-A883-0AB89874B972}" = Adobe Extension Manager CS4
"{07AA84F8-EF8E-A01C-B6B1-0EC130157CBD}" = CCC Help Greek
"{098727E1-775A-4450-B573-3F441F1CA243}" = kuler
"{0B0F231F-CE6A-483D-AA23-77B364F75917}" = Windows Live Installer
"{0C42FE26-F225-B4AF-B6C5-1CFFF3076A9F}" = ATI AVIVO Codecs
"{0D6013AB-A0C7-41DC-973C-E93129C9A29F}" = Adobe Color JA Extra Settings CS4
"{0F723FC1-7606-4867-866C-CE80AD292DAF}" = Adobe CSI CS4
"{14F70205-1940-4000-88C7-BE799A6B2CAD}" = Adobe Soundbooth CS4
"{15BF7AAF-846C-4A6D-80E1-5D1FC7FB461B}" = Adobe SGM CS4
"{1618734A-3957-4ADD-8199-F973763109A8}" = Adobe Anchor Service CS4
"{16E16F01-2E2D-4248-A42F-76261C147B6C}" = Adobe Drive CS4
"{16E6D2C1-7C90-4309-8EC4-D2212690AAA4}" = AdobeColorCommonSetRGB
"{197A3012-8C85-4FD3-AB66-9EC7E13DB92E}" = Adobe AIR
"{1B365895-EB49-428D-0B62-92C419305468}" = CCC Help Czech
"{1B7C06E1-4888-47A6-992A-0990B9683486}" = Adobe Version Cue CS4 Server
"{1C00C7C5-E615-4139-B817-7F4003DE68C0}" = Nero PhotoSnap Help
"{1DCA3EAA-6EB5-4563-A970-EA14D75037BA}" = Adobe InDesign CS4
"{1E04CB54-AF4E-4AC3-B4B7-C0A160BE57F1}" = Adobe InDesign CS4 Icon Handler
"{1E958728-CFA3-454A-A2D6-42A9FF718480}" = Intel® C++ Redistributables for Windows* on IA-32
"{1F1C2DFC-2D24-3E06-BCB8-725134ADF989}" = Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.4148
"{200FEC62-3C34-4D60-9CE8-EC372E01C08F}" = Windows Live SOXE Definitions
"{20400DBD-E6DB-45B8-9B6B-1DD7033818EC}" = Nero InfoTool Help
"{2168245A-B5AD-40D8-A641-48E3E070B5B6}" = Adobe Flash CS4 STI-en
"{2348B586-C9AE-46CE-936C-A68E9426E214}" = Nero StartSmart Help
"{2375BC18-66B0-FA52-F110-CF3CF1018E34}" = Catalyst Control Center Localization All
"{26A24AE4-039D-4CA4-87B4-2F83216023FF}" = Java™ 6 Update 23
"{297190A1-4B0D-4CD6-8B9F-3907F15C3FD8}" = Adobe CS4 American English Speech Analysis Models
"{2A981294-F14C-4F0F-9627-D793270922F8}" = Bonjour
"{2BAF2B96-7560-48B4-87D4-10178DDBE217}" = Adobe InDesign CS4 Application Feature Set Files (Roman)
"{2F9CA2D0-EF4F-4EE3-80B2-0164FB9D448F}" = CCC Help Korean
"{308B6AEA-DE50-4666-996D-0FA461719D6B}" = Apple Mobile Device Support
"{30C8AA56-4088-426F-91D1-0EDFD3A25678}" = Adobe Dreamweaver CS4
"{30DBA5A1-9E59-84A7-5B2D-5A8486096C57}" = CCC Help English
"{32D67656-20CD-8C6C-7CC4-E345AC059CDE}" = AMD Drag and Drop Transcoding
"{33CF58F5-48D8-4575-83D6-96F574E4D83A}" = Nero DriveSpeed
"{359CFC0A-BEB1-440D-95BA-CF63A86DA34F}" = Nero Recode
"{35D94F92-1D3A-43C5-8605-EA268B1A7BD9}" = PDF Settings CS4
"{365EB5F8-ABD0-1D30-B0E5-C7250B200B8F}" = CCC Help Thai
"{39EA0008-A05B-FDEB-EF5D-A8EEFFB14006}" = CCC Help Chinese Standard
"{39F6E2B4-CFE8-C30A-66E8-489651F0F34C}" = Adobe Media Player
"{3A4E8896-C2E7-4084-A4A4-B8FD1894E739}" = Adobe XMP Panels CS4
"{3A6829EF-0791-4FDD-9382-C690DD0821B9}" = Adobe Flash Player 10 ActiveX
"{3B092BE6-7A2B-711E-207A-D5EEC9195E39}" = ccc-utility
"{3D2C9DE6-9ADE-4252-A241-E43723B0CE02}" = Adobe Color - Photoshop Specific CS4
"{3D347E6D-5A03-4342-B5BA-6A771885F379}" = Autodesk Backburner 2011.0.0
"{3DA8DF9A-044E-46C4-8531-DEDBB0EE37FF}" = Adobe WinSoft Linguistics Plugin
"{3E30120B-5BDF-4CB8-BB70-6B481CAC3CB2}" = Max 5.1.7
"{3F54B9C1-16A6-B1CC-ADB3-81C4CE3E1D18}" = ATI Catalyst Install Manager
"{404C18ED-873A-4191-BA03-30F627445418}" = Sentinel Protection Installer 7.3.0
"{428FDF9F-E010-4C4C-A8BB-156960AFCA1C}" = Adobe Fireworks CS4
"{43509E18-076E-40FE-AF38-CA5ED400A5A9}" = Pixel Bender Toolkit
"{43E39830-1826-415D-8BAE-86845787B54B}" = Nero Vision
"{43E7798A-248E-4A3D-9969-FEA63543A462}" = Native Instruments Kontakt 4
"{43E8D9E7-AFC9-4BA3-8106-B95E02B87AB7}" = EZdrummer
"{44E240EC-2224-4078-A88B-2CEE0D3016EF}" = Adobe After Effects CS4 Presets
"{45EC816C-0771-4C14-AE6D-72D1B578F4C8}" = Adobe After Effects CS4
"{4859F815-DF4D-C463-EDBE-9F620B98FA0F}" = CCC Help Swedish
"{490BF87E-1F75-4453-BF55-9F540543A3CA}" = Steinberg Drum Loop Expansion 01
"{491DF203-7B61-4F0E-BDCB-A1218C4DAFE9}" = Native Instruments Massive
"{4943EFF5-229F-435D-BEA9-BE3CAEA783A7}" = Adobe Service Manager Extension
"{4A03706F-666A-4037-7777-5F2748764D10}" = Java Auto Updater
"{4A19D6AC-ADE0-4A07-80FF-9C9812C45557}" = Steinberg Cubase 5
"{4A52555C-032A-4083-BDD9-6A85ABFB39A8}" = Adobe SING CS4
"{4D43D635-6FDA-4FA5-AA9B-23CF73D058EA}" = Nero StartSmart OEM
"{4D454CF8-12FD-464D-B57B-B46FE27B78BB}" = Steinberg LoopMash Content
"{50A2F735-4BC0-CB18-80F7-3CFD5E12ED23}" = CCC Help Norwegian
"{532B917B-8235-4FA5-BE36-643A8BB053A5}" = Steinberg REVerence Content 01
"{5570C7F0-43D0-4916-8A9E-AEDD52FA86F4}" = Adobe Color EU Extra Settings CS4
"{56C049BE-79E9-4502-BEA7-9754A3E60F9B}" = neroxml
"{57752979-A1C9-4C02-856B-FBB27AC4E02C}" = QuickTime
"{577A6872-1535-0591-E5FE-E23D503D42C8}" = CCC Help Hungarian
"{579684A4-DDD5-4CA3-9EA8-7BE7D9593DB4}" = Windows Live UX Platform Language Pack
"{595A3116-40BB-4E0F-A2E8-D7951DA56270}" = NeroExpress
"{5C700FC9-2039-3C01-C7EF-2A55C7B6E68B}" = CCC Help Finnish
"{5D9BE3C1-8BA4-4E7E-82FD-9F74FA6815D1}" = Nero Vision Help
"{5EAD5443-7194-46CC-A055-428E6ABB1BAF}" = Adobe Encore CS4
"{60C731FB-C951-41CE-AD41-8E54C8594609}" = Nero Disc Copy Gadget Help
"{60DB5894-B5A1-4B62-B0F3-669A22C0EE5D}" = Adobe Dynamiclink Support
"{61AD15B2-50DB-4686-A739-14FE180D4429}" = Windows Live ID Sign-in Assistant
"{61D6891E-E822-4448-9F9A-0AAAAEB6AF6C}" = Adobe Creative Suite 4 Master Collection
"{62AC81F6-BDD3-4110-9D36-3E9EAAB40999}" = Nero CoverDesigner
"{639673E9-D53F-44F4-A046-485C8A6ADA15}" = Paint.NET v3.5.6
"{63C24A08-70F3-4C8E-B9FB-9F21A903801D}" = Adobe Color Video Profiles CS CS4
"{63E5CDBF-8214-4F03-84F8-CD3CE48639AD}" = Adobe Photoshop CS4 Support
"{6406E3EA-9777-45B7-A0C0-89741E629352}" = Composite 2011
"{64522D5F-4743-4939-8E22-B1878FB68772}" = M-Audio FireWire Driver 6.0.1 (x86)
"{67A9747A-E1F5-4E9A-81CC-12B5D5B81B6E}" = Adobe After Effects CS4 Third Party Content
"{67EFADAD-D448-CF11-4785-BF7F95D1980B}" = Catalyst Control Center InstallProxy
"{67F0E67A-8E93-4C2C-B29D-47C48262738A}" = Adobe Device Central CS4
"{68243FF8-83CA-466B-B2B8-9F99DA5479C4}" = AdobeColorCommonSetCMYK
"{682B3E4F-696A-42DE-A41C-4C07EA1678B4}" = Windows Live SOXE
"{697EEF19-844D-94BD-9E72-986216C6911B}" = ccc-core-static
"{69C44DB6-7E2F-23A1-409D-E5FBA7D73D78}" = Catalyst Control Center Graphics Previews Common
"{6E58BEA7-DDFB-F4F8-39C5-0723165706F3}" = CCC Help Spanish
"{702EC1FF-A081-48AE-8363-8D78A0919F86}" = Autodesk DirectConnect 2010 R1
"{7299052b-02a4-4627-81f2-1818da5d550d}" = Microsoft Visual C++ 2005 Redistributable
"{7406DF60-016D-476B-A2C7-55D997592047}" = Adobe OnLocation CS4
"{774088D4-0777-4D78-904D-E435B318F5D2}" = Microsoft Antimalware
"{7748AC8C-18E3-43BB-959B-088FAEA16FB2}" = Nero StartSmart
"{77A776C4-D10F-416D-88F0-53F2D9DCD9B3}" = Microsoft Security Client
"{7829DB6F-A066-4E40-8912-CB07887C20BB}" = Nero BurnRights
"{793D1D88-6141-43DE-BE58-59BCE31B4090}" = Adobe Flash CS4 Extension - Flash Lite STI en
"{7CC7BDD5-6F10-4724-96A1-EAC7D9F2831C}" = Adobe InDesign CS4 Common Base Files
"{7E69F2E7-BECC-CBAB-A09C-97AD974298EF}" = CCC Help Russian
"{80956555-A512-4190-9CAD-B000C36D6B6B}" = Windows Live Messenger
"{820D3F45-F6EE-4AAF-81EF-CE21FF21D230}" = Adobe Type Support CS4
"{83202942-84B3-4C50-8622-B8C0AA2D2885}" = Nero Express Help
"{837b34e3-7c30-493c-8f6a-2b0f04e2912c}" = Microsoft Visual C++ 2005 Redistributable
"{83877DB1-8B77-45BC-AB43-2BAC22E093E0}" = Adobe Bridge CS4
"{83C292B7-38A5-440B-A731-07070E81A64F}" = Windows Live PIMT Platform
"{842B4B72-9E8F-4962-B3C1-1C422A5C4434}" = Suite Shared Configuration CS4
"{84656952-D528-4DF8-9504-2E9ACBE81676}" = Blue Cat's FreqAnalyst CM VST 1.2
"{865D9ED1-EAC2-436D-AFA7-0B750EB5AAAB}" = Steinberg HALionOne Studio Drum Set
"{869200DB-287A-4DC0-B02B-2B6787FBCD4C}" = Nero DiscSpeed
"{87532CAB-7932-4F84-8937-823337622807}" = Adobe Illustrator CS4
"{881F5DE8-9367-4B81-A325-E91BBC6472F9}" = iTunes
"{89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}" = Microsoft Silverlight
"{8A864555-554E-4DE2-BB36-BC4810355525}" = Autodesk MatchMover 2011 32-bit
"{8DD46C6A-0056-4FEC-B70A-28BB16A1F11F}" = MSVCRT
"{8EB8E60B-315D-44EB-A896-10D88602EE46}" = Adobe Setup
"{90A64EC9-64E0-7725-684C-F9CCD67C61A8}" = CCC Help French
"{931AB7EA-3656-4BB7-864D-022B09E3DD67}" = Adobe Linguistics CS4
"{94D398EB-D2FD-4FD1-B8C4-592635E8A191}" = Adobe CMaps CS4
"{95120000-00B9-0409-0000-0000000FF1CE}" = Microsoft Application Error Reporting
"{9A25302D-30C0-39D9-BD6F-21E6EC160475}" = Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.17
"{9E82B934-9A25-445B-B8DF-8012808074AC}" = Nero PhotoSnap
"{9E85BA11-D075-668B-5212-582A70F08BDF}" = CCC Help Chinese Traditional
"{9FAE3CF7-D17E-45CF-470B-E282BF3A5B79}" = CCC Help Japanese
"{A0C32A95-848F-73FD-ACFC-C66EF566B91B}" = HydraVision
"{A3DFC9F6-0BF2-2138-11FA-064D94DFC902}" = CCC Help Danish
"{A49F249F-0C91-497F-86DF-B2585E8E76B7}" = Microsoft Visual C++ 2005 Redistributable
"{A6EC82A0-1414-475D-8AFD-469089F3080D}" = Adobe Contribute CS4
"{A8F2089B-1F79-4BF6-B385-A2C2B0B9A74D}" = ImagXpress
"{A9474D45-F7B9-7E7B-609B-671EE5FA508D}" = CCC Help Polish
"{A9BDCA6B-3653-467B-AC83-94367DA3BFE3}" = Windows Live Photo Common
"{AA1D2BF3-E347-7232-119A-7F62DD4901B3}" = WMV9/VC-1 Video Playback
"{AC075837-7071-4c07-B9A1-CF5586060FE1}" = Autodesk Maya 2011 English Documentation 32-bit
"{AC76BA86-1033-F400-7760-000000000004}" = Adobe Acrobat 9 Pro - English, Français, Deutsch
"{AC997F93-0757-4ED4-A701-F40C2D654D09}" = Steinberg HALionOne GM Drum Set
"{AD6BC5CC-2EF0-49C4-B33D-CDC8B2C4DC80}" = Nero Recode Help
"{B05DE7B7-0B40-4411-BD4B-222CAE2D8F15}" = Adobe MotionPicture Color Files CS4
"{B15381DD-FF97-4FCD-A881-ED4DB0975500}" = Adobe Color Video Profiles AE CS4
"{B169BC97-B8AA-4ACA-9CF2-9D0FF5BABDF7}" = Adobe Premiere Pro CS4 Functional Content
"{B1ADF008-E898-4FE2-8A1F-690D9A06ACAF}" = DolbyFiles
"{B29AD377-CC12-490A-A480-1452337C618D}" = Connect
"{B2EC4A38-B545-4A00-8214-13FE0E915E6D}" = Advertising Center
"{B4092C6D-E886-4CB2-BA68-FE5A88D31DE6}_is1" = Spybot - Search & Destroy
"{B65BA85C-0A27-4BC0-A22D-A66F0E5B9494}" = Adobe Photoshop CS4
"{B6CAF3AD-4B86-AFF4-5779-6BDDD92C6CD4}" = CCC Help Italian
"{B6D12710-26FC-11DF-AA8E-AE2756D89593}_is1" = RhinoCM 2.09
"{B8A817D7-AE0F-42BA-AEB9-B5F1F3EFB7AF}" = Sound Forge Pro 10.0
"{B9F4561A-924D-4510-A85A-BB0960C338CB}" = Adobe Asset Services CS4
"{BB4E33EC-8181-4685-96F7-8554293DEC6A}" = Adobe Output Module
"{BD5CA0DA-71AD-43DA-B19E-6EEE0C9ADC9A}" = Nero ControlCenter
"{BD86F1AC-B594-46E4-85DC-1258AC9E2232}" = Steinberg Groove Agent ONE Content
"{BE9CEAAA-F069-4331-BF2F-8D350F6504F4}" = Adobe Media Encoder CS4 Additional Exporter
"{C41300B9-185D-475E-BFEC-39EF732F19B1}" = Apple Software Update
"{C52E3EC1-048C-45E1-8D53-10B0C6509683}" = Adobe Default Language CS4
"{C81A2FE0-3574-00A9-CED4-BDAA334CBE8E}" = Nero Online Upgrade
"{C86E7C99-E4AD-79C7-375B-1AEF9A91EC2B}" = Acrobat.com
"{c8ded016-96e1-4d68-84f6-878f64a1540b}" = Nero 9 Essentials
"{CA1F6B80-A1D2-A63F-55E4-1195041562FC}" = Catalyst Control Center Graphics Previews Vista
"{CC019E3F-59D2-4486-8D4B-878105B62A71}" = Nero DiscSpeed Help
"{CC75AB5C-2110-4A7F-AF52-708680D22FE8}" = Photoshop Camera Raw
"{CC8E94A2-55C7-4460-953C-2A790180578C}" = LightScribe System Software
"{CCEB497B-5427-FCA1-3DD8-172CB3AE9378}" = CCC Help Portuguese
"{CDDCBBF1-2703-46BC-938B-BCC81A1EEAAA}" = SUPERAntiSpyware
"{CE95A79E-E4FC-4FFF-8A75-29F04B942FF2}" = Windows Live UX Platform
"{CE96F5A5-584D-4F8F-AA3E-9BAED413DB72}" = Nero CoverDesigner Help
"{CFF2B115-FB28-4D06-8852-25D21112B63C}" = CCC Help Turkish
"{D23CBFDA-C46B-4920-BA70-FC7878A3F05A}" = Steinberg HALionOne Studio Set
"{D436F577-1695-4D2F-8B44-AC76C99E0002}" = Windows Live Photo Common
"{D45240D3-B6B3-4FF9-B243-54ECE3E10066}" = Windows Live Communications Platform
"{D499F8DE-3F31-4900-9157-61061613704B}" = Adobe Premiere Pro CS4
"{D82CDA0D-C182-42C8-8FF2-5649C98D6003}" = Steinberg HALionOne Pro Set
"{D9DCF92E-72EB-412D-AC71-3B01276E5F8B}" = Nero ShowTime
"{DEB90B8E-0DCB-48CE-B90E-8842A2BD643E}" = Adobe Media Encoder CS4
"{E09C4DB7-630C-4F06-A631-8EA7239923AF}" = D3DX10
"{E22AD5D3-EB60-4A8F-835C-6C10E369DCE2}" = Steinberg HALionOne Expression Set
"{E4386119-2C33-4023-9836-783F43A90E3C}" = Autodesk Maya 2011 32-bit
"{E5C7D048-F9B4-4219-B323-8BDB01A2563D}" = Nero DriveSpeed Help
"{E680879B-0745-69F0-5766-8E96555532B8}" = CCC Help Dutch
"{E70E7159-93B1-470D-9FBD-D8E9EF34B538}" = Steinberg HALionOne
"{E8A80433-302B-4FF1-815D-FCC8EAC482FF}" = Nero Installer
"{E8EE9410-8AC4-4F43-A626-DDECA75C79F3}" = Adobe Setup
"{EB4DF488-AAEF-406F-A341-CB2AAA315B90}" = Windows Live Messenger
"{EC015649-3B3C-4611-9C66-453F8011E944}" = Native Instruments Kontakt 4
"{EE353798-E875-42E0-B58D-7E6696182EA8}" = Adobe Media Encoder CS4 Dolby
"{EE6097DD-05F4-4178-9719-D3170BF098E8}" = Apple Application Support
"{F057965A-D974-4C64-ADB1-4381CD4B8956}" = Steinberg HALionOne GM Set
"{F09EF8F2-0976-42C1-8D9D-8DF78337C6E3}" = Sony Ericsson PC Companion 1.60.13
"{F0E64E2E-3A60-40D8-A55D-92F6831875DA}" = Adobe Search for Help
"{F132AF7F-7BCA-4EDE-8A7C-958108FE7DBC}" = Realtek High Definition Audio Driver
"{F1861F30-3419-44DB-B2A1-C274825698B3}" = Nero Disc Copy Gadget
"{F333A33D-125C-32A2-8DCE-5C5D14231E27}" = Visual C++ 2008 x86 Runtime - (v9.0.30729)
"{F333A33D-125C-32A2-8DCE-5C5D14231E27}.vc_x86runtime_30729_01" = Visual C++ 2008 x86 Runtime - v9.0.30729.01
"{F3AFD063-8BAD-485E-B641-E7F5A2C5AE71}" = Steinberg HALionOne Additional Content Set 01
"{F4041DCE-3FE1-4E18-8A9E-9DE65231EE36}" = Nero ControlCenter
"{F6BDD7C5-89ED-4569-9318-469AA9732572}" = Nero BurnRights Help
"{F6E99614-F042-4459-82B7-8B38B2601356}" = Adobe Flash CS4
"{F8EF2B3F-C345-4F20-8FE4-791A20333CD5}" = Adobe ExtendScript Toolkit CS4
"{F93C84A6-0DC6-42AF-89FA-776F7C377353}" = Adobe PDF Library Files CS4
"{FBCDFD61-7DCF-4E71-9226-873BA0053139}" = Nero InfoTool
"{FCC78952-DF5D-C8F1-6A38-8F4CAAAF0D0A}" = CCC Help German
"{FCDD51BB-CAD0-4BB1-B7DF-CE86D1032794}" = Adobe Fonts All
"{FE044230-9CA5-43F7-9B58-5AC5A28A1F33}" = Windows Live Essentials
"{FF66E9F6-83E7-3A3E-AF14-8DE9A809A6A4}" = Microsoft Visual C++ 2008 Redistributable - x86 9.0.21022
"Adobe AIR" = Adobe AIR
"Adobe Flash Player Plugin" = Adobe Flash Player 10 Plugin
"Adobe_5aab5a491a3a52ae624fd639f6aaa95" = Adobe After Effects CS4 Third Party Content
"Adobe_b2d6abde968e6f277ddbfd501383e02" = Adobe Creative Suite 4 Master Collection
"Antares Filter VST DX v1.01" = Antares Filter VST DX v1.01
"Antares Tube v1.02 RTAS" = Antares Tube v1.02 RTAS
"Artillery2 CM Edition" = Artillery2 CM Edition
"Artillery2_is1" = Sugar Bytes Artillery2 Demo 2.3
"Astralis_0" = Astralis CM v1.0 1.0
"CM Alpha" = CM Alpha
"CM WaveShaper" = CM WaveShaper
"com.adobe.amp.4875E02D9FB21EE389F73B8D1702B320485DF8CE.1" = Adobe Media Player
"com.adobe.mauby.4875E02D9FB21EE389F73B8D1702B320485DF8CE.1" = Acrobat.com
"ComputerMusic Wusikstation VSTi Installer_is1" = Wusikstation CM VSTi V1.1.062
"eLicenser Control" = eLicenser Control
"EyeCandy5Impact" = Alien Skin Eye Candy 5 Impact
"EyeCandy5Nature" = Alien Skin Eye Candy 5 Nature
"EyeCandy5Textures" = Alien Skin Eye Candy 5 Textures
"FabFilter One 2.01" = FabFilter One 2.01
"Google Desktop" = Google Desktop
"GRM TOOLS Classic v1.6" = GRM TOOLS Classic v1.6
"GRM TOOLS ST v1.6" = GRM TOOLS ST v1.6
"GSuiteCM" = Guitar Suite CM
"iZotope Ozone 3_is1" = iZotope Ozone 3
"iZotope Spectron_is1" = iZotope Spectron
"KLiteCodecPack_is1" = K-Lite Mega Codec Pack 1.38
"LightWave 3D 9" = LightWave 3D 9
"Live 8.1.1" = Live 8.1.1
"Magic ISO Maker v5.4 (build 0256)" = Magic ISO Maker v5.4 (build 0256)
"MagicDisc 2.7.106" = MagicDisc 2.7.106
"Malwarebytes' Anti-Malware_is1" = Malwarebytes' Anti-Malware
"Microsoft Security Client" = Microsoft Security Essentials
"Microtonal_0" = Microtonal Patches v2 2.0
"Mozilla Firefox 4.0 (x86 en-US)" = Mozilla Firefox 4.0 (x86 en-US)
"Native Instruments Absynth 4" = Native Instruments Absynth 4
"Native Instruments Kontakt 3" = Native Instruments Kontakt 3
"Native Instruments Kontakt 4" = Native Instruments Kontakt 4
"Native Instruments Massive" = Native Instruments Massive
"Native Instruments Service Center" = Native Instruments Service Center
"Native.Instruments Battery v3.0.1.005 VSTi DXi RTAS" = Native.Instruments Battery v3.0.1.005 VSTi DXi RTAS
"Ohmygod VST2" = OhmForce Ohmygod VST2
"Predator_is1" = Rob Papen Predator V1.1.0
"PSP SpringVerbCM" = PSP SpringVerb CM
"PSP VintageWarmer 2.0.0" = PSP VintageWarmer 2.0.0
"PSP_Nitro" = PSP Nitro 1.1.0
"Reason4_is1" = Reason 4.0.1
"Rob Papen Albino 3" = Rob Papen Albino 3
"Rob Papen BLUE Version 1.7.0_is1" = Rob Papen BLUE Version 1.7.0
"Steinberg Hypersonic v1.0" = Steinberg Hypersonic v1.0
"StereoizerCM_is1" = Stereoizer - Computer Music Edition v1.0
"SubBoomBass_is1" = Rob Papen SubBoomBass 1.0.3c
"SynapsePluckedString_is1" = Plucked String VSTi/DXi v4.0
"SyncroSoft Emu" = SyncroSoft Emu (Remove only)
"uTorrent" = µTorrent
"VLC media player" = VLC media player 1.1.5
"Wacom Tablet Driver" = Wacom Tablet
"Wacom WebTabletPlugin for IE" = WebTablet IE Plugin
"Wacom WebTabletPlugin for Netscape" = WebTablet Netscape Plugin
"Waves Diamond Bundle 4.05" = Waves Diamond Bundle 4.05
"Waves L3 LL" = Waves L3 LL
"Waves SSL Collection v1.2" = Waves SSL Collection v1.2
"WinLiveSuite" = Windows Live Essentials
"WinRAR archiver" = WinRAR archiver

========== HKEY_CURRENT_USER Uninstall List ==========

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall]

========== Last 10 Event Log Errors ==========

[ Application Events ]
Error - 4/12/2011 5:31:54 PM | Computer Name = RNS-PC | Source = Application Error | ID = 1000
Description = Faulting application name: svchost.exe, version: 6.1.7600.16385, time
stamp: 0x4a5bc100 Faulting module name: KERNELBASE.dll, version: 6.1.7600.16385,
time stamp: 0x4a5bdaae Exception code: 0xe06d7363 Fault offset: 0x00009617 Faulting
process id: 0x4b4 Faulting application start time: 0x01cbf957601a5300 Faulting application
path: C:\Windows\system32\svchost.exe Faulting module path: C:\Windows\system32\KERNELBASE.dll
Report
Id: 48aacb6c-654c-11e0-a748-0024213116bd

Error - 4/12/2011 6:19:59 PM | Computer Name = RNS-PC | Source = Application Error | ID = 1000
Description = Faulting application name: svchost.exe, version: 6.1.7600.16385, time
stamp: 0x4a5bc100 Faulting module name: unknown, version: 0.0.0.0, time stamp: 0x00000000
Exception
code: 0xc0000005 Fault offset: 0x09090909 Faulting process id: 0x7a8 Faulting application
start time: 0x01cbf95acb6e48c6 Faulting application path: C:\Windows\system32\svchost.exe
Faulting
module path: unknown Report Id: 0038e013-6553-11e0-a748-0024213116bd

Error - 4/13/2011 12:03:20 AM | Computer Name = RNS-PC | Source = Application Error | ID = 1000
Description = Faulting application name: svchost.exe, version: 6.1.7600.16385, time
stamp: 0x4a5bc100 Faulting module name: KERNELBASE.dll, version: 6.1.7600.16385,
time stamp: 0x4a5bdaae Exception code: 0xe06d7363 Fault offset: 0x00009617 Faulting
process id: 0xd6c Faulting application start time: 0x01cbf95ff6a7d937 Faulting application
path: C:\Windows\system32\svchost.exe Faulting module path: C:\Windows\system32\KERNELBASE.dll
Report
Id: f7518e51-6582-11e0-a748-0024213116bd

Error - 4/13/2011 3:34:58 AM | Computer Name = RNS-PC | Source = Application Error | ID = 1000
Description = Faulting application name: svchost.exe, version: 6.1.7600.16385, time
stamp: 0x4a5bc100 Faulting module name: jvm.dll, version: 19.0.0.9, time stamp:
0x4cddfd7f Exception code: 0xc0000005 Fault offset: 0x000ca9b2 Faulting process id:
0x1574 Faulting application start time: 0x01cbf98fbd917f35 Faulting application path:
C:\Windows\system32\svchost.exe Faulting module path: C:\PROGRA~1\Java\jre6\bin\client\jvm.dll
Report
Id: 880189f3-65a0-11e0-a748-0024213116bd

Error - 4/13/2011 5:41:11 AM | Computer Name = RNS-PC | Source = Application Error | ID = 1000
Description = Faulting application name: svchost.exe, version: 6.1.7600.16385, time
stamp: 0x4a5bc100 Faulting module name: KERNELBASE.dll, version: 6.1.7600.16385,
time stamp: 0x4a5bdaae Exception code: 0xe06d7363 Fault offset: 0x00009617 Faulting
process id: 0x560 Faulting application start time: 0x01cbf9ad5b5873f6 Faulting application
path: C:\Windows\system32\svchost.exe Faulting module path: C:\Windows\system32\KERNELBASE.dll
Report
Id: 2a249069-65b2-11e0-a748-0024213116bd

Error - 4/13/2011 9:45:52 AM | Computer Name = RNS-PC | Source = Application Error | ID = 1000
Description = Faulting application name: svchost.exe, version: 6.1.7600.16385, time
stamp: 0x4a5bc100 Faulting module name: KERNELBASE.dll, version: 6.1.7600.16385,
time stamp: 0x4a5bdaae Exception code: 0xe06d7363 Fault offset: 0x00009617 Faulting
process id: 0x1608 Faulting application start time: 0x01cbf9bef56bf725 Faulting application
path: C:\Windows\system32\svchost.exe Faulting module path: C:\Windows\system32\KERNELBASE.dll
Report
Id: 587bce17-65d4-11e0-a748-0024213116bd

Error - 4/13/2011 3:19:24 PM | Computer Name = RNS-PC | Source = SideBySide | ID = 16842785
Description = Activation context generation failed for "C:\Program Files\Autodesk\Composite
2011\python\lib\distutils\command\wininst-8_d.exe". Dependent Assembly Microsoft.VC80.DebugCRT,processorArchitecture="x86",publicKeyToken="1fc8b3b9a1e18e3b",type="win32",version="8.0.50608.0"
could not be found. Please use sxstrace.exe for detailed diagnosis.

Error - 4/13/2011 3:19:39 PM | Computer Name = RNS-PC | Source = SideBySide | ID = 16842815
Description = Activation context generation failed for "c:\Program Files\Common
Files\Adobe AIR\Versions\1.0\Adobe AIR.dll".Error in manifest or policy file "c:\Program
Files\Common Files\Adobe AIR\Versions\1.0\Adobe AIR.dll" on line 3. The value "MAJOR_VERSION.MINOR_VERSION.BUILD_NUMBER_MAJOR.BUILD_NUMBER_MINOR"
of attribute "version" in element "assemblyIdentity" is invalid.

Error - 4/13/2011 3:20:05 PM | Computer Name = RNS-PC | Source = SideBySide | ID = 16842815
Description = Activation context generation failed for "c:\program files\spybot
- search & destroy\DelZip179.dll".Error in manifest or policy file "c:\program files\spybot
- search & destroy\DelZip179.dll" on line 8. The value "*" of attribute "language"
in element "assemblyIdentity" is invalid.

Error - 4/13/2011 3:20:06 PM | Computer Name = RNS-PC | Source = SideBySide | ID = 16842785
Description = Activation context generation failed for "c:\program files\sony ericsson\sony
ericsson pc companion\Drivers\DPInst64.exe". Dependent Assembly Microsoft.Windows.Common-Controls,language="*",processorArchitecture="amd64",publicKeyToken="6595b64144ccf1df",type="win32",version="6.0.0.0"
could not be found. Please use sxstrace.exe for detailed diagnosis.

[ System Events ]
Error - 4/13/2011 5:20:21 AM | Computer Name = RNS-PC | Source = Microsoft-Windows-DNS-Client | ID = 1012
Description = There was an error while attempting to read the local hosts file.

Error - 4/13/2011 5:41:12 AM | Computer Name = RNS-PC | Source = Service Control Manager | ID = 7034
Description = The Windows Management Instrumentation service terminated unexpectedly.
It has done this 6 time(s).

Error - 4/13/2011 9:45:52 AM | Computer Name = RNS-PC | Source = Service Control Manager | ID = 7034
Description = The Windows Management Instrumentation service terminated unexpectedly.
It has done this 7 time(s).

Error - 4/13/2011 2:25:11 PM | Computer Name = RNS-PC | Source = EventLog | ID = 6008
Description = The previous system shutdown at 11:23:44 AM on ?4/?13/?2011 was unexpected.

Error - 4/13/2011 2:25:12 PM | Computer Name = RNS-PC | Source = BugCheck | ID = 1001
Description =

Error - 4/13/2011 2:25:14 PM | Computer Name = RNS-PC | Source = Service Control Manager | ID = 7000
Description = The Nsynas32 service failed to start due to the following error: %%2

Error - 4/13/2011 2:25:17 PM | Computer Name = RNS-PC | Source = Microsoft-Windows-DNS-Client | ID = 1012
Description = There was an error while attempting to read the local hosts file.

Error - 4/13/2011 2:25:34 PM | Computer Name = RNS-PC | Source = Microsoft-Windows-DNS-Client | ID = 1012
Description = There was an error while attempting to read the local hosts file.

Error - 4/13/2011 4:17:56 PM | Computer Name = RNS-PC | Source = Microsoft-Windows-DNS-Client | ID = 1012
Description = There was an error while attempting to read the local hosts file.

Error - 4/13/2011 4:17:56 PM | Computer Name = RNS-PC | Source = Microsoft-Windows-DNS-Client | ID = 1012
Description = There was an error while attempting to read the local hosts file.


< End of report >
I was hoping the virus wasn't that bad;(…I really appreciate your help, I wish I could reinstall windows but at the moment it will be devastating cause I have many unfinished music sessions and the preferences, presets and 3rd party plugins and the audio files are all over the hard drives, any change of settings could make me loose a lot of work. Fortunately I don't use this pc for bankin and stuff. So my goal is to get it as clean as possible until i'm ready to reinstall… Thanks!
Hi Nightsight,


It's ok, thank you for the logs.


You are using peer-to-peer programs, specifically uTorrent. These are what we call an optional removal. However, anytime you are running any type of peer-to-peer application, you are more prone to infection by malware, and this is probably how you became infected in the first place. The choice to remove them is entirely up to you, but I would strongly recommend that you do. If you do not want to, please at least refrain from using any peer-to-peer programs for the remainder of my fix.


Please do the following:


Please double click the aswMBR icon to run it.
Vista and Windows 7 users right click the icon and choose "Run as administrator".

  • Click the Scan button to start scan.
  • When scan finishes, press the Fix Button. Once the Fix is done, press the Save Log button and save the log to your desktop. You need to reboot your computer when its done before you do anything else, then post the log that will be on your desktop.

[external image: Posted Image]
Click the image to enlarge it
aswMBR version 0.9.4 Copyright© 2011 AVAST Software Run date: 2011-04-11 14:18:42 —————————– 14:18:42.632 OS Version: Windows 6.1.7600 14:18:42.632 Number of processors: 8 586 0x1A05 14:18:42.632 ComputerName: RNS-PC UserName: RNS 14:18:44.125 Initialize success 14:18:56.625 Disk 0 \Device\Harddisk0\DR0 -> \Device\Ide\IdeDeviceP0T0L0-0 14:18:56.627 Disk 0 Vendor: ST31000528AS 0953 Size: 953869MB BusType: 3 14:18:56.630 Disk 1 (boot) \Device\Harddisk1\DR1 -> \Device\Ide\IdePort2 14:18:56.632 Disk 1 Vendor: ST31000528AS CC38 Size: 953869MB BusType: 3 14:18:56.635 Device \Device\Ide\IdeDeviceP2T0L0-3 -> \??\IDE#DiskST31000528AS____________________________CC38____#5&3007a5e1&0&0.0.0#{53f56307-b6bf-11d0-94f2-00a0c91efb8b} not found 14:18:58.639 Disk 1 MBR read successfully 14:18:58.643 Disk 1 MBR scan 14:18:58.647 Disk 1 TDL4@MBR code has been found 14:18:58.651 Disk 1 MBR hidden 14:18:58.655 Disk 1 MBR [TDL4] **ROOTKIT** 14:18:58.660 Disk 1 trace - called modules: 14:18:58.665 ntoskrnl.exe CLASSPNP.SYS disk.sys ACPI.sys halmacpi.dll >>UNKNOWN [0x869a7439]<< 14:18:58.670 1 nt!IofCallDriver -> \Device\Harddisk1\DR1[0x8697f8e8] 14:18:58.676 3 CLASSPNP.SYS[8c67d59e] -> nt!IofCallDriver -> [0x867d6918] 14:18:58.682 5 ACPI.sys[83a3b3b2] -> nt!IofCallDriver -> \IdeDeviceP2T0L0-3[0x867ff030] 14:18:58.688 \Driver\atapi[0x86980510] -> IRP_MJ_CREATE -> 0x869a7439 14:18:58.695 Scan finished successfully aswMBR version 0.9.4 Copyright© 2011 AVAST Software Run date: 2011-04-15 01:37:59 —————————– 01:37:59.687 OS Version: Windows 6.1.7600 01:37:59.687 Number of processors: 8 586 0x1A05 01:37:59.687 ComputerName: RNS-PC UserName: RNS 01:38:05.147 Initialize success 01:38:32.232 Disk 0 \Device\Harddisk0\DR0 -> \Device\Ide\IdeDeviceP0T0L0-0 01:38:32.233 Disk 0 Vendor: ST31000528AS 0953 Size: 953869MB BusType: 3 01:38:32.235 Disk 1 (boot) \Device\Harddisk1\DR1 -> \Device\Ide\IdePort2 01:38:32.236 Disk 1 Vendor: ST31000528AS CC38 Size: 953869MB BusType: 3 01:38:32.238 Device \Device\Ide\IdeDeviceP2T0L0-3 -> \??\IDE#DiskST31000528AS____________________________CC38____#5&3007a5e1&0&0.0.0#{53f56307-b6bf-11d0-94f2-00a0c91efb8b} not found 01:38:34.240 Disk 1 MBR read successfully 01:38:34.244 Disk 1 MBR scan 01:38:34.248 Disk 1 TDL4@MBR code has been found 01:38:34.252 Disk 1 MBR hidden 01:38:34.256 Disk 1 MBR [TDL4] **ROOTKIT** 01:38:34.261 Disk 1 trace - called modules: 01:38:34.264 ntoskrnl.exe CLASSPNP.SYS disk.sys ACPI.sys halmacpi.dll >>UNKNOWN [0x869a7439]<< 01:38:34.267 1 nt!IofCallDriver -> \Device\Harddisk1\DR1[0x8697f5e0] 01:38:34.270 3 CLASSPNP.SYS[8c65659e] -> nt!IofCallDriver -> [0x8681e918] 01:38:34.284 5 ACPI.sys[83a293b2] -> nt!IofCallDriver -> \IdeDeviceP2T0L0-3[0x8680c030] 01:38:34.288 \Driver\atapi[0x86983f38] -> IRP_MJ_CREATE -> 0x869a7439 01:38:34.291 Scan finished successfully 01:38:55.712 Disk 1 fixing MBR 01:39:05.720 Disk 1 MBR restored successfully 01:39:05.724 Infection fixed successfully - please reboot ASAP
Please download Combofix from either of the links below and save it to your desktop.

Link 1
Link 2


**Note: It is important that it is saved directly to your desktop**

——————————————————————–
IMPORTANT - Disable your AntiVirus and AntiSpyware applications, usually via a right click on the System Tray icon. They may otherwise interfere with our tools. If you have difficulty properly disabling your protective programs, refer to this link here
——————————————————————–

  • Right-click and choose "Run as administrator" on Combofix & follow the prompts. When finished, it will produce a report for you.
  • As part of it's process, ComboFix will check to see if the Microsoft Windows Recovery Console is installed. With malware infections being as they are today, it's strongly recommended to have this pre-installed on your machine before doing any malware removal. It will allow you to boot up into a special recovery/repair mode that will allow us to more easily help you should your computer have a problem after an attempted removal of malware.
  • Follow the prompts to allow ComboFix to download and install the Microsoft Windows Recovery Console, and when prompted, agree to the End-User License Agreement to install the Microsoft Windows Recovery Console.
**Please note: If the Microsoft Windows Recovery Console is already installed, ComboFix will continue it's malware removal procedures.

[external image: Posted Image]


  • Once the Microsoft Windows Recovery Console is installed using ComboFix, you should see the following message:

[external image: Posted Image]


  • Click on Yes, to continue scanning for malware.
  • When finished, it will produce a log for you. Please include the C:\ComboFix.txt in your next reply.

If you need help, see this link:
http://www.bleepingcomputer.com/combofix/how-to-use-combofix
ComboFix 11-04-14.03 - RNS 04/16/2011 1:15.1.8 - x86 Microsoft Windows 7 Ultimate 6.1.7600.0.1252.1.1033.18.3062.2029 [GMT -7:00] Running from: c:\users\[removed]\Desktop\ComboFix.exe AV: Microsoft Security Essentials *Disabled/Updated* {108DAC43-C256-20B7-BB05-914135DA5160} SP: Microsoft Security Essentials *Disabled/Updated* {ABEC4DA7-E46C-2F39-81B5-AA334E5D1BDD} SP: Windows Defender *Disabled/Outdated* {D68DDC3A-831F-4fae-9E44-DA132C1ACF46} * Created a new restore point . . ((((((((((((((((((((((((((((((((((((((( Other Deletions ))))))))))))))))))))))))))))))))))))))))))))))))) . . c:\users\RNS\AppData\Local\akaxayug.dll c:\windows\57756.exe . . ((((((((((((((((((((((((( Files Created from 2011-03-16 to 2011-04-16 ))))))))))))))))))))))))))))))) . . 2011-04-16 08:20 . 2011-04-16 08:20 ——– d—–w- c:\users\Default\AppData\Local\temp 2011-04-16 08:13 . 2011-04-16 08:13 ——– d—–w- C:\32788R22FWJFW 2011-04-15 08:04 . 2011-03-23 17:11 6792528 —-a-w- c:\programdata\Microsoft\Microsoft Antimalware\Definition Updates\{CD56772B-EB53-4B28-A35D-D835F0087E14}\mpengine.dll 2011-04-14 22:07 . 2011-04-14 22:07 ——– d—–w- c:\users\RNS\AppData\Local\{42B4EF6B-CF6D-4A12-B0BB-925F8B63627B} 2011-04-08 23:48 . 2011-04-08 23:48 ——– d—–w- c:\users\RNS\AppData\Local\{F889C204-4786-4501-991B-EE83912B6F7A} 2011-04-08 20:41 . 2011-04-08 20:41 ——– d—–w- c:\users\Default\AppData\Local\Apple Computer 2011-04-08 20:41 . 2011-04-08 20:41 ——– d—–w- c:\users\Default\AppData\Roaming\Apple Computer 2011-04-08 19:38 . 2011-04-08 19:38 ——– d—–w- c:\program files\COMODO 2011-04-08 19:33 . 2010-11-30 18:43 439632 —-a-w- c:\programdata\Microsoft\Microsoft Antimalware\Definition Updates\NISBackup\gapaengine.dll 2011-04-08 19:33 . 2010-11-30 18:43 439632 —-a-w- c:\programdata\Microsoft\Microsoft Antimalware\Definition Updates\{B205184F-14BF-40E8-BF9B-FBE57257EB1D}\gapaengine.dll 2011-04-08 19:32 . 2011-03-23 17:11 6792528 —-a-w- c:\programdata\Microsoft\Microsoft Antimalware\Definition Updates\Backup\mpengine.dll 2011-04-05 07:18 . 2011-04-05 07:18 ——– d—–w- c:\users\RNS\AppData\Roaming\SUPERAntiSpyware.com 2011-04-05 07:18 . 2011-04-05 07:18 ——– d—–w- c:\programdata\SUPERAntiSpyware.com 2011-04-05 07:14 . 2011-04-08 19:38 ——– d—–w- c:\program files\SUPERAntiSpyware 2011-04-04 22:00 . 2011-04-04 22:00 ——– d—–w- c:\users\RNS\AppData\Local\{8883D476-BF69-4B53-827D-4FBC02AB6C04} 2011-04-02 05:52 . 2011-04-02 05:52 ——– d—–w- c:\users\RNS\AppData\Roaming\Malwarebytes 2011-04-02 05:52 . 2010-12-21 01:09 38224 —-a-w- c:\windows\system32\drivers\mbamswissarmy.sys 2011-04-02 05:52 . 2011-04-02 05:52 ——– d—–w- c:\programdata\Malwarebytes 2011-04-02 05:52 . 2011-04-02 05:52 ——– d—–w- c:\program files\Malwarebytes' Anti-Malware 2011-04-02 05:52 . 2010-12-21 01:08 20952 —-a-w- c:\windows\system32\drivers\mbam.sys 2011-04-02 01:55 . 2011-04-02 01:55 ——– d—–w- c:\users\RNS\AppData\Roaming\TrojanHunter 2011-04-02 00:37 . 2011-04-02 01:56 ——– d—–w- c:\program files\TrojanHunter 5.3 2011-04-01 23:32 . 2011-04-01 23:47 ——– d—–w- c:\programdata\Spybot - Search & Destroy 2011-04-01 23:32 . 2011-04-01 23:33 ——– d—–w- c:\program files\Spybot - Search & Destroy 2011-04-01 22:31 . 2011-04-01 22:31 ——– d—–w- c:\program files\Microsoft Security Client 2011-04-01 22:31 . 2010-04-09 07:24 1285000 —-a-w- c:\windows\system32\drivers\tcpip.sys 2011-04-01 22:31 . 2010-04-09 07:24 240008 —-a-w- c:\windows\system32\drivers\netio.sys 2011-04-01 22:00 . 2011-04-01 22:00 98392 —-a-w- c:\windows\system32\drivers\SBREDrv.sys 2011-04-01 20:49 . 2011-04-08 19:36 ——– d—–w- c:\programdata\Lavasoft 2011-04-01 20:10 . 2011-04-01 20:10 ——– d—–w- c:\users\RNS\AppData\Local\{8254B4F4-0814-4AA3-A2F4-4DFA97A2F9FD} 2011-04-01 19:35 . 2011-04-01 19:35 ——– d—–w- c:\users\RNS\AppData\Local\{AE5D8B17-DA29-4E35-968B-7EA948EA2BAD} 2011-04-01 19:34 . 2011-04-01 19:56 ——– d—–w- c:\programdata\MFAData 2011-04-01 19:29 . 2011-04-01 19:29 ——– d—–w- c:\users\RNS\AppData\Roaming\Waves Audio 2011-03-30 18:49 . 2011-03-30 18:49 ——– d—–w- c:\users\RNS\AppData\Local\{B1B7536E-0DD8-4439-8E99-70A8E66D1734} 2011-03-30 06:48 . 2011-03-30 06:49 ——– d—–w- c:\users\RNS\AppData\Local\{804B2304-02FC-4948-A8A5-FF3627202746} 2011-03-29 18:48 . 2011-03-29 18:48 ——– d—–w- c:\users\RNS\AppData\Local\{92205DA8-C505-445B-955C-6644972E8B02} 2011-03-29 06:47 . 2011-03-29 06:48 ——– d—–w- c:\users\RNS\AppData\Local\{78C71C97-0A08-4AD9-BEC0-CB5253C6BE8D} 2011-03-28 18:47 . 2011-03-28 18:47 ——– d—–w- c:\users\RNS\AppData\Local\{2BF69A3F-CE2B-49B4-BB7E-0EDE494A3322} 2011-03-23 22:47 . 2011-03-23 22:48 ——– d—–w- c:\users\RNS\AppData\Local\{49DAC749-60EF-4986-B17F-5B51B73AF910} 2011-03-23 10:47 . 2011-03-23 10:47 ——– d—–w- c:\users\RNS\AppData\Local\{3E206A6B-9510-442C-89E9-5877B6F49B3D} 2011-03-22 22:47 . 2011-03-22 22:47 ——– d—–w- c:\users\RNS\AppData\Local\{898B7304-1063-4919-B960-761F25204244} 2011-03-21 22:33 . 2011-03-22 10:34 ——– d—–w- c:\users\RNS\AppData\Local\{1E277148-96B2-4A24-8AA9-A275F171E237} 2011-03-18 05:19 . 2011-03-18 05:19 ——– d—–w- c:\users\RNS\AppData\Local\{0E78C31C-32A5-4C9D-B20D-7311E4EF57C4} . . . (((((((((((((((((((((((((((((((((((((((( Find3M Report )))))))))))))))))))))))))))))))))))))))))))))))))))) . 2011-03-10 01:58 . 2010-06-24 19:33 18328 —-a-w- c:\programdata\Microsoft\IdentityCRL\production\ppcrlconfig600.dll 2011-01-30 08:33 . 2011-01-30 08:33 1228579 —-a-w- c:\windows\LightWave 3D 9 Uninstaller.exe 2011-01-20 04:15 . 2011-01-20 04:16 472808 —-a-w- c:\windows\system32\deployJava1.dll 2009-11-20 05:08 . 2009-11-20 05:08 3749224 —-a-w- c:\program files\Common Files\adlmint_libFNP.dll 2009-11-20 05:08 . 2009-11-20 05:08 2941288 —-a-w- c:\program files\Common Files\adlmint.dll 2011-03-18 17:53 . 2011-04-06 03:05 142296 —-a-w- c:\program files\mozilla firefox\components\browsercomps.dll . . ((((((((((((((((((((((((((((((((((((( Reg Loading Points )))))))))))))))))))))))))))))))))))))))))))))))))) . . *Note* empty entries & legit default entries are not shown REGEDIT4 . [HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "Sony Ericsson PC Companion"="c:\program files\Sony Ericsson\Sony Ericsson PC Companion\PCCompanion.exe" [2009-12-08 774144] "SpybotSD TeaTimer"="c:\program files\Spybot - Search & Destroy\TeaTimer.exe" [2009-03-05 2260480] . [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "StartCCC"="c:\program files\ATI Technologies\ATI.ACE\Core-Static\CLIStart.exe" [2010-10-27 98304] "RtHDVCpl"="c:\program files\Realtek\Audio\HDA\RtHDVCpl.exe" [2009-03-24 7289376] "M-Audio Taskbar Icon"="c:\windows\system32\MAFWTray.exe" [2009-07-29 252424] "Google Desktop Search"="c:\program files\Google\Google Desktop Search\GoogleDesktop.exe" [2010-12-07 30192] "AdobeCS4ServiceManager"="c:\program files\Common Files\Adobe\CS4ServiceManager\CS4ServiceManager.exe" [2008-08-14 611712] "Adobe Acrobat Speed Launcher"="c:\program files\Adobe\Acrobat 9.0\Acrobat\Acrobat_sl.exe" [2008-06-12 37232] "Acrobat Assistant 8.0"="c:\program files\Adobe\Acrobat 9.0\Acrobat\Acrotray.exe" [2008-06-12 640376] "QuickTime Task"="c:\program files\K-Lite Codec Pack\QuickTime\QTTask.exe" [2010-11-30 421888] "iTunesHelper"="c:\program files\iTunes\iTunesHelper.exe" [2010-12-14 421160] "SunJavaUpdateSched"="c:\program files\Common Files\Java\Java Update\jusched.exe" [2010-05-14 248552] "MSC"="c:\program files\Microsoft Security Client\msseces.exe" [2010-11-30 997408] . c:\users\RNS\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\ MagicDisc.lnk - c:\program files\MagicDisc\MagicDisc.exe [2010-12-6 576000] . [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\policies\system] "ConsentPromptBehaviorAdmin"= 0 (0x0) "ConsentPromptBehaviorUser"= 3 (0x3) "EnableLUA"= 0 (0x0) "EnableUIADesktopToggle"= 0 (0x0) "PromptOnSecureDesktop"= 0 (0x0) . [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\windows] "AppInit_DLLs"=c:\progra~1\Google\GOOGLE~1\GoogleDesktopNetwork3.dll . [HKEY_LOCAL_MACHINE\system\currentcontrolset\control\lsa] Security Packages REG_MULTI_SZ kerberos msv1_0 schannel wdigest tspkg pku2u livessp . [HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Lavasoft Ad-Aware Service] @="" . [HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\MsMpSvc] @="Service" . R3 A3AB;D-Link AirPro 802.11a/b Wireless Adapter Service(A3AB);c:\windows\system32\DRIVERS\A3AB.sys [2005-03-23 450400] R3 Adobe Version Cue CS4;Adobe Version Cue CS4;c:\program files\Common Files\Adobe\Adobe Version Cue CS4\Server\bin\VersionCueCS4.exe [2008-08-15 284016] R3 GoogleDesktopManager-051210-111108;Google Desktop Manager 5.9.1005.12335;c:\program files\Google\Google Desktop Search\GoogleDesktop.exe [2010-12-07 30192] R3 MpNWMon;Microsoft Malware Protection Network Driver;c:\windows\system32\DRIVERS\MpNWMon.sys [2010-10-25 43392] R3 NisDrv;Microsoft Network Inspection System;c:\windows\system32\DRIVERS\NisDrvWFP.sys [2010-10-25 54144] R3 NisSrv;Microsoft Network Inspection;c:\program files\Microsoft Security Client\Antimalware\NisSrv.exe [2010-11-11 206360] R3 s1018bus;Sony Ericsson Device 1018 driver (WDM);c:\windows\system32\DRIVERS\s1018bus.sys [2009-03-25 86824] R3 s1018mdfl;Sony Ericsson Device 1018 USB WMC Modem Filter;c:\windows\system32\DRIVERS\s1018mdfl.sys [2009-03-25 15016] R3 s1018mdm;Sony Ericsson Device 1018 USB WMC Modem Driver;c:\windows\system32\DRIVERS\s1018mdm.sys [2009-03-25 114728] R3 s1018mgmt;Sony Ericsson Device 1018 USB WMC Device Management Drivers (WDM);c:\windows\system32\DRIVERS\s1018mgmt.sys [2009-03-25 106208] R3 s1018nd5;Sony Ericsson Device 1018 USB Ethernet Emulation (NDIS);c:\windows\system32\DRIVERS\s1018nd5.sys [2009-03-25 26024] R3 s1018obex;Sony Ericsson Device 1018 USB WMC OBEX Interface;c:\windows\system32\DRIVERS\s1018obex.sys [2009-03-25 104744] R3 s1018unic;Sony Ericsson Device 1018 USB Ethernet Emulation (WDM);c:\windows\system32\DRIVERS\s1018unic.sys [2009-03-25 109864] R3 wacmoumonitor;Wacom Mode Helper;c:\windows\system32\DRIVERS\wacmoumonitor.sys [2010-11-03 10752] S1 SASDIFSV;SASDIFSV;c:\program files\SUPERAntiSpyware\SASDIFSV.SYS [2010-02-17 12872] S1 SASKUTIL;SASKUTIL;c:\program files\SUPERAntiSpyware\SASKUTIL.SYS [2010-05-10 67656] S1 vwififlt;Virtual WiFi Filter Driver;c:\windows\system32\DRIVERS\vwififlt.sys [2009-07-13 48128] S2 AMD External Events Utility;AMD External Events Utility;c:\windows\system32\atiesrxx.exe [2010-10-27 176128] S2 SBSDWSCService;SBSD Security Center Service;c:\program files\Spybot - Search & Destroy\SDWinSec.exe [2009-01-26 1153368] S2 TabletServiceWacom;TabletServiceWacom;c:\program files\Tablet\Wacom\Wacom_Tablet.exe [2010-11-15 4807536] S3 amdkmdag;amdkmdag;c:\windows\system32\DRIVERS\atikmdag.sys [2010-10-27 6573568] S3 amdkmdap;amdkmdap;c:\windows\system32\DRIVERS\atikmpag.sys [2010-10-27 229888] S3 AtiHDAudioService;ATI Function Driver for HD Audio Service;c:\windows\system32\drivers\AtihdW73.sys [2010-09-25 102416] S3 CLEDX;Team H2O CLEDX service;c:\windows\system32\DRIVERS\cledx.sys [2005-05-10 33792] S3 MAFW;Service for M-Audio FireWire;c:\windows\system32\DRIVERS\mafw.sys [2009-07-29 192392] S3 RTL8167;Realtek 8167 NT Driver;c:\windows\system32\DRIVERS\Rt86win7.sys [2009-07-13 139776] . . [HKEY_LOCAL_MACHINE\software\microsoft\active setup\installed components\{10880D85-AAD9-4558-ABDC-2AB1552D831F}] 2009-08-20 21:24 451872 —-a-w- c:\program files\Common Files\LightScribe\LSRunOnce.exe . Contents of the 'Scheduled Tasks' folder . . ——- Supplementary Scan ——- . uStart Page = hxxp://www.musicradar.com/computermusic uInternet Settings,ProxyOverride = *.local uSearchURL,(Default) = hxxp://www.google.com/search/?q=%s IE: Append Link Target to Existing PDF - c:\program files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIEAppendSelLinks.html IE: Append to Existing PDF - c:\program files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIEAppend.html IE: Convert Link Target to Adobe PDF - c:\program files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIECaptureSelLinks.html IE: Convert to Adobe PDF - c:\program files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIECapture.html FF - ProfilePath - c:\users\RNS\AppData\Roaming\Mozilla\Firefox\Profiles\ehuykxlg.default\ FF - prefs.js: browser.startup.homepage - hxxp://www.musicradar.com/computermusic . - - - - ORPHANS REMOVED - - - - . HKCU-Run-4E3E0230868C0F5D - c:\calc.bin\Calc.Bin.exe HKLM-Run-H2O - c:\program files\SyncroSoft\Pos\H2O\cledx.exe AddRemove-EyeCandy5Impact - c:\progra~1\ALIENS~1\EYECAN~1\Unwise32.exe AddRemove-Rob Papen BLUE Version 1.7.0_is1 - c:\program files\steinberg\vstplugins\unins001.exe AddRemove-SubBoomBass_is1 - c:\program files\steinberg\vstplugins\unins002.exe . . . ——————— LOCKED REGISTRY KEYS ——————— . [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0000\AllUserSettings] @Denied: (A) (Users) @Denied: (A) (Everyone) @Allowed: (B 1 2 3 4 5) (S-1-5-20) "BlindDial"=dword:00000000 . [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0001\AllUserSettings] @Denied: (A) (Users) @Denied: (A) (Everyone) @Allowed: (B 1 2 3 4 5) (S-1-5-20) "BlindDial"=dword:00000000 . [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\PCW\Security] @Denied: (Full) (Everyone) . Completion time: 2011-04-16 01:21:23 ComboFix-quarantined-files.txt 2011-04-16 08:21 . Pre-Run: 144,081,227,776 bytes free Post-Run: 144,187,682,816 bytes free . - - End Of File - - 5A85D442F720DF141FC3B9798175C197
Hi Nightsight,


There's still more to do. Please go to the following site to scan a file: Virus Total

  • Click on Browse, and upload the following file for analysis:

    • c:\program files\Common Files\adlmint_libFNP.dll
      c:\program files\Common Files\adlmint.dll
  • Then click Submit. Allow the file to be scanned, and then please copy and paste the results here for me to see.
  • If it says already scanned – click "reanalyze now"
  • Please post the results in your next reply.
I'm confused, there's is UPLOAD (a file) and SUBMIT is for URL's I believe you want to me to Upload and press "SEND FILE" since there's is no "SUBMIT" under "Upload A file" I'm I correct?

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI