manicd
Topic Starter
Hi
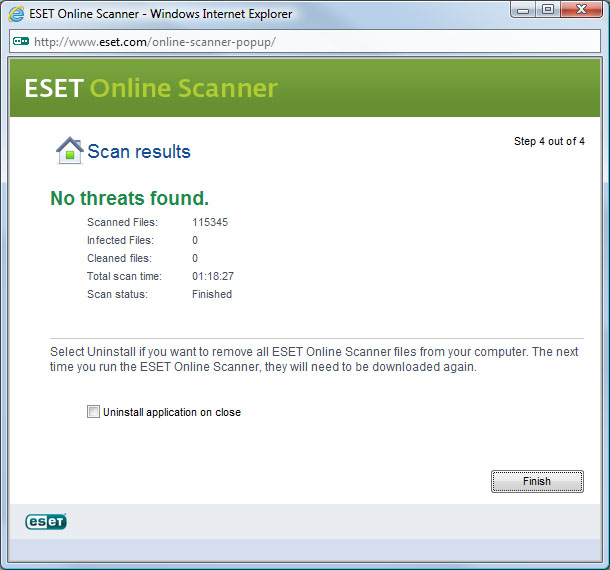
Ive just this minute updated & installed the latest version of Java (Version 6 Update 24) & Nod has flagged up the following infection: Java.OpenConnection.dm which at present is causing no noticeable problems.
This is the third or fourth time this has happened when installing Java & as unlikely as this sounds but does the Java download contain this Trojan?
Sun\Java\Deployment\cache\6.0\62
Jotti Scan
Thank You.
OTL.txt
EXTRAS.txt
Ive just this minute updated & installed the latest version of Java (Version 6 Update 24) & Nod has flagged up the following infection: Java.OpenConnection.dm which at present is causing no noticeable problems.
This is the third or fourth time this has happened when installing Java & as unlikely as this sounds but does the Java download contain this Trojan?
Sun\Java\Deployment\cache\6.0\62
Jotti Scan
Thank You.
OTL.txt
OTL logfile created on: 01/04/2011 00:41:45 - Run 1
OTL by OldTimer - Version 3.2.22.3	 Folder = C:\Users\Dan\Desktop
Windows Vista Home Basic Edition Service Pack 2 (Version = 6.0.6002) - Type = NTWorkstation
Internet Explorer (Version = 9.0.8112.16421)
Locale: 00000809 | Country: United Kingdom | Language: ENG | Date Format: dd/MM/yyyy

3.00 Gb Total Physical Memory | 1.00 Gb Available Physical Memory | 49.00% Memory free
6.00 Gb Paging File | 5.00 Gb Available in Paging File | 77.00% Paging File free
Paging file location(s): ?:\pagefile.sys [binary data]

%SystemDrive% = C: | %SystemRoot% = C:\Windows | %ProgramFiles% = C:\Program Files
Drive C: | 69.52 Gb Total Space | 19.94 Gb Free Space | 28.67% Space Free | Partition Type: NTFS
Drive D: | 69.53 Gb Total Space | 69.44 Gb Free Space | 99.87% Space Free | Partition Type: NTFS
Drive H: | 1.92 Gb Total Space | 1.91 Gb Free Space | 99.40% Space Free | Partition Type: FAT
Drive I: | 698.64 Gb Total Space | 168.04 Gb Free Space | 24.05% Space Free | Partition Type: NTFS

Computer Name: DAN-PC | User Name: Dan | Logged in as Administrator.
Boot Mode: Normal | Scan Mode: Current user
Company Name Whitelist: Off | Skip Microsoft Files: Off | No Company Name Whitelist: On | File Age = 30 Days

========== Processes (SafeList) ==========

PRC - C:\Users\Dan\Desktop\OTL.exe (OldTimer Tools)
PRC - C:\Program Files\Malwarebytes' Anti-Malware\mbamservice.exe (Malwarebytes Corporation)
PRC - C:\Program Files\Malwarebytes' Anti-Malware\mbamgui.exe (Malwarebytes Corporation)
PRC - C:\Program Files\Common Files\Autodesk Shared\Service\AdskScSrv.exe (Autodesk)
PRC - C:\Program Files\TomTom HOME 2\TomTomHOMEService.exe (TomTom)
PRC - C:\Program Files\BillP Studios\WinPatrol\WinPatrol.exe (BillP Studios)
PRC - C:\Windows\explorer.exe (Microsoft Corporation)
PRC - C:\Program Files\ESET\ESET Smart Security\ekrn.exe (ESET)
PRC - C:\Program Files\ESET\ESET Smart Security\egui.exe (ESET)
PRC - C:\Program Files\Acronis\TrueImageHome\TimounterMonitor.exe (Acronis)
PRC - C:\Program Files\Common Files\Acronis\Schedule2\schedhlp.exe (Acronis)
PRC - C:\Program Files\Common Files\Acronis\Schedule2\schedul2.exe (Acronis)
PRC - C:\Program Files\Acronis\TrueImageHome\TrueImageMonitor.exe (Acronis)
PRC - C:\Program Files\Intel\Intel Matrix Storage Manager\IAANTmon.exe (Intel Corporation)
PRC - C:\Program Files\Intel\Intel Matrix Storage Manager\IAAnotif.exe (Intel Corporation)
PRC - C:\Program Files\Launch Manager\QtZgAcer.EXE (Dritek System Inc.)
PRC - C:\Program Files\Acer\Empowering Technology\Service\ETService.exe ()
PRC - C:\Windows\System32\agrsmsvc.exe (Agere Systems)
PRC - C:\Program Files\Autodesk\3ds Max 2009\mentalray\satellite\raysat_3dsMax2009_32server.exe ()
PRC - C:\Program Files\Acer\Empowering Technology\eDataSecurity\x86\eDSService.exe (Egis Incorporated)
PRC - C:\Program Files\Windows Defender\MSASCui.exe (Microsoft Corporation)
PRC - C:\ACER\Mobility Center\MobilityService.exe ()
PRC - C:\Windows\PLFSetI.exe ()


========== Modules (SafeList) ==========

MOD - C:\Users\Dan\Desktop\OTL.exe (OldTimer Tools)
MOD - C:\Windows\winsxs\x86_microsoft.windows.common-controls_6595b64144ccf1df_6.0.6002.18305_none_5cb72f2a088b0ed3\comctl32.dll (Microsoft Corporation)


========== Win32 Services (SafeList) ==========

SRV - (nosGetPlusHelper) getPlus(R) – C:\Program Files\NOS\bin\getPlus_Helper_3004.dll (NOS Microsystems Ltd.)
SRV - (MBAMService) – C:\Program Files\Malwarebytes' Anti-Malware\mbamservice.exe (Malwarebytes Corporation)
SRV - (Autodesk Licensing Service) – C:\Program Files\Common Files\Autodesk Shared\Service\AdskScSrv.exe (Autodesk)
SRV - (TomTomHOMEService) – C:\Program Files\TomTom HOME 2\TomTomHOMEService.exe (TomTom)
SRV - (EhttpSrv) – C:\Program Files\ESET\ESET Smart Security\EHttpSrv.exe (ESET)
SRV - (ekrn) – C:\Program Files\ESET\ESET Smart Security\ekrn.exe (ESET)
SRV - (AcrSch2Svc) – C:\Program Files\Common Files\Acronis\Schedule2\schedul2.exe (Acronis)
SRV - (IAANTMON) Intel(R) – C:\Program Files\Intel\Intel Matrix Storage Manager\IAANTmon.exe (Intel Corporation)
SRV - (ETService) – C:\Program Files\Acer\Empowering Technology\Service\ETService.exe ()
SRV - (AgereModemAudio) – C:\Windows\System32\agrsmsvc.exe (Agere Systems)
SRV - (mi-raysat_3dsMax2009_32) – C:\Program Files\Autodesk\3ds Max 2009\mentalray\satellite\raysat_3dsMax2009_32server.exe ()
SRV - (eDataSecurity Service) – C:\Program Files\Acer\Empowering Technology\eDataSecurity\x86\eDSService.exe (Egis Incorporated)
SRV - (WinDefend) – C:\Program Files\Windows Defender\MpSvc.dll (Microsoft Corporation)
SRV - (MobilityService) – C:\Acer\Mobility Center\MobilityService.exe ()
SRV - (AcronisOSSReinstallSvc) – C:\Program Files\Common Files\Acronis\Acronis Disk Director\oss_reinstall_svc.exe ()


========== Driver Services (SafeList) ==========

DRV - (sptd) – C:\Windows\System32\Drivers\sptd.sys ()
DRV - (MBAMProtector) – C:\Windows\System32\drivers\mbam.sys (Malwarebytes Corporation)
DRV - (tdrpman174) Acronis Try&Decide and Restore Points filter (build 174) – C:\Windows\system32\DRIVERS\tdrpm174.sys (Acronis)
DRV - (timounter) – C:\Windows\system32\DRIVERS\timntr.sys (Acronis)
DRV - (tifsfilter) – C:\Windows\System32\drivers\tifsfilt.sys (Acronis)
DRV - (snapman380) Acronis Snapshots Manager (Build 380) – C:\Windows\system32\DRIVERS\snman380.sys (Acronis)
DRV - (epfwwfp) – C:\Windows\System32\drivers\epfwwfp.sys (ESET)
DRV - (Epfwndis) – C:\Windows\System32\drivers\epfwndis.sys (ESET)
DRV - (epfw) – C:\Windows\System32\drivers\epfw.sys (ESET)
DRV - (ehdrv) – C:\Windows\System32\drivers\ehdrv.sys (ESET)
DRV - (eamon) – C:\Windows\System32\drivers\eamon.sys (ESET)
DRV - (IntcHdmiAddService) Intel(R) – C:\Windows\System32\drivers\IntcHdmi.sys (Intel(R) Corporation)
DRV - (ISODrive) – C:\Program Files\UltraISO\drivers\ISODrive.sys (EZB Systems, Inc.)
DRV - (NETw5v32) Intel(R) – C:\Windows\System32\drivers\NETw5v32.sys (Intel Corporation)
DRV - (JMCR) – C:\Windows\System32\drivers\jmcr.sys (JMicron Technology Corp.)
DRV - (A310) – C:\Windows\System32\drivers\AVerA310USB.sys (AVerMedia TECHNOLOGIES, Inc.)
DRV - (BDASwCap) – C:\Windows\System32\drivers\AVerA310Cap.sys (AVerMedia TECHNOLOGIES, Inc.)
DRV - (int15) – C:\Windows\System32\drivers\int15.sys (Acer, Inc.)
DRV - (AgereSoftModem) – C:\Windows\System32\drivers\AGRSM.sys (Agere Systems)
DRV - (WSVD) – C:\Windows\System32\drivers\WSVD.sys (Wasay)
DRV - (winbondcir) – C:\Windows\System32\drivers\winbondcir.sys (Winbond Electronics Corporation)


========== Standard Registry (SafeList) ==========


========== Internet Explorer ==========

IE - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = http://homepage.acer.com/rdr.aspx?b=ACAW&l=0809&s=2&o=vb32&d=0710&m=aspire_7730
IE - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://homepage.acer.com/rdr.aspx?b=ACAW&l=0809&s=2&o=vb32&d=0710&m=aspire_7730

IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = http://homepage.acer.com/rdr.aspx?b=ACAW&l=0809&s=2&o=vb32&d=0710&m=aspire_7730
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Secondary_Page_URL = http://global.acer.com [binary data]
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,SearchDefaultBranded = 1
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://homepage.acer.com/rdr.aspx?b=ACAW&l=0809&s=2&o=vb32&d=0710&m=aspire_7730
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,StartPageCache = 1
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyEnable" = 0
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyOverride" = *.local

========== FireFox ==========


FF - HKLM\software\mozilla\Mozilla Firefox 3.6.16\extensions\\Components: C:\Program Files\Firefox 3.6.16\components [2011/03/31 19:52:29 | 000,000,000 | —D | M]
FF - HKLM\software\mozilla\Mozilla Firefox 3.6.16\extensions\\Plugins: C:\Program Files\Firefox 3.6.16\plugins [2011/03/31 23:14:26 | 000,000,000 | —D | M]
FF - HKLM\software\mozilla\Mozilla Firefox 4.0\extensions\\Components: C:\Program Files\Mozilla Firefox\components [2011/03/30 22:40:17 | 000,000,000 | —D | M]
FF - HKLM\software\mozilla\Mozilla Firefox 4.0\extensions\\Plugins: C:\Program Files\Mozilla Firefox\plugins
FF - HKLM\software\mozilla\Thunderbird\Extensions\\[removed]: C:\Program Files\ESET\ESET Smart Security\Mozilla Thunderbird [2010/09/05 01:51:57 | 000,000,000 | —D | M]

[2011/03/29 19:55:23 | 000,000,000 | —D | M] (No name found) – C:\Users\Dan\AppData\Roaming\Mozilla\Extensions
[2011/03/31 22:14:49 | 000,000,000 | —D | M] (No name found) – C:\Users\Dan\AppData\Roaming\Mozilla\Firefox\Profiles\fmc69kie.Firefox3.6.16\extensions
[2011/03/31 21:33:57 | 000,000,000 | —D | M] (Microsoft .NET Framework Assistant) – C:\Users\Dan\AppData\Roaming\Mozilla\Firefox\Profiles\fmc69kie.Firefox3.6.16\extensions\{20a82645-c095-46ed-80e3-08825760534b}
[2011/03/31 22:14:46 | 000,000,000 | —D | M] (DownloadHelper) – C:\Users\Dan\AppData\Roaming\Mozilla\Firefox\Profiles\fmc69kie.Firefox3.6.16\extensions\{b9db16a4-6edc-47ec-a1f4-b86292ed211d}
[2011/03/30 22:17:46 | 000,000,000 | —D | M] (No name found) – C:\Users\Dan\AppData\Roaming\Mozilla\Firefox\Profiles\g7lq900p.default\extensions
[2011/03/29 20:03:31 | 000,000,000 | —D | M] (Microsoft .NET Framework Assistant) – C:\Users\Dan\AppData\Roaming\Mozilla\Firefox\Profiles\g7lq900p.default\extensions\{20a82645-c095-46ed-80e3-08825760534b}
[2011/03/30 22:40:17 | 000,000,000 | —D | M] (No name found) – C:\Program Files\Mozilla Firefox\extensions
[2011/03/18 18:53:24 | 000,142,296 | —- | M] (Mozilla Foundation) – C:\Program Files\Mozilla Firefox\components\browsercomps.dll
[2010/01/01 09:00:00 | 000,002,252 | —- | M] () – C:\Program Files\Mozilla Firefox\searchplugins\bing.xml

O1 HOSTS File: ([2006/09/18 22:41:30 | 000,000,761 | —- | M]) - C:\Windows\System32\drivers\etc\hosts
O1 - Hosts: 127.0.0.1	   localhost
O1 - Hosts: ::1			 localhost
O2 - BHO: (no name) - {02478D38-C3F9-4efb-9B51-7695ECA05670} - No CLSID value found.
O2 - BHO: (ShowBarObj Class) - {83A2F9B1-01A2-4AA5-87D1-45B6B8505E96} - C:\Program Files\Acer\Empowering Technology\eDataSecurity\x86\ActiveToolBand.dll (Egis)
O3 - HKLM\..\Toolbar: (no name) - {0BF43445-2F28-4351-9252-17FE6E806AA0} - No CLSID value found.
O3 - HKLM\..\Toolbar: (Acer eDataSecurity Management) - {5CBE3B7C-1E47-477e-A7DD-396DB0476E29} - C:\Program Files\Acer\Empowering Technology\eDataSecurity\x86\eDStoolbar.dll (Egis Incorporated.)
O3 - HKCU\..\Toolbar\ShellBrowser: (Acer eDataSecurity Management) - {5CBE3B7C-1E47-477E-A7DD-396DB0476E29} - C:\Program Files\Acer\Empowering Technology\eDataSecurity\x86\eDStoolbar.dll (Egis Incorporated.)
O4 - HKLM..\Run: [Acronis Scheduler2 Service] C:\Program Files\Common Files\Acronis\Schedule2\schedhlp.exe (Acronis)
O4 - HKLM..\Run: [AcronisTimounterMonitor] C:\Program Files\Acronis\TrueImageHome\TimounterMonitor.exe (Acronis)
O4 - HKLM..\Run: [egui] C:\Program Files\ESET\ESET Smart Security\egui.exe (ESET)
O4 - HKLM..\Run: [eRecoveryService]  File not found
O4 - HKLM..\Run: [IAAnotif] C:\Program Files\Intel\Intel Matrix Storage Manager\IAAnotif.exe (Intel Corporation)
O4 - HKLM..\Run: [LManager] C:\Program Files\Launch Manager\QtZgAcer.EXE (Dritek System Inc.)
O4 - HKLM..\Run: [Malwarebytes' Anti-Malware] C:\Program Files\Malwarebytes' Anti-Malware\mbamgui.exe (Malwarebytes Corporation)
O4 - HKLM..\Run: [PLFSetI] C:\Windows\PLFSetI.exe ()
O4 - HKLM..\Run: [TrueImageMonitor.exe] C:\Program Files\Acronis\TrueImageHome\TrueImageMonitor.exe (Acronis)
O4 - HKLM..\Run: [Windows Defender] C:\Program Files\Windows Defender\MSASCui.exe (Microsoft Corporation)
O4 - HKLM..\Run: [WinPatrol] C:\Program Files\BillP Studios\WinPatrol\winpatrol.exe (BillP Studios)
O10 - NameSpace_Catalog5\Catalog_Entries\000000000008 [] - C:\Program Files\Bonjour\mdnsNSP.dll (Apple Inc.)
O13 - gopher Prefix: missing
O16 - DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} http://java.sun.com/update/1.6.0/jinstall-1_6_0_24-windows-i586.cab (Java Plug-in 1.6.0_24)
O16 - DPF: {CAFEEFAC-0016-0000-0024-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-1_6_0_24-windows-i586.cab (Java Plug-in 1.6.0_24)
O16 - DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-1_6_0_24-windows-i586.cab (Java Plug-in 1.6.0_24)
O16 - DPF: {CF84DAC5-A4F5-419E-A0BA-C01FFD71112F} http://content.systemrequirementslab.com.s3.amazonaws.com/global/bin/srldetect_intel_4.4.22.0.cab (SysInfo Class)
O16 - DPF: {E2883E8F-472F-4FB0-9522-AC9BF37916A7} http://platformdl.adobe.com/NOS/getPlusPlus/1.6/gp.cab (get_atlcom Class)
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: DhcpNameServer = 192.168.0.1
O20 - HKLM Winlogon: Shell - (explorer.exe) - C:\Windows\explorer.exe (Microsoft Corporation)
O24 - Desktop WallPaper: C:\Users\Dan\Pictures\Wallpapers\Mac & Apple Wallpapers\Colorful_without_text\colorful_1920x1200.jpg
O24 - Desktop BackupWallPaper: C:\Users\Dan\Pictures\Wallpapers\Mac & Apple Wallpapers\Colorful_without_text\colorful_1920x1200.jpg
O32 - HKLM CDRom: AutoRun - 1
O32 - AutoRun File - [2006/09/18 22:43:36 | 000,000,024 | —- | M] () - C:\autoexec.bat – [ NTFS ]
O32 - AutoRun File - [2007/08/17 14:48:16 | 000,000,040 | —- | M] () - I:\autorun.inf – [ NTFS ]
O34 - HKLM BootExecute: (autocheck autochk *) -  File not found
O35 - HKLM\..comfile [open] – "%1" %*
O35 - HKLM\..exefile [open] – "%1" %*
O37 - HKLM\…com [@ = comfile] – "%1" %*
O37 - HKLM\…exe [@ = exefile] – "%1" %*

NetSvcs: FastUserSwitchingCompatibility -  File not found
NetSvcs: Ias -  File not found
NetSvcs: Nla -  File not found
NetSvcs: Ntmssvc -  File not found
NetSvcs: NWCWorkstation -  File not found
NetSvcs: Nwsapagent -  File not found
NetSvcs: SRService -  File not found
NetSvcs: WmdmPmSp -  File not found
NetSvcs: LogonHours -  File not found
NetSvcs: PCAudit -  File not found
NetSvcs: helpsvc -  File not found
NetSvcs: uploadmgr -  File not found

Drivers32: msacm.l3acm - C:\Windows\System32\l3codeca.acm (Fraunhofer Institut Integrierte Schaltungen IIS)
Drivers32: MSVideo8 - C:\Windows\System32\vfwwdm32.dll (Microsoft Corporation)
Drivers32: vidc.cvid - C:\Windows\System32\iccvid.dll (Radius Inc.)
Drivers32: vidc.tscc - C:\Windows\System32\tsccvid.dll (TechSmith Corporation)

CREATERESTOREPOINT
Restore point Set: OTL Restore Point

========== Files/Folders - Created Within 30 Days ==========

[2011/04/01 00:25:51 | 000,580,608 | —- | C] (OldTimer Tools) – C:\Users\Dan\Desktop\OTL.exe
[2011/03/31 23:14:26 | 000,157,472 | —- | C] (Sun Microsystems, Inc.) – C:\Windows\System32\javaws.exe
[2011/03/31 23:14:26 | 000,145,184 | —- | C] (Sun Microsystems, Inc.) – C:\Windows\System32\javaw.exe
[2011/03/31 23:14:26 | 000,145,184 | —- | C] (Sun Microsystems, Inc.) – C:\Windows\System32\java.exe
[2011/03/31 22:50:21 | 000,000,000 | —D | C] – C:\ProgramData\NOS
[2011/03/31 22:50:21 | 000,000,000 | —D | C] – C:\Program Files\NOS
[2011/03/31 22:19:59 | 000,000,000 | —D | C] – C:\Users\Dan\Desktop\Firefox (3.6.16) Alternative Install
[2011/03/31 19:52:27 | 000,000,000 | —D | C] – C:\Program Files\Firefox 3.6.16
[2011/03/30 22:51:54 | 000,000,000 | —D | C] – C:\Program Files\SystemRequirementsLab
[2011/03/30 22:40:16 | 000,000,000 | —D | C] – C:\Program Files\Mozilla Firefox
[2011/03/30 06:58:37 | 001,068,544 | —- | C] (Microsoft Corporation) – C:\Windows\System32\DWrite.dll
[2011/03/30 06:58:37 | 000,288,768 | —- | C] (Microsoft Corporation) – C:\Windows\System32\XpsGdiConverter.dll
[2011/03/29 21:49:46 | 000,000,000 | —D | C] – C:\Users\Dan\Desktop\downloads_from_firefox_by_kjags-d3793gq
[2011/03/29 19:55:18 | 000,000,000 | —D | C] – C:\Users\Dan\AppData\Roaming\Mozilla
[2011/03/29 19:55:18 | 000,000,000 | —D | C] – C:\Users\Dan\AppData\Local\Mozilla
[2011/03/29 19:05:25 | 000,161,792 | —- | C] (Microsoft Corporation) – C:\Windows\System32\msls31.dll
[2011/03/29 19:05:25 | 000,065,024 | —- | C] (Microsoft Corporation) – C:\Windows\System32\jsproxy.dll
[2011/03/29 19:05:24 | 000,176,640 | —- | C] (Microsoft Corporation) – C:\Windows\System32\ieui.dll
[2011/03/29 19:05:24 | 000,162,304 | —- | C] (Microsoft Corporation) – C:\Windows\System32\msrating.dll
[2011/03/29 19:05:24 | 000,086,528 | —- | C] (Microsoft Corporation) – C:\Windows\System32\iesysprep.dll
[2011/03/29 19:05:24 | 000,076,800 | —- | C] (Microsoft Corporation) – C:\Windows\System32\SetIEInstalledDate.exe
[2011/03/29 19:05:24 | 000,074,752 | —- | C] (Microsoft Corporation) – C:\Windows\System32\RegisterIEPKEYs.exe
[2011/03/29 19:05:24 | 000,048,640 | —- | C] (Microsoft Corporation) – C:\Windows\System32\mshtmler.dll
[2011/03/29 19:05:23 | 003,695,416 | —- | C] (Microsoft Corporation) – C:\Windows\System32\ieapfltr.dat
[2011/03/29 19:05:23 | 000,434,176 | —- | C] (Microsoft Corporation) – C:\Windows\System32\ieapfltr.dll
[2011/03/29 19:05:23 | 000,367,104 | —- | C] (Microsoft Corporation) – C:\Windows\System32\html.iec
[2011/03/29 19:05:23 | 000,353,792 | —- | C] (Microsoft Corporation) – C:\Windows\System32\dxtmsft.dll
[2011/03/29 19:05:23 | 000,231,936 | —- | C] (Microsoft Corporation) – C:\Windows\System32\url.dll
[2011/03/29 19:05:23 | 000,223,232 | —- | C] (Microsoft Corporation) – C:\Windows\System32\dxtrans.dll
[2011/03/29 19:05:23 | 000,074,752 | —- | C] (Microsoft Corporation) – C:\Windows\System32\iesetup.dll
[2011/03/29 19:05:23 | 000,074,240 | —- | C] (Microsoft Corporation) – C:\Windows\System32\ie4uinit.exe
[2011/03/29 19:05:23 | 000,031,744 | —- | C] (Microsoft Corporation) – C:\Windows\System32\iernonce.dll
[2011/03/29 19:05:22 | 001,427,456 | —- | C] (Microsoft Corporation) – C:\Windows\System32\inetcpl.cpl
[2011/03/29 19:05:22 | 000,580,608 | —- | C] (Microsoft Corporation) – C:\Windows\System32\msfeeds.dll
[2011/03/29 19:05:22 | 000,420,864 | —- | C] (Microsoft Corporation) – C:\Windows\System32\vbscript.dll
[2011/03/29 19:05:22 | 000,353,584 | —- | C] (Microsoft Corporation) – C:\Windows\System32\iedkcs32.dll
[2011/03/29 19:05:22 | 000,152,064 | —- | C] (Microsoft Corporation) – C:\Windows\System32\wextract.exe
[2011/03/29 19:05:22 | 000,150,528 | —- | C] (Microsoft Corporation) – C:\Windows\System32\iexpress.exe
[2011/03/29 19:05:22 | 000,078,848 | —- | C] (Microsoft Corporation) – C:\Windows\System32\inseng.dll
[2011/03/29 19:05:22 | 000,023,552 | —- | C] (Microsoft Corporation) – C:\Windows\System32\licmgr10.dll
[2011/03/29 19:05:21 | 002,382,848 | —- | C] (Microsoft Corporation) – C:\Windows\System32\mshtml.tlb
[2011/03/29 19:05:21 | 001,797,632 | —- | C] (Microsoft Corporation) – C:\Windows\System32\jscript9.dll
[2011/03/29 19:05:21 | 000,716,800 | —- | C] (Microsoft Corporation) – C:\Windows\System32\jscript.dll
[2011/03/29 19:05:21 | 000,227,840 | —- | C] (Microsoft Corporation) – C:\Windows\System32\ieaksie.dll
[2011/03/29 19:05:21 | 000,163,840 | —- | C] (Microsoft Corporation) – C:\Windows\System32\ieakui.dll
[2011/03/29 19:05:21 | 000,142,848 | —- | C] (Microsoft Corporation) – C:\Windows\System32\ieUnatt.exe
[2011/03/29 19:05:21 | 000,118,784 | —- | C] (Microsoft Corporation) – C:\Windows\System32\iepeers.dll
[2011/03/29 19:05:21 | 000,101,888 | —- | C] (Microsoft Corporation) – C:\Windows\System32\admparse.dll
[2011/03/29 19:05:21 | 000,054,272 | —- | C] (Microsoft Corporation) – C:\Windows\System32\pngfilt.dll
[2011/03/29 19:05:21 | 000,035,840 | —- | C] (Microsoft Corporation) – C:\Windows\System32\imgutil.dll
[2011/03/29 19:05:20 | 000,130,560 | —- | C] (Microsoft Corporation) – C:\Windows\System32\ieakeng.dll
[2011/03/29 19:05:20 | 000,110,592 | —- | C] (Microsoft Corporation) – C:\Windows\System32\IEAdvpack.dll
[2011/03/29 19:05:20 | 000,041,472 | —- | C] (Microsoft Corporation) – C:\Windows\System32\msfeedsbs.dll
[2011/03/29 19:05:20 | 000,010,752 | —- | C] (Microsoft Corporation) – C:\Windows\System32\msfeedssync.exe
[2011/03/27 02:14:34 | 000,000,000 | —D | C] – C:\Users\Dan\AppData\Local\ElevatedDiagnostics
[2011/03/27 02:12:37 | 000,000,000 | —D | C] – C:\Program Files\Microsoft ATS
[2011/03/21 22:10:57 | 000,000,000 | —D | C] – C:\Users\Dan\Documents\MyBackups
[2011/03/18 19:33:14 | 000,000,000 | -H-D | C] – C:\Acapela.lic
[2011/03/11 23:59:36 | 000,000,000 | —D | C] – C:\Program Files\GanttProject
[2011/03/11 22:26:28 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\iTunes
[2011/03/11 22:25:16 | 000,000,000 | —D | C] – C:\Program Files\iPod
[2011/03/11 22:25:15 | 000,000,000 | —D | C] – C:\Program Files\iTunes
[2011/03/11 22:19:57 | 000,000,000 | —D | C] – C:\Program Files\Bonjour
[2011/03/09 22:41:27 | 000,000,000 | —D | C] – C:\Users\Dan\Documents\AdobeStockPhotos
[2011/03/09 17:56:05 | 000,429,056 | —- | C] (Microsoft Corporation) – C:\Windows\System32\EncDec.dll
[2011/03/09 17:56:05 | 000,322,560 | —- | C] (Microsoft Corporation) – C:\Windows\System32\sbe.dll
[2011/03/09 17:56:04 | 000,177,664 | —- | C] (Microsoft Corporation) – C:\Windows\System32\mpg2splt.ax
[2011/03/09 17:56:04 | 000,153,088 | —- | C] (Microsoft Corporation) – C:\Windows\System32\sbeio.dll
[2011/03/02 19:13:37 | 000,000,000 | —D | C] – C:\Users\Dan\AppData\Local\Microsoft_Corporation
[2008/07/22 09:01:25 | 000,049,152 | —- | C] ( ) – C:\Windows\Interop.IWshRuntimeLibrary.dll

========== Files - Modified Within 30 Days ==========

[2011/04/01 00:26:01 | 000,580,608 | —- | M] (OldTimer Tools) – C:\Users\Dan\Desktop\OTL.exe
[2011/03/31 23:36:02 | 000,609,196 | —- | M] () – C:\Windows\System32\perfh009.dat
[2011/03/31 23:36:02 | 000,108,672 | —- | M] () – C:\Windows\System32\perfc009.dat
[2011/03/31 23:33:51 | 000,003,216 | -H– | M] () – C:\Windows\System32\7B296FB0-376B-497e-B012-9C450E1B7327-2P-1.C7483456-A289-439d-8115-601632D005A0
[2011/03/31 23:33:51 | 000,003,216 | -H– | M] () – C:\Windows\System32\7B296FB0-376B-497e-B012-9C450E1B7327-2P-0.C7483456-A289-439d-8115-601632D005A0
[2011/03/31 23:14:05 | 000,472,808 | —- | M] (Sun Microsystems, Inc.) – C:\Windows\System32\deployJava1.dll
[2011/03/31 23:14:05 | 000,157,472 | —- | M] (Sun Microsystems, Inc.) – C:\Windows\System32\javaws.exe
[2011/03/31 23:14:05 | 000,145,184 | —- | M] (Sun Microsystems, Inc.) – C:\Windows\System32\javaw.exe
[2011/03/31 23:14:05 | 000,145,184 | —- | M] (Sun Microsystems, Inc.) – C:\Windows\System32\java.exe
[2011/03/31 22:03:47 | 000,000,850 | —- | M] () – C:\Users\Dan\Application Data\Microsoft\Internet Explorer\Quick Launch\firefox.exe.lnk
[2011/03/31 21:33:51 | 000,001,795 | —- | M] () – C:\Users\Dan\Application Data\Microsoft\Internet Explorer\Quick Launch\Firefox 3.6.16.lnk
[2011/03/31 09:34:12 | 000,000,000 | —- | M] () – C:\Windows\System32\LogConfigTemp.xml
[2011/03/31 09:33:51 | 000,067,584 | —- | M] () – C:\Windows\bootstat.dat
[2011/03/31 07:15:41 | 000,000,012 | —- | M] () – C:\Windows\bthservsdp.dat
[2011/03/29 21:48:49 | 000,020,273 | —- | M] () – C:\Users\Dan\Desktop\Firefox_Color_Alternative_Icon_by_augustodeskmod.zip
[2011/03/29 21:43:30 | 000,147,693 | —- | M] () – C:\Users\Dan\Desktop\downloads_from_firefox_by_kjags-d3793gq.zip
[2011/03/29 20:34:21 | 000,072,823 | —- | M] () – C:\Users\Dan\Desktop\Default Firefox Bookmarks.pdf
[2011/03/29 19:05:49 | 000,008,798 | —- | M] () – C:\Windows\System32\icrav03.rat
[2011/03/29 19:05:49 | 000,001,988 | —- | M] () – C:\Windows\System32\ticrf.rat
[2011/03/29 19:05:25 | 000,161,792 | —- | M] (Microsoft Corporation) – C:\Windows\System32\msls31.dll
[2011/03/29 19:05:25 | 000,065,024 | —- | M] (Microsoft Corporation) – C:\Windows\System32\jsproxy.dll
[2011/03/29 19:05:24 | 000,176,640 | —- | M] (Microsoft Corporation) – C:\Windows\System32\ieui.dll
[2011/03/29 19:05:24 | 000,162,304 | —- | M] (Microsoft Corporation) – C:\Windows\System32\msrating.dll
[2011/03/29 19:05:24 | 000,086,528 | —- | M] (Microsoft Corporation) – C:\Windows\System32\iesysprep.dll
[2011/03/29 19:05:24 | 000,076,800 | —- | M] (Microsoft Corporation) – C:\Windows\System32\SetIEInstalledDate.exe
[2011/03/29 19:05:24 | 000,074,752 | —- | M] (Microsoft Corporation) – C:\Windows\System32\RegisterIEPKEYs.exe
[2011/03/29 19:05:24 | 000,048,640 | —- | M] (Microsoft Corporation) – C:\Windows\System32\mshtmler.dll
[2011/03/29 19:05:23 | 003,695,416 | —- | M] (Microsoft Corporation) – C:\Windows\System32\ieapfltr.dat
[2011/03/29 19:05:23 | 000,434,176 | —- | M] (Microsoft Corporation) – C:\Windows\System32\ieapfltr.dll
[2011/03/29 19:05:23 | 000,367,104 | —- | M] (Microsoft Corporation) – C:\Windows\System32\html.iec
[2011/03/29 19:05:23 | 000,353,792 | —- | M] (Microsoft Corporation) – C:\Windows\System32\dxtmsft.dll
[2011/03/29 19:05:23 | 000,231,936 | —- | M] (Microsoft Corporation) – C:\Windows\System32\url.dll
[2011/03/29 19:05:23 | 000,223,232 | —- | M] (Microsoft Corporation) – C:\Windows\System32\dxtrans.dll
[2011/03/29 19:05:23 | 000,074,752 | —- | M] (Microsoft Corporation) – C:\Windows\System32\iesetup.dll
[2011/03/29 19:05:23 | 000,074,240 | —- | M] (Microsoft Corporation) – C:\Windows\System32\ie4uinit.exe
[2011/03/29 19:05:23 | 000,072,822 | —- | M] () – C:\Windows\System32\ieuinit.inf
[2011/03/29 19:05:23 | 000,031,744 | —- | M] (Microsoft Corporation) – C:\Windows\System32\iernonce.dll
[2011/03/29 19:05:22 | 001,427,456 | —- | M] (Microsoft Corporation) – C:\Windows\System32\inetcpl.cpl
[2011/03/29 19:05:22 | 000,580,608 | —- | M] (Microsoft Corporation) – C:\Windows\System32\msfeeds.dll
[2011/03/29 19:05:22 | 000,420,864 | —- | M] (Microsoft Corporation) – C:\Windows\System32\vbscript.dll
[2011/03/29 19:05:22 | 000,353,584 | —- | M] (Microsoft Corporation) – C:\Windows\System32\iedkcs32.dll
[2011/03/29 19:05:22 | 000,152,064 | —- | M] (Microsoft Corporation) – C:\Windows\System32\wextract.exe
[2011/03/29 19:05:22 | 000,150,528 | —- | M] (Microsoft Corporation) – C:\Windows\System32\iexpress.exe
[2011/03/29 19:05:22 | 000,078,848 | —- | M] (Microsoft Corporation) – C:\Windows\System32\inseng.dll
[2011/03/29 19:05:22 | 000,023,552 | —- | M] (Microsoft Corporation) – C:\Windows\System32\licmgr10.dll
[2011/03/29 19:05:21 | 002,382,848 | —- | M] (Microsoft Corporation) – C:\Windows\System32\mshtml.tlb
[2011/03/29 19:05:21 | 001,797,632 | —- | M] (Microsoft Corporation) – C:\Windows\System32\jscript9.dll
[2011/03/29 19:05:21 | 000,716,800 | —- | M] (Microsoft Corporation) – C:\Windows\System32\jscript.dll
[2011/03/29 19:05:21 | 000,227,840 | —- | M] (Microsoft Corporation) – C:\Windows\System32\ieaksie.dll
[2011/03/29 19:05:21 | 000,163,840 | —- | M] (Microsoft Corporation) – C:\Windows\System32\ieakui.dll
[2011/03/29 19:05:21 | 000,142,848 | —- | M] (Microsoft Corporation) – C:\Windows\System32\ieUnatt.exe
[2011/03/29 19:05:21 | 000,118,784 | —- | M] (Microsoft Corporation) – C:\Windows\System32\iepeers.dll
[2011/03/29 19:05:21 | 000,101,888 | —- | M] (Microsoft Corporation) – C:\Windows\System32\admparse.dll
[2011/03/29 19:05:21 | 000,054,272 | —- | M] (Microsoft Corporation) – C:\Windows\System32\pngfilt.dll
[2011/03/29 19:05:21 | 000,035,840 | —- | M] (Microsoft Corporation) – C:\Windows\System32\imgutil.dll
[2011/03/29 19:05:20 | 000,130,560 | —- | M] (Microsoft Corporation) – C:\Windows\System32\ieakeng.dll
[2011/03/29 19:05:20 | 000,110,592 | —- | M] (Microsoft Corporation) – C:\Windows\System32\IEAdvpack.dll
[2011/03/29 19:05:20 | 000,041,472 | —- | M] (Microsoft Corporation) – C:\Windows\System32\msfeedsbs.dll
[2011/03/29 19:05:20 | 000,010,752 | —- | M] (Microsoft Corporation) – C:\Windows\System32\msfeedssync.exe
[2011/03/27 03:10:53 | 000,076,844 | —- | M] () – C:\Users\Dan\Desktop\Profile - Extensions.jpg
[2011/03/27 01:04:01 | 000,448,413 | —- | M] () – C:\Users\Dan\Desktop\adblock_plus-1.3.5-tb+fn+fx+sm.xpi
[2011/03/26 23:34:29 | 000,083,289 | —- | M] () – C:\Users\Dan\Desktop\flashblock-1.5.14.xpi
[2011/03/26 23:31:38 | 000,250,729 | —- | M] () – C:\Users\Dan\Desktop\british_english_dictionary-1.19.1-fx+tb+sm.xpi
[2011/03/23 21:02:07 | 000,033,792 | —- | M] () – C:\Users\Dan\AppData\Local\DCBC2A71-70D8-4DAN-EHR8-E0D61DEA3FDF.ini
[2011/03/20 01:53:35 | 000,003,284 | —- | M] () – C:\Users\Dan\.ganttproject
[2011/03/15 19:30:03 | 000,000,947 | —- | M] () – C:\Users\Dan\Application Data\Microsoft\Internet Explorer\Quick Launch\Launch Internet Explorer Browser.lnk

========== Files Created - No Company Name ==========

[2011/03/31 22:03:47 | 000,000,850 | —- | C] () – C:\Users\Dan\Application Data\Microsoft\Internet Explorer\Quick Launch\firefox.exe.lnk
[2011/03/31 19:57:09 | 000,001,795 | —- | C] () – C:\Users\Dan\Application Data\Microsoft\Internet Explorer\Quick Launch\Firefox 3.6.16.lnk
[2011/03/30 22:40:18 | 000,000,862 | —- | C] () – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Mozilla Firefox.lnk
[2011/03/29 21:48:49 | 000,020,273 | —- | C] () – C:\Users\Dan\Desktop\Firefox_Color_Alternative_Icon_by_augustodeskmod.zip
[2011/03/29 21:43:29 | 000,147,693 | —- | C] () – C:\Users\Dan\Desktop\downloads_from_firefox_by_kjags-d3793gq.zip
[2011/03/29 20:34:20 | 000,072,823 | —- | C] () – C:\Users\Dan\Desktop\Default Firefox Bookmarks.pdf
[2011/03/29 19:05:23 | 000,072,822 | —- | C] () – C:\Windows\System32\ieuinit.inf
[2011/03/27 03:10:52 | 000,076,844 | —- | C] () – C:\Users\Dan\Desktop\Profile - Extensions.jpg
[2011/03/27 01:03:58 | 000,448,413 | —- | C] () – C:\Users\Dan\Desktop\adblock_plus-1.3.5-tb+fn+fx+sm.xpi
[2011/03/26 23:34:29 | 000,083,289 | —- | C] () – C:\Users\Dan\Desktop\flashblock-1.5.14.xpi
[2011/03/26 23:31:37 | 000,250,729 | —- | C] () – C:\Users\Dan\Desktop\british_english_dictionary-1.19.1-fx+tb+sm.xpi
[2010/10/17 13:22:29 | 000,000,036 | —- | C] () – C:\Users\Dan\AppData\Local\housecall.guid.cache
[2010/10/12 22:45:54 | 000,000,809 | —- | C] () – C:\Windows\NTIWVEDT.INI
[2010/09/20 22:30:54 | 000,004,096 | -H– | C] () – C:\Users\Dan\AppData\Local\keyfile3.drm
[2010/09/15 21:07:03 | 000,033,792 | —- | C] () – C:\Users\Dan\AppData\Local\DCBC2A71-70D8-4DAN-EHR8-E0D61DEA3FDF.ini
[2010/09/06 22:52:10 | 000,000,000 | —- | C] () – C:\Windows\nsreg.dat
[2010/07/31 19:30:19 | 000,117,248 | —- | C] () – C:\Windows\System32\EhStorAuthn.dll
[2010/07/31 19:30:19 | 000,107,612 | —- | C] () – C:\Windows\System32\StructuredQuerySchema.bin
[2010/07/31 03:59:32 | 000,626,688 | —- | C] () – C:\Windows\Image.dll
[2010/07/31 03:59:32 | 000,200,704 | —- | C] () – C:\Windows\PLFSetI.exe
[2010/07/31 03:59:32 | 000,000,036 | —- | C] () – C:\Windows\PidList.ini
[2010/07/31 03:42:36 | 000,018,904 | —- | C] () – C:\Windows\System32\StructuredQuerySchemaTrivial.bin
[2008/09/03 09:28:46 | 000,004,608 | —- | C] () – C:\Windows\System32\HdmiCoin.dll
[2008/09/03 09:28:40 | 000,147,456 | —- | C] () – C:\Windows\System32\igfxCoIn_v1527.dll
[2008/09/03 09:28:39 | 002,192,024 | —- | C] () – C:\Windows\System32\igkrng500.bin
[2008/09/03 09:28:31 | 000,147,172 | —- | C] () – C:\Windows\System32\igfcg550.bin
[2008/09/03 09:28:28 | 000,495,376 | —- | C] () – C:\Windows\System32\igcompkrng500.bin
[2008/04/17 18:28:07 | 000,000,012 | —- | C] () – C:\Windows\bthservsdp.dat
[2008/04/17 17:09:32 | 000,001,024 | RH– | C] () – C:\Windows\System32\NTIOFM4.dll
[2008/04/17 17:09:32 | 000,001,024 | RH– | C] () – C:\Windows\System32\NTIBUN5.dll
[2008/04/17 17:08:48 | 001,060,424 | —- | C] () – C:\Windows\System32\WdfCoInstaller01000.dll
[2008/04/17 16:38:04 | 000,204,800 | —- | C] () – C:\Windows\System32\SysHook.dll
[2008/04/17 16:34:50 | 000,487,424 | —- | C] () – C:\Windows\System32\INT15.dll
[2008/04/17 16:24:51 | 000,001,694 | —- | C] () – C:\Windows\RtDefLvl.ini
[2008/04/17 16:24:51 | 000,000,520 | —- | C] () – C:\Windows\System32\drivers\RTEQEX1.dat
[2008/04/17 16:24:51 | 000,000,520 | —- | C] () – C:\Windows\System32\drivers\RTEQEX0.dat
[2008/04/17 16:24:51 | 000,000,008 | —- | C] () – C:\Windows\System32\drivers\rtkhdaud.dat
[2006/11/02 13:53:49 | 000,067,584 | —- | C] () – C:\Windows\bootstat.dat
[2006/11/02 13:44:53 | 000,370,104 | —- | C] () – C:\Windows\System32\FNTCACHE.DAT
[2006/11/02 11:33:01 | 000,609,196 | —- | C] () – C:\Windows\System32\perfh009.dat
[2006/11/02 11:33:01 | 000,287,440 | —- | C] () – C:\Windows\System32\perfi009.dat
[2006/11/02 11:33:01 | 000,108,672 | —- | C] () – C:\Windows\System32\perfc009.dat
[2006/11/02 11:33:01 | 000,030,674 | —- | C] () – C:\Windows\System32\perfd009.dat
[2006/11/02 11:23:21 | 000,215,943 | —- | C] () – C:\Windows\System32\dssec.dat
[2006/11/02 09:58:30 | 000,043,131 | —- | C] () – C:\Windows\mib.bin
[2006/11/02 09:19:00 | 000,000,741 | —- | C] () – C:\Windows\System32\NOISE.DAT
[2006/11/02 08:40:29 | 000,013,750 | —- | C] () – C:\Windows\System32\pacerprf.ini
[2006/11/02 08:25:31 | 000,673,088 | —- | C] () – C:\Windows\System32\mlang.dat
[2001/12/27 00:12:30 | 000,065,536 | —- | C] () – C:\Windows\System32\multiplex_vcd.dll
[2001/09/04 07:46:38 | 000,110,592 | —- | C] () – C:\Windows\System32\Hmpg12.dll
[2001/07/31 00:33:56 | 000,118,784 | —- | C] () – C:\Windows\System32\HMPV2_ENC.dll
[2001/07/24 06:04:36 | 000,118,784 | —- | C] () – C:\Windows\System32\HMPV2_ENC_MMX.dll

========== LOP Check ==========

[2010/09/16 19:30:50 | 000,000,000 | —D | M] – C:\Users\Dan\AppData\Roaming\Acronis
[2011/02/25 02:25:30 | 000,000,000 | —D | M] – C:\Users\Dan\AppData\Roaming\Autodesk
[2011/01/27 02:09:05 | 000,000,000 | —D | M] – C:\Users\Dan\AppData\Roaming\DAEMON Tools Lite
[2010/11/25 22:31:20 | 000,000,000 | —D | M] – C:\Users\Dan\AppData\Roaming\EPSON
[2010/09/04 21:18:12 | 000,000,000 | —D | M] – C:\Users\Dan\AppData\Roaming\ESET
[2010/12/19 21:11:59 | 000,000,000 | —D | M] – C:\Users\Dan\AppData\Roaming\Foxit Software
[2010/11/14 01:12:45 | 000,000,000 | —D | M] – C:\Users\Dan\AppData\Roaming\TomTom
[2011/02/06 21:38:03 | 000,000,000 | —D | M] – C:\Users\Dan\AppData\Roaming\WinFellow
[2010/10/04 00:54:29 | 000,000,000 | —D | M] – C:\Users\Dan\AppData\Roaming\WinPatrol
[2011/03/31 07:15:41 | 000,032,622 | —- | M] () – C:\Windows\Tasks\SCHEDLGU.TXT
[2010/12/15 20:01:06 | 000,000,418 | -H– | M] () – C:\Windows\Tasks\User_Feed_Synchronization-{CB2794BB-D4F6-4120-873B-5250B6D0BA38}.job

========== Purity Check ==========


========== Custom Scans ==========


< %SYSTEMDRIVE%\*.* >
[2006/09/18 22:43:36 | 000,000,024 | —- | M] () – C:\autoexec.bat
[2009/07/14 02:38:58 | 000,383,562 | RHS- | M] () – C:\bootmgr
[2010/09/19 05:51:13 | 000,008,192 | RHS- | M] () – C:\BOOTSECT.BAK
[2006/09/18 22:43:37 | 000,000,010 | —- | M] () – C:\config.sys
[2011/03/31 09:33:25 | 3460,235,264 | -HS- | M] () – C:\pagefile.sys

< %systemroot%\Fonts\*.com >
[2006/11/02 13:35:34 | 000,026,040 | —- | M] () – C:\Windows\Fonts\GlobalMonospace.CompositeFont
[2006/11/02 13:35:34 | 000,026,489 | —- | M] () – C:\Windows\Fonts\GlobalSansSerif.CompositeFont
[2006/11/02 13:35:34 | 000,029,779 | —- | M] () – C:\Windows\Fonts\GlobalSerif.CompositeFont
[2010/07/31 20:26:16 | 000,037,665 | —- | M] () – C:\Windows\Fonts\GlobalUserInterface.CompositeFont

< %systemroot%\Fonts\*.dll >

< %systemroot%\Fonts\*.ini >
[2006/09/18 22:37:34 | 000,000,065 | —- | M] () – C:\Windows\Fonts\desktop.ini

< %systemroot%\Fonts\*.ini2 >

< %systemroot%\Fonts\*.exe >

< %systemroot%\system32\spool\prtprocs\w32x86\*.* >
[2006/10/27 03:56:12 | 000,033,104 | —- | M] (Microsoft Corporation) – C:\Windows\System32\spool\prtprocs\w32x86\msonpppr.dll

< %systemroot%\REPAIR\*.bak1 >

< %systemroot%\REPAIR\*.ini >

< %systemroot%\system32\*.jpg >

< %systemroot%\*.jpg >

< %systemroot%\*.png >

< %systemroot%\*.scr >

< %systemroot%\*._sy >

< %APPDATA%\Adobe\Update\*.* >

< %ALLUSERSPROFILE%\Favorites\*.* >

< %APPDATA%\Microsoft\*.* >

< %PROGRAMFILES%\*.* >
[2008/01/21 03:57:01 | 000,000,174 | -HS- | M] () – C:\Program Files\desktop.ini

< %APPDATA%\Update\*.* >

< %systemroot%\*. /mp /s >

< %systemroot%\System32\config\*.sav >
[2008/01/21 04:31:11 | 015,716,352 | —- | M] () – C:\Windows\System32\config\COMPONENTS.SAV
[2008/01/21 04:31:01 | 000,102,400 | —- | M] () – C:\Windows\System32\config\DEFAULT.SAV
[2008/01/21 04:31:12 | 000,020,480 | —- | M] () – C:\Windows\System32\config\SECURITY.SAV
[2006/11/02 11:34:08 | 010,133,504 | —- | M] () – C:\Windows\System32\config\SOFTWARE.SAV
[2006/11/02 11:34:08 | 001,826,816 | —- | M] () – C:\Windows\System32\config\SYSTEM.SAV

< %PROGRAMFILES%\bak. /s >

< %systemroot%\system32\bak. /s >

< %ALLUSERSPROFILE%\Start Menu\*.lnk /x >

< %systemroot%\system32\config\systemprofile\*.dat /x >

< %systemroot%\*.config >

< %systemroot%\system32\*.db >

< %PROGRAMFILES%\Internet Explorer\*.dat >

< %APPDATA%\Microsoft\Internet Explorer\Quick Launch\*.lnk /x >
[2011/03/15 19:30:03 | 000,000,221 | -HS- | M] () – C:\Users\Dan\AppData\Roaming\Microsoft\Internet Explorer\Quick Launch\desktop.ini

< %USERPROFILE%\Desktop\*.exe >
[2011/04/01 00:26:01 | 000,580,608 | —- | M] (OldTimer Tools) – C:\Users\Dan\Desktop\OTL.exe

< %PROGRAMFILES%\Common Files\*.* >

< %systemroot%\*.src >

< %systemroot%\install\*.* >

< %systemroot%\system32\DLL\*.* >

< %systemroot%\system32\HelpFiles\*.* >

< %systemroot%\system32\rundll\*.* >

< %systemroot%\winn32\*.* >

< %systemroot%\Java\*.* >

< %systemroot%\system32\test\*.* >

< %systemroot%\system32\Rundll32\*.* >

< %systemroot%\AppPatch\Custom\*.* >

< HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU >

< HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install|LastSuccessTime /rs >
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install\\LastSuccessTime: 2011-03-30 22:00:42

< End of report >
EXTRAS.txt
OTL Extras logfile created on: 01/04/2011 00:41:45 - Run 1
OTL by OldTimer - Version 3.2.22.3	 Folder = C:\Users\Dan\Desktop
Windows Vista Home Basic Edition Service Pack 2 (Version = 6.0.6002) - Type = NTWorkstation
Internet Explorer (Version = 9.0.8112.16421)
Locale: 00000809 | Country: United Kingdom | Language: ENG | Date Format: dd/MM/yyyy

3.00 Gb Total Physical Memory | 1.00 Gb Available Physical Memory | 49.00% Memory free
6.00 Gb Paging File | 5.00 Gb Available in Paging File | 77.00% Paging File free
Paging file location(s): ?:\pagefile.sys [binary data]

%SystemDrive% = C: | %SystemRoot% = C:\Windows | %ProgramFiles% = C:\Program Files
Drive C: | 69.52 Gb Total Space | 19.94 Gb Free Space | 28.67% Space Free | Partition Type: NTFS
Drive D: | 69.53 Gb Total Space | 69.44 Gb Free Space | 99.87% Space Free | Partition Type: NTFS
Drive H: | 1.92 Gb Total Space | 1.91 Gb Free Space | 99.40% Space Free | Partition Type: FAT
Drive I: | 698.64 Gb Total Space | 168.04 Gb Free Space | 24.05% Space Free | Partition Type: NTFS

Computer Name: DAN-PC | User Name: Dan | Logged in as Administrator.
Boot Mode: Normal | Scan Mode: Current user
Company Name Whitelist: Off | Skip Microsoft Files: Off | No Company Name Whitelist: On | File Age = 30 Days

========== Extra Registry (SafeList) ==========


========== File Associations ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\]
.cpl [@ = cplfile] – C:\Windows\System32\control.exe (Microsoft Corporation)
.hlp [@ = hlpfile] – C:\Windows\winhlp32.exe (Microsoft Corporation)

[HKEY_CURRENT_USER\SOFTWARE\Classes\]
.html [@ = FirefoxHTML] – C:\Program Files\Mozilla Firefox\firefox.exe (Mozilla Corporation)

========== Shell Spawning ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\\shell\[command]\command]
batfile [open] – "%1" %*
cmdfile [open] – "%1" %*
comfile [open] – "%1" %*
cplfile [cplopen] – %SystemRoot%\System32\control.exe "%1",%* (Microsoft Corporation)
exefile [open] – "%1" %*
helpfile [open] – Reg Error: Key error.
hlpfile [open] – %SystemRoot%\winhlp32.exe %1 (Microsoft Corporation)
inffile [install] – %SystemRoot%\System32\InfDefaultInstall.exe "%1" (Microsoft Corporation)
piffile [open] – "%1" %*
regfile [merge] – Reg Error: Key error.
scrfile [config] – "%1"
scrfile [install] – rundll32.exe desk.cpl,InstallScreenSaver %l
scrfile [open] – "%1" /S
txtfile [edit] – Reg Error: Key error.
Unknown [openas] – %SystemRoot%\system32\rundll32.exe %SystemRoot%\system32\shell32.dll,OpenAs_RunDLL %1
Directory [AddToPlaylistVLC] – "C:\Program Files\VideoLAN\VLC\vlc.exe" –started-from-file –playlist-enqueue "%1" ()
Directory [cmd] – cmd.exe /s /k pushd "%V" (Microsoft Corporation)
Directory [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Directory [PlayWithVLC] – "C:\Program Files\VideoLAN\VLC\vlc.exe" –started-from-file –no-playlist-enqueue "%1" ()
Folder [open] – %SystemRoot%\Explorer.exe /separate,/idlist,%I,%L (Microsoft Corporation)
Folder [explore] – %SystemRoot%\Explorer.exe /separate,/e,/idlist,%I,%L (Microsoft Corporation)
Drive [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)

========== Security Center Settings ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center]
"cval" = 1

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Monitoring]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Monitoring\McAfeeAntiSpyware]
"DisableMonitoring" = 1

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Svc]
"AntiVirusOverride" = 0
"AntiSpywareOverride" = 0
"FirewallOverride" = 0
"VistaSp1" = Reg Error: Unknown registry data type – File not found
"VistaSp2" = Reg Error: Unknown registry data type – File not found

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Svc\Vol]

========== Firewall Settings ==========

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\DomainProfile]
"EnableFirewall" = 0
"DisableNotifications" = 0

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\StandardProfile]
"EnableFirewall" = 0
"DisableNotifications" = 0

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\PublicProfile]
"EnableFirewall" = 0
"DisableNotifications" = 0

========== Authorized Applications List ==========


========== Vista Active Open Ports Exception List ==========

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules]
"{13154130-59A9-4459-9D49-0F3485328C33}" = lport=49160 | protocol=6 | dir=in | name=akamai netsession interface |
"{17AD3DEB-554C-4ADF-BE36-5C4FB8D0EBAB}" = lport=445 | protocol=6 | dir=in | app=system |
"{46BC9395-43FF-4DCC-8878-A37067345835}" = lport=rpc-epmap | protocol=6 | dir=in | svc=rpcss | name=@firewallapi.dll,-28539 |
"{4F512E7D-9742-4444-B4C0-D6D7F8EEAF7A}" = lport=139 | protocol=6 | dir=in | app=system |
"{5D676F3F-1244-42BD-A79A-7742D101353E}" = rport=139 | protocol=6 | dir=out | app=system |
"{6BA1358D-1B0F-4C8A-A5BD-ACD623C9D427}" = lport=rpc | protocol=6 | dir=in | svc=spooler | app=%systemroot%\system32\spoolsv.exe |
"{8D4591DB-E51F-4CB2-B1F0-161583BD161B}" = lport=5000 | protocol=17 | dir=in | name=akamai netsession interface |
"{A0C0C593-6D01-42E8-9B5D-648971B1E798}" = lport=137 | protocol=17 | dir=in | app=system |
"{B35DC04C-9E79-49D7-B33D-A0096D6D9CB7}" = rport=138 | protocol=17 | dir=out | app=system |
"{BAEBA52A-23C7-4967-A91D-501F1C2FE1EB}" = rport=137 | protocol=17 | dir=out | app=system |
"{E40FB2BA-5F65-493B-A206-00EED6868231}" = rport=445 | protocol=6 | dir=out | app=system |
"{E7BF4D8A-3F14-4924-B282-2D696F4B9E5D}" = lport=138 | protocol=17 | dir=in | app=system |

========== Vista Active Application Exception List ==========

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules]
"{006F9AC7-DF45-4629-8896-DEDCAA54312F}" = protocol=17 | dir=in | app=%programfiles%\windows media player\wmplayer.exe |
"{16AD7072-69DE-4BE9-9C9A-311DB38DB329}" = protocol=17 | dir=in | app=c:\program files\autodesk\backburner\manager.exe |
"{1DD6BD40-1FB2-4EBC-AC41-5A5803996D9E}" = protocol=6 | dir=in | app=c:\program files\newtech infosystems\nti backup now 5\backupsvc.exe |
"{24B4C567-D664-4BE3-A0D7-AF1C042D733A}" = protocol=6 | dir=out | app=%programfiles%\windows media player\wmplayer.exe |
"{37A2C38B-902D-43B1-8E90-D28F19CF3EC5}" = protocol=17 | dir=in | app=c:\program files\autodesk\3ds max 2009\3dsmax.exe |
"{3CDFC0BF-9FD1-4E04-8881-C19DBAD8427B}" = protocol=17 | dir=in | app=c:\program files\bonjour\mdnsresponder.exe |
"{40D8A515-30B7-4957-B650-FB1A39EAAABE}" = protocol=6 | dir=in | app=c:\program files\autodesk\backburner\server.exe |
"{498EB6C6-DA1C-4D63-BF12-215E9EE88DCD}" = dir=in | app=c:\program files\itunes\itunes.exe |
"{5A0A3F3B-D3AD-44C6-9D28-FECA53F81E48}" = protocol=6 | dir=in | app=c:\program files\bonjour\mdnsresponder.exe |
"{6B542205-0045-4827-8EA0-5C9D41291D56}" = protocol=17 | dir=in | app=c:\program files\autodesk\backburner\server.exe |
"{76864BE6-5E83-45B6-B456-931A56E4F997}" = protocol=17 | dir=in | app=c:\program files\newtech infosystems\nti backup now 5\backupsvc.exe |
"{7917EFEC-EE23-4BC0-A01B-1493DC55EED8}" = protocol=6 | dir=in | app=c:\program files\autodesk\backburner\monitor.exe |
"{7EFF4BA9-A366-403E-B3A4-8B46393AFBE0}" = protocol=58 | dir=in | name=@firewallapi.dll,-28545 |
"{8001CE8C-70B9-4072-A2D1-629D7C34296C}" = protocol=6 | dir=in | app=c:\program files\autodesk\3ds max 2009\3dsmax.exe |
"{804CD80D-896D-4A9F-8C97-1A67EBD6A0EF}" = protocol=6 | dir=in | app=c:\program files\newtech infosystems\nti backup now 5\client\agentsvc.exe |
"{99401448-DB03-4DE6-B611-5B2C65B47933}" = protocol=1 | dir=out | name=@firewallapi.dll,-28544 |
"{AA701428-0F7D-4E85-BE93-DFD39F190CEC}" = protocol=17 | dir=in | app=c:\program files\newtech infosystems\nti backup now 5\client\agentsvc.exe |
"{AB501317-3CBB-42B4-85FB-A1CEEA019AEA}" = protocol=58 | dir=out | name=@firewallapi.dll,-28546 |
"{BE87BD0B-72EA-4C2B-A91F-ACC56030C733}" = protocol=17 | dir=in | app=c:\program files\autodesk\backburner\monitor.exe |
"{C510BE09-4211-4FBB-9D24-521ED17C67CB}" = protocol=17 | dir=out | app=%programfiles%\windows media player\wmplayer.exe |
"{E36E7731-EDF7-4653-930C-6848777B86E0}" = protocol=6 | dir=in | app=c:\program files\autodesk\backburner\manager.exe |
"{E90441C6-7CD3-42B7-8446-CD5ACF9238A8}" = protocol=6 | dir=in | app=c:\program files\newtech infosystems\nti backup now 5\schedulersvc.exe |
"{E99D7FBE-C3BB-48DC-B9CF-9A1D4E03A7B6}" = protocol=17 | dir=in | app=c:\program files\newtech infosystems\nti backup now 5\schedulersvc.exe |
"{EDEE1EDE-8451-495F-874B-E9620542F8A4}" = protocol=1 | dir=in | name=@firewallapi.dll,-28543 |

========== HKEY_LOCAL_MACHINE Uninstall List ==========

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall]
"{0134A1A1-C283-4A47-91A1-92F19F960372}" = Adobe Creative Suite 2
"{10F498FF-5392-4DF3-8F73-FE172A9F3800}" = Winbond CIR Device Drivers
"{11316260-6666-467B-AC34-183FCB5D4335}" = Acer Mobility Center Plug-In
"{12EFA1A4-AC3B-443C-8143-237EDE760403}" = NTI Backup Now Standard
"{13D85C14-2B85-419F-AC41-C7F21E68B25D}" = Acer eSettings Management
"{2300EE96-0A41-4FAB-BD03-989EC44577A0}" = Acronis Disk Director Suite
"{236BB7C4-4419-42FD-0409-1E257A25E34D}" = Adobe Photoshop CS2
"{2413930C-8309-47A6-BC61-5EF27A4222BC}" = NTI Media Maker 8
"{26604C7E-A313-4D12-867F-7C6E7820BE4C}" = JMicron JMB38X Flash Media Controller
"{26A24AE4-039D-4CA4-87B4-2F83216024FF}" = Java(TM) 6 Update 24
"{27CC6AB1-E72B-4179-AF1A-EAE507EBAF51}_is1" = ConvertHelper 2.2
"{2A697B53-0DE3-42DA-B41D-C3F804B1C538}" = iTunes
"{2A981294-F14C-4F0F-9627-D793270922F8}" = Bonjour
"{2DC94AFD-A6E2-4AB4-9132-4A3F8E07B386}" = Apple Application Support
"{37C8899D-FD70-481F-94AA-1F1B08765E22}" = Acronis True Image Home
"{3C3901C5-3455-3E0A-A214-0B093A5070A6}" = Microsoft .NET Framework 4 Client Profile
"{3D347E6D-5A03-4342-B5BA-6A771885F379}" = Autodesk Backburner 2008.1
"{46203E16-C938-41A4-A15B-082FF673B9D6}_is1" = Grand Theft Auto(TM): Vice City
"{4A03706F-666A-4037-7777-5F2748764D10}" = Java Auto Updater
"{53FA9A9F-3C19-4D43-AD6B-DEF365D469BA}" = Camtasia Studio 7
"{5545EEE1-FA36-4F76-B6BE-5696E7F4E2D6}" = VBA (2627.01)
"{57265292-228A-41FA-9AEC-4620CBCC2739}" = Acer eAudio Management
"{57752979-A1C9-4C02-856B-FBB27AC4E02C}" = QuickTime
"{5783F2D7-7001-0409-0002-0060B0CE6BBA}" = AutoCAD 2009 - English
"{58E5844B-7CE2-413D-83D1-99294BF6C74F}" = Acer ePower Management
"{6D52C408-B09A-4520-9B18-475B81D393F1}" = Microsoft Works
"{7299052b-02a4-4627-81f2-1818da5d550d}" = Microsoft Visual C++ 2005 Redistributable
"{76CE5B47-F5A4-4E5C-99A0-CEFF6146EA4A}" = System Requirements Lab for Intel
"{786C5747-1033-0000-B58E-000000000001}" = Adobe Stock Photos 1.0
"{7F4C8163-F259-49A0-A018-2857A90578BC}" = Adobe InDesign CS2
"{7F811A54-5A09-4579-90E1-C93498E230D9}" = Acer eRecovery Management
"{8EDBA74D-0686-4C99-BFDD-F894678E5B39}" = Adobe Common File Installer
"{8F1B6239-FEA0-450A-A950-B05276CE177C}" = Acer Empowering Technology
"{8F3C31C5-9C3A-4AA8-8EFA-71290A7AD533}" = TomTom HOME Visual Studio Merge Modules
"{90120000-0015-0409-0000-0000000FF1CE}" = Microsoft Office Access MUI (English) 2007
"{90120000-0016-0409-0000-0000000FF1CE}" = Microsoft Office Excel MUI (English) 2007
"{90120000-0018-0409-0000-0000000FF1CE}" = Microsoft Office PowerPoint MUI (English) 2007
"{90120000-0019-0409-0000-0000000FF1CE}" = Microsoft Office Publisher MUI (English) 2007
"{90120000-001A-0409-0000-0000000FF1CE}" = Microsoft Office Outlook MUI (English) 2007
"{90120000-001B-0409-0000-0000000FF1CE}" = Microsoft Office Word MUI (English) 2007
"{90120000-001F-0409-0000-0000000FF1CE}" = Microsoft Office Proof (English) 2007
"{90120000-001F-040C-0000-0000000FF1CE}" = Microsoft Office Proof (French) 2007
"{90120000-001F-0C0A-0000-0000000FF1CE}" = Microsoft Office Proof (Spanish) 2007
"{90120000-002C-0409-0000-0000000FF1CE}" = Microsoft Office Proofing (English) 2007
"{90120000-0030-0000-0000-0000000FF1CE}" = Microsoft Office Enterprise 2007
"{90120000-0044-0409-0000-0000000FF1CE}" = Microsoft Office InfoPath MUI (English) 2007
"{90120000-006E-0409-0000-0000000FF1CE}" = Microsoft Office Shared MUI (English) 2007
"{90120000-00A1-0409-0000-0000000FF1CE}" = Microsoft Office OneNote MUI (English) 2007
"{90120000-00B2-0409-0000-0000000FF1CE}" = Microsoft Save as PDF or XPS Add-in for 2007 Microsoft Office programs
"{90120000-00BA-0409-0000-0000000FF1CE}" = Microsoft Office Groove MUI (English) 2007
"{90120000-0114-0409-0000-0000000FF1CE}" = Microsoft Office Groove Setup Metadata MUI (English) 2007
"{90120000-0115-0409-0000-0000000FF1CE}" = Microsoft Office Shared Setup Metadata MUI (English) 2007
"{90120000-0117-0409-0000-0000000FF1CE}" = Microsoft Office Access Setup Metadata MUI (English) 2007
"{9068B2BE-D93A-4C0A-861C-5E35E2C0E09E}" = Intel® Matrix Storage Manager
"{A5633652-3795-4829-BB0B-644F0279E279}" = Acer eDataSecurity Management
"{A64A5576-D862-44F8-89DC-2B17FCC9B86E}" = Broadcom Gigabit Integrated Controller
"{A77255C4-AFCB-44A3-BF0F-2091A71FFD9E}" = Acer Crystal Eye Webcam 2.0.8
"{B74D4E10-1033-0000-0000-000000000001}" = Adobe Bridge 1.0
"{C41300B9-185D-475E-BFEC-39EF732F19B1}" = Apple Software Update
"{C49DAA9C-5BA8-459A-8244-E57B69DF0F04}" = Suite Specific
"{CACAEB5F-174D-4C7C-AC56-A33289A807CA}" = Apple Mobile Device Support
"{CE2CDD62-0124-36CA-84D3-9F4DCF5C5BD9}" = Microsoft .NET Framework 3.5 SP1
"{CE386A4E-D0DA-4208-8235-BCE43275C694}" = LightScribe  1.4.142.1
"{E2883E8F-472F-4fb0-9522-AC9BF37916A7}" = Adobe Download Manager
"{E9787678-1033-0000-8E67-000000000001}" = Adobe Help Center 1.0
"{F132AF7F-7BCA-4EDE-8A7C-958108FE7DBC}" = Realtek High Definition Audio Driver
"{F3E2505F-AA57-476B-9F67-F8C5E3938080}" = ESET Smart Security
"{FDD8070F-E3B9-0409-822C-CCFE5E82C14D}" = Autodesk 3ds Max 2009 32-bit
"Adobe Flash Player ActiveX" = Adobe Flash Player 10 ActiveX
"Adobe Flash Player Plugin" = Adobe Flash Player 10 Plugin
"Adobe Shockwave Player" = Adobe Shockwave Player 11.5
"Agere Systems Soft Modem" = Agere Systems HDA Modem
"Audacity_is1" = Audacity 1.2.6
"AutoCAD 2009 - English" = AutoCAD 2009 - English
"AVerMedia A310 (MiniCard, DVB-T)" = AVerMedia A310 (MiniCard, DVB-T) [removed]
"CCleaner" = CCleaner
"ENTERPRISE" = Microsoft Office Enterprise 2007
"EPSON Printer and Utilities" = EPSON Printer Software
"EPSON Scanner" = EPSON Scan
"ERUNT_is1" = ERUNT 1.1j
"FBX Plugin 2009.0 for Max 2009" = FBX Plugin 2009.0 for Max 2009
"Foxit Reader" = Foxit Reader
"GanttProject" = GanttProject
"HDMI" = Intel(R) Graphics Media Accelerator Driver
"InstallShield_{12EFA1A4-AC3B-443C-8143-237EDE760403}" = NTI Backup Now 5
"InstallShield_{2413930C-8309-47A6-BC61-5EF27A4222BC}" = NTI Media Maker 8
"LAME for Audacity_is1" = LAME v3.98.2 for Audacity
"LManager" = Launch Manager
"Malwarebytes' Anti-Malware_is1" = Malwarebytes' Anti-Malware
"Microsoft .NET Framework 3.5 SP1" = Microsoft .NET Framework 3.5 SP1
"Microsoft .NET Framework 4 Client Profile" = Microsoft .NET Framework 4 Client Profile
"Mozilla Firefox (3.6.16)" = Mozilla Firefox (3.6.16)
"Mozilla Firefox 4.0 (x86 en-US)" = Mozilla Firefox 4.0 (x86 en-US)
"Revo Uninstaller" = Revo Uninstaller 1.91
"SynTPDeinstKey" = Synaptics Pointing Device Driver
"TomTom HOME" = TomTom HOME 2.7.6.2056
"UltraISO_is1" = UltraISO Premium V9.31
"VLC media player" = VLC media player 1.1.4
"WinPatrol" = WinPatrol
"WinRAR archiver" = WinRAR archiver

========== HKEY_CURRENT_USER Uninstall List ==========

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall]
"GanttProject 2.0.10" = GanttProject 2.0.10

========== Last 10 Event Log Errors ==========

[ Application Events ]
Error - 26/03/2011 18:10:05 | Computer Name = Dan-PC | Source = Windows Search Service | ID = 3013
Description =

Error - 26/03/2011 18:10:05 | Computer Name = Dan-PC | Source = Windows Search Service | ID = 3013
Description =

Error - 26/03/2011 21:07:02 | Computer Name = Dan-PC | Source = WinMgmt | ID = 10
Description =

Error - 26/03/2011 21:36:45 | Computer Name = Dan-PC | Source = WinMgmt | ID = 10
Description =

Error - 26/03/2011 22:20:35 | Computer Name = Dan-PC | Source = WinMgmt | ID = 10
Description =

Error - 27/03/2011 07:51:45 | Computer Name = Dan-PC | Source = WinMgmt | ID = 10
Description =

Error - 27/03/2011 09:32:06 | Computer Name = Dan-PC | Source = WinMgmt | ID = 10
Description =

Error - 28/03/2011 04:29:27 | Computer Name = Dan-PC | Source = WinMgmt | ID = 10
Description =

Error - 28/03/2011 06:52:50 | Computer Name = Dan-PC | Source = WinMgmt | ID = 10
Description =

Error - 28/03/2011 08:49:54 | Computer Name = Dan-PC | Source = WinMgmt | ID = 10
Description =

[ System Events ]
Error - 29/03/2011 14:05:14 | Computer Name = Dan-PC | Source = Service Control Manager | ID = 7011
Description =

Error - 29/03/2011 14:05:44 | Computer Name = Dan-PC | Source = Service Control Manager | ID = 7011
Description =

Error - 29/03/2011 14:06:14 | Computer Name = Dan-PC | Source = Service Control Manager | ID = 7011
Description =

Error - 29/03/2011 14:06:26 | Computer Name = Dan-PC | Source = WinDefend | ID = 2004
Description = %%827 has encountered an error trying to load signatures and will
attempt reverting back to a known-good set of signatures.	 Signatures Attempted: %%824

	Error
 Code: 0x8050a001	 Error description: The program can't find definition files that
 help detect unwanted software. Check for updates to the definition files, and then
 try again. For information on installing updates, see Help and Support.	  Signatures
 loading: %%825	 Loading signature version: 1.101.118.0	 Loading engine version: 1.1.6603.0

Error - 29/03/2011 14:06:44 | Computer Name = Dan-PC | Source = Service Control Manager | ID = 7011
Description =

Error - 29/03/2011 14:07:14 | Computer Name = Dan-PC | Source = Service Control Manager | ID = 7011
Description =

Error - 30/03/2011 01:58:19 | Computer Name = Dan-PC | Source = Microsoft-Windows-WindowsUpdateClient | ID = 20
Description =

Error - 30/03/2011 17:51:56 | Computer Name = Dan-PC | Source = DCOM | ID = 10016
Description =

Error - 30/03/2011 17:52:01 | Computer Name = Dan-PC | Source = DCOM | ID = 10016
Description =

Error - 30/03/2011 17:52:05 | Computer Name = Dan-PC | Source = DCOM | ID = 10016
Description =


< End of report >