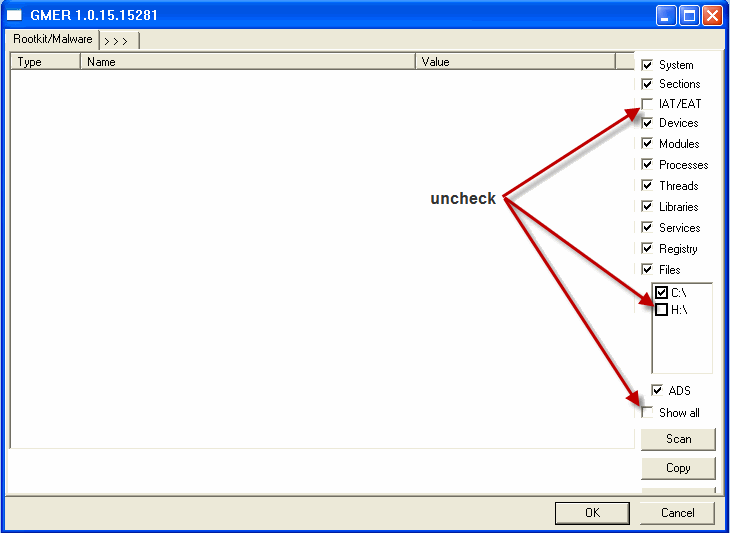
Here are the results Catbyte,
OTL logfile created on: 8/10/2010 12:49:11 PM - Run 1
OTL by OldTimer - Version 3.2.9.1 Folder = C:\Users\Bryan\Desktop
64bit- Home Premium Edition (Version = 6.1.7600) - Type = NTWorkstation
Internet Explorer (Version = 8.0.7600.16385)
Locale: 00000409 | Country: United States | Language: ENU | Date Format: M/d/yyyy
4.00 Gb Total Physical Memory | 3.00 Gb Available Physical Memory | 75.00% Memory free
7.00 Gb Paging File | 6.00 Gb Available in Paging File | 82.00% Paging File free
Paging file location(s): ?:\pagefile.sys [binary data]
%SystemDrive% = C: | %SystemRoot% = C:\Windows | %ProgramFiles% = C:\Program Files (x86)
Drive C: | 684.87 Gb Total Space | 570.14 Gb Free Space | 83.25% Space Free | Partition Type: NTFS
D: Drive not present or media not loaded
E: Drive not present or media not loaded
F: Drive not present or media not loaded
G: Drive not present or media not loaded
H: Drive not present or media not loaded
I: Drive not present or media not loaded
Computer Name: FAMILY
Current User Name: Bryan
Logged in as Administrator.
Current Boot Mode: Normal
Scan Mode: Current user
Include 64bit Scans
Company Name Whitelist: On
Skip Microsoft Files: On
File Age = 90 Days
Output = Minimal
Quick Scan
========== Processes (SafeList) ==========
PRC - C:\Windows\SysWow64\oem\SetEvent.exe File not found
PRC - C:\Users\Bryan\Desktop\OTL.exe (OldTimer Tools)
PRC - C:\Program Files (x86)\Online Armor\oacat.exe (Emsi Software GmbH)
PRC - C:\Windows\SysWOW64\PnkBstrB.exe ()
PRC - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbarUser_32.exe (Google Inc.)
PRC - C:\Program Files\Alwil Software\Avast5\AvastUI.exe (AVAST Software)
PRC - C:\Program Files\Alwil Software\Avast5\AvastSvc.exe (AVAST Software)
PRC - C:\Program Files (x86)\OpenDNS Updater\OpenDNSUpdater.exe ()
PRC - C:\Program Files (x86)\Secunia\PSI\psi.exe (Secunia)
PRC - C:\Windows\SysWOW64\PnkBstrA.exe ()
PRC - C:\Program Files (x86)\Microsoft\Search Enhancement Pack\SCServer\SCServer.exe (Microsoft Corporation)
PRC - C:\Program Files (x86)\Microsoft\Search Enhancement Pack\SeaPort\SeaPort.exe (Microsoft Corporation)
PRC - C:\Program Files (x86)\Common Files\Oberon Media\Parts\1.0.0.11\OberonParts.exe (Oberon Media)
PRC - C:\Program Files (x86)\HostsMan\hostssrv.exe (abelhadigital.com)
PRC - C:\Program Files (x86)\Razer\Lachesis\razerhid.exe ()
PRC - C:\Program Files (x86)\Razer\Lachesis\razertra.exe ()
PRC - C:\Program Files (x86)\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe (Google Inc.)
PRC - C:\Program Files (x86)\EgisTec\MyWinLocker 3\x86\MWLService.exe (Egis Technology Inc.)
PRC - C:\Program Files (x86)\Acer\Registration\GregHSRW.exe (Acer Incorporated)
PRC - C:\Program Files (x86)\NewTech Infosystems\Acer Backup Manager\IScheduleSvc.exe (NewTech Infosystems, Inc.)
PRC - C:\Program Files\Acer\Acer Updater\UpdaterService.exe (Acer)
PRC - C:\Program Files (x86)\Razer\Lachesis\OSD.exe (razercfg MFC Application)
PRC - C:\Program Files (x86)\Razer\Lachesis\razerofa.exe (Razer Inc.)
========== Modules (SafeList) ==========
MOD - C:\Users\Bryan\Desktop\OTL.exe (OldTimer Tools)
MOD - C:\Windows\SysWOW64\msscript.ocx (Microsoft Corporation)
MOD - C:\Windows\winsxs\x86_microsoft.windows.common-controls_6595b64144ccf1df_6.0.7600.16385_none_421189da2b7fabfc\comctl32.dll (Microsoft Corporation)
========== Win32 Services (SafeList) ==========
SRV:
64bit: - (PnkBstrB) – C:\Windows\SysNative\PnkBstrB.exe File not found
SRV:
64bit: - (PnkBstrA) – C:\Windows\SysNative\PnkBstrA.exe File not found
SRV:
64bit: - (avast! Web Scanner) – C:\Program Files\Alwil Software\Avast5\AvastSvc.exe (AVAST Software)
SRV:
64bit: - (avast! Mail Scanner) – C:\Program Files\Alwil Software\Avast5\AvastSvc.exe (AVAST Software)
SRV:
64bit: - (avast! Antivirus) – C:\Program Files\Alwil Software\Avast5\AvastSvc.exe (AVAST Software)
SRV:
64bit: - (!SASCORE) – C:\Program Files\SUPERAntiSpyware\SASCORE64.EXE (SUPERAntiSpyware.com)
SRV:
64bit: - (SbieSvc) – C:\Program Files\Sandboxie\SbieSvc.exe (tzuk)
SRV:
64bit: - (wlidsvc) – C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSVC.EXE (Microsoft Corporation)
SRV:
64bit: - (WinDefend) – C:\Program Files\Windows Defender\MpSvc.dll (Microsoft Corporation)
SRV:
64bit: - (Updater Service) – C:\Program Files\Acer\Acer Updater\UpdaterService.exe (Acer)
SRV:
64bit: - (ForceWare Intelligent Application Manager (IAM)) – C:\Program Files\NVIDIA Corporation\NetworkAccessManager\bin32\nSvcAppFlt.exe ()
SRV:
64bit: - (nSvcIp) – C:\Program Files\NVIDIA Corporation\NetworkAccessManager\bin32\nSvcIp.exe ()
SRV - (SvcOnlineArmor) – C:\Program Files (x86)\Online Armor\oasrv.exe (Emsi Software GmbH)
SRV - (OAcat) – C:\Program Files (x86)\Online Armor\OAcat.exe (Emsi Software GmbH)
SRV - (PnkBstrB) – C:\Windows\SysWOW64\PnkBstrB.exe ()
SRV - (Steam Client Service) – C:\Program Files (x86)\Common Files\Steam\SteamService.exe (Valve Corporation)
SRV - (GoogleDesktopManager-051210-111108) – C:\Program Files (x86)\Google\Google Desktop Search\GoogleDesktop.exe (Google)
SRV - (PnkBstrA) – C:\Windows\SysWOW64\PnkBstrA.exe ()
SRV - (SeaPort) – C:\Program Files (x86)\Microsoft\Search Enhancement Pack\SeaPort\SeaPort.exe (Microsoft Corporation)
SRV - (fsssvc) – C:\Program Files (x86)\Windows Live\Family Safety\fsssvc.exe (Microsoft Corporation)
SRV - (GameConsoleService) – C:\Program Files (x86)\Acer Games\Acer Game Console\GameConsoleService.exe (WildTangent, Inc.)
SRV - (clr_optimization_v4.0.30319_64) – C:\Windows\Microsoft.NET\Framework64\v4.0.30319\mscorsvw.exe (Microsoft Corporation)
SRV - (clr_optimization_v4.0.30319_32) – C:\Windows\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe (Microsoft Corporation)
SRV - (MWLService) – C:\Program Files (x86)\EgisTec\MyWinLocker 3\x86\\MWLService.exe ()
SRV - (Greg_Service) – C:\Program Files (x86)\Acer\Registration\GregHSRW.exe (Acer Incorporated)
SRV - (Nero BackItUp Scheduler 4.0) – C:\Program Files (x86)\Common Files\Nero\Nero BackItUp 4\NBService.exe (Nero AG)
SRV - (NTI IScheduleSvc) – C:\Program Files (x86)\NewTech Infosystems\Acer Backup Manager\IScheduleSvc.exe (NewTech Infosystems, Inc.)
========== Driver Services (SafeList) ==========
DRV:
64bit: - (OAnet) – C:\Windows\SysNative\drivers\OAnet.sys (Emsisoft)
DRV:
64bit: - (aswMonFlt) – C:\Windows\SysNative\drivers\aswMonFlt.sys (ALWIL Software)
DRV:
64bit: - (pxrts) – C:\Windows\SysNative\drivers\pxrts.sys (Prevx)
DRV:
64bit: - (pxscan) – C:\Windows\SysNative\drivers\pxscan.sys (Prevx)
DRV:
64bit: - (PSI) – C:\Windows\SysNative\drivers\psi_mf.sys (Secunia)
DRV:
64bit: - (MEMSWEEP2) – C:\Windows\SysNative\5AFC.tmp (Sophos Plc)
DRV:
64bit: - (fssfltr) – C:\Windows\SysNative\drivers\fssfltr.sys (Microsoft Corporation)
DRV:
64bit: - (SbieDrv) – C:\Program Files\Sandboxie\SbieDrv.sys (tzuk)
DRV:
64bit: - (pwdrvio) – C:\Windows\SysNative\pwdrvio.sys ()
DRV:
64bit: - (pwdspio) – C:\Windows\SysNative\pwdspio.sys ()
DRV:
64bit: - (SASDIFSV) – C:\Program Files\SUPERAntiSpyware\sasdifsv64.sys (SUPERAdBlocker.com and SUPERAntiSpyware.com)
DRV:
64bit: - (SASKUTIL) – C:\Program Files\SUPERAntiSpyware\saskutil64.sys (SUPERAdBlocker.com and SUPERAntiSpyware.com)
DRV:
64bit: - (NVNET) – C:\Windows\SysNative\drivers\nvmf6264.sys (NVIDIA Corporation)
DRV:
64bit: - (amdsata) – C:\Windows\SysNative\drivers\amdsata.sys (Advanced Micro Devices)
DRV:
64bit: - (amdxata) – C:\Windows\SysNative\drivers\amdxata.sys (Advanced Micro Devices)
DRV:
64bit: - (amdsbs) – C:\Windows\SysNative\drivers\amdsbs.sys (AMD Technologies Inc.)
DRV:
64bit: - (LSI_SAS2) – C:\Windows\SysNative\drivers\lsi_sas2.sys (LSI Corporation)
DRV:
64bit: - (HpSAMD) – C:\Windows\SysNative\drivers\HpSAMD.sys (Hewlett-Packard Company)
DRV:
64bit: - (stexstor) – C:\Windows\SysNative\drivers\stexstor.sys (Promise Technology)
DRV:
64bit: - (NVHDA) – C:\Windows\SysNative\drivers\nvhda64v.sys (NVIDIA Corporation)
DRV:
64bit: - (Ntfs) – C:\Windows\SysNative\wbem\ntfs.mof ()
DRV:
64bit: - (NVENETFD) – C:\Windows\SysNative\drivers\nvm62x64.sys (NVIDIA Corporation)
DRV:
64bit: - (ebdrv) – C:\Windows\SysNative\drivers\evbda.sys (Broadcom Corporation)
DRV:
64bit: - (b06bdrv) – C:\Windows\SysNative\drivers\bxvbda.sys (Broadcom Corporation)
DRV:
64bit: - (b57nd60a) – C:\Windows\SysNative\drivers\b57nd60a.sys (Broadcom Corporation)
DRV:
64bit: - (hcw85cir) – C:\Windows\SysNative\drivers\hcw85cir.sys (Hauppauge Computer Works, Inc.)
DRV:
64bit: - (SaiNtBus) – C:\Windows\SysNative\drivers\SaiBus.sys (Saitek)
DRV:
64bit: - (SaiMini) – C:\Windows\SysNative\drivers\SaiMini.sys (Saitek)
DRV:
64bit: - (SaiKF622) – C:\Windows\SysNative\drivers\SaiKF622.sys (Saitek)
DRV:
64bit: - (mwlPSDVDisk) – C:\Windows\SysNative\drivers\mwlPSDVDisk.sys (Egis Technology Inc.)
DRV:
64bit: - (mwlPSDFilter) – C:\Windows\SysNative\drivers\mwlPSDFilter.sys (Egis Technology Inc.)
DRV:
64bit: - (mwlPSDNServ) – C:\Windows\SysNative\drivers\mwlPSDNserv.sys (Egis Technology Inc.)
DRV:
64bit: - (NTIDrvr) – C:\Windows\SysNative\drivers\NTIDrvr.sys (NewTech Infosystems, Inc.)
DRV:
64bit: - (UBHelper) – C:\Windows\SysNative\drivers\UBHelper.sys (NewTech Infosystems Corporation)
DRV:
64bit: - (VaneFltr) – C:\Windows\SysNative\drivers\Lachesis.sys (Razer (Asia-Pacific) Pte Ltd)
DRV - (oahlpXX) – C:\Windows\SysWOW64\drivers\oahlp64.sys ()
DRV - (OAmon) – C:\Windows\SysWOW64\drivers\OAmon.sys (Emsisoft)
DRV - (OADevice) – C:\Windows\SysWOW64\drivers\OADriver.sys ()
========== Standard Registry (SafeList) ==========
========== Internet Explorer ==========
IE:
64bit: - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = http://homepage.acer.com/rdr.aspx?b=ACAW&a;…28v1j5w45j1t539
IE - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = http://homepage.acer.com/rdr.aspx?b=ACAW&a;…28v1j5w45j1t539
IE - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Local Page = C:\Windows\SysWOW64\blank.htm
IE - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://homepage.acer.com/rdr.aspx?b=ACAW&a;…28v1j5w45j1t539
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Default_Page_URL = http://homepage.acer.com/rdr.aspx?b=ACAW&a;…28v1j5w45j1t539
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page =
http://www.google.com/
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page Redirect Cache = http://www.msn.com/
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page Redirect Cache AcceptLangs = en-us
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page Redirect Cache_TIMESTAMP = 20 33 D2 BE EF F5 CA 01 [binary data]
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Search,Default_Search_URL = http://www.google.com/ie
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyEnable" = 0
[2010/06/10 21:24:39 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\Mozilla\Extensions
[2010/06/10 21:24:39 | 000,000,000 | —D | M] (No name found) – C:\Users\Bryan\AppData\Roaming\Mozilla\Extensions\{3550f703-e582-4d05-9a08-453d09bdfdc6}
O1 HOSTS File: ([2010/08/06 19:38:17 | 000,601,965 | —- | M]) - C:\Windows\SysNative\drivers\etc\HOSTS
O1 - Hosts: 127.0.0.1 localhost
O1 - Hosts: 127.0.0.1 fr.a2dfp.net
O1 - Hosts: 127.0.0.1 m.fr.a2dfp.net
O1 - Hosts: 127.0.0.1 ad.a8.net
O1 - Hosts: 127.0.0.1 asy.a8ww.net
O1 - Hosts: 127.0.0.1 adserver.abv.bg
O1 - Hosts: 127.0.0.1 adv.abv.bg
O1 - Hosts: 127.0.0.1 bimg.abv.bg
O1 - Hosts: 127.0.0.1 www2.a-counter.kiev.ua
O1 - Hosts: 127.0.0.1 track.acclaimnetwork.com
O1 - Hosts: 127.0.0.1 accuserveadsystem.com
O1 - Hosts: 127.0.0.1 www.accuserveadsystem.com
O1 - Hosts: 127.0.0.1 achmedia.com
O1 - Hosts: 127.0.0.1 aconti.net
O1 - Hosts: 127.0.0.1 secure.aconti.net
O1 - Hosts: 127.0.0.1 www.aconti.net #[Dialer.Aconti]
O1 - Hosts: 127.0.0.1 ads.active.com
O1 - Hosts: 127.0.0.1 am1.activemeter.com
O1 - Hosts: 127.0.0.1 www.activemeter.com #[Tracking.Cookie]
O1 - Hosts: 127.0.0.1 ads.activepower.net
O1 - Hosts: 127.0.0.1 stat.active24stats.nl #[Tracking.Cookie]
O1 - Hosts: 127.0.0.1 ad2games.com
O1 - Hosts: 127.0.0.1 cms.ad2click.nl
O1 - Hosts: 127.0.0.1 ads.ad2games.com
O1 - Hosts: 127.0.0.1 content.ad20.net
O1 - Hosts: 16333 more lines…
O2:
64bit: - BHO: (Windows Live Family Safety Browser Helper Class) - {4f3ed5cd-0726-42a9-87f5-d13f3d2976ac} - C:\Program Files\Windows Live\Family Safety\fssbho.dll (Microsoft Corporation)
O2:
64bit: - BHO: (Windows Live ID Sign-in Helper) - {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll (Microsoft Corporation)
O2:
64bit: - BHO: (Google Toolbar Helper) - {AA58ED58-01DD-4d91-8333-CF10577473F7} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll (Google Inc.)
O2:
64bit: - BHO: (Google Toolbar Notifier BHO) - {AF69DE43-7D58-4638-B6FA-CE66B5AD205D} - C:\Program Files\Google\GoogleToolbarNotifier\5.5.5126.1836\swg64.dll (Google Inc.)
O2 - BHO: (no name) - {02478D38-C3F9-4efb-9B51-7695ECA05670} - No CLSID value found.
O2 - BHO: (Search Helper) - {6EBF7485-159F-4bff-A14F-B9E3AAC4465B} - C:\Program Files (x86)\Microsoft\Search Enhancement Pack\Search Helper\SEPsearchhelperie.dll (Microsoft Corporation)
O2 - BHO: (Google Toolbar Helper) - {AA58ED58-01DD-4d91-8333-CF10577473F7} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll (Google Inc.)
O2 - BHO: (Google Toolbar Notifier BHO) - {AF69DE43-7D58-4638-B6FA-CE66B5AD205D} - C:\Program Files (x86)\Google\GoogleToolbarNotifier\5.5.5126.1836\swg.dll (Google Inc.)
O2 - BHO: (no name) - {C84D72FE-E17D-4195-BB24-76C02E2E7C4E} - No CLSID value found.
O2 - BHO: (WOT Helper) - {C920E44A-7F78-4E64-BDD7-A57026E7FEB7} - C:\Program Files (x86)\WOT\WOT.dll ()
O2 - BHO: (GamesBarBHO Class) - {CB0D163C-E9F4-4236-9496-0597E24B23A5} - C:\Program Files (x86)\GamesBar\2.0.1.53\oberontb.dll (Oberon Media Ltd.)
O2 - BHO: (Windows Live Toolbar Helper) - {E15A8DC0-8516-42A1-81EA-DC94EC1ACF10} - C:\Program Files (x86)\Windows Live\Toolbar\wltcore.dll (Microsoft Corporation)
O3:
64bit: - HKLM\..\Toolbar: (Google Toolbar) - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll (Google Inc.)
O3 - HKLM\..\Toolbar: (&Windows; Live Toolbar) - {21FA44EF-376D-4D53-9B0F-8A89D3229068} - C:\Program Files (x86)\Windows Live\Toolbar\wltcore.dll (Microsoft Corporation)
O3 - HKLM\..\Toolbar: (Google Toolbar) - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll (Google Inc.)
O3 - HKLM\..\Toolbar: (GamesBar) - {6F282B65-56BF-4BD1-A8B2-A4449A05863D} - C:\Program Files (x86)\GamesBar\2.0.1.53\oberontb.dll (Oberon Media Ltd.)
O3 - HKLM\..\Toolbar: (WOT) - {71576546-354D-41c9-AAE8-31F2EC22BF0D} - C:\Program Files (x86)\WOT\WOT.dll ()
O3 - HKCU\..\Toolbar\WebBrowser: (&Windows; Live Toolbar) - {21FA44EF-376D-4D53-9B0F-8A89D3229068} - C:\Program Files (x86)\Windows Live\Toolbar\wltcore.dll (Microsoft Corporation)
O3:
64bit: - HKCU\..\Toolbar\WebBrowser: (Google Toolbar) - {2318C2B1-4965-11D4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll (Google Inc.)
O3 - HKCU\..\Toolbar\WebBrowser: (Google Toolbar) - {2318C2B1-4965-11D4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll (Google Inc.)
O3 - HKCU\..\Toolbar\WebBrowser: (WOT) - {71576546-354D-41C9-AAE8-31F2EC22BF0D} - C:\Program Files (x86)\WOT\WOT.dll ()
O4:
64bit: - HKLM..\Run: [@OnlineArmor GUI] C:\Program Files (x86)\Online Armor\oaui.exe (Emsi Software GmbH)
O4:
64bit: - HKLM..\Run: [PLD_FrameworkRun] C:\Windows\SysNative\OEM\_NowIntoDT.vbs ()
O4:
64bit: - HKLM..\Run: [RtHDVCpl] C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe (Realtek Semiconductor)
O4 - HKLM..\Run: [avast5] C:\Program Files\Alwil Software\Avast5\avastUI.exe (AVAST Software)
O4 - HKLM..\Run: [Lachesis] C:\Program Files (x86)\Razer\Lachesis\razerhid.exe ()
O4 - HKCU..\Run: [HostsServer] C:\Program Files (x86)\HostsMan\hostssrv.exe (abelhadigital.com)
O4 - HKCU..\Run: [OpenDNS Updater] C:\Program Files (x86)\OpenDNS Updater\OpenDNSUpdater.exe ()
O4 - HKCU..\Run: [RESTART_STICKY_NOTES] C:\Windows\SysWOW64\StikyNot.exe ()
O4 - HKCU..\Run: [swg] C:\Program Files (x86)\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe (Google Inc.)
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoActiveDesktop = 1
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: EnableShellExecuteHooks = 1
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: ConsentPromptBehaviorAdmin = 5
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: ConsentPromptBehaviorUser = 3
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDriveTypeAutoRun = 145
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: LogonHoursAction = 2
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: DontDisplayLogonHoursWarnings = 1
O8:
64bit: - Extra context menu item: Google Sidewiki… - C:\Program Files (x86)\Google\Google Toolbar\Component\GoogleToolbarDynamic_mui_en_89D8574934B26AC4.dll (Google Inc.)
O8 - Extra context menu item: Add to Google Photos Screensa&ver; - C:\Windows\SysWow64\GPhotos.scr (Google Inc.)
O8 - Extra context menu item: Google Sidewiki… - C:\Program Files (x86)\Google\Google Toolbar\Component\GoogleToolbarDynamic_mui_en_89D8574934B26AC4.dll (Google Inc.)
O9 - Extra 'Tools' menuitem : GamesBar - {1A93C934-025B-4c3a-B38E-9654A7003239} - Reg Error: Value error. File not found
O9 - Extra Button: Blog This - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files (x86)\Windows Live\Writer\WriterBrowserExtension.dll (Microsoft Corporation)
O9 - Extra 'Tools' menuitem : &Blog; This in Windows Live Writer - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files (x86)\Windows Live\Writer\WriterBrowserExtension.dll (Microsoft Corporation)
O9 - Extra Button: PokerStars - {3AD14F0C-ED16-4e43-B6D8-661B03F6A1EF} - C:\Program Files (x86)\PokerStars\PokerStarsUpdate.exe (PokerStars)
O9 - Extra 'Tools' menuitem : Spybot - Search && Destroy Configuration - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - Reg Error: Key error. File not found
O10:
64bit: - NameSpace_Catalog5\Catalog_Entries\000000000007 [] - C:\Program Files (x86)\Common Files\microsoft shared\Windows Live\WLIDNSP.DLL (Microsoft Corporation)
O10:
64bit: - NameSpace_Catalog5\Catalog_Entries\000000000008 [] - C:\Program Files (x86)\Common Files\microsoft shared\Windows Live\WLIDNSP.DLL (Microsoft Corporation)
O10:
64bit: - Protocol_Catalog9\Catalog_Entries\000000000001 - C:\Windows\SysNative\nvLsp.dll File not found
O10:
64bit: - Protocol_Catalog9\Catalog_Entries\000000000002 - C:\Windows\SysNative\nvLsp.dll File not found
O10:
64bit: - Protocol_Catalog9\Catalog_Entries\000000000003 - C:\Windows\SysNative\nvLsp.dll File not found
O10:
64bit: - Protocol_Catalog9\Catalog_Entries\000000000004 - C:\Windows\SysNative\nvLsp.dll File not found
O10:
64bit: - Protocol_Catalog9\Catalog_Entries\000000000005 - C:\Windows\SysNative\nvLsp.dll File not found
O10:
64bit: - Protocol_Catalog9\Catalog_Entries\000000000006 - C:\Windows\SysNative\nvLsp.dll File not found
O10:
64bit: - Protocol_Catalog9\Catalog_Entries\000000000017 - C:\Windows\SysNative\nvLsp.dll File not found
O10:
64bit: - Protocol_Catalog9\Catalog_Entries\000000000018 - C:\Windows\SysNative\nvLsp.dll File not found
O10 - NameSpace_Catalog5\Catalog_Entries\000000000007 [] - C:\Program Files (x86)\Common Files\microsoft shared\Windows Live\WLIDNSP.DLL (Microsoft Corporation)
O10 - NameSpace_Catalog5\Catalog_Entries\000000000008 [] - C:\Program Files (x86)\Common Files\microsoft shared\Windows Live\WLIDNSP.DLL (Microsoft Corporation)
O10 - Protocol_Catalog9\Catalog_Entries\000000000001 - C:\Windows\SysWOW64\nvLsp.dll (NVIDIA)
O10 - Protocol_Catalog9\Catalog_Entries\000000000002 - C:\Windows\SysWOW64\nvLsp.dll (NVIDIA)
O10 - Protocol_Catalog9\Catalog_Entries\000000000003 - C:\Windows\SysWOW64\nvLsp.dll (NVIDIA)
O10 - Protocol_Catalog9\Catalog_Entries\000000000004 - C:\Windows\SysWOW64\nvLsp.dll (NVIDIA)
O10 - Protocol_Catalog9\Catalog_Entries\000000000005 - C:\Windows\SysWOW64\nvLsp.dll (NVIDIA)
O10 - Protocol_Catalog9\Catalog_Entries\000000000006 - C:\Windows\SysWOW64\nvLsp.dll (NVIDIA)
O10 - Protocol_Catalog9\Catalog_Entries\000000000017 - C:\Windows\SysWOW64\nvLsp.dll (NVIDIA)
O10 - Protocol_Catalog9\Catalog_Entries\000000000018 - C:\Windows\SysWOW64\nvLsp.dll (NVIDIA)
O13 - gopher Prefix: missing
O13 - gopher Prefix: missing
O15 - HKCU\..Trusted Domains: gmail.com ([]https in Trusted sites)
O15 - HKCU\..Trusted Domains: google.com ([www] https in Trusted sites)
O15 - HKCU\..Trusted Domains: localhost ([]http in Local intranet)
O15 - HKCU\..Trusted Ranges: GD ([http] in Local intranet)
O16 - DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93}
http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_21)
O16 - DPF: {CAFEEFAC-0016-0000-0021-ABCDEFFEDCBA}
http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_21)
O16 - DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA}
http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Reg Error: Key error.)
O16 - DPF: {0742B9EF-8C83-41CA-BFBA-830A59E23533} https://oas.support.microsoft.com/ActiveX/MSDcode.cab (Microsoft Data Collection Control)
O16 - DPF: {0E5F0222-96B9-11D3-8997-00104BD12D94} http://www.pcpitstop.com/betapit/PCPitStop.CAB (PCPitstop Utility)
O16 - DPF: {140E4DF8-9E14-4A34-9577-C77561ED7883} http://content.systemrequirementslab.com.s…ri_4.1.71.0.cab (SysInfo Class)
O16 - DPF: {3107C2A8-9F0B-4404-A58B-21BD85268FBC}
http://www.pogo.com/cdl/launcher/PogoWebLa…erInstaller.CAB (PogoWebLauncher Control)
O16 - DPF: {5D86DDB5-BDF9-441B-9E9E-D4730F4EE499} http://download.bitdefender.com/resources/…can8/oscan8.cab (BDSCANONLINE Control)
O16 - DPF: {7530BFB8-7293-4D34-9923-61A11451AFC5}
http://download.eset.com/special/eos/OnlineScanner.cab (OnlineScanner Control)
O16 - DPF: {784797A8-342D-4072-9486-03C8D0F2F0A1} https://www.battlefieldheroes.com/static/up…er_4.0.53.0.cab (Battlefield Heroes Updater)
O16 - DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_20)
O16 - DPF: {A27C56D2-3F58-4ABB-AA31-1168EDA6636F}
http://utilities.pcpitstop.com/Nirvana/controls/pcmatic.cab (PCMaticVer Class)
O16 - DPF: {CAFEEFAC-0016-0000-0020-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_20)
O16 - DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_20)
O16 - DPF: {E2883E8F-472F-4FB0-9522-AC9BF37916A7}
http://platformdl.adobe.com/NOS/getPlusPlus/1.6/gp.cab (Reg Error: Key error.)
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: DhcpNameServer = [removed] [removed]
O18:
64bit: - Protocol\Handler\belarc {6318E0AB-2E93-11D1-B8ED-00608CC9A71F} - Reg Error: Key error. File not found
O18:
64bit: - Protocol\Handler\livecall {828030A1-22C1-4009-854F-8E305202313F} - Reg Error: Key error. File not found
O18:
64bit: - Protocol\Handler\ms-itss {0A9007C0-4076-11D3-8789-0000F8105754} - Reg Error: Key error. File not found
O18:
64bit: - Protocol\Handler\msnim {828030A1-22C1-4009-854F-8E305202313F} - Reg Error: Key error. File not found
O18:
64bit: - Protocol\Handler\wlmailhtml {03C514A3-1EFB-4856-9F99-10D7BE1653C0} - Reg Error: Key error. File not found
O18:
64bit: - Protocol\Handler\wot {C2A44D6B-CB9F-4663-88A6-DF2F26E4D952} - Reg Error: Key error. File not found
O18 - Protocol\Handler\belarc {6318E0AB-2E93-11D1-B8ED-00608CC9A71F} - C:\Program Files (x86)\Belarc\Advisor\System\BAVoilaX.dll (Belarc, Inc.)
O18 - Protocol\Handler\livecall {828030A1-22C1-4009-854F-8E305202313F} - C:\Program Files (x86)\Windows Live\Messenger\msgrapp.14.0.8117.0416.dll (Microsoft Corporation)
O18 - Protocol\Handler\msnim {828030A1-22C1-4009-854F-8E305202313F} - C:\Program Files (x86)\Windows Live\Messenger\msgrapp.14.0.8117.0416.dll (Microsoft Corporation)
O18 - Protocol\Handler\wot {C2A44D6B-CB9F-4663-88A6-DF2F26E4D952} - C:\Program Files (x86)\WOT\WOT.dll ()
O20 - AppInit_DLLs: (C:\PROGRA~2\Google\GOOGLE~3\GO36F4~1.DLL) - C:\Program Files (x86)\Google\Google Desktop Search\GoogleDesktopNetwork3.dll (Google)
O20:
64bit: - HKLM Winlogon: Shell - (explorer.exe) - C:\Windows\explorer.exe (Microsoft Corporation)
O20:
64bit: - HKLM Winlogon: VMApplet - (SystemPropertiesPerformance.exe) - C:\Windows\SysNative\SystemPropertiesPerformance.exe (Microsoft Corporation)
O20:
64bit: - HKLM Winlogon: VMApplet - (/pagefile) - File not found
O20 - HKLM Winlogon: Shell - (explorer.exe) - C:\Windows\SysWow64\explorer.exe (Microsoft Corporation)
O20 - HKLM Winlogon: VMApplet - (SystemPropertiesPerformance.exe) - C:\Windows\SysWow64\SystemPropertiesPerformance.exe (Microsoft Corporation)
O20 - HKLM Winlogon: VMApplet - (/pagefile) - File not found
O21:
64bit: - SSODL: WebCheck - {E6FB5E20-DE35-11CF-9C87-00AA005127ED} - CLSID or File not found.
O21 - SSODL: WebCheck - {E6FB5E20-DE35-11CF-9C87-00AA005127ED} - CLSID or File not found.
O30:
64bit: - LSA: Security Packages - (livessp) - C:\Windows\SysNative\livessp.dll (Microsoft Corporation)
O30 - LSA: Security Packages - (livessp) - C:\Windows\SysWow64\livessp.dll (Microsoft Corporation)
O32 - HKLM CDRom: AutoRun - 1
O34 - HKLM BootExecute: (autocheck autochk *) - File not found
O35:
64bit: - HKLM\..comfile [open] – "%1" %*
O35:
64bit: - HKLM\..exefile [open] – "%1" %*
O35 - HKLM\..comfile [open] – "%1" %*
O35 - HKLM\..exefile [open] – "%1" %*
O37:
64bit: - HKLM\…com [@ = comfile] – "%1" %*
O37:
64bit: - HKLM\…exe [@ = exefile] – "%1" %*
O37 - HKLM\…com [@ = comfile] – "%1" %*
O37 - HKLM\…exe [@ = exefile] – "%1" %*
Drivers32:
64bit: aux - wdmaud.drv (Microsoft Corporation)
Drivers32:
64bit: midi - wdmaud.drv (Microsoft Corporation)
Drivers32:
64bit: midi1 - wdmaud.drv (Microsoft Corporation)
Drivers32:
64bit: midimapper - midimap.dll (Microsoft Corporation)
Drivers32:
64bit: mixer - wdmaud.drv (Microsoft Corporation)
Drivers32:
64bit: mixer1 - wdmaud.drv (Microsoft Corporation)
Drivers32:
64bit: msacm.imaadpcm - imaadp32.acm (Microsoft Corporation)
Drivers32:
64bit: msacm.l3acm - C:\Windows\System32\l3codeca.acm (Fraunhofer Institut Integrierte Schaltungen IIS)
Drivers32:
64bit: msacm.msadpcm - msadp32.acm (Microsoft Corporation)
Drivers32:
64bit: msacm.msg711 - msg711.acm (Microsoft Corporation)
Drivers32:
64bit: msacm.msgsm610 - msgsm32.acm (Microsoft Corporation)
Drivers32:
64bit: vidc.i420 - iyuv_32.dll (Microsoft Corporation)
Drivers32:
64bit: vidc.iyuv - iyuv_32.dll (Microsoft Corporation)
Drivers32:
64bit: vidc.mrle - msrle32.dll (Microsoft Corporation)
Drivers32:
64bit: vidc.msvc - msvidc32.dll (Microsoft Corporation)
Drivers32:
64bit: vidc.uyvy - msyuv.dll (Microsoft Corporation)
Drivers32:
64bit: vidc.yuy2 - msyuv.dll (Microsoft Corporation)
Drivers32:
64bit: vidc.yvu9 - tsbyuv.dll (Microsoft Corporation)
Drivers32:
64bit: vidc.yvyu - msyuv.dll (Microsoft Corporation)
Drivers32:
64bit: wave - wdmaud.drv (Microsoft Corporation)
Drivers32:
64bit: wave1 - wdmaud.drv (Microsoft Corporation)
Drivers32:
64bit: wavemapper - msacm32.drv (Microsoft Corporation)
Drivers32: aux - C:\Windows\SysWow64\wdmaud.drv (Microsoft Corporation)
Drivers32: midi - C:\Windows\SysWow64\wdmaud.drv (Microsoft Corporation)
Drivers32: midi1 - C:\Windows\SysWow64\wdmaud.drv (Microsoft Corporation)
Drivers32: midimapper - C:\Windows\SysWow64\midimap.dll (Microsoft Corporation)
Drivers32: mixer - C:\Windows\SysWow64\wdmaud.drv (Microsoft Corporation)
Drivers32: mixer1 - C:\Windows\SysWow64\wdmaud.drv (Microsoft Corporation)
Drivers32: msacm.imaadpcm - C:\Windows\SysWow64\imaadp32.acm (Microsoft Corporation)
Drivers32: msacm.l3acm - C:\Windows\SysWOW64\l3codeca.acm (Fraunhofer Institut Integrierte Schaltungen IIS)
Drivers32: msacm.msadpcm - C:\Windows\SysWow64\msadp32.acm (Microsoft Corporation)
Drivers32: msacm.msg711 - C:\Windows\SysWow64\msg711.acm (Microsoft Corporation)
Drivers32: msacm.msgsm610 - C:\Windows\SysWow64\msgsm32.acm (Microsoft Corporation)
Drivers32: msacm.siren - C:\Windows\SysWow64\sirenacm.dll (Microsoft Corporation)
Drivers32: vidc.cvid - C:\Windows\SysWow64\iccvid.dll (Radius Inc.)
Drivers32: vidc.i420 - C:\Windows\SysWow64\iyuv_32.dll (Microsoft Corporation)
Drivers32: vidc.iyuv - C:\Windows\SysWow64\iyuv_32.dll (Microsoft Corporation)
Drivers32: vidc.mrle - C:\Windows\SysWow64\msrle32.dll (Microsoft Corporation)
Drivers32: vidc.msvc - C:\Windows\SysWow64\msvidc32.dll (Microsoft Corporation)
Drivers32: vidc.uyvy - C:\Windows\SysWow64\msyuv.dll (Microsoft Corporation)
Drivers32: vidc.yuy2 - C:\Windows\SysWow64\msyuv.dll (Microsoft Corporation)
Drivers32: vidc.yvu9 - C:\Windows\SysWow64\tsbyuv.dll (Microsoft Corporation)
Drivers32: vidc.yvyu - C:\Windows\SysWow64\msyuv.dll (Microsoft Corporation)
Drivers32: wave - C:\Windows\SysWow64\wdmaud.drv (Microsoft Corporation)
Drivers32: wave1 - C:\Windows\SysWow64\wdmaud.drv (Microsoft Corporation)
Drivers32: wavemapper - C:\Windows\SysWow64\msacm32.drv (Microsoft Corporation)
CREATERESTOREPOINT
Error creating restore point.
========== Files/Folders - Created Within 90 Days ==========
[2010/08/10 12:44:43 | 000,574,976 | —- | C] (OldTimer Tools) – C:\Users\Bryan\Desktop\OTL.exe
[2010/08/09 13:19:22 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\OnlineArmor
[2010/08/09 13:19:22 | 000,000,000 | —D | C] – C:\ProgramData\OnlineArmor
[2010/08/09 13:14:08 | 020,085,840 | —- | C] (Emsi Software GmbH ) – C:\Users\Bryan\Desktop\OnlineArmor_Setup.exe
[2010/08/09 12:40:57 | 000,425,568 | —- | C] (Emsi Software GmbH) – C:\Windows\oaevent.dll
[2010/08/09 12:40:57 | 000,037,800 | —- | C] (Emsisoft) – C:\Windows\SysWow64\drivers\OAmon.sys
[2010/08/09 12:40:57 | 000,032,656 | —- | C] (Emsisoft) – C:\Windows\SysNative\drivers\OAnet.sys
[2010/08/09 12:40:54 | 000,000,000 | —D | C] – C:\Program Files (x86)\Online Armor
[2010/08/06 22:20:43 | 000,000,000 | -HSD | C] – C:\found.000
[2010/07/29 13:05:05 | 000,000,000 | —D | C] – C:\ProgramData\PICTUREKA! MUSEUM MAYHEM
[2010/07/29 11:56:00 | 000,000,000 | —D | C] – C:\ProgramData\GamesBar
[2010/07/29 11:55:57 | 000,000,000 | —D | C] – C:\Program Files (x86)\Common Files\Oberon Media
[2010/07/29 11:55:57 | 000,000,000 | —D | C] – C:\Program Files (x86)\GamesBar
[2010/07/26 14:02:49 | 000,468,480 | —- | C] (Oracle) – C:\Windows\SysNative\deployJava1.dll
[2010/07/26 14:02:49 | 000,183,296 | —- | C] (Oracle) – C:\Windows\SysNative\javaws.exe
[2010/07/26 14:02:49 | 000,165,888 | —- | C] (Oracle) – C:\Windows\SysNative\javaw.exe
[2010/07/26 14:02:49 | 000,165,888 | —- | C] (Oracle) – C:\Windows\SysNative\java.exe
[2010/07/26 14:02:34 | 000,000,000 | —D | C] – C:\Program Files\Java
[2010/07/22 16:03:19 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Local\Spencerberus.com
[2010/07/22 15:48:52 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\SystemNucleus
[2010/07/22 15:48:06 | 000,000,000 | —D | C] – C:\Program Files\System Nucleus
[2010/07/22 12:00:15 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\Panda Security
[2010/07/22 11:59:27 | 000,000,000 | —D | C] – C:\ProgramData\Panda Security
[2010/07/22 11:59:27 | 000,000,000 | —D | C] – C:\Program Files (x86)\Panda Security
[2010/07/18 10:38:37 | 000,000,000 | —D | C] – C:\Program Files (x86)\Common Files\Adobe
[2010/07/15 00:07:14 | 000,000,000 | —D | C] – C:\ProgramData\Belkin
[2010/07/15 00:05:18 | 000,000,000 | —D | C] – C:\Program Files (x86)\Belkin
[2010/07/14 20:48:25 | 000,000,000 | —D | C] – C:\Program Files (x86)\PokerStars
[2010/07/14 19:09:32 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Local\PokerStars.NET
[2010/07/14 19:09:08 | 000,000,000 | —D | C] – C:\Program Files (x86)\PokerStars.NET
[2010/07/11 14:14:26 | 000,000,000 | —D | C] – C:\ProgramData\F-Secure
[2010/07/08 18:52:02 | 000,000,000 | —D | C] – C:\Program Files\SDExplorer
[2010/07/08 18:51:53 | 000,000,000 | —D | C] – C:\Users\Bryan\Documents\SDExplorer Logs
[2010/07/03 20:07:05 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\Razer
[2010/07/03 16:08:29 | 000,000,000 | —D | C] – C:\ProgramData\Razer
[2010/07/03 16:08:25 | 000,000,000 | —D | C] – C:\Program Files (x86)\Razer
[2010/07/03 16:08:11 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\InstallShield
[2010/06/30 01:59:10 | 000,000,000 | —D | C] – C:\ProgramData\Tracker Software
[2010/06/29 10:56:01 | 000,038,848 | —- | C] (ALWIL Software) – C:\Windows\avastSS.scr
[2010/06/28 12:52:23 | 000,000,000 | —D | C] – C:\Users\Bryan\Documents\RipOutOffice2007[1]
[2010/06/28 09:17:29 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\Media Player Classic
[2010/06/28 09:17:09 | 000,000,000 | —D | C] – C:\Program Files\MPC HomeCinema (x64)
[2010/06/28 08:25:20 | 000,000,000 | —D | C] – C:\ProgramData\NVIDIA Corporation
[2010/06/28 08:23:09 | 000,065,128 | —- | C] (Khronos Group) – C:\Windows\SysNative\OpenCL.dll
[2010/06/28 08:23:09 | 000,056,936 | —- | C] (Khronos Group) – C:\Windows\SysWow64\OpenCL.dll
[2010/06/27 17:05:35 | 000,000,000 | —D | C] – C:\ProgramData\Yahoo!
[2010/06/27 17:05:31 | 000,000,000 | —D | C] – C:\ProgramData\TEMP
[2010/06/27 17:05:23 | 000,000,000 | —D | C] – C:\ProgramData\Oberon Media
[2010/06/27 17:04:37 | 000,000,000 | —D | C] – C:\Program Files (x86)\Oberon Media
[2010/06/24 22:24:28 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\X-Setup Pro
[2010/06/24 22:24:28 | 000,000,000 | —D | C] – C:\ProgramData\X-Setup Pro
[2010/06/23 14:57:28 | 000,000,000 | —D | C] – C:\Program Files\7-Zip
[2010/06/23 14:06:45 | 000,000,000 | —D | C] – C:\Users\Bryan\.bh_gui
[2010/06/20 18:39:25 | 000,000,000 | —D | C] – C:\ProgramData\Ubisoft
[2010/06/20 18:18:23 | 000,000,000 | —D | C] – C:\Program Files (x86)\Ubisoft
[2010/06/20 17:22:16 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Local\NOS
[2010/06/20 17:22:05 | 000,000,000 | —D | C] – C:\ProgramData\NOS
[2010/06/19 20:24:47 | 000,000,000 | —D | C] – C:\Program Files (x86)\Common Files\Steam
[2010/06/19 20:24:44 | 000,000,000 | —D | C] – C:\Program Files (x86)\Steam
[2010/06/18 19:15:33 | 000,000,000 | —D | C] – C:\ProgramData\Hitman Pro
[2010/06/18 19:15:25 | 000,000,000 | —D | C] – C:\Program Files\Hitman Pro 3.5
[2010/06/17 22:53:10 | 000,020,048 | —- | C] (ALWIL Software) – C:\Windows\SysNative\drivers\aswFsBlk.sys
[2010/06/17 22:53:03 | 000,121,936 | —- | C] (ALWIL Software) – C:\Windows\SysNative\drivers\aswSP.sys
[2010/06/17 22:52:57 | 000,028,752 | —- | C] (ALWIL Software) – C:\Windows\SysNative\drivers\aswRdr.sys
[2010/06/17 22:52:43 | 000,051,280 | —- | C] (ALWIL Software) – C:\Windows\SysNative\drivers\aswTdi.sys
[2010/06/17 22:52:14 | 000,061,008 | —- | C] (ALWIL Software) – C:\Windows\SysNative\drivers\aswMonFlt.sys
[2010/06/17 22:51:52 | 000,165,032 | —- | C] (AVAST Software) – C:\Windows\SysWow64\aswBoot.exe
[2010/06/17 21:51:50 | 000,000,000 | —D | C] – C:\Users\Bryan\Documents\cports-x64[1]
[2010/06/17 21:39:19 | 000,062,464 | —- | C] (Prevx) – C:\Windows\SysWow64\PxSecure.dll
[2010/06/17 21:39:19 | 000,034,696 | —- | C] (Prevx) – C:\Windows\SysNative\drivers\pxscan.sys
[2010/06/17 21:39:09 | 000,055,808 | —- | C] (Prevx) – C:\Windows\SysNative\drivers\pxrts.sys
[2010/06/17 21:39:09 | 000,022,336 | —- | C] (Prevx) – C:\Windows\SysNative\drivers\pxkbf.sys
[2010/06/12 02:20:44 | 000,000,000 | —D | C] – C:\Users\Bryan\Documents\My Google Gadgets
[2010/06/11 22:37:55 | 000,000,000 | -H-D | C] – C:\VritualRoot
[2010/06/11 10:42:42 | 000,000,000 | —D | C] – C:\Users\Bryan\Documents\PDFXVwer
[2010/06/11 10:36:42 | 000,000,000 | —D | C] – C:\Program Files\Tracker Software
[2010/06/11 02:38:43 | 000,000,000 | —D | C] – C:\Program Files (x86)\Conduit
[2010/06/10 21:24:38 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\Thunderbird
[2010/06/10 21:24:38 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Local\Thunderbird
[2010/06/10 20:55:55 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\SUPERAntiSpyware.com
[2010/06/10 20:55:55 | 000,000,000 | —D | C] – C:\ProgramData\SUPERAntiSpyware.com
[2010/06/10 20:55:30 | 000,000,000 | —D | C] – C:\ProgramData\!SASCORE
[2010/06/10 20:55:26 | 000,000,000 | —D | C] – C:\Program Files\SUPERAntiSpyware
[2010/06/04 17:38:22 | 000,000,000 | —D | C] – C:\Users\Bryan\DoctorWeb
[2010/06/01 11:29:51 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Local\cache
[2010/06/01 11:29:06 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Local\FullTiltPoker
[2010/05/29 00:31:41 | 000,000,000 | —D | C] – C:\Users\Bryan\Documents\gameprofiles[1]
[2010/05/29 00:10:31 | 000,000,000 | —D | C] – C:\Program Files (x86)\Secunia
[2010/05/28 21:58:42 | 000,000,000 | —D | C] – C:\Program Files\Saitek
[2010/05/28 10:11:07 | 000,000,000 | —D | C] – C:\Program Files (x86)\FileHippo.com
[2010/05/28 04:04:52 | 000,017,456 | —- | C] (Secunia) – C:\Windows\SysNative\drivers\psi_mf.sys
[2010/05/26 12:16:08 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\VSRevoGroup
[2010/05/25 14:37:26 | 000,000,000 | —D | C] – C:\Program Files (x86)\RadioBar
[2010/05/25 13:35:11 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Local\IsolatedStorage
[2010/05/25 02:42:20 | 000,000,000 | —D | C] – C:\Users\Bryan\Documents\Autoruns[1]
[2010/05/24 08:06:05 | 000,000,000 | —D | C] – C:\Users\Bryan\Desktop\GAMES
[2010/05/23 18:06:02 | 000,000,000 | —D | C] – C:\Users\Bryan\New folder
[2010/05/23 17:56:55 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Local\Pando_Temp
[2010/05/23 17:56:40 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Local\GamersFirst LIVE!
[2010/05/23 17:56:20 | 000,000,000 | —D | C] – C:\Program Files (x86)\GamersFirst
[2010/05/23 17:30:37 | 000,000,000 | —D | C] – C:\Users\Bryan\Documents\Battlefield Heroes
[2010/05/23 16:26:57 | 000,000,000 | —D | C] – C:\Program Files (x86)\EA Games
[2010/05/23 12:17:49 | 000,000,000 | —D | C] – C:\Users\Bryan\Documents\radix_installer[1]
[2010/05/23 00:32:57 | 000,000,000 | —D | C] – C:\Users\Public\Documents\HostsMan Backups
[2010/05/23 00:32:57 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\abelhadigital.com
[2010/05/23 00:32:57 | 000,000,000 | —D | C] – C:\ProgramData\abelhadigital.com
[2010/05/23 00:32:54 | 000,000,000 | —D | C] – C:\Program Files (x86)\HostsMan
[2010/05/21 12:41:58 | 000,000,000 | R–D | C] – C:\Sandbox
[2010/05/21 12:39:01 | 000,000,000 | —D | C] – C:\Program Files\Sandboxie
[2010/05/21 00:28:00 | 000,000,000 | —D | C] – C:\ProgramData\NexonUS
[2010/05/21 00:28:00 | 000,000,000 | —D | C] – C:\Nexon
[2010/05/20 22:38:42 | 000,000,000 | —D | C] – C:\Windows\ERDNT
[2010/05/20 22:36:01 | 000,000,000 | —D | C] – C:\Program Files (x86)\WOT
[2010/05/20 21:52:29 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\Auslogics
[2010/05/20 21:52:24 | 000,000,000 | —D | C] – C:\Program Files (x86)\Auslogics
[2010/05/19 13:05:25 | 000,000,000 | —D | C] – C:\Windows\BDOSCAN8
[2010/05/19 11:51:08 | 000,000,000 | —D | C] – C:\Users\Bryan\Documents\md5[1]
[2010/05/17 13:05:00 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\U3
[2010/05/17 11:32:30 | 000,000,000 | —D | C] – C:\Program Files\Windows Live
[2010/05/17 11:31:51 | 000,000,000 | —D | C] – C:\Program Files (x86)\Microsoft Sync Framework
[2010/05/17 10:57:41 | 000,000,000 | R-SD | C] – C:\Users\Bryan\Documents\My Stationery
[2010/05/16 23:31:32 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\vlc
[2010/05/16 23:25:21 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Local\Graboid_Inc
[2010/05/16 23:25:20 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Local\Graboid
[2010/05/16 23:25:19 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\MozillaControl
[2010/05/16 23:25:19 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\Mozilla
[2010/05/16 23:25:08 | 000,000,000 | —D | C] – C:\Program Files (x86)\Mozilla ActiveX Control v1.7.12
[2010/05/16 23:24:53 | 000,000,000 | —D | C] – C:\Program Files (x86)\VideoLAN
[2010/05/16 13:35:50 | 002,719,504 | —- | C] (Waves Audio Ltd.) – C:\Windows\SysNative\WavesGUILib.dll
[2010/05/16 13:35:50 | 000,155,888 | —- | C] (SRS Labs, Inc.) – C:\Windows\SysNative\SRSWOW64.dll
[2010/05/16 13:35:49 | 000,518,896 | —- | C] (SRS Labs, Inc.) – C:\Windows\SysNative\SRSTSX64.dll
[2010/05/16 13:35:49 | 000,211,184 | —- | C] (SRS Labs, Inc.) – C:\Windows\SysNative\SRSTSH64.dll
[2010/05/16 13:35:49 | 000,198,896 | —- | C] (SRS Labs, Inc.) – C:\Windows\SysNative\SRSHP64.dll
[2010/05/16 13:35:47 | 000,372,936 | —- | C] (Dolby Laboratories, Inc.) – C:\Windows\SysNative\RTEEP64A.dll
[2010/05/16 13:35:47 | 000,201,928 | —- | C] (Dolby Laboratories, Inc.) – C:\Windows\SysNative\RTEED64A.dll
[2010/05/16 13:35:47 | 000,099,016 | —- | C] (Dolby Laboratories, Inc.) – C:\Windows\SysNative\RTEEL64A.dll
[2010/05/16 13:35:47 | 000,076,488 | —- | C] (Dolby Laboratories, Inc.) – C:\Windows\SysNative\RTEEG64A.dll
[2010/05/16 13:35:46 | 000,307,920 | —- | C] (Dolby Laboratories, Inc.) – C:\Windows\SysNative\RP3DHT64.dll
[2010/05/16 13:35:46 | 000,307,920 | —- | C] (Dolby Laboratories, Inc.) – C:\Windows\SysNative\RP3DAA64.dll
[2010/05/16 13:35:44 | 002,197,264 | —- | C] (Waves Audio Ltd.) – C:\Windows\SysNative\MaxxAudioEQ.dll
[2010/05/16 13:35:44 | 000,325,904 | —- | C] (Waves Audio Ltd.) – C:\Windows\SysNative\MaxxAudioAPO20.dll
[2010/05/16 13:35:43 | 001,325,328 | —- | C] (DTS) – C:\Windows\SysNative\DTSS2SpeakerDLL64.dll
[2010/05/16 13:35:43 | 001,178,384 | —- | C] (DTS) – C:\Windows\SysNative\DTSS2HeadphoneDLL64.dll
[2010/05/16 13:35:43 | 000,489,744 | —- | C] (DTS) – C:\Windows\SysNative\DTSSymmetryDLL64.dll
[2010/05/16 13:35:43 | 000,474,896 | —- | C] (DTS) – C:\Windows\SysNative\DTSVoiceClarityDLL64.dll
[2010/05/16 13:35:43 | 000,331,168 | —- | C] (Fortemedia Corporation) – C:\Windows\SysNative\FMAPO64.dll
[2010/05/16 13:35:42 | 001,110,800 | —- | C] (DTS) – C:\Windows\SysNative\DTSBoostDLL64.dll
[2010/05/16 13:35:42 | 000,315,152 | —- | C] (DTS) – C:\Windows\SysNative\DTSNeoPCDLL64.dll
[2010/05/16 13:35:42 | 000,268,560 | —- | C] (DTS) – C:\Windows\SysNative\DTSLimiterDLL64.dll
[2010/05/16 13:35:42 | 000,265,488 | —- | C] (DTS) – C:\Windows\SysNative\DTSGainCompensatorDLL64.dll
[2010/05/16 13:35:42 | 000,123,664 | —- | C] (DTS) – C:\Windows\SysNative\DTSLFXAPO64.dll
[2010/05/16 13:35:42 | 000,123,152 | —- | C] (DTS) – C:\Windows\SysNative\DTSGFXAPO64.dll
[2010/05/16 13:35:42 | 000,122,128 | —- | C] (DTS) – C:\Windows\SysNative\DTSGFXAPONS64.dll
[2010/05/16 13:35:41 | 000,504,592 | —- | C] (DTS) – C:\Windows\SysNative\DTSBassEnhancementDLL64.dll
[2010/05/15 16:03:45 | 000,000,000 | —D | C] – C:\Windows\Minidump
[2010/05/15 11:47:25 | 000,000,000 | —D | C] – C:\Program Files (x86)\Belarc
[2010/05/15 09:26:07 | 000,000,000 | —D | C] – C:\Program Files (x86)\ESET
[2010/05/14 21:58:30 | 000,000,000 | —D | C] – C:\Program Files (x86)\Trend Micro
[2010/05/14 16:16:33 | 000,000,000 | —D | C] – C:\Program Files (x86)\Rockstar Games
[2010/05/14 16:00:35 | 000,000,000 | —D | C] – C:\Program Files\Registrar Registry Manager
[2010/05/14 15:44:25 | 000,000,000 | —D | C] – C:\Program Files (x86)\CCleaner
[2010/05/14 14:28:01 | 000,000,000 | —D | C] – C:\ProgramData\PCPitstop
[2010/05/14 14:28:00 | 000,000,000 | —D | C] – C:\Program Files (x86)\PCPitstop
[2010/05/13 21:03:26 | 000,000,000 | —D | C] – C:\ubuntu
[2010/05/13 10:59:13 | 000,000,000 | —D | C] – C:\Users\Bryan\Documents\My Drivers
[2010/05/13 10:59:13 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Local\Innovative Solutions
[2010/05/13 10:59:13 | 000,000,000 | —D | C] – C:\ProgramData\Innovative Solutions
[2010/05/13 10:59:07 | 000,000,000 | —D | C] – C:\Program Files (x86)\Innovative Solutions
[2010/05/12 22:10:54 | 000,000,000 | —D | C] – C:\Users\Bryan\AppData\Roaming\ImgBurn
[2010/05/12 22:09:42 | 000,000,000 | —D | C] – C:\Program Files (x86)\ImgBurn
[2010/05/12 21:32:17 | 000,000,000 | —D | C] – C:\Program Files (x86)\Partition Wizard Home Edition 5.0
[6 C:\Windows\SysNative\*.tmp files -> C:\Windows\SysNative\*.tmp -> ]
========== Files - Modified Within 90 Days ==========
[2010/08/10 12:50:35 | 002,883,584 | -HS- | M] () – C:\Users\Bryan\ntuser.dat
[2010/08/10 12:44:45 | 000,574,976 | —- | M] (OldTimer Tools) – C:\Users\Bryan\Desktop\OTL.exe
[2010/08/10 12:43:06 | 000,067,584 | –S- | M] () – C:\Windows\bootstat.dat
[2010/08/10 11:40:30 | 000,293,376 | —- | M] () – C:\Users\Bryan\Desktop\7bv3lz8r.exe
[2010/08/10 11:37:46 | 000,525,824 | —- | M] () – C:\Users\Bryan\Desktop\dds.com
[2010/08/10 11:35:30 | 000,080,384 | —- | M] () – C:\Users\Bryan\Desktop\MBRCheck.exe
[2010/08/10 11:33:00 | 000,000,896 | —- | M] () – C:\Windows\tasks\GoogleUpdateTaskMachineUA.job
[2010/08/10 09:32:48 | 000,009,920 | -H– | M] () – C:\Windows\SysNative\7B296FB0-376B-497e-B012-9C450E1B7327-5P-1.C7483456-A289-439d-8115-601632D005A0
[2010/08/10 09:32:48 | 000,009,920 | -H– | M] () – C:\Windows\SysNative\7B296FB0-376B-497e-B012-9C450E1B7327-5P-0.C7483456-A289-439d-8115-601632D005A0
[2010/08/10 09:29:57 | 000,726,316 | —- | M] () – C:\Windows\SysNative\PerfStringBackup.INI
[2010/08/10 09:29:57 | 000,623,940 | —- | M] () – C:\Windows\SysNative\perfh009.dat
[2010/08/10 09:29:57 | 000,106,316 | —- | M] () – C:\Windows\SysNative\perfc009.dat
[2010/08/10 09:25:52 | 000,000,892 | —- | M] () – C:\Windows\tasks\GoogleUpdateTaskMachineCore.job
[2010/08/10 09:25:42 | 000,000,006 | -H– | M] () – C:\Windows\tasks\SA.DAT
[2010/08/10 09:25:20 | 3018,756,096 | -HS- | M] () – C:\hiberfil.sys
[2010/08/09 16:58:49 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{80370c4f-a3ed-11df-b50b-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/08/09 16:58:49 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{80370c4f-a3ed-11df-b50b-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/08/09 16:58:49 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{80370c4f-a3ed-11df-b50b-00262d289fc4}.TM.blf
[2010/08/09 16:58:47 | 001,582,518 | -H– | M] () – C:\Users\Bryan\AppData\Local\IconCache.db
[2010/08/09 13:16:55 | 020,085,840 | —- | M] (Emsi Software GmbH ) – C:\Users\Bryan\Desktop\OnlineArmor_Setup.exe
[2010/08/08 19:05:35 | 000,011,018 | —- | M] () – C:\Users\Bryan\Documents\cc_20100808_190530.reg
[2010/08/07 11:46:18 | 000,002,975 | —- | M] () – C:\Users\Bryan\Desktop\HiJackThis.lnk
[2010/08/07 01:40:05 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{743a8986-a1fc-11df-bdfa-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/08/07 01:40:05 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{743a8986-a1fc-11df-bdfa-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/08/07 01:40:05 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{743a8986-a1fc-11df-bdfa-00262d289fc4}.TM.blf
[2010/08/07 01:17:05 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{62eb801e-a1f0-11df-82a7-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/08/07 01:17:05 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{62eb801e-a1f0-11df-82a7-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/08/07 01:17:05 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{62eb801e-a1f0-11df-82a7-00262d289fc4}.TM.blf
[2010/08/07 00:20:44 | 000,054,824 | —- | M] () – C:\Windows\SysWow64\drivers\oahlp64.sys
[2010/08/07 00:19:52 | 000,037,800 | —- | M] (Emsisoft) – C:\Windows\SysWow64\drivers\OAmon.sys
[2010/08/07 00:19:52 | 000,032,656 | —- | M] (Emsisoft) – C:\Windows\SysNative\drivers\OAnet.sys
[2010/08/07 00:19:50 | 000,425,568 | —- | M] (Emsi Software GmbH) – C:\Windows\oaevent.dll
[2010/08/07 00:19:50 | 000,053,768 | —- | M] () – C:\Windows\SysWow64\drivers\OADriver.sys
[2010/08/06 22:32:17 | 000,012,674 | —- | M] () – C:\Users\Bryan\Documents\cc_20100806_222925.reg
[2010/08/06 19:38:17 | 000,601,965 | —- | M] () – C:\Windows\SysNative\drivers\etc\HOSTS
[2010/07/31 18:51:48 | 000,219,128 | —- | M] () – C:\Windows\SysWow64\PnkBstrB.xtr
[2010/07/31 18:50:44 | 000,219,128 | —- | M] () – C:\Windows\SysWow64\PnkBstrB.exe
[2010/07/29 13:04:34 | 000,002,238 | —- | M] () – C:\Users\Bryan\Desktop\PICTUREKA! MUSEUM MAYHEM.lnk
[2010/07/29 13:04:34 | 000,001,142 | —- | M] () – C:\Users\Bryan\Desktop\Pogo Games.lnk
[2010/07/29 11:56:16 | 000,002,311 | —- | M] () – C:\Users\Bryan\Desktop\Classic Adventures The Great Gatsby.lnk
[2010/07/27 06:40:41 | 000,000,000 | —- | M] () – C:\Windows\SysNative\drivers\etc\lmhosts
[2010/07/26 14:02:35 | 000,468,480 | —- | M] (Oracle) – C:\Windows\SysNative\deployJava1.dll
[2010/07/26 14:02:35 | 000,183,296 | —- | M] (Oracle) – C:\Windows\SysNative\javaws.exe
[2010/07/26 14:02:35 | 000,165,888 | —- | M] (Oracle) – C:\Windows\SysNative\javaw.exe
[2010/07/26 14:02:35 | 000,165,888 | —- | M] (Oracle) – C:\Windows\SysNative\java.exe
[2010/07/26 12:50:08 | 000,025,578 | —- | M] () – C:\Users\Bryan\Documents\cc_20100726_124941.regbu726.reg
[2010/07/26 12:46:06 | 000,001,011 | —- | M] () – C:\Users\Bryan\Desktop\CCleaner.lnk
[2010/07/22 15:48:10 | 000,000,819 | —- | M] () – C:\Users\Public\Desktop\System Nucleus.lnk
[2010/07/21 07:58:40 | 000,000,219 | —- | M] () – C:\Users\Bryan\Desktop\Alien Swarm.url
[2010/07/18 10:39:02 | 000,002,018 | —- | M] () – C:\Users\Public\Desktop\Adobe Reader 9.lnk
[2010/07/14 20:48:30 | 000,001,089 | —- | M] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\PokerStars.lnk
[2010/07/14 20:48:30 | 000,001,065 | —- | M] () – C:\Users\Public\Desktop\PokerStars.lnk
[2010/07/08 14:53:52 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{54fc1738-8abc-11df-85ca-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/07/08 14:53:52 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{54fc1738-8abc-11df-85ca-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/07/08 14:53:52 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{54fc1738-8abc-11df-85ca-00262d289fc4}.TM.blf
[2010/07/08 11:08:21 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{a905fc21-8aba-11df-bc32-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/07/08 11:08:21 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{a905fc21-8aba-11df-bc32-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/07/08 11:08:21 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{a905fc21-8aba-11df-bc32-00262d289fc4}.TM.blf
[2010/07/07 10:05:00 | 000,001,085 | —- | M] () – C:\Users\Bryan\Desktop\PDF-Viewer.lnk
[2010/07/04 10:23:20 | 000,000,174 | —- | M] () – C:\Users\Bryan\Desktop\Audit My PC.url
[2010/06/30 17:09:53 | 000,078,320 | —- | M] () – C:\Users\Bryan\AppData\Local\GDIPFONTCACHEV1.DAT
[2010/06/29 10:56:03 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\config.nt
[2010/06/28 13:57:33 | 000,038,848 | —- | M] (ALWIL Software) – C:\Windows\avastSS.scr
[2010/06/28 13:57:12 | 000,165,032 | —- | M] (AVAST Software) – C:\Windows\SysWow64\aswBoot.exe
[2010/06/28 13:37:56 | 000,051,280 | —- | M] (ALWIL Software) – C:\Windows\SysNative\drivers\aswTdi.sys
[2010/06/28 13:37:36 | 000,121,936 | —- | M] (ALWIL Software) – C:\Windows\SysNative\drivers\aswSP.sys
[2010/06/28 13:33:17 | 000,028,752 | —- | M] (ALWIL Software) – C:\Windows\SysNative\drivers\aswRdr.sys
[2010/06/28 13:33:00 | 000,061,008 | —- | M] (ALWIL Software) – C:\Windows\SysNative\drivers\aswMonFlt.sys
[2010/06/28 13:32:36 | 000,020,048 | —- | M] (ALWIL Software) – C:\Windows\SysNative\drivers\aswFsBlk.sys
[2010/06/28 13:02:16 | 000,330,472 | —- | M] () – C:\Windows\SysNative\FNTCACHE.DAT
[2010/06/28 11:29:13 | 000,020,424 | —- | M] () – C:\Users\Bryan\Documents\cc_20100628_112406.reg
[2010/06/28 11:23:34 | 000,000,082 | —- | M] () – C:\Users\Bryan\Documents\cc_20100628_112326.reg
[2010/06/28 09:17:11 | 000,000,848 | —- | M] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\Media Player Classic - Home Cinema x64.lnk
[2010/06/28 09:17:11 | 000,000,824 | —- | M] () – C:\Users\Public\Desktop\Media Player Classic - Home Cinema x64.lnk
[2010/06/28 00:38:06 | 000,001,118 | —- | M] () – C:\Users\Bryan\Desktop\DriverMax.lnk
[2010/06/27 23:01:22 | 000,001,965 | —- | M] () – C:\Users\Public\Desktop\SUPERAntiSpyware Free Edition.lnk
[2010/06/24 22:36:11 | 000,001,268 | —- | M] () – C:\Users\Bryan\Desktop\Revo Uninstaller.lnk
[2010/06/20 19:36:12 | 000,000,778 | —- | M] () – C:\Users\Bryan\Desktop\Tom Clancy's Splinter Cell Conviction - Shortcut.lnk
[2010/06/19 21:10:07 | 000,000,221 | —- | M] () – C:\Users\Bryan\Desktop\Call of Duty Modern Warfare 2.url
[2010/06/19 21:10:07 | 000,000,221 | —- | M] () – C:\Users\Bryan\Desktop\Call of Duty Modern Warfare 2 - Multiplayer.url
[2010/06/19 20:42:01 | 000,000,921 | —- | M] () – C:\Users\Public\Desktop\Steam.lnk
[2010/06/18 19:16:01 | 000,019,016 | —- | M] () – C:\Windows\SysNative\drivers\hitmanpro35.sys
[2010/06/17 22:53:20 | 000,001,856 | —- | M] () – C:\Users\Public\Desktop\avast! Free Antivirus.lnk
[2010/06/17 21:39:19 | 000,062,464 | —- | M] (Prevx) – C:\Windows\SysWow64\PxSecure.dll
[2010/06/17 21:39:19 | 000,055,808 | —- | M] (Prevx) – C:\Windows\SysNative\drivers\pxrts.sys
[2010/06/17 21:39:19 | 000,034,696 | —- | M] (Prevx) – C:\Windows\SysNative\drivers\pxscan.sys
[2010/06/17 21:39:09 | 000,022,336 | —- | M] (Prevx) – C:\Windows\SysNative\drivers\pxkbf.sys
[2010/06/15 23:25:58 | 000,000,050 | —- | M] () – C:\Windows\wininit.ini
[2010/06/15 16:50:27 | 000,001,368 | —- | M] () – C:\Windows\Sandboxie.ini
[2010/06/12 02:33:56 | 000,001,134 | —- | M] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\Picasa 3.lnk
[2010/06/12 02:33:56 | 000,001,110 | —- | M] () – C:\Users\Public\Desktop\Picasa 3.lnk
[2010/06/11 19:47:04 | 000,001,140 | —- | M] () – C:\Users\Bryan\Desktop\Auslogics Disk Defrag.lnk
[2010/06/11 10:34:32 | 013,528,139 | —- | M] () – C:\Users\Bryan\Documents\PDFXVwer.zip
[2010/06/10 22:55:37 | 000,018,528 | —- | M] () – C:\Users\Bryan\Documents\cc_20100610_225525.reg
[2010/06/10 21:24:39 | 000,000,000 | —- | M] () – C:\Windows\nsreg.dat
[2010/06/07 19:58:00 | 000,065,128 | —- | M] (Khronos Group) – C:\Windows\SysNative\OpenCL.dll
[2010/06/07 19:58:00 | 000,056,936 | —- | M] (Khronos Group) – C:\Windows\SysWow64\OpenCL.dll
[2010/06/07 19:58:00 | 000,012,507 | —- | M] () – C:\Windows\SysNative\nvinfo.pb
[2010/06/06 00:13:36 | 000,001,607 | —- | M] () – C:\Users\Public\Desktop\Combat Arms.lnk
[2010/06/05 23:49:01 | 000,007,594 | —- | M] () – C:\Users\Bryan\AppData\Local\Resmon.ResmonCfg
[2010/06/05 16:18:18 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{faea86da-70f0-11df-8bf9-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/06/05 16:18:18 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{faea86da-70f0-11df-8bf9-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/06/05 16:18:18 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{faea86da-70f0-11df-8bf9-00262d289fc4}.TM.blf
[2010/06/01 16:21:15 | 001,167,702 | —- | M] () – C:\Users\Bryan\Documents\draft_guide.cbs2010.pdf
[2010/05/30 20:24:20 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\WindowsAnytimeUpgradeUI.exe
[2010/05/29 02:12:21 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{81e1dd90-6aee-11df-95dc-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/29 02:12:21 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{81e1dd90-6aee-11df-95dc-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/29 02:12:21 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{81e1dd90-6aee-11df-95dc-00262d289fc4}.TM.blf
[2010/05/28 20:43:21 | 000,001,222 | —- | M] () – C:\Users\Public\Desktop\Google Desktop.lnk
[2010/05/28 15:42:20 | 000,000,000 | -H– | M] () – C:\Windows\SysNative\drivers\Msft_Kernel_SaiKF622_01005.Wdf
[2010/05/28 11:16:49 | 000,037,598 | —- | M] () – C:\Users\Bryan\Documents\cc_20100528_111630.regbackup.reg
[2010/05/28 10:11:08 | 000,001,973 | —- | M] () – C:\Users\Bryan\Desktop\Update Checker.lnk
[2010/05/28 04:04:52 | 000,017,456 | —- | M] (Secunia) – C:\Windows\SysNative\drivers\psi_mf.sys
[2010/05/26 11:36:14 | 000,001,369 | —- | M] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\Launch Internet Explorer Browser.lnk
[2010/05/25 18:03:41 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{7400f97e-682a-11df-8657-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/25 18:03:41 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{7400f97e-682a-11df-8657-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/25 18:03:41 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{7400f97e-682a-11df-8657-00262d289fc4}.TM.blf
[2010/05/25 02:42:24 | 000,670,072 | —- | M] (Sysinternals - www.sysinternals.com) – C:\Users\Bryan\Desktop\autoruns.exe
[2010/05/23 17:29:25 | 002,427,248 | —- | M] () – C:\Windows\SysWow64\pbsvc_heroes.exe
[2010/05/23 17:29:25 | 000,075,064 | —- | M] () – C:\Windows\SysWow64\PnkBstrA.exe
[2010/05/23 01:59:40 | 000,607,013 | —- | M] () – C:\Windows\SysNative\drivers\etc\HOSTS.bak
[2010/05/23 01:59:40 | 000,001,615 | —- | M] () – C:\Windows\SysNative\drivers\etc\mvps.bat
[2010/05/22 12:20:28 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{be3a6db8-65cf-11df-b488-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/22 12:20:28 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{be3a6db8-65cf-11df-b488-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/22 12:20:28 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{be3a6db8-65cf-11df-b488-00262d289fc4}.TM.blf
[2010/05/22 11:29:36 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{1a9c8dd3-65ce-11df-b300-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/22 11:29:36 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{1a9c8dd3-65ce-11df-b300-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/22 11:29:36 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{1a9c8dd3-65ce-11df-b300-00262d289fc4}.TM.blf
[2010/05/22 11:26:34 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{abfe7c72-65c6-11df-bf90-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/22 11:26:34 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{abfe7c72-65c6-11df-bf90-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/22 11:26:34 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{abfe7c72-65c6-11df-bf90-00262d289fc4}.TM.blf
[2010/05/21 16:43:13 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\recdisc.exe
[2010/05/21 14:46:10 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\vdsldr.exe
[2010/05/21 12:39:05 | 000,000,900 | —- | M] () – C:\Users\Bryan\Desktop\Sandboxed Web Browser.lnk
[2010/05/21 12:39:05 | 000,000,900 | —- | M] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\Sandboxed Web Browser.lnk
[2010/05/21 11:00:01 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\wsqmcons.exe
[2010/05/21 10:00:01 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\sdclt.exe
[2010/05/21 08:04:46 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\defrag.exe
[2010/05/20 21:10:55 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{d2ad8a2b-645e-11df-a4c1-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/20 21:10:55 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{d2ad8a2b-645e-11df-a4c1-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/20 21:10:55 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{d2ad8a2b-645e-11df-a4c1-00262d289fc4}.TM.blf
[2010/05/17 13:27:24 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\mdres.exe
[2010/05/17 13:12:28 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\MdSched.exe
[2010/05/17 01:11:45 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{911b0d48-6171-11df-89fd-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/17 01:11:45 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{911b0d48-6171-11df-89fd-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/17 01:11:45 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{911b0d48-6171-11df-89fd-00262d289fc4}.TM.blf
[2010/05/17 00:54:34 | 000,001,662 | —- | M] () – C:\Users\Bryan\Desktop\Recuva.lnk
[2010/05/15 15:10:25 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\DXPServer.exe
[2010/05/15 15:10:18 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\DeviceDisplayObjectProvider.exe
[2010/05/15 15:10:16 | 000,000,000 | -H– | M] () – C:\Windows\SysNative\drivers\Msft_User_WpdMtpDr_01_09_00.Wdf
[2010/05/15 14:58:18 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{e18fb18c-6035-11df-ad70-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/15 14:58:18 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{e18fb18c-6035-11df-ad70-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/15 14:58:18 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{e18fb18c-6035-11df-ad70-00262d289fc4}.TM.blf
[2010/05/15 11:47:26 | 000,002,031 | —- | M] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\Belarc Advisor.lnk
[2010/05/15 11:47:26 | 000,002,007 | —- | M] () – C:\Users\Public\Desktop\Belarc Advisor.lnk
[2010/05/14 23:29:49 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{3bb27f3f-5fd3-11df-ad2e-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/14 23:29:49 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{3bb27f3f-5fd3-11df-ad2e-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/14 23:29:49 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{3bb27f3f-5fd3-11df-ad2e-00262d289fc4}.TM.blf
[2010/05/14 00:17:20 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{133bfd4a-5ec9-11df-a441-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/14 00:17:20 | 000,524,288 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{133bfd4a-5ec9-11df-a441-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/14 00:17:20 | 000,065,536 | -HS- | M] () – C:\Users\Bryan\ntuser.dat{133bfd4a-5ec9-11df-a441-00262d289fc4}.TM.blf
[2010/05/14 00:16:58 | 000,088,813 | —- | M] () – C:\wubildr
[2010/05/14 00:16:58 | 000,008,192 | —- | M] () – C:\wubildr.mbr
[2010/05/13 19:08:49 | 000,000,036 | —- | M] () – C:\Users\Bryan\AppData\Local\housecall.guid.cache
[2010/05/13 11:13:07 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\nvuSMU.exe
[2010/05/12 22:09:42 | 000,001,893 | —- | M] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\ImgBurn.lnk
[2010/05/12 22:09:42 | 000,001,869 | —- | M] () – C:\Users\Public\Desktop\ImgBurn.lnk
[2010/05/12 21:40:30 | 000,001,127 | —- | M] () – C:\Users\Bryan\Desktop\Partition Wizard Home Edition.lnk
[2010/05/12 13:52:21 | 000,000,000 | —- | M] () – C:\Windows\SysWow64\CompMgmtLauncher.exe
[6 C:\Windows\SysNative\*.tmp files -> C:\Windows\SysNative\*.tmp -> ]
========== Files Created - No Company Name ==========
[2010/08/10 11:40:27 | 000,293,376 | —- | C] () – C:\Users\Bryan\Desktop\7bv3lz8r.exe
[2010/08/10 11:37:44 | 000,525,824 | —- | C] () – C:\Users\Bryan\Desktop\dds.com
[2010/08/10 11:35:30 | 000,080,384 | —- | C] () – C:\Users\Bryan\Desktop\MBRCheck.exe
[2010/08/09 12:52:27 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{80370c4f-a3ed-11df-b50b-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/08/09 12:52:27 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{80370c4f-a3ed-11df-b50b-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/08/09 12:52:27 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{80370c4f-a3ed-11df-b50b-00262d289fc4}.TM.blf
[2010/08/09 12:40:57 | 000,054,824 | —- | C] () – C:\Windows\SysWow64\drivers\oahlp64.sys
[2010/08/09 12:40:57 | 000,053,768 | —- | C] () – C:\Windows\SysWow64\drivers\OADriver.sys
[2010/08/08 19:05:33 | 000,011,018 | —- | C] () – C:\Users\Bryan\Documents\cc_20100808_190530.reg
[2010/08/07 11:46:18 | 000,002,975 | —- | C] () – C:\Users\Bryan\Desktop\HiJackThis.lnk
[2010/08/07 01:31:02 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{743a8986-a1fc-11df-bdfa-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/08/07 01:31:02 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{743a8986-a1fc-11df-bdfa-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/08/07 01:31:02 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{743a8986-a1fc-11df-bdfa-00262d289fc4}.TM.blf
[2010/08/07 01:17:05 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{62eb801e-a1f0-11df-82a7-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/08/07 01:17:05 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{62eb801e-a1f0-11df-82a7-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/08/07 01:17:05 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{62eb801e-a1f0-11df-82a7-00262d289fc4}.TM.blf
[2010/08/06 22:29:27 | 000,012,674 | —- | C] () – C:\Users\Bryan\Documents\cc_20100806_222925.reg
[2010/07/29 13:04:34 | 000,002,238 | —- | C] () – C:\Users\Bryan\Desktop\PICTUREKA! MUSEUM MAYHEM.lnk
[2010/07/29 11:56:16 | 000,002,311 | —- | C] () – C:\Users\Bryan\Desktop\Classic Adventures The Great Gatsby.lnk
[2010/07/26 12:50:03 | 000,025,578 | —- | C] () – C:\Users\Bryan\Documents\cc_20100726_124941.regbu726.reg
[2010/07/22 15:48:10 | 000,000,819 | —- | C] () – C:\Users\Public\Desktop\System Nucleus.lnk
[2010/07/21 07:58:40 | 000,000,219 | —- | C] () – C:\Users\Bryan\Desktop\Alien Swarm.url
[2010/07/18 10:38:39 | 000,002,018 | —- | C] () – C:\Users\Public\Desktop\Adobe Reader 9.lnk
[2010/07/14 20:48:30 | 000,001,089 | —- | C] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\PokerStars.lnk
[2010/07/14 20:48:30 | 000,001,065 | —- | C] () – C:\Users\Public\Desktop\PokerStars.lnk
[2010/07/08 12:54:52 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{54fc1738-8abc-11df-85ca-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/07/08 12:54:52 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{54fc1738-8abc-11df-85ca-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/07/08 12:54:51 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{54fc1738-8abc-11df-85ca-00262d289fc4}.TM.blf
[2010/07/08 11:08:21 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{a905fc21-8aba-11df-bc32-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/07/08 11:08:21 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{a905fc21-8aba-11df-bc32-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/07/08 11:08:21 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{a905fc21-8aba-11df-bc32-00262d289fc4}.TM.blf
[2010/06/28 11:45:16 | 000,000,174 | —- | C] () – C:\Users\Bryan\Desktop\Audit My PC.url
[2010/06/28 11:24:09 | 000,020,424 | —- | C] () – C:\Users\Bryan\Documents\cc_20100628_112406.reg
[2010/06/28 11:23:33 | 000,000,082 | —- | C] () – C:\Users\Bryan\Documents\cc_20100628_112326.reg
[2010/06/28 09:17:11 | 000,000,848 | —- | C] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\Media Player Classic - Home Cinema x64.lnk
[2010/06/28 09:17:11 | 000,000,824 | —- | C] () – C:\Users\Public\Desktop\Media Player Classic - Home Cinema x64.lnk
[2010/06/28 00:50:18 | 000,005,979 | —- | C] () – C:\Windows\SysNative\nvnrm.nvu
[2010/06/27 17:05:10 | 000,001,142 | —- | C] () – C:\Users\Bryan\Desktop\Pogo Games.lnk
[2010/06/20 19:36:12 | 000,000,778 | —- | C] () – C:\Users\Bryan\Desktop\Tom Clancy's Splinter Cell Conviction - Shortcut.lnk
[2010/06/19 21:10:07 | 000,000,221 | —- | C] () – C:\Users\Bryan\Desktop\Call of Duty Modern Warfare 2.url
[2010/06/19 21:10:07 | 000,000,221 | —- | C] () – C:\Users\Bryan\Desktop\Call of Duty Modern Warfare 2 - Multiplayer.url
[2010/06/19 20:24:45 | 000,000,921 | —- | C] () – C:\Users\Public\Desktop\Steam.lnk
[2010/06/18 19:15:51 | 000,019,016 | —- | C] () – C:\Windows\SysNative\drivers\hitmanpro35.sys
[2010/06/17 22:53:20 | 000,001,856 | —- | C] () – C:\Users\Public\Desktop\avast! Free Antivirus.lnk
[2010/06/15 23:22:22 | 000,000,050 | —- | C] () – C:\Windows\wininit.ini
[2010/06/12 02:33:56 | 000,001,134 | —- | C] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\Picasa 3.lnk
[2010/06/12 02:33:56 | 000,001,110 | —- | C] () – C:\Users\Public\Desktop\Picasa 3.lnk
[2010/06/11 19:47:04 | 000,001,140 | —- | C] () – C:\Users\Bryan\Desktop\Auslogics Disk Defrag.lnk
[2010/06/11 10:42:26 | 013,528,139 | —- | C] () – C:\Users\Bryan\Documents\PDFXVwer.zip
[2010/06/11 10:36:54 | 000,001,085 | —- | C] () – C:\Users\Bryan\Desktop\PDF-Viewer.lnk
[2010/06/10 22:55:34 | 000,018,528 | —- | C] () – C:\Users\Bryan\Documents\cc_20100610_225525.reg
[2010/06/10 21:24:39 | 000,000,000 | —- | C] () – C:\Windows\nsreg.dat
[2010/06/10 20:55:29 | 000,001,965 | —- | C] () – C:\Users\Public\Desktop\SUPERAntiSpyware Free Edition.lnk
[2010/06/06 00:13:36 | 000,001,607 | —- | C] () – C:\Users\Public\Desktop\Combat Arms.lnk
[2010/06/05 15:40:42 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{faea86da-70f0-11df-8bf9-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/06/05 15:40:42 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{faea86da-70f0-11df-8bf9-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/06/05 15:40:42 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{faea86da-70f0-11df-8bf9-00262d289fc4}.TM.blf
[2010/06/01 16:21:15 | 001,167,702 | —- | C] () – C:\Users\Bryan\Documents\draft_guide.cbs2010.pdf
[2010/05/30 20:24:20 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\WindowsAnytimeUpgradeUI.exe
[2010/05/29 00:00:35 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{81e1dd90-6aee-11df-95dc-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/29 00:00:35 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{81e1dd90-6aee-11df-95dc-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/29 00:00:35 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{81e1dd90-6aee-11df-95dc-00262d289fc4}.TM.blf
[2010/05/28 20:43:21 | 000,001,222 | —- | C] () – C:\Users\Public\Desktop\Google Desktop.lnk
[2010/05/28 15:42:20 | 000,000,000 | -H– | C] () – C:\Windows\SysNative\drivers\Msft_Kernel_SaiKF622_01005.Wdf
[2010/05/28 11:16:45 | 000,037,598 | —- | C] () – C:\Users\Bryan\Documents\cc_20100528_111630.regbackup.reg
[2010/05/28 10:26:20 | 000,001,011 | —- | C] () – C:\Users\Bryan\Desktop\CCleaner.lnk
[2010/05/28 10:11:08 | 000,001,973 | —- | C] () – C:\Users\Bryan\Desktop\Update Checker.lnk
[2010/05/25 14:46:54 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{7400f97e-682a-11df-8657-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/25 14:46:54 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{7400f97e-682a-11df-8657-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/25 14:46:54 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{7400f97e-682a-11df-8657-00262d289fc4}.TM.blf
[2010/05/23 17:29:22 | 002,427,248 | —- | C] () – C:\Windows\SysWow64\pbsvc_heroes.exe
[2010/05/22 11:31:47 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{be3a6db8-65cf-11df-b488-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/22 11:31:47 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{be3a6db8-65cf-11df-b488-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/22 11:31:47 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{be3a6db8-65cf-11df-b488-00262d289fc4}.TM.blf
[2010/05/22 11:28:19 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{1a9c8dd3-65ce-11df-b300-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/22 11:28:19 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{1a9c8dd3-65ce-11df-b300-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/22 11:28:19 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{1a9c8dd3-65ce-11df-b300-00262d289fc4}.TM.blf
[2010/05/22 11:16:45 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{abfe7c72-65c6-11df-bf90-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/22 11:16:45 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{abfe7c72-65c6-11df-bf90-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/22 11:16:45 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{abfe7c72-65c6-11df-bf90-00262d289fc4}.TM.blf
[2010/05/21 16:43:13 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\recdisc.exe
[2010/05/21 14:46:10 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\vdsldr.exe
[2010/05/21 12:39:56 | 000,000,900 | —- | C] () – C:\Users\Bryan\Desktop\Sandboxed Web Browser.lnk
[2010/05/21 12:39:56 | 000,000,900 | —- | C] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\Sandboxed Web Browser.lnk
[2010/05/21 12:39:54 | 000,001,368 | —- | C] () – C:\Windows\Sandboxie.ini
[2010/05/21 11:00:01 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\wsqmcons.exe
[2010/05/21 10:00:01 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\sdclt.exe
[2010/05/21 08:04:46 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\defrag.exe
[2010/05/20 15:31:31 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{d2ad8a2b-645e-11df-a4c1-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/20 15:31:31 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{d2ad8a2b-645e-11df-a4c1-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/20 15:31:31 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{d2ad8a2b-645e-11df-a4c1-00262d289fc4}.TM.blf
[2010/05/17 13:27:24 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\mdres.exe
[2010/05/17 13:12:28 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\MdSched.exe
[2010/05/17 00:54:34 | 000,001,662 | —- | C] () – C:\Users\Bryan\Desktop\Recuva.lnk
[2010/05/16 22:21:07 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{911b0d48-6171-11df-89fd-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/16 22:21:07 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{911b0d48-6171-11df-89fd-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/16 22:21:07 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{911b0d48-6171-11df-89fd-00262d289fc4}.TM.blf
[2010/05/15 15:10:25 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\DXPServer.exe
[2010/05/15 15:10:18 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\DeviceDisplayObjectProvider.exe
[2010/05/15 15:10:16 | 000,000,000 | -H– | C] () – C:\Windows\SysNative\drivers\Msft_User_WpdMtpDr_01_09_00.Wdf
[2010/05/15 11:47:26 | 000,002,031 | —- | C] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\Belarc Advisor.lnk
[2010/05/15 11:47:26 | 000,002,007 | —- | C] () – C:\Users\Public\Desktop\Belarc Advisor.lnk
[2010/05/15 08:30:11 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{e18fb18c-6035-11df-ad70-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/15 08:30:11 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{e18fb18c-6035-11df-ad70-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/15 08:30:11 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{e18fb18c-6035-11df-ad70-00262d289fc4}.TM.blf
[2010/05/14 21:26:13 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{3bb27f3f-5fd3-11df-ad2e-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/14 21:26:13 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{3bb27f3f-5fd3-11df-ad2e-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/14 21:26:13 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{3bb27f3f-5fd3-11df-ad2e-00262d289fc4}.TM.blf
[2010/05/14 00:16:58 | 000,088,813 | —- | C] () – C:\wubildr
[2010/05/14 00:16:58 | 000,008,192 | —- | C] () – C:\wubildr.mbr
[2010/05/13 22:07:16 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{133bfd4a-5ec9-11df-a441-00262d289fc4}.TMContainer00000000000000000002.regtrans-ms
[2010/05/13 22:07:16 | 000,524,288 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{133bfd4a-5ec9-11df-a441-00262d289fc4}.TMContainer00000000000000000001.regtrans-ms
[2010/05/13 22:07:16 | 000,065,536 | -HS- | C] () – C:\Users\Bryan\ntuser.dat{133bfd4a-5ec9-11df-a441-00262d289fc4}.TM.blf
[2010/05/13 19:08:49 | 000,000,036 | —- | C] () – C:\Users\Bryan\AppData\Local\housecall.guid.cache
[2010/05/13 11:13:07 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\nvuSMU.exe
[2010/05/13 11:12:10 | 000,001,463 | —- | C] () – C:\Windows\SysNative\nvsmu.nvu
[2010/05/13 10:59:10 | 000,001,118 | —- | C] () – C:\Users\Bryan\Desktop\DriverMax.lnk
[2010/05/12 22:09:42 | 000,001,893 | —- | C] () – C:\Users\Bryan\Application Data\Microsoft\Internet Explorer\Quick Launch\ImgBurn.lnk
[2010/05/12 22:09:42 | 000,001,869 | —- | C] () – C:\Users\Public\Desktop\ImgBurn.lnk
[2010/05/12 21:40:30 | 000,001,127 | —- | C] () – C:\Users\Bryan\Desktop\Partition Wizard Home Edition.lnk
[2010/05/12 21:33:41 | 000,611,400 | —- | C] () – C:\Windows\SysNative\pwNative.exe
[2010/05/12 21:33:40 | 000,019,936 | —- | C] () – C:\Windows\SysNative\pwdrvio.sys
[2010/05/12 21:33:40 | 000,013,280 | —- | C] () – C:\Windows\SysNative\pwdspio.sys
[2010/05/12 13:52:21 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\CompMgmtLauncher.exe
[2010/05/10 12:45:12 | 000,000,331 | —- | C] () – C:\Windows\game.ini
[2010/05/07 17:39:36 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\pcwutl.dll
[2010/05/05 01:17:07 | 000,000,000 | —- | C] () – C:\Windows\SysWow64\WerConCpl.dll
[2009/07/13 16:42:10 | 000,064,000 | —- | C] () – C:\Windows\SysWow64\BWContextHandler.dll
[2009/07/13 14:03:59 | 000,364,544 | —- | C] () – C:\Windows\SysWow64\msjetoledb40.dll
[2009/01/05 15:44:10 | 000,000,453 | —- | C] () – C:\Windows\bdoscandellang.ini
========== LOP Check ==========
[2010/08/07 01:28:13 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\abelhadigital.com
[2010/05/01 22:39:25 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\Acer
[2010/05/20 21:52:29 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\Auslogics
[2010/05/12 22:10:54 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\ImgBurn
[2010/05/01 22:39:24 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\Leadertech
[2010/05/12 11:46:15 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\Locate32
[2010/05/10 12:07:38 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\Masque
[2010/08/09 13:19:31 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\OnlineArmor
[2010/07/14 18:01:02 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\OpenDNS Updater
[2010/07/22 12:00:15 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\Panda Security
[2010/07/03 20:07:05 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\Razer
[2010/07/29 20:04:41 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\SystemNucleus
[2010/05/02 14:44:55 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\Template
[2010/06/10 21:24:38 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\Thunderbird
[2010/05/26 12:16:08 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\VSRevoGroup
[2010/05/02 14:46:49 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\WildTangent
[2010/06/25 12:03:34 | 000,000,000 | —D | M] – C:\Users\Bryan\AppData\Roaming\X-Setup Pro
[2010/07/31 07:33:32 | 000,032,542 | —- | M] () – C:\Windows\Tasks\SCHEDLGU.TXT
========== Purity Check ==========
========== Custom Scans ==========
< %SYSTEMDRIVE%\*.* >
[2009/10/27 23:29:13 | 000,008,192 | RHS- | M] () – C:\BOOTSECT.BAK
[2009/10/07 09:24:27 | 000,003,411 | —- | M] () \E0Z0LP11.MD5 – C:\E0Z0LP11.MD5
[2010/08/10 09:25:20 | 3018,756,096 | -HS- | M] () – C:\hiberfil.sys
[2009/10/07 09:23:28 | 000,000,308 | —- | M] () – C:\LPCD.DAT
[2010/08/10 09:25:24 | 4025,012,224 | -HS- | M] () – C:\pagefile.sys
[2009/10/27 22:47:27 | 000,002,035 | —- | M] () – C:\RHDSetup.log
[2010/05/14 00:16:58 | 000,088,813 | —- | M] () – C:\wubildr
[2010/05/14 00:16:58 | 000,008,192 | —- | M] () – C:\wubildr.mbr
< %systemroot%\system32\*.wt >
< %systemroot%\system32\*.ruy >
< %systemroot%\Fonts\*.com >
[2009/07/13 22:32:31 | 000,026,040 | —- | M] () – C:\Windows\Fonts\GlobalMonospace.CompositeFont
[2009/07/13 22:32:31 | 000,026,489 | —- | M] () – C:\Windows\Fonts\GlobalSansSerif.CompositeFont
[2009/07/13 22:32:31 | 000,029,779 | —- | M] () – C:\Windows\Fonts\GlobalSerif.CompositeFont
[2009/07/13 22:32:31 | 000,043,318 | —- | M] () – C:\Windows\Fonts\GlobalUserInterface.CompositeFont
< %systemroot%\Fonts\*.dll >
< %systemroot%\Fonts\*.ini >
[2009/06/10 13:49:50 | 000,000,065 | —- | M] () – C:\Windows\Fonts\desktop.ini
< %systemroot%\Fonts\*.ini2 >
< %systemroot%\system32\spool\prtprocs\w32x86\*.* >
< %systemroot%\REPAIR\*.bak1 >
< %systemroot%\REPAIR\*.ini >
< %systemroot%\system32\*.jpg >
< %systemroot%\*.scr >
[2010/06/28 13:57:33 | 000,038,848 | —- | M] (ALWIL Software) – C:\Windows\avastSS.scr
[2010/04/17 00:04:40 | 000,306,032 | —- | M] (Microsoft Corporation) – C:\Windows\WLXPGSS.SCR
< %systemroot%\*._sy >
< %APPDATA%\Adobe\Update\*.* >
< %ALLUSERSPROFILE%\Favorites\*.* >
< %APPDATA%\Microsoft\*.* >
< %PROGRAMFILES%\*.* >
[2009/07/13 21:54:24 | 000,000,174 | -HS- | M] () – C:\Program Files (x86)\desktop.ini
< %APPDATA%\Update\*.* >
< %systemroot%\*. /mp /s >
< %systemroot%\system32\*.dll /lockedfiles >
[2009/07/13 18:15:13 | 000,346,112 | —- | M] (Microsoft Corporation)
Unable to obtain MD5 – C:\Windows\SysWOW64\dxtmsft.dll
[2009/07/13 18:15:13 | 000,215,552 | —- | M] (Microsoft Corporation)
Unable to obtain MD5 – C:\Windows\SysWOW64\dxtrans.dll
[2009/07/13 18:16:15 | 000,496,128 | —- | M] (Microsoft Corporation)
Unable to obtain MD5 – C:\Windows\SysWOW64\taskschd.dll
< %systemroot%\Tasks\*.job /lockedfiles >
< %systemroot%\System32\config\*.sav >
< %systemroot%\system32\user32.dll /md5 >
[2009/07/13 18:11:24 | 000,833,024 | —- | M] (Microsoft Corporation) MD5=E8B0FFC209E504CB7E79FC24E6C085F0 – C:\Windows\SysWOW64\user32.dll
< %systemroot%\system32\ws2_32.dll /md5 >
[2009/07/13 18:16:20 | 000,206,336 | —- | M] (Microsoft Corporation) MD5=DAAE8A9B8C0ACC7F858454132553C30D – C:\Windows\SysWOW64\ws2_32.dll
< %systemroot%\system32\ws2help.dll /md5 >
[2009/07/13 18:11:26 | 000,004,608 | —- | M] (Microsoft Corporation) MD5=808AABDF9337312195CAFF76D1804786 – C:\Windows\SysWOW64\ws2help.dll
< HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU >
< HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install|LastSuccessTime /rs >
========== Alternate Data Streams ==========
@Alternate Data Stream - 145 bytes -> C:\ProgramData\TEMP:CDF47D67
@Alternate Data Stream - 127 bytes -> C:\ProgramData\TEMP:9B7E8561
@Alternate Data Stream - 122 bytes -> C:\ProgramData\TEMP:6987107A
< End of report >
OTL Extras logfile created on: 8/10/2010 12:49:11 PM - Run 1
OTL by OldTimer - Version 3.2.9.1 Folder = C:\Users\Bryan\Desktop
64bit- Home Premium Edition (Version = 6.1.7600) - Type = NTWorkstation
Internet Explorer (Version = 8.0.7600.16385)
Locale: 00000409 | Country: United States | Language: ENU | Date Format: M/d/yyyy
4.00 Gb Total Physical Memory | 3.00 Gb Available Physical Memory | 75.00% Memory free
7.00 Gb Paging File | 6.00 Gb Available in Paging File | 82.00% Paging File free
Paging file location(s): ?:\pagefile.sys [binary data]
%SystemDrive% = C: | %SystemRoot% = C:\Windows | %ProgramFiles% = C:\Program Files (x86)
Drive C: | 684.87 Gb Total Space | 570.14 Gb Free Space | 83.25% Space Free | Partition Type: NTFS
D: Drive not present or media not loaded
E: Drive not present or media not loaded
F: Drive not present or media not loaded
G: Drive not present or media not loaded
H: Drive not present or media not loaded
I: Drive not present or media not loaded
Computer Name: FAMILY
Current User Name: Bryan
Logged in as Administrator.
Current Boot Mode: Normal
Scan Mode: Current user
Include 64bit Scans
Company Name Whitelist: On
Skip Microsoft Files: On
File Age = 90 Days
Output = Minimal
Quick Scan
========== Extra Registry (SafeList) ==========
========== File Associations ==========
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\]
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\]
.cpl [@ = cplfile] – C:\Windows\SysWow64\control.exe (Microsoft Corporation)
[HKEY_CURRENT_USER\SOFTWARE\Classes\]
.html [@ = ChromeHTML] – Reg Error: Key error. File not found
========== Shell Spawning ==========
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\\shell\[command]\command]
batfile [open] – "%1" %* File not found
cmdfile [open] – "%1" %* File not found
comfile [open] – "%1" %* File not found
exefile [open] – "%1" %* File not found
helpfile [open] – Reg Error: Key error.
htmlfile – Reg Error: Key error.
htmlfile [print] – rundll32.exe %windir%\system32\mshtml.dll,PrintHTML "%1" File not found
http [open] – Reg Error: Key error.
https [open] – Reg Error: Key error.
inffile [install] – %SystemRoot%\System32\InfDefaultInstall.exe "%1" (Microsoft Corporation)
InternetShortcut [print] – "C:\Windows\System32\rundll32.exe" "C:\Windows\System32\mshtml.dll",PrintHTML "%1" (Microsoft Corporation)
piffile [open] – "%1" %* File not found
regfile [merge] – Reg Error: Key error.
scrfile [config] – "%1" File not found
scrfile [install] – rundll32.exe desk.cpl,InstallScreenSaver %l (Microsoft Corporation)
scrfile [open] – "%1" /S File not found
txtfile – Reg Error: Key error.
Unknown [openas] – %SystemRoot%\system32\rundll32.exe %SystemRoot%\system32\shell32.dll,OpenAs_RunDLL %1 File not found
Directory [cmd] – cmd.exe /s /k pushd "%V" (Microsoft Corporation)
Directory [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Folder [open] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Folder [explore] – Reg Error: Value error.
Drive [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\\shell\[command]\command]
batfile [open] – "%1" %*
cmdfile [open] – "%1" %*
comfile [open] – "%1" %*
cplfile [cplopen] – %SystemRoot%\System32\control.exe "%1",%* (Microsoft Corporation)
exefile [open] – "%1" %*
helpfile [open] – Reg Error: Key error.
htmlfile – Reg Error: Key error.
htmlfile [print] – rundll32.exe %windir%\system32\mshtml.dll,PrintHTML "%1"
http [open] – Reg Error: Key error.
https [open] – Reg Error: Key error.
inffile [install] – %SystemRoot%\System32\InfDefaultInstall.exe "%1" (Microsoft Corporation)
InternetShortcut [print] – "C:\Windows\System32\rundll32.exe" "C:\Windows\System32\mshtml.dll",PrintHTML "%1" (Microsoft Corporation)
piffile [open] – "%1" %*
regfile [merge] – Reg Error: Key error.
scrfile [config] – "%1"
scrfile [install] – rundll32.exe desk.cpl,InstallScreenSaver %l (Microsoft Corporation)
scrfile [open] – "%1" /S
txtfile – Reg Error: Key error.
Unknown [openas] – %SystemRoot%\system32\rundll32.exe %SystemRoot%\system32\shell32.dll,OpenAs_RunDLL %1
Directory [cmd] – cmd.exe /s /k pushd "%V" (Microsoft Corporation)
Directory [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Folder [open] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Folder [explore] – Reg Error: Value error.
Drive [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
========== Security Center Settings ==========
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center]
"cval" = 1
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Monitoring]
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Svc]
"VistaSp1" = 28 4D B2 76 41 04 CA 01 [binary data]
"AntiVirusOverride" = 0
"AntiSpywareOverride" = 0
"FirewallOverride" = 0
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Svc\Vol]
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center]
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Svc]
[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\DomainProfile]
"DisableNotifications" = 0
"EnableFirewall" = 1
[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\StandardProfile]
"DisableNotifications" = 0
"EnableFirewall" = 0
[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\PublicProfile]
"DisableNotifications" = 0
"EnableFirewall" = 0
"DefaultOutboundAction" = 0
"DefaultInboundAction" = 1
========== Authorized Applications List ==========
========== HKEY_LOCAL_MACHINE Uninstall List ==========
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall]
"{23170F69-40C1-2702-0915-000001000000}" = 7-Zip 9.15 (x64 edition)
"{26A24AE4-039D-4CA4-87B4-2F86416021FF}" = Java™ 6 Update 21 (64-bit)
"{2ACBF1FA-F5C3-4B19-A774-B22A31F231B9}_is1" = Media Player Classic - Home Cinema v. 1.3.1249.0
"{3D3E663D-4E7E-4577-A560-7ECDDD45548A}" = PVSonyDll
"{5AC309D7-93D6-418F-8DCA-DD710724A5B4}" = Windows Live Family Safety
"{7CFA46E3-CC2F-4355-82AE-6012DC3633FD}" = NVIDIA ForceWare Network Access Manager
"{8CBBBC4D-B0B6-49DB-A421-98C65080D8EE}" = Eraser 6.0.7.1893
"{8D273DE5-ABFA-4BD0-A9D7-EE9C971438C4}_is1" = PDF-Viewer
"{95120000-00B9-0409-1000-0000000FF1CE}" = Microsoft Application Error Reporting
"{9B48B0AC-C813-4174-9042-476A887592C7}" = Windows Live ID Sign-in Assistant
"{CDDCBBF1-2703-46BC-938B-BCC81A1EEAAA}" = SUPERAntiSpyware
"{D40DBBFD-B87E-4E45-B15F-753B75C0D7F8}_is1" = Spencerberus System Nucleus
"{F5B09CFD-F0B2-36AF-8DF4-1DF6B63FC7B4}" = Microsoft .NET Framework 4 Client Profile
"Microsoft .NET Framework 4 Client Profile" = Microsoft .NET Framework 4 Client Profile
"NVIDIA Display Control Panel" = NVIDIA Display Control Panel
"NVIDIA Drivers" = NVIDIA Drivers
"Recuva" = Recuva
"Sandboxie" = Sandboxie 3.442 (64-bit)
"SDEPRO20_is1" = SDExplorer 2.1
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall]
"{048298C9-A4D3-490B-9FF9-AB023A9238F3}" = Steam
"{06E6E30D-B498-442F-A943-07DE41D7F785}" = Microsoft Search Enhancement Pack
"{0b739e85-e796-499c-98fe-3be76860dfd0}" = Nero 9 Essentials
"{15D967B5-A4BE-42AE-9E84-64CD062B25AA}" = eSobi v2
"{178832DE-9DE0-4C87-9F82-9315A9B03985}" = Windows Live Writer
"{18455581-E099-4BA8-BC6B-F34B2F06600C}" = Google Toolbar for Internet Explorer
"{1BD07DF4-FB06-41BA-B896-B2DA59000C96}" = Windows Live Toolbar
"{1F1C2DFC-2D24-3E06-BCB8-725134ADF989}" = Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.4148
"{20400dbd-e6db-45b8-9b6b-1dd7033818ec}" = Nero InfoTool Help
"{205C6BDD-7B73-42DE-8505-9A093F35A238}" = Windows Live Upload Tool
"{22B775E7-6C42-4FC5-8E10-9A5E3257BD94}" = MSVCRT
"{2318C2B1-4965-11d4-9B18-009027A5CD4F}" = Google Toolbar for Internet Explorer
"{2348b586-c9ae-46ce-936c-a68e9426e214}" = Nero StartSmart Help
"{26A24AE4-039D-4CA4-87B4-2F83216020FF}" = Java™ 6 Update 20
"{287ECFA4-719A-2143-A09B-D6A12DE54E40}" = Acrobat.com
"{30075A70-B5D2-440B-AFA3-FB2021740121}" = Backup Manager Advance
"{3175E049-F9A9-4A3D-8F19-AC9FB04514D1}" = Windows Live Communications Platform
"{33cf58f5-48d8-4575-83d6-96f574e4d83a}" = Nero DriveSpeed
"{45A66726-69BC-466B-A7A4-12FCBA4883D7}" = HiJackThis
"{474F25F5-BDC9-40E5-B1B6-F6BF23FC106F}" = Windows Live Essentials
"{4A03706F-666A-4037-7777-5F2748764D10}" = Java Auto Updater
"{4D43D635-6FDA-4fa5-AA9B-23CF73D058EA}" = Nero StartSmart OEM
"{56C049BE-79E9-4502-BEA7-9754A3E60F9B}" = neroxml
"{595a3116-40bb-4e0f-a2e8-d7951da56270}" = NeroExpress
"{6412CECE-8172-4BE5-935B-6CECACD2CA87}" = Windows Live Mail
"{67E03279-F703-408F-B4BF-46B5FC8D70CD}" = Microsoft Works
"{68301905-2DEA-41CE-A4D4-E8B443B099BA}" = MyWinLocker
"{6D8DDB4A-C263-40DE-BA16-AFDAD159D59A}" = Tom Clancy's Splinter Cell Conviction
"{6ED53E0C-EAC0-4F0F-947D-6BA817E4C8C3}" = HostsMan 3.2.73
"{7299052b-02a4-4627-81f2-1818da5d550d}" = Microsoft Visual C++ 2005 Redistributable
"{7748ac8c-18e3-43bb-959b-088faea16fb2}" = Nero StartSmart
"{7F811A54-5A09-4579-90E1-C93498E230D9}" = Acer eRecovery Management
"{82C36957-D2B8-4EF2-B88C-5FA03AA848C7-11562057}" = PICTUREKA! MUSEUM MAYHEM
"{82C36957-D2B8-4EF2-B88C-5FA03AA848C7-119045237}" = Classic Adventures The Great Gatsby
"{83202942-84b3-4c50-8622-b8c0aa2d2885}" = Nero Express Help
"{837b34e3-7c30-493c-8f6a-2b0f04e2912c}" = Microsoft Visual C++ 2005 Redistributable
"{869200db-287a-4dc0-b02b-2b6787fbcd4c}" = Nero DiscSpeed
"{888F1505-C2B3-4FDE-835D-36353EBD4754}" = Ubisoft Game Launcher
"{89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}" = Microsoft Silverlight
"{8A74E887-8F0F-4017-AF53-CBA42211AAA5}" = Microsoft Sync Framework Runtime Native v1.0 (x86)
"{8DC910CD-8EE3-4ffc-A4EB-9B02701059C4}" = Battlefield Heroes
"{8E5233E1-7495-44FB-8DEB-4BE906D59619}" = Junk Mail filter update
"{90120000-0020-0409-0000-0000000FF1CE}" = Compatibility Pack for the 2007 Office system
"{95120000-00AF-0409-0000-0000000FF1CE}" = Microsoft Office PowerPoint Viewer 2007 (English)
"{980A182F-E0A2-4A40-94C1-AE0C1235902E}" = Pando Media Booster
"{9E1BAB75-EB78-440D-94C0-A3857BE2E733}" = System Requirements Lab
"{9F479685-180E-4C05-9400-D59292A1B29C}" = Windows Live Movie Maker
"{A54F806B-A2E1-4794-A7FE-365167EC67CB}" = Masque IGT Slots Little Green Men
"{A8F2089B-1F79-4BF6-B385-A2C2B0B9A74D}" = ImagXpress
"{A92DAB39-4E2C-4304-9AB6-BC44E68B55E2}" = Google Update Helper
"{AA468551-1794-42FE-B504-C41D75EEBDF2}_is1" = Partition Wizard Home Edition 5.0
"{AC76BA86-7AD7-1033-7B44-A93000000001}" = Adobe Reader 9.3.3
"{B10914FD-8812-47A4-85A1-50FCDE7F1F33}" = Windows Live Sync
"{B194272D-1F92-46DF-99EB-8D5CE91CB4EC}" = Adobe AIR
"{b2ec4a38-b545-4a00-8214-13fe0e915e6d}" = Advertising Center
"{B57EAFF2-D6EE-4C6C-9175-ED9F17BFC1BC}" = Windows Live Messenger
"{bd5ca0da-71ad-43da-b19e-6eee0c9adc9a}" = Nero ControlCenter
"{BD64AF4A-8C80-4152-AD77-FCDDF05208AB}" = Microsoft Sync Framework Services Native v1.0 (x86)
"{CB4532F7-A1BD-46D2-9938-3E7D4656FB18}" = Razer Lachesis
"{cc019e3f-59d2-4486-8d4b-878105b62a71}" = Nero DiscSpeed Help
"{DB0BB9FA-1B60-4036-8E29-3D56D8085256}" = WOT for Internet Explorer
"{dba84796-8503-4ff0-af57-1747dd9a166d}" = Nero Online Upgrade
"{DF6A13C0-77DF-41FE-BD05-6D5201EB0CE7}_is1" = Auslogics Disk Defrag
"{E48469CC-635E-4FD5-A122-1497C286D217}" = Call of Duty® 4 - Modern Warfare™
"{E50AE784-FABE-46DA-A1F8-7B6B56DCB22E}" = Microsoft Office Suite Activation Assistant
"{e5c7d048-f9b4-4219-b323-8bdb01a2563d}" = Nero DriveSpeed Help
"{E6158D07-2637-4ECF-B576-37C489669174}" = Windows Live Call
"{e8a80433-302b-4ff1-815d-fcc8eac482ff}" = Nero Installer
"{EE171732-BEB4-4576-887D-CB62727F01CA}" = Acer Updater
"{EE39FFBD-544E-49E4-A999-6819828EAE91}" = Windows Live Photo Gallery
"{F0B430D1-B6AA-473D-9B06-AA3DD01FD0B8}" = Microsoft SQL Server 2005 Compact Edition [ENU]
"{F0E12BBA-AD66-4022-A453-A1C8A0C4D570}" = Microsoft Choice Guard
"{F132AF7F-7BCA-4EDE-8A7C-958108FE7DBC}" = Realtek High Definition Audio Driver
"{f4041dce-3fe1-4e18-8a9e-9de65231ee36}" = Nero ControlCenter
"{F40BBEC7-C2A4-4A00-9B24-7A055A2C5262}" = Microsoft Office Live Add-in 1.5
"{fbcdfd61-7dcf-4e71-9226-873ba0053139}" = Nero InfoTool
"Acer Assist" = Acer Assist
"Acer Registration" = Acer Registration
"Acer Screensaver" = Acer ScreenSaver
"Acer Welcome Center" = Welcome Center
"Adobe AIR" = Adobe AIR
"Adobe Flash Player ActiveX" = Adobe Flash Player 10 ActiveX
"Adobe Flash Player Plugin" = Adobe Flash Player 10 Plugin
"avast5" = avast! Free Antivirus
"Belarc Advisor" = Belarc Advisor 8.1
"CCleaner" = CCleaner
"Combat Arms" = Combat Arms
"DMX5_is1" = DriverMax 5
"ESET Online Scanner" = ESET Online Scanner v3
"FileHippo.com" = FileHippo.com Update Checker
"GamersFirst LIVE!" = GamersFirst LIVE!
"GamesBar" = GamesBar [removed]
"Google Desktop" = Google Desktop
"Hotkey Utility" = Hotkey Utility
"Identity Card" = Identity Card
"ImgBurn" = ImgBurn
"InstallShield_{15D967B5-A4BE-42AE-9E84-64CD062B25AA}" = eSobi v2
"InstallShield_{30075A70-B5D2-440B-AFA3-FB2021740121}" = Acer Backup Manager
"InstallShield_{7CFA46E3-CC2F-4355-82AE-6012DC3633FD}" = NVIDIA ForceWare Network Access Manager
"InstallShield_{E48469CC-635E-4FD5-A122-1497C286D217}" = Call of Duty® 4 - Modern Warfare™
"Malwarebytes' Anti-Malware_is1" = Malwarebytes' Anti-Malware
"OnlineArmor_is1" = Online Armor 4.0
"OpenDNS Updater" = OpenDNS Updater 2.2.1
"Picasa 3" = Picasa 3
"PokerStars" = PokerStars
"PunkBusterSvc" = PunkBuster Services
"Revo Uninstaller" = Revo Uninstaller 1.89
"Secunia PSI" = Secunia PSI
"Sophos-AntiRootkit" = Sophos Anti-Rootkit 1.5.4
"Steam App 10180" = Call of Duty: Modern Warfare 2
"Steam App 10190" = Call of Duty: Modern Warfare 2 - Multiplayer
"Steam App 240" = Counter-Strike: Source
"Steam App 630" = Alien Swarm
"SystemRequirementsLab" = System Requirements Lab
"WildTangent acer Master Uninstall" = Acer Games
"WinLiveSuite_Wave3" = Windows Live Essentials
"Wubi" = Ubuntu
========== Last 10 Event Log Errors ==========
[ Application Events ]
Error - 8/6/2010 5:13:21 PM | Computer Name = Family | Source = Microsoft-Windows-CAPI2 | ID = 4107
Description = Failed extract of third-party root list from auto update cab at: <
http://www.download.windowsupdate.com/msdownload/update/v3/static/trustedr/en/authrootstl.cab>
with error: A required certificate is not within its validity period when verifying
against the current system clock or the timestamp in the signed file. .
Error - 8/6/2010 5:21:07 PM | Computer Name = Family | Source = Application Hang | ID = 1002
Description = The program oaui.exe version 4.0.0.164 stopped interacting with Windows
and was closed. To see if more information about the problem is available, check
the problem history in the Action Center control panel. Process ID: 740 Start Time:
01cb35ad0b50b4e0 Termination Time: 0 Application Path: C:\Program Files (x86)\Online
Armor\oaui.exe Report Id:
Error - 8/6/2010 5:27:18 PM | Computer Name = Family | Source = Application Hang | ID = 1002
Description = The program oaui.exe version 4.0.0.164 stopped interacting with Windows
and was closed. To see if more information about the problem is available, check
the problem history in the Action Center control panel. Process ID: d00 Start Time:
01cb35ade7069e00 Termination Time: 16 Application Path: C:\Program Files (x86)\Online
Armor\oaui.exe Report Id:
Error - 8/6/2010 6:13:43 PM | Computer Name = Family | Source = Microsoft-Windows-CAPI2 | ID = 4107
Description = Failed extract of third-party root list from auto update cab at: <
http://www.download.windowsupdate.com/msdownload/update/v3/static/trustedr/en/authrootstl.cab>
with error: A required certificate is not within its validity period when verifying
against the current system clock or the timestamp in the signed file. .
Error - 8/6/2010 6:44:36 PM | Computer Name = Family | Source = Application Hang | ID = 1002
Description = The program oaui.exe version 4.0.0.164 stopped interacting with Windows
and was closed. To see if more information about the problem is available, check
the problem history in the Action Center control panel. Process ID: 97c Start Time:
01cb35b521740760 Termination Time: 0 Application Path: C:\Program Files (x86)\Online
Armor\oaui.exe Report Id:
Error - 8/6/2010 7:04:29 PM | Computer Name = Family | Source = Microsoft-Windows-CAPI2 | ID = 4107
Description = Failed extract of third-party root list from auto update cab at: <
http://www.download.windowsupdate.com/msdownload/update/v3/static/trustedr/en/authrootstl.cab>
with error: A required certificate is not within its validity period when verifying
against the current system clock or the timestamp in the signed file. .
Error - 8/6/2010 7:36:41 PM | Computer Name = Family | Source = Application Hang | ID = 1002
Description = The program oaui.exe version 4.0.0.174 stopped interacting with Windows
and was closed. To see if more information about the problem is available, check
the problem history in the Action Center control panel. Process ID: 1378 Start Time:
01cb35bf772d1520 Termination Time: 16 Application Path: C:\Program Files (x86)\Online
Armor\oaui.exe Report Id:
Error - 8/6/2010 8:00:11 PM | Computer Name = Family | Source = Microsoft-Windows-CAPI2 | ID = 4107
Description = Failed extract of third-party root list from auto update cab at: <
http://www.download.windowsupdate.com/msdownload/update/v3/static/trustedr/en/authrootstl.cab>
with error: A required certificate is not within its validity period when verifying
against the current system clock or the timestamp in the signed file. .
Error - 8/6/2010 8:55:28 PM | Computer Name = Family | Source = Application Hang | ID = 1002
Description = The program iexplore.exe version 8.0.7600.16385 stopped interacting
with Windows and was closed. To see if more information about the problem is available,
check the problem history in the Action Center control panel. Process ID: b80 Start
Time: 01cb35caf36e0210 Termination Time: 16 Application Path: C:\Program Files (x86)\Internet
Explorer\iexplore.exe Report Id: 6c06f651-a1be-11df-93f6-00262d289fc4
Error - 8/6/2010 9:08:51 PM | Computer Name = Family | Source = Microsoft-Windows-CAPI2 | ID = 4107
Description = Failed extract of third-party root list from auto update cab at: <
http://www.download.windowsupdate.com/msdownload/update/v3/static/trustedr/en/authrootstl.cab>
with error: A required certificate is not within its validity period when verifying
against the current system clock or the timestamp in the signed file. .
[ System Events ]
Error - 6/18/2010 4:59:34 PM | Computer Name = Family | Source = Service Control Manager | ID = 7000
Description = The CSIScanner service failed to start due to the following error:
%%2
Error - 6/18/2010 10:16:00 PM | Computer Name = Family | Source = Service Control Manager | ID = 7006
Description = The ScRegSetValueExW call failed for ImagePath with the following
error: %%5
Error - 6/18/2010 10:21:48 PM | Computer Name = Family | Source = Service Control Manager | ID = 7000
Description = The CSIScanner service failed to start due to the following error:
%%2
Error - 6/19/2010 2:13:07 AM | Computer Name = Family | Source = Service Control Manager | ID = 7000
Description = The CSIScanner service failed to start due to the following error:
%%2
Error - 6/19/2010 9:31:10 AM | Computer Name = Family | Source = Service Control Manager | ID = 7000
Description = The CSIScanner service failed to start due to the following error:
%%2
Error - 6/19/2010 11:20:26 AM | Computer Name = Family | Source = Service Control Manager | ID = 7000
Description = The CSIScanner service failed to start due to the following error:
%%2
Error - 6/19/2010 1:01:57 PM | Computer Name = Family | Source = DCOM | ID = 10001
Description =
Error - 6/19/2010 11:34:06 PM | Computer Name = Family | Source = Service Control Manager | ID = 7009
Description = A timeout was reached (30000 milliseconds) while waiting for the Steam
Client Service service to connect.
Error - 6/19/2010 11:34:06 PM | Computer Name = Family | Source = Service Control Manager | ID = 7000
Description = The Steam Client Service service failed to start due to the following
error: %%1053
Error - 6/20/2010 2:03:50 AM | Computer Name = Family | Source = Service Control Manager | ID = 7000
Description = The CSIScanner service failed to start due to the following error:
%%2
< End of report >