Here's the two DDS things.
DDS (Ver_10-03-17.01) - NTFSx86
Run by [removed] at 9:58:25.08 on Mon 06/28/2010
Internet Explorer: 6.0.2900.2180 BrowserJavaVersion: 1.6.0_17
Microsoft Windows XP Professional 5.1.2600.2.1252.1.1033.18.128.8 [GMT -5:00]
AV: AntiVir Desktop *On-access scanning enabled* (Outdated) {AD166499-45F9-482A-A743-FDD3350758C7}
============== Running Processes ===============
C:\WINDOWS\system32\svchost -k DcomLaunch
svchost.exe
C:\WINDOWS\System32\svchost.exe -k netsvcs
svchost.exe
svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\Program Files\Avira\AntiVir Desktop\sched.exe
svchost.exe
C:\Program Files\Avira\AntiVir Desktop\avguard.exe
C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
C:\Program Files\Belkin\Belkin Wireless Network Utility\WLService.exe
C:\Program Files\Belkin\Belkin Wireless Network Utility\WLanCfgG.exe
C:\Program Files\Java\jre6\bin\jqs.exe
C:\Program Files\Avira\AntiVir Desktop\avgnt.exe
C:\Program Files\Java\jre6\bin\jusched.exe
C:\Program Files\iTunes\iTunesHelper.exe
C:\Program Files\uTorrent\uTorrent.exe
C:\Program Files\Messenger\msmsgs.exe
C:\Program Files\iPod\bin\iPodService.exe
C:\Program Files\Mozilla Firefox\firefox.exe
C:\WINDOWS\system32\wuauclt.exe
C:\WINDOWS\system32\wscntfy.exe
C:\WINDOWS\explorer.exe
C:\Documents and Settings\Dain Neuharth\My Documents\Downloads\dds.com
============== Pseudo HJT Report ===============
uInternet Settings,ProxyServer = http=127.0.0.1:5577
uInternet Settings,ProxyOverride =
BHO: Gamevance: {0ed403e8-470a-4a8a-85a4-d7688cfe39a3} - c:\program files\gamevance\gamevancelib32.dll
BHO: Java™ Plug-In 2 SSV Helper: {dbc80044-a445-435b-bc74-9c25c1c588a9} - c:\program files\java\jre6\bin\jp2ssv.dll
BHO: kikin Plugin: {e601996f-e400-41ca-804b-cd6373a7eee2} - c:\program files\kikin\ie_kikin.dll
BHO: JQSIEStartDetectorImpl Class: {e7e6f031-17ce-4c07-bc86-eabfe594f69c} - c:\program files\java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll
EB: {32683183-48a0-441b-a342-7c2a440a9478} - No File
uRun: [uTorrent] "c:\program files\utorrent\uTorrent.exe"
uRun: [MSMSGS] "c:\program files\messenger\msmsgs.exe" /background
uRun: [oodwprvk] c:\documents and settings\dain neuharth\local settings\application data\yqkbsubps\kudiysftssd.exe
mRun: [avgnt] "c:\program files\avira\antivir desktop\avgnt.exe" /min
mRun: [SunJavaUpdateSched] "c:\program files\java\jre6\bin\jusched.exe"
mRun: [QuickTime Task] "c:\program files\quicktime\QTTask.exe" -atboottime
mRun: [iTunesHelper] "c:\program files\itunes\iTunesHelper.exe"
mRun: [Gamevance] c:\program files\gamevance\gamevance32.exe a
mRun: [oodwprvk] c:\documents and settings\dain neuharth\local settings\application data\yqkbsubps\kudiysftssd.exe
StartupFolder: c:\docume~1\dainne~1\startm~1\programs\startup\imtooy~1.lnk - c:\program files\imtoo\youtube video converter\YoutubeVideoConverter.exe
IE: Download with ImTOO YouTube Video Converter - c:\program files\imtoo\youtube video converter\upod_link.HTM
IE: E&xport to Microsoft Excel - c:\progra~1\micros~2\office11\EXCEL.EXE/3000
IE: {FB5F1910-F110-11d2-BB9E-00C04F795683} - c:\program files\messenger\msmsgs.exe
IE: {0F7195C2-6713-4d93-A1BC-DA5FA33F0A65} - {E601996F-E400-41CA-804B-CD6373A7EEE2} - c:\program files\kikin\ie_kikin.dll
IE: {92780B25-18CC-41C8-B9BE-3C9C571A8263} - {FF059E31-CC5A-4E2E-BF3B-96E929D65503} - c:\progra~1\micros~2\office11\REFIEBAR.DLL
DPF: {00000162-9980-0010-8000-00AA00389B71} - hxxp://download.microsoft.com/download/0/B/B/0BB06A5C-8611-4840-86B3-54DDDD0344B9/wma9dmo.cab
DPF: {31435657-9980-0010-8000-00AA00389B71} - hxxp://download.microsoft.com/download/e/2/f/e2fcec4b-6c8b-48b7-adab-ab9c403a978f/wvc1dmo.cab
DPF: {33564D57-9980-0010-8000-00AA00389B71} - hxxp://download.microsoft.com/download/D/0/D/D0DD87DA-994F-4334-8B55-AF2E4D98ED0C/wmv9dmo.cab
DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_17-windows-i586.cab
DPF: {CAFEEFAC-0016-0000-0017-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_17-windows-i586.cab
DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_17-windows-i586.cab
DPF: {D27CDB6E-AE6D-11CF-96B8-444553540000} - hxxp://download.macromedia.com/pub/shockwave/cabs/flash/swflash.cab
DPF: {E2883E8F-472F-4FB0-9522-AC9BF37916A7} - hxxp://platformdl.adobe.com/NOS/getPlusPlus/1.6/gp.cab
================= FIREFOX ===================
FF - ProfilePath - c:\docume~1\dainne~1\applic~1\mozilla\firefox\profiles\fw94j1zx.default\
FF - component: c:\documents and settings\dain neuharth\application data\mozilla\firefox\profiles\fw94j1zx.default\extensions\{7b13ec3e-999a-4b70-b9cb-2617b8323822}\components\FFExternalAlert.dll
FF - component: c:\documents and settings\dain neuharth\application data\mozilla\firefox\profiles\fw94j1zx.default\extensions\{7b13ec3e-999a-4b70-b9cb-2617b8323822}\components\RadioWMPCore.dll
FF - plugin: c:\documents and settings\dain neuharth\my documents\bin\npbyond.dll
FF - plugin: c:\documents and settings\dain neuharth\my documents\byond\bin\npbyond.dll
FF - plugin: c:\program files\byond\bin\npbyond.dll
FF - plugin: c:\program files\mozilla firefox\plugins\npbyond.dll
FF - plugin: c:\program files\pando networks\media booster\npPandoWebPlugin.dll
FF - HiddenExtension: Java Console: No Registry Reference - c:\program files\mozilla firefox\extensions\{CAFEEFAC-0016-0000-0017-ABCDEFFEDCBA}
—- FIREFOX POLICIES —-
FF - user.js: yahoo.homepage.dontask - truec:\program files\mozilla firefox\greprefs\security-prefs.js - pref("security.ssl.allow_unrestricted_renego_everywhere__temporarily_available_pr
ef", true);
c:\program files\mozilla firefox\greprefs\security-prefs.js - pref("security.ssl.renego_unrestricted_hosts", "");
c:\program files\mozilla firefox\greprefs\security-prefs.js - pref("security.ssl.treat_unsafe_negotiation_as_broken", false);
c:\program files\mozilla firefox\greprefs\security-prefs.js - pref("security.ssl.require_safe_negotiation", false);
c:\program files\mozilla firefox\greprefs\security-prefs.js - pref("security.ssl3.rsa_seed_sha", true);
c:\program files\mozilla firefox\defaults\pref\firefox-branding.js - pref("app.update.url.manual", "http://www.firefox.com");
============= SERVICES / DRIVERS ===============
R0 avgntmgr;avgntmgr;c:\windows\system32\drivers\avgntmgr.sys [2009-10-4 22360]
R1 avgntdd;avgntdd;c:\windows\system32\drivers\avgntdd.sys [2009-10-4 45416]
=============== Created Last 30 ================
2010-06-25 15:23:12 0 d—–w- c:\program files\MSXML 4.0
2010-06-25 05:16:54 0 d—–w- c:\windows\system32\PreInstall
2010-06-25 05:16:49 0 d–h–w- c:\windows\$hf_mig$
2010-06-24 21:05:13 0 d—–w- c:\program files\Dofus 2
2010-06-23 22:05:54 0 d—–w- c:\docume~1\dainne~1\applic~1\LolClient
2010-06-23 21:43:02 68616 —-a-w- c:\windows\system32\XAPOFX1_1.dll
2010-06-23 21:43:02 509448 —-a-w- c:\windows\system32\XAudio2_2.dll
2010-06-23 21:42:44 467984 —-a-w- c:\windows\system32\d3dx10_39.dll
2010-06-23 21:42:44 1493528 —-a-w- c:\windows\system32\D3DCompiler_39.dll
2010-06-23 21:42:10 3851784 —-a-w- c:\windows\system32\D3DX9_39.dll
2010-06-23 21:09:23 0 d—–w- C:\Riot Games
2010-06-23 20:43:04 0 d—–w- c:\docume~1\alluse~1\applic~1\PMB Files
2010-06-23 20:42:20 0 d—–w- c:\program files\Pando Networks
2010-06-17 20:39:42 0 d—–w- c:\windows\system32\appmgmt
2010-06-09 18:11:25 177664 -c—-w- c:\windows\system32\dllcache\wintrust.dll
==================== Find3M ====================
2010-06-22 15:20:55 2496 —-a-w- c:\windows\system32\d3d8caps.dat
2010-06-04 00:46:59 2608 —-a-w- c:\windows\system32\d3d9caps.dat
2010-05-31 02:41:37 87 —-a-w- c:\documents and settings\dain neuharth\jagex_runescape_preferences2.dat
2010-05-31 02:34:12 42 —-a-w- c:\documents and settings\dain neuharth\jagex_runescape_preferences.dat
2010-05-02 05:56:34 1850880 —-a-w- c:\windows\system32\win32k.sys
2010-04-20 05:51:20 285696 —-a-w- c:\windows\system32\atmfd.dll
2010-04-16 15:36:49 662016 —-a-w- c:\windows\system32\wininet.dll
2010-04-16 15:36:45 81920 ——w- c:\windows\system32\ieencode.dll
2010-04-03 01:34:12 0 -c–a-w- c:\documents and settings\dain neuharth\jagex__preferences3.dat
============= FINISH: 10:00:00.61 ===============
UNLESS SPECIFICALLY INSTRUCTED, DO NOT POST THIS LOG.
IF REQUESTED, ZIP IT UP & ATTACH IT
DDS (Ver_10-03-17.01)
Microsoft Windows XP Professional
Boot Device: \Device\HarddiskVolume1
Install Date: 10/3/2009 8:26:38 PM
System Uptime: 6/28/2010 9:37:19 AM (1 hours ago)
Motherboard: Compaq | | 0550h
Processor: Intel Pentium III processor | XU1 | 730/133mhz
==== Disk Partitions =========================
A: is Removable
C: is FIXED (NTFS) - 13 GiB total, 6.415 GiB free.
D: is CDROM ()
==== Disabled Device Manager Items =============
Class GUID: {4D36E972-E325-11CE-BFC1-08002BE10318}
Description: Intel® PRO/100+ Management Adapter with Alert On LAN*
Device ID: PCI\VEN_8086&DEV_1229&SUBSYS_000E8086&REV_08\4&24AB0D93&0&40F0
Manufacturer: Intel
Name: Intel® PRO/100+ Management Adapter with Alert On LAN*
PNP Device ID: PCI\VEN_8086&DEV_1229&SUBSYS_000E8086&REV_08\4&24AB0D93&0&40F0
Service: E100B
Class GUID: {4D36E96F-E325-11CE-BFC1-08002BE10318}
Description: PS/2 Compatible Mouse
Device ID: ACPI\PNP0F13\4&264480D3&0
Manufacturer: Microsoft
Name: PS/2 Compatible Mouse
PNP Device ID: ACPI\PNP0F13\4&264480D3&0
Service: i8042prt
==== System Restore Points ===================
RP232: 6/8/2010 8:02:38 PM - System Checkpoint
RP233: 6/9/2010 8:33:13 PM - System Checkpoint
RP234: 6/10/2010 9:02:32 PM - System Checkpoint
RP235: 6/11/2010 9:33:18 PM - System Checkpoint
RP236: 6/12/2010 11:14:16 PM - System Checkpoint
RP237: 6/13/2010 11:34:13 PM - System Checkpoint
RP238: 6/15/2010 12:23:59 AM - System Checkpoint
RP239: 6/16/2010 12:38:45 AM - System Checkpoint
RP240: 6/17/2010 1:38:43 AM - System Checkpoint
RP241: 6/17/2010 3:38:33 PM - Removed Bonjour
RP242: 6/18/2010 4:38:32 PM - System Checkpoint
RP243: 6/19/2010 5:38:38 PM - System Checkpoint
RP244: 6/20/2010 9:35:14 PM - System Checkpoint
RP245: 6/21/2010 11:11:04 PM - System Checkpoint
RP246: 6/22/2010 11:52:31 PM - System Checkpoint
RP247: 6/23/2010 4:09:06 PM - Installed League of Legends
RP248: 6/23/2010 6:05:27 PM - Removed League of Legends
RP249: 6/25/2010 12:16:27 AM - Software Distribution Service 3.0
RP250: 6/25/2010 10:21:47 AM - Software Distribution Service 3.0
RP251: 6/25/2010 11:02:05 PM - Software Distribution Service 3.0
RP252: 6/27/2010 11:03:52 PM - Software Distribution Service 3.0
==== Installed Programs ======================
µTorrent
Adobe AIR
Adobe Download Manager
Adobe Flash Player 10 ActiveX
Adobe Flash Player 10 Plugin
Apple Application Support
Apple Mobile Device Support
Apple Software Update
Avira AntiVir Personal - Free Antivirus
Belkin 54g USB Network Adapter
Build Your Own Net Dream (remove only)
Counter-Strike 2D 0.1.1.7
Free NaturalReader
Gamevance
Halo Zero Final V1.8.3
Hotfix for Windows XP (KB952287)
ImTOO YouTube Video Converter
iTunes
Java™ 6 Update 17
kikin plugin (CounterStrike2D Edition) 2.0
League of Legends
Microsoft .NET Framework 2.0
Microsoft Office Professional Edition 2003
Microsoft Visual C++ 2008 Redistributable - x86 9.0.21022
Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.17
Mozilla Firefox (3.5.10)
MSXML 4.0 SP2 (KB954430)
MSXML 4.0 SP2 (KB973688)
Pando Media Booster
QuickTime
Security Update for Windows Media Player (KB952069)
Security Update for Windows Media Player (KB954155)
Security Update for Windows Media Player (KB973540)
Security Update for Windows Media Player (KB978695)
Security Update for Windows Media Player (KB979402)
Security Update for Windows XP (KB923561)
Security Update for Windows XP (KB944338-v2)
Security Update for Windows XP (KB946648)
Security Update for Windows XP (KB950760)
Security Update for Windows XP (KB950762)
Security Update for Windows XP (KB950974)
Security Update for Windows XP (KB951376-v2)
Security Update for Windows XP (KB951748)
Security Update for Windows XP (KB952004)
Security Update for Windows XP (KB952954)
Security Update for Windows XP (KB955069)
Security Update for Windows XP (KB956572)
Security Update for Windows XP (KB956802)
Security Update for Windows XP (KB956803)
Security Update for Windows XP (KB956844)
Security Update for Windows XP (KB958470)
Security Update for Windows XP (KB958644)
Security Update for Windows XP (KB958869)
Security Update for Windows XP (KB959426)
Security Update for Windows XP (KB960225)
Security Update for Windows XP (KB960803)
Security Update for Windows XP (KB960859)
Security Update for Windows XP (KB961501)
Security Update for Windows XP (KB969059)
Security Update for Windows XP (KB970238)
Security Update for Windows XP (KB971032)
Security Update for Windows XP (KB971468)
Security Update for Windows XP (KB971657)
Security Update for Windows XP (KB971961)
Security Update for Windows XP (KB972270)
Security Update for Windows XP (KB973507)
Security Update for Windows XP (KB973869)
Security Update for Windows XP (KB973904)
Security Update for Windows XP (KB974112)
Security Update for Windows XP (KB974318)
Security Update for Windows XP (KB974392)
Security Update for Windows XP (KB974571)
Security Update for Windows XP (KB975025)
Security Update for Windows XP (KB975560)
Security Update for Windows XP (KB975561)
Security Update for Windows XP (KB975562)
Security Update for Windows XP (KB975713)
Security Update for Windows XP (KB977816)
Security Update for Windows XP (KB977914)
Security Update for Windows XP (KB978037)
Security Update for Windows XP (KB978338)
Security Update for Windows XP (KB978542)
Security Update for Windows XP (KB978601)
Security Update for Windows XP (KB978706)
Security Update for Windows XP (KB979309)
Security Update for Windows XP (KB979482)
Security Update for Windows XP (KB979559)
Security Update for Windows XP (KB979683)
Security Update for Windows XP (KB980195)
Security Update for Windows XP (KB980218)
Security Update for Windows XP (KB980232)
Security Update for Windows XP (KB981350)
Security Update for Windows XP (KB982381)
SnagIt 5
Update for Windows XP (KB898461)
Update for Windows XP (KB955759)
Update for Windows XP (KB967715)
Update for Windows XP (KB973687)
Update for Windows XP (KB973815)
WebFldrs XP
Windows Installer 3.1 (KB893803)
Windows XP Service Pack 2
WinRAR archiver
==== Event Viewer Messages From Past Week ========
6/27/2010 11:04:23 PM, error: ipnathlp [32003] - The Network Address Translator (NAT) was unable to request an operation of the kernel-mode translation module. This may indicate misconfiguration, insufficient resources, or an internal error. The data is the error code.
6/25/2010 10:30:50 AM, error: Windows Update Agent [20] - Installation Failure: Windows failed to install the following update with error 0xd0000135: Update for Windows XP (KB981793).
6/25/2010 10:21:59 AM, error: Windows Update Agent [20] - Installation Failure: Windows failed to install the following update with error 0xf00b0004: Update for Windows XP (KB968389).
6/24/2010 6:21:58 PM, information: Windows File Protection [64005] - The protected system file rundll32.exe was not restored to its original, valid version because the Windows File Protection restoration process was cancelled by user interaction, user name is Dain Neuharth. The file version of the bad file is unknown.
6/24/2010 6:00:07 PM, error: Service Control Manager [7022] - The Avira AntiVir Guard service hung on starting.
6/24/2010 5:58:45 PM, error: W32Time [17] - Time Provider NtpClient: An error occurred during DNS lookup of the manually configured peer 'time.nist.gov,0x1'. NtpClient will try the DNS lookup again in 15 minutes. The error was: A socket operation was attempted to an unreachable host. (0x80072751)
6/24/2010 5:57:57 PM, error: ACPI [5] - AMLI: ACPI BIOS is attempting to write to an illegal IO port address (0x70), which lies in the 0x70 - 0x71 protected address range. This could lead to system instability. Please contact your system vendor for technical assistance.
6/24/2010 5:57:57 PM, error: ACPI [4] - AMLI: ACPI BIOS is attempting to read from an illegal IO port address (0x71), which lies in the 0x70 - 0x71 protected address range. This could lead to system instability. Please contact your system vendor for technical assistance.
6/24/2010 4:01:17 PM, error: Dhcp [1001] - Your computer was not assigned an address from the network (by the DHCP Server) for the Network Card with network address 001150BB7625. The following error occurred: The operation was canceled by the user. . Your computer will continue to try and obtain an address on its own from the network address (DHCP) server.
6/21/2010 10:30:49 AM, error: Service Control Manager [7000] - The Application Layer Gateway Service service failed to start due to the following error: The service did not respond to the start or control request in a timely fashion.
6/21/2010 10:30:34 AM, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the Application Layer Gateway Service service to connect.
==== End Of File ===========================
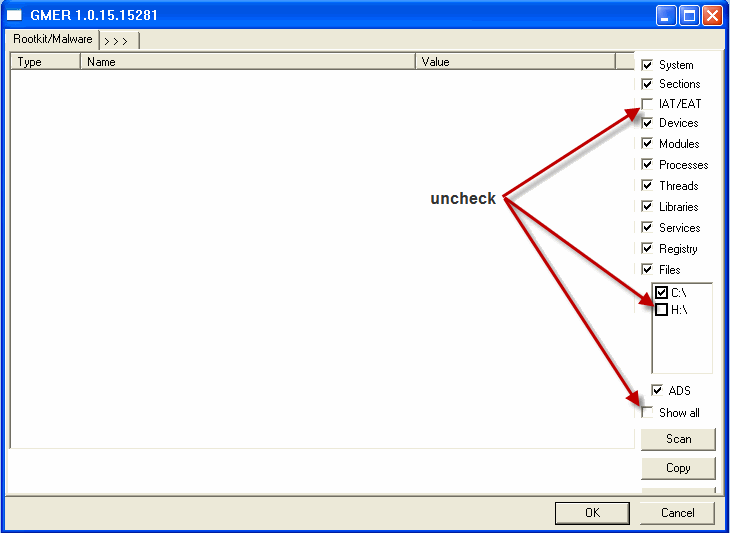
GMER 1.0.15.15281 -
http://www.gmer.net
Rootkit scan 2010-06-28 10:27:16
Windows 5.1.2600 Service Pack 2
Running: lt2upb8s.exe; Driver: C:\DOCUME~1\DAINNE~1\LOCALS~1\Temp\kxtdapog.sys
—- System - GMER 1.0.15 —-
SSDT FCB2571E ZwCreateKey
SSDT FCB25714 ZwCreateThread
SSDT FCB25723 ZwDeleteKey
SSDT FCB2572D ZwDeleteValueKey
SSDT FCB25732 ZwLoadKey
SSDT FCB25700 ZwOpenProcess
SSDT FCB25705 ZwOpenThread
SSDT FCB2573C ZwReplaceKey
SSDT FCB25737 ZwRestoreKey
SSDT FCB25728 ZwSetValueKey
SSDT FCB2570F ZwTerminateProcess
—- Devices - GMER 1.0.15 —-
AttachedDevice \FileSystem\Ntfs \Ntfs avgntmgr.sys (Avira AntiVir File Filter Driver Manager/Avira GmbH)
AttachedDevice \FileSystem\Fastfat \Fat avgntmgr.sys (Avira AntiVir File Filter Driver Manager/Avira GmbH)
—- EOF - GMER 1.0.15 —-
And you'll probably notice something not too smart I did. I'm not too smart when it comes to this kind of stuff.