This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

[Resolved] my internet explorer has disapeared off my desktop

41 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

hi catbyte, iv uninstalled all that antivirus and its immeadiatley made the machine loads faster and it doesnt stall on a page and think about letting me work on it!!! i guees it must have been all the antivirus working on it against each other !!! would you recomend using just the microsoft security essentials only and nothing else ?? and would you recomend i do the same on my laptop as well or leave it i think i just need to clean up my desktop now if thats ok whith you ?? you really are a STAR thanks so much for your help over these days regards phil c
If you are behind a secured router, then a third party firewall isn't absolutely necessary unless you want the added security:

Keep the Microsoft Security Essentials, malwarebytes AntiMalware and the Web of Trust, every once in a while visit the online scanners such as kaspersky or ESET, other than that, just practice safe surfing habits and you should be fine.
Too many security programs can have the opposite effect and really bog a system down, causing conflicts and crashes:

Do a defrag on the lap top after running Temp File Cleaner again:

then do the final clean up:

Follow these steps to uninstall Combofix

  • Click START then RUN
  • Now copy/paste Combofix /uninstall into the runbox and click OK. Note the space between the ..X and the /U, it needs to be there.

[external image: Posted Image]


NEXT

Now to remove the rest of the tools that we have used in fixing your machine:
  • Make sure you have an Internet Connection.
  • Download OTC to your desktop and run it
  • A list of tool components used in the Cleanup of malware will be downloaded.
  • If your Firewall or Real Time protection attempts to block OTC to reach the Internet, please allow the application to do so.
  • Click Yes to begin the Cleanup process and remove these components, including this application.
  • You will be asked to reboot the machine to finish the Cleanup process. If you are asked to reboot the machine choose Yes.

If any logs/tools remain on your desktop > right click and delete them.


NEXT


Below I have included a number of recommendations for how to protect your computer against malware infections.

  • It is good security practice to change your passwords to all your online accounts on a fairly regular basis, this is especially true after an infection. Refer to this Microsoft article
    Strong passwords: How to create and use them

    Then consider a password keeper, to keep all your passwords safe.

  • Keep Windows updated by regularly checking their website at :
    http://windowsupdate.microsoft.com/
    This will ensure your computer has always the latest security updates available installed on your computer.

  • Make Internet Explorer more secure
    • Click Start > Run
    • Type Inetcpl.cpl & click OK
    • Click on the Security tab
    • Click Reset all zones to default level
    • Make sure the Internet Zone is selected & Click Custom level
    • In the ActiveX section, set the first two options ("Download signed and unsigned ActiveX controls) to "Prompt", and ("Initialize and Script ActiveX controls not marked as safe") to "Disable".
    • Next Click OK, then Apply button and then OK to exit the Internet Properties page.

  • Download TFC to your desktop
    • Close any open windows.
    • Double click the TFC icon to run the program
    • TFC will close all open programs itself in order to run,
    • Click the Start button to begin the process.
    • Allow TFC to run uninterrupted.
    • The program should not take long to finish it's job
    • Once its finished it should automatically reboot your machine,
    • if it doesn't, manually reboot to ensure a complete clean
    It's normal after running TFC cleaner that the PC will be slower to boot the first time.


    WOT, Web of Trust, warns you about risky websites that try to scam visitors, deliver malware or send spam. Protect your computer against online threats by using WOT as your front-line layer of protection when browsing or searching in unfamiliar territory. WOT's color-coded icons show you ratings for 21 million websites, helping you avoid the dangerous sites:
    • Green to go
    • Yellow for caution
    • Red to stop
    WOT has an addon available for both Firefox, IE and chrome.

  • Keep a backup of your important files - Now, more than ever, it's especially important to protect your digital files and memories. This article is full of good information on alternatives for home backup solutions.

  • ERUNT (Emergency Recovery Utility NT) allows you to keep a complete backup of your registry and restore it when needed. The standard registry backup options that come with Windows back up most of the registry but not all of it. ERUNT however creates a complete backup set, including the Security hive and user related sections. ERUNT is easy to use and since it creates a full backup, there are no options or choices other than to select the location of the backup files. The backup set includes a small executable that will launch the registry restore if needed.

  • In light of your recent issue, I'm sure you'd like to avoid any future infections. Please take a look at these well written articles:
    Think Prevention.
    PC Safety and Security–What Do I Need?.


**Be very wary with any security software that is advertised in popups or in other ways. They are not only usually of no use, but often have malware in them.


If you have a third computer to clean go ahead and post logs from the DDS and GMER programs:

I'll give you the instructions again to save scrolling back through this thread:

Please download DDS from either of these links

LINK 1
LINK 2

and save it to your desktop.
  • Disable any script blocking protection
  • Double click dds.pif to run the tool.
  • When done, two DDS.txt's will open.
  • Save both reports to your desktop.
—————————————————
Please include the contents of the following in your next reply:

DDS.txt
Attach.txt.


NEXT


Download GMER Rootkit Scanner from here to your desktop. It will be a randomly named executable.
  • Double click the exe file.
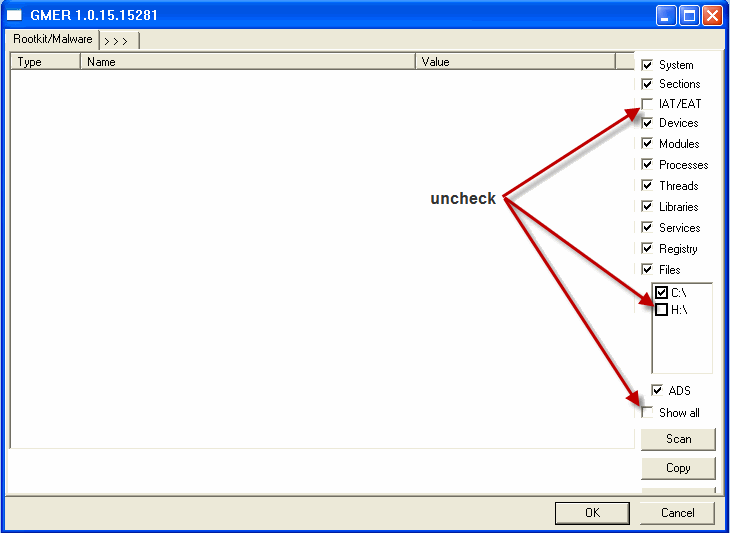
  • If it gives you a warning about rootkit activity and asks if you want to run scan…click on NO, then use the following settings for a more complete scan.


    [external image: Posted Image]
    Click the image to enlarge it


  • In the right panel, you will see several boxes that have been checked. Ensure the following are unchecked
    • IAT/EAT
    • Drives/Partition other than Systemdrive (typically C:\)
    • Show All (don't miss this one)
  • Then click the Scan button & wait for it to finish.
  • Once done click on the [Save..] button, and in the File name area, type in "Gmer.txt" or it will save as a .log file which cannot be uploaded to your post.
  • Save it where you can easily find it, such as your desktop, and attach it in reply.

**Caution**
Rootkit scans often produce false positives. Do NOT take any action on any "<— ROOKIT" entries
hi catbyte , my daughters computer is now running ok, before we move on to my wifes and our third machine , i thought id go back to my laptop which was the first machine you cured for me , i tried to uninstall avg using its own uninstall programme which was unsucseesful and then i tried remove programmes which was also unsuccessful,it comes up with this either time i try to remove Installer initialization failed due to the following error: Error: Initialization of the setup data file failed. Specified file was not found. ive even tried to reinstall but come up with same any ideas how i can erase it ? i also have adawaaare and superantispyware on this machine and i know you said its not good to have all that virus ware running and thought id put on the mcrosoft on its own regards phil c
Try the removal tool


http://www.avg.com/filedir/util/avg_arm_su…/avgremover.exe


If that doesn't work, try Revo Uninstaller:

Download and install the Revo Uninstaller
  • Double click the new Revo Uninstaller icon on your desktop to start the program
  • Scroll through the listed programs and Right Click on the program you wish to uninstall
  • From the pop out menu choose Uninstall
  • Click Yes to the confirmation dialogue
  • In the next window select the Advanced mode
  • Click Next to start uninstalling the program
  • Answer Yes to confirm the uninstall
  • When the program has completed the four steps, click Next to allow the program to search for leftovers
  • Once complete, click Next, then Finish
  • Repeat the above steps for any other programs you wish to remove.


As for security programs,

it's recommended to have ONE antivirus, one Firewall (if you choose to have one) and 1-2 antispyware programs


Keep Malwarebytes Antimalware and choose another one that you like.
hi cat byte,
the revo remval tool worked great i am now running only the microsoft windows anti virus suite as recommended.

here are the dds logs from my wifes computer one pasted and one attached, i shall now do the gmer one and post it to you asap.
i have already taken off the avg and all the others off here as well .
thank you phil c


DDS (Ver_10-03-17.01) - NTFSx86
Run by [removed] at 13:52:50.95 on 30/05/2010
Internet Explorer: 8.0.6001.18702
Microsoft Windows XP Professional 5.1.2600.3.1252.1.1033.18.1015.568 [GMT 1:00]


============== Running Processes ===============

C:\WINDOWS\system32\svchost -k DcomLaunch
svchost.exe
C:\WINDOWS\System32\svchost.exe -k netsvcs
C:\WINDOWS\system32\svchost.exe -k WudfServiceGroup
svchost.exe
svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\WINDOWS\system32\acs.exe
svchost.exe
C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe
C:\Program Files\Bonjour\mDNSResponder.exe
C:\WINDOWS\system32\cisvc.exe
C:\Program Files\Windows Live\Family Safety\fsssvc.exe
C:\WINDOWS\Explorer.EXE
C:\WINDOWS\system32\svchost.exe -k hpdevmgmt
C:\Program Files\Java\jre6\bin\jqs.exe
C:\WINDOWS\System32\svchost.exe -k HPZ12
C:\Program Files\Polar\Daemon\polard.exe
C:\Program Files\Microsoft\Search Enhancement Pack\SeaPort\SeaPort.exe
C:\WINDOWS\system32\svchost.exe -k imgsvc
C:\Program Files\Analog Devices\Core\smax4pnp.exe
C:\WINDOWS\system32\00THotkey.exe
C:\Program Files\iTunes\iTunesHelper.exe
C:\WINDOWS\system32\ctfmon.exe
C:\Program Files\iPod\bin\iPodService.exe
C:\WINDOWS\system32\wscntfy.exe
C:\WINDOWS\System32\svchost.exe -k HTTPFilter
C:\Program Files\Internet Explorer\IEXPLORE.EXE
C:\Program Files\Windows Live\Toolbar\wltuser.exe
C:\Program Files\Internet Explorer\IEXPLORE.EXE
C:\Documents and Settings\compton\Desktop\dds.com

============== Pseudo HJT Report ===============

uStart Page = hxxp://uk.yahoo.com/
uSearchMigratedDefaultURL = hxxp://search.yahoo.com/search?p={searchTerms}&ei=utf-8&fr=b1ie7
uInternet Settings,ProxyOverride = *.local
mSearchAssistant = hxxp://www.google.com/ie
uURLSearchHooks: Vuze Remote Toolbar: {ba14329e-9550-4989-b3f2-9732e92d17cc} - c:\program files\vuze_remote\tbVuze.dll
BHO: Adobe PDF Link Helper: {18df081c-e8ad-4283-a596-fa578c2ebdc3} - c:\program files\common files\adobe\acrobat\activex\AcroIEHelperShim.dll
BHO: Windows Live Family Safety Browser Helper Class: {4f3ed5cd-0726-42a9-87f5-d13f3d2976ac} - c:\program files\windows live\family safety\fssbho.dll
BHO: {5C255C8A-E604-49b4-9D64-90988571CECB} - No File
BHO: Java™ Plug-In SSV Helper: {761497bb-d6f0-462c-b6eb-d4daf1d92d43} - c:\program files\java\jre6\bin\ssv.dll
BHO: Windows Live Sign-in Helper: {9030d464-4c02-4abf-8ecc-5164760863c6} - c:\program files\common files\microsoft shared\windows live\WindowsLiveLogin.dll
BHO: Google Toolbar Helper: {aa58ed58-01dd-4d91-8333-cf10577473f7} - c:\program files\google\googletoolbar1.dll
BHO: Vuze Remote Toolbar: {ba14329e-9550-4989-b3f2-9732e92d17cc} - c:\program files\vuze_remote\tbVuze.dll
BHO: Java™ Plug-In 2 SSV Helper: {dbc80044-a445-435b-bc74-9c25c1c588a9} - c:\program files\java\jre6\bin\jp2ssv.dll
BHO: Windows Live Toolbar Helper: {e15a8dc0-8516-42a1-81ea-dc94ec1acf10} - c:\program files\windows live\toolbar\wltcore.dll
BHO: JQSIEStartDetectorImpl Class: {e7e6f031-17ce-4c07-bc86-eabfe594f69c} - c:\program files\java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll
TB: &Google: {2318c2b1-4965-11d4-9b18-009027a5cd4f} - c:\program files\google\googletoolbar1.dll
TB: &Windows Live Toolbar: {21fa44ef-376d-4d53-9b0f-8a89d3229068} - c:\program files\windows live\toolbar\wltcore.dll
TB: Vuze Remote Toolbar: {ba14329e-9550-4989-b3f2-9732e92d17cc} - c:\program files\vuze_remote\tbVuze.dll
TB: {A057A204-BACC-4D26-9990-79A187E2698E} - No File
TB: {BDAD1DAD-C946-4A17-ADC1-64B5B4FF55D0} - No File
uRun: [CTFMON.EXE] c:\windows\system32\ctfmon.exe
mRun: [SoundMAX] "c:\program files\analog devices\soundmax\smax4.exe" /tray
mRun: [SoundMAXPnP] c:\program files\analog devices\core\smax4pnp.exe
mRun: [00THotkey] c:\windows\system32\00THotkey.exe
mRun: [000StTHK] 000StTHK.exe
mRun: [QuickTime Task] "c:\program files\quicktime\qttask.exe" -atboottime
mRun: [iTunesHelper] "c:\program files\itunes\iTunesHelper.exe"
dRun: [CTFMON.EXE] c:\windows\system32\CTFMON.EXE
IE: &Google Search - c:\program files\google\GoogleToolbar1.dll/cmsearch.html
IE: Add to Windows &Live Favorites - http://favorites.live.com/quickadd.aspx
IE: Backward &Links - c:\program files\google\GoogleToolbar1.dll/cmbacklinks.html
IE: Cac&hed Snapshot of Page - c:\program files\google\GoogleToolbar1.dll/cmcache.html
IE: E&xport to Microsoft Excel - c:\progra~1\micros~2\office10\EXCEL.EXE/3000
IE: Si&milar Pages - c:\program files\google\GoogleToolbar1.dll/cmsimilar.html
IE: Translate into English - c:\program files\google\GoogleToolbar1.dll/cmtrans.html
IE: {e2e2dd38-d088-4134-82b7-f2ba38496583} - %windir%\Network Diagnostic\xpnetdiag.exe
IE: {FB5F1910-F110-11d2-BB9E-00C04F795683} - c:\program files\messenger\msmsgs.exe
IE: {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - {5F7B1267-94A9-47F5-98DB-E99415F33AEC} - c:\program files\windows live\writer\WriterBrowserExtension.dll
DPF: {0CCA191D-13A6-4E29-B746-314DEE697D83} - hxxp://upload.facebook.com/controls/2008.10.10_v5.5.8/FacebookPhotoUploader5.cab
DPF: {138E6DC9-722B-4F4B-B09D-95D191869696} - hxxp://www.bebo.com/files/BeboUploader.5.1.4.cab
DPF: {166B1BCA-3F9C-11CF-8075-444553540000} - hxxp://download.macromedia.com/pub/shockwave/cabs/director/sw.cab
DPF: {680285A8-96D3-43DA-9D3D-51DD987D0B77} - hxxp://www.nero.com/doc/NeroVersionCheckerControl.cab
DPF: {8100D56A-5661-482C-BEE8-AFECE305D968} - hxxp://upload.facebook.com/controls/2009.07.28_v5.5.8.1/FacebookPhotoUploader55.cab
DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_11-windows-i586.cab
DPF: {8FFBE65D-2C9C-4669-84BD-5829DC0B603C} - hxxp://fpdownload.macromedia.com/get/flashplayer/current/polarbear/ultrashim.cab
DPF: {C3F79A2B-B9B4-4A66-B012-3EE46475B072} - hxxp://messenger.zone.msn.com/binary/MessengerStatsPAClient.cab56907.cab
DPF: {CAFEEFAC-0015-0000-0006-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.5.0/jinstall-1_5_0_06-windows-i586.cab
DPF: {CAFEEFAC-0016-0000-0011-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_11-windows-i586.cab
DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_11-windows-i586.cab
DPF: {CF40ACC5-E1BB-4AFF-AC72-04C2F616BCA7} - hxxp://wwwimages.adobe.com/www.adobe.com/products/acrobat/nos/gp.cab
DPF: {D27CDB6E-AE6D-11CF-96B8-444553540000} - hxxp://fpdownload2.macromedia.com/get/shockwave/cabs/flash/swflash.cab
DPF: {DF780F87-FF2B-4DF8-92D0-73DB16A1543A} - hxxp://www.shockwave.com/content/bejeweled2/sis/popcaploader_v10.cab
DPF: {F5A7706B-B9C0-4C89-A715-7A0C6B05DD48} - hxxp://messenger.zone.msn.com/binary/MineSweeper.cab56986.cab
Notify: igfxcui - igfxdev.dll
SSODL: WPDShServiceObj - {AAA288BA-9A4C-45B0-95D7-94D524869DB5} - c:\windows\system32\WPDShServiceObj.dll

============= SERVICES / DRIVERS ===============

R2 fssfltr;FssFltr;c:\windows\system32\drivers\fssfltr_tdi.sys [2008-12-21 55136]
R2 fsssvc;Windows Live Family Safety;c:\program files\windows live\family safety\fsssvc.exe [2009-2-6 533360]
R2 Polar Daemon;Polar Daemon;c:\program files\polar\daemon\polard.exe [2009-8-25 163840]
S2 ipfw;ipfw_helper; [x]
S3 Boonty Games;Boonty Games;c:\program files\common files\boonty shared\service\Boonty.exe [2010-1-10 69120]
S3 ip_fw;ipfw kernel-mode driver;\??\c:\windows\system32\drivers\ip_fw.sys –> c:\windows\system32\drivers\ip_fw.sys [?]
S3 USBFVNETR;Belkin 11Mbps Wireless USB Network Adapter;c:\windows\system32\drivers\vnetusbr.sys [2009-7-7 69632]

=============== Created Last 30 ================

2010-05-06 03:29:49 2621558 -c–a-w- C:\az.log.bak
2010-05-02 13:39:37 37 -c–a-w- c:\windows\wwwbatch.ini

==================== Find3M ====================

2010-03-10 06:15:52 420352 -c–a-w- c:\windows\system32\vbscript.dll
2008-12-25 20:54:27 32768 -csha-w- c:\windows\system32\config\systemprofile\local settings\history\history.ie5\mshist012008120820081215\index.dat
2008-12-25 20:54:27 32768 -csha-w- c:\windows\system32\config\systemprofile\local settings\history\history.ie5\mshist012008122520081226\index.dat
2009-05-16 08:23:01 16384 -csha-w- c:\windows\temp\cookies\index.dat
2009-05-16 08:23:01 16384 -csha-w- c:\windows\temp\history\history.ie5\index.dat

============= FINISH: 13:53:18.07 ===============

Attachments:

hi catbyte , sorry , ran the gmer scan and it completed , but when i tried to save it froze my machine up and i had to make a hard restart.!! regards phil c
Hi,

Try this scanner instead


Please download this file, and save it to your Desktop. Once you have downloaded it, save and close all other programs and run it by double-clicking on the file named "RootRepeal.exe".

Once the main window shows up, please click on the "Report" button on the bottom of the window. Next, please click the "Scan" button.

Another window will pop up asking you to select what to include in the scan. Please uncheck everything except for the "Stealth Code" checkbox, and then click OK.

Once the program has finished scanning, the results will appear. Click on the "Save Report" button, and save the report to your desktop.

Finally, please open this report with Notepad, and post it here.
hi catbyet here is the rootrepeal log ROOTREPEAL © AD, 2007-2010 ================================================== Report Save Time: 2010/05/30 21:14 Program Version: Version 2.0.0.0 Windows Version: Windows XP SP3 ================================================== STEALTH CODE ——————-
Hi,

Please do the following:

(by the way, make sure you don't connect to the internet unless downloaded tools I request, with no antivirus installed. - Install Microsoft security Essentials once we are done using combofix)


Download ComboFix from one of the following locations:
Link 1
Link 2

VERY IMPORTANT !!! Save ComboFix.exe to your Desktop

* IMPORTANT - Disable your AntiVirus and AntiSpyware applications, usually via a right click on the System Tray icon. They may otherwise interfere with our tools. If you have difficulty properly disabling your protective programs, refer to this link here
  • Double click on ComboFix.exe & follow the prompts.
As part of it's process, ComboFix will check to see if the Microsoft Windows Recovery Console is installed. With malware infections being as they are today, it's strongly recommended to have this pre-installed on your machine before doing any malware removal. It will allow you to boot up into a special recovery/repair mode that will allow us to more easily help you should your computer have a problem after an attempted removal of malware.

  • Follow the prompts to allow ComboFix to download and install the Microsoft Windows Recovery Console, and when prompted, agree to the End-User License Agreement to install the Microsoft Windows Recovery Console.
**Please note: If the Microsoft Windows Recovery Console is already installed, ComboFix will continue it's malware removal procedures.

[external image: Posted Image]

  • Once the Microsoft Windows Recovery Console is installed using ComboFix, you should see the following message:

[external image: Posted Image]

  • Click on Yes, to continue scanning for malware.
When finished, it shall produce a log for you. Please include the C:\ComboFix.txt in your next reply.
Notes:
1. Do not mouse-click Combofix's window while it is running. That may cause it to stall.
2. Do not "re-run" Combofix. If you have a problem, reply back for further instructions.
Hi Catbyte,
here is the combofix log


ComboFix 10-05-29.05 - compton 30/05/2010 21:46:06.1.2 - x86
Microsoft Windows XP Professional 5.1.2600.3.1252.1.1033.18.1015.598 [GMT 1:00]
Running from: c:\documents and settings\[removed]\Desktop\ComboFix.exe
.

((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.

c:\documents and settings\compton\Application Data\.#
c:\documents and settings\compton\Application Data\.#\MBX@270@384180.###
c:\documents and settings\compton\Application Data\.#\MBX@270@3841B0.###
c:\documents and settings\compton\Application Data\.#\MBX@270@3841E0.###
c:\documents and settings\compton\Recent\Thumbs.db
c:\windows\Downloaded Program Files\popcaploader.dll
c:\windows\Downloaded Program Files\popcaploader.inf
c:\windows\system32\NWlxXIvx.exe.a_a
c:\windows\Tasks\{783AF354-B514-42d6-970E-3E8BF0A5279C}.job

.
((((((((((((((((((((((((((((((((((((((( Drivers/Services )))))))))))))))))))))))))))))))))))))))))))))))))
.

——-\Legacy_BOONTY_GAMES
——-\Legacy_IPFW
——-\Service_Boonty Games
——-\Service_ip_fw
——-\Service_ipfw


((((((((((((((((((((((((( Files Created from 2010-04-28 to 2010-05-30 )))))))))))))))))))))))))))))))
.

2010-05-30 13:03 . 2010-05-30 13:03 ——– dc—-w- c:\program files\VS Revo Group

.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2010-05-27 15:41 . 2008-12-20 10:48 ——– dc—-w- c:\documents and settings\compton\Application Data\Azureus
2010-05-26 14:53 . 2008-12-11 15:50 ——– dc—-w- c:\program files\Azureus
2010-04-26 16:09 . 2010-04-23 20:36 ——– dc—-w- c:\program files\Ask.com
2010-04-26 16:09 . 2010-04-26 16:09 ——– dc—-w- c:\program files\Analog Devices
2010-04-26 16:09 . 2010-04-23 21:03 ——– dc—-w- c:\program files\Analog Devices(2)
2010-04-26 15:53 . 2008-12-11 12:17 ——– dc—-w- c:\program files\Toshiba
2010-04-26 15:53 . 2008-12-11 10:31 ——– dc-h–w- c:\program files\InstallShield Installation Information
2010-04-22 17:41 . 2009-12-27 18:02 ——– dc—-w- c:\program files\Polar
2010-04-18 19:32 . 2009-12-31 17:59 ——– dc—-w- c:\documents and settings\compton\Application Data\Amazon
2010-04-18 05:50 . 2010-01-06 13:45 ——– dc—-w- c:\documents and settings\All Users\Application Data\MumboJumbo
2010-04-13 20:07 . 2010-04-13 09:04 ——– dc—-w- c:\program files\Free DVD Creator
2010-04-13 17:35 . 2010-04-13 17:35 ——– dc—-w- c:\documents and settings\All Users\Application Data\Ahead
2010-04-13 09:07 . 2010-04-13 09:07 ——– dc—-w- c:\program files\ffdshow
2010-04-12 16:10 . 2010-04-12 16:10 ——– dc—-w- c:\documents and settings\compton\Application Data\SmartDVDCreatorPro
2010-04-12 14:50 . 2009-01-18 00:35 ——– dc—-w- c:\documents and settings\compton\Application Data\dvdcss
2010-04-10 18:04 . 2008-12-11 15:41 ——– dc—-w- c:\program files\Google
2010-04-10 17:52 . 2010-04-10 17:52 7282688 -c–a-w- c:\documents and settings\compton\Application Data\Azureus\plugins\vuzexcode\ffmpeg.exe
2010-04-10 17:52 . 2010-04-10 17:52 4141117 -c–a-w- c:\documents and settings\compton\Application Data\Azureus\plugins\vuzexcode\mediainfo.exe
2010-04-10 17:23 . 2010-04-10 17:23 ——– dc—-w- c:\program files\Conduit
2010-04-10 17:23 . 2010-04-10 17:23 ——– dc—-w- c:\program files\Vuze_Remote
2010-04-09 20:10 . 2010-04-09 16:57 57344 -c–a-w- c:\documents and settings\All Users\Application Data\DivX\RunAsUser\RUNASUSERPROCESS.dll
2010-04-09 19:47 . 2010-04-09 16:53 ——– dc—-w- c:\documents and settings\All Users\Application Data\DivX
2010-04-09 19:45 . 2010-04-09 19:45 144696 -c–a-w- c:\documents and settings\All Users\Application Data\DivX\RunAsUser\RUNASUSERPROCESS.exe
2010-04-09 18:14 . 2010-04-09 18:14 ——– dc—-w- c:\documents and settings\compton\Application Data\vlc
2010-04-09 18:13 . 2008-12-11 15:35 ——– dc—-w- c:\program files\VideoLAN
2010-04-09 17:49 . 2010-04-09 16:56 ——– dc—-w- c:\documents and settings\compton\Application Data\DivX
2010-04-09 17:21 . 2010-04-09 16:57 1180952 -c–a-w- c:\documents and settings\All Users\Application Data\DivX\Setup\DivXSetup.exe
2010-03-10 06:15 . 2004-08-04 12:00 420352 -c–a-w- c:\windows\system32\vbscript.dll
.

((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4

[HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\URLSearchHooks]
"{ba14329e-9550-4989-b3f2-9732e92d17cc}"= "c:\program files\Vuze_Remote\tbVuze.dll" [2010-03-17 2355224]

[HKEY_CLASSES_ROOT\clsid\{ba14329e-9550-4989-b3f2-9732e92d17cc}]

[HKEY_LOCAL_MACHINE\~\Browser Helper Objects\{ba14329e-9550-4989-b3f2-9732e92d17cc}]
2010-03-17 14:45 2355224 -c–a-w- c:\program files\Vuze_Remote\tbVuze.dll

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Internet Explorer\Toolbar]
"{ba14329e-9550-4989-b3f2-9732e92d17cc}"= "c:\program files\Vuze_Remote\tbVuze.dll" [2010-03-17 2355224]

[HKEY_CLASSES_ROOT\clsid\{ba14329e-9550-4989-b3f2-9732e92d17cc}]

[HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Toolbar\Webbrowser]
"{BA14329E-9550-4989-B3F2-9732E92D17CC}"= "c:\program files\Vuze_Remote\tbVuze.dll" [2010-03-17 2355224]

[HKEY_CLASSES_ROOT\clsid\{ba14329e-9550-4989-b3f2-9732e92d17cc}]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SoundMAXPnP"="c:\program files\Analog Devices\Core\smax4pnp.exe" [2005-05-20 925696]
"00THotkey"="c:\windows\system32\00THotkey.exe" [2006-07-05 258048]
"000StTHK"="000StTHK.exe" [2001-06-23 24576]
"QuickTime Task"="c:\program files\QuickTime\qttask.exe" [2009-11-10 417792]
"iTunesHelper"="c:\program files\iTunes\iTunesHelper.exe" [2010-01-22 141608]

[HKEY_USERS\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\Run]
"CTFMON.EXE"="c:\windows\system32\CTFMON.EXE" [2008-04-14 15360]

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"c:\\Program Files\\Messenger\\msmsgs.exe"=
"c:\\Program Files\\Bonjour\\mDNSResponder.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\msnmsgr.exe"=
"c:\\Program Files\\Windows Live\\Sync\\WindowsLiveSync.exe"=
"c:\\WINDOWS\\system32\\dpvsetup.exe"=
"c:\\Program Files\\iTunes\\iTunes.exe"=
"c:\\Program Files\\Azureus\\Azureus.exe"=

R2 Polar Daemon;Polar Daemon;c:\program files\Polar\Daemon\polard.exe [25/08/2009 11:03 163840]
S3 USBFVNETR;Belkin 11Mbps Wireless USB Network Adapter;c:\windows\system32\drivers\vnetusbr.sys [07/07/2009 21:32 69632]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost]
HPZ12 REG_MULTI_SZ Pml Driver HPZ12 Net Driver HPZ12
hpdevmgmt REG_MULTI_SZ hpqcxs08 hpqddsvc
.
Contents of the 'Scheduled Tasks' folder

2010-05-17 c:\windows\Tasks\AppleSoftwareUpdate.job
- c:\program files\Apple Software Update\SoftwareUpdate.exe [2008-07-30 12:34]

2010-05-30 c:\windows\Tasks\RegCure Program Check.job
- c:\program files\RegCure\RegCure.exe [2007-10-16 09:20]

2010-05-06 c:\windows\Tasks\RegCure.job
- c:\program files\RegCure\RegCure.exe [2007-10-16 09:20]
.
.
——- Supplementary Scan ——-
.
uStart Page = hxxp://uk.yahoo.com/
uSearchMigratedDefaultURL = hxxp://search.yahoo.com/search?p={searchTerms}&ei=utf-8&fr=b1ie7
uInternet Settings,ProxyOverride = *.local
IE: &Google Search - c:\program files\Google\GoogleToolbar1.dll/cmsearch.html
IE: Add to Windows &Live Favorites - http://favorites.live.com/quickadd.aspx
IE: Backward &Links - c:\program files\Google\GoogleToolbar1.dll/cmbacklinks.html
IE: Cac&hed Snapshot of Page - c:\program files\Google\GoogleToolbar1.dll/cmcache.html
IE: E&xport to Microsoft Excel - c:\progra~1\MICROS~2\Office10\EXCEL.EXE/3000
IE: Si&milar Pages - c:\program files\Google\GoogleToolbar1.dll/cmsimilar.html
IE: Translate into English - c:\program files\Google\GoogleToolbar1.dll/cmtrans.html
.
- - - - ORPHANS REMOVED - - - -

AddRemove-Uninstall_is1 - c:\program files\Common Files\DVDVideoSoft\unins000.exe


**************************************************************************

catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net
Rootkit scan 2010-05-30 21:53
Windows 5.1.2600 Service Pack 3 NTFS

scanning hidden processes …

scanning hidden autostart entries …

scanning hidden files …


c:\windows\TEMP\SEP4.tmp 0 bytes

scan completed successfully
hidden files: 1

**************************************************************************
.
——————— DLLs Loaded Under Running Processes ———————

- - - - - - - > 'explorer.exe'(2140)
c:\windows\system32\WININET.dll
c:\windows\system32\ieframe.dll
c:\windows\system32\webcheck.dll
c:\windows\system32\WPDShServiceObj.dll
c:\windows\system32\PortableDeviceTypes.dll
c:\windows\system32\PortableDeviceApi.dll
.
———————— Other Running Processes ————————
.
c:\windows\system32\acs.exe
c:\program files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe
c:\program files\Bonjour\mDNSResponder.exe
c:\program files\Windows Live\Family Safety\fsssvc.exe
c:\program files\Java\jre6\bin\jqs.exe
c:\program files\Microsoft\Search Enhancement Pack\SeaPort\SeaPort.exe
c:\windows\system32\wscntfy.exe
c:\program files\iPod\bin\iPodService.exe
.
**************************************************************************
.
Completion time: 2010-05-30 21:57:41 - machine was rebooted
ComboFix-quarantined-files.txt 2010-05-30 20:57

Pre-Run: 15,665,864,704 bytes free
Post-Run: 16,006,635,520 bytes free

WindowsXP-KB310994-SP2-Pro-BootDisk-ENU.exe
[boot loader]
timeout=2
default=multi(0)disk(0)rdisk(0)partition(1)\WINDOWS
[operating systems]
c:\cmdcons\BOOTSECT.DAT="Microsoft Windows Recovery Console" /cmdcons
multi(0)disk(0)rdisk(0)partition(1)\WINDOWS="Microsoft Windows XP Professional" /noexecute=optin /fastdetect

- - End Of File - - 1FCDCA8CC1F80CC4331616DEC4219F6D
Hi,

Please do the following:

Download TFC to your desktop
  • Close any open windows.
  • Double click the TFC icon to run the program
  • TFC will close all open programs itself in order to run,
  • Click the Start button to begin the process.
  • Allow TFC to run uninterrupted.
  • The program should not take long to finish it's job
  • Once its finished it should automatically reboot your machine,
  • if it doesn't, manually reboot to ensure a complete clean
It's normal after running TFC cleaner that the PC will be slower to boot the first time.


NEXT


Please download Malwarebytes' Anti-Malware
  • Double Click mbam-setup.exe to install the application.
  • Make sure a checkmark is placed next to Update Malwarebytes' Anti-Malware and Launch Malwarebytes' Anti-Malware, then click Finish.
  • If an update is found, it will download and install the latest version.
  • Once the program has loaded, select "Perform Quick Scan", then click Scan.
  • The scan may take some time to finish, so please be patient.
  • When the scan is complete, click OK, then Show Results to view the results.
  • Make sure that everything is checked, and click Remove Selected. <– very important
  • When disinfection is completed, a log will open in Notepad and you may be prompted to Restart. (See Extra Note)
  • The log is automatically saved by MBAM and can be viewed by clicking the Logs tab in MBAM.
  • Copy&Paste the entire report in your next reply.

Extra Note:If MBAM encounters a file that is difficult to remove, you will be presented with 1 of 2 prompts, click OK to either and let MBAM proceed with the disinfection process, if asked to restart the computer, please do so immediately.


NEXT


Run an on-line scan with Kaspersky

Using Internet Explorer or Firefox, visit Kaspersky On-line Scanner

1. Click Accept, when prompted to download and install the program files and database of malware definitions.
2. To optimize scanning time and produce a more sensible report for review:
  • Close any open programs
  • Turn off the real time scanner of any existing antivirus program while performing the online scan
3. Click Run at the Security prompt.
The program will then begin downloading and installing and will also update the database.
Please be patient as this can take several minutes.
  • Once the update is complete, click on My Computer under the green Scan bar to the left to start the scan.
  • Once the scan is complete, it will display if your system has been infected. It does not provide an option to clean/disinfect. We only require a report from it.
  • Do NOT be alarmed by what you see in the report. Many of the finds have likely been quarantined.
  • Click View scan report at the bottom.

    [external image: Posted Image]
  • Click the Save as Text button to save the file to your desktop so that you may post it in your next reply
Hi Catbyte, this is the mbam log as req Malwarebytes' Anti-Malware 1.46 www.malwarebytes.org Database version: 4157 Windows 5.1.2600 Service Pack 3 Internet Explorer 8.0.6001.18702 30/05/2010 23:17:33 mbam-log-2010-05-30 (23-17-33).txt Scan type: Quick scan Objects scanned: 119836 Time elapsed: 5 minute(s), 42 second(s) Memory Processes Infected: 0 Memory Modules Infected: 0 Registry Keys Infected: 2 Registry Values Infected: 0 Registry Data Items Infected: 0 Folders Infected: 0 Files Infected: 0 Memory Processes Infected: (No malicious items detected) Memory Modules Infected: (No malicious items detected) Registry Keys Infected: HKEY_CLASSES_ROOT\popcaploader.popcaploaderctrl2 (Adware.PopCap) -> Quarantined and deleted successfully. HKEY_CLASSES_ROOT\popcaploader.popcaploaderctrl2.1 (Adware.PopCap) -> Quarantined and deleted successfully. Registry Values Infected: (No malicious items detected) Registry Data Items Infected: (No malicious items detected) Folders Infected: (No malicious items detected) Files Infected: (No malicious items detected) i shall now do the kaspersky lo regards phil c
hi catbyte, here is the kaspersky log KASPERSKY ONLINE SCANNER 7.0: scan report
KASPERSKY ONLINE SCANNER 7.0: scan report
Monday, May 31, 2010
Operating system: Microsoft Windows XP Professional Service Pack 3 (build 2600)
Kaspersky Online Scanner version: 7.0.26.13
Last database update: Sunday, May 30, 2010 18:00:32
Records in database: 4193466
Scan settings
scan using the following database extended
Scan archives yes
Scan e-mail databases yes
Scan area My Computer
C:\
D:\
Scan statistics
Objects scanned 64079
Threats found 0
Infected objects found 0
Suspicious objects found 0
Scan duration 02:13:50

No threats found. Scanned area is clean.
Selected area has been scanned.
Hi,

Please do the following:

Visit ADOBEand download the latest version of Acrobat Reader (version 9.3)
Having the latest updates ensures there are no security vulnerabilities in your system


NEXT


[external image: Posted Image]
Your Java is out of date. Older versions have vulnerabilities that malware can use to infect your system. Please follow these steps to remove older version Java components and update.
  • Download the latest version of Java Runtime Environment (JRE) 20 and save it to your desktop.
  • Scroll down to where it says JDK 6 Update 20 (JDK or JRE)
  • Click the Download JRE button to the right
  • Select the Windows platform from the dropdown menu.
  • Read the License Agreement and then check the box that says: "I agree to the Java SE Runtime Environment 6u20 with JavaFX 1 License Agreement". Click on Continue.The page will refresh.
  • Click on the link to download Windows Offline Installation and save the file to your desktop.
  • Close any programs you may have running - especially your web browser.
  • Go to Start > Control Panel, double-click on Add or Remove Programs and remove all older versions of Java.
  • Check (highlight) any item with Java Runtime Environment (JRE or J2SE or Java™ 6) in the name.
  • Click the Remove or Change/Remove button.
  • Repeat as many times as necessary to remove each Java versions.
  • Reboot your computer once all Java components are removed.
  • Then from your desktop double-click on jre-6u20-windows-i586-p.exe to install the newest version.
  • After the install is complete, go into the Control Panel (using Classic View) and double-click the Java Icon. (looks like a coffee cup)
    • On the General tab, under Temporary Internet Files, click the Settings button.
    • Next, click on the Delete Files button
    • There are two options in the window to clear the cache - Leave BOTH CheckedApplications and Applets
      Trace and Log Files
  • Click OK on Delete Temporary Files Window
    Note: This deletes ALL the Downloaded Applications and Applets from the CACHE.
  • Click OK to leave the Temporary Files Window
  • Click OK to leave the Java Control Panel.


NEXT


P2P - I see you have P2P software Vuse installed on your machine. We are not here to pass judgment on file-sharing as a concept. However, we will warn you that engaging in this activity and having this kind of software installed on your machine will always make you more susceptible to re-infections. It likely contributed to your current situation. This page will give you further information.
Please note: Even if you are using a "safe" P2P program, it is only the program that is safe. You will be sharing files from uncertified sources, and these are often infected. The bad guys use P2P filesharing as a major conduit to spread their wares.
Please see this topic for more information:
Perils of P2P File Sharing.
I would strongly recommend that you uninstall this now. You can do so via Control Panel >> Add or Remove Programs.

NEXT


Install Microsoft Security Essentials

Run a scan.


Let me know how the computer is running now, if all is good, we can do the final tool clean up.
hi catbyte , ok thats all done and yes it feels like its running good, !! thank you , time to clean up i think regards phil c

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI