This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

[Resolved] my internet explorer has disapeared off my desktop

41 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

dont know if this is a virus prob or just config my internet explorer 7 has disapeared of my desktop and i cant find it in programmes, ive tried downloading it again and it goes through the install process but then nothing happens, ive tried doing an up date off windows update site and i keep getting error 0x8007043B and when i play video off some sites it wont run saying sometimes something about addons being disabled or another one is a message about windows management instrumentation ???? i m wondering if its a virus or have i got some muddled software im running windows xp sp 3, duo core,t7600 intel 2.33ghz 3gb ram and a new 512 ati gfx card , ive just install the ati card my nvidia one gave up on me . the only two probs ive experienced are the explorer not working and windows up dater keeps coming up with this error code. if you think you can help me id really appreciate it thanks very much phil c
Hi,

Please do the following:

Please download DDS from either of these links

LINK 1
LINK 2

and save it to your desktop.
  • Disable any script blocking protection
  • Double click dds.pif to run the tool.
  • When done, two DDS.txt's will open.
  • Save both reports to your desktop.
—————————————————
Please include the contents of the following in your next reply:

DDS.txt
Attach.txt.


NEXT


Download GMER Rootkit Scanner from here to your desktop. It will be a randomly named executable.
  • Double click the exe file.
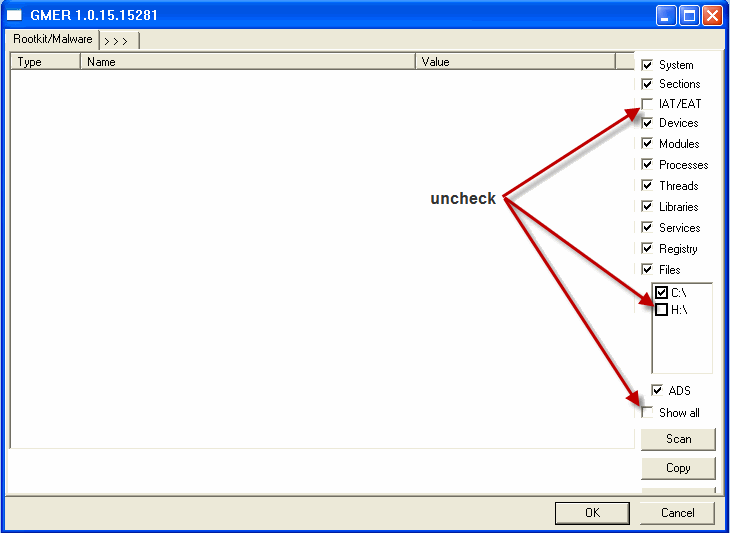
  • If it gives you a warning about rootkit activity and asks if you want to run scan…click on NO, then use the following settings for a more complete scan.


    [external image: Posted Image]
    Click the image to enlarge it


  • In the right panel, you will see several boxes that have been checked. Ensure the following are unchecked
    • IAT/EAT
    • Drives/Partition other than Systemdrive (typically C:\)
    • Show All (don't miss this one)
  • Then click the Scan button & wait for it to finish.
  • Once done click on the [Save..] button, and in the File name area, type in "Gmer.txt" or it will save as a .log file which cannot be uploaded to your post.
  • Save it where you can easily find it, such as your desktop, and attach it in reply.

**Caution**
Rootkit scans often produce false positives. Do NOT take any action on any "<— ROOKIT" entries
Hi catbyte, thank you very much for working on this problem with me.i shall do only as instructed by yourslf and no more. this is one of the dds logs copied and pasted . DDS (Ver_10-03-17.01) - NTFSx86 Run by [removed] at 11:12:16.28 on 23/05/2010 Internet Explorer: 7.0.5730.13 Microsoft Windows XP Professional 5.1.2600.3.1252.44.1033.18.3070.2371 [GMT 1:00] AV: AVG Anti-Virus Free *On-access scanning enabled* (Updated) {17DDD097-36FF-435F-9E1B-52D74245D6BF} ============== Running Processes =============== C:\WINDOWS\system32\Ati2evxx.exe C:\WINDOWS\system32\svchost -k DcomLaunch svchost.exe C:\WINDOWS\System32\svchost.exe -k netsvcs C:\WINDOWS\system32\svchost.exe -k WudfServiceGroup svchost.exe svchost.exe C:\WINDOWS\system32\Ati2evxx.exe C:\Program Files\AVG\AVG9\avgchsvx.exe C:\Program Files\AVG\AVG9\avgrsx.exe C:\Program Files\AVG\AVG9\avgcsrvx.exe C:\Program Files\Lavasoft\Ad-Aware\AAWService.exe C:\WINDOWS\system32\spoolsv.exe C:\WINDOWS\Explorer.EXE C:\Program Files\BillP Studios\WinPatrol\winpatrol.exe C:\Program Files\Synaptics\SynTP\SynTPEnh.exe C:\PROGRA~1\AVG\AVG9\avgtray.exe C:\Program Files\iTunes\iTunesHelper.exe C:\WINDOWS\system32\rundll32.exe C:\Program Files\ATI Technologies\ATI.ACE\CLI.EXE C:\WINDOWS\RTHDCPL.EXE C:\Program Files\SUPERAntiSpyware\2c34bb8a-9201-41d5-8c90-500b2af1c301.exe C:\WINDOWS\system32\ctfmon.exe C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe C:\Program Files\AVG\AVG9\avgwdsvc.exe C:\Program Files\IVT Corporation\BlueSoleil\BTNtService.exe C:\Program Files\Bonjour\mDNSResponder.exe svchost.exe C:\Program Files\AVG\AVG9\avgnsx.exe C:\WINDOWS\system32\svchost.exe -k hpdevmgmt C:\Program Files\Java\jre6\bin\jqs.exe C:\WINDOWS\System32\svchost.exe -k HPZ12 C:\WINDOWS\System32\svchost.exe -k HPZ12 C:\WINDOWS\system32\svchost.exe -k imgsvc C:\WINDOWS\system32\SearchIndexer.exe C:\Program Files\Yahoo!\SoftwareUpdate\YahooAUService.exe C:\Program Files\AVG\AVG9\avgemc.exe C:\Program Files\AVG\AVG9\avgcsrvx.exe C:\Program Files\iPod\bin\iPodService.exe C:\Program Files\ATI Technologies\ATI.ACE\cli.exe C:\Program Files\ATI Technologies\ATI.ACE\cli.exe C:\Program Files\Lavasoft\Ad-Aware\AAWTray.exe C:\Program Files\Internet Explorer\IEXPLORE.EXE C:\WINDOWS\system32\SearchProtocolHost.exe C:\Documents and Settings\P Compton\Desktop\dds.com ============== Pseudo HJT Report =============== uStart Page = hxxp://uk.yahoo.com/ uInternet Settings,ProxyOverride = ;*.local uSearchURL,(Default) = hxxp://uk.rd.yahoo.com/customize/ie/defaults/su/msgr8/*http://uk.search.yahoo.com BHO: &Yahoo! Toolbar Helper: {02478d38-c3f9-4efb-9b51-7695eca05670} - c:\program files\yahoo!\companion\installs\cpn3\yt.dll BHO: Adobe PDF Reader Link Helper: {06849e9f-c8d7-4d59-b87d-784b7d6be0b3} - c:\program files\common files\adobe\acrobat\activex\AcroIEHelper.dll BHO: AVG Safe Search: {3ca2f312-6f6e-4b53-a66e-4e65e497c8c0} - c:\program files\avg\avg9\avgssie.dll BHO: Vuze Remote Toolbar: {ba14329e-9550-4989-b3f2-9732e92d17cc} - c:\program files\vuze_remote\tbVuz1.dll BHO: Sopcast Ask Toolbar: {d4027c7f-154a-4066-a1ad-4243d8127440} - c:\program files\ask.com\GenericAskToolbar.dll BHO: Java™ Plug-In 2 SSV Helper: {dbc80044-a445-435b-bc74-9c25c1c588a9} - c:\program files\java\jre6\bin\jp2ssv.dll BHO: JQSIEStartDetectorImpl Class: {e7e6f031-17ce-4c07-bc86-eabfe594f69c} - c:\program files\java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll BHO: SingleInstance Class: {fdad4da1-61a2-4fd8-9c17-86f7ac245081} - c:\program files\yahoo!\companion\installs\cpn3\YTSingleInstance.dll TB: Yahoo! Toolbar: {ef99bd32-c1fb-11d2-892f-0090271d4f88} - c:\program files\yahoo!\companion\installs\cpn3\yt.dll TB: {CCC7A320-B3CA-4199-B1A6-9F516DD69829} - No File TB: Vuze Remote Toolbar: {ba14329e-9550-4989-b3f2-9732e92d17cc} - c:\program files\vuze_remote\tbVuz1.dll TB: Sopcast Ask Toolbar: {d4027c7f-154a-4066-a1ad-4243d8127440} - c:\program files\ask.com\GenericAskToolbar.dll uRun: [SUPERAntiSpyware] c:\program files\superantispyware\2c34bb8a-9201-41d5-8c90-500b2af1c301.exe uRun: [ctfmon.exe] c:\windows\system32\ctfmon.exe mRun: [WinPatrol] c:\program files\billp studios\winpatrol\winpatrol.exe mRun: [KTPWare] c:\program files\elantech\ktp.exe mRun: [IMJPMIG8.1] "c:\windows\ime\imjp8_1\IMJPMIG.EXE" /Spoil /RemAdvDef /Migration32 mRun: [SynTPEnh] c:\program files\synaptics\syntp\SynTPEnh.exe mRun: [AVG9_TRAY] c:\progra~1\avg\avg9\avgtray.exe mRun: [AppleSyncNotifier] c:\program files\common files\apple\mobile device support\AppleSyncNotifier.exe mRun: [iTunesHelper] "c:\program files\itunes\iTunesHelper.exe" mRun: [Adobe ARM] "c:\program files\common files\adobe\arm\1.0\AdobeARM.exe" mRun: [BluetoothAuthenticationAgent] rundll32.exe bthprops.cpl,,BluetoothAuthenticationAgent mRun: [ATICCC] "c:\program files\ati technologies\ati.ace\CLIStart.exe" mRun: [MSPY2002] c:\windows\system32\ime\pintlgnt\ImScInst.exe /SYNC mRun: [PHIME2002ASync] c:\windows\system32\ime\tintlgnt\TINTSETP.EXE /SYNC mRun: [PHIME2002A] c:\windows\system32\ime\tintlgnt\TINTSETP.EXE /IMEName mRun: [RTHDCPL] RTHDCPL.EXE mRun: [Alcmtr] ALCMTR.EXE dRunOnce: [tscuninstall] %systemroot%\system32\tscupgrd.exe IE: {e2e2dd38-d088-4134-82b7-f2ba38496583} - %windir%\Network Diagnostic\xpnetdiag.exe IE: {FB5F1910-F110-11d2-BB9E-00C04F795683} - c:\program files\messenger\msmsgs.exe DPF: {6414512B-B978-451D-A0D8-FCFDF33E833C} - hxxp://update.microsoft.com/windowsupdate/v6/V5Controls/en/x86/client/wuweb_site.cab?1263498871678 DPF: {8100D56A-5661-482C-BEE8-AFECE305D968} - hxxp://upload.facebook.com/controls/2009.07.28_v5.5.8.1/FacebookPhotoUploader55.cab DPF: {8FEFF364-6A5F-4966-A917-A3AC28411659} - hxxp://download.sopcast.com/download/SOPCORE.CAB DPF: {8FFBE65D-2C9C-4669-84BD-5829DC0B603C} - hxxp://fpdownload.macromedia.com/get/flashplayer/current/polarbear/ultrashim.cab DPF: {E2883E8F-472F-4FB0-9522-AC9BF37916A7} - hxxp://platformdl.adobe.com/NOS/getPlusPlus/1.6/gp.cab Handler: linkscanner - {F274614C-63F8-47D5-A4D1-FBDDE494F8D1} - c:\program files\avg\avg9\avgpp.dll Notify: !SASWinLogon - c:\program files\superantispyware\SASWINLO.DLL Notify: AtiExtEvent - Ati2evxx.dll Notify: avgrsstarter - avgrsstx.dll SSODL: WPDShServiceObj - {AAA288BA-9A4C-45B0-95D7-94D524869DB5} - c:\windows\system32\WPDShServiceObj.dll SEH: Windows Desktop Search Namespace Manager: {56f9679e-7826-4c84-81f3-532071a8bcc5} - c:\program files\windows desktop search\MSNLNamespaceMgr.dll mASetup: {A509B1FF-37FF-4bFF-8CFF-4F3A747040FF} - c:\windows\system32\rundll32.exe c:\windows\system32\advpack.dll,launchinfsectionex c:\program files\internet explorer\clrtour.inf,DefaultInstall.ResetTour,,12 ============= SERVICES / DRIVERS =============== R0 Lbd;Lbd;c:\windows\system32\drivers\Lbd.sys [2009-4-25 64160] R1 AvgLdx86;AVG Free AVI Loader Driver x86;c:\windows\system32\drivers\avgldx86.sys [2010-4-10 216200] R1 AvgMfx86;AVG Free On-access Scanner Minifilter Driver x86;c:\windows\system32\drivers\avgmfx86.sys [2010-4-10 29512] R1 AvgTdiX;AVG Free Network Redirector;c:\windows\system32\drivers\avgtdix.sys [2010-4-10 242896] R1 cdrblock;cdrblock;c:\windows\system32\drivers\cdrblock.sys [2007-11-21 20992] R1 cdrport;cdrport;c:\windows\system32\drivers\cdrport.sys [2007-11-21 4608] R1 SASDIFSV;SASDIFSV;c:\program files\superantispyware\sasdifsv.sys [2009-3-23 9968] R1 SASKUTIL;SASKUTIL;c:\program files\superantispyware\SASKUTIL.SYS [2009-3-23 74480] R2 avg9emc;AVG Free E-mail Scanner;c:\program files\avg\avg9\avgemc.exe [2010-4-10 916760] R2 avg9wd;AVG Free WatchDog;c:\program files\avg\avg9\avgwdsvc.exe [2010-4-10 308064] R2 Lavasoft Ad-Aware Service;Lavasoft Ad-Aware Service;c:\program files\lavasoft\ad-aware\AAWService.exe [2009-3-9 1029456] R3 SASENUM;SASENUM;c:\program files\superantispyware\SASENUM.SYS [2009-3-23 7408] S2 AutoExNT;AutoExNT;c:\windows\system32\Autoexnt.exe [2010-4-10 5904] S3 cpuz132;cpuz132;\??\c:\docume~1\pcompt~1\locals~1\temp\cpuz132\cpuz132_x32.sys –> c:\docume~1\pcompt~1\locals~1\temp\cpuz132\cpuz132_x32.sys [?] S3 MotDev;Motorola Inc. USB Device;c:\windows\system32\drivers\motodrv.sys [2008-6-21 42112] =============== Created Last 30 ================ 2010-05-20 22:13:47 0 d—–w- c:\docume~1\pcompt~1\applic~1\AVG9 2010-05-20 21:32:13 488 —ha-r- c:\windows\system32\logonui.exe.manifest 2010-05-20 21:32:08 749 —ha-r- c:\windows\WindowsShell.Manifest 2010-05-20 21:32:08 749 —ha-r- c:\windows\system32\wuaucpl.cpl.manifest 2010-05-20 21:32:08 749 —ha-r- c:\windows\system32\sapi.cpl.manifest 2010-05-20 21:32:08 749 —ha-r- c:\windows\system32\nwc.cpl.manifest 2010-05-20 21:32:08 749 —ha-r- c:\windows\system32\ncpa.cpl.manifest 2010-05-20 21:18:12 88192 —-a-w- c:\windows\system32\drivers\irda.sys 2010-05-20 21:18:12 8192 —-a-w- c:\windows\system32\wshirda.dll 2010-05-20 21:18:12 28160 —-a-w- c:\windows\system32\irmon.dll 2010-05-20 21:18:12 151552 —-a-w- c:\windows\system32\irftp.exe 2010-05-20 21:10:24 16535 —-a-r- c:\windows\SETFF.tmp 2010-05-20 21:10:21 1088840 —-a-r- c:\windows\SETEE.tmp 2010-05-20 21:10:18 1296669 —-a-r- c:\windows\SETEB.tmp 2010-05-20 20:47:27 19584 —-a-w- c:\windows\system32\drivers\rasirda.sys 2010-05-20 19:19:55 0 d—–w- c:\windows\setupupd 2010-05-20 17:38:51 39936 -c–a-w- c:\windows\system32\dllcache\hostmib.dll 2010-05-20 17:38:51 39936 —-a-w- c:\windows\system32\hostmib.dll 2010-05-20 17:38:47 0 d—–w- C:\Inetpub 2010-05-20 17:15:48 6144 -c–a-w- c:\windows\system32\dllcache\snmpmib.dll 2010-05-20 17:15:48 6144 —-a-w- c:\windows\system32\snmpmib.dll 2010-05-20 16:55:40 16535 —-a-r- c:\windows\SET103.tmp 2010-05-20 16:55:37 1088840 —-a-r- c:\windows\SETF7.tmp 2010-05-20 16:55:35 1296669 —-a-r- c:\windows\SETF1.tmp 2010-05-20 16:37:10 0 d—–w- c:\windows\setup.pss 2010-05-19 09:04:02 0 d—–w- c:\program files\ATI Technologies 2010-05-14 10:28:11 0 d—–w- c:\program files\CamStudio 2010-05-14 10:06:27 0 d—–w- c:\program files\NirSoft 2010-05-13 10:15:29 73 —-a-w- c:\windows\system32\-1 2010-05-12 09:34:44 16535 —-a-r- c:\windows\SETF6.tmp 2010-05-12 09:34:40 1088840 —-a-r- c:\windows\SETEA.tmp 2010-05-12 09:34:38 1296669 —-a-r- c:\windows\SETE7.tmp 2010-05-12 09:23:11 0 d-sh–w- C:\found.000 2010-05-10 17:31:02 16535 —-a-r- c:\windows\SETF5.tmp 2010-05-10 17:30:58 1088840 —-a-r- c:\windows\SETE9.tmp 2010-05-10 17:30:56 1296669 —-a-r- c:\windows\SETE6.tmp 2010-05-10 16:59:35 16535 —-a-r- c:\windows\SET14D.tmp 2010-05-10 16:59:31 1088840 —-a-r- c:\windows\SET141.tmp 2010-05-10 16:59:29 1296669 —-a-r- c:\windows\SET140.tmp 2010-05-05 11:47:31 0 d—–w- c:\docume~1\pcompt~1\applic~1\Office Genuine Advantage 2010-04-27 10:05:34 69632 —-a-w- c:\windows\ALCMTR.EXE 2010-04-26 21:17:05 0 d—–w- c:\windows\system32\wbem\Repository ==================== Find3M ==================== 2010-05-20 21:27:32 23392 -c–a-w- c:\windows\system32\emptyregdb.dat 2010-04-21 16:25:24 242896 —-a-w- c:\windows\system32\drivers\avgtdix.sys 2010-04-10 16:01:36 12464 —-a-w- c:\windows\system32\avgrsstx.dll 2010-04-10 16:01:28 216200 —-a-w- c:\windows\system32\drivers\avgldx86.sys 2010-04-08 23:07:37 71680 –sha-r- c:\windows\system32\kbdtuq5.dll 2010-03-29 23:46:30 38224 —-a-w- c:\windows\system32\drivers\mbamswissarmy.sys 2010-03-29 23:45:52 20824 —-a-w- c:\windows\system32\drivers\mbam.sys 2009-04-20 17:33:51 2098 -csha-w- c:\windows\system32\KGyGaAvL.sys ============= FINISH: 11:12:52.34 =============== the other as instructed is attached ok i downloaded gmer successfully and run it got about 2 hours in and froze up . i stopped it and run again started at lunchtime it was still scanning at 2am and then turned into a white solid block and froze my comp up again , wouldnt even let me bring up the manager to shut it down the only thing i could do was a hard reset on the power off button . what would you like me to do next ? once again thanks for your help phil c

Attachments:

Please run this following program instead:

Please download this file, and save it to your Desktop. Once you have downloaded it, save and close all other programs and run it by double-clicking on the file named "RootRepeal.exe".

Once the main window shows up, please click on the "Report" button on the bottom of the window. Next, please click the "Scan" button.

Another window will pop up asking you to select what to include in the scan. Please uncheck everything except for the "Stealth Code" checkbox, and then click OK.

Once the program has finished scanning, the results will appear. Click on the "Save Report" button, and save the report to your desktop.

Finally, please open this report with Notepad, and post it here.
hi there, is this what you want ? seems very fast and not much there ROOTREPEAL © AD, 2007-2010 ================================================== Report Save Time: 2010/05/24 16:08 Program Version: Version 2.0.0.0 Windows Version: Windows XP SP3 ================================================== STEALTH CODE ——————-
Hi,

Please do the following:


Download ComboFix from one of the following locations:
Link 1
Link 2

VERY IMPORTANT !!! Save ComboFix.exe to your Desktop

* IMPORTANT - Disable your AntiVirus and AntiSpyware applications, usually via a right click on the System Tray icon. They may otherwise interfere with our tools. If you have difficulty properly disabling your protective programs, refer to this link here
  • Double click on ComboFix.exe & follow the prompts.
As part of it's process, ComboFix will check to see if the Microsoft Windows Recovery Console is installed. With malware infections being as they are today, it's strongly recommended to have this pre-installed on your machine before doing any malware removal. It will allow you to boot up into a special recovery/repair mode that will allow us to more easily help you should your computer have a problem after an attempted removal of malware.

  • Follow the prompts to allow ComboFix to download and install the Microsoft Windows Recovery Console, and when prompted, agree to the End-User License Agreement to install the Microsoft Windows Recovery Console.
**Please note: If the Microsoft Windows Recovery Console is already installed, ComboFix will continue it's malware removal procedures.

[external image: Posted Image]

  • Once the Microsoft Windows Recovery Console is installed using ComboFix, you should see the following message:

[external image: Posted Image]

  • Click on Yes, to continue scanning for malware.
When finished, it shall produce a log for you. Please include the C:\ComboFix.txt in your next reply.
Notes:
1. Do not mouse-click Combofix's window while it is running. That may cause it to stall.
2. Do not "re-run" Combofix. If you have a problem, reply back for further instructions.
hi catbye, here as ask for is the combofix log
ComboFix 10-05-23.08 - P Compton 24/05/2010 18:23:43.4.2 - x86
Microsoft Windows XP Professional 5.1.2600.3.1252.44.1033.18.3070.2454 [GMT 1:00]
Running from: c:\documents and settings\[removed]\Desktop\ComboFix.exe
AV: AVG Anti-Virus Free *On-access scanning disabled* (Updated) {17DDD097-36FF-435F-9E1B-52D74245D6BF}
.

((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.

c:\windows\system32\winlogon.bak

.
((((((((((((((((((((((((( Files Created from 2010-04-24 to 2010-05-24 )))))))))))))))))))))))))))))))
.

2010-05-20 21:18 . 2008-04-14 04:42 151552 —-a-w- c:\windows\system32\irftp.exe
2010-05-20 21:18 . 2008-04-14 04:42 8192 —-a-w- c:\windows\system32\wshirda.dll
2010-05-20 21:18 . 2008-04-14 04:41 28160 —-a-w- c:\windows\system32\irmon.dll
2010-05-20 21:18 . 2008-04-13 23:24 88192 —-a-w- c:\windows\system32\drivers\irda.sys
2010-05-20 20:47 . 2001-08-17 12:51 19584 —-a-w- c:\windows\system32\drivers\rasirda.sys
2010-05-20 20:40 . 2008-04-14 12:00 24661 -c–a-w- c:\windows\system32\dllcache\spxcoins.dll
2010-05-20 20:40 . 2008-04-14 12:00 24661 —-a-w- c:\windows\system32\spxcoins.dll
2010-05-20 20:40 . 2008-04-14 12:00 13312 -c–a-w- c:\windows\system32\dllcache\irclass.dll
2010-05-20 20:40 . 2008-04-14 12:00 13312 —-a-w- c:\windows\system32\irclass.dll
2010-05-20 17:38 . 2008-04-14 12:00 39936 -c–a-w- c:\windows\system32\dllcache\hostmib.dll
2010-05-20 17:38 . 2008-04-14 12:00 39936 —-a-w- c:\windows\system32\hostmib.dll
2010-05-20 17:38 . 2010-05-20 17:38 ——– d—–w- C:\Inetpub
2010-05-20 17:15 . 2008-04-14 12:00 6144 -c–a-w- c:\windows\system32\dllcache\snmpmib.dll
2010-05-20 17:15 . 2008-04-14 12:00 6144 —-a-w- c:\windows\system32\snmpmib.dll
2010-05-19 09:08 . 2010-05-19 09:08 ——– d—–w- c:\documents and settings\P Compton\Local Settings\Application Data\ATI
2010-05-19 09:08 . 2010-05-19 09:08 ——– d—–w- c:\documents and settings\P Compton\Application Data\ATI
2010-05-19 09:08 . 2010-05-19 09:08 132 —-a-w- c:\documents and settings\P Compton\Local Settings\Application Data\fusioncache.dat
2010-05-19 09:04 . 2010-05-19 09:04 ——– d—–w- c:\program files\ATI Technologies
2010-05-19 08:55 . 2006-11-13 10:13 5144576 —-a-w- c:\windows\system32\atioglxx.dll
2010-05-19 08:55 . 2006-11-13 10:13 307200 —-a-w- c:\windows\system32\atiiiexx.dll
2010-05-19 08:55 . 2006-11-13 10:13 303104 —-a-w- c:\windows\system32\ATIDEMGR.dll
2010-05-19 08:55 . 2006-11-13 10:13 2515656 —-a-w- c:\windows\system32\ativvaxx.dat
2010-05-19 08:55 . 2006-11-13 10:13 221184 —-a-w- c:\windows\system32\atikvmag.dll
2010-05-19 08:55 . 2006-11-13 10:13 17408 —-a-w- c:\windows\system32\atitvo32.dll
2010-05-19 08:55 . 2006-11-13 10:13 136650 —-a-w- c:\windows\system32\atiicdxx.dat
2010-05-19 08:55 . 2006-11-13 10:13 90112 —-a-w- c:\windows\system32\ati2evxx.dll
2010-05-19 08:55 . 2006-11-13 10:13 49152 —-a-w- c:\windows\system32\drivers\ati2erec.dll
2010-05-19 08:55 . 2006-11-13 10:13 425984 —-a-w- c:\windows\system32\ati2evxx.exe
2010-05-19 08:55 . 2006-11-13 10:13 41984 —-a-w- c:\windows\system32\ati2edxx.dll
2010-05-19 08:55 . 2006-11-13 10:13 26112 —-a-w- c:\windows\system32\Ati2mdxx.exe
2010-05-14 10:28 . 2010-05-14 12:01 ——– d—–w- c:\program files\CamStudio
2010-05-14 10:06 . 2010-05-20 11:02 ——– d—–w- c:\program files\NirSoft
2010-05-12 09:23 . 2010-05-12 09:23 ——– d—–w- C:\found.000
2010-05-08 16:20 . 2010-05-08 16:20 ——– d—–w- c:\documents and settings\All Users\Application Data\Office Genuine Advantage
2010-05-05 11:47 . 2010-05-05 11:47 ——– d—–w- c:\documents and settings\P Compton\Application Data\Office Genuine Advantage
2010-04-27 10:05 . 2006-11-13 03:12 69632 —-a-w- c:\windows\ALCMTR.EXE
2010-04-26 21:17 . 2010-05-20 15:38 ——– d—–w- c:\windows\system32\wbem\Repository

.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2010-05-24 15:20 . 2010-02-23 22:17 ——– d—–w- c:\documents and settings\P Compton\Application Data\vlc
2010-05-24 10:56 . 2008-02-03 21:59 ——– d—–w- c:\documents and settings\P Compton\Application Data\Azureus
2010-05-20 22:13 . 2010-05-20 22:13 ——– d—–w- c:\documents and settings\P Compton\Application Data\AVG9
2010-05-20 21:27 . 2007-11-20 15:36 23392 -c–a-w- c:\windows\system32\emptyregdb.dat
2010-05-20 17:54 . 2010-02-21 17:21 ——– d—–w- c:\documents and settings\All Users\Application Data\avg9
2010-05-19 09:04 . 2007-11-21 10:41 ——– d–h–w- c:\program files\InstallShield Installation Information
2010-05-12 10:16 . 2010-04-13 11:35 ——– d—–w- c:\program files\Vuze_Remote
2010-05-05 16:50 . 2009-04-26 22:36 117760 —-a-w- c:\documents and settings\P Compton\Application Data\SUPERAntiSpyware.com\SUPERAntiSpyware\SDDLLS\UIREPAIR.DLL
2010-04-27 10:05 . 2007-11-21 11:15 ——– d—–w- c:\program files\Realtek
2010-04-21 16:25 . 2010-04-10 16:01 242896 —-a-w- c:\windows\system32\drivers\avgtdix.sys
2010-04-16 18:23 . 2008-09-07 15:19 ——– d—–w- c:\documents and settings\P Compton\Application Data\dvdcss
2010-04-14 21:21 . 2009-01-13 22:11 ——– d—–w- c:\program files\SopCast
2010-04-14 21:21 . 2010-04-14 21:21 ——– d—–w- c:\program files\Ask.com
2010-04-13 19:59 . 2010-04-03 16:00 ——– d—–w- c:\program files\TVUPlayer
2010-04-13 11:36 . 2008-02-03 21:58 ——– d—–w- c:\program files\Azureus
2010-04-13 11:35 . 2010-04-13 11:35 52224 —-a-w- c:\documents and settings\P Compton\Application Data\Mozilla\Firefox\Profiles\jorb9q2r.default\extensions\{ba14329e-9550-4989-b3f2-9732e92d17cc}\components\FFExternalAlert.dll
2010-04-13 11:35 . 2010-04-13 11:35 101376 —-a-w- c:\documents and settings\P Compton\Application Data\Mozilla\Firefox\Profiles\jorb9q2r.default\extensions\{ba14329e-9550-4989-b3f2-9732e92d17cc}\components\RadioWMPCore.dll
2010-04-13 11:35 . 2010-04-13 11:35 ——– d—–w- c:\program files\Conduit
2010-04-12 00:29 . 2010-02-05 12:36 ——– d—–w- c:\documents and settings\All Users\Application Data\NCH Swift Sound
2010-04-11 19:06 . 2010-04-11 19:05 ——– d—–w- c:\program files\iTunes
2010-04-11 19:06 . 2010-04-11 19:05 ——– d—–w- c:\documents and settings\All Users\Application Data\{429CAD59-35B1-4DBC-BB6D-1DB246563521}
2010-04-11 19:05 . 2010-04-11 19:05 ——– d—–w- c:\program files\iPod
2010-04-11 19:05 . 2009-12-29 14:16 ——– d—–w- c:\program files\Common Files\Apple
2010-04-11 19:01 . 2009-07-28 13:01 ——– d—–w- c:\program files\QuickTime
2010-04-11 18:57 . 2010-04-11 18:57 ——– d—–w- c:\program files\Bonjour
2010-04-11 18:44 . 2010-04-11 18:44 73000 —-a-w- c:\documents and settings\All Users\Application Data\Apple Computer\Installer Cache\iTunes 9.1.0.79\SetupAdmin.exe
2010-04-11 18:20 . 2010-04-11 18:20 ——– d—–w- c:\program files\Safari
2010-04-11 18:17 . 2010-04-11 18:17 79144 —-a-w- c:\documents and settings\All Users\Application Data\Apple Computer\Installer Cache\Safari 5.31.22.7\SetupAdmin.exe
2010-04-10 17:33 . 2010-04-10 17:33 ——– d—–w- c:\program files\MSXML 6.0
2010-04-10 16:01 . 2010-04-10 16:01 12464 —-a-w- c:\windows\system32\avgrsstx.dll
2010-04-10 16:01 . 2010-04-10 16:01 216200 —-a-w- c:\windows\system32\drivers\avgldx86.sys
2010-04-10 16:01 . 2010-04-10 16:01 29512 —-a-w- c:\windows\system32\drivers\avgmfx86.sys
2010-04-10 13:03 . 2010-04-10 01:00 ——– d—–w- c:\program files\Malwarebytes' Anti-Malware
2010-04-10 00:48 . 2010-04-10 00:21 ——– d—–w- c:\program files\AVG
2010-04-09 00:59 . 2009-04-26 22:35 ——– d—–w- c:\program files\SUPERAntiSpyware
2010-04-09 00:41 . 2010-04-09 00:41 664 —-a-w- c:\windows\system32\d3d9caps.dat
2010-04-08 23:07 . 2010-04-08 23:07 71680 –sha-r- c:\windows\system32\kbdtuq5.dll
2010-04-08 18:15 . 2010-04-08 18:15 ——– d—–w- c:\documents and settings\All Users\Application Data\PC Drivers HeadQuarters
2010-04-07 17:21 . 2007-12-01 22:54 ——– d—–w- c:\documents and settings\All Users\Application Data\Yahoo! Companion
2010-04-03 16:07 . 2010-04-03 16:07 ——– d—–w- c:\documents and settings\All Users\Application Data\TVU Networks
2010-04-03 16:00 . 2010-04-03 16:00 ——– d—–w- c:\documents and settings\P Compton\Application Data\TVU Networks
2010-03-29 23:46 . 2010-04-10 13:03 38224 —-a-w- c:\windows\system32\drivers\mbamswissarmy.sys
2010-03-29 23:45 . 2010-04-10 13:03 20824 —-a-w- c:\windows\system32\drivers\mbam.sys
2010-03-26 12:41 . 2010-03-26 12:41 ——– d—–w- c:\documents and settings\P Compton\Application Data\NCH Software
2010-03-26 12:40 . 2010-03-26 12:40 ——– d—–w- c:\documents and settings\All Users\Application Data\NCH Software
2009-04-20 17:33 . 2007-11-30 17:38 2098 -csha-w- c:\windows\system32\KGyGaAvL.sys
.

((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4

[HKEY_LOCAL_MACHINE\~\Browser Helper Objects\{ba14329e-9550-4989-b3f2-9732e92d17cc}]
2010-05-12 10:16 2515552 —-a-w- c:\program files\Vuze_Remote\tbVuz1.dll

[HKEY_LOCAL_MACHINE\~\Browser Helper Objects\{D4027C7F-154A-4066-A1AD-4243D8127440}]
2010-02-04 15:50 1197448 —-a-w- c:\program files\Ask.com\GenericAskToolbar.dll

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Internet Explorer\Toolbar]
"{ba14329e-9550-4989-b3f2-9732e92d17cc}"= "c:\program files\Vuze_Remote\tbVuz1.dll" [2010-05-12 2515552]
"{D4027C7F-154A-4066-A1AD-4243D8127440}"= "c:\program files\Ask.com\GenericAskToolbar.dll" [2010-02-04 1197448]

[HKEY_CLASSES_ROOT\clsid\{ba14329e-9550-4989-b3f2-9732e92d17cc}]

[HKEY_CLASSES_ROOT\clsid\{d4027c7f-154a-4066-a1ad-4243d8127440}]
[HKEY_CLASSES_ROOT\GenericAskToolbar.ToolbarWnd.1]
[HKEY_CLASSES_ROOT\TypeLib\{2996F0E7-292B-4CAE-893F-47B8B1C05B56}]
[HKEY_CLASSES_ROOT\GenericAskToolbar.ToolbarWnd]

[HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Toolbar\Webbrowser]
"{BA14329E-9550-4989-B3F2-9732E92D17CC}"= "c:\program files\Vuze_Remote\tbVuz1.dll" [2010-05-12 2515552]
"{D4027C7F-154A-4066-A1AD-4243D8127440}"= "c:\program files\Ask.com\GenericAskToolbar.dll" [2010-02-04 1197448]

[HKEY_CLASSES_ROOT\clsid\{ba14329e-9550-4989-b3f2-9732e92d17cc}]

[HKEY_CLASSES_ROOT\clsid\{d4027c7f-154a-4066-a1ad-4243d8127440}]
[HKEY_CLASSES_ROOT\GenericAskToolbar.ToolbarWnd.1]
[HKEY_CLASSES_ROOT\TypeLib\{2996F0E7-292B-4CAE-893F-47B8B1C05B56}]
[HKEY_CLASSES_ROOT\GenericAskToolbar.ToolbarWnd]

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SUPERAntiSpyware"="c:\program files\SUPERAntiSpyware\2c34bb8a-9201-41d5-8c90-500b2af1c301.exe" [2009-11-24 2001648]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"WinPatrol"="c:\program files\BillP Studios\WinPatrol\winpatrol.exe" [2007-10-26 292152]
"KTPWare"="c:\program files\Elantech\ktp.exe" [2009-01-14 512000]
"IMJPMIG8.1"="c:\windows\IME\imjp8_1\IMJPMIG.EXE" [2007-07-27 208952]
"SynTPEnh"="c:\program files\Synaptics\SynTP\SynTPEnh.exe" [2008-02-28 786521]
"AppleSyncNotifier"="c:\program files\Common Files\Apple\Mobile Device Support\AppleSyncNotifier.exe" [2010-03-16 47392]
"iTunesHelper"="c:\program files\iTunes\iTunesHelper.exe" [2010-03-26 142120]
"Adobe ARM"="c:\program files\Common Files\Adobe\ARM\1.0\AdobeARM.exe" [2010-03-24 952768]
"BluetoothAuthenticationAgent"="bthprops.cpl" [2008-04-14 110592]
"ATICCC"="c:\program files\ATI Technologies\ATI.ACE\CLIStart.exe" [2006-05-10 90112]
"RTHDCPL"="RTHDCPL.EXE" [2007-10-16 16855552]

[HKEY_USERS\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\RunOnce]
"tscuninstall"="c:\windows\system32\tscupgrd.exe" [2007-07-27 44544]

[hkey_local_machine\software\microsoft\windows\currentversion\explorer\ShellExecuteHooks]
"{56F9679E-7826-4C84-81F3-532071A8BCC5}"= "c:\program files\Windows Desktop Search\MSNLNamespaceMgr.dll" [2009-05-24 304128]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\!SASWinLogon]
2009-09-09 10:39 548352 —-a-w- c:\program files\SUPERAntiSpyware\SASWINLO.DLL

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\avgrsstarter]
2010-04-10 16:01 12464 —-a-w- c:\windows\system32\avgrsstx.dll

[HKEY_LOCAL_MACHINE\system\currentcontrolset\control\session manager]
BootExecute REG_MULTI_SZ autocheck autochk *\0lsdelete\0sprestrt

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Lavasoft Ad-Aware Service]
@="Service"

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Adobe Reader Speed Launcher]
2010-04-02 18:05 40368 —-a-w- c:\program files\Adobe\Reader 8.0\Reader\reader_sl.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\QuickTime Task]
2010-03-17 20:53 421888 —-a-w- c:\program files\QuickTime\QTTask.exe

[HKEY_LOCAL_MACHINE\software\microsoft\security center]
"AntiVirusOverride"=dword:00000001
"FirewallOverride"=dword:00000001

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile]
"DisableNotifications"= 1 (0x1)

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"c:\\Program Files\\IVT Corporation\\BlueSoleil\\BlueSoleil.exe"=
"c:\\Program Files\\Yahoo!\\Messenger\\YahooMessenger.exe"=
"c:\\Program Files\\Messenger\\msmsgs.exe"=
"c:\\Program Files\\LimeWire\\LimeWire.exe"=
"c:\\StubInstaller.exe"=
"c:\\Program Files\\TVAnts\\Tvants.exe"=
"c:\\Program Files\\SopCast\\adv\\SopAdver.exe"=
"c:\\Program Files\\SopCast\\SopCast.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\wlcsdk.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\msnmsgr.exe"=
"c:\\Program Files\\TVUPlayer\\TVUPlayer.exe"=
"c:\\Program Files\\AVG\\AVG9\\avgemc.exe"=
"c:\\Program Files\\AVG\\AVG9\\avgupd.exe"=
"c:\\Program Files\\AVG\\AVG9\\avgnsx.exe"=
"c:\\Program Files\\Bonjour\\mDNSResponder.exe"=
"c:\\Program Files\\iTunes\\iTunes.exe"=
"c:\\Program Files\\Azureus\\Azureus.exe"=

R0 Lbd;Lbd;c:\windows\system32\drivers\Lbd.sys [4/25/2009 9:56 AM 64160]
R1 AvgLdx86;AVG Free AVI Loader Driver x86;c:\windows\system32\drivers\avgldx86.sys [4/10/2010 5:01 PM 216200]
R1 AvgTdiX;AVG Free Network Redirector;c:\windows\system32\drivers\avgtdix.sys [4/10/2010 5:01 PM 242896]
R1 cdrblock;cdrblock;c:\windows\system32\drivers\cdrblock.sys [11/21/2007 12:45 PM 20992]
R1 cdrport;cdrport;c:\windows\system32\drivers\cdrport.sys [11/21/2007 12:45 PM 4608]
R1 SASDIFSV;SASDIFSV;c:\program files\SUPERAntiSpyware\sasdifsv.sys [3/23/2009 2:07 PM 9968]
R1 SASKUTIL;SASKUTIL;c:\program files\SUPERAntiSpyware\SASKUTIL.SYS [3/23/2009 2:07 PM 74480]
R2 avg9emc;AVG Free E-mail Scanner;c:\program files\AVG\AVG9\avgemc.exe [4/10/2010 5:00 PM 916760]
R2 avg9wd;AVG Free WatchDog;c:\program files\AVG\AVG9\avgwdsvc.exe [4/10/2010 5:00 PM 308064]
R3 SASENUM;SASENUM;c:\program files\SUPERAntiSpyware\SASENUM.SYS [3/23/2009 2:07 PM 7408]
S2 AutoExNT;AutoExNT;c:\windows\system32\Autoexnt.exe [4/10/2010 6:21 PM 5904]
S2 Lavasoft Ad-Aware Service;Lavasoft Ad-Aware Service;c:\program files\Lavasoft\Ad-Aware\AAWService.exe [3/9/2009 8:06 PM 1029456]
S3 MotDev;Motorola Inc. USB Device;c:\windows\system32\drivers\motodrv.sys [6/21/2008 8:05 PM 42112]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost]
HPZ12 REG_MULTI_SZ Pml Driver HPZ12 Net Driver HPZ12
hpdevmgmt REG_MULTI_SZ hpqcxs08 hpqddsvc

[HKEY_LOCAL_MACHINE\software\microsoft\active setup\installed components\{A509B1FF-37FF-4bFF-8CFF-4F3A747040FF}]
2007-08-13 17:39 123904 —-a-w- c:\windows\system32\advpack.dll
.
Contents of the 'Scheduled Tasks' folder

2010-05-24 c:\windows\Tasks\Ad-Aware Update (Weekly).job
- c:\program files\Lavasoft\Ad-Aware\Ad-AwareAdmin.exe [2009-03-09 19:28]

2010-05-20 c:\windows\Tasks\AppleSoftwareUpdate.job
- c:\program files\Apple Software Update\SoftwareUpdate.exe [2008-07-30 12:34]

2010-04-12 c:\windows\Tasks\expressripShakeIcon.job
- c:\program files\NCH Swift Sound\ExpressRip\expressrip.exe [2010-02-05 12:37]

2010-05-24 c:\windows\Tasks\OGALogon.job
- c:\windows\system32\OGAEXEC.exe [2009-08-03 14:07]

2010-05-24 c:\windows\Tasks\RegCure Program Check.job
- c:\program files\RegCure\RegCure.exe [2007-10-16 08:20]

2010-05-20 c:\windows\Tasks\RegCure.job
- c:\program files\RegCure\RegCure.exe [2007-10-16 08:20]

2010-05-24 c:\windows\Tasks\Scheduled Update for Ask Toolbar.job
- c:\program files\Ask.com\UpdateTask.exe [2010-02-04 15:50]
.
.
——- Supplementary Scan ——-
.
uStart Page = hxxp://uk.yahoo.com/
uInternet Settings,ProxyOverride = ;*.local
uSearchURL,(Default) = hxxp://uk.rd.yahoo.com/customize/ie/defaults/su/msgr8/*http://uk.search.yahoo.com
.
- - - - ORPHANS REMOVED - - - -

Toolbar-{CCC7A320-B3CA-4199-B1A6-9F516DD69829} - (no file)
WebBrowser-{CCC7A320-B3CA-4199-B1A6-9F516DD69829} - (no file)
HKLM-Run-MSPY2002 - c:\windows\system32\IME\PINTLGNT\ImScInst.exe
HKLM-Run-PHIME2002ASync - c:\windows\system32\IME\TINTLGNT\TINTSETP.EXE
HKLM-Run-PHIME2002A - c:\windows\system32\IME\TINTLGNT\TINTSETP.EXE


**************************************************************************

catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net
Rootkit scan 2010-05-24 18:28
Windows 5.1.2600 Service Pack 3 NTFS

scanning hidden processes …

scanning hidden autostart entries …

scanning hidden files …

scan completed successfully
hidden files: 0

**************************************************************************
.
——————— LOCKED REGISTRY KEYS ———————

[HKEY_LOCAL_MACHINE\software\Microsoft\Windows NT\CurrentVersion\WPAEvents]
@Denied: (Full) (LocalSystem)
"OOBETimer"=hex:ff,d5,71,d6,8b,6a,8d,6f,d5,33,93,fd
"LastWPAEventLogged"=hex:d5,07,05,00,06,00,07,00,0f,00,38,00,24,00,fd,02
.
——————— DLLs Loaded Under Running Processes ———————

- - - - - - - > 'winlogon.exe'(796)
c:\program files\SUPERAntiSpyware\SASWINLO.DLL
c:\windows\system32\Ati2evxx.dll
.
Completion time: 2010-05-24 18:29:55
ComboFix-quarantined-files.txt 2010-05-24 17:29
ComboFix2.txt 2010-04-10 14:07

Pre-Run: 14,335,614,976 bytes free
Post-Run: 14,401,327,104 bytes free

Current=1 Default=1 Failed=0 LastKnownGood=2 Sets=1,2,3,4,5,6,7,8
- - End Of File - - E657DF4190C57721BE0D172B36C846D4
regards phil c
Hi,

That was the fourth run of Combo Fix

can you please find the first three logs and zip them up for me and attach them so I can have a look at them

you should be able to locate the older logs at c:\qoobox\combofix2.txt, c:\qoobox\combofix3.txt & c:\qoobox\combofix4.txt

thanks

NEXT

Please do the following:


  • Very Important! Temporarily disable your anti-virus, script blocking and any anti-malware real-time protection before following the steps below.
  • They can interfere with ComboFix or remove some of its embedded files which may cause "unpredictable results".
Copy/paste the text inside the Codebox below into notepad:

Here's how to do that:
Click Start > Run type Notepad click OK.
This will open an empty notepad file:

Copy all the text inside of the code box - Press Ctrl+C (or right click on the highlighted section and choose 'copy')

RegLock::
[HKEY_LOCAL_MACHINE\software\Microsoft\Windows NT\CurrentVersion\WPAEvents]

FixCSet::

Now paste the copied text into the open notepad - press CTRL+V (or right click and choose 'paste')

Save this file to your desktop, Save this as "CFScript"


Here's how to do that:

1.Click File;
2.Click Save As… Change the directory to your desktop;
3.Change the Save as type to "All Files";
4.Type in the file name: CFScript
5.Click Save …

[external image: Posted Image]
  • Referring to the screenshot above, drag CFScript.txt into ComboFix.exe.
  • ComboFix will now run a scan on your system. It may reboot your system when it finishes. This is normal.
  • When finished, it shall produce a log for you.
  • Copy and paste the contents of the log in your next reply.

CAUTION: Do not mouse-click ComboFix's window while it is running. That may cause it to stall.
here are what i could find i can only find text file 2 cant find 3, iv attached all the text files in that folder there arnt any others
ComboFix 10-04-09.06 - P Compton 10/04/2010 14:59:50.3.2 - x86
Microsoft Windows XP Professional 5.1.2600.2.1252.44.1033.18.3070.2706 [GMT 1:00]
Running from: G:\ABCD.exe
.

((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.

c:\documents and settings\All Users\Application Data\Microsoft\Network\Downloader\qmgr0.dat
c:\documents and settings\All Users\Application Data\Microsoft\Network\Downloader\qmgr1.dat
c:\documents and settings\All Users\Favorites\_favdata.dat
c:\documents and settings\P Compton\Application Data\D7EB3A933DF06CE0CAD5F116CE4A10C2
c:\documents and settings\P Compton\Application Data\D7EB3A933DF06CE0CAD5F116CE4A10C2\appreg70700.exe
c:\documents and settings\P Compton\Application Data\D7EB3A933DF06CE0CAD5F116CE4A10C2\enemies-names.txt
c:\documents and settings\P Compton\Application Data\sdra64.exe
c:\windows\_VOIDnmdbdetuij
c:\windows\_VOIDnmdbdetuij\_VOIDd.sys
c:\windows\system32\_VOIDdsppljttbp.dll
c:\windows\system32\_VOIDegqfuyuicx.dat
c:\windows\system32\_VOIDetuwqxnsvj.dat
c:\windows\system32\_VOIDgibeabedbw.dat
c:\windows\system32\_VOIDjnssxgqfwy.dll
c:\windows\system32\_VOIDjxvstjqrxi.dll
c:\windows\system32\_VOIDkedfbphxdt.dat
c:\windows\system32\_VOIDlmocqpaieq.dat
c:\windows\system32\_VOIDlowixgalau.dll
c:\windows\system32\_VOIDnbutpdienw.dll
c:\windows\system32\_VOIDnxtaaxidjv.dat
c:\windows\system32\_VOIDospeqvraft.dat
c:\windows\system32\_VOIDpeerqbotav.dll
c:\windows\system32\_VOIDrqciblaxel.dll
c:\windows\system32\_VOIDrvxfubeacx.dat
c:\windows\system32\_VOIDtevrxuenqf.dat
c:\windows\system32\_VOIDtikseeticr.dat
c:\windows\system32\_VOIDvcsegcpcua.dll
c:\windows\system32\_VOIDvpwtiqmivk.dat
c:\windows\system32\_VOIDwmqpqjxnlp.dll
c:\windows\system32\_VOIDwxorabuyrm.dll
c:\windows\system32\drivers\_VOIDipfyiqjimn.sys
c:\windows\system32\winlogon.bak

—– BITS: Possible infected sites —–

hxxp://download.yimg.com
.
((((((((((((((((((((((((((((((((((((((( Drivers/Services )))))))))))))))))))))))))))))))))))))))))))))))))
.

——-\Legacy__VOIDd.sys
——-\Service__VOIDnmdbdetuij
——-\Legacy__VOIDnmdbdetuij


((((((((((((((((((((((((( Files Created from 2010-03-10 to 2010-04-10 )))))))))))))))))))))))))))))))
.

2010-04-10 13:03 . 2010-03-29 23:46 38224 —-a-w- c:\windows\system32\drivers\mbamswissarmy.sys
2010-04-10 13:03 . 2010-03-29 23:45 20824 —-a-w- c:\windows\system32\drivers\mbam.sys
2010-04-10 01:00 . 2010-04-10 13:03 ——– d—–w- c:\program files\Malwarebytes' Anti-Malware
2010-04-10 00:51 . 2010-04-10 00:51 ——– d—–w- c:\documents and settings\P Compton\Application Data\AVG8
2010-04-10 00:21 . 2010-04-10 00:48 ——– d—–w- c:\program files\AVG
2010-04-09 15:39 . 2004-08-04 12:00 79872 -c–a-w- c:\windows\system32\dllcache\rwia330.dll
2010-04-09 15:38 . 2004-08-04 12:00 42496 -c–a-w- c:\windows\system32\dllcache\davcdata.exe
2010-04-09 15:34 . 2004-08-03 23:56 152576 —-a-w- c:\windows\system32\irftp.exe
2010-04-09 15:34 . 2004-08-03 23:56 8192 —-a-w- c:\windows\system32\wshirda.dll
2010-04-09 15:34 . 2004-08-03 23:56 27136 —-a-w- c:\windows\system32\irmon.dll
2010-04-09 15:34 . 2004-08-03 22:00 87424 —-a-w- c:\windows\system32\drivers\irda.sys
2010-04-09 15:27 . 2001-08-17 12:51 19584 —-a-w- c:\windows\system32\drivers\rasirda.sys
2010-04-09 12:54 . 2004-08-04 12:00 24661 -c–a-w- c:\windows\system32\dllcache\spxcoins.dll
2010-04-09 12:54 . 2004-08-04 12:00 24661 —-a-w- c:\windows\system32\spxcoins.dll
2010-04-09 12:54 . 2004-08-04 12:00 13312 -c–a-w- c:\windows\system32\dllcache\irclass.dll
2010-04-09 12:54 . 2004-08-04 12:00 13312 —-a-w- c:\windows\system32\irclass.dll
2010-04-09 11:55 . 2004-08-04 12:00 16384 -c–a-w- c:\windows\system32\dllcache\isignup.exe
2010-04-09 11:32 . 2010-04-09 11:32 ——– d-s—w- c:\windows\system32\config\systemprofile\History
2010-04-09 00:41 . 2010-04-09 00:41 664 —-a-w- c:\windows\system32\d3d9caps.dat
2010-04-09 00:41 . 2010-04-09 01:10 ——– d—–w- c:\documents and settings\NetworkService\Local Settings\Application Data\Adobe
2010-04-08 23:07 . 2010-04-08 23:07 71680 –sha-r- c:\windows\system32\kbdtuq5.dll
2010-04-08 18:15 . 2010-04-08 18:15 ——– d—–w- c:\documents and settings\All Users\Application Data\PC Drivers HeadQuarters
2010-04-03 16:07 . 2010-04-03 16:07 ——– d—–w- c:\documents and settings\All Users\Application Data\TVU Networks
2010-04-03 16:00 . 2010-04-03 16:00 ——– d—–w- c:\documents and settings\P Compton\Application Data\TVU Networks
2010-04-03 16:00 . 2010-04-03 16:07 ——– d—–w- c:\program files\TVUPlayer
2010-03-26 12:41 . 2010-03-26 12:41 ——– d—–w- c:\documents and settings\P Compton\Application Data\NCH Software
2010-03-26 12:40 . 2010-03-26 12:40 ——– d—–w- c:\documents and settings\All Users\Application Data\NCH Software

.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2010-04-10 00:53 . 2010-02-21 17:21 ——– d—–w- c:\documents and settings\All Users\Application Data\avg9
2010-04-09 21:22 . 2010-02-23 22:17 ——– d—–w- c:\documents and settings\P Compton\Application Data\vlc
2010-04-09 15:35 . 2007-11-20 15:36 23392 -c–a-w- c:\windows\system32\emptyregdb.dat
2010-04-09 01:00 . 2009-04-26 22:36 117760 —-a-w- c:\documents and settings\P Compton\Application Data\SUPERAntiSpyware.com\SUPERAntiSpyware\SDDLLS\UIREPAIR.DLL
2010-04-09 00:59 . 2009-04-26 22:35 ——– d—–w- c:\program files\SUPERAntiSpyware
2010-04-09 00:24 . 2008-02-03 21:59 ——– d—–w- c:\documents and settings\P Compton\Application Data\Azureus
2010-04-08 22:24 . 2010-02-21 23:07 ——– d—–w- c:\program files\Graboid
2010-04-07 17:21 . 2007-12-01 22:54 ——– d—–w- c:\documents and settings\All Users\Application Data\Yahoo! Companion
2010-03-22 19:29 . 2009-06-22 08:57 315736 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\threatwork.exe
2010-03-22 19:29 . 2009-06-22 08:57 25440 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\savapibridge.dll
2010-03-22 19:29 . 2009-06-22 08:57 173408 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\lavamessage.dll
2010-03-22 19:29 . 2009-06-22 08:57 15688 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\lsdelete.exe
2010-03-22 19:29 . 2009-06-22 08:57 350544 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\lavalicense.dll
2010-03-22 19:29 . 2009-06-22 08:57 303456 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\UpdateManager.dll
2010-03-22 19:29 . 2009-06-22 08:57 89952 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\ShellExt.dll
2010-03-22 19:29 . 2009-06-22 08:56 1630560 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\Resources.dll
2010-03-22 19:29 . 2009-06-22 08:56 45408 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\PrivacyClean.dll
2010-03-22 19:29 . 2009-06-22 08:56 254832 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\RPAPI.dll
2010-03-22 19:28 . 2009-09-23 13:29 3701760 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\AutoLaunch.exe
2010-03-22 19:28 . 2009-06-22 08:56 671592 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\CEAPI.dll
2010-03-22 19:28 . 2009-06-22 08:56 566648 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\Ad-AwareCommand.exe
2010-03-22 19:28 . 2009-06-22 08:56 567144 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\Ad-AwareAdmin.exe
2010-03-22 19:28 . 2009-06-22 08:56 2357064 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\Ad-Aware.exe
2010-03-22 19:28 . 2009-06-22 08:56 524632 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\AAWTray.exe
2010-03-22 19:28 . 2009-06-22 08:56 1029456 —-a-w- c:\documents and settings\All Users\Application Data\Lavasoft\Ad-Aware\Update\AAWService.exe
2010-03-22 19:25 . 2010-02-05 12:36 ——– d—–w- c:\documents and settings\All Users\Application Data\NCH Swift Sound
2010-03-22 19:16 . 2009-05-27 00:18 ——– d—–w- c:\documents and settings\P Compton\Application Data\Red Kawa
2010-03-22 10:25 . 2010-02-05 12:34 ——– d—–w- c:\documents and settings\P Compton\Application Data\NCH Swift Sound
2010-03-09 13:57 . 2010-03-09 13:57 ——– d—–w- c:\program files\H.264 Encoder
2010-02-21 23:57 . 2009-04-26 22:33 ——– d—a-w- c:\documents and settings\All Users\Application Data\TEMP
2010-02-13 19:05 . 2009-04-26 22:33 ——– d—–w- c:\program files\SpywareBlaster
2010-02-13 18:47 . 2010-02-13 18:47 ——– dc—-w- c:\documents and settings\All Users\Application Data\{BC9FCCF7-E686-494B-8C9B-55C9A39A7CA9}
2010-02-13 18:14 . 2010-02-13 18:14 ——– d—–w- c:\program files\iTunes
2010-02-13 18:14 . 2010-02-13 18:14 ——– d—–w- c:\program files\iPod
2010-02-13 18:14 . 2009-12-29 14:16 ——– d—–w- c:\program files\Common Files\Apple
2010-02-13 18:14 . 2010-02-13 18:14 ——– d—–w- c:\program files\Apple Software Update
2010-02-12 18:38 . 2007-11-20 15:51 99088 -c–a-w- c:\documents and settings\P Compton\Local Settings\Application Data\GDIPFONTCACHEV1.DAT
2010-02-10 18:18 . 2007-11-21 11:14 ——– d—–w- c:\program files\Common Files\Adobe
2010-02-05 12:37 . 2010-02-05 12:37 33848 —-a-w- c:\windows\system32\drivers\nchssvad.sys
2010-01-26 11:41 . 2009-12-18 10:34 52224 —-a-w- c:\documents and settings\P Compton\Application Data\SUPERAntiSpyware.com\SUPERAntiSpyware\SDDLLS\SD10005.dll
2010-01-22 19:51 . 2010-01-22 19:51 72488 —-a-w- c:\documents and settings\All Users\Application Data\Apple Computer\Installer Cache\iTunes 9.0.3.15\SetupAdmin.exe
2009-04-20 17:33 . 2007-11-30 17:38 2098 -csha-w- c:\windows\system32\KGyGaAvL.sys
.

((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SUPERAntiSpyware"="c:\program files\SUPERAntiSpyware\2c34bb8a-9201-41d5-8c90-500b2af1c301.exe" [2009-11-24 2001648]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"WinPatrol"="c:\program files\BillP Studios\WinPatrol\winpatrol.exe" [2007-10-26 292152]
"NvCplDaemon"="c:\windows\system32\NvCpl.dll" [2006-11-13 7585792]
"nwiz"="nwiz.exe" [2006-11-13 1519616]
"KTPWare"="c:\program files\Elantech\ktp.exe" [2009-01-14 512000]
"iTunesHelper"="c:\program files\iTunes\iTunesHelper.exe" [2010-01-22 141608]
"IMJPMIG8.1"="c:\windows\IME\imjp8_1\IMJPMIG.EXE" [2007-07-27 208952]
"SynTPEnh"="c:\program files\Synaptics\SynTP\SynTPEnh.exe" [2008-02-28 786521]
"RTHDCPL"="RTHDCPL.EXE" [2007-10-16 16855552]

[hkey_local_machine\software\microsoft\windows\currentversion\explorer\ShellExecuteHooks]
"{56F9679E-7826-4C84-81F3-532071A8BCC5}"= "c:\program files\Windows Desktop Search\MSNLNamespaceMgr.dll" [2009-05-24 304128]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\!SASWinLogon]
2009-09-09 10:39 548352 —-a-w- c:\program files\SUPERAntiSpyware\SASWINLO.DLL

[HKEY_LOCAL_MACHINE\system\currentcontrolset\control\session manager]
BootExecute REG_MULTI_SZ autocheck autochk /p \??\c:\0autocheck autochk *\0lsdelete\0sprestrt

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Lavasoft Ad-Aware Service]
@="Service"

[HKEY_LOCAL_MACHINE\software\microsoft\security center]
"AntiVirusOverride"=dword:00000001
"FirewallOverride"=dword:00000001

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile]
"EnableFirewall"= 0 (0x0)
"DisableNotifications"= 1 (0x1)

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"c:\\Program Files\\IVT Corporation\\BlueSoleil\\BlueSoleil.exe"=
"c:\\Program Files\\Yahoo!\\Messenger\\YahooMessenger.exe"=
"c:\\Program Files\\Messenger\\msmsgs.exe"=
"c:\\Program Files\\LimeWire\\LimeWire.exe"=
"c:\\Program Files\\Azureus\\Azureus.exe"=
"c:\\StubInstaller.exe"=
"c:\\Program Files\\TVAnts\\Tvants.exe"=
"c:\\Program Files\\SopCast\\adv\\SopAdver.exe"=
"c:\\Program Files\\SopCast\\SopCast.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\wlcsdk.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\msnmsgr.exe"=
"c:\\Program Files\\Bonjour\\mDNSResponder.exe"=
"c:\\Program Files\\iTunes\\iTunes.exe"=
"c:\\Program Files\\TVUPlayer\\TVUPlayer.exe"=

R0 Lbd;Lbd;c:\windows\system32\drivers\Lbd.sys [25/04/2009 09:56 64160]
R1 cdrblock;cdrblock;c:\windows\system32\drivers\cdrblock.sys [21/11/2007 12:45 20992]
R1 cdrport;cdrport;c:\windows\system32\drivers\cdrport.sys [21/11/2007 12:45 4608]
R1 SASDIFSV;SASDIFSV;c:\program files\SUPERAntiSpyware\sasdifsv.sys [23/03/2009 14:07 9968]
R1 SASKUTIL;SASKUTIL;c:\program files\SUPERAntiSpyware\SASKUTIL.SYS [23/03/2009 14:07 74480]
R2 Lavasoft Ad-Aware Service;Lavasoft Ad-Aware Service;c:\program files\Lavasoft\Ad-Aware\AAWService.exe [09/03/2009 20:06 1029456]
S3 MotDev;Motorola Inc. USB Device;c:\windows\system32\drivers\motodrv.sys [21/06/2008 20:05 42112]
S3 SASENUM;SASENUM;c:\program files\SUPERAntiSpyware\SASENUM.SYS [23/03/2009 14:07 7408]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost]
HPZ12 REG_MULTI_SZ Pml Driver HPZ12 Net Driver HPZ12
hpdevmgmt REG_MULTI_SZ hpqcxs08 hpqddsvc

[HKEY_LOCAL_MACHINE\software\microsoft\active setup\installed components\{A509B1FF-37FF-4bFF-8CFF-4F3A747040FF}]
2004-08-04 12:00 99840 —-a-w- c:\windows\system32\advpack.dll
.
Contents of the 'Scheduled Tasks' folder

2010-03-27 c:\windows\Tasks\Ad-Aware Update (Weekly).job
- c:\program files\Lavasoft\Ad-Aware\Ad-AwareAdmin.exe [2009-03-09 19:28]

2010-02-13 c:\windows\Tasks\AppleSoftwareUpdate.job
- c:\program files\Apple Software Update\SoftwareUpdate.exe [2008-07-30 12:34]

2010-02-05 c:\windows\Tasks\expressripSevenDays.job
- c:\program files\NCH Swift Sound\ExpressRip\expressrip.exe [2010-02-05 12:37]

2010-02-05 c:\windows\Tasks\expressripShakeIcon.job
- c:\program files\NCH Swift Sound\ExpressRip\expressrip.exe [2010-02-05 12:37]

2010-04-10 c:\windows\Tasks\RegCure Program Check.job
- c:\program files\RegCure\RegCure.exe [2007-10-16 08:20]

2010-01-14 c:\windows\Tasks\RegCure.job
- c:\program files\RegCure\RegCure.exe [2007-10-16 08:20]
.
.
——- Supplementary Scan ——-
.
uStart Page = hxxp://uk.yahoo.com/
uInternet Settings,ProxyOverride = ;*.local
uSearchURL,(Default) = hxxp://uk.rd.yahoo.com/customize/ie/defaults/su/msgr8/*http://uk.search.yahoo.com
IE: E&xport to Microsoft Excel - c:\progra~1\MICROS~2\Office10\EXCEL.EXE/3000
.
- - - - ORPHANS REMOVED - - - -

Toolbar-{CCC7A320-B3CA-4199-B1A6-9F516DD69829} - (no file)
WebBrowser-{CCC7A320-B3CA-4199-B1A6-9F516DD69829} - (no file)
ShellExecuteHooks-{5AE067D3-9AFB-48E0-853A-EBB7F4A000DA} - (no file)


**************************************************************************

catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net
Rootkit scan 2010-04-10 15:06
Windows 5.1.2600 Service Pack 2 NTFS

scanning hidden processes …

scanning hidden autostart entries …

scanning hidden files …

scan completed successfully
hidden files: 0

**************************************************************************
.
——————— DLLs Loaded Under Running Processes ———————

- - - - - - - > 'winlogon.exe'(996)
c:\program files\SUPERAntiSpyware\SASWINLO.DLL
.
Completion time: 2010-04-10 15:07:55
ComboFix-quarantined-files.txt 2010-04-10 14:07

Pre-Run: 16,584,249,344 bytes free
Post-Run: 17,759,907,840 bytes free

Current=9 Default=9 Failed=8 LastKnownGood=10 Sets=3,4,5,6,7,8,9,10
- - End Of File - - B79F7E05CF624590D28A3B302ECB8BF6


2010-05-24 17:28:54 . 2010-05-24 17:28:54 156 —-a-w- C:\Qoobox\Quarantine\Registry_backups\HKLM-Run-PHIME2002A.reg.dat
2010-05-24 17:28:54 . 2010-05-24 17:28:54 157 —-a-w- C:\Qoobox\Quarantine\Registry_backups\HKLM-Run-PHIME2002ASync.reg.dat
2010-05-24 17:28:54 . 2010-05-24 17:28:54 151 —-a-w- C:\Qoobox\Quarantine\Registry_backups\HKLM-Run-MSPY2002.reg.dat
2010-05-24 17:28:53 . 2010-05-24 17:28:53 171 —-a-w- C:\Qoobox\Quarantine\Registry_backups\WebBrowser-{CCC7A320-B3CA-4199-B1A6-9F516DD69829}.reg.dat
2010-05-24 17:28:52 . 2010-05-24 17:28:52 213 —-a-w- C:\Qoobox\Quarantine\Registry_backups\Toolbar-{CCC7A320-B3CA-4199-B1A6-9F516DD69829}.reg.dat
2010-05-24 17:26:59 . 2010-05-24 17:26:59 12,364 —-a-w- C:\Qoobox\Quarantine\Registry_backups\tcpip.reg
2010-05-24 17:16:16 . 2010-05-24 17:16:16 51 —-a-w- C:\Qoobox\Quarantine\catchme.log
2004-08-04 12:00:00 . 2004-08-04 12:00:00 502,272 —-a-w- C:\Qoobox\Quarantine\C\WINDOWS\system32\winlogon.bak.vir


32 Bit HP CIO Components Installer
7-Zip 4.57
Ad-Aware
Adobe After Effects CS4
Adobe After Effects CS4 Presets
Adobe After Effects CS4 Third Party Content
Adobe AIR
Adobe Anchor Service CS4
Adobe Bridge CS4
Adobe CMaps CS4
Adobe Color Video Profiles AE CS4
Adobe Default Language CS4
Adobe Device Central CS4
Adobe Dynamiclink Support
Adobe ExtendScript Toolkit CS4
Adobe Extension Manager CS4
Adobe Flash Player 10 ActiveX
Adobe Flash Player 10 Plugin
Adobe Fonts All
Adobe Media Encoder CS4
Adobe Media Encoder CS4 Additional Exporter
Adobe Media Encoder CS4 Exporter
Adobe Media Encoder CS4 Importer
Adobe Media Player
Adobe MotionPicture Color Files CS4
Adobe MPEG Encoder
Adobe Output Module
Adobe PDF Library Files CS4
Adobe Photoshop 7.0
Adobe Premiere 6.5
Adobe Reader 8.2.2
Adobe Setup
Adobe Shockwave Player 11.5
Adobe Type Support CS4
Adobe Update Manager CS4
Adobe XMP Panels CS4
AdobeColorCommonSetRGB
Apple Application Support
Apple Mobile Device Support
Apple Software Update
ArcSoft TotalMedia
Ask Toolbar
ATI - Software Uninstall Utility
ATI Catalyst Control Center
ATI Display Driver
AudioCatalyst
Audioro iPod Converter 1.01
AVG Free 9.0
AviSynth 2.5
BCC AE Swish Pan 6
BisonCam
BlueSoleil
Bonjour
Boris Continuum Complete AE 6
BPD_Scan
BPDSoftware
BPDSoftware_Ini
BufferChm
CamStudio
Canopus Codec Option
Canopus GXF SpeedEncoder 1.3
Canopus ProCoder 2
Canopus ProCoder Express For EDIUS
Compatibility Pack for the 2007 Office system
Destinations
DeviceManagementQFolder
DocProc
DocProcQFolder
EDIUS Core
EDIUS4 Settings
EDIUS4(SetupManager)
EDIUS4(XplodePro)
eSupportQFolder
Express Rip
Factory for Adobe Premiere
Fax
Final Effects for Adobe Premiere
GRF LTD for Adobe Premiere
H.264 Encoder 1.5
HDAUDIO Soft Data Fax Modem with SmartCP
HijackThis 2.0.2
Hotfix for Microsoft .NET Framework 3.0 (KB932471)
Hotfix for Microsoft .NET Framework 3.5 SP1 (KB953595)
Hotfix for Microsoft .NET Framework 3.5 SP1 (KB958484)
HP Imaging Device Functions 8.0
HP OCR Software 8.0
HP Officejet J3600 Series
HP Solution Center 8.0
HPProductAssistant
iTunes
Java DB 10.4.1.3
Java™ 6 Update 13
Java™ SE Development Kit 6 Update 13
JavaFX™ 1.1 SDK
Juicer 3.58
Junk Mail filter update
KTP Ware PS/2-WDM 5.0.1.9
LimeWire PRO 4.12.6
Logitech Desktop Messenger
Logitech IM Video Companion
Logitech ImageStudio
Malwarebytes' Anti-Malware
Microsoft .NET Framework 1.1
Microsoft .NET Framework 1.1 Security Update (KB953297)
Microsoft .NET Framework 2.0 Service Pack 2
Microsoft .NET Framework 3.0 Service Pack 2
Microsoft .NET Framework 3.5 SP1
Microsoft Application Error Reporting
Microsoft Choice Guard
Microsoft Compression Client Pack 1.0 for Windows XP
Microsoft Internationalized Domain Names Mitigation APIs
Microsoft National Language Support Downlevel APIs
Microsoft Office XP Professional
Microsoft Silverlight
Microsoft Visual C++ 2005 Redistributable
MobileMe Control Panel
MP3 CD Converter 4.20
MPEGcapture
MSN
MSVCRT
MSXML 4.0 SP2 (KB927978)
MSXML 4.0 SP2 (KB936181)
MSXML 4.0 SP2 (KB954430)
MSXML 4.0 SP2 (KB973688)
MSXML 6 Service Pack 2 (KB973686)
Multimedia / Internet Keyboard Driver VerR8.16
Nero 7 Essentials
neroxml
NewBlue Free Effects for Windows
OGA Notifier 2.0.0048.0
Photoshop Camera Raw
Pixel Bender Toolkit
Pixillion Image Converter
PowerDVD
Prism Video Converter
ProCoder 3
QuickTime
REALTEK Gigabit and Fast Ethernet NIC Driver
Realtek High Definition Audio Driver
RecordPad Sound Recorder
RegCure
Remove DivX Pro Codec
Safari
Scan
Security Update for Windows XP (KB923789)
Segoe UI
Setup
simplewebhosting.co.uk Desktop
SmartSound Quicktracks for Premiere 6.5
SolutionCenter
Sonic Foundry Sound Forge 6.0b
SopCast 3.2.9
SoundTap Streaming Audio Recorder
SpywareBlaster 4.2
Status
Suite Shared Configuration CS4
SUPERAntiSpyware Free Edition
Switch Sound File Converter
Synaptics Pointing Device Driver
T_Caustic for After Effects
TC Native Essentials 2.02
Texas Instruments PCIxx21/x515/xx12 drivers.
TIPCI
TomTom HOME 2.5.2.60
Toolbox
TrayApp
TVAnts 1.0
TVUPlayer 2.5.2.2
Tweak UI
Update for Microsoft .NET Framework 3.5 SP1 (KB963707)
VC_MergeModuleToMSI
VideoLAN VLC media player 0.8.6d
Videora iPod Converter 4.07
Visual C++ 2008 x86 Runtime - (v9.0.30729)
Visual C++ 2008 x86 Runtime - v9.0.30729.01
Vuze
Vuze_Remote Toolbar
WavePad Sound Editor
WebFldrs XP
WebReg
Windows Genuine Advantage Notifications (KB905474)
Windows Genuine Advantage Validation Tool (KB892130)
Windows Internet Explorer 7
Windows Live Call
Windows Live Communications Platform
Windows Live Essentials
Windows Live Mail
Windows Live Messenger
Windows Live Sign-in Assistant
Windows Live Upload Tool
Windows Media Format 11 runtime
Windows Media Player 11
Windows Presentation Foundation
WinPatrol 2007
WinRAR archiver
WinZip 12.1
XingMP3 Player
XML Paper Specification Shared Components Pack 1.0
Xvid 1.2.2 final uninstall
Yahoo! Extras
Yahoo! Install Manager
Yahoo! Internet Mail
Yahoo! Messenger
Yahoo! Software Update
Yahoo! Toolbar
YouTube Downloader App 1.02
YouTube Uploader


thats all i shall now get on with second part youve asked me to do
r phil c
hi catbyte,
Thanks for your patience when helping me its very much appreciated
here is the combofix log generated after i added that text to it .


ComboFix 10-05-23.08 - P Compton 24/05/2010 19:51:17.5.2 - x86
Microsoft Windows XP Professional 5.1.2600.3.1252.44.1033.18.3070.2423 [GMT 1:00]
Running from: c:\documents and settings\[removed]\Desktop\ComboFix.exe
Command switches used :: c:\documents and settings\P Compton\Desktop\CFSCRIPT.txt
AV: AVG Anti-Virus Free *On-access scanning disabled* (Updated) {17DDD097-36FF-435F-9E1B-52D74245D6BF}
.

((((((((((((((((((((((((( Files Created from 2010-04-24 to 2010-05-24 )))))))))))))))))))))))))))))))
.

2010-05-20 22:15 . 2009-08-06 18:24 44768 —-a-w- c:\windows\system32\wups2.dll
2010-05-20 22:13 . 2010-05-20 22:13 ——– d—–w- c:\documents and settings\P Compton\Application Data\AVG9
2010-05-20 21:18 . 2008-04-14 04:42 151552 —-a-w- c:\windows\system32\irftp.exe
2010-05-20 21:18 . 2008-04-14 04:42 8192 —-a-w- c:\windows\system32\wshirda.dll
2010-05-20 21:18 . 2008-04-14 04:41 28160 —-a-w- c:\windows\system32\irmon.dll
2010-05-20 21:18 . 2008-04-13 23:24 88192 —-a-w- c:\windows\system32\drivers\irda.sys
2010-05-20 20:47 . 2001-08-17 12:51 19584 —-a-w- c:\windows\system32\drivers\rasirda.sys
2010-05-20 20:40 . 2008-04-14 12:00 24661 -c–a-w- c:\windows\system32\dllcache\spxcoins.dll
2010-05-20 20:40 . 2008-04-14 12:00 24661 —-a-w- c:\windows\system32\spxcoins.dll
2010-05-20 20:40 . 2008-04-14 12:00 13312 -c–a-w- c:\windows\system32\dllcache\irclass.dll
2010-05-20 20:40 . 2008-04-14 12:00 13312 —-a-w- c:\windows\system32\irclass.dll
2010-05-20 17:38 . 2008-04-14 12:00 39936 -c–a-w- c:\windows\system32\dllcache\hostmib.dll
2010-05-20 17:38 . 2008-04-14 12:00 39936 —-a-w- c:\windows\system32\hostmib.dll
2010-05-20 17:38 . 2010-05-20 17:38 ——– d—–w- C:\Inetpub
2010-05-20 17:15 . 2008-04-14 12:00 6144 -c–a-w- c:\windows\system32\dllcache\snmpmib.dll
2010-05-20 17:15 . 2008-04-14 12:00 6144 —-a-w- c:\windows\system32\snmpmib.dll
2010-05-19 09:08 . 2010-05-19 09:08 ——– d—–w- c:\documents and settings\P Compton\Local Settings\Application Data\ATI
2010-05-19 09:08 . 2010-05-19 09:08 ——– d—–w- c:\documents and settings\P Compton\Application Data\ATI
2010-05-19 09:08 . 2010-05-19 09:08 132 —-a-w- c:\documents and settings\P Compton\Local Settings\Application Data\fusioncache.dat
2010-05-19 09:04 . 2010-05-19 09:04 ——– d—–w- c:\program files\ATI Technologies
2010-05-19 08:55 . 2006-11-13 10:13 5144576 —-a-w- c:\windows\system32\atioglxx.dll
2010-05-19 08:55 . 2006-11-13 10:13 307200 —-a-w- c:\windows\system32\atiiiexx.dll
2010-05-19 08:55 . 2006-11-13 10:13 303104 —-a-w- c:\windows\system32\ATIDEMGR.dll
2010-05-19 08:55 . 2006-11-13 10:13 2515656 —-a-w- c:\windows\system32\ativvaxx.dat
2010-05-19 08:55 . 2006-11-13 10:13 221184 —-a-w- c:\windows\system32\atikvmag.dll
2010-05-19 08:55 . 2006-11-13 10:13 17408 —-a-w- c:\windows\system32\atitvo32.dll
2010-05-19 08:55 . 2006-11-13 10:13 136650 —-a-w- c:\windows\system32\atiicdxx.dat
2010-05-19 08:55 . 2006-11-13 10:13 90112 —-a-w- c:\windows\system32\ati2evxx.dll
2010-05-19 08:55 . 2006-11-13 10:13 49152 —-a-w- c:\windows\system32\drivers\ati2erec.dll
2010-05-19 08:55 . 2006-11-13 10:13 425984 —-a-w- c:\windows\system32\ati2evxx.exe
2010-05-19 08:55 . 2006-11-13 10:13 41984 —-a-w- c:\windows\system32\ati2edxx.dll
2010-05-19 08:55 . 2006-11-13 10:13 26112 —-a-w- c:\windows\system32\Ati2mdxx.exe
2010-05-14 10:28 . 2010-05-14 12:01 ——– d—–w- c:\program files\CamStudio
2010-05-14 10:06 . 2010-05-20 11:02 ——– d—–w- c:\program files\NirSoft
2010-05-12 09:23 . 2010-05-12 09:23 ——– d—–w- C:\found.000
2010-05-08 16:20 . 2010-05-08 16:20 ——– d—–w- c:\documents and settings\All Users\Application Data\Office Genuine Advantage
2010-05-05 11:47 . 2010-05-05 11:47 ——– d—–w- c:\documents and settings\P Compton\Application Data\Office Genuine Advantage
2010-04-27 10:05 . 2006-11-13 03:12 69632 —-a-w- c:\windows\ALCMTR.EXE
2010-04-26 21:17 . 2010-05-20 15:38 ——– d—–w- c:\windows\system32\wbem\Repository

.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2010-05-24 15:20 . 2010-02-23 22:17 ——– d—–w- c:\documents and settings\P Compton\Application Data\vlc
2010-05-24 10:56 . 2008-02-03 21:59 ——– d—–w- c:\documents and settings\P Compton\Application Data\Azureus
2010-05-20 21:27 . 2007-11-20 15:36 23392 -c–a-w- c:\windows\system32\emptyregdb.dat
2010-05-20 17:54 . 2010-02-21 17:21 ——– d—–w- c:\documents and settings\All Users\Application Data\avg9
2010-05-19 09:04 . 2007-11-21 10:41 ——– d–h–w- c:\program files\InstallShield Installation Information
2010-05-12 10:16 . 2010-04-13 11:35 ——– d—–w- c:\program files\Vuze_Remote
2010-05-05 16:50 . 2009-04-26 22:36 117760 —-a-w- c:\documents and settings\P Compton\Application Data\SUPERAntiSpyware.com\SUPERAntiSpyware\SDDLLS\UIREPAIR.DLL
2010-04-27 10:05 . 2007-11-21 11:15 ——– d—–w- c:\program files\Realtek
2010-04-21 16:25 . 2010-04-10 16:01 242896 —-a-w- c:\windows\system32\drivers\avgtdix.sys
2010-04-16 18:23 . 2008-09-07 15:19 ——– d—–w- c:\documents and settings\P Compton\Application Data\dvdcss
2010-04-14 21:21 . 2009-01-13 22:11 ——– d—–w- c:\program files\SopCast
2010-04-14 21:21 . 2010-04-14 21:21 ——– d—–w- c:\program files\Ask.com
2010-04-13 19:59 . 2010-04-03 16:00 ——– d—–w- c:\program files\TVUPlayer
2010-04-13 11:36 . 2008-02-03 21:58 ——– d—–w- c:\program files\Azureus
2010-04-13 11:35 . 2010-04-13 11:35 52224 —-a-w- c:\documents and settings\P Compton\Application Data\Mozilla\Firefox\Profiles\jorb9q2r.default\extensions\{ba14329e-9550-4989-b3f2-9732e92d17cc}\components\FFExternalAlert.dll
2010-04-13 11:35 . 2010-04-13 11:35 101376 —-a-w- c:\documents and settings\P Compton\Application Data\Mozilla\Firefox\Profiles\jorb9q2r.default\extensions\{ba14329e-9550-4989-b3f2-9732e92d17cc}\components\RadioWMPCore.dll
2010-04-13 11:35 . 2010-04-13 11:35 ——– d—–w- c:\program files\Conduit
2010-04-12 00:29 . 2010-02-05 12:36 ——– d—–w- c:\documents and settings\All Users\Application Data\NCH Swift Sound
2010-04-11 19:06 . 2010-04-11 19:05 ——– d—–w- c:\program files\iTunes
2010-04-11 19:06 . 2010-04-11 19:05 ——– d—–w- c:\documents and settings\All Users\Application Data\{429CAD59-35B1-4DBC-BB6D-1DB246563521}
2010-04-11 19:05 . 2010-04-11 19:05 ——– d—–w- c:\program files\iPod
2010-04-11 19:05 . 2009-12-29 14:16 ——– d—–w- c:\program files\Common Files\Apple
2010-04-11 19:01 . 2009-07-28 13:01 ——– d—–w- c:\program files\QuickTime
2010-04-11 18:57 . 2010-04-11 18:57 ——– d—–w- c:\program files\Bonjour
2010-04-11 18:44 . 2010-04-11 18:44 73000 —-a-w- c:\documents and settings\All Users\Application Data\Apple Computer\Installer Cache\iTunes 9.1.0.79\SetupAdmin.exe
2010-04-11 18:20 . 2010-04-11 18:20 ——– d—–w- c:\program files\Safari
2010-04-11 18:17 . 2010-04-11 18:17 79144 —-a-w- c:\documents and settings\All Users\Application Data\Apple Computer\Installer Cache\Safari 5.31.22.7\SetupAdmin.exe
2010-04-10 17:33 . 2010-04-10 17:33 ——– d—–w- c:\program files\MSXML 6.0
2010-04-10 16:01 . 2010-04-10 16:01 12464 —-a-w- c:\windows\system32\avgrsstx.dll
2010-04-10 16:01 . 2010-04-10 16:01 216200 —-a-w- c:\windows\system32\drivers\avgldx86.sys
2010-04-10 16:01 . 2010-04-10 16:01 29512 —-a-w- c:\windows\system32\drivers\avgmfx86.sys
2010-04-10 13:03 . 2010-04-10 01:00 ——– d—–w- c:\program files\Malwarebytes' Anti-Malware
2010-04-10 00:48 . 2010-04-10 00:21 ——– d—–w- c:\program files\AVG
2010-04-09 00:59 . 2009-04-26 22:35 ——– d—–w- c:\program files\SUPERAntiSpyware
2010-04-09 00:41 . 2010-04-09 00:41 664 —-a-w- c:\windows\system32\d3d9caps.dat
2010-04-08 23:07 . 2010-04-08 23:07 71680 –sha-r- c:\windows\system32\kbdtuq5.dll
2010-04-08 18:15 . 2010-04-08 18:15 ——– d—–w- c:\documents and settings\All Users\Application Data\PC Drivers HeadQuarters
2010-04-07 17:21 . 2007-12-01 22:54 ——– d—–w- c:\documents and settings\All Users\Application Data\Yahoo! Companion
2010-04-03 16:07 . 2010-04-03 16:07 ——– d—–w- c:\documents and settings\All Users\Application Data\TVU Networks
2010-04-03 16:00 . 2010-04-03 16:00 ——– d—–w- c:\documents and settings\P Compton\Application Data\TVU Networks
2010-03-29 23:46 . 2010-04-10 13:03 38224 —-a-w- c:\windows\system32\drivers\mbamswissarmy.sys
2010-03-29 23:45 . 2010-04-10 13:03 20824 —-a-w- c:\windows\system32\drivers\mbam.sys
2010-03-26 12:41 . 2010-03-26 12:41 ——– d—–w- c:\documents and settings\P Compton\Application Data\NCH Software
2010-03-26 12:40 . 2010-03-26 12:40 ——– d—–w- c:\documents and settings\All Users\Application Data\NCH Software
2009-04-20 17:33 . 2007-11-30 17:38 2098 -csha-w- c:\windows\system32\KGyGaAvL.sys
.

((((((((((((((((((((((((((((( SnapShot@2010-05-24_17.28.05 )))))))))))))))))))))))))))))))))))))))))
.
+ 2010-05-24 18:55 . 2010-05-24 18:55 16384 c:\windows\Temp\Perflib_Perfdata_274.dat
.
((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4

[HKEY_LOCAL_MACHINE\~\Browser Helper Objects\{ba14329e-9550-4989-b3f2-9732e92d17cc}]
2010-05-12 10:16 2515552 —-a-w- c:\program files\Vuze_Remote\tbVuz1.dll

[HKEY_LOCAL_MACHINE\~\Browser Helper Objects\{D4027C7F-154A-4066-A1AD-4243D8127440}]
2010-02-04 15:50 1197448 —-a-w- c:\program files\Ask.com\GenericAskToolbar.dll

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Internet Explorer\Toolbar]
"{ba14329e-9550-4989-b3f2-9732e92d17cc}"= "c:\program files\Vuze_Remote\tbVuz1.dll" [2010-05-12 2515552]
"{D4027C7F-154A-4066-A1AD-4243D8127440}"= "c:\program files\Ask.com\GenericAskToolbar.dll" [2010-02-04 1197448]

[HKEY_CLASSES_ROOT\clsid\{ba14329e-9550-4989-b3f2-9732e92d17cc}]

[HKEY_CLASSES_ROOT\clsid\{d4027c7f-154a-4066-a1ad-4243d8127440}]
[HKEY_CLASSES_ROOT\GenericAskToolbar.ToolbarWnd.1]
[HKEY_CLASSES_ROOT\TypeLib\{2996F0E7-292B-4CAE-893F-47B8B1C05B56}]
[HKEY_CLASSES_ROOT\GenericAskToolbar.ToolbarWnd]

[HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Toolbar\Webbrowser]
"{BA14329E-9550-4989-B3F2-9732E92D17CC}"= "c:\program files\Vuze_Remote\tbVuz1.dll" [2010-05-12 2515552]
"{D4027C7F-154A-4066-A1AD-4243D8127440}"= "c:\program files\Ask.com\GenericAskToolbar.dll" [2010-02-04 1197448]

[HKEY_CLASSES_ROOT\clsid\{ba14329e-9550-4989-b3f2-9732e92d17cc}]

[HKEY_CLASSES_ROOT\clsid\{d4027c7f-154a-4066-a1ad-4243d8127440}]
[HKEY_CLASSES_ROOT\GenericAskToolbar.ToolbarWnd.1]
[HKEY_CLASSES_ROOT\TypeLib\{2996F0E7-292B-4CAE-893F-47B8B1C05B56}]
[HKEY_CLASSES_ROOT\GenericAskToolbar.ToolbarWnd]

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SUPERAntiSpyware"="c:\program files\SUPERAntiSpyware\2c34bb8a-9201-41d5-8c90-500b2af1c301.exe" [2009-11-24 2001648]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"WinPatrol"="c:\program files\BillP Studios\WinPatrol\winpatrol.exe" [2007-10-26 292152]
"KTPWare"="c:\program files\Elantech\ktp.exe" [2009-01-14 512000]
"IMJPMIG8.1"="c:\windows\IME\imjp8_1\IMJPMIG.EXE" [2007-07-27 208952]
"SynTPEnh"="c:\program files\Synaptics\SynTP\SynTPEnh.exe" [2008-02-28 786521]
"AppleSyncNotifier"="c:\program files\Common Files\Apple\Mobile Device Support\AppleSyncNotifier.exe" [2010-03-16 47392]
"iTunesHelper"="c:\program files\iTunes\iTunesHelper.exe" [2010-03-26 142120]
"Adobe ARM"="c:\program files\Common Files\Adobe\ARM\1.0\AdobeARM.exe" [2010-03-24 952768]
"BluetoothAuthenticationAgent"="bthprops.cpl" [2008-04-14 110592]
"ATICCC"="c:\program files\ATI Technologies\ATI.ACE\CLIStart.exe" [2006-05-10 90112]
"RTHDCPL"="RTHDCPL.EXE" [2007-10-16 16855552]

[HKEY_USERS\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\RunOnce]
"tscuninstall"="c:\windows\system32\tscupgrd.exe" [2007-07-27 44544]

[hkey_local_machine\software\microsoft\windows\currentversion\explorer\ShellExecuteHooks]
"{56F9679E-7826-4C84-81F3-532071A8BCC5}"= "c:\program files\Windows Desktop Search\MSNLNamespaceMgr.dll" [2009-05-24 304128]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\!SASWinLogon]
2009-09-09 10:39 548352 —-a-w- c:\program files\SUPERAntiSpyware\SASWINLO.DLL

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\avgrsstarter]
2010-04-10 16:01 12464 —-a-w- c:\windows\system32\avgrsstx.dll

[HKEY_LOCAL_MACHINE\system\currentcontrolset\control\session manager]
BootExecute REG_MULTI_SZ autocheck autochk *\0lsdelete\0sprestrt

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Lavasoft Ad-Aware Service]
@="Service"

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Adobe Reader Speed Launcher]
2010-04-02 18:05 40368 —-a-w- c:\program files\Adobe\Reader 8.0\Reader\reader_sl.exe

[HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\QuickTime Task]
2010-03-17 20:53 421888 —-a-w- c:\program files\QuickTime\QTTask.exe

[HKEY_LOCAL_MACHINE\software\microsoft\security center]
"AntiVirusOverride"=dword:00000001
"FirewallOverride"=dword:00000001

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile]
"DisableNotifications"= 1 (0x1)

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"c:\\Program Files\\IVT Corporation\\BlueSoleil\\BlueSoleil.exe"=
"c:\\Program Files\\Yahoo!\\Messenger\\YahooMessenger.exe"=
"c:\\Program Files\\Messenger\\msmsgs.exe"=
"c:\\Program Files\\LimeWire\\LimeWire.exe"=
"c:\\StubInstaller.exe"=
"c:\\Program Files\\TVAnts\\Tvants.exe"=
"c:\\Program Files\\SopCast\\adv\\SopAdver.exe"=
"c:\\Program Files\\SopCast\\SopCast.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\wlcsdk.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\msnmsgr.exe"=
"c:\\Program Files\\TVUPlayer\\TVUPlayer.exe"=
"c:\\Program Files\\AVG\\AVG9\\avgemc.exe"=
"c:\\Program Files\\AVG\\AVG9\\avgupd.exe"=
"c:\\Program Files\\AVG\\AVG9\\avgnsx.exe"=
"c:\\Program Files\\Bonjour\\mDNSResponder.exe"=
"c:\\Program Files\\iTunes\\iTunes.exe"=
"c:\\Program Files\\Azureus\\Azureus.exe"=

R0 Lbd;Lbd;c:\windows\system32\drivers\Lbd.sys [4/25/2009 9:56 AM 64160]
R1 AvgLdx86;AVG Free AVI Loader Driver x86;c:\windows\system32\drivers\avgldx86.sys [4/10/2010 5:01 PM 216200]
R1 AvgTdiX;AVG Free Network Redirector;c:\windows\system32\drivers\avgtdix.sys [4/10/2010 5:01 PM 242896]
R1 cdrblock;cdrblock;c:\windows\system32\drivers\cdrblock.sys [11/21/2007 12:45 PM 20992]
R1 cdrport;cdrport;c:\windows\system32\drivers\cdrport.sys [11/21/2007 12:45 PM 4608]
R1 SASDIFSV;SASDIFSV;c:\program files\SUPERAntiSpyware\sasdifsv.sys [3/23/2009 2:07 PM 9968]
R1 SASKUTIL;SASKUTIL;c:\program files\SUPERAntiSpyware\SASKUTIL.SYS [3/23/2009 2:07 PM 74480]
R2 avg9emc;AVG Free E-mail Scanner;c:\program files\AVG\AVG9\avgemc.exe [4/10/2010 5:00 PM 916760]
R2 avg9wd;AVG Free WatchDog;c:\program files\AVG\AVG9\avgwdsvc.exe [4/10/2010 5:00 PM 308064]
R2 Lavasoft Ad-Aware Service;Lavasoft Ad-Aware Service;c:\program files\Lavasoft\Ad-Aware\AAWService.exe [3/9/2009 8:06 PM 1029456]
R3 SASENUM;SASENUM;c:\program files\SUPERAntiSpyware\SASENUM.SYS [3/23/2009 2:07 PM 7408]
S2 AutoExNT;AutoExNT;c:\windows\system32\Autoexnt.exe [4/10/2010 6:21 PM 5904]
S3 MotDev;Motorola Inc. USB Device;c:\windows\system32\drivers\motodrv.sys [6/21/2008 8:05 PM 42112]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost]
HPZ12 REG_MULTI_SZ Pml Driver HPZ12 Net Driver HPZ12
hpdevmgmt REG_MULTI_SZ hpqcxs08 hpqddsvc

[HKEY_LOCAL_MACHINE\software\microsoft\active setup\installed components\{A509B1FF-37FF-4bFF-8CFF-4F3A747040FF}]
2007-08-13 17:39 123904 —-a-w- c:\windows\system32\advpack.dll
.
Contents of the 'Scheduled Tasks' folder

2010-05-24 c:\windows\Tasks\Ad-Aware Update (Weekly).job
- c:\program files\Lavasoft\Ad-Aware\Ad-AwareAdmin.exe [2009-03-09 19:28]

2010-05-20 c:\windows\Tasks\AppleSoftwareUpdate.job
- c:\program files\Apple Software Update\SoftwareUpdate.exe [2008-07-30 12:34]

2010-04-12 c:\windows\Tasks\expressripShakeIcon.job
- c:\program files\NCH Swift Sound\ExpressRip\expressrip.exe [2010-02-05 12:37]

2010-05-24 c:\windows\Tasks\OGALogon.job
- c:\windows\system32\OGAEXEC.exe [2009-08-03 14:07]

2010-05-24 c:\windows\Tasks\RegCure Program Check.job
- c:\program files\RegCure\RegCure.exe [2007-10-16 08:20]

2010-05-20 c:\windows\Tasks\RegCure.job
- c:\program files\RegCure\RegCure.exe [2007-10-16 08:20]

2010-05-24 c:\windows\Tasks\Scheduled Update for Ask Toolbar.job
- c:\program files\Ask.com\UpdateTask.exe [2010-02-04 15:50]
.
.
——- Supplementary Scan ——-
.
uStart Page = hxxp://uk.yahoo.com/
uInternet Settings,ProxyOverride = ;*.local
uSearchURL,(Default) = hxxp://uk.rd.yahoo.com/customize/ie/defaults/su/msgr8/*http://uk.search.yahoo.com
.

**************************************************************************

catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net
Rootkit scan 2010-05-24 19:57
Windows 5.1.2600 Service Pack 3 NTFS

scanning hidden processes …

scanning hidden autostart entries …

scanning hidden files …

scan completed successfully
hidden files: 0

**************************************************************************
.
——————— DLLs Loaded Under Running Processes ———————

- - - - - - - > 'winlogon.exe'(800)
c:\program files\SUPERAntiSpyware\SASWINLO.DLL
c:\windows\system32\Ati2evxx.dll

- - - - - - - > 'explorer.exe'(2580)
c:\windows\system32\ieframe.dll
c:\windows\system32\WPDShServiceObj.dll
c:\windows\system32\PortableDeviceTypes.dll
c:\windows\system32\PortableDeviceApi.dll
.
———————— Other Running Processes ————————
.
c:\windows\system32\Ati2evxx.exe
c:\program files\AVG\AVG9\avgchsvx.exe
c:\program files\AVG\AVG9\avgrsx.exe
c:\program files\AVG\AVG9\avgcsrvx.exe
c:\program files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
c:\program files\IVT Corporation\BlueSoleil\BTNtService.exe
c:\program files\Bonjour\mDNSResponder.exe
c:\program files\Java\jre6\bin\jqs.exe
c:\program files\AVG\AVG9\avgnsx.exe
c:\windows\system32\SearchIndexer.exe
c:\windows\system32\rundll32.exe
c:\windows\RTHDCPL.EXE
c:\program files\ATI Technologies\ATI.ACE\CLI.EXE
c:\program files\Yahoo!\SoftwareUpdate\YahooAUService.exe
c:\program files\AVG\AVG9\avgcsrvx.exe
c:\program files\iPod\bin\iPodService.exe
c:\program files\ATI Technologies\ATI.ACE\cli.exe
c:\windows\system32\SearchProtocolHost.exe
c:\windows\system32\SearchFilterHost.exe
.
**************************************************************************
.
Completion time: 2010-05-24 20:01:39 - machine was rebooted
ComboFix-quarantined-files.txt 2010-05-24 19:01
ComboFix2.txt 2010-05-24 17:29
ComboFix3.txt 2010-04-10 14:07

Pre-Run: 14,424,793,088 bytes free
Post-Run: 14,383,828,992 bytes free

- - End Of File - - 5A0E045559EF1C96F8FB3A7C5D071B35
Hi,

Please do the following:

  • Please open your MalwareBytes AntiMalware Program
  • Click the Update Tab and search for updates
  • If an update is found, it will download and install the latest version.
  • Once the program has loaded, select "Perform Quick Scan", then click Scan.
  • The scan may take some time to finish, so please be patient.
  • When the scan is complete, click OK, then Show Results to view the results.
  • Make sure that everything is checked, and click Remove Selected. <– very important
  • When disinfection is completed, a log will open in Notepad and you may be prompted to Restart. (See Extra Note)
  • The log is automatically saved by MBAM and can be viewed by clicking the Logs tab in MBAM.
  • Copy&Paste the entire report in your next reply.

Extra Note:If MBAM encounters a file that is difficult to remove, you will be presented with 1 of 2 prompts, click OK to either and let MBAM proceed with the disinfection process, if asked to restart the computer, please do so immediately.


NEXT


Run an on-line scan with Kaspersky

Using Internet Explorer or Firefox, visit Kaspersky On-line Scanner

1. Click Accept, when prompted to download and install the program files and database of malware definitions.
2. To optimize scanning time and produce a more sensible report for review:
  • Close any open programs
  • Turn off the real time scanner of any existing antivirus program while performing the online scan
3. Click Run at the Security prompt.
The program will then begin downloading and installing and will also update the database.
Please be patient as this can take several minutes.
  • Once the update is complete, click on My Computer under the green Scan bar to the left to start the scan.
  • Once the scan is complete, it will display if your system has been infected. It does not provide an option to clean/disinfect. We only require a report from it.
  • Do NOT be alarmed by what you see in the report. Many of the finds have likely been quarantined.
  • Click View scan report at the bottom.

    [external image: Posted Image]
  • Click the Save as Text button to save the file to your desktop so that you may post it in your next reply
hi catbyte, here is the malware bytes log Malwarebytes' Anti-Malware 1.46 www.malwarebytes.org Database version: 4052 Windows 5.1.2600 Service Pack 3 Internet Explorer 7.0.5730.13 24/05/2010 21:24:04 mbam-log-2010-05-24 (21-24-04).txt Scan type: Quick scan Objects scanned: 125849 Time elapsed: 3 minute(s), 53 second(s) Memory Processes Infected: 0 Memory Modules Infected: 0 Registry Keys Infected: 0 Registry Values Infected: 0 Registry Data Items Infected: 0 Folders Infected: 0 Files Infected: 0 Memory Processes Infected: (No malicious items detected) Memory Modules Infected: (No malicious items detected) Registry Keys Infected: (No malicious items detected) Registry Values Infected: (No malicious items detected) Registry Data Items Infected: (No malicious items detected) Folders Infected: (No malicious items detected) Files Infected: (No malicious items detected) i will now do the kaspersky online scan as directed and then get back to you
hi catbyte, this is the kaspersky log you requested ——————————————————————————– KASPERSKY ONLINE SCANNER 7.0: scan report Tuesday, May 25, 2010 Operating system: Microsoft Windows XP Professional Service Pack 3 (build 2600) Kaspersky Online Scanner version: 7.0.26.13 Last database update: Monday, May 24, 2010 15:45:27 Records in database: 4169439 ——————————————————————————– Scan settings: scan using the following database: extended Scan archives: yes Scan e-mail databases: yes Scan area - My Computer: C:\ D:\ K:\ Scan statistics: Objects scanned: 143822 Threats found: 0 Infected objects found: 0 Suspicious objects found: 0 Scan duration: 02:32:58 No threats found. Scanned area is clean. Selected area has been scanned. thanks phil c
Please do the following.

Visit ADOBEand download the latest version of Acrobat Reader (version 9.3)
Having the latest updates ensures there are no security vulnerabilities in your system.


NEXT


Your Java is out of date. Older versions have vulnerabilities that malware can use to infect your system.
Please follow these steps to remove older version Java components and update.
  • Download the latest version of Java Runtime Environment (JRE) 6 and Save it to your Desktop.
  • Scroll down to where it says Java Runtime Environment (JRE) 6 Update 20 The Java SE Runtime Environment (JRE) allows end-users to run Java applications.
  • Click the Download button to the right.
  • Select the Windows platform from the dropdown menu.
  • Read the License Agreement and then check the box that says: I agree to the Java SE Runtime Environment 6 with JavaFX License Agreement
  • Click Continue The page will refresh.
  • Click on the link to download Windows Offline Installation and Save the file to your Desktop.
  • Close any programs you may have running - especially your web browser.
  • Go to Start(or My Computer) > Control Panel and double-click on Add or Remove Programs and remove all older versions of Java.
  • Click (highlight) any item with Java Runtime Environment (JRE, J2SE, Java™ SE or Java™ 6) in the name.
  • Click the Remove or Change/Remove button.
  • Repeat as many times as necessary to remove each Java version.
  • Reboot your computer once all Java components are removed.
  • Then from your desktop double-click on jre-6u20-windows-i586-p.exe to install the newest version.
  • After the install is complete, go back to your Control Panel(using Classic View) and click the Java icon. (looks like a coffee cup)
    • On the General tab, under Temporary Internet Files, click the Settings button.
    • Next, click on the Delete Files button.
    • There are two options in the window to clear the cache - Leave BOTH Checked
    • Applications and Applets
    • Trace and Log Files
  • Click OK on Delete Temporary Files Window. Note: This deletes ALL the Downloaded Applications and Applets from the CACHE
  • Click OK to leave the Temporary Files Window.
  • Click OK to leave the Java Control Panel.
  • Delete jre-6u20-windows-i586-p.exe from your desktop.


NEXT


Please post a fresh DDS log and advise how your computer is running now and if there are any outstanding issues.
hi catbyte, did the adobe and did the java here is one log from dds and ive attached other one as instructed. the machine runs ok but it virtually did before i only had no explorer and could do updates from microsoft !!!!! i still dont have explorer 7 and ive not tried microsoft should i now try to install ie7 and try updates from microsoft ???? DDS (Ver_10-03-17.01) - NTFSx86 Run by [removed] at 16:49:54.15 on 25/05/2010 Internet Explorer: 7.0.5730.13 Microsoft Windows XP Professional 5.1.2600.3.1252.44.1033.18.3070.2458 [GMT 1:00] AV: AVG Anti-Virus Free *On-access scanning disabled* (Updated) {17DDD097-36FF-435F-9E1B-52D74245D6BF} ============== Running Processes =============== C:\WINDOWS\system32\Ati2evxx.exe C:\WINDOWS\system32\svchost -k DcomLaunch svchost.exe C:\WINDOWS\System32\svchost.exe -k netsvcs C:\WINDOWS\system32\svchost.exe -k WudfServiceGroup svchost.exe svchost.exe C:\WINDOWS\system32\Ati2evxx.exe C:\Program Files\AVG\AVG9\avgchsvx.exe C:\Program Files\AVG\AVG9\avgrsx.exe C:\Program Files\AVG\AVG9\avgcsrvx.exe C:\WINDOWS\system32\spoolsv.exe C:\WINDOWS\Explorer.EXE C:\Program Files\Synaptics\SynTP\SynTPEnh.exe C:\Program Files\iTunes\iTunesHelper.exe C:\WINDOWS\system32\rundll32.exe C:\Program Files\ATI Technologies\ATI.ACE\CLI.EXE C:\WINDOWS\RTHDCPL.EXE C:\WINDOWS\system32\ctfmon.exe C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe C:\Program Files\AVG\AVG9\avgwdsvc.exe C:\Program Files\IVT Corporation\BlueSoleil\BTNtService.exe C:\Program Files\Bonjour\mDNSResponder.exe svchost.exe C:\WINDOWS\system32\svchost.exe -k hpdevmgmt C:\Program Files\AVG\AVG9\avgnsx.exe C:\WINDOWS\System32\svchost.exe -k HPZ12 C:\WINDOWS\System32\svchost.exe -k HPZ12 C:\WINDOWS\system32\svchost.exe -k imgsvc C:\WINDOWS\system32\SearchIndexer.exe C:\Program Files\Yahoo!\SoftwareUpdate\YahooAUService.exe C:\Program Files\AVG\AVG9\avgemc.exe C:\Program Files\AVG\AVG9\avgcsrvx.exe C:\Program Files\iPod\bin\iPodService.exe C:\Program Files\ATI Technologies\ATI.ACE\cli.exe C:\Program Files\Internet Explorer\IEXPLORE.EXE C:\WINDOWS\system32\msiexec.exe C:\Program Files\Java\jre6\bin\jqs.exe C:\WINDOWS\system32\SearchProtocolHost.exe C:\Documents and Settings\P Compton\Desktop\dds.com ============== Pseudo HJT Report =============== uStart Page = hxxp://uk.yahoo.com/ uInternet Settings,ProxyOverride = ;*.local uSearchURL,(Default) = hxxp://uk.rd.yahoo.com/customize/ie/defaults/su/msgr8/*http://uk.search.yahoo.com BHO: &Yahoo! Toolbar Helper: {02478d38-c3f9-4efb-9b51-7695eca05670} - c:\program files\yahoo!\companion\installs\cpn3\yt.dll BHO: Adobe PDF Link Helper: {18df081c-e8ad-4283-a596-fa578c2ebdc3} - c:\program files\common files\adobe\acrobat\activex\AcroIEHelperShim.dll BHO: AVG Safe Search: {3ca2f312-6f6e-4b53-a66e-4e65e497c8c0} - c:\program files\avg\avg9\avgssie.dll BHO: Vuze Remote Toolbar: {ba14329e-9550-4989-b3f2-9732e92d17cc} - c:\program files\vuze_remote\tbVuz1.dll BHO: Sopcast Ask Toolbar: {d4027c7f-154a-4066-a1ad-4243d8127440} - c:\program files\ask.com\GenericAskToolbar.dll BHO: Java™ Plug-In 2 SSV Helper: {dbc80044-a445-435b-bc74-9c25c1c588a9} - c:\program files\java\jre6\bin\jp2ssv.dll BHO: JQSIEStartDetectorImpl Class: {e7e6f031-17ce-4c07-bc86-eabfe594f69c} - c:\program files\java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll BHO: SingleInstance Class: {fdad4da1-61a2-4fd8-9c17-86f7ac245081} - c:\program files\yahoo!\companion\installs\cpn3\YTSingleInstance.dll TB: Yahoo! Toolbar: {ef99bd32-c1fb-11d2-892f-0090271d4f88} - c:\program files\yahoo!\companion\installs\cpn3\yt.dll TB: Vuze Remote Toolbar: {ba14329e-9550-4989-b3f2-9732e92d17cc} - c:\program files\vuze_remote\tbVuz1.dll TB: Sopcast Ask Toolbar: {d4027c7f-154a-4066-a1ad-4243d8127440} - c:\program files\ask.com\GenericAskToolbar.dll uRun: [SUPERAntiSpyware] c:\program files\superantispyware\2c34bb8a-9201-41d5-8c90-500b2af1c301.exe uRun: [ctfmon.exe] c:\windows\system32\ctfmon.exe mRun: [WinPatrol] c:\program files\billp studios\winpatrol\winpatrol.exe mRun: [KTPWare] c:\program files\elantech\ktp.exe mRun: [IMJPMIG8.1] "c:\windows\ime\imjp8_1\IMJPMIG.EXE" /Spoil /RemAdvDef /Migration32 mRun: [SynTPEnh] c:\program files\synaptics\syntp\SynTPEnh.exe mRun: [AppleSyncNotifier] c:\program files\common files\apple\mobile device support\AppleSyncNotifier.exe mRun: [iTunesHelper] "c:\program files\itunes\iTunesHelper.exe" mRun: [BluetoothAuthenticationAgent] rundll32.exe bthprops.cpl,,BluetoothAuthenticationAgent mRun: [ATICCC] "c:\program files\ati technologies\ati.ace\CLIStart.exe" mRun: [RTHDCPL] RTHDCPL.EXE mRun: [Adobe Reader Speed Launcher] "c:\program files\adobe\reader 9.0\reader\Reader_sl.exe" mRun: [KernelFaultCheck] %systemroot%\system32\dumprep 0 -k mRun: [SunJavaUpdateSched] "c:\program files\common files\java\java update\jusched.exe" dRunOnce: [tscuninstall] %systemroot%\system32\tscupgrd.exe IE: {e2e2dd38-d088-4134-82b7-f2ba38496583} - %windir%\Network Diagnostic\xpnetdiag.exe IE: {FB5F1910-F110-11d2-BB9E-00C04F795683} - c:\program files\messenger\msmsgs.exe DPF: {6414512B-B978-451D-A0D8-FCFDF33E833C} - hxxp://update.microsoft.com/windowsupdate/v6/V5Controls/en/x86/client/wuweb_site.cab?1263498871678 DPF: {8100D56A-5661-482C-BEE8-AFECE305D968} - hxxp://upload.facebook.com/controls/2009.07.28_v5.5.8.1/FacebookPhotoUploader55.cab DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_20-windows-i586.cab DPF: {8FEFF364-6A5F-4966-A917-A3AC28411659} - hxxp://download.sopcast.com/download/SOPCORE.CAB DPF: {8FFBE65D-2C9C-4669-84BD-5829DC0B603C} - hxxp://fpdownload.macromedia.com/get/flashplayer/current/polarbear/ultrashim.cab DPF: {CAFEEFAC-0016-0000-0020-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_20-windows-i586.cab DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_20-windows-i586.cab DPF: {E2883E8F-472F-4FB0-9522-AC9BF37916A7} - hxxp://platformdl.adobe.com/NOS/getPlusPlus/1.6/gp.cab Handler: linkscanner - {F274614C-63F8-47D5-A4D1-FBDDE494F8D1} - c:\program files\avg\avg9\avgpp.dll Notify: !SASWinLogon - c:\program files\superantispyware\SASWINLO.DLL Notify: AtiExtEvent - Ati2evxx.dll Notify: avgrsstarter - avgrsstx.dll SSODL: WPDShServiceObj - {AAA288BA-9A4C-45B0-95D7-94D524869DB5} - c:\windows\system32\WPDShServiceObj.dll SEH: Windows Desktop Search Namespace Manager: {56f9679e-7826-4c84-81f3-532071a8bcc5} - c:\program files\windows desktop search\MSNLNamespaceMgr.dll mASetup: {A509B1FF-37FF-4bFF-8CFF-4F3A747040FF} - c:\windows\system32\rundll32.exe c:\windows\system32\advpack.dll,launchinfsectionex c:\program files\internet explorer\clrtour.inf,DefaultInstall.ResetTour,,12 ============= SERVICES / DRIVERS =============== R0 Lbd;Lbd;c:\windows\system32\drivers\Lbd.sys [2009-4-25 64160] R1 AvgLdx86;AVG Free AVI Loader Driver x86;c:\windows\system32\drivers\avgldx86.sys [2010-4-10 216200] R1 AvgMfx86;AVG Free On-access Scanner Minifilter Driver x86;c:\windows\system32\drivers\avgmfx86.sys [2010-4-10 29512] R1 AvgTdiX;AVG Free Network Redirector;c:\windows\system32\drivers\avgtdix.sys [2010-4-10 242896] R1 cdrblock;cdrblock;c:\windows\system32\drivers\cdrblock.sys [2007-11-21 20992] R1 cdrport;cdrport;c:\windows\system32\drivers\cdrport.sys [2007-11-21 4608] R1 SASDIFSV;SASDIFSV;c:\program files\superantispyware\sasdifsv.sys [2009-3-23 9968] R1 SASKUTIL;SASKUTIL;c:\program files\superantispyware\SASKUTIL.SYS [2009-3-23 74480] R2 avg9emc;AVG Free E-mail Scanner;c:\program files\avg\avg9\avgemc.exe [2010-4-10 916760] R2 avg9wd;AVG Free WatchDog;c:\program files\avg\avg9\avgwdsvc.exe [2010-4-10 308064] R3 SASENUM;SASENUM;c:\program files\superantispyware\SASENUM.SYS [2009-3-23 7408] S2 AutoExNT;AutoExNT;c:\windows\system32\Autoexnt.exe [2010-4-10 5904] S2 Lavasoft Ad-Aware Service;Lavasoft Ad-Aware Service;c:\program files\lavasoft\ad-aware\AAWService.exe [2009-3-9 1029456] S3 cpuz132;cpuz132;\??\c:\docume~1\pcompt~1\locals~1\temp\cpuz132\cpuz132_x32.sys –> c:\docume~1\pcompt~1\locals~1\temp\cpuz132\cpuz132_x32.sys [?] S3 MotDev;Motorola Inc. USB Device;c:\windows\system32\drivers\motodrv.sys [2008-6-21 42112] =============== Created Last 30 ================ 2010-05-25 15:46:21 73728 —-a-w- c:\windows\system32\javacpl.cpl 2010-05-25 15:46:21 411368 —-a-w- c:\windows\system32\deployJava1.dll 2010-05-24 17:16:26 98816 —-a-w- c:\windows\sed.exe 2010-05-24 17:16:26 77312 —-a-w- c:\windows\MBR.exe 2010-05-24 17:16:26 256512 —-a-w- c:\windows\PEV.exe 2010-05-24 17:16:26 161792 —-a-w- c:\windows\SWREG.exe 2010-05-20 22:13:47 0 d—–w- c:\docume~1\pcompt~1\applic~1\AVG9 2010-05-20 21:32:13 488 —ha-r- c:\windows\system32\logonui.exe.manifest 2010-05-20 21:32:08 749 —ha-r- c:\windows\WindowsShell.Manifest 2010-05-20 21:32:08 749 —ha-r- c:\windows\system32\wuaucpl.cpl.manifest 2010-05-20 21:32:08 749 —ha-r- c:\windows\system32\sapi.cpl.manifest 2010-05-20 21:32:08 749 —ha-r- c:\windows\system32\nwc.cpl.manifest 2010-05-20 21:32:08 749 —ha-r- c:\windows\system32\ncpa.cpl.manifest 2010-05-20 21:18:12 88192 —-a-w- c:\windows\system32\drivers\irda.sys 2010-05-20 21:18:12 8192 —-a-w- c:\windows\system32\wshirda.dll 2010-05-20 21:18:12 28160 —-a-w- c:\windows\system32\irmon.dll 2010-05-20 21:18:12 151552 —-a-w- c:\windows\system32\irftp.exe 2010-05-20 21:10:24 16535 —-a-r- c:\windows\SETFF.tmp 2010-05-20 21:10:21 1088840 —-a-r- c:\windows\SETEE.tmp 2010-05-20 21:10:18 1296669 —-a-r- c:\windows\SETEB.tmp 2010-05-20 21:07:51 2145386496 —-a-w- c:\windows\MEMORY.DMP 2010-05-20 20:47:27 19584 —-a-w- c:\windows\system32\drivers\rasirda.sys 2010-05-20 19:19:55 0 d—–w- c:\windows\setupupd 2010-05-20 17:38:51 39936 -c–a-w- c:\windows\system32\dllcache\hostmib.dll 2010-05-20 17:38:51 39936 —-a-w- c:\windows\system32\hostmib.dll 2010-05-20 17:38:47 0 d—–w- C:\Inetpub 2010-05-20 17:15:48 6144 -c–a-w- c:\windows\system32\dllcache\snmpmib.dll 2010-05-20 17:15:48 6144 —-a-w- c:\windows\system32\snmpmib.dll 2010-05-20 16:55:40 16535 —-a-r- c:\windows\SET103.tmp 2010-05-20 16:55:37 1088840 —-a-r- c:\windows\SETF7.tmp 2010-05-20 16:55:35 1296669 —-a-r- c:\windows\SETF1.tmp 2010-05-20 16:37:10 0 d—–w- c:\windows\setup.pss 2010-05-19 09:04:02 0 d—–w- c:\program files\ATI Technologies 2010-05-14 10:28:11 0 d—–w- c:\program files\CamStudio 2010-05-14 10:06:27 0 d—–w- c:\program files\NirSoft 2010-05-13 10:15:29 73 —-a-w- c:\windows\system32\-1 2010-05-12 09:34:44 16535 —-a-r- c:\windows\SETF6.tmp 2010-05-12 09:34:40 1088840 —-a-r- c:\windows\SETEA.tmp 2010-05-12 09:34:38 1296669 —-a-r- c:\windows\SETE7.tmp 2010-05-12 09:23:11 0 d—–w- C:\found.000 2010-05-10 17:31:02 16535 —-a-r- c:\windows\SETF5.tmp 2010-05-10 17:30:58 1088840 —-a-r- c:\windows\SETE9.tmp 2010-05-10 17:30:56 1296669 —-a-r- c:\windows\SETE6.tmp 2010-05-10 16:59:35 16535 —-a-r- c:\windows\SET14D.tmp 2010-05-10 16:59:31 1088840 —-a-r- c:\windows\SET141.tmp 2010-05-10 16:59:29 1296669 —-a-r- c:\windows\SET140.tmp 2010-04-27 10:05:34 69632 —-a-w- c:\windows\ALCMTR.EXE 2010-04-26 21:17:05 0 d—–w- c:\windows\system32\wbem\Repository ==================== Find3M ==================== 2010-05-20 21:27:32 23392 -c–a-w- c:\windows\system32\emptyregdb.dat 2010-04-29 14:39:38 38224 —-a-w- c:\windows\system32\drivers\mbamswissarmy.sys 2010-04-29 14:39:26 20952 —-a-w- c:\windows\system32\drivers\mbam.sys 2010-04-21 16:25:24 242896 —-a-w- c:\windows\system32\drivers\avgtdix.sys 2010-04-10 16:01:36 12464 —-a-w- c:\windows\system32\avgrsstx.dll 2010-04-10 16:01:28 216200 —-a-w- c:\windows\system32\drivers\avgldx86.sys 2010-04-08 23:07:37 71680 –sha-r- c:\windows\system32\kbdtuq5.dll 2009-04-20 17:33:51 2098 -csha-w- c:\windows\system32\KGyGaAvL.sys ============= FINISH: 16:50:18.23 ===============

Attachments:

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI