AplusWebMaster
FYI…
Fake LinkedIn SPAM / applockrapidfire .biz
- http://blog.dynamoo.com/2013/03/linkedin-s…pidfirebiz.html
18 March 2013 - "This fake LinkedIn spam leads to malware on applockrapidfire .biz:
From: David O'Connor - LinkedIn [mailto:kissp @gartenplandesign .de]
Sent: 18 March 2013 15:34
Subject: Join my network on LinkedIn
Importance: High
LinkedIn
REMINDERS
Invitation reminders:
From David O\'Connor (animator at ea)
PENDING MESSAGES
There are a total of 9 messages awaiting your response. Go to InBox now.
This message was sent to username @domain .com. Don't want to receive email notifications? Login to your LinkedIn account to Unsubscribe.
LinkedIn values your privacy. At no time has LinkedIn made your email address available to any other LinkedIn user without your permission. c 2013, LinkedIn Corporation.
The link in the message goes through a legitimate hacked site to a malware landing page on [donotclick]applockrapidfire .biz/closest/209tuj2dsljdglsgjwrigslgkjskga.php (report here*) hosted on 78.46.222.237 (Hetzner, Germany). applockrapidfire .biz was registered just today to a presumably fake address…
URLquery detects traffic to these additional IPs that you might want to block too:
50.22.196.70 (Softlayer / Maxmind LLC, US)
66.85.130.234 (Secured Servers LLC / Phoenix NAP, US)
194.165.17.3 (ADM Service Ltd, Monaco)
The nameservers are NS1.QUANTUMISPS .COM (5.9.212.43: Hetzner, Germany) and NS2.QUANTUMISPS .COM (66.85.131.123: Secured Servers LLC / Phoenix NAP, US). quantumisps .com was registered to an anonymous person on 2013-03-15…
Recommended blocklist:
[removed]
50.22.196.70
66.85.130.234
66.85.131.123
78.46.222.237
194.165.17.3
quantumisps .com
applockrapidfire .biz"
* http://urlquery.net/report.php?id=1500577
… Detected live BlackHole v2.0 exploit kit
___
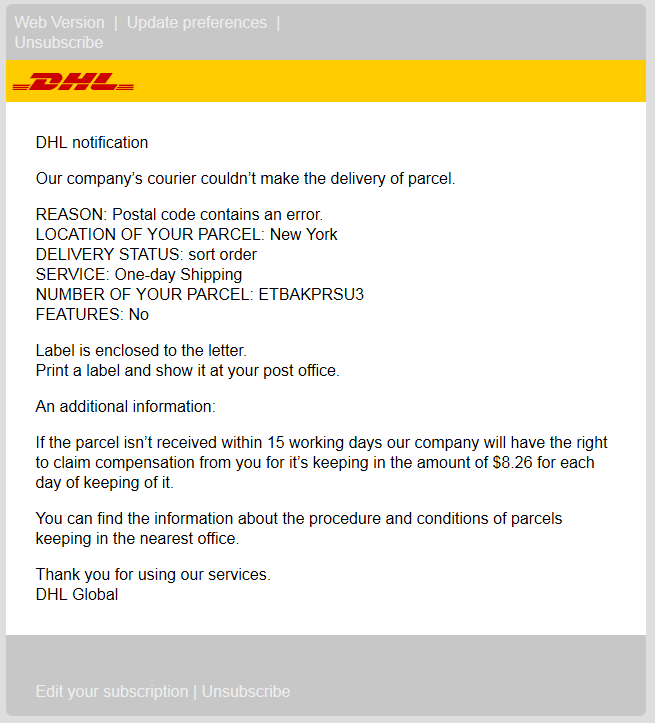
Fake DHL emails contain malware
- http://nakedsecurity.sophos.com/2013/03/18…emails-malware/
March 18, 2013 - "… Online criminals have spammed out a large number of messages, claiming to come from DHL Express International, that are designed to install malware onto the computers of unsuspecting PC users. Here is what a typical example of an email spammed out in the attack looks like:
> https://sophosnews.files.wordpress.com/2013/03/dhl.jpg?w=640
Attached to the emails is a ZIP file, containing malware. The filename of the ZIP file can vary, but takes the form "DHL reportXXXXXX.zip" (where the 'X's are a random code)… Troj/BredoZp-S* …"
* http://www.sophos.com/en-us/threat-center/…~BredoZp-S.aspx
 <_<
Fake LinkedIn SPAM / applockrapidfire .biz
- http://blog.dynamoo.com/2013/03/linkedin-s…pidfirebiz.html
18 March 2013 - "This fake LinkedIn spam leads to malware on applockrapidfire .biz:
From: David O'Connor - LinkedIn [mailto:kissp @gartenplandesign .de]
Sent: 18 March 2013 15:34
Subject: Join my network on LinkedIn
Importance: High
REMINDERS
Invitation reminders:
From David O\'Connor (animator at ea)
PENDING MESSAGES
There are a total of 9 messages awaiting your response. Go to InBox now.
This message was sent to username @domain .com. Don't want to receive email notifications? Login to your LinkedIn account to Unsubscribe.
LinkedIn values your privacy. At no time has LinkedIn made your email address available to any other LinkedIn user without your permission. c 2013, LinkedIn Corporation.
The link in the message goes through a legitimate hacked site to a malware landing page on [donotclick]applockrapidfire .biz/closest/209tuj2dsljdglsgjwrigslgkjskga.php (report here*) hosted on 78.46.222.237 (Hetzner, Germany). applockrapidfire .biz was registered just today to a presumably fake address…
URLquery detects traffic to these additional IPs that you might want to block too:
50.22.196.70 (Softlayer / Maxmind LLC, US)
66.85.130.234 (Secured Servers LLC / Phoenix NAP, US)
194.165.17.3 (ADM Service Ltd, Monaco)
The nameservers are NS1.QUANTUMISPS .COM (5.9.212.43: Hetzner, Germany) and NS2.QUANTUMISPS .COM (66.85.131.123: Secured Servers LLC / Phoenix NAP, US). quantumisps .com was registered to an anonymous person on 2013-03-15…
Recommended blocklist:
[removed]
50.22.196.70
66.85.130.234
66.85.131.123
78.46.222.237
194.165.17.3
quantumisps .com
applockrapidfire .biz"
* http://urlquery.net/report.php?id=1500577
… Detected live BlackHole v2.0 exploit kit
___
Fake DHL emails contain malware
- http://nakedsecurity.sophos.com/2013/03/18…emails-malware/
March 18, 2013 - "… Online criminals have spammed out a large number of messages, claiming to come from DHL Express International, that are designed to install malware onto the computers of unsuspecting PC users. Here is what a typical example of an email spammed out in the attack looks like:
> https://sophosnews.files.wordpress.com/2013/03/dhl.jpg?w=640

Attached to the emails is a ZIP file, containing malware. The filename of the ZIP file can vary, but takes the form "DHL reportXXXXXX.zip" (where the 'X's are a random code)… Troj/BredoZp-S* …"
* http://www.sophos.com/en-us/threat-center/…~BredoZp-S.aspx
<_<