AplusWebMaster
FYI…
Fake ACH emails serve client-side exploits and malware
- http://blog.webroot.com/2013/02/25/malicio…ts-and-malware/
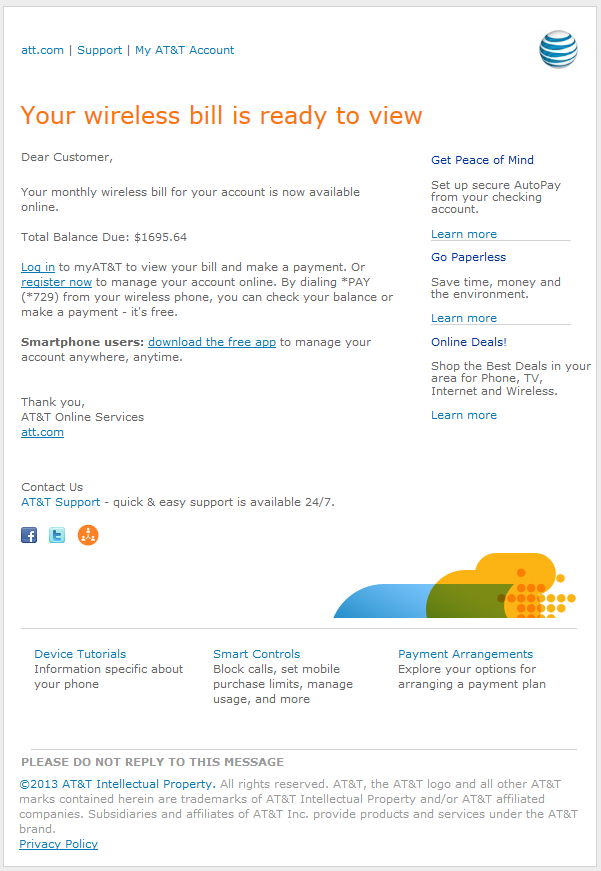
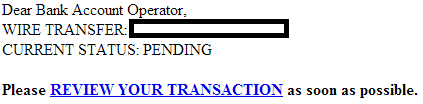
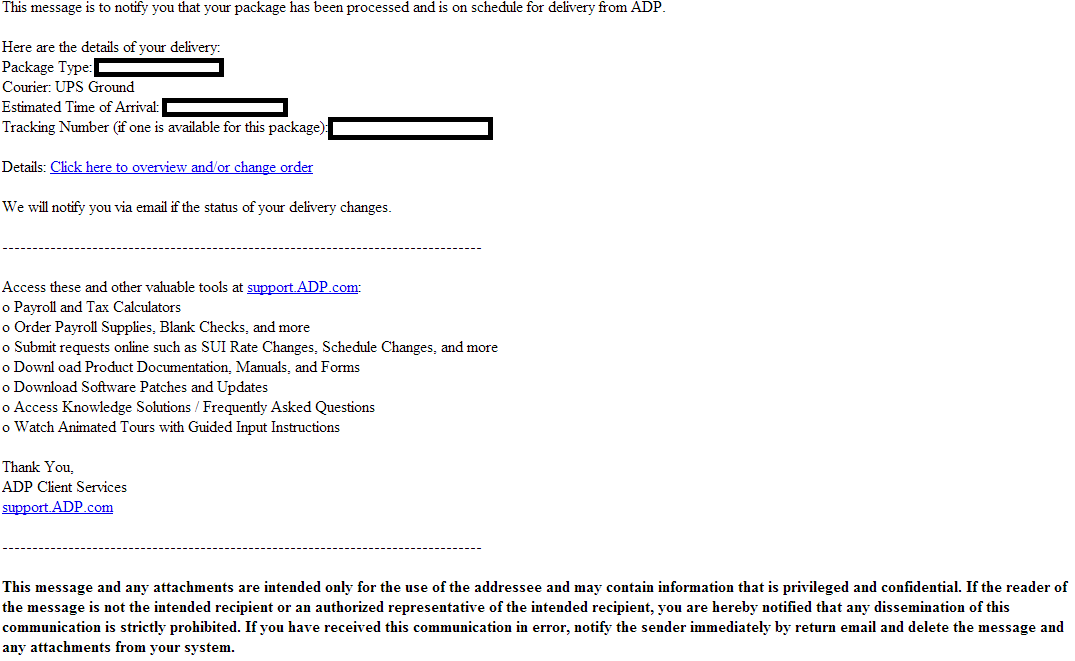
Feb 25, 2013 - "… yet another spam campaign, this time impersonating the “Data Processing Service” company, in an attempt to trick its customers into interacting with the malicious emails. Once they do so, they are automatically exposed to the client-side exploits served by the BlackHole Exploit Kit…
Sample screenshot of the spamvertised email:
> https://webrootblog.files.wordpress.com/201…service_ach.png
… Upon successful client-side exploitation, the campaign drops MD5: faa3a6c7bbf5b0449f60409c8bf63859 * … Trojan-Spy.Win32.Zbot.jfpy.
… It then attempts to connect to the following IPs:
[removed], [removed], [removed], [removed], [removed], [removed],
[removed], [removed], [removed], 81.136.230.235, 101.162.73.132, 99.76.3.38,
85.29.177.249, 24.126.54.116, 108.130.34.42, 99.116.134.54, 80.252.59.142
Malicious domain name reconnaissance:
dekolink .net – 50.7.251.59; 176.120.38.238 – Email: wondermitch @hotmail .com
Name Server: NS1.THEREGISTARS .COM – 31.170.106.17 – Email: lockwr @rocketmail .com
Name Server: NS2.THEREGISTARS .COM – 67.15.223.219 – Email: lockwr @rocketmail .com …"
(More detail available at the webroot URL above.)
* https://www.virustotal.com/en/file/1313dd0c…8ca62/analysis/
File name: info.exe
Detection ratio: 27/45
Analysis date: 2013-02-25
___
Trustwave Trustkeeper Phish
- https://isc.sans.edu/diary.html?storyid=15271
Last Updated: 2013-02-25 17:41:36 UTC - … the give away that this is a fake is the from e-mail address as well as the link leading to a different site then advertised. Click on the image for a full size example.
> https://isc.sans.edu/diaryimages/images/trustwavephish.png
[Update:] An analysis of this phish by Trustwave's own Spiderlabs can be found here:
- http://blog.spiderlabs.com/2013/02/more-on…eper-phish.html
- http://blog.dynamoo.com/2013/02/trustkeepe…ities-scan.html
25 Feb 2013 - "… this "TrustKeeper Vulnerabilities Scan Information" -spam- leads to an exploit kit on saberdelvino .net…
> https://lh3.ggpht.com/-Gyic2-WNNZE/USu7TzQl…0/trustwave.png
… The malicious payload is at [donotclick]saberdelvino .net/detects/random-ship-members-daily.php (report here*) hosted on the following IPs:
118.97.77.122 (PT Telekon, Indonesia)
176.120.38.238 (Langate, Ukraine)…"
* http://www.urlquery.net/report.php?id=1120754
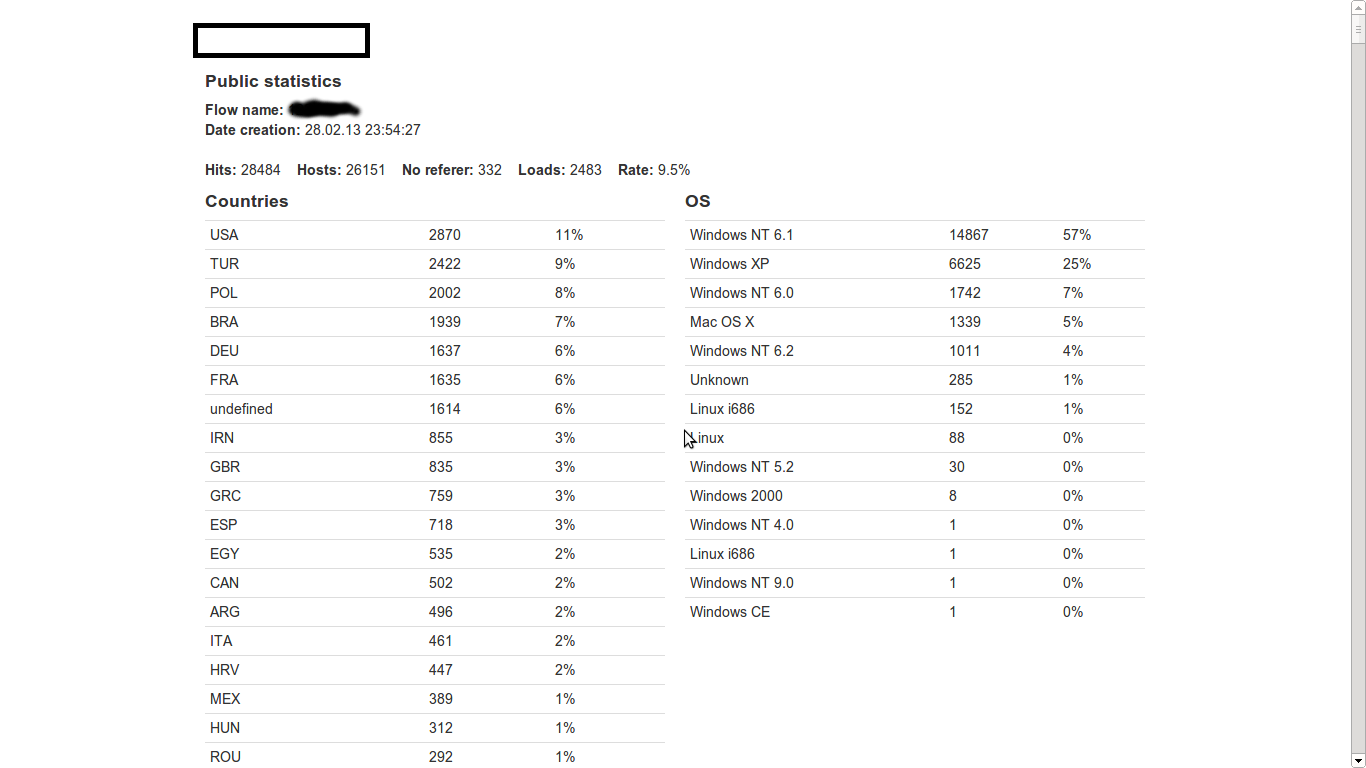
… Blackhole 2
 <_<
Fake ACH emails serve client-side exploits and malware
- http://blog.webroot.com/2013/02/25/malicio…ts-and-malware/
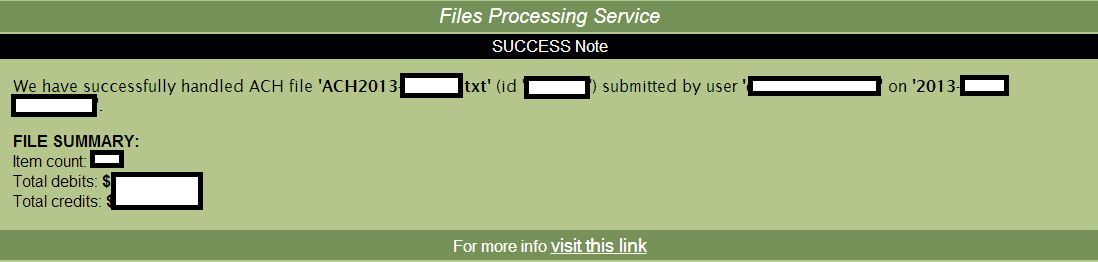
Feb 25, 2013 - "… yet another spam campaign, this time impersonating the “Data Processing Service” company, in an attempt to trick its customers into interacting with the malicious emails. Once they do so, they are automatically exposed to the client-side exploits served by the BlackHole Exploit Kit…
Sample screenshot of the spamvertised email:
> https://webrootblog.files.wordpress.com/201…service_ach.png
… Upon successful client-side exploitation, the campaign drops MD5: faa3a6c7bbf5b0449f60409c8bf63859 * … Trojan-Spy.Win32.Zbot.jfpy.
… It then attempts to connect to the following IPs:
[removed], [removed], [removed], [removed], [removed], [removed],
[removed], [removed], [removed], 81.136.230.235, 101.162.73.132, 99.76.3.38,
85.29.177.249, 24.126.54.116, 108.130.34.42, 99.116.134.54, 80.252.59.142
Malicious domain name reconnaissance:
dekolink .net – 50.7.251.59; 176.120.38.238 – Email: wondermitch @hotmail .com
Name Server: NS1.THEREGISTARS .COM – 31.170.106.17 – Email: lockwr @rocketmail .com
Name Server: NS2.THEREGISTARS .COM – 67.15.223.219 – Email: lockwr @rocketmail .com …"
(More detail available at the webroot URL above.)
* https://www.virustotal.com/en/file/1313dd0c…8ca62/analysis/
File name: info.exe
Detection ratio: 27/45
Analysis date: 2013-02-25
___
Trustwave Trustkeeper Phish
- https://isc.sans.edu/diary.html?storyid=15271
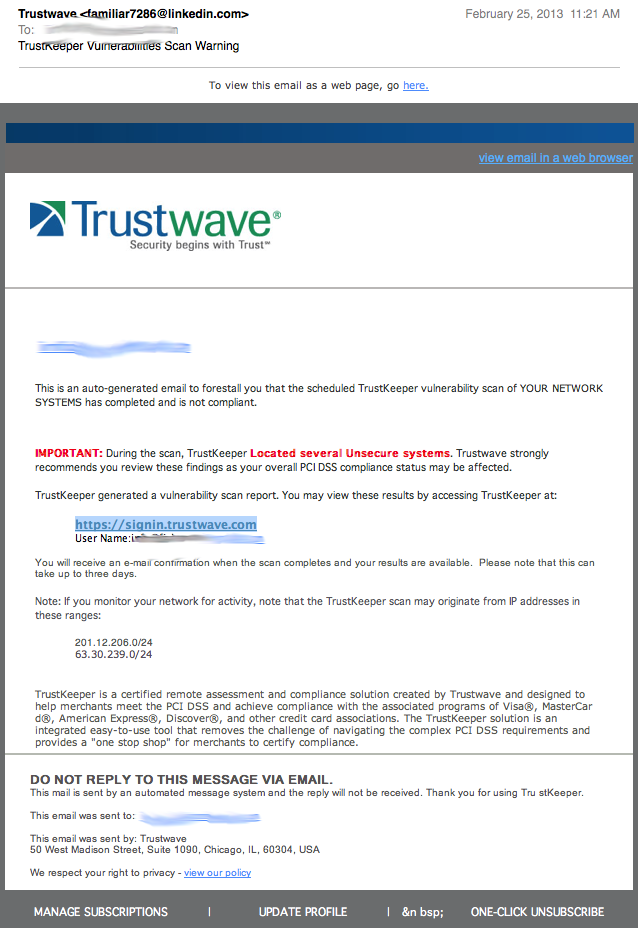
Last Updated: 2013-02-25 17:41:36 UTC - … the give away that this is a fake is the from e-mail address as well as the link leading to a different site then advertised. Click on the image for a full size example.
> https://isc.sans.edu/diaryimages/images/trustwavephish.png
[Update:] An analysis of this phish by Trustwave's own Spiderlabs can be found here:
- http://blog.spiderlabs.com/2013/02/more-on…eper-phish.html
- http://blog.dynamoo.com/2013/02/trustkeepe…ities-scan.html
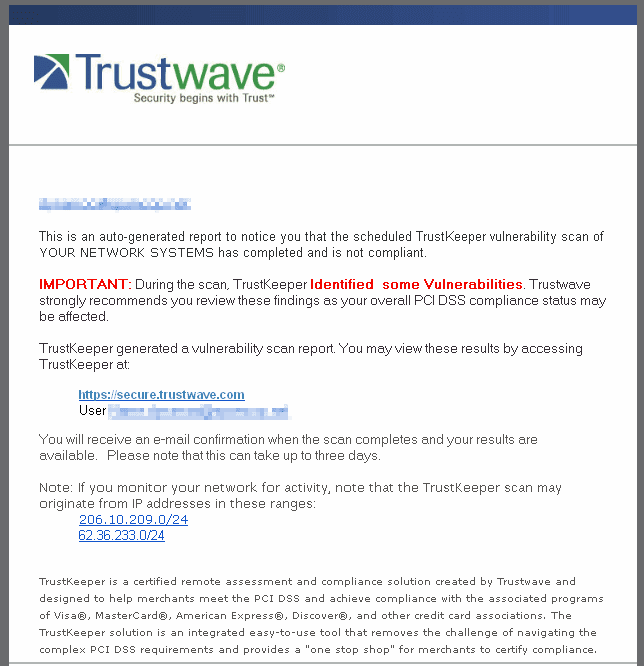
25 Feb 2013 - "… this "TrustKeeper Vulnerabilities Scan Information" -spam- leads to an exploit kit on saberdelvino .net…
> https://lh3.ggpht.com/-Gyic2-WNNZE/USu7TzQl…0/trustwave.png
… The malicious payload is at [donotclick]saberdelvino .net/detects/random-ship-members-daily.php (report here*) hosted on the following IPs:
118.97.77.122 (PT Telekon, Indonesia)
176.120.38.238 (Langate, Ukraine)…"
* http://www.urlquery.net/report.php?id=1120754
… Blackhole 2
<_<