They are sending these emails from a whole range of IP addresses (all tracking back to various subdomains of the 2 main -fraudulent- domains) under the control of these criminals that pass email authentication for the -fake- domains:
46.105.101.20
46.105.101.72
46.105.101.110
54.36.192.0/24
94.23.32.95
188.165.217.40
188.165.217.44
188.165.200.80
188.165.215.105
188.165.215.115
[removed]
[removed]
[removed]
… The emails are just about identical to those on these 2 pages with the dates and amounts changed:
> 'Virgin Media Your Virgin Media bill is ready' … and 'e Fax' …
The link in the email goes to a -compromised- or fraudulently-set-up OneDrive for business/SharePoint site where a zip file containing a .js file is downloaded…
The virgin site is:
https ://grllen-my.sharepoint .com/personal/misaacs_grllen_com_au/_layouts/15/guestaccess.aspx?docid=0f577514318c64d3a83fdc412856063e6&authkey;=AZhzom6O9TOyFzZv4HUJ6zM
where a .js file is downloaded. That downloads 46.105.102.161 /PDF/Virginmedia_bill_25_09_2017_3 .pdf
an innocent PDF file of a -genuine- Virgin media bill and displays that while at the same time downloads the Dridex banking Trojan in the background (I cannot determine the actual download location of the Dridex Trojan from the reports)
Virginmedia_bill_25_09_2017_3.zip: Extracts to: Virginmedia_bill_25_09_2017_3.js
Current Virus total detections 4/58[1]. Payload Security[2] | Dridex Payload - VirusTotal 13/61[3]|
Payload Security[4] |
The eFax site is:
https ://ucg1-my.sharepoint .com/personal/janet_lau_ucg_co_nz/_layouts/15/guestaccess.aspx?docid=0eab92172e4fb424093bc21e476a6a698&authkey;=AT_9AE00prV_R0aRf9HYOtg
where another js file is downloaded. That also downloads an innocent PDF file from
188.165.193.38 /PDF/FAX_20170925_1401908954_6.pdf
saying it all about the Rural Payments agency and displays that while at the same time downloads the -Dridex- banking Trojan in the background (I cannot determine the actual download location of the Dridex Trojan from the reports)…:
FAX_20170925_1401908954_6.zip: Extracts to: FAX_20170925_1401908954_6.js
Current Virus total detections 7/59[5]: Payload Security[6] | Dridex Payload - VirusTotal 13/61[7] |
Payload Security[8] |
… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
1] https://www.virustotal.com/en/file/0df50f3718c1718a4d75e8cf473446cf1a9268d9095459f60aafd28873b4f6fa/analysis/1506415697/
Virginmedia_bill_25_09_2017_3.js
This is a slightly more complicated infection chain that usual. There are -dozens- of different sites in the emails -hidden- behind the shipment details link. A lot of them don’t do anything except display a -fake- UPS website. Some however are connecting via an -iframe- to download
http ://rateventrithathen .info/track.php which gave me TRACK-1Z68725Y5236890147.js
Current Virus total detections 2/59*. Payload Security** | Joe Security***
Neither online sandbox retrieved any payload, whether the sites are blocked or the JS is VM aware is unknown… The basic rule is NEVER open any attachment or link in email, unless you are expecting it…"
* https://www.virustotal.com/en/file/a6c8824c80f4b2330921963ce277a9ad4c189f6f8850128a15f80d9a91d87dcc/analysis/1506504272/
TRACK-1Z68725Y5236890147.js
The next -phishing-scam- works right out of the box with no effort:
2] https://myonlinesecurity.co.uk/wp-content/uploads/2017/09/Request-For-Proforma-Invoice-Urgent.png
This PDF attachment looks like:
> https://myonlinesecurity.co.uk/wp-content/uploads/2017/09/Ugent-New-Order_pdf.png
Where -if- you follow the link you go to
https ://app-onlinedoc.000webhostapp .com/Inv-47654345584.php?code=2000500 where you see:
> https://myonlinesecurity.co.uk/wp-content/uploads/2017/09/000webhost_adobe_scam.png
Entering details tries to -redirect- you to
http ://alliancecr .com/skd/xendr.php , Where I get a 404 page not found (a quick look up shows the site registered by Godaddy in 2001, The DNS is managed by Cloudflare and there is no site found, so it is highly likely that Cloudflare have null routed the DNS already)… A quick look at the source code of the 000webhost page shows that it appears to try to send the information via Googlemail… Update: within minutes of reporting the 000webhost site, it was taken down. That is fast abuse response. I wish all webhosts were so quick and efficient…"
Fake 'Scan xxx' SPAM - Necurs sent Locky/Trickbot
- https://myonlinesecurity.co.uk/necurs-botnet-spam-now-distributing-locky-and-trickbot-via-same-vbs-file-using-geo-location-techniques/
28 Sep 2017 - "… malware downloaders coming from the necurs botnet… email with the subject of 'Emailing: Scan0253' (random numbers) pretending to come from random names at your-own-email-address or company domain. Today they have changed delivery method and will give either Locky Ransomware or Trickbot banking Trojan depending on your IP address and country of origin…
Scan0253.7z: Extracts to: Scan0277.vbs - Current Virus total detections 11/59*. Payload Security** |
In this particular VBS example there were 6 hard coded urls
“geeks-online .de/9hciunery8g?”,
”freevillemusic .com/9hciunery8g?” (VirusTotal 9/65[3]) (Payload Security[4]) Looks like Trickbot
“anarakdesert .com/LUYTbjnrf?”,
”americanbulldogradio .com/LUYTbjnrf?”
”sherylbro .net/p66/LUYTbjnrf” (VirusTotal 20/65[5]) (Payload Security[6]) This one is Locky
“poemsan .info/p66/d8743fgh” - Also Locky but a different file hash (VirusTotal 39/64[7]) (Payload Security[8])
The lookup services used are : “https ://ipinfo .io/json”,
”http ://www.geoplugin .net/json.gp”,
”http ://freegeoip .net/json/”
Update: thanks to Racco42[9] we have full list of currently known URLs posted on Pastebin[10]…
The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/882d308ab744d112b60f62faabc0dfdd6ff5dd2ff77a8fd0c664098f01ec7ea6/analysis/1506589221/
Scan0277.vbs
> http://blog.dynamoo.com/2017/09/malware-spam-emailing-scan0xxx-from.html
28 Sep 2017 - "This -fake- 'document scan' delivers different malware depending on the victim's location…
… All these recent attacks have used .7z archive files which would require 7zip or a compatible program to unarchive. Most decent mail filtering tools should be able to block -or- strip this extension, more clever ones would be able to determine that there is a .vbs script in there and block on that too."
Fake 'invoice' SPAM - deliver Locky/Trickbot
- https://myonlinesecurity.co.uk/another-change-with-locky-delivery-methods-today-payload-embedded-in-a-large-js-file/
29 Sep 2017 - "… Locky downloaders… an email with a blank/empty subject pretending to come from random names and email addresses. The body content pretends to be an 'invoice' notification. There are -no- attachments with these emails but a link-in-the-email-bodygoes to various -compromised- sites to download a .js file. As far as I can tell the actual Locky payload is -embedded- inside the .js file. For some strange reason the js file is named voicemsg_random numbers.js which would indicate that this was intended or has also been used in a voice message scam attempt to deliver Locky as well. The other strange thing in this campaign is the url in the body. All the ones I received are broken and start with 'ttp://' but looking at the mailscanner they look normal with a -complete- html on my server they look -normal- with a complete html and start with the proper 'http://'…
voicemsg_088436.js - 410.7 KB (420558 bytes) - Current Virus total detections 5/59*. Payload Security**
| drops 1102.exe 298.0 KB (305152 bytes) - VirusTotal 14/65[3] - Payload Security[4].
Nothing is actually detecting these as -Locky- Ransomware and in fact some AV on VirusTotal detect as
-Cerber- Ransomware. I am only calling these Locky based on the
moroplinghaptan .info/eroorrrs post request (giving a 404) shown in the Payload Security report. This has been a strong Indicator-of-Compromise (IOC) for Locky recently.
> Update: I am reliably informed that it depends on your IP address and location what malware you get. You will either get -Locky- Ransomware or -Trickbot- banking Trojan embedded inside the .js file.
Some of the download sites in the emails include:
http ://resortphotographics .com/invoice.html
http ://somallc .com/invoice.html
http ://pinkyardflamingos .com/invoice.html
http ://agregate-cariera .ro/invoice.html
http ://sgtenterprises .com/invoice.html
http ://weloveflowers .co.uk/invoice.html
They all use an -iframe- to actually download from
http ://moroplinghaptan .info/offjsjs/ - This site has been used in a later Locky campaign today that was spoofing voicemessages…
The basic rule is NEVER open any attachment or -link- an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/beab97c46f237c07a12390f3002516a5b62f2dbc4a56a6bcc3f0dc59e0fbf5c5/analysis/1506691940/
voicemsg_088436.js
Fake 'Office 365 invoice' - delivers Locky
- https://myonlinesecurity.co.uk/fake-office-365-invoice-delivers-locky-ransomware/
29 Sep 2017 - "The 3rd version I have seen today… Locky downloaders has gone back to a traditional zip (7z) attachmentcontaining a vbs file. This is an email pretending to be an 'Office 365 Invoice' with the subject of 'Invoice' pretending to come from the -same-name- that is in the recipient field. Random names & email addresses…
Fake 'order' SPAM - delivers malware
- https://myonlinesecurity.co.uk/fake-order-malspam-email-with-uue-attachment-delivers-malware/
29 Sep 2017 - "… malware today, all using -different- or unusual delivery methods. This next example is about an order confirmation. The attachment is a .uue attachment. Winzip says it can open .UUE files but only extracted a -garbled- encrypted/encoded txt file. Universal extractor extracted a working .exe file…
Order0210177.doc - Current Virus total detections 15/58*. Payload Security** downloads
http ://birsekermasali .com/hta/gen.hta (VirusTotal 15/57[3]) (Payload Security[4]) which in turn downloads
http ://birsekermasali .com/css_files/gen/quote.exe (VirusTotal 25/66[5]) (Payload Security[6])… This email attachment contains what appears to be a genuine word doc or Excel XLS spreadsheet with either a macro script or an embedded OLE object that when run will infect you… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/fd8ed18547954c8355cef69167f01ebc65330ba585e24645beb977967a01e322/analysis/1506949614/
Order0210177.doc
Fake 'FedEx' SPAM - leads to info stealer
- https://isc.sans.edu/diary/rss/22888
2017-10-03 - "… On Monday 2017-10-02, I ran across malicious spam (malspam) pushing Formbook, an information stealer. Arbor Networks has a good article about Formbook here:
> https://www.arbornetworks.com/blog/asert/formidable-formbook-form-grabber/
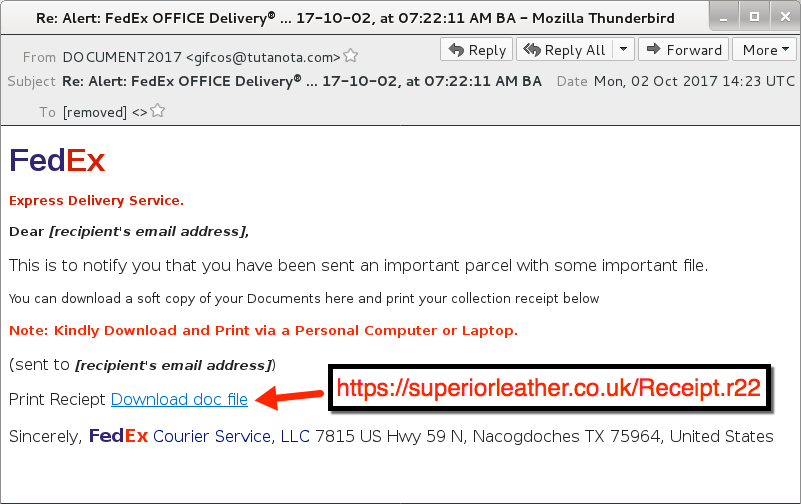
… The email is disguised as a 'FedEx delivery notice'. It has a-link-to-a-compromised-website that's hosting malware. The link points to a supposed document for this fake delivery:
> https://isc.sans.edu/diaryimages/images/2017-10-03-ISC-diary-image-01.jpg Clicking on-the-link (DON'T) returned a RAR archive. The RAR archive contains a Windows executable that's poorly-disguised as some sort of receipt… indicators seen during the infection from Formbook malspam on Monday 2017-10-02: Email:
Date/Time: 2017-11-02 at 14:23 UTC
Subject: Re: Alert: FedEx OFFICE Delivery® … 17-10-02, at 07:22:11 AM BA
From: "DOCUMENT2017"
Link from the email: hxxps ://superiorleather .co.uk/Receipt.r22
Traffic seen when retrieving the RAR archive: 185.46.121.66 [1] port 443 - superiorleather .co.uk - GET /Receipt.r22 …
1] 185.46.121.66: https://www.virustotal.com/en/ip-address/185.46.121.66/information/
> https://www.virustotal.com/en/url/97b66925f5ddbb92974955a3cc28c0d6d6049cedc3bdc9497f1334c0dcfc6369/analysis/
Post-infection traffic: 47.90.52.201 port 80 - www .shucancan .com - GET /ch/?id=[80 character ID string] 52.87.61.120 port 80 - www .ias39 .com - GET /ch/?id=[80 character ID string] 66.206.43.242 port 80 - www .fairwaytablet .com - GET /ch/?id=[80 character ID string] 103.38.43.236 port 80 - www .chunsujiayuan .com - GET /ch/?id=[80 character ID string] 104.250.134.156 port 80 - www .ebjouv .info - GET /ch/?id=[80 character ID string] 104.31.80.135 port 80 - www .dailyredherald .com - GET /ch/?id=[80 character ID string] 153.92.6.50 port 80 - www .beykozevdenevenakliyatci .com - GET /ch/?id=[80 character ID string] 162.242.173.39 port 80 - www .238thrift .com - GET /ch/?id=[80 character ID string] 180.178.39.66 port 80 - www .et551 .com - GET /ch/?id=[80 character ID string] 195.154.21.65 port 80 - www .lesjardinsdemilady .com - GET /ch/?id=[80 character ID string] 198.54.114.238 port 80 - www .prfitvxnfe .info - GET /ch/?id=[80 character ID string] 199.34.228.59 port 80 - www .craigjrspestservice .com - GET /ch/?id=[80 character ID string]
162.242.173.39 port 80 - www .238thrift .com - POST /ch/ 198.54.114.238 port 80 - www .prfitvxnfe .info - POST /ch/ " (More detail @ the isc URL above.)
There is a-link-in-the-email body to
http ://www.oysterpublicschool .com//hy/reciept/_outputC9E322F.exe which gives a 404,
but there is also a RAR attachment with a file of the same name. It is highly likely that other versions of this email will have a different download link, that might be active.
InvoiceA5165059014.7z: Extracts to: Invoice558727316499528791952132.vbs - Current Virus total detections 6/59*
Payload Security** downloads from one of these hard coded locations in this vbs. (There will be numerous others):
“spazioireos .it/8etyfh3ni?”,
”derainlay .info/p66/8etyfh3ni”,
”turfschiploge .nl/8etyfh3ni?” (VirusTotal 16/65[3])…
Xpress Money Payment Confirmation.jar (462kb) - Current Virus total detections 16/62*. Payload Security**…
All the links-in-the-email (including the -image- of an XLS file) go to the-same-url (guaranteed to be a compromised site), where the all the site content is now about QTUM, a -bitcoin- exchange. I have been seeing several compromised malware delivery sites recently with all their content changed to the QTUM content) to download a zip file:
http ://restaurantelburladero .com/Xpress Money Payment Confirmation.z (.z is a file extension that many unzipping utilities will extract from, although not commonly used)… The basic rule is NEVER open any attachment or link in an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/e724c779d3bd6062dda5f682d85a2cd715278c4950ee38e5f54918b9b41137ac/analysis/1507035357/
Scan 2017100323 114727.xls Here.JAR
Fake 'Payment Advice' SPAM - delivers Trickbot
- https://myonlinesecurity.co.uk/fake-hsbc-important-payment-advice-delivers-trickbot-banking-trojan/
5 Oct 2017 - "An email with the subject of 'Important – Payment Advice' pretending to come from HSBC but actually coming from a look-a-like domain HSBC or HSBC with a malicious word doc attachment is today’s latest spoof of a well-known company, bank or public authority delivering Trickbot banking Trojan… there is a slight formatting problem in Outlook, where the emails arrive with a -blank- body. Reading in plain text or using view source, shows the content…
SecureMessage.doc - Current Virus total detections 10/59*. Payload Security**
This malware file downloads from
http ://diga-consult .de/ser1004.png which of course is -not- an image file but a renamed .exe file that gets renamed to aqdccc.exE (VirusTotal 13/65***). An alternative download location is
http ://hill-familie .de/ser1004.png
This email -attachment- contains a genuine word doc with a macro script that when run will infect you.
The word doc looks like:
> https://myonlinesecurity.co.uk/wp-content/uploads/2017/10/hsbc_PaymentAdvice_doc_4_Oct_17.png
… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/0d92b1656112ed73fe98fd6c714d7959dd8ecc85759b87a6b01747a2ab0f8335/analysis/1507166812/
62046_Remittance.7z: decoded from base 64 and Extracts to: 872042 Remittance.vbs
Current Virus total detections 9/60*. Payload Security**
This particular VBS has these URLs hardcoded (there will be loads of others)
"asheardontheradiogreens .com/uywtfgh36?”,
”thedarkpvp .net/p66/uywtfgh36″
”2-wave .com/uywtfgh36?” (virusTotal 14/66[3]) (Payload Security[4])…
The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/a53ad9751059a2c1d298cb11868c3016ebc40cb69c562d7b1d5fad1dae75e581/analysis/1507281470/
872042 Remittance.vbs
43699 Remittance.7z: decoded from base 64 and Extracts to: Invoice IP8729962.vbs
Current Virus total detections 6/59*. Payload Security** | This particular VBS has these URLs hardcoded (there will be loads of others)
“anderlaw .com/8734gf3hf?”,
”scottfranch .org/p66/8734gf3hf”,
”cagliaricity .it/8734gf3hf?” (virusTotal 13/65***)… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/5355686920487f0b58f82532217c188d9f822d1264b71cc2d71e2b85b68ebd9c/analysis/1507542515/
Invoice IP8729962.vbs
'FormBook' malware…
- https://www.helpnetsecurity.com/2017/10/10/formbook-malware/
Oct 10, 2017 - "Information stealing FormBook malware is being lobbed at defense contractors, manufacturers and firms in the aerospace sector in the US and South Korea… The malware is delivered via high-volume spam campaigns and email attachments that take the form of:
- DOC/XLS files loaded with malicious macros that initiate the download of FormBook payloads
- Archive files containing FormBook executable files
- PDFs containing links to the tny .im URL-shortening service, which point to FormBook executables hosted on a staging server.
> https://www.helpnetsecurity.com/images/posts/formbook-industry.jpg
… The emails are made to look like they are coming from FedEx and DHL (with the PDF attachment), as emails delivering invoices, price quotations or purchase orders (with the malicious-macros-carrying Office files), and payment confirmations and purchase orders (archive files containing malicious executables)…"
Fake 'Amazon' SPAM - delivers banking trojan
- https://myonlinesecurity.co.uk/fake-amazon-associates-network-malspam-email-delivers-cthonic-banking-trojan/
11 Oct 2017 - "… malware scammers are imitating Amazon Associates to deliver their malware. An email with the subject of coming from 'Amazon Associates Network' with a malicious word doc or Excel XLS spreadsheet attachment delivers Cthonic banking trojan. These are coming via a -compromised- umbc .edu email account. All the sites in the malware delivery chain are -compromised- sites…
The link-in-the-email goes to a broken link
ttps ://www.angelbasar .de/skin/form.php it should be
https ://www.angelbasar .de/skin/form.php where it downloads Your account, statement.docm
Current Virus total detections 5/61*. Payload Security** Where you can see the same screenshots as described yesterday where the content only appears after enabling and allowing macros to run. This malware doc downloads from
http ://shirtlounge .eu/skin/priv8.exe (VirusTotal 50/62[3]) (Payload Security[4]) Cthonic banking trojan…
DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment -or- link in an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/4ae26d1113eb2cdb0f18cedb036179cfaf0ff74e0cb6a605e4cdf357e3109a8c/analysis/1507708534/
bddca74a4da71137b8f780ff9c959a54_doc
Equifax website hacked again - redirects to fake Flash update
- https://arstechnica.com/information-technology/2017/10/equifax-website-hacked-again-this-time-to-redirect-to-fake-flash-update/
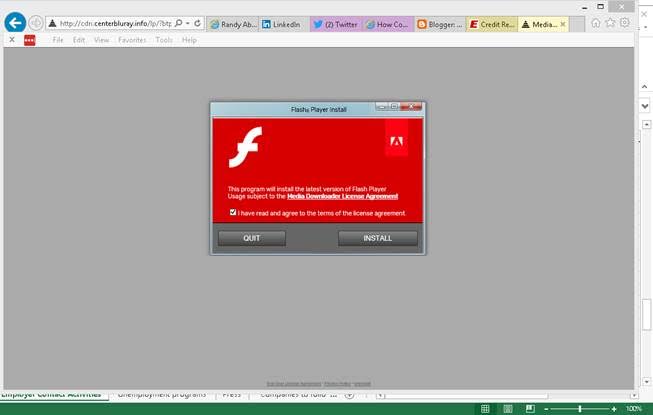
10/12/2017 - "In May credit reporting service Equifax's website was breached by attackers who eventually made off with Social Security numbers, names, and a dizzying amount of other details for some 145.5 million US consumers. For several hours on Wednesday the site was compromised again, this time to deliver -fraudulent- Adobe Flash updates, which when clicked, infected visitors' computers with adware that was detected by only three of 65 antivirus providers. Randy Abrams, an independent security analyst by day, happened to visit the site Wednesday evening to contest what he said was false information he had just found on his credit report. Eventually, his browser opened up a page on the domain hxxp :centerbluray .info that looked like this:
> https://cdn.arstechnica.net/wp-content/uploads/2017/10/first-flash.jpg
… he encountered the -bogus- Flash download links on at least three subsequent visits. The picture above this post is the higher-resolution screenshot he captured during one visit… The file that got delivered when Abrams clicked through is called MediaDownloaderIron.exe. This VirusTotal entry* shows only Panda, Symantec, and Webroot detecting the file as adware. This separate malware analysis from Packet Security** shows the code is highly obfuscated and takes pains to conceal itself from reverse engineering. Malwarebytes[3] flagged the centerbluray .info site as one that pushes malware, while both Eset and Avira provided similar malware warnings for one of the intermediate domains, newcyclevaults .com. In the hour this post was being reported and written, Abrams was unable to reproduce the -redirects- leading to the malicious download. It's possible Equifax has cleaned up its site. It's also possible the attackers have shut down for the night and have the ability to return at will to visit still worse misfortunes on visitors. Equifax representatives didn't respond to an e-mail that included a link to the video and sought comment for this post."
* https://www.virustotal.com/en/file/6153f429c0cedc721846e60255834ae0f43829cc6a387b766de6f301dab54eca/analysis/1506995209/
MediaDownloaderIron.exe
The link-in-the-email goes to
http ://analab .it/TransactionQuery_10-16-2017.zip which is actually a .rar file that needs to be renamed to .rar to extract it.
TransactionQuery_10-16-2017.jar (307kb) - Current Virus total detections 19/58*. Payload Security**… The basic rule is NEVER open any attachment or link in an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/5929096cdbee19f5fced5a00d69305c788ea1f7978655b1530ab52f1ee6c5185/analysis/
TransactionQuery_10-16-2017.jar
Fake 'Invoice' SPAM - delivers Locky or Trickbot
- https://myonlinesecurity.co.uk/necurs-downloaders-changed-to-fingerprint-the-computer-before-delivering-locky-or-trickbot/
18 Oct 2017 - "… downloaders from the Necurs botnet that deliver Locky ransomware or Trickbot banking trojan… I saw a few twitter links leading to this post on Bleeping Computer[1] saying that Locky (Necurs Downloaders) will take screenshots of the “victim’s” computer and send back error messages to base… Todays is an email pretending to come from invoicing@ random names and email addresses, with a subject like 'Invoice 009863361 10.18.2017' where the numbers are random with a blank/empty body…
One of the emails looks like: From: Invoicing
Date: Wed 18/10/2017 10:27
Subject: Invoice 009863361 10.18.2017
Attachment: Invoice 009863361 10.18.2017.7z
Body content:
totally empty blank
Invoice 009863361 10.18.2017.7z: Extracts to: Invoice 364776483 10.18.2017.vbs
Current Virus total detections 10/56[2]. Payload Security [3]| JoeSandbox[4].
Thanks to various Twitter contacts (my grateful thanks to them all for their hard work and expert knowledge) we have some downloads sites delivering Locky ransomware using USA IP numbers - VirusTotal 17/56[5]. Payload Security[6] from these locations:
dbatee .gr/niv785yg
goliathstoneindustries .com/niv785yg
3overpar .com/niv785yg
pciholog .ru/niv785yg
disfrance .net/p66/niv785yg
Joesandbox was given a different binary (sandbox pcap) that is a totally different size (VirusTotal 17/66[7]) (Payload Security[8]) it looks like the file must have been cut off during download. Using a different UK IP number, one researcher was given Trickbot banking trojan (VirusTotal 21/66[9]) (Payload Security[10]) from:
envi-herzog .de/iuty56g
pac-provider .com/iuty56g
pesonamas .co.id/iuty56g
disfrance .net/p66/iuty56g
… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
2] https://www.virustotal.com/en/file/d7767dfdbc9a2b607b8ae485e039d9fc910a39a80b0efe696f53a5f69d69914f/analysis/1508316046/
Invoice 364776483 10.18.2017.vbs