Fake 'pdf attachment' SPAM - delivers Locky/Dridex
- https://myonlinesecurity.co.uk/more-malware-via-embedded-word-macro-docs-in-pdf-attachments/
11 May 2017 - "… well used email template with subjects varying from with literally hundreds if not thousands of subjects. These generally deliver either Locky ransomware or Dridex banking Trojan.
File_69348406
PDF_9859
Scan_2441975
Document_11048
Copy_9762
They -all- have a pdf attachment that drops a word doc with macros… all downloads from these locations which delivers an encrypted txt file that should be converted by the macro to a working.exe file but Payload security…. doesn’t seem able to convert it… wipersdirect .com/f87346b
tending .info/f87346b
julian-g .ro/f87346b
I am being told this is a -new- ransomware called jaff ransomware*…
* https://twitter.com/siri_urz/status/862586080507424769
… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
Fake 'DHL Statements' SPAM - delivers js malware
- https://myonlinesecurity.co.uk/fake-dhl-statements-x-requests-required-delivers-malware/
11 May 2017 - "… an email with the subject of '6109175302 Statements x Requests Required' (random numbers) pretending to come frombgyhub@ dhl .com with a zip attachment containing -2- differently named .js files which delivers some sort of malware…
TYPE OF GOODS_DECLARATION.zip: Extracts to: DECLARATION (FORM).PDF.js -and- TYPE OF GOODS DOC.pdf.js
Current Virus total detections [1] [2]: Payload Security [3] [4] shows a download from one or both of these locations:
http ://schuetzen-neusalz .de/images/banners/gbfont.se -or- http ://wersy .net/cuts.vs which is renamed and autorun by the script (VirusTotal [5]) (Payload Security[6])… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
1] https://www.virustotal.com/en/file/36bd26e5331c26f7bc94e5ffa51dfd4db9356d74d885aa5f24d4c3b629b0ff1d/analysis/1494487534/
Malware spam with 'nm.pdf' attachment
- http://blog.dynamoo.com/2017/05/malware-spam-with-nmpdf-attachment.html
11 May 2017 - "Currently underway is a malicious spam run with various subjects, for example:
Scan_5902
Document_10354
File_43359
Senders are random, and there is -no- body text. In -all- cases there is a PDF attached named nm.pdf with an MD5 of D4690177C76B5E86FBD9D6B8E8EE23ED -or- 6B305C5B59C235122FD8049B1C4C794D (and possibly more). Detection rates at VirusTotal are moderate [1] [2].
The PDF file contains an embedded Word .docm macro document. Hybrid Analysis [3] [4] is partly successful, but it shows a run-time error for the malicious code, but it does demonstrate that malicious .docm file is dropped with a detection rate of 15/58[5].
Putting the .docm file back into Hybrid Analysis and Malwr [6] [7] shows the same sort of results, namely a download from: easysupport .us/f87346b …
UPDATE: A contact pointed out this Hybrid Analysis[X] which looks like basically the same thing, only in this sample the download seems to work. Note the references to "jaff" in the report, which -matches- this Tweet[8] about something called "Jaff ransomware".
That report also gives two other locations to look out for: trialinsider .com/f87346b
fkksjobnn43 .org/a5/
This currently gives a recommended blocklist of: 47.91.107.213
trialinsider .com
easysupport .us "
1] https://virustotal.com/en/file/e148fd38f2958aa8b0a3f64dae50f917e2d7f8ccf43c1f3dcdc6a2d43f4825e5/analysis/1494492097/
request-redelivery-2017053299810.pdf.js - Current Virus total detections 1/57*. Payload Security** shows a download from one of both or these locations
http ://schuetzen-neusalz .de/images/banners/gbfont.se -or- http ://wersy .net/cuts.vs
which is -renamed- and autorun by the script (VirusTotal 9/62***) (Payload Security[4])… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/28c866cf8ba31738592d0cfde6f2069b6e7888be190169fbd1037ccb27f430e6/analysis/1494500118/
7398219046.docx - Current Virus total detections 2/58*. Payload Security** shows the dropped .js file but doesn’t make it available for download. I had to get that manually (VirusTotal 1/55***) (Payload Security[4]) which shows
the same connections and download from one or both of these locations
http ://schuetzen-neusalz .de/images/banners/gbfont.se -or- http ://wersy .net/cuts.vs which is renamed and autorun by the script (VirusTotal 9/62[5]) (Payload Security[6])… This email attachment contains what appears to be a genuine word doc or Excel XLS spreadsheet with either a macro script or an embedded OLE object that when run will infect you… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/70cf3c05dcba5b3cfaa1e00fed8b954606b797bdc88346338a3c231b5a2561d4/analysis/1494509580/
20170512605164.pdf - which drops N5OSUHX.docm - Current Virus total detections [pdf*] [docm**]:
Payload Security [pdf…] [docm(4)] shows a download of an encrypted txt file from
http ://trebleimp .com/77g643 which is converted to by the macro to ratchet20.exe … It also shows a connection to
http ://h552terriddows .com/a5/ which gives a created message…
>> Update: managed to get the ratchet20.exe file via:
> https://jbxcloud.joesecurity.org/analysis/268338/1/html- (VirusTotal [5]) (Payload Security[6])… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/07c7f31f49a80220787f67a8f7de5966509cde051927a880e6eb411b39b8221f/analysis/1494559929/
U.K. Hospitals Hit - Widespread Ransomware Attack
- https://krebsonsecurity.com/2017/05/u-k-hospitals-hit-in-widespread-ransomware-attack/
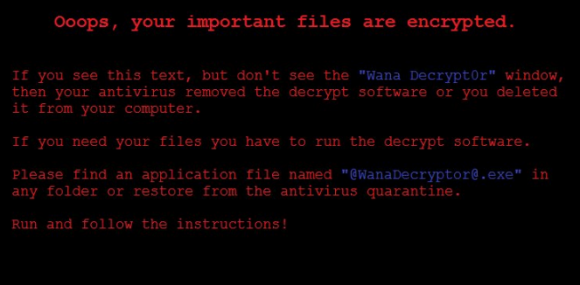
May 12, 2017 - "At least 16 hospitals in the United Kingdom are being forced to divert emergency patients today after computer systems there were infected with ransomware… there are indications the malware may be spreading to vulnerable systems through a security hole in Windows that was recently patched by Microsoft: Ransom note left behind on computers infected with the Wanna Decryptor ransomware strain.
Image: BleepingComputer
> https://krebsonsecurity.com/wp-content/uploads/2017/05/wanna-580x285.png
In a statement*, the U.K.’s National Health Service (NHS) said a number of NHS organizations had suffered ransomware attacks… According to CCN-CERT, that flaw is MS17-010**, a vulnerability in the Windows Server Message Block (SMB) service, which Windows computers rely upon to share files and printers across a local network. Malware that exploits SMB flaws could be extremely dangerous inside of corporate networks because the file-sharing component may help the ransomware spread rapidly from one infected machine to another…"
* https://www.digital.nhs.uk/article/1491/Statement-on-reported-NHS-cyber-attack
Indicators Associated With WannaCry Ransomware
- https://www.us-cert.gov/ncas/alerts/TA17-132A
Last revised: May 15, 2017 - "… According to numerous open-source reports, a widespread ransomware campaign is affecting various organizations with reports of tens of thousands of infections in as many as 74 countries, including the United States, United Kingdom, Spain, Russia, Taiwan, France, and Japan. The software can run in as many as 27 different languages. The latest version of this ransomware variant, known as WannaCry, WCry, or Wanna Decryptor, was discovered the morning of May 12, 2017, by an independent security researcher and has spread rapidly over several hours… Initial reports indicate the hacker or hacking group behind the WannaCry campaign is gaining access to enterprise servers either through Remote Desktop Protocol (RDP) compromise or through the exploitation of a critical Windows SMB vulnerability. Microsoft released a security update for the MS17-010* (link is external) vulnerability on March 14, 2017. Additionally, Microsoft released patches for Windows XP, Windows 8, and Windows Server 2003 (link is external) operating systems on May 13, 2017. According to open sources, one possible infection vector is via phishing emails…
* https://technet.microsoft.com/en-us/library/security/ms17-010.aspx
March 14, 2017
The WannaCry ransomware received and analyzed by US-CERT is a loader that contains an AES-encrypted DLL. During runtime, the loader writes a file to disk named “t.wry”. The malware then uses an embedded 128-bit key to decrypt this file. This DLL, which is then loaded into the parent process, is the actual Wanna Cry Ransomware responsible for encrypting the user’s files. Using this cryptographic loading method, the WannaCry DLL is never directly exposed on disk and not vulnerable to antivirus software scans…
Precautionary measures to mitigate ransomware threats include:
- Ensure anti-virus software is up-to-date.
- Implement a data back-up and recovery plan to maintain copies of sensitive or proprietary data in a separate and secure location. Backup copies of sensitive data should not be readily accessible from local networks.
- Scrutinize -links- contained in -e-mails- and do -not- open -attachments- included in unsolicited e-mails.
- Only download software – especially free software – from sites you know and trust.
- Enable automated patches for your operating system and Web browser…" (More detail at the us-cert URL at the top of this post).
Fake 'invoice' SPAM - delivers pdf attachment jaff ransomware
- https://myonlinesecurity.co.uk/more-fake-invoice-malspam-with-pdf-attachments-deliver-malware/
15 May 2017 - "An email pretending to be an invoice coming from random senders with a PDF attachment that drops a malicious macro enabled word doc…
Update: confirmed as Jaff ransomware (VirusTotal 5/61*) (Payload Security**)…
… An alternative docm file that was extracted confirms it to be jaff ransomware downloads
ecuamiaflowers .com/hHGFjd encrypted txt (Payload Security[3]) (VirusTotal 13/56[4]) JoeSandbox[/5]… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/41bce3e382cee06aa65fbee15fd38f7187fb090d5da78d868f57c84197689287/analysis/1494846406/
Fake 'invoice' SPAM - downloads Cerber ransomware
- https://myonlinesecurity.co.uk/blank-email-with-fake-invoice-attachment-tries-to-deliver-malware/
16 May 2017 - "… an empty/blank email with the subject of 'Re: invoice 28769' coming or pretending to come from random companies, names and email addresses with a semi-random named zip attachment that contains another zip that in turn contains a .js file… downloads Cerber ransomware…
… I am reliably informed[1] that with a couple of minor fixes to correct the malware developers mistakes this downloads Cerber ransomware from
hxxp ://mdnchdbde .pw/search.php which delivers a file 1 (VirusTotal 6/59*) (Payload Security**)… 'certain that they will fix it in the next malspam run. These criminal gangs often send a small spam run out to “test the waters” and when they don’t get any expected result they double check & fix the errors ready for the next spam run.
262647732.zip: extracts to 27000_packed.zip: which in turn Extracts to: 27000.js
Current Virus total detections 0/57[3]: Payload Security[4] Joebox[5] - none of the online sandboxes managed to get any download location or malware content from the .js file… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
1] https://twitter.com/Techhelplistcom/status/864350538112016385
Fake 'pdf attachments' SPAM - delivers Jaff ransomware
- https://myonlinesecurity.co.uk/pdf-pretending-to-come-from-your-own-email-address-delivers-jaff-ransomware/
16 May 2017 - "… series of emails with pdf attachments that drops a malicious macro enabled word doc is an email with the subject of 'Emailing: 2650032.pdf' (random numbers) pretending to come from random names at your-own-email-address that delivers Jaff ransomware…
2650032.pdf - Current Virus total detections 8/54*: Payload Security**… drops EYRCUD.docm
(VirusTotal 8/59***) (Payload Security[4])… downloads an encrypted txt file from
http ://personalizar .net/Nbiyure3 which is converted by the script to galaperidol8.exe … DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/81263bf1012dc78c945d651d9c4b07c435292eeb23429d4fc8204c8606a2d565/analysis/1494926923/
… criminals sending these have registered various domains that look like genuine bank domains. Normally there are 3 or 4 newly registered domains that imitate the bank or some message sending service that can easily be confused with a legitimate organisation in some way that send these. So far we have only found 1 domain today banklinersa .co.uk. As usual they are registered via Godaddy as registrar and for a change the emails are sent via rackspace hosting not the usual citynetwork AB in Sweden. They are currently using IP numbers [removed], [removed], [removed], [removed], 104.239.169.15, 104.130.29.243, 104.130.29.245, 172.99.115.29…
SecureMessage.doc - Current Virus total detections 4/56*. Payload Security** downloads from
http ://ocysf .org/wp-content/GktpotdC7dyTH1aoroa.png which of course is -not- an image file but a renamed .exe file that gets -renamed- to a .exe and autorun (VirusTotal 10/60***)… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/e2c6710d4d1b9aa22073404195644b43318b75fd35812dcb485407d92aaa4c68/analysis/1495019899/
Adobe account - Phish
- https://myonlinesecurity.co.uk/adobe-account-phishing-scam-using-text-data-urls/
17 May 2017 - "… 'thought this was going to be some newer malware delivery method, but it is only -phishing- for email credentials, which of course is also extremely serious and very bad.
NOTE: This phishing scam only works in Google Chrome. Internet Explorer will not open data:text/html urls and gives a 'cannot display' page message. Firefox refuses to display anything - just a white screen with the original url in the address bar…
This email has a genuine PDF attachment that contains a blurred out image of an invoice with the prompt to view the Secured PDF Online Document on Adobe:
> https://myonlinesecurity.co.uk/wp-content/uploads/2017/05/invoice1246_pdf.png
-If- you click on the blurred image you get a pop up warning about links. When you follow the link inside the pdf it sends you to http ://tiny .cc/tis7ky which immediately -redirects- to
http ://qualifiedplans .com/administrator/components/com_smartformer/plugins/tiny_mce/plugins/inlinepopups/skins/clearlooks2/img/phmho/
where it downloads/opens a data:text url that displays a web page on your computer -not- an external site looking like:
> https://myonlinesecurity.co.uk/wp-content/uploads/2017/05/timed_out.png
After you press OK you get what looks-like an Adobe Business sign in page with what looks-like a download button. I inserted the usual set of fake details & pressed download, expecting some sort of malware to appear, but no it just -bounced- me on to the genuine Adobe page while your stolen data is sent to http ://setas2016 .com/image/catalog/Katalog/files/pageConfig/PDF3/index/adobe.php
With a bit of digging around We have discovered the compete phish is also hosted on http ://setas2016 .com/image/catalog/Katalog/files/pageConfig …
> https://myonlinesecurity.co.uk/wp-content/uploads/2017/05/adobe_sign_in.png
The data:text/html file is available for download via Payload Security*. It is in the extracted files section named urlref_httptiny .cctis7ky …"
* https://www.hybrid-analysis.com/sample/55c88958e5bf3b9f8c940ce3bbd2e5e0a7e437f56402e0b6b807191af30d913f?environmentId=100
ICS-ALERT-17-135-01A Indicators Associated With WannaCry Ransomware (Update A)
> https://ics-cert.us-cert.gov/alerts/ICS-ALERT-17-135-01A
Original release date: May 15, 2017 | Last revised: May 16, 2017
"… updated alert is a follow-up to the original alert titled ICS-ALERT-17-135-01 Indicators Associated With WannaCry Ransomware that was published May 15, 2017, on the NCCIC/ICS-CERT web site…" (More detail at the URL above.)
Fake 'UPS' SPAM - delivers banking Trojan
- https://myonlinesecurity.co.uk/fake-parcel-delivery-services-malspam-with-word-doc-attachment-delivers-ursnif-banking-trojan/
18 May 2017 - "… some are being delivered with the word -doc- attachment, but about half are just getting the email body with an -HTML- attachment which has the same details as the email body and no word doc attachment… the details with an email with the subject of 'Fwd: UPS Worldwide Saver Notification' pretending to come from various random names @ yahoo. es -or- .de -or- .pt -or- from random@ hotmail .es -or- de . We are also seeing a sprinking from other free webmail services like web .de with a malicious word doc attachment with a random number delivers ursnif banking Trojan. I am also seeing other parcel delivery companies like TNT and unnamed delivery services also being imitated and -spoofed- in this campaign. The TNT ones are zips with word docs inside. -All- of them today are using embedded OLE objects rather than macros to deliver Ursnif banking and password stealing Trojans. Update: Now seeing some coming through with zip attachments containing .js files
Some subjects include:
TNT Express – Documents – RL54413826 ( random numbers)
Order Processed
Export Scan
Fwd: UPS Worldwide Saver Notification …
doc60 for clearance.doc - Current Virus total detections 0/58*. Payload Security** drops a js file
(VirusTotal 1/22***) (Payload Security[4]) downloads from one of these 2 locations:
http ://dacera .net/horizont.cv -or- http ://raimco .com/case.sub
and gets converted/renamed to a working .exe file (VirusTotal 9/61[5])
TNT version: RL82670483822.zip extracts to RL02993847001.doc VirusTotal 0/57[6]| Payload Security[7]
Fake 'FedEx' SPAM - delivers -kovter- malware
- https://myonlinesecurity.co.uk/big-changes-in-fedex-fake-delivery-emails-now-using-macros/
18 May 2017 - ""An email with the subject of 'FedEx Parcel #262844740, Delivery Unsuccessful' pretending to come from FedEx Customer Service (random email addresses) with a malicious word doc attachment delivers multiple malware… 'used to seeing these -fake- FedEx and other parcel delivery services emails, but they usually contain zip files and js files. It is -unusual- to have word macro attachments…
info_delivery.doc - Current Virus total detections 5/58*. Payload Security** shows a download from
http ://regereeeeee .com/gate2.php?ff1 which appears to be a massive encrypted txt file (833kb) which appears to drop -kovter- (b215.exe ***) (VirusTotal 14/61[4])… This email attachment contains what appears to be a genuine word doc or Excel XLS spreadsheet with either a macro script -or- an embedded OLE object that when run will infect you… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/0c0460a6c234300c13c65bc1e63f9930a9b86df6ed68dde1645b557c0cdc2b00/analysis/
625855442530.zip - extracts to 1.doc - Current Virus total detections 0/56*. Payload Security**
- drops a js file… (BR16E2~1 .JS) - VirusTotal 2/56[3] | Payload Security[4] downloads from
http ://oldloverfg .top/admin.php?f=2 which gave yez348746.tae (VirusTotal 12/61[5]) | Payload Security[6]
While encrypting your files the js file drops this html file with instructions how to pay the ransom & retrieve your files. They are charging 1 bitcoin which is currently approx. $2000 USD…
> https://myonlinesecurity.co.uk/wp-content/uploads/2017/05/GlobeImposter-ransom-note.png
… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/73344f56cbd115c785632bae76ddfd1371399a5ba2bd06af0397ba5c000217fe/analysis/1495370663/
43412591.PDF - Current Virus total detections 13/56*. Payload Security** - drops QDLCPQKK.doc
(VirusTotal 10/58[3]) (Payload Security [4]) downloads an encrypted txt file from
http ://primary-ls .ru/jhg6fgh which is converted by the script to buzinat8.exe (VirusTotal 7/58[5])
There are 4 hardcoded (slightly obfuscated) download sites in the macro (there will be more in other versions)
primary-ls .ru\jhg6fgh
brotexxshferrogd .net\af\jhg6fgh
herrossoidffr6644qa .top\af\jhg6fgh
joesrv .com\jhg6fgh
… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/7f966606c28752e0ab7a45b07c48f078e6f7ec8ea8070c7af64a66c9f0897bec/analysis/1495454756/
Jaff ransomware gets a makeover: fake -invoice- theme
- https://isc.sans.edu/forums/diary/Jaff+ransomware+gets+a+makeover/22446/
2017-05-24 - "Since 2017-05-11, a new ransomware named 'Jaff' has been distributed through malicious spam (malspam) from the 'Necurs botnet':
> https://securityintelligence.com/the-necurs-botnet-a-pandoras-box-of-malicious-spam/
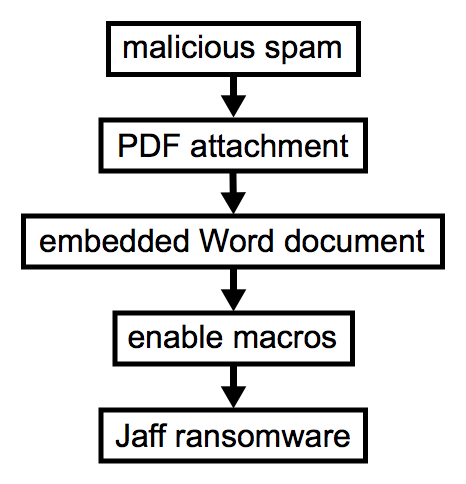
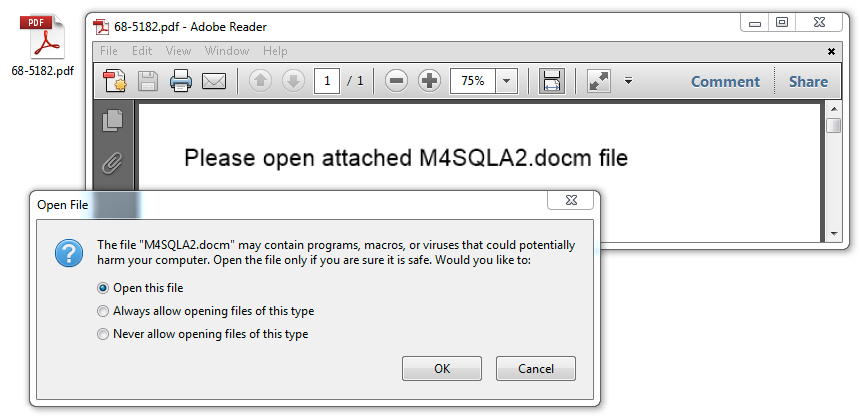
This malspam uses PDF -attachments- with 'embedded Word documents' containing -malicious- macros. Victims must open the PDF attachment, -agree- to open the embedded Word document, then -enable- macros on the embedded Word document to -infect- their Windows computers:
> https://isc.sans.edu/diaryimages/images/2017-05-24-ISC-diary-image-01.jpg
Prior to -Jaff- we've seen waves of malspam using the same PDF attachment/embedded Word doc scheme to push
-Locky- ransomware. Prior to that, this type of malspam was pushing -Dridex-. With all the recent news about
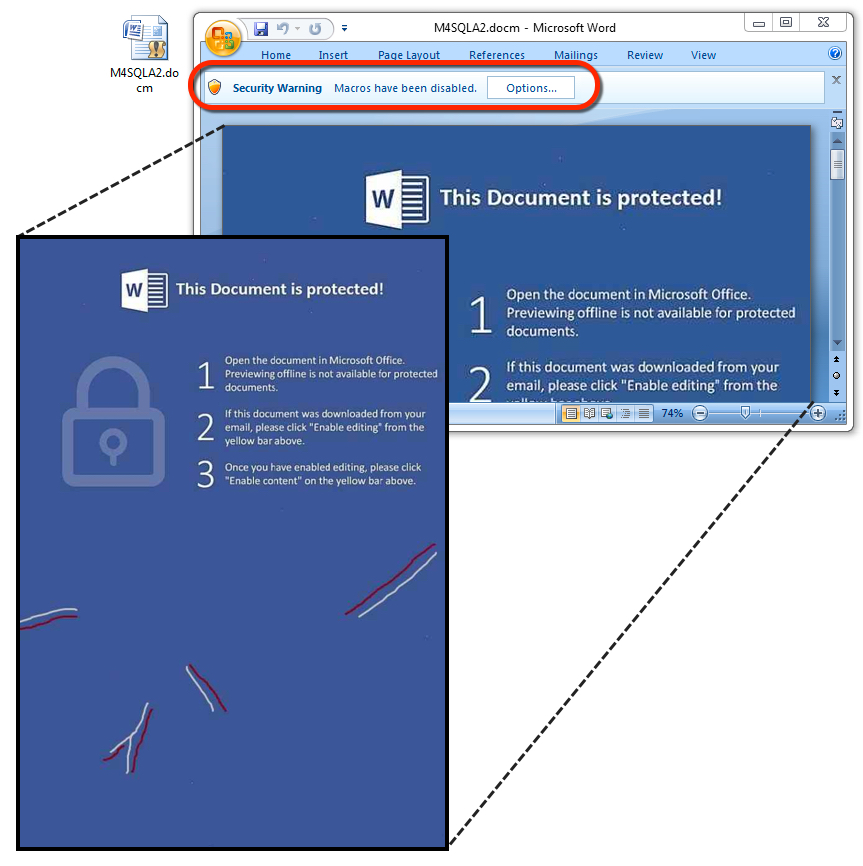
-WannaCry- ransomware, people might forget Jaff is an ongoing threat. Worse yet, some people might not know about it at all since its debut about 2 weeks ago. Jaff has already gotten a makeover, so an infected host looks noticeably different now… The emails: This specific wave of malspam used a -fake- invoice theme… I collected -20- emails… these emails -all- have PDF attachments, and each one contains an embedded Word document. The Word document contains malicious-macros designed to -infect- a Windows computer:
> https://isc.sans.edu/diaryimages/images/2017-05-24-ISC-diary-image-05.jpg
The embedded Word document with malicious macros:
> https://isc.sans.edu/diaryimages/images/2017-05-24-ISC-diary-image-06.jpg
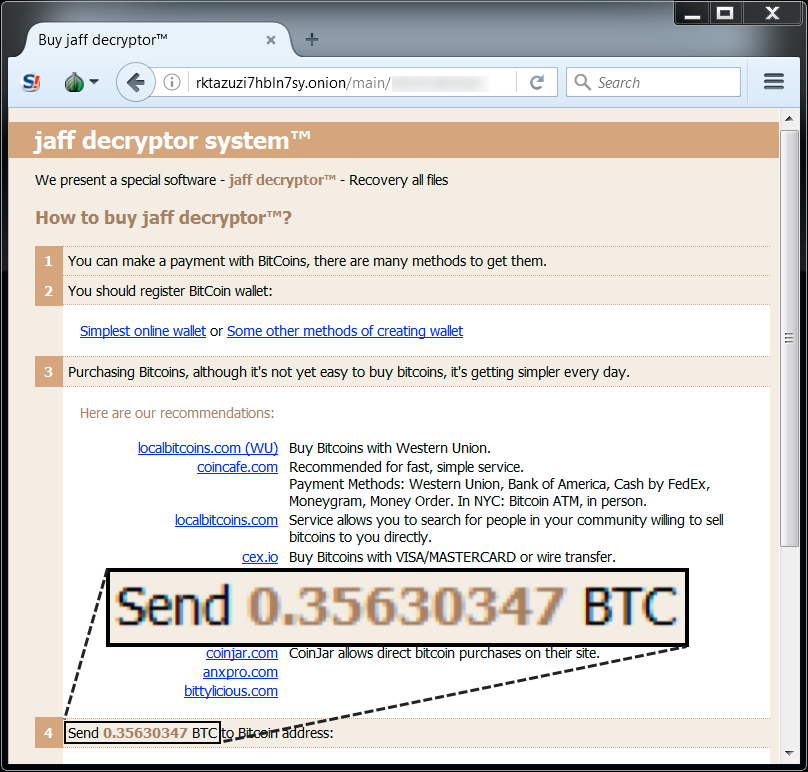
Follow the entire infection chain, and you'll see minimal network traffic compared to other types of malware. The Word macros generate an initial URL to download an encoded Jaff binary, then we see one other URL for post-infection callback from an infected host… My infected host asked for 0.35630347 bitcoin as a ransom payment:
> https://isc.sans.edu/diaryimages/images/2017-05-24-ISC-diary-image-14.jpg
… Much of this malspam is easy to spot among the daily deluge of spam most organizations receive. However, this PDF attachment/embedded Word doc scheme is likely an attempt to bypass spam filtering… as long as it's profitable for the criminals behind it, we'll continue to see this type of malspam…"
> http://www.malware-traffic-analysis.net/2017/05/24/index.html (More detail at the isc URL at the top of this post.)
Fake 'receipt' SPAM - delivers Jaff ransomware
- https://myonlinesecurity.co.uk/more-jaff-ransomware-delivered-via-fake-receipts-or-payments-emails/
25 May 2017 - "… emails with pdf attachments that drops a malicious macro enabled word doc is an email with various subjects along the line of 'receipt, payment, payment receipt' etc. (random numbers) pretending to come from donotreply@ random email addresses and companies that delivers Jaff ransomware…
P4830.pdf - Current Virus total detections 12/56*. Payload Security** drops ELMIRJX.doc
(VirusTotal 4/23[3]) (Payload Security[4]) downloads an encrypted txt file from
http ://dreamybean .de/TrfHn4 which should be converted by the script to bruhadson8.exe (unfortunately payload security is showing this as a tiny data file, so something is going wrong there and there must be an anti-analysis element to the malware). There are 4 hardcoded (slightly obfuscated) download sites in the macro (there will be more in other versions)… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/dc799fd5ae8f2fcbb6379ab278beddb3c950fe8abf5de0bbfa59b0982c59b75d/analysis/1495710733/
… email with the subject of '2nd Reminder Final Demand – Notice of Legal Intention' pretending to come from creditcontrol@ bookatable .com with a malicious word doc attachment eventually delivers sharik/smoke loader after a convoluted download system involving .hta files and PowerShell…
294616_05152017.rtf - Current Virus total detections 28/57[1]. Payload Security[2] downloads an HTA file from
http :// 185.162.8.231 :64646/logo.doc (VirusTotal 0/57[3]) which in turn uses powershell to download
http :// 185.162.8.231 :64646/00001.exe (VirusTotal 48/59[4]) (Payload Security[5])… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
1] https://www.virustotal.com/en/file/cccb5e19651e18a6ca1642ec337be70972efe160778a2407136af031ca9242e9/analysis/1494977406/
invoice-0063827410370260857-000001870346531780753154078347.pdf.js - Current Virus total detections 5/56[1]
Payload Security[2] shows a download of various files from the same server one being auvrq.exe
(VirusTotal 20/61[3]) (Payload Security[4])… The link in email body (in the working versions) goes to
http ://dhlmailsystem .com/documentdir/777126146374729609489374827 where you get slightly different behaviour depending on what browser you use to visit. If you use Internet Explorer or Google Chrome, you get a zip file containing a .js file. Using Firefox you get the .js file itself… you first see a page like this (-b-) with a message saying 'preparing download' with a countdown marker. When it reaches 0 the message becomes a -link- saying “click here to download if not started automatically” and the malware file is delivered… The basic rule is NEVER open any attachment -or- link in an email, unless you are expecting it…"
1] https://www.virustotal.com/en/file/eb20f58ad1f75f7f30456a0a82e985cd9cea5fd0d7c50d76b7ee06a9b7a1b10f/analysis/1495836615/
Fake 'documents' SPAM - xls attachment delivers malware
- https://myonlinesecurity.co.uk/documents-malspam-delivers-unknown-malware/
30 May 2017 - "An email with the subject of 'documents' pretending to come from random senders with a malicious word doc or Excel XLS spreadsheet attachment delivers malware… Some subjects in this malspam campaign include … inv. payment
documents
Fake 'FedEx USPS UPS' SPAM - delivers Kovter and ransomware
- https://myonlinesecurity.co.uk/fake-fedex-usps-ups-delivery-notifications-continue-to-deliver-kovter-and-ransomware/
1 Jun 2017 - "… malware via the “cannot deliver your parcel notifications” or “check where your parcel is”
-spoofing- FedEx, DHL, UPS, USPS etc. have changed the delivery method. The emails are still very similar to the ones we are used to seeing with this sort of subject line: USPS issue #06914074: unable to delivery parcel
Parcel #006514814 shipment problem, please review
USPS parcel #3150281 delivery problem
Courier was not able to deliver your parcel (ID006976677, USPS)
Parcel 05836911 delivery notification, USPS
Delivery Status Notification
… What has changed is the -attachment- to the emails contains the malware. These now contain an HTML attachment that when opened displays a webpage on your computer that pretends to be a Microsoft Word online website and says you need to download the 'MSOffice365 Webview Plugin update', with a -blurry-image- of scrambled writing in the background with this message prominantly displayed:
'This document cannot be read in your browser. Download and install latest plugin version':
> https://i2.wp.com/myonlinesecurity.co.uk/wp-content/uploads/2017/06/fedex_msoffice_webview.png?ssl=1
… 'previously described in THIS post from Mid April 2017* which shows the obfuscated/encoded nature of the files and how to decode/de-obfuscate them… At that time they linked to a remote website using the -fake- MSOffice365 scam. These malware gangs use a mix-and-match of different techniques to try to stay one step ahead of researchers and antivirus companies and gain more victims:
* https://myonlinesecurity.co.uk/changes-to-fake-usps-delivery-messages-delivering-malware/
… Infection chain from 31 May 2017:
1. FedEx-Delivery-Details-ID-8AXP4QH0.doc.html attachment (VirusTotal 2/56[1]) (Payload Security[2])
2. Install-MSOffice365-WebView-Plugin-Update-0.165.11a.zip extracts to:
3. Install-MSOffice365-WebView-Plugin-Update-0.165.11a.exe.js (VirusTotal 8/55[3]) (Payload Security[4])
Counter.js (VirusTotal 5/56[5]) which downloads 2 files pretending to be png (image files that are -renamed- .exe files) 1.exe currently Cerber -Ransomware- (VirusTotal 8/61[6]) (Payload Security[7]) 2.exe currently Kovter
(VirusTotal 12/60[8]) (Payload Security[9]). The 5 sites embeded in the original webview plugin.js are:
leadsfunnel360 .com
khushsingh .com
kskazan .ru
moodachainzgear .com
thegreenbook .ca
… where you get counter.js … that when decrypted gives these 5 sites:
sharplending .com
moodachainzgear .com
buildthenewcity .biz
valdigresta .com
leadsfunnel360 .com
… Where Cerber ransomware and Kovter… the js files try to contact the sites in order they are listed. It then tries each combination of sitename/counter/etc. and if any site fails to respond, then moves to next site in the list and continues to do that until the counter.js & the actual malware files are downloaded-and-run on the victim’s computer… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
1] https://www.virustotal.com/en/file/68bbe1e4ca5a73a688912dbe70fc0f71f23aaadb740bbdb549b653a451c11e03/analysis/1496239829/
FedEx-Delivery-Details-ID-8AXP4QH0.doc.html
Invoice INV-0790.pdf - Current Virus total detections 12/56*. Payload Security** drops 231GEOHJWMQN935.docm
(VirusTotal 10/59[3]) (Payload Security[4]) downloads an encrypted txt file from
http ://lanphuong .vn\hH60bd which is converted by the script to miniramon8.exe
(VirusTotal 8/62[5]) (Payload Security[6]).
There are 4 hardcoded (slightly obfuscated) download sites in the macro (there will be more in other versions)
lanphuong .vn\hH60bd
newserniggrofg .net\af\hH60bd
resevesssetornument .com\af\hH60bd
mountmary .ca\hH60bd
… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/d1fd17c76c4458c45e7edd077ed8afab3ae2589fa2e81e6d593c7d8f5cc2846d/analysis/1496395482/