Fake 'Sage Invoice' SPAM - delivers Trickbot
- https://myonlinesecurity.co.uk/trickbot-banking-trojan-delivered-by-spoofed-sage-outdated-invoice/
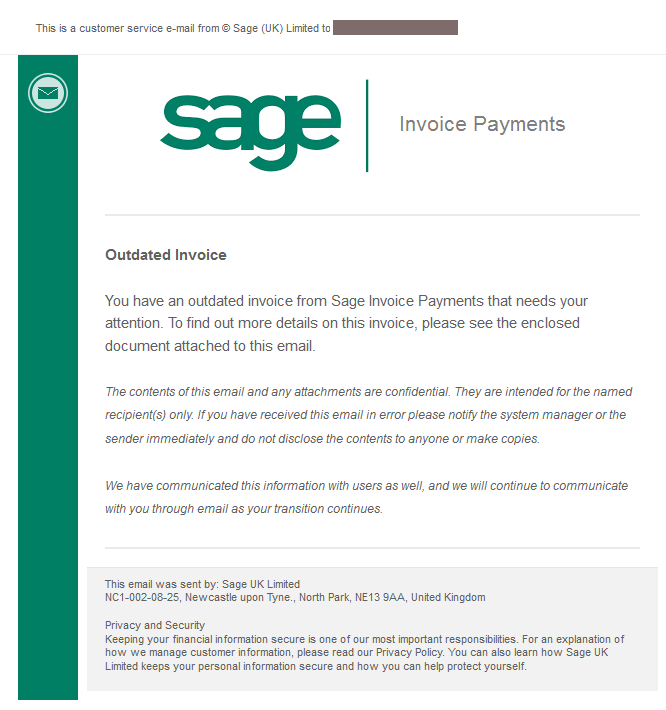
17 Nov 2016 - "An email with the subject of ' pretending to come from 'Sage Invoice' with a malicious word docdelivers Trickbot banking Trojan… sageinvoices .com / sage-invoice .com /sage-invoices .com are all newly created -yesterday- … domains sending these emails include:
Sage Invoice
Sage Invoice
Sage Invoice …
17 November 2016: SageInvoice.doc - Current Virus total detections 3/54*
Payload Security** shows a download from http ://delexdart .com/images/gfjfgklmslifdsfnln.png which is not a png file but a renamed .exe file which is renamed by the macro to scsadmin.exe and auto run using PowerShell (VirusTotal ***)… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/6f5f73e8917c99da56ce48d7f9a0cecd969aee6023ce04841a623aaed4681da2/analysis/1479380615/
Attached is a malicious Word document named SageInvoice.doc with a detection rate of 3/54*. Hybrid Analysis** shows malicious network traffic to:
substan.merahost .ru/petrov.bin [185.86.77.224] (Mulgin Alexander Sergeevich aka gmhost .com.ua, Ukraine)
A malicious file scsnsys.exe is dropped with a detection rate of 8/53***.
The domain sage-invoices .com has been registered by criminals for this action, presumably to allow encrypted end-to-end communication… I recommend that you -block- traffic from that domain or check your filters to see who may have it.
Recommended blocklist: sage-invoices .com
185.86.77.0/24 "
* https://virustotal.com/en/file/79ff976c5ca6025f3bb90ddfa7298286217c21309c897e6b530603d48dea0369/analysis/
17 November 2016: invoice_2222.zip: Extracts to: invoice_1711.js - Current Virus total detections 2/54*
MALWR** shows an attempted download of a file from http ://www .tessaban .com/admin/images/ospspps.png currently giving a 404 not found which should be renamed by the script to an .exe file… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/40679f44e4d62b42b621a3450f51b5fa5a706796cbe2d203e1dc128fa4d511e8/analysis/1479370770/
Fake AMEX Phish
- https://myonlinesecurity.co.uk/please-activate-your-personal-security-key-american-express-phishing/
17 Nov 2016 - "… The subject is 'Please activate your Personal Security Key' coming from American Express
. Additional sending addresses so far found include:
Amex-mails .com | amexmails .com | amex-emails .com | amexmails .com
were -all- registered -today- by surprise, surprise: Godaddy .com. They currently do not have an IP number associated with them. When they were received, the emails came from:
[removed] - San Antonio Texas US AS27357 Rackspace Hosting …
The weird thing is the emails appear -blank- when opened in Outlook, but using view source I can see the email in its full glory, including the links-to-click to get to the-phishing-site… A screenshot of the html is:
> https://i1.wp.com/myonlinesecurity.co.uk/wp-content/uploads/2016/11/american_express_safe_key.png?fit=678%2C913&ssl;=1
Alternative links in emails go to:
http :// amexsafekeys .com | http ://americanexpressafekey .com | http ://amex-mails .com
| http:// amexmails .com
aexpsafekeys .com was registered -yesterday- 16 November 2016 and hosted on these IP addresses: [removed] | [removed] which look like they belong to a -Russian- network.
http ://amexsafekeys .com was also registered -yesterday- by the same Russian name and hosted on same IP addresses: [removed] | [removed]
http ://americanexpressafekey .com also registered -yesterday- same IP addresses. Following the link to aexpsafekeys .com, you get a typical phishing page like this, where they want all the usual information about you, your family and bank/credit cards etc.:
> https://i2.wp.com/myonlinesecurity.co.uk/wp-content/uploads/2016/11/amex_phishing_safe_key.png?resize=1024%2C603&ssl;=1 "
18 November 2016: Exceeded Limit Spreadsheet.exe - Current Virus total detections 15/57*
Payload Security** shows lots of files being dropped/extracted from this file which is renamed by itself to winlogin.exe and in turn drops a multitude of identical xml files and a java.jar file which is Java Jacksbot (VirusTotal 23/56***)… All 3 links (there is one behind the image) go to:
http ://webkamagi .com/admin/images/Send Limit Exceeded.html where you see this screenshot that starts off with a circle and the words scanning and ends up looking like this that auto-downloads a file from:
http ://gicfamily .org/admin/file/Exceeded%20Limit%20Spreadsheet.exe (if for some reason it doesn’t auto-download then the download button delivers the malware):
> https://i1.wp.com/myonlinesecurity.co.uk/wp-content/uploads/2016/11/nortonscan.png?w=863&ssl=1
The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/a7d17122ff9a948d7b21464f75ce7644d44307c20c3536385ec0926e913d32d4/analysis/1479432563/
Ransomware hits record levels
- https://www.helpnetsecurity.com/2016/11/18/encryption-ransomware-hits-record-levels/
Nov 18, 2016 - "The amount of phishing emails containing a form of ransomware grew to 97.25 percent during the third quarter of 2016 up from 92 percent in Q1:
> https://www.helpnetsecurity.com/images/posts/phishme-112016-1.jpg
PhishMe’s Q3 2016 Malware Review identified three major trends previously recorded throughout 2016, but have come to full fruition in the last few months:
Locky continues to dominate: While numerous encryption ransomware varieties have been identified in 2016, Locky has demonstrated adaptability and longevity.
Ransomware encryption: The proportion of phishing emails analyzed that delivered some form of ransomware has grown to 97.25 percent, leaving only 2.75 percent of phishing emails to deliver all other forms of malware utilities. Increase in deployment of ‘quiet malware’: PhishMe identified an increase in the deployment of remote access Trojan malware like jRAT, suggesting that these threat actors intend to remain within their victims’ networks for a long time. During the third quarter of 2016, PhishMe Intelligence conducted 689 malware analyses, showing a significant increase over the 559 analyses conducted during Q2 2016. Research reveals that the increase is due, in large part, to the consistent deployment of the Locky encryption ransomware. Locky executables were the most commonly-identified file type during the third quarter, with threat actors constantly evolving the ransomware to focus on keeping this malware’s delivery process as effective as possible…
> https://www.helpnetsecurity.com/images/posts/phishme-112016-2.jpg
While ransomware dominates the headlines, PhishMe’s Q3 Malware Review reveals that other forms of malicious software delivered using remote access Trojans, keyloggers and botnets still represent a significant hazard in 2016. Unlike ransomware, so-called ‘quiet malware’ is designed to avoid detection while maintaining a presence within the affected organization for extended periods of time. While only 2.75 percent of phishing emails delivered non-ransomware malware, the diversity of unique malware samples delivered by these emails far exceeded that of the more numerous ransomware delivery campaigns…"
> http://phishme.com/2016-q3-malware-review/
Fake 'Spam mailout' SPAM - delievers Locky
- https://myonlinesecurity.co.uk/locky-delivered-by-spoofed-isp-you-have-been-sending-spam-notifications/
21 Nov 2016 - "… Locky downloader… an email pretending to come from an ISP, saying that you have been sending spam with the subject of 'Spam mailout' coming as usual from random companies, names and email addresses with a semi-random named zip attachment in the form of logs_recipients name.zip… Locky has changed the encrypted file extension to .aesir - See:
- https://myonlinesecurity.co.uk/locky-changed-to-use-aesir-file-extension-and-changed-c2-format/
"… Locky has changed the encrypted file extension to .aesir as well as the C2 to “/information.cgi”. I am also informed there is a slight change to the name of the ransomware notification file that they drop on your desktop. It appears to now be _[number]-INSTRUCTION.html "
One of the emails looks like: From: Lula Mcmahon
Date:Mon 21/11/2016 07:37
Subject: Spam mailout
Attachment: logs_hajighasem1c.zip
Dear hajighasem1c
We’ve been receiving spam mailout from your address recently.
Contents and logging of such messages are in the attachment.
Please look into it and contact us.
Best Regards,
Lula Mcmahon
ISP Support …
Fake 'Amazon' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/locky-delivered-by-spoofed-your-amazon-com-order-has-dispatched/
21 Nov 2016 - "… email with the subject of 'Your Amazon .com order has dispatched (#713-7377848-7745100)
(random numbers) pretending to come from Amazon Inc with a zip attachment matching the subject. It looks like -Locky has- changed the encrypted file extension to .aesir as well as the C2 to “/information.cgi”… One of the emails looks like: From: Amazon Inc
Date: Mon 21/11/2016 09:40
Subject: Your Amazon .com order has dispatched (#713-7377848-7745100)
Attachment: ORDER-713-7377848-7745100.zip
Dear Customer,
Greetings from Amazon .com,
We are writing to let you know that the following item has been sent using Royal Mail.
For more information about delivery estimates and any open orders, please visit…
Your order #713-7377848-7745100 (received November 20, 2016)
Note: this e-mail was sent from a notification-only e-mail address that can=
not accept incoming e-mail. Please do not reply to this message.=20
Thank you for shopping at Amazon .com …
21 November 2016: ORDER-713-7377848-7745100.zip: Extracts to: KBDGUB350132.js
Current Virus total detections 11/55*. MALWR** shows a download of an encrypted file from
http ://jmltda .cl/hfvg623?wCTlMeE=wCTlMeE which is renamed by the script to wCTlMeE1.dll
(VirusTotal 9/57***). C2 are http :// 89.108.73.124 /information.cgi | http :// 91.211.119.98 /information.cgi
http ://185.75.46.73 /information.cgi. Payload Security [4]shows the same… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/7d8f69106ca48bd9c3946487e9c0bce95347a6705487b23bc2df7e3d51469ba0/analysis/1479721475/
The link in the email actually goes to a page at reg .vn /en/view_bill.php?id=encoded-email-address (where the last part is the email address in Base 64 encoding). It downloads a malicious document lgm_bill69290.doc with a current detection rate of 8/55*. Automated analysis [1] [2] shows malicious network traffic… A malicious executable is dropped with a detection rate of 7/57**. The payload appears to be Hancitor/Vawtrak. The domain secure-lgm .com appears to have been created for the purposes of sending the email… probably fake WHOIS details…
Recommended blocklist: 95.215.111.222
newaronma .com
libinvestusa .com "
* https://www.virustotal.com/en/file/fc1f1845e47d4494a02407c524eb0e94b6484045adb783e90406367ae20a83ac/analysis/
Something evil on 64.20.51.16/29…
- http://blog.dynamoo.com/2016/11/something-evil-on-6420511629-customer.html
21 Nov 2016 - "I wrote about this evil network on 64.20.51.16/29 (a customer of Interserver, Inc) over a year ago*, identifying it as a hotbed of fraud. Usually these bad networks don't hang around for very long, but in this case it seems to be -very- persistent. This time it came to notice from a terse spam with a PDF attached: From: Lisa Liang [ineedu98@ hanmail .net]
To: me@ yahoo .com
Date: 20 November 2016 at 23:23
Subject: 11/21/2016 Amended
FYI
Attached is a file Amended copy.pdf which when you open it (-not- recommended) looks blurry with "VIEW" in big red letters… The link-in-the-email goes to bit .ly/2fJbyol - if you put the "+" on the end of a Bitly link then you can see the number of -clickthroughs- and what the landing page is (www .serviceupgrade .tech/pdf.php in this case)… Clicking through gives you a login page for "Adobe PDF Online" which is of course a generic -phishing- page… Analysis of the 64.20.51.16/29 range finds -193- sites historically connected with it marked as being -phishing- or some other -malicious- activity. There are at least -284- sites currently within that range, of which the following are -both- hosted in that range currently and are malicious… 11% of the total sites in the range have been tagged by SURBL or Google as being -bad- and to be honest there are probably a LOT more but those services haven't caught up yet. In any case, there seems to be nothing of value in 64.20.51.16/29 and I strongly recommend that you -block- traffic to the entire range."
* http://blog.dynamoo.com/2015/09/evil-network-6420511629-interserver-inc.html
Fake 'Delivery status' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/locky-aesir-delivered-by-delivery-status-malspam/
22 Nov 2016 - "… Locky downloader… an email with the subject of 'Delivery status' coming as usual from random companies, names and email addresses with a semi-random named zip attachment in the format of document_recipients name .zip… One of the emails looks like: From: Jocelyn Sears
Date: Tue 22/11/2016 07:20
Subject: Delivery status
Attachment: document_mrilw.zip
Dear Client! Our delivery department could not accept your operation due to a problem with your current account.
In order to avoid falling into arrears and getting charged, please fill out the document in the attachment as soon as possible and send it to us.
22 November 2016: document_mrilw.zip: Extracts to: R9SZO3SDB89J399GW52V80-N2AXBG71NVG2XT.js
Current Virus total detections 10/55*. MALWR** shows a download of a file from
http ://sadhekoala .com/lvqh1 which is converted by the script to 7wYxQEPdqwq.dll (VirusTotal 5/56***).
Payload Security [4]… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/3d0956e798b0763a612ff4deeeedda81ad79093ec73f46dc2cf391c67bf20737/analysis/1479802918/
- http://blog.dynamoo.com/2016/11/malware-spam-delivery-status-leads-to.html
22 Nov 2016 - "This -fake- financial spam leads to Locky ransomware: Subject: Delivery status
From: Gilbert Hancock
Date: Tuesday, 22 November 2016, 8:51
Dear Client! Our delivery department could not accept your operation due to a problem with your current account.
In order to avoid falling into arrears and getting charged, please fill out the document in the attachment as soon as possible and send it to us.
In the sample I analysed there was an attachment named document_recipientname.zip (i.e. the first part of the recipient's email address was in the name), containing a malicious javascript with a random name. This particular script (and there are probably many others) attempts to download a component… According to this Malwr analysis*, a malicious DLL is dropped with an MD5 of ebf03567c2a907705a026ff0821d8e63 and a detection rate of 6/55**. The Hybrid Analysis*** reveals the following C2 locations:
91.201.202.130 /information.cgi [hostname: dominfo.dp .ua] (FLP Anoprienko Artem Arkadevich aka host-ua.com, Ukraine)
95.213.186.93 /information.cgi [hostname: djaksa.airplexalator .com] (Selectel, Russia)
188.120.250.138 /information.cgi [hostname: olezhkakovtonyuk.fvds .ru] (TheFirst-RU, Russia)
213.32.66.16 /information.cgi (OVH, France)
For those Russian and Ukranian networks I would be tempted to block the entire /24 at least, but this is my minimum recommended blocklist: 91.201.202.130
95.213.186.93
188.120.250.138
213.32.66.16 "
* https://malwr.com/analysis/ZWYyZWY1YTI2Zjk1NDgwYzk0ZGIwZTIzNTQ4NTgzZDA/
Hosts 187.45.240.4
Fake 'Invoice' SPAM - delivers Locky
- http://blog.dynamoo.com/2016/11/malware-spam-invoice-123456-from-random.html
22 Nov 2016 - "This -fake- financial spam appears to come from a random sender in the victim's-own-domain, but this is just a simple forgery. The payload is Locky ransomware. Subject: Invoice 5639438
From: random sender (random.sender@ victimdomain .tld)
Date: Tuesday, 22 November 2016, 8:43
Attached is the document 'Invoice 5639438'.
The reference number varies from email to email, but is consistent in the subject, body and the name of the attachment (e.g. Invoice 5639438.zip). This ZIP file contains a malicious WSF script (e.g. Invoice 7868933153.wsf)… According the the Malwr analysis*, that script downloads from:
manage .parafx .com/98y4h?AdIXigNCmu=UdJVux
There are no doubt many other locations. That same analysis shows a DLL being dropped with an MD5 of de5d8250edf98262f335cd87fe6f6740 and a detection rate of 9/56**. The Hybrid Analysis*** of the same sample shows the malware contacting the following C2 locations:
89.108.73.124 /information.cgi (Agava, Russia)
91.211.119.98 /information.cgi (Zharkov Mukola Mukolayovuch aka 0x2a.com.ua, Ukraine)
94.242.55.81 /information.cgi (RNet, Russia)
Recommended blocklist: 89.108.73.0/24
91.211.119.98
94.242.55.81 "
* https://malwr.com/analysis/YTdlYzE1NWUzNWNiNGJkMGIxN2YwNzk5YmRkZTQ1YmE/
Hosts 69.57.3.3
91.211.119.98
Fake 'Documents Requested' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/documents-requested-pretending-to-come-from-random-names-at-your-own-email-domain-delivers-locky/
22 Nov 2016 - "… Locky downloader… an email with the subject of 'Documents Requested' pretending to come from random names at your-own-email-domain… One of the emails looks like: From: Darlene
Date: Tue 22/11/2016 11:26
Subject: Documents Requested
Attachment: doc(598).zip
Dear [redacted]
Please find attached documents as requested.
Best Regards,
Darlene
Fake 'tax bill' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/your-tax-bill-debt-due-date-is-today-malspam-delivers-locky-aesir/
22 Nov 2016 - "… Locky downloader… an email pretending to be a tax bill with the subject of 'Please note' coming as usual from random companies, names and email addresses with a semi-random named zip attachment in the format of tax_recipients name.zip… One of the emails looks like: From: Lance Barron <Barron.Lance@ dramaticallybetterhealth .com>
Date: Tue 22/11/2016 17:41
Subject: Please note
Attachment: tax_goal.zip
Dear goal
Your tax bill debt due date is today . Please fulfill the debt.
All the information and payment instructions can be found in the attached document.
Best Wishes,
Lance Barron
Tax Collector …
22 November 2016: tax_goal.zip: Extracts to: 6WMK287O33R4XN6.js - Current Virus total detections 6/55*
MALWR** shows a download of an encrypted file from:
http ://govorokhm .ru/huz9ex2sd8 which is converted by the script to xHVh9Aflvj4.dll (VirusTotal 9/57***)
Payload Security [4]… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/e680822da8be44d75e19ff21747a0c49008b934b6b3e3bc979deed9c94fac7ce/analysis/1479836521/
Fake 'DocuSign' SPAM - delivers ASN1 ransomware
- https://myonlinesecurity.co.uk/spoofed-docusign-you-have-a-new-encrypted-document-malspam-attempts-to-download-asn1-ransomware/
21 Nov 2016 - "An email with the subject of 'You have a new Encrypted Document' pretending to come from DocuSign with a malicious macro enabled word doc tries to download ASN1 ransomware… These do -not- come from the genuine DocuSign company. docusigndocuments .com and the other domains listed have been registered -today- and hosted at Godaddy .com with what are probably -fake- details…
The three domains and sending email addresses also used in this malspam ransomware attempt are:
DocuSign
DocuSign
DocuSign …
21 November 2016: EncryptedDocument.doc - Current Virus total detections 18/54*
Both MALWR** & Payload Security*** show it tries to download
http ://majesticbrass .com/1061911a3e0a74827a76bbd7bfe16d20.exe which is currently giving a 404 not found. This site was used in an similar ransomware attack at the end of last week[4]… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/ec397faf8be5ad9e4ace5d7cb570d268f982a91cfb63ceb3b06338fd9ab17966/analysis/1479766715/
Fake 'Pay Attention' SPAM - leads to Locky
- http://blog.dynamoo.com/2016/11/malware-spam-please-pay-attention-leads.html
23 Nov 2016 - "This -fake- financial spam leads to Locky ransomware: Subject: Please Pay Attention
From: Bill Rivera
Date: Wednesday, 23 November 2016, 9:45
Dear [redacted], we have received your payment but the amount was not full.
Probably, this occurred due to taxes we take from the amount.
All the details are in the attachment - please check it out.
The name of the sender will vary. In the sample I analysed, a ZIP file was attached with a filename beginning
lastpayment_ followed by the first part of the recipients email address. This archive contains a randomly-named malicious .JS script… According to this Malwr report* a malicious DLL is dropped with an MD5 of def0d0070d4aed411b84ebd713fd8b92 and a detection rate of 6/56**. The Hybrid Analysis*** clearly shows the ransomware in action and shows it communicating with the following URLs:
95.213.186.93 /information.cgi [hostname: djaksa.airplexalator .com] (Selectel, Russia)
195.123.209.8 /information.cgi [hostname: kostya234.itldc-customer .net] (Layer6, Latvia)
213.32.66.16 /information.cgi (OVH, France)
Recommended blocklist: 95.213.186.93
195.123.209.8
213.32.66.16 "
* https://malwr.com/analysis/MWY5ZDY1MDk2YjBmNDE1NmFkNzY0MWMwN2UyMTMzYWQ/
Hosts 31.204.153.171
- https://myonlinesecurity.co.uk/please-pay-attention-you-havent-paid-the-full-amount-malspam-delivers-locky/
23 Nov 2016 - "… Locky downloader… an email pretending to tell you that you haven’t paid the full amount, with the subject of 'Please Pay Attention' coming as usual from random companies, names and email addresses with a semi-random named zip attachment in the format of lastpayment_recipient name.zip… One of the emails looks like: From: Gabriela Diaz
Date: Wed 23/11/2016 08:27
Subject: Please Pay Attention
Attachment: lastpayment_lickit.zip
Dear lickit, we have received your payment but the amount was not full.
Probably, this occurred due to taxes we take from the amount.
All the details are in the attachment – please check it out.
23 November 2016: payment_history_64b96be.zip: Extracts to: 2BE46B4PX7ZU28.js
Current Virus total detections 7/55*. MALWR** shows a download of an encrypted file from
http ://risewh .com/pg31nkp which is renamed by the script to
W0heF8ZofNrqpj9Z .dll (VirusTotal 5/56***). Payload Security[4]…
Other download sites include:
risewh .com/pg31nkp
jinxlaze .com/rysuuttn
naturalnepodlogi .cba .pl/utnnyduqa
offerrat .com/12mi44q
pineysprat .com/zqdjx …
The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/f70ff5b1c8e04a3b73ff53b4784d8ec6a35195679f5b0eafec31f7af792fad2f/analysis/1479894064/
Fake 'Bill' SPAM - delivers more Locky
- https://myonlinesecurity.co.uk/random-bills-coming-from-random-senders-at-your-own-email-domain-delivers-even-more-locky/
23 Nov 2016 - "… Locky downloader… a -blank/empty- email with the subject of 'Bill-85548' (random numbers) pretending to come from random names at your-own-email-address/company or domain with a totally random numbered zip attachment… One of the emails looks like: From: paris hymer
Date: Thu 01/09/2016 19:22
Subject: paris hymer …
Attachment: 7c8b9b79dd4ef599dd5d0c6db9b2d530.zip
Body content: totally blank
23 November 2016: 7c8b9b79dd4ef599dd5d0c6db9b2d530.zip: Extracts to: qivrlftajqpvl4kfverdv6vu8ecbwdxe.js
Current Virus total detections 10/55*. MALWR** shows a download of an encrypted file from
http ://parenclub-devilsenangels .nl/08yhrf3?ELghUu=ELghUu which is converted by the script to
ELghUu1.dll (VirusTotal 8/55***). Payload Security[4]… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/7f219892244608787ea17b46ad7df45045541f45af47b5b0e9f85758a8ea59af/analysis/1479893531/
- http://blog.dynamoo.com/2016/11/moar-locky-bill-12345-from-victims-own.html
23 Nov 2016 - "This spam has no-body-text and appears to come from within the sender's-own-domain. It leads to Locky ransomware. For example: From: julia newenham [julia.newenham@ victimdomain .tld]
Date: 23 November 2016 at 10:44
Subject: Bill-76137
There is a randomly-named ZIP (e.g. 589af1aa1aaf4cb9ce571fced687b8ac.zip) containing a randomly-named malicious javascript… A malicious DLL is dropped with an MD5 of 4e207b30c5eae01fa136f3d89d59bbbe and
a detection rate of 9/56*. The malware then communicates with:
80.87.202.49 /information.cgi (JSC Server, Russia)
94.242.55.81 /information.cgi (RNet, Russia)
95.46.114.205 /information.cgi (PE Gornostay Mikhailo Ivanovich aka time-host .net, Ukraine)
Recommended blocklist: 80.87.202.49
94.242.55.81
95.46.114.205 "
* https://virustotal.com/en/file/675c681f4c9684685dda43e5e96983c1688bef6d68583562d60fe673dafb3d0c/analysis/
___
Fake 'Scanned Documents' SPAM - delivers Trickbot
- https://myonlinesecurity.co.uk/trickbot-banking-trojan-delivered-by-spoofed-hp_printer-at-your-own-email-address-malspam/
23 Nov 2016 - "An email with the subject of 'Scanned Documents' pretending to come from HP Digital Device with a malicious macro enabled word docdelivers Trickbot banking Trojan…
The email looks like: From: HP Digital Device
Date: Wed 23/11/2016 04:27
Subject: Scanned Documents
Attachment: Scan552.doc
Please open the attached document.
This document was digitally sent to you using an HP Digital Sending device.
This email has been scanned for viruses and spam.
23 November 2016: Scan552.doc - Current Virus total detections 11/51*
Payload Security**.. shows downloads from http ://wingsbiotech .com/images/kjcoiejceiwejf.png
which is -not- an image file but a renamed .exe that the macro renames to newfle.exe and autoruns
(VirusTotal 12/56***)… DO NOT follow the advice they give to enable macros or enable editing to see the content…
The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/d692c5e5b0284352c42cf48c42f439f3b15c6c2f9d3726d7c5e1d89d0b070818/analysis/1479879729/
Fake 'LETTER' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/more-fake-spoofed-emails-from-your-own-email-address-delivering-locky-aesir/
23 Nov 2015 - "… Locky downloader… an email with the subject of 'Emailing: LETTER 5.pdf' (random numbers) pretending to come from random names at your-own-email-domain… One of the emails looks like: From: queen
Date: Wed 23/11/2016 13:39
Subject: Emailing: LETTER 5.pdf
Attachment: LETTER 5.zip
Please find attachment.
—
This email has been checked for viruses by Avast antivirus software.
23 November 2016: LETTER 5.zip: Extracts to: fnpqatfwistcg4r3ccoanyajwkqjlgq7.js
Current Virus total detections 13/55*… Payload Security** shows a download of an encrypted file from
http ://paulking .it/08yhrf3?yRLXgsuxJ=yRLXgsuxJ which is converted by the script to yRLXgsuxJ1.dll
(VirusTotal 7/57***)… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/e10ecc1cad2a5bd09a60c9ee9344099694cfd1e19b197346cfa5da863bfb46fc/analysis/1479908406/
Fake 'subpoena' SPAM - leads to malware
- http://blog.dynamoo.com/2016/11/malware-spam-financial-records-subpoena.html
23 Nov 2016 - "This spam purports to come from Michael T Diver who is a real Oklahoma attorney, but it doesn't really and is just a simple forgery: From: MICHAEL T. DIVER [michael -at- lawfirmofoklahoma .com]
Date: 23 November 2016 at 15:24
Subject: RE:RE: financial records subpoena
See you in court !!!
Subpoena for server
Thank you,
MICHAEL T. DIVER …
The telephone number and also potentially the email address are genuine, but they are certainly not being sent from this law firm. The link-in-the-email goes to a legitimate but -hacked- Vietnamese site at techsmart .vn/backup2/get.php?id=[base64-encoded-part] (the last bit is a Base 64 representation of the victim's email address). In testing the payload site was -down- but previous emails of this type have lead to the Vawtrak banking trojan."
23 November 2016: PaymentConfirmation7477.zip: Extracts to: wbxz7lyfob8mwyygqstzfffj7aere8wz.js
Current Virus total detections 13/54*. MALWR** shows a download of an encrypted file from
http ://rdyy .cn/08yhrf3?OYxgQhzazR=OYxgQhzazR which is converted by the script to OYxgQhzazR1.dll
(VirusTotal 12/56***). Payload Security[4]… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/9c6a9138670c0c2a11b5e8f7eefc2ac194473ee01dfb85c38866b09e574eb366/analysis/1479919853/
Fake 'Attention Required' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/attention-required-hr-department-havent-received-the-receipt-malspam-delivers-even-more-locky-today/
23 Nov 2016 - "… Locky malware… with the subject of 'Attention Required' coming as usual from random companies, names and email addresses with a semi-random named zip attachment in the format of receipt_recipient.name.zip… One of the emails looks like: From: Angela Holmes <Holmes.Angela@ murilobertini .com>
Date: Wed 23/11/2016 16:14
Subject: Attention Required
Attachment: receipt_xerox.805.zip
Dear xerox.805, our HR Department told us they haven’t received the receipt you’d promised to send them.
Fines may apply from the third party. We are sending you the details in the attachment.
Please check it out when possible.
23 November 2016: receipt_xerox.805.zip: Extracts to: Z8B105E8IK89A9HX.js - Current Virus total detections 15/55*
MALWR** shows a download of a file from http ://orantpamir .net/el3w488r9 which is converted by the script to
fWk6epu1.dll (VirusTotal 9/57***). Payload Security[4]…
Manual analysis shows these download locations
orantpamir .net/el3w488r9
oimeferio .net/sl60vci
websdns .com/k0ais
gigabothosting .com/kiltoonxqa
gpsfiles .nl/lywk0py
… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/1d69bb8fa98cdce5b8725b7c6ad08a1bcd3d55decbb78819612f0e8fe6505204/analysis/1479921317/
Fake 'Important Info' SPAM - leads to Locky
- http://blog.dynamoo.com/2016/11/malware-spam-important-information.html
25 Nov 2016 - "This spam leads to Locky ransomware: Subject: Important Information
From: Etta Figueroa
Date: Friday, 25 November 2016, 10:28
Dear [redacted], your payment was not processed due to the problem with credentials.
Payment details are in the attached document.
Please check it out as soon as possible.
The name of the sender varies. Attached is a ZIP file beginning with payment_ and then the first part of the victim's email address. This analysis comes from my trusted usual source (thank you!). It contains a randomly-named malicious javascript that downloads a component… The malware then phones home to:
213.32.66.16 /information.cgi (OVH, France)
89.108.118.180 /information.cgi (Datalogika / Agava, Russia)
91.201.42.83 /information.cgi [hostname: aportom .com] (RuWeb, Russia)
Recommended blocklist: 213.32.66.16
89.108.118.180
91.201.42.83 "
- https://myonlinesecurity.co.uk/important-information-your-payment-was-not-processed-malspam-delivers-more-locky-zzzzz/
25 Nov 2016 - "… Locky downloader… an email with the subject of 'Important Information' coming or pretending to come from random companies, names and email addresses with a semi-random named zip attachment in the format of payment_recipient’s name.zip… One of the emails looks like: From: Clay Clarke
Date: Thu 01/09/2016 19:22
Subject: Important Information
Attachment: payment_montag.zip
Dear montag, your payment was not processed due to the problem with credentials.
Payment details are in the attached document.
Please check it out as soon as possible.
25 November 2016: payment_montag.zip: Extracts to: HQ5q97uu9s2.js - Current Virus total detections 8/54*
Payload Security**. MALWR*** shows a download of an encrypted file from
http ://thinx .net/rkp2tpxlrg which is converted by the script to Oe3cTld33aTOQyLh.tdb (VirusTotal 15/56[4]). The tdb file is actually a dll file that is run by rundll32 but given a different extension to attempt to fool anyone having a quick look at it. We describe this here[5] and Bleeping computer[6] has a good write up about the use of non standard file extensions by Locky… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/8cd5ebd6f4789fd83fb694b05f2d80882145a2f3781717de7033ea5f9422560c/analysis/1477646733/
Fake -blank/body- SPAM - more Locky
- https://myonlinesecurity.co.uk/blank-email-with-random-subjects-delivers-even-more-locky-zzzzz/
25 Nov 2016 - "… Locky downloader… a -blank- email with the subject of (random number recipient name) coming or pretending to come from recipient name_olive at random email addresses with a semi-random named zip attachment in the format of INFO_random number_recipients name.zip that contains another zip file… One of the emails looks like: From: derekolive@ blueyonder .co.uk
Date: Fri 25/11/2016 08:10
Subject: 57051 derek
Attachment: INFO_052297_derek.zip
Body content: Totally Blank/empty
25 November 2016: INFO_052297_derek.zip: which extracts to MONEY_14189_ZIP.zip which in turn Extracts to:
MONEY_14189.js. Current Virus total detections 3/55*. MALWR** shows a download of a file from
http ://www .vollyuper .top/admin.php?f=2.dat which gave MALWR rad68D08.tmp (VirusTotal 4/57***)…
Update: the same series of emails with these .js files also have -other- links that are currently downloading Cerber ransomware. These sites include:
http ://otreytl .bid/search.php?f=x1.dat | http ://hqtrssx .top/search.php?f=x2.dat (VirusTotal 5/57[4])
(Payload Security [5]). (MALWR [6])… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/7fad0a74e5cc06505ccf5d88dab2a1db5fb18618618e117b9adeab44bb5fa2da/analysis/1480061873/
Moar Locky 2016-11-25
- http://blog.dynamoo.com/2016/11/moar-locky-2016-11-25.html
25 Nov 2016 - "This data comes from my trusted usual source, so far I have only seen a single example. This morning's spam run has a -subject- with one of the following words:
DOC, DOCUMENT, FAX, IMG, LABEL, ORD, PHOTO, PIC, SCAN, SHEET
..plus a four digit random number. Attached is a ZIP file with a name mating the subject, containing a randomly-named malicious javascript that attempts to download a component… The payload is Locky ransomware, phoning home to:
185.118.167.144 /information.cgi [hostname: bogdankarpenko1998.pserver .ru] (Chelyabinsk-Signal, Russia)
91.142.90.55 /information.cgi (Miran, Russia)
Recommended blocklist: 185.118.167.144
91.142.90.55 "
___
Fake 'New voice mail' SPAM - leads to Locky
- http://blog.dynamoo.com/2016/11/malware-spam-vigor2820-series-new-voice.html
25 Nov 2016 - "This -fake- voicemail spam leads to Locky ransomware and appears to come from within the victim's own domain, but this is just a simple forgery. Subject: [Vigor2820 Series] New voice mail message from 01435773591 on 2016/11/25 18:29:39
From: voicemail@ victimdomain .tld
To: victim@ victimdomain .tld
Date: Friday, 25 November 2016, 12:58
Dear webmaster :
There is a message for you from 01435773591, on 2016/11/25 18:29:39 .
You might want to check it when you get a chance.Thanks!
The number in the message will vary, but is consistent throughout. Attached is a ZIP file referencing the same number, e.g. Message_from_01435773591.wav.zip which contains a malicious Javascript… This Malwr analysis* shows behaviour consistent with Locky ransomware… The C2s to block are the same as here**, namely:
185.118.167.144 /information.cgi [hostname: bogdankarpenko1998.pserver .ru] (Chelyabinsk-Signal, Russia)
91.142.90.55 /information.cgi (Miran, Russia)
Recommended blocklist: 185.118.167.144
91.142.90.55 "
* https://malwr.com/analysis/YWU1NzQ4MmJhNGRlNGJmNGFmMjBhZGVmNTdlMzQ4NWU/
Hosts 92.60.224.52
185.118.167.144
91.142.90.55
** http://blog.dynamoo.com/2016/11/moar-locky-2016-11-25.html
___
Locky hidden in image file hitting Facebook, LinkedIn
- https://www.helpnetsecurity.com/2016/11/25/locky-image-file-facebook-linkedin/
Nov 25, 2016 - "Malware masquerading as an image file is still spreading on Facebook, LinkedIn, and other social networks. Check Point researchers have apparently discovered how cyber crooks are embedding malware in graphic and image files, and how they are executing the malicious code within these images to infect social media users with Locky ransomware variants… As they are searching for a solution, the Check Point research team advises* users not-to-open-any-image they have received from another user and have downloaded on their machine… A video demonstration of the attack can be viewed below:
> https://youtu.be/sGlrLFo43pY "
* http://blog.checkpoint.com/2016/11/24/imagegate-check-point-uncovers-new-method-distributing-malware-images/
2016/11/24 - "… attackers have built a new capability to embed malicious code into an image file and successfully upload it to the social media website. The attackers exploit a misconfiguration on the social media infrastructure to deliberately force their victims to download the image file. This results in infection of the users’ device as soon as the end-user -clicks- on the downloaded file…"
Fake 'Purchase Order' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/spoofed-purchase-order-donotreplysouth-staffordshire-com-delivers-locky/
28 Nov 2016 - "… Locky downloader… an email with the subject of 'Purchase Order No. 90373' (random numbers) coming or pretending to come donotreply@ south-staffordshire .com with a semi-random named zip attachment that matches the subject line… One of the emails looks like: From: donotreply@ south-staffordshire .com
Date: Mon 28/11/2016 09:45
Subject: Purchase Order No. 90373
Attachment: PO90373.zip
Please find attached Purchase Order No. 90373.
PLEASE DO NOT REPLY TO THIS ADDRESS.
If you have any queries in regards to your Purchase Order, please contact your requestor, Reinaldo horrocks on 01922 062460 ext 5580…
28 November 2016: payment_history_64b96be.zip: Extracts to: 93410605.wsf - Current Virus total detections 8/55*
MALWR* is not giving any payload or download sites. Payload Security*** shows a download of an encrypted file from
restauranttajmahal .ca/87nft3?iNKevOML=ChKIolivpc which is converted by the script to a dll and autorun.
Unfortunately Payload Security does not show or make the dll available for download in the free web version… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/f4bc93583d1a56568c2c20a313709cd61e433699aed650aa877d1c82ab2a6ceb/analysis/1480327255/
Fake 'Urgent Alert' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/urgent-alert-we-have-detected-a-suspicious-money-atm-withdrawal-from-your-card-delivers-locky/
28 Nov 2016 - "… Locky downloader… an email with the subject of 'Urgent Alert' coming or pretending to come from random companies, names and email addresses with a semi-random named zip attachment in the format of ATM_recipients name.zip… One of the emails looks like: From: Tami Soto
Date: Mon 28/11/2016 09:22
Subject: Urgent Alert
Attachment: ATM_etgord34truew.zip
Dear etgord34truew, we have detected a suspicious money ATM withdrawal from your card.
For your security, we have temporarily blocked the card.
All the details are in the attachment. Please open it when possible.
28 November 2016: ATM_etgord34truew.zip: Extracts to: HQ6za5d7.js - Current Virus total detections 7/53*
MALWR** shows a download of an encrypted file from http ://dodowiz .com/ynux4ac
which is converted by the script to x3NzzWXgCcwO.tdb (VirusTotal 6/52***). The tdb file is actually a dll file that is run by rundll32 but given a different extension to attempt to fool anyone having a quick look at it. We describe this here[4] and Bleeping computer[5] has a good write up about the use of non standard file extensions by Locky
(Payload Security [6])… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/7fdc3a28aafd165fd28bfd379675453c8aa890cf43c3faaaf0d1f3b0b835f481/analysis/1480324767/
Fake 'Bill' SPAM - more Locky
- https://myonlinesecurity.co.uk/more-locky-delivered-by-bill-malspam-spoofed-to-come-from-your-own-email-address/
28 Nov 2016 - "… Locky downloader… another blank/empty malspam pretending to come from random names at your-own-email-address with the subject of 'Bill-4491989' (random numbers) with a random named zip attachment. All these emails have a To: line of resort@ doggiespalace .com with a hidden bcc: to your email address… One of the emails looks like: From: earlene mitchel
Date: Mon 28/11/2016 12:07
Subject: Bill-4491989
To: resort@ doggiespalace .com
Attachment: d58e224b0e2266fb80b74c3b46f03fd1.zip
Body content: totally blank/empty
28 November 2016: d58e224b0e2266fb80b74c3b46f03fd1.zip: Extracts to: 64621603.wsf
Current Virus total detections 8/50*. MALWR is unable to get any malware or download sites. Payload Security** shows a download of an encrypted file from sinmotor .com/87nft3?XztYNBph=nhYXdz which is converted by the script to MxoWCE1.dll (VirusTotal 9/56***)… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/c247ccf81e4c83e930f9068c81d693bbbe26ebac32b36ce2a021ed58ba910cc7/analysis/1480329075/
Fake 'Message' SPAM - more Locky
- https://myonlinesecurity.co.uk/even-more-locky-spoofed-to-come-from-your-own-email-address/
28 Nov 2016 - "… Locky downloader… another malspam pretending to come from donotreply at your-own-email-address that pretends to be an email from a scanner/printer with the subject of 'Message from RNP0024D5D73B3A' (random numbers) with a semi-random named zip attachment in the format of todays date random numbers_random numbers.zip… One of the emails looks like: From: donotreply@ your-own-email-address .co.uk
Date: Mon 28/11/2016 11:30
Subject: Message from “RNP0024D5D73B3A”
Attachment: 201611281559326883_0033.zip
This E-mail was sent from “RNP0024D5D73B3A” (Aficio MP 2352).
Scan Date: Mon, 28 Nov 2016 15:59:32 +0430)
Queries to: {redacted}
28 November 2016: 201611281559326883_0033.zip: Extracts to: 95130643.wsf - Current Virus total detections 6/55*
Payload Security** shows a download of an encrypted file from somersetautotints .co.uk/87nft3?viqtJpG=zELkPdJaI which is converted by the script to lkVpqyuH1.dll which VirusTotal 9/56*** shows is the same file as this concurrent malspam run[4]… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/d941a5d08b5c5d5326a87ee5487e9545f4c8ab7dd2598cab10907290ae9363d0/analysis/1480336074/
Fake 'XLS Invoice' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/please-find-attached-a-xls-invoice-spoofing-ansell-lighting-delivers-locky/
29 Nov 2016 - "An email with the subject of 'Please find attached a XLS Invoice 293192' (random numbers) pretending to come from creditcontrol@ random companies with a malicious Excel XLS spreadsheet attachment delivers Locky… The email looks like: From: creditcontrol@ riversideglass .com
Date: Tue 29/11/2016 08:01
Subject: Please find attached a XLS Invoice 293192
Attachment: INVOICE.TAM_293192_20161129_C415186AD.xls
Please find attached your Invoice for Goods/Services recently delivered. If you have any questions, then pleasedo not hesitate in contacting us.Karen Lightfoot -Credit Controller, Ansell Lighting …
29 November 2016: INVOICE.TAM_293192_20161129_C415186AD.xls - Current Virus total detections 9/56*
Payload Security** shows a download from thegarageteam .gr/087gbdv4 which is an encrypted file that gets converted by the macro to luswiacs1.dll. Unfortunately Payload Security does not make this file available in the free web version. MALWR*** did give the dll (VirusTotal 9/57[4])… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/129ec23c0ba2f25c2d16979b5cba49bcede8dd1810be9ee7692ecd81928f984a/analysis/1480406523/
Fake 'For Your Consideration' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/for-your-consideration-malspam-delivers-locky/
29 Nov 2016 - "… Locky downloader… an email with the subject of 'For Your Consideration' coming or pretending to come from random companies, names and email addresses with a semi-random named zip attachment in the format of unpaid_recipient’s name.zip… One of the emails looks like: From: Elliott Osborn
Date: Tue 29/11/2016 11:22
Subject: For Your Consideration
Attachment: unpaid_evf.zip
Greetings! You paid for yesterday’s invoice – the total sum was $4636.
Unfortunately, you hadn’t included the item #47089-14743 of $688.
Please transfer the remainder as soon as possible.
All details are in the attachment. Please check it out to see whether we are right.
29 November 2016: unpaid_evf.zip: Extracts to: -snk-7030904.js - Current Virus total detections 12/55*
MALWR** shows a download of an encrypted file from one of these 2 locations
http ://tytswirl .com/u2asa61 and http ://kalbould .wa .gov.au/n9zz5r8 which is converted by the script to AddoClgYDJ4J3F.tdb (VirusTotal 6/57***). The tdb file is actually a dll file that is run by rundll32 but given a different extension… Payload Security[4]… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/c63301b2c4fd9c12a6448d8ed62b02233a82b955cf4a3a0f6cae8dc789510be5/analysis/1480418735/
Fake 'File COPY' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/can-you-please-pass-this-invoice-for-payment-thank-you-malspam-delivers-locky/
29 Nov 2016 - "An email with the subject of 'File COPY.29112016.94400.XLS Sent 29/11/2016' (random numbers) pretending to come from random senders with a malicious Excel XLS spreadsheet attachment delivers Locky ransomware… The email looks like: From: ALLGREEN-USSING, RODOLFO
Date: Tue 29/11/2016 13:23
Subject: File COPY.29112016.94400.XLS Sent 29/11/2016
Attachment: COPY.29112016.94400.XLS
can you please pass this invoice for payment thank you…
The link in the email goes to a -hacked- Sharepoint account, in this case:
https ://supremeselfstorage-my.sharepoint .com/personal/andrew_supremeselfstorage_com_au/_layouts/15/guestaccess.aspx?guestaccesstoken=GTQPc%2brKLAsKHba4nXtvl0hXrBsUmCUxoYGuu9msk0U%3d&docid;=0c4b96dfd3319496a8feb1a56d88de679&rev;=1
It seems to belong to a legitimate company, but maybe one that has suffered an Office 365 compromise[2]. The ZIP file it leads to is named Fax_11292016.zip (there may be other versions) containing two identical -scripts- named:
Fax_11292016_page1.js
Fax_11292016_page2.js
… Hybrid Analysis* of the script indicates this is Nymaim[3] downloading a component from:
siliguribarassociation .org/images/staffs/documetns.png
A malicious EXE is dropped with an MD5 of bdf952b2388bf429097b771746395a4c and a detection rate of 9/56**. The malware then phones home to:
stengeling .com/20aml/index.php
The domain stengeling .com appears to have been -created- for this malware and has -anonymous- registration details. It is apparently -multihomed- on the following IPs:
4.77.129.110, 18.17.224.92, [removed], [removed], [removed], [removed], [removed]
[removed], [removed], [removed], [removed], [removed], [removed], [removed]
[removed], [removed], [removed], [removed], [removed], [removed], [removed]
[removed], [removed], [removed]
Each of those IPs appears to be a -hacked- legitimate host, with a high turnover of IPs. Those IPs appear to be associated with the following domains that may be worth blocking: butestsis .com
sievecnda .com
specsotch .com
crileliste .com
stengeling .com "
* https://www.hybrid-analysis.com/sample/eb01f7d4eb17acc99795dac1fe11cff6897f9367f7c4cbd9192d464b68f8a382?environmentId=100
Contacted Hosts 216.158.76.73
115.249.171.24
45.249.111.213
168.227.171.254
31.209.107.100
Fake 'Insufficient funds' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/insufficient-funds-malspam-delivers-locky/
28 Nov 2016 - "… Locky.. an email with the subject of 'Insufficient funds' coming or pretending to come from random companies, names and email addresses with a semi-random named zip attachment in the format of payment-recipient name.zip… One of the emails looks like: From: Ruby Quinn
Date: Mon 28/11/2016 20:58
Subject: Travel expense sheet
Attachment: payment-gold.zip
Dear gold,
Your bill payment was rejected due to insufficient funds on your account.
Payment details are given in the attachment.
28 November 2016: payment-gold.zip: Extracts to: -snk-007064018.js - Current Virus total detections 14/55*
MALWR** shows a download of an encrypted file from http ://leyuego .com/ejxgf1iy which is converted by the script to Ddrh0VO4W20.tdb (VirusTotal 7/57***). The tdb file is actually a dll file that is run by rundll32 but given a different extension to attempt to fool anyone having a quick look at it. We describe this here[4] and Bleeping computer[5] has a good write up about the use of non standard file extensions by Locky (Payload Security [6])… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/7eca0c5aed0dbffbad69ef6a54c81897738c0ce3aa13b4add2d052c9f36bb475/analysis/1480370317/
Apple ID – Phish
- https://myonlinesecurity.co.uk/reset-your-password-or-unlock-your-apple-id-phishing/
29 Nov 2016 - "… mass Apple phish… received about 200 so far this morning. Many of which are getting past spam filters because they seem to have found some sending addresses that aren’t yet listed in spam databases and that don’t use SPF /DKIM /DMARC so authentication checks don’t fail. Most mail servers are set up to ignore lack of mail authentication, rather than automatically delete or quarantine…
Fake 'Urgent bill' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/urgent-bill-has-invalid-account-number-malspam-delivers-locky/
30 Nov 2016 - "… Locky downloader… an email with the subject of 'Urgent' coming or pretending to come from random companies, names and email addresses with a semi-random named zip attachment in the format of unpaid_recipient’s name.zip… One of the emails looks like: From: Adolfo Alexander
Date: Wed 30/11/2016 09:06
Subject: Urgent
Attachment: unpaid_forum.zip
Dear forum, our accountant informed me that in the bill you processed, the invalid account number had been specified.
Please be guided by instructions in the attachment to fix it up.
30 November 2016: unpaid_forum.zip: Extracts to: -snk-284042943.js - Current Virus total detections 10/55*
MALWR** shows a download of an encrypted file from http ://revaitsolutions .com/ij1driqioc which is converted by the script to K3GepPJAfH.tdb (VirusTotal 5/57***). Payload Security[4]. The tdb file is actually a dll file that is run by rundll32 but given a different extension… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/7f4910729fb867976838d0f3bf255c543b9bc11b3ecfc1caeda3a35c37e76c7d/analysis/1480496588/
30 November 2016: 6479_005.docm - Current Virus total detections 9/55*
Both MALWR** and Payload Security*** show a download from satherm .pt/873nf3g which is converted by the macro to ajufr51.dll (VirusTotal 5/57[4]). Manual analysis shows an attempt to download from
http ://travelinsider .com.au/021ygs7 which is currently giving me a 404. There are normally 5 or 6 download locations buried inside the macro or scrpt files with these Locky versions.
C2 http ://91.142.90.61 /information.cgi | 95.213.195.123 /information.cgi… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/92bad79438931ff897bc4bb6cc01b873cc79c4aa1418bd2ba2800dc495cdd55b/analysis/1480498411/
1 December 2016: Fax.zip: Extracts to: Fax_page1.js - Current Virus total detections 3/55*
MALWR** shows a download of a file from ‘http ://mohdsuhaimy .com/wp-content/uploads/2006/06/background.png’ which is -not- a png (image file) but a -renamed- .exe which is renamed back by the script to an .exe file (VirusTotal 15/57***). (Payload Security [4]). Previously this trick & delivery method has delivered Trickbot banking Trojan. However this binary looks different and gives some indication of ransomware behaviour…
Update: I am reliably informed that this is Dridex Banking Trojan… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/eab3ba338c11bb3b4d569845a3183b0f397d21cdffe116c7cd5797e1f525c570/analysis/1480579221/
Fake 'Invoices' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/more-spoofed-invoices-from-random-companies-with-a-zip-file-that-pretends-to-be-a-docm-delivers-locky/
1 Dec 2016 - "… Locky downloader… an email with the subject of 'E-Mailed Invoices Invoice_87313391' (random numbers) coming or pretending to come from random companies, names and email addresses with what appears to be a word docm attachment - In reality this attachment is a standard zip file that has been erroneously named as a word macro doc. It will not open in word or any other word processing program. This zip contains a VBS file. Trying to open the alleged word doc in Word gives this error message:
> https://i2.wp.com/myonlinesecurity.co.uk/wp-content/uploads/2016/12/word-cannot-open.png?w=524&ssl=1
… One of the emails looks like: From: WAUGH, HORACIO
Date: Thu 01/12/2016 09:23
Subject: E-Mailed Invoices Invoice_87313391
Attachment: Invoice_87313391.docm
Please find attached your latest purchase invoice…
Any queries with either the quantity or price MUST be notified immediately to the department below.
Yours sincerely, Sales Ledger Department…
This email has been scanned by the Symantec Email Security.cloud service…
1 December 2016: Invoice_87313391.docm (actually a zip file): Extracts to: fGDpAMD-0438.vbs
Current Virus total detections on docm(zip) VirusTotal on VBS 20/55*. Payload Security** shows a download of an encrypted file from speckftp .de/978t6rve which is converted by the script to nhbzalOHj.343 (VirusTotal 37/56***) Locky has recently started to use non standard file extensions on the binaries. Sometimes they are numbers like 342, 343, 552 etc or sometimes tdb or .zk. All of these are actually DLL files that rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it to… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/0aa96f85e76db5ece5c1e9f237f03f88d460d5e6d104709a1c3fcf7d29b838aa/analysis/1480587704/
fGDpAMD-0438.vbs
Fake 'Invoice' SPAM - links to Dridex
- https://myonlinesecurity.co.uk/invoices-from-random-companies-accounts-messaging-servicepost-xero-org-delivers-dridex-banking-trojan/
1 Dec 2016 - "… an email with the subject of 'Invoice INV-01823 (Amended)' from Fleurs (random numbers and random companies) coming from Accounts . There is no zip attachment but a -link- in the email to download a zip… post-xero .org is a newly created domain that is registered to a Chinese entity with probably -fake- details. It appears to be hosted on OVH in France… One of the emails looks like: From: Accounts
Date: Thu 01/12/2016 08:02
Subject: Invoice INV-01823 (Amended) from Fleurs
Attachment: link-in-email to INV-01823.zip
Dear Customer, Please find attached invoice INV-01823 (Amended) for 421.59 GBP. This invoice was sent too early in error. The payment date should be 7th December 2016. Kindly accept our apologies for the oversight and for any inconvenience caused. The amount outstanding of 421.59 GBP is due on 07 Dec 2016. View and pay your bill:
https ://in.xero .com/vjNPxBRausdmfvsgnZKOMWvyHsISTwYm If you have any questions, please do not hesitate to contact us. Kind regards, Accounts Department …
The link in the body does -not- go to xero .com which is a legitimate small business accounting software but to a criminal controlled site on SharePoint: ‘https :// ryandixon-my.sharepoint .com personal/judy_dixonconstructionwa_com_au/_layouts/15/guestaccess.aspx?guestaccesstoken=k9xc1qR8YuAKTF6D2%2bMExORcjRIY3nQj8RB7WhdXaSw%3d&docid=09d01294b7e434b2aad87127682150354&rev=1’
Fake 'Payment Information' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/payment-information-you-have-forgotten-to-specify-insurance-payments-delivers-locky/
1 Dec 2016 - "… Locky downloader… an email with the subject of 'Payment Information' coming or pretending to come from random companies, names and email addresses with a semi-random named zip attachment in the format of P_recipient’s name.zip… One of the emails looks like: From: Helga Hull <Hull.Helga@ dreamactunion .org>
Date: Thu 01/12/2016 18:23
Subject: Payment Information
Attachment: P_rek.zip
Good afternoon. Thank you for sending the bill.
Unfortunately, you have forgotten to specify insurance payments.
So, we cannot accept the payment without them.
All details are in the attachment.
1 December 2016: P_rek.zip: Extracts to: -6dt874p53077.js - Current Virus total detections 16/55*
MALWR** shows a download of an encrypted file from http ://trewincefarm .co.uk/xlyy7 which is converted by the script to 0UBE8YF7q1BcN.zk (VirusTotal 11/57***). Payload Security[4]. Locky has recently started to use non standard file extensions on the binaries. Sometimes they are numbers like 342, 343, 552 or sometimes tdb or .zk. All of these are actually DLL files that rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it to…
The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/794dcfdcc1362140eee6fcda11ddf239ab048a965bba634bb787321db9672cfa/analysis/1480616575/
Worldwide cyber-crime network hit in coordinated raids
- http://www.reuters.com/article/us-germany-cyber-idUSKBN13Q4Z6
Dec 1, 2016 - "One of the world's biggest networks of hijacked computers, which is suspected of being used to attack online banking customers, has been taken down following police swoops in 10 countries, German police said on Thursday. In an internationally coordinated campaign, authorities carried out the raids on Wednesday, seized servers and website domains and arrested suspected leaders of a criminal organization, said police and prosecutors in northern Germany. Officials said they had seized 39 servers and several hundred thousand domains, depriving criminals of control of more than 50,000 computers in Germany alone. These hijacked computers were used to form a 'botnet' to knock out other websites. Two people who are believed to have been the administrators of the botnet infrastructure known as 'AVALANCHE' were arrested in Ukraine, investigators said. Another person was arrested in Berlin, officials added. The strike came in the same week that hackers tried to create the world's biggest botnet, or an army of zombie computers, by infecting the routers of 900,000 Deutsche Telekom (DTEGn.DE) with malicious software. The attack failed but froze the routers, causing outages in homes, businesses and government offices across Germany on Sunday and Monday, Deutsche Telekom executives said. Police said criminals had used the 'AVALANCHE' botnet targeted in Wednesday's international raids since 2009 to send phishing and spam emails. More than a million emails were sent per week with malicious attachments or links. When users opened the attachment or clicked on the link, their infected computers became part of the botnet. Investigators said the suspects had operated the commandeered network and made it available to other criminal groups, who had used it to send spam and phishing mails, defraud online banking user and to spread ransomware, a form of online extortion scheme. Officials estimated worldwide damages at upward of several hundred million euros. Authorities have identified 16 suspected leaders of the organization from 10 different countries. A court in Verden, northern Germany, has issued arrest warrants for seven people on suspicion of forming a criminal organization, commercial computer fraud and other criminal offences. The raids came after more than four years of intensive investigation by specialists in 41 countries."
Fake 'Pay Attention' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/please-pay-attention-the-contractor-requires-including-vat-in-the-service-receipt-malspam-delivers-locky/
2 Dec 2016 - "… Locky downloader… an email with the subject of 'Please Pay Attention' coming or pretending to come from random companies, names and email addresses with a semi-random named zip attachment in the format of SCAN_recipient’s name.zip… One of the emails looks like: From: Claud Hopper
Date: Fri 02/12/2016 09:35
Subject: Please Pay Attention
Attachment: SCAN_ard.zip
Greetings! Informing you that the contractor requires including VAT in the service receipt.
Sending the new invoice and payment details in the attached file.
Please open and study it as soon as possible – we need your decision.
2 December 2016: SCAN_ard.zip: Extracts to: -uvk3166985727v.js - Current Virus total detections 8/55*
MALWR** shows a download of an encrypted file from http ://supermarkety24 .pl/levsyp8vp which is converted by the script to 5viAGx9N.zk (VirusTotal 8/56***) | Payload Security[4] | Locky has recently started to use non standard file extensions on the binaries. Sometimes they are numbers like 342, 343, 552 or sometimes tdb or .zk. All of these are actually DLL files that rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it to…
The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/9df0d08438cce099ad9c81e5385ddb4c75cb9b02411a8f1316dddc49716f138f/analysis/1480674917/
Fake 'Emailing…" SPAM - delivers Locky
- https://myonlinesecurity.co.uk/emailing-eps000007-spoofed-from-random-names-at-your-own-email-address-delivers-locky/
2 Dec 2016 - "An email with the subject of 'Emailing: EPS000007' (random numbers) pretending to come from random names at your-own-email-address with a malicious word doc attachment delivers Locky… The email looks like: From: edmund
Date: Fri 02/12/2016 12:39
Subject: Emailing: EPS000007
Attachment: EPS000007.docm
Please find attachment.
—
This email has been checked for viruses by Avast antivirus software…
2 December 2016: EPS000007.docm - Current Virus total detections 10/56*
MALWR** shows a download of an encrypted file from http ://solid-consulting .nl/74t3nf4gv4 which is converted by the macro to likyir1.exe (VirusTotal 8/57***). Payload security[4]. C2: http ://195.19.192.99 /information.cgi
Other download locations seen on manual analysis of the macro include:
solid-consulting .nl/74t3nf4gv4 | taikosushibar .com.br/74t3nf4gv4 | tatooshsfds .com/74t3nf4gv4
sudeepgurtu .com/74t3nf4gv4 … DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/800ad944808ea513b1a7964bb22d7f44a0d0b071404638878692794ceaec7b8c/analysis/1480682348/
Fake 'Attached Document' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/attached-document-in-blank-email-spoofed-to-come-from-canonyour-own-email-address-delivers-locky/
2 Dec 2016 - "A -blank- email with the subject of 'Attached Document' pretending to come from canon@ your-own-email-domain with a malicious word doc attachment delivers Locky. This series of malspam emails contain the same macro downloaders and end up delivering the -same- Locky payload as described in THIS* earlier post where they used an Epson scanner/printer… The email looks like: From: canon@ my onlinesecurity .co.uk
Date: Fri 02/12/2016 15:52
Subject: Attached Document
Attachment: 0160_004.docm
Fake blank body SPAM - delivers Locky
- https://myonlinesecurity.co.uk/blank-email-from-random-senders-with-random-numbers-starting-051220160-or-041220161-malspam-delivers-locky/
5 Dec 2016 - "… Locky downloader… a completely -blank- email with the subject consisting of random numbers coming or pretending to come from random companies, names and email addresses with a zip attachment that matches the subject line numbers. I have received about 1500 copies of this malspam overnight. All the ones that I have seen start with either 051220160 or 041220161… One of the emails looks like: From: Monica clare
Date: Mon 05/12/2016 00:47
Subject: 051220160746377790277
Attachment: 051220160746377790277.zip
Body content: totally blank/empty
5 December 2016: 051220160746377790277.zip: Extracts to: 201612031200123557933004.vbs
Current Virus total detections 14/55*. Payload Security** shows a download of an encrypted file from
http ://natashacollis .com/8765r which is converted by the script to yqUePnct.343 (VirusTotal 11/53***). Locky has recently started to use non standard file extensions on the binaries. Sometimes they are numbers like 342, 343, 552 or sometimes tdb or .zk. All of these are actually DLL files that rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it to… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/b2e7d2181bd70ff519676f25ae5d8a548969d58b3e702d22c7dc7248dff54499/analysis/1480911167/
Fake 'No subject' SPAM - leads to Locky
- http://blog.dynamoo.com/2016/12/malware-spam-emailing-9376924272-no.html
5 Dec 2016 - "This spam comes in a few different variants, and it leads to Locky ransomware encrypting files with an extension '.osiris'. The more word version comes from random senders with a subject like _9376_924272 or some other randomly-numbered sequence. Attached to that is an XLS file of the same name and it includes this body text: Your message is ready to be sent with the following file or link
attachments:
_9376_924272
Note: To protect against computer viruses, e-mail programs may prevent
sending or receiving certain types of file attachments. Check your e-mail
security settings to determine how attachments are handled.
The second version has no body text and the subject No subject or (No subject). The XLS file is named in a format incorporating the date, e.g. 2016120517082126121298.xls . The macro in the malicious Excel file downloads a component… (Long list of domain-names at the dynamoo URL above.)
… You can see some of the things done in these two Malwr reports [1] [2]. The Locky ransomware dropped then phones home to one of the following locations:
185.82.217.28 /checkupdate [hostname: olezhkakovtony11.example .com] (ITL, Bulgaria)
91.142.90.61 /checkupdate (Miran, Russia)
195.19.192.99 /checkupdate (OOO EkaComp, Russia)
Recommended blocklist: 185.82.217.28
91.142.90.61
195.19.192.99 "
1] https://malwr.com/analysis/YTQzZjMwNjI5NTI2NDNlNTg5OTA3YzlmYTg3YzBjZjA/
Hosts 66.96.147.105
91.142.90.61
- https://myonlinesecurity.co.uk/blank-email-with-no-subject-xls-attachment-delivers-locky/
5 Dec 2016 - "… Locky downloader… another -blank- email with no-subject coming or pretending to come from random companies, names and email addresses with an XLS spreadsheet attachment… One of the emails looks like: From: Rolf titterington
Date: Mon 05/12/2016 09:44
Subject: no subject
Attachment: 2016120502434302394842.xls
Body content: empty
5 December 2016: 2016120502434302394842.xls - Current Virus total detections 16/55*
MALWR** shows a download of an encrypted file from http ://soulscooter .com/87t34f which is converted by the script to shtefans1.spe (VirusTotal 6/56***). Payload Security[4]. Locky has recently started to use non standard file extensions on the binaries. Sometimes they are numbers like 342, 343, 552 or sometimes tdb or .zk. All of these are actually DLL files that rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it to. I am informed that Locky is now using .Osiris file extensions on the encrypted files… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/794dcfdcc1362140eee6fcda11ddf239ab048a965bba634bb787321db9672cfa/analysis/1480616575/
Fake 'Consider This' SPAM - leads to Locky
- http://blog.dynamoo.com/2016/12/malware-spam-please-consider-this-leads.html
5 Dec 2016 - "This -fake- financial spam leads to malware: From: Aimee Guy
Date: 5 December 2016 at 13:32
Subject: Please Consider This
Dear [redacted],
Our accountants have noticed a mistake in the payment bill #DEC-5956047.
The full information regarding the mistake, and further recommendations are in the attached document.
Please confirm the amount and let us know if you have any questions.
Attached is a ZIP file with a name somewhat matching the reference in the email, containing a malicious VBS script with a filename made up in part of the date. The scripts download another component… (Long list of domain-names at the dynamoo URL above.)
… It drops a payload with an MD5 of 529789f27eb971ff822989a5247474ce and a current detection rate of just 1/54*. The malware then phones home to the following locations:
91.142.90.61 /information.cgi [hostname: smtp-server1.ru] (Miran, Russia)
195.19.192.99 /information.cgi (EkaComp, Russia)
These IPs were also used in this earlier attack**.
Recommended blocklist: 185.82.217.28
91.142.90.61
195.19.192.99 "
* https://virustotal.com/en/file/6a186b353bbd729a2cbaa42b0c78ee67cfe69d3b1e56e1a10f1d33afc5ac473e/analysis/
Fake 'Sage invoice' SPAM - delivers Dridex
- https://myonlinesecurity.co.uk/spoofed-sage-outdated-invoice-delivers-dridex-banking-trojan/
5 Dec 2016 - "… an email with the subject of 'Outdated invoice' coming or pretending to come from Sage invoice . There is no zip attachment with this Dridex delivery today, but a-link-in-the-body to download an invoice.zip from a hacked/compromised/fraudulently set up sharepoint site… from a site set up by the criminals to malspam the Dridex banking Trojan. The site is registered to a Chinese entity and hosted on an OVH server in France (SAGE-UK .ORG 46.105.101.84 ns3060005.ip-188-165-252.eu). One of the emails looks like: From: Sage invoice
Date: Mon 05/12/2016 12:48
Subject: Outdated invoice
Attachment: link in email to download invoice.zip
Software for business
Sage Account & Payroll
You have an outdated invoice from Sage Accounting that is ready for payment. To find out more details on this invoice, please follow the link below to download your account invoice:
https ://invoice.sage .co.uk/Account?864394=xUzlmOHtPY
If we have any information about you which is incorrect or if there are any changes to your details please let us know so that we could keep our records accurate…
5 December 2016: Invoice.zip: Extracts to: Invoice.js - Current Virus total detections 3/53*
Payload Security** shows a download from ‘http ://neelkanthelevators .com/images/about1.png’ (VirusTotal 10/56***). Payload Security[4]. This is -not- a png (image file) but a -renamed- .exe file, which the script renames to LzG7FzcEz.exe and runs… The basic rule is NEVER open any attachment to an email [OR click-a-link in it] unless you are expecting it…"
* https://www.virustotal.com/en/file/cff532924f6bcb240cbee418f0bdc0845c7da0a05c936411959e3b65dcf9bc83/analysis/1480944742/
The link-in-the-email actually goes to a URL vantaiduonganh .vn/api/get.php?id= plus a Base 64 encoded part of the URL (e.g. aGVscGRlc2tAZmJpLmdvdg==) and it downloads a Word document with the recipients email address included in it. This type of malware is typically seen using hacked but legitimate Vietnamese sites for this stage in the infection chain. This DOC file contains a malicious macro, the Malwr report* indicates that it downloads components from:
parkovka-rostov .ru/inst.exe
stela-krasnodar .ru/wp-content/uploads/pm22.dll
Those two locations are legitimate -hacked- sites. This has a detection rate of 7/56** plus a DLL with a detection rate of 37/56***. The malware appears to be Hancitor/Pony/Vawtrak, phoning home to:
cothenperci .ru/borjomi/gate.php
madingtoftling .com/ls5/forum.php
Both of these are hosted on the same IP address of 185.31.160.11 (Planetahost, Russia)… malicious domains are also hosted on the same IP… (List of domain-names at the dynamoo URL above.
… Recommended blocklist: 185.31.160.11
parkovka-rostov .ru
stela-krasnodar .ru "
* https://malwr.com/analysis/YmM1OGI0Mjk0MzU5NDJiNDkxNzk1MDM1OTg2MmYyM2I/
Hosts 54.243.91.166
185.31.160.11
77.222.42.115
81.177.165.101
Fake 'Urgent Data' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/urgent-data-the-error-occurred-during-payment-malspam-delivers-locky/
5 Dec 2016 - "… Locky downloader… an email with the subject of 'Urgent Data' coming or pretending to come from random companies, names and email addresses with a semi-random named zip attachment in the format of payment random numbers.zip… One of the emails looks like: From: Consuelo Wells <Wells.Consuelo@ skriverconsult .ch>
Date: Mon 05/12/2016 20:20
Subject: Urgent Data
Attachment: payment9095450.zip
Dear [redacted],
The error occurred during payment. Sending you details of the transaction.
Please pay the remaining amount as soon as possible.
King Regards,
Consuelo Wells
5 December 2016: payment9095450.zip: Extracts to: ~3X072I792ZJ.js - Current Virus total detections 4/55*
MALWR** shows a download of an encrypted file from http ://prosperer .mg/3n7uihwc0p which is converted by the script to yQC6CSDVn.zk (VirusTotal 5/57***). Payload Security[4]. Locky has recently started to use non standard file extensions on the binaries. Sometimes they are numbers like 342, 343, 552 or sometimes tdb or .zk. All of these are actually DLL files that rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it to… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/26ba3b70d022cf6b0e5d3fb886cb2385d4606cd5034329bc10f9b9b432a6ab7c/analysis/1480969517/
Fake 'PO' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/inv-1465095170-for-po-0ac27757-malspam-delivers-locky/
6 Dec 2016 - "An email with the subject of 'Inv# 1465095170 for PO# 0AC27757' (random numbers) pretending to come from random senders with a malicious word doc spreadsheet attachmentdelivers Locky osiris… The email looks like: From: From: pettengell, judith
Date: Tue 06/12/2016 12:18
Subject: Inv# 1465095170 for PO# 0AC27757
Attachment: 0AC27757_1465095170.docm
Please do not respond to this email address. For questions/inquires, please
contact our Accounts Receivable Department.
This email has been scanned by the MessageLabs outbound
Email Security System for CIRCOR International Inc…
6 December 2016: 0AC27757_1465095170.docm - Current Virus total detections 8/51*
MALWR** shows a download of an encrypted file from http ://union1 .cn/0bgsvtr3 which is converted by the script to dipund1.rap (VirusTotal 9/56***). Payload Security[4]. Locky has recently started to use non standard file extensions on the binaries. Sometimes they are numbers like 342, 343, 552 or sometimes tdb or .zk. All of these are actually DLL files that rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it to…
C2 http ://185.115.140.210 /checkupdate | http ://91.142.90.46 /checkupdate | http ://213.32.66.16 /checkupdate …
DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/f8f226d3a018ceae734fb0d99d3eb24b824be1691fe3a58a67b6fc1b5602c37d/analysis/1481027450/
Fake 'Recent order' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/recent-order-malspam-delivers-locky/
6 Dec 2016 - "… an email with the subject of 'Recent order' coming or pretending to come from random companies, names and email addresses with a semi-random named zip attachment in the format of order random numbers.zip which delivers Locky ransomware… One of the emails looks like: From: Jocelyn Dodson
Date: Tue 06/12/2016 09:29
Subject: Recent order
Attachment: order3202227.zip
Dear adkins,
The counteragent has conducted the checking and found no confirmed payment for the recent order…
All details are in the attachment.
Feel free to email us if you have any inquiry.
King Regards,
Jocelyn Dodson
6 December 2016: order3202227.zip Extracts to: ~8FX934T59F85.js - Current Virus total detections 6/54*
MALWR** shows a download of an encrypted file from http ://steffweb .dk/bkjybit which is converted by the script to AEyjwjkWiBbl6.zk (VirusTotal 7/57***). Payload Security[4]. Locky has recently started to use non standard file extensions on the binaries. Sometimes they are numbers like 342, 343, 552 or sometimes tdb or .zk. All of these are actually DLL files that rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it what to do…
The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/696a04cd293935e41bd24965ee66984c7cb87f3a2843268ef43628358eafcd7c/analysis/1481018575/
Amazon - phish
- https://myonlinesecurity.co.uk/new-return-requested-on-amazon-for-order-502-2849265-1928845-phishing/
6 Dec 2016 - "'New Return Requested on Amazon for order 502-2849265-1928845' pretending to come from Amazon .co.uk is one of the latest -phish- attempts to steal your Amazon Account. This one only wants your Amazon log in details… The link leads to http ://tolmasoft .ru/ViewListingAccount-dvk@ [redacted].co.uk.html…
When you fill in your user name and password you get immediately -redirected- to the genuine Amazon.co.uk home page, where you think that you have logged in properly. All of these emails use Social engineering tricks to persuade you to open the attachments that come with the email…"
The website appieid-support .com is hosted on 108.167.141.128 which is a customer of WebsiteWelcome… no-doubt-fake WHOIS details… The domain was created just today. Avoid."
Fake 'Invoices' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/three-invoices-4282-284-4283-99-4287-564-are-not-paid-malspam-delivers-locky/
7 Dec 2016 - "… an email with the subject of 'Invoices' pretending to come from random companies, names and email addresses with a semi-random named zip attachment which delivers Locky ransomware… One of the emails looks like: From: Margery Hinton
Date: Wed 07/12/2016 10:10
Subject: Invoices
Attachment: invoices0660953.zip
Dear zowm,
By today, three invoices (4282, $284; 4283, $99; 4287, $564) are not paid.
Starting tomorrow, fines will be charged. Please make appropriate payments.
All details are in the attachment.
Best Regards,
Margery Hinton
Sales Director
7 December 2016: invoices0660953.zip: Extracts to: ~8G9Z5BP2U18O48QKC6O54YE4.js
Current Virus total detections 2/55* Payload Security** shows a download of an encrypted file from
sagaoil .ro/jv5f0mrnea which is converted by the script to BQODhCNNx.zk … Locky has recently started to use non standard file extensions on the binaries. Sometimes they are numbers like 342, 343, 552 or sometimes tdb or .zk. All of these are actually DLL files that rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it what to do… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/dabd27dcf3e5a3ef3c2b89c480a1c69c10bb1f9b2b53614c5e5d45026a175f64/analysis/1481105284/
7 December 2016: CARD547 8914860.docm - Current Virus total detections 12/56*
MALWR** shows a download of an encrypted file from http ://unilite .ro/hfycn33 which is converted by the script to spircent1.mda (Payload Security ***) (virusTotal 10/54[4]). Locky has recently started to use non standard file extensions on the binaries. Sometimes they are numbers like 342, 343, 552 or sometimes tdb or .zk. All of these are actually DLL files that rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it what to do… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/7c2122fabf2336ff47b075e6686c688eac30933c5aed813a42c5e8b8c3918284/analysis/1481104682/
Stegano EK hiding in pixels of malicious ads
- http://www.welivesecurity.com/2016/12/06/readers-popular-websites-targeted-stealthy-stegano-exploit-kit-hiding-pixels-malicious-ads/
Dec 6, 2016 - "Millions of readers who visited popular news websites have been targeted by a series of malicious ads -redirecting- to an exploit kit exploiting several -Flash- vulnerabilities. Since at least the beginning of October, users might have encountered ads promoting applications calling themselves 'Browser Defence' and 'Broxu' using banners similar to the ones below:
1] http://www.welivesecurity.com/wp-content/uploads/2016/12/1-xlch3.png
…
2] http://www.welivesecurity.com/wp-content/uploads/2016/12/2-y0vbp.png
These advertisement banners were stored on a remote domain with the URL hxxps ://browser-defence .com and hxxps ://broxu .com. Without requiring any user interaction, the initial script reports information about the victim’s machine to the attacker’s remote server. Based on server-side logic, the target is then served either a clean image or its almost imperceptibly modified malicious evil twin. The malicious version of the graphic has a script encoded in its alpha channel, which defines the transparency of each pixel… After successful redirection, the landing page checks the userAgent looking for Internet Explorer, loads a Flash file, and sets the FlashVars parameters via an encrypted JSON file. The landing page also serves as a middleman for the Flash and the server via ExternalInterface and provides basic encryption and decryption functions. The Flash file has another Flash file embedded inside and, similarly to the -Neutrino- exploit kit, it comes with three different exploits based on the Flash version… Conclusion: The Stegano exploit kit has been trying to fly under the radar since at least 2014. Its authors have put quite some effort into implementing several techniques to achieve self-concealment. In one of the most recent campaigns we detected, which we traced back at least to the beginning of October 2016, they had been distributing the kit through advertisement banners using steganography and performing several checks to confirm that they were not being monitored. In the event of successful exploitation, the vulnerable victims’ systems had been left exposed to -further- compromise by various malicious payloads including backdoors, spyware and banking Trojans. Exploitation by the Stegano kit, or any other known exploit kit for that matter, can often be avoided by running fully patched software and by using a reliable, updated internet security solution…" (More detail at the welivesecurity/ESET URL above.)
browser-defence .com: Could not find an IP address for this domain name…
AdGholas malvertising …
- https://blog.malwarebytes.com/cybercrime/exploits/2016/12/adgholas-malvertising-business-as-usual/
Dec 6, 2016 - "… A group identified as AdGholas* by Proofpoint which has been involved in the stealthiest attacks we have seen in recent history, was caught again and exposed by Eset**… The last bit of activity from AdGholas after the Proofpoint exposé was July 20th of this year. However, according to our telemetry, less than two months later the group was back at it with some of the -largest- malvertising attacks we have ever documented… The interesting aspect about this malvertising campaign is that the US was -not- one of the targets. Instead we saw Canada, the UK, Australia, Spain, Italy, and Switzerland as the most active geolocations. We observed most attacks happen in Canada and the UK as seen below on this heat map:
> https://blog.malwarebytes.com/wp-content/uploads/2016/12/heatmap.png
Despite not targeting the US, the latest AdGholas campaign has once again reached epic proportions and unsuspecting users visiting top trusted portals like Yahoo or MSN (not to mention many top level publishers) were exposed to malvertising and malware if they were not protected…"
* https://www.proofpoint.com/us/threat-insight/post/massive-adgholas-malvertising-campaigns-use-steganography-and-file-whitelisting-to-hide-in-plain-sight
Fake 'Emailing' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/emailing-mx62edo-08-12-2016-documents-your-own-email-address/
8 Dec 2016 - "An email with the subject of 'Emailing: MX62EDO 08.12.2016' pretending to come from documents@ your-own-email-address with a malicious word docdelivers Locky Osiris… The email looks like: From: documents@ thespykiller .co.uk
Date: Thu 08/12/2016 10:05
Subject: Emailing: MX62EDO 08.12.2016
Attachment:
Your message is ready to be sent with the following file or link
attachments:
MX62EDO 08.12.2016
Note: To protect against computer viruses, e-mail programs may prevent
sending or receiving certain types of file attachments. Check your e-mail
security settings to determine how attachments are handled.
This email has been checked for viruses by Avast antivirus software…
8 December 2016: MX62EDO 08.12.2016.docm - Current Virus total detections 10/54*
MALWR** shows a download of an encrypted file from http ://netfun .be/hb74 which is converted by the script to clsooach1.feds (VirusTotal 11/56***). Payload Security[4]. Locky has recently started to use non standard file extensions on the binaries. Sometimes they are numbers like 342, 343, 552 or sometimes tdb or .zk. All of these are actually DLL files that rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it what to do… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/4cefb793010150a0c217ca7eb3410a70221e11c6ba7cb094c8d0bf743bc3bb79/analysis/1481192959/
Fake 'Order' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/more-random-orders-with-long-random-reference-number-malspam-delivers-locky/
8 Dec 2016 - "… an email with the subject of 'Order #0850834' (random numbers) coming or pretending to come from random companies, names and email addresses with a semi-random named zip attachment matching the subject line which delivers Locky ransomware… One of the emails looks like: From: Latoya Byrd
Date: Thu 08/12/2016 11:29
Subject: Order #0850834
Attachment: order-0850834.zip
Hello ard, your order #0850834 …
Sending you the receipt. Please pay it prior to next week.
The receipt is in the attachment.
Best Wishes,
Latoya Byrd
Delivery Manager
8 December 2016: order-0850834.zip: Extracts to: ~5Z36TWQXK9014CO228K8V0C.js
Current Virus total detections 6/55*. MALWR** shows a download of an encrypted file from
http ://file4hosti .info/ne92o1u which is converted by the script to 7JpjNVpwmyeHv.zk (VirusTotal 4/53***).
Payload Security[4]. Locky has recently started to use non standard file extensions on the binaries. Sometimes they are numbers like 342, 343, 552 or sometimes tdb or .zk. All of these are actually DLL files that rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it what to do… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/144de00c3ac9373089eb01ed192bb412008bf3300941deb6f72a5fe4caf0a767/analysis/1481196535/
Fake 'Scan' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/scan-from-a-samsung-mfp-malspam-delivers-locky-osiris/
8 Dec 2016 - "… an email with the subject of 'Scan' from a Samsung MFP coming or pretending to come from random companies, names and email addresses with a semi-random named zip attachment in the format of Untitled_date_random numbers.zip which delivers Locky ransomware… One of the emails looks like: From: GARRY MENZIES
Date: Wed 07/12/2016 21:41
Subject: Travel expense sheet
Attachment: Untitled_07122016_46160.zip
Regards
Garry
Please open the attached document. It was scanned and sent to you using a
Samsung MFP. For more information on Samsung products and solutions, please
visit …
This message has been scanned for malware by Websense…
8 December 2016: Untitled_07122016_46160.zip: Extracts to: N396390423.jse - Current Virus total detections 19/55*
MALWR** shows a download of an encrypted file from http ://raivel .pt/45gdfgf?SEOtErERwE=yLVujYkT which is converted by the script to XtPmJmcsvIP1.dll (VirusTotal 24/56***). Payload Security[4]. Locky has recently started to use non standard file extensions on the binaries… DLL files… rundll32.exe will run via the macro or VBS/JS/WSF scripting file telling it what to do… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/011ad4aeaa6bcdb5327f0a0c44429dfd062bef3708e5f273c6053dc974926f78/analysis/1481168279/
If you follow the links you end up on an identical copy of the gov .uk site asking for usual identity and financial details:
> https://i1.wp.com/myonlinesecurity.co.uk/wp-content/uploads/2016/12/fake-gov_uk_vehicle-tax-refund-site.png?resize=1024%2C533&ssl=1 Phishing sites so far discovered include (email links go to a site which -redirects- you to other sites):
- https ://cissdemexico .com/.2DriverLicence2ADM2/2y2Driving2e2Licences2acc2/24w823w82Driving2w25and22w2Transport2w826w2gov28uk25/23Lega2r28obligations62Apply2refund2x82driving24/Refund.php
- https ://chadena .com/.cha/
- https ://fyfe-interiors .com/.lol/
- https ://partnersinsharing .com/.124DL828ADM825/2384x48390Driving9019x319Licences0638cbd419/7836Lega523x92148obligations639Apply915x3420/517x9427c481Driving827x5and32v0417Transport71x5638x319gov31uk24/Refund "