'Credit/Debit Card temporarily disabled' – PHISH
- https://myonlinesecurity.co.uk/we-have-temporarily-disabled-your-creditdebit-card-phishing/
18 June 2016 - "There are a few major common subjects in a phishing attempt. Lots of them are either PayPal, your Bank or your Credit Card, with a message saying some thing like : Urgent: Your card has been stopped !
There have been unauthorised or suspicious attempts to log in to your account, please verify
Your account has exceeded its limit and needs to be verified
Your account will be suspended !
You have received a secure message from < your bank>
We are unable to verify your account information
Update Personal Information
Urgent Account Review Notification
We recently noticed one or more attempts to log in to your PayPal account from a foreign IP address
Confirmation of Order
We have temporarily disabled your Credit/Debit Card
The original email looks like this. It will NEVER be a genuine email from PayPal, your Bank or credit card so don’t ever follow the links or fill in the html (webpage) form that comes attached to the email. Note the bad spelling of norepply and the VLSA .COM that is supposed to say visa .com (using lookalike domains is a common trick that phishers use. The English Grammar in the email is just not quite right, so suggesting that this was created by somebody that doesn’t have English as their primary language…
Fake 'Apple ID' SPAM / Phish
- https://myonlinesecurity.co.uk/your-apple-id-has-been-disabled-for-security-reasons-phishing/
20 June 2016 - "… Apple phishing attempt… 300 copies in the last couple of hours. The subject is one we see regularly 'Your Apple ID has been disabled for security reasons!'… several copies where all the body content is in the subject line & nothing in the body: From: Apple
Date: Mon 20/06/2016 11:12
Subject: Your Apple ID has been disabled for security reasons!
Attachment: None
The link behind the verify now goes to http ://interwurlitzer .com/write/it.html which -redirects- to
http ://flyingstart .ca/science/disabled/apple/index.php neither of which look even vaguely like any Apple site so shouldn’t fool anybody… some careless users will click through, not look at the URL in the browser and give all their details:
> https://myonlinesecurity.co.uk/wp-content/uploads/2016/06/flyinmgstart_apple_phish-1024x596.png
If you are careless enough or unwise enough to enter your apple ID & password, you get to this page where they ask for all the personal & financial information:
> https://myonlinesecurity.co.uk/wp-content/uploads/2016/06/verify_apple_ID_ab-754x1024.png
… Watch for any site that invites you to enter -ANY- personal or financial information. It might be an email that says 'you have won a prize' or 'sign up to this website for discounts, prizes and special offers'…"
Fake 'Swift Payment Notice' SPAM - malicious link
- https://isc.sans.edu/diary.html?storyid=21177
2016-06-20 - "Some of our readers reported spam messages related to the recent Swift case. With all the buzz around this story, it looks legitimate to see more and more attackers using this scenario to entice victims to open malicious files. The mail subject is "Swift Payment Notice, pls check" and contains an image of a receipt embedded in an HTML page… The HTML-link-points to a malicious PE file called "SWIFT COPY.exe" (MD5: 6ccabab506ad6a8f13c6d84b955c3037). The file is downloaded from a compromized Wordpress instance and seems to contain a keylogger. Data are sent to onyeoma5050s .ddns .net. The host resolved to [removed] but it is not valid anymore (take down already completed?). Even if PE files should be blocked by most web proxies, the current VT score remains low (6/55*) which still makes it dangerous."
* https://www.virustotal.com/en/file/364e3388c27dd27f8d07951535d1589d0a522e3c84f65529b8f2b8979732d794/analysis/
___
Fake Dropbox SPAM - js malware
- https://myonlinesecurity.co.uk/andrew-lumley-sent-you-scan001-zip/
20 June 2016 - "… an email with the subject of 'Andrew Lumley sent you Scan001.zip' pretending to come from Andrew Lumley via Dropbox with a link to a zip file containing 3 identical JavaScript files…
20 June 2016: scan001.zip: Extracts to: scan0001.js - Current Virus total detections 3/56*
.. Payload security** shows a download from 69.20.55.160 :80/Scripts/rex7.exe (VirusTotal 3/56[3])
(Payload Security[4])… This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/ccf1ebcc76bd843a1a91d49fccc5e3c91c2d37dc28c777247ea6f1c278f5e2a3/analysis/1466428353/
20 June 2016: vat030116-0530161.doc - Current Virus total detections 4/55*.
.. Payload Security[2] shows it downloads http ://xbdev .net/hmrc.zip (VirusTotal 4/56**)… it is Sharik which is a password stealer… DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/a7ac9f54bf64e4bb09fdcf74bea7e9430c4c13d418f94add3578a806e6cfdf21/analysis/1466424536/
Fake 'PO' SPAM - Java malware attachment
- https://myonlinesecurity.co.uk/order-for-scarves-java-malware/
20 June 2016 - "An email pretending to be an order for scarves with the subject of 'Re: PO' pretending to come from Martina O’Shea with a Java jar attachment… One of the emails looks like: From: Martina O’Shea
Date: Mon 20/06/2016 11:46
Subject: Re: PO
Attachment: 23456445.jar
Good morning
Please find attached an order for some scarves
for delivery to our warehouse in Churchfield,
Cork.
Please confirm all scarves are available and a
delivery date for same.
Many thanks.
Kind regards,
Manager – Buying Administration Dept
The Kilkenny Group …
20 June 2016: 23456445.jar - Current Virus total detections 15/56*
I don’t have Java installed and none of the online analysers ever tell us anything really useful about java files but MALWR** does show several files being dropped or downloaded… This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/61961155846e65e4f2362ad9e8da7a204099b0b26446c4c01f9a08abe55addbb/analysis/1466389366/
JavaScript ransomware
- http://www.trendmicro.com.au/vinfo/au/security/news/cybercrime-and-digital-threats/new-raa-ransomware-uses-only-javascript-to-infect-computers
June 16, 2016 - "… ransomware called RAA is composed entirely of JavaScript and has been spreading via email attachments that pretend to be doc files with names like mgJaXnwanxlS_doc_.js. Once the JavaScript is opened, it will encrypt files in the affected machine and demand a ransom amounting roughly to US$250 to get the files. Reportedly, RAA infections display the ransom note in Russian, however, it’s only a matter of time until it’s distributed more widely and localized for other languages. Additionally, the ransomware also infects the victim’s computer by installing Pony, a well-known password-stealing malware embedded in the JavaScript file. This malware can collect browser passwords and other user information from an infected machine, and is usually used by hackers to gather critical information on infected systems. Pony is similar with banking trojans, but its behavior was not manifested in RAA. The RAA ransomware is considered unique because it’s rare to see client-side malware written in web-based languages like JavaScript, which are primarily designed to be interpreted by browsers. Microsoft has previously warned* about a spike in malicious email attachments containing JavaScript files in April 2016. The following month, security researchers alerted about spam emails that delivers and distributes the Locky ransomware via .js attachments. Both Locky and RAA uses JavaScript files as malware downloaders — designed to download and install a traditional malware program. With RAA however, the entire ransomware is written in JavaScript…"
* https://blogs.technet.microsoft.com/mmpc/2016/04/18/javascript-toting-spam-emails-what-should-you-know-and-how-to-avoid-them/
"… The spam email contains a .zip or .rar file attachment which carries a malicious JavaScript…"
Fake 'Invoice' SPAM - malicious attachment
- https://myonlinesecurity.co.uk/fw-invoice_515002/
21 June 2016 - "An email pretending to be a sage invoice with the subject of 'FW: Invoice_515002' coming from “[removed]”@ footballplayers19 .gq; on behalf of; Leanna Sage Whitaker with a zip attachment… We have been seeing a few emails over the last couple of weeks from the footballplayers*.g* domains. Some pure spam, some phishing and some malware. It looks like a mailing list that must have some vulnerability to allow external users to be sent emails via them. One of the emails looks like: From:”[removed]”@ footballplayers19 .gq; on behalf of; Leanna Sage Whitaker
Date: Tue 21/06/2016 10:05
Subject: FW: Invoice_515002
Attachment:
Please see attached copy of the original invoice (sage_invoice_131340_711410101502668.pdf).
21 June 2016: sage_invoice_515002_3841674267107.zip: Extracts to: sage_invoice_225224_4233.exe
Current Virus total detections 6/56*.. Payload Security** shows it posts some information to a Ukrainian IP 217.12.199.87… This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/d22a50f6a2e2aa98197135f39113ed54a2d037e2b59d9d9faea3971997205c66/analysis/1466500334/
Fake 'RE:' SPAM - Locky .js attachment
- https://myonlinesecurity.co.uk/it-looks-like-locky-is-back/
21 June 2016 - "It looks like Locky ransomware is back tonight with a series of generic emails pretending to be invoices with the subject of 'RE:' pretending to come from random senders with a zip attachment which downloads what looks suspiciously like Locky Ransomware… None of the auto analysers can effectively decode these encrypted javascripts inside the zips… One of the emails looks like: From: Titus Sampson
Date: Tue 21/06/2016 18:16
Subject: RE:
Attachment: wilbarger_invoice_181696.zip
Dear wilbarger:
Please find attached our invoice for services rendered and additional disbursements in the above-
mentioned matter.
Hoping the above to your satisfaction, we remain.
Sincerely,
Titus Sampson
General Manager
Ransomware decrypter released
- https://www.helpnetsecurity.com/2016/06/22/decrypter-apocalypsevm/
June 22, 2016 - "… Emsisoft has added yet another ransomware decrypter tool to its stable: a decrypter for ApocalypseVM*. The tool works on the latest versions of the ransomware in question:
> https://www.helpnetsecurity.com/images/posts/Decrypter-ApocalypseVM.jpg
… The victim can then decide to use it on one, some, or all encrypted files. The tool selects the C: partition of the disk by default, but victims can choose other partitions or files to be decrypted. Emsisoft recommends testing the key first on a few files, then to proceed decrypting the rest if everything goes well with the test…"
* https://decrypter.emsisoft.com
Jun, 18, 2016 - Version: 1.0.0.23
___
Fake 'Corresponding Invoice' SPAM - leads to Locky
- http://blog.dynamoo.com/2016/06/malware-spam-corresponding-invoice.html
22 June 2016 - "This spam has a malicious attachment… leading to Locky ransomware: From: Althea Duke
Date: 22 June 2016 at 16:00
Subject: Corresponding Invoice
Dear lisa:
Thank you for your email regarding your order of 21 June, and sorry for the delay in replying. I am
writing to confirm receipt of your order, and to inform you that the item you requested will be delivered
by 25 June at the latest. If you require more information regarding this order, please do not hesitate to
contact me.
Also, our records show that we have not yet received payment for the previous order of 11 June,
so I would be grateful if you could send payment as soon as possible. Please find attached the
corresponding invoice.
If there is anything else you require, our company would be pleased to help. Looking forward to
hearing from you soon.
Yours sincerely
Althea Duke
Managing Director
UPDATE: A little bit of analysis, via these automated reports [1] [2].. show some download locations as:
personal-architecture .nl/6gcpaey
ding-a-ling-tel .com/b289dg
plasticsmachine .com/d43ndxna
hyip-all .com/9qwmc65
Various files are dropped, including these samples [6] [7] the latter of which is a three week old version of Locky. Go figure. The comments in this report show C2 servers at:
51.254.240.48 (Andrey Orlov aka Relink LLC, Russia / OVH, France)
91.219.29.41 (FLP Kochenov Aleksej Vladislavovich aka uadomen.com, Ukraine)
185.82.216.55 (ITL, Bulgaria)
93.170.169.188 (PE Dunaeivskyi Denys Leonidovich, Ukraine) Three out of those four servers are the -same- as yesterday*.
Recommended blocklist: 51.254.240.48
91.219.29.41
185.82.216.55
93.170.169.188."
* http://blog.dynamoo.com/2016/06/malware-spam-please-find-attached-our.html
- https://myonlinesecurity.co.uk/thank-you-for-your-email-regarding-your-order-of-21-june-and-sorry-for-the-delay-in-replying-delivers-locky-ransomware/
22 June 2016 - "An email with the subject of 'Corresponding Invoice' pretending to come from random senders with a zip attachment which downloads Locky ransomware… These contain a heavily obfuscated JavaScript inside the zip. It has several layers of obfuscation. The alleged senders name matches the name in the body of the email. The job title is also random and can be anything from Sales Director, Account Director or any other position that any company might think of… This Blog post* describes how to manually deobfuscate these horridly difficult & tricky JavaScript files.
* https://malcat.moe/?p=53
One of the emails looks like: From: Mariano Hoover
Date: Wed 22/06/2016 15:10
Subject: Corresponding Invoice
Attachment: rob_unpaid_673442.zip
Dear rob:
Thank you for your email regarding your order of 21 June, and sorry for the delay in replying. I am
writing to confirm receipt of your order, and to inform you that the item you requested will be delivered
by 25 June at the latest. If you require more information regarding this order, please do not hesitate to
contact me.
Also, our records show that we have not yet received payment for the previous order of 11 June,
so I would be grateful if you could send payment as soon as possible. Please find attached the
corresponding invoice.
If there is anything else you require, our company would be pleased to help. Looking forward to
hearing from you soon.
Yours sincerely
Mariano Hoover
Regional Sales Director
22 June 2016: rob_unpaid_673442.zip: Extracts to: unpaid-5967.js - Current Virus total detections 2/56**
.. Payload Security*** shows us downloads from totalsportnetwork .com/kpbrp2mq or modelestrazackie .za.pl/zfww8nx which are encrypted files that get decrypted by the original JavaScript files to give
%TEMP%\OVAkXuGy.exe (VirusTotal 12/55[4]). These encrypted files make it very difficult for an antivirus to prevent download because they are are plain text, albeit in total gibberish to a human reader… This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected…"
Fake 'On Hold Transactions' SPAM - malicious attachment
- https://myonlinesecurity.co.uk/on-hold-transactions-from-21-06-2016-xpress-money-services/
22 June 2016 - "An email with the subject of 'On Hold Transactions From 21.06.2016' pretending to come from Saeed Abugharbieh with a zip attachment that contains a Barys Trojan and a copy of the image in the email. The .exe file drops a JAVA jar file that is most likely Java Jacksbot Trojan…
22 June 2016: On Hold Transactions From 21.06.2016.zip: Extracts to: On Hold Transactions From 21.06.2016.exe
Current Virus total detections 15/56*.. MALWR** shows this drops a JAVA.jar file 812594500.jar which appears to be Java Jacksbot Trojan (VirusTotal 29/56***). MALWR[4]… This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/c79000167a1ba40bbf4c38425f1e0eb1932bfeb8e555458944ed602ea4c4249c/analysis/1466613297/
Fake 'Payment' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/our-records-show-that-we-have-not-yet-received-payment-for-the-previous-order-delivers-locky/
22 June 2016 - "An email with the subject of 'Payment' pretending to come from random senders with a zip attachment which downloads Locky ransomware… These contain a heavily obfuscated JavaScript inside the zip. It has several layers of obfuscation. The alleged senders name matches the name in the body of the email. The job title is also random and can be anything from Sales Director, Account Director or any other position that any company might think of… This Blog post* describes how to manually deobfuscate… JavaScript files. The JavaScript in this one is the -same- as THIS earlier run of Locky downloaders**…
* https://malcat.moe/?p=53
This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected…"
___
Fake 'documents for your reference' PHISH
- https://myonlinesecurity.co.uk/please-find-below-documents-for-your-reference-kindly-sign-owa-phishing/
22 June 2016 - "An email saying 'Please find below documents for your reference kindly sign' pretending to come from gccremittance@ emirates .net.ae is one of the latest -phish- attempts to steal your Outlook Web App log on details which is generally your Microsoft account details…
Fake 'invoice' SPAM - leads to Locky
- http://blog.dynamoo.com/2016/06/malware-spam-please-find-attached-our.html
21 June 2016 - "This malicious spam leads to Locky ransomware, something that we haven't seen for several weeks: From: Lilian Fletcher
Date: 21 June 2016 at 20:01
Subject: Re:
Dear lisa:
Please find attached our invoice for services rendered and additional disbursements in the above-
mentioned matter.
Hoping the above to your satisfaction, we remain.
Sincerely,
Lilian Fletcher
Head of Maintenance
These are being sent out in huge numbers at the moment. Details vary from message to message, but the body text is essentially the same. Attached is a ZIP file containing the words 'addition', 'invoice' or 'services' plus the recipients email address and a number (e.g. lisa_addition_278292.zip) containing a malicious script beginning with the word "addition"… Analysis.. shows that it phones home to:
51.254.240.48 (Andrey Orlov aka Relink LLC, Russia / OVH, France)
91.219.29.41 (FLP Kochenov Aleksej Vladislavovich aka uadomen.com, Ukraine)
185.82.216.55 (ITL, Bulgaria)
217.12.223.83 (ITL, Ukraine)
As I mentioned before, this is Locky ransomware which has not been circulating at all since about 31st May.
Recommended blocklist: 51.254.240.48
91.219.29.41
185.82.216.55
217.12.223.83 "
Fake 'report' SPAM - leads to Locky
- http://blog.dynamoo.com/2016/06/malware-spam-final-version-of-report.html
23 June 2016 - "This spam leads to malware: From: Julianne Pittman
Date: 23 June 2016 at 09:48
Subject: Final version of the report
Dear info,
Patrica Ramirez asked me to send you the attached Word document, which contains the final version of the report.
Please let me know if you have any trouble with the file, and please let Patrica know if you have any questions about the contents of the report.
Kind regards
Julianne Pittman
Operations Director (CEO Designate)
The names in each version of the email vary. Attached is a ZIP file with a filename containing some version of the recipients email address and the word "report" which contains in turn a malicious ZIP .js script beginning with the words "unpaid"…
UPDATE… Hybrid Analysis of three sample scripts [1] [2].. show three download locations (you can bet there will be many more):
bptec .ir/kvk9leho
promoresults .com.au/gx4al
boranwebshop .nl/ggc7ld
Each one drops a slightly different binary (VirusTotal results [4] [5]..).. C2 servers are at:
51.254.240.48 (Rackspace, US)
91.219.29.41 (FLP Kochenov Aleksej Vladislavovich aka uadomen.com, Ukraine)
[removed] (ITL, Ukraine)
195.123.209.227 (ITL, Latvia)
93.170.169.188 (PE Dunaeivskyi Denys Leonidovich, Ukraine)
The malware uses the path /upload/_dispatch.php on the C2 servers.
Recommended blocklist: 51.254.240.48
91.219.29.41
217.12.223.88
195.123.209.227
93.170.169.188 "
1] https://www.hybrid-analysis.com/sample/1a0b5636e168c262e7c0d9c4a7a88874877856615c2207d7c82d7349cfd557e4?environmentId=100
- https://myonlinesecurity.co.uk/final-version-of-the-report-malspam-leads-to-locky-ransomware/
23 June 2016 - "An email with the subject of 'Final version of the report' pretending to come from random senders with a zip attachment containing a JavaScript file which downloads Locky Ransomware… One of the emails looks like: From: Jeri Kline
Date: Thu 23/06/2016 09:41
Subject: Final version of the report
Attachment: rob_scan_report_094249.zip
Dear rob,
Randall Franks asked me to send you the attached Word document, which contains the final version of the report.
Please let me know if you have any trouble with the file, and please let Randall know if you have any questions about the contents of the report.
Kind regards
Jeri Kline
Key Account Director Municipalities
23 June 2016: rob_scan_report_094249.zip: Extracts to: unpaid-068.js - Current Virus total detections 1/56*
.. Payload security** shows a download of encrypted Locky from
abligl .com/8v62l4i4 which the JavaScript from the email converts to 2oyWQ1WPdr1i.exe (VirusTotal 4/55***).
These encrypted files make it very difficult for an antivirus to prevent download because they are just plain text, albeit in total gibberish to a human reader… This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/d44a916aab7adab16e0440f766138e3036e30e64eca2575421545693e685cf7d/analysis/1466674224/
23 June 2016: TRANSFER STATEMENT.doc - Current Virus total detections 15/55*
.. where it is described as CVE-2010-3333[1] exploit which was fixed by Microsoft in 2010/2011…
Update: The download site is http ://www.akkoprint .ro/wp-content/uploads/2016/06/office.exe (VirusTotal 43/55**)
Payload Security*** … DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/f86ae6af50668da4fe06e17f4fd8534b038fc0eeddee16f3102a2eeab5bb1b16/analysis/1466692832/
Ransomware epidemic - 2014-2016
- https://securelist.com/analysis/publications/75145/pc-ransomware-in-2014-2016/
June 22, 2016 - "… Main findings:
• The total number of users who encountered ransomware between April 2015 and March 2016 rose by 17.7% compared to the previous 12 months (April 2014 to March 2015) – from 1,967,784 to 2,315,931 users around the world;
• The proportion of users who encountered ransomware at least once out of the total number of users who encountered malware rose 0.7 percentage points, from 3.63% in 2014-2015 to 4.34% in 2015-2016;
• Among those who encountered ransomware, the proportion who encountered cryptors rose dramatically – up 25 percentage points, from 6.6% in 2014-2015 to 31.6% in 2015-2016;
• The number of users attacked with cryptors rose 5.5 times, from 131,111 in 2014-2015 to 718,536 in 2015-2016;
• The number of users attacked with Win-lockers decreased 13.03%, from 1,836,673 in 2014-2015 to 1,597,395 in 2015-2016…"
> https://noransom.kaspersky.com/
Piracy extortion SCAM emails
- https://torrentfreak.com/piracy-phishing-scam-targets-u-s-isps-subscribers-160624/
Jun 24, 2016 - "… TorrentFreak was alerted to a takedown notice Lionsgate purportedly sent to a Cox subscriber, for allegedly downloading a pirated copy of the movie Allegiant. Under threat of a lawsuit, the subscriber was asked to pay a $150 settlement fee. This request is unique as neither Lionsgate nor its tracking company IP-Echelon are known to engage in this practice. When we contacted IP-Echelon about Lionsgate’s supposed settlement offer, we heard to our surprise that these emails are part of a large phishing scam, which has at least one large ISPs fooled. 'The notices are fake and not sent by us. It’s a phishing scam', IP-Echelon informed TorrentFreak. For a phishing scam the -fake- DMCA notice does its job well. At first sight the email appears to be legit, and for Cox Communications it was real enough to forward it to their customers… In response, a Cox representative confirmed that the email is real and explained that it was forwarded by the network security team. Apparently, the -phishing-scam- was good enough to have the security experts fooled. TorrentFreak alerted Cox to the -fake- notices but at the time of writing we have yet to receive a response. Whether any other ISPs have fallen for the same scam is unknown at this point…"
Contained within the ZIP file is one of several different .js scripts. Trusted third-party analysis (you know who you are, thank you!) shows download locations at:
calcoastlogistics .com/09ujnb76v5?yNVICJbit=nFikKFve
labthanhthanhpg .com/09ujnb76v5?yNVICJbit=nFikKFve
patmagifts .asia/09ujnb76v5?yNVICJbit=nFikKFve
shadowbi .com/09ujnb76v5?yNVICJbit=nFikKFve
www .tmdmagento .com/09ujnb76v5?yNVICJbit=nFikKFve
Detection rates for the dropped binary are 5/54**. The malware phones home to the following IPs:
51.254.240.48 (Andrey Orlov aka Relink LLC, Russia / OVH, France)
217.12.223.88 (ITL, Ukraine)
195.123.209.227 (ITL, Latvia)
185.82.216.61 (ITL, Bulgaria)
Recommended blocklist: 51.254.240.48
217.12.223.88
195.123.209.227
185.82.216.61 "
** https://www.virustotal.com/en/file/3f5ff5d9d0615cc04e644297dcbfa999f6d6930850848f038464d0a486e6b8d0/analysis/
___
Fake 'Requested document' SPAM - leads to Locky
- http://blog.dynamoo.com/2016/06/malware-spam-requested-document.html
27 June 2016 - "This spam comes from various senders, and leads to Locky ransomware: From: Trudy Bonner
Date: 27 June 2016 at 15:39
Subject: Requested document
Dear [redacted],
The document you requested is attached.
Best regards
Trudy Bonner
Group Director of Strategy
Attached is a ZIP file containing elements of the recipients email address, the words "document", "doc" or "scanned" plus a random number. Contained within is a random .js script beginning with 'unpaid'. Trusted external analysis (thank you as ever) shows the scripts downloading… The malware phones home to the following hosts:
51.254.240.48 (Andrey Orlov aka Relink LLC, Russia / OVH, France)
109.234.35.71 (McHost.ru, Russia)
185.82.216.61 (ITL, Bulgaria)
185.146.169.16 (Pavel Poddubniy aka CloudPro, Russia)
[removed] (ITL, Latvia)
217.12.223.88 (ITL, Ukraine)
217.12.223.89 (ITL, Ukraine)
Lots of ITL recently… you might want to block /24s here instead of single IPs.
Recommended blocklist: 51.254.240.48
109.234.35.71
185.82.216.61
185.146.169.16
195.123.209.227
217.12.223.88
217.12.223.89 "
___
The link behind the activate line goes to http ://whatdoesmybusinessneed .com/wp-admin/hhaa.html and -redirects-
to another page on the same hacked site http ://whatdoesmybusinessneed .com/wp-admin/auth/b.htm
where they have a fairly good imitation of a genuine Barclays bank site asking for all the usual personal data, log ins and financial information."
Fake 'report' SPAM - malicious attachment
- http://blog.dynamoo.com/2016/06/malware-spam-report-ie-attached-report.html
28 June 2016 - "This spam has a weird problem with its apostrophe and comes with a malicious attachment: From: Kris Ruiz
Date: 28 June 2016 at 10:38
Subject: report
Hi info,
I致e attached the report you asked me to send.
Regards
Kris Ruiz
Head of Finance UKGI Planning
The details of the sender will vary from message to message. Attached is a ZIP file containing components of the recipient's email address and the words "report" and/or "pdf". Contained within is a malicious .js script file with a name starting with 'swift'. This analysis comes from a trusted third party (thank you again). The script downloads a file… The file is then decrypted (although I don't have a sample yet) and appears to be Locky ransomware. It phones home to the following servers:
109.234.35.71 (McHost.ru, Russia)
185.146.169.16 (Pavel Poddubniy aka Cloudpro LLC, Russia)
[removed] (FLP Kochenov Aleksej Vladislavovich aka uadomen.com, Ukraine)
[removed] (HostBar, Russia)
[removed] (Layer6 Networks, Latvia)
[removed] (ITL, Ukraine)
[removed] (ITL, Ukraine)
Recommended blocklist: 109.234.35.71
185.146.169.16
193.9.28.254
194.31.59.147
195.123.209.227
217.12.223.88
217.12.223.89 "
___
28 June 2016: New Xpress Money Certificate.zip: Extracts to: New Xpress Money Certificate.jar and a copy of the image in the email. Current Virus total detections 24/55*
This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/6fe3370b10d1e41c2fa22b9651604db4636fad9cb5029d3015b262bb973c29d2/analysis/1467110905/
.JAR File: "… runs -if- the [Java] JRE is installed on the computer.."
29 June 2016: PO_70386804.jar - Current Virus total detections 15/56*. Payload Security** shows a contact with a Russian IP number 185.17.1.82 which is fairly well known for malicious activity over the last few weeks although nothing appearing on VirusTotal, until today… This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/5dea187ee0102862c61808e31fc3ea604a6708270a433e08ee88c42f8493da4f/analysis/1467176037/
Fake 'Financial report' SPAM - malicious attachment
- http://blog.dynamoo.com/2016/06/malware-spam-financial-report-i-have.html
29 June 2016 - "This spam appears to come from various sources, but has a malicious attachment: From: Hester Stanley
Date: 29 June 2016 at 13:25
Subject: Financial report
Hello [redacted],
I have attached the financial report you requested.
Regards
Hester Stanley
Chief Executive Officer
Attached is a ZIP file containing some version of the recipient's email address, the words "report" or "freport" or "financial" plus a number. This contains a malicious .js file beginning with "swift". Trusted analysis by another party (thank you as ever) gives download locations… The payload is Locky ransomware, phoning home to the following servers:
93.170.123.219 (PE Gornostay Mikhailo Ivanovich aka time-host.net, Ukraine)
[removed] (EDIS, Germany)
[removed] (EDIS, Germany)
[removed] (EDIS, Germany)
[removed] (Hostbar, Russia)
I don't currently have a copy of the payload.
Recommended blocklist: 93.170.123.219
149.154.159.125
151.236.17.45
151.236.17.47
194.31.59.147 "
- https://myonlinesecurity.co.uk/continuing-with-locky-delivered-via-malspam/
29 June 2016 - "… continual Locky JavaScript downloaders… Today’s are no different so far coming in 2 batches. 1st about a financial report and the second with a totally blank body saying images, photos or pictures. The 1st ones contain a heavily obfuscated JavaScript inside the zip. It has several layers of obfuscation. The alleged senders name matches the name in the body of the email. The job title is also random and can be anything from Sales Director, Account Director or any other position that any company might think of… They all deliver Ransomware versions that encrypt your files and demand money…
29 June 2016: photo42744.zip: Extracts to: NIKON00061473034407.js - Current Virus total detections 10/54*
.. MALWR** shows a download from http ://www.cristaleriadominguez .com/8y7gvt65v?utajtJu=UwxvtvuRe which was -renamed- on download to spuMCzFlvvg.exe (VirusTotal 6/53***).
29 June 2016: rob_report_xls_227699.zip: Extracts to: swift 7c7.js - Current Virus total detections 2/54[4]
.. MALWR [5] shows a download from http ://www.oemsen.gmxhome .de/sh91u3a which gives an encrypted file that is detected as plain txt or data but gets -converted- by the javascript to ye6WVhz4F2H94WZX.exe (VirusTotal 5/56[6])… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/fbec22d0d98b4fb2013d445c450814c9a6773e163fe5c97d0ae9d72b7f65289f/analysis/1467205005/
Phish - via JavaScript Google
- https://myonlinesecurity.co.uk/phishing-via-javascript-google-this-time-not-paypal/
29 June 2016 - "… This one fulfils our worst fears and the entire -phish- is performed on a website that actually is the genuine Google log in page and really makes you believe that you are entering your Google credentials only on the genuine Google page, but in fact you are sending your details to the phisher whilst on the genuine Google site… shortly after publishing this post & reporting the http ://goo .gl/NL4EmV to Google, they -removed- that short URL redirect. However the nwfacilities page is still-active & live and it will be trivial for the phisher to create other short urls on Goo .gl and malspam them out… This is the Genuine Google page that you are on while your browser still has the http ://nwfacilities .top pages & JavaScript still loaded but -hidden- to view completely and performing all the nefarious actions and stealing your information. The only difference between you going to the Google log in page yourself & this one are the words data:text/html, at the start of the url
> https://myonlinesecurity.co.uk/wp-content/uploads/2016/06/google_phish_javascript-1024x791.png
This only appears to work in Google Chrome because Internet Explorer gives this message and doesn’t know what to do with data:text/html commands in the browser (thankfully). Firefox just gives a blank page until you use the view source option:
> https://myonlinesecurity.co.uk/wp-content/uploads/2016/06/IE_Google_phish.png "
Fake 'WeTransfer' SPAM - delivers Cerber ransomware
- https://myonlinesecurity.co.uk/wetransfer-random-name-at-your-own-domain-has-sent-you-a-file-malspam-delivers-cerber-ransomware/
30 June 2016 - "An email with the subject of 'name@ victim domain .tld' has sent you a file via 'WeTransfer' pretending to come from WeTransfer with a link to download a zip attachment which downloads Cerber Ransomware. Luckily Cerber doesn’t mass malspam in the same way that Locky does. These Cerber emails tend to be slightly more targeted (spear Phishing) at small business or organisations where IT might not be such a high priority or be so aware…
The link behind the download goes to
https ://www.cubbyusercontent .com/pl/Scanned+Documents.zip/_08fa4c28262f424b970037c786caf840 -not- to any WeTransfer page…
30 June 2016: Scanned Documents.zip: Extracts to: 3 identical copies of Scan001.js
Current Virus total detections 1/53*. MALWR** shows a download of Cerber Ransomware from
http ://69.24.80.121 /Styles/ie7/header.css which is -not- a css file but a -renamed- .exe file
(VirusTotal 4/53***).. This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/8bdfe41712f323f21ac518c9402db3fbf00f6c6855ad58fd15cd44b4c3781509/analysis/1467276692/
Phish - with Blurred Images
- https://isc.sans.edu/diary.html?storyid=21207
Last Updated: 2016-06-30 - "… seeing a lot of phishing emails that try to steal credentials from victims… this time, the scenario is quite different:
- The malicious email contains an HTML body with nice logos and texts pretending to be from a renowned company or service provider. There is a link that opens a page with a -fake- document but -blurred- with a popup login page on top of it. The victim is enticed to enter his/her credentials to read the document. I found samples for most of the well-known office documents. Here are some screenshots:
1] https://isc.sans.edu/diaryimages/images/isc_blurry1.png
4] https://isc.sans.edu/diaryimages/images/isc_blurry4.png
The strange fact is that it is -not- clear which credentials are targeted: Google, Microsoft or corporate accounts? The success of an efficient phishing is to take the victim by the hand and "force" him/her to -disclose- what we are expecting. So, nothing fancy behind this kind of phishing but it’s always interesting to perform further investigations and, for one of them, it was a good idea. Everybody makes mistakes and attackers too! The phishing page was hosted on a Brazilian website. Usually, such material is hosted on a -compromised- CMS like, not mentioning names but Wordpress, Joomla or Drupal. The Apache server had the feature 'directory indexing' enabled making all the files publicly available and, amongst the .php and .js files, a zip archive containing the "package" used by the attackers to build the phishing campaign. It was too tempting to have a look at it. The “blurred” effect was implemented in a very easy way: the -fake- document is a low-resolution screenshot displayed with a higher resolution. Like this:
> https://isc.sans.edu/diaryimages/images/blurred.jpg
… the presence of a JavaScript function to validate the victim’s email address but also to check the TLD. Is it a targeted attack? The presence of .mil, .edu or .gov is interesting while .com included all major -free- email providers… Then, an HTTP -redirect- is performed to a second page: "phone.html" which mimics a Google authentication page and asks for the user phone number. Here again, POST data are processed via "phone.php" which sends a second email with the victim's phone number. Emails are sent to two addresses (not disclosed here):
One @gmail .com account
One @inbox .ru account …"
AVOID and DELETE.
Fake 'Transactions' SPAM - Java adwind Trojans
- https://myonlinesecurity.co.uk/malspam-emails-with-java-adwind-trojans/
1 July 2016 - "We are seeing emails -daily- with a zip attachment containing java jar file which are variants of Java Adwind Trojan(1)… There are 2 different emails that arrived overnight both containing the same Java Adwind Trojan, although both having different subjects, senders and file names. For some reason the image that appears in the -body- of the email is also included in the zip files…
1) https://securelist.com/blog/research/73660/adwind-faq/
The Second email looks like: From: z.hraahleh@ shift-sg .com
Date: Fri 01/07/2016 02:44
Subject: Transactions for Amendment
Attachment: PENDING REMITTANCE RECIEPTS FOR APPROVAL.zip extracts to PENDING REMITTANCE RECIEPTS FOR APPROVAL..jar
kindly find attached listed trasactions for amendment,please do the corrections and send back to us. thanks
1 July 2016: Confirm Transactions.zip: Extracts to: Transactions on Hold.Reason because beneficiary last name is wrong..jar
Current Virus total detections 15/56*. MALWR** shows the usual masses of files created/dropped and entries created on the computer. This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/9d84124240032c60948c7df4cffa9c85f8609cf262bc7b94d6f186ed8f43f35f/analysis/1467206759/
Fake 'RE: info' SPAM - Cerber Ransomware
- https://myonlinesecurity.co.uk/blank-malspam-email-with-jse-attachment-downloading-unknown-malware/
2 July 2016 - "A blank email with the subject of 'RE: info' pretending to come from asisianu@ pauleycreative .co.uk with a zip attachment with a jse file… Update: I am assured that it definitely is Cerber Ransomware… One of the emails looks like: From: asisianu@ pauleycreative .co.uk
Date: Sat 02/07/2016 19:40
Subject: RE: info
Attachment: info_1218307442.zip
Body content: Totally blank/empty
2 July 2016: info_1218307442.zip: Extracts to: 5.jse - Current Virus total detections 2/55*
.. PayLoad Security** | MALWR*** shows a download from
http ://adiidiam .top/admin.php?f=1.jpg (which is -not- a jpg but a .exe file)
(VirusTotal 1/56[4]) (MALWR[5]) (Payload Security[6])… This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/a259fb8946b843227ead174be057d2711642726ee6ef5bfb68c4773c5973d177/analysis/1467464033/
Fake 'Scanned image' SPAM - delivers Locky
- https://myonlinesecurity.co.uk/scanned-image-pretending-to-come-from-your-own-email-domain-delivers-locky-2/
4 July 2016 - "An email with the subject of 'Scanned image' pretending to come from random names at your own email domain or company with a malicious word doc macro attachmentdelivers Locky Ransomware… The email looks like: From: Random names at your own email domain
Date: Mon 04/07/2016 11:33
Subject: Scanned image
Attachment: 04-07-2016_rndnum(4,9)}}.docm
Image data has been attached to this email.
4 July 2016: 04-07-2016_rndnum(4,9)}}.docm - Current Virus total detections 6/54*
.. MALWR** shows a download from http ://clear-sky .tk/nb4vervge which is Locky Ransomware although not showing in the sandbox analysis. This means that once again the Locky gang have upped the stakes and changed their anti-analysis/ anti-sandbox protections to make it more difficult to detect and protect against (VirusTotal 3/53***).. DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/9b194174fcf4cde35aa6315c7723898602a82e4a114b5e39459b16027aa01eaf/analysis/1467628388/
Fake 'Rechnung' SPAM - downloads Locky
- https://myonlinesecurity.co.uk/rechnung-2016-93910-mpsmobile-gmbh-malspam-delivers-locky-ransomware/
5 July 2016 - "An email partly in German and partly in English pretending to be a-mobile-phone-bill with the subject of 'Rechnung 2016-93910' [random numbered] pretending to come from mpsmobile GmbH with a zip attachment which downloads Locky ransomware… One of the emails looks like: From: mpsmobile GmbH
Date: Tue 05/07/2016 10:45
Subject: Rechnung 2016-93910
Attachment: 52751_Rechnung_2016-93910_20160705.zip
Sehr geehrte Damen und Herren, anbei erhalten Sie das Dokument ‘Rechnung 2016-93910′ im PDF-Format. Um es betrachten und ausdrucken zu können, ist der PDF Reader erforderlich. Diesen können Sie sich kostenlos in der aktuellen Version aus dem Internet installieren. Mit freundlichen Grüssen mpsmobile Team …
Dear Ladies and Gentlemen, please find attached document ”Rechnung 2016-93910’ im PDF-Format. To view and print these forms, you need the PDF Reader, which can be downloaded on the Internet free of charge. Best regards mpsmobile GmbH …
5 July 2016: 52751_Rechnung_2016-93910_20160705.zip: Extracts to: 63227_2016-53001_20160705.js
Current Virus total detections 23/56*. Payload Security** | MALWR*** was unable to find anything but manual analysis shows a download from http ://brewinbooks .com/98uhnvcx4x (VirusTotal 3/53[4]) which looks like Locky Ransomware but MALWR[5] doesn’t show any activity which is probably due to anti-sandbox protection in the file. Other download locations so far found include:
http ://brazilmart .com/98uhnvcx4x
http ://brewinbooks .com/98uhnvcx4x
http ://thecorporate .gift/98uhnvcx4x
http ://lojaeberlin .com/98uhnvcx4x
http ://topbag .com.au/98uhnvcx4x
http ://hangusaxachtay .com/98uhnvcx4x
http ://flyingcarts .com/98uhnvcx4x
http ://imbagscanta .com/98uhnvcx4x
http ://foxprint .ro/98uhnvcx4x
This is another one of the files that unless you have “show known file extensions enabled“, can easily be mistaken for a genuine DOC/PDF/JPG or other common file instead of the .EXE/.JS file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/15c7846d81bfb2b62431d57ee39e12e0cc30ba907d7281a162181c8b430078d1/analysis/1441173827/
Fake 'Scanned image' SPAM - leads to Locky
- http://blog.dynamoo.com/2016/07/malware-spam-scanned-image-leads-to.html
5 July 2016 - "This -fake- document scan appears to come from within the victim's own domain but has a malicious attachment. From: administrator8991@ victimdomain .com
Date: 5 July 2016 at 12:47
Subject: Scanned image
Image data has been attached to this email.
Possibly due to an error in setting up the spam run, there is an attachment named 05-07-2016_rndnum(4,9)}}.docm which contains a malicious macro. We haven't seen much in the way of Word-based malware recently. The two samples I received have VirusTotal detection rates of 5/52* and 6/52**. The Malwr analysis for those samples [1] [2] shows the macro downloading a binary from:
leafyrushy .com/98uhnvcx4x
sgi-shipping .com/98uhnvcx4x
There will be a lot more locations too. This drops a binary with a detection rate of 5/55[3] which appears to be Locky ransomware. Hybrid Analysis[4] shows it phoning home to:
185.106.122.38 (Host Sailor, Romania / UAE)
185.106.122.46 (Host Sailor, Romania / UAE)
185.129.148.6 (MWTV, Latvia)
Host Sailor is a notoriously Black Hat web host, MWTV has is problems too. The payload appears to be Locky ransomware.
Recommended blocklist: 185.106.122.0/24
185.129.148.0/24 "
* https://virustotal.com/en/file/26202e93dc56ac9b3d76cc68c787ad70099aa1ee6b5610277feed23501d8f5ee/analysis/1467721871/
Fake 'Quick cash' fraud SCAM/PHISH
- https://myonlinesecurity.co.uk/fake-invoices-quick-cash-systems-binary-options-fraud-scams/
5 July 2016 - "… Instead of the usual spam emails, we are seeing loads of -fake- invoices, all with links to various companies that pass through or redirect the user to
http ://www.quickcashsystem .biz/?offerID=1062&p=10274a38b6a0b47645075132d8d48c (They are probably affiliate references so the scummy scammers can pay the evil fraudsters who send victims to them). The reference number is different, depending on the “victim’s IP number”. I visited via different proxies and got a different reference number each visit… This all starts off with an email like one of these:
This first one pretends to be an Account Balance Warning from an unnamed bank. All the links go to
http ://beckham7 .com/lists/link.php?M=28914&N=33&L=18&F=H where you are -redirected- (eventually) to
http ://www.quickcashsystem .biz/?offerID=1062&p=102798821e1ff5eaafa8251b9ba26e where a video immediately starts playing offering you, showing you a big mansion, expensive cars and the chance to make $$$$$.
This one pretends to be an electronics invoice and at a first quick glance, you could quite easily mistake it for an Ebay invoice and follow the links to see what on earth has happened, because you don’t remember ordering anything. This one leads to http ://a2cd .com/lists/link.php?M=29114&N=33&L=18&F=H which -redirects- to
http ://www.quickcashsystem .biz/?offerID=1062&p=102798821e1ff5eaafa8251b9ba26e :
> https://myonlinesecurity.co.uk/wp-content/uploads/2016/07/fake_invoice_a2cd-1-1024x608.png
This 3rd example is so generic that almost anyone receiving it would click through to see what or how this mistake could have been made. This goes to
http ://steps123 .com/lists/link.php?M=29215&N=41&L=20&F=H and -redirects- to
http ://www.quickcashsystem .biz/?offerID=1062&p=102798821e1ff5eaafa8251b9ba26e :
> https://myonlinesecurity.co.uk/wp-content/uploads/2016/07/fake_invoice_steps123-1024x580.png
You eventually end up on this page, whichever link you follow to start with:
> https://myonlinesecurity.co.uk/wp-content/uploads/2016/07/quick_cash-1024x644.png
If you look at the small print at the very bottom of the page, you just see in very light type a link to disclaimer and privacy:
> https://myonlinesecurity.co.uk/wp-content/uploads/2016/07/QC_disclaimer_link.png
Following the disclaimer link, you get a page that does warn you “The www .quickcashsystem .biz sales video is fictitious and was produced to portray the potential of the www .quickcashsystem .biz 3rd party signals software. Actors have been used to present this opportunity and it should be viewed for entertainment purposes. We do not guarantee income or success, and example results in the video and anywhere else on this website do not represent an indication of future success or earnings.”
Fake 'random hex numbers' SPAM - Locky ransomware
- http://blog.dynamoo.com/2016/07/malware-spam-with-random-hexadecimal.html
6 July 2016 - "I only have a couple of samples of this very minimalist spam, consisting of just a "Subject" with a random hex number (e.g. 90027696CCCC611D) and a matching .DOCM attachment (e.g. 90027696CCCC611D.docm).
My trusted analysis source (thank you) says that these DOCM files contain a macro (no surprises there) that downloads a binary from the following locations:
blingberry24 .com/90ujn3b8c3
danseduchat .com/90ujn3b8c3
harveyventuresltd .com/90ujn3b8c3
noveltybella .com/90ujn3b8c3
www .proxiassistant-ao .com/90ujn3b8c3
www .sacandolalengua .com/90ujn3b8c3 The payload is Locky ransomware with a detection rate of 3/52*. The same source says that C2 locations are:
89.108.84.42 (Agava JSC, Russia)
148.163.73.29 (GreencloudVPS JSC, Vietnam)
Agava in particular is a regular source of badness, and I would suggest that you consider blocking the entire 89.108.80.0/20 range, or at least this minimum recommended blocklist: 89.108.84.42
148.163.73.29 "
* https://www.virustotal.com/en/file/62224461417f991f95d5ea08ebb19e15434cf0c3d28ae15450c1e4910ea3a2b6/analysis/
___
CryptXXX ransomware updated
- https://isc.sans.edu/diary.html?storyid=21229
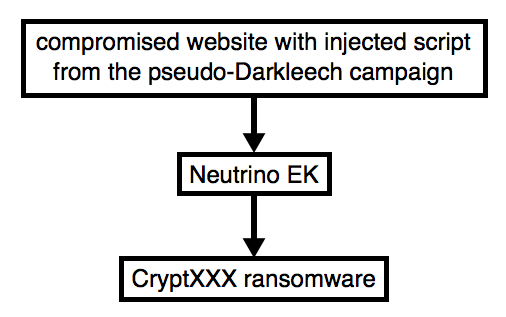
2016-07-06 - "When generating exploit kit (EK) traffic earlier today, I noticed a change in post-infection activity on a Windows host infected with CryptXXX ransomware. This happened after an infection caused by Neutrino EK triggered from the pseudoDarkleech campaign: Flow chart for Neutrino EK/CryptXXX caused by pseudoDarkleech
> https://isc.sans.edu/diaryimages/images/2016-07-06-ISC-diary-image-01.jpg
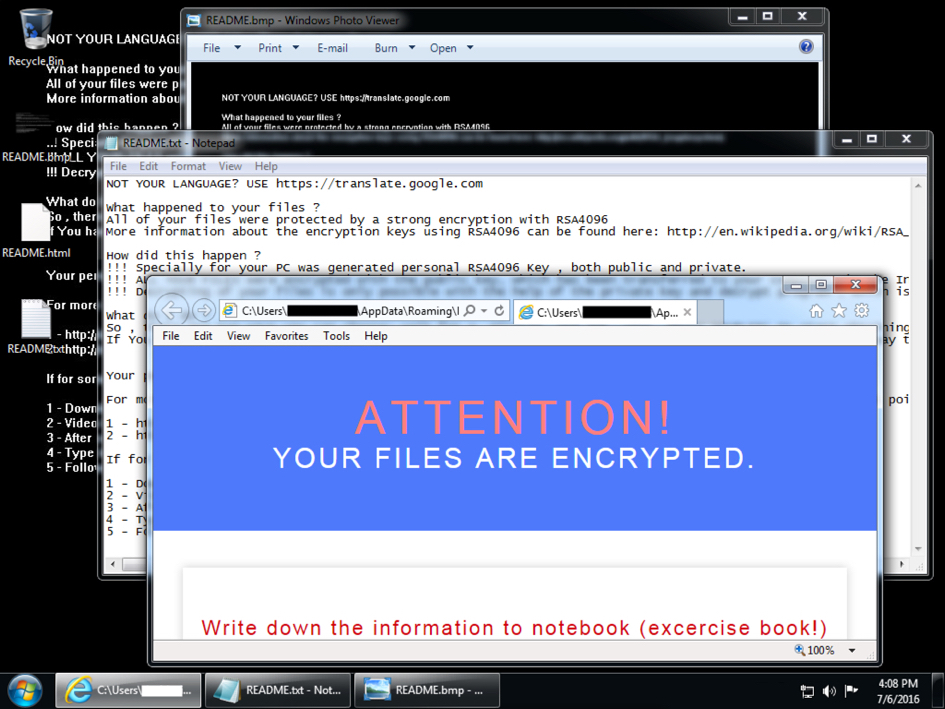
This morning, the decryption instructions for CryptXXX ransomware looked different. A closer examination indicates CryptXXX has been updated. As I write this, I haven't found anything online yet describing these recent changes, so this diary takes a quick look at the traffic: An infected Windows desktop from earlier today
> https://isc.sans.edu/diaryimages/images/2016-07-06-ISC-diary-image-02a.jpg
Details: Today's EK traffic was on 198.71.54.211 using the same domain shadowing technique we've seen before from various campaigns using Neutrino EK… Post-infection traffic was over91.220.131.147 on TCP port 443 using custom encoding, a method CryptXXX has used since it first appeared earlier this year…" (More detail at the isc URL above.)