Attackers are turning -MySQL- servers into DDoS bots
- http://net-security.org/malware_news.php?id=3134
28.10.2015 - "Someone has been compromising MySQL servers around the world and using them to mount DDoS attacks. The latest targets of these attacks are an (unnamed) US hosting provider and a Chinese IP address. Most of the servers affected in this campaign are located in India, China, Brazil and the Netherlands, but others can be found around the globe:
> http://www.net-security.org/images/articles/pie-28102015.jpg
"We believe that the attackers compromised MySQL servers to take advantage of their large bandwidth. With these resources, the attackers could launch bigger DDoS campaigns than if they used traditional consumer targets," Symantec researchers explained*. "MySQL is also the second most popular database management system in the world, giving the attackers a wide range of potential targets." The researchers didn't say how many servers in total were compromised. The attackers used a variant of the Chickdos Trojan to make the servers listen to their commands. The variant is very similar to the initial Chickdos Trojan first spotted by cyber defenders in December 2013. The attackers perform an SQL injection attack in order to install a malicious user-defined function (UDF) on the target server, which is then loaded into MySQL and executed… The researchers advised admins -never- to run SQL servers with administrator privileges (if possible), and to regularly patch apps** that use them…"
* http://www.symantec.com/connect/app#!/blogs/mysql-servers-hijacked-malware-perform-ddos-attacks
28 Oct 2015 - "… identified active command-and-control (C&C) servers for Chikdos are as follows:
•183.60.202.16: 10888
•61.160.247.7: 10991
•103.17.118.124: 10991 …"
- http://blog.dynamoo.com/2015/10/this-fake-order-spam-does-not-come-from.html
28 Oct 2015 - "This -fake- order spam does not come from IKEA but is instead a simple -forgery- with a malicious attachment. From: DoNotReply@ ikea .com
Date: 28 October 2015 at 08:57
Subject: Thank you for your order
Order acknowledgement:
To print, right click and select print or use keys Ctrl and P.
Thank you for ordering with IKEA Shop Online. Your order is now being processed. Please check your order and contact us as soon as possible if any details are incorrect. IKEA Customer Relations, Kingston Park, Fletton, Peterborough, PE2 9ET. Tel: 0203 645 0015 …
Attached is a file IKEA receipt 607656390.doc which contains this malicious macro and which has a VirusTotal detection rate of 4/55*…
UPDATE 1: The reverse .it analysis** of the first sample shows a download from:
alvarezsantos .com/4f67g7/d6f7g8.exe
This dropped binary has a detection rate of just 2/55*. Two further samples have now been seen (VT results [1] [2]) and according to the analysis of one them, it downloads from:
experassistance .fr/4f67g7/d6f7g8.exe
… Two further samples have now been seen (VT results [1] [2]) and according to the analysis[3] of one them, it downloads from:
experassistance.fr/4f67g7/d6f7g8.exe
… UPDATE 2: A further reverse .it analysis[4] shows another download location of:
www .retrogame .de/4f67g7/d6f7g8.exe …"
- http://blog.dynamoo.com/2015/10/malware-spam-efax-message-from.html
28 Oct 2015 - "This fake fax spam comes with a malicious attachment: From: eFax [message@ inbound .efax .com]
Date: 28 October 2015 at 10:08
Subject: eFax message from "Booking.com - HylaFa" - 1 page(s), Caller-ID: 031207944200
Fax Message [Caller-ID: 031207944200]
You have received a 1 page fax at 2015-10-28 08:57:17 GMT.
* The reference number for this fax is lon1_did14-1445421403-1407880525-89.
View this fax using your Microsoft Word…
Fake 'ADP' SPAM - PDF malware
- http://myonlinesecurity.co.uk/adp-payroll-invoice-with-a-password-protected-zip-attachment-fake-pdf-malware/
28 Oct 2015 - "An email with the subject of 'ADP Payroll Invoice' pretending to come from ADPClientServices@ adp .com with a password protected zip attachment is another one from the current bot runs… The content of the email says : Your ADP Payroll invoice is attached for your review. If you have any questions regarding this invoice, please contact your ADP service team at the number provided on the invoice for assistance.
Important: Please open the attached file using your temporary password. Your temporary password is: 941VAX332ED
Please note that your bank account will be debited within one banking business day for the amount(s) shown on the invoice.
Thank you for choosing ADP Payroll.
Please do not respond to this message. It comes from an unattended mailbox.
28 October 2015: invoice381624185029.zip: Extracts to: invoice381624185029.exe
Current Virus total detections 3/55* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/895e23a7f5094fbab7b1392c56c4e3d50154c6d141d26a3933c3a09e47fe33bc/analysis/1446048560/
___
Fake 'résumé' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/10/malware-spam-id9828myresume.html
27 Oct 2015 - "This fake résumé spam comes with a malicious attachment. It seems that the names are randomly-generated from a list. From: Trinh [zhanxing1497kcuo@ 163 .com]
Date: 27 October 2015 at 18:30
Subject: id:9828_My_Resume
Signed by: 163 .com
Good afternoon!!! my name is Bobette Gloster. my resume is doc file.
I would appreciate your immediate attention to this matter.
Yours faithfully
Bobette Gloster
Fake 'Doc Scan' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/10/malware-spam-documents-for-review-and.html
29 Oct 2015 - "This -fake- document scan email has a malicious attachment: From: Sarah [johnson@ jbrakes .com]
Date: 29 October 2015 at 08:27
Subject: Documents for Review and Comments
Hi Morning,
Attached are the return documents.
Call me if you need anything.
See you soon.
Sarah
The attached file is SCANNED DOCS,jpg.z which is a type of compressed file. If you have the right file decompression software, it will extact a malicious executable SCANNED DOCS,jpg.exe which has a VirusTotal detection rate of 17/55*. According to various automated analysis tools [1] [2] [3] it drops a file %TEMP%\XP000.TMP\M.exe which itself has a detection rate of 19/54**. Out of all the standard analysis tools I have used, only Comodo CAMAS identified the network traffic, a POST to:
eyeseen .net/swift/gate.php
This is hosted on a SoftLayer IP of [removed] in Singapore. A quick look at VirusTotal*** indicates a lot of badness on this IP address, so it is probably one worth blocking. The payload is Pony / Fareit, which is basically a password stealer."
* https://www.virustotal.com/en/file/9fd03451e18b8c33caca6d89aee260886e2b6a2e77f2d6af9d6981389e7822e3/analysis/1446107638/
Fake 'eBay Invoice' SPAM – PDF malware
- http://myonlinesecurity.co.uk/your-ebay-invoice-is-ready-fake-pdf-malware-2/
29 Oct 2015 - "An email with the subject of 'Your eBay Invoice is Ready' pretending to come from eBay with a zip attachment is another one from the current bot runs… The content of the email says : PLEASE DO NOT RESPOND – Emails to this address are not monitored or responded to.
Dear Customer,
Please open the attached file to view invoice.
If the attachment is in PDF format you may need Adobe Acrobat Reader to read or download this attachment. If you require Adobe Acrobat Reader this is available at no cost…
This email has been scanned by the Symantec Email Security.cloud service.
This email and any attachment are intended solely for the addressee, are strictly confidential and may be legally privileged. If you are not the intended recipient any reading, dissemination, copying or any other use or reliance is prohibited. If you have received this email in error please notify the sender immediately by email and then permanently delete the email.
29 October 2015: ebay_591278156712819_291015.zip: Extracts to: ebay_591278156712819_291015.exe
Current Virus total detections 1/55* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/311132c9f241d4f0be5982e1680751d3051b38291d0aaf2821e27520de356773/analysis/1446114782/
___
Fake 'Your Invoice' SPAM - doc malware
- http://myonlinesecurity.co.uk/heather-crawford-barclaycomms-com-your-invoice-i0000040777-word-doc-malware/
29 Oct 2015 - "An email with the subject of 'Your Invoice I0000040777' pretending to come from Heather Crawford with a malicious word doc attachment is another one from the current bot runs… The email looks like: Dear Customer. Please find attached your Invoice. Invoice Number: 0000040777 Invoice Date: 28/10/2015 Invoice Total: 78.40 Invoice Description: Barclay Fresh Direct Debit 1 V (x1.00000)
This e-mail, and any attachment, is confidential. If you have received it in error, please delete it from your system, do not use or disclose the information in any way, and notify me immediately. The contents of this message may contain personal views which are not the views of Barclay Communications, unless specifically stated.
29 October 2015: I0000040777.doc - Current Virus total detections 3/55*
… Downloads Dridex banking malware from
0319225577 .com/46435/087965.exe (VirusTotal 0/55**)… DO NOT follow the advice they give to enable macros or enable editing to see the content. Most of these malicious word documents appear to be blank or look something like these images when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21-1024x412.png
… Many versions pretend to have a digital RSA key and say you need to enable editing and Macros to see the content. Do NOT enable Macros… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/a793aef1bbcdef406c90a4166cc5a42032c703aaf485b00027c24a63dee602af/analysis/1446115712/
29 October 2015: label_737929223.doc - Current Virus total detections 2/55* . Analysis via Payload Security hybrid analysis** tells me that it downloads writeonlabels .biz/media/system/m.exe
(VirusTotal 0/55***) and posts some information to dethetear .ru/sliva/gate.php. This looks a bit like the behaviour of the new Shifu banking malware which combines the worse elements of Dridex, Zeus, Pony and all the other information stealers… DO NOT follow the advice they give to enable macros or enable editing to see the content. Most of these malicious word documents appear to be blank or look something like these images when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21-1024x412.png
… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/4be1077cdd7e821b3999b9c24c1e9070eadf87163ee27773e61197b68e21edda/analysis/1446133593/
Fake 'Domain Suspension Notice' SPAM - Cryptowall ransomware payload
- http://blog.dynamoo.com/2015/10/malware-spam-domain-domain-suspension.html
29 Oct 2015 - "There appear to be many versions of this spam, aimed at domain owners and apparently coming from the actual registrar of the domain. For added authenticity, the owner's name is included in the spam… From: ENOM, INC. [abuse@ enom.com .org]
Date: 30 October 2015 at 04:11
Subject: Domain … Suspension Notice
Dear Sir/Madam,
The following domain names have been suspended for violation of the ENOM, INC. Abuse Policy …
Click here and download a copy of complaints we have received…
… clicking on the link goes to edecisions .com/abuse_report.php?LAPTOP-MEMORY.COM and downloads a file LAPTOP-MEMORY.COM_copy_of_complaints.pdf.scr - it looks more authentic because the domain name is in the file download, but in fact you can specify -any- domain name and it gives a matching file. Before we look at the analysis of the downloaded executable, let's look at the domain name edecisions .com. It looks like the sort of domain that might contain abuse reports, but in fact it is a -hijacked- GoDaddy domain hosted on 65.78.174.100 and a quick look at VirusTotal* indicates that one of the other 4 sites on the same server was also -compromised- and was serving up malware in 2013. This is definitely a good candidate to block… several compromised domains on the same server, indicating that the entire box has been popped…"
* https://www.virustotal.com/en/ip-address/65.78.174.100/information/
… UPDATE: The payload appears to be the Cryptowall ransomware." (More detail and IP's to block at the dynamoo URL above.)
>> http://support.melbourneit.com.au/articles/help/Spam-Alert-27th-October-2015
27 Oct 2015 - "… advise that any customer that receives the email is to -delete- it immediately. If you are unsure of the validity of your emails please check the email headers to determine the source and return path for the email address…"
Fake 'Purchase Order' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/11/malware-spam-purchase-order-37087-por.html
2 Nov 2015 - "This -fake- financial spam does not come from K. Stevens (Leicester) Ltd but is instead a simple -forgery- with a malicious attachment. From Margaret Wimperis [MargaretWimperis@ biasbinding .com]
Date Mon, 02 Nov 2015 18:28:23 +0700
Subject Purchase Order 37087-POR
Hi
Please confirm receipt of order
Kind regards
Margaret
K. Stevens (Leicester) Ltd. Portishead Road, Leicester LE5 0JL Reg. No. 3125088
This email and any attachments are believed to be virus free, however
recipients are responsible for appropriate virus checks. The email and
attachments are confidential to the addressee and unauthorised use, copying or
retention by others is prohibited…
Attached is a file PORDER.DOC which comes in three different versions (although I only have two samples [1] [2]) containing a malicious macro… which download a binary from the following locations:
saltup .com/34g3f3g/68k7jh65g.exe
landprosystems .com/34g3f3g/68k7jh65g.exe
jambidaily .com/34g3f3g/68k7jh65g.exe
This binary has a detection rate of 4/55* and according that that VirusTotal report, this reverse.it report** this Malwr report*** it contacts the following IP: 128.199.122.196 (DigitalOcean, Singapore)
I strongly recommend that you -block- that IP. The payload is likely to be the Dridex banking trojan…"
1] https://www.virustotal.com/en/file/b3c483e304a52e2e5724e7b637146da62d285a37736461d4280366c98ee74125/analysis/1446464337/
Fake 'American Airlines' SPAM - doc malware
- http://myonlinesecurity.co.uk/american-airlines-e-ticket-confirmation-word-doc-malware/
2 Nov 2015 - "An email appearing to be an American Airlines E-Ticket with the subject of 'E-Ticket Confirmation' pretending to come from American Airlines@ aa .com with a malicious word doc or Excel XLS spreadsheet attachment is another one from the current bot runs…
2 November 2015 : ticket_AA77799543.doc - Current Virus total detections 4/55*
… Contains an embedded ole object that drops a pony malware pu .exe (VirusTotal 2/55**), posts -stolen- information to
- http ://wicytergo .ru/sliva/gate.php
- http ://unlaccothe .ru/sliva/gate.php
- http ://thetedrenre .ru/sliva/gate.php
… Which in turn downloads Dyreza banking malware from one of these 3 sites:
- http ://eextensions .co/m.exe
- http ://www.10203040 .at/m.exe
- http ://www.eshtari .me/m.exe (VirusTotal 2/55***)
… DO NOT follow the advice they give to enable macros or enable editing to see the content. Most of these malicious word documents appear to be blank or look something like these images when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21-1024x412.png
… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/7e28f1b5f5738a3ce1e38dc80a169cf0850b5f22015bd9555f7ad1d48b9f7b47/analysis/1446486517/
Fake 'Delivery Confirmation' SPAM - doc malware
- http://myonlinesecurity.co.uk/delivery-confirmation-0068352929-acuvue-com-word-doc-malware/
3 Nov 2015 - "An email with the subject of 'Delivery Confirmation: 0068352929' pretending to come from ACUVUE_DEL with a malicious word doc or Excel XLS spreadsheet attachment is another one from the current bot runs… The email looks like: PLEASE DO NOT REPLY TO THIS E-MAIL. IT IS A SYSTEM GENERATED MESSAGE.
Attached is a pdf file containing items that have shipped
Please contact us if there are any questions or further assistance we can provide
Fake 'New Invoice' SPAM - PDF malware
- http://myonlinesecurity.co.uk/new-invoice-from-documents-online-fake-pdf-malware/
3 Nov 2015 - "An email with the subject of 'New Invoice from Documents Online' pretending to come from Documents Online Limited with a zip attachment is another one from the current bot runs… The content of the email says : Dear Customer,
This is a notice that an invoice has been generated against your account, details of the invoice are as follows:
Invoice #241
Amount Due: 90.00GBP
Due Date: 01/12/2015
Payment Method: Bank Transfer
Invoice Items
… 75.00GBP
Sub Total: 75.00GBP
20.00% UK VAT: 15.00GBP
Credit: 0.00GBP
Total: 90.00GBP
Please find attached a copy of this invoice in PDF format for your records.
IMPORTANT: Please open the attached file using your temporary password. Your temporary password is: UCZ941QXO941 …
3 November 2015: Invoice-241.zip: Extracts to: Invoice-241.exe
Current Virus total detections 0/53* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/d0da209f011c514c1b15e8ccca3f94618d279439a28394067b6579d171e515c3/analysis/1446550339/
Angler -and- Nuclear EK's integrate Pawn Storm Flash Exploit
- http://blog.trendmicro.com/trendlabs-security-intelligence/angler-and-nuclear-exploit-kits-integrate-pawn-storm-flash-exploit/
Nov 3, 2015 - "… We found -two- vulnerabilities that were now being targeted by exploit kits, with one being the recent Pawn Storm Flash zero-day. Starting on October 28, we found that these two vulnerabilities were being targeted by the Angler and Nuclear exploit kits. (The second vulnerability was a Flash vulnerability that worked on versions up to 18.0.0.232; we are currently working with Adobe to confirm the CVE number for this exploit)… Our latest research confirms that the two exploit kits abusing the Diffie-Hellman key exchange, with some minor differences from the previous usage. This is being done to hide their network traffic and to get around certain security products. The changes are an attempt to make analysis of their key exchange by researchers more difficult. The Angler EK has made the following changes to its usage of the Diffie-Hellman protocol. They add some obfuscation to what had previously been a relatively clear and obvious process… activity for the Angler exploit kit was higher in the earlier weeks of October; perhaps the addition of these vulnerabilities is an attempt to raise the traffic levels of the exploit back to the earlier levels. Users in Japan, the United States, and Australia were the most affected…"
Current Flash version - 19,0,0,226
Test here: https://www.adobe.com/software/flash/about/
Fake 'Transport' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/11/malware-spam-email-from-transport-for.html
4 Nov 2015 - "This -fake- Transport for London spam is a variation of something used before. It does not actually come from TfL, but is a simple -forgery- with a malicious attachment: From "Transport for London" [noresponse@ cclondon .com]
Date Wed, 4 Nov 2015 14:33:44 +0100
Subject Email from Transport for London
Dear Customer
Please open the attached file to view correspondence from Transport for London.
If the attachment is in PDF format you may need Adobe Acrobat Reader to read or download
this attachment…
Thank you for contacting Transport for London.
Business Operations
Customer Service Representative …
This email has been scanned by the Symantec Email Security.cloud service…
Attached is a file 6305093.zip of which I have seen just one sample, containing a malicious executable 6305093.scr (MD5 6a4cce90ba28720fa9e6813f681b1f75) which has a VirusTotal detection rate of 7/54*. This Hybrid Analysis report** shows it communicating with the well-known malicious IP address of 197.149.90.166 (Cobranet, Nigeria) which I recommend you block. The payload here seems to be Upatre dropping the Dyre banking trojan."
* https://www.virustotal.com/en/file/2e82c5534c04bcf50c9afb9dd5e28bba23c418fbfa0ffed19645a30de56b25aa/analysis/1446645968/
Fake 'Document from AL-KO' SPAM - doc malware
- http://myonlinesecurity.co.uk/document-from-al-ko-word-doc-malware/
5 Nov 2015 - "An email with the subject of 'Document from AL-KO' pretending to come from info@ alko .co.uk with a malicious word doc attachment is another one from the current bot runs… The email looks like: This document is DOC created by Osiris OSFAX(R) V3.5.
It can be viewed and printed with Microsoft Word(R)
5 November 2015: Document from AL-KO.doc - Current Virus total detections 0/54*.
… Downloads Dridex banking malware from:
www .mazzoni-hardware .de/f75f9juu/009u98j9.exe
deklompjes .nl/~maurice/f75f9juu/009u98j9.exe
members.dodo .com.au/~mfranklin17/f75f9juu/009u98j9.exe
www .www .www.enhancedpixel .com/f75f9juu/009u98j9.exe (VirusTotal 3/54**)
… DO NOT follow the advice they give to enable macros or enable editing to see the content. Most of these malicious word documents appear to be blank or look something like these images when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21-1024x412.png
… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/134f4cd2f17b312083bee6fb6d502dd0dd3b70f5716b8d17aae8acdcbad0e610/analysis/1446722835/
Fake 'Billing' SPAM – PDF malware
- http://myonlinesecurity.co.uk/monthly-billing-920493380924127516-e-online-data-amerikicks-fake-pdf-malware/
5 Nov 2015 - "An email with the subject of 'Monthly Billing 920493380924127516 – e-Online Data – amerikicks' coming from random companies, email addresses and names with a zip attachment is another one from the current bot runs… The content of the email says : Amerikick Studios
Invoice #: 920493380924127516
Please use the HelpDesk for all problems/questions/suggestions. It is located at the bottom of the admin pages.
A full report in the attachment.
Billing for Nov 2015
This is your Payment Gateway monthly invoice…
5 November 2015: Final overdue bill order document.zip: Extracts to: 745348208.exe
Current Virus total detections 1/55* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/2ba09e25d6d9f0b9a5f0db14a6eb6e792270a2ec71e4d377f3a761055b726560/analysis/1446738837/
___
Fake 'subpoena' attachment SPAM - doc malware
- http://myonlinesecurity.co.uk/i-got-this-subpoena-in-my-mail-box-today-doug-little-cardataconsultants-com-word-doc-malware/
5 Nov 2015 - "An email saying 'I got this subpoena in my mail box today' with the subject of 'sued used' pretending to come from dlittle@ cardataconsultants .com with a malicious word doc or Excel XLS spreadsheet attachment is another one from the current bot runs… Nobody is being sued. Nobody is actually sending a subpoena to you by email. The email looks like: I got this subpoena in my mail box today, saying that I have been sued by you.
I am sorry but I don’t even know what this is.
I am attaching a scanned copy , please let me know what this is about
Doug Little
Special Services Co-ordinator
CarDATA Consultants
Phone [removed] …
5 November 2015 : subpoena.doc - Current Virus total detections 2/54*
This malicious word doc has -2- copies of a RTF file embedded inside it (MALWR**) that when extracted deliver an embedded fareit password stealing malware pm3.exe (VirusTotal 2/55***) that posts information to http ://littonredse .ru/gate.php
These malicious word docs normally also drop an Upatre downloader that in turn downloads a Dyreza banking malware… the macro inside the word doc seems to indicate that it should…
Update: somewhere along the line it also downloads:
- http ://s.teamzerostudio .com/x1.exe (VirusTotal[4])…
… DO NOT follow the advice they give to enable macros or enable editing to see the content. Most of these malicious word documents appear to be blank or look something like these images when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21-1024x412.png
… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/15db7d387b7e6dcbb7ea6a502526c7103329fab1cd4e05db406cd93efe55fff6/analysis/
PayPal Spam
- http://threattrack.tumblr.com/post/132616332398/paypal-spam
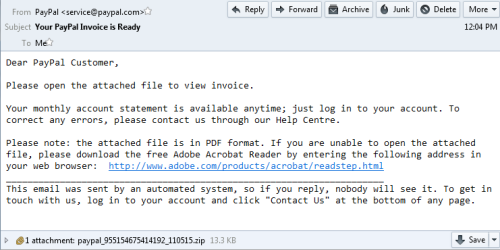
Nov 5, 2015 - "Subjects Seen: Your PayPal Invoice is Ready
Typical e-mail details: Dear PayPal Customer,
Please open the attached file to view invoice.
Your monthly account statement is available anytime; just log in to your account. To correct any errors, please contact us through our Help Centre.
Malicious File Name and MD5:
paypal_955154675414192_110515.exe (2364e385b3fe22c9381e20a72ce520e5)
Trojanized adware; 20K popular apps caught in the crossfire
- https://blog.lookout.com/blog/2015/11/04/trojanized-adware/
Nov 4, 2015 - "Auto-rooting adware is a worrying development in the Android ecosystem in which malware roots the device automatically after the user installs it, embeds itself as a system application, and becomes nearly impossible to remove. Adware, which has traditionally been used to aggressively push ads, is now becoming trojanized and sophisticated. This is a new trend for adware… detected over 20,000 samples of this type of trojanized adware masquerading as legitimate top applications, including Candy Crush, Facebook, GoogleNow, NYTimes, Okta, Snapchat, Twitter, WhatsApp, and many others…"
- http://net-security.org/malware_news.php?id=3144
05.11.2015
Instagram 'free $50 Xbox cards' - Phish …
- https://blog.malwarebytes.org/online-security/2015/11/nice-instagram-shame-about-the-code-generator/
Nov 5, 2015
> https://blog.malwarebytes.org/wp-content/uploads/2015/11/xboxinsta1-300x261.jpg
"… This tiled effect is achieved by uploading pieces of the larger image one by one, and could well help to attract attention from anybody interested in free $50 Xbox cards… it’s certainly a lot better looking than most similar promo splashes we see elsewhere… It claims to be a code generator, and wants visitors to enter an email-address-to-proceed after having selected their chosen reward. After hitting the 'Generate Code' button, the would-be recipient of free Xbox goodness sees one of those “We’re doing hacking stuff, honest” boxes pop up in the middle of the screen complete with regulation standard green text on black background:
> https://blog.malwarebytes.org/wp-content/uploads/2015/11/xboxinsta3.jpg
… convincing people to fill in surveys has been around for many years, yet they continue to bring in those hopeful of a little free console cash. I’ve seen pretty much every variation of the above there is, and have yet to see a single supposed code generator which actually did just that. All you’ll get for your time and trouble is handing over personal information to marketers and / or potentially unwanted downloads. And after you’ve done all of that, there’s still no guarantee you’ll get anything at the end of it. Our advice is -not- to bother with offers such as these – no matter how nice their Instagram page looks."
Fake 'Invoice' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/11/malware-spam-invoice-00004232-from.html
6 Nov 2015 - "This -fake- invoice does not come from Timber Solutions but is instead a simple -forgery- with a malicious attachment: From: Kes [kerryadamson@ bigpond .com]
Date: 6 November 2015 at 11:07
Subject: Invoice #00004232; From Timber Solutions
Hi, please find attached our invoice for goods ordered under Order
No. 11146, which will be delivered tomorrow. Please pay into the
account, details of which are at the foot of the invoice. Kes
Attached is a file ESale.xls which I have seen just a single variant of across multiple emails. This has a VirusTotal detection rate of 3/54* and contains this malicious macro… which (according to this Hybrid Analysis report**) downloads a binary from:
advancedgroup .net .au/~incantin/334g5j76/897i7uxqe.exe
..this is saved as %TEMP%\tghtop.exe and has a detection rate of… zero***. Automated analysis of this binary [1] [2] shows network traffic to: 89.108.71.148 (Agava Ltd, Russia)
I strongly recommend that you -block- traffic that that IP. The payload is most likely to be the Dridex banking trojan."
* https://www.virustotal.com/en/file/5be589570751f4d8ead65ec9ce502637464568eca45f35dca61a195e6cb35f90/analysis/1446810013/
5 November 2015: barf vermilion.zip: Extracts to: 018648187082.exe
Current Virus total detections 0/55* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/e07d6c40cd9199559f4fe90515f7a583a1d2a073d58182ca9548f2bb037a96a2/analysis/1446759940/
___
DirectRev Ad loads Flash Exploit, CryptoWall…
- https://blog.malwarebytes.org/malvertising-2/2015/11/directrev-advert-loads-self-sufficient-flash-exploit-cryptowall/
Nov 5, 2015 - "We have been observing a series of -malvertising- attacks using an unusual but familiar delivery method recently… instead of relying on an exploit kit to compromise the victims’ machines, this technique simply relies on a disguised Flash advert that downloads its own exploit and payload. We previously encountered this attack pattern on two occasions, one for a Sparta Ad and another that involved RTB platform DirectRev. This latest attack features various ad platforms leading to a booby-trapped DirectRev ad…
> https://blog.malwarebytes.org/wp-content/uploads/2015/11/Final_flow.png
… The Flash exploit is hosted on sensentive[.]com… The malware payload, CryptoWall, is retrieved from gearsmog[.]com… Both domains were created only a few seconds apart but reside on different IP addresses: [removed] and [removed]…"
Fake 'OUTSTANDING INVOICES' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/11/malware-spam-outstanding-invoices-steve.html
9 Nov 2015 - "This -fake- financial email does not come from Resimac but is instead a simple -forgery- with a malicious attachment. From "Steve McDonnell" [stevem@ resimac .co.uk]
Date Mon, 09 Nov 2015 18:24:23 +0530
Subject OUTSTANDING INVOICES
Dear,
Please find attached invoices 1396 & 1406 which are now outstanding.
I should be grateful if you would let me know when they are going to be paid.
Kind Regards
Steve McDonnell
Company Secretary
Resimac Ltd
Unit 11, Poplars Industrial Estate …
I have only seen a single sample of this with an attachment named Invoices001396,1406-11.2015.xls which has a VirusTotal detection rate of 3/54* … which contains this malicious macro… which (according to this Hybrid Analysis report**) in this case downloads a binary from:
www .davidcaballero .com/87yte55/6t45eyv.exe
The VirusTotal detection rate for this binary is 3/55***. That report indicates network traffic to: 89.108.71.148 (Agava Ltd, Russia)
Other analyses are pending, however I strongly recommend that you block traffic to that IP. The payload is likely to be the Dridex banking trojan."
* https://www.virustotal.com/en/file/6c9952b0712c9726373be21b1db570bcaf73d66a4dc286b383b773a654c68fc3/analysis/
The link in the email actually goes to sharefile .com where it downloads a file Amendment or the Agreement_09-11-2015.zip containing a malicious executable Amendment or the Agreement_09-11-2015.scr which has a VirusTotal detection rate of 2/54*. Automated analysis is inconclusive [1] [2] but you can guarantee that this is nothing good. Because of the low detection rates, it might be worth -temporarily- blocking sharefile .com."
* https://www.virustotal.com/en/file/47de271bdf0bbe10f19cff2bb53846ba805824cf18a00577d0ea9dcce4585d00/analysis/1447072746/
New crypto-ransomware targets Linux web servers
- http://net-security.org/malware_news.php?id=3148
09.11.2015 - "There's a new piece of crypto-ransomware out there, but unlike most malware of this particular type, this one is mainly directed at web servers running on Linux. The threat has been dubbed Linux Encoder by Dr. Web researchers, and is currently detected by a small fraction of AV solutions*:
> http://www.net-security.org/images/articles/ransom-09112015-big.jpg
… "Once launched with administrator privileges, the Trojan (…) downloads files containing cybercriminals' demands and a file with the path to a public RSA key. After that, the malicious program starts as a daemon and deletes the original files," the researchers explained**. "Subsequently, the RSA key is used to store AES keys which will be employed by the Trojan to encrypt files on the infected computer"… It encrypts a wide variety of files - including Office, documents, image files, HTML and PHP files, archives, DLLs and EXE files - and adds the .encrypted extension to them. Instructions on what to do in order to get the files decrypted are included in each directory. Dr. Web researchers are working on a technology that can help decrypt data encrypted by this malware, but in the meantime the best protection against its destructiveness is to backup crucial files regularly…"
* https://www.virustotal.com/en/file/fd042b14ae659e420a15c3b7db25649d3b21d92c586fe8594f88c21ae6770956/analysis/
Fake 'Itinerary' SPAM - malcious attachment
- http://blog.dynamoo.com/2015/11/malware-spam-itinerary-c003ns39-no.html
10 Nov 2015 - "This rather terse -fake- business spam does not come from Click Travel but is instead a simple -forgery- with a malcious attachment: From: no-reply@ clicktravel .com [mailto:no-reply@ clicktravel .com]
Sent: Tuesday, November 10, 2015 11:21 AM
Subject: Itinerary #C003NS39
Please see document attached
Attached is a file Hotel-Fax-V0045G2B_8308427510989318361.xls which contains this malicious macro… which (according to this Hybrid Analysis report*) downloads a component from:
www .clemenciaortiz .com/87yte55/6t45eyv.exe
So far I have only seen one sample of this, there are likely to be others with different download locations but the same binary. This executable file has a detection rate of 2/55** and that VirusTotal report and this Malwr report*** indicate traffic to the following IP: [removed] (Agava Ltd, Russia)
I strongly recommend blocking traffic to that IP address. The payload is the Dridex banking trojan."
* https://www.hybrid-analysis.com/sample/89f5ad1914f34c192f93d72db0e0f98befd5e55ee862e66ccc621dd0d0b61af9?environmentId=1
Linux Encoder victims catch a lucky break: flaw in the malware
- http://net-security.org/malware_news.php?id=3151
10.11.2015 - "… the good news is that the malware makers have made a mistake that allowed Bitdefender researchers to recover the AES encryption key without having to decrypt it with the RSA private key held by the criminals… "We looked into the way the key and initialization vector are generated by reverse-engineering the Linux.Encoder.1 sample in our lab," they added. "We realized that, rather than generating secure random keys and IVs, the sample would derive these two pieces of information from the libc rand() function seeded with the current system timestamp at the moment of encryption. This information can be easily retrieved by looking at the file’s timestamp. This is a huge design flaw that allows retrieval of the AES key without having to decrypt it with the RSA public key sold by the Trojan’s operator(s)." This knowledge allowed them to create an effective decryption script, and given that this piece of ransomware targets more tech savvy users, they should not have a problem deploying it (check out this blog post* for the download link and instructions on how to use it)… They advised users never to run applications that they don’t completely trust, and to backup often - and keep the backup away from the system. In this particular case, that was the initial way to avoid paying the ransom, as the Trojan also encrypted backups found on the server."
* http://labs.bitdefender.com/2015/11/linux-ransomware-debut-fails-on-predictable-encryption-key/
___
Fake 'PO99631' SPAM - xls malware
- http://myonlinesecurity.co.uk/po99631-mark-singleton-gilkes-pumping-systems-direct-excel-xls-spreadsheet-malware/
10 Nov 2015 - "An email with the subject of 'PO99631' pretending to come from Mark Singleton with a malicious Excel XLS spreadsheet attachment is another one from the current bot runs… The email looks like: Please find PO99631 attached.
Kind Regards
Mark Singleton Sourcing Specialist Gilkes Pumping Systems Direct: +44 (0) 1539 790051
Tel: +44 (0) 1539 720028 Fax: +44 (0) 1539 732110 Gilbert Gilkes & Gordon Ltd ・Kendal ・Cumbria ・LA9 7BZ・United Kingdom
Registered Office: Gilbert Gilkes & Gordon Ltd. Kendal, Cumbria, LA9 7BZ Registration No: 173768 England & Wales
Fake 'PayPal' SPAM - PDF malware
- http://myonlinesecurity.co.uk/your-paypal-extras-mastercard-bill-payment-has-been-sent-fake-pdf-malware/
9 Nov 2015 - "An email with the subject of 'Your PayPal Extras MasterCard bill payment' has been sent pretending to come from admin@ eight-point .com with a zip attachment is another one from the current bot runs… The content of the email says : Hello customer,
Your payment for 654.35 USD has been sent.
Recipient: PayPal Extras MasterCard® Payment Method: Echeck Payment Amount: 654.35 USD Payment Date: Mon, 09 Nov 2015 22:04:27 +0100 Details in the attachment
Thanks for choosing the PayPal Extras MasterCard®.
Sincerely, PayPal …
PayPal Email ID PP0822 – yrV3fNFlU5JL13 …
9 November 2015: firm prices swordplay.zip: Extracts to: 353444754788.exe
Current Virus total detections 8/54* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/a5ea7f981a3bcba7886e398753e3ccf8021958ce670c2ce76681c064c7a5669f/analysis/
Fake 'scanner' SPAM - xls macro malware
- http://myonlinesecurity.co.uk/scanneryour-own-email-domain-email-sent-from-aficio-mp-c5000-excel-xls-spreadsheet-malware/
11 Nov 2015 - "An email with -no- subject pretending to come from a scanner at your own email domain about a document from 'Aficio MP C5000' with a malicious Excel XLS spreadsheet attachment is another one from the current bot runs… The email looks like: This E-mail was sent from “RNPF137EA” (Aficio MP C5000).
Scan Date: Wed, 11 Nov 2015 12:53:35 +0300
Queries to: scanner@ [redacted]
Fake 'PayPal' refund SPAM - malicious link
- http://blog.dynamoo.com/2015/11/malware-spam-refund-from-bowater.html
11 Nov 2015 - "This -fake- PayPal email leads to malware: From: service@ paypal .co.uk
Date: 11 November 2015 at 16:27
Subject: Refund from Bowater Incorporated
Bowater Incorporated has just sent you a refund
Wed, 11 Nov 2015 17:27:26 +0100
Transaction ID: 47E30904DC4145388
Dear Customer,
Bowater Incorporated has just sent you a full refund of £7849.90 GBP for your purchase.
If you have any questions about this refund, please contact Bowater Incorporated
The refund will go to your PayPal account. It may take a few moments for this transaction to appear in your account.
To see all the transaction details, please download and view from the link below…
Merchant information
Bowater Incorporated Note from merchant
None provided
Original transaction details
Description Unit price Qty Amount
Purchase from Bowater Incorporated £7849.90 GBP 1 £7849.90 GBP
Insurance: —-
Total: £7849.90 GBP
Refund to PayPal Balance: £7849.90 GBP
Invoice Number: 59266315
Yours sincerely,
PayPal …
The -link- in the email goes to a download location at sharefile .com which leads to a file transaction details.zip containing a malicious executable 'transaction details.scr'. This binary has a VirusTotal detection rate of just 1/55*. The Hybrid Analysis report** shows network traffic consistent with Upatre download the Dyre banking trojan. One key IP address in [removed] (Cobranet, Nigeria) which is well worth blocking."
* https://www.virustotal.com/en/file/6193e4256d68b6f21dd3cd165cc25b9d1502dbff5c8613fd0b63584cc3301fd3/analysis/1447260291/
11 November 2015: transaction details.zip: Extracts to: transaction details.scr
Current Virus total detections 1/53* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/6193e4256d68b6f21dd3cd165cc25b9d1502dbff5c8613fd0b63584cc3301fd3/analysis/1447256652/
___
Fake 'Invoice' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/11/malware-spam-invoice-si823610-from.html
11 Nov 2015 - "This -fake- invoice does not come from OfficeFurnitureOnline .co.uk but is instead a simple -forgery- with a malicious attachment. From accounts [accounts@ equip4work .co.uk]
Date Wed, 11 Nov 2015 14:54:33 +0400
Subject Invoice SI823610 from OfficeFurnitureOnline .co.uk Order Ref 4016584
Please find attached a sales invoice from OfficeFurnitureOnline .co.uk.
This email address is only for account enquiries, please check your confirmation
for any information regarding the order details or delivery lead times.
Thank you for your order.
Attached is a file SI823610.XLS which I have seen only one version of in several samples of the email. Usually there are different variants. In this case, the spreadsheet contains this malicious macro… and has a VirusTotal score of 4/54*. According to this Hybrid Analysis report** it then downloads a malicious binary from:
kdojinyhb .wz.cz/87yte55/6t45eyv.exe
In turn, this binary has a detection rate of zero***. Those two reports plus this Malwr report[4] show between them malicious traffic to the following IPs:
95.154.203.249 (Iomart / Rapidswitch, UK)
182.93.220.146 (Ministry Of Education, Thailand)
89.32.145.12 (Elvsoft SRL / Coreix , Romania / UK)
The payload is the Dridex banking trojan.
Recommended blocklist: 95.154.203.249
182.93.220.146
89.32.145.12
wz.cz "
* https://www.virustotal.com/en/file/173189a2f4247f80faf91e160294099f12fa8718659a2633e662fbd9d03280c6/analysis/1447239924/
Anti-Virus alone is not enough …
- https://blog.malwarebytes.org/security-threat/2015/11/three-reasons-why-anti-virus-alone-is-no-longer-enough/
Nov 11, 2015 - "… The malware ecosystem has changed drastically in the past 10 years, to the point that the old precautions are just no longer enough. Here are the three top reasons for this:
• You don’t have to click to get hit. In the past, it was sufficient to simply avoid clicking on suspect links or visiting bad sites. This is no longer the case because of new attack vectors like malvertising. In a malvertising attack, a legitimate site unknowingly pulls malicious content from a bad site, and the malicious content seeks ways (often exploits) to install itself on your computer. You may have heard these attacks called “drive by downloads.” Just by visiting a good site on the wrong day, you get infected…
• Traditional AV response times to new threats are too slow. According to data compiled by Panda Research, traditional AV only stops 30-50 percent of new zero-hour malware when it’s first seen. A few take up to eight hours to reach even the 90 percent level, with the majority needing a full 24 hours. And it takes them a full seven days to get to the high 90’s. That’s a whole lot of time to be missing protection. A recent study by the Enterprise Strategy Group showed that almost -half- of the enterprises polled had suffered a successful malware attack even though they were running anti-virus.
• Exploits are everywhere. Many software products, notably including Java and Flash, were designed in an era when computer security was a much less serious concern. And the worst part of exploit based malware is that the time from the initial exploit to detection and remediation – is on average almost a year…
… we believe in what’s called a layered approach to security.
• The layered approach is just like using a seat belt and an airbag – they both help keep you safe, but they work in different ways. In layered security, you don’t put all your eggs in the AV basket – you use multiple types of defense, each of which has its own strengths, and does different things. An anti-malware program is a zero-day focused, lightweight product that works with your traditional anti-virus product to block threats that AV misses. An anti-exploit program takes a different – yet still complimentary – approach. While anti-malware concerns itself with the what – files, URLs, domains, and so forth, anti-exploit worries about the how. How is a particular application behaving, and is it only performing actions which are expected? Using advanced behavior analysis, anti-exploit can stop a compromise at the beginning of the attack chain, rather than waiting until malware is already installed. And of course, you can augment your vendor provided protection by simply maintaining your computer according to the Three Basic Rules of Online Security, written by expert Brian Krebs:
• Don’t install software you didn’t explicitly request
• Keep your installed software up to date
• If you no longer need a piece of software, uninstall it…"
Fake 'Invoice' SPAM - xls malware
- http://myonlinesecurity.co.uk/debbie-haydon-mvmilk-co-uk-invoice-excel-xls-spreadsheet-malware/
12 Nov 2015 - "An email with the subject of 'Invoice' pretending to come from Debbie Haydon with a malicious Excel XLS spreadsheet attachment is another one from the current bot runs… The email looks like: Thank you for your order. Your Invoice – V414980 – is attached.
As agreed this invoice will NOT be sent via post.
If you have any questions regarding the attached invoice please telephone our office on 01708 688422.
kind regards
Fake 'Remittance Advice' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/11/malware-spam-remittance-advice.html
12 Nov 2015 - "This fake financial spam does -not- come from Norfolk County Council but is instead a simple -forgery- with a malicious attachment: From AccountsPayable@ Norfolk .gov.uk
Date Thu, 12 Nov 2015 14:09:46 +0430
Subject Remittance Advice
Dear Sir/Madam,
Please find attached your remittance advice.
Regards,
NCC …
Attached is a file 6134443_101115_141851.xls which apparently comes in two or three versions, although I have only seen one with a VirusTotal detection rate of 3/54* and containing this malicious macro… These documents then download a malicious binary from:
aniretak .wz.cz/5t546523/lhf3f334f.exe
sanoko .jp/5t546523/lhf3f334f.exe
www .delianfoods .com/5t546523/lhf3f334f.exe
This binary has a VirusTotal detection rate of 3/54**, and that report plus this Hybrid Analysis report*** show malicious traffic to:
95.154.203.249 (Iomart Hosting / Rapidswitch, UK)
182.93.220.146 (Ministry of Education, Thailand)
The payload is the Dridex banking trojan.
Recommended blocklist: 95.154.203.249
182.93.220.146 "
* https://www.virustotal.com/en/file/b4afaeb8c54b24c0d3de694407ddab56ba68bdd625410a72e6f918a73bf3a41d/analysis/1447326664/
Fake 'e-Transfer' SPAM - Dyre banking trojan
- http://blog.dynamoo.com/2015/11/malware-spam-fyi-interac-e-transfer-to.html
12 Nov 2015 - "This -fake- financial spam leads to malware: From: Bank of Montreal [notify@ payments .interac.ca]
Date: 30 September 2015 at 13:34
Subject: FYI: INTERAC e-Transfer to Guillaume Davis accepted
Dear Customer
The INTERAC e-Transfer for $2997.60 (CAD) you sent to Guillaume Davis was accepted. The transfer is now complete.
Recipient's message: A message was not provided
Thank you for using Bank of Montreal INTERAC e-Transfer Service.
Please follow the link below to download the transaction details …
12 November 2015: INTERAC e-Transfer transaction details.doc - Current Virus total detections 1/53*
MALWR** which contains an embedded rtf file(VirusTotal 2/54***) , which in turn has an embedded dyre / dyreza banking malware (VirusTotal[4])…DO NOT follow the advice they give to enable macros or enable editing to see the content… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/fbcd41ac2b4da177e97eb2696703b64c53512ec6aaa7743e4b1feb0c23bfd2ba/analysis/1447344188/
Buhtrap gang distributed malware thru Ammyy’s remote desktop software
- http://net-security.org/malware_news.php?id=3154
12.11.2015 - "… Researchers noticed in late October that, for about a week, visitors to ammyy .com were downloading an installer that contained malware along with the Ammyy product. While Ammyy Admin is legitimate software, it has a long history of being used by fraudsters, and several security products detect it as a Potentially Unsafe Application. Similarly, Download .com, a major download site, doesn’t provide a direct-download link to Ammyy software to users, instead listing the Ammyy Admin page for information purposes only. However, Ammyy Admin is still widely used: Ammyy’s website lists clients that include TOP500 Fortune companies as well as Russian banks. According to the investigation, -five- different malware families were distributed through Ammyy’s website during the recent incident. The first malware, the Lurk downloader, was distributed on October 26. Next was Corebot on October 29, then Buhtrap on October 30, and finally Ranbyus and Netwire RAT on November 2.
Although these families are not linked, the droppers that could potentially have been downloaded from Ammyy’s website were the same in every case. Thus it is quite possible that the cybercriminals responsible for the website hack sold the access to different groups. Of the malware distributed via Ammyy’s website, of particular interest is the install package used in Operation Buhtrap. “The fact that cybercriminals now use strategic web compromises is another sign of the gap closing between techniques used by cybercriminals and by actors behind so called Advanced Persistent Threats,” said Jean-Ian Boutin, Malware Researcher at ESET."
- http://www.welivesecurity.com/2015/11/11/operation-buhtrap-malware-distributed-via-ammyy-com/
'Magnitude EK' activity increases via Malvertising attacks
- https://blog.malwarebytes.org/exploits-2/2015/11/magnitude-exploit-kit-activity-increases-via-malvertising-attacks/
Nov 13, 2015 - "During the past few days we have noticed a higher than usual number of 'malvertising attacks' pushing the Magnitude exploit kit – which had been relatively quiet – to drop ransomware. Magnitude EK is one of those exploit kits we don’t hear about as much in comparison to others such as Angler EK or Nuclear EK. Its unique URL pattern makes it easy to spot from the clutter of network traffic captures because it uses chained subdomains typically ending in a shady Top Level Domain like -pw- (Palau Pacific island)… Perhaps this increased activity is due to the fact that Magnitude EK is the third exploit kit to leverage the latest Flash Player vulnerability (CVE-2015-7645*) recently patched by Adobe… CryptoWall was dropped via two separate malware binaries…"
* Latest Flash version is -19.0.0.245- check yours to avoid trouble:
> https://www.adobe.com/software/flash/about/
___
13 November 2015: TRPB_1_1107991874.pxls - Current Virus total detections 3/54*
… some of these emails have a plxs attachment which I never heard of. It is either a mistake by the malware bot sender or it is a new excel extension that needs a new version of excel to open it. My gut feel is that it was a mistake and the P added in error. Renaming the file to a simple xls makes it work as normal and shows a download of Dridex banking malware from
http ://rgr-sa .ch/~testing/345u754/433fd.exe (VirusTotal 3/53**). Many other copies of the email had a -normal- xls extension… DO NOT follow the advice they give to enable macros or enable editing to see the content. Most of these malicious word documents appear to be blank or look something like these images when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21.png
…The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/9ce4022b73e9c9f656de082d6ae6374d1aa4e391ac06597c218a32255b0a4ef4/analysis/1447408547/
Fake 'Invoice' SPAM - xls malware
- http://myonlinesecurity.co.uk/november-invoice-inv-9771-from-eye-on-books-excel-xls-spreadsheet-malware/
13 Nov 2015 - "An email with the subject of 'November Invoice INV-9771' from 'Eye on Books' pretending to come from Charles Klvana with a malicious Excel XLS spreadsheet attachment is another one from the current bot runs… The email looks like: Hi,
Please find attached this months invoice for Xero & Receiptbank software. You’ve completed a direct debit form, so this will have been paid from your nominated account, so please don’t send through payment separately.
Thanks again for your business, it’s greatly appreciated.
Kind regards,
Charles Klvana
EYE ON BOOKS
Fake 'Statements' SPAM - xls malware
- http://myonlinesecurity.co.uk/statements-and-related-documents-for-october-david-bartels-miriam-benda-professionals-ashgrove-excel-xls-spreadsheet-malware/
13 Nov 2015 - "The -third- version of a Dridex dropper today so far is an email with the subject of 'Statement(s) and related document(s) for October' pretending to come from David Bartels with a malicious Excel XLS spreadsheet attachment is another one from the current bot runs… The email looks like: Dear Sir/Madam
Please find attached:
Your Statement(s) and related document(s) for October.
Regards,
Miriam Benda
Professionals Ashgrove
Fake 'Invoice' SPAM - doc malware
- http://myonlinesecurity.co.uk/november-invoice-78909675-wahl-canada-word-doc-malware/
13 Nov 2015 - "An email with the subject of 'November Invoice #78909675' pretending to come from Logan Courtney (probably random, -faked- headers) with a malicious word doc attachment is another one from the current bot runs… The email looks like: Hello ,
Please review the attached copy of your Electronic document.
A paper copy of this document is being mailed, but this email is being sent in addition for your convenience.
Thank you for your business,
Wahl Canada Inc.
NOTICE OF CONFIDENTIALITY. This communication, including any information transmitted with it, is intended only for the use of the individual(s) to which it is addressed and is confidential. If you are not an intended recipient…
13 November 2015: INVOICE-78909675.doc - Current Virus total detections 0/54*
This has an embedded ole object in base 64 format that I couldn’t manually decode however MALWR** showed it connecting to http ://109.234.37.214 /alikaps/terminator.php where it downloaded ulysse.exe (VirusTotal 1/51***)… DO NOT follow the advice they give to enable macros or enable editing to see the content. Most of these malicious word documents appear to be blank or look something like these images when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21-1024x412.png
… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/87aa26f16d507f66386c2f1d60f00499aab7aaeeea723d5bb848abbc9f2f4055/analysis/1447416661/
Fake 'Payment Confirmation' SPAM - doc malware
- http://myonlinesecurity.co.uk/transaction-and-payment-confirmation-from-spilo-worldwide-word-doc-malware/
13 Nov 2015 - "An email with the subject of 'Transaction and Payment Confirmation' from Spilo Worldwide pretending to come from random names, companies and email addresses with a malicious word doc attachment is another one from the current bot runs… The email looks like:
Transaction and Payment Confirmation from Spilo Worldwide
13 November 2015: Spilo_Worldwide_payment_17650687.doc - Current Virus total detections 0/54*
This is another one of the -new- type macro downloaders that I first saw earlier today that have an embedded base 64 file inside the word doc that uses a post command to a php file on a remote server instead of the more usual -get- to download malware. MALWR analysis shows that this one contacts http ://91.223.88.54 /alikaps/terminator.php to download a different Dridex version by the same file name ulysse.exe from today’s earlier one (VirusTotal 0/54**)… DO NOT follow the advice they give to enable macros or enable editing to see the content. Most of these malicious word documents appear to be blank or look something like these images when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21-1024x412.png
… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/4e56c84d20accba4f66496221a0d192cd5e7760690f6a9e71fcb3f973b095566/analysis/1447423504/
Fake 'DHL' SPAM - PDF malware
- http://myonlinesecurity.co.uk/dhl-express-credit-card-billing-adjustment-ref-3383095-fake-pdf-malware/
16 Nov 2015 - "… An email with the subject of 'DHL Express – Credit Card Billing Adjustment. Ref# 3383095' pretending to come from eInvoicing with a zip attachment is another one from the current bot runs… The content of the email says : DHL Express Customer:
The attached file details adjustments that have been made to shipping charges originally billed to your credit card. These adjustments are for charges or credits that have occurred after the initial processing of your shipment(s). These adjustments have been applied to your credit card and will appear on your next credit card statement.
All shipments are subject to the terms and conditions contained in the DHL Express Tariff and the DHL Express Terms and Conditions of Service…
16 November 2015: dhl16112015_6987878544212.zip: Extracts to: dhl16112015_6987878544212exe
Current Virus total detections 2/54* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/9eadcc852b87429dfb8c7e61da7951a8fb8c28eb88ec91d90eea290248747dff/analysis/1447663550/
___
Fake 'Toll' SPAM - xls malware
- http://myonlinesecurity.co.uk/toll-ipec-invoicestatement-80458249-excel-xls-spreadsheet-malware/
16 Nov 2015 - "An email with the subject of 'Toll IPEC invoice/statement (80458249)' pretending to come from ipecar@ tollgroup .com with a malicious Excel XLS spreadsheet attachment is another one from the current bot runs… The email looks like: Please find attached your current Toll IPEC invoice/statement..
Should you have a query with your account, please contact the telephone number detailed on your invoice/statement or email your enquiry to ipecar@ tollgroup .com
16 November 2015 : 80458249_1519.pxls - Current Virus total detections 3/55*
… Downloads Dridex banking malware from http ://gospi .eu/~gospi/45yfqfwg/6ugesgsg.exe (VirusTotal 1/55**)… the xls spreadsheet has been accidentally renamed to pxls, so windows doesn’t know what to do with it. Some versions then were PXLS and some proper XLS… Other download locations include www .kolumbus .fi/~kf0963/45yfqfwg/6ugesgsg.exe and piotrektest .cba .pl/45yfqfwg/6ugesgsg.exe … DO NOT follow the advice they give to enable macros or enable editing to see the content. Most of these malicious word documents appear to be blank or look something like these images when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21-1024x412.png
… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/cefc0857a0dda3991bdad3aa3800b1175c96c7acb8feaa6cffed0b79ce649a13/analysis/1447675709/
Fake 'Invoices' SPAM - doc malware
- http://myonlinesecurity.co.uk/accounting-specialist-metropolitan-an-rr-donnelley-company-2-invoices-attached-word-doc-malware/
16 Nov 2015 - "An email with the subject of '2 Invoices Attached' pretending to come from random names, companies and email addresses with a malicious word doc attachment is another one from the current bot runs… The email looks like: Good morning,
Please see the attached invoices and remit payment according to the terms listed at the bottom of the invoice. If you have any questions please let us know.
Thank you!
Loris Lecomte
Accounting Specialist| Metropolitan, An RR Donnelley Company
Fake 'Remittance' SPAM - doc malware
- http://myonlinesecurity.co.uk/cook-medical-cook-remittance-advice-ach-word-doc-malware/
16 Nov 2015 - "An email with the subject of 'COOK Remittance Advice-ACH' pretending to come from random companies, names and email addresses with a malicious word doc or attachment is another one from the current bot runs… The email looks like: Please find attached your Remittance Details for the funds that will be deposited to your bank account, PLEASE ALLOW 1-2 BUSINESS DAYS.
Cook Medical is now sending through the bank the addenda information including your remit information.
If you are not seeing your addenda information in your bank reporting you may have to contact your local bank representative.
Accounts Payable
Fake 'DoT' SPAM - xls malware
- http://myonlinesecurity.co.uk/dot-payment-receipt-excel-xls-spreadsheet-malware/
16 Nov 2015 - "An email with the subject of 'DoT Payment Receipt' pretending to come from donotreply@ transport .gov .uk with a malicious Excel XLS spreadsheet attachment is another one from the current bot runs… The email looks like: [Automated message. Do not reply]
Thank you for your payment. It is important that you print this receipt and record the receipt number as proof of your payment. You may be asked to provide your receipt details should you have an enquiry regarding this payment.
DISCLAIMER
This email and any attachments are confidential and may contain legally privileged
and/or copyright material. You should not read, copy, use or disclose any of the
information contained in this email without authorisation. If you have received it in
error please contact us at once by return email and then delete both emails. There is
no warranty that this email is error or virus free.
MS 'Outlook Web Access' – Phish …
15 Oct 2015 - "… a lot of phishing attempts against Microsoft Outlook Web Access (Microsoft Outlook Web App (formerly known as Outlook on the Web or Outlook Web Access) is a browser-based email client. Outlook Web App lets you access your Microsoft Exchange Server mailbox from almost any web browser.) These sort of phishing attempts are much harder to protect against, because the OWA web address will -not- be a Microsoft website or any common site name but is normally a subdomain or part of your own company web domain. To make it harder, many companies do have numerous different email domains, so email messages might come from any of the company domains. To make it even more plausible, many companies have policies that insist on a user updating and changing their passwords every 30 or 60 or 90 days… One of the major common subjects in this sort of phishing attempt is Your password will expire soon or update your email or something very similar. This one wants only wants your email log in details…
… The from address is -spoofed- to read from Administrator whereas a very high proportion of them will be spoofed to appear to come from Administrator @ your own email domain. If you are unwise enough to follow the link you see a webpage looking like:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/11/Your-password-will-expire-soon-1024x514.png
… If you do fill in the details you get sent on to the next page saying : Your information was successfully submitted, please ensure that you entered your email details correctly; to enable us complete your security updates. If you have entered your details wrongly kindly click back and refill in details correctly.
N.B Please be informed that filling in the wrong details will be resulting to the deactivation of your email address.
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/11/Your-password-will-expire-soon2-1024x355.png
All of these emails use Social engineering tricks to persuade you to open the attachments that come with the email… Or whether it is a straight forward attempt, like this one, to steal your personal, bank, credit card or email and social networking log in details…"
Britain to build cyber attack forces to tackle IS, hackers
- http://www.reuters.com/article/2015/11/17/us-britain-security-cybersecurity-idUSKCN0T604K20151117
Nov 17, 2015 - "British spies are building elite cyber offensive forces to strike at Islamic State fighters, hackers and hostile powers, finance minister George Osborne said on Tuesday after warning militants wanted to launch deadly digital attacks. Islamic State was trying to develop the capability to attack British infrastructure such as hospitals, power networks and air traffic control systems with potentially lethal consequences, Osborne said. In response, Britain will bolster spending on cyber defenses, simplify its state cyber structures and build its own offensive cyber capability to attack adversaries… Britain's new cyber attack forces will be run jointly between GCHQ and the Defence Ministry and will target individual hackers, criminal gangs, militant groups and hostile powers, using a "full spectrum" of actions, Osborne said…"
___
Casino Malvertising Campaign
- https://blog.malwarebytes.org/malvertising-2/2015/11/the-casino-malvertising-campaign/
Nov 17, 2015 - "We identified one of the largest malvertising campaigns in recent months going through -10- different ad domains receiving massive volumes of Internet traffic. Although we only recently uncovered and reported this campaign, telemetry data indicates that it actually started on October 21, making this at least a three-week operation. This malvertising attack preyed on visitors to sketchy websites offering anything from torrents of copyrighted movies, live streams of the latest flicks, or pirated software. The malicious ads would automatically (no click required) redirect users to a casino website used as decoy to silently load malicious iframes from disposable domains which ultimately lead to the Angler exploit kit. In one case, the casino website was a direct gateway to Angler EK. The ad networks were almost all registered via Domains By Proxy LLC, meaning -no- information was available about the registrant but they were all through GoDaddy and on the same ASN: AS15169. This made us believe that they were actually all related to one another. Moreover, one of them, AdCash, did have a point of contact and this is how we were able to report the incidents. A look at some of the stats behind those ad domains shows some staggering numbers. According to SimilarWeb a service that estimates website traffic and provides various analytics, these ad networks generated over 2 -billion- visits in October. To be clear, this is -not- how many people were exposed to malvertising since this only affected a few particular rogue campaigns, and not all campaigns running on these networks… before September, the traffic on those three domains was quasi nonexistent but all of the sudden spiked through the roof for a combined total of over 1 million visits:
> https://blog.malwarebytes.org/wp-content/uploads/2015/11/similarweb.png
… a very large number of people were exposed to malware because of this campaign. Over the three-week course, several different payloads were dropped by Angler EK. We found the infamous CryptoWall ransomware as well as the Bunitu Trojan… We contacted AdCash on November 10th and the following day the malvertising attacks appeared to have stopped. However, on November 14th we observed -another- incident again also using one of the casino websites but with a .space domain now to redirect to Angler EK… We will continue to monitor and report future incidents we encounter via this ad network and take necessary actions to protect our users from malware.
Highlights:
• Torrent, crack, video sites targeted
• Malvertising via AdCash and related networks (> 2 billion traffic)
• Casino websites used a decoy/redirectors ( > 1 million traffic)
• Angler exploit kit
• Over 30 different malware payloads
• Three-week campaign …"
> https://blog.malwarebytes.org/wp-content/uploads/2015/11/Casino_Flow.png
___
Blackhole EK resurfaces…
- https://blog.malwarebytes.org/exploits-2/2015/11/blast-from-the-past-blackhole-exploit-kit-resurfaces-in-live-attacks/
Nov 17, 2015 - "… a threat actor is using the defunct Blackhole exploit kit in active drive-by download campaigns via -compromised- websites. We noticed Java and PDF exploits collected by our honeypot which we haven’t seen in ages. Looking closer at the structure of this attack, we were surprised when we realized this was the infamous Blackhole. Blackhole’s author, Paunch, was arrested in October 2013 and while criminals kept using the kit for the next few months, the exploits slowly deprecated and lost value because of lack of development. The new drive-by download attacks we caught over the weekend rely on the same structure as the original Blackhole, even reusing the old PDF and Java exploits. The only difference is the malware payload being dropped, which is current and had very -low- detection on VirusTotal… Although the exploits are old, there are probably still vulnerable computers out there who could get compromised. We also noticed that the author behind this Blackhole edition was working on new landing pages, so it is possible there might be additional changes in the future… Indicators of compromise: Server IP: 88.208.0.217 …"