Fake 'Website Invoice' SPAM – PDF malware
- http://myonlinesecurity.co.uk/here-is-your-bt-website-invoice-pdf-malware/
11 Aug 2015 - "'Here is your BT Website Invoice. pretending to come from btd.billing.noreply@ bt .com with a PDF attachment is another one from the current bot runs… The email comes in corrupt… There is an HTML attachment which contains what the actual email should read: ***Please do not reply to this automated e-mail as responses are not read***
Hello
Here is your latest billing information from BT Directories – please check the details carefully.
If you need to contact us then you’ll find the numbers in the attachment.
Kind Regards
BT Directories Billing & Credit Management …
And there is a PDF attachment which contains the malware:
11 August 2015 : DirectDebit Invoice_5262307_011220140151449702826.pdf
Current Virus total detections: 4/56* which is a PDF containing a word doc with embedded macros in the same way as described in today’s earlier malspam run**… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/08af5513378e9186ba26b4ba1aa8b2e3951d61328f8d7a8c98a43f087cb7a97a/analysis/1439286155/
Fake 'Congratulations on your purchase Windows' SPAM – fake PDF malware
- http://myonlinesecurity.co.uk/congratulations-on-your-purchase-windows-fake-pdf-malware/
11 Aug 2015 - "'Congratulations on your purchase Windows' with a zip attachment is another one from the current bot runs… The email looks like: The invoice for the license windows 10.
Invoice id: 5661255582
License number: 211883074666
License serial number: XXXXXX-XXXXXX-XXXXXX-QF7303-DG7S86
Details of the attachment.
THANKS A LOT FOR BEING WITH US.
Todays Date: Invoice Windows10 1648726511-en.zip:
Extracts to: Invoice Windows10 7848342350-en.exe
Current Virus total detections: 6/57* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/ac95e5be477cbddf2478632d28ada80bd4d235bef526de210c964084460fcabf/analysis/1439303996/
___
Asprox botnet… disappears
- http://www.infoworld.com/article/2969322/malware/asprox-botnet-a-longrunning-nuisance-disappears.html
Aug 11, 2015 - "The Asprox botnet, whose malware-spamming activities have been followed for years by security researchers, appears to be gone… the botnet seemed to be shut down, wrote Ryan Olson, intelligence director for Palo Alto Networks, in a blog post:
> http://researchcenter.paloaltonetworks.com/2015/08/whats-next-in-malware-after-kuluoz/
Olson wrote that Palo Alto thought the botnet's operators may have changed their tactics, and Palo Alto missed the shift. But they verified that Asprox's command-and-control structure shut down - at least for now… Earlier this year, Brad Duncan, a security researcher at Rackspace, also noticed a change:
> https://isc.sans.edu/forums/diary/What+Happened+to+You+Asprox+Botnet/19435/
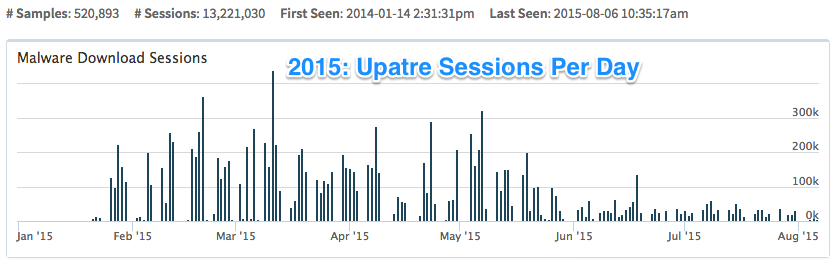
… Spam that appeared stylistically close to that sent by Asprox had -different- malware. Asprox has taken a hit before. In November 2008, it was one of several botnets affected by the shutdown of McColo, a notorious California-based ISP that was providing network connectivity for cybercriminals. The shutdown of McColo dramatically cut the amount of spam, but Asprox as well as other botnets came back. The most frequent malware now seen by Palo Alto is Upatre. That malware downloads other harmful programs to a computer, and Palo Alto has seen it involved in installing a banking trojan called Dyre and the Cryptowall ransomware…"
>> http://researchcenter.paloaltonetworks.com/wp-content/uploads/2015/08/kuluoz-2.png
12 August 2015: Invoice.jar - Current Virus total detections: 4/57*
Luckily, Outlook (as you can see from the screenshot above) and many other email clients automatically -block- java jar files from being accessed or opened in the email client. Webmail clients are more at risk as most allow any attachment. Java is a crossbrowser and cross OS program and that is why it is so dangerous. Malicious Java files can infect and compromise ANY computer whether it is windows or Apple or Android or Linux. You will not be infected and cannot be harmed if you do -not- have Java installed on the computer.
This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like an unknown instead of the java executable file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/f2188d223305092fe0a9c8be89c69e149c33c3ea4b1c0843fda00771ac72272d/analysis/1439362101/
___
12 August 2015: smo.pdf - Current Virus total detections: 5/56*
… which drops/creates 4.docm (VirusTotal**) which contains a macro that connects to http ://konspektau.republika .pl/07jhnb4/0kn7b6gf.exe and downloads Dridex banking malware (VirusTotal***). Other download locations include http ://madrigalchor-schloss-benrath .de/07jhnb4/0kn7b6gf.exe … The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/a4a7b540630853ca92c87ddbde759e85dbfe762ff13ab917b6db3433dea28d7a/analysis/1439370949/
Fake 'Invoice for 415 Litmus' SPAM – doc malware
- http://myonlinesecurity.co.uk/invoice-for-415-litmus-word-doc/
12 Aug 2015 - "'Invoice for 415 Litmus' pretending to come from angela_lrc088128@ btinternet .com (the lrc088128 is random and I am seeing -hundreds- of lrc******@ btinternet .com being -spoofed- as the from addresses) with a malicious word doc attachment is another one from the current bot runs… DO NOT follow the advice they give to enable macros or enable editing to see the content. Almost all of these malicious word documents appear to be blank or look something like this image when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21.png
12 August 2015: 415 Litmus Cleaning invoice.docm - Current Virus total detections: 6/56*
The -malicious- macro inside this version of the word doc connects to and downloads Dridex banking malware from http ://madrigalchor-schloss-benrath .de/07jhnb4/0kn7b6gf.exe (Virus Total**) Which is the -same- malware as described in today’s other Malspam run[1] containing malicious PDF dropping word docs… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/8cc4da70ab176d2f942325ac74615d80b5968d817e3e52377ad2c9feb1ee1484/analysis/1439371782/
Fake 'transferred into Your account HSBC' SPAM – PDF malware
- http://myonlinesecurity.co.uk/this-is-to-confirm-that-amounts-were-transferred-into-your-account-hsbc-fake-pdf-malware/
12 Aug 2015 - "A series of emails on the theme of 'This is to confirm that amounts were transferred into Your account' with subjects like 'Payment affirmation' or 'Conducted transaction information' with an email -link- to entice you into downloading a zip attachment is another one from the current bot runs… Some of the subjects include:
Conducted transaction information
Deposited funds receipt
Fund transfer receipt
Deposited funds acknowledgment
Transaction statement
Transfer verification
Deposited funds affirmation
Deposited funds statement
Balance change receipt
The senders pretend to be bank employees from HSBC and include such titles as:
Forward Applications Strategist
Principal Assurance Developer
Corporate Web Architect
Principal Factors Director
And hundreds of other similar style of seemingly important sounding titles. The sender matches the job title in the body of the email although the names are totally random…
12 August 2015: invoice.pdf.zip: Extracts to: invoice.pdf.exe*
Current Virus total detections: 3/56*. These -Upatre- downloaders normally download either Dridex or Dyreza banking malware. So far the automatic tools haven’t managed to get any actual download. This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/21d56cfe59c7ae00096ccee20bf480350ca88bac5f2c4b267442b07f876bc64c/analysis/1439376577/
___
Fake 'Important documents BoA' SPAM – PDF malware
- http://myonlinesecurity.co.uk/fw-important-documents-bankofamerica-com-fake-pdf-malware/
12 Aug 2015 - "'FW: Important documents' pretending to come from Guadalupe Aldridge or Mariano Cotton (and probably loads of other random names @ bankofamerica .com) with a zip attachment is another one from the current bot runs…
12 August 2015: AccountDocuments.zip: Extracts to: AccountDocuments.scr
Current Virus total detections: 0/56* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/6ac32eeb2a0be4b0f8aac5c306f3c99eeabfa71afc1777adcc75ea9fe5489f0a/analysis/1439398277/
___
13 August 2015: INVOICE_I623792760.zip: Extracts to: INVOICE_I9288320.exe
Current Virus total detections: 1/57*. This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/3eb08a1fc4c27ecc5bb1e512327fc645076b00c3a62555871d8b8ed395517c79/analysis/1439455676/
___
13 August 2015: AccountDocuments.doc - Current Virus total detections: 5/56*
This goes through a convoluted download procedure linking to: http ://hutsul .biz/administrator/components/com_joomlaupdate/rara.txt which is just a simple instruction to download what looks like -Upatre- downloader which will eventually download Dridex banking malware from http ://klosetaffair .com/scripts/jquery-1.8.3.exe (VirusTotal**)… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/c683e3a12ab2e80aa4247a1c8ed6b9c565e0241212bc9730596e69ee54807b57/analysis/1439461278/
- http://threattrack.tumblr.com/post/126606969628/rbc-secure-webmail-spam
Aug 13, 2015 - Subjects Seen: RBC Secure Webmail/Courriel secure
Typical e-mail details: Hello
You have received a secure e-mail, which may contain personal/confidential information.
To read and/or reply to the secure e-mail, please follow the simple steps below:
· Double click on the attached Click2View.zip
IMPORTANT:
1.) You must be connected to the Internet to view the secure e-mail.
2.) Please ONLY reply from the above link. DO NOT reply by clicking the “reply” option as this will not be secured.
Malicious File Name and MD5:
Click2View.scr (51cabd5eb93920043db1b18cf163b108)
Tagged: RBC, Upatre
___
Fake 'Notice of payment' SPAM – PDF malware
- http://myonlinesecurity.co.uk/notice-of-payment-national-bank-of-canada-fake-pdf-malware/
13 Aug 2015 - "'Notice of payment' pretending to come from sac.sbi@ sibn .bnc.ca with a zip attachment is another one from the current bot runs… The email looks like: You can view and print the notice of payment using the Netscape or Microsoft
Explorer browsers, versions 6.2 and 5.5. You can export and store the
notice of payment data in your spreadsheet by choosing the attached file in
pdf format “.pdf”.
If you have received this document by mistake, please advise us immediately
and return it to us at the following E-mail address: “sac.sbi@ sibn .bnc .ca“.
Thank you.
National Bank of Canada
600 de La Gauchetire West, 13th Floor
Montreal, Quebec H3B 4L2 …
13 August 2015: PaymentNotice.zip: Extracts to: PaymentNotice.scr
Current Virus total detections: 1/57* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/a978053fe90cc25dacc95b3f8e71884c88c3757027b98be120f1df46bf80f202/analysis/1439483960/
___
SSL Malvertising Campaign Continues
- https://blog.malwarebytes.org/malvertising-2/2015/08/ssl-malvertising-campaign-continues/
Aug 13, 2015 - "The actors behind the recent Yahoo! malvertising attack are still very much active and able to infect people who browse popular websites. We have been tracking this campaign and noticed that is has recently moved to a new ad network used by many top publishers:
- drudgereport .com 61.8M visits per month
- wunderground .com 49.9M visits per month
- findagrave .com 6M visits per month
- webmaila.juno .com 3.6M visits per month
- my.netzero .net 3.2M visits per month
- sltrib .com 1.8M visits per month
The malvertising is loaded via AdSpirit .de and includes a -redirection- to an Azure website. Note how both URLs are using HTTPS encryption, making it harder to detect the malicious traffic at the network layer:
> https://blog.malwarebytes.org/wp-content/uploads/2015/08/malvertising.png
Redirection chain
Publisher’s website
https ://pub.adspirit .de/adframe.php?pid=[redacted]
https ://pr2-35s.azurewebsites .net/?=pr2-35s-981ef52345
abcmenorca .net/?xvQtdNvLGcvSehsbLCdz Angler Exploit Kit…
We informed the ad network and although they did not immediately get back to us, the rogue advert was taken down."
abcmenorca .net: 88.198.188.158:
- https://www.virustotal.com/en/ip-address/88.198.188.158/information/
Country: DE
Autonomous System: 24940 (Hetzner Online AG)
Diagnostic page for AS24940 (HETZNER-AS)
- https://www.google.com/safebrowsing/diagnostic?site=AS:24940
"… over the past 90 days, 2335 site(s)… served content that resulted in malicious software being downloaded and installed without user consent. The last time Google tested a site on this network was on 2015-08-13, and the last time suspicious content was found was on 2015-08-13… this network has hosted sites that have distributed malicious software in the past 90 days. We found 224 site(s)… that infected 837 other site(s)…"
Fake 'Invoice' SPAM – doc/xls malware
- http://myonlinesecurity.co.uk/invoice-bristol-rope-twine-co-word-doc-or-excel-xls-spreadsheet-malware/
14 Aug 2015 - "'Invoice Bristol Rope & Twine Co' pretending to come from Roger Luke with a malicious word doc or Excel XLS spreadsheet attachment is another one from the current bot runs… DO NOT follow the advice they give to enable macros or enable editing to see the content. Almost all of these malicious word documents appear to be -blank- or look something like this image when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21.png
The email looks like: Thank you for your order. Your Invoice – 14/0238 – from Bristol Rope &
Twine Co is attached.
Fake 'Account management' SPAM – PDF malware
- http://myonlinesecurity.co.uk/account-management-was-limited-jpmorgan-chase-bank-fake-pdf-malware/
14 Aug 2015 - "'Account management was limited' pretending to be a message from JPMorgan Chase Bank with a zip attachment is another one from the current bot runs… Other subjects in this malware run include:
Personal account access has been minimized
Bank account control has been minimized
Personal account management had been restricted
Bank account access was blocked …
The email looks like: Dear Bank member,
Please consider this e-mail alert highly urgent. Kindly note that our
security department has detected the attempt to withdraw money from Your
account without confirmation.
As a security measure the bank had to restrict access to the account
until we get relevant request from the signatory. Please see attached
the document to be filled in order to get full access to the account.
Peter Malcolm,
Security Department Specialist
JPMorgan Chase Bank PLC
14 August 2015: Formsheet_to_be_filled in_.zip: Extracts to: Formsheet_to_be_executed_.exe
Current Virus total detections: 2/56* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/6b18f506d572f8f422a5568a84797ce355aedb897353310eb30d959986565e31/analysis/1439572799/
19 August 2015: ship20150817.zip: Extracts to: ship20150817.exe
Current Virus total detections: 2/54* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/b936cf05514ede49c63a732717ac901d22d3038e46a5820d7955f55c1ef7d6d0/analysis/1439977857/
- http://blog.dynamoo.com/2015/08/malware-spam-shipment-notice.html
19 Aug 2015 - "… the malware attempts to phone home to:
megapolisss006 .su/go/gate.php
.SU (Soviet Union) domains are bad news in general, if you can I would recommend blocking traffic to -all- of them. This domain is hosted on the following IPs:
195.2.88.196 (Zenon N.S.P., Russia)
[removed] (Bashrtcomm LIR, Russia)
94.229.22.42 (Bashrtcomm LIR, Russia)
You might want to consider blocking: 195.2.88.0/24
94.229.16.0/21
This though is the recommended minimum blocklist: 195.2.88.196
94.229.22.39
94.229.22.42 …"
___
Fake 'lawsuit' SPAM – doc/xls malware
- http://myonlinesecurity.co.uk/wtf-is-thislawsuit-word-doc-or-excel-xls-spreadsheet-malware/
19 Aug 2015 - "'wtf is this?lawsuit?' coming from random names and random email addresses with a malicious word doc attachment is another one from the current bot runs… This email has what appears to be a genuine word doc or Excel XLS spreadsheet attached which is malformed and contains a macro script virus… DO NOT follow the advice they give to enable macros or enable editing to see the content. Almost all of these malicious word documents appear to be -blank- or look something like this image when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21.png
The email looks like: why have you sued me? wtf is this?
i am attaching the subpoena
19 August 2015: subpoena.doc - Current Virus total detections: 5/54*
Connects to http ://bigdiscountsonline .info/css/_notes/rara.txt which is a simple text instruction to download Dridex banking malware from http ://allthatandmore .info/css/_notes/pa.exe (VirusTotal**). It also connects to http ://bigdiscountsonline .info/css/_notes/8179826378126.txt which is a VBS downloader (VirusTotal***)… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/61f94cafd9a0186dcc2f50bd907f712ddda5a284fe8900543014177c9bf484b9/analysis/1439998392/
20 August 2015: LIST_141114_jpg (2).xls - Current Virus total detections: 4/56*
So far automatic analysis hasn’t retrieved any payload so we are waiting for a manual analysis to be performed. These normally download Dridex banking malware.. Update: we now have managed to get an automatic analysis[2] which gave us: ceece.exe that looks like Dridex but no download location for it (VirusTotal)[3]… We always have problems with automatic analysis when the Doc or LS file is in Russian language and character set… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/5e77f6a84ef5179824f2a110a73c10927d32cb8efe306f6d333295a5cbac9467/analysis/1440065594/
Fake 'new ID and password' SPAM – PDF malware
- http://myonlinesecurity.co.uk/your-new-id-and-password-fake-pdf-malware/
20 Aug 2015 - "'Your new ID and password' coming from random names and email addresses with a zip attachment is another one from the current bot runs… The email looks like:
Your ID name and password has been changed according to your request dated August 19, 2015. Check attachment to view the renewed information.
20 August 2015: doc_ad78120.zip : Extracts to: doc_in30541.exe
Current Virus total detections 3/57* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/6f90a6b02b5de4bee197449581a10c8b897aa784e63579ae40e2d0597692a427/analysis/1440069970/
___
Fake 'order not avaliable' SPAM – doc malware
- http://myonlinesecurity.co.uk/we-are-sorry-but-the-product-youve-ordered-is-not-avaliable-now-fake-word-doc-malware/
20 Aug 2015 - "An email saying 'We are sorry but the product you’ve ordered is not avaliable now' with a subject of Order #y0CD3mxQizcBk88ovaw [random characters] coming from random names and email addresses with a zip attachment is another one from the current bot runs… The email looks like: Good afternoon,
We are sorry but the product you’ve ordered is not avaliable now.
Please fill up the attached form of refund and choose a gift as a token
of our apology for the inconvenience.
Order #fNcszeK2PW9J1rjN
Date sent: Thu, 20 Aug 2015 11:42:51 +0100
Mariam Olson Sr…
-Or- Good afternoon,
We are sorry but the product you’ve ordered is not avaliable now.
Please fill up the attached form of refund and choose a gift as a token
of our apology for the inconvenience.
Order #4y3Rs24VDxJ8BBW8
Date sent: Thu, 20 Aug 2015 11:45:02 +0100
Carolyn Raynor…
20 August 2015: Order Beier-Swaniawski_fNcszeK2PW9J1rjN.zip: Extracts to: order id283694136_Angus Ferry.exe
Current Virus total detections 2/57* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper word document instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/6e57b64a48eda1b367d41502dd4251521cb30799f3b371f236c806d97328f4bf/analysis/1440070000/
___
Fake 'Transport for London' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/08/malware-spam-email-from-transport-for.html
20 Aug 2015 - "This -fake- TfL spam comes with a malicious attachment: From "Transport for London" [noresponse@ cclondon .com]
Date Thu, 20 Aug 2015 17:04:26 +0530
Subject Email from Transport for London
Dear Customer
Please open the attached file(7887775.zip) to view correspondence from Transport
for London.
If the attachment is in PDF format you may need Adobe Acrobat Reader to read or download
this attachment. If you require Adobe Acrobat Reader this is available at no cost…
Thank you for contacting Transport for London.
Business Operations
Customer Service Representative…
The attachment name seems to vary, in the samples I have seen there is 7887775.zip, 0174458.zip and rather oddly [?var=partorderb].zip. From these I have recovered two malicious samples with a VirusTotal detection rate of 6/56* and 1/57**… Hybrid Analysis reports… show the malware connecting to various malicious and non-malicious IPs, but in particular we see a traffic pattern like this:
93.185.4.90 :12326/2008uk77/jI7tL6q34q/0/61-SP1/0/FDMBEFJBMKBEMM
93.185.4.90 :12326/2008uk77/jI7tL6q34q/41/5/42/FDMBEFJBMKBEMM
These GET requests are a characteristic of Upatre/Dyre. 93.185.4.90 is allocated to C2NET, Czech Republic and I strongly recommend that you -block- it."
* https://www.virustotal.com/en/file/6bd9680283424eb294a6a2b788bac911a15b47eb7f1a251cc6ad501df7e1acff/analysis/1440071767/
Fake 'ACH failed' SPAM – doc malware
- http://myonlinesecurity.co.uk/ach-failed-due-to-technical-error-the-electronic-payments-association-word-doc-malware/
20 Aug 2015 - "'ACH failed due to technical error' pretending to come from The Electronic Payments Association with a malicious word doc attachment is another one from the current bot runs… DO NOT follow the advice they give to enable macros or enable editing to see the content. Almost all of these malicious word documents appear to be blank or look something like this image when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21.png
This malicious word doc has what pretends to be a RSA encrypted security key and it wants you to enable editing to see the content. This is almost identical to this slightly older version with a different date. Once again DO NOT not enable editing or macros:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/RSA-key-protected-view.png
The email looks like: ACH PAYMENT REJECTED
The ACH Payment (ID: 49583071624518), recently initiated from your savings account (by you or any other person), was REJECTED by other financial institution.
Rejection Reason: See details in the attached report.
Payment Report: report_49583071624518.doc (Microsoft Word)
13450 Sunrise Valley Drive, Suite 100
Herndon, VA 20171
2014 NACHA – The Electronic Payments Association
20 August 2015 : report_49583071624518.doc - Current Virus total detections 16/57*
… connects to http ://luckytravelshop .info/wp-content/uploads/2015/05/sasa.txt which tells it to download a Dridex banking malware from http: //tadarokab .com/temp/recent.exe (VirusTotal**)… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/617e96e03ed78aae59ea049c5f856aead2f6cf3ba958aa38629503c6f51fca48/analysis/1440087068/
Fake 'ACH Payment' SPAM – PDF malware
- http://myonlinesecurity.co.uk/ach-payment-notification-logicease-solutions-inc-fake-pdf-malware/
20 Aug 2015 - "'ACH Payment Notification' pretending to come from ap_vendor_pay2@ bankofamerica .com with a zip attachment is another one from the current bot runs…
The email looks like: LOGICEASE SOLUTIONS INC Vendor:10288253 Pay Dt: 20150820 Pay Ref Num: 2000542353
Your invoice has been processed for payment by Bank of America Corporate Accounts Payable. The following items are included in this payment:
The net amount deposited to account number ending XXXX8014 designated by you is $1843.73
IMPORTANT: AVAILABILITY OF FUNDS FOR WITHDRAWAL IS SUBJECT TO POSTING BY RECEIVING BANK (USUALLY WITHIN THREE BUSINESS DAYS)
Please do not respond to this e-mail. Should you have questions, please contact the Purchasing, Payment & Reimbursement helpline at [removed]…
All these emails have random senders & companies, random phone numbers but the alleged sender matches the name in the body of the email and the name of the attachment.
21 August 2015: Bank-Reagan Bashirian DDS_(278) 789-4975_client-268119023428458.zip:
Extracts to: Bank Client992322638_West Jermainemouth.exe - Current Virus total detections: 2/57*.
This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/3f81ba9dd277971969eab270e00dfcd590a42b41d20ab8123a2369590ab58f06/analysis/1440154416/
___
Fake 'translator job' SCAMs
- http://myonlinesecurity.co.uk/real-translator-jobs-scam/
21 Aug 2015 - "We all see thousands of adverts and get loads of emails offering us jobs. This one caught my eye earlier:
'Earn Up To $315 A Day Translating Words'. Sent by Real Translator Jobs
The email reads like a godsend for somebody who speaks an extra language and needs a few $$ or ££ but has all the hallmarks of a scam/multi level marketing/pyramid scheme.
… If you follow the links to the website you see http ://www.realtranslatorjobs .com/ and a referrer link at the end of the url. I have blanked out the referrer link so he/she doesn’t get any income from the scam by following links from here:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/translator-jobs-website.png
… The first thing that jumps out at you is:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/home-sidebar-checklist2.jpg
… The only people who get rich and make a lot of money are the originators for this scam and the “affiliates” who promote it and get a commission on every sign up or click through to the website… it will cost you $68 to sign up but there is a special offer for today only for $34 dollars (save 50%!)… don’t fall for it and don’t waste your money. You won’t earn a thing…"
___
21 August 2015 : CRFC, Invoice 2018.pdf.zip: Extracts to: CRFC, Invoice 2018.pdf.exe
Current Virus total detections: 3/57* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/229e15d3a63ad632045395f7fee9c0193ccfdeba25c0d5205f382cb2ab57aa83/analysis/1440155507/
___
What is event.swupdateservice .net?
- http://blog.dynamoo.com/2015/08/what-hell-is-eventswupdateservicenet.html
21 Aug 2015 - "… I saw some mysterious outbound traffic to event.swupdateservice .net/event (138.91.189.124 / Microsoft, US). Googling around for the domain came up with some references to malware, but nothing very conclusive. The WHOIS details for the domain are -anonymised- (never a good sign), and the IP address is also used by event.ezwebservices .net which uses similarly -hidden- details. Team Cymru have an analysis* of what is being phoned home to this mystery server, and I found an existing Malwr analysis** referencing the alternate domain. I eventually found the mystery executable in C:\Users\[username]\AppData\Local\SoftUpdate\SoftUpdate.exe on the afflicted machine… The binary itself does not identify its creator. I found various references (such as in this report***) linking this software and the domains to Emaze .com (a "free" presentation tool)… Neither domain identifies itself through the WHOIS details, nor can I find any contact details on either site… I don't like sharing data with commercial operations who are not prepared to fully reveal their identity, and I personally recommend -blocking- traffic to:
visualbee .com: 168.62.20.37: https://www.virustotal.com/en/ip-address/168.62.20.37/information/
emaze .com: 54.83.51.169: https://www.virustotal.com/en/ip-address/54.83.51.169/information/ swupdateservice .net ezwebservices .net "
* https://totalhash.cymru.com/analysis/?a10211e1a1549147630704aa6cfd89b27bc51970
Fake Malwarebytes?…
- https://blog.malwarebytes.org/online-security/2015/08/exploring-an-mbam-for-windows-10-website/
Aug 21, 2015 - "Here at Malwarebytes, we offer support for a wide variety of Windows Operating Systems – from XP right up to Windows 10. The latter OS is the starting point for this blog post, with a website located at: malwarebytes-windows10(dot)com which seemed to offer up a “Windows 10 ready” version of Malwarebytes Anti-Malware:
This installer is -not- ours, so it’s clear that this is a download manager of some sort, and – one would hope – gave the downloader a copy of MBAM at the end of the process. However, the download kept breaking, so we couldn’t get any further than the initial installer splash…
Since we started looking into this, the site has also now apparently rolled down the shutters:
> https://blog.malwarebytes.org/wp-content/uploads/2015/08/mbam104.jpg
However, the EULA / Privacy Policy on the installer took us to a site located at
qpdownload(dot)com which also offered up a variety of programs including Adblock Plus and yet another MBAM:
> https://blog.malwarebytes.org/wp-content/uploads/2015/08/mbam105.jpg
… Users of Malwarebytes Anti-Malware will find we detect the “Download Manager” as PUP.Optional.InstallCore.A. Download sites can be cool, but it seems counter-intuitive to offer products designed to reduce advertisements / advertising software on your desktop alongside… adverts…"
Neutrino Campaign leveraging WordPress, Flash for CryptoWall
- http://research.zscaler.com/2015/08/neutrino-campaign-leveraging-wordpress.html
Aug 20, 2015 - "Neutrino Exploit Kit… in the past few days we've seen a massive uptick in the use of the kit. The cause for this uptick appears due to widespread WordPress site compromises… the image below illustrates the components involved in this campaign:
> https://4.bp.blogspot.com/-f2_q0ogBa9I/VdZGAFpgoHI/AAAAAAAAAYU/s7NvxOgAHZs/s1600/WordPress_Neutrino_nexus.PNG
… there are multiple recent changes in the Neutrino code, some that are normally characteristics of Angler Exploit Kit, but others that remain unique to Neutrino… The goal of this campaign is to completely and fully compromise the site, which includes adding a webshell, harvesting credentials, and finally injecting an iframe that loads a Neutrino landing page… the primary IP for the observed Neutrino landing pages is '185.44.105.7' which is owned by VPS2DAY .com. Many of the domains pointing to that IP utilize 'xyz', 'ga', 'gq', and 'ml' TLDs. Taking a look at the whois data for some of these domains, a common attribute seems to be the name 'Max Vlapet' for .XYZ domains… This campaign also reconfirms that Neutrino Exploit Kit activity is on the rise and is still a major player in the exploit kit arena…"
- http://it.slashdot.org/story/15/08/22/030246/wordpress-hacks-behind-surging-neutrino-ek-traffic
Aug 22, 2015
Fake 'Message from scanner' SPAM – PDF malware
- http://myonlinesecurity.co.uk/message-from-scanner-fake-pdf-malware/
24 Aug 2015 - "'Message from scanner' pretending to come from scanner.coventrycitycentre@ brianholt .co.uk with a zip attachment but a completely -empty/blank- body of the email is another one from the current bot runs…
24 August 2015: Sscanner15081208190.zip: Extracts to: Sscanner15081208190.exe
Current Virus total detections: 3/57* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/891f5c4ca2a835e32b773b6179b21e9737000a862bce81229fbc8b8930992e38/analysis/1440408248/
- http://blog.dynamoo.com/2015/08/malware-spam-message-from-scanner.html
24 Aug 2015 - "… malicious executable Sscanner15081208190.exe embedded into the attachment Sscanner15081208190.zip . This executable has a detection rate of just 5/54*. The Hybrid Analysis report** shows the malware POSTing to:
smboy .su/mu/tasks.php
.SU (Soviet Union) domains are almost always bad news. If you can block them on your web filter then I recommend that you do so. This particular site is hosted on 95.172.146.73 (RTComm-Sibir, Russia). The network range of 95.172.146.0/23 does seem to contain some legitimate Russian-language sites, but you might want to -block- the whole range to be on the safe side. The payload is unknown, but typically malware like this will drop either the Dyre banking trojan or some sort of ransomware."
* https://www.virustotal.com/en/file/891f5c4ca2a835e32b773b6179b21e9737000a862bce81229fbc8b8930992e38/analysis/1440414098/
Fake 'Visa Card' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/08/malware-spam-visa-card-aug-2015.html
25 Aug 2015 - "This -fake- financial spam does not come from Ellesemere Engineering but is in fact a simple forgery with a malicious attachment: From [david@ ellesmere .engineering]
To "'Sharon Howarth'" [sharon@ ellesmere .engineering]
Date Tue, 25 Aug 2015 09:52:47 +0200
Subject Visa Card Aug 2015
Visa Card payments this month
—
This email has been checked for viruses…
I have seen three different samples with different download locations:
https ://www.sugarsync .com/pf/D3941255_827_052066225?directDownload=true
https ://www.sugarsync .com/pf/D160756_82_6104120627?directDownload=true
https ://www.sugarsync .com/pf/D2694666_265_638165437?directDownload=true
In each case, the binary downloaded is identical and has a VirusTotal detection rate of 3/55*. Analysis is pending, but the payload appears to be the Dyre banking trojan.
UPDATE: The Hybrid Analysis report** shows traffic to 197.149.90.166 (Cobranet, Nigeria) which I recommend you block."
* https://www.virustotal.com/en/file/8f1d2ccdce1e260b4ec648a71210250eedaa8af5c9d8a7e64366343d9e384a4f/analysis/1440506327/
Fake 'Invoice 26949' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/08/malware-spam-invoice-26949-from-i-spi.html
25 Aug 2015 - "My spam traps did not collect the body text from this message, so all I have is headers. However, this -fake- financial email is not from i-Spi Ltd and is instead a simple forgery with a malicious attachment: From [sales@ ispitrade .com]
Date Tue, 25 Aug 2015 20:37:09 +0800
Subject Invoice 26949 from I - SPI Ltd
Attached is a file Inv_26949_from_I__SPI_Ltd_7888.doc which actually comes in several different versions… which contains a malicious macro… that downloads an executable from one of the following locations:
http ://landrevie.g.free .fr/45gf3/7uf3ref.exe
http ://e-projekt.ns1.internetdsl .pl/45gf3/7uf3ref.exe
http ://nathalieetalain.free .fr/45gf3/7uf3ref.exe
http ://claudio.locatelli.free .fr/45gf3/7uf3ref.exe
http ://spitlame.free .fr/45gf3/7uf3ref.exe
http ://nathalieetalain.free .fr/45gf3/7uf3ref.exe
This Hybrid Analysis report* shows network traffic to: 91.239.232.9 (Hostpro Ltd, Ukraine)
This is the same bad IP as found in this earlier spam run**, I recommend that you block it. The payload here is almost definitely the Dridex banking trojan."
* https://www.hybrid-analysis.com/sample/5e4b69e8ce31c8cf51cc6d5b49651bec9e239b7616f81744b656b7228a63a065?environmentId=1
Browsefox variant High Stairs - browser hijackers
- https://blog.malwarebytes.org/security-threat/2015/08/browsefox-variant-high-stairs/
Aug 25, 2015 - "Browsefox aka Sambreel aka Yontoo is a family of browser hijackers. When advertised they promise to “customize and enhance your interaction with the websites you visit”, but in reality they are almost never a users choice install. They come -bundled- with other software at many major download sites and at best you will see this screen when the installation starts:
> https://blog.malwarebytes.org/wp-content/uploads/2015/08/main1.png
High Stairs is one of the latest additions to this family. It is being offered as a browser extension -without- making clear what it does for the user. If you want to have a look at the EULA and Privacy Policy you will have to visit their website:
> https://blog.malwarebytes.org/wp-content/uploads/2015/08/EULA.png
… The EULA clearly states that it allows the “Software” to use -any- means imaginable to deliver advertisements and that it will collect your data. The Privacy Policy lets you know that they will use, share and sell those data to any and all parent, subsidiary or affiliate companies. Bottom line, as long as it brings in cash. Browser hijackers of this family are VM aware, meaning they will not do a full install if they detect they are run on a Virtual Machine. Sometimes the files are downloaded and put in place, but the extensions are not installed and enabled. The -hijackers- from this family do provide browser extensions for IE, Firefox, Chrome and Opera (and probably more)… invisible iframes can be used to deliver anything and everything to your computer, ranging from advertisements (which is very likely in this case) to (in theory) exploit kits. In theory in this case means, that we haven’t seen any exploit kits being delivered through the advertisements these PUPs deliver, but if the PUP has a vulnerability or their network is compromised a third party could use this in the same manner as has been done with malvertisements on legitimate sites. This browser hijacker is relatively easy to remove. Other variants have been known to install services as well, making them a bit harder to tackle. Unfortunately “High Stairs” is not alone. We see a new Sanbreel variant at least a few times every week. The installer and the installed files are all detected as 'PUP.Optional.HighStairs.A'. Logs, more screenshots and removal instructions for “High Stairs” can be found on our forums*…"
* https://forums.malwarebytes.org/index.php?/topic/171926-removal-instructions-for-high-stairs/
Fake 'Scanned image - MX-2600N' SPAM – doc/xls malware
- http://myonlinesecurity.co.uk/scanned-image-from-mx-2600n-word-doc-macro-malware/
26 Aug 2015 - "'Scanned image from MX-2600N' pretending to come from noreply@ your email domain with a malicious word doc or Excel XLS spreadsheet attachment is another one from the current bot runs… DO NOT follow the advice they give to enable macros or enable editing to see the content. Almost all of these malicious word documents appear to be blank or look something like this image when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21.png
The email looks like: Reply to: noreply@ securityandprivacy .co.uk
Device Name: Not Set
Device Model: MX-2600N
Location: Not Set
File Format: DOC MMR(G4)
Resolution: 200dpi x 200dpi
Attached file is scanned image in DOC format.
Use Microsoft(R)Word(R) of Microsoft Systems Incorporated to view the document.
26 August 2015: [removed].uk_20150826_181106.doc
Current Virus total detections 7/57*: Downloads Dridex banking malware from one of these locations:
detocoffee.ojiji .net/45ygege/097uj.exe (virus Total**)
students.johnbryce .co.il/nagare/45ygege/097uj.exe
groupedanso .fr/45ygege/097uj.exe
asterixpr.republika .pl/45ygege/097uj.exe
fotolagi .com/45ygege/097uj.exe
… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/38736bb58af7e8a640656a661129d0150dd3a46c996f9fb91a6586108333c17d/analysis/1440582748/
- http://blog.dynamoo.com/2015/08/malware-spam-scanned-image-from-mx.html
26 Aug 2015 - "… The email appears to come from the victim's own domain, but it does not. The "From" address on email is extremely easy to forge. So far I have seen three different malicious attachments, each one in the format noreply@ victimdomain.com_20150826_181106.doc with detection rates of around 7/56 [1] [2] [3] containing one of three malicious macros… which attempt to download a malicious component from one of the following locations:
http ://fotolagi .com/45ygege/097uj.exe
http ://asterixpr.republika .pl/45ygege/097uj.exe
http ://detocoffee.ojiji .net/45ygege/097uj.exe
This malicious binary currently has a VirusTotal detection rate of just 2/54. Automated analysis… shows network traffic to 91.239.232.9 (Hostpro Ltd, Ukraine) which has been used in serveral attacks recently. The payload is almost definitely the Dridex banking trojan."
1] https://www.virustotal.com/en/file/7bd4d8d48a4e64ee8bdd8814c805a8a5ff69ad0fe8200b86a10bfbe81e193b9d/analysis/1440583485/
Fake 'invoice A4545945' SPAM - PDF malware
- http://myonlinesecurity.co.uk/screwfix-copy-of-invoice-a4545945-please-find-your-invoice-attached-fake-pdf-malware/
26 Aug 2015 - "'Copy of invoice A4545945. Please find your invoice attached' pretending to come from Screwfix Direct with a zip attachment is another one from the current bot runs… The email looks like: Dear Customer
Thank you for shopping at Screwfix.
As requested please find attached a copy of invoice: A4545945.
You will require a PDF file reader in order to view and print the invoice. Should your invoice not be attached please email invoice@ screwfix .com ensuring that you quote your order reference.
Please do not reply to this e-mail.
If you have any queries, please quote the Invoice Number: A4545945, when contacting us:
Phone: 0500 41 41 41 (03330 112 320 from a mobile) UK based Contact Centre
E-mail: online@ screwfix .com
Write to: Screwfix, Trade House, Mead Avenue, Yeovil, BA88 8RT …
26 August 2015: Invoice_A3176864.zip: Extracts to: Invoice.scr
Current Virus total detections 2/57* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/a3bc75083b29d70f6c156d3f987bbe654b56f58708755528ecc7eeab13eee30a/analysis/1440580919/
___
Fake 'Invoices from UBM' SPAM - PDF malware
- http://myonlinesecurity.co.uk/your-invoices-from-ubm-fake-pdf-malware-2/
26 Aug 2015 - "'Your Invoices from UBM' pretending to come form UBM (UK) Limited with a zip attachment is another one from the current bot runs… The email looks like: Dear Customer,
Please find attached your invoice(s) from UBM. If you have any queries regarding the invoice, payment or service delivered please don’t hesitate to contact us on the details below.
Regards,
UBM Receivables Team.
Tel : +44 [removed] (21627)
Email : bogumila.murzyn@ ubm .com
Fax :
****PLEASE DO NOT REPLY TO THE EMAIL ADDRESS ubm@ ubm .com AS IT IS NOT MONITORED**** …
26 August 2015:65550757_Invoices_26-AUG-2015.zip:
Extracts to: 65550757_Invoices_26-AUG-2015.scr … which is the -same- Upatre malware that is described in today’s other malspam run with Zip attachments*. This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* http://myonlinesecurity.co.uk/screwfix-copy-of-invoice-a4545945-please-find-your-invoice-attached-fake-pdf-malware/
___
Fake 'new fax delivery svc' – PDF malware
- http://myonlinesecurity.co.uk/we-are-a-new-fax-delivery-service-fake-pdf-malware/
26 Aug 2015 - "A series of emails saying 'We are a new fax delivery service' with the subject reading Fax #[ random characters] from [random name] with a zip attachment is another one from the current bot runs… The email looks like: You have a fax.
Data sent: Wed, 26 Aug 2015 14:08:41 +0000
TO: [redacted]
*********************************
We are a new fax delivery service – Walker-Gerlach.
Our company develops rapidly and services remain fastest and open to everyone.
As our slogan goes: “Fast. Cheap. Best quality.”
*********************************
-Or- You have a fax.
Data sent: Wed, 26 Aug 2015 14:06:21 +0000
TO: [REDACTED]
*********************************
We are a new fax delivery service – Hirthe-Bayer.
Our company develops rapidly and services remain fastest and open to everyone.
As our slogan goes: “Fast. Cheap. Best quality.”
*********************************
26 August 2015: fax_jxJ3O9_Walker-Gerlach_Colton Leffler.zip
Extracts to: Invoice East Marta.exe
Current Virus total detections 2/57* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/87a540174bab81d657b678ef03872a70113db3989609d290776773e9f8f0d62e/analysis/1440598735/
- http://blog.dynamoo.com/2015/08/fake-fax-spam-spoofs-multiple-senders.html
26 Aug 2015 - "… - fake- fax spam comes from random senders - company names and attachment names vary from spam to spam… Attached is a ZIP file combining various elements from the spam (for example, in this case it was fax_AhnxlQ8_Heaney, Vandervort and Hilll_Donny Kub.zip). This contains a malicious executable (e.g. Invoice Lake Janeview.exe) which currently has a 2/56* detection rate at VirusTotal. The Hybrid Analysis report** shows it phoning home to:
197.149.90.166 /260822U/Yd1D3h1R87/0/61-SP1/0/FDMBEFJBMKBEMM
197.149.90.166 /260822U/Yd1D3h1R87/41/5/42/FDMBEFJBMKBEMM
This pattern marks the malware out as being Upatre/Dyre. 197.149.90.166 is an IP address belonging to Cobranet in Nigeria which was also used in a similar attack yesterday.*** "
* https://www.virustotal.com/en/file/93b1f8dbe6a531475b90f1d426e918790960f924180ec3c172f037342f00a4d1/analysis/1440599515/
Angler Exploit Kit strikes MSN.com via Malvertising Campaign
- https://blog.malwarebytes.org/malvertising-2/2015/08/angler-exploit-kit-strikes-on-msn-com-via-malvertising-campaign/
Aug 27, 2015 - "The same ad network – AdSpirit .de – which was recently abused in malicious advertising attacks against a slew of top media sites was caught serving malvertising on MSN .com. This is the work of the -same- threat actors that were behind the Yahoo! malvertising. The incident occurred when people who where simply browsing MSN’s news, lifestyle or other portals were served with a malicious advertisement that silently loaded the Angler exploit kit and attempted to infect their computers. The ad request came from AppNexus, which loaded the booby-trapped advert from AdSpirit and the subsequent malvertising chain.
Infection chain:
msn .com/en-us/news/politics/dozens-of-clinton-emails-were-classified-from-the-start-us-rules-suggest/ar-BBlXPkl?ocid=iehp (publisher)
lax1.ib.adnxs .com/{redacted} (AppNexus Ad network)
pub.adspirit .de/adframe.php?pid=7&ord=[timestamp]prdclick_0 (AdSpirit Ad network)
trkp-a1009.rhcloud .com/?tr28-0a22 (OpenShift redhat Redirection)
fox23tv .com/?cn67CuYcDcbvV (Same ad but with redirection to malicious URL)
abbezcqerrd.irica.wieshrealclimate .com (iframe to exploit kit)
hapme.viwahcvonline .com (Angler EK landing page)
> https://blog.malwarebytes.org/wp-content/uploads/2015/08/redir_flow.png
This time, rogue actors are leveraging RedHat’s cloud platform, rhcloud .com to perform multiple -redirections- to the Angler exploit kit (in the previous attack they were using Microsoft’s Azure). While we did not collect the malware payload associated with this campaign, we believe it is either Ad fraud or ransomware, Angler’s trademark. Angler has been acting up strange lately, for instance last week it fell out of favour briefly for the Neutrino EK when compromised sites decided to redirect to the latter. Following our report, AppNexus -deactivated- the creative in question and said they were investigating this issue in greater depth…"
Fake 'resume' SPAM leads to Cryptowall
- http://blog.dynamoo.com/2015/08/malware-spam-reresume-leads-to.html
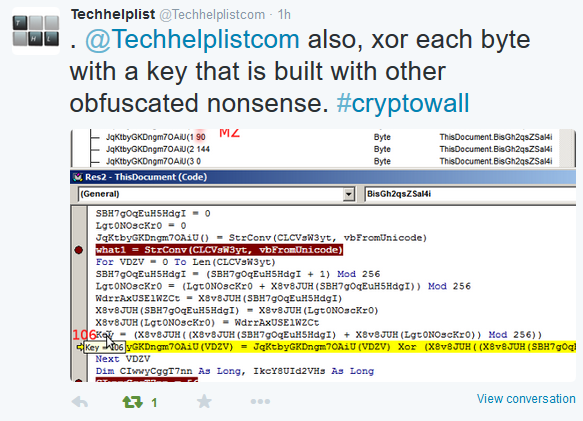
26 Aug 2015 at 22:48 - "This -fake- resume spam has a malicious payload. I got part way through decrypting it to discover that @Techhelplistcom had done all the hard bits which saved me some effort. This particular spam delivers a version of the Cryptowall ransomware. In the only sample I saw, the spam looks like this: From: emmetrutzmoser@ yahoo .com
To:
Date: 26 August 2015 at 23:29
Subject: RE:resume
Signed by: yahoo .com
Hi! my name is Janet Ronald it is my resume!Awaiting your prompt reply
Best regards
Janet Ronald
Fake 'Attachement' SPAM – doc/xls malware
- http://myonlinesecurity.co.uk/attachement-word-doc-or-excel-xls-spreadsheet-malware/
27 Aug 2015 - "A -blank- email with the subject of 'Attachement' pretending to come from your own email address with a malicious word doc or Excel XLS spreadsheet attachment is another one from the current bot runs… DO NOT follow the advice they give to enable macros or enable editing to see the content. Almost all of these malicious word documents appear to be blank or look something like this image when opened in protected view mode, which should be the default in Office 2010, 2013 and 365:
> http://myonlinesecurity.co.uk/wp-content/uploads/2015/08/protected-view-macros_21.png
The email has a totally empty-blank body and just an XLS Excel spreadsheet attachment:
Fake 'Payslip' SPAM - PDF malware
- http://myonlinesecurity.co.uk/payslip-for-period-end-date-27082015-fake-pdf-malware/
27 Aug 2015 - "'Payslip for period end date 27/08/2015' pretending to come from noreply@ fermanagh. gov.uk with a zip attachment is another one from the current bot runs… The email looks like: Dear administrator
Please find attached your payslip for period end 27/08/2015
Payroll Section …
Some emails have arrived malformed-and-damaged and look like: This is a multi-part message in MIME format.
——————=_Next_25232_7367279505.4684370133215
Content-Type: text/plain; charset=ISO-8859-1; format=flowed
Content-Transfer-Encoding: 7bit
Dear ae48852507a
Please find attached your payslip for period end 27/08/2015
Payroll Section …
27 August 2015: payslip.zip: Extracts to: payslip.scr
Current Virus total detections 3/56* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/6bfc6e82b5a288ffa91a1cab9dae06c968b3bc36d5fd07d2557f517b79465298/analysis/
Fake 'Girls List' Spam …
- https://blog.malwarebytes.org/online-security/2015/08/girls-list-spam-landing-in-mailboxes/
Aug 27, 2015 - "… spammers are changing up their dating site spam tactics a little bit in the wake of the continued Ashley Madison fallout, with the below curious missives landing in spamtraps over the last day or so:
> https://blog.malwarebytes.org/wp-content/uploads/2015/08/crowdspam1.jpg
… emails are identical, and read as follows:
> https://blog.malwarebytes.org/wp-content/uploads/2015/08/crowdspam2.jpg
… well, they -would- read as follows if they had any text in them to read. The emails are entirely -blank- instead offering up two attachments called “girls_list”. A “girl list” would seem to conjure up visions of swiped data and things you’re not supposed to have access to; as it turns out, opening up the .HTML attachment -redirects- you in a browser to a -porn- dating site which splashes… many nude photos around the screen… These emails are already caught by Gmail as spam, but other providers may -not- be flagging them yet. While I’m sure there are lots of fun things you can do with a list, allowing yourself to be redirected-to-porno-spam is probably not one of them and you should avoid these mails. With websites and services jumping on the AM data bandwagon*, it’s clear that anything involving dating and lists is going to be a hot topic for some time to come. Don’t fall for it."
* http://www.troyhunt.com/2015/08/ashley-madison-search-sites-like.html
24 Aug 2015 - "… harvesting email addresses and spamming searched victims…"
___
Malvertising campaigns increase 325%
- http://net-security.org/malware_news.php?id=3088
26.08.2015 - "Cyphort* investigated the practices used by cyber criminals to inject malicious advertisements into legitimate online advertising networks. Researchers found that malvertising campaigns carried out by hackers increased 325 percent in the past year… The problem of malvertising isn’t going away and cyber criminals will continue finding ways to monetize their attacks. According to the Association of National Advertisers, ad-fraud will cost global advertisers more than $6 billion in 2015…"
* http://www.cyphort.com/category/malvertising/
Dropbox Spam
- http://threattrack.tumblr.com/post/127784805983/dropbox-spam
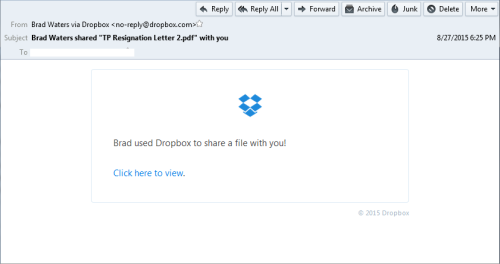
Aug 28, 2015 - "Subjects Seen: Brad Waters shared “TP Resignation Letter 2.pdf” with you
Reed Contreras shared “TP Resignation Letter 2.pdf” with you
Typical e-mail details: Brad used Dropbox to share a file with you!
Click here to view.
Malicious URLs:
newyearpartyistanbul .com/securestorage/getdocument.html
Malicious File Name and MD5:
TP Resignation Letter 2.scr (90a60d95b2f0db6722755e535e854e82)
Fake 'FedEx delivery problem' SPAM – JS malware
- http://myonlinesecurity.co.uk/fedex-shipment-delivery-problem-0000639746-js-malware/
31 Aug 2015 - "An email with the subject of 'Shipment delivery problem #0000639746' pretending to come from FedEx… with a zip attachment that extracts to a JS file is another one from the current bot runs…The content of the email says : Dear Customer,
Your parcel has arrived at August 28. Courier was unable to deliver the parcel to you.
Please, open email attachment to print shipment label.
Yours faithfully,
Jeffrey Kendall,
Operation Agent.
31 August 2015: FedEx_ID_0000639746.zip: Extracts to: FedEx_ID_0000639746.doc.js
Current Virus total detections 17/57*. I am not getting any payload via the automatic analysers so far although Wepawet indicates it connects to one of these sites:
selmaryachtmarket .com
riggst .com
harmacrebar .com …
Update: managed to get the malware 92305548.exe (VirusTotal**) and ba892f004ed[1].gif (VirusTotal***)
Fake 'Private message' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/09/malware-spam-private-message.html
1 Sep 2015 - "This spam comes with a malicious attachment: From: Adrien Abbott
Date: 1 September 2015 at 12:34
Subject: Private message notification 41447
You've received a private message. Please open the attached to view it.
Adrien Abbott
Chief Tactics Executive
home: [removed]
work: [removed]
twitter: @nicole
skype: nicole
messenger: nicole
I have only seen a single sample of this spam, and the attachment was not formatted properly making it harmless, however other -variants- could be more dangerous. If properly decoded, the attachment should have been named 89867740_Torphy and Sons_Adrien Abbott.zip containing a malicious executable jodie_okonofficia-quo.exe. This executable has a VirusTotal detection rate of just 2/56*, the Hybrid Analysis report** shows network activity consistent with this being Upatre dropping the Dyre banking trojan, with communications made to: 197.149.90.166 (Cobranet, Nigeria)
..which is an IP that has been used several times for this sort of attack recently and is worth blocking. The report details other IP addresses too, but this seems to be the key one to block or monitor."
* https://www.virustotal.com/en/file/8092a0200a1fbc9e1917aa58483af308120f22fe750e83ba944e0adfe7d51bc5/analysis/1441111004/
- http://myonlinesecurity.co.uk/private-message-notification-fake-pdf-malware/
1 Sep 2015 - "… random names and email addresses from with a zip attachment is another one from the current bot runs… -hundreds- of other names. All details in the body of the email are random. The alleged sender matches the name in the body of the email and the attachment contains those names as well…
1 September 2015: 27121259_Zemlak-Rodriguez_Hans Mohr.zip: Extracts to: velmasuscipit.incidunt.exe
Current Virus total detections 1/57*. This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/27c1a31c9896a8f9fd6e62265934dcba3d6842c7b45932d1dad77ebe6701a73b/analysis/1441109597/
___
Fake 'Complaint notice' SPAM – PDF malware
- http://myonlinesecurity.co.uk/complaint-notice-fake-pdf-malware/
1 Sep 2015 - "Following on from the earlier malspam run* we now have a series of emails with the subject of 'Complaint notice' [random numbers] also coming from random names and email addresses with a zip attachment is another one from the current bot runs…
* http://myonlinesecurity.co.uk/private-message-notification-fake-pdf-malware/
The content of the email says : This is a complaint notification. Full details attached. Please notify us within 24 hours with taken actions.
Martine McDermott
Lead Metrics Designer
T: [removed]
F: [removed]
-Or- This is a complaint notification. Full details attached. Please notify us within 24 hours with taken actions.
Jordane Emard
Internal Intranet Designer
T: [removed]
F: [removed]
And -hundreds- of other names. All details in the body of the email are random. The alleged sender matches the name in the body of the email and the attachment contains those names as well…
1 September 2015: 8961683689_Bahringer-Jacobs_Martine McDermott.zip:
Extracts to: alekvoluptatibus-at.exe
Current Virus total detections 2/57*. This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/09873fd725eb7a1d7ea7914afc41c854627179b7371607251923fe0f7c5b17e5/analysis/1441122287/
- http://blog.dynamoo.com/2015/09/malware-spam-complaint-of-your-internet.html
1 Sep 2015 - "This spam comes with a malicious attachment: From: Margret Kuhic
Date: 1 September 2015 at 16:10
Subject: Complaint of your Internet activity
This is a complaint notification. Full details attached. Please notify us within 24 hours with taken actions.
Margret Kuhic
Dynamic Communications Agent
T: [removed]
F: [removed]
All the sames I have seen have a corrupt attachment which is Base 64 encoded, it is possible that other people might receive a -valid- attachment though. The attachment was meant to be 723296788_Marquardt-Bailey_Margret Kuhic.zip containing the malicious executable june_stiedemannmolestiae.et.exe which has a VirusTotal detection rate of 2/56*. This Hybrid Analysis report** shows it to be just another variant of Update/Dyre with the same characteristics as the malspam seen earlier today***, sending traffic to an IP that I suggest you -block- or monitor: 197.149.90.166 (Cobranet, Nigeria)
Some other subjects spotted include:
Complaint notification 50646
Infringement of your Internet activity
Infringement notification 51494 "
* https://www.virustotal.com/en/file/17795e0988bd3a5326ef445c5d35a2e30c8b5bbad0e90d3242573f16e4e52e17/analysis/1441121661/
Fake 'ACH rejection' SPAM – PDF malware
- http://myonlinesecurity.co.uk/ach-rejection-due-to-system-malfunctioning-fake-pdf-malware/
1 Sep 2015 - "An email with the subject of 'ACH rejection due to system malfunctioning' pretending to come from The ACH Network with a link to download a zip attachment is another one from the current bot runs… The content of the email says : ACH PAYMENT CANCELLED
The ACH Transaction (ID: 86440585067071), recently sent from your savings account (by you or any other person), was CANCELLED by other financial institution.
Rejection Reason: See details in the report below
Transaction Report: New Banking Details.pdf (Adobe Reader PDF)
13450 Sunrise Valley Drive, Suite 100
Herndon, VA 20171
2014 NACHA – The Electronic Payments Association
The link in the email sends you to http ://cheenichetty .com/securestorage/get_document.html where a zip file is downloaded automatically and you are -bounced- immediately to Dropbox and you think you were on Dropbox the whole time. These 'NACHA/ACH/The Electronic Payments Association payment cancelled' or 'payment rejected' emails are a persistent method of trying to deliver malware to your computer…
1 September 2015: New Banking Details.zip: Extracts to: New Banking Details.scr
Current Virus total detections 6/56* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/58e9c8f22f7d06cff615fb95ecdc201d902bf15c078ca2c9130e3a8d1926439f/analysis/1441127390/
Your Worst Day In IT
- http://www.darkreading.com/partner-perspectives/tenable/your-worst-day-in-it/a/d-id/1321999
9/1/2015 - "At VMworld 2015 in San Francisco, I roamed the floor with a camera asking attendees, "What was your worst day in IT?" When we initially came up with this question, we thought everyone's worst day would have something to do with a security breach or malware. Turns out that hardware failures and human error are far more common. As much as we talk about threat protection, what we really need to watch out for is our equipment and ourselves."