Something evil on 92.63.88.0/24 (MWTV, Latvia)
- http://blog.dynamoo.com/2015/02/something-evil-on-926388024-mwtv-latvia.html
17 Feb 2015 - "I've been tracking -Dridex- for some time, and I keep seeing IPs for MWTV in Latvia cropping up. So far I have seen:
92.63.88.87
92.63.88.97
[removed]
[removed]
[removed]
[removed]
I'm not sure how widely this spreads through the MWTV network, but I would certainly recommend -blocking- 92.63.88.0/24 on your network perimeter." ___
Fake 'Customer statement' SPAM - doc malware
- http://myonlinesecurity.co.uk/customer-statement-0001031389-02052015-word-doc-malware/
17 Feb 2015 - "'Customer statement 0001031389 as on 02/05/2015' pretending to come from [removed] and being addressed to minutemanpresschicago@ comcast .net and sent to you via a bcc with a malicious word doc attachment is another one from the current bot runs… All these emails have random invoice numbers in the subject line and the invoice number matches the attachment name & number in most cases so far today…
Fake 'Service Suspension' SPAM - xls malware
- http://myonlinesecurity.co.uk/service-suspension-notification-idfecc254778-excel-xls-malware/
17 Feb 2015 - "'Service Suspension Notification [ID:FECC254778] (random numbers)' with a malicious word excel XLS attachment is another one from the current bot runs… All these emails have random numbers in the subject line and the attachment name…
Fake 'Unpaid invoice' SPAM – XLS malware
- http://myonlinesecurity.co.uk/unpaid-invoice-excel-xls-malware/
17 Feb 2015 - "'Unpaid invoice [ID:AFCBF43812] ( random numbers)' with a malicious Excel XLS attachment is another one from the current bot runs… All these emails have random invoice numbers in the subject line and the invoice number matches the attachment name & number in most cases so far today…All these emails have random invoice numbers in the subject line and the invoice number matches the attachment name & number in most cases so far today. The email has a totally -blank- body…
- http://blog.dynamoo.com/2015/02/malware-spam-unpaid-invoice-id9876543210.html
17 Feb 2015
"… fake invoice comes with no body text, a random ID: in the subject and a randomly-named malicious Excel attachment…
Recommended blocklist: 92.63.88.97
92.63.88.87
78.129.153.27
62.76.43.194
46.4.232.206
136.243.237.194
74.208.68.243 "
___
FedEx Notification Spam
- http://threattrack.tumblr.com/post/111277461208/fedex-notification-spam
Feb 17, 2015 - "Subjects Seen Postal Notification Service
Typical e-mail details: Dear Customer,
You parcel arrived, read the account in the attachment.
Consignment: #149700366
Submit time: Tue, 17 Feb 2015 11:11:55 +0000
Malicious File Name and MD5:
invoice.exe (6E3EF30E49B69E8AA6F487816A4AC9F9)
Equation Group IP ranges and domains
- http://blog.dynamoo.com/2015/02/an-analysis-of-reported-equation-group.html
17 Feb 2915 - "There has been a lot of buzz this morning about "The Equation Group", a possible state actor involved in placing malware on hard disks…" (Good read, but WAY too many IPs to be listed here - see the dynamoo URL above.)
Multiple SPAM emails using malicious XLS or XLSM attachment
- http://blog.dynamoo.com/2015/02/multiple-spam-emails-using-malicious.html
18 Feb 2015 - "I'm seeing multiple spam runs (probably pushing the Dridex banking trojan) with no-body-text, various subjects and either an XLS or XLSM attachment. Example subjects include:
Copy [ID:15E376774] attaced
RE: Requests documentation [458C28133]
Request error [C3843]
Request error [FDF396530]
Requests documentation [242B035667]
Attachments look something similar to this:
15E376774.xlsm
242B035667.xlsm
458C28133.xls
C3843.xls
FDF396530.xlsm
The XLS and XLSM files are different structurally.. the XLSM files are basically an Office 2007 ZIP archive of all the data components, the XLS files are an old school Office 2003 file. Nevertheless, they contain a macro with 23 components to make it harder to analyse, although the important modules are Module 11 which contains the text string to decrypt, and Module 14 which contains the decryption function itself. Almost everything else is irrelevant. Once the string is decrypted, it becomes fairly obvious what it going on. So far, there appear to be four strings with different download locations… we can see a file dxzq.jpg being downloaded which is actually a CAB file (JIOiodfhioIH.cab) which is then expanded to JIOiodfhioIH.exe and then run. For information, these IPs are hosted by:
5.196.243.7 (OVH, Ireland)
46.30.42.151 (Eurobtye LLC, Russia)
176.31.28.235 (OVH, France)
92.63.88.63 (MWTV, Latvia)
This executable has a detection rate of 4/56. Automated analysis… shows attempted network connections to:
82.151.131.129 (Doruknet, Turkey)
121.50.43.175 (Tsukaeru.net, Japan)
74.208.68.243 (1&1, US)
The Malwr report shows that it also drops a DLL with a detection rate of just 1/56*.
Recommended blocklist: 82.151.131.129
121.50.43.175
74.208.68.243
5.196.243.7
46.30.42.151
176.31.28.235
92.63.88.63 …"
* https://www.virustotal.com/en/file/2884d4315258fab8917731b996b7536470558f7f61e969be469e1f874e50d9d5/analysis/1424263599/
Fake 'Esso E-bill' SPAM – doc malware
- http://blog.dynamoo.com/2015/02/malware-spam-uk-fuels-esso-e-bill.html
18 Feb 2015 - "This fake invoice is a -forgery- with a malicious attachment: From: invoices@ ebillinvoice .com
Date: 18 February 2015 at 09:01
Subject: UK Fuels Esso E-bill
Customer No : 90714
Email address : [redacted]
Attached file name : 36890_06_2015.DOC (ZIP)
Dear Customer
Please find attached your invoice for Week 06 2015.
If you have any queries regarding your e-bill you can contact us at invoices@ ebillinvoice .com.
Alternatively you can log on to your account at www .velocitycardmanagement .com to review your transactions and manage your account online.
Yours sincerely
Customer Services
UK Fuels…
I have only seen a single sample of this, with a ZIP file 36890_06_2015.zip attached, which in turn contains a document 36890_06_2015.doc. This document contains a malicious macro, and is exactly the same as the one used in this campaign* leading to the Dridex banking trojan."
* http://blog.dynamoo.com/2015/02/this-fake-financial-spam-has-malicious.html
Fake 'auto insurance' SPAM - doc malware
- http://blog.dynamoo.com/2015/02/this-fake-financial-spam-has-malicious.html
18 Feb 2015 - "This -fake- financial spam has a malicious attachment: From: Dan Bigelow [dan@ express-insurance .net]
Date: 18 February 2015 at 09:18
Subject: Auto insurance apps and documents
Hello ,
Please print “All” attached forms and sign and initial where I highlighted.
Scan and email back to me or fax to me at [removed].
Sincerely,
Dan Bigelow
Referrals are important to us. If you know anyone who would benefit from our services, please contact me.
We would appreciate the opportunity to work with them.
2636 West State Rd 434 # 112
Longwood, Fl 32779 …
This spam does -not- actually come from Express Insurance nor have their systems or data been compromised in any way. Instead this is a simple -forgery- with a malicious Word document attached. There are actually at least two different versions of the document with zero detections [1] [2]… Despite the difference, both seem to download from:
http ://ecv.bookingonline .it/js/bin.exe
The download file is saved as %TEMP%\FfdgF.exe and has a VirusTotal detection rate of 3/57*. Automated analysis tools… indicate that it attempts to phone home to:
83.169.4.178 (Hosteurope, Germany)
[removed] (World Internetwork Corporation, Thailand)
[removed] (Microtech Tel, US)
This probably drops a Dridex DLL, however the Malwr analysis appears to have malfunctioned and I don't have a sample.
Recommended blocklist: 83.169.4.178
202.44.54.5
66.110.179.66 "
1] https://www.virustotal.com/en/file/7c1c37569f1e6a7128c832cb54fb5505b431a2f70101ebd68673a9a2ac73903a/analysis/1424256101/
Fake 'Statement' SPAM – XLS malware
- http://myonlinesecurity.co.uk/maria-wilson-securigroup-statement-excel-xls-malware/
19 Feb 2015 - "'Maria Wilson Securigroup Statement' pretending to come from Maria Wilson (the email address that pretends to send changes with each email so you get maria.wilson@securigroup .co .uk) with a malicious xls attachment is another one from the current bot runs… So far today -3- different versions of the malware attachment have been seen…
Fake 'Remittance Advice' SPAM - XLS malware
- http://myonlinesecurity.co.uk/this-is-your-remittance-advice-cci36306-excel-xls-malware/
19 Feb 2015 - "Following on from -other- Excel XLS macro laden malwares today we are seeing a load of -damaged/misconfigured- emails with a malicious Excel XLS attachment arriving. The subject says 'This is your Remittance Advice #CCI36306' and pretends to come from Violet Garner The email has -garbled- plain text content with 3 attachments. They are supposed to be a rerun of 'SGBD National Payments Centre – This is your Remittance Advice' – Excel XLS malware* … the 3rd is the malware attachment, which is named CCI36306.xls and contains exactly the same malware payload as the other malixcious XLS files from today 'Marylou Proforma Invoice'** – Excel XLS malware and "Maria Wilson Securigroup Statement'*** – Excel XLS malware… All these emails have random invoice numbers in the subject line and the invoice number matches the attachment name & number in most cases so far today…
… Some mail clients and mail servers ( particularly web based email services) might deliver these emails intact and readable. My mail server is very precise and doesn’t try to fix broken/misconfigured emails and either rejects/quarantines them or delivers them as is and leaves it up to the receiving email client to make heads or tails of them. These all are from the current bot runs… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* http://myonlinesecurity.co.uk/sgbd-national-payments-centre-remittance-advice-excel-xls-malware/
Macros? Really?!
- https://isc.sans.edu/diary.html?storyid=19349
2015-02-19 - "… While the past 15 years or so were mostly devoid of any significant macro viruses, macro-based malware is now making a "successful" comeback. Last week, we saw a significant Dridex malware run that was using macros in Excel files (.XLSM), and earlier this week, the crooks behind the banking spyware "Vawtraq" started to spam the usual "Fedex Package" and "Tax Refund" emails, but unlike in other malspam runs, the attachment was no longer a ZIP with an EXE or SCR inside, but rather a file in Microsoft Office .DOC format. File extension based blocking on the email gateway is not going to save your bacon on this one… For Vawtraq, -if- the recipient -opens- the DOC, the content looks garbled, and the only readable portion is in (apparently) user-convincing red font, asking the recipient to enable macros. You can guess what happens next if the user falls for it…: A VBS and Powershell file get extracted from the DOC, and then download and -run- the Vawtraq malware executable. The whole mess has very low detection in anti-virus, yesterday's Vawtraq started with zero hits on VirusTotal, and even today, one day later, it hasn't made it past 7/52 anti-virus engines detecting the threat yet. Thus, odds are you will need to revert to manual analysis to determine if a suspicious Office document is indeed malicious, and to extract any indicators from it that can help to discover users on your network who have been "had"…"
___
Fake 'DVLA' Phish…
- http://myonlinesecurity.co.uk/dvla-you-are-eligible-to-receive-a-tax-disc-refund-phishing/
19 Feb 2015 "'You are eligible to receive a tax disc refund' pretending to come from DVLA is a brand new -phish- attempt to steal your Personal information, driving licence details and your Bank details. I have never previously seen one of these and definitely have never seen any phishing attempt that asks you to scan/photograph your driving licence and upload a copy of that. This one wants your personal details, A copy of your driving licence to be uploaded and bank details…
Apple GSX Access – Phish…
- http://myonlinesecurity.co.uk/apple-gsx-access-privileges-phishing/
19 Feb 2015 - "'Apple GSX Access Privileges' pretending to come from gsx_notifications@ apple .com is one of the latest phish attempts to steal your Apple account. This one only wants your Apple log in details Many of them are also designed to specifically steal your credit card and bank details, your email, facebook and other social network log in details as well… Some versions of this phish will ask you fill in the html (webpage) form that comes -attached- to the email. Dear GSX User,
Your access privileges on the Apple Global Service Exchange (GSX) system were revoked by GSX_Rejections@ group .apple .com on 19-Feb-2015
Reason for Revoking access :
http ://idmsa-gsx-apple .net/WebApp-login.html
Please contact your GSX administrator for more information.
Some Superfish domains and IP addresses and ranges…
- http://blog.dynamoo.com/2015/02/some-superfish-domains-and-ip-addresse.html
19 Feb 2015 - "In the light of the growing Lenovo/Superfish* fuss, I set out to identify those Superfish domains and IPs that I could, for the purposes of -blocking- or monitoring. The domains and IPs that I have been able to identify are here [csv**]. Superfish appear to operate the following domains (and several subdomains thereof):
venn .me
best-deals-products .com
superfish .com
pin2buy .net
pintobuy .net
similarproducts .net
adowynel .com
govenn .com
group-albums .com
jewelryviewer .com
likethatapps .com
likethatdecor .com
likethatpet .com
likethatpets .com
testsdomain .info
superfish .mobi
vennit .net
superfish .us
These following IP addresses and ranges appear to be used exclusively by Superfish (some of their other domains are on shared infrastructure). 66.70.35.240/28
66.70.34.64/26
66.70.34.128/26
66.70.34.251
66.70.35.12
66.70.35.48
All of those IPs are allocated to Datapipe in the US. Superfish itself is based in Israel, which seems to be a popular place to develop adware…"
* http://thenextweb.com/insider/2015/02/19/lenovo-caught-installing-adware-new-computers/
Fake 'Bank' SPAM - PDF malware
- http://myonlinesecurity.co.uk/lloyds-bank-pendeford-securities-please-read-action-requiredpi-documents-region-code-east-2-9147056-fake-pdf-malware/
20 Feb 2015 - "'Lloyds Bank – Pendeford Securities – Please Read Action Required/PI Documents/ Region code East 2/ 9147056/' pretending to come from RSTNAME} Woodruff with a zip attachment is another one from the current bot runs… The email looks like: Please find attached our document pack for the above customer. Once completed please return via email to the below address.
If you have any queries relating to the above feel free to contact us at MN2Lloydsbanking@ lloydsbanking .com
Lloyds Banking Group plc. Registered Office: The Mound, Edinburgh EH1 1YZ. Registered in Scotland no. SC95000. Telephone: 0131 225 4555. Lloyds Bank plc. Registered Office: 25 Gresham Street, London EC2V 7HN. Registered in England and Wales no. 2065. Telephone 0207626 1500. Bank of Scotland plc. Registered Office: The Mound, Edinburgh EH1 1YZ. Registered in Scotland no. SC327000. Telephone: 08457 21 31 41. Cheltenham & Gloucester plc. Registered Office: Barnett Way, Gloucester GL4 3RL. Registered in England and Wales 0128078. Telephone: 0845 603 1637
Lloyds Bank plc, Bank of Scotland plc are authorised by the Prudential Regulation Authority and regulated by the Financial Conduct Authority and Prudential Regulation Authority.
Cheltenham & Gloucester plc is authorised and regulated by the Financial Conduct Authority.
Halifax is a division of Bank of Scotland plc. Cheltenham & Gloucester Savings is a division of Lloyds Bank plc.
HBOS plc. Registered Office: The Mound, Edinburgh EH1 1YZ. Registered in Scotland no. SC272200.
This e-mail (including any attachments) is private and confidential and may contain privileged material. If you have received this e-mail in error, please notify the sender and delete it (including any attachments) immediately. You must not copy, distribute, disclose or use any of the information in it or any attachments. Telephone calls may be monitored or recorded…
The malware attached to this email is the same malware as in today’s other Upatre "delivery supply only quotation 16822 in total"* – fake PDF malware . If previous days are anything to go by, we -will- see -numerous- different emails all containing the same upatre malware and all with different file names…"
* http://myonlinesecurity.co.uk/supply-only-quotation-16822-in-total-fake-pdf-malware/
20 Feb 2015 - "'supply only quotation 16822 in total' pretending to come from wendy@ burwoodsupply .co .uk with a zip attachment is another one from the current bot runs… The email looks like: Hi
Attached are 1 quotes so far they are in excel format so they can be altered if necessary (I normally only send the quotes in PDF so they can’t be altered but Mike asked me not to do this).
The rest to follow tomorrow a.m.
Regards
Teresa Byron
Office Administrator
ECY Armco Barley Castle Lane, Appleton Thorn, Warrington, Cheshire, WA4 4RB t: +44(0)1925 860000 f: +44(0)1925 861111
This email is confidential. It may also be privileged or otherwise protected by work product immunity or other legal rules. If you are not the intended recipient please notify the sender. Please delete the message from all places in your computer where it is stored…
Fake 'NYC Parking Fine' SPAM - malware
- http://www.hoax-slayer.com/new-york-parking-fines-malware.shtml
Feb 20, 2015 - "Email purporting to be from the NYC Department of Finance thanks you for paying $7900 in parking fines via your credit card and suggests you open an -attached- file to view details… claims to be from the NYC Department of Finance… Opening the attached .zip file will reveal a malicious .exe file. If you then click-the-.exe file, -malware- may be installed on your computer. The exact type of malware varies…"
___
Lenovo - vulnerable to HTTPS Spoofing
- https://www.us-cert.gov/ncas/current-activity/2015/02/20/Lenovo-Computers-Vulnerable-HTTPS-Spoofing
Feb 20, 2015 - "Lenovo consumer personal computers employing the pre-installed Superfish Visual Discovery software contain a critical vulnerability through a compromised root CA certificate. Exploitation of this vulnerability could allow a remote attacker to read -all- encrypted web browser traffic (HTTPS), successfully impersonate (spoof) any website, or perform other attacks on the affected system. US-CERT recommends users and administrators review Vulnerability Note VU#529496* and US-CERT Alert TA15-051A** for additional information and mitigation details."
* http://www.kb.cert.org/vuls/id/529496
Feb 20, 2015 - "… Solution: The CERT/CC is currently unaware of any official solutions to this problem and recommends the following workarounds.
- Uninstall Komodia Redirector SDK and associated root CA certificates
- Uninstall any software that includes the Komodia Redirector and SSL Digestor libraries…"
** https://www.us-cert.gov/ncas/alerts/TA15-051A
Feb 20, 2015 - "… Solution: Uninstall Superfish VisualDiscovery and associated root CA certificate
- Uninstall any software that includes the Komodia Redirector and SSL Digestor libraries. In the case of Lenovo PCs, this includes Superfish Visual Discovery.
It is also necessary to remove affected root CA certificates. Simply uninstalling the software does not remove the certificate. Microsoft provides guidance on [3] deleting (link is external) and [4] managing (link is external) certificates in the Windows certificate store. In the case of Superfish Visual Discovery, the offending trusted root certification authority certificate is issued to “Superfish, Inc.”
Mozilla provides similar [5] guidance for their software, including the Firefox and Thunderbird certificate stores."
Fake Magazine Invoice SPAM - PDF malware
- http://myonlinesecurity.co.uk/essex-central-magazine-invoice-fake-pdf-malware/
23 Feb 2015 - "'Essex Central Magazine Invoice' pretending to come from Essex Central Magazine with a zip attachment is another one from the current bot runs… The email looks like: Please see attached invoice for the upcoming issue of Essex Central
Magazine.
Regards,
Accounts Dept.
Fake Invoice SPAM - doc malware
- http://blog.dynamoo.com/2015/02/malware-spam-berendsen-uk-ltd-invoice.html
24 Feb 2015 - "This -fake- invoice is not from Berendsen UK Ltd but is a simple forgery. They are not sending out the spam and their systems have not been compromised in any way. Instead, this email has a malicious Word document attached. From: donotreply@ berendsen .co .uk
Date: 24 February 2015 at 08:09
Subject: Berendsen UK Ltd Invoice 60020918 117
Dear Sir/Madam,
Please find attached your invoice dated 21st February.
All queries should be directed to your branch that provides the service. This detail can be found on your invoice.
Thank you…
I have only seen one sample of this email, with a Word document IRN001549_60020918_I_01_01.doc which has a -zero- detection rate*. Contained within this is a malicious Word macro which downloads a component from the following location:
http ://heikehall .de/js/bin.exe
This binary has a VirusTotal detection rate of 2/57**. Automated analysis tools… show that it attempts to phone home to:
92.63.87.13 (MWTV, Latvia)
5.196.241.196 (OVH, Ireland)
[removed] (Microtech Tel, US)
[removed] (World Internetwork Corporation, Thailand)
[removed] (Webazilla, US)
[removed] (KPN, Netherlands)
[removed] (UA Servers, Ukraine)
86.104.134.156 (One Telecom, Moldova)
MWTV have featured several times on this blog. A close examination of their 92.63.80.0/20 block indicates a mix of legitimate and illegitimate sites, however the bad sites are concentrated in the following ranges:
92.63.82.0/23
92.63.84.0/22
92.63.88.0/24
In addition to this, the malware attempts to drop a Dridex DLL which is widely detected by AV vendors with a detection rate of 30/57***.
Recommended blocklist: 92.63.82.0/23
92.63.84.0/22
92.63.88.0/24
5.196.241.196
66.110.179.66
202.44.54.5
78.140.164.160
31.160.233.212
185.14.30.98
86.104.134.156 "
* https://www.virustotal.com/en/file/10841585f9856262b8fa5fdeab9ff5ae3adab09a73af00c3fbc772bb96028275/analysis/1424770482/
… exactly the -same- as the attachments to today’s other malicious word and excel macros Izabela Pachucka Arsenal LTD document do confirm – Word doc malware* and Berendsen UK Ltd Invoice 60020918 117 – Word doc malware** although re-named as SCAN_20150224_100752437.doc or SCAN_20150224_100752437.xls …"
* http://myonlinesecurity.co.uk/izabela-pachucka-arsenal-ltd-document-do-confirm-word-doc-malware/
Fake 'Time Sheet' SPAM – PDF malware
- http://myonlinesecurity.co.uk/bobby-time-sheet-fake-pdf-malware/
24 Feb 2015 - "'Time Sheet' pretending to come from hartsellb@ mtpleasantnc .us with a zip attachment is another one from the current bot runs… The email looks like: Sorry again this time it has a attachment.
Thanks
Bobby
Fake 'EFT Notification' SPAM – PDF malware
- http://myonlinesecurity.co.uk/town-of-mt-pleasant-here-is-your-eft-notification-fake-pdf-malware/
24 Feb 2015 - "'TOWN OF MT PLEASANT, here is your EFT Notification' pretending to come from finance_ap@ cabarruscounty .us with a zip attachment is another one from the current bot runs… The email is very basic and terse and simply has this in the body :
7,038 new security vulnerabilities - 2014 stats
- http://www.gfi.com/blog/most-vulnerable-operating-systems-and-applications-in-2014/
Feb 18, 2015 - "… 7,038 -new- security vulnerabilities were added to the NVD database in 2014. This means an average of 19 new vulnerabilities per day. The number is significantly higher than in 2013 and continues the ascending trend over the past few years.
> http://www.gfi.com/blog/wp-content/uploads/2015/02/number-of-vulnerabilities-09-14.jpg
24% of these vulnerabilities are rated as high severity. The percentage is lower than in 2013, but the actual number of high security vulnerabilities has -increased- compared to last year.
> http://www.gfi.com/blog/wp-content/uploads/2015/02/high-severity-vulnerabilities.jpg
Third-party applications are the most important source of vulnerabilities with over 80% of the reported vulnerabilities in third-party applications. Operating systems are only responsible for 13% of vulnerabilities and hardware devices for 4%.
> http://www.gfi.com/blog/wp-content/uploads/2015/02/vulnerability-distribution-by-product-type.jpg Top operating systems by vulnerabilities reported in 2014
> http://www.gfi.com/blog/wp-content/uploads/2015/02/OS-chart.jpg Top applications by vulnerabilities reported in 2014
> http://www.gfi.com/blog/wp-content/uploads/2015/02/application-chart.jpg
… Not surprisingly at all, web browsers continue to have the most security vulnerabilities because they are a popular gateway to access a server and to spread malware on the clients. Adobe free products and Java are the main challengers but web browsers have continuously topped the table for the last six years. Mozilla Firefox had the most vulnerabilities reported in 2009 and 2012; Google Chrome in 2010 and 2011; Internet Explorer was at the top for the last two years.
To keep systems secure, it is -critical- that they are fully patched. IT admins should focus on (patch them first):
- Operating systems (Windows, Linux, OS X)
- Web browsers
- Java
- Adobe free products (Flash Player, Reader, Shockwave Player, AIR).
Vulnerability and patch management should be priority tasks for every sysadmin. Microsoft’s updates are -not- enough because third-party applications are just as problematic…"
Fake 'LogMeIn' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/02/malware-spam-your-logmein-pro-payment.html
25 Feb 2015 - "This -fake- financial email does not come from LogMeIn, instead it has a malicious attachment: From: LogMeIn .com [no_reply@ logmein .com]
Date: 25 February 2015 at 08:52
Subject: Your LogMeIn Pro payment has been processed!
Dear client,
Thank you for purchasing our yearly plan for LogMeIn Pro on 25 computers.
Your credit card has been successfully charged.
Date : 25/2/2015
Amount : $999 ( you saved $749.75)
The transaction details can be found in the attached receipt.
Your computers will be automatically upgraded the next time you sign in.
Thank you for choosing LogMeIn!
Attached is a malicious Excel document called logmein_pro_receipt.xls with a VirusTotal detection rate of 0/56*. Usually in a spam run like this there are several different versions of the document but so far I have only seen one, containing this malicious macro. The macro downloads a file from:
http ://junidesign .de/js/bin.exe
This is saved as %TEMP%\GHjkdfg.exe and has a VirusTotal detection rate of 3/57**. Automated analysis tools… show this calling home to the following IPs:
92.63.87.13 (MTWV, Latvia)
86.104.134.156 (One Telecom, Moldova)
[removed] (ITL, Bulgaria)
[removed] (Choopa LLC, Netherlands)
[removed] (OVH, Ireland)
[removed] (Microtech Tel, US)
[removed] (World Internetwork Corporation, Thailand)
[removed] (Digital Networks aka DINETHOSTING, Russia)
59.97.137.171 (Broadband Multiplay, India)
78.140.164.160 (Webazilla, US)
107.181.174.104 (Colo at 55, US / UA Servers, Ukraine)
… The Malwr report shows that among other activities, this drops an executable that seems to be another version of itself [VT 3/57***] and a malicious DLL which is probably a Dridex component [VT 4/57****].
Recommended blocklist: 92.63.82.0/23
92.63.84.0/22
92.63.88.0/24
86.104.134.156
217.12.203.34
108.61.165.19
5.196.241.196
66.110.179.66
202.44.54.5
95.163.121.179
59.97.137.171
78.140.164.160
107.181.174.104 "
* https://www.virustotal.com/en/file/2036453918e928f3a1931c5554c2e0167bd2fce399f76f090e4ba3bd2bedd72f/analysis/1424856686/
Copy .com used to distribute Crypto Ransomware
- https://isc.sans.edu/diary.html?storyid=19371
2015-02-25 01:04:23 UTC - "Thanks to Marco for sending us a sample of yet another piece of crypto-ransom malware. The file was retrieved after visiting a compromised site (www .my-sda24 .com) . Interestingly, the malware itself was stored on copy .com. Copy .com is a cloud based file sharing service targeting corporate users. It is run by Barracuda, a company also known for its e-mail and web filtering products that protect users from just such malware. To its credit, Barracuda removed the malware within minutes of Marco finding it. At least right now, detection for this sample is not great. According to Virustotal, 8 out of 57 virus engines identify the file as malicious [1]. A URL blacklist approach may identify the original site as malicious, but copy .com is unlikely to be blocked. It has become very popular for miscreants to store malicious files on cloud services, in particular if they offer free trial accounts. Not all of them are as fast as Barracuda in removing these files."
Dropbox SPAM - malware
- http://blog.dynamoo.com/2015/02/malware-spam-info-chemicals-shared-mt.html
25 Feb 2015 - "This spam leads to a malware download via Dropbox. From: Info via Dropbox
Reply-To: hcm0366@ gmail .com
Date: 25 February 2015 at 05:38
Subject: Info Chemicals shared "MT 103_PO_NO!014.zip" with you
Signed by: dropbox .com
From Info:
"Good day ,
How are you today
pls check attached, my manager had requested I email you our new order details together with TT copy of balance payment. Kindly confirm in return.
regards,
Frank Manner
Broad Oak Ltd, Tiverton, Tiverton Way, Tiverton Business Park, Tiverton, Devon, EX16 6TG
Registered No. 1971053 England & Wales…
The email has been digitally signed by Dropbox (which means exactly nothing) and is -spoofing- the wholly legitimate Broad Oak Ltd who have been a target of this sort of thing several times before. In this case, the link in the email goes to:
https ://www .dropbox .com/l/dFxVxjuDRo3j2oANVURy2v
and then to
https ://www .dropbox .com/s/fnsprei93c45ts6/MT%20103_PO_NO!014.zip
Which leads to a malicious EXE file called MT 103_PO_NO!014.zip. Inside that is the malware itself, a file .pdf.scr which has a detection rate of 11/57*. According to the Malwr report it drops another executable with a detection rate of 9/57**. The payload looks similar to the Zeus trojan. Also, according to Malwr and ThreatExpertit attempts to communicate with an apparent web-to-Tor gateway at
mmc65z4xsgbcbazl .onion .am
onion .am is hosted on [removed] (YISP Colo, Netherlands)… Be aware that there are probably many other Dropbox locations in use for this spam run. If you see more, I suggest you forward the email to abuse -at- dropbox.com …"
* https://www.virustotal.com/en/file/ed7d56bf1e579bdaac0ba2d4f1c5be18256f58f2acf667c2a82a3f62341aca76/analysis/1424849825/
cPanel ‘Account Suspended’ PHISH serves exploits
- https://blog.malwarebytes.org/exploits-2/2015/02/deceiving-cpanel-account-suspended-page-serves-exploits/
Feb 26, 2015 - "cPanel is one of the most popular web hosting control panels out there. It allows administrators to manage their website(s) using a graphical front end, perform maintenance and review important logs among other things. cPanel also has a user interface for CGI (short for Common Gateway Interface) typically used to run scripts and generate dynamic content. One such script populates a fairly well-known (and somewhat dreaded) page known as the “Account Suspended” page:
> https://blog.malwarebytes.org/wp-content/uploads/2015/02/suspended1.png
Visitors to a site are -redirected- to this screen for one of many reasons ranging from the site owner’s failure to pay for his hosting, violating the Terms and Conditions, or perhaps exceeding their allocated bandwidth… The page itself is made of HTML code, and can be edited by an administrator, often via a Web Host Manager (WHM). Many sites that were once used to distribute malware and have been suspended will sport that kind of page. One would assume that the site would now be harmless, since the hosting provider has already taken action. If you aren’t looking at the URL carefully (the suspended page should be displayed at the root of the domain) and assumed so, you might just run into a case where the site is actually fully compromised and still active… The injected iframe redirects straight to a Fiesta exploit kit landing page. The landing page usually performs various checks and prepares the exploits that are going to get fired at the victim. As is often the case with exploit kits, that page is heavily obfuscated to make identification a little bit more difficult… This case is a reminder not to trust a book by its cover and always exercise caution. Attackers were clever to hide the malicious redirect code where they did because they might trick someone into brushing off the site as “already terminated by the hosting provider”, when in fact it’s not. They might have fooled some, but they didn’t fool us…" (More detail at the malwarebytes URL at the top.)
___
Fake 'Copy Invoices' SPAM - malicious attachment
- http://blog.dynamoo.com/2015/02/malware-spam-chris-christou.html
26 Feb 2015 - "This -fake- invoice spam comes with a malicious attachment: From: Chris Christou [chris.christou@ greysimmonds .co.uk]
Date: 26 February 2015 at 10:45
Subject: Copy invoices
Hello ,
Please find copy invoices attached as per our telephone conversation.
Kind regards,
Chris
Chris Christou
Credit Control
Grey Simmonds
Cranes Point
Gardiners Lane South
Basildon
Essex SS14 3AP
Tel: 0845 130 9070
Fax: 0845 370 9071…
It does -NOT- come from Grey Simmons, nor have their systems been compromised in any way. Instead, this is a simple forgery. I have only seen one sample so far, with an attachment IGM135809.doc [detection rate 0/57*] which contains this malicious macro… which downloads a further component from:
http ://xomma .net/js/bin.exe
This is saved as %TEMP%\GVhjJJVJH.exe and has a VirusTotal detection rate of 4/56**. Automated analysis tools… show it attempting to phone home to the following IPs:
92.63.87.13 (MWTV, Latvia)
[removed] (Webazilla, US)
[removed] (One Telecom, Moldova)
104.232.32.119 (Net 3, US)
This Malwr report shows dropped files with an MD5 of 590fc032ac747d970eb8818671f2bbd3 [VT 3/57***] and 1997b0031ad702c8347267db0ae65539 [VT 4/57****].
Recommended blocklist: 92.63.82.0/23
92.63.84.0/22
92.63.88.0/24
78.140.164.160
86.104.134.156
104.232.32.119 "
* https://www.virustotal.com/en/file/73d0d60b84393ffbc09a94230384772ec688ff2c39a2a4de58ff705b2aa55e50/analysis/1424948249/
Bogus Search Engine leads to Exploits
- https://blog.malwarebytes.org/online-security/2015/02/bogus-search-engine-leads-to-exploits/
Feb 27, 2015 - "… Sadly, devious software makers are using all the tricks in the books to fool users into installing their programs. Even when you take all the precautions necessary and never download anything from an untrusted source, you could still end up with Adware. The recent Lenovo/Superfish fiasco is a good example of that. Brand new computers were pre-installed with Adware that surreptitiously injected ads into the browser by introducing vulnerabilities, in an almost undetectable way. Adware is not only annoying but can also weaken a computer’s security status. Today, we have another case to prove that point. Potentially Unwanted Programs often install a search assistant (or rather a browser and search -hijacker-) on people’s machines:
> https://blog.malwarebytes.org/wp-content/uploads/2015/02/webfindfast2.png
The idea is simple: To redirect people’s searches to affiliates or other sponsors and earn pay-per-click commissions. This one is hosted at webfindfast .com*:
> https://blog.malwarebytes.org/wp-content/uploads/2015/02/searches.png
For the end-user, the search experience is simply terrible but yet not the end of their troubles. In this case, clicking on any link results in a -redirection- to an exploit kit landing page, quickly followed by malware… As usual, after several convoluted redirects, the user ends up on the door step of the famous Angler exploit kit… Vulnerable computers are infected with a piece of malware detected as Trojan.Crypt.NKN by Malwarebytes Anti-Malware. It will install a rogue Antivirus program known as 'Malware Defender 2015' and pull up a purchase page from an IP address located in Istanbul (176.53.125.20)**… The lesson to learn from this is to once again stay away from bundled software and other programs that appear to be free but come with a catch. Also, if you’re starting to see a different home page or search engine than you used to, you should make sure your browser has not been altered in some way."
* 136.243.24.248: https://www.virustotal.com/en/ip-address/136.243.24.248/information/
Fake 'Invoice' SPAM - doc malware
- http://blog.dynamoo.com/2015/02/malware-spam-dennys-invoice-inv650988.html
27 Feb 2015 - "This -fake- invoice email is not from Dennys but is a simple forgery with a malicious attachment. Dennys are not sending the spam, and their systems have not been compromised in any way. From: accounts@ dennys .co.uk
Date: 27 February 2015 at 09:14
Subject: Dennys Invoice INV650988
To view the attached document, you will need the Microsoft Word installed on your system.
So far I have only seen a single sample, with an attachment INV650988.doc which has a VirusTotal detection rate of exactly zero*. This contains this malicious macro… which downloads another component from the following location:
http ://hew.homepage.t-online. de/js/bin.exe
This is saved as %TEMP%\324235235.exe and has a VirusTotal detection rate of 1/57**.
According to the Malwr report, this executable then goes on and downloads another version of itself and a config file from:
http ://apartmentprofile .su/conlib.php
http ://paczuje.cba .pl/java/bin.exe
It drops several files, KB2896~1.EXE [VT 3/57***], edg2.exe [VT 3/57****] and a Dridex DLL which is much more widely detected (and we saw this same DLL yesterday)… Between the Malwr and VirusTotal analyses, we see attempts to communicate with the following IPs:
[removed] (Centarra Networks, US)
[removed] (Leaseweb, Netherlands)
[removed] (SuperHost.pl, Poland)
[removed] (MWTV, Latvia)
[removed] (Webazilla, US)
[removed] (Broadband Multiplay Project, India)
[removed] (Net 3, US)
Some of these are shared hosting, I recommend for maximum protection that you apply the following blocklist: 92.63.82.0/23
92.63.84.0/22
92.63.88.0/24
198.52.200.15
78.140.164.160
59.97.137.171
104.232.32.119 "
* https://www.virustotal.com/en/file/42efc98ed3f157b3a607a768e49f00f28a5f3eaeac167b9f7007a5510e3d8aec/analysis/1425029078/
Fake job offer SPAM
- http://blog.dynamoo.com/2015/02/fake-job-offer-tradeconstructioncouk.html
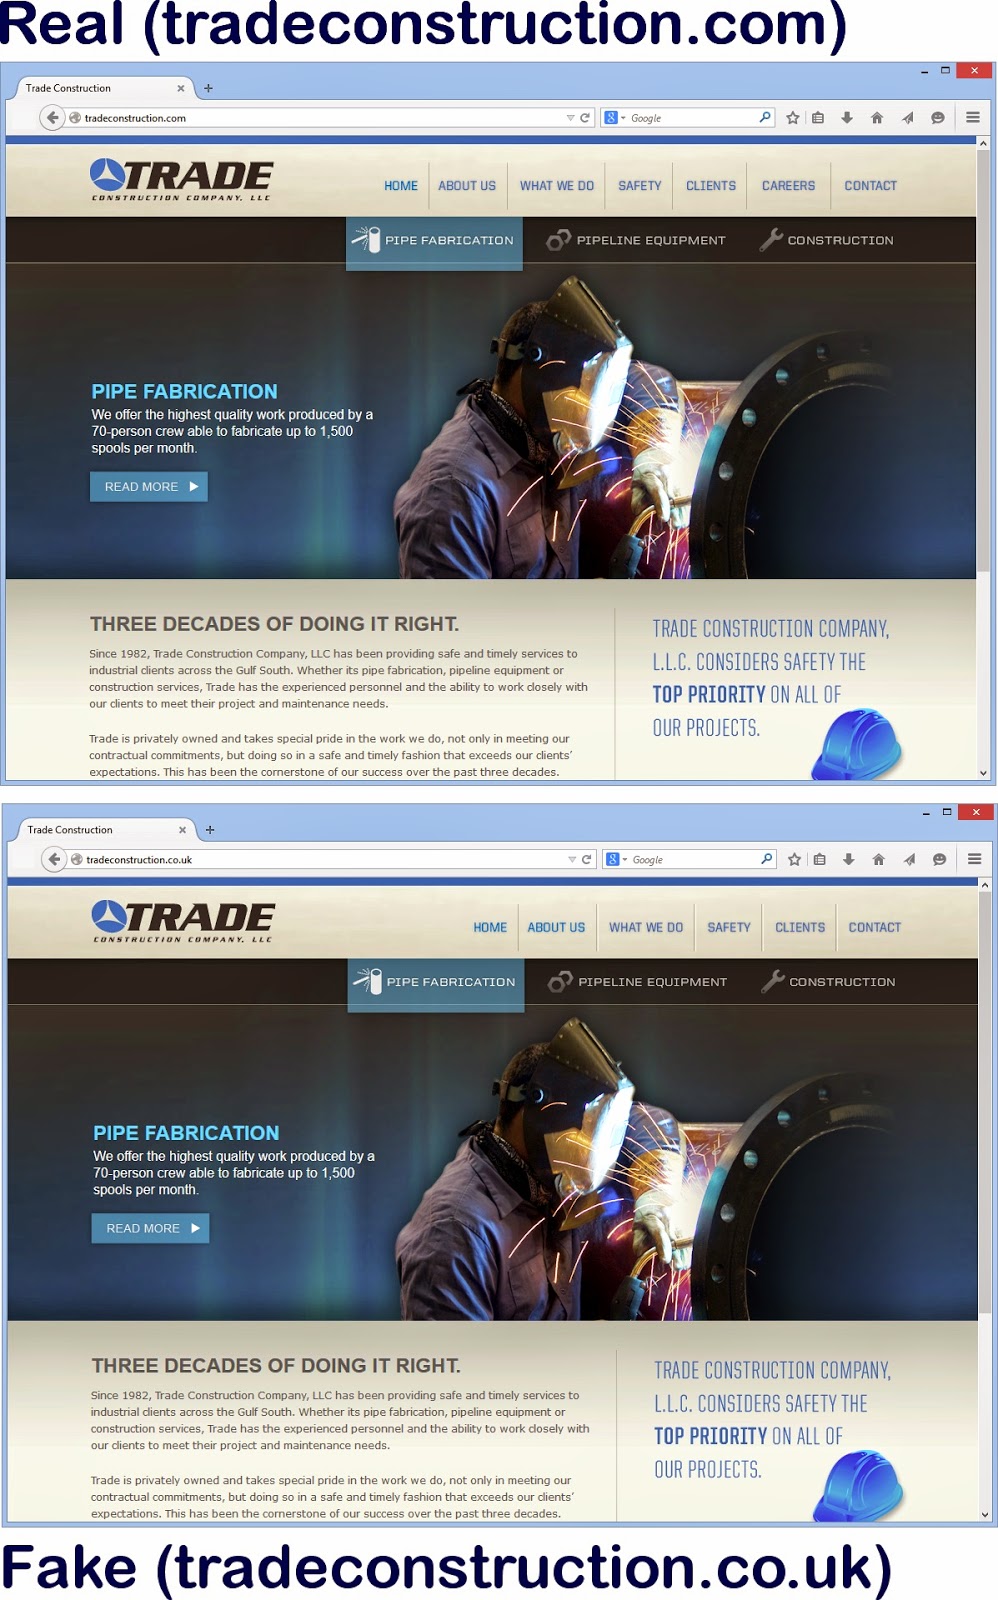
28 Feb 2015 - "This -fake- job offer claimed to be from a UK-based company called Trade Construction Company LLC using a website at tradeconstruction .co .uk. However, no such company exists in the UK, and this is a rip-off of a wholly legitimate US firm that is actually called Trade Construction Company LLC who are -not- involved in this scam at all.
From: JOB ALERT [klakogroups@ gmail .com]
Reply-To: klakogroups@ gmail .com
To: Recipients [klakogroups@ gmail .com]
Date: 27 February 2015 at 18:37
Subject: NEW JOB VACANCIES IN LONDON.
Trade Construction Company,
L.L.C,
70 Gracechurch Street.
EC3V 0XL, London. UK
We require the services of devoted and hardworking workers, who are ready to work after undergoing enlistment training. in all sectors
as The Trade Construction Company Management intends to increase its man power base due to increasing number of customers and contract in the Company.
Available Positions…
Fake 'Secure Message' SPAM – PDF malware
- http://myonlinesecurity.co.uk/jp-morgan-access-secure-message-fake-pdf-malware/
2 Mar 2015 - "'JP Morgan Access Secure Message' pretending to come from JP Morgan Access with a zip attachment is another one from the current bot runs… The email looks like: Please check attached file(s) for your latest account documents regarding your online account.
Forrest Blackwell
Level III Account Management Officer
[removed] office
[removed] cell
Forrest .Blackwell@ jpmorgan .com
Investments in securities and insurance products are:
NOT FDIC-INSURED/NO BANK-GUARANTEES/MAY LOSE VALUE
2015 JPMorgan Chase & Co…
2 March 2015: JP Morgan Access – Secure.zip : Extracts to: JP Morgan Access – Secure.scr
Current Virus total detections: 9/57** . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/2e6326d840a7656321ea9a946efb2a57f15ab6cf3b07a668e8a14bb56229150e/analysis/1425314842/
Fake 'Apple ID' – phish…
- http://myonlinesecurity.co.uk/your-recent-download-with-your-apple-id-phishing/
2 Mar 2015 - "'Your recent download with your Apple ID' pretending to come from Apple iTunes is one of the latest -phish- attempts to steal your Apple Account and your Bank, credit card and personal details. This one only wants your personal details, Apple log in details and your credit card and bank details… This one has a short url link in the email which -redirects- you…
Fraud Alert: Unauthorised Appstore Payment – phish
- http://myonlinesecurity.co.uk/fraud-alert-unauthorised-appstore-payment-phishing/
3 Mar 2015 - "Fraud Alert: Unauthorised Appstore Payment' pretending to come from iTunes is one of the latest -phish- attempts to steal your Apple Account and your Bank, credit card and personal details…
All of these emails use Social engineering tricks to persuade you to open the attachments that come with the email…:
___
Worm.Gazon: Want Gift Card? Get Malware
- http://www.adaptivemobile.com/blog/worm-gazon-want-gift-card-get-malware
2 Mar 2015 - "… A simple piece of -malware- is on the way to become one of the 'spammiest' mobile malware outbreaks seen yet. This malware we have dubbed Gazon spreads via SMS with a shortened link to itself in the spam message, redirecting a potential victim to a webpage that promises an Amazon gift card if you install an APK file hosted on the page:
The malware passes itself as an app that gives Amazon rewards. However, the only thing it actually does is pulling up a scam page inside the app which asks you to participate in the -survey- … Each of the options below ends up taking you to either another scam page or asks you to download a game in the Google Play. While you are busy clicking through pages the author just earns money through your clicks as we have seen in other pieces of mobile malware.
> http://www.adaptivemobile.com/images/blog-uploads/gazon-scam1.png
However, in the background this malware harvests all your contacts and sends a -spam- message to each of them with the URL pointing to the body of the worm… Thousands of people have seemingly installed this malware and been a victim. We are seeing over 4k infected devices in all of the major networks in North America, and we've blocked over 200k spam messages generated by these infected devices. Stopping the spread via messaging is critical as each one of these messages was an attempt to spread the app to an infected user's contacts. Based on click-throughs from the shortened URL it also seems this malware has been encountered in multiple other countries as well, worldwide. At the moment none of the AV engines detect this malware according to VirusTotal.
> http://www.adaptivemobile.com/images/blog-uploads/gazon-virustotal.png
… users should be aware of this -scam- and as always, be careful clicking on links in text messages that seem suspect. In this case, like other worm malware we have seen recently, even messages your contacts send you may not be safe. The malware can be removed using standard Android app uninstall utilities…"
Fake no body text SPAM - malicious attachment
- http://blog.dynamoo.com/2015/03/malware-spam-john-donald.html
4 Mar 2015 - "This rather terse email comes with a malicious attachment: From: John Donald [john@ kingfishermanagement .uk .com]
Date: 4 March 2015 at 09:09
Subject: Document1
There is no body text, but there is an attachment Document1.doc which is not currently detected by AV vendors*, in turn it contains this malicious macro… which downloads another component from the following location:
http ://retro-moto .cba .pl/js/bin.exe
Note that there may be other different versions of this document with different download locations, but it should be an identical binary that is downloaded. This file is saved as %TEMP%\GHjkdjfgjkGKJ.exe and has a VirusTotal detection rate of 2/57**. Automated analysis tools… show attempted network traffic to the following IPs:
92.63.87.13 (MWTV, Latvia)
104.232.32.119 (Net3, US)
87.236.215.103 (OneGbits, Lithunia)
108.61.198.33 (Gameservers.com / Choopa LLC, Netherlands)
According to the Malwr report it also drops another version of itself with a detection rate of just 1/57*** plus a DLL with a detection rate of 7/56****.
Recommended blocklist: 92.63.82.0/23
92.63.84.0/22
92.63.88.0/24
104.232.32.119
87.236.215.103
108.61.198.33 "
* https://www.virustotal.com/en/file/20afc565c00d30b2d194366d088b73b20913af78857c906305fab79a5c726f83/analysis/1425464228/
Fake 'Remittance advice SPAM – word doc or excel xls malware
- http://myonlinesecurity.co.uk/remittance-advice-rem_5556yj-xml-word-doc-or-excel-xls-spreadsheet-malware/
4 Mar 2015 - "'Remittance advice [Rem_5556YJ.xml] (random numbers)' pretending to come from random addresses and random companies with a malicious word doc or Excel XLS spreadsheet attachment, these are actually XLM word files is another one from the current bot runs… This email has what appears to be a genuine word doc or Excel XLS spreadsheet attached which is malformed and contains a macro script virus. Modern versions of Microsoft office, that is Office 2010 and 2013 and Office 365 have Macros disabled by default, UNLESS you or your company have enabled them… The email looks like: Good morning
You can find remittance advice [Rem_5556YJ.xml] in the attachment
Kind Regards
Lenny Madden
GLAXOSMITHKLINE
4 March 2015 : Rem_5892GV.xml Current Virus total detections: 0/56* | 0/56**
So far I have only seen 2 versions of this malware, but previous campaigns over the last few weeks have delivered 2 or 3 or even more different versions, some with word doc attachments and some with Excel xls attachments… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/d40d05316db62ea3d27830f87892aaeab3ff22b63babadb755aad10dcba85a7d/analysis/1425470968/
Many common sites might be temporarily offline
- http://myonlinesecurity.co.uk/many-common-sites-might-be-temporarily-offline/
4 Mar 2015 - "… Amazon and Rackspace have both announced that they will need to -reboot- some of their servers to address the issue before March 10, when the Xen Project plans to disclose the latest bugs*. Details of the vulns are being withheld for now, to give the cloud vendors time to patch. In a FAQ** about the upcoming maintenance, Amazon Web Services said that only some of its earliest Elastic Compute Cloud (EC2) customers should be affected."
* http://xenbits.xen.org/xsa/
- http://blog.trendmicro.com/trendlabs-security-intelligence/freak-vulnerability-forces-weaker-encryption/
Mar 4, 2015 - "… We advise Android users to refrain from using the default Android browser in their devices. They can instead use the Google Chrome app as it is not affected by the bug. Furthermore, connections to the Google search site are not affected. According to Deep Security Labs Director Pawan Kinger, FREAK is a serious and very real vulnerability which may require some level of sophistication to exploit. However, its sophistication won’t dissuade determined attackers. Carrying out a FREAK exploit requires attackers to be able to first create a man-in-the-middle (MITM) attack against the servers. It would also require the ability to control an SSL session between client and server and then force that session to downgrade to the lower encryption level. Then, the attacker would have to take the weakly encrypted traffic and perform a brute force attack against it that would take several hours, as opposed to days or weeks with higher encryption… Administrators can also check if their site is vulnerable by using the SSL Labs’ SSL Server Test*…"
* https://www.ssllabs.com/ssltest/
5 March 2015 : Brochure2.doc - Current Virus total detections: 1/57* … the malicious macro connects to & downloads data.gmsllp.com/js/bin.exe (dridex banking Trojan) which is saved as %Temp%\324235235.exe that has a virus total rate of 2/57** … So far I am only seeing 1 version of this malware, but previous campaigns over the last few weeks have delivered 2 or 3 different versions, some with word doc attachments and some with Excel xls attachments… The basic rule is NEVER open any attachment to an email, unless you are expecting it…"
* https://www.virustotal.com/en/file/b400baf11a2a402f8ac05d1ecb99e81bbedebea859aae6918b16eaba8feff296/analysis/1425549729/
Fake Natwest SPAM - PDF malware
- http://myonlinesecurity.co.uk/natwest-bankline-re-incident-im00491288-fake-pdf-malware/
5 Mar 2015 - "'RE: Incident IM00491288' pretending to come from Kevin Otero with a zip attachment is another one from the current bot runs… different random names. So far names and email addresses seen are
Kevin Otero
Collin Stovall
Lavern Olsen
Rae Bouchard
Nadine Kerr
… The email looks like: Good Afternoon ,
Attached are more details regarding your account incident.
Please extract the attached content and check the details.
Please be advised we have raised this as a high priority incident and will endeavour to resolve it as soon as possible. The incident reference for this is IM00491288.
We would let you know once this issue has been resolved, but with any further questions or issues, please let me know.
Kind Regards,
Kevin Otero
Level 2 Adviser | Customer Experience Team, IB Service & Operations 7th Floor, 1 …
5 March 2015: Incident IM00491288.zip: Extracts to: IM0743436407_pdf.exe
Current Virus total detections: 3/57* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/60243596f8d978350fdacc417e9945d4da6bd713733fa31fc44611c7f8a8eba8/analysis/1425548558/
___
5 March 2015 : invoice7985974765.zip: Extracts to: invoice7985974765.exe
Current Virus total detections: 4/56* . This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/6c69e4579d565906827983246c93ed0d43f408326a1e3fac351a4730226424f2/analysis/1425547819/
Fake IRS SPAM - doc malware
- http://blog.dynamoo.com/2015/03/malware-spam-your-2015-electronic-ip.html
6 Mar 2015 - "This -fake- IRS email comes with a malicious attachment. From: Internal Revenue Service [refund.noreply@ irs .gov]
Date: 6 March 2015 at 08:48
Subject: Your 2015 Electronic IP Pin!
Dear Member
This is to inform you that our system has generated your new secured Electronic PIN to e-file your 2014 tax return.
Please kindly download the microsoft file to securely review it.
Thanks
Internal Revenue Service …
… attachment TaxReport(IP_PIN).doc … there are usually several different versions[1]. Currently this is -undetected- by AV vendors*. This contains a malicious macro… which downloads a component from the following location:
http ://chihoiphunumos .ru/js/bin.exe
There are probably other download locations, but the payload will be the same. This is saved as %TEMP%\324235235.exe and has a detection rate of 1/55**. Automated analysis tools… show attempted connections to:
92.63.87.13 (MWTV, Latvia)
95.163.121.200 (Digital Networks CJSC aka DINETHOSTING, Russia)
[removed] (Net3, US)
87.236.215.103 (OneGbits, Lithunia)
According to the Malwr report this executable drops another version of itself [VT 1/56***] and a malicious DLL [VT 2/56****].
Recommended blocklist: 92.63.82.0/23
92.63.84.0/22
92.63.88.0/24
95.163.121.0/24
104.232.32.119
87.236.215.103 "
* https://www.virustotal.com/en/file/d3a6e6b43461f3cf80b8e664d61213e67755fd20569332ec35e4502822a7231b/analysis/1425632162/
Fake 'Invoice' SPAM – doc/xls malware
- http://myonlinesecurity.co.uk/mick-george-invoice-395687-for-dudley-construction-ltd-word-doc-or-excel-xls-spreadsheet-malware/
6 Mar 2015 - "'Mick George Invoice 395687 for Dudley Construction Ltd' pretending to come from Mick George Invoicing with a malicious word doc or Excel XLS spreadsheet attachment is another one from the current bot runs… These emails today, so far, are all malformed and broken. Every copy that I have received appears garbled and doesn’t actually have an attachment. Some mail servers will be configured to repair the damage and deliver the email in its full glory, where it will potentially infect you. This email has what appears to be a genuine word doc or Excel XLS spreadsheet attached which is malformed and contains a macro script virus…
… the malware payload will be identical to today’s other malicious office document run Internal Revenue Service Your 2015 Electronic IP Pin! – word doc or excel xls spreadsheet malware*. We do notice that the bad guys are using 2 or 3 subjects and email templates but using the same malware that has been -renamed- …
Edit: I have managed to extract the malware payload from a quarantined copy on the server and can confirm that it is the -same- malware payload as today’s other run although renamed as Invoice395687.DOC . So far I am only seeing 1 version of this malware, but previous campaigns over the last few weeks have delivered 2 or 3 different versions, some with word doc attachments and some with Excel xls attachments…"
* http://myonlinesecurity.co.uk/internal-revenue-service-your-2015-electronic-ip-pin-word-doc-or-excel-xls-spreadsheet-malware/
Fake Bankline SPAM - malware
- http://blog.dynamoo.com/2015/03/malware-spam-you-have-received-new.html
6 Mar 2015 - "This fake banking spam leads to malware. From: Bankline [secure.message@ business .natwest .com]
Date: 6 March 2015 at 10:36
Subject: You have received a new secure message from BankLine
You have received a secure message.
Your Documents have been uploaded to Cubby cloud storage.
Cubby cloud storage is a cloud data service powered by LogMeIn, Inc.
Read your secure message by following the link bellow: …
…
You will be prompted to open (view) the file or save (download) it to your computer. For best results, save the file first, then open it.
If you have concerns about the validity of this message, please contact the sender directly. For questions please contact the Bankline Bank Secure Email Help Desk at 0131 556 8719.
First time users - will need to register after opening the attachment…
Fake Gateway SPAM - PDF malware
- http://myonlinesecurity.co.uk/your-online-gateway-gov-uk-submission-fake-pdf-malware/
6 Mar 2015 - "'Your online Gateway .gov .uk Submission' pretending to come from Gateway .gov.uk with a link to download a zip attachment is another one from the current bot runs… The email looks like: Your online Gateway .gov.uk Submission
Government Gateway logo
Electronic Submission Gateway
Thank you for your submission for the Government Gateway.
The Government Gateway is the UK’s centralized registration service for e-Government services.
To view/download your form to the Government Gateway please visit http ://www.gateway .gov.uk/
This is an automatically generated email. Please do not reply as the email address is not
monitored for received mail.
gov .uk - the best place to find government services and information - Opens in new window
The best place to find government services and information
The link in the email leads to… the same malware as today’s run of 'You have received a new secure message from BankLine' -fake- PDF malware*.
* http://myonlinesecurity.co.uk/received-new-secure-message-bankline-fake-pdf-malware/
This is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper PDF file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
___
Cryptowall, again!
- https://isc.sans.edu/diary.html?storyid=19427
Last Updated: 2015-03-06 - "A new variant of Cryptowall (An advanced version of cryptolocker) is now using a malicious .chm file attachment to infect systems. According to net-security.org*, Bitdefender labs has found a -spam- wave that spread a malicious .chm attachments. CHM is the compiled version of html that support technologies such as JavaScript which can -redirect- a user to an external link. “Once the content of the .chm archive is accessed, the malicious code downloads from this location http :// *********/putty.exe, saves itself as %temp%\natmasla2.exe and executes the malware. A command prompt window opens during the process”…"
* http://net-security.org/malware_news.php?id=2981
Mar 5, 2015
> http://www.net-security.org/images/articles/cryptowall-calc.jpg