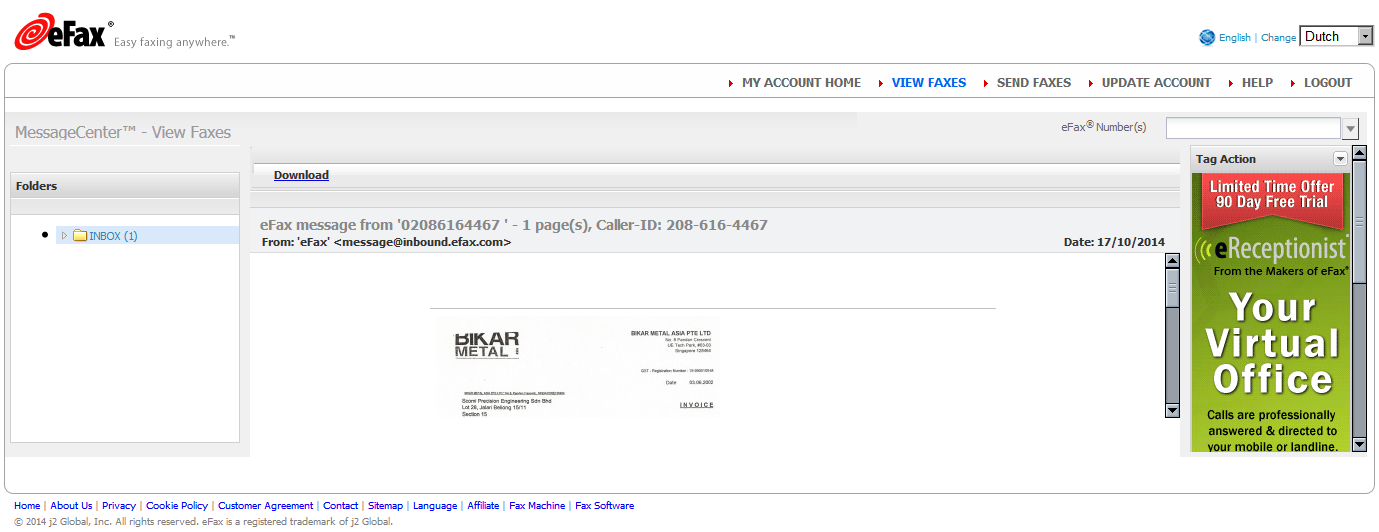
FYI…
Fake NatWest, new FAX SPAM
- http://blog.dynamoo.com/2014/09/malware-spam-natwest-you-have-new.html
30 Sep 2014 - "The daily mixed spam run has just started again, these two samples seen so far this morning:
NatWest: "You have a new Secure Message"
From: NatWest [secure.message@ natwest .com]
Date: 30 September 2014 09:58
Subject: You have a new Secure Message - file-3800
You have received a encrypted message from NatWest Customer Support
In order to view the attachment please open it using your email client ( Microsoft Outlook, Mozilla Thunderbird, Lotus )
Please download your ecnrypted message at …
"You've received a new fax"
From: Fax [fax@victimdomain .com]
Date: 30 September 2014 09:57
Subject: You've received a new fax
New fax at SCAN4148711 from EPSON by https ://victimdomain .com
Scan date: Tue, 30 Sep 2014 14:27:24 +0530
Number of pages: 2
Resolution: 400x400 DPI
You can secure download your fax message at …
The link in the email goes through a script to ensure that you are using a Windows PC and then downloads a file document3009.zip which contains a malicious executable document3009.scr which has a VirusTotal detection rate of 3/54*. The Comodo CAMAS report and Anubis report are rather inconclusive."
* https://www.virustotal.com/en/file/1b09eaabd81bb0a64dc297e1d8fbbde5892e97e43c1fcec237d9f4a4eaf0c566/analysis/1412070442/
… Behavioural information
DNS requests
maazmedia .com ([removed])
TCP connections
188.165.198.52: https://www.virustotal.com/en/ip-address/188.165.198.52/information/
69.89.22.130: https://www.virustotal.com/en/ip-address/69.89.22.130/information/
___
Fake Delta Air SPAM - word doc malware
- http://myonlinesecurity.co.uk/delta-air-thank-order-fake-word-doc-malware/
30 Sep 2014 - "'Delta Air Thank you for your order' being sent to bookings@ uktservices .com and BCC copied to you pretending to come from Delta Air is another one from the current bot runs which try to download various Zbots, cryptolocker, ransomware and loads of other malware on your computer. They are using email addresses and subjects that will entice a user to read the email and open the attachment… The email looks like:
Order Notification,
E-TICKET NUMBER / ET-98191471
SEAT / 79F/ZONE 1
DATE / TIME 2 OCTOBER, 2014, 11:15 PM
ARRIVING / Berlin
FORM OF PAYMENT / XXXXXX
TOTAL PRICE / 214.61 GBP
REF / OE.2368 ST / OK
BAG / 3PC
Your electronic ticket is attached to the letter as a scan document.
You can print your ticket.
Thank you for your attention.
Delta Air Lines.
30 September 2014: ET-17843879.zip: Extracts to: DT-ET_5859799188.exe
Current Virus total detections: 4/55* . This 'Delta Air Thank you for your order' is another one of the spoofed icon files that unless you have “show known file extensions enabled“, will look like a proper Microsoft word .doc file instead of the .exe file it really is, so making it much more likely for you to accidentally open it and be infected…"
* https://www.virustotal.com/en/file/3761b84ab4ee6bded5fd2ed4717d84f73e749d733a2d8bb3765d62e0c4d9fd53/analysis/1412075964/
 <_<