Paulz12
Topic Starter
Installed suspicious .exe by mistake and seems im paying for it.
Task manager completely disabled, when i try and delete the registry value disabling it it simply reappears.
Yellow exclamation banner appears in task bar and several pop ups consistently appear.
Slowed down system performance and ironically messages telling me of this appear in balloons in taskbar.
Have tried using other solutions on this site but have only succeeded in blocking not removing the problems (eg taskbar still greyed, popups mostly stopped)
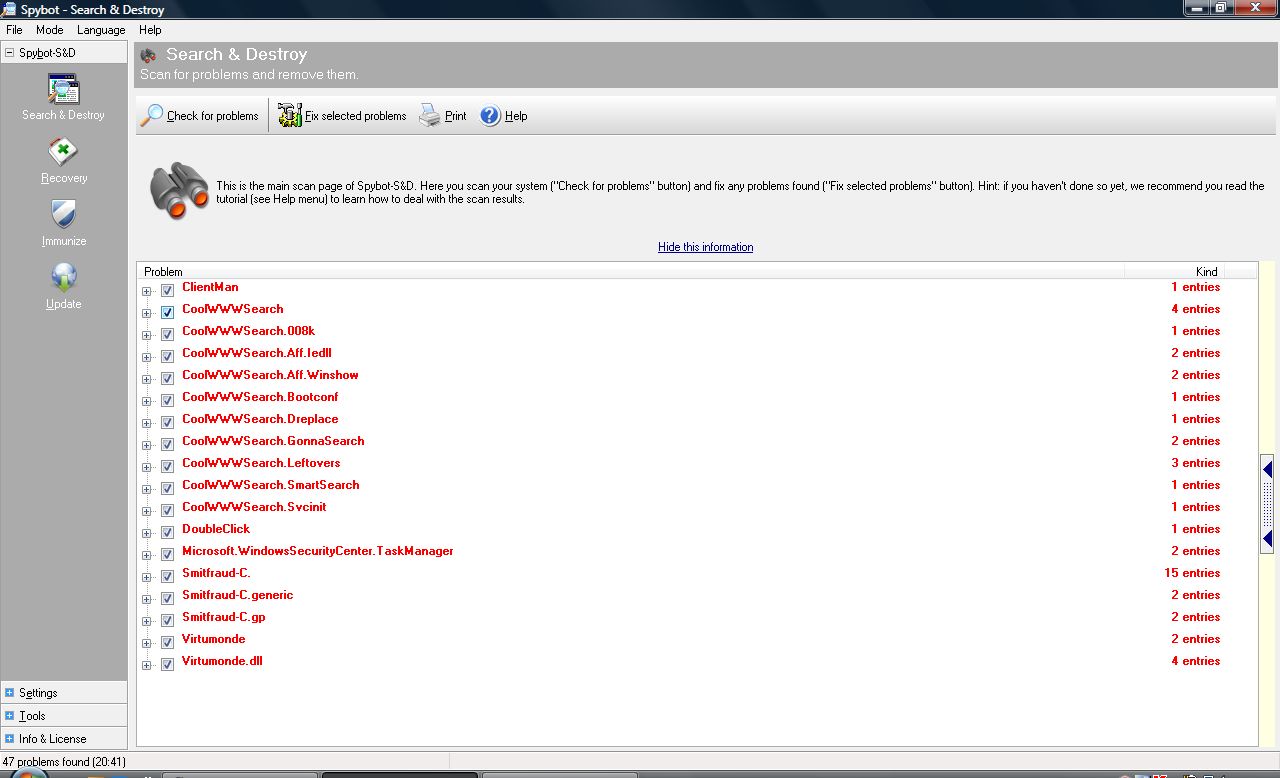
spybot and others still find up to 60 problems
Capture2.JPG
initially scanned with hijackthis and found;
Logfile of HijackThis v1.99.1
Scan saved at 18:09:46, on 26/06/2008
Platform: Unknown Windows (WinNT 6.00.1904)
MSIE: Internet Explorer v7.00 (7.00.6000.16681)
Running processes:
C:\Windows\system32\taskeng.exe
C:\Windows\system32\Dwm.exe
C:\Windows\Explorer.EXE
C:\Program Files\Sony\Wireless Switch Setting Utility\Switcher.exe
C:\Program Files\Sony\VAIO Update 3\VAIOUpdt.exe
C:\Windows\System32\rundll32.exe
C:\Program Files\Kaspersky Lab\Kaspersky Anti-Virus 7.0\avp.exe
C:\Program Files\Windows Live\Messenger\msnmsgr.exe
C:\Program Files\Windows Media Player\wmpnscfg.exe
C:\Windows\system32\wbem\unsecapp.exe
C:\Windows\system32\SearchFilterHost.exe
C:\Program Files\Hijackthis\HijackThis.exe
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =
O2 - BHO: (no name) - {00110011-4b0b-44d5-9718-90c88817369b} - (no file)
O2 - BHO: Adobe PDF Reader Link Helper - {06849E9F-C8D7-4D59-B87D-784B7D6BE0B3} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelper.dll
O2 - BHO: (no name) - {086ae192-23a6-48d6-96ec-715f53797e85} - (no file)
O2 - BHO: (no name) - {150fa160-130d-451f-b863-b655061432ba} - (no file)
O2 - BHO: (no name) - {17da0c9e-4a27-4ac5-bb75-5d24b8cdb972} - (no file)
O2 - BHO: (no name) - {1f48aa48-c53a-4e21-85e7-ac7cc6b5ffb1} - (no file)
O2 - BHO: (no name) - {1f48aa48-c53a-4e21-85e7-ac7cc6b5ffb2} - (no file)
O2 - BHO: (no name) - {2d38a51a-23c9-48a1-a33c-48675aa2b494} - (no file)
O2 - BHO: (no name) - {2e9caff6-30c7-4208-8807-e79d4ec6f806} - (no file)
O2 - BHO: (no name) - {467faeb2-5f5b-4c81-bae0-2a4752ca7f4e} - (no file)
O2 - BHO: (no name) - {5321e378-ffad-4999-8c62-03ca8155f0b3} - (no file)
O2 - BHO: (no name) - {587dbf2d-9145-4c9e-92c2-1f953da73773} - (no file)
O2 - BHO: (no name) - {6cc1c91a-ae8b-4373-a5b4-28ba1851e39a} - (no file)
O2 - BHO: (no name) - {79369d5c-2903-4b7a-ade2-d5e0dee14d24} - (no file)
O2 - BHO: (no name) - {799a370d-5993-4887-9df7-0a4756a77d00} - (no file)
O2 - BHO: Windows Live Sign-in Helper - {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O2 - BHO: (no name) - {98dbbf16-ca43-4c33-be80-99e6694468a4} - (no file)
O2 - BHO: (no name) - {a55581dc-2cdb-4089-8878-71a080b22342} - (no file)
O2 - BHO: (no name) - {b847676d-72ac-4393-bfff-43a1eb979352} - (no file)
O2 - BHO: (no name) - {bc97b254-b2b9-4d40-971d-78e0978f5f26} - (no file)
O2 - BHO: (no name) - {cf021f40-3e14-23a5-cba2-717765721306} - (no file)
O2 - BHO: (no name) - {e2ddf680-9905-4dee-8c64-0a5de7fe133c} - (no file)
O2 - BHO: (no name) - {e3eebbe8-9cab-4c76-b26a-747e25ebb4c6} - (no file)
O2 - BHO: (no name) - {e7afff2a-1b57-49c7-bf6b-e5123394c970} - (no file)
O2 - BHO: (no name) - {E88FAD22-6FD1-471A-B91F-A5364BF55BB1} - C:\Windows\system32\jkkJyvWQ.dll
O2 - BHO: (no name) - {fcaddc14-bd46-408a-9842-cdbe1c6d37eb} - (no file)
O2 - BHO: (no name) - {fd9bc004-8331-4457-b830-4759ff704c22} - (no file)
O2 - BHO: (no name) - {ff1bf4c7-4e08-4a28-a43f-9d60a9f7a880} - (no file)
O4 - HKLM\..\Run: [MSServer] rundll32.exe C:\Windows\system32\ddcDwuRK.dll,#1
O4 - HKLM\..\Run: [AVP] "C:\Program Files\Kaspersky Lab\Kaspersky Anti-Virus 7.0\avp.exe"
O4 - HKLM\..\Run: [BM9129716d] Rundll32.exe "C:\Windows\system32\rxkvpqop.dll",s
O4 - HKCU\..\Run: [msnmsgr] "C:\Program Files\Windows Live\Messenger\msnmsgr.exe" /background
O10 - Unknown file in Winsock LSP: c:\windows\system32\nlaapi.dll
O10 - Unknown file in Winsock LSP: c:\windows\system32\napinsp.dll
O10 - Unknown file in Winsock LSP: c:\program files\bonjour\mdnsnsp.dll
O23 - Service: a-squared Free Service (a2free) - Emsi Software GmbH - C:\Program Files\a-squared Free\a2service.exe
O23 - Service: Kaspersky Anti-Virus 7.0 (AVP) - Unknown owner - C:\Program Files\Kaspersky Lab\Kaspersky Anti-Virus 7.0\avp.exe" -r (file missing)
O23 - Service: @%SystemRoot%\ehome\ehstart.dll,-101 (ehstart) - Unknown owner - %windir%\system32\svchost.exe (file missing)
O23 - Service: SQL Server (VAIO_VEDB) (MSSQL$VAIO_VEDB) - Unknown owner - C:\Program Files\Microsoft SQL Server\MSSQL.1\MSSQL\Binn\sqlservr.exe" -sVAIO_VEDB (file missing)
O23 - Service: @%SystemRoot%\system32\qwave.dll,-1 (QWAVE) - Unknown owner - %windir%\system32\svchost.exe (file missing)
O23 - Service: SBSD Security Center Service (SBSDWSCService) - Safer Networking Ltd. - C:\Program Files\Spybot - Search & Destroy\SDWinSec.exe
O23 - Service: @%SystemRoot%\system32\seclogon.dll,-7001 (seclogon) - Unknown owner - %windir%\system32\svchost.exe (file missing)
O23 - Service: VundoFix Service (VundoFixSvc) - Atribune.org - C:\Windows\SYSTEM32\VundoFixSVC.exe
O23 - Service: @%ProgramFiles%\Windows Media Player\wmpnetwk.exe,-101 (WMPNetworkSvc) - Unknown owner - %ProgramFiles%\Windows Media Player\wmpnetwk.exe (file missing)
removed as many files as possible and blocked one exe using kapersky and logfile is now;
Logfile of HijackThis v1.99.1
Scan saved at 18:34:57, on 26/06/2008
Platform: Unknown Windows (WinNT 6.00.1904)
MSIE: Internet Explorer v7.00 (7.00.6000.16681)
Running processes:
C:\Windows\system32\taskeng.exe
C:\Windows\system32\Dwm.exe
C:\Program Files\Sony\Wireless Switch Setting Utility\Switcher.exe
C:\Program Files\Sony\VAIO Update 3\VAIOUpdt.exe
C:\Program Files\Kaspersky Lab\Kaspersky Anti-Virus 7.0\avp.exe
C:\Program Files\Windows Media Player\wmpnscfg.exe
C:\Windows\system32\wbem\unsecapp.exe
C:\Program Files\Mozilla Firefox\firefox.exe
C:\Windows\explorer.exe
C:\Windows\System32\mobsync.exe
C:\Program Files\Spybot - Search & Destroy\SpybotSD.exe
C:\Windows\system32\SearchFilterHost.exe
C:\Program Files\Hijackthis\HijackThis.exe
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =
O2 - BHO: (no name) - {E88FAD22-6FD1-471A-B91F-A5364BF55BB1} - C:\Windows\system32\jkkJyvWQ.dll
O4 - HKLM\..\Run: [AVP] "C:\Program Files\Kaspersky Lab\Kaspersky Anti-Virus 7.0\avp.exe"
O10 - Unknown file in Winsock LSP: c:\windows\system32\nlaapi.dll
O10 - Unknown file in Winsock LSP: c:\windows\system32\napinsp.dll
O10 - Unknown file in Winsock LSP: c:\program files\bonjour\mdnsnsp.dll
O23 - Service: a-squared Free Service (a2free) - Emsi Software GmbH - C:\Program Files\a-squared Free\a2service.exe
O23 - Service: Kaspersky Anti-Virus 7.0 (AVP) - Unknown owner - C:\Program Files\Kaspersky Lab\Kaspersky Anti-Virus 7.0\avp.exe" -r (file missing)
O23 - Service: @%SystemRoot%\ehome\ehstart.dll,-101 (ehstart) - Unknown owner - %windir%\system32\svchost.exe (file missing)
O23 - Service: SQL Server (VAIO_VEDB) (MSSQL$VAIO_VEDB) - Unknown owner - C:\Program Files\Microsoft SQL Server\MSSQL.1\MSSQL\Binn\sqlservr.exe" -sVAIO_VEDB (file missing)
O23 - Service: @%SystemRoot%\system32\qwave.dll,-1 (QWAVE) - Unknown owner - %windir%\system32\svchost.exe (file missing)
O23 - Service: SBSD Security Center Service (SBSDWSCService) - Safer Networking Ltd. - C:\Program Files\Spybot - Search & Destroy\SDWinSec.exe
O23 - Service: @%SystemRoot%\system32\seclogon.dll,-7001 (seclogon) - Unknown owner - %windir%\system32\svchost.exe (file missing)
O23 - Service: VundoFix Service (VundoFixSvc) - Atribune.org - C:\Windows\SYSTEM32\VundoFixSVC.exe
O23 - Service: @%ProgramFiles%\Windows Media Player\wmpnetwk.exe,-101 (WMPNetworkSvc) - Unknown owner - %ProgramFiles%\Windows Media Player\wmpnetwk.exe (file missing)
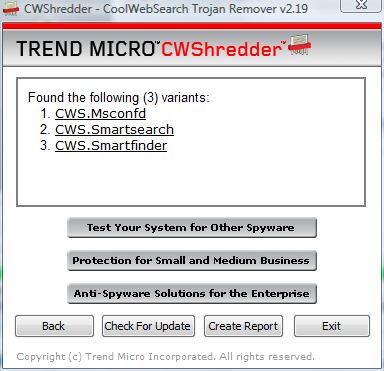
Capture.JPG
used to show around 11 items but now only detects these three : S
any help in getting things back to normal without factore restore would be greatly appreciated