This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

Pop-up window & Browser Alert [Solved]

7 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

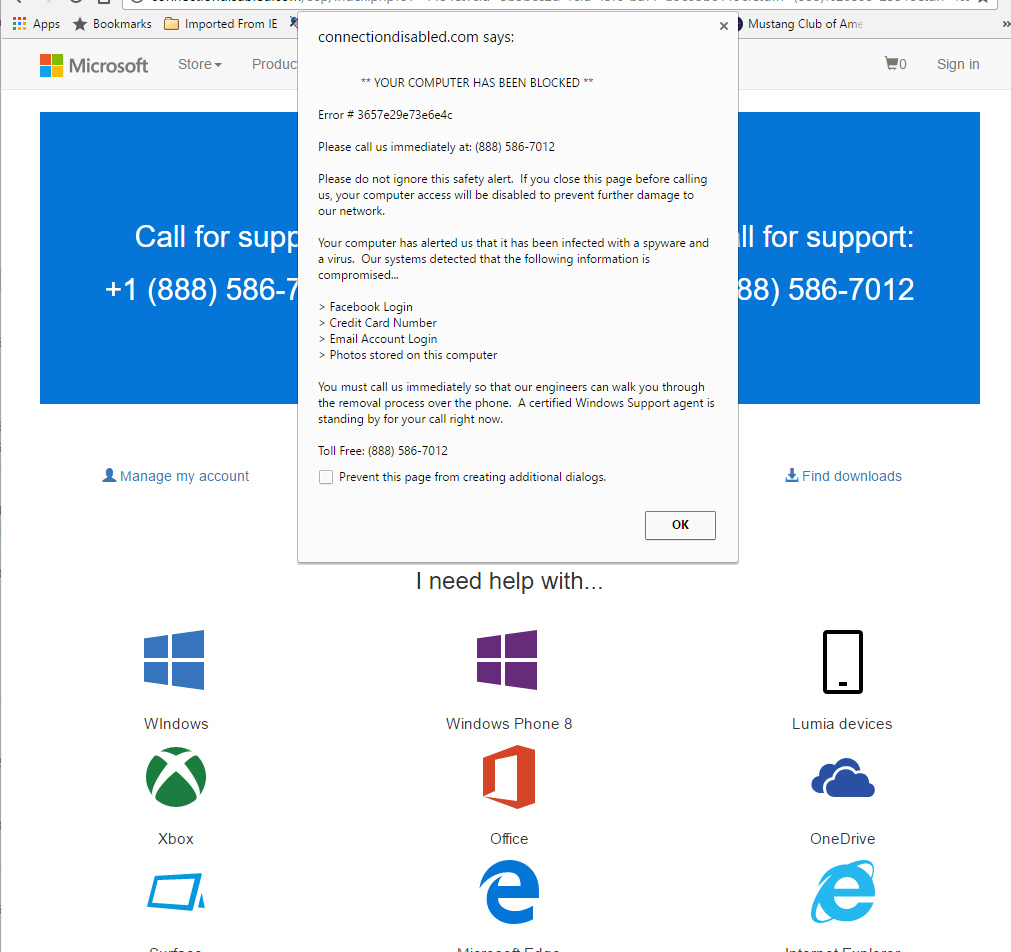
A couple of times over the course of the past week or two, I've had my browser display a page and also open up a sub-window telling me that my computer was infected and that my internet access was blocked.  It said to call a specific number so their technicians can walk me thru the process of removing the virus.  I can eventually close the window and browser tab and move on as nothing happened.  My access doesn't turn off as it said it would…  I did a screen capture of this that I"m hoping will show up here, along with the logs from the aswMBR and FRST.  

Hoping this is something simple!  I appreciate any and all assistance!


Regards, Bob


aswMBR version 1.0.1.2252 Copyright© 2014 AVAST Software
Run date: 2016-09-21 11:54:12
—————————–
11:54:12.964    OS Version: Windows x64 6.2.9200 
11:54:12.964    Number of processors: 8 586 0x2A07
11:54:12.965    ComputerName: PADDY1  UserName: Paddy
11:54:18.595    Initialize success
11:54:18.667    VM: initialized successfully
11:54:18.668    VM: Intel CPU BiosDisabled 
12:05:43.342    AVAST engine defs: 16091202
12:07:56.118    Disk 0 (boot) \Device\Harddisk0\DR0 -> \Device\00000028
12:07:56.119    Disk 0 Vendor: ST31500341AS HP23 Size: 1430799MB BusType: 11
12:07:56.289    Disk 0 MBR read successfully
12:07:56.291    Disk 0 MBR scan
12:07:56.352    Disk 0 unknown MBR code
12:07:56.394    Disk 0 Partition 1 80 (A) 07    HPFS/NTFS NTFS          100 MB offset 2048
12:07:56.456    Disk 0 Partition 2 00     07    HPFS/NTFS NTFS       998979 MB offset 206848
12:07:56.477    Disk 0 Partition - 00     0F Extended LBA            420000 MB offset 2046115840
12:07:56.513    Disk 0 Partition 3 00     07    HPFS/NTFS NTFS        11718 MB offset 2906275840
12:07:56.559    Disk 0 Partition 4 00     07    HPFS/NTFS NTFS       419999 MB offset 2046117888
12:07:56.696    Disk 0 scanning C:\WINDOWS\system32\drivers
12:08:19.291    Service scanning
12:09:04.702    Modules scanning
12:09:04.710    Disk 0 trace - called modules:
12:09:04.745    ntoskrnl.exe CLASSPNP.SYS disk.sys storport.sys hal.dll storahci.sys 
12:09:04.751    1 nt!IofCallDriver -> \Device\Harddisk0\DR0[0xffffe0015a98e060]
12:09:04.758    3 CLASSPNP.SYS[fffff8002d407d95] -> nt!IofCallDriver -> \Device\00000028[0xffffe0015a78a060]
12:09:08.235    AVAST engine scan C:\WINDOWS
12:09:17.667    AVAST engine scan C:\WINDOWS\system32
12:15:55.916    AVAST engine scan C:\WINDOWS\system32\drivers
12:16:37.225    AVAST engine scan C:\Users\Paddy
12:16:41.051    File: C:\Users\Paddy\AppData\Local\Cctbplt\BackgroundContainer\TBUpdaterLogic_4.0.0.2.dll  **INFECTED** Win32:Adware-gen [Adw]
12:16:54.705    File: C:\Users\Paddy\AppData\Local\Conduit\BackgroundContainer\TBUpdaterLogic_4.0.0.1.dll  **INFECTED** Win32:Adware-gen [Adw]
12:16:54.873    File: C:\Users\Paddy\AppData\Local\Conduit\BackgroundContainer\TBUpdaterLogic_4.0.0.2.dll  **INFECTED** Win32:Adware-gen [Adw]
12:16:55.414    File: C:\Users\Paddy\AppData\Local\Conduit\Community Alerts\Alert.dll  **INFECTED** Win32:SearchProtect-DU [Adw]
12:22:14.946    File: C:\Users\Paddy\AppData\Local\Microsoft\Windows\INetCache\IE\DM0J8EE8\TBUpdaterLogic[1].dll  **INFECTED** Win32:Adware-gen [Adw]
12:22:18.923    File: C:\Users\Paddy\AppData\Local\Microsoft\Windows\INetCache\IE\IA1ONQWO\TBUpdaterLogic[1].dll  **INFECTED** Win32:Adware-gen [Adw]
12:45:39.972    File: C:\Users\Paddy\AppData\LocalLow\WhiteSmoke_New\hk64tbWhi0.dll  **INFECTED** Win32:SearchProtect-DU [Adw]
12:45:43.389    File: C:\Users\Paddy\AppData\LocalLow\WhiteSmoke_New\ldrtbWhi0.dll  **INFECTED** Win32:SearchProtect-DU [Adw]
12:45:44.480    File: C:\Users\Paddy\AppData\LocalLow\WhiteSmoke_New\prxtbWhi0.dll  **INFECTED** Win32:SearchProtect-DU [Adw]
12:45:46.097    File: C:\Users\Paddy\AppData\LocalLow\WhiteSmoke_New\tbWhi1.dll  **INFECTED** Win32:BHO-APX [Adw]
12:49:27.584    AVAST engine scan C:\ProgramData
12:55:03.073    Disk 0 statistics 5833254/0/0 @ 1.53 MB/s
12:55:03.085    Scan finished successfully
12:55:49.119    Disk 0 MBR has been saved successfully to "C:\Users\Paddy\Desktop\MBR.dat"
12:55:49.156    The log file has been saved successfully to "C:\Users\Paddy\Desktop\aswMBR.txt"
 
Scan result of Farbar Recovery Scan Tool (FRST) (x64) Version: 21-09-2016
Ran by [removed] (administrator) on PADDY1 (21-09-2016 12:58:17)
Running from C:\Users\[removed]\Desktop
[removed]
Platform: Windows 10 Home Version 1511 (X64) Language: English (United States)
Internet Explorer Version 11 (Default browser: Edge)
Boot Mode: Normal
Tutorial for Farbar Recovery Scan Tool: http://www.geekstogo.com/forum/topic/335081-frst-tutorial-how-to-use-farbar-recovery-scan-tool/
 
==================== Processes (Whitelisted) =================
 
(If an entry is included in the fixlist, the process will be closed. The file will not be moved.)
 
(AMD) C:\Windows\System32\atiesrxx.exe
(IDT, Inc.) C:\Program Files\IDT\WDM\stacsv64.exe
(Microsoft Corporation) C:\Windows\System32\mqsvc.exe
(Apple Inc.) C:\Program Files\Bonjour\mDNSResponder.exe
(Microsoft Corporation) C:\Program Files (x86)\Microsoft Application Virtualization Client\sftvsa.exe
(PDF Complete Inc) C:\Program Files (x86)\PDF Complete\pdfsvc.exe
() C:\Program Files (x86)\Cyberlink\Shared files\RichVideo.exe
(Andrea Electronics Corporation) C:\Program Files\IDT\WDM\AESTSr64.exe
(Apple Inc.) C:\Program Files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
() C:\Program Files\CyberLink\Shared files\RichVideo64.exe
(Microsoft Corporation) C:\Program Files\Windows Defender\MsMpEng.exe
(Hewlett-Packard Company) C:\Program Files\Hewlett-Packard\HP Client Services\HPClientServices.exe
(Microsoft Corporation) C:\Windows\Microsoft.NET\Framework64\v4.0.30319\SMSvcHost.exe
(Microsoft Corporation) C:\Program Files (x86)\Microsoft Application Virtualization Client\sftlist.exe
(Microsoft Corporation) C:\Program Files (x86)\Common Files\Microsoft Shared\Virtualization Handler\CVHSVC.EXE
(Microsoft Corporation) C:\Program Files\Windows Defender\NisSrv.exe
(HP Inc.) C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\HPSupportSolutionsFrameworkService.exe
(Intel Corporation) C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\LMS\LMS.exe
(Intel Corporation) C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\UNS\UNS.exe
(Hewlett-Packard Company) C:\Program Files (x86)\Hewlett-Packard\Shared\hpqwmiex.exe
(AMD) C:\Windows\System32\atieclxx.exe
(Microsoft Corporation) C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\RemindersServer.exe
(Hewlett-Packard) C:\Program Files (x86)\Hewlett-Packard\HP Odometer\hpsysdrv.exe
(IDT, Inc.) C:\Program Files\IDT\WDM\sttray64.exe
(Hewlett-Packard ) C:\Program Files\IDT\WDM\beats64.exe
(AMD) C:\Program Files (x86)\ATI Technologies\HydraVision\HydraDM.exe
(Microsoft Corporation) C:\Windows\SysWOW64\rundll32.exe
(AMD) C:\Program Files (x86)\ATI Technologies\HydraVision\HydraDM64.exe
(Advanced Micro Devices Inc.) C:\Program Files (x86)\ATI Technologies\ATI.ACE\Core-Static\MOM.exe
(Hewlett-Packard) C:\Program Files (x86)\Hp\HP Software Update\hpwuschd2.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Advanced Micro Devices Inc.) C:\Program Files (x86)\ATI Technologies\ATI.ACE\Core-Static\CCC.exe
() C:\Program Files\WindowsApps\Microsoft.Messaging_2.15.20002.0_x86__8wekyb3d8bbwe\SkypeHost.exe
(Microsoft Corporation) C:\Windows\System32\SettingSyncHost.exe
() C:\Program Files\WindowsApps\Microsoft.Windows.Photos_16.722.10060.0_x64__8wekyb3d8bbwe\Microsoft.Photos.exe
() C:\Program Files\WindowsApps\Microsoft.WindowsCalculator_10.1608.2213.0_x64__8wekyb3d8bbwe\Calculator.exe
(Microsoft Corporation) C:\Program Files\Common Files\microsoft shared\ink\InputPersonalization.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Microsoft Inc.) C:\Program Files\WindowsApps\Microsoft.MicrosoftSolitaireCollection_3.12.8312.0_x64__8wekyb3d8bbwe\Solitaire.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\53.0.2785.116\nacl64.exe
(Apache Software Foundation) C:\Program Files (x86)\OpenOffice 4\program\swriter.exe
(Apache Software Foundation) C:\Program Files (x86)\OpenOffice 4\program\soffice.exe
(Apache Software Foundation) C:\Program Files (x86)\OpenOffice 4\program\soffice.bin
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Microsoft Corporation) C:\Program Files\Windows Defender\MpCmdRun.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Microsoft Corporation) C:\Program Files\WindowsApps\microsoft.windowscommunicationsapps_17.7167.40721.0_x64__8wekyb3d8bbwe\HxTsr.exe
 
 
==================== Registry (Whitelisted) ===========================
 
(If an entry is included in the fixlist, the registry item will be restored to default or removed. The file will not be moved.)
 
HKLM\…\Run: [Logitech Download Assistant] => C:\Windows\System32\LogiLDA.dll [1832760 2012-09-20] (Logitech, Inc.)
HKLM\…\Run: [hpsysdrv] => c:\program files (x86)\hewlett-packard\HP odometer\hpsysdrv.exe [62768 2008-11-20] (Hewlett-Packard)
HKLM\…\Run: [SysTrayApp] => C:\Program Files\IDT\WDM\sttray64.exe [1425408 2012-04-24] (IDT, Inc.)
HKLM\…\Run: [BeatsOSDApp] => C:\Program Files\IDT\WDM\beats64.exe [37888 2011-08-24] (Hewlett-Packard )
HKLM-x32\…\Run: [StartCCC] => C:\Program Files (x86)\ATI Technologies\ATI.ACE\Core-Static\amd64\CLIStart.exe [767176 2015-11-04] (Advanced Micro Devices, Inc.)
HKLM-x32\…\Run: [HP Software Update] => c:\Program Files (x86)\HP\HP Software Update\HPWuSchd2.exe [54576 2008-12-08] (Hewlett-Packard)
HKLM-x32\…\Run: [mcui_exe] => "C:\Program Files\McAfee.com\Agent\mcagent.exe" /runkey
HKLM-x32\…\Run: [APSDaemon] => C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe [43848 2014-04-23] (Apple Inc.)
HKLM-x32\…\Run: [iTunesHelper] => C:\Program Files (x86)\iTunes\iTunesHelper.exe [152392 2014-05-26] (Apple Inc.)
HKLM-x32\…\Run: [SunJavaUpdateSched] => C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe [596528 2015-11-09] (Oracle Corporation)
HKLM-x32\…\Run: [QuickTime Task] => C:\Program Files (x86)\QuickTime\QTTask.exe [421888 2015-06-17] (Apple Inc.)
Winlogon\Notify\ScCertProp: wlnotify.dll [X]
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\Run: [HydraVisionDesktopManager] => C:\Program Files (x86)\ATI Technologies\HydraVision\HydraDM.exe [393216 2011-10-24] (AMD)
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\Run: [GoogleChromeAutoLaunch_3C506A97676A871F60321234A2B923FD] => C:\Program Files (x86)\Google\Chrome\Application\chrome.exe [967496 2016-09-13] (Google Inc.)
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\Run: [BackgroundContainerV3] => C:\Users\Paddy\AppData\Local\Cctbplt\BackgroundContainer\BackgroundContainer.dll [300352 2016-04-29] (ClientConnect Ltd.)
ShellIconOverlayIdentifiers: [MOBK] -> {3c3f3c1a-9153-7c05-f938-622e7003894d} => C:\Program Files (x86)\McAfee Online Backup\MOBKshell.dll [2010-04-13] (McAfee, Inc.)
ShellIconOverlayIdentifiers: [MOBK2] -> {e6ea1d7d-144e-b977-98c4-84c53c1a69d0} => C:\Program Files (x86)\McAfee Online Backup\MOBKshell.dll [2010-04-13] (McAfee, Inc.)
ShellIconOverlayIdentifiers: [MOBK3] -> {b4caf489-1eec-c617-49ad-8d7088598c06} => C:\Program Files (x86)\McAfee Online Backup\MOBKshell.dll [2010-04-13] (McAfee, Inc.)
Startup: C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Startup\Adobe Gamma.lnk [2013-01-09]
ShortcutTarget: Adobe Gamma.lnk -> C:\Program Files (x86)\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe (Adobe Systems, Inc.)
 
==================== Internet (Whitelisted) ====================
 
(If an item is included in the fixlist, if it is a registry item it will be removed or restored to default.)
 
Tcpip\Parameters: [DhcpNameServer] 10.1.10.1
Tcpip\..\Interfaces\{54536d99-20d6-4e60-948b-17d85e127466}: [DhcpNameServer] 10.1.10.1
 
Internet Explorer:
==================
HKLM\SOFTWARE\Policies\Microsoft\Internet Explorer: Restriction <======= ATTENTION
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\Policies\Microsoft\Internet Explorer: Restriction <======= ATTENTION
HKU\.DEFAULT\Software\Microsoft\Internet Explorer\Main,Search Page = hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar;=iesearch
HKU\.DEFAULT\Software\Microsoft\Internet Explorer\Main,Start Page = hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar;=msnhome
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\Main,Search Page = hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar;=iesearch
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\Main,Start Page Redirect Cache = hxxp://www.msn.com/
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\Main,Start Page = hxxp://www.bing.com/?pc=COSP&ptag;=G3A0B15BED265&conlogo;=CT3210127
URLSearchHook: HKLM-x32 - WhiteSmoke New Toolbar - {739df940-c5ee-4bab-9d7e-270894ae687a} - C:\Users\Paddy\AppData\LocalLow\WhiteSmoke_New\prxtbWhi0.dll (ClientConnect Ltd.)
URLSearchHook: HKU\S-1-5-21-648858125-4165233436-1298442668-1001 - WhiteSmoke New Toolbar - {739df940-c5ee-4bab-9d7e-270894ae687a} - C:\Users\Paddy\AppData\LocalLow\WhiteSmoke_New\prxtbWhi0.dll (ClientConnect Ltd.)
SearchScopes: HKLM -> DefaultScope value is missing
SearchScopes: HKLM -> {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL = hxxp://www.bing.com/search?q={searchTerms}&form;=HPDTDF&pc;=HPDTDF&src;=IE-SearchBox
SearchScopes: HKLM -> {b7fca997-d0fb-4fe0-8afd-255e89cf9671} URL = hxxp://search.yahoo.com/search?p={searchTerms}&ei;={inputEncoding}&fr;=chr-hp-psg&type;=HPDTDF
SearchScopes: HKLM -> {BC005D3D-84AA-42A0-913D-5F80610219F5} URL = hxxp://www.amazon.com/s/ref=azs_osd_iea?ie=UTF-8&tag;=hp-us1-vsb-20&link;%5Fcode=qs&index;=aps&field-keywords;={searchTerms}
SearchScopes: HKLM -> {d43b3890-80c7-4010-a95d-1e77b5924dc3} URL = hxxp://en.wikipedia.org/wiki/Special:Search?search={searchTerms}
SearchScopes: HKLM -> {D944BB61-2E34-4DBF-A683-47E505C587DC} URL = hxxp://rover.ebay.com/rover/1/711-30572-11896-1/4?mpre=hxxp://shop.ebay.com/?_nkw={searchTerms}
SearchScopes: HKLM-x32 -> DefaultScope {863FD1AF-2869-4CE9-A223-2BA9F9620E61} URL = 
SearchScopes: HKLM-x32 -> {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL = hxxp://www.bing.com/search?q={searchTerms}&form;=HPDTDF&pc;=HPDTDF&src;=IE-SearchBox
SearchScopes: HKLM-x32 -> {b7fca997-d0fb-4fe0-8afd-255e89cf9671} URL = hxxp://search.yahoo.com/search?p={searchTerms}&ei;={inputEncoding}&fr;=chr-hp-psg&type;=HPDTDF
SearchScopes: HKLM-x32 -> {BC005D3D-84AA-42A0-913D-5F80610219F5} URL = hxxp://www.amazon.com/s/ref=azs_osd_iea?ie=UTF-8&tag;=hp-us1-vsb-20&link;%5Fcode=qs&index;=aps&field-keywords;={searchTerms}
SearchScopes: HKLM-x32 -> {d43b3890-80c7-4010-a95d-1e77b5924dc3} URL = hxxp://en.wikipedia.org/wiki/Special:Search?search={searchTerms}
SearchScopes: HKLM-x32 -> {D944BB61-2E34-4DBF-A683-47E505C587DC} URL = hxxp://rover.ebay.com/rover/1/711-30572-11896-1/4?mpre=hxxp://shop.ebay.com/?_nkw={searchTerms}
SearchScopes: HKU\S-1-5-21-648858125-4165233436-1298442668-1001 -> DefaultScope {863FD1AF-2869-4CE9-A223-2BA9F9620E61} URL = hxxp://search.conduit.com/ResultsExt.aspx?q={searchTerms}&SearchSource;=4&ctid;=CT3289847&CUI;=UN19383994629633973&UM;=2&SSPV;=TB_T5
SearchScopes: HKU\S-1-5-21-648858125-4165233436-1298442668-1001 -> {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL = hxxp://www.bing.com/search?pc=COSP&ptag;=G3A0B15BED265&form;=CONBDF&conlogo;=CT3210127&q;={searchTerms}
SearchScopes: HKU\S-1-5-21-648858125-4165233436-1298442668-1001 -> {77E4343C-FD7A-48DD-A140-771EF668F9E6} URL = hxxp://us.yhs4.search.yahoo.com/yhs/search?hspart=mcafee&hsimp;=yhs-01&type;=mcafee&p;={SearchTerms}
SearchScopes: HKU\S-1-5-21-648858125-4165233436-1298442668-1001 -> {863FD1AF-2869-4CE9-A223-2BA9F9620E61} URL = hxxp://search.conduit.com/ResultsExt.aspx?q={searchTerms}&SearchSource;=4&ctid;=CT3289847&CUI;=UN19383994629633973&UM;=2&SSPV;=TB_T5
SearchScopes: HKU\S-1-5-21-648858125-4165233436-1298442668-1001 -> {BC005D3D-84AA-42A0-913D-5F80610219F5} URL = 
SearchScopes: HKU\S-1-5-21-648858125-4165233436-1298442668-1001 -> {d43b3890-80c7-4010-a95d-1e77b5924dc3} URL = 
SearchScopes: HKU\S-1-5-21-648858125-4165233436-1298442668-1001 -> {D944BB61-2E34-4DBF-A683-47E505C587DC} URL = 
BHO: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2016-04-26] (Google Inc.)
BHO: HP Network Check Helper -> {E76FD755-C1BA-4DCB-9F13-99BD91223ADE} -> C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPNetworkCheck\HPNetworkCheckPluginx64.dll [2016-07-21] (HP Inc.)
BHO-x32: HelperObject Class -> {00C6482D-C502-44C8-8409-FCE54AD9C208} -> C:\Program Files (x86)\TechSmith\SnagIt 7\SnagItBHO.dll [2005-03-09] (TechSmith Corporation)
BHO-x32: &Yahoo;! Toolbar Helper -> {02478D38-C3F9-4efb-9B51-7695ECA05670} -> C:\Program Files (x86)\Yahoo!\Companion\Installs\cpn1\yt.dll [2012-03-20] (Yahoo! Inc.)
BHO-x32: WhiteSmoke New Toolbar -> {739df940-c5ee-4bab-9d7e-270894ae687a} -> C:\Users\Paddy\AppData\LocalLow\WhiteSmoke_New\prxtbWhi0.dll [2014-09-23] (ClientConnect Ltd.)
BHO-x32: Java™ Plug-In SSV Helper -> {761497BB-D6F0-462C-B6EB-D4DAF1D92D43} -> C:\Program Files (x86)\Java\jre1.8.0_66\bin\ssv.dll [2015-12-22] (Oracle Corporation)
BHO-x32: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2016-04-26] (Google Inc.)
BHO-x32: Java™ Plug-In 2 SSV Helper -> {DBC80044-A445-435b-BC74-9C25C1C588A9} -> C:\Program Files (x86)\Java\jre1.8.0_66\bin\jp2ssv.dll [2015-12-22] (Oracle Corporation)
BHO-x32: HP Network Check Helper -> {E76FD755-C1BA-4DCB-9F13-99BD91223ADE} -> C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPNetworkCheck\HPNetworkCheckPlugin.dll [2016-07-21] (HP Inc.)
Toolbar: HKLM - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2016-04-26] (Google Inc.)
Toolbar: HKLM-x32 - SnagIt - {8FF5E183-ABDE-46EB-B09E-D2AAB95CABE3} - C:\Program Files (x86)\TechSmith\SnagIt 7\SnagItIEAddin.dll [2005-03-09] (TechSmith Corporation)
Toolbar: HKLM-x32 - Yahoo! Toolbar - {EF99BD32-C1FB-11D2-892F-0090271D4F88} - C:\Program Files (x86)\Yahoo!\Companion\Installs\cpn1\yt.dll [2012-03-20] (Yahoo! Inc.)
Toolbar: HKLM-x32 - WhiteSmoke New Toolbar - {739df940-c5ee-4bab-9d7e-270894ae687a} - C:\Users\Paddy\AppData\LocalLow\WhiteSmoke_New\prxtbWhi0.dll [2014-09-23] (ClientConnect Ltd.)
Toolbar: HKLM-x32 - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2016-04-26] (Google Inc.)
Toolbar: HKU\S-1-5-21-648858125-4165233436-1298442668-1001 -> No Name - {739DF940-C5EE-4BAB-9D7E-270894AE687A} -  No File
DPF: HKLM-x32 {0E5F0222-96B9-11D3-8997-00104BD12D94} hxxp://pcpitstop.com/betapit/PCPitStop.CAB
DPF: HKLM-x32 {1851174C-97BD-4217-A0CC-E908F60D5B7A} hxxps://h50203.www5.hp.com/HPISWeb/Customer/cabs/HPISDataManager.CAB
 
FireFox:
========
FF Plugin: @adobe.com/FlashPlayer -> C:\WINDOWS\system32\Macromed\Flash\NPSWF64_23_0_0_179.dll [2016-09-21] ()
FF Plugin: @Microsoft.com/NpCtrl,version=1.0 -> c:\Program Files\Microsoft Silverlight\5.1.50709.0\npctrl.dll [2016-07-11] ( Microsoft Corporation)
FF Plugin-x32: @adobe.com/FlashPlayer -> C:\WINDOWS\SysWOW64\Macromed\Flash\NPSWF32_23_0_0_179.dll [2016-09-21] ()
FF Plugin-x32: @Apple.com/iTunes,version=1.0 -> C:\Program Files (x86)\iTunes\Mozilla Plugins\npitunes.dll [2014-02-21] ()
FF Plugin-x32: @canon.com/MycameraPlugin -> C:\Program Files (x86)\Canon\MyCamera Download Plugin\NPCIG.dll [2008-10-15] (CANON INC.)
FF Plugin-x32: @Google.com/GoogleEarthPlugin -> C:\Program Files (x86)\Google\Google Earth\plugin\npgeplugin.dll [2015-05-21] (Google)
FF Plugin-x32: @java.com/DTPlugin,version=11.66.2 -> C:\WINDOWS\SysWOW64\npdeployJava1.dll [2015-12-22] (Oracle Corporation)
FF Plugin-x32: @java.com/JavaPlugin -> C:\Program Files (x86)\Java\jre1.8.0_66\bin\plugin2\npjp2.dll [2015-12-22] (Oracle Corporation)
FF Plugin-x32: @java.com/JavaPlugin,version=11.66.2 -> C:\Program Files (x86)\Java\jre1.8.0_66\bin\plugin2\npjp2.dll [2015-12-22] (Oracle Corporation)
FF Plugin-x32: @Microsoft.com/NpCtrl,version=1.0 -> c:\Program Files (x86)\Microsoft Silverlight\5.1.50709.0\npctrl.dll [2016-07-11] ( Microsoft Corporation)
FF Plugin-x32: @microsoft.com/SharePoint,version=14.0 -> C:\PROGRA~2\MICROS~1\Office14\NPSPWRAP.DLL [2010-03-24] (Microsoft Corporation)
FF Plugin-x32: @microsoft.com/WLPG,version=15.4.3502.0922 -> C:\Program Files (x86)\Windows Live\Photo Gallery\NPWLPG.dll [2014-03-31] (Microsoft Corporation)
FF Plugin-x32: @microsoft.com/WLPG,version=16.4.3528.0331 -> C:\Program Files (x86)\Windows Live\Photo Gallery\NPWLPG.dll [2014-03-31] (Microsoft Corporation)
FF Plugin-x32: @tools.google.com/Google Update;version=3 -> C:\Program Files (x86)\Google\Update\1.3.31.5\npGoogleUpdate3.dll [2016-07-29] (Google Inc.)
FF Plugin-x32: @tools.google.com/Google Update;version=9 -> C:\Program Files (x86)\Google\Update\1.3.31.5\npGoogleUpdate3.dll [2016-07-29] (Google Inc.)
FF Plugin-x32: @videolan.org/vlc,version=2.0.8 -> C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll [2015-04-13] (VideoLAN)
FF Plugin-x32: @videolan.org/vlc,version=2.1.2 -> C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll [2015-04-13] (VideoLAN)
FF Plugin-x32: @videolan.org/vlc,version=2.2.1 -> C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll [2015-04-13] (VideoLAN)
FF Plugin-x32: @WildTangent.com/GamesAppPresenceDetector,Version=1.0 -> C:\Program Files (x86)\WildTangent Games\App\BrowserIntegration\Registered\0\NP_wtapp.dll [2010-12-07] ()
FF Plugin-x32: Adobe Reader -> C:\Program Files (x86)\Adobe\Acrobat Reader DC\Reader\AIR\nppdf32.dll [2016-06-30] (Adobe Systems Inc.)
FF Plugin HKU\S-1-5-21-648858125-4165233436-1298442668-1001: @hulu.com/Hulu Desktop -> C:\Users\Default.migrated\AppData\Local\HuluDesktop\instances\0.9.13.1\nphdplg.dll [No File]
StartMenuInternet: FIREFOX.EXE - firefox.exe
 
Chrome: 
=======
CHR HomePage: Default -> hxxp://www.hotmail.com/
CHR StartupUrls: Default -> "hxxp://www.google.com/","hxxp://search.conduit.com/?ctid=CT3289847&SearchSource;=48&CUI;=UN19927041542956553&UM;=2"
CHR Session Restore: Default -> is enabled.
CHR Plugin: (Widevine Content Decryption Module) - C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\WidevineCDM\1.4.2.464\_platform_specific\win_x86\widevinecdmadapter.dll => No File
CHR Plugin: (Shockwave Flash) - C:\Program Files (x86)\Google\Chrome\Application\53.0.2785.116\PepperFlash\pepflashplayer.dll ()
CHR Plugin: (Native Client) - C:\Program Files (x86)\Google\Chrome\Application\53.0.2785.116\ppGoogleNaClPluginChrome.dll => No File
CHR Plugin: (Chrome PDF Viewer) - C:\Program Files (x86)\Google\Chrome\Application\53.0.2785.116\pdf.dll => No File
CHR Plugin: (QuickTime Plug-in 7.7.4) - C:\Program Files (x86)\QuickTime\plugins\npqtplugin.dll (Apple Inc.)
CHR Plugin: (QuickTime Plug-in 7.7.4) - C:\Program Files (x86)\QuickTime\plugins\npqtplugin2.dll (Apple Inc.)
CHR Plugin: (QuickTime Plug-in 7.7.4) - C:\Program Files (x86)\QuickTime\plugins\npqtplugin3.dll (Apple Inc.)
CHR Plugin: (QuickTime Plug-in 7.7.4) - C:\Program Files (x86)\QuickTime\plugins\npqtplugin4.dll (Apple Inc.)
CHR Plugin: (QuickTime Plug-in 7.7.4) - C:\Program Files (x86)\QuickTime\plugins\npqtplugin5.dll (Apple Inc.)
CHR Plugin: (Microsoft Office 2010) - C:\PROGRA~2\MICROS~1\Office14\NPSPWRAP.DLL (Microsoft Corporation)
CHR Plugin: (NPCIG.dll) - C:\Program Files (x86)\Canon\MyCamera Download Plugin\NPCIG.dll (CANON INC.)
CHR Plugin: (Google Earth Plugin) - C:\Program Files (x86)\Google\Google Earth\plugin\npgeplugin.dll (Google)
CHR Plugin: (Google Update) - C:\Program Files (x86)\Google\Update\1.3.22.5\npGoogleUpdate3.dll => No File
CHR Plugin: (Java Deployment Toolkit 7.0.510.13) - C:\Program Files (x86)\Java\jre7\bin\dtplugin\npDeployJava1.dll => No File
CHR Plugin: (Java(TM) Platform SE 7 U51) - C:\Program Files (x86)\Java\jre7\bin\plugin2\npjp2.dll => No File
CHR Plugin: (McAfee Virtual Technician) - C:\Program Files (x86)\McAfee\Supportability\MVT\npmvtplugin.dll => No File
CHR Plugin: (VLC Web Plugin) - C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll (VideoLAN)
CHR Plugin: (Windows Live Photo Gallery) - C:\Program Files (x86)\Windows Live\Photo Gallery\NPWLPG.dll (Microsoft Corporation)
CHR Plugin: (Hulu Desktop) - C:\Windows\..\Users\Default\AppData\Local\HuluDesktop\instances\0.9.13.1\npHDPlg.dll (Hulu LLC)
CHR Plugin: (Shockwave Flash) - C:\Windows\SysWOW64\Macromed\Flash\NPSWF32_13_0_0_154.dll => No File
CHR Plugin: (McAfee SecurityCenter) - c:\PROGRA~2\mcafee\msc\NPMCSN~1.DLL => No File
CHR Plugin: (Silverlight Plug-In) - c:\Program Files (x86)\Microsoft Silverlight\5.1.20913.0\npctrl.dll => No File
CHR Profile: C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default [2016-09-21]
CHR Extension: (YouTube) - C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Extensions\blpcfgokakmgnkcojhhkbfbldkacnbeo [2015-12-16]
CHR Extension: (Google Search) - C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Extensions\coobgpohoikkiipiblmjeljniedjpjpf [2015-12-16]
CHR Extension: (Chrome Web Store Payments) - C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Extensions\nmmhkkegccagdldgiimedpiccmgmieda [2016-04-29]
CHR Extension: (Gmail) - C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Extensions\pjkljhegncpnkpknbcohdijeoejaedia [2015-04-12]
CHR Extension: (Chrome Media Router) - C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Extensions\pkedcjkdefgpdelpbcmbmeomcjbeemfm [2016-09-18]
CHR HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\Google\Chrome\Extensions\…\Chrome\Extension: [klibnahbojhkanfgaglnlalfkgpcppfi] - C:\Users\Paddy\AppData\Local\CRE\klibnahbojhkanfgaglnlalfkgpcppfi.crx
CHR HKLM-x32\…\Chrome\Extension: [klibnahbojhkanfgaglnlalfkgpcppfi] - C:\Users\Paddy\AppData\Local\CRE\klibnahbojhkanfgaglnlalfkgpcppfi.crx
 
==================== Services (Whitelisted) ========================
 
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
 
S3 Adobe LM Service; C:\Program Files (x86)\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe [72704 2013-01-09] (Adobe Systems) [File not signed]
S2 CLKMSVC10_38F51D56; c:\Program Files (x86)\Cyberlink\PowerDVD10\NavFilter\kmsvc.exe [241648 2011-01-25] (CyberLink)
R2 HPSupportSolutionsFrameworkService; C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\HPSupportSolutionsFrameworkService.exe [29728 2016-08-15] (HP Inc.)
R2 pdfcDispatcher; C:\Program Files (x86)\PDF Complete\pdfsvc.exe [1127448 2011-02-01] (PDF Complete Inc)
R2 RichVideo; C:\Program Files (x86)\Cyberlink\Shared files\RichVideo.exe [254552 2012-10-18] ()
R2 RichVideo64; C:\Program Files\CyberLink\Shared files\RichVideo64.exe [390672 2012-10-16] ()
S3 vmicvss; C:\Windows\System32\ICSvc.dll [511488 2016-09-07] (Microsoft Corporation)
R3 WdNisSvc; C:\Program Files\Windows Defender\NisSrv.exe [364456 2016-09-07] (Microsoft Corporation)
R2 WinDefend; C:\Program Files\Windows Defender\MsMpEng.exe [24864 2016-09-07] (Microsoft Corporation)
 
===================== Drivers (Whitelisted) ==========================
 
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
 
R3 AtiHDAudioService; C:\Windows\system32\drivers\AtihdWT6.sys [102912 2015-05-28] (Advanced Micro Devices)
S3 dot4; C:\Windows\system32\DRIVERS\Dot4.sys [151968 2012-10-19] (Windows (R) Win 7 DDK provider)
S3 Dot4Print; C:\Windows\System32\drivers\Dot4Prt.sys [27040 2012-10-19] (Windows (R) Win 7 DDK provider)
R1 MOBKFilter; C:\Windows\System32\DRIVERS\MOBK.sys [66040 2010-04-13] (Mozy, Inc.)
R3 rt640x64; C:\Windows\System32\drivers\rt640x64.sys [589824 2015-10-30] (Realtek                                            )
R3 S3XXx64; C:\Windows\system32\DRIVERS\S3XXx64.sys [73856 2015-02-17] (Identiv)
R3 scsiscan; C:\Windows\system32\DRIVERS\scsiscan.sys [20480 2015-10-30] (Microsoft Corporation)
R0 szkg5; C:\Windows\SysWow64\DRIVERS\szkg64.sys [74768 2011-09-26] (iS3 Inc.)
R3 tilfilter; C:\Windows\System32\drivers\TIxHCIlfilter.sys [34424 2016-08-20] (Texas Instruments, Inc.)
R3 tiufilter; C:\Windows\System32\drivers\TIxHCIufilter.sys [39032 2016-08-20] (Texas Instruments, Inc.)
S0 WdBoot; C:\Windows\System32\drivers\WdBoot.sys [44568 2015-10-30] (Microsoft Corporation)
R0 WdFilter; C:\Windows\System32\drivers\WdFilter.sys [293216 2015-10-30] (Microsoft Corporation)
R3 WdNisDrv; C:\Windows\System32\Drivers\WdNisDrv.sys [118112 2015-10-30] (Microsoft Corporation)
R2 {B154377D-700F-42cc-9474-23858FBDF4BD}; C:\Program Files (x86)\CyberLink\PowerDVD9\000.fcl [146928 2009-09-01] (CyberLink Corp.)
U3 aswMBR; C:\Users\Paddy\AppData\Local\Temp\aswMBR.sys [62728 2016-09-21] () [File not signed]
U3 aswVmm; C:\Users\Paddy\AppData\Local\Temp\aswVmm.sys [224896 2016-09-21] ()
U3 idsvc; no ImagePath
U3 wpcsvc; no ImagePath
 
==================== NetSvcs (Whitelisted) ===================
 
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
 
 
==================== One Month Created files and folders ========
 
(If an entry is included in the fixlist, the file/folder will be moved.)
 
2016-09-21 12:58 - 2016-09-21 12:58 - 00027642 _____ C:\Users\Paddy\Desktop\FRST.txt
2016-09-21 12:57 - 2016-09-21 12:58 - 00000000 ____D C:\FRST
2016-09-21 12:55 - 2016-09-21 12:55 - 00003578 _____ C:\Users\Paddy\Desktop\aswMBR.txt
2016-09-21 12:55 - 2016-09-21 12:55 - 00000512 _____ C:\Users\Paddy\Desktop\MBR.dat
2016-09-21 11:51 - 2016-09-21 12:57 - 02402816 _____ (Farbar) C:\Users\Paddy\Desktop\FRST64.exe
2016-09-21 11:51 - 2016-09-21 11:54 - 05198336 _____ (AVAST Software) C:\Users\Paddy\Desktop\aswMBR.exe
2016-09-21 10:54 - 2016-09-21 10:54 - 00000000 ____D C:\BadStuff
2016-09-20 22:38 - 2016-09-20 22:38 - 00000000 ___HD C:\$WINDOWS.~BT
2016-09-14 08:29 - 2016-09-07 01:26 - 02544256 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfcore.dll
2016-09-14 08:29 - 2016-09-07 00:48 - 22379520 _____ (Microsoft Corporation) C:\WINDOWS\system32\edgehtml.dll
2016-09-14 08:29 - 2016-09-07 00:43 - 16985600 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Xaml.dll
2016-09-14 08:29 - 2016-09-07 00:35 - 24611840 _____ (Microsoft Corporation) C:\WINDOWS\system32\mshtml.dll
2016-09-14 08:29 - 2016-09-07 00:31 - 00794624 _____ (Microsoft Corporation) C:\WINDOWS\system32\winhttp.dll
2016-09-14 08:29 - 2016-09-07 00:30 - 00602624 _____ (Microsoft Corporation) C:\WINDOWS\system32\vbscript.dll
2016-09-14 08:29 - 2016-09-07 00:29 - 19350016 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mshtml.dll
2016-09-14 08:28 - 2016-09-07 01:39 - 02656952 _____ C:\WINDOWS\system32\CoreUIComponents.dll
2016-09-14 08:28 - 2016-09-07 01:39 - 01098640 _____ (Microsoft Corporation) C:\WINDOWS\system32\MrmCoreR.dll
2016-09-14 08:28 - 2016-09-07 01:39 - 00277848 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\sdbus.sys
2016-09-14 08:28 - 2016-09-07 01:37 - 00572272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\taskschd.dll
2016-09-14 08:28 - 2016-09-07 01:33 - 00026408 _____ (Microsoft Corporation) C:\WINDOWS\system32\wuauclt.exe
2016-09-14 08:28 - 2016-09-07 01:26 - 01299504 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfnetsrc.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 01152320 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfasfsrcsnk.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 01092464 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfplat.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 00858952 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfnetcore.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 00847648 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfsvr.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 00785088 _____ (Microsoft Corporation) C:\WINDOWS\system32\evr.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 00588320 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmdrmdev.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 00245840 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfps.dll
2016-09-14 08:28 - 2016-09-07 01:25 - 02607336 _____ (Microsoft Corporation) C:\WINDOWS\system32\combase.dll
2016-09-14 08:28 - 2016-09-07 01:25 - 01270064 _____ (Microsoft Corporation) C:\WINDOWS\system32\WinTypes.dll
2016-09-14 08:28 - 2016-09-07 01:24 - 01349632 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\winmde.dll
2016-09-14 08:28 - 2016-09-07 01:24 - 00511312 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mf.dll
2016-09-14 08:28 - 2016-09-07 01:24 - 00496360 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wmdrmdev.dll
2016-09-14 08:28 - 2016-09-07 01:23 - 01750440 _____ (Microsoft Corporation) C:\WINDOWS\system32\WpcMon.exe
2016-09-14 08:28 - 2016-09-07 01:23 - 01603224 _____ (Microsoft Corporation) C:\WINDOWS\system32\propsys.dll
2016-09-14 08:28 - 2016-09-07 01:23 - 01040792 _____ (Microsoft Corporation) C:\WINDOWS\system32\twinapi.appcore.dll
2016-09-14 08:28 - 2016-09-07 01:23 - 00725776 _____ (Microsoft Corporation) C:\WINDOWS\system32\SHCore.dll
2016-09-14 08:28 - 2016-09-07 01:22 - 01128096 _____ (Microsoft Corporation) C:\WINDOWS\system32\ClipUp.exe
2016-09-14 08:28 - 2016-09-07 01:20 - 00569744 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SHCore.dll
2016-09-14 08:28 - 2016-09-07 01:19 - 00294752 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msv1_0.dll
2016-09-14 08:28 - 2016-09-07 01:15 - 00911640 _____ (Microsoft Corporation) C:\WINDOWS\system32\dcomp.dll
2016-09-14 08:28 - 2016-09-07 01:12 - 01174008 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msctf.dll
2016-09-14 08:28 - 2016-09-07 00:46 - 00123392 _____ (Microsoft Corporation) C:\WINDOWS\system32\mssprxy.dll
2016-09-14 08:28 - 2016-09-07 00:41 - 00313856 _____ (Microsoft Corporation) C:\WINDOWS\system32\DictationManager.dll
2016-09-14 08:28 - 2016-09-07 00:41 - 00124928 _____ (Microsoft Corporation) C:\WINDOWS\system32\shsetup.dll
2016-09-14 08:28 - 2016-09-07 00:41 - 00094720 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\UserDataTimeUtil.dll
2016-09-14 08:28 - 2016-09-07 00:39 - 01567744 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Globalization.dll
2016-09-14 08:28 - 2016-09-07 00:39 - 00075264 _____ (Microsoft Corporation) C:\WINDOWS\system32\wiarpc.dll
2016-09-14 08:28 - 2016-09-07 00:38 - 00206848 _____ (Microsoft Corporation) C:\WINDOWS\system32\LegacyNetUXHost.exe
2016-09-14 08:28 - 2016-09-07 00:37 - 00617984 _____ (Microsoft Corporation) C:\WINDOWS\system32\StorSvc.dll
2016-09-14 08:28 - 2016-09-07 00:37 - 00381952 _____ (Microsoft Corporation) C:\WINDOWS\system32\apprepsync.dll
2016-09-14 08:28 - 2016-09-07 00:37 - 00092160 _____ (Microsoft Corporation) C:\WINDOWS\system32\mshtmled.dll
2016-09-14 08:28 - 2016-09-07 00:36 - 00489984 _____ (Microsoft Corporation) C:\WINDOWS\system32\authfwcfg.dll
2016-09-14 08:28 - 2016-09-07 00:36 - 00457216 _____ (Microsoft Corporation) C:\WINDOWS\system32\azroleui.dll
2016-09-14 08:28 - 2016-09-07 00:36 - 00287744 _____ (Microsoft Corporation) C:\WINDOWS\system32\apprepapi.dll
2016-09-14 08:28 - 2016-09-07 00:36 - 00174592 _____ (Microsoft Corporation) C:\WINDOWS\system32\easwrt.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00814592 _____ (Microsoft Corporation) C:\WINDOWS\system32\msctfuimanager.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00394240 _____ (Microsoft Corporation) C:\WINDOWS\system32\Search.ProtocolHandler.MAPI2.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00393216 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wbemcomn.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00383488 _____ (Microsoft Corporation) C:\WINDOWS\system32\iedkcs32.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00339968 _____ (Microsoft Corporation) C:\WINDOWS\system32\SensorService.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00254464 _____ (Microsoft Corporation) C:\WINDOWS\system32\ExecModelClient.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00206848 _____ (Microsoft Corporation) C:\WINDOWS\system32\SharedStartModelShim.dll
2016-09-14 08:28 - 2016-09-07 00:34 - 00952320 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.PointOfService.dll
2016-09-14 08:28 - 2016-09-07 00:34 - 00727040 _____ (Microsoft Corporation) C:\WINDOWS\system32\nshwfp.dll
2016-09-14 08:28 - 2016-09-07 00:33 - 00316416 _____ (Microsoft Corporation) C:\WINDOWS\system32\sti.dll
2016-09-14 08:28 - 2016-09-07 00:32 - 00643584 _____ (Microsoft Corporation) C:\WINDOWS\system32\wiaservc.dll
2016-09-14 08:28 - 2016-09-07 00:32 - 00581632 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\apphelp.dll
2016-09-14 08:28 - 2016-09-07 00:32 - 00356864 _____ (Microsoft Corporation) C:\WINDOWS\system32\ActivationManager.dll
2016-09-14 08:28 - 2016-09-07 00:32 - 00334848 _____ (Microsoft Corporation) C:\WINDOWS\system32\SearchProtocolHost.exe
2016-09-14 08:28 - 2016-09-07 00:32 - 00275968 _____ (Microsoft Corporation) C:\WINDOWS\system32\facecredentialprovider.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00828928 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.AccountsControl.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00821760 _____ (Microsoft Corporation) C:\WINDOWS\system32\MrmIndexer.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00753664 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msctfuimanager.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00610304 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmdrmsdk.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00504320 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppReadiness.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00335872 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\iedkcs32.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00262144 _____ (Microsoft Corporation) C:\WINDOWS\system32\webcheck.dll
2016-09-14 08:28 - 2016-09-07 00:30 - 18676224 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\edgehtml.dll
2016-09-14 08:28 - 2016-09-07 00:30 - 02127360 _____ (Microsoft Corporation) C:\WINDOWS\system32\inetcpl.cpl
2016-09-14 08:28 - 2016-09-07 00:30 - 01707520 _____ (Microsoft Corporation) C:\WINDOWS\system32\msdtctm.dll
2016-09-14 08:28 - 2016-09-07 00:30 - 01001472 _____ (Microsoft Corporation) C:\WINDOWS\system32\schedsvc.dll
2016-09-14 08:28 - 2016-09-07 00:30 - 00904704 _____ (Microsoft Corporation) C:\WINDOWS\system32\rpcss.dll
2016-09-14 08:28 - 2016-09-07 00:30 - 00870400 _____ (Microsoft Corporation) C:\WINDOWS\system32\modernexecserver.dll
2016-09-14 08:28 - 2016-09-07 00:30 - 00784384 _____ (Microsoft Corporation) C:\WINDOWS\system32\msfeeds.dll
2016-09-14 08:28 - 2016-09-07 00:28 - 00938496 _____ (Microsoft Corporation) C:\WINDOWS\system32\SearchIndexer.exe
2016-09-14 08:28 - 2016-09-07 00:28 - 00780800 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\tdh.dll
2016-09-14 08:28 - 2016-09-07 00:28 - 00674816 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MiracastReceiver.dll
2016-09-14 08:28 - 2016-09-07 00:28 - 00400896 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\winspool.drv
2016-09-14 08:28 - 2016-09-07 00:28 - 00296448 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\sysdm.cpl
2016-09-14 08:28 - 2016-09-07 00:27 - 01743872 _____ (Microsoft Corporation) C:\WINDOWS\system32\wevtsvc.dll
2016-09-14 08:28 - 2016-09-07 00:27 - 01131520 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Media.Audio.dll
2016-09-14 08:28 - 2016-09-07 00:27 - 00963072 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wsp_health.dll
2016-09-14 08:28 - 2016-09-07 00:27 - 00552960 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\AppointmentApis.dll
2016-09-14 08:28 - 2016-09-07 00:27 - 00521728 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wmdrmsdk.dll
2016-09-14 08:28 - 2016-09-07 00:27 - 00329216 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\upnphost.dll
2016-09-14 08:28 - 2016-09-07 00:26 - 13392384 _____ (Microsoft Corporation) C:\WINDOWS\system32\ieframe.dll
2016-09-14 08:28 - 2016-09-07 00:26 - 02050048 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\inetcpl.cpl
2016-09-14 08:28 - 2016-09-07 00:26 - 01508352 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\winmsipc.dll
2016-09-14 08:28 - 2016-09-07 00:26 - 01063936 _____ (Microsoft Corporation) C:\WINDOWS\system32\comdlg32.dll
2016-09-14 08:28 - 2016-09-07 00:26 - 00854528 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Devices.Bluetooth.dll
2016-09-14 08:28 - 2016-09-07 00:26 - 00687616 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msfeeds.dll
2016-09-14 08:28 - 2016-09-07 00:26 - 00638464 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Networking.dll
2016-09-14 08:28 - 2016-09-07 00:25 - 01526272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ieapfltr.dll
2016-09-14 08:28 - 2016-09-07 00:25 - 01166848 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Pimstore.dll
2016-09-14 08:28 - 2016-09-07 00:25 - 00769536 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ContactApis.dll
2016-09-14 08:28 - 2016-09-07 00:24 - 03695104 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\D3DCompiler_47.dll
2016-09-14 08:28 - 2016-09-07 00:24 - 03428864 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Media.dll
2016-09-14 08:28 - 2016-09-07 00:24 - 01276928 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wsp_fs.dll
2016-09-14 08:28 - 2016-09-07 00:24 - 00785920 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mprddm.dll
2016-09-14 08:28 - 2016-09-07 00:23 - 00980480 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\winipcsecproc.dll
2016-09-14 08:28 - 2016-09-07 00:23 - 00838144 _____ (Microsoft Corporation) C:\WINDOWS\system32\uDWM.dll
2016-09-14 08:28 - 2016-09-07 00:23 - 00701952 _____ (Microsoft Corporation) C:\WINDOWS\system32\twinapi.dll
2016-09-14 08:28 - 2016-09-07 00:22 - 12134400 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ieframe.dll
2016-09-14 08:28 - 2016-09-07 00:22 - 02582016 _____ (Microsoft Corporation) C:\WINDOWS\system32\MFMediaEngine.dll
2016-09-14 08:28 - 2016-09-07 00:21 - 03046400 _____ (Microsoft Corporation) C:\WINDOWS\system32\xpsservices.dll
2016-09-14 08:28 - 2016-09-07 00:21 - 01797120 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Immersive.dll
2016-09-14 08:28 - 2016-09-07 00:20 - 02352128 _____ (Microsoft Corporation) C:\WINDOWS\system32\authui.dll
2016-09-14 08:28 - 2016-09-07 00:19 - 03663360 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\jscript9.dll
2016-09-14 08:28 - 2016-09-07 00:19 - 02102272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\xpsservices.dll
2016-09-14 08:28 - 2016-09-07 00:19 - 01072128 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Web.Http.dll
2016-09-14 08:28 - 2016-09-07 00:18 - 03577344 _____ (Microsoft Corporation) C:\WINDOWS\system32\tquery.dll
2016-09-14 08:28 - 2016-09-07 00:18 - 02876928 _____ (Microsoft Corporation) C:\WINDOWS\system32\Wpc.dll
2016-09-14 08:28 - 2016-09-07 00:18 - 00592384 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Web.dll
2016-09-14 08:28 - 2016-09-07 00:18 - 00451072 _____ (Microsoft Corporation) C:\WINDOWS\system32\XpsDocumentTargetPrint.dll
2016-09-14 08:28 - 2016-09-07 00:17 - 02679808 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\netshell.dll
2016-09-14 08:28 - 2016-09-07 00:17 - 02285568 _____ (Microsoft Corporation) C:\WINDOWS\system32\WpcWebSync.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 04412928 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ExplorerFrame.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 03671040 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msi.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 02911744 _____ (Microsoft Corporation) C:\WINDOWS\system32\CertEnroll.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 02746368 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.StateRepository.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 02597888 _____ (Microsoft Corporation) C:\WINDOWS\system32\mssrch.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 02280960 _____ (Microsoft Corporation) C:\WINDOWS\system32\wuaueng.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 02217984 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Wpc.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 01676800 _____ (Microsoft Corporation) C:\WINDOWS\system32\XpsPrint.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 01194496 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Xaml.Phone.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 01123328 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\XpsPrint.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 00314880 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\XpsDocumentTargetPrint.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 07831552 _____ (Microsoft Corporation) C:\WINDOWS\system32\Chakra.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 05659136 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Chakra.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 02604032 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\CertEnroll.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 02055168 _____ (Microsoft Corporation) C:\WINDOWS\system32\OpcServices.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 00835072 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Media.Streaming.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 00573440 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\UserLanguagesCpl.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 00416256 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\hnetcfg.dll
2016-09-14 08:28 - 2016-09-07 00:14 - 06743040 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mstscax.dll
2016-09-14 08:28 - 2016-09-07 00:14 - 04895232 _____ (Microsoft Corporation) C:\WINDOWS\system32\jscript9.dll
2016-09-14 08:28 - 2016-09-07 00:14 - 01946112 _____ (Microsoft Corporation) C:\WINDOWS\system32\dwmcore.dll
2016-09-14 08:28 - 2016-09-07 00:13 - 04171264 _____ (Microsoft Corporation) C:\WINDOWS\system32\rdpcorets.dll
2016-09-14 08:28 - 2016-09-07 00:13 - 02874880 _____ (Microsoft Corporation) C:\WINDOWS\system32\mmcndmgr.dll
2016-09-14 08:28 - 2016-09-07 00:11 - 03065344 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mstsc.exe
2016-09-14 08:27 - 2016-09-07 01:39 - 00845568 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MrmCoreR.dll
2016-09-14 08:27 - 2016-09-07 01:39 - 00754664 _____ (Microsoft Corporation) C:\WINDOWS\system32\CoreMessaging.dll
2016-09-14 08:27 - 2016-09-07 01:39 - 00620176 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\kernel32.dll
2016-09-14 08:27 - 2016-09-07 01:34 - 02587696 _____ (Microsoft Corporation) C:\WINDOWS\system32\msxml6.dll
2016-09-14 08:27 - 2016-09-07 01:33 - 01297760 _____ (Microsoft Corporation) C:\WINDOWS\system32\LicenseManager.dll
2016-09-14 08:27 - 2016-09-07 01:33 - 00986976 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\LicenseManager.dll
2016-09-14 08:27 - 2016-09-07 01:27 - 00538632 _____ (Microsoft Corporation) C:\WINDOWS\system32\WWanAPI.dll
2016-09-14 08:27 - 2016-09-07 01:27 - 00413536 _____ (Microsoft Corporation) C:\WINDOWS\system32\wifitask.exe
2016-09-14 08:27 - 2016-09-07 01:26 - 00586200 _____ (Microsoft Corporation) C:\WINDOWS\system32\mf.dll
2016-09-14 08:27 - 2016-09-07 01:24 - 03693064 _____ (Microsoft Corporation) C:\WINDOWS\system32\iertutil.dll
2016-09-14 08:27 - 2016-09-07 01:24 - 00808288 _____ (Microsoft Corporation) C:\WINDOWS\system32\WWAHost.exe
2016-09-14 08:27 - 2016-09-07 01:24 - 00501600 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\NetSetupEngine.dll
2016-09-14 08:27 - 2016-09-07 01:24 - 00355672 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\netcfgx.dll
2016-09-14 08:27 - 2016-09-07 01:23 - 22561256 _____ (Microsoft Corporation) C:\WINDOWS\system32\shell32.dll
2016-09-14 08:27 - 2016-09-07 01:23 - 06605544 _____ (Microsoft Corporation) C:\WINDOWS\system32\windows.storage.dll
2016-09-14 08:27 - 2016-09-07 01:23 - 06536248 _____ (Microsoft Corporation) C:\WINDOWS\system32\sppsvc.exe
2016-09-14 08:27 - 2016-09-07 01:22 - 02937384 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\iertutil.dll
2016-09-14 08:27 - 2016-09-07 01:22 - 01085728 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\webservices.dll
2016-09-14 08:27 - 2016-09-07 01:22 - 00604920 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\cng.sys
2016-09-14 08:27 - 2016-09-07 01:12 - 02195632 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\d3d10warp.dll
2016-09-14 08:27 - 2016-09-07 01:08 - 00116216 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\sspicli.dll
2016-09-14 08:27 - 2016-09-07 00:52 - 01035776 _____ (Microsoft Corporation) C:\WINDOWS\system32\XboxNetApiSvc.dll
2016-09-14 08:27 - 2016-09-07 00:52 - 00084480 _____ (Microsoft Corporation) C:\WINDOWS\system32\rdpudd.dll
2016-09-14 08:27 - 2016-09-07 00:49 - 00649216 _____ (Microsoft Corporation) C:\WINDOWS\system32\ngcsvc.dll
2016-09-14 08:27 - 2016-09-07 00:48 - 00957952 _____ (Microsoft Corporation) C:\WINDOWS\system32\IKEEXT.DLL
2016-09-14 08:27 - 2016-09-07 00:47 - 00824320 _____ (Microsoft Corporation) C:\WINDOWS\system32\WpcWebFilter.dll
2016-09-14 08:27 - 2016-09-07 00:46 - 00088576 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\olepro32.dll
2016-09-14 08:27 - 2016-09-07 00:44 - 00134656 _____ (Microsoft Corporation) C:\WINDOWS\system32\wificonnapi.dll
2016-09-14 08:27 - 2016-09-07 00:44 - 00069120 _____ (Microsoft Corporation) C:\WINDOWS\system32\pngfilt.dll
2016-09-14 08:27 - 2016-09-07 00:42 - 00572928 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WpcWebFilter.dll
2016-09-14 08:27 - 2016-09-07 00:42 - 00050176 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MosHostClient.dll
2016-09-14 08:27 - 2016-09-07 00:41 - 00066048 _____ (Microsoft Corporation) C:\WINDOWS\system32\OnDemandConnRouteHelper.dll
2016-09-14 08:27 - 2016-09-07 00:41 - 00056832 _____ (Microsoft Corporation) C:\WINDOWS\system32\fwcfg.dll
2016-09-14 08:27 - 2016-09-07 00:41 - 00047616 _____ (Microsoft Corporation) C:\WINDOWS\system32\deviceassociation.dll
2016-09-14 08:27 - 2016-09-07 00:41 - 00025600 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\odbcconf.dll
2016-09-14 08:27 - 2016-09-07 00:40 - 00027648 _____ (Microsoft Corporation) C:\WINDOWS\system32\CheckNetIsolation.exe
2016-09-14 08:27 - 2016-09-07 00:39 - 00059904 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\udhisapi.dll
2016-09-14 08:27 - 2016-09-07 00:38 - 00254464 _____ (Microsoft Corporation) C:\WINDOWS\system32\prnntfy.dll
2016-09-14 08:27 - 2016-09-07 00:38 - 00059392 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MosStorage.dll
2016-09-14 08:27 - 2016-09-07 00:38 - 00038912 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wsmprovhost.exe
2016-09-14 08:27 - 2016-09-07 00:38 - 00035840 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\upnpcont.exe
2016-09-14 08:27 - 2016-09-07 00:37 - 00435712 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.AllJoyn.dll
2016-09-14 08:27 - 2016-09-07 00:37 - 00145408 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WsmAuto.dll
2016-09-14 08:27 - 2016-09-07 00:37 - 00087040 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MapsBtSvc.dll
2016-09-14 08:27 - 2016-09-07 00:37 - 00035328 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\deviceassociation.dll
2016-09-14 08:27 - 2016-09-07 00:37 - 00026624 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WsmAgent.dll
2016-09-14 08:27 - 2016-09-07 00:36 - 06572032 _____ (Microsoft Corporation) C:\WINDOWS\system32\wwanmm.dll
2016-09-14 08:27 - 2016-09-07 00:36 - 01568768 _____ (Microsoft Corporation) C:\WINDOWS\system32\msdt.exe
2016-09-14 08:27 - 2016-09-07 00:36 - 01051136 _____ (Microsoft Corporation) C:\WINDOWS\system32\DiagCpl.dll
2016-09-14 08:27 - 2016-09-07 00:36 - 00764928 _____ (Microsoft Corporation) C:\WINDOWS\system32\Chakradiag.dll
2016-09-14 08:27 - 2016-09-07 00:36 - 00319488 _____ (Microsoft Corporation) C:\WINDOWS\system32\dot3ui.dll
2016-09-14 08:27 - 2016-09-07 00:36 - 00200192 _____ (Microsoft Corporation) C:\WINDOWS\system32\WUDFPlatform.dll
2016-09-14 08:27 - 2016-09-07 00:36 - 00102912 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\shsetup.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00704000 _____ (Microsoft Corporation) C:\WINDOWS\system32\CellularAPI.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00591872 _____ (Microsoft Corporation) C:\WINDOWS\system32\SmsRouterSvc.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00577536 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.ApplicationModel.Wallet.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00458752 _____ (Microsoft Corporation) C:\WINDOWS\system32\PlayToDevice.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00256512 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\unimdm.tsp
2016-09-14 08:27 - 2016-09-07 00:35 - 00119296 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Media.Streaming.ps.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00070656 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\AppCapture.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00052736 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\vsstrace.dll
2016-09-14 08:27 - 2016-09-07 00:34 - 00387072 _____ (Microsoft Corporation) C:\WINDOWS\system32\qdvd.dll
2016-09-14 08:27 - 2016-09-07 00:34 - 00371712 _____ (Microsoft Corporation) C:\WINDOWS\system32\MDEServer.exe
2016-09-14 08:27 - 2016-09-07 00:34 - 00344064 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.Picker.dll
2016-09-14 08:27 - 2016-09-07 00:34 - 00305152 _____ (Microsoft Corporation) C:\WINDOWS\system32\edputil.dll
2016-09-14 08:27 - 2016-09-07 00:33 - 00847360 _____ (Microsoft Corporation) C:\WINDOWS\system32\netlogon.dll
2016-09-14 08:27 - 2016-09-07 00:33 - 00576000 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Networking.UX.EapRequestHandler.dll
2016-09-14 08:27 - 2016-09-07 00:33 - 00330240 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.ApplicationModel.Store.TestingFramework.dll
2016-09-14 08:27 - 2016-09-07 00:33 - 00290304 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WmpDui.dll
2016-09-14 08:27 - 2016-09-07 00:33 - 00238080 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WsmWmiPl.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 01048576 _____ (Microsoft Corporation) C:\WINDOWS\system32\WebcamUi.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 00947200 _____ (Microsoft Corporation) C:\WINDOWS\system32\rasgcw.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 00738816 _____ (Microsoft Corporation) C:\WINDOWS\system32\SmartCardSimulator.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 00517632 _____ (Microsoft Corporation) C:\WINDOWS\system32\winspool.drv
2016-09-14 08:27 - 2016-09-07 00:32 - 00466944 _____ (Microsoft Corporation) C:\WINDOWS\system32\wwanconn.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 00444928 _____ (Microsoft Corporation) C:\WINDOWS\system32\das.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 00432640 _____ (Microsoft Corporation) C:\WINDOWS\system32\CredProvDataModel.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 00407040 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\srv.sys
2016-09-14 08:27 - 2016-09-07 00:31 - 01216512 _____ (Microsoft Corporation) C:\WINDOWS\system32\netcenter.dll
2016-09-14 08:27 - 2016-09-07 00:31 - 00859136 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.ApplicationModel.Store.dll
2016-09-14 08:27 - 2016-09-07 00:31 - 00578560 _____ (Microsoft Corporation) C:\WINDOWS\system32\mscms.dll
2016-09-14 08:27 - 2016-09-07 00:31 - 00541184 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\GamePanel.exe
2016-09-14 08:27 - 2016-09-07 00:31 - 00538112 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Cortana.Desktop.dll
2016-09-14 08:27 - 2016-09-07 00:31 - 00435200 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.ApplicationModel.Wallet.dll
2016-09-14 08:27 - 2016-09-07 00:31 - 00334336 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\bcastdvr.exe
2016-09-14 08:27 - 2016-09-07 00:31 - 00114688 _____ (Microsoft Corporation) C:\WINDOWS\system32\offlinelsa.dll
2016-09-14 08:27 - 2016-09-07 00:30 - 02476032 _____ (Microsoft Corporation) C:\WINDOWS\system32\MSAJApi.dll
2016-09-14 08:27 - 2016-09-07 00:30 - 00698368 _____ (Microsoft Corporation) C:\WINDOWS\system32\PlayToManager.dll
2016-09-14 08:27 - 2016-09-07 00:30 - 00436224 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mprdim.dll
2016-09-14 08:27 - 2016-09-07 00:30 - 00349696 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MapConfiguration.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 02624512 _____ (Microsoft Corporation) C:\WINDOWS\system32\InputService.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 01319424 _____ (Microsoft Corporation) C:\WINDOWS\system32\wifinetworkmanager.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 01213440 _____ (Microsoft Corporation) C:\WINDOWS\system32\wwansvc.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00888320 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Networking.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00841728 _____ (Microsoft Corporation) C:\WINDOWS\system32\win32spl.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00669696 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.Sensors.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00499712 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MessagingDataModel2.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00442368 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\dlnashext.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00286208 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\mrxsmb10.sys
2016-09-14 08:27 - 2016-09-07 00:29 - 00250880 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.ApplicationModel.Store.TestingFramework.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00242688 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\sti.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00199680 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SyncSettings.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 01752576 _____ (Microsoft Corporation) C:\WINDOWS\system32\ieapfltr.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 01291776 _____ (Microsoft Corporation) C:\WINDOWS\system32\werconcpl.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00879616 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WebcamUi.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00846336 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\rasgcw.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00800768 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\JpMapControl.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00755712 _____ (Microsoft Corporation) C:\WINDOWS\system32\spoolsv.exe
2016-09-14 08:27 - 2016-09-07 00:28 - 00673280 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00654336 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\winipcsecproc_ssp.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00645120 _____ (Microsoft Corporation) C:\WINDOWS\system32\wpnapps.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00614400 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\winhttp.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00381952 _____ (Microsoft Corporation) C:\WINDOWS\system32\wuuhext.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00337920 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Geolocation.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00334848 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\CredProvDataModel.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00284160 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\eappcfg.dll
2016-09-14 08:27 - 2016-09-07 00:27 - 01139712 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\vssapi.dll
2016-09-14 08:27 - 2016-09-07 00:27 - 00784896 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\NMAA.dll
2016-09-14 08:27 - 2016-09-07 00:27 - 00708608 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\CPFilters.dll
2016-09-14 08:27 - 2016-09-07 00:27 - 00549888 _____ (Microsoft Corporation) C:\WINDOWS\system32\SearchFolder.dll
2016-09-14 08:27 - 2016-09-07 00:27 - 00230400 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\webcheck.dll
2016-09-14 08:27 - 2016-09-07 00:26 - 01588224 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msxml3.dll
2016-09-14 08:27 - 2016-09-07 00:26 - 01497088 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WMPDMC.exe
2016-09-14 08:27 - 2016-09-07 00:26 - 00711680 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MapControlCore.dll
2016-09-14 08:27 - 2016-09-07 00:26 - 00482816 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\duser.dll
2016-09-14 08:27 - 2016-09-07 00:26 - 00321024 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\syncutil.dll
2016-09-14 08:27 - 2016-09-07 00:25 - 06312448 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Search.dll
2016-09-14 08:27 - 2016-09-07 00:25 - 06296064 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mos.dll
2016-09-14 08:27 - 2016-09-07 00:25 - 04404736 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Search.dll
2016-09-14 08:27 - 2016-09-07 00:25 - 01944576 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\InputService.dll
2016-09-14 08:27 - 2016-09-07 00:25 - 00888832 _____ (Microsoft Corporation) C:\WINDOWS\system32\printfilterpipelinesvc.exe
2016-09-14 08:27 - 2016-09-07 00:25 - 00501760 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Devices.Sensors.dll
2016-09-14 08:27 - 2016-09-07 00:23 - 01562112 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mmc.exe
2016-09-14 08:27 - 2016-09-07 00:23 - 01309696 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wdc.dll
2016-09-14 08:27 - 2016-09-07 00:23 - 00787456 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Web.dll
2016-09-14 08:27 - 2016-09-07 00:22 - 02106368 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\storagewmi.dll
2016-09-14 08:27 - 2016-09-07 00:21 - 02527232 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mispace.dll
2016-09-14 08:27 - 2016-09-07 00:21 - 01410560 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Web.Http.dll
2016-09-14 08:27 - 2016-09-07 00:20 - 00870400 _____ (Microsoft Corporation) C:\WINDOWS\system32\wpncore.dll
2016-09-14 08:27 - 2016-09-07 00:19 - 05325824 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Data.Pdf.dll
2016-09-14 08:27 - 2016-09-07 00:19 - 01388544 _____ (Microsoft Corporation) C:\WINDOWS\system32\lsasrv.dll
2016-09-14 08:27 - 2016-09-07 00:19 - 00503296 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SettingSync.dll
2016-09-14 08:27 - 2016-09-07 00:18 - 07536640 _____ (Microsoft Corporation) C:\WINDOWS\system32\mstscax.dll
2016-09-14 08:27 - 2016-09-07 00:18 - 05205504 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\BingMaps.dll
2016-09-14 08:27 - 2016-09-07 00:18 - 04826624 _____ (Microsoft Corporation) C:\WINDOWS\system32\ExplorerFrame.dll
2016-09-14 08:27 - 2016-09-07 00:18 - 00450560 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SyncController.dll
2016-09-14 08:27 - 2016-09-07 00:17 - 03459584 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\UIRibbon.dll
2016-09-14 08:27 - 2016-09-07 00:17 - 02175488 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppXDeploymentServer.dll
2016-09-14 08:27 - 2016-09-07 00:17 - 01526784 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Xaml.Phone.dll
2016-09-14 08:27 - 2016-09-07 00:17 - 01502208 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\urlmon.dll
2016-09-14 08:27 - 2016-09-07 00:16 - 02444288 _____ (Microsoft Corporation) C:\WINDOWS\system32\twinui.appcore.dll
2016-09-14 08:27 - 2016-09-07 00:16 - 02361856 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mmcndmgr.dll
2016-09-14 08:27 - 2016-09-07 00:16 - 02155008 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\authui.dll
2016-09-14 08:27 - 2016-09-07 00:16 - 00232448 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\notepad.exe
2016-09-14 08:27 - 2016-09-07 00:15 - 02067968 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppXDeploymentExtensions.dll
2016-09-14 08:27 - 2016-09-07 00:15 - 01626112 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\dwmcore.dll
2016-09-14 08:27 - 2016-09-07 00:15 - 01448960 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\dui70.dll
2016-09-14 08:27 - 2016-09-07 00:15 - 01249280 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\usercpl.dll
2016-09-14 08:27 - 2016-09-07 00:15 - 01121792 _____ (Microsoft Corporation) C:\WINDOWS\system32\localspl.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 03351040 _____ (Microsoft Corporation) C:\WINDOWS\system32\msi.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 03078656 _____ (Microsoft Corporation) C:\WINDOWS\system32\wininet.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 02573824 _____ (Microsoft Corporation) C:\WINDOWS\system32\WsmSvc.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 02553856 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wininet.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 02177024 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WsmSvc.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 01708032 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ActiveSyncProvider.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 01487872 _____ (Microsoft Corporation) C:\WINDOWS\system32\SpeechPal.dll
2016-09-14 08:27 - 2016-09-07 00:12 - 02180096 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.StateRepository.dll
2016-09-14 08:27 - 2016-09-07 00:11 - 03053568 _____ (Microsoft Corporation) C:\WINDOWS\system32\rdpcore.dll
2016-09-14 08:27 - 2016-09-07 00:10 - 01035776 _____ (Microsoft Corporation) C:\WINDOWS\system32\TSWorkspace.dll
2016-09-14 08:27 - 2016-09-07 00:10 - 00341504 _____ (Microsoft Corporation) C:\WINDOWS\system32\RADCUI.dll
2016-09-14 08:27 - 2016-09-04 20:37 - 00445765 _____ C:\WINDOWS\system32\ApnDatabase.xml
2016-09-14 08:26 - 2016-09-07 01:39 - 01317640 _____ (Microsoft Corporation) C:\WINDOWS\system32\winload.efi
2016-09-14 08:26 - 2016-09-07 01:39 - 01142560 _____ (Microsoft Corporation) C:\WINDOWS\system32\winload.exe
2016-09-14 08:26 - 2016-09-07 01:39 - 01030408 _____ (Microsoft Corporation) C:\WINDOWS\system32\winresume.efi
2016-09-14 08:26 - 2016-09-07 01:39 - 00875480 _____ (Microsoft Corporation) C:\WINDOWS\system32\winresume.exe
2016-09-14 08:26 - 2016-09-07 01:39 - 00799568 _____ (Microsoft Corporation) C:\WINDOWS\system32\oleaut32.dll
2016-09-14 08:26 - 2016-09-07 01:39 - 00601744 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\oleaut32.dll
2016-09-14 08:26 - 2016-09-07 01:39 - 00175120 _____ (Microsoft Corporation) C:\WINDOWS\system32\sspicli.dll
2016-09-14 08:26 - 2016-09-07 01:37 - 00129888 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\ksecdd.sys
2016-09-14 08:26 - 2016-09-07 01:36 - 00405856 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\FWPKCLNT.SYS
2016-09-14 08:26 - 2016-09-07 01:33 - 02026736 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msxml6.dll
2016-09-14 08:26 - 2016-09-07 01:26 - 00131424 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\ufxsynopsys.sys
2016-09-14 08:26 - 2016-09-07 01:25 - 01447776 _____ (Microsoft Corporation) C:\WINDOWS\system32\webservices.dll
2016-09-14 08:26 - 2016-09-07 01:25 - 01322248 _____ (Microsoft Corporation) C:\WINDOWS\system32\ole32.dll
2016-09-14 08:26 - 2016-09-07 01:24 - 02180128 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mfcore.dll
2016-09-14 08:26 - 2016-09-07 01:24 - 01118200 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mfnetsrc.dll
2016-09-14 08:26 - 2016-09-07 01:21 - 04074160 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\explorer.exe
2016-09-14 08:26 - 2016-09-07 01:21 - 00465760 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SettingSyncHost.exe
2016-09-14 08:26 - 2016-09-07 01:20 - 01355336 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\propsys.dll
2016-09-14 08:26 - 2016-09-07 01:16 - 02773088 _____ (Microsoft Corporation) C:\WINDOWS\system32\d3d11.dll
2016-09-14 08:26 - 2016-09-07 01:15 - 01415200 _____ (Microsoft Corporation) C:\WINDOWS\system32\msctf.dll
2016-09-14 08:26 - 2016-09-07 01:13 - 01865584 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\d3d9.dll
2016-09-14 08:26 - 2016-09-07 01:12 - 01522152 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WindowsCodecs.dll
2016-09-14 08:26 - 2016-09-07 01:11 - 00057912 _____ (Microsoft Corporation) C:\WINDOWS\system32\lsass.exe
2016-09-14 08:26 - 2016-09-07 01:07 - 01951848 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\hevcdecoder.dll
2016-09-14 08:26 - 2016-09-07 00:51 - 00089088 _____ (Microsoft Corporation) C:\WINDOWS\system32\MapsCSP.dll
2016-09-14 08:26 - 2016-09-07 00:47 - 00066560 _____ (Microsoft Corporation) C:\WINDOWS\system32\MosHostClient.dll
2016-09-14 08:26 - 2016-09-07 00:46 - 00031232 _____ (Microsoft Corporation) C:\WINDOWS\system32\odbcconf.dll
2016-09-14 08:26 - 2016-09-07 00:45 - 00086528 _____ (Microsoft Corporation) C:\WINDOWS\system32\spcompat.dll
2016-09-14 08:26 - 2016-09-07 00:45 - 00037376 _____ (Microsoft Corporation) C:\WINDOWS\system32\cmintegrator.dll
2016-09-14 08:26 - 2016-09-07 00:44 - 00028672 _____ (Microsoft Corporation) C:\WINDOWS\system32\mapsupdatetask.dll
2016-09-14 08:26 - 2016-09-07 00:44 - 00014848 _____ (Microsoft Corporation) C:\WINDOWS\system32\IconCodecService.dll
2016-09-14 08:26 - 2016-09-07 00:43 - 00584704 _____ (Microsoft Corporation) C:\WINDOWS\system32\UIRibbonRes.dll
2016-09-14 08:26 - 2016-09-07 00:43 - 00074240 _____ (Microsoft Corporation) C:\WINDOWS\system32\MosStorage.dll
2016-09-14 08:26 - 2016-09-07 00:43 - 00037376 _____ (Microsoft Corporation) C:\WINDOWS\system32\wsmprovhost.exe
2016-09-14 08:26 - 2016-09-07 00:43 - 00015872 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\MTConfig.sys
2016-09-14 08:26 - 2016-09-07 00:42 - 00163328 _____ (Microsoft Corporation) C:\WINDOWS\system32\WsmAuto.dll
2016-09-14 08:26 - 2016-09-07 00:42 - 00140288 _____ (Microsoft Corporation) C:\WINDOWS\system32\WcnApi.dll
2016-09-14 08:26 - 2016-09-07 00:42 - 00120320 _____ (Microsoft Corporation) C:\WINDOWS\system32\MapsBtSvc.dll
2016-09-14 08:26 - 2016-09-07 00:42 - 00117760 _____ (Microsoft Corporation) C:\WINDOWS\system32\dafWCN.dll
2016-09-14 08:26 - 2016-09-07 00:42 - 00112640 _____ (Microsoft Corporation) C:\WINDOWS\system32\fdWCN.dll
2016-09-14 08:26 - 2016-09-07 00:42 - 00031744 _____ (Microsoft Corporation) C:\WINDOWS\system32\WsmAgent.dll
2016-09-14 08:26 - 2016-09-07 00:41 - 00125952 _____ (Microsoft Corporation) C:\WINDOWS\system32\MediaFoundation.DefaultPerceptionProvider.dll
2016-09-14 08:26 - 2016-09-07 00:41 - 00072704 _____ (Microsoft Corporation) C:\WINDOWS\system32\moshost.dll
2016-09-14 08:26 - 2016-09-07 00:40 - 00471040 _____ (Microsoft Corporation) C:\WINDOWS\system32\wbemcomn.dll
2016-09-14 08:26 - 2016-09-07 00:40 - 00086528 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppCapture.dll
2016-09-14 08:26 - 2016-09-07 00:39 - 00379392 _____ (Microsoft Corporation) C:\WINDOWS\system32\usocore.dll
2016-09-14 08:26 - 2016-09-07 00:39 - 00270848 _____ (Microsoft Corporation) C:\WINDOWS\system32\moshostcore.dll
2016-09-14 08:26 - 2016-09-07 00:39 - 00096256 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\VoipRT.dll
2016-09-14 08:26 - 2016-09-07 00:39 - 00053760 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Cortana.ProxyStub.dll
2016-09-14 08:26 - 2016-09-07 00:38 - 00584704 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\UIRibbonRes.dll
2016-09-14 08:26 - 2016-09-07 00:38 - 00288768 _____ (Microsoft Corporation) C:\WINDOWS\system32\WsmWmiPl.dll
2016-09-14 08:26 - 2016-09-07 00:38 - 00157184 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingsHandlers_Geolocation.dll
2016-09-14 08:26 - 2016-09-07 00:37 - 00642048 _____ (Microsoft Corporation) C:\WINDOWS\system32\enterprisecsps.dll
2016-09-14 08:26 - 2016-09-07 00:37 - 00373248 _____ (Microsoft Corporation) C:\WINDOWS\system32\WmpDui.dll
2016-09-14 08:26 - 2016-09-07 00:37 - 00274944 _____ (Microsoft Corporation) C:\WINDOWS\system32\DisplayManager.dll
2016-09-14 08:26 - 2016-09-07 00:37 - 00126464 _____ (Microsoft Corporation) C:\WINDOWS\system32\dialserver.dll
2016-09-14 08:26 - 2016-09-07 00:37 - 00100352 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WcnApi.dll
2016-09-14 08:26 - 2016-09-07 00:37 - 00095744 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\fdWCN.dll
2016-09-14 08:26 - 2016-09-07 00:36 - 00752128 _____ (Microsoft Corporation) C:\WINDOWS\system32\PhoneService.dll
2016-09-14 08:26 - 2016-09-07 00:36 - 00414720 _____ (Microsoft Corporation) C:\WINDOWS\system32\bcastdvr.exe
2016-09-14 08:26 - 2016-09-07 00:36 - 00047104 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\fwcfg.dll
2016-09-14 08:26 - 2016-09-07 00:35 - 00715264 _____ (Microsoft Corporation) C:\WINDOWS\system32\GamePanel.exe
2016-09-14 08:26 - 2016-09-07 00:35 - 00522240 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.WiFiDirect.dll
2016-09-14 08:26 - 2016-09-07 00:35 - 00460800 _____ (Microsoft Corporation) C:\WINDOWS\system32\MapConfiguration.dll
2016-09-14 08:26 - 2016-09-07 00:35 - 00412672 _____ (Microsoft Corporation) C:\WINDOWS\system32\wlanui.dll
2016-09-14 08:26 - 2016-09-07 00:35 - 00205312 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\oemlicense.dll
2016-09-14 08:26 - 2016-09-07 00:35 - 00115712 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mmcshext.dll
2016-09-14 08:26 - 2016-09-07 00:35 - 00024064 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\CheckNetIsolation.exe
2016-09-14 08:26 - 2016-09-07 00:34 - 00630784 _____ (Microsoft Corporation) C:\WINDOWS\system32\MessagingDataModel2.dll
2016-09-14 08:26 - 2016-09-07 00:34 - 00619520 _____ (Microsoft Corporation) C:\WINDOWS\system32\efswrt.dll
2016-09-14 08:26 - 2016-09-07 00:34 - 00510464 _____ (Microsoft Corporation) C:\WINDOWS\system32\WlanMediaManager.dll
2016-09-14 08:26 - 2016-09-07 00:34 - 00497664 _____ (Microsoft Corporation) C:\WINDOWS\system32\WalletService.dll
2016-09-14 08:26 - 2016-09-07 00:34 - 00300032 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mmcbase.dll
2016-09-14 08:26 - 2016-09-07 00:34 - 00278016 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Internal.Management.dll
2016-09-14 08:26 - 2016-09-07 00:34 - 00163840 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\cic.dll
2016-09-14 08:26 - 2016-09-07 00:33 - 00904704 _____ (Microsoft Corporation) C:\WINDOWS\system32\azroles.dll
2016-09-14 08:26 - 2016-09-07 00:33 - 00321536 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Devices.AllJoyn.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 04213248 _____ (Microsoft Corporation) C:\WINDOWS\system32\WlanMM.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 01294336 _____ (Microsoft Corporation) C:\WINDOWS\system32\wcnwiz.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00757248 _____ (Microsoft Corporation) C:\WINDOWS\system32\winipcsecproc_ssp.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00651776 _____ (Microsoft Corporation) C:\WINDOWS\system32\UserLanguagesCpl.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00506880 _____ (Microsoft Corporation) C:\WINDOWS\system32\tileobjserver.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00471040 _____ (Microsoft Corporation) C:\WINDOWS\system32\wcncsvc.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00386048 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Devices.LowLevel.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00339456 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\azroleui.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00310784 _____ (Microsoft Corporation) C:\WINDOWS\system32\sysdm.cpl
2016-09-14 08:26 - 2016-09-07 00:31 - 09920512 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\twinui.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 01985024 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\certmgr.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 01094656 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Networking.Vpn.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 01056256 _____ (Microsoft Corporation) C:\WINDOWS\system32\JpMapControl.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00988160 _____ (Microsoft Corporation) C:\WINDOWS\system32\NMAA.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00970752 _____ (Microsoft Corporation) C:\WINDOWS\system32\nettrace.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00941568 _____ (Microsoft Corporation) C:\WINDOWS\system32\MiracastReceiver.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00900608 _____ (Microsoft Corporation) C:\WINDOWS\system32\CPFilters.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00852992 _____ (Microsoft Corporation) C:\WINDOWS\system32\MapsStore.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00839680 _____ (Microsoft Corporation) C:\WINDOWS\system32\comuid.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00607232 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppxApplicabilityEngine.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00519680 _____ (Microsoft Corporation) C:\WINDOWS\system32\WLanConn.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00358912 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\authfwcfg.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 01575936 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Media.Speech.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 01500160 _____ (Microsoft Corporation) C:\WINDOWS\system32\RecoveryDrive.exe
2016-09-14 08:26 - 2016-09-07 00:30 - 01144320 _____ (Microsoft Corporation) C:\WINDOWS\system32\qmgr.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00982016 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppxPackaging.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00939520 _____ (Microsoft Corporation) C:\WINDOWS\system32\MapControlCore.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00817152 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Storage.Search.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00585728 _____ (Microsoft Corporation) C:\WINDOWS\system32\ieui.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00576000 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\nshwfp.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00569856 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\qdvd.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00471552 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\filemgmt.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00368128 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Graphics.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00294912 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\PhoneOm.dll
2016-09-14 08:26 - 2016-09-07 00:29 - 07977984 _____ (Microsoft Corporation) C:\WINDOWS\system32\mos.dll
2016-09-14 08:26 - 2016-09-07 00:29 - 01902592 _____ (Microsoft Corporation) C:\WINDOWS\system32\msxml3.dll
2016-09-14 08:26 - 2016-09-07 00:29 - 01465344 _____ (Microsoft Corporation) C:\WINDOWS\system32\VSSVC.exe
2016-09-14 08:26 - 2016-09-07 00:29 - 00553472 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\cryptui.dll
2016-09-14 08:26 - 2016-09-07 00:29 - 00268288 _____ (Microsoft Corporation) C:\WINDOWS\system32\updatehandlers.dll
2016-09-14 08:26 - 2016-09-07 00:28 - 04143104 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WlanMM.dll
2016-09-14 08:26 - 2016-09-07 00:28 - 01648640 _____ (Microsoft Corporation) C:\WINDOWS\system32\comsvcs.dll
2016-09-14 08:26 - 2016-09-07 00:28 - 01226752 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wcnwiz.dll
2016-09-14 08:26 - 2016-09-07 00:28 - 00638976 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MrmIndexer.dll
2016-09-14 08:26 - 2016-09-07 00:28 - 00489984 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mbsmsapi.dll
2016-09-14 08:26 - 2016-09-07 00:28 - 00413696 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WLanConn.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 01872896 _____ (Microsoft Corporation) C:\WINDOWS\system32\workfolderssvc.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 01424384 _____ (Microsoft Corporation) C:\WINDOWS\system32\wdc.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 00502272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mscms.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 00477184 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ieui.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 00458752 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wlidprov.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 00400896 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\OneDriveSettingSyncProvider.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 00248320 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\resutils.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 00100864 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\offlinelsa.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 02881536 _____ (Microsoft Corporation) C:\WINDOWS\system32\storagewmi.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 01915392 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MSAJApi.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 01537536 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\pla.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 00736768 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SmartcardCredentialProvider.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 00673280 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MbaeApiPublic.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 00645632 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Storage.Search.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 00501760 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\vbscript.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 00488960 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\clusapi.dll
2016-09-14 08:26 - 2016-09-07 00:25 - 00207872 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\licensingdiag.exe
2016-09-14 08:26 - 2016-09-07 00:24 - 07200256 _____ (Microsoft Corporation) C:\WINDOWS\system32\BingMaps.dll
2016-09-14 08:26 - 2016-09-07 00:24 - 00489984 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ShareHost.dll
2016-09-14 08:26 - 2016-09-07 00:24 - 00460800 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SearchFolder.dll
2016-09-14 08:26 - 2016-09-07 00:22 - 01987072 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\DWrite.dll
2016-09-14 08:26 - 2016-09-07 00:22 - 01297408 _____ (Microsoft Corporation) C:\WINDOWS\system32\SensorDataService.exe
2016-09-14 08:26 - 2016-09-07 00:22 - 00778240 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MsSpellCheckingFacility.dll
2016-09-14 08:26 - 2016-09-07 00:21 - 01063936 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\gpedit.dll
2016-09-14 08:26 - 2016-09-07 00:21 - 00639488 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\TokenBroker.dll
2016-09-14 08:26 - 2016-09-07 00:20 - 00900608 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Networking.BackgroundTransfer.dll
2016-09-14 08:26 - 2016-09-07 00:20 - 00882688 _____ (Microsoft Corporation) C:\WINDOWS\system32\ntshrui.dll
2016-09-14 08:26 - 2016-09-07 00:20 - 00417792 _____ (Microsoft Corporation) C:\WINDOWS\system32\dmenrollengine.dll
2016-09-14 08:26 - 2016-09-07 00:19 - 04169728 _____ (Microsoft Corporation) C:\WINDOWS\system32\UIRibbon.dll
2016-09-14 08:26 - 2016-09-07 00:19 - 03555840 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\xpsrchvw.exe
2016-09-14 08:26 - 2016-09-07 00:19 - 02798080 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Media.dll
2016-09-14 08:26 - 2016-09-07 00:19 - 02295808 _____ (Microsoft Corporation) C:\WINDOWS\system32\wlansvc.dll
2016-09-14 08:26 - 2016-09-07 00:19 - 00733184 _____ (Microsoft Corporation) C:\WINDOWS\system32\rasapi32.dll
2016-09-14 08:26 - 2016-09-07 00:18 - 05503488 _____ (Microsoft Corporation) C:\WINDOWS\system32\d2d1.dll
2016-09-14 08:26 - 2016-09-07 00:17 - 01674240 _____ (Microsoft Corporation) C:\WINDOWS\system32\quartz.dll
2016-09-14 08:26 - 2016-09-07 00:16 - 02680320 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msftedit.dll
2016-09-14 08:26 - 2016-09-07 00:16 - 01984000 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mssrch.dll
2016-09-14 08:26 - 2016-09-07 00:16 - 00162816 _____ (Microsoft Corporation) C:\WINDOWS\system32\enrollmentapi.dll
2016-09-14 08:26 - 2016-09-07 00:15 - 02772480 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\tquery.dll
2016-09-14 08:26 - 2016-09-07 00:15 - 01556992 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\OpcServices.dll
2016-09-14 08:26 - 2016-09-07 00:14 - 03355136 _____ (Microsoft Corporation) C:\WINDOWS\system32\msftedit.dll
2016-09-14 08:26 - 2016-09-07 00:14 - 01799680 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Logon.dll
2016-09-14 08:26 - 2016-09-07 00:14 - 01732096 _____ (Microsoft Corporation) C:\WINDOWS\system32\urlmon.dll
2016-09-14 08:26 - 2016-09-07 00:12 - 00754176 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SettingSyncCore.dll
2016-09-14 08:26 - 2016-09-07 00:12 - 00339456 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\certcli.dll
2016-09-14 08:26 - 2016-09-07 00:11 - 03294208 _____ (Microsoft Corporation) C:\WINDOWS\system32\mstsc.exe
2016-09-14 08:26 - 2016-09-07 00:10 - 00712704 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\RemoteNaturalLanguage.dll
2016-09-14 08:26 - 2016-09-07 00:09 - 00824832 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\adtschema.dll
2016-09-14 08:26 - 2016-09-07 00:09 - 00218624 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\ahcache.sys
2016-09-14 08:26 - 2016-09-07 00:09 - 00063488 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msobjs.dll
2016-09-14 08:25 - 2016-09-07 01:39 - 04387680 _____ (Microsoft Corporation) C:\WINDOWS\system32\setupapi.dll
2016-09-14 08:25 - 2016-09-07 01:39 - 01238584 _____ (Microsoft Corporation) C:\WINDOWS\system32\Taskmgr.exe
2016-09-14 08:25 - 2016-09-07 01:39 - 00705576 _____ (Microsoft Corporation) C:\WINDOWS\system32\kernel32.dll
2016-09-14 08:25 - 2016-09-07 01:39 - 00414232 _____ (Microsoft Corporation) C:\WINDOWS\system32\BCP47Langs.dll
2016-09-14 08:25 - 2016-09-07 01:39 - 00337328 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Storage.ApplicationData.dll
2016-09-14 08:25 - 2016-09-07 01:39 - 00328520 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\BCP47Langs.dll
2016-09-14 08:25 - 2016-09-07 01:36 - 00528736 _____ (Microsoft Corporation) C:\WINDOWS\system32\pcasvc.dll
2016-09-14 08:25 - 2016-09-07 01:35 - 01613664 _____ (Microsoft Corporation) C:\WINDOWS\system32\diagtrack.dll
2016-09-14 08:25 - 2016-09-07 01:35 - 00989536 _____ (Microsoft Corporation) C:\WINDOWS\system32\SecConfig.efi
2016-09-14 08:25 - 2016-09-07 01:35 - 00523616 _____ (Microsoft Corporation) C:\WINDOWS\system32\wimserv.exe
2016-09-14 08:25 - 2016-09-07 01:26 - 01554152 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmpmde.dll
2016-09-14 08:25 - 2016-09-07 01:26 - 00693592 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetSetupEngine.dll
2016-09-14 08:25 - 2016-09-07 01:26 - 00439136 _____ (Microsoft Corporation) C:\WINDOWS\system32\netcfgx.dll
2016-09-14 08:25 - 2016-09-07 01:24 - 00980352 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mfasfsrcsnk.dll
2016-09-14 08:25 - 2016-09-07 01:24 - 00925064 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mfplat.dll
2016-09-14 08:25 - 2016-09-07 01:24 - 00709176 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mfsvr.dll
2016-09-14 08:25 - 2016-09-07 01:24 - 00652312 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\evr.dll
2016-09-14 08:25 - 2016-09-07 01:24 - 00451928 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MFCaptureEngine.dll
2016-09-14 08:25 - 2016-09-07 01:22 - 00957608 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ole32.dll
2016-09-14 08:25 - 2016-09-07 01:22 - 00359256 _____ (Microsoft Corporation) C:\WINDOWS\system32\msv1_0.dll
2016-09-14 08:25 - 2016-09-07 01:16 - 02548936 _____ (Microsoft Corporation) C:\WINDOWS\system32\d3d10warp.dll
2016-09-14 08:25 - 2016-09-07 01:16 - 02144512 _____ (Microsoft Corporation) C:\WINDOWS\system32\d3d9.dll
2016-09-14 08:25 - 2016-09-07 01:16 - 01988448 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\dxgkrnl.sys
2016-09-14 08:25 - 2016-09-07 01:15 - 00550656 _____ (Microsoft Corporation) C:\WINDOWS\system32\directmanipulation.dll
2016-09-14 08:25 - 2016-09-07 01:12 - 00871776 _____ (Microsoft Corporation) C:\WINDOWS\system32\drvstore.dll
2016-09-14 08:25 - 2016-09-07 01:11 - 00503600 _____ (Microsoft Corporation) C:\WINDOWS\system32\DMRServer.dll
2016-09-14 08:25 - 2016-09-07 00:53 - 01033216 _____ (Microsoft Corporation) C:\WINDOWS\system32\termsrv.dll
2016-09-14 08:25 - 2016-09-07 00:46 - 00068608 _____ (Microsoft Corporation) C:\WINDOWS\system32\fdProxy.dll
2016-09-14 08:25 - 2016-09-07 00:46 - 00061952 _____ (Microsoft Corporation) C:\WINDOWS\system32\vss_ps.dll
2016-09-14 08:25 - 2016-09-07 00:44 - 00120832 _____ (Microsoft Corporation) C:\WINDOWS\system32\VoipRT.dll
2016-09-14 08:25 - 2016-09-07 00:44 - 00105984 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Cortana.ProxyStub.dll
2016-09-14 08:25 - 2016-09-07 00:44 - 00068608 _____ (Microsoft Corporation) C:\WINDOWS\system32\udhisapi.dll
2016-09-14 08:25 - 2016-09-07 00:43 - 00041472 _____ (Microsoft Corporation) C:\WINDOWS\system32\upnpcont.exe
2016-09-14 08:25 - 2016-09-07 00:42 - 00219136 _____ (Microsoft Corporation) C:\WINDOWS\system32\EnterpriseModernAppMgmtCSP.dll
2016-09-14 08:25 - 2016-09-07 00:41 - 00309760 _____ (Microsoft Corporation) C:\WINDOWS\system32\wusa.exe
2016-09-14 08:25 - 2016-09-07 00:41 - 00091136 _____ (Microsoft Corporation) C:\WINDOWS\system32\browserbroker.dll
2016-09-14 08:25 - 2016-09-07 00:41 - 00047616 _____ (Microsoft Corporation) C:\WINDOWS\system32\TpmTasks.dll
2016-09-14 08:25 - 2016-09-07 00:40 - 13018624 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Xaml.dll
2016-09-14 08:25 - 2016-09-07 00:40 - 00297472 _____ (Microsoft Corporation) C:\WINDOWS\system32\unimdm.tsp
2016-09-14 08:25 - 2016-09-07 00:40 - 00245248 _____ (Microsoft Corporation) C:\WINDOWS\system32\MicrosoftAccountExtension.dll
2016-09-14 08:25 - 2016-09-07 00:40 - 00135680 _____ (Microsoft Corporation) C:\WINDOWS\system32\vdsutil.dll
2016-09-14 08:25 - 2016-09-07 00:40 - 00070144 _____ (Microsoft Corporation) C:\WINDOWS\system32\vsstrace.dll
2016-09-14 08:25 - 2016-09-07 00:39 - 00356352 _____ (Microsoft Corporation) C:\WINDOWS\system32\mcbuilder.exe
2016-09-14 08:25 - 2016-09-07 00:38 - 00210432 _____ (Microsoft Corporation) C:\WINDOWS\system32\wcmcsp.dll
2016-09-14 08:25 - 2016-09-07 00:38 - 00187392 _____ (Microsoft Corporation) C:\WINDOWS\system32\BootMenuUX.dll
2016-09-14 08:25 - 2016-09-07 00:37 - 00846848 _____ (Microsoft Corporation) C:\WINDOWS\system32\ipsecsnp.dll
2016-09-14 08:25 - 2016-09-07 00:37 - 00308736 _____ (Microsoft Corporation) C:\WINDOWS\system32\eapphost.dll
2016-09-14 08:25 - 2016-09-07 00:37 - 00250880 _____ (Microsoft Corporation) C:\WINDOWS\system32\MicrosoftAccountCloudAP.dll
2016-09-14 08:25 - 2016-09-07 00:37 - 00198144 _____ (Microsoft Corporation) C:\WINDOWS\system32\winsrv.dll
2016-09-14 08:25 - 2016-09-07 00:37 - 00118784 _____ (Microsoft Corporation) C:\WINDOWS\system32\fhsvc.dll
2016-09-14 08:25 - 2016-09-07 00:37 - 00099328 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\srpapi.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 01582080 _____ (Microsoft Corporation) C:\WINDOWS\system32\aitstatic.exe
2016-09-14 08:25 - 2016-09-07 00:36 - 00567808 _____ (Microsoft Corporation) C:\WINDOWS\system32\MBMediaManager.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00479744 _____ (Microsoft Corporation) C:\WINDOWS\system32\apphelp.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00467968 _____ (Microsoft Corporation) C:\WINDOWS\system32\swprv.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00394752 _____ (Microsoft Corporation) C:\WINDOWS\system32\WMPhoto.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00332800 _____ (Microsoft Corporation) C:\WINDOWS\system32\eapp3hst.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00317952 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetworkBindingEngineMigPlugin.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00314368 _____ (Microsoft Corporation) C:\WINDOWS\system32\EnterpriseAppMgmtSvc.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00250880 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\AppLockerCSP.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00112640 _____ (Microsoft Corporation) C:\WINDOWS\system32\eapsvc.dll
2016-09-14 08:25 - 2016-09-07 00:35 - 00945664 _____ (Microsoft Corporation) C:\WINDOWS\system32\autochk.exe
2016-09-14 08:25 - 2016-09-07 00:35 - 00685568 _____ (Microsoft Corporation) C:\WINDOWS\system32\scapi.dll
2016-09-14 08:25 - 2016-09-07 00:35 - 00368640 _____ (Microsoft Corporation) C:\WINDOWS\system32\diagtrack_win.dll
2016-09-14 08:25 - 2016-09-07 00:35 - 00363008 _____ (Microsoft Corporation) C:\WINDOWS\system32\PhoneOm.dll
2016-09-14 08:25 - 2016-09-07 00:35 - 00342016 _____ (Microsoft Corporation) C:\WINDOWS\system32\APHostService.dll
2016-09-14 08:25 - 2016-09-07 00:35 - 00131072 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\usbceip.dll
2016-09-14 08:25 - 2016-09-07 00:34 - 00667136 _____ (Microsoft Corporation) C:\WINDOWS\system32\vds.exe
2016-09-14 08:25 - 2016-09-07 00:34 - 00440320 _____ (Microsoft Corporation) C:\WINDOWS\system32\fhcfg.dll
2016-09-14 08:25 - 2016-09-07 00:34 - 00318464 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Cortana.OneCore.dll
2016-09-14 08:25 - 2016-09-07 00:34 - 00304128 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Devices.Midi.dll
2016-09-14 08:25 - 2016-09-07 00:34 - 00270336 _____ (Microsoft Corporation) C:\WINDOWS\system32\netplwiz.dll
2016-09-14 08:25 - 2016-09-07 00:34 - 00265728 _____ (Microsoft Corporation) C:\WINDOWS\system32\netman.dll
2016-09-14 08:25 - 2016-09-07 00:33 - 01813504 _____ (Microsoft Corporation) C:\WINDOWS\system32\pnidui.dll
2016-09-14 08:25 - 2016-09-07 00:33 - 00948736 _____ (Microsoft Corporation) C:\WINDOWS\system32\XblAuthManager.dll
2016-09-14 08:25 - 2016-09-07 00:33 - 00606720 _____ (Microsoft Corporation) C:\WINDOWS\system32\wcmsvc.dll
2016-09-14 08:25 - 2016-09-07 00:33 - 00504832 _____ (Microsoft Corporation) C:\WINDOWS\system32\dlnashext.dll
2016-09-14 08:25 - 2016-09-07 00:33 - 00276480 _____ (Microsoft Corporation) C:\WINDOWS\system32\WindowsCodecsExt.dll
2016-09-14 08:25 - 2016-09-07 00:33 - 00092160 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\IdCtrls.dll
2016-09-14 08:25 - 2016-09-07 00:32 - 00892416 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.SmartCards.dll
2016-09-14 08:25 - 2016-09-07 00:32 - 00708608 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Security.Authentication.Web.Core.dll
2016-09-14 08:25 - 2016-09-07 00:32 - 00352768 _____ (Microsoft Corporation) C:\WINDOWS\system32\eappcfg.dll
2016-09-14 08:25 - 2016-09-07 00:32 - 00292864 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\dot3ui.dll
2016-09-14 08:25 - 2016-09-07 00:32 - 00283648 _____ (Microsoft Corporation) C:\WINDOWS\system32\PlayToReceiver.dll
2016-09-14 08:25 - 2016-09-07 00:32 - 00260096 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\apprepsync.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00984576 _____ (Microsoft Corporation) C:\WINDOWS\system32\tdh.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00970752 _____ (Microsoft Corporation) C:\WINDOWS\system32\kerberos.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00915456 _____ (Microsoft Corporation) C:\WINDOWS\system32\configurationclient.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00588288 _____ (Microsoft Corporation) C:\WINDOWS\system32\wlidprov.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00527872 _____ (Microsoft Corporation) C:\WINDOWS\system32\defragsvc.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00511488 _____ (Microsoft Corporation) C:\WINDOWS\system32\icsvc.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00452608 _____ (Microsoft Corporation) C:\WINDOWS\system32\upnphost.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00313344 _____ (Microsoft Corporation) C:\WINDOWS\system32\resutils.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00282624 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Search.ProtocolHandler.MAPI2.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00190464 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\apprepapi.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 14251520 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmp.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 01558528 _____ (Microsoft Corporation) C:\WINDOWS\system32\vssapi.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 01387520 _____ (Microsoft Corporation) C:\WINDOWS\system32\win32kbase.sys
2016-09-14 08:25 - 2016-09-07 00:30 - 01318400 _____ (Microsoft Corporation) C:\WINDOWS\system32\wsp_health.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 00697344 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Security.Authentication.OnlineId.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 00649216 _____ (Microsoft Corporation) C:\WINDOWS\system32\clusapi.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 00599040 _____ (Microsoft Corporation) C:\WINDOWS\system32\duser.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 00436736 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppXDeploymentClient.dll
2016-09-14 08:25 - 2016-09-07 00:29 - 01847808 _____ (Microsoft Corporation) C:\WINDOWS\system32\WMPDMC.exe
2016-09-14 08:25 - 2016-09-07 00:29 - 01487360 _____ (Microsoft Corporation) C:\WINDOWS\system32\pla.dll
2016-09-14 08:25 - 2016-09-07 00:29 - 01443328 _____ (Microsoft Corporation) C:\WINDOWS\system32\diagperf.dll
2016-09-14 08:25 - 2016-09-07 00:29 - 00853504 _____ (Microsoft Corporation) C:\WINDOWS\system32\aadtb.dll
2016-09-14 08:25 - 2016-09-07 00:29 - 00785408 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\azroles.dll
2016-09-14 08:25 - 2016-09-07 00:29 - 00387584 _____ (Microsoft Corporation) C:\WINDOWS\system32\syncutil.dll
2016-09-14 08:25 - 2016-09-07 00:29 - 00283136 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.BioFeedback.dll
2016-09-14 08:25 - 2016-09-07 00:28 - 01783808 _____ (Microsoft Corporation) C:\WINDOWS\system32\wsp_fs.dll
2016-09-14 08:25 - 2016-09-07 00:28 - 01717760 _____ (Microsoft Corporation) C:\WINDOWS\system32\GdiPlus.dll
2016-09-14 08:25 - 2016-09-07 00:28 - 01671168 _____ (Microsoft Corporation) C:\WINDOWS\system32\FntCache.dll
2016-09-14 08:25 - 2016-09-07 00:28 - 00889344 _____ (Microsoft Corporation) C:\WINDOWS\system32\mprddm.dll
2016-09-14 08:25 - 2016-09-07 00:28 - 00282624 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SearchProtocolHost.exe
2016-09-14 08:25 - 2016-09-07 00:27 - 04456448 _____ (Microsoft Corporation) C:\WINDOWS\system32\D3DCompiler_47.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 01395712 _____ (Microsoft Corporation) C:\WINDOWS\system32\UIAutomationCore.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00865792 _____ (Microsoft Corporation) C:\WINDOWS\system32\AzureSettingSyncProvider.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00792576 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\kerberos.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00651776 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\comuid.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00585216 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.AccountsControl.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00555520 _____ (Microsoft Corporation) C:\WINDOWS\system32\SyncController.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00517632 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\PlayToManager.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00502272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\DevicePairing.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00372224 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\LockAppBroker.dll
2016-09-14 08:25 - 2016-09-07 00:26 - 02057216 _____ (Microsoft Corporation) C:\WINDOWS\system32\wlidsvc.dll
2016-09-14 08:25 - 2016-09-07 00:26 - 01570816 _____ (Microsoft Corporation) C:\WINDOWS\system32\wbengine.exe
2016-09-14 08:25 - 2016-09-07 00:26 - 01117184 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Media.Speech.dll
2016-09-14 08:25 - 2016-09-07 00:26 - 00821760 _____ (Microsoft Corporation) C:\WINDOWS\system32\TokenBroker.dll
2016-09-14 08:25 - 2016-09-07 00:26 - 00738816 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\appwiz.cpl
2016-09-14 08:25 - 2016-09-07 00:26 - 00434688 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\LogonController.dll
2016-09-14 08:25 - 2016-09-07 00:25 - 02578432 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\gameux.dll
2016-09-14 08:25 - 2016-09-07 00:25 - 01467392 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\GdiPlus.dll
2016-09-14 08:25 - 2016-09-07 00:25 - 01328128 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\comsvcs.dll
2016-09-14 08:25 - 2016-09-07 00:25 - 01105920 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Media.Audio.dll
2016-09-14 08:25 - 2016-09-07 00:25 - 01052160 _____ (Microsoft Corporation) C:\WINDOWS\system32\MsSpellCheckingFacility.dll
2016-09-14 08:25 - 2016-09-07 00:25 - 00759808 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SearchIndexer.exe
2016-09-14 08:25 - 2016-09-07 00:24 - 00764928 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Cred.dll
2016-09-14 08:25 - 2016-09-07 00:24 - 00667648 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\AzureSettingSyncProvider.dll
2016-09-14 08:25 - 2016-09-07 00:23 - 04646912 _____ (Microsoft Corporation) C:\WINDOWS\system32\xpsrchvw.exe
2016-09-14 08:25 - 2016-09-07 00:23 - 00918016 _____ (Microsoft Corporation) C:\WINDOWS\system32\XpsFilt.dll
2016-09-14 08:25 - 2016-09-07 00:22 - 12585472 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wmp.dll
2016-09-14 08:25 - 2016-09-07 00:22 - 03093504 _____ (Microsoft Corporation) C:\WINDOWS\system32\mispace.dll
2016-09-14 08:25 - 2016-09-07 00:22 - 00465920 _____ (Microsoft Corporation) C:\WINDOWS\system32\StikyNot.exe
2016-09-14 08:25 - 2016-09-07 00:21 - 00620544 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\XpsFilt.dll
2016-09-14 08:25 - 2016-09-07 00:20 - 02800128 _____ (Microsoft Corporation) C:\WINDOWS\system32\netshell.dll
2016-09-14 08:25 - 2016-09-07 00:20 - 01385472 _____ (Microsoft Corporation) C:\WINDOWS\system32\usercpl.dll
2016-09-14 08:25 - 2016-09-07 00:20 - 00683008 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Networking.BackgroundTransfer.dll
2016-09-14 08:25 - 2016-09-07 00:20 - 00581632 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\twinapi.dll
2016-09-14 08:25 - 2016-09-07 00:20 - 00513024 _____ (Microsoft Corporation) C:\WINDOWS\system32\hnetcfg.dll
2016-09-14 08:25 - 2016-09-07 00:19 - 06471168 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mspaint.exe
2016-09-14 08:25 - 2016-09-07 00:19 - 03589120 _____ (Microsoft Corporation) C:\WINDOWS\system32\win32kfull.sys
2016-09-14 08:25 - 2016-09-07 00:19 - 02902528 _____ (Microsoft Corporation) C:\WINDOWS\system32\themeui.dll
2016-09-14 08:25 - 2016-09-07 00:19 - 01997312 _____ (Microsoft Corporation) C:\WINDOWS\system32\ActiveSyncProvider.dll
2016-09-14 08:25 - 2016-09-07 00:19 - 01213440 _____ (Microsoft Corporation) C:\WINDOWS\system32\sdengin2.dll
2016-09-14 08:25 - 2016-09-07 00:17 - 02062336 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MFMediaEngine.dll
2016-09-14 08:25 - 2016-09-07 00:16 - 04759040 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\d2d1.dll
2016-09-14 08:25 - 2016-09-07 00:16 - 01582080 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Immersive.dll
2016-09-14 08:25 - 2016-09-07 00:16 - 00574976 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\hgcpl.dll
2016-09-14 08:25 - 2016-09-07 00:15 - 01755648 _____ (Microsoft Corporation) C:\WINDOWS\system32\dui70.dll
2016-09-14 08:25 - 2016-09-07 00:14 - 02519552 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\themecpl.dll
2016-09-14 08:25 - 2016-09-07 00:12 - 00899072 _____ (Microsoft Corporation) C:\WINDOWS\system32\D3D12.dll
2016-09-14 08:25 - 2016-09-07 00:10 - 01087488 _____ (Microsoft Corporation) C:\WINDOWS\system32\reseteng.dll
2016-09-14 08:25 - 2016-09-07 00:10 - 00627200 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\certca.dll
2016-09-14 08:25 - 2016-09-07 00:09 - 00824832 _____ (Microsoft Corporation) C:\WINDOWS\system32\adtschema.dll
2016-09-14 08:25 - 2016-09-07 00:09 - 00063488 _____ (Microsoft Corporation) C:\WINDOWS\system32\msobjs.dll
2016-09-14 08:25 - 2016-09-07 00:09 - 00058368 _____ (Microsoft Corporation) C:\WINDOWS\system32\csrsrv.dll
2016-09-14 08:25 - 2016-09-06 23:57 - 00461824 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\CoreMessaging.dll
2016-09-14 08:24 - 2016-09-07 01:39 - 07468896 _____ (Microsoft Corporation) C:\WINDOWS\system32\ntoskrnl.exe
2016-09-14 08:24 - 2016-09-07 01:39 - 01997832 _____ (Microsoft Corporation) C:\WINDOWS\system32\KernelBase.dll
2016-09-14 08:24 - 2016-09-07 01:39 - 01862000 _____ C:\WINDOWS\SysWOW64\CoreUIComponents.dll
2016-09-14 08:24 - 2016-09-07 01:39 - 01557768 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\KernelBase.dll
2016-09-14 08:24 - 2016-09-07 01:39 - 00428896 _____ (Microsoft Corporation) C:\WINDOWS\system32\hal.dll
2016-09-14 08:24 - 2016-09-07 01:34 - 03449168 _____ (Microsoft Corporation) C:\WINDOWS\system32\WSService.dll
2016-09-14 08:24 - 2016-09-07 01:26 - 01552104 _____ (Microsoft Corporation) C:\WINDOWS\system32\winmde.dll
2016-09-14 08:24 - 2016-09-07 01:26 - 00516544 _____ (Microsoft Corporation) C:\WINDOWS\system32\AudioEng.dll
2016-09-14 08:24 - 2016-09-07 01:23 - 04515256 _____ (Microsoft Corporation) C:\WINDOWS\explorer.exe
2016-09-14 08:24 - 2016-09-07 01:23 - 01540216 _____ (Microsoft Corporation) C:\WINDOWS\system32\sppobjs.dll
2016-09-14 08:24 - 2016-09-07 01:23 - 00730344 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Internal.Shell.Broker.dll
2016-09-14 08:24 - 2016-09-07 01:23 - 00692136 _____ (Microsoft Corporation) C:\WINDOWS\system32\sppwinob.dll
2016-09-14 08:24 - 2016-09-07 01:23 - 00565600 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingSyncHost.exe
2016-09-14 08:24 - 2016-09-07 01:23 - 00374008 _____ (Microsoft Corporation) C:\WINDOWS\system32\SystemSettingsAdminFlows.exe
2016-09-14 08:24 - 2016-09-07 01:23 - 00303216 _____ (Microsoft Corporation) C:\WINDOWS\system32\LockAppHost.exe
2016-09-14 08:24 - 2016-09-07 01:22 - 01824264 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\combase.dll
2016-09-14 08:24 - 2016-09-07 01:22 - 00742192 _____ (Microsoft Corporation) C:\WINDOWS\system32\EditionUpgradeManagerObj.dll
2016-09-14 08:24 - 2016-09-07 01:22 - 00703840 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WWAHost.exe
2016-09-14 08:24 - 2016-09-07 01:22 - 00638816 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\ClipSp.sys
2016-09-14 08:24 - 2016-09-07 01:22 - 00625000 _____ (Microsoft Corporation) C:\WINDOWS\system32\ClipSVC.dll
2016-09-14 08:24 - 2016-09-07 01:22 - 00431296 _____ (Microsoft Corporation) C:\WINDOWS\system32\bcryptprimitives.dll
2016-09-14 08:24 - 2016-09-07 01:21 - 21123320 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\shell32.dll
2016-09-14 08:24 - 2016-09-07 01:21 - 05240952 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\windows.storage.dll
2016-09-14 08:24 - 2016-09-07 01:20 - 00836752 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\twinapi.appcore.dll
2016-09-14 08:24 - 2016-09-07 01:19 - 00360480 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\bcryptprimitives.dll
2016-09-14 08:24 - 2016-09-07 01:15 - 01776768 _____ (Microsoft Corporation) C:\WINDOWS\system32\WindowsCodecs.dll
2016-09-14 08:24 - 2016-09-07 01:14 - 00430944 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\mrxsmb.sys
2016-09-14 08:24 - 2016-09-07 01:14 - 00216416 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\mrxsmb20.sys
2016-09-14 08:24 - 2016-09-07 01:13 - 02186856 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\d3d11.dll
2016-09-14 08:24 - 2016-09-07 01:12 - 28851224 _____ (Microsoft Corporation) C:\WINDOWS\system32\WindowsCodecsRaw.dll
2016-09-14 08:24 - 2016-09-07 01:11 - 02187408 _____ (Microsoft Corporation) C:\WINDOWS\system32\hevcdecoder.dll
2016-09-14 08:24 - 2016-09-07 01:11 - 00388888 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmpps.dll
2016-09-14 08:24 - 2016-09-07 01:11 - 00305296 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmpeffects.dll
2016-09-14 08:24 - 2016-09-07 01:08 - 28083144 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WindowsCodecsRaw.dll
2016-09-14 08:24 - 2016-09-07 01:07 - 00253080 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wmpeffects.dll
2016-09-14 08:24 - 2016-09-07 00:46 - 00119296 _____ (Microsoft Corporation) C:\WINDOWS\system32\UserDataTimeUtil.dll
2016-09-14 08:24 - 2016-09-07 00:44 - 00095232 _____ (Microsoft Corporation) C:\WINDOWS\system32\SecureTimeAggregator.dll
2016-09-14 08:24 - 2016-09-07 00:40 - 00285184 _____ (Microsoft Corporation) C:\WINDOWS\system32\oemlicense.dll
2016-09-14 08:24 - 2016-09-07 00:40 - 00129024 _____ (Microsoft Corporation) C:\WINDOWS\system32\mmcshext.dll
2016-09-14 08:24 - 2016-09-07 00:39 - 09324032 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmploc.DLL
2016-09-14 08:24 - 2016-09-07 00:39 - 00238592 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Media.Streaming.ps.dll
2016-09-14 08:24 - 2016-09-07 00:38 - 00413696 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.Midi.dll
2016-09-14 08:24 - 2016-09-07 00:38 - 00335360 _____ (Microsoft Corporation) C:\WINDOWS\system32\mmcbase.dll
2016-09-14 08:24 - 2016-09-07 00:38 - 00203776 _____ (Microsoft Corporation) C:\WINDOWS\system32\cic.dll
2016-09-14 08:24 - 2016-09-07 00:36 - 00600064 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.LowLevel.dll
2016-09-14 08:24 - 2016-09-07 00:35 - 09324032 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wmploc.DLL
2016-09-14 08:24 - 2016-09-07 00:35 - 00714240 _____ (Microsoft Corporation) C:\WINDOWS\system32\SystemSettings.Handlers.dll
2016-09-14 08:24 - 2016-09-07 00:35 - 00475648 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.BlockedShutdown.dll
2016-09-14 08:24 - 2016-09-07 00:35 - 00450048 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Internal.Bluetooth.dll
2016-09-14 08:24 - 2016-09-07 00:34 - 11545088 _____ (Microsoft Corporation) C:\WINDOWS\system32\twinui.dll
2016-09-14 08:24 - 2016-09-07 00:34 - 00790528 _____ (Microsoft Corporation) C:\WINDOWS\system32\EmailApis.dll
2016-09-14 08:24 - 2016-09-07 00:34 - 00572928 _____ (Microsoft Corporation) C:\WINDOWS\system32\filemgmt.dll
2016-09-14 08:24 - 2016-09-07 00:34 - 00507904 _____ (Microsoft Corporation) C:\WINDOWS\system32\mprdim.dll
2016-09-14 08:24 - 2016-09-07 00:34 - 00414720 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.BioFeedback.dll
2016-09-14 08:24 - 2016-09-07 00:34 - 00273408 _____ (Microsoft Corporation) C:\WINDOWS\system32\SyncSettings.dll
2016-09-14 08:24 - 2016-09-07 00:33 - 00726528 _____ (Microsoft Corporation) C:\WINDOWS\system32\ChatApis.dll
2016-09-14 08:24 - 2016-09-07 00:33 - 00602112 _____ (Microsoft Corporation) C:\WINDOWS\system32\cryptui.dll
2016-09-14 08:24 - 2016-09-07 00:33 - 00448000 _____ (Microsoft Corporation) C:\WINDOWS\system32\winipcfile.dll
2016-09-14 08:24 - 2016-09-07 00:33 - 00315392 _____ (Microsoft Corporation) C:\WINDOWS\system32\RDXTaskFactory.dll
2016-09-14 08:24 - 2016-09-07 00:33 - 00224256 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\prnntfy.dll
2016-09-14 08:24 - 2016-09-07 00:33 - 00200704 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\DisplayManager.dll
2016-09-14 08:24 - 2016-09-07 00:32 - 00689664 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\srv2.sys
2016-09-14 08:24 - 2016-09-07 00:32 - 00674304 _____ (Microsoft Corporation) C:\WINDOWS\system32\mbsmsapi.dll
2016-09-14 08:24 - 2016-09-07 00:32 - 00556032 _____ (Microsoft Corporation) C:\WINDOWS\system32\PsmServiceExtHost.dll
2016-09-14 08:24 - 2016-09-07 00:32 - 00492544 _____ (Microsoft Corporation) C:\WINDOWS\system32\SystemSettings.UserAccountsHandlers.dll
2016-09-14 08:24 - 2016-09-07 00:32 - 00484352 _____ (Microsoft Corporation) C:\WINDOWS\system32\DataSenseHandlers.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 02125312 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingsHandlers_Bluetooth.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 01417728 _____ (Microsoft Corporation) C:\WINDOWS\system32\mqqm.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00965632 _____ (Microsoft Corporation) C:\WINDOWS\system32\SRH.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00700416 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppointmentApis.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00564224 _____ (Microsoft Corporation) C:\WINDOWS\system32\DevicePairing.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00515072 _____ (Microsoft Corporation) C:\WINDOWS\system32\OneDriveSettingSyncProvider.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00480768 _____ (Microsoft Corporation) C:\WINDOWS\system32\LockAppBroker.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00472064 _____ (Microsoft Corporation) C:\WINDOWS\system32\Geolocation.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00236544 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\srvnet.sys
2016-09-14 08:24 - 2016-09-07 00:30 - 02012672 _____ (Microsoft Corporation) C:\WINDOWS\system32\winmsipc.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 01159168 _____ (Microsoft Corporation) C:\WINDOWS\system32\ApplicationFrame.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 01054208 _____ (Microsoft Corporation) C:\WINDOWS\system32\audiosrv.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 01037824 _____ (Microsoft Corporation) C:\WINDOWS\system32\SmartcardCredentialProvider.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 00990208 _____ (Microsoft Corporation) C:\WINDOWS\system32\SharedStartModel.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 00912384 _____ (Microsoft Corporation) C:\WINDOWS\system32\usermgr.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 00814080 _____ (Microsoft Corporation) C:\WINDOWS\system32\appwiz.cpl
2016-09-14 08:24 - 2016-09-07 00:30 - 00775168 _____ (Microsoft Corporation) C:\WINDOWS\system32\Display.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 00531456 _____ (Microsoft Corporation) C:\WINDOWS\system32\sppcext.dll
2016-09-14 08:24 - 2016-09-07 00:29 - 01239552 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.Bluetooth.dll
2016-09-14 08:24 - 2016-09-07 00:29 - 00896512 _____ (Microsoft Corporation) C:\WINDOWS\system32\MbaeApiPublic.dll
2016-09-14 08:24 - 2016-09-07 00:29 - 00529920 _____ (Microsoft Corporation) C:\WINDOWS\system32\LogonController.dll
2016-09-14 08:24 - 2016-09-07 00:29 - 00238592 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WindowsCodecsExt.dll
2016-09-14 08:24 - 2016-09-07 00:28 - 02731008 _____ (Microsoft Corporation) C:\WINDOWS\system32\gameux.dll
2016-09-14 08:24 - 2016-09-07 00:28 - 01466368 _____ (Microsoft Corporation) C:\WINDOWS\system32\Pimstore.dll
2016-09-14 08:24 - 2016-09-07 00:28 - 01211904 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Cred.dll
2016-09-14 08:24 - 2016-09-07 00:28 - 00938496 _____ (Microsoft Corporation) C:\WINDOWS\system32\ContactApis.dll
2016-09-14 08:24 - 2016-09-07 00:28 - 00638976 _____ (Microsoft Corporation) C:\WINDOWS\system32\ShareHost.dll
2016-09-14 08:24 - 2016-09-07 00:27 - 03415040 _____ (Microsoft Corporation) C:\WINDOWS\system32\SyncCenter.dll
2016-09-14 08:24 - 2016-09-07 00:27 - 01073152 _____ (Microsoft Corporation) C:\WINDOWS\system32\RDXService.dll
2016-09-14 08:24 - 2016-09-07 00:27 - 00961024 _____ (Microsoft Corporation) C:\WINDOWS\system32\WSShared.dll
2016-09-14 08:24 - 2016-09-07 00:27 - 00799744 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SRH.dll
2016-09-14 08:24 - 2016-09-07 00:25 - 02445312 _____ (Microsoft Corporation) C:\WINDOWS\system32\DWrite.dll
2016-09-14 08:24 - 2016-09-07 00:25 - 01965568 _____ (Microsoft Corporation) C:\WINDOWS\system32\mmc.exe
2016-09-14 08:24 - 2016-09-07 00:25 - 01228800 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Globalization.dll
2016-09-14 08:24 - 2016-09-07 00:25 - 01139712 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\UIAutomationCore.dll
2016-09-14 08:24 - 2016-09-07 00:25 - 00508416 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wpnapps.dll
2016-09-14 08:24 - 2016-09-07 00:25 - 00489984 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.dll
2016-09-14 08:24 - 2016-09-07 00:24 - 03994624 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingsHandlers_nt.dll
2016-09-14 08:24 - 2016-09-07 00:24 - 00805888 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WSShared.dll
2016-09-14 08:24 - 2016-09-07 00:23 - 01490432 _____ (Microsoft Corporation) C:\WINDOWS\system32\UserDataService.dll
2016-09-14 08:24 - 2016-09-07 00:22 - 01113600 _____ (Microsoft Corporation) C:\WINDOWS\system32\gpedit.dll
2016-09-14 08:24 - 2016-09-07 00:21 - 00636928 _____ (Microsoft Corporation) C:\WINDOWS\system32\hgcpl.dll
2016-09-14 08:24 - 2016-09-07 00:21 - 00613376 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingSync.dll
2016-09-14 08:24 - 2016-09-07 00:20 - 06976000 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Data.Pdf.dll
2016-09-14 08:24 - 2016-09-07 00:20 - 03585536 _____ (Microsoft Corporation) C:\WINDOWS\system32\SystemSettingsThresholdAdminFlowUI.dll
2016-09-14 08:24 - 2016-09-07 00:20 - 00583680 _____ (Microsoft Corporation) C:\WINDOWS\system32\PhotoScreensaver.scr
2016-09-14 08:24 - 2016-09-07 00:19 - 04078592 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\dbgeng.dll
2016-09-14 08:24 - 2016-09-07 00:19 - 02610176 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetworkMobileSettings.dll
2016-09-14 08:24 - 2016-09-07 00:19 - 02563584 _____ (Microsoft Corporation) C:\WINDOWS\system32\themecpl.dll
2016-09-14 08:24 - 2016-09-07 00:19 - 01141248 _____ (Microsoft Corporation) C:\WINDOWS\system32\winipcsecproc.dll
2016-09-14 08:24 - 2016-09-07 00:19 - 00527872 _____ (Microsoft Corporation) C:\WINDOWS\system32\w32time.dll
2016-09-14 08:24 - 2016-09-07 00:19 - 00515584 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\PhotoScreensaver.scr
2016-09-14 08:24 - 2016-09-07 00:17 - 05123072 _____ (Microsoft Corporation) C:\WINDOWS\system32\dbgeng.dll
2016-09-14 08:24 - 2016-09-07 00:16 - 02635776 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Logon.dll
2016-09-14 08:24 - 2016-09-07 00:15 - 00802816 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ntshrui.dll
2016-09-14 08:24 - 2016-09-07 00:14 - 02000896 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\twinui.appcore.dll
2016-09-14 08:24 - 2016-09-07 00:14 - 01097216 _____ (Microsoft Corporation) C:\WINDOWS\system32\dosvc.dll
2016-09-14 08:24 - 2016-09-07 00:13 - 01390592 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Shell.dll
2016-09-14 08:24 - 2016-09-07 00:13 - 00984576 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingSyncCore.dll
2016-09-14 08:24 - 2016-09-07 00:13 - 00711680 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\D3D12.dll
2016-09-14 08:24 - 2016-09-07 00:12 - 02632192 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\rdpcore.dll
2016-09-14 08:24 - 2016-09-07 00:12 - 01036288 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Media.Streaming.dll
2016-09-14 08:24 - 2016-09-07 00:11 - 00958976 _____ (Microsoft Corporation) C:\WINDOWS\system32\RemoteNaturalLanguage.dll
2016-09-14 08:24 - 2016-09-07 00:11 - 00621568 _____ (Microsoft Corporation) C:\WINDOWS\system32\DbgModel.dll
2016-09-14 08:24 - 2016-09-07 00:11 - 00459776 _____ (Microsoft Corporation) C:\WINDOWS\system32\certcli.dll
2016-09-14 08:24 - 2016-09-07 00:10 - 00770048 _____ (Microsoft Corporation) C:\WINDOWS\system32\certca.dll
2016-09-14 08:24 - 2016-09-07 00:10 - 00438784 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\DbgModel.dll
2016-09-14 08:23 - 2016-09-07 00:39 - 00090624 _____ (Microsoft Corporation) C:\WINDOWS\system32\FingerprintEnrollment.dll
2016-09-14 08:23 - 2016-09-07 00:38 - 00110080 _____ (Microsoft Corporation) C:\WINDOWS\system32\IdCtrls.dll
2016-09-14 08:23 - 2016-09-07 00:36 - 00237056 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetworkDesktopSettings.dll
2016-09-14 08:23 - 2016-09-07 00:36 - 00233984 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\DictationManager.dll
2016-09-14 08:23 - 2016-09-07 00:35 - 00813056 _____ (Microsoft Corporation) C:\WINDOWS\system32\mqsnap.dll
2016-09-14 08:23 - 2016-09-07 00:35 - 00318976 _____ (Microsoft Corporation) C:\WINDOWS\system32\domgmt.dll
2016-09-14 08:23 - 2016-09-07 00:35 - 00258560 _____ (Microsoft Corporation) C:\WINDOWS\system32\credprovs.dll
2016-09-14 08:23 - 2016-09-07 00:35 - 00188416 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.PicturePassword.dll
2016-09-14 08:23 - 2016-09-07 00:34 - 00492544 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingsHandlers_StorageSense.dll
2016-09-14 08:23 - 2016-09-07 00:34 - 00392192 _____ (Microsoft Corporation) C:\WINDOWS\system32\zipfldr.dll
2016-09-14 08:23 - 2016-09-07 00:31 - 00769536 _____ (Microsoft Corporation) C:\WINDOWS\system32\sppinst.dll
2016-09-14 08:23 - 2016-09-07 00:31 - 00183808 _____ (Microsoft Corporation) C:\WINDOWS\system32\WSSync.dll
2016-09-14 08:23 - 2016-09-07 00:30 - 01500672 _____ (Microsoft Corporation) C:\WINDOWS\system32\dbghelp.dll
2016-09-14 08:23 - 2016-09-07 00:30 - 00607232 _____ (Microsoft Corporation) C:\WINDOWS\system32\WUDFx.dll
2016-09-14 08:23 - 2016-09-07 00:29 - 00236032 _____ (Microsoft Corporation) C:\WINDOWS\system32\licensingdiag.exe
2016-09-14 08:23 - 2016-09-07 00:28 - 00243712 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingMonitor.dll
2016-09-14 08:23 - 2016-09-07 00:27 - 00153088 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WSSync.dll
2016-09-14 08:23 - 2016-09-07 00:20 - 06675968 _____ (Microsoft Corporation) C:\WINDOWS\system32\mspaint.exe
2016-09-14 08:23 - 2016-09-07 00:19 - 00088064 _____ (Microsoft Corporation) C:\WINDOWS\system32\ImplatSetup.dll
2016-09-13 11:35 - 2016-09-15 08:49 - 00000000 ____D C:\GT500
2016-09-12 11:06 - 2016-09-12 11:06 - 00001956 _____ C:\Users\Public\Desktop\QuickTime Player.lnk
2016-09-12 11:06 - 2016-09-12 11:06 - 00000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\QuickTime
2016-09-12 11:06 - 2016-09-12 11:06 - 00000000 ____D C:\Program Files (x86)\QuickTime
2016-09-12 11:00 - 2016-09-13 11:00 - 00004562 _____ C:\WINDOWS\System32\Tasks\Adobe Acrobat Update Task
2016-09-12 11:00 - 2016-09-13 11:00 - 00002457 _____ C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Acrobat Reader DC.lnk
2016-09-12 11:00 - 2016-09-12 11:00 - 00002166 _____ C:\Users\Public\Desktop\Acrobat Reader DC.lnk
2016-08-26 08:55 - 2016-08-26 08:55 - 00003324 _____ C:\WINDOWS\System32\Tasks\OneDrive Standalone Update Task
2016-08-26 08:54 - 2016-08-26 08:54 - 00000000 ____D C:\Users\Paddy\AppData\Roaming\Skype
 
==================== One Month Modified files and folders ========
 
(If an entry is included in the fixlist, the file/folder will be moved.)
 
2016-09-21 12:44 - 2012-04-07 08:06 - 00000830 _____ C:\WINDOWS\Tasks\Adobe Flash Player Updater.job
2016-09-21 12:34 - 2012-09-21 12:27 - 00000920 _____ C:\WINDOWS\Tasks\GoogleUpdateTaskMachineUA.job
2016-09-21 12:34 - 2012-09-21 12:27 - 00000916 _____ C:\WINDOWS\Tasks\GoogleUpdateTaskMachineCore.job
2016-09-21 10:44 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\SysWOW64\Macromed
2016-09-21 10:44 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\system32\Macromed
2016-09-20 22:38 - 2015-12-22 18:21 - 00000000 ___DC C:\WINDOWS\Panther
2016-09-20 21:12 - 2016-06-05 18:36 - 00003238 _____ C:\WINDOWS\System32\Tasks\HPCeeScheduleForPaddy
2016-09-20 21:12 - 2016-06-05 18:36 - 00000346 _____ C:\WINDOWS\Tasks\HPCeeScheduleForPaddy.job
2016-09-20 20:39 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\AppReadiness
2016-09-20 16:36 - 2015-10-30 03:24 - 00000000 ___HD C:\Program Files\WindowsApps
2016-09-20 10:34 - 2012-01-21 12:52 - 00000000 ____D C:\Job
2016-09-19 08:37 - 2011-09-14 01:11 - 00000000 ____D C:\ProgramData\PDFC
2016-09-16 20:34 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\rescache
2016-09-16 19:55 - 2012-09-21 12:29 - 00002314 _____ C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Google Chrome.lnk
2016-09-16 18:53 - 2015-10-30 03:21 - 00000000 ____D C:\WINDOWS\INF
2016-09-16 18:48 - 2015-12-22 15:59 - 00000000 __RHD C:\Users\Public\AccountPictures
2016-09-16 18:45 - 2015-12-22 15:54 - 00000006 ____H C:\WINDOWS\Tasks\SA.DAT
2016-09-16 18:45 - 2015-12-22 15:47 - 00142832 ____N (CyberLink Corp.) C:\WINDOWS\system32\Drivers\rikvm_38F51D56.sys
2016-09-16 18:44 - 2015-10-30 02:28 - 00524288 ___SH C:\WINDOWS\system32\config\BBI
2016-09-16 18:40 - 2015-10-30 03:24 - 00000000 ___SD C:\WINDOWS\SysWOW64\F12
2016-09-16 18:40 - 2015-10-30 03:24 - 00000000 ___SD C:\WINDOWS\system32\F12
2016-09-16 18:40 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\system32\SystemResetPlatform
2016-09-16 18:40 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\system32\setup
2016-09-16 18:40 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\system32\oobe
2016-09-16 18:40 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\system32\migwiz
2016-09-16 18:40 - 2015-10-30 02:31 - 00000000 ____D C:\WINDOWS\SysWOW64\AdvancedInstallers
2016-09-16 18:40 - 2015-10-30 02:31 - 00000000 ____D C:\WINDOWS\system32\AdvancedInstallers
2016-09-16 18:40 - 2015-10-30 02:28 - 00000000 ____D C:\WINDOWS\SysWOW64\Dism
2016-09-16 18:40 - 2015-10-30 02:28 - 00000000 ____D C:\WINDOWS\system32\Dism
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ___RD C:\WINDOWS\PrintDialog
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ___RD C:\WINDOWS\ImmersiveControlPanel
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ___RD C:\WINDOWS\DevicesFlow
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ____D C:\Program Files\Windows Photo Viewer
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ____D C:\Program Files\Windows Defender
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ____D C:\Program Files (x86)\Windows Photo Viewer
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ____D C:\Program Files (x86)\Windows Defender
2016-09-16 18:34 - 2013-03-13 21:58 - 00000000 ____D C:\Program Files\Microsoft Silverlight
2016-09-16 18:34 - 2013-03-13 21:58 - 00000000 ____D C:\Program Files (x86)\Microsoft Silverlight
2016-09-15 14:16 - 2015-12-22 15:32 - 01010622 _____ C:\WINDOWS\system32\PerfStringBackup.INI
2016-09-14 08:46 - 2015-10-30 03:11 - 00000000 ____D C:\WINDOWS\CbsTemp
2016-09-14 08:42 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\system32\appraiser
2016-09-14 08:42 - 2013-03-13 21:59 - 00000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Microsoft Silverlight
2016-09-14 08:41 - 2013-07-13 08:28 - 00000000 ____D C:\WINDOWS\system32\MRT
2016-09-14 08:36 - 2011-10-08 17:15 - 144199024 ____C (Microsoft Corporation) C:\WINDOWS\system32\MRT.exe
2016-09-13 11:00 - 2012-09-21 12:27 - 00000000 ____D C:\ProgramData\Adobe
2016-09-12 23:33 - 2015-12-22 15:59 - 00000000 ____D C:\Users\Paddy\AppData\Local\Packages
2016-09-12 11:01 - 2016-06-02 09:45 - 00000000 ____D C:\Users\Paddy\AppData\Local\Adobe
2016-09-12 10:59 - 2012-11-13 15:09 - 00000000 ____D C:\Program Files (x86)\Adobe
2016-09-12 09:59 - 2016-07-18 08:19 - 00000000 ____D C:\Expenses
2016-09-11 20:22 - 2011-11-16 22:23 - 00000000 ____D C:\MyDocs
2016-09-09 12:13 - 2016-01-21 12:49 - 00000000 ____D C:\Legal
2016-09-07 02:04 - 2015-12-22 15:26 - 02718208 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\PrintConfig.dll
2016-09-06 21:00 - 2015-10-30 03:26 - 00828408 _____ (Adobe Systems Incorporated) C:\WINDOWS\SysWOW64\FlashPlayerApp.exe
2016-09-06 21:00 - 2015-10-30 03:26 - 00176632 _____ (Adobe Systems Incorporated) C:\WINDOWS\SysWOW64\FlashPlayerCPLApp.cpl
2016-09-05 22:27 - 2011-10-04 21:03 - 00000000 ____D C:\Users\Paddy\AppData\Roaming\SoftGrid Client
2016-08-26 09:13 - 2015-12-23 22:26 - 00000000 ____D C:\Scans
2016-08-26 08:55 - 2015-12-22 16:04 - 00002403 _____ C:\Users\Paddy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\OneDrive.lnk
2016-08-26 08:55 - 2015-12-22 16:04 - 00000000 ___RD C:\Users\Paddy\OneDrive
 
==================== Files in the root of some directories =======
 
2012-11-17 20:29 - 2012-11-18 14:10 - 0005632 _____ () C:\Users\Paddy\AppData\Local\DCBC2A71-70D8-4DAN-EHR8-E0D61DEA3FDF.ini
 
Some files in TEMP:
====================
C:\Users\Paddy\AppData\Local\Temp\jre-8u66-windows-au.exe
C:\Users\Paddy\AppData\Local\Temp\mccspuninstall.exe
C:\Users\Paddy\AppData\Local\Temp\Runner.exe
C:\Users\Paddy\AppData\Local\Temp\vlc-2.2.1-win32.exe
 
 
==================== Bamital & volsnap =================
 
(There is no automatic fix for files that do not pass verification.)
 
C:\WINDOWS\system32\winlogon.exe => File is digitally signed
C:\WINDOWS\system32\wininit.exe => File is digitally signed
C:\WINDOWS\explorer.exe => File is digitally signed
C:\WINDOWS\SysWOW64\explorer.exe => File is digitally signed
C:\WINDOWS\system32\svchost.exe => File is digitally signed
C:\WINDOWS\SysWOW64\svchost.exe => File is digitally signed
C:\WINDOWS\system32\services.exe => File is digitally signed
C:\WINDOWS\system32\User32.dll => File is digitally signed
C:\WINDOWS\SysWOW64\User32.dll => File is digitally signed
C:\WINDOWS\system32\userinit.exe => File is digitally signed
C:\WINDOWS\SysWOW64\userinit.exe => File is digitally signed
C:\WINDOWS\system32\rpcss.dll => File is digitally signed
C:\WINDOWS\system32\dnsapi.dll => File is digitally signed
C:\WINDOWS\SysWOW64\dnsapi.dll => File is digitally signed
C:\WINDOWS\system32\Drivers\volsnap.sys => File is digitally signed
 
 
LastRegBack: 2016-09-16 19:31
 
==================== End of FRST.txt ============================
 
Additional scan result of Farbar Recovery Scan Tool (x64) Version: 21-09-2016
Ran by [removed] (21-09-2016 13:00:19)
Running from C:\Users\[removed]\Desktop
Windows 10 Home Version 1511 (X64) (2015-12-22 19:58:01)
Boot Mode: Normal
==========================================================
 
 
==================== Accounts: =============================
 
Administrator (S-1-5-21-648858125-4165233436-1298442668-500 - Administrator - Disabled)
DefaultAccount (S-1-5-21-648858125-4165233436-1298442668-503 - Limited - Disabled)
Guest (S-1-5-21-648858125-4165233436-1298442668-501 - Limited - Disabled)
HomeGroupUser$ (S-1-5-21-648858125-4165233436-1298442668-1002 - Limited - Enabled)
Paddy (S-1-5-21-648858125-4165233436-1298442668-1001 - Administrator - Enabled) => C:\Users\Paddy
 
==================== Security Center ========================
 
(If an entry is included in the fixlist, it will be removed.)
 
AV: Windows Defender (Enabled - Up to date) {D68DDC3A-831F-4fae-9E44-DA132C1ACF46}
AS: Windows Defender (Enabled - Up to date) {D68DDC3A-831F-4fae-9E44-DA132C1ACF46}
 
==================== Installed Programs ======================
 
(Only the adware programs with "Hidden" flag could be added to the fixlist to unhide them. The adware programs should be uninstalled manually.)
 
7-Zip 9.22beta (HKLM-x32\…\7-Zip) (Version:  - )
Adobe Acrobat Reader DC (HKLM-x32\…\{AC76BA86-7AD7-1033-7B44-AC0F074E4100}) (Version: 15.017.20053 - Adobe Systems Incorporated)
Adobe AIR (HKLM-x32\…\Adobe AIR) (Version: 1.5.3.9130 - Adobe Systems Inc.)
Adobe Creative Suite 2 (HKLM-x32\…\{0134A1A1-C283-4A47-91A1-92F19F960372}) (Version:  - )
Adobe Flash Player 23 NPAPI (HKLM-x32\…\Adobe Flash Player NPAPI) (Version: 23.0.0.179 - Adobe Systems Incorporated)
Adobe SVG Viewer 3.0 (HKLM-x32\…\Adobe SVG Viewer) (Version:  3.0 - Adobe Systems, Inc.)
Agatha Christie - Peril at End House (x32 Version: 2.2.0.95 - WildTangent) Hidden
AMD Catalyst Control Center (HKLM-x32\…\WUCCCApp) (Version: 1.00.0000 - AMD)
AMD Catalyst Install Manager (HKLM\…\{5E03A267-415E-5383-FA8F-3CE4145663B9}) (Version: 8.0.903.0 - Advanced Micro Devices, Inc.)
Apple Application Support (HKLM-x32\…\{D9DAD0FF-495A-472B-9F10-BAE430A26682}) (Version: 3.0.3 - Apple Inc.)
Apple Mobile Device Support (HKLM\…\{787136D2-F0F8-4625-AA3F-72D7795AC842}) (Version: 7.1.1.3 - Apple Inc.)
Apple Software Update (HKLM-x32\…\{789A5B64-9DD9-4BA5-915A-F0FC0A1B7BFE}) (Version: 2.1.3.127 - Apple Inc.)
ArtecMedia ATSC Digital TV Player 2.0.3.1 (HKLM-x32\…\{A864C2E4-D1DC-4487-82A9-6B988F30A42B}) (Version: 6.00.0000 - Ultima)
AviSynth 2.5 (HKLM-x32\…\AviSynth) (Version:  - )
AVStoDVD 2.5.1 (HKLM-x32\…\AVStoDVD) (Version: 2.5.1 - MrC)
Bejeweled 2 Deluxe (x32 Version: 2.2.0.95 - WildTangent) Hidden
Bejeweled 3 (x32 Version: 2.2.0.95 - WildTangent) Hidden
Blackhawk Striker 2 (x32 Version: 2.2.0.95 - WildTangent) Hidden
Blasterball 3 (x32 Version: 2.2.0.95 - WildTangent) Hidden
Blio (HKLM-x32\…\{9368DDD5-CE7F-4BD7-A83A-F00FABE338EC}) (Version: 2.2.6699 - K-NFB Reading Technology, Inc.)
Bonjour (HKLM\…\{6E3610B2-430D-4EB0-81E3-2B57E8B9DE8D}) (Version: 3.0.0.10 - Apple Inc.)
Bounce Symphony (x32 Version: 2.2.0.95 - WildTangent) Hidden
Build-a-lot 2 (x32 Version: 2.2.0.95 - WildTangent) Hidden
Cake Mania (x32 Version: 2.2.0.95 - WildTangent) Hidden
Canon Auto Update Service (HKLM-x32\…\Auto Update Service) (Version: 1.1.2.18 - Canon Inc.)
Canon Camera WIA Driver (x32 Version: 5.0.4 - Canon) Hidden
Canon Camera WIA Driver (x32 Version: 5.1 - Canon) Hidden
Canon EOS 10D WIA Driver (HKLM-x32\…\InstallShield_{095659A2-739F-4D9A-A916-66C7CAD16F9E}) (Version: 5.1 - Canon)
Canon EOS Kiss REBEL 300D WIA Driver (HKLM-x32\…\InstallShield_{31A57C3E-30DD-421F-B5C7-974DACB0D05F}) (Version: 5.1 - Canon)
Canon FV M10, OPTURA20 WIA Driver (HKLM-x32\…\InstallShield_{6A30F2AE-03B2-47EB-9754-BCF2EC56B7AF}) (Version: 5.0.4 - Canon)
CANON iMAGE GATEWAY MyCamera Download Plugin (HKLM-x32\…\MyCamera Download Plugin) (Version: 3.1.1.2 - Canon Inc.)
CANON iMAGE GATEWAY Task for ZoomBrowser EX (HKLM-x32\…\CANON iMAGE GATEWAY Task) (Version: 1.9.0.9 - Canon Inc.)
Canon MOV Decoder (HKLM-x32\…\Canon MOV Decoder) (Version: 1.9.0.8 - Canon Inc.)
Canon MOV Encoder (HKLM-x32\…\Canon MOV Encoder) (Version: 1.8.0.1 - Canon Inc.)
Canon MovieEdit Task for ZoomBrowser EX (HKLM-x32\…\MovieEditTask) (Version: 3.9.0.6 - Canon Inc.)
Canon OPTURA10 WIA Driver (HKLM-x32\…\InstallShield_{85906114-22EE-4B4F-833A-7907F9D046D4}) (Version: 5.0.4 - Canon)
Canon PhotoRecord (HKLM-x32\…\PhotoRecord) (Version:  - )
Canon Utilities Digital Photo Professional 3.4 (HKLM-x32\…\DPP) (Version: 3.4.1.1 - )
Canon Utilities EOS Utility (HKLM-x32\…\EOS Utility) (Version: 2.12.3.1 - Canon Inc.)
Canon Utilities EOS Video Snapshot Task for ZoomBrowser EX (HKLM-x32\…\EOS Video Snapshot Task) (Version: 1.0.0.10 - Canon Inc.)
Canon Utilities File Viewer Utility 1.3 (HKLM-x32\…\InstallShield_{74344F10-34CA-480E-BD02-B3F4FA692BFA}) (Version: 1.3.1 - Canon)
Canon Utilities PhotoStitch 3.1 (HKLM-x32\…\InstallShield_{F11A403B-0DE9-4953-B790-7A2F014FBB2B}) (Version: 3.1.10 - Canon)
Canon Utilities RemoteCapture 2.7 (HKLM-x32\…\InstallShield_{EF91B23E-3819-43A1-AE47-043E1900EB2B}) (Version: 2.7.4 - Canon)
Canon Utilities ZoomBrowser EX (HKLM-x32\…\ZoomBrowser EX) (Version: 6.9.0.1 - Canon Inc.)
Canon ZoomBrowser EX Memory Card Utility (HKLM-x32\…\ZoomBrowser EX Memory Card Utility) (Version: 1.6.0.15 - Canon Inc.)
Chuzzle Deluxe (x32 Version: 2.2.0.95 - WildTangent) Hidden
Corel Applications (HKLM-x32\…\Corel Applications) (Version:  - )
CPUID HWMonitor 1.24 (HKLM\…\CPUID HWMonitor_is1) (Version:  - )
CyberLink Blu-ray Disc Suite (HKLM-x32\…\InstallShield_{1FBF6C24-C1FD-4101-A42B-0C564F9E8E79}) (Version: 7.0.1929 - CyberLink Corp.)
CyberLink Power2Go (HKLM-x32\…\InstallShield_{40BF1E83-20EB-11D8-97C5-0009C5020658}) (Version: 6.1.3401 - CyberLink Corp.)
CyberLink PowerDirector (HKLM-x32\…\InstallShield_{CB099890-1D5F-11D5-9EA9-0050BAE317E1}) (Version: 7.0.3227a - CyberLink Corp.)
CyberLink PowerDirector 11 (HKLM-x32\…\InstallShield_{551F492A-01B0-4DC4-866F-875EC4EDC0A8}) (Version: 11.0.0.2215 - CyberLink Corp.)
CyberLink PowerDirector 11 (Version: 11.0.0.2215 - CyberLink Corp.) Hidden
CyberLink PowerDirector 11 Content Pack Essential (HKLM-x32\…\InstallShield_{03AD770A-1530-437E-967F-ADD4E5B23164}) (Version: 11 - CyberLink Corp.)
CyberLink PowerDirector 11 Content Pack Premium (HKLM-x32\…\InstallShield_{37672760-7930-4911-9685-227E29AE2C55}) (Version: 11 - CyberLink Corp.)
CyberLink PowerDVD 10 (HKLM-x32\…\InstallShield_{DEC235ED-58A4-4517-A278-C41E8DAEAB3B}) (Version: 10.0.1.2615 - CyberLink Corp.)
CyberLink PowerDVD 9 (HKLM-x32\…\InstallShield_{A8516AC9-AAF1-47F9-9766-03E2D4CDBCF8}) (Version: 9.0.2101 - CyberLink Corp.)
CyberLink WaveEditor 2 (HKLM-x32\…\InstallShield_{324F76CC-D8DD-4D87-B77D-D4AF5E1AA7B3}) (Version: 2.0.3206 - CyberLink Corp.)
D3DX10 (x32 Version: 15.4.2368.0902 - Microsoft) Hidden
Digital Copy (HKLM-x32\…\Digital Copy) (Version:  - )
Diner Dash 2 Restaurant Rescue (x32 Version: 2.2.0.95 - WildTangent) Hidden
Dora's World Adventure (x32 Version: 2.2.0.95 - WildTangent) Hidden
ESET Online Scanner v3 (HKLM-x32\…\ESET Online Scanner) (Version:  - )
Farm Frenzy (x32 Version: 2.2.0.95 - WildTangent) Hidden
FATE - The Traitor Soul (x32 Version: 2.2.0.95 - WildTangent) Hidden
File Viewer Utility 1.3.1 (x32 Version: 1.3.1 - Canon) Hidden
Google Chrome (HKLM-x32\…\Google Chrome) (Version: 53.0.2785.116 - Google Inc.)
Google Earth (HKLM-x32\…\{817750FA-EC6A-485D-9901-0683AE6FFDF1}) (Version: 7.1.5.1557 - Google)
Google Toolbar for Internet Explorer (HKLM-x32\…\{2318C2B1-4965-11d4-9B18-009027A5CD4F}) (Version: 7.5.7619.1252 - Google Inc.)
Google Toolbar for Internet Explorer (x32 Version: 1.0.0 - Google Inc.) Hidden
Google Update Helper (x32 Version: 1.3.25.11 - Google Inc.) Hidden
Google Update Helper (x32 Version: 1.3.31.5 - Google Inc.) Hidden
Grab & Burn, Version 4.0.1 ( Build 2005-09-21, Win32, CSS ) (HKLM-x32\…\Rocket Division Software Grab & Burn_is1) (Version:  - Rocket Division Software)
Haali Media Splitter (HKLM-x32\…\HaaliMkx) (Version:  - )
Hewlett-Packard ACLM.NET v1.2.2.3 (x32 Version: 1.00.0000 - Hewlett-Packard Company) Hidden
HP Games (HKLM-x32\…\WildTangent hp Master Uninstall) (Version: 1.0.2.4 - WildTangent)
HP LinkUp (HKLM-x32\…\{C1AD9241-3ADD-483F-914D-071F3E50855A}) (Version: 2.01.026 - Hewlett-Packard)
HP MediaSmart/TouchSmart Netflix (HKLM-x32\…\{BB760C1D-98F4-4E38-8CC4-3B67329AA981}) (Version: 1.0.6.0 - Hewlett-Packard)
HP MovieStore (HKLM-x32\…\{9008D736-35CA-40DB-A2BE-5F32D954E5AA}) (Version: 2.0 - Hewlett-Packard)
HP Odometer (HKLM-x32\…\{B8AC1A89-FFD1-4F97-8051-E505A160F562}) (Version: 2.10.0000 - Hewlett-Packard)
HP Product Detection (HKLM-x32\…\{A436F67F-687E-4736-BD2B-537121A804CF}) (Version: 11.14.0001 - HP)
HP Setup (HKLM-x32\…\{210A03F5-B2ED-4947-B27E-516F50CBB292}) (Version: 8.6.4530.3651 - Hewlett-Packard Company)
HP Setup Manager (HKLM-x32\…\{AE856388-AFAD-4753-81DF-D96B19D0A17C}) (Version: 1.1.13253.3682 - Hewlett-Packard Company)
HP Support Assistant (HKLM-x32\…\{79C54A05-F146-4EA0-8A70-D4EFE6181E52}) (Version: 8.3.34.7 - Hewlett-Packard Company)
HP Support Information (HKLM-x32\…\{7F2A11F4-EAE8-4325-83EC-E3E99F85169E}) (Version: 10.1.1000 - Hewlett-Packard)
HP Support Solutions Framework (HKLM-x32\…\{55065080-504F-43BB-BE00-36B80D7D39A5}) (Version: 12.5.32.37 - Hewlett-Packard Company)
HP Update (HKLM-x32\…\{DE77FE3F-A33D-499A-87AD-5FC406617B40}) (Version: 5.002.003.003 - Hewlett-Packard)
HP Vision Hardware Diagnostics (HKLM\…\{D79A02E9-6713-4335-9668-AAC7474C0C0E}) (Version: 2.5.0.0 - Hewlett-Packard)
Hulu Desktop (HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\HuluDesktop) (Version: 0.9.13 - Hulu LLC)
HydraVision (x32 Version: 4.2.212.0 - Advanced Micro Devices, Inc.) Hidden
iCloud (HKLM\…\{81E20D41-C277-4526-934D-F2380AF91B78}) (Version: 3.1.0.40 - Apple Inc.)
IDT Audio (HKLM-x32\…\{E3A5A8AB-58F6-45FF-AFCB-C9AE18C05001}) (Version: 1.0.6325.0 - IDT)
ImgBurn (HKLM-x32\…\ImgBurn) (Version: 2.5.5.0 - LIGHTNING UK!)
Intel(R) Management Engine Components (HKLM-x32\…\{65153EA5-8B6E-43B6-857B-C6E4FC25798A}) (Version: 7.0.0.1144 - Intel Corporation)
iTunes (HKLM\…\{5A68A656-979F-4168-8795-E2E368AA4DC2}) (Version: 11.2.2.3 - Apple Inc.)
Java 8 Update 66 (HKLM-x32\…\{26A24AE4-039D-4CA4-87B4-2F83218066F0}) (Version: 8.0.660.18 - Oracle Corporation)
Junk Mail filter update (x32 Version: 16.4.3528.0331 - Microsoft Corporation) Hidden
Kobo (HKLM-x32\…\Kobo) (Version: 1.6 - Kobo Inc.)
LabelPrint (HKLM-x32\…\InstallShield_{C59C179C-668D-49A9-B6EA-0121CCFC1243}) (Version: 2.5.3609 - CyberLink Corp.)
LabelPrint (x32 Version: 2.5.3609 - CyberLink Corp.) Hidden
Mah Jong Medley (x32 Version: 2.2.0.95 - WildTangent) Hidden
Malwarebytes Anti-Malware version 1.75.0.1300 (HKLM-x32\…\Malwarebytes' Anti-Malware_is1) (Version: 1.75.0.1300 - Malwarebytes Corporation)
McAfee Online Backup (Version: 1.16.4.0 - McAfee, Inc.) Hidden
McAfee Online Backup (x32 Version:  - McAfee, Inc.) Hidden
MediaInfo 0.7.61 (HKLM\…\MediaInfo) (Version: 0.7.61 - MediaArea.net)
Microsoft Office 2010 (HKLM-x32\…\{95140000-0070-0000-0000-0000000FF1CE}) (Version: 14.0.4763.1000 - Microsoft Corporation)
Microsoft Office Click-to-Run 2010 (HKLM-x32\…\Office14.Click2Run) (Version: 14.0.4763.1000 - Microsoft Corporation)
Microsoft Office Starter 2010 - English (HKLM-x32\…\{90140011-0066-0409-0000-0000000FF1CE}) (Version: 14.0.4763.1000 - Microsoft Corporation)
Microsoft Silverlight (HKLM\…\{89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}) (Version: 5.1.50709.0 - Microsoft Corporation)
Microsoft SQL Server 2005 Compact Edition [ENU] (HKLM-x32\…\{F0B430D1-B6AA-473D-9B06-AA3DD01FD0B8}) (Version: 3.1.0000 - Microsoft Corporation)
Microsoft Visio Professional 2002 [English] (HKLM-x32\…\{90500409-6D54-11D4-BEE3-00C04F990354}) (Version: 10.2.5110 - Microsoft Corporation)
Microsoft Visual C++ 2005 Redistributable (HKLM-x32\…\{710f4c1c-cc18-4c49-8cbf-51240c89a1a2}) (Version: 8.0.61001 - Microsoft Corporation)
Microsoft Visual C++ 2005 Redistributable (HKLM-x32\…\{7299052b-02a4-4627-81f2-1818da5d550d}) (Version: 8.0.56336 - Microsoft Corporation)
Microsoft Visual C++ 2005 Redistributable (x64) (HKLM\…\{071c9b48-7c32-4621-a0ac-3f809523288f}) (Version: 8.0.56336 - Microsoft Corporation)
Microsoft Visual C++ 2005 Redistributable (x64) (HKLM\…\{ad8a2fa1-06e7-4b0d-927d-6e54b3d31028}) (Version: 8.0.61000 - Microsoft Corporation)
Microsoft Visual C++ 2008 Redistributable - x64 9.0.30729.17 (HKLM\…\{8220EEFE-38CD-377E-8595-13398D740ACE}) (Version: 9.0.30729 - Microsoft Corporation)
Microsoft Visual C++ 2008 Redistributable - x64 9.0.30729.4148 (HKLM\…\{4B6C7001-C7D6-3710-913E-5BC23FCE91E6}) (Version: 9.0.30729.4148 - Microsoft Corporation)
Microsoft Visual C++ 2008 Redistributable - x64 9.0.30729.6161 (HKLM\…\{5FCE6D76-F5DC-37AB-B2B8-22AB8CEDB1D4}) (Version: 9.0.30729.6161 - Microsoft Corporation)
Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.17 (HKLM-x32\…\{9A25302D-30C0-39D9-BD6F-21E6EC160475}) (Version: 9.0.30729 - Microsoft Corporation)
Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.4148 (HKLM-x32\…\{1F1C2DFC-2D24-3E06-BCB8-725134ADF989}) (Version: 9.0.30729.4148 - Microsoft Corporation)
Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.6161 (HKLM-x32\…\{9BE518E6-ECC6-35A9-88E4-87755C07200F}) (Version: 9.0.30729.6161 - Microsoft Corporation)
Microsoft Visual C++ 2010  x64 Redistributable - 10.0.30319 (HKLM\…\{DA5E371C-6333-3D8A-93A4-6FD5B20BCC6E}) (Version: 10.0.30319 - Microsoft Corporation)
Microsoft Visual C++ 2010  x86 Redistributable - 10.0.30319 (HKLM-x32\…\{196BB40D-1578-3D01-B289-BEFC77A11A1E}) (Version: 10.0.30319 - Microsoft Corporation)
Microsoft Visual C++ 2012 Redistributable (x64) - 11.0.61030 (HKLM-x32\…\{ca67548a-5ebe-413a-b50c-4b9ceb6d66c6}) (Version: 11.0.61030.0 - Microsoft Corporation)
Microsoft Visual C++ 2012 Redistributable (x86) - 11.0.61030 (HKLM-x32\…\{33d1fd90-4274-48a1-9bc1-97e33d9c2d6f}) (Version: 11.0.61030.0 - Microsoft Corporation)
MKVToolNix 5.7.0 (HKLM-x32\…\MKVToolNix) (Version: 5.7.0 - Moritz Bunkus)
Movie Maker (x32 Version: 16.4.3528.0331 - Microsoft Corporation) Hidden
MSXML 4.0 SP2 (KB954430) (HKLM-x32\…\{86493ADD-824D-4B8E-BD72-8C5DCDC52A71}) (Version: 4.20.9870.0 - Microsoft Corporation)
MSXML 4.0 SP2 (KB973688) (HKLM-x32\…\{F662A8E6-F4DC-41A2-901E-8C11F044BDEC}) (Version: 4.20.9876.0 - Microsoft Corporation)
Mystery P.I. - Stolen in San Francisco (x32 Version: 2.2.0.95 - WildTangent) Hidden
Namco All-Stars PAC-MAN (x32 Version: 2.2.0.95 - WildTangent) Hidden
Newblue Art Effects for PowerDirector (HKLM\…\NewBlue Art Effects for PowerDirector) (Version: 2.0 - NewBlue)
OpenOffice 4.1.2 (HKLM-x32\…\{E6AD67BB-1C33-4AB3-A387-E0D48137AB70}) (Version: 4.12.9782 - Apache Software Foundation)
PDF Complete Special Edition (HKLM-x32\…\PDF Complete) (Version: 4.0.35 - PDF Complete, Inc)
Penguins! (x32 Version: 2.2.0.95 - WildTangent) Hidden
PhotoStitch (x32 Version: 3.1.10 - Canon) Hidden
Plants vs. Zombies - Game of the Year (x32 Version: 2.2.0.95 - WildTangent) Hidden
PlayReady PC Runtime amd64 (HKLM\…\{BCA9334F-B6C9-4F65-9A73-AC5A329A4D04}) (Version: 1.3.0 - Microsoft Corporation)
PlayReady PC Runtime x86 (HKLM-x32\…\{CCA5EAAD-92F4-4B7A-B5EE-14294C66AB61}) (Version: 1.3.0 - Microsoft Corporation)
Poker Superstars III (x32 Version: 2.2.0.95 - WildTangent) Hidden
Polar Bowler (x32 Version: 2.2.0.95 - WildTangent) Hidden
Polar Golfer (x32 Version: 2.2.0.95 - WildTangent) Hidden
PressReader (HKLM-x32\…\{912CED74-88D3-4C5B-ACB0-132318649765}) (Version: 5.10.1217.0 -  NewspaperDirect Inc.)
QuickTime 7 (HKLM-x32\…\{627FFC10-CE0A-497F-BA2B-208CAC638010}) (Version: 7.77.80.95 - Apple Inc.)
RAR File Open Knife - Free Opener (HKLM-x32\…\RAR File Open Knife - Free Opener) (Version: 3.40 - Philipp Winterberg)
Recovery Manager (x32 Version: 5.5.3621 - CyberLink Corp.) Hidden
RegiStax 6 (HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\RegiStax 6) (Version:  - )
RegiStax 6.1.0.8 update (HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\RegiStax 6.1.0.8 update) (Version:  - )
Remote Graphics Receiver (HKLM-x32\…\{16FC3056-90C0-4757-8A68-64D8DA846ADA}) (Version: 5.4.5 - Hewlett-Packard)
RemoteCapture 2.7.4 (x32 Version: 2.7.4 - Canon) Hidden
RoxioNow Player (HKLM-x32\…\{0EDEB615-1A60-425E-8306-0E10519C7B55}) (Version: 1.9.5.103 - RoxioNow)
SentriCard Utility (HKLM-x32\…\{14B8F58C-4BD8-4122-9FE6-827527626392}_is1) (Version: 4.0.0 - SentriLock, LLC)
Shared C Run-time for x64 (HKLM\…\{EF79C448-6946-4D71-8134-03407888C054}) (Version: 10.0.0 - McAfee)
Slingo Supreme (x32 Version: 2.2.0.95 - WildTangent) Hidden
SmartSound Quicktracks 5 (HKLM-x32\…\InstallShield_{2F8BA3FD-1FA9-4279-B696-712ABB12F09F}) (Version: 5.1.8 - SmartSound Software Inc.)
SmartSound Quicktracks 5 (x32 Version: 5.1.8 - SmartSound Software Inc.) Hidden
SnagIt 7 (HKLM-x32\…\SnagIt7) (Version: 7.2 - TechSmith Corporation)
SpeedFan (remove only) (HKLM-x32\…\SpeedFan) (Version:  - ) <==== ATTENTION
STOPzilla (HKLM-x32\…\{4E1D975D-9BF3-43CF-AA30-7186CEE3D9DE}) (Version: 5.0.98.115 - iS3 Inc.)
StreamTorrent 1.0 (HKLM-x32\…\StreamTorrent 1.0) (Version:  - )
Suite Specific (x32 Version: 2.0.0 - Adobe Systems, Incorporated) Hidden
Update Installer for WildTangent Games App (x32 Version:  - WildTangent) Hidden
VAFPlayer (HKLM-x32\…\{EBE677C0-CBCB-4EBF-8098-E27E1B5271CF}) (Version: 1.6.8 - Tuguu SL) <==== ATTENTION
Virtual Villagers 4 - The Tree of Life (x32 Version: 2.2.0.95 - WildTangent) Hidden
VLC media player (HKLM-x32\…\VLC media player) (Version: 2.2.1 - VideoLAN)
VueScan x64 (HKLM\…\VueScan x64) (Version:  - )
Wheel of Fortune 2 (x32 Version: 2.2.0.95 - WildTangent) Hidden
WhiteSmoke New Toolbar (HKLM-x32\…\WhiteSmoke_New Toolbar) (Version: 6.13.50.5 - WhiteSmoke New) <==== ATTENTION
WhoCrashed 5.00 (HKLM\…\WhoCrashed_is1) (Version:  - Resplendence Software Projects Sp.)
WildTangent Games App (HP Games) (x32 Version: 4.0.5.2 - WildTangent) Hidden
Windows Live Essentials (HKLM-x32\…\WinLiveSuite) (Version: 16.4.3528.0331 - Microsoft Corporation)
Wondershare Dr.Fone for iOS(Build 4.5.1.6) (HKLM-x32\…\{A26F8BBD-EC10-4bdc-8AD8-F146825A8A63}_is1) (Version: 4.5.1.6 - Wondershare Software Co.,Ltd.)
Yahoo! Software Update (HKLM-x32\…\Yahoo! Software Update) (Version:  - )
Yahoo! Toolbar (HKLM-x32\…\Yahoo! Companion) (Version:  - Yahoo! Inc.)
Zuma Deluxe (x32 Version: 2.2.0.95 - WildTangent) Hidden
 
==================== Custom CLSID (Whitelisted): ==========================
 
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
 
CustomCLSID: HKU\S-1-5-21-648858125-4165233436-1298442668-1001_Classes\CLSID\{71DCE5D6-4B57-496B-AC21-CD5B54EB93FD}\localserver32 -> C:\Users\Paddy\AppData\Local\Microsoft\OneDrive\17.3.6517.0809\FileCoAuth.exe (Microsoft Corporation)
 
==================== Scheduled Tasks (Whitelisted) =============
 
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
 
Task: {042937CB-5476-4C2A-8480-C5E036578E2B} - System32\Tasks\Microsoft\Windows\Media Center\OCURActivate => C:\Windows\ehome\ehPrivJob.exe
Task: {08C5B79B-286B-438C-9068-A979952C531F} - \Microsoft\Windows\Setup\GWXTriggers\ScheduleUpgradeReminderTime -> No File <==== ATTENTION
Task: {0987D9CD-C136-4608-81D4-64E705CAAAD4} - \Microsoft\Windows\Setup\GWXTriggers\Logon-5d -> No File <==== ATTENTION
Task: {2BF673A6-60F6-4999-B64B-2AB220858EE9} - System32\Tasks\OneDrive Standalone Update Task => C:\Users\Paddy\AppData\Local\Microsoft\OneDrive\17.3.6517.0809\OneDriveStandaloneUpdater.exe [2016-08-26] (Microsoft Corporation)
Task: {2F04F48E-5A44-435C-AB51-3BE5C3C1CA62} - \Microsoft\Windows\Setup\gwx\runappraiser -> No File <==== ATTENTION
Task: {2F7FDCDC-5B7D-4D76-ADAD-56B53EDC15CA} - System32\Tasks\Microsoft\Windows\RemovalTools\MRT_HB => C:\WINDOWS\system32\MRT.exe [2016-09-14] (Microsoft Corporation)
Task: {356A9E84-A83A-4B9C-9D93-B133D8480A15} - \Microsoft\Windows\Setup\gwx\refreshgwxconfig -> No File <==== ATTENTION
Task: {35A742C1-2971-4943-A2E3-29AD462FFAAC} - System32\Tasks\Microsoft\Windows\Media Center\ActivateWindowsSearch => C:\Windows\ehome\ehPrivJob.exe
Task: {36FE09F7-3866-4448-8EA0-5A57BA498920} - \Microsoft\Windows\Setup\GWXTriggers\Time-5d -> No File <==== ATTENTION
Task: {3ACF76E4-F5DF-431C-BEA2-BE70CF85AE6D} - System32\Tasks\Microsoft\Windows\Media Center\MediaCenterRecoveryTask => C:\Windows\ehome\mcupdate.exe
Task: {448270B0-5154-498D-B24D-AE71E7DB5927} - System32\Tasks\Microsoft\Windows\Media Center\RegisterSearch => C:\Windows\ehome\ehPrivJob.exe
Task: {4EF9C94A-BEB8-4886-8EFB-6F8DC72DE967} - System32\Tasks\Microsoft\Windows\Media Center\ReindexSearchRoot => C:\Windows\ehome\ehPrivJob.exe
Task: {53ABC437-1B0B-41C8-BFA8-0949927B2CAE} - System32\Tasks\Microsoft\Windows\Media Center\PBDADiscoveryW1 => C:\Windows\ehome\ehPrivJob.exe
Task: {55FDF64B-3C5A-49F4-9EC4-597B575CA285} - System32\Tasks\Microsoft\Windows\Media Center\InstallPlayReady => C:\Windows\ehome\ehPrivJob.exe
Task: {60C6872D-D8C5-4B88-8980-45D08F81447E} - System32\Tasks\Microsoft\Windows\Media Center\PvrScheduleTask => C:\Windows\ehome\mcupdate.exe
Task: {66373DB8-4A8D-49A8-88A9-7AC45A9257AE} - System32\Tasks\Microsoft\Windows\Media Center\PeriodicScanRetry => C:\Windows\ehome\MCUpdate.exe
Task: {69A85CF5-3B46-41A1-B827-33B63DB62BAE} - System32\Tasks\Adobe Acrobat Update Task => C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe [2016-09-08] (Adobe Systems Incorporated)
Task: {7293FCCA-AC47-4346-9D5F-E0A9DE260C61} - \Microsoft\Windows\Setup\GWXTriggers\OutOfSleep-5d -> No File <==== ATTENTION
Task: {7502276F-9935-472B-ABF9-2F920A8A92EB} - System32\Tasks\Hewlett-Packard\HP Support Assistant\PC Health Analysis => C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\HPSF.exe [2016-08-23] (HP Inc.)
Task: {76028AB5-AC97-4F06-8327-7D5A47A19935} - System32\Tasks\Microsoft\Windows\Media Center\OCURDiscovery => C:\Windows\ehome\ehPrivJob.exe
Task: {7953A881-3F54-4DC6-A2C4-8D0F4AB8AF05} - System32\Tasks\Hewlett-Packard\HP Support Assistant\HP Support Assistant Quick Start => C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\HPSF.exe [2016-08-23] (HP Inc.)
Task: {8019363D-BCAD-4773-B90D-F17D42075CBA} - System32\Tasks\Microsoft\Windows\Media Center\PvrRecoveryTask => C:\Windows\ehome\mcupdate.exe
Task: {864A4654-1B29-4B85-8A8F-1AC23D143017} - \Microsoft\Windows\Setup\gwx\refreshgwxconfigandcontent -> No File <==== ATTENTION
Task: {8D77A25D-FD6A-481A-B0D6-9678902CB9A5} - System32\Tasks\Microsoft\Windows\Media Center\mcupdate => C:\Windows\ehome\mcupdate.exe
Task: {9476FD46-509C-405E-A723-F3191093CD98} - \Microsoft\Windows\Setup\gwx\launchtrayprocess -> No File <==== ATTENTION
Task: {97D57FBC-B035-440C-88E7-9E676CD64057} - System32\Tasks\Microsoft\Windows\Media Center\PBDADiscovery => C:\Windows\ehome\ehPrivJob.exe
Task: {9EE88514-786B-4C6B-B761-AD00A3815399} - System32\Tasks\Microsoft\Windows\Media Center\RecordingRestart => C:\Windows\ehome\ehrec.exe
Task: {A67AFEE4-8A57-4634-9B58-0147D5676442} - System32\Tasks\Microsoft\Windows\Media Center\mcupdate_scheduled => C:\Windows\ehome\mcupdate.exe
Task: {ABE81196-0AAC-419A-993A-CA0F9FA7E738} - System32\Tasks\Microsoft\Windows\Media Center\ObjectStoreRecoveryTask => C:\Windows\ehome\mcupdate.exe
Task: {AC32D329-1AFB-40FB-97DE-9A3C3DAD84EA} - System32\Tasks\HPCeeScheduleForPaddy => C:\Program Files (x86)\Hewlett-Packard\HP Ceement\HPCEE.exe [2015-06-16] (Hewlett-Packard)
Task: {B0783751-AFAE-4BFF-B02A-3C74BBADC98E} - System32\Tasks\Microsoft\Windows\Media Center\ConfigureInternetTimeService => C:\Windows\ehome\ehPrivJob.exe
Task: {B9B19DBD-DEB0-463E-B056-B24AF351100E} - \Microsoft\Windows\Setup\GWXTriggers\refreshgwxconfig-B -> No File <==== ATTENTION
Task: {BB891099-3F04-45DA-8DFA-066AB33B0F7D} - System32\Tasks\Microsoft\Windows\Media Center\UpdateRecordPath => C:\Windows\ehome\ehPrivJob.exe
Task: {BD615D59-154D-4007-B4A6-01251AA04433} - \Microsoft\Windows\Setup\GWXTriggers\ScheduleUpgradeTime -> No File <==== ATTENTION
Task: {C0F395F2-9715-4314-A840-2E6C417F6A32} - System32\Tasks\Microsoft\Windows\Media Center\DispatchRecoveryTasks => C:\Windows\ehome\ehPrivJob.exe
Task: {C6429797-F491-4F5C-BD36-6AC08CF60D18} - System32\Tasks\Microsoft\Windows\Media Center\PBDADiscoveryW2 => C:\Windows\ehome\ehPrivJob.exe
Task: {CBC948F4-094E-49B0-A43E-1A0A975816EA} - System32\Tasks\Apple\AppleSoftwareUpdate => C:\Program Files (x86)\Apple Software Update\SoftwareUpdate.exe [2011-06-01] (Apple Inc.)
Task: {CCF91531-C250-4DEE-B2A3-F8FA5E9761F5} - System32\Tasks\Hewlett-Packard\HP Active Health\HP Active Health Scan (HPSA) => C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPActiveHealth\ActiveHealth.exe [2016-08-18] (HP Inc.)
Task: {CE2BBC8A-6C4B-4CB9-AE83-72AFD4AF3BFA} - \Microsoft\Windows\Setup\gwx\refreshgwxcontent -> No File <==== ATTENTION
Task: {D588F24B-0CB5-48A9-8D4D-52E4F49E1456} - System32\Tasks\Hewlett-Packard\HP Support Assistant\HP Support Solutions Framework Report => C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\Modules\HPSFReport.exe [2016-05-09] (Hewlett-Packard)
Task: {D89EFC2B-6D28-469D-B9D4-75421845C936} - System32\Tasks\Adobe Flash Player Updater => C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerUpdateService.exe [2016-09-21] (Adobe Systems Incorporated)
Task: {DAAC26AC-48E4-44F6-9A40-111EA60CC416} - System32\Tasks\GoogleUpdateTaskMachineCore => C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [2015-09-07] (Google Inc.)
Task: {E1E9ACF7-7C92-4A6F-9CDB-969A6B91D997} - System32\Tasks\Hewlett-Packard\HP Support Assistant\HP Support Solutions Framework Updater => C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\Modules\HPSSFUpdater.exe [2016-08-03] (HP Inc.)
Task: {EB742961-64B3-4AB1-B927-56DC6435D158} - \Microsoft\Windows\Setup\GWXTriggers\MachineUnlock-5d -> No File <==== ATTENTION
Task: {EDFE8E53-52CB-4A29-9EEE-F4918D2920D1} - System32\Tasks\GoogleUpdateTaskMachineUA => C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [2015-09-07] (Google Inc.)
Task: {EE44F1BC-3A65-4249-BBAC-F4DEB17CDF61} - System32\Tasks\Microsoft\Windows\Media Center\SqlLiteRecoveryTask => C:\Windows\ehome\mcupdate.exe
Task: {F1C5FBDD-5DC6-4AFC-8653-F0D805F6DE51} - \Microsoft\Windows\Setup\GWXTriggers\OutOfIdle-5d -> No File <==== ATTENTION
Task: {F2511BEE-366D-49C8-BB06-D1D74AAAE162} - System32\Tasks\Microsoft\Windows\Media Center\ehDRMInit => C:\Windows\ehome\ehPrivJob.exe
 
(If an entry is included in the fixlist, the task (.job) file will be moved. The file which is running by the task will not be moved.)
 
Task: C:\WINDOWS\Tasks\Adobe Flash Player Updater.job => C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerUpdateService.exe
Task: C:\WINDOWS\Tasks\GoogleUpdateTaskMachineCore.job => C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
Task: C:\WINDOWS\Tasks\GoogleUpdateTaskMachineUA.job => C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
Task: C:\WINDOWS\Tasks\HPCeeScheduleForPaddy.job => C:\Program Files (x86)\Hewlett-Packard\HP Ceement\HPCEE.exe
 
==================== Shortcuts =============================
 
(The entries could be listed to be restored or removed.)
 
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\-10958392170.lnk -> hxxp://www.wunderground.com/radar/mixedcomposite.asp?region=b5&size;=2x&type;=loop
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\-16889357780.lnk -> hxxp://wtop.com/
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\-21249524730.lnk -> hxxp://www.wunderground.com/radar/radblast.asp?zoommode=out#=10&delay;=15&scale;=0.125&noclutter;=1&ID;=LWX&type;=N0R⪫=38.69638062&lon;=-77.85234070&label;=Warrenton, VA&showstorms;=0&map.x;=219&map.y;=426¢erx=400¢ery=288&lightning;=1&smooth;=1&showlabels;=1&rainsnow;=1
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\-2952022830.lnk -> hxxp://saacforum.com/index.php?board=12.0
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\1243244850.lnk -> hxxp://mail.mris.com/a/webmail.php?wsid=ebd093f2fb7d1c56f0f729509a4733950b0c0336
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\13796260060.lnk -> hxxp://www.nascar.com/en_us/sprint-cup-series/leaderboard/leaderboard-live.html
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\16263942420.lnk -> hxxp://www.cbssports.com/
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\17609734960.lnk -> hxxp://www.stltoday.com/sports/baseball/professional/
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\3144898580.lnk -> hxxp://www.intellicast.com/National/Radar/Current.aspx?animate=true
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\6739343990.lnk -> hxxp://www.nascar.com/en_us/sprint-cup-series.html
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\6964688600.lnk -> hxxp://espn.go.com/olympics/winter/2014/results
 
==================== Loaded Modules (Whitelisted) ==============
 
2015-10-30 03:17 - 2015-10-30 03:17 - 00028672 _____ () C:\WINDOWS\SYSTEM32\efsext.dll
2012-11-13 15:02 - 2012-10-18 15:53 - 00254552 ____N () C:\Program Files (x86)\Cyberlink\Shared files\RichVideo.exe
2012-11-21 19:45 - 2012-10-16 17:44 - 00390672 _____ () C:\Program Files\CyberLink\Shared files\RichVideo64.exe
2015-10-30 03:18 - 2015-10-30 03:18 - 00185856 _____ () C:\WINDOWS\SYSTEM32\ism32k.dll
2016-09-14 08:28 - 2016-09-07 01:39 - 02656952 _____ () C:\WINDOWS\System32\CoreUIComponents.dll
2016-09-14 08:24 - 2016-09-07 00:10 - 00591360 _____ () C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\Cortana.Core.dll
2016-09-14 08:24 - 2016-09-07 00:10 - 02483200 _____ () C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\Cortana.BackgroundTask.dll
2016-08-26 08:54 - 2016-08-26 08:54 - 01864384 _____ () C:\Users\Paddy\AppData\Local\Microsoft\OneDrive\17.3.6517.0809\amd64\ClientTelemetry.dll
2016-09-14 08:28 - 2016-09-07 01:39 - 02656952 _____ () C:\WINDOWS\system32\CoreUIComponents.dll
2015-12-22 18:18 - 2015-12-22 18:18 - 00093696 _____ () C:\Windows\SystemApps\ShellExperienceHost_cw5n1h2txyewy\Windows.UI.Shell.SharedUtilities.dll
2016-07-17 20:32 - 2016-06-30 23:48 - 00472064 _____ () C:\Windows\SystemApps\ShellExperienceHost_cw5n1h2txyewy\QuickActions.dll
2016-09-14 08:24 - 2016-09-07 00:15 - 07992832 _____ () C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\CortanaApi.dll
2016-09-14 08:24 - 2016-09-07 00:11 - 00936448 _____ () C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\Cortana.Actions.dll
2016-09-14 08:25 - 2016-09-07 00:13 - 04089856 _____ () C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\RemindersUI.dll
2016-04-19 14:32 - 2016-04-19 14:32 - 00144384 _____ () C:\Program Files\WindowsApps\Microsoft.Messaging_2.15.20002.0_x86__8wekyb3d8bbwe\SkypeHost.exe
2016-08-15 20:13 - 2016-08-15 20:13 - 00017408 _____ () C:\Program Files\WindowsApps\Microsoft.Windows.Photos_16.722.10060.0_x64__8wekyb3d8bbwe\Microsoft.Photos.exe
2016-08-15 20:13 - 2016-08-15 20:13 - 13475840 _____ () C:\Program Files\WindowsApps\Microsoft.Windows.Photos_16.722.10060.0_x64__8wekyb3d8bbwe\Microsoft.Photos.dll
2016-06-03 08:34 - 2016-06-03 08:34 - 00680448 _____ () C:\Program Files\WindowsApps\Microsoft.Windows.Photos_16.722.10060.0_x64__8wekyb3d8bbwe\Microsoft.DesignCore.dll
2016-03-04 09:16 - 2016-03-04 09:16 - 00291328 _____ () C:\Program Files\WindowsApps\Microsoft.Windows.Photos_16.722.10060.0_x64__8wekyb3d8bbwe\StoreRatingPromotion.dll
2016-08-26 08:52 - 2016-08-26 08:52 - 03763712 _____ () C:\Program Files\WindowsApps\Microsoft.WindowsCalculator_10.1608.2213.0_x64__8wekyb3d8bbwe\Calculator.exe
2016-09-19 19:06 - 2016-09-19 19:12 - 00176640 _____ () C:\Program Files\WindowsApps\Microsoft.MicrosoftSolitaireCollection_3.12.8312.0_x64__8wekyb3d8bbwe\CellNativeClientUniversal.dll
2014-04-23 16:05 - 2014-04-23 16:05 - 00073544 _____ () C:\Program Files (x86)\Common Files\Apple\Apple Application Support\zlib1.dll
2014-04-23 16:04 - 2014-04-23 16:04 - 01044808 _____ () C:\Program Files (x86)\Common Files\Apple\Apple Application Support\libxml2.dll
2016-08-26 08:54 - 2016-08-26 08:54 - 01383616 _____ () C:\Users\Paddy\AppData\Local\Microsoft\OneDrive\17.3.6517.0809\ClientTelemetry.dll
2016-09-16 19:55 - 2016-09-13 20:38 - 01806152 _____ () C:\Program Files (x86)\Google\Chrome\Application\53.0.2785.116\libglesv2.dll
2016-09-16 19:54 - 2016-09-13 20:38 - 00094024 _____ () C:\Program Files (x86)\Google\Chrome\Application\53.0.2785.116\libegl.dll
2016-09-16 19:53 - 2016-09-13 20:25 - 17754304 _____ () C:\Program Files (x86)\Google\Chrome\Application\53.0.2785.116\PepperFlash\pepflashplayer.dll
2016-04-19 14:32 - 2016-04-19 14:32 - 00141312 _____ () C:\Program Files\WindowsApps\Microsoft.Messaging_2.15.20002.0_x86__8wekyb3d8bbwe\SkypeBackgroundTasks.dll
2016-04-19 14:32 - 2016-04-19 14:32 - 22284800 _____ () C:\Program Files\WindowsApps\Microsoft.Messaging_2.15.20002.0_x86__8wekyb3d8bbwe\SkyWrap.dll
2016-09-19 08:18 - 2016-09-12 17:48 - 17754304 _____ () C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\PepperFlash\23.0.0.166\pepflashplayer.dll
2015-10-21 15:50 - 2015-10-21 15:50 - 00988160 _____ () C:\Program Files (x86)\OpenOffice 4\program\libxml2.dll
2015-10-21 15:49 - 2015-10-21 15:49 - 00170496 _____ () C:\Program Files (x86)\OpenOffice 4\program\libxslt.dll
2016-08-26 08:54 - 2016-08-26 08:54 - 00118976 _____ () C:\Users\Paddy\AppData\Local\Microsoft\OneDrive\17.3.6517.0809\FileSyncViews.dll
 
==================== Alternate Data Streams (Whitelisted) =========
 
(If an entry is included in the fixlist, only the ADS will be removed.)
 
 
==================== Safe Mode (Whitelisted) ===================
 
(If an entry is included in the fixlist, it will be removed from the registry. The "AlternateShell" will be restored.)
 
HKLM\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\mcpltsvc => ""=""
HKLM\SYSTEM\CurrentControlSet\Control\SafeBoot\Network\mcpltsvc => ""=""
 
==================== Association (Whitelisted) ===============
 
(If an entry is included in the fixlist, the registry item will be restored to default or removed.)
 
 
==================== Internet Explorer trusted/restricted ===============
 
(If an entry is included in the fixlist, it will be removed from the registry.)
 
IE trusted site: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\sentrilock.com -> hxxp://alt.sentrilock.com
 
==================== Hosts content: ===============================
 
(If needed Hosts: directive could be included in the fixlist to reset Hosts.)
 
2009-07-13 22:34 - 2012-12-04 12:19 - 00000027 ____A C:\WINDOWS\system32\Drivers\etc\hosts
 
127.0.0.1       localhost
 
==================== Other Areas ============================
 
(Currently there is no automatic fix for this section.)
 
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Control Panel\Desktop\\Wallpaper -> C:\Users\Paddy\AppData\Local\Microsoft\Windows\Themes\RoamedThemeFiles\DesktopBackground\sept06passlg.jpg
DNS Servers: 10.1.10.1
HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System => (ConsentPromptBehaviorAdmin: 5) (ConsentPromptBehaviorUser: 3) (EnableLUA: 1)
Windows Firewall is enabled.
 
==================== MSCONFIG/TASK MANAGER disabled items ==
 
MSCONFIG\Services: RoxioNow Service => 2
MSCONFIG\Services: YahooAUService => 2
MSCONFIG\startupfolder: C:^ProgramData^Microsoft^Windows^Start Menu^Programs^Startup^Adobe Gamma Loader.lnk => C:\Windows\pss\Adobe Gamma Loader.lnk.CommonStartup
MSCONFIG\startupfolder: C:^ProgramData^Microsoft^Windows^Start Menu^Programs^Startup^ArtecMedia Remote Control.lnk => C:\Windows\pss\ArtecMedia Remote Control.lnk.CommonStartup
MSCONFIG\startupfolder: C:^ProgramData^Microsoft^Windows^Start Menu^Programs^Startup^ArtecMedia Schedule Recording.lnk => C:\Windows\pss\ArtecMedia Schedule Recording.lnk.CommonStartup
MSCONFIG\startupreg: APSDaemon => "C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe"
MSCONFIG\startupreg: BDRegion => C:\Program Files (x86)\Cyberlink\Shared Files\brs.exe
MSCONFIG\startupreg: BeatsOSDApp => C:\Program Files\IDT\WDM\beats64.exe
MSCONFIG\startupreg: CLMLServer => "C:\Program Files (x86)\Cyberlink\Power2Go\CLMLSvc.exe"
MSCONFIG\startupreg: PDF Complete => C:\Program Files (x86)\PDF Complete\pdfsty.exe
MSCONFIG\startupreg: PDVD9LanguageShortcut => "C:\Program Files (x86)\CyberLink\PowerDVD9\Language\Language.exe"
MSCONFIG\startupreg: QuickTime Task => "C:\Program Files (x86)\QuickTime\QTTask.exe" -atboottime
MSCONFIG\startupreg: RemoteControl9 => "C:\Program Files (x86)\CyberLink\PowerDVD9\PDVD9Serv.exe"
MSCONFIG\startupreg: UpdateP2GoShortCut => "C:\Program Files (x86)\CyberLink\Power2Go\MUITransfer\MUIStartMenu.exe" "C:\Program Files (x86)\CyberLink\Power2Go" UpdateWithCreateOnce "SOFTWARE\CyberLink\Power2Go\6.0"
MSCONFIG\startupreg: UpdatePDRShortCut => "C:\Program Files (x86)\CyberLink\PowerDirector\MUITransfer\MUIStartMenu.exe" "C:\Program Files (x86)\CyberLink\PowerDirector" UpdateWithCreateOnce "Software\CyberLink\PowerDirector\7.0"
MSCONFIG\startupreg: UpdatePSTShortCut => "C:\Program Files (x86)\CyberLink\Blu-ray Disc Suite\MUITransfer\MUIStartMenu.exe" "C:\Program Files (x86)\CyberLink\Blu-ray Disc Suite" UpdateWithCreateOnce "Software\CyberLink\PowerStarter"
HKLM\…\StartupApproved\Run: => "Logitech Download Assistant"
HKLM\…\StartupApproved\Run32: => "APSDaemon"
HKLM\…\StartupApproved\Run32: => "iTunesHelper"
HKLM\…\StartupApproved\Run32: => "SunJavaUpdateSched"
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\StartupApproved\Run: => "OneDrive"
 
==================== FirewallRules (Whitelisted) ===============
 
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
 
FirewallRules: [vm-monitoring-nb-session] => (Allow) LPort=139
FirewallRules: [MSMQ-In-TCP] => (Allow) %systemroot%\system32\mqsvc.exe
FirewallRules: [MSMQ-Out-TCP] => (Allow) %systemroot%\system32\mqsvc.exe
FirewallRules: [MSMQ-In-UDP] => (Allow) %systemroot%\system32\mqsvc.exe
FirewallRules: [MSMQ-Out-UDP] => (Allow) %systemroot%\system32\mqsvc.exe
FirewallRules: [WCF-NetTcpActivator-In-TCP-64bit] => (Allow) LPort=808
FirewallRules: [{DEABC349-19EB-4369-B572-3C279236C045}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPWarrantyCheck\HPDeviceDetection3.exe
FirewallRules: [{DB444F26-0E1B-4A32-87A0-01F64E405CC5}] => (Allow) C:\Program Files (x86)\iTunes\iTunes.exe
FirewallRules: [{26CFCF99-B53F-4CEA-876C-EDE9669B0813}] => (Allow) C:\Program Files (x86)\Bonjour\mDNSResponder.exe
FirewallRules: [{83251747-F430-4973-8017-E7DD953AEEEB}] => (Allow) C:\Program Files (x86)\Bonjour\mDNSResponder.exe
FirewallRules: [{E8C4F0AA-9C29-45C3-9B88-6B93E44A7C28}] => (Allow) C:\Program Files\Bonjour\mDNSResponder.exe
FirewallRules: [{4F61D85B-71AA-494C-AADF-DCF60AA4262A}] => (Allow) C:\Program Files\Bonjour\mDNSResponder.exe
FirewallRules: [{69BAEFC9-DB18-4E80-8861-4F0C45280296}] => (Allow) C:\Program Files\Common Files\McAfee\Platform\McSvcHost\McSvHost.exe
FirewallRules: [{B55735F8-54C1-4C9E-95D0-D9FE81A1A972}] => (Allow) C:\Program Files\Common Files\McAfee\Platform\McSvcHost\McSvHost.exe
FirewallRules: [{5EA62BE4-492D-43E6-96E1-CA5B927DE56E}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPWarrantyCheck\HPWarrantyChecker.exe
FirewallRules: [{04FF7D16-EAA8-4C59-89F4-E2E24157BE24}] => (Allow) C:\Program Files\CyberLink\PowerDirector11\PDR10.EXE
FirewallRules: [{EB24B7D9-7B73-45C3-8781-170972332BDA}] => (Allow) C:\Program Files (x86)\CyberLink\PowerDVD9\PowerDVD9.EXE
FirewallRules: [{16ABADF5-B2D4-458C-9C1C-38BFE261868A}] => (Allow) C:\Program Files (x86)\CyberLink\PowerDVD9\PowerDVD Cinema\PowerDVDCinema.exe
FirewallRules: [{6FDDB205-C907-493A-95A9-7DD83088FA49}] => (Allow) C:\Program Files (x86)\CyberLink\PowerDirector\PDR.EXE
FirewallRules: [{AAD33E6F-AD94-43D5-83CE-EFE2879FC720}] => (Allow) C:\Program Files\Common Files\McAfee\McSvcHost\McSvHost.exe
FirewallRules: [{4F72BB7E-3F36-433F-A5A8-4BC31BFBCDCD}] => (Allow) c:\Program Files (x86)\CyberLink\PowerDVD10\PowerDVD10.EXE
FirewallRules: [{6ADE23A3-B480-469A-AC0B-936F52CA998D}] => (Allow) c:\Program Files (x86)\CyberLink\PowerDVD10\PowerDVD Cinema\PowerDVDCinema10.exe
FirewallRules: [{BC51E63F-AB23-485F-ABD1-CE519591ABB0}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\HP LinkUp\HP LinkUp Viewer.exe
FirewallRules: [{1B073C0A-FFFF-4A00-BC40-663D4FAAD941}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\HP LinkUp\HP LinkUp Viewer.exe
FirewallRules: [{8AF4995C-056B-4C9B-8A50-0C0C6B012D62}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\Remote Graphics Receiver\rgreceiver.exe
FirewallRules: [{697D68E3-44D6-4E44-A175-92C8FA4A871D}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\Remote Graphics Receiver\rgreceiver.exe
FirewallRules: [{34C0235A-132B-46C7-A9F3-C4B87383F530}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\MediaSmart\RoxioNow\RNow.exe
FirewallRules: [{9ACFF156-5CD5-4E95-BB1A-0D8D489C25C1}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\MediaSmart\RoxioNow\RNow.exe
FirewallRules: [{1EDFA286-AFBC-4BD1-B3B9-92DBE348E59A}] => (Allow) C:\Program Files (x86)\Roxio\RoxioNow Player\RNowShell.exe
FirewallRules: [{F7DF14D0-003A-4DD1-ABEC-359237F69087}] => (Allow) C:\Program Files (x86)\Roxio\RoxioNow Player\RNowShell.exe
FirewallRules: [{C3850B55-3143-456A-8C28-1640BB664605}] => (Allow) C:\Program Files\VueScan\vuescan.exe
FirewallRules: [{1B5B1700-2798-4AD9-A4A2-A4EBFFD6CE0A}] => (Allow) C:\Program Files\VueScan\vuescan.exe
FirewallRules: [{E4B2786A-C4F8-4D82-B600-004EF2A3E114}] => (Allow) C:\Program Files (x86)\Windows Live\Contacts\wlcomm.exe
FirewallRules: [{16F090B0-5A0E-4115-AC4C-EF28DDC47EF8}] => (Allow) LPort=2869
FirewallRules: [{33BAF1D9-78B1-415C-A2B7-F20BF1468EBE}] => (Allow) LPort=1900
FirewallRules: [{64F6EAA3-62DC-4891-8260-7AA040AA0979}] => (Allow) C:\Program Files (x86)\Windows Live\Messenger\msnmsgr.exe
FirewallRules: [{9B5A3CDC-A091-4C33-B9F5-24AB04908E31}] => (Allow) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
 
==================== Restore Points =========================
 
01-09-2016 10:05:52 Windows Update
11-09-2016 21:26:51 Scheduled Checkpoint
19-09-2016 17:56:47 Scheduled Checkpoint
 
==================== Faulty Device Manager Devices =============
 
Name: 
Description: 
Class Guid: 
Manufacturer: 
Service: 
Problem: : The drivers for this device are not installed. (Code 28)
Resolution: To install the drivers for this device, click "Update Driver", which starts the Hardware Update wizard.
 
 
==================== Event log errors: =========================
 
Application errors:
==================
Error: (09/21/2016 12:23:39 AM) (Source: CVHSVC) (EventID: 100) (User: )
Description: Information only.
(Patch task for {90140011-0066-0409-0000-0000000FF1CE}): DownloadLatest Failed: HTTP status 403: The client does not have sufficient access rights to the requested server object.
 
Error: (09/19/2016 05:57:00 PM) (Source: Microsoft-Windows-CAPI2) (EventID: 513) (User: )
Description: Cryptographic Services failed while processing the OnIdentity() call in the System Writer Object.
 
Details:
AddLegacyDriverFiles: Unable to back up image of binary Microsoft Link-Layer Discovery Protocol.
 
System Error:
Access is denied.
.
 
Error: (09/18/2016 08:56:02 PM) (Source: Windows Backup) (EventID: 4103) (User: )
Description: The backup did not complete because of an error writing to the backup location J:\. The error is: The backup location cannot be found or is not valid. Review your backup settings and check the backup location. (0x81000006).
 
Error: (09/18/2016 08:52:49 PM) (Source: Bonjour Service) (EventID: 100) (User: )
Description: Local Hostname Paddy1.local already in use; will try Paddy1-2.local instead
 
Error: (09/18/2016 08:52:49 PM) (Source: Bonjour Service) (EventID: 100) (User: )
Description: mDNSCoreReceiveResponse: ProbeCount 2; will deregister    4 Paddy1.local. Addr 10.1.10.11
 
Error: (09/18/2016 08:52:49 PM) (Source: Bonjour Service) (EventID: 100) (User: )
Description: mDNSCoreReceiveResponse: Received from 10.1.10.11:5353   16 Paddy1.local. AAAA 2601:05CD:C001:0D00:EC1A:E505:401B:9EC4
 
Error: (09/16/2016 06:56:08 PM) (Source: CVHSVC) (EventID: 100) (User: )
Description: Information only.
(Patch task for {90140011-0066-0409-0000-0000000FF1CE}): DownloadLatest Failed: HTTP status 403: The client does not have sufficient access rights to the requested server object.
 
Error: (09/14/2016 07:05:44 PM) (Source: CVHSVC) (EventID: 100) (User: )
Description: Information only.
(Patch task for {90140011-0066-0409-0000-0000000FF1CE}): DownloadLatest Failed: HTTP status 403: The client does not have sufficient access rights to the requested server object.
 
Error: (09/14/2016 04:50:11 PM) (Source: SideBySide) (EventID: 63) (User: )
Description: Activation context generation failed for "c:\program files (x86)\common files\adobe air\versions\1.0\Adobe AIR.dll".Error in manifest or policy file "c:\program files (x86)\common files\adobe air\versions\1.0\Adobe AIR.dll" on line 3.
The value "MAJOR_VERSION.MINOR_VERSION.BUILD_NUMBER_MAJOR.BUILD_NUMBER_MINOR" of attribute "version" in element "assemblyIdentity" is invalid.
 
Error: (09/14/2016 04:49:30 PM) (Source: SideBySide) (EventID: 78) (User: )
Description: Activation context generation failed for "c:\program files (x86)\eset\eset online scanner\ESETSmartInstaller.exe".Error in manifest or policy file "" on line .
A component version required by the application conflicts with another component version already active.
Conflicting components are:.
Component 1: C:\WINDOWS\WinSxS\manifests\x86_microsoft.windows.common-controls_6595b64144ccf1df_6.0.10586.494_none_ea85e725b9ba5a4b.manifest.
Component 2: C:\WINDOWS\WinSxS\manifests\amd64_microsoft.windows.common-controls_6595b64144ccf1df_6.0.10586.494_none_a2d8b04ea53e3145.manifest.
 
 
System errors:
=============
Error: (09/20/2016 10:39:32 PM) (Source: Microsoft-Windows-WindowsUpdateClient) (EventID: 20) (User: NT AUTHORITY)
Description: Installation Failure: Windows failed to install the following update with error 0x8024200d: Feature update to Windows 10, version 1607.
 
Error: (09/18/2016 09:12:56 PM) (Source: Service Control Manager) (EventID: 7031) (User: )
Description: The User Data Access_221a624 service terminated unexpectedly.  It has done this 1 time(s).  The following corrective action will be taken in 10000 milliseconds: Restart the service.
 
Error: (09/18/2016 09:12:56 PM) (Source: Service Control Manager) (EventID: 7031) (User: )
Description: The User Data Storage_221a624 service terminated unexpectedly.  It has done this 1 time(s).  The following corrective action will be taken in 10000 milliseconds: Restart the service.
 
Error: (09/18/2016 09:12:56 PM) (Source: Service Control Manager) (EventID: 7031) (User: )
Description: The Contact Data_221a624 service terminated unexpectedly.  It has done this 1 time(s).  The following corrective action will be taken in 10000 milliseconds: Restart the service.
 
Error: (09/18/2016 09:12:56 PM) (Source: Service Control Manager) (EventID: 7031) (User: )
Description: The Sync Host_221a624 service terminated unexpectedly.  It has done this 1 time(s).  The following corrective action will be taken in 10000 milliseconds: Restart the service.
 
Error: (09/16/2016 10:01:40 PM) (Source: Service Control Manager) (EventID: 7031) (User: )
Description: The User Data Access_33c65d service terminated unexpectedly.  It has done this 1 time(s).  The following corrective action will be taken in 10000 milliseconds: Restart the service.
 
Error: (09/16/2016 10:01:40 PM) (Source: Service Control Manager) (EventID: 7031) (User: )
Description: The User Data Storage_33c65d service terminated unexpectedly.  It has done this 1 time(s).  The following corrective action will be taken in 10000 milliseconds: Restart the service.
 
Error: (09/16/2016 10:01:40 PM) (Source: Service Control Manager) (EventID: 7031) (User: )
Description: The Contact Data_33c65d service terminated unexpectedly.  It has done this 1 time(s).  The following corrective action will be taken in 10000 milliseconds: Restart the service.
 
Error: (09/16/2016 10:01:40 PM) (Source: Service Control Manager) (EventID: 7031) (User: )
Description: The Sync Host_33c65d service terminated unexpectedly.  It has done this 1 time(s).  The following corrective action will be taken in 10000 milliseconds: Restart the service.
 
Error: (09/16/2016 06:52:34 PM) (Source: DCOM) (EventID: 10016) (User: PADDY1)
Description: The machine-default permission settings do not grant Local Activation permission for the COM Server application with CLSID 
{C2F03A33-21F5-47FA-B4BB-156362A2F239}
 and APPID 
{316CDED5-E4AE-4B15-9113-7055D84DCC97}
 to the user Paddy1\Paddy SID (S-1-5-21-648858125-4165233436-1298442668-1001) from address LocalHost (Using LRPC) running in the application container Microsoft.Windows.Cortana_1.6.1.52_neutral_neutral_cw5n1h2txyewy SID (S-1-15-2-1861897761-1695161497-2927542615-642690995-327840285-2659745135-2630312742). This security permission can be modified using the Component Services administrative tool.
 
 
CodeIntegrity:
===================================
  Date: 2016-09-21 12:51:22.320
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Bonjour\mdnsNSP.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 12:51:22.307
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Bonjour\mdnsNSP.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 12:51:19.885
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Microsoft Silverlight\xapauthenticodesip.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 12:51:19.839
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Microsoft Silverlight\xapauthenticodesip.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 12:51:19.776
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Microsoft Silverlight\xapauthenticodesip.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 12:26:24.937
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Bonjour\mdnsNSP.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 12:26:24.911
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Bonjour\mdnsNSP.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 12:26:24.023
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Microsoft Silverlight\xapauthenticodesip.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 12:26:23.992
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Microsoft Silverlight\xapauthenticodesip.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 12:26:23.974
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Microsoft Silverlight\xapauthenticodesip.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
 
==================== Memory info =========================== 
 
Processor: Intel(R) Core(TM) i7-2600 CPU @ 3.40GHz
Percentage of memory in use: 76%
Total physical RAM: 8172.31 MB
Available physical RAM: 1939.54 MB
Total Virtual: 12780.31 MB
Available Virtual: 3058.3 MB
 
==================== Drives ================================
 
Drive c: (Paddy) (Fixed) (Total:975.57 GB) (Free:521.87 GB) NTFS
Drive d: (HP_RECOVERY) (Fixed) (Total:11.44 GB) (Free:1.39 GB) NTFS ==>[system with boot components (obtained from drive)]
Drive x: (Scratch Disk) (Fixed) (Total:410.16 GB) (Free:410.01 GB) NTFS
 
==================== MBR & Partition Table ==================
 
========================================================
Disk: 0 (Size: 1397.3 GB) (Disk ID: FBDF8A01)
Partition 1: (Active) - (Size=100 MB) - (Type=07 NTFS)
Partition 2: (Not Active) - (Size=975.6 GB) - (Type=07 NTFS)
Partition 3: (Not Active) - (Size=410.2 GB) - (Type=OF Extended)
Partition 4: (Not Active) - (Size=11.4 GB) - (Type=07 NTFS)
 
==================== End of Addition.txt ============================📎PopupBadstuff.jpg


:welcome:


Yep, thats a scam alright. Had a friend a few months back actually called them and they wanted remote access to her computer and a fee of around $400.


I see Whitesmoke installed , its malware . You have Malwarebytes installed but its an older version so go to Programs and Features in the Control Panel and uninstall it , if its the Premium version which it is not showing make sure you have your ID and Key handy for when we reinstall it. The instructions to download and install the latest version is in my post


All our tools and scanners work more efficiently when run from the DESKTOP in lieu of being buried in some folder, so download and run these tools right from the DESKTOP
 
 
-AdwCleaner-by Xplode
 
Click on this link to download : ADWCleaner TO YOUR DESKTOP
 
Use my link only, do not do a search for AdwCleaner as there is a bogus copy going around by scammers
 
[external image: AdwCleaner4.201_zpsxrbk2llq.jpg]
 
 
  •  
  • Close all open programs and internet browsers.
  • Double click on AdwCleaner.exe to run the tool.
  • Click on Scan.
  • After the scan is complete click on "Clean"
  • Confirm each time with Ok.
  • Your computer will be rebooted automatically. A text file will open after the restart.
  • Please post the content of that logfile with your next reply.
  • You can find the logfile at C:\AdwCleaner[S1].txt as well.


===============================================================================


[external image: Capture_zpsge1t2tk9.jpg] Please download Junkware Removal Tool TO YOUR DESKTOP
  •  
  • Download the one from Bleeping Computer
  • Shut down your protection software now to avoid potential conflicts.
  • Run the tool by double-clicking it. If you are using Windows Vista, 7, or 8; instead of double-clicking, right-mouse click JRT.exe and select "Run as Administrator".
  • The tool will open and start scanning your system.
  • Please be patient as this can take a while to complete depending on your system's specifications.
  • On completion, a log (JRT.txt) is saved to your desktop and will automatically open.
  • Post the contents of JRT.txt into your next message.


===============================================================================
 
Download Malwarebytes' Anti-Malware  TO YOUR DESKTOP
 
  •  
  • Windows XP : Double click on the icon to run it.
  • Windows Vista, Windows 7 , 8, 8.1 and 10 : Right click and select "Run as Administrator"
 
 
[external image: MBAM221%201043_zpsdtasp5xe.jpg]
 
  •  
  • On the Dashboard click on Update Now
  • Go to the Setting Tab
  • Under Setting go to Detection and Protection
  • Under PUP and PUM make sure both are set to show Treat Detections as Malware
  • Go to Advanced setting and make sure Automatically Quarantine Detected Items is checked
  • Then on the Dashboard click on Scan
  • Make sure to select THREAT SCAN
  • Then click on Scan
  • When the scan is finished on the bottom right click on SAVE RESULTS then select Copy to Clipboard
  • Please paste the log back into this thread for review
  • Exit Malwarebytes


Ken,  Can't thank you enough for the assistance.  Accomplished everything, log files pasted below….  Let me know your thoughts.


Regards, Bob


# AdwCleaner v6.020 - Logfile created 21/09/2016 at 15:51:57
# Updated on 14/09/2016 by ToolsLib
# Database : 2016-09-21.1 [Server]
# Operating System : Windows 10 Home  (X64)
# Username : Paddy - PADDY1
# Running from : C:\Users\Paddy\Desktop\AdwCleaner.exe
# Mode: Clean
# Support : https://toolslib.net/forum


***** [ Services ] *****
 
[-] Service deleted: YahooAUService
 
 
***** [ Folders ] *****
 
[-] Folder deleted: C:\Users\Paddy\AppData\Local\Conduit
[-] Folder deleted: C:\Users\Paddy\AppData\Local\SwvUpdater
[-] Folder deleted: C:\Users\Paddy\AppData\LocalLow\Conduit
[-] Folder deleted: C:\Users\Paddy\AppData\LocalLow\PriceGong
[-] Folder deleted: C:\Users\Paddy\AppData\LocalLow\Yahoo! Companion
[-] Folder deleted: C:\Users\Paddy\AppData\LocalLow\Yahoo!\Companion
[-] Folder deleted: C:\Users\Paddy\AppData\Roaming\Yahoo!\Companion
[-] Folder deleted: C:\ProgramData\apn
[-] Folder deleted: C:\ProgramData\Uniblue
[-] Folder deleted: C:\ProgramData\Yahoo! Companion
[#] Folder deleted on reboot: C:\ProgramData\Application Data\apn
[#] Folder deleted on reboot: C:\ProgramData\Application Data\Uniblue
[#] Folder deleted on reboot: C:\ProgramData\Application Data\Yahoo! Companion
[-] Folder deleted: C:\ProgramData\Microsoft\Windows\Start Menu\Programs\VAFPlayer
[-] Folder deleted: C:\Program Files (x86)\Conduit
[-] Folder deleted: C:\Program Files (x86)\tuguu sl
[-] Folder deleted: C:\Program Files (x86)\Yahoo!\Companion
 
 
***** [ Files ] *****
 
[-] File deleted: C:\END
[-] File deleted: C:\Program Files (x86)\Yahoo!\Common\unyt.exe
 
 
***** [ DLL ] *****


***** [ WMI ] *****


***** [ Shortcuts ] *****


***** [ Scheduled Tasks ] *****


***** [ Registry ] *****
 
[-] Key deleted: HKLM\SOFTWARE\Classes\Toolbar.CT3289847
[-] Key deleted: [x64] HKLM\SOFTWARE\Microsoft\Shared Tools\MSConfig\services\YahooAUService
[-] Key deleted: HKLM\SOFTWARE\Classes\driverscanner
[-] Key deleted: HKLM\SOFTWARE\Classes\protector_dll.Protector
[-] Key deleted: HKLM\SOFTWARE\Classes\protector_dll.Protector.1
[-] Key deleted: HKLM\SOFTWARE\Classes\protector_dll.ProtectorBho
[-] Key deleted: HKLM\SOFTWARE\Classes\protector_dll.ProtectorBho.1
[-] Key deleted: HKLM\SOFTWARE\Classes\protector_dll.ProtectorLib
[-] Key deleted: HKLM\SOFTWARE\Classes\protector_dll.ProtectorLib.1
[-] Key deleted: HKLM\SOFTWARE\Classes\Sample.BrowserHandler
[-] Key deleted: HKLM\SOFTWARE\Classes\Sample.BrowserHandler.1
[-] Key deleted: HKLM\SOFTWARE\Classes\Sample.YTBPartnerSample
[-] Key deleted: HKLM\SOFTWARE\Classes\Sample.YTBPartnerSample.1
[-] Key deleted: HKLM\SOFTWARE\Classes\YBrowserToolbar.YBrowserToolbar
[-] Key deleted: HKLM\SOFTWARE\Classes\YBrowserToolbar.YBrowserToolbar.1
[-] Key deleted: HKLM\SOFTWARE\Classes\yt.CacheLoader
[-] Key deleted: HKLM\SOFTWARE\Classes\yt.CacheLoader.1
[-] Key deleted: HKLM\SOFTWARE\Classes\yt.Clickstream
[-] Key deleted: HKLM\SOFTWARE\Classes\yt.Clickstream.1
[-] Key deleted: HKLM\SOFTWARE\Classes\yt.YTHelper
[-] Key deleted: HKLM\SOFTWARE\Classes\yt.YTHelper.2
[-] Key deleted: HKLM\SOFTWARE\Classes\yt.YTNavAssistPlugin
[-] Key deleted: HKLM\SOFTWARE\Classes\yt.YTNavAssistPlugin.1
[-] Key deleted: HKLM\SOFTWARE\Classes\yt.YToolbarBand
[-] Key deleted: HKLM\SOFTWARE\Classes\yt.YToolbarBand.1
[-] Key deleted: HKLM\SOFTWARE\Classes\ytbbroker.YTBAutoSearchAssistant
[-] Key deleted: HKLM\SOFTWARE\Classes\ytbbroker.YTBAutoSearchAssistant.1
[-] Key deleted: HKLM\SOFTWARE\Classes\ytbbroker.YTBAutoUpdaterAssistant
[-] Key deleted: HKLM\SOFTWARE\Classes\ytbbroker.YTBAutoUpdaterAssistant.1
[-] Key deleted: HKLM\SOFTWARE\Classes\ytbbroker.YTBCustomizerAssistant
[-] Key deleted: HKLM\SOFTWARE\Classes\ytbbroker.YTBCustomizerAssistant.1
[-] Key deleted: HKLM\SOFTWARE\Classes\ytbbroker.YTBGeneralAssistant
[-] Key deleted: HKLM\SOFTWARE\Classes\ytbbroker.YTBGeneralAssistant.1
[-] Key deleted: HKLM\SOFTWARE\Classes\ytbbroker.YTBMessengerAssistant
[-] Key deleted: HKLM\SOFTWARE\Classes\ytbbroker.YTBMessengerAssistant.1
[-] Key deleted: HKLM\SOFTWARE\Classes\ytbbroker.YTBSingleInstanceAssistant
[-] Key deleted: HKLM\SOFTWARE\Classes\ytbbroker.YTBSingleInstanceAssistant.1
[-] Key deleted: HKLM\SOFTWARE\Classes\YTNavAssist.NameSpaceCF
[-] Key deleted: HKLM\SOFTWARE\Classes\YTNavAssist.NameSpaceCF.1
[-] Key deleted: HKLM\SOFTWARE\Classes\YTNavAssist.NameSpacePP
[-] Key deleted: HKLM\SOFTWARE\Classes\YTNavAssist.NameSpacePP.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\driverscanner
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\protector_dll.Protector
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\protector_dll.Protector.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\protector_dll.ProtectorBho
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\protector_dll.ProtectorBho.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\protector_dll.ProtectorLib
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\protector_dll.ProtectorLib.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\Sample.BrowserHandler
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\Sample.BrowserHandler.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\Sample.YTBPartnerSample
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\Sample.YTBPartnerSample.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\YBrowserToolbar.YBrowserToolbar
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\YBrowserToolbar.YBrowserToolbar.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\yt.CacheLoader
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\yt.CacheLoader.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\yt.Clickstream
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\yt.Clickstream.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\yt.YTHelper
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\yt.YTHelper.2
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\yt.YTNavAssistPlugin
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\yt.YTNavAssistPlugin.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\yt.YToolbarBand
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\yt.YToolbarBand.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\ytbbroker.YTBAutoSearchAssistant
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\ytbbroker.YTBAutoSearchAssistant.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\ytbbroker.YTBAutoUpdaterAssistant
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\ytbbroker.YTBAutoUpdaterAssistant.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\ytbbroker.YTBCustomizerAssistant
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\ytbbroker.YTBCustomizerAssistant.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\ytbbroker.YTBGeneralAssistant
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\ytbbroker.YTBGeneralAssistant.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\ytbbroker.YTBMessengerAssistant
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\ytbbroker.YTBMessengerAssistant.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\ytbbroker.YTBSingleInstanceAssistant
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\ytbbroker.YTBSingleInstanceAssistant.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\YTNavAssist.NameSpaceCF
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\YTNavAssist.NameSpaceCF.1
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\YTNavAssist.NameSpacePP
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\YTNavAssist.NameSpacePP.1
[-] Key deleted: HKLM\SOFTWARE\Classes\AppID\{1CAE874F-F5C7-4BCC-BA46-9AD26DF35B93}
[-] Key deleted: HKLM\SOFTWARE\Classes\AppID\{EFC0651C-B6D7-49CD-A6E0-B1CE9AB5FE46}
[-] Key deleted: HKLM\SOFTWARE\Classes\AppID\{7375D127-3955-4654-8E7D-1949A7A9C902}
[-] Key deleted: HKCU\Software\Classes\CLSID\{66E8DCC7-97D2-4A89-8E08-D0610FF0878C}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{02478D38-C3F9-4EFB-9B51-7695ECA05670}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{058F0E48-61CA-4964-9FBA-1978A1BB060D}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{18F33C35-8EF2-40D7-8BA4-932B0121B472}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{3C471948-F874-49F5-B338-4F214A2EE0B1}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{6E993643-8FBC-44FE-BC85-D318495C4D96}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{EF99BD32-C1FB-11D2-892F-0090271D4F88}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{81017EA9-9AA8-4A6A-9734-7AF40E7D593F}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{1E57256D-9F39-4267-AB39-D7813D644C5A}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{31371420-098D-4C0E-A11E-EBEC2305DD01}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{3A06AA27-D94B-48C2-BB55-9FD0FF2120E3}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{46140CE4-76FE-440E-AE88-4C2272BC05C7}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{9F9C4C5C-2BA8-4E00-A697-9F710BB1026B}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{C60CCE95-6AF9-4E74-B66B-3212D19F1D2F}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{FBE30D66-39A2-4b72-8B43-6D4C335A6F34}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{3C16E079-E4C7-493C-BE9F-E0F2BB0B7430}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{6EB4349D-4333-442F-ACA4-4C72AF28B6ED}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{7DB8B625-DBF0-4491-B544-5A06F7B17BB4}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{8E74A0AE-F0ED-47ED-A940-A8E99687646B}
[-] Key deleted: HKLM\SOFTWARE\Classes\CLSID\{9DE77B51-89F6-468E-9402-16050382E950}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{F56ACA29-1C99-40F1-AC64-2E44C4F6BC71}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{12D3E096-0FDF-42CC-8F44-04944F9C1648}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{22389F39-2CF4-47C4-B8B2-273BB16BF70C}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{23E3CEB3-D63A-433E-A5D0-4DB1C501B915}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{26A3152F-CF87-4C5B-8093-4D4B9EC084EB}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{29E3319C-4B3C-479F-8692-BDD2CA30BEDD}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{367BD1CD-74A3-451F-B1A4-6A2DE4129A2D}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{49F018EE-F362-4B5B-8EC8-BCF9246ABF21}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{63B73044-FC1A-4FE1-991B-FDBD4CDAA868}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{7207E52B-821E-4C05-A8D6-2965B2BE77CF}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{863FCF5D-DC39-4DA9-AF32-CB0025990EEE}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{B09E015A-4D4E-4F8D-A436-95E19140947D}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{B1E712C4-03AA-495F-B0F5-0F057E126E2A}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{D13DC65C-C77B-4986-9078-DEA3D34C71BB}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{371AD4A5-1520-4AA2-A8A4-F9AD3BAC6957}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{7F124846-5453-4BB8-A41D-E11481FFC9DF}
[-] Key deleted: HKLM\SOFTWARE\Classes\Interface\{8FD65019-BF09-45DA-AD81-E95AE911F1FD}
[-] Key deleted: HKLM\SOFTWARE\Classes\TypeLib\{61A2027D-B837-4080-A925-6E30E10DEF32}
[-] Key deleted: HKLM\SOFTWARE\Classes\TypeLib\{F6C2BABA-9E4C-425F-9AEC-24AB8F2B640D}
[-] Key deleted: HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{02478D38-C3F9-4EFB-9B51-7695ECA05670}
[-] Key deleted: HKCU\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{02478D38-C3F9-4EFB-9B51-7695ECA05670}
[-] Key deleted: HKCU\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{EF99BD32-C1FB-11D2-892F-0090271D4F88}
[-] Key deleted: HKCU\Software\Microsoft\Windows\CurrentVersion\Ext\Settings\{02478D38-C3F9-4EFB-9B51-7695ECA05670}
[-] Key deleted: HKCU\Software\Microsoft\Windows\CurrentVersion\Ext\Settings\{EF99BD32-C1FB-11D2-892F-0090271D4F88}
[-] Key deleted: HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Ext\PreApproved\{02478D38-C3F9-4EFB-9B51-7695ECA05670}
[-] Key deleted: HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Ext\PreApproved\{EF99BD32-C1FB-11D2-892F-0090271D4F88}
[-] Value deleted: HKLM\SOFTWARE\Microsoft\Internet Explorer\Toolbar [{EF99BD32-C1FB-11D2-892F-0090271D4F88}]
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\BackgroundContainer
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\BackgroundContainerV2
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Conduit
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\tuguu sl
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Yahoo\Companion
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Yahoo\YFriendsBar
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\AppDataLow\Toolbar
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\AppDataLow\Software\ConduitSearchScopes
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\AppDataLow\Software\PriceGong
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\AppDataLow\Software\Yahoo\Companion
[#] Key deleted on reboot: HKCU\Software\BackgroundContainer
[#] Key deleted on reboot: HKCU\Software\BackgroundContainerV2
[#] Key deleted on reboot: HKCU\Software\Conduit
[#] Key deleted on reboot: HKCU\Software\tuguu sl
[#] Key deleted on reboot: HKCU\Software\Yahoo\Companion
[#] Key deleted on reboot: HKCU\Software\Yahoo\YFriendsBar
[#] Key deleted on reboot: HKCU\Software\AppDataLow\Toolbar
[#] Key deleted on reboot: HKCU\Software\AppDataLow\Software\ConduitSearchScopes
[#] Key deleted on reboot: HKCU\Software\AppDataLow\Software\PriceGong
[#] Key deleted on reboot: HKCU\Software\AppDataLow\Software\Yahoo\Companion
[-] Key deleted: HKLM\SOFTWARE\Conduit
[-] Key deleted: HKLM\SOFTWARE\InstallIQ
[-] Key deleted: HKLM\SOFTWARE\Uniblue
[#] Key deleted on reboot: HKLM\SOFTWARE\Uniblue\DriverScanner
[-] Key deleted: HKLM\SOFTWARE\Yahoo\Companion
[-] Key deleted: HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\{EBE677C0-CBCB-4EBF-8098-E27E1B5271CF}
[-] Key deleted: HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Yahoo! Companion
[-] Key deleted: HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Yahoo! Toolbar
[#] Key deleted on reboot: [x64] HKCU\Software\BackgroundContainer
[#] Key deleted on reboot: [x64] HKCU\Software\BackgroundContainerV2
[#] Key deleted on reboot: [x64] HKCU\Software\Conduit
[#] Key deleted on reboot: [x64] HKCU\Software\tuguu sl
[#] Key deleted on reboot: [x64] HKCU\Software\Yahoo\Companion
[#] Key deleted on reboot: [x64] HKCU\Software\Yahoo\YFriendsBar
[#] Key deleted on reboot: [x64] HKCU\Software\AppDataLow\Toolbar
[#] Key deleted on reboot: [x64] HKCU\Software\AppDataLow\Software\ConduitSearchScopes
[#] Key deleted on reboot: [x64] HKCU\Software\AppDataLow\Software\PriceGong
[#] Key deleted on reboot: [x64] HKCU\Software\AppDataLow\Software\Yahoo\Companion
[-] Key deleted: [x64] HKLM\SOFTWARE\DomaIQ
[-] Key deleted: HKLM\SOFTWARE\Classes\Installer\Features\0C776EBEBCBCFBE408892EE7B12517FC
[-] Key deleted: HKLM\SOFTWARE\Classes\Installer\Products\0C776EBEBCBCFBE408892EE7B12517FC
[-] Key deleted: [x64] HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\UserData\S-1-5-18\Products\0C776EBEBCBCFBE408892EE7B12517FC
[-] Key deleted: [x64] HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\UserData\S-1-5-18\Components\0C776EBEBCBCFBE408892EE7B12517FC
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\UserData\S-1-5-18\Products\0C776EBEBCBCFBE408892EE7B12517FC
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\Installer\Features\0C776EBEBCBCFBE408892EE7B12517FC
[#] Key deleted on reboot: [x64] HKLM\SOFTWARE\Classes\Installer\Products\0C776EBEBCBCFBE408892EE7B12517FC
[-] Data restored: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\Main [Start Page] 
[-] Data restored: HKCU\Software\Microsoft\Internet Explorer\Main [Start Page] 
[-] Data restored: [x64] HKCU\Software\Microsoft\Internet Explorer\Main [Start Page] 
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\SearchScopes\{0633EE93-D776-472f-A0FF-E1416B8B2E3A}
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\SearchScopes\{77E4343C-FD7A-48DD-A140-771EF668F9E6}
[-] Key deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\SearchScopes\{863FD1AF-2869-4CE9-A223-2BA9F9620E61}
[-] Data restored: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\SearchScopes [DefaultScope] {0633EE93-D776-472f-A0FF-E1416B8B2E3A}
[#] Key deleted on reboot: HKCU\Software\Microsoft\Internet Explorer\SearchScopes\{0633EE93-D776-472f-A0FF-E1416B8B2E3A}
[#] Key deleted on reboot: HKCU\Software\Microsoft\Internet Explorer\SearchScopes\{77E4343C-FD7A-48DD-A140-771EF668F9E6}
[#] Key deleted on reboot: HKCU\Software\Microsoft\Internet Explorer\SearchScopes\{863FD1AF-2869-4CE9-A223-2BA9F9620E61}
[-] Data restored: HKCU\Software\Microsoft\Internet Explorer\SearchScopes [DefaultScope] {0633EE93-D776-472f-A0FF-E1416B8B2E3A}
[#] Key deleted on reboot: [x64] HKCU\Software\Microsoft\Internet Explorer\SearchScopes\{0633EE93-D776-472f-A0FF-E1416B8B2E3A}
[#] Key deleted on reboot: [x64] HKCU\Software\Microsoft\Internet Explorer\SearchScopes\{77E4343C-FD7A-48DD-A140-771EF668F9E6}
[#] Key deleted on reboot: [x64] HKCU\Software\Microsoft\Internet Explorer\SearchScopes\{863FD1AF-2869-4CE9-A223-2BA9F9620E61}
[-] Data restored: [x64] HKCU\Software\Microsoft\Internet Explorer\SearchScopes [DefaultScope] {0633EE93-D776-472f-A0FF-E1416B8B2E3A}
[-] Key deleted: HKCU\Software\Microsoft\Internet Explorer\LowRegistry\DOMStorage\ask.com
[#] Key deleted on reboot: [x64] HKCU\Software\Microsoft\Internet Explorer\LowRegistry\DOMStorage\ask.com
[-] Value deleted: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Windows\CurrentVersion\Explorer\StartupApproved\Run [BackgroundContainerV2]
[-] Key deleted: HKLM\SOFTWARE\Classes\AppID\yt.DLL
[-] Key deleted: HKLM\SOFTWARE\Classes\AppID\ytbbroker.EXE
[-] Key deleted: HKCU\Software\Google\Chrome\Extensions\klibnahbojhkanfgaglnlalfkgpcppfi
[-] Key deleted: HKLM\SOFTWARE\Google\Chrome\Extensions\klibnahbojhkanfgaglnlalfkgpcppfi
[#] Key deleted on reboot: [x64] HKCU\Software\Google\Chrome\Extensions\klibnahbojhkanfgaglnlalfkgpcppfi
 
 
***** [ Web browsers ] *****
 
[-] [C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Web data] [Search Provider] Deleted: search.conduit.com
[-] [C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Web data] [Search Provider] Deleted: aol.com
[-] [C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Web data] [Search Provider] Deleted: McAfee
[-] [C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Web data] [Search Provider] Deleted: ask.com
[-] [C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default] [startup_urls] Deleted: hxxp://search.conduit.com/?ctid=CT3289847&SearchSource=48&CUI=UN19927041542956553&UM=2
 
 
*************************
 
:: "Tracing" keys deleted
:: Winsock settings cleared
 
*************************
 
C:\AdwCleaner\AdwCleaner[C0].txt - [19266 Bytes] - [21/09/2016 15:51:57]
C:\AdwCleaner\AdwCleaner[S0].txt - [17967 Bytes] - [21/09/2016 15:50:23]
 
########## EOF - C:\AdwCleaner\AdwCleaner[C0].txt - [19414 Bytes] ##########
 
 ~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~
Junkware Removal Tool (JRT) by Malwarebytes
Version: 8.0.7 (07.03.2016)
Operating System: Windows 10 Home x64 
Ran by [removed] (Administrator) on Wed 09/21/2016 at 16:00:16.29
~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~


File System: 9 
 
Successfully deleted: C:\ProgramData\esellerate (Folder) 
Successfully deleted: C:\Users\Paddy\AppData\Local\{1488060C-A14E-44B9-B23F-DE73165463F1} (Empty Folder)
Successfully deleted: C:\Users\Paddy\AppData\Local\{1902AF05-3A03-4C97-82B9-4312FC6E9454} (Empty Folder)
Successfully deleted: C:\Users\Paddy\AppData\Local\{4D1246C0-F965-42C6-A14B-271C9B5C4FC6} (Empty Folder)
Successfully deleted: C:\Users\Paddy\AppData\Local\{59358025-E84C-4824-A0CF-698D851AB6AF} (Empty Folder)
Successfully deleted: C:\Users\Paddy\AppData\Local\{9E8FA02A-C2EA-496B-8AFD-9DBC99475BCF} (Empty Folder)
Successfully deleted: C:\Users\Paddy\AppData\Local\{CC395B82-DE65-4427-9865-46416D8FFC35} (Empty Folder)
Successfully deleted: C:\Users\Paddy\Appdata\LocalLow\whitesmoke_new (Folder) 
Successfully deleted: C:\Program Files (x86)\whitesmoke_new (Folder) 


Registry: 9 
 
Successfully deleted: HKCU\Software\Microsoft\Windows\CurrentVersion\Run\\GoogleChromeAutoLaunch_3C506A97676A871F60321234A2B923FD (Registry Value) 
Successfully deleted: HKCU\Software\Microsoft\Internet Explorer\Toolbar\WebBrowser\\{739DF940-C5EE-4BAB-9D7E-270894AE687A} (Registry Value) 
Successfully deleted: HKCU\Software\Microsoft\Internet Explorer\SearchScopes\{BC005D3D-84AA-42A0-913D-5F80610219F5} (Registry Key)
Successfully deleted: HKCU\Software\Microsoft\Internet Explorer\SearchScopes\{d43b3890-80c7-4010-a95d-1e77b5924dc3} (Registry Key)
Successfully deleted: HKCU\Software\Microsoft\Internet Explorer\SearchScopes\{D944BB61-2E34-4DBF-A683-47E505C587DC} (Registry Key)
Successfully deleted: HKLM\Software\Microsoft\Internet Explorer\SearchScopes\{BC005D3D-84AA-42A0-913D-5F80610219F5} (Registry Key)
Successfully deleted: HKLM\Software\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{739df940-c5ee-4bab-9d7e-270894ae687a} (Registry Key)
Successfully deleted: HKLM\Software\Wow6432Node\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{739df940-c5ee-4bab-9d7e-270894ae687a} (Registry Key)
Successfully deleted: HKLM\Software\Wow6432Node\Microsoft\Internet Explorer\Toolbar\\{739DF940-C5EE-4BAB-9D7E-270894AE687A} (Registry Value) 


~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~
Scan was completed on Wed 09/21/2016 at 16:03:59.09
End of JRT log
~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~
Malwarebytes Anti-Malware
www.malwarebytes.org
 
Scan Date: 9/21/2016
Scan Time: 6:19 PM
Logfile: 
Administrator: Yes
 
Version: 2.2.1.1043
Malware Database: v2016.09.21.12
Rootkit Database: v2016.08.15.01
License: Trial
Malware Protection: Enabled
Malicious Website Protection: Enabled
Self-protection: Disabled
 
OS: Windows 10
CPU: x64
File System: NTFS
User: Paddy
 
Scan Type: Threat Scan
Result: Completed
Objects Scanned: 396303
Time Elapsed: 19 min, 4 sec
 
Memory: Enabled
Startup: Enabled
Filesystem: Enabled
Archives: Enabled
Rootkits: Disabled
Heuristics: Enabled
PUP: Enabled
PUM: Enabled
 
Processes: 0
(No malicious items detected)
 
Modules: 0
(No malicious items detected)
 
Registry Keys: 7
PUP.Optional.WhiteSmoke, HKLM\SOFTWARE\WOW6432NODE\CLASSES\CLSID\{739DF940-C5EE-4BAB-9D7E-270894AE687A}, , [7e52155fbddd63d3e1eb3a5931d154ac], 
PUP.Optional.WhiteSmoke, HKLM\SOFTWARE\CLASSES\WOW6432NODE\CLSID\{739DF940-C5EE-4BAB-9D7E-270894AE687A}, , [7e52155fbddd63d3e1eb3a5931d154ac], 
PUP.Optional.WhiteSmoke, HKLM\SOFTWARE\WOW6432NODE\WhiteSmoke_New, , [f9d714609efc80b646d8e9d39b688b75], 
PUP.Optional.ConduitTB.Gen, HKLM\SOFTWARE\WOW6432NODE\MICROSOFT\INTERNET EXPLORER\LOW RIGHTS\ELEVATIONPOLICY\{1B1173BD-FC80-485F-9889-5A3B66E64226}, , [7957d4a08e0cbf77534b9c0047bcf60a], 
PUP.Optional.WhiteSmoke, HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\APPDATALOW\SOFTWARE\WhiteSmoke_New, , [f8d84a2af9a152e478a2ccf031d28977], 
PUP.Optional.ConduitTB.Gen, HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\MICROSOFT\INTERNET EXPLORER\LOW RIGHTS\ELEVATIONPOLICY\{1B1173BD-FC80-485F-9889-5A3B66E64226}, , [369a2252eeac1026d1cc514b53b0ee12], 
PUP.Optional.ConduitTB.Gen, HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\MICROSOFT\INTERNET EXPLORER\LOW RIGHTS\ELEVATIONPOLICY\{70645C8C-01E8-4296-B46B-1181DC2B0239}, , [a22ef2820a90b77f26772f6dca3911ef], 
 
Registry Values: 8
PUP.Optional.WhiteSmoke, HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\MICROSOFT\INTERNET EXPLORER\URLSEARCHHOOKS|{739DF940-C5EE-4BAB-9D7E-270894AE687A}, , [7e52155fbddd63d3e1eb3a5931d154ac], 
PUP.Optional.WhiteSmoke, HKLM\SOFTWARE\WOW6432NODE\MICROSOFT\INTERNET EXPLORER\URLSEARCHHOOKS|{739DF940-C5EE-4BAB-9D7E-270894AE687A}, , [7e52155fbddd63d3e1eb3a5931d154ac], 
PUP.Optional.WhiteSmoke, HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\MICROSOFT\INTERNET EXPLORER\URLSEARCHHOOKS\{739df940-c5ee-4bab-9d7e-270894ae687a}, , [dcf453211486e056efdd2a6917ebfc04], 
PUP.Optional.WhiteSmoke, HKLM\SOFTWARE\WOW6432NODE\MICROSOFT\INTERNET EXPLORER\URLSEARCHHOOKS\{739df940-c5ee-4bab-9d7e-270894ae687a}, , [339d13617b1fc175f0dc5f3437cb40c0], 
PUP.Optional.ConduitTB.Gen, HKLM\SOFTWARE\WOW6432NODE\MICROSOFT\INTERNET EXPLORER\LOW RIGHTS\ELEVATIONPOLICY\{1B1173BD-FC80-485F-9889-5A3B66E64226}|AppPath, C:\Users\Paddy\AppData\Local\Conduit\CT3289847, , [7957d4a08e0cbf77534b9c0047bcf60a]
PUP.Optional.ConduitTB.Gen, HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\MICROSOFT\INTERNET EXPLORER\LOW RIGHTS\ELEVATIONPOLICY\{1B1173BD-FC80-485F-9889-5A3B66E64226}|AppPath, C:\Users\Paddy\AppData\Local\Conduit\CT3289847, , [369a2252eeac1026d1cc514b53b0ee12]
PUP.Optional.ConduitTB.Gen, HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\MICROSOFT\INTERNET EXPLORER\LOW RIGHTS\ELEVATIONPOLICY\{70645C8C-01E8-4296-B46B-1181DC2B0239}|AppPath, C:\Users\Paddy\AppData\Local\Conduit\CT3289847, , [a22ef2820a90b77f26772f6dca3911ef]
PUP.Optional.Conduit, HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\MICROSOFT\WINDOWS\CURRENTVERSION\RUN|BackgroundContainerV3, "C:\WINDOWS\SysWOW64\Rundll32.exe" "C:\Users\Paddy\AppData\Local\Cctbplt\BackgroundContainer\BackgroundContainer.dll",DllRun, , [27a9076d95056acc4be47763a75b52ae]
 
Registry Data: 0
(No malicious items detected)
 
Folders: 2
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images, , [4e82730116848caa21bf922856ade41c], 
 
Files: 44
PUP.Optional.SearchProtect, C:\Users\Paddy\AppData\Local\Temp\Runner.exe, , [844cea8ac1d9c472c8fd7443867b7b85], 
PUP.Optional.ClientConnect, C:\Users\Paddy\AppData\Local\Cctbplt\BackgroundContainer\BackgroundContainer.dll, , [9838da9a1387102679e16e5eb848fb05], 
PUP.Optional.ClientConnect, C:\Users\Paddy\AppData\Local\Cctbplt\BackgroundContainer\TBUpdaterLogic_4.0.0.2.dll, , [08c84430b2e8d0660f4b73598f71ce32], 
PUP.Optional.ClientConnect, C:\Users\Paddy\AppData\Local\Cctbplt\BackgroundContainer\TBUpdaterLogic_5.0.0.1.dll, , [39978ee6811932049ac0715be818ec14], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\playlist.vpl, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\config.ini, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_193.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_199.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_200.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_201.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_204.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_219.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_221.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_224.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_268.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_28.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_34.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_37.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_49.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_57.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_86.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_99.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_103.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_11.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_120.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_121.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_122.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_123.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_124.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_125.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_126.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_127.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_136.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_137.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_140.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_141.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_149.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_150.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_160.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_165.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_181.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.VPLMedia, C:\Users\Paddy\AppData\Roaming\player\images\channel_ld_191.png, , [4e82730116848caa21bf922856ade41c], 
PUP.Optional.Conduit, C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Local Storage\http_app.mam.conduit.com_0.localstorage, , [dff1155f6b2f63d3ab1cca16a75cee12], 
PUP.Optional.Conduit, C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Local Storage\http_app.mam.conduit.com_0.localstorage-journal, , [dbf5c4b07d1dce68a91ed01031d220e0], 
 
Physical Sectors: 0
(No malicious items detected)
 
 
(end)
 

So far so good but let me ask you, did you set up Malwarebytes per my instructions because all those entries it found need to be gone, they should show on the log as QUARANTINED and they do not, you may need to run the program again and do it this way if you can


These are not from your log, its just and example from another post from another user, see how the entries are QUARANTINED 


PUP.Optional.Amonetize.A, HKLM\SOFTWARE\CLASSES\TYPELIB\{B0660298-91AA-421F-BF0D-BFF6BB8BF3AE}, Quarantined, [d8771a9c444610265bd9f3af73904ab6],
PUP.Optional.Amonetize.A, HKLM\SOFTWARE\CLASSES\INTERFACE\{EAC7DE5C-9520-435D-91AA-4A02E4773CEA}, Quarantined, [d8771a9c444610265bd9f3af73904ab6],


  •  
  • You can highlight one of the detections by left clicking on it.
  • Then, right click on the highlighted detection, and select 'Check All Items'.
  • Next, click 'Remove Selected'. That should remove them all


After you sure that Malwarebytes removed those entries and the new scan comes back clean, then right click on FRST64 and select RUN AS ADMINISTRATOR ,  besure to checkmark ADDITIONS, leave everything else as is , click SCAN and post both the new FRST and Additions logs please
Ken,  Thanks again for your assistance.  Once I reopened Malwarebytes, all of the problems it found were still there, so I selected Fix, or maybe Remove and it then removed everything and the rescan came back clean as noted below.  Not sure why it would not have quarantined them initially, but they appear to be gone now.  Rescanned with FRST64, results also pasted below.  I await your next instruction…
 
Regards, Bob
 
Scan result of Farbar Recovery Scan Tool (FRST) (x64) Version: 21-09-2016
Ran by [removed] (administrator) on PADDY1 (21-09-2016 20:45:56)
Running from C:\Users\[removed]\Desktop
[removed]
Platform: Windows 10 Home Version 1511 (X64) Language: English (United States)
Internet Explorer Version 11 (Default browser: Edge)
Boot Mode: Normal
Tutorial for Farbar Recovery Scan Tool: http://www.geekstogo.com/forum/topic/335081-frst-tutorial-how-to-use-farbar-recovery-scan-tool/
 
==================== Processes (Whitelisted) =================
 
(If an entry is included in the fixlist, the process will be closed. The file will not be moved.)
 
(AMD) C:\Windows\System32\atiesrxx.exe
(IDT, Inc.) C:\Program Files\IDT\WDM\stacsv64.exe
(Andrea Electronics Corporation) C:\Program Files\IDT\WDM\AESTSr64.exe
(Microsoft Corporation) C:\Windows\System32\mqsvc.exe
(Apple Inc.) C:\Program Files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
() C:\Program Files (x86)\Cyberlink\Shared files\RichVideo.exe
(Microsoft Corporation) C:\Program Files\Windows Defender\MsMpEng.exe
() C:\Program Files\CyberLink\Shared files\RichVideo64.exe
(PDF Complete Inc) C:\Program Files (x86)\PDF Complete\pdfsvc.exe
(Hewlett-Packard Company) C:\Program Files\Hewlett-Packard\HP Client Services\HPClientServices.exe
(Apple Inc.) C:\Program Files\Bonjour\mDNSResponder.exe
(Microsoft Corporation) C:\Program Files (x86)\Microsoft Application Virtualization Client\sftvsa.exe
(Microsoft Corporation) C:\Windows\Microsoft.NET\Framework64\v4.0.30319\SMSvcHost.exe
(Microsoft Corporation) C:\Program Files (x86)\Microsoft Application Virtualization Client\sftlist.exe
(Microsoft Corporation) C:\Windows\Microsoft.NET\Framework64\v4.0.30319\SMSvcHost.exe
(Microsoft Corporation) C:\Program Files (x86)\Common Files\Microsoft Shared\Virtualization Handler\CVHSVC.EXE
(Microsoft Corporation) C:\Program Files\Windows Defender\NisSrv.exe
(Microsoft Corporation) C:\Program Files\Windows Defender\MpCmdRun.exe
() C:\Program Files\WindowsApps\Microsoft.Messaging_2.15.20002.0_x86__8wekyb3d8bbwe\SkypeHost.exe
(HP Inc.) C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\HPSupportSolutionsFrameworkService.exe
(Intel Corporation) C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\LMS\LMS.exe
(Intel Corporation) C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\UNS\UNS.exe
(Microsoft Corporation) C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\RemindersServer.exe
(Hewlett-Packard Company) C:\Program Files (x86)\Hewlett-Packard\Shared\hpqwmiex.exe
(Microsoft Corporation) C:\Windows\System32\SettingSyncHost.exe
() C:\Program Files\WindowsApps\Microsoft.WindowsCalculator_10.1608.2213.0_x64__8wekyb3d8bbwe\Calculator.exe
(Microsoft Corporation) C:\Windows\ImmersiveControlPanel\SystemSettings.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
(Malwarebytes) C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamservice.exe
(Malwarebytes) C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamscheduler.exe
(Malwarebytes) C:\Program Files (x86)\Malwarebytes Anti-Malware\mbam.exe
(Google Inc.) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
() C:\Program Files\WindowsApps\Microsoft.Windows.Photos_16.722.10060.0_x64__8wekyb3d8bbwe\Microsoft.Photos.exe
 
 
==================== Registry (Whitelisted) ===========================
 
(If an entry is included in the fixlist, the registry item will be restored to default or removed. The file will not be moved.)
 
HKLM\…\Run: [Logitech Download Assistant] => C:\Windows\System32\LogiLDA.dll [1832760 2012-09-20] (Logitech, Inc.)
HKLM\…\Run: [hpsysdrv] => c:\program files (x86)\hewlett-packard\HP odometer\hpsysdrv.exe [62768 2008-11-20] (Hewlett-Packard)
HKLM\…\Run: [SysTrayApp] => C:\Program Files\IDT\WDM\sttray64.exe [1425408 2012-04-24] (IDT, Inc.)
HKLM\…\Run: [BeatsOSDApp] => C:\Program Files\IDT\WDM\beats64.exe [37888 2011-08-24] (Hewlett-Packard )
HKLM-x32\…\Run: [StartCCC] => C:\Program Files (x86)\ATI Technologies\ATI.ACE\Core-Static\amd64\CLIStart.exe [767176 2015-11-04] (Advanced Micro Devices, Inc.)
HKLM-x32\…\Run: [HP Software Update] => c:\Program Files (x86)\HP\HP Software Update\HPWuSchd2.exe [54576 2008-12-08] (Hewlett-Packard)
HKLM-x32\…\Run: [mcui_exe] => "C:\Program Files\McAfee.com\Agent\mcagent.exe" /runkey
HKLM-x32\…\Run: [APSDaemon] => C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe [43848 2014-04-23] (Apple Inc.)
HKLM-x32\…\Run: [iTunesHelper] => C:\Program Files (x86)\iTunes\iTunesHelper.exe [152392 2014-05-26] (Apple Inc.)
HKLM-x32\…\Run: [SunJavaUpdateSched] => C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe [596528 2015-11-09] (Oracle Corporation)
HKLM-x32\…\Run: [QuickTime Task] => C:\Program Files (x86)\QuickTime\QTTask.exe [421888 2015-06-17] (Apple Inc.)
HKLM-x32\…\RunOnce: [Malwarebytes Anti-Malware (cleanup)] => C:\ProgramData\Malwarebytes\Malwarebytes Anti-Malware\mbamdor.exe [55264 2016-03-10] (Malwarebytes)
Winlogon\Notify\ScCertProp: wlnotify.dll [X]
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\Run: [HydraVisionDesktopManager] => C:\Program Files (x86)\ATI Technologies\HydraVision\HydraDM.exe [393216 2011-10-24] (AMD)
ShellIconOverlayIdentifiers: [MOBK] -> {3c3f3c1a-9153-7c05-f938-622e7003894d} => C:\Program Files (x86)\McAfee Online Backup\MOBKshell.dll [2010-04-13] (McAfee, Inc.)
ShellIconOverlayIdentifiers: [MOBK2] -> {e6ea1d7d-144e-b977-98c4-84c53c1a69d0} => C:\Program Files (x86)\McAfee Online Backup\MOBKshell.dll [2010-04-13] (McAfee, Inc.)
ShellIconOverlayIdentifiers: [MOBK3] -> {b4caf489-1eec-c617-49ad-8d7088598c06} => C:\Program Files (x86)\McAfee Online Backup\MOBKshell.dll [2010-04-13] (McAfee, Inc.)
Startup: C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Startup\Adobe Gamma.lnk [2013-01-09]
ShortcutTarget: Adobe Gamma.lnk -> C:\Program Files (x86)\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe (Adobe Systems, Inc.)
 
==================== Internet (Whitelisted) ====================
 
(If an item is included in the fixlist, if it is a registry item it will be removed or restored to default.)
 
Tcpip\Parameters: [DhcpNameServer] 10.1.10.1
Tcpip\..\Interfaces\{54536d99-20d6-4e60-948b-17d85e127466}: [DhcpNameServer] 10.1.10.1
 
Internet Explorer:
==================
HKLM\SOFTWARE\Policies\Microsoft\Internet Explorer: Restriction <======= ATTENTION
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\Policies\Microsoft\Internet Explorer: Restriction <======= ATTENTION
HKU\.DEFAULT\Software\Microsoft\Internet Explorer\Main,Search Page = hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar;=iesearch
HKU\.DEFAULT\Software\Microsoft\Internet Explorer\Main,Start Page = hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar;=msnhome
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\Main,Search Page = hxxp://www.microsoft.com/isapi/redir.dll?prd=ie&ar;=iesearch
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\Main,Start Page Redirect Cache = hxxp://www.msn.com/
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\Main,Start Page = 
SearchScopes: HKLM -> DefaultScope value is missing
SearchScopes: HKLM -> {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL = hxxp://www.bing.com/search?q={searchTerms}&form;=HPDTDF&pc;=HPDTDF&src;=IE-SearchBox
SearchScopes: HKLM -> {b7fca997-d0fb-4fe0-8afd-255e89cf9671} URL = hxxp://search.yahoo.com/search?p={searchTerms}&ei;={inputEncoding}&fr;=chr-hp-psg&type;=HPDTDF
SearchScopes: HKLM -> {BC005D3D-84AA-42A0-913D-5F80610219F5} URL = hxxp://www.amazon.com/s/ref=azs_osd_iea?ie=UTF-8&tag;=hp-us1-vsb-20&link;%5Fcode=qs&index;=aps&field-keywords;={searchTerms}
SearchScopes: HKLM -> {d43b3890-80c7-4010-a95d-1e77b5924dc3} URL = hxxp://en.wikipedia.org/wiki/Special:Search?search={searchTerms}
SearchScopes: HKLM -> {D944BB61-2E34-4DBF-A683-47E505C587DC} URL = hxxp://rover.ebay.com/rover/1/711-30572-11896-1/4?mpre=hxxp://shop.ebay.com/?_nkw={searchTerms}
SearchScopes: HKLM-x32 -> DefaultScope {863FD1AF-2869-4CE9-A223-2BA9F9620E61} URL = 
SearchScopes: HKLM-x32 -> {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL = hxxp://www.bing.com/search?q={searchTerms}&form;=HPDTDF&pc;=HPDTDF&src;=IE-SearchBox
SearchScopes: HKLM-x32 -> {b7fca997-d0fb-4fe0-8afd-255e89cf9671} URL = hxxp://search.yahoo.com/search?p={searchTerms}&ei;={inputEncoding}&fr;=chr-hp-psg&type;=HPDTDF
SearchScopes: HKLM-x32 -> {d43b3890-80c7-4010-a95d-1e77b5924dc3} URL = hxxp://en.wikipedia.org/wiki/Special:Search?search={searchTerms}
SearchScopes: HKLM-x32 -> {D944BB61-2E34-4DBF-A683-47E505C587DC} URL = hxxp://rover.ebay.com/rover/1/711-30572-11896-1/4?mpre=hxxp://shop.ebay.com/?_nkw={searchTerms}
SearchScopes: HKU\S-1-5-21-648858125-4165233436-1298442668-1001 -> DefaultScope {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL = 
BHO: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2016-04-26] (Google Inc.)
BHO: HP Network Check Helper -> {E76FD755-C1BA-4DCB-9F13-99BD91223ADE} -> C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPNetworkCheck\HPNetworkCheckPluginx64.dll [2016-07-21] (HP Inc.)
BHO-x32: HelperObject Class -> {00C6482D-C502-44C8-8409-FCE54AD9C208} -> C:\Program Files (x86)\TechSmith\SnagIt 7\SnagItBHO.dll [2005-03-09] (TechSmith Corporation)
BHO-x32: Java™ Plug-In SSV Helper -> {761497BB-D6F0-462C-B6EB-D4DAF1D92D43} -> C:\Program Files (x86)\Java\jre1.8.0_66\bin\ssv.dll [2015-12-22] (Oracle Corporation)
BHO-x32: Google Toolbar Helper -> {AA58ED58-01DD-4d91-8333-CF10577473F7} -> C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2016-04-26] (Google Inc.)
BHO-x32: Java™ Plug-In 2 SSV Helper -> {DBC80044-A445-435b-BC74-9C25C1C588A9} -> C:\Program Files (x86)\Java\jre1.8.0_66\bin\jp2ssv.dll [2015-12-22] (Oracle Corporation)
BHO-x32: HP Network Check Helper -> {E76FD755-C1BA-4DCB-9F13-99BD91223ADE} -> C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPNetworkCheck\HPNetworkCheckPlugin.dll [2016-07-21] (HP Inc.)
Toolbar: HKLM - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_64.dll [2016-04-26] (Google Inc.)
Toolbar: HKLM-x32 - SnagIt - {8FF5E183-ABDE-46EB-B09E-D2AAB95CABE3} - C:\Program Files (x86)\TechSmith\SnagIt 7\SnagItIEAddin.dll [2005-03-09] (TechSmith Corporation)
Toolbar: HKLM-x32 - Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll [2016-04-26] (Google Inc.)
DPF: HKLM-x32 {0E5F0222-96B9-11D3-8997-00104BD12D94} hxxp://pcpitstop.com/betapit/PCPitStop.CAB
DPF: HKLM-x32 {1851174C-97BD-4217-A0CC-E908F60D5B7A} hxxps://h50203.www5.hp.com/HPISWeb/Customer/cabs/HPISDataManager.CAB
 
FireFox:
========
FF Plugin: @adobe.com/FlashPlayer -> C:\WINDOWS\system32\Macromed\Flash\NPSWF64_23_0_0_179.dll [2016-09-21] ()
FF Plugin: @Microsoft.com/NpCtrl,version=1.0 -> c:\Program Files\Microsoft Silverlight\5.1.50709.0\npctrl.dll [2016-07-11] ( Microsoft Corporation)
FF Plugin-x32: @adobe.com/FlashPlayer -> C:\WINDOWS\SysWOW64\Macromed\Flash\NPSWF32_23_0_0_179.dll [2016-09-21] ()
FF Plugin-x32: @Apple.com/iTunes,version=1.0 -> C:\Program Files (x86)\iTunes\Mozilla Plugins\npitunes.dll [2014-02-21] ()
FF Plugin-x32: @canon.com/MycameraPlugin -> C:\Program Files (x86)\Canon\MyCamera Download Plugin\NPCIG.dll [2008-10-15] (CANON INC.)
FF Plugin-x32: @Google.com/GoogleEarthPlugin -> C:\Program Files (x86)\Google\Google Earth\plugin\npgeplugin.dll [2015-05-21] (Google)
FF Plugin-x32: @java.com/DTPlugin,version=11.66.2 -> C:\WINDOWS\SysWOW64\npdeployJava1.dll [2015-12-22] (Oracle Corporation)
FF Plugin-x32: @java.com/JavaPlugin -> C:\Program Files (x86)\Java\jre1.8.0_66\bin\plugin2\npjp2.dll [2015-12-22] (Oracle Corporation)
FF Plugin-x32: @java.com/JavaPlugin,version=11.66.2 -> C:\Program Files (x86)\Java\jre1.8.0_66\bin\plugin2\npjp2.dll [2015-12-22] (Oracle Corporation)
FF Plugin-x32: @Microsoft.com/NpCtrl,version=1.0 -> c:\Program Files (x86)\Microsoft Silverlight\5.1.50709.0\npctrl.dll [2016-07-11] ( Microsoft Corporation)
FF Plugin-x32: @microsoft.com/SharePoint,version=14.0 -> C:\PROGRA~2\MICROS~1\Office14\NPSPWRAP.DLL [2010-03-24] (Microsoft Corporation)
FF Plugin-x32: @microsoft.com/WLPG,version=15.4.3502.0922 -> C:\Program Files (x86)\Windows Live\Photo Gallery\NPWLPG.dll [2014-03-31] (Microsoft Corporation)
FF Plugin-x32: @microsoft.com/WLPG,version=16.4.3528.0331 -> C:\Program Files (x86)\Windows Live\Photo Gallery\NPWLPG.dll [2014-03-31] (Microsoft Corporation)
FF Plugin-x32: @tools.google.com/Google Update;version=3 -> C:\Program Files (x86)\Google\Update\1.3.31.5\npGoogleUpdate3.dll [2016-07-29] (Google Inc.)
FF Plugin-x32: @tools.google.com/Google Update;version=9 -> C:\Program Files (x86)\Google\Update\1.3.31.5\npGoogleUpdate3.dll [2016-07-29] (Google Inc.)
FF Plugin-x32: @videolan.org/vlc,version=2.0.8 -> C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll [2015-04-13] (VideoLAN)
FF Plugin-x32: @videolan.org/vlc,version=2.1.2 -> C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll [2015-04-13] (VideoLAN)
FF Plugin-x32: @videolan.org/vlc,version=2.2.1 -> C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll [2015-04-13] (VideoLAN)
FF Plugin-x32: @WildTangent.com/GamesAppPresenceDetector,Version=1.0 -> C:\Program Files (x86)\WildTangent Games\App\BrowserIntegration\Registered\0\NP_wtapp.dll [2010-12-07] ()
FF Plugin-x32: Adobe Reader -> C:\Program Files (x86)\Adobe\Acrobat Reader DC\Reader\AIR\nppdf32.dll [2016-06-30] (Adobe Systems Inc.)
FF Plugin HKU\S-1-5-21-648858125-4165233436-1298442668-1001: @hulu.com/Hulu Desktop -> C:\Users\Default.migrated\AppData\Local\HuluDesktop\instances\0.9.13.1\nphdplg.dll [No File]
StartMenuInternet: FIREFOX.EXE - firefox.exe
 
Chrome: 
=======
CHR HomePage: Default -> hxxp://www.hotmail.com/
CHR StartupUrls: Default -> "hxxp://www.google.com/","hxxp://search.conduit.com/?ctid=CT3289847&SearchSource;=48&CUI;=UN19927041542956553&UM;=2"
CHR Session Restore: Default -> is enabled.
CHR Plugin: (Widevine Content Decryption Module) - C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\WidevineCDM\1.4.2.464\_platform_specific\win_x86\widevinecdmadapter.dll => No File
CHR Plugin: (Shockwave Flash) - C:\Program Files (x86)\Google\Chrome\Application\53.0.2785.116\PepperFlash\pepflashplayer.dll ()
CHR Plugin: (Native Client) - C:\Program Files (x86)\Google\Chrome\Application\53.0.2785.116\ppGoogleNaClPluginChrome.dll => No File
CHR Plugin: (Chrome PDF Viewer) - C:\Program Files (x86)\Google\Chrome\Application\53.0.2785.116\pdf.dll => No File
CHR Plugin: (QuickTime Plug-in 7.7.4) - C:\Program Files (x86)\QuickTime\plugins\npqtplugin.dll (Apple Inc.)
CHR Plugin: (QuickTime Plug-in 7.7.4) - C:\Program Files (x86)\QuickTime\plugins\npqtplugin2.dll (Apple Inc.)
CHR Plugin: (QuickTime Plug-in 7.7.4) - C:\Program Files (x86)\QuickTime\plugins\npqtplugin3.dll (Apple Inc.)
CHR Plugin: (QuickTime Plug-in 7.7.4) - C:\Program Files (x86)\QuickTime\plugins\npqtplugin4.dll (Apple Inc.)
CHR Plugin: (QuickTime Plug-in 7.7.4) - C:\Program Files (x86)\QuickTime\plugins\npqtplugin5.dll (Apple Inc.)
CHR Plugin: (Microsoft Office 2010) - C:\PROGRA~2\MICROS~1\Office14\NPSPWRAP.DLL (Microsoft Corporation)
CHR Plugin: (NPCIG.dll) - C:\Program Files (x86)\Canon\MyCamera Download Plugin\NPCIG.dll (CANON INC.)
CHR Plugin: (Google Earth Plugin) - C:\Program Files (x86)\Google\Google Earth\plugin\npgeplugin.dll (Google)
CHR Plugin: (Google Update) - C:\Program Files (x86)\Google\Update\1.3.22.5\npGoogleUpdate3.dll => No File
CHR Plugin: (Java Deployment Toolkit 7.0.510.13) - C:\Program Files (x86)\Java\jre7\bin\dtplugin\npDeployJava1.dll => No File
CHR Plugin: (Java(TM) Platform SE 7 U51) - C:\Program Files (x86)\Java\jre7\bin\plugin2\npjp2.dll => No File
CHR Plugin: (McAfee Virtual Technician) - C:\Program Files (x86)\McAfee\Supportability\MVT\npmvtplugin.dll => No File
CHR Plugin: (VLC Web Plugin) - C:\Program Files (x86)\VideoLAN\VLC\npvlc.dll (VideoLAN)
CHR Plugin: (Windows Live Photo Gallery) - C:\Program Files (x86)\Windows Live\Photo Gallery\NPWLPG.dll (Microsoft Corporation)
CHR Plugin: (Hulu Desktop) - C:\Windows\..\Users\Default\AppData\Local\HuluDesktop\instances\0.9.13.1\npHDPlg.dll (Hulu LLC)
CHR Plugin: (Shockwave Flash) - C:\Windows\SysWOW64\Macromed\Flash\NPSWF32_13_0_0_154.dll => No File
CHR Plugin: (McAfee SecurityCenter) - c:\PROGRA~2\mcafee\msc\NPMCSN~1.DLL => No File
CHR Plugin: (Silverlight Plug-In) - c:\Program Files (x86)\Microsoft Silverlight\5.1.20913.0\npctrl.dll => No File
CHR Profile: C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default [2016-09-21]
CHR Extension: (YouTube) - C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Extensions\blpcfgokakmgnkcojhhkbfbldkacnbeo [2015-12-16]
CHR Extension: (Google Search) - C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Extensions\coobgpohoikkiipiblmjeljniedjpjpf [2015-12-16]
CHR Extension: (Chrome Web Store Payments) - C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Extensions\nmmhkkegccagdldgiimedpiccmgmieda [2016-04-29]
CHR Extension: (Gmail) - C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Extensions\pjkljhegncpnkpknbcohdijeoejaedia [2015-04-12]
CHR Extension: (Chrome Media Router) - C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\Default\Extensions\pkedcjkdefgpdelpbcmbmeomcjbeemfm [2016-09-21]
 
==================== Services (Whitelisted) ========================
 
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
 
S3 Adobe LM Service; C:\Program Files (x86)\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe [72704 2013-01-09] (Adobe Systems) [File not signed]
S2 CLKMSVC10_38F51D56; c:\Program Files (x86)\Cyberlink\PowerDVD10\NavFilter\kmsvc.exe [241648 2011-01-25] (CyberLink)
R2 HPSupportSolutionsFrameworkService; C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\HPSupportSolutionsFrameworkService.exe [29728 2016-08-15] (HP Inc.)
R2 MBAMScheduler; C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamscheduler.exe [1514464 2016-03-10] (Malwarebytes)
R2 MBAMService; C:\Program Files (x86)\Malwarebytes Anti-Malware\mbamservice.exe [1136608 2016-03-10] (Malwarebytes)
R2 pdfcDispatcher; C:\Program Files (x86)\PDF Complete\pdfsvc.exe [1127448 2011-02-01] (PDF Complete Inc)
R2 RichVideo; C:\Program Files (x86)\Cyberlink\Shared files\RichVideo.exe [254552 2012-10-18] ()
R2 RichVideo64; C:\Program Files\CyberLink\Shared files\RichVideo64.exe [390672 2012-10-16] ()
S3 vmicvss; C:\Windows\System32\ICSvc.dll [511488 2016-09-07] (Microsoft Corporation)
R3 WdNisSvc; C:\Program Files\Windows Defender\NisSrv.exe [364456 2016-09-07] (Microsoft Corporation)
R2 WinDefend; C:\Program Files\Windows Defender\MsMpEng.exe [24864 2016-09-07] (Microsoft Corporation)
 
===================== Drivers (Whitelisted) ==========================
 
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
 
R3 AtiHDAudioService; C:\Windows\system32\drivers\AtihdWT6.sys [102912 2015-05-28] (Advanced Micro Devices)
S3 dot4; C:\Windows\system32\DRIVERS\Dot4.sys [151968 2012-10-19] (Windows (R) Win 7 DDK provider)
S3 Dot4Print; C:\Windows\System32\drivers\Dot4Prt.sys [27040 2012-10-19] (Windows (R) Win 7 DDK provider)
U0 jrwn; C:\Windows\System32\drivers\bgifq.sys [79064 2016-09-21] (Malwarebytes)
R3 MBAMProtector; C:\WINDOWS\system32\drivers\mbam.sys [27008 2016-03-10] (Malwarebytes)
R3 MBAMSwissArmy; C:\WINDOWS\system32\drivers\MBAMSwissArmy.sys [192216 2016-09-21] (Malwarebytes)
R3 MBAMWebAccessControl; C:\WINDOWS\system32\drivers\mwac.sys [65408 2016-03-10] (Malwarebytes Corporation)
R1 MOBKFilter; C:\Windows\System32\DRIVERS\MOBK.sys [66040 2010-04-13] (Mozy, Inc.)
R3 rt640x64; C:\Windows\System32\drivers\rt640x64.sys [589824 2015-10-30] (Realtek                                            )
R3 S3XXx64; C:\Windows\system32\DRIVERS\S3XXx64.sys [73856 2015-02-17] (Identiv)
R3 scsiscan; C:\Windows\system32\DRIVERS\scsiscan.sys [20480 2015-10-30] (Microsoft Corporation)
R0 szkg5; C:\Windows\SysWow64\DRIVERS\szkg64.sys [74768 2011-09-26] (iS3 Inc.)
R3 tilfilter; C:\Windows\System32\drivers\TIxHCIlfilter.sys [34424 2016-08-20] (Texas Instruments, Inc.)
R3 tiufilter; C:\Windows\System32\drivers\TIxHCIufilter.sys [39032 2016-08-20] (Texas Instruments, Inc.)
S0 WdBoot; C:\Windows\System32\drivers\WdBoot.sys [44568 2015-10-30] (Microsoft Corporation)
R0 WdFilter; C:\Windows\System32\drivers\WdFilter.sys [293216 2015-10-30] (Microsoft Corporation)
R3 WdNisDrv; C:\Windows\System32\Drivers\WdNisDrv.sys [118112 2015-10-30] (Microsoft Corporation)
R2 {B154377D-700F-42cc-9474-23858FBDF4BD}; C:\Program Files (x86)\CyberLink\PowerDVD9\000.fcl [146928 2009-09-01] (CyberLink Corp.)
U3 idsvc; no ImagePath
U3 wpcsvc; no ImagePath
 
==================== NetSvcs (Whitelisted) ===================
 
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
 
 
==================== One Month Created files and folders ========
 
(If an entry is included in the fixlist, the file/folder will be moved.)
 
2016-09-21 20:45 - 2016-09-21 20:46 - 00022675 _____ C:\Users\Paddy\Desktop\FRST.txt
2016-09-21 19:26 - 2016-09-21 19:26 - 00079064 _____ (Malwarebytes) C:\WINDOWS\system32\Drivers\bgifq.sys
2016-09-21 18:17 - 2016-09-21 20:36 - 00192216 _____ (Malwarebytes) C:\WINDOWS\system32\Drivers\MBAMSwissArmy.sys
2016-09-21 18:17 - 2016-09-21 18:17 - 00001213 _____ C:\Users\Public\Desktop\Malwarebytes Anti-Malware.lnk
2016-09-21 18:17 - 2016-09-21 18:17 - 00000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Malwarebytes Anti-Malware
2016-09-21 18:17 - 2016-09-21 18:17 - 00000000 ____D C:\Program Files (x86)\Malwarebytes Anti-Malware
2016-09-21 18:17 - 2016-03-10 14:09 - 00065408 _____ (Malwarebytes Corporation) C:\WINDOWS\system32\Drivers\mwac.sys
2016-09-21 18:17 - 2016-03-10 14:08 - 00140672 _____ (Malwarebytes) C:\WINDOWS\system32\Drivers\mbamchameleon.sys
2016-09-21 18:17 - 2016-03-10 14:08 - 00027008 _____ (Malwarebytes) C:\WINDOWS\system32\Drivers\mbam.sys
2016-09-21 18:16 - 2016-09-21 18:17 - 22851472 _____ (Malwarebytes ) C:\Users\Paddy\Desktop\mbam-setup-2.2.1.1043.exe
2016-09-21 16:03 - 2016-09-21 16:03 - 00002687 _____ C:\Users\Paddy\Desktop\JRT.txt
2016-09-21 15:59 - 2016-09-21 16:00 - 01610560 _____ (Malwarebytes) C:\Users\Paddy\Desktop\JRT.exe
2016-09-21 15:48 - 2016-09-21 15:51 - 00000000 ____D C:\AdwCleaner
2016-09-21 15:43 - 2016-09-21 15:48 - 03861056 _____ C:\Users\Paddy\Desktop\AdwCleaner.exe
2016-09-21 15:03 - 2016-09-21 12:57 - 02402816 _____ (Farbar) C:\Users\Paddy\Desktop\FRST64.exe
2016-09-21 15:03 - 2016-09-21 11:54 - 05198336 _____ (AVAST Software) C:\Users\Paddy\Desktop\aswMBR.exe
2016-09-21 12:57 - 2016-09-21 20:45 - 00000000 ____D C:\FRST
2016-09-21 10:54 - 2016-09-21 20:45 - 00000000 ____D C:\BadStuff
2016-09-14 08:29 - 2016-09-07 01:26 - 02544256 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfcore.dll
2016-09-14 08:29 - 2016-09-07 00:48 - 22379520 _____ (Microsoft Corporation) C:\WINDOWS\system32\edgehtml.dll
2016-09-14 08:29 - 2016-09-07 00:43 - 16985600 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Xaml.dll
2016-09-14 08:29 - 2016-09-07 00:35 - 24611840 _____ (Microsoft Corporation) C:\WINDOWS\system32\mshtml.dll
2016-09-14 08:29 - 2016-09-07 00:31 - 00794624 _____ (Microsoft Corporation) C:\WINDOWS\system32\winhttp.dll
2016-09-14 08:29 - 2016-09-07 00:30 - 00602624 _____ (Microsoft Corporation) C:\WINDOWS\system32\vbscript.dll
2016-09-14 08:29 - 2016-09-07 00:29 - 19350016 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mshtml.dll
2016-09-14 08:28 - 2016-09-07 01:39 - 02656952 _____ C:\WINDOWS\system32\CoreUIComponents.dll
2016-09-14 08:28 - 2016-09-07 01:39 - 01098640 _____ (Microsoft Corporation) C:\WINDOWS\system32\MrmCoreR.dll
2016-09-14 08:28 - 2016-09-07 01:39 - 00277848 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\sdbus.sys
2016-09-14 08:28 - 2016-09-07 01:37 - 00572272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\taskschd.dll
2016-09-14 08:28 - 2016-09-07 01:33 - 00026408 _____ (Microsoft Corporation) C:\WINDOWS\system32\wuauclt.exe
2016-09-14 08:28 - 2016-09-07 01:26 - 01299504 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfnetsrc.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 01152320 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfasfsrcsnk.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 01092464 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfplat.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 00858952 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfnetcore.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 00847648 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfsvr.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 00785088 _____ (Microsoft Corporation) C:\WINDOWS\system32\evr.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 00588320 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmdrmdev.dll
2016-09-14 08:28 - 2016-09-07 01:26 - 00245840 _____ (Microsoft Corporation) C:\WINDOWS\system32\mfps.dll
2016-09-14 08:28 - 2016-09-07 01:25 - 02607336 _____ (Microsoft Corporation) C:\WINDOWS\system32\combase.dll
2016-09-14 08:28 - 2016-09-07 01:25 - 01270064 _____ (Microsoft Corporation) C:\WINDOWS\system32\WinTypes.dll
2016-09-14 08:28 - 2016-09-07 01:24 - 01349632 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\winmde.dll
2016-09-14 08:28 - 2016-09-07 01:24 - 00511312 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mf.dll
2016-09-14 08:28 - 2016-09-07 01:24 - 00496360 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wmdrmdev.dll
2016-09-14 08:28 - 2016-09-07 01:23 - 01750440 _____ (Microsoft Corporation) C:\WINDOWS\system32\WpcMon.exe
2016-09-14 08:28 - 2016-09-07 01:23 - 01603224 _____ (Microsoft Corporation) C:\WINDOWS\system32\propsys.dll
2016-09-14 08:28 - 2016-09-07 01:23 - 01040792 _____ (Microsoft Corporation) C:\WINDOWS\system32\twinapi.appcore.dll
2016-09-14 08:28 - 2016-09-07 01:23 - 00725776 _____ (Microsoft Corporation) C:\WINDOWS\system32\SHCore.dll
2016-09-14 08:28 - 2016-09-07 01:22 - 01128096 _____ (Microsoft Corporation) C:\WINDOWS\system32\ClipUp.exe
2016-09-14 08:28 - 2016-09-07 01:20 - 00569744 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SHCore.dll
2016-09-14 08:28 - 2016-09-07 01:19 - 00294752 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msv1_0.dll
2016-09-14 08:28 - 2016-09-07 01:15 - 00911640 _____ (Microsoft Corporation) C:\WINDOWS\system32\dcomp.dll
2016-09-14 08:28 - 2016-09-07 01:12 - 01174008 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msctf.dll
2016-09-14 08:28 - 2016-09-07 00:46 - 00123392 _____ (Microsoft Corporation) C:\WINDOWS\system32\mssprxy.dll
2016-09-14 08:28 - 2016-09-07 00:41 - 00313856 _____ (Microsoft Corporation) C:\WINDOWS\system32\DictationManager.dll
2016-09-14 08:28 - 2016-09-07 00:41 - 00124928 _____ (Microsoft Corporation) C:\WINDOWS\system32\shsetup.dll
2016-09-14 08:28 - 2016-09-07 00:41 - 00094720 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\UserDataTimeUtil.dll
2016-09-14 08:28 - 2016-09-07 00:39 - 01567744 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Globalization.dll
2016-09-14 08:28 - 2016-09-07 00:39 - 00075264 _____ (Microsoft Corporation) C:\WINDOWS\system32\wiarpc.dll
2016-09-14 08:28 - 2016-09-07 00:38 - 00206848 _____ (Microsoft Corporation) C:\WINDOWS\system32\LegacyNetUXHost.exe
2016-09-14 08:28 - 2016-09-07 00:37 - 00617984 _____ (Microsoft Corporation) C:\WINDOWS\system32\StorSvc.dll
2016-09-14 08:28 - 2016-09-07 00:37 - 00381952 _____ (Microsoft Corporation) C:\WINDOWS\system32\apprepsync.dll
2016-09-14 08:28 - 2016-09-07 00:37 - 00092160 _____ (Microsoft Corporation) C:\WINDOWS\system32\mshtmled.dll
2016-09-14 08:28 - 2016-09-07 00:36 - 00489984 _____ (Microsoft Corporation) C:\WINDOWS\system32\authfwcfg.dll
2016-09-14 08:28 - 2016-09-07 00:36 - 00457216 _____ (Microsoft Corporation) C:\WINDOWS\system32\azroleui.dll
2016-09-14 08:28 - 2016-09-07 00:36 - 00287744 _____ (Microsoft Corporation) C:\WINDOWS\system32\apprepapi.dll
2016-09-14 08:28 - 2016-09-07 00:36 - 00174592 _____ (Microsoft Corporation) C:\WINDOWS\system32\easwrt.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00814592 _____ (Microsoft Corporation) C:\WINDOWS\system32\msctfuimanager.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00394240 _____ (Microsoft Corporation) C:\WINDOWS\system32\Search.ProtocolHandler.MAPI2.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00393216 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wbemcomn.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00383488 _____ (Microsoft Corporation) C:\WINDOWS\system32\iedkcs32.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00339968 _____ (Microsoft Corporation) C:\WINDOWS\system32\SensorService.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00254464 _____ (Microsoft Corporation) C:\WINDOWS\system32\ExecModelClient.dll
2016-09-14 08:28 - 2016-09-07 00:35 - 00206848 _____ (Microsoft Corporation) C:\WINDOWS\system32\SharedStartModelShim.dll
2016-09-14 08:28 - 2016-09-07 00:34 - 00952320 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.PointOfService.dll
2016-09-14 08:28 - 2016-09-07 00:34 - 00727040 _____ (Microsoft Corporation) C:\WINDOWS\system32\nshwfp.dll
2016-09-14 08:28 - 2016-09-07 00:33 - 00316416 _____ (Microsoft Corporation) C:\WINDOWS\system32\sti.dll
2016-09-14 08:28 - 2016-09-07 00:32 - 00643584 _____ (Microsoft Corporation) C:\WINDOWS\system32\wiaservc.dll
2016-09-14 08:28 - 2016-09-07 00:32 - 00581632 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\apphelp.dll
2016-09-14 08:28 - 2016-09-07 00:32 - 00356864 _____ (Microsoft Corporation) C:\WINDOWS\system32\ActivationManager.dll
2016-09-14 08:28 - 2016-09-07 00:32 - 00334848 _____ (Microsoft Corporation) C:\WINDOWS\system32\SearchProtocolHost.exe
2016-09-14 08:28 - 2016-09-07 00:32 - 00275968 _____ (Microsoft Corporation) C:\WINDOWS\system32\facecredentialprovider.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00828928 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.AccountsControl.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00821760 _____ (Microsoft Corporation) C:\WINDOWS\system32\MrmIndexer.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00753664 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msctfuimanager.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00610304 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmdrmsdk.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00504320 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppReadiness.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00335872 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\iedkcs32.dll
2016-09-14 08:28 - 2016-09-07 00:31 - 00262144 _____ (Microsoft Corporation) C:\WINDOWS\system32\webcheck.dll
2016-09-14 08:28 - 2016-09-07 00:30 - 18676224 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\edgehtml.dll
2016-09-14 08:28 - 2016-09-07 00:30 - 02127360 _____ (Microsoft Corporation) C:\WINDOWS\system32\inetcpl.cpl
2016-09-14 08:28 - 2016-09-07 00:30 - 01707520 _____ (Microsoft Corporation) C:\WINDOWS\system32\msdtctm.dll
2016-09-14 08:28 - 2016-09-07 00:30 - 01001472 _____ (Microsoft Corporation) C:\WINDOWS\system32\schedsvc.dll
2016-09-14 08:28 - 2016-09-07 00:30 - 00904704 _____ (Microsoft Corporation) C:\WINDOWS\system32\rpcss.dll
2016-09-14 08:28 - 2016-09-07 00:30 - 00870400 _____ (Microsoft Corporation) C:\WINDOWS\system32\modernexecserver.dll
2016-09-14 08:28 - 2016-09-07 00:30 - 00784384 _____ (Microsoft Corporation) C:\WINDOWS\system32\msfeeds.dll
2016-09-14 08:28 - 2016-09-07 00:28 - 00938496 _____ (Microsoft Corporation) C:\WINDOWS\system32\SearchIndexer.exe
2016-09-14 08:28 - 2016-09-07 00:28 - 00780800 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\tdh.dll
2016-09-14 08:28 - 2016-09-07 00:28 - 00674816 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MiracastReceiver.dll
2016-09-14 08:28 - 2016-09-07 00:28 - 00400896 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\winspool.drv
2016-09-14 08:28 - 2016-09-07 00:28 - 00296448 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\sysdm.cpl
2016-09-14 08:28 - 2016-09-07 00:27 - 01743872 _____ (Microsoft Corporation) C:\WINDOWS\system32\wevtsvc.dll
2016-09-14 08:28 - 2016-09-07 00:27 - 01131520 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Media.Audio.dll
2016-09-14 08:28 - 2016-09-07 00:27 - 00963072 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wsp_health.dll
2016-09-14 08:28 - 2016-09-07 00:27 - 00552960 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\AppointmentApis.dll
2016-09-14 08:28 - 2016-09-07 00:27 - 00521728 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wmdrmsdk.dll
2016-09-14 08:28 - 2016-09-07 00:27 - 00329216 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\upnphost.dll
2016-09-14 08:28 - 2016-09-07 00:26 - 13392384 _____ (Microsoft Corporation) C:\WINDOWS\system32\ieframe.dll
2016-09-14 08:28 - 2016-09-07 00:26 - 02050048 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\inetcpl.cpl
2016-09-14 08:28 - 2016-09-07 00:26 - 01508352 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\winmsipc.dll
2016-09-14 08:28 - 2016-09-07 00:26 - 01063936 _____ (Microsoft Corporation) C:\WINDOWS\system32\comdlg32.dll
2016-09-14 08:28 - 2016-09-07 00:26 - 00854528 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Devices.Bluetooth.dll
2016-09-14 08:28 - 2016-09-07 00:26 - 00687616 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msfeeds.dll
2016-09-14 08:28 - 2016-09-07 00:26 - 00638464 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Networking.dll
2016-09-14 08:28 - 2016-09-07 00:25 - 01526272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ieapfltr.dll
2016-09-14 08:28 - 2016-09-07 00:25 - 01166848 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Pimstore.dll
2016-09-14 08:28 - 2016-09-07 00:25 - 00769536 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ContactApis.dll
2016-09-14 08:28 - 2016-09-07 00:24 - 03695104 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\D3DCompiler_47.dll
2016-09-14 08:28 - 2016-09-07 00:24 - 03428864 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Media.dll
2016-09-14 08:28 - 2016-09-07 00:24 - 01276928 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wsp_fs.dll
2016-09-14 08:28 - 2016-09-07 00:24 - 00785920 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mprddm.dll
2016-09-14 08:28 - 2016-09-07 00:23 - 00980480 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\winipcsecproc.dll
2016-09-14 08:28 - 2016-09-07 00:23 - 00838144 _____ (Microsoft Corporation) C:\WINDOWS\system32\uDWM.dll
2016-09-14 08:28 - 2016-09-07 00:23 - 00701952 _____ (Microsoft Corporation) C:\WINDOWS\system32\twinapi.dll
2016-09-14 08:28 - 2016-09-07 00:22 - 12134400 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ieframe.dll
2016-09-14 08:28 - 2016-09-07 00:22 - 02582016 _____ (Microsoft Corporation) C:\WINDOWS\system32\MFMediaEngine.dll
2016-09-14 08:28 - 2016-09-07 00:21 - 03046400 _____ (Microsoft Corporation) C:\WINDOWS\system32\xpsservices.dll
2016-09-14 08:28 - 2016-09-07 00:21 - 01797120 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Immersive.dll
2016-09-14 08:28 - 2016-09-07 00:20 - 02352128 _____ (Microsoft Corporation) C:\WINDOWS\system32\authui.dll
2016-09-14 08:28 - 2016-09-07 00:19 - 03663360 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\jscript9.dll
2016-09-14 08:28 - 2016-09-07 00:19 - 02102272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\xpsservices.dll
2016-09-14 08:28 - 2016-09-07 00:19 - 01072128 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Web.Http.dll
2016-09-14 08:28 - 2016-09-07 00:18 - 03577344 _____ (Microsoft Corporation) C:\WINDOWS\system32\tquery.dll
2016-09-14 08:28 - 2016-09-07 00:18 - 02876928 _____ (Microsoft Corporation) C:\WINDOWS\system32\Wpc.dll
2016-09-14 08:28 - 2016-09-07 00:18 - 00592384 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Web.dll
2016-09-14 08:28 - 2016-09-07 00:18 - 00451072 _____ (Microsoft Corporation) C:\WINDOWS\system32\XpsDocumentTargetPrint.dll
2016-09-14 08:28 - 2016-09-07 00:17 - 02679808 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\netshell.dll
2016-09-14 08:28 - 2016-09-07 00:17 - 02285568 _____ (Microsoft Corporation) C:\WINDOWS\system32\WpcWebSync.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 04412928 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ExplorerFrame.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 03671040 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msi.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 02911744 _____ (Microsoft Corporation) C:\WINDOWS\system32\CertEnroll.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 02746368 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.StateRepository.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 02597888 _____ (Microsoft Corporation) C:\WINDOWS\system32\mssrch.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 02280960 _____ (Microsoft Corporation) C:\WINDOWS\system32\wuaueng.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 02217984 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Wpc.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 01676800 _____ (Microsoft Corporation) C:\WINDOWS\system32\XpsPrint.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 01194496 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Xaml.Phone.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 01123328 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\XpsPrint.dll
2016-09-14 08:28 - 2016-09-07 00:16 - 00314880 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\XpsDocumentTargetPrint.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 07831552 _____ (Microsoft Corporation) C:\WINDOWS\system32\Chakra.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 05659136 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Chakra.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 02604032 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\CertEnroll.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 02055168 _____ (Microsoft Corporation) C:\WINDOWS\system32\OpcServices.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 00835072 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Media.Streaming.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 00573440 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\UserLanguagesCpl.dll
2016-09-14 08:28 - 2016-09-07 00:15 - 00416256 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\hnetcfg.dll
2016-09-14 08:28 - 2016-09-07 00:14 - 06743040 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mstscax.dll
2016-09-14 08:28 - 2016-09-07 00:14 - 04895232 _____ (Microsoft Corporation) C:\WINDOWS\system32\jscript9.dll
2016-09-14 08:28 - 2016-09-07 00:14 - 01946112 _____ (Microsoft Corporation) C:\WINDOWS\system32\dwmcore.dll
2016-09-14 08:28 - 2016-09-07 00:13 - 04171264 _____ (Microsoft Corporation) C:\WINDOWS\system32\rdpcorets.dll
2016-09-14 08:28 - 2016-09-07 00:13 - 02874880 _____ (Microsoft Corporation) C:\WINDOWS\system32\mmcndmgr.dll
2016-09-14 08:28 - 2016-09-07 00:11 - 03065344 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mstsc.exe
2016-09-14 08:27 - 2016-09-07 01:39 - 00845568 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MrmCoreR.dll
2016-09-14 08:27 - 2016-09-07 01:39 - 00754664 _____ (Microsoft Corporation) C:\WINDOWS\system32\CoreMessaging.dll
2016-09-14 08:27 - 2016-09-07 01:39 - 00620176 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\kernel32.dll
2016-09-14 08:27 - 2016-09-07 01:34 - 02587696 _____ (Microsoft Corporation) C:\WINDOWS\system32\msxml6.dll
2016-09-14 08:27 - 2016-09-07 01:33 - 01297760 _____ (Microsoft Corporation) C:\WINDOWS\system32\LicenseManager.dll
2016-09-14 08:27 - 2016-09-07 01:33 - 00986976 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\LicenseManager.dll
2016-09-14 08:27 - 2016-09-07 01:27 - 00538632 _____ (Microsoft Corporation) C:\WINDOWS\system32\WWanAPI.dll
2016-09-14 08:27 - 2016-09-07 01:27 - 00413536 _____ (Microsoft Corporation) C:\WINDOWS\system32\wifitask.exe
2016-09-14 08:27 - 2016-09-07 01:26 - 00586200 _____ (Microsoft Corporation) C:\WINDOWS\system32\mf.dll
2016-09-14 08:27 - 2016-09-07 01:24 - 03693064 _____ (Microsoft Corporation) C:\WINDOWS\system32\iertutil.dll
2016-09-14 08:27 - 2016-09-07 01:24 - 00808288 _____ (Microsoft Corporation) C:\WINDOWS\system32\WWAHost.exe
2016-09-14 08:27 - 2016-09-07 01:24 - 00501600 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\NetSetupEngine.dll
2016-09-14 08:27 - 2016-09-07 01:24 - 00355672 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\netcfgx.dll
2016-09-14 08:27 - 2016-09-07 01:23 - 22561256 _____ (Microsoft Corporation) C:\WINDOWS\system32\shell32.dll
2016-09-14 08:27 - 2016-09-07 01:23 - 06605544 _____ (Microsoft Corporation) C:\WINDOWS\system32\windows.storage.dll
2016-09-14 08:27 - 2016-09-07 01:23 - 06536248 _____ (Microsoft Corporation) C:\WINDOWS\system32\sppsvc.exe
2016-09-14 08:27 - 2016-09-07 01:22 - 02937384 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\iertutil.dll
2016-09-14 08:27 - 2016-09-07 01:22 - 01085728 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\webservices.dll
2016-09-14 08:27 - 2016-09-07 01:22 - 00604920 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\cng.sys
2016-09-14 08:27 - 2016-09-07 01:12 - 02195632 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\d3d10warp.dll
2016-09-14 08:27 - 2016-09-07 01:08 - 00116216 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\sspicli.dll
2016-09-14 08:27 - 2016-09-07 00:52 - 01035776 _____ (Microsoft Corporation) C:\WINDOWS\system32\XboxNetApiSvc.dll
2016-09-14 08:27 - 2016-09-07 00:52 - 00084480 _____ (Microsoft Corporation) C:\WINDOWS\system32\rdpudd.dll
2016-09-14 08:27 - 2016-09-07 00:49 - 00649216 _____ (Microsoft Corporation) C:\WINDOWS\system32\ngcsvc.dll
2016-09-14 08:27 - 2016-09-07 00:48 - 00957952 _____ (Microsoft Corporation) C:\WINDOWS\system32\IKEEXT.DLL
2016-09-14 08:27 - 2016-09-07 00:47 - 00824320 _____ (Microsoft Corporation) C:\WINDOWS\system32\WpcWebFilter.dll
2016-09-14 08:27 - 2016-09-07 00:46 - 00088576 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\olepro32.dll
2016-09-14 08:27 - 2016-09-07 00:44 - 00134656 _____ (Microsoft Corporation) C:\WINDOWS\system32\wificonnapi.dll
2016-09-14 08:27 - 2016-09-07 00:44 - 00069120 _____ (Microsoft Corporation) C:\WINDOWS\system32\pngfilt.dll
2016-09-14 08:27 - 2016-09-07 00:42 - 00572928 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WpcWebFilter.dll
2016-09-14 08:27 - 2016-09-07 00:42 - 00050176 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MosHostClient.dll
2016-09-14 08:27 - 2016-09-07 00:41 - 00066048 _____ (Microsoft Corporation) C:\WINDOWS\system32\OnDemandConnRouteHelper.dll
2016-09-14 08:27 - 2016-09-07 00:41 - 00056832 _____ (Microsoft Corporation) C:\WINDOWS\system32\fwcfg.dll
2016-09-14 08:27 - 2016-09-07 00:41 - 00047616 _____ (Microsoft Corporation) C:\WINDOWS\system32\deviceassociation.dll
2016-09-14 08:27 - 2016-09-07 00:41 - 00025600 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\odbcconf.dll
2016-09-14 08:27 - 2016-09-07 00:40 - 00027648 _____ (Microsoft Corporation) C:\WINDOWS\system32\CheckNetIsolation.exe
2016-09-14 08:27 - 2016-09-07 00:39 - 00059904 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\udhisapi.dll
2016-09-14 08:27 - 2016-09-07 00:38 - 00254464 _____ (Microsoft Corporation) C:\WINDOWS\system32\prnntfy.dll
2016-09-14 08:27 - 2016-09-07 00:38 - 00059392 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MosStorage.dll
2016-09-14 08:27 - 2016-09-07 00:38 - 00038912 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wsmprovhost.exe
2016-09-14 08:27 - 2016-09-07 00:38 - 00035840 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\upnpcont.exe
2016-09-14 08:27 - 2016-09-07 00:37 - 00435712 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.AllJoyn.dll
2016-09-14 08:27 - 2016-09-07 00:37 - 00145408 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WsmAuto.dll
2016-09-14 08:27 - 2016-09-07 00:37 - 00087040 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MapsBtSvc.dll
2016-09-14 08:27 - 2016-09-07 00:37 - 00035328 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\deviceassociation.dll
2016-09-14 08:27 - 2016-09-07 00:37 - 00026624 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WsmAgent.dll
2016-09-14 08:27 - 2016-09-07 00:36 - 06572032 _____ (Microsoft Corporation) C:\WINDOWS\system32\wwanmm.dll
2016-09-14 08:27 - 2016-09-07 00:36 - 01568768 _____ (Microsoft Corporation) C:\WINDOWS\system32\msdt.exe
2016-09-14 08:27 - 2016-09-07 00:36 - 01051136 _____ (Microsoft Corporation) C:\WINDOWS\system32\DiagCpl.dll
2016-09-14 08:27 - 2016-09-07 00:36 - 00764928 _____ (Microsoft Corporation) C:\WINDOWS\system32\Chakradiag.dll
2016-09-14 08:27 - 2016-09-07 00:36 - 00319488 _____ (Microsoft Corporation) C:\WINDOWS\system32\dot3ui.dll
2016-09-14 08:27 - 2016-09-07 00:36 - 00200192 _____ (Microsoft Corporation) C:\WINDOWS\system32\WUDFPlatform.dll
2016-09-14 08:27 - 2016-09-07 00:36 - 00102912 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\shsetup.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00704000 _____ (Microsoft Corporation) C:\WINDOWS\system32\CellularAPI.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00591872 _____ (Microsoft Corporation) C:\WINDOWS\system32\SmsRouterSvc.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00577536 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.ApplicationModel.Wallet.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00458752 _____ (Microsoft Corporation) C:\WINDOWS\system32\PlayToDevice.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00256512 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\unimdm.tsp
2016-09-14 08:27 - 2016-09-07 00:35 - 00119296 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Media.Streaming.ps.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00070656 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\AppCapture.dll
2016-09-14 08:27 - 2016-09-07 00:35 - 00052736 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\vsstrace.dll
2016-09-14 08:27 - 2016-09-07 00:34 - 00387072 _____ (Microsoft Corporation) C:\WINDOWS\system32\qdvd.dll
2016-09-14 08:27 - 2016-09-07 00:34 - 00371712 _____ (Microsoft Corporation) C:\WINDOWS\system32\MDEServer.exe
2016-09-14 08:27 - 2016-09-07 00:34 - 00344064 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.Picker.dll
2016-09-14 08:27 - 2016-09-07 00:34 - 00305152 _____ (Microsoft Corporation) C:\WINDOWS\system32\edputil.dll
2016-09-14 08:27 - 2016-09-07 00:33 - 00847360 _____ (Microsoft Corporation) C:\WINDOWS\system32\netlogon.dll
2016-09-14 08:27 - 2016-09-07 00:33 - 00576000 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Networking.UX.EapRequestHandler.dll
2016-09-14 08:27 - 2016-09-07 00:33 - 00330240 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.ApplicationModel.Store.TestingFramework.dll
2016-09-14 08:27 - 2016-09-07 00:33 - 00290304 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WmpDui.dll
2016-09-14 08:27 - 2016-09-07 00:33 - 00238080 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WsmWmiPl.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 01048576 _____ (Microsoft Corporation) C:\WINDOWS\system32\WebcamUi.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 00947200 _____ (Microsoft Corporation) C:\WINDOWS\system32\rasgcw.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 00738816 _____ (Microsoft Corporation) C:\WINDOWS\system32\SmartCardSimulator.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 00517632 _____ (Microsoft Corporation) C:\WINDOWS\system32\winspool.drv
2016-09-14 08:27 - 2016-09-07 00:32 - 00466944 _____ (Microsoft Corporation) C:\WINDOWS\system32\wwanconn.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 00444928 _____ (Microsoft Corporation) C:\WINDOWS\system32\das.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 00432640 _____ (Microsoft Corporation) C:\WINDOWS\system32\CredProvDataModel.dll
2016-09-14 08:27 - 2016-09-07 00:32 - 00407040 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\srv.sys
2016-09-14 08:27 - 2016-09-07 00:31 - 01216512 _____ (Microsoft Corporation) C:\WINDOWS\system32\netcenter.dll
2016-09-14 08:27 - 2016-09-07 00:31 - 00859136 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.ApplicationModel.Store.dll
2016-09-14 08:27 - 2016-09-07 00:31 - 00578560 _____ (Microsoft Corporation) C:\WINDOWS\system32\mscms.dll
2016-09-14 08:27 - 2016-09-07 00:31 - 00541184 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\GamePanel.exe
2016-09-14 08:27 - 2016-09-07 00:31 - 00538112 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Cortana.Desktop.dll
2016-09-14 08:27 - 2016-09-07 00:31 - 00435200 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.ApplicationModel.Wallet.dll
2016-09-14 08:27 - 2016-09-07 00:31 - 00334336 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\bcastdvr.exe
2016-09-14 08:27 - 2016-09-07 00:31 - 00114688 _____ (Microsoft Corporation) C:\WINDOWS\system32\offlinelsa.dll
2016-09-14 08:27 - 2016-09-07 00:30 - 02476032 _____ (Microsoft Corporation) C:\WINDOWS\system32\MSAJApi.dll
2016-09-14 08:27 - 2016-09-07 00:30 - 00698368 _____ (Microsoft Corporation) C:\WINDOWS\system32\PlayToManager.dll
2016-09-14 08:27 - 2016-09-07 00:30 - 00436224 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mprdim.dll
2016-09-14 08:27 - 2016-09-07 00:30 - 00349696 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MapConfiguration.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 02624512 _____ (Microsoft Corporation) C:\WINDOWS\system32\InputService.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 01319424 _____ (Microsoft Corporation) C:\WINDOWS\system32\wifinetworkmanager.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 01213440 _____ (Microsoft Corporation) C:\WINDOWS\system32\wwansvc.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00888320 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Networking.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00841728 _____ (Microsoft Corporation) C:\WINDOWS\system32\win32spl.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00669696 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.Sensors.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00499712 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MessagingDataModel2.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00442368 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\dlnashext.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00286208 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\mrxsmb10.sys
2016-09-14 08:27 - 2016-09-07 00:29 - 00250880 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.ApplicationModel.Store.TestingFramework.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00242688 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\sti.dll
2016-09-14 08:27 - 2016-09-07 00:29 - 00199680 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SyncSettings.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 01752576 _____ (Microsoft Corporation) C:\WINDOWS\system32\ieapfltr.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 01291776 _____ (Microsoft Corporation) C:\WINDOWS\system32\werconcpl.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00879616 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WebcamUi.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00846336 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\rasgcw.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00800768 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\JpMapControl.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00755712 _____ (Microsoft Corporation) C:\WINDOWS\system32\spoolsv.exe
2016-09-14 08:27 - 2016-09-07 00:28 - 00673280 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00654336 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\winipcsecproc_ssp.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00645120 _____ (Microsoft Corporation) C:\WINDOWS\system32\wpnapps.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00614400 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\winhttp.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00381952 _____ (Microsoft Corporation) C:\WINDOWS\system32\wuuhext.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00337920 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Geolocation.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00334848 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\CredProvDataModel.dll
2016-09-14 08:27 - 2016-09-07 00:28 - 00284160 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\eappcfg.dll
2016-09-14 08:27 - 2016-09-07 00:27 - 01139712 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\vssapi.dll
2016-09-14 08:27 - 2016-09-07 00:27 - 00784896 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\NMAA.dll
2016-09-14 08:27 - 2016-09-07 00:27 - 00708608 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\CPFilters.dll
2016-09-14 08:27 - 2016-09-07 00:27 - 00549888 _____ (Microsoft Corporation) C:\WINDOWS\system32\SearchFolder.dll
2016-09-14 08:27 - 2016-09-07 00:27 - 00230400 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\webcheck.dll
2016-09-14 08:27 - 2016-09-07 00:26 - 01588224 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msxml3.dll
2016-09-14 08:27 - 2016-09-07 00:26 - 01497088 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WMPDMC.exe
2016-09-14 08:27 - 2016-09-07 00:26 - 00711680 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MapControlCore.dll
2016-09-14 08:27 - 2016-09-07 00:26 - 00482816 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\duser.dll
2016-09-14 08:27 - 2016-09-07 00:26 - 00321024 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\syncutil.dll
2016-09-14 08:27 - 2016-09-07 00:25 - 06312448 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Search.dll
2016-09-14 08:27 - 2016-09-07 00:25 - 06296064 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mos.dll
2016-09-14 08:27 - 2016-09-07 00:25 - 04404736 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Search.dll
2016-09-14 08:27 - 2016-09-07 00:25 - 01944576 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\InputService.dll
2016-09-14 08:27 - 2016-09-07 00:25 - 00888832 _____ (Microsoft Corporation) C:\WINDOWS\system32\printfilterpipelinesvc.exe
2016-09-14 08:27 - 2016-09-07 00:25 - 00501760 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Devices.Sensors.dll
2016-09-14 08:27 - 2016-09-07 00:23 - 01562112 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mmc.exe
2016-09-14 08:27 - 2016-09-07 00:23 - 01309696 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wdc.dll
2016-09-14 08:27 - 2016-09-07 00:23 - 00787456 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Web.dll
2016-09-14 08:27 - 2016-09-07 00:22 - 02106368 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\storagewmi.dll
2016-09-14 08:27 - 2016-09-07 00:21 - 02527232 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mispace.dll
2016-09-14 08:27 - 2016-09-07 00:21 - 01410560 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Web.Http.dll
2016-09-14 08:27 - 2016-09-07 00:20 - 00870400 _____ (Microsoft Corporation) C:\WINDOWS\system32\wpncore.dll
2016-09-14 08:27 - 2016-09-07 00:19 - 05325824 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Data.Pdf.dll
2016-09-14 08:27 - 2016-09-07 00:19 - 01388544 _____ (Microsoft Corporation) C:\WINDOWS\system32\lsasrv.dll
2016-09-14 08:27 - 2016-09-07 00:19 - 00503296 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SettingSync.dll
2016-09-14 08:27 - 2016-09-07 00:18 - 07536640 _____ (Microsoft Corporation) C:\WINDOWS\system32\mstscax.dll
2016-09-14 08:27 - 2016-09-07 00:18 - 05205504 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\BingMaps.dll
2016-09-14 08:27 - 2016-09-07 00:18 - 04826624 _____ (Microsoft Corporation) C:\WINDOWS\system32\ExplorerFrame.dll
2016-09-14 08:27 - 2016-09-07 00:18 - 00450560 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SyncController.dll
2016-09-14 08:27 - 2016-09-07 00:17 - 03459584 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\UIRibbon.dll
2016-09-14 08:27 - 2016-09-07 00:17 - 02175488 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppXDeploymentServer.dll
2016-09-14 08:27 - 2016-09-07 00:17 - 01526784 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Xaml.Phone.dll
2016-09-14 08:27 - 2016-09-07 00:17 - 01502208 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\urlmon.dll
2016-09-14 08:27 - 2016-09-07 00:16 - 02444288 _____ (Microsoft Corporation) C:\WINDOWS\system32\twinui.appcore.dll
2016-09-14 08:27 - 2016-09-07 00:16 - 02361856 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mmcndmgr.dll
2016-09-14 08:27 - 2016-09-07 00:16 - 02155008 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\authui.dll
2016-09-14 08:27 - 2016-09-07 00:16 - 00232448 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\notepad.exe
2016-09-14 08:27 - 2016-09-07 00:15 - 02067968 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppXDeploymentExtensions.dll
2016-09-14 08:27 - 2016-09-07 00:15 - 01626112 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\dwmcore.dll
2016-09-14 08:27 - 2016-09-07 00:15 - 01448960 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\dui70.dll
2016-09-14 08:27 - 2016-09-07 00:15 - 01249280 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\usercpl.dll
2016-09-14 08:27 - 2016-09-07 00:15 - 01121792 _____ (Microsoft Corporation) C:\WINDOWS\system32\localspl.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 03351040 _____ (Microsoft Corporation) C:\WINDOWS\system32\msi.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 03078656 _____ (Microsoft Corporation) C:\WINDOWS\system32\wininet.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 02573824 _____ (Microsoft Corporation) C:\WINDOWS\system32\WsmSvc.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 02553856 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wininet.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 02177024 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WsmSvc.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 01708032 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ActiveSyncProvider.dll
2016-09-14 08:27 - 2016-09-07 00:14 - 01487872 _____ (Microsoft Corporation) C:\WINDOWS\system32\SpeechPal.dll
2016-09-14 08:27 - 2016-09-07 00:12 - 02180096 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.StateRepository.dll
2016-09-14 08:27 - 2016-09-07 00:11 - 03053568 _____ (Microsoft Corporation) C:\WINDOWS\system32\rdpcore.dll
2016-09-14 08:27 - 2016-09-07 00:10 - 01035776 _____ (Microsoft Corporation) C:\WINDOWS\system32\TSWorkspace.dll
2016-09-14 08:27 - 2016-09-07 00:10 - 00341504 _____ (Microsoft Corporation) C:\WINDOWS\system32\RADCUI.dll
2016-09-14 08:27 - 2016-09-04 20:37 - 00445765 _____ C:\WINDOWS\system32\ApnDatabase.xml
2016-09-14 08:26 - 2016-09-07 01:39 - 01317640 _____ (Microsoft Corporation) C:\WINDOWS\system32\winload.efi
2016-09-14 08:26 - 2016-09-07 01:39 - 01142560 _____ (Microsoft Corporation) C:\WINDOWS\system32\winload.exe
2016-09-14 08:26 - 2016-09-07 01:39 - 01030408 _____ (Microsoft Corporation) C:\WINDOWS\system32\winresume.efi
2016-09-14 08:26 - 2016-09-07 01:39 - 00875480 _____ (Microsoft Corporation) C:\WINDOWS\system32\winresume.exe
2016-09-14 08:26 - 2016-09-07 01:39 - 00799568 _____ (Microsoft Corporation) C:\WINDOWS\system32\oleaut32.dll
2016-09-14 08:26 - 2016-09-07 01:39 - 00601744 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\oleaut32.dll
2016-09-14 08:26 - 2016-09-07 01:39 - 00175120 _____ (Microsoft Corporation) C:\WINDOWS\system32\sspicli.dll
2016-09-14 08:26 - 2016-09-07 01:37 - 00129888 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\ksecdd.sys
2016-09-14 08:26 - 2016-09-07 01:36 - 00405856 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\FWPKCLNT.SYS
2016-09-14 08:26 - 2016-09-07 01:33 - 02026736 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msxml6.dll
2016-09-14 08:26 - 2016-09-07 01:26 - 00131424 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\ufxsynopsys.sys
2016-09-14 08:26 - 2016-09-07 01:25 - 01447776 _____ (Microsoft Corporation) C:\WINDOWS\system32\webservices.dll
2016-09-14 08:26 - 2016-09-07 01:25 - 01322248 _____ (Microsoft Corporation) C:\WINDOWS\system32\ole32.dll
2016-09-14 08:26 - 2016-09-07 01:24 - 02180128 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mfcore.dll
2016-09-14 08:26 - 2016-09-07 01:24 - 01118200 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mfnetsrc.dll
2016-09-14 08:26 - 2016-09-07 01:21 - 04074160 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\explorer.exe
2016-09-14 08:26 - 2016-09-07 01:21 - 00465760 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SettingSyncHost.exe
2016-09-14 08:26 - 2016-09-07 01:20 - 01355336 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\propsys.dll
2016-09-14 08:26 - 2016-09-07 01:16 - 02773088 _____ (Microsoft Corporation) C:\WINDOWS\system32\d3d11.dll
2016-09-14 08:26 - 2016-09-07 01:15 - 01415200 _____ (Microsoft Corporation) C:\WINDOWS\system32\msctf.dll
2016-09-14 08:26 - 2016-09-07 01:13 - 01865584 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\d3d9.dll
2016-09-14 08:26 - 2016-09-07 01:12 - 01522152 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WindowsCodecs.dll
2016-09-14 08:26 - 2016-09-07 01:11 - 00057912 _____ (Microsoft Corporation) C:\WINDOWS\system32\lsass.exe
2016-09-14 08:26 - 2016-09-07 01:07 - 01951848 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\hevcdecoder.dll
2016-09-14 08:26 - 2016-09-07 00:51 - 00089088 _____ (Microsoft Corporation) C:\WINDOWS\system32\MapsCSP.dll
2016-09-14 08:26 - 2016-09-07 00:47 - 00066560 _____ (Microsoft Corporation) C:\WINDOWS\system32\MosHostClient.dll
2016-09-14 08:26 - 2016-09-07 00:46 - 00031232 _____ (Microsoft Corporation) C:\WINDOWS\system32\odbcconf.dll
2016-09-14 08:26 - 2016-09-07 00:45 - 00086528 _____ (Microsoft Corporation) C:\WINDOWS\system32\spcompat.dll
2016-09-14 08:26 - 2016-09-07 00:45 - 00037376 _____ (Microsoft Corporation) C:\WINDOWS\system32\cmintegrator.dll
2016-09-14 08:26 - 2016-09-07 00:44 - 00028672 _____ (Microsoft Corporation) C:\WINDOWS\system32\mapsupdatetask.dll
2016-09-14 08:26 - 2016-09-07 00:44 - 00014848 _____ (Microsoft Corporation) C:\WINDOWS\system32\IconCodecService.dll
2016-09-14 08:26 - 2016-09-07 00:43 - 00584704 _____ (Microsoft Corporation) C:\WINDOWS\system32\UIRibbonRes.dll
2016-09-14 08:26 - 2016-09-07 00:43 - 00074240 _____ (Microsoft Corporation) C:\WINDOWS\system32\MosStorage.dll
2016-09-14 08:26 - 2016-09-07 00:43 - 00037376 _____ (Microsoft Corporation) C:\WINDOWS\system32\wsmprovhost.exe
2016-09-14 08:26 - 2016-09-07 00:43 - 00015872 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\MTConfig.sys
2016-09-14 08:26 - 2016-09-07 00:42 - 00163328 _____ (Microsoft Corporation) C:\WINDOWS\system32\WsmAuto.dll
2016-09-14 08:26 - 2016-09-07 00:42 - 00140288 _____ (Microsoft Corporation) C:\WINDOWS\system32\WcnApi.dll
2016-09-14 08:26 - 2016-09-07 00:42 - 00120320 _____ (Microsoft Corporation) C:\WINDOWS\system32\MapsBtSvc.dll
2016-09-14 08:26 - 2016-09-07 00:42 - 00117760 _____ (Microsoft Corporation) C:\WINDOWS\system32\dafWCN.dll
2016-09-14 08:26 - 2016-09-07 00:42 - 00112640 _____ (Microsoft Corporation) C:\WINDOWS\system32\fdWCN.dll
2016-09-14 08:26 - 2016-09-07 00:42 - 00031744 _____ (Microsoft Corporation) C:\WINDOWS\system32\WsmAgent.dll
2016-09-14 08:26 - 2016-09-07 00:41 - 00125952 _____ (Microsoft Corporation) C:\WINDOWS\system32\MediaFoundation.DefaultPerceptionProvider.dll
2016-09-14 08:26 - 2016-09-07 00:41 - 00072704 _____ (Microsoft Corporation) C:\WINDOWS\system32\moshost.dll
2016-09-14 08:26 - 2016-09-07 00:40 - 00471040 _____ (Microsoft Corporation) C:\WINDOWS\system32\wbemcomn.dll
2016-09-14 08:26 - 2016-09-07 00:40 - 00086528 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppCapture.dll
2016-09-14 08:26 - 2016-09-07 00:39 - 00379392 _____ (Microsoft Corporation) C:\WINDOWS\system32\usocore.dll
2016-09-14 08:26 - 2016-09-07 00:39 - 00270848 _____ (Microsoft Corporation) C:\WINDOWS\system32\moshostcore.dll
2016-09-14 08:26 - 2016-09-07 00:39 - 00096256 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\VoipRT.dll
2016-09-14 08:26 - 2016-09-07 00:39 - 00053760 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Cortana.ProxyStub.dll
2016-09-14 08:26 - 2016-09-07 00:38 - 00584704 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\UIRibbonRes.dll
2016-09-14 08:26 - 2016-09-07 00:38 - 00288768 _____ (Microsoft Corporation) C:\WINDOWS\system32\WsmWmiPl.dll
2016-09-14 08:26 - 2016-09-07 00:38 - 00157184 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingsHandlers_Geolocation.dll
2016-09-14 08:26 - 2016-09-07 00:37 - 00642048 _____ (Microsoft Corporation) C:\WINDOWS\system32\enterprisecsps.dll
2016-09-14 08:26 - 2016-09-07 00:37 - 00373248 _____ (Microsoft Corporation) C:\WINDOWS\system32\WmpDui.dll
2016-09-14 08:26 - 2016-09-07 00:37 - 00274944 _____ (Microsoft Corporation) C:\WINDOWS\system32\DisplayManager.dll
2016-09-14 08:26 - 2016-09-07 00:37 - 00126464 _____ (Microsoft Corporation) C:\WINDOWS\system32\dialserver.dll
2016-09-14 08:26 - 2016-09-07 00:37 - 00100352 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WcnApi.dll
2016-09-14 08:26 - 2016-09-07 00:37 - 00095744 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\fdWCN.dll
2016-09-14 08:26 - 2016-09-07 00:36 - 00752128 _____ (Microsoft Corporation) C:\WINDOWS\system32\PhoneService.dll
2016-09-14 08:26 - 2016-09-07 00:36 - 00414720 _____ (Microsoft Corporation) C:\WINDOWS\system32\bcastdvr.exe
2016-09-14 08:26 - 2016-09-07 00:36 - 00047104 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\fwcfg.dll
2016-09-14 08:26 - 2016-09-07 00:35 - 00715264 _____ (Microsoft Corporation) C:\WINDOWS\system32\GamePanel.exe
2016-09-14 08:26 - 2016-09-07 00:35 - 00522240 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.WiFiDirect.dll
2016-09-14 08:26 - 2016-09-07 00:35 - 00460800 _____ (Microsoft Corporation) C:\WINDOWS\system32\MapConfiguration.dll
2016-09-14 08:26 - 2016-09-07 00:35 - 00412672 _____ (Microsoft Corporation) C:\WINDOWS\system32\wlanui.dll
2016-09-14 08:26 - 2016-09-07 00:35 - 00205312 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\oemlicense.dll
2016-09-14 08:26 - 2016-09-07 00:35 - 00115712 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mmcshext.dll
2016-09-14 08:26 - 2016-09-07 00:35 - 00024064 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\CheckNetIsolation.exe
2016-09-14 08:26 - 2016-09-07 00:34 - 00630784 _____ (Microsoft Corporation) C:\WINDOWS\system32\MessagingDataModel2.dll
2016-09-14 08:26 - 2016-09-07 00:34 - 00619520 _____ (Microsoft Corporation) C:\WINDOWS\system32\efswrt.dll
2016-09-14 08:26 - 2016-09-07 00:34 - 00510464 _____ (Microsoft Corporation) C:\WINDOWS\system32\WlanMediaManager.dll
2016-09-14 08:26 - 2016-09-07 00:34 - 00497664 _____ (Microsoft Corporation) C:\WINDOWS\system32\WalletService.dll
2016-09-14 08:26 - 2016-09-07 00:34 - 00300032 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mmcbase.dll
2016-09-14 08:26 - 2016-09-07 00:34 - 00278016 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Internal.Management.dll
2016-09-14 08:26 - 2016-09-07 00:34 - 00163840 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\cic.dll
2016-09-14 08:26 - 2016-09-07 00:33 - 00904704 _____ (Microsoft Corporation) C:\WINDOWS\system32\azroles.dll
2016-09-14 08:26 - 2016-09-07 00:33 - 00321536 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Devices.AllJoyn.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 04213248 _____ (Microsoft Corporation) C:\WINDOWS\system32\WlanMM.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 01294336 _____ (Microsoft Corporation) C:\WINDOWS\system32\wcnwiz.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00757248 _____ (Microsoft Corporation) C:\WINDOWS\system32\winipcsecproc_ssp.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00651776 _____ (Microsoft Corporation) C:\WINDOWS\system32\UserLanguagesCpl.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00506880 _____ (Microsoft Corporation) C:\WINDOWS\system32\tileobjserver.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00471040 _____ (Microsoft Corporation) C:\WINDOWS\system32\wcncsvc.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00386048 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Devices.LowLevel.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00339456 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\azroleui.dll
2016-09-14 08:26 - 2016-09-07 00:32 - 00310784 _____ (Microsoft Corporation) C:\WINDOWS\system32\sysdm.cpl
2016-09-14 08:26 - 2016-09-07 00:31 - 09920512 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\twinui.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 01985024 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\certmgr.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 01094656 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Networking.Vpn.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 01056256 _____ (Microsoft Corporation) C:\WINDOWS\system32\JpMapControl.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00988160 _____ (Microsoft Corporation) C:\WINDOWS\system32\NMAA.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00970752 _____ (Microsoft Corporation) C:\WINDOWS\system32\nettrace.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00941568 _____ (Microsoft Corporation) C:\WINDOWS\system32\MiracastReceiver.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00900608 _____ (Microsoft Corporation) C:\WINDOWS\system32\CPFilters.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00852992 _____ (Microsoft Corporation) C:\WINDOWS\system32\MapsStore.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00839680 _____ (Microsoft Corporation) C:\WINDOWS\system32\comuid.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00607232 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppxApplicabilityEngine.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00519680 _____ (Microsoft Corporation) C:\WINDOWS\system32\WLanConn.dll
2016-09-14 08:26 - 2016-09-07 00:31 - 00358912 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\authfwcfg.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 01575936 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Media.Speech.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 01500160 _____ (Microsoft Corporation) C:\WINDOWS\system32\RecoveryDrive.exe
2016-09-14 08:26 - 2016-09-07 00:30 - 01144320 _____ (Microsoft Corporation) C:\WINDOWS\system32\qmgr.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00982016 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppxPackaging.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00939520 _____ (Microsoft Corporation) C:\WINDOWS\system32\MapControlCore.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00817152 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Storage.Search.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00585728 _____ (Microsoft Corporation) C:\WINDOWS\system32\ieui.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00576000 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\nshwfp.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00569856 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\qdvd.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00471552 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\filemgmt.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00368128 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Graphics.dll
2016-09-14 08:26 - 2016-09-07 00:30 - 00294912 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\PhoneOm.dll
2016-09-14 08:26 - 2016-09-07 00:29 - 07977984 _____ (Microsoft Corporation) C:\WINDOWS\system32\mos.dll
2016-09-14 08:26 - 2016-09-07 00:29 - 01902592 _____ (Microsoft Corporation) C:\WINDOWS\system32\msxml3.dll
2016-09-14 08:26 - 2016-09-07 00:29 - 01465344 _____ (Microsoft Corporation) C:\WINDOWS\system32\VSSVC.exe
2016-09-14 08:26 - 2016-09-07 00:29 - 00553472 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\cryptui.dll
2016-09-14 08:26 - 2016-09-07 00:29 - 00268288 _____ (Microsoft Corporation) C:\WINDOWS\system32\updatehandlers.dll
2016-09-14 08:26 - 2016-09-07 00:28 - 04143104 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WlanMM.dll
2016-09-14 08:26 - 2016-09-07 00:28 - 01648640 _____ (Microsoft Corporation) C:\WINDOWS\system32\comsvcs.dll
2016-09-14 08:26 - 2016-09-07 00:28 - 01226752 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wcnwiz.dll
2016-09-14 08:26 - 2016-09-07 00:28 - 00638976 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MrmIndexer.dll
2016-09-14 08:26 - 2016-09-07 00:28 - 00489984 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mbsmsapi.dll
2016-09-14 08:26 - 2016-09-07 00:28 - 00413696 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WLanConn.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 01872896 _____ (Microsoft Corporation) C:\WINDOWS\system32\workfolderssvc.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 01424384 _____ (Microsoft Corporation) C:\WINDOWS\system32\wdc.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 00502272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mscms.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 00477184 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ieui.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 00458752 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wlidprov.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 00400896 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\OneDriveSettingSyncProvider.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 00248320 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\resutils.dll
2016-09-14 08:26 - 2016-09-07 00:27 - 00100864 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\offlinelsa.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 02881536 _____ (Microsoft Corporation) C:\WINDOWS\system32\storagewmi.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 01915392 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MSAJApi.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 01537536 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\pla.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 00736768 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SmartcardCredentialProvider.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 00673280 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MbaeApiPublic.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 00645632 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Storage.Search.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 00501760 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\vbscript.dll
2016-09-14 08:26 - 2016-09-07 00:26 - 00488960 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\clusapi.dll
2016-09-14 08:26 - 2016-09-07 00:25 - 00207872 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\licensingdiag.exe
2016-09-14 08:26 - 2016-09-07 00:24 - 07200256 _____ (Microsoft Corporation) C:\WINDOWS\system32\BingMaps.dll
2016-09-14 08:26 - 2016-09-07 00:24 - 00489984 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ShareHost.dll
2016-09-14 08:26 - 2016-09-07 00:24 - 00460800 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SearchFolder.dll
2016-09-14 08:26 - 2016-09-07 00:22 - 01987072 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\DWrite.dll
2016-09-14 08:26 - 2016-09-07 00:22 - 01297408 _____ (Microsoft Corporation) C:\WINDOWS\system32\SensorDataService.exe
2016-09-14 08:26 - 2016-09-07 00:22 - 00778240 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MsSpellCheckingFacility.dll
2016-09-14 08:26 - 2016-09-07 00:21 - 01063936 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\gpedit.dll
2016-09-14 08:26 - 2016-09-07 00:21 - 00639488 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\TokenBroker.dll
2016-09-14 08:26 - 2016-09-07 00:20 - 00900608 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Networking.BackgroundTransfer.dll
2016-09-14 08:26 - 2016-09-07 00:20 - 00882688 _____ (Microsoft Corporation) C:\WINDOWS\system32\ntshrui.dll
2016-09-14 08:26 - 2016-09-07 00:20 - 00417792 _____ (Microsoft Corporation) C:\WINDOWS\system32\dmenrollengine.dll
2016-09-14 08:26 - 2016-09-07 00:19 - 04169728 _____ (Microsoft Corporation) C:\WINDOWS\system32\UIRibbon.dll
2016-09-14 08:26 - 2016-09-07 00:19 - 03555840 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\xpsrchvw.exe
2016-09-14 08:26 - 2016-09-07 00:19 - 02798080 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Media.dll
2016-09-14 08:26 - 2016-09-07 00:19 - 02295808 _____ (Microsoft Corporation) C:\WINDOWS\system32\wlansvc.dll
2016-09-14 08:26 - 2016-09-07 00:19 - 00733184 _____ (Microsoft Corporation) C:\WINDOWS\system32\rasapi32.dll
2016-09-14 08:26 - 2016-09-07 00:18 - 05503488 _____ (Microsoft Corporation) C:\WINDOWS\system32\d2d1.dll
2016-09-14 08:26 - 2016-09-07 00:17 - 01674240 _____ (Microsoft Corporation) C:\WINDOWS\system32\quartz.dll
2016-09-14 08:26 - 2016-09-07 00:16 - 02680320 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msftedit.dll
2016-09-14 08:26 - 2016-09-07 00:16 - 01984000 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mssrch.dll
2016-09-14 08:26 - 2016-09-07 00:16 - 00162816 _____ (Microsoft Corporation) C:\WINDOWS\system32\enrollmentapi.dll
2016-09-14 08:26 - 2016-09-07 00:15 - 02772480 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\tquery.dll
2016-09-14 08:26 - 2016-09-07 00:15 - 01556992 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\OpcServices.dll
2016-09-14 08:26 - 2016-09-07 00:14 - 03355136 _____ (Microsoft Corporation) C:\WINDOWS\system32\msftedit.dll
2016-09-14 08:26 - 2016-09-07 00:14 - 01799680 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Logon.dll
2016-09-14 08:26 - 2016-09-07 00:14 - 01732096 _____ (Microsoft Corporation) C:\WINDOWS\system32\urlmon.dll
2016-09-14 08:26 - 2016-09-07 00:12 - 00754176 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SettingSyncCore.dll
2016-09-14 08:26 - 2016-09-07 00:12 - 00339456 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\certcli.dll
2016-09-14 08:26 - 2016-09-07 00:11 - 03294208 _____ (Microsoft Corporation) C:\WINDOWS\system32\mstsc.exe
2016-09-14 08:26 - 2016-09-07 00:10 - 00712704 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\RemoteNaturalLanguage.dll
2016-09-14 08:26 - 2016-09-07 00:09 - 00824832 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\adtschema.dll
2016-09-14 08:26 - 2016-09-07 00:09 - 00218624 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\ahcache.sys
2016-09-14 08:26 - 2016-09-07 00:09 - 00063488 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\msobjs.dll
2016-09-14 08:25 - 2016-09-07 01:39 - 04387680 _____ (Microsoft Corporation) C:\WINDOWS\system32\setupapi.dll
2016-09-14 08:25 - 2016-09-07 01:39 - 01238584 _____ (Microsoft Corporation) C:\WINDOWS\system32\Taskmgr.exe
2016-09-14 08:25 - 2016-09-07 01:39 - 00705576 _____ (Microsoft Corporation) C:\WINDOWS\system32\kernel32.dll
2016-09-14 08:25 - 2016-09-07 01:39 - 00414232 _____ (Microsoft Corporation) C:\WINDOWS\system32\BCP47Langs.dll
2016-09-14 08:25 - 2016-09-07 01:39 - 00337328 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Storage.ApplicationData.dll
2016-09-14 08:25 - 2016-09-07 01:39 - 00328520 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\BCP47Langs.dll
2016-09-14 08:25 - 2016-09-07 01:36 - 00528736 _____ (Microsoft Corporation) C:\WINDOWS\system32\pcasvc.dll
2016-09-14 08:25 - 2016-09-07 01:35 - 01613664 _____ (Microsoft Corporation) C:\WINDOWS\system32\diagtrack.dll
2016-09-14 08:25 - 2016-09-07 01:35 - 00989536 _____ (Microsoft Corporation) C:\WINDOWS\system32\SecConfig.efi
2016-09-14 08:25 - 2016-09-07 01:35 - 00523616 _____ (Microsoft Corporation) C:\WINDOWS\system32\wimserv.exe
2016-09-14 08:25 - 2016-09-07 01:26 - 01554152 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmpmde.dll
2016-09-14 08:25 - 2016-09-07 01:26 - 00693592 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetSetupEngine.dll
2016-09-14 08:25 - 2016-09-07 01:26 - 00439136 _____ (Microsoft Corporation) C:\WINDOWS\system32\netcfgx.dll
2016-09-14 08:25 - 2016-09-07 01:24 - 00980352 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mfasfsrcsnk.dll
2016-09-14 08:25 - 2016-09-07 01:24 - 00925064 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mfplat.dll
2016-09-14 08:25 - 2016-09-07 01:24 - 00709176 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mfsvr.dll
2016-09-14 08:25 - 2016-09-07 01:24 - 00652312 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\evr.dll
2016-09-14 08:25 - 2016-09-07 01:24 - 00451928 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MFCaptureEngine.dll
2016-09-14 08:25 - 2016-09-07 01:22 - 00957608 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ole32.dll
2016-09-14 08:25 - 2016-09-07 01:22 - 00359256 _____ (Microsoft Corporation) C:\WINDOWS\system32\msv1_0.dll
2016-09-14 08:25 - 2016-09-07 01:16 - 02548936 _____ (Microsoft Corporation) C:\WINDOWS\system32\d3d10warp.dll
2016-09-14 08:25 - 2016-09-07 01:16 - 02144512 _____ (Microsoft Corporation) C:\WINDOWS\system32\d3d9.dll
2016-09-14 08:25 - 2016-09-07 01:16 - 01988448 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\dxgkrnl.sys
2016-09-14 08:25 - 2016-09-07 01:15 - 00550656 _____ (Microsoft Corporation) C:\WINDOWS\system32\directmanipulation.dll
2016-09-14 08:25 - 2016-09-07 01:12 - 00871776 _____ (Microsoft Corporation) C:\WINDOWS\system32\drvstore.dll
2016-09-14 08:25 - 2016-09-07 01:11 - 00503600 _____ (Microsoft Corporation) C:\WINDOWS\system32\DMRServer.dll
2016-09-14 08:25 - 2016-09-07 00:53 - 01033216 _____ (Microsoft Corporation) C:\WINDOWS\system32\termsrv.dll
2016-09-14 08:25 - 2016-09-07 00:46 - 00068608 _____ (Microsoft Corporation) C:\WINDOWS\system32\fdProxy.dll
2016-09-14 08:25 - 2016-09-07 00:46 - 00061952 _____ (Microsoft Corporation) C:\WINDOWS\system32\vss_ps.dll
2016-09-14 08:25 - 2016-09-07 00:44 - 00120832 _____ (Microsoft Corporation) C:\WINDOWS\system32\VoipRT.dll
2016-09-14 08:25 - 2016-09-07 00:44 - 00105984 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Cortana.ProxyStub.dll
2016-09-14 08:25 - 2016-09-07 00:44 - 00068608 _____ (Microsoft Corporation) C:\WINDOWS\system32\udhisapi.dll
2016-09-14 08:25 - 2016-09-07 00:43 - 00041472 _____ (Microsoft Corporation) C:\WINDOWS\system32\upnpcont.exe
2016-09-14 08:25 - 2016-09-07 00:42 - 00219136 _____ (Microsoft Corporation) C:\WINDOWS\system32\EnterpriseModernAppMgmtCSP.dll
2016-09-14 08:25 - 2016-09-07 00:41 - 00309760 _____ (Microsoft Corporation) C:\WINDOWS\system32\wusa.exe
2016-09-14 08:25 - 2016-09-07 00:41 - 00091136 _____ (Microsoft Corporation) C:\WINDOWS\system32\browserbroker.dll
2016-09-14 08:25 - 2016-09-07 00:41 - 00047616 _____ (Microsoft Corporation) C:\WINDOWS\system32\TpmTasks.dll
2016-09-14 08:25 - 2016-09-07 00:40 - 13018624 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Xaml.dll
2016-09-14 08:25 - 2016-09-07 00:40 - 00297472 _____ (Microsoft Corporation) C:\WINDOWS\system32\unimdm.tsp
2016-09-14 08:25 - 2016-09-07 00:40 - 00245248 _____ (Microsoft Corporation) C:\WINDOWS\system32\MicrosoftAccountExtension.dll
2016-09-14 08:25 - 2016-09-07 00:40 - 00135680 _____ (Microsoft Corporation) C:\WINDOWS\system32\vdsutil.dll
2016-09-14 08:25 - 2016-09-07 00:40 - 00070144 _____ (Microsoft Corporation) C:\WINDOWS\system32\vsstrace.dll
2016-09-14 08:25 - 2016-09-07 00:39 - 00356352 _____ (Microsoft Corporation) C:\WINDOWS\system32\mcbuilder.exe
2016-09-14 08:25 - 2016-09-07 00:38 - 00210432 _____ (Microsoft Corporation) C:\WINDOWS\system32\wcmcsp.dll
2016-09-14 08:25 - 2016-09-07 00:38 - 00187392 _____ (Microsoft Corporation) C:\WINDOWS\system32\BootMenuUX.dll
2016-09-14 08:25 - 2016-09-07 00:37 - 00846848 _____ (Microsoft Corporation) C:\WINDOWS\system32\ipsecsnp.dll
2016-09-14 08:25 - 2016-09-07 00:37 - 00308736 _____ (Microsoft Corporation) C:\WINDOWS\system32\eapphost.dll
2016-09-14 08:25 - 2016-09-07 00:37 - 00250880 _____ (Microsoft Corporation) C:\WINDOWS\system32\MicrosoftAccountCloudAP.dll
2016-09-14 08:25 - 2016-09-07 00:37 - 00198144 _____ (Microsoft Corporation) C:\WINDOWS\system32\winsrv.dll
2016-09-14 08:25 - 2016-09-07 00:37 - 00118784 _____ (Microsoft Corporation) C:\WINDOWS\system32\fhsvc.dll
2016-09-14 08:25 - 2016-09-07 00:37 - 00099328 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\srpapi.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 01582080 _____ (Microsoft Corporation) C:\WINDOWS\system32\aitstatic.exe
2016-09-14 08:25 - 2016-09-07 00:36 - 00567808 _____ (Microsoft Corporation) C:\WINDOWS\system32\MBMediaManager.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00479744 _____ (Microsoft Corporation) C:\WINDOWS\system32\apphelp.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00467968 _____ (Microsoft Corporation) C:\WINDOWS\system32\swprv.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00394752 _____ (Microsoft Corporation) C:\WINDOWS\system32\WMPhoto.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00332800 _____ (Microsoft Corporation) C:\WINDOWS\system32\eapp3hst.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00317952 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetworkBindingEngineMigPlugin.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00314368 _____ (Microsoft Corporation) C:\WINDOWS\system32\EnterpriseAppMgmtSvc.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00250880 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\AppLockerCSP.dll
2016-09-14 08:25 - 2016-09-07 00:36 - 00112640 _____ (Microsoft Corporation) C:\WINDOWS\system32\eapsvc.dll
2016-09-14 08:25 - 2016-09-07 00:35 - 00945664 _____ (Microsoft Corporation) C:\WINDOWS\system32\autochk.exe
2016-09-14 08:25 - 2016-09-07 00:35 - 00685568 _____ (Microsoft Corporation) C:\WINDOWS\system32\scapi.dll
2016-09-14 08:25 - 2016-09-07 00:35 - 00368640 _____ (Microsoft Corporation) C:\WINDOWS\system32\diagtrack_win.dll
2016-09-14 08:25 - 2016-09-07 00:35 - 00363008 _____ (Microsoft Corporation) C:\WINDOWS\system32\PhoneOm.dll
2016-09-14 08:25 - 2016-09-07 00:35 - 00342016 _____ (Microsoft Corporation) C:\WINDOWS\system32\APHostService.dll
2016-09-14 08:25 - 2016-09-07 00:35 - 00131072 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\usbceip.dll
2016-09-14 08:25 - 2016-09-07 00:34 - 00667136 _____ (Microsoft Corporation) C:\WINDOWS\system32\vds.exe
2016-09-14 08:25 - 2016-09-07 00:34 - 00440320 _____ (Microsoft Corporation) C:\WINDOWS\system32\fhcfg.dll
2016-09-14 08:25 - 2016-09-07 00:34 - 00318464 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Cortana.OneCore.dll
2016-09-14 08:25 - 2016-09-07 00:34 - 00304128 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Devices.Midi.dll
2016-09-14 08:25 - 2016-09-07 00:34 - 00270336 _____ (Microsoft Corporation) C:\WINDOWS\system32\netplwiz.dll
2016-09-14 08:25 - 2016-09-07 00:34 - 00265728 _____ (Microsoft Corporation) C:\WINDOWS\system32\netman.dll
2016-09-14 08:25 - 2016-09-07 00:33 - 01813504 _____ (Microsoft Corporation) C:\WINDOWS\system32\pnidui.dll
2016-09-14 08:25 - 2016-09-07 00:33 - 00948736 _____ (Microsoft Corporation) C:\WINDOWS\system32\XblAuthManager.dll
2016-09-14 08:25 - 2016-09-07 00:33 - 00606720 _____ (Microsoft Corporation) C:\WINDOWS\system32\wcmsvc.dll
2016-09-14 08:25 - 2016-09-07 00:33 - 00504832 _____ (Microsoft Corporation) C:\WINDOWS\system32\dlnashext.dll
2016-09-14 08:25 - 2016-09-07 00:33 - 00276480 _____ (Microsoft Corporation) C:\WINDOWS\system32\WindowsCodecsExt.dll
2016-09-14 08:25 - 2016-09-07 00:33 - 00092160 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\IdCtrls.dll
2016-09-14 08:25 - 2016-09-07 00:32 - 00892416 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.SmartCards.dll
2016-09-14 08:25 - 2016-09-07 00:32 - 00708608 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Security.Authentication.Web.Core.dll
2016-09-14 08:25 - 2016-09-07 00:32 - 00352768 _____ (Microsoft Corporation) C:\WINDOWS\system32\eappcfg.dll
2016-09-14 08:25 - 2016-09-07 00:32 - 00292864 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\dot3ui.dll
2016-09-14 08:25 - 2016-09-07 00:32 - 00283648 _____ (Microsoft Corporation) C:\WINDOWS\system32\PlayToReceiver.dll
2016-09-14 08:25 - 2016-09-07 00:32 - 00260096 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\apprepsync.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00984576 _____ (Microsoft Corporation) C:\WINDOWS\system32\tdh.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00970752 _____ (Microsoft Corporation) C:\WINDOWS\system32\kerberos.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00915456 _____ (Microsoft Corporation) C:\WINDOWS\system32\configurationclient.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00588288 _____ (Microsoft Corporation) C:\WINDOWS\system32\wlidprov.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00527872 _____ (Microsoft Corporation) C:\WINDOWS\system32\defragsvc.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00511488 _____ (Microsoft Corporation) C:\WINDOWS\system32\icsvc.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00452608 _____ (Microsoft Corporation) C:\WINDOWS\system32\upnphost.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00313344 _____ (Microsoft Corporation) C:\WINDOWS\system32\resutils.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00282624 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Search.ProtocolHandler.MAPI2.dll
2016-09-14 08:25 - 2016-09-07 00:31 - 00190464 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\apprepapi.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 14251520 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmp.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 01558528 _____ (Microsoft Corporation) C:\WINDOWS\system32\vssapi.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 01387520 _____ (Microsoft Corporation) C:\WINDOWS\system32\win32kbase.sys
2016-09-14 08:25 - 2016-09-07 00:30 - 01318400 _____ (Microsoft Corporation) C:\WINDOWS\system32\wsp_health.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 00697344 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Security.Authentication.OnlineId.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 00649216 _____ (Microsoft Corporation) C:\WINDOWS\system32\clusapi.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 00599040 _____ (Microsoft Corporation) C:\WINDOWS\system32\duser.dll
2016-09-14 08:25 - 2016-09-07 00:30 - 00436736 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppXDeploymentClient.dll
2016-09-14 08:25 - 2016-09-07 00:29 - 01847808 _____ (Microsoft Corporation) C:\WINDOWS\system32\WMPDMC.exe
2016-09-14 08:25 - 2016-09-07 00:29 - 01487360 _____ (Microsoft Corporation) C:\WINDOWS\system32\pla.dll
2016-09-14 08:25 - 2016-09-07 00:29 - 01443328 _____ (Microsoft Corporation) C:\WINDOWS\system32\diagperf.dll
2016-09-14 08:25 - 2016-09-07 00:29 - 00853504 _____ (Microsoft Corporation) C:\WINDOWS\system32\aadtb.dll
2016-09-14 08:25 - 2016-09-07 00:29 - 00785408 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\azroles.dll
2016-09-14 08:25 - 2016-09-07 00:29 - 00387584 _____ (Microsoft Corporation) C:\WINDOWS\system32\syncutil.dll
2016-09-14 08:25 - 2016-09-07 00:29 - 00283136 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.BioFeedback.dll
2016-09-14 08:25 - 2016-09-07 00:28 - 01783808 _____ (Microsoft Corporation) C:\WINDOWS\system32\wsp_fs.dll
2016-09-14 08:25 - 2016-09-07 00:28 - 01717760 _____ (Microsoft Corporation) C:\WINDOWS\system32\GdiPlus.dll
2016-09-14 08:25 - 2016-09-07 00:28 - 01671168 _____ (Microsoft Corporation) C:\WINDOWS\system32\FntCache.dll
2016-09-14 08:25 - 2016-09-07 00:28 - 00889344 _____ (Microsoft Corporation) C:\WINDOWS\system32\mprddm.dll
2016-09-14 08:25 - 2016-09-07 00:28 - 00282624 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SearchProtocolHost.exe
2016-09-14 08:25 - 2016-09-07 00:27 - 04456448 _____ (Microsoft Corporation) C:\WINDOWS\system32\D3DCompiler_47.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 01395712 _____ (Microsoft Corporation) C:\WINDOWS\system32\UIAutomationCore.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00865792 _____ (Microsoft Corporation) C:\WINDOWS\system32\AzureSettingSyncProvider.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00792576 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\kerberos.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00651776 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\comuid.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00585216 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.AccountsControl.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00555520 _____ (Microsoft Corporation) C:\WINDOWS\system32\SyncController.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00517632 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\PlayToManager.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00502272 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\DevicePairing.dll
2016-09-14 08:25 - 2016-09-07 00:27 - 00372224 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\LockAppBroker.dll
2016-09-14 08:25 - 2016-09-07 00:26 - 02057216 _____ (Microsoft Corporation) C:\WINDOWS\system32\wlidsvc.dll
2016-09-14 08:25 - 2016-09-07 00:26 - 01570816 _____ (Microsoft Corporation) C:\WINDOWS\system32\wbengine.exe
2016-09-14 08:25 - 2016-09-07 00:26 - 01117184 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Media.Speech.dll
2016-09-14 08:25 - 2016-09-07 00:26 - 00821760 _____ (Microsoft Corporation) C:\WINDOWS\system32\TokenBroker.dll
2016-09-14 08:25 - 2016-09-07 00:26 - 00738816 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\appwiz.cpl
2016-09-14 08:25 - 2016-09-07 00:26 - 00434688 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\LogonController.dll
2016-09-14 08:25 - 2016-09-07 00:25 - 02578432 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\gameux.dll
2016-09-14 08:25 - 2016-09-07 00:25 - 01467392 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\GdiPlus.dll
2016-09-14 08:25 - 2016-09-07 00:25 - 01328128 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\comsvcs.dll
2016-09-14 08:25 - 2016-09-07 00:25 - 01105920 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Media.Audio.dll
2016-09-14 08:25 - 2016-09-07 00:25 - 01052160 _____ (Microsoft Corporation) C:\WINDOWS\system32\MsSpellCheckingFacility.dll
2016-09-14 08:25 - 2016-09-07 00:25 - 00759808 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SearchIndexer.exe
2016-09-14 08:25 - 2016-09-07 00:24 - 00764928 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Cred.dll
2016-09-14 08:25 - 2016-09-07 00:24 - 00667648 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\AzureSettingSyncProvider.dll
2016-09-14 08:25 - 2016-09-07 00:23 - 04646912 _____ (Microsoft Corporation) C:\WINDOWS\system32\xpsrchvw.exe
2016-09-14 08:25 - 2016-09-07 00:23 - 00918016 _____ (Microsoft Corporation) C:\WINDOWS\system32\XpsFilt.dll
2016-09-14 08:25 - 2016-09-07 00:22 - 12585472 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wmp.dll
2016-09-14 08:25 - 2016-09-07 00:22 - 03093504 _____ (Microsoft Corporation) C:\WINDOWS\system32\mispace.dll
2016-09-14 08:25 - 2016-09-07 00:22 - 00465920 _____ (Microsoft Corporation) C:\WINDOWS\system32\StikyNot.exe
2016-09-14 08:25 - 2016-09-07 00:21 - 00620544 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\XpsFilt.dll
2016-09-14 08:25 - 2016-09-07 00:20 - 02800128 _____ (Microsoft Corporation) C:\WINDOWS\system32\netshell.dll
2016-09-14 08:25 - 2016-09-07 00:20 - 01385472 _____ (Microsoft Corporation) C:\WINDOWS\system32\usercpl.dll
2016-09-14 08:25 - 2016-09-07 00:20 - 00683008 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Networking.BackgroundTransfer.dll
2016-09-14 08:25 - 2016-09-07 00:20 - 00581632 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\twinapi.dll
2016-09-14 08:25 - 2016-09-07 00:20 - 00513024 _____ (Microsoft Corporation) C:\WINDOWS\system32\hnetcfg.dll
2016-09-14 08:25 - 2016-09-07 00:19 - 06471168 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\mspaint.exe
2016-09-14 08:25 - 2016-09-07 00:19 - 03589120 _____ (Microsoft Corporation) C:\WINDOWS\system32\win32kfull.sys
2016-09-14 08:25 - 2016-09-07 00:19 - 02902528 _____ (Microsoft Corporation) C:\WINDOWS\system32\themeui.dll
2016-09-14 08:25 - 2016-09-07 00:19 - 01997312 _____ (Microsoft Corporation) C:\WINDOWS\system32\ActiveSyncProvider.dll
2016-09-14 08:25 - 2016-09-07 00:19 - 01213440 _____ (Microsoft Corporation) C:\WINDOWS\system32\sdengin2.dll
2016-09-14 08:25 - 2016-09-07 00:17 - 02062336 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\MFMediaEngine.dll
2016-09-14 08:25 - 2016-09-07 00:16 - 04759040 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\d2d1.dll
2016-09-14 08:25 - 2016-09-07 00:16 - 01582080 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.Immersive.dll
2016-09-14 08:25 - 2016-09-07 00:16 - 00574976 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\hgcpl.dll
2016-09-14 08:25 - 2016-09-07 00:15 - 01755648 _____ (Microsoft Corporation) C:\WINDOWS\system32\dui70.dll
2016-09-14 08:25 - 2016-09-07 00:14 - 02519552 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\themecpl.dll
2016-09-14 08:25 - 2016-09-07 00:12 - 00899072 _____ (Microsoft Corporation) C:\WINDOWS\system32\D3D12.dll
2016-09-14 08:25 - 2016-09-07 00:10 - 01087488 _____ (Microsoft Corporation) C:\WINDOWS\system32\reseteng.dll
2016-09-14 08:25 - 2016-09-07 00:10 - 00627200 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\certca.dll
2016-09-14 08:25 - 2016-09-07 00:09 - 00824832 _____ (Microsoft Corporation) C:\WINDOWS\system32\adtschema.dll
2016-09-14 08:25 - 2016-09-07 00:09 - 00063488 _____ (Microsoft Corporation) C:\WINDOWS\system32\msobjs.dll
2016-09-14 08:25 - 2016-09-07 00:09 - 00058368 _____ (Microsoft Corporation) C:\WINDOWS\system32\csrsrv.dll
2016-09-14 08:25 - 2016-09-06 23:57 - 00461824 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\CoreMessaging.dll
2016-09-14 08:24 - 2016-09-07 01:39 - 07468896 _____ (Microsoft Corporation) C:\WINDOWS\system32\ntoskrnl.exe
2016-09-14 08:24 - 2016-09-07 01:39 - 01997832 _____ (Microsoft Corporation) C:\WINDOWS\system32\KernelBase.dll
2016-09-14 08:24 - 2016-09-07 01:39 - 01862000 _____ C:\WINDOWS\SysWOW64\CoreUIComponents.dll
2016-09-14 08:24 - 2016-09-07 01:39 - 01557768 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\KernelBase.dll
2016-09-14 08:24 - 2016-09-07 01:39 - 00428896 _____ (Microsoft Corporation) C:\WINDOWS\system32\hal.dll
2016-09-14 08:24 - 2016-09-07 01:34 - 03449168 _____ (Microsoft Corporation) C:\WINDOWS\system32\WSService.dll
2016-09-14 08:24 - 2016-09-07 01:26 - 01552104 _____ (Microsoft Corporation) C:\WINDOWS\system32\winmde.dll
2016-09-14 08:24 - 2016-09-07 01:26 - 00516544 _____ (Microsoft Corporation) C:\WINDOWS\system32\AudioEng.dll
2016-09-14 08:24 - 2016-09-07 01:23 - 04515256 _____ (Microsoft Corporation) C:\WINDOWS\explorer.exe
2016-09-14 08:24 - 2016-09-07 01:23 - 01540216 _____ (Microsoft Corporation) C:\WINDOWS\system32\sppobjs.dll
2016-09-14 08:24 - 2016-09-07 01:23 - 00730344 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Internal.Shell.Broker.dll
2016-09-14 08:24 - 2016-09-07 01:23 - 00692136 _____ (Microsoft Corporation) C:\WINDOWS\system32\sppwinob.dll
2016-09-14 08:24 - 2016-09-07 01:23 - 00565600 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingSyncHost.exe
2016-09-14 08:24 - 2016-09-07 01:23 - 00374008 _____ (Microsoft Corporation) C:\WINDOWS\system32\SystemSettingsAdminFlows.exe
2016-09-14 08:24 - 2016-09-07 01:23 - 00303216 _____ (Microsoft Corporation) C:\WINDOWS\system32\LockAppHost.exe
2016-09-14 08:24 - 2016-09-07 01:22 - 01824264 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\combase.dll
2016-09-14 08:24 - 2016-09-07 01:22 - 00742192 _____ (Microsoft Corporation) C:\WINDOWS\system32\EditionUpgradeManagerObj.dll
2016-09-14 08:24 - 2016-09-07 01:22 - 00703840 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WWAHost.exe
2016-09-14 08:24 - 2016-09-07 01:22 - 00638816 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\ClipSp.sys
2016-09-14 08:24 - 2016-09-07 01:22 - 00625000 _____ (Microsoft Corporation) C:\WINDOWS\system32\ClipSVC.dll
2016-09-14 08:24 - 2016-09-07 01:22 - 00431296 _____ (Microsoft Corporation) C:\WINDOWS\system32\bcryptprimitives.dll
2016-09-14 08:24 - 2016-09-07 01:21 - 21123320 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\shell32.dll
2016-09-14 08:24 - 2016-09-07 01:21 - 05240952 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\windows.storage.dll
2016-09-14 08:24 - 2016-09-07 01:20 - 00836752 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\twinapi.appcore.dll
2016-09-14 08:24 - 2016-09-07 01:19 - 00360480 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\bcryptprimitives.dll
2016-09-14 08:24 - 2016-09-07 01:15 - 01776768 _____ (Microsoft Corporation) C:\WINDOWS\system32\WindowsCodecs.dll
2016-09-14 08:24 - 2016-09-07 01:14 - 00430944 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\mrxsmb.sys
2016-09-14 08:24 - 2016-09-07 01:14 - 00216416 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\mrxsmb20.sys
2016-09-14 08:24 - 2016-09-07 01:13 - 02186856 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\d3d11.dll
2016-09-14 08:24 - 2016-09-07 01:12 - 28851224 _____ (Microsoft Corporation) C:\WINDOWS\system32\WindowsCodecsRaw.dll
2016-09-14 08:24 - 2016-09-07 01:11 - 02187408 _____ (Microsoft Corporation) C:\WINDOWS\system32\hevcdecoder.dll
2016-09-14 08:24 - 2016-09-07 01:11 - 00388888 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmpps.dll
2016-09-14 08:24 - 2016-09-07 01:11 - 00305296 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmpeffects.dll
2016-09-14 08:24 - 2016-09-07 01:08 - 28083144 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WindowsCodecsRaw.dll
2016-09-14 08:24 - 2016-09-07 01:07 - 00253080 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wmpeffects.dll
2016-09-14 08:24 - 2016-09-07 00:46 - 00119296 _____ (Microsoft Corporation) C:\WINDOWS\system32\UserDataTimeUtil.dll
2016-09-14 08:24 - 2016-09-07 00:44 - 00095232 _____ (Microsoft Corporation) C:\WINDOWS\system32\SecureTimeAggregator.dll
2016-09-14 08:24 - 2016-09-07 00:40 - 00285184 _____ (Microsoft Corporation) C:\WINDOWS\system32\oemlicense.dll
2016-09-14 08:24 - 2016-09-07 00:40 - 00129024 _____ (Microsoft Corporation) C:\WINDOWS\system32\mmcshext.dll
2016-09-14 08:24 - 2016-09-07 00:39 - 09324032 _____ (Microsoft Corporation) C:\WINDOWS\system32\wmploc.DLL
2016-09-14 08:24 - 2016-09-07 00:39 - 00238592 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Media.Streaming.ps.dll
2016-09-14 08:24 - 2016-09-07 00:38 - 00413696 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.Midi.dll
2016-09-14 08:24 - 2016-09-07 00:38 - 00335360 _____ (Microsoft Corporation) C:\WINDOWS\system32\mmcbase.dll
2016-09-14 08:24 - 2016-09-07 00:38 - 00203776 _____ (Microsoft Corporation) C:\WINDOWS\system32\cic.dll
2016-09-14 08:24 - 2016-09-07 00:36 - 00600064 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.LowLevel.dll
2016-09-14 08:24 - 2016-09-07 00:35 - 09324032 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wmploc.DLL
2016-09-14 08:24 - 2016-09-07 00:35 - 00714240 _____ (Microsoft Corporation) C:\WINDOWS\system32\SystemSettings.Handlers.dll
2016-09-14 08:24 - 2016-09-07 00:35 - 00475648 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.BlockedShutdown.dll
2016-09-14 08:24 - 2016-09-07 00:35 - 00450048 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Internal.Bluetooth.dll
2016-09-14 08:24 - 2016-09-07 00:34 - 11545088 _____ (Microsoft Corporation) C:\WINDOWS\system32\twinui.dll
2016-09-14 08:24 - 2016-09-07 00:34 - 00790528 _____ (Microsoft Corporation) C:\WINDOWS\system32\EmailApis.dll
2016-09-14 08:24 - 2016-09-07 00:34 - 00572928 _____ (Microsoft Corporation) C:\WINDOWS\system32\filemgmt.dll
2016-09-14 08:24 - 2016-09-07 00:34 - 00507904 _____ (Microsoft Corporation) C:\WINDOWS\system32\mprdim.dll
2016-09-14 08:24 - 2016-09-07 00:34 - 00414720 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.BioFeedback.dll
2016-09-14 08:24 - 2016-09-07 00:34 - 00273408 _____ (Microsoft Corporation) C:\WINDOWS\system32\SyncSettings.dll
2016-09-14 08:24 - 2016-09-07 00:33 - 00726528 _____ (Microsoft Corporation) C:\WINDOWS\system32\ChatApis.dll
2016-09-14 08:24 - 2016-09-07 00:33 - 00602112 _____ (Microsoft Corporation) C:\WINDOWS\system32\cryptui.dll
2016-09-14 08:24 - 2016-09-07 00:33 - 00448000 _____ (Microsoft Corporation) C:\WINDOWS\system32\winipcfile.dll
2016-09-14 08:24 - 2016-09-07 00:33 - 00315392 _____ (Microsoft Corporation) C:\WINDOWS\system32\RDXTaskFactory.dll
2016-09-14 08:24 - 2016-09-07 00:33 - 00224256 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\prnntfy.dll
2016-09-14 08:24 - 2016-09-07 00:33 - 00200704 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\DisplayManager.dll
2016-09-14 08:24 - 2016-09-07 00:32 - 00689664 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\srv2.sys
2016-09-14 08:24 - 2016-09-07 00:32 - 00674304 _____ (Microsoft Corporation) C:\WINDOWS\system32\mbsmsapi.dll
2016-09-14 08:24 - 2016-09-07 00:32 - 00556032 _____ (Microsoft Corporation) C:\WINDOWS\system32\PsmServiceExtHost.dll
2016-09-14 08:24 - 2016-09-07 00:32 - 00492544 _____ (Microsoft Corporation) C:\WINDOWS\system32\SystemSettings.UserAccountsHandlers.dll
2016-09-14 08:24 - 2016-09-07 00:32 - 00484352 _____ (Microsoft Corporation) C:\WINDOWS\system32\DataSenseHandlers.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 02125312 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingsHandlers_Bluetooth.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 01417728 _____ (Microsoft Corporation) C:\WINDOWS\system32\mqqm.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00965632 _____ (Microsoft Corporation) C:\WINDOWS\system32\SRH.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00700416 _____ (Microsoft Corporation) C:\WINDOWS\system32\AppointmentApis.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00564224 _____ (Microsoft Corporation) C:\WINDOWS\system32\DevicePairing.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00515072 _____ (Microsoft Corporation) C:\WINDOWS\system32\OneDriveSettingSyncProvider.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00480768 _____ (Microsoft Corporation) C:\WINDOWS\system32\LockAppBroker.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00472064 _____ (Microsoft Corporation) C:\WINDOWS\system32\Geolocation.dll
2016-09-14 08:24 - 2016-09-07 00:31 - 00236544 _____ (Microsoft Corporation) C:\WINDOWS\system32\Drivers\srvnet.sys
2016-09-14 08:24 - 2016-09-07 00:30 - 02012672 _____ (Microsoft Corporation) C:\WINDOWS\system32\winmsipc.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 01159168 _____ (Microsoft Corporation) C:\WINDOWS\system32\ApplicationFrame.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 01054208 _____ (Microsoft Corporation) C:\WINDOWS\system32\audiosrv.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 01037824 _____ (Microsoft Corporation) C:\WINDOWS\system32\SmartcardCredentialProvider.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 00990208 _____ (Microsoft Corporation) C:\WINDOWS\system32\SharedStartModel.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 00912384 _____ (Microsoft Corporation) C:\WINDOWS\system32\usermgr.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 00814080 _____ (Microsoft Corporation) C:\WINDOWS\system32\appwiz.cpl
2016-09-14 08:24 - 2016-09-07 00:30 - 00775168 _____ (Microsoft Corporation) C:\WINDOWS\system32\Display.dll
2016-09-14 08:24 - 2016-09-07 00:30 - 00531456 _____ (Microsoft Corporation) C:\WINDOWS\system32\sppcext.dll
2016-09-14 08:24 - 2016-09-07 00:29 - 01239552 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Devices.Bluetooth.dll
2016-09-14 08:24 - 2016-09-07 00:29 - 00896512 _____ (Microsoft Corporation) C:\WINDOWS\system32\MbaeApiPublic.dll
2016-09-14 08:24 - 2016-09-07 00:29 - 00529920 _____ (Microsoft Corporation) C:\WINDOWS\system32\LogonController.dll
2016-09-14 08:24 - 2016-09-07 00:29 - 00238592 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WindowsCodecsExt.dll
2016-09-14 08:24 - 2016-09-07 00:28 - 02731008 _____ (Microsoft Corporation) C:\WINDOWS\system32\gameux.dll
2016-09-14 08:24 - 2016-09-07 00:28 - 01466368 _____ (Microsoft Corporation) C:\WINDOWS\system32\Pimstore.dll
2016-09-14 08:24 - 2016-09-07 00:28 - 01211904 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Cred.dll
2016-09-14 08:24 - 2016-09-07 00:28 - 00938496 _____ (Microsoft Corporation) C:\WINDOWS\system32\ContactApis.dll
2016-09-14 08:24 - 2016-09-07 00:28 - 00638976 _____ (Microsoft Corporation) C:\WINDOWS\system32\ShareHost.dll
2016-09-14 08:24 - 2016-09-07 00:27 - 03415040 _____ (Microsoft Corporation) C:\WINDOWS\system32\SyncCenter.dll
2016-09-14 08:24 - 2016-09-07 00:27 - 01073152 _____ (Microsoft Corporation) C:\WINDOWS\system32\RDXService.dll
2016-09-14 08:24 - 2016-09-07 00:27 - 00961024 _____ (Microsoft Corporation) C:\WINDOWS\system32\WSShared.dll
2016-09-14 08:24 - 2016-09-07 00:27 - 00799744 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\SRH.dll
2016-09-14 08:24 - 2016-09-07 00:25 - 02445312 _____ (Microsoft Corporation) C:\WINDOWS\system32\DWrite.dll
2016-09-14 08:24 - 2016-09-07 00:25 - 01965568 _____ (Microsoft Corporation) C:\WINDOWS\system32\mmc.exe
2016-09-14 08:24 - 2016-09-07 00:25 - 01228800 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.Globalization.dll
2016-09-14 08:24 - 2016-09-07 00:25 - 01139712 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\UIAutomationCore.dll
2016-09-14 08:24 - 2016-09-07 00:25 - 00508416 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\wpnapps.dll
2016-09-14 08:24 - 2016-09-07 00:25 - 00489984 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\Windows.UI.dll
2016-09-14 08:24 - 2016-09-07 00:24 - 03994624 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingsHandlers_nt.dll
2016-09-14 08:24 - 2016-09-07 00:24 - 00805888 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WSShared.dll
2016-09-14 08:24 - 2016-09-07 00:23 - 01490432 _____ (Microsoft Corporation) C:\WINDOWS\system32\UserDataService.dll
2016-09-14 08:24 - 2016-09-07 00:22 - 01113600 _____ (Microsoft Corporation) C:\WINDOWS\system32\gpedit.dll
2016-09-14 08:24 - 2016-09-07 00:21 - 00636928 _____ (Microsoft Corporation) C:\WINDOWS\system32\hgcpl.dll
2016-09-14 08:24 - 2016-09-07 00:21 - 00613376 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingSync.dll
2016-09-14 08:24 - 2016-09-07 00:20 - 06976000 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Data.Pdf.dll
2016-09-14 08:24 - 2016-09-07 00:20 - 03585536 _____ (Microsoft Corporation) C:\WINDOWS\system32\SystemSettingsThresholdAdminFlowUI.dll
2016-09-14 08:24 - 2016-09-07 00:20 - 00583680 _____ (Microsoft Corporation) C:\WINDOWS\system32\PhotoScreensaver.scr
2016-09-14 08:24 - 2016-09-07 00:19 - 04078592 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\dbgeng.dll
2016-09-14 08:24 - 2016-09-07 00:19 - 02610176 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetworkMobileSettings.dll
2016-09-14 08:24 - 2016-09-07 00:19 - 02563584 _____ (Microsoft Corporation) C:\WINDOWS\system32\themecpl.dll
2016-09-14 08:24 - 2016-09-07 00:19 - 01141248 _____ (Microsoft Corporation) C:\WINDOWS\system32\winipcsecproc.dll
2016-09-14 08:24 - 2016-09-07 00:19 - 00527872 _____ (Microsoft Corporation) C:\WINDOWS\system32\w32time.dll
2016-09-14 08:24 - 2016-09-07 00:19 - 00515584 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\PhotoScreensaver.scr
2016-09-14 08:24 - 2016-09-07 00:17 - 05123072 _____ (Microsoft Corporation) C:\WINDOWS\system32\dbgeng.dll
2016-09-14 08:24 - 2016-09-07 00:16 - 02635776 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Logon.dll
2016-09-14 08:24 - 2016-09-07 00:15 - 00802816 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\ntshrui.dll
2016-09-14 08:24 - 2016-09-07 00:14 - 02000896 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\twinui.appcore.dll
2016-09-14 08:24 - 2016-09-07 00:14 - 01097216 _____ (Microsoft Corporation) C:\WINDOWS\system32\dosvc.dll
2016-09-14 08:24 - 2016-09-07 00:13 - 01390592 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.Shell.dll
2016-09-14 08:24 - 2016-09-07 00:13 - 00984576 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingSyncCore.dll
2016-09-14 08:24 - 2016-09-07 00:13 - 00711680 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\D3D12.dll
2016-09-14 08:24 - 2016-09-07 00:12 - 02632192 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\rdpcore.dll
2016-09-14 08:24 - 2016-09-07 00:12 - 01036288 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.Media.Streaming.dll
2016-09-14 08:24 - 2016-09-07 00:11 - 00958976 _____ (Microsoft Corporation) C:\WINDOWS\system32\RemoteNaturalLanguage.dll
2016-09-14 08:24 - 2016-09-07 00:11 - 00621568 _____ (Microsoft Corporation) C:\WINDOWS\system32\DbgModel.dll
2016-09-14 08:24 - 2016-09-07 00:11 - 00459776 _____ (Microsoft Corporation) C:\WINDOWS\system32\certcli.dll
2016-09-14 08:24 - 2016-09-07 00:10 - 00770048 _____ (Microsoft Corporation) C:\WINDOWS\system32\certca.dll
2016-09-14 08:24 - 2016-09-07 00:10 - 00438784 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\DbgModel.dll
2016-09-14 08:23 - 2016-09-07 00:39 - 00090624 _____ (Microsoft Corporation) C:\WINDOWS\system32\FingerprintEnrollment.dll
2016-09-14 08:23 - 2016-09-07 00:38 - 00110080 _____ (Microsoft Corporation) C:\WINDOWS\system32\IdCtrls.dll
2016-09-14 08:23 - 2016-09-07 00:36 - 00237056 _____ (Microsoft Corporation) C:\WINDOWS\system32\NetworkDesktopSettings.dll
2016-09-14 08:23 - 2016-09-07 00:36 - 00233984 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\DictationManager.dll
2016-09-14 08:23 - 2016-09-07 00:35 - 00813056 _____ (Microsoft Corporation) C:\WINDOWS\system32\mqsnap.dll
2016-09-14 08:23 - 2016-09-07 00:35 - 00318976 _____ (Microsoft Corporation) C:\WINDOWS\system32\domgmt.dll
2016-09-14 08:23 - 2016-09-07 00:35 - 00258560 _____ (Microsoft Corporation) C:\WINDOWS\system32\credprovs.dll
2016-09-14 08:23 - 2016-09-07 00:35 - 00188416 _____ (Microsoft Corporation) C:\WINDOWS\system32\Windows.UI.PicturePassword.dll
2016-09-14 08:23 - 2016-09-07 00:34 - 00492544 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingsHandlers_StorageSense.dll
2016-09-14 08:23 - 2016-09-07 00:34 - 00392192 _____ (Microsoft Corporation) C:\WINDOWS\system32\zipfldr.dll
2016-09-14 08:23 - 2016-09-07 00:31 - 00769536 _____ (Microsoft Corporation) C:\WINDOWS\system32\sppinst.dll
2016-09-14 08:23 - 2016-09-07 00:31 - 00183808 _____ (Microsoft Corporation) C:\WINDOWS\system32\WSSync.dll
2016-09-14 08:23 - 2016-09-07 00:30 - 01500672 _____ (Microsoft Corporation) C:\WINDOWS\system32\dbghelp.dll
2016-09-14 08:23 - 2016-09-07 00:30 - 00607232 _____ (Microsoft Corporation) C:\WINDOWS\system32\WUDFx.dll
2016-09-14 08:23 - 2016-09-07 00:29 - 00236032 _____ (Microsoft Corporation) C:\WINDOWS\system32\licensingdiag.exe
2016-09-14 08:23 - 2016-09-07 00:28 - 00243712 _____ (Microsoft Corporation) C:\WINDOWS\system32\SettingMonitor.dll
2016-09-14 08:23 - 2016-09-07 00:27 - 00153088 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\WSSync.dll
2016-09-14 08:23 - 2016-09-07 00:20 - 06675968 _____ (Microsoft Corporation) C:\WINDOWS\system32\mspaint.exe
2016-09-14 08:23 - 2016-09-07 00:19 - 00088064 _____ (Microsoft Corporation) C:\WINDOWS\system32\ImplatSetup.dll
2016-09-13 11:35 - 2016-09-15 08:49 - 00000000 ____D C:\GT500
2016-09-12 11:06 - 2016-09-12 11:06 - 00000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\QuickTime
2016-09-12 11:06 - 2016-09-12 11:06 - 00000000 ____D C:\Program Files (x86)\QuickTime
2016-09-12 11:00 - 2016-09-13 11:00 - 00004562 _____ C:\WINDOWS\System32\Tasks\Adobe Acrobat Update Task
2016-09-12 11:00 - 2016-09-13 11:00 - 00002457 _____ C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Acrobat Reader DC.lnk
2016-08-26 08:55 - 2016-08-26 08:55 - 00003324 _____ C:\WINDOWS\System32\Tasks\OneDrive Standalone Update Task
2016-08-26 08:54 - 2016-08-26 08:54 - 00000000 ____D C:\Users\Paddy\AppData\Roaming\Skype
 
==================== One Month Modified files and folders ========
 
(If an entry is included in the fixlist, the file/folder will be moved.)
 
2016-09-21 20:44 - 2012-04-07 08:06 - 00000830 _____ C:\WINDOWS\Tasks\Adobe Flash Player Updater.job
2016-09-21 20:34 - 2012-09-21 12:27 - 00000920 _____ C:\WINDOWS\Tasks\GoogleUpdateTaskMachineUA.job
2016-09-21 19:26 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\PLA
2016-09-21 18:58 - 2016-01-21 12:49 - 00000000 ____D C:\Legal
2016-09-21 18:57 - 2012-01-21 12:52 - 00000000 ____D C:\Job
2016-09-21 18:17 - 2012-12-04 22:53 - 00000000 ____D C:\ProgramData\Malwarebytes
2016-09-21 17:54 - 2015-10-30 03:24 - 00000000 ___HD C:\Program Files\WindowsApps
2016-09-21 17:54 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\AppReadiness
2016-09-21 15:56 - 2012-09-21 12:27 - 00000916 _____ C:\WINDOWS\Tasks\GoogleUpdateTaskMachineCore.job
2016-09-21 15:54 - 2015-12-22 15:54 - 00000006 ____H C:\WINDOWS\Tasks\SA.DAT
2016-09-21 15:54 - 2015-12-22 15:47 - 00142832 ____N (CyberLink Corp.) C:\WINDOWS\system32\Drivers\rikvm_38F51D56.sys
2016-09-21 15:54 - 2011-09-14 01:11 - 00000000 ____D C:\ProgramData\PDFC
2016-09-21 15:52 - 2015-10-30 02:28 - 00524288 ___SH C:\WINDOWS\system32\config\BBI
2016-09-21 15:50 - 2012-11-28 19:00 - 00000000 ____D C:\Users\Paddy\AppData\Roaming\Yahoo!
2016-09-21 15:50 - 2012-11-28 18:51 - 00000000 ____D C:\Users\Paddy\AppData\LocalLow\Yahoo!
2016-09-21 15:50 - 2012-11-28 18:51 - 00000000 ____D C:\Program Files (x86)\Yahoo!
2016-09-21 15:15 - 2015-12-22 18:21 - 00000000 ___DC C:\WINDOWS\Panther
2016-09-21 13:17 - 2016-07-16 11:17 - 00000000 ___HD C:\$WINDOWS.~BT
2016-09-21 10:44 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\SysWOW64\Macromed
2016-09-21 10:44 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\system32\Macromed
2016-09-20 21:12 - 2016-06-05 18:36 - 00003238 _____ C:\WINDOWS\System32\Tasks\HPCeeScheduleForPaddy
2016-09-20 21:12 - 2016-06-05 18:36 - 00000346 _____ C:\WINDOWS\Tasks\HPCeeScheduleForPaddy.job
2016-09-16 20:34 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\rescache
2016-09-16 19:55 - 2012-09-21 12:29 - 00002314 _____ C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Google Chrome.lnk
2016-09-16 18:53 - 2015-10-30 03:21 - 00000000 ____D C:\WINDOWS\INF
2016-09-16 18:48 - 2015-12-22 15:59 - 00000000 __RHD C:\Users\Public\AccountPictures
2016-09-16 18:40 - 2015-10-30 03:24 - 00000000 ___SD C:\WINDOWS\SysWOW64\F12
2016-09-16 18:40 - 2015-10-30 03:24 - 00000000 ___SD C:\WINDOWS\system32\F12
2016-09-16 18:40 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\system32\SystemResetPlatform
2016-09-16 18:40 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\system32\setup
2016-09-16 18:40 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\system32\oobe
2016-09-16 18:40 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\system32\migwiz
2016-09-16 18:40 - 2015-10-30 02:31 - 00000000 ____D C:\WINDOWS\SysWOW64\AdvancedInstallers
2016-09-16 18:40 - 2015-10-30 02:31 - 00000000 ____D C:\WINDOWS\system32\AdvancedInstallers
2016-09-16 18:40 - 2015-10-30 02:28 - 00000000 ____D C:\WINDOWS\SysWOW64\Dism
2016-09-16 18:40 - 2015-10-30 02:28 - 00000000 ____D C:\WINDOWS\system32\Dism
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ___RD C:\WINDOWS\PrintDialog
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ___RD C:\WINDOWS\ImmersiveControlPanel
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ___RD C:\WINDOWS\DevicesFlow
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ____D C:\Program Files\Windows Photo Viewer
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ____D C:\Program Files\Windows Defender
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ____D C:\Program Files (x86)\Windows Photo Viewer
2016-09-16 18:39 - 2015-10-30 03:24 - 00000000 ____D C:\Program Files (x86)\Windows Defender
2016-09-16 18:34 - 2013-03-13 21:58 - 00000000 ____D C:\Program Files\Microsoft Silverlight
2016-09-16 18:34 - 2013-03-13 21:58 - 00000000 ____D C:\Program Files (x86)\Microsoft Silverlight
2016-09-15 14:16 - 2015-12-22 15:32 - 01010622 _____ C:\WINDOWS\system32\PerfStringBackup.INI
2016-09-14 08:46 - 2015-10-30 03:11 - 00000000 ____D C:\WINDOWS\CbsTemp
2016-09-14 08:42 - 2015-10-30 03:24 - 00000000 ____D C:\WINDOWS\system32\appraiser
2016-09-14 08:42 - 2013-03-13 21:59 - 00000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Microsoft Silverlight
2016-09-14 08:41 - 2013-07-13 08:28 - 00000000 ____D C:\WINDOWS\system32\MRT
2016-09-14 08:36 - 2011-10-08 17:15 - 144199024 ____C (Microsoft Corporation) C:\WINDOWS\system32\MRT.exe
2016-09-13 11:00 - 2012-09-21 12:27 - 00000000 ____D C:\ProgramData\Adobe
2016-09-12 23:33 - 2015-12-22 15:59 - 00000000 ____D C:\Users\Paddy\AppData\Local\Packages
2016-09-12 11:01 - 2016-06-02 09:45 - 00000000 ____D C:\Users\Paddy\AppData\Local\Adobe
2016-09-12 10:59 - 2012-11-13 15:09 - 00000000 ____D C:\Program Files (x86)\Adobe
2016-09-12 09:59 - 2016-07-18 08:19 - 00000000 ____D C:\Expenses
2016-09-11 20:22 - 2011-11-16 22:23 - 00000000 ____D C:\MyDocs
2016-09-07 02:04 - 2015-12-22 15:26 - 02718208 _____ (Microsoft Corporation) C:\WINDOWS\SysWOW64\PrintConfig.dll
2016-09-06 21:00 - 2015-10-30 03:26 - 00828408 _____ (Adobe Systems Incorporated) C:\WINDOWS\SysWOW64\FlashPlayerApp.exe
2016-09-06 21:00 - 2015-10-30 03:26 - 00176632 _____ (Adobe Systems Incorporated) C:\WINDOWS\SysWOW64\FlashPlayerCPLApp.cpl
2016-09-05 22:27 - 2011-10-04 21:03 - 00000000 ____D C:\Users\Paddy\AppData\Roaming\SoftGrid Client
2016-08-26 09:13 - 2015-12-23 22:26 - 00000000 ____D C:\Scans
2016-08-26 08:55 - 2015-12-22 16:04 - 00002403 _____ C:\Users\Paddy\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\OneDrive.lnk
2016-08-26 08:55 - 2015-12-22 16:04 - 00000000 ___RD C:\Users\Paddy\OneDrive
 
==================== Files in the root of some directories =======
 
2012-11-17 20:29 - 2012-11-18 14:10 - 0005632 _____ () C:\Users\Paddy\AppData\Local\DCBC2A71-70D8-4DAN-EHR8-E0D61DEA3FDF.ini
 
Some files in TEMP:
====================
C:\Users\Paddy\AppData\Local\Temp\jre-8u66-windows-au.exe
C:\Users\Paddy\AppData\Local\Temp\libeay32.dll
C:\Users\Paddy\AppData\Local\Temp\mccspuninstall.exe
C:\Users\Paddy\AppData\Local\Temp\msvcr120.dll
C:\Users\Paddy\AppData\Local\Temp\sqlite3.dll
C:\Users\Paddy\AppData\Local\Temp\vlc-2.2.1-win32.exe
 
 
==================== Bamital & volsnap =================
 
(There is no automatic fix for files that do not pass verification.)
 
C:\WINDOWS\system32\winlogon.exe => File is digitally signed
C:\WINDOWS\system32\wininit.exe => File is digitally signed
C:\WINDOWS\explorer.exe => File is digitally signed
C:\WINDOWS\SysWOW64\explorer.exe => File is digitally signed
C:\WINDOWS\system32\svchost.exe => File is digitally signed
C:\WINDOWS\SysWOW64\svchost.exe => File is digitally signed
C:\WINDOWS\system32\services.exe => File is digitally signed
C:\WINDOWS\system32\User32.dll => File is digitally signed
C:\WINDOWS\SysWOW64\User32.dll => File is digitally signed
C:\WINDOWS\system32\userinit.exe => File is digitally signed
C:\WINDOWS\SysWOW64\userinit.exe => File is digitally signed
C:\WINDOWS\system32\rpcss.dll => File is digitally signed
C:\WINDOWS\system32\dnsapi.dll => File is digitally signed
C:\WINDOWS\SysWOW64\dnsapi.dll => File is digitally signed
C:\WINDOWS\system32\Drivers\volsnap.sys => File is digitally signed
 
 
LastRegBack: 2016-09-16 19:31
 
==================== End of FRST.txt ============================
 
Additional scan result of Farbar Recovery Scan Tool (x64) Version: 21-09-2016
Ran by [removed] (21-09-2016 20:47:04)
Running from C:\Users\[removed]\Desktop
Windows 10 Home Version 1511 (X64) (2015-12-22 19:58:01)
Boot Mode: Normal
==========================================================
 
 
==================== Accounts: =============================
 
Administrator (S-1-5-21-648858125-4165233436-1298442668-500 - Administrator - Disabled)
DefaultAccount (S-1-5-21-648858125-4165233436-1298442668-503 - Limited - Disabled)
Guest (S-1-5-21-648858125-4165233436-1298442668-501 - Limited - Disabled)
HomeGroupUser$ (S-1-5-21-648858125-4165233436-1298442668-1002 - Limited - Enabled)
Paddy (S-1-5-21-648858125-4165233436-1298442668-1001 - Administrator - Enabled) => C:\Users\Paddy
 
==================== Security Center ========================
 
(If an entry is included in the fixlist, it will be removed.)
 
AV: Windows Defender (Enabled - Up to date) {D68DDC3A-831F-4fae-9E44-DA132C1ACF46}
AS: Windows Defender (Enabled - Up to date) {D68DDC3A-831F-4fae-9E44-DA132C1ACF46}
 
==================== Installed Programs ======================
 
(Only the adware programs with "Hidden" flag could be added to the fixlist to unhide them. The adware programs should be uninstalled manually.)
 
7-Zip 9.22beta (HKLM-x32\…\7-Zip) (Version:  - )
Adobe Acrobat Reader DC (HKLM-x32\…\{AC76BA86-7AD7-1033-7B44-AC0F074E4100}) (Version: 15.017.20053 - Adobe Systems Incorporated)
Adobe AIR (HKLM-x32\…\Adobe AIR) (Version: 1.5.3.9130 - Adobe Systems Inc.)
Adobe Creative Suite 2 (HKLM-x32\…\{0134A1A1-C283-4A47-91A1-92F19F960372}) (Version:  - )
Adobe Flash Player 23 NPAPI (HKLM-x32\…\Adobe Flash Player NPAPI) (Version: 23.0.0.179 - Adobe Systems Incorporated)
Adobe SVG Viewer 3.0 (HKLM-x32\…\Adobe SVG Viewer) (Version:  3.0 - Adobe Systems, Inc.)
Agatha Christie - Peril at End House (x32 Version: 2.2.0.95 - WildTangent) Hidden
AMD Catalyst Control Center (HKLM-x32\…\WUCCCApp) (Version: 1.00.0000 - AMD)
AMD Catalyst Install Manager (HKLM\…\{5E03A267-415E-5383-FA8F-3CE4145663B9}) (Version: 8.0.903.0 - Advanced Micro Devices, Inc.)
Apple Application Support (HKLM-x32\…\{D9DAD0FF-495A-472B-9F10-BAE430A26682}) (Version: 3.0.3 - Apple Inc.)
Apple Mobile Device Support (HKLM\…\{787136D2-F0F8-4625-AA3F-72D7795AC842}) (Version: 7.1.1.3 - Apple Inc.)
Apple Software Update (HKLM-x32\…\{789A5B64-9DD9-4BA5-915A-F0FC0A1B7BFE}) (Version: 2.1.3.127 - Apple Inc.)
ArtecMedia ATSC Digital TV Player 2.0.3.1 (HKLM-x32\…\{A864C2E4-D1DC-4487-82A9-6B988F30A42B}) (Version: 6.00.0000 - Ultima)
AviSynth 2.5 (HKLM-x32\…\AviSynth) (Version:  - )
AVStoDVD 2.5.1 (HKLM-x32\…\AVStoDVD) (Version: 2.5.1 - MrC)
Bejeweled 2 Deluxe (x32 Version: 2.2.0.95 - WildTangent) Hidden
Bejeweled 3 (x32 Version: 2.2.0.95 - WildTangent) Hidden
Blackhawk Striker 2 (x32 Version: 2.2.0.95 - WildTangent) Hidden
Blasterball 3 (x32 Version: 2.2.0.95 - WildTangent) Hidden
Blio (HKLM-x32\…\{9368DDD5-CE7F-4BD7-A83A-F00FABE338EC}) (Version: 2.2.6699 - K-NFB Reading Technology, Inc.)
Bonjour (HKLM\…\{6E3610B2-430D-4EB0-81E3-2B57E8B9DE8D}) (Version: 3.0.0.10 - Apple Inc.)
Bounce Symphony (x32 Version: 2.2.0.95 - WildTangent) Hidden
Build-a-lot 2 (x32 Version: 2.2.0.95 - WildTangent) Hidden
Cake Mania (x32 Version: 2.2.0.95 - WildTangent) Hidden
Canon Auto Update Service (HKLM-x32\…\Auto Update Service) (Version: 1.1.2.18 - Canon Inc.)
Canon Camera WIA Driver (x32 Version: 5.0.4 - Canon) Hidden
Canon Camera WIA Driver (x32 Version: 5.1 - Canon) Hidden
Canon EOS 10D WIA Driver (HKLM-x32\…\InstallShield_{095659A2-739F-4D9A-A916-66C7CAD16F9E}) (Version: 5.1 - Canon)
Canon EOS Kiss REBEL 300D WIA Driver (HKLM-x32\…\InstallShield_{31A57C3E-30DD-421F-B5C7-974DACB0D05F}) (Version: 5.1 - Canon)
Canon FV M10, OPTURA20 WIA Driver (HKLM-x32\…\InstallShield_{6A30F2AE-03B2-47EB-9754-BCF2EC56B7AF}) (Version: 5.0.4 - Canon)
CANON iMAGE GATEWAY MyCamera Download Plugin (HKLM-x32\…\MyCamera Download Plugin) (Version: 3.1.1.2 - Canon Inc.)
CANON iMAGE GATEWAY Task for ZoomBrowser EX (HKLM-x32\…\CANON iMAGE GATEWAY Task) (Version: 1.9.0.9 - Canon Inc.)
Canon MOV Decoder (HKLM-x32\…\Canon MOV Decoder) (Version: 1.9.0.8 - Canon Inc.)
Canon MOV Encoder (HKLM-x32\…\Canon MOV Encoder) (Version: 1.8.0.1 - Canon Inc.)
Canon MovieEdit Task for ZoomBrowser EX (HKLM-x32\…\MovieEditTask) (Version: 3.9.0.6 - Canon Inc.)
Canon OPTURA10 WIA Driver (HKLM-x32\…\InstallShield_{85906114-22EE-4B4F-833A-7907F9D046D4}) (Version: 5.0.4 - Canon)
Canon PhotoRecord (HKLM-x32\…\PhotoRecord) (Version:  - )
Canon Utilities Digital Photo Professional 3.4 (HKLM-x32\…\DPP) (Version: 3.4.1.1 - )
Canon Utilities EOS Utility (HKLM-x32\…\EOS Utility) (Version: 2.12.3.1 - Canon Inc.)
Canon Utilities EOS Video Snapshot Task for ZoomBrowser EX (HKLM-x32\…\EOS Video Snapshot Task) (Version: 1.0.0.10 - Canon Inc.)
Canon Utilities File Viewer Utility 1.3 (HKLM-x32\…\InstallShield_{74344F10-34CA-480E-BD02-B3F4FA692BFA}) (Version: 1.3.1 - Canon)
Canon Utilities PhotoStitch 3.1 (HKLM-x32\…\InstallShield_{F11A403B-0DE9-4953-B790-7A2F014FBB2B}) (Version: 3.1.10 - Canon)
Canon Utilities RemoteCapture 2.7 (HKLM-x32\…\InstallShield_{EF91B23E-3819-43A1-AE47-043E1900EB2B}) (Version: 2.7.4 - Canon)
Canon Utilities ZoomBrowser EX (HKLM-x32\…\ZoomBrowser EX) (Version: 6.9.0.1 - Canon Inc.)
Canon ZoomBrowser EX Memory Card Utility (HKLM-x32\…\ZoomBrowser EX Memory Card Utility) (Version: 1.6.0.15 - Canon Inc.)
Chuzzle Deluxe (x32 Version: 2.2.0.95 - WildTangent) Hidden
Corel Applications (HKLM-x32\…\Corel Applications) (Version:  - )
CPUID HWMonitor 1.24 (HKLM\…\CPUID HWMonitor_is1) (Version:  - )
CyberLink Blu-ray Disc Suite (HKLM-x32\…\InstallShield_{1FBF6C24-C1FD-4101-A42B-0C564F9E8E79}) (Version: 7.0.1929 - CyberLink Corp.)
CyberLink Power2Go (HKLM-x32\…\InstallShield_{40BF1E83-20EB-11D8-97C5-0009C5020658}) (Version: 6.1.3401 - CyberLink Corp.)
CyberLink PowerDirector (HKLM-x32\…\InstallShield_{CB099890-1D5F-11D5-9EA9-0050BAE317E1}) (Version: 7.0.3227a - CyberLink Corp.)
CyberLink PowerDirector 11 (HKLM-x32\…\InstallShield_{551F492A-01B0-4DC4-866F-875EC4EDC0A8}) (Version: 11.0.0.2215 - CyberLink Corp.)
CyberLink PowerDirector 11 (Version: 11.0.0.2215 - CyberLink Corp.) Hidden
CyberLink PowerDirector 11 Content Pack Essential (HKLM-x32\…\InstallShield_{03AD770A-1530-437E-967F-ADD4E5B23164}) (Version: 11 - CyberLink Corp.)
CyberLink PowerDirector 11 Content Pack Premium (HKLM-x32\…\InstallShield_{37672760-7930-4911-9685-227E29AE2C55}) (Version: 11 - CyberLink Corp.)
CyberLink PowerDVD 10 (HKLM-x32\…\InstallShield_{DEC235ED-58A4-4517-A278-C41E8DAEAB3B}) (Version: 10.0.1.2615 - CyberLink Corp.)
CyberLink PowerDVD 9 (HKLM-x32\…\InstallShield_{A8516AC9-AAF1-47F9-9766-03E2D4CDBCF8}) (Version: 9.0.2101 - CyberLink Corp.)
CyberLink WaveEditor 2 (HKLM-x32\…\InstallShield_{324F76CC-D8DD-4D87-B77D-D4AF5E1AA7B3}) (Version: 2.0.3206 - CyberLink Corp.)
D3DX10 (x32 Version: 15.4.2368.0902 - Microsoft) Hidden
Digital Copy (HKLM-x32\…\Digital Copy) (Version:  - )
Diner Dash 2 Restaurant Rescue (x32 Version: 2.2.0.95 - WildTangent) Hidden
Dora's World Adventure (x32 Version: 2.2.0.95 - WildTangent) Hidden
ESET Online Scanner v3 (HKLM-x32\…\ESET Online Scanner) (Version:  - )
Farm Frenzy (x32 Version: 2.2.0.95 - WildTangent) Hidden
FATE - The Traitor Soul (x32 Version: 2.2.0.95 - WildTangent) Hidden
File Viewer Utility 1.3.1 (x32 Version: 1.3.1 - Canon) Hidden
Google Chrome (HKLM-x32\…\Google Chrome) (Version: 53.0.2785.116 - Google Inc.)
Google Earth (HKLM-x32\…\{817750FA-EC6A-485D-9901-0683AE6FFDF1}) (Version: 7.1.5.1557 - Google)
Google Toolbar for Internet Explorer (HKLM-x32\…\{2318C2B1-4965-11d4-9B18-009027A5CD4F}) (Version: 7.5.7619.1252 - Google Inc.)
Google Toolbar for Internet Explorer (x32 Version: 1.0.0 - Google Inc.) Hidden
Google Update Helper (x32 Version: 1.3.25.11 - Google Inc.) Hidden
Google Update Helper (x32 Version: 1.3.31.5 - Google Inc.) Hidden
Grab & Burn, Version 4.0.1 ( Build 2005-09-21, Win32, CSS ) (HKLM-x32\…\Rocket Division Software Grab & Burn_is1) (Version:  - Rocket Division Software)
Haali Media Splitter (HKLM-x32\…\HaaliMkx) (Version:  - )
Hewlett-Packard ACLM.NET v1.2.2.3 (x32 Version: 1.00.0000 - Hewlett-Packard Company) Hidden
HP Games (HKLM-x32\…\WildTangent hp Master Uninstall) (Version: 1.0.2.4 - WildTangent)
HP LinkUp (HKLM-x32\…\{C1AD9241-3ADD-483F-914D-071F3E50855A}) (Version: 2.01.026 - Hewlett-Packard)
HP MediaSmart/TouchSmart Netflix (HKLM-x32\…\{BB760C1D-98F4-4E38-8CC4-3B67329AA981}) (Version: 1.0.6.0 - Hewlett-Packard)
HP MovieStore (HKLM-x32\…\{9008D736-35CA-40DB-A2BE-5F32D954E5AA}) (Version: 2.0 - Hewlett-Packard)
HP Odometer (HKLM-x32\…\{B8AC1A89-FFD1-4F97-8051-E505A160F562}) (Version: 2.10.0000 - Hewlett-Packard)
HP Product Detection (HKLM-x32\…\{A436F67F-687E-4736-BD2B-537121A804CF}) (Version: 11.14.0001 - HP)
HP Setup (HKLM-x32\…\{210A03F5-B2ED-4947-B27E-516F50CBB292}) (Version: 8.6.4530.3651 - Hewlett-Packard Company)
HP Setup Manager (HKLM-x32\…\{AE856388-AFAD-4753-81DF-D96B19D0A17C}) (Version: 1.1.13253.3682 - Hewlett-Packard Company)
HP Support Assistant (HKLM-x32\…\{79C54A05-F146-4EA0-8A70-D4EFE6181E52}) (Version: 8.3.34.7 - Hewlett-Packard Company)
HP Support Information (HKLM-x32\…\{7F2A11F4-EAE8-4325-83EC-E3E99F85169E}) (Version: 10.1.1000 - Hewlett-Packard)
HP Support Solutions Framework (HKLM-x32\…\{55065080-504F-43BB-BE00-36B80D7D39A5}) (Version: 12.5.32.37 - Hewlett-Packard Company)
HP Update (HKLM-x32\…\{DE77FE3F-A33D-499A-87AD-5FC406617B40}) (Version: 5.002.003.003 - Hewlett-Packard)
HP Vision Hardware Diagnostics (HKLM\…\{D79A02E9-6713-4335-9668-AAC7474C0C0E}) (Version: 2.5.0.0 - Hewlett-Packard)
Hulu Desktop (HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\HuluDesktop) (Version: 0.9.13 - Hulu LLC)
HydraVision (x32 Version: 4.2.212.0 - Advanced Micro Devices, Inc.) Hidden
iCloud (HKLM\…\{81E20D41-C277-4526-934D-F2380AF91B78}) (Version: 3.1.0.40 - Apple Inc.)
IDT Audio (HKLM-x32\…\{E3A5A8AB-58F6-45FF-AFCB-C9AE18C05001}) (Version: 1.0.6325.0 - IDT)
ImgBurn (HKLM-x32\…\ImgBurn) (Version: 2.5.5.0 - LIGHTNING UK!)
Intel(R) Management Engine Components (HKLM-x32\…\{65153EA5-8B6E-43B6-857B-C6E4FC25798A}) (Version: 7.0.0.1144 - Intel Corporation)
iTunes (HKLM\…\{5A68A656-979F-4168-8795-E2E368AA4DC2}) (Version: 11.2.2.3 - Apple Inc.)
Java 8 Update 66 (HKLM-x32\…\{26A24AE4-039D-4CA4-87B4-2F83218066F0}) (Version: 8.0.660.18 - Oracle Corporation)
Junk Mail filter update (x32 Version: 16.4.3528.0331 - Microsoft Corporation) Hidden
Kobo (HKLM-x32\…\Kobo) (Version: 1.6 - Kobo Inc.)
LabelPrint (HKLM-x32\…\InstallShield_{C59C179C-668D-49A9-B6EA-0121CCFC1243}) (Version: 2.5.3609 - CyberLink Corp.)
LabelPrint (x32 Version: 2.5.3609 - CyberLink Corp.) Hidden
Mah Jong Medley (x32 Version: 2.2.0.95 - WildTangent) Hidden
Malwarebytes Anti-Malware version 2.2.1.1043 (HKLM-x32\…\Malwarebytes Anti-Malware_is1) (Version: 2.2.1.1043 - Malwarebytes)
McAfee Online Backup (Version: 1.16.4.0 - McAfee, Inc.) Hidden
McAfee Online Backup (x32 Version:  - McAfee, Inc.) Hidden
MediaInfo 0.7.61 (HKLM\…\MediaInfo) (Version: 0.7.61 - MediaArea.net)
Microsoft Office 2010 (HKLM-x32\…\{95140000-0070-0000-0000-0000000FF1CE}) (Version: 14.0.4763.1000 - Microsoft Corporation)
Microsoft Office Click-to-Run 2010 (HKLM-x32\…\Office14.Click2Run) (Version: 14.0.4763.1000 - Microsoft Corporation)
Microsoft Office Starter 2010 - English (HKLM-x32\…\{90140011-0066-0409-0000-0000000FF1CE}) (Version: 14.0.4763.1000 - Microsoft Corporation)
Microsoft Silverlight (HKLM\…\{89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}) (Version: 5.1.50709.0 - Microsoft Corporation)
Microsoft SQL Server 2005 Compact Edition [ENU] (HKLM-x32\…\{F0B430D1-B6AA-473D-9B06-AA3DD01FD0B8}) (Version: 3.1.0000 - Microsoft Corporation)
Microsoft Visio Professional 2002 [English] (HKLM-x32\…\{90500409-6D54-11D4-BEE3-00C04F990354}) (Version: 10.2.5110 - Microsoft Corporation)
Microsoft Visual C++ 2005 Redistributable (HKLM-x32\…\{710f4c1c-cc18-4c49-8cbf-51240c89a1a2}) (Version: 8.0.61001 - Microsoft Corporation)
Microsoft Visual C++ 2005 Redistributable (HKLM-x32\…\{7299052b-02a4-4627-81f2-1818da5d550d}) (Version: 8.0.56336 - Microsoft Corporation)
Microsoft Visual C++ 2005 Redistributable (x64) (HKLM\…\{071c9b48-7c32-4621-a0ac-3f809523288f}) (Version: 8.0.56336 - Microsoft Corporation)
Microsoft Visual C++ 2005 Redistributable (x64) (HKLM\…\{ad8a2fa1-06e7-4b0d-927d-6e54b3d31028}) (Version: 8.0.61000 - Microsoft Corporation)
Microsoft Visual C++ 2008 Redistributable - x64 9.0.30729.17 (HKLM\…\{8220EEFE-38CD-377E-8595-13398D740ACE}) (Version: 9.0.30729 - Microsoft Corporation)
Microsoft Visual C++ 2008 Redistributable - x64 9.0.30729.4148 (HKLM\…\{4B6C7001-C7D6-3710-913E-5BC23FCE91E6}) (Version: 9.0.30729.4148 - Microsoft Corporation)
Microsoft Visual C++ 2008 Redistributable - x64 9.0.30729.6161 (HKLM\…\{5FCE6D76-F5DC-37AB-B2B8-22AB8CEDB1D4}) (Version: 9.0.30729.6161 - Microsoft Corporation)
Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.17 (HKLM-x32\…\{9A25302D-30C0-39D9-BD6F-21E6EC160475}) (Version: 9.0.30729 - Microsoft Corporation)
Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.4148 (HKLM-x32\…\{1F1C2DFC-2D24-3E06-BCB8-725134ADF989}) (Version: 9.0.30729.4148 - Microsoft Corporation)
Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.6161 (HKLM-x32\…\{9BE518E6-ECC6-35A9-88E4-87755C07200F}) (Version: 9.0.30729.6161 - Microsoft Corporation)
Microsoft Visual C++ 2010  x64 Redistributable - 10.0.30319 (HKLM\…\{DA5E371C-6333-3D8A-93A4-6FD5B20BCC6E}) (Version: 10.0.30319 - Microsoft Corporation)
Microsoft Visual C++ 2010  x86 Redistributable - 10.0.30319 (HKLM-x32\…\{196BB40D-1578-3D01-B289-BEFC77A11A1E}) (Version: 10.0.30319 - Microsoft Corporation)
Microsoft Visual C++ 2012 Redistributable (x64) - 11.0.61030 (HKLM-x32\…\{ca67548a-5ebe-413a-b50c-4b9ceb6d66c6}) (Version: 11.0.61030.0 - Microsoft Corporation)
Microsoft Visual C++ 2012 Redistributable (x86) - 11.0.61030 (HKLM-x32\…\{33d1fd90-4274-48a1-9bc1-97e33d9c2d6f}) (Version: 11.0.61030.0 - Microsoft Corporation)
MKVToolNix 5.7.0 (HKLM-x32\…\MKVToolNix) (Version: 5.7.0 - Moritz Bunkus)
Movie Maker (x32 Version: 16.4.3528.0331 - Microsoft Corporation) Hidden
MSXML 4.0 SP2 (KB954430) (HKLM-x32\…\{86493ADD-824D-4B8E-BD72-8C5DCDC52A71}) (Version: 4.20.9870.0 - Microsoft Corporation)
MSXML 4.0 SP2 (KB973688) (HKLM-x32\…\{F662A8E6-F4DC-41A2-901E-8C11F044BDEC}) (Version: 4.20.9876.0 - Microsoft Corporation)
Mystery P.I. - Stolen in San Francisco (x32 Version: 2.2.0.95 - WildTangent) Hidden
Namco All-Stars PAC-MAN (x32 Version: 2.2.0.95 - WildTangent) Hidden
Newblue Art Effects for PowerDirector (HKLM\…\NewBlue Art Effects for PowerDirector) (Version: 2.0 - NewBlue)
OpenOffice 4.1.2 (HKLM-x32\…\{E6AD67BB-1C33-4AB3-A387-E0D48137AB70}) (Version: 4.12.9782 - Apache Software Foundation)
PDF Complete Special Edition (HKLM-x32\…\PDF Complete) (Version: 4.0.35 - PDF Complete, Inc)
Penguins! (x32 Version: 2.2.0.95 - WildTangent) Hidden
PhotoStitch (x32 Version: 3.1.10 - Canon) Hidden
Plants vs. Zombies - Game of the Year (x32 Version: 2.2.0.95 - WildTangent) Hidden
PlayReady PC Runtime amd64 (HKLM\…\{BCA9334F-B6C9-4F65-9A73-AC5A329A4D04}) (Version: 1.3.0 - Microsoft Corporation)
PlayReady PC Runtime x86 (HKLM-x32\…\{CCA5EAAD-92F4-4B7A-B5EE-14294C66AB61}) (Version: 1.3.0 - Microsoft Corporation)
Poker Superstars III (x32 Version: 2.2.0.95 - WildTangent) Hidden
Polar Bowler (x32 Version: 2.2.0.95 - WildTangent) Hidden
Polar Golfer (x32 Version: 2.2.0.95 - WildTangent) Hidden
PressReader (HKLM-x32\…\{912CED74-88D3-4C5B-ACB0-132318649765}) (Version: 5.10.1217.0 -  NewspaperDirect Inc.)
QuickTime 7 (HKLM-x32\…\{627FFC10-CE0A-497F-BA2B-208CAC638010}) (Version: 7.77.80.95 - Apple Inc.)
RAR File Open Knife - Free Opener (HKLM-x32\…\RAR File Open Knife - Free Opener) (Version: 3.40 - Philipp Winterberg)
Recovery Manager (x32 Version: 5.5.3621 - CyberLink Corp.) Hidden
RegiStax 6 (HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\RegiStax 6) (Version:  - )
RegiStax 6.1.0.8 update (HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\RegiStax 6.1.0.8 update) (Version:  - )
Remote Graphics Receiver (HKLM-x32\…\{16FC3056-90C0-4757-8A68-64D8DA846ADA}) (Version: 5.4.5 - Hewlett-Packard)
RemoteCapture 2.7.4 (x32 Version: 2.7.4 - Canon) Hidden
RoxioNow Player (HKLM-x32\…\{0EDEB615-1A60-425E-8306-0E10519C7B55}) (Version: 1.9.5.103 - RoxioNow)
SentriCard Utility (HKLM-x32\…\{14B8F58C-4BD8-4122-9FE6-827527626392}_is1) (Version: 4.0.0 - SentriLock, LLC)
Shared C Run-time for x64 (HKLM\…\{EF79C448-6946-4D71-8134-03407888C054}) (Version: 10.0.0 - McAfee)
Slingo Supreme (x32 Version: 2.2.0.95 - WildTangent) Hidden
SmartSound Quicktracks 5 (HKLM-x32\…\InstallShield_{2F8BA3FD-1FA9-4279-B696-712ABB12F09F}) (Version: 5.1.8 - SmartSound Software Inc.)
SmartSound Quicktracks 5 (x32 Version: 5.1.8 - SmartSound Software Inc.) Hidden
SnagIt 7 (HKLM-x32\…\SnagIt7) (Version: 7.2 - TechSmith Corporation)
SpeedFan (remove only) (HKLM-x32\…\SpeedFan) (Version:  - ) <==== ATTENTION
STOPzilla (HKLM-x32\…\{4E1D975D-9BF3-43CF-AA30-7186CEE3D9DE}) (Version: 5.0.98.115 - iS3 Inc.)
StreamTorrent 1.0 (HKLM-x32\…\StreamTorrent 1.0) (Version:  - )
Suite Specific (x32 Version: 2.0.0 - Adobe Systems, Incorporated) Hidden
Update Installer for WildTangent Games App (x32 Version:  - WildTangent) Hidden
Virtual Villagers 4 - The Tree of Life (x32 Version: 2.2.0.95 - WildTangent) Hidden
VLC media player (HKLM-x32\…\VLC media player) (Version: 2.2.1 - VideoLAN)
VueScan x64 (HKLM\…\VueScan x64) (Version:  - )
Wheel of Fortune 2 (x32 Version: 2.2.0.95 - WildTangent) Hidden
WhiteSmoke New Toolbar (HKLM-x32\…\WhiteSmoke_New Toolbar) (Version: 6.13.50.5 - WhiteSmoke New) <==== ATTENTION
WhoCrashed 5.00 (HKLM\…\WhoCrashed_is1) (Version:  - Resplendence Software Projects Sp.)
WildTangent Games App (HP Games) (x32 Version: 4.0.5.2 - WildTangent) Hidden
Windows Live Essentials (HKLM-x32\…\WinLiveSuite) (Version: 16.4.3528.0331 - Microsoft Corporation)
Wondershare Dr.Fone for iOS(Build 4.5.1.6) (HKLM-x32\…\{A26F8BBD-EC10-4bdc-8AD8-F146825A8A63}_is1) (Version: 4.5.1.6 - Wondershare Software Co.,Ltd.)
Yahoo! Software Update (HKLM-x32\…\Yahoo! Software Update) (Version:  - )
Zuma Deluxe (x32 Version: 2.2.0.95 - WildTangent) Hidden
 
==================== Custom CLSID (Whitelisted): ==========================
 
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
 
CustomCLSID: HKU\S-1-5-21-648858125-4165233436-1298442668-1001_Classes\CLSID\{71DCE5D6-4B57-496B-AC21-CD5B54EB93FD}\localserver32 -> C:\Users\Paddy\AppData\Local\Microsoft\OneDrive\17.3.6517.0809\FileCoAuth.exe (Microsoft Corporation)
 
==================== Scheduled Tasks (Whitelisted) =============
 
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
 
Task: {042937CB-5476-4C2A-8480-C5E036578E2B} - System32\Tasks\Microsoft\Windows\Media Center\OCURActivate => C:\Windows\ehome\ehPrivJob.exe
Task: {08C5B79B-286B-438C-9068-A979952C531F} - \Microsoft\Windows\Setup\GWXTriggers\ScheduleUpgradeReminderTime -> No File <==== ATTENTION
Task: {0987D9CD-C136-4608-81D4-64E705CAAAD4} - \Microsoft\Windows\Setup\GWXTriggers\Logon-5d -> No File <==== ATTENTION
Task: {2BF673A6-60F6-4999-B64B-2AB220858EE9} - System32\Tasks\OneDrive Standalone Update Task => C:\Users\Paddy\AppData\Local\Microsoft\OneDrive\17.3.6517.0809\OneDriveStandaloneUpdater.exe [2016-08-26] (Microsoft Corporation)
Task: {2F04F48E-5A44-435C-AB51-3BE5C3C1CA62} - \Microsoft\Windows\Setup\gwx\runappraiser -> No File <==== ATTENTION
Task: {2F7FDCDC-5B7D-4D76-ADAD-56B53EDC15CA} - System32\Tasks\Microsoft\Windows\RemovalTools\MRT_HB => C:\WINDOWS\system32\MRT.exe [2016-09-14] (Microsoft Corporation)
Task: {356A9E84-A83A-4B9C-9D93-B133D8480A15} - \Microsoft\Windows\Setup\gwx\refreshgwxconfig -> No File <==== ATTENTION
Task: {35A742C1-2971-4943-A2E3-29AD462FFAAC} - System32\Tasks\Microsoft\Windows\Media Center\ActivateWindowsSearch => C:\Windows\ehome\ehPrivJob.exe
Task: {36FE09F7-3866-4448-8EA0-5A57BA498920} - \Microsoft\Windows\Setup\GWXTriggers\Time-5d -> No File <==== ATTENTION
Task: {3ACF76E4-F5DF-431C-BEA2-BE70CF85AE6D} - System32\Tasks\Microsoft\Windows\Media Center\MediaCenterRecoveryTask => C:\Windows\ehome\mcupdate.exe
Task: {448270B0-5154-498D-B24D-AE71E7DB5927} - System32\Tasks\Microsoft\Windows\Media Center\RegisterSearch => C:\Windows\ehome\ehPrivJob.exe
Task: {4EF9C94A-BEB8-4886-8EFB-6F8DC72DE967} - System32\Tasks\Microsoft\Windows\Media Center\ReindexSearchRoot => C:\Windows\ehome\ehPrivJob.exe
Task: {53ABC437-1B0B-41C8-BFA8-0949927B2CAE} - System32\Tasks\Microsoft\Windows\Media Center\PBDADiscoveryW1 => C:\Windows\ehome\ehPrivJob.exe
Task: {55FDF64B-3C5A-49F4-9EC4-597B575CA285} - System32\Tasks\Microsoft\Windows\Media Center\InstallPlayReady => C:\Windows\ehome\ehPrivJob.exe
Task: {60C6872D-D8C5-4B88-8980-45D08F81447E} - System32\Tasks\Microsoft\Windows\Media Center\PvrScheduleTask => C:\Windows\ehome\mcupdate.exe
Task: {66373DB8-4A8D-49A8-88A9-7AC45A9257AE} - System32\Tasks\Microsoft\Windows\Media Center\PeriodicScanRetry => C:\Windows\ehome\MCUpdate.exe
Task: {69A85CF5-3B46-41A1-B827-33B63DB62BAE} - System32\Tasks\Adobe Acrobat Update Task => C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe [2016-09-08] (Adobe Systems Incorporated)
Task: {7293FCCA-AC47-4346-9D5F-E0A9DE260C61} - \Microsoft\Windows\Setup\GWXTriggers\OutOfSleep-5d -> No File <==== ATTENTION
Task: {7502276F-9935-472B-ABF9-2F920A8A92EB} - System32\Tasks\Hewlett-Packard\HP Support Assistant\PC Health Analysis => C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\HPSF.exe [2016-08-23] (HP Inc.)
Task: {76028AB5-AC97-4F06-8327-7D5A47A19935} - System32\Tasks\Microsoft\Windows\Media Center\OCURDiscovery => C:\Windows\ehome\ehPrivJob.exe
Task: {7953A881-3F54-4DC6-A2C4-8D0F4AB8AF05} - System32\Tasks\Hewlett-Packard\HP Support Assistant\HP Support Assistant Quick Start => C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\HPSF.exe [2016-08-23] (HP Inc.)
Task: {8019363D-BCAD-4773-B90D-F17D42075CBA} - System32\Tasks\Microsoft\Windows\Media Center\PvrRecoveryTask => C:\Windows\ehome\mcupdate.exe
Task: {864A4654-1B29-4B85-8A8F-1AC23D143017} - \Microsoft\Windows\Setup\gwx\refreshgwxconfigandcontent -> No File <==== ATTENTION
Task: {87C1362C-3742-47B6-8C81-6538E1258203} - System32\Tasks\Hewlett-Packard\HP Active Health\HP Active Health Scan (HPSA) => C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPActiveHealth\ActiveHealth.exe [2016-08-18] (HP Inc.)
Task: {8D77A25D-FD6A-481A-B0D6-9678902CB9A5} - System32\Tasks\Microsoft\Windows\Media Center\mcupdate => C:\Windows\ehome\mcupdate.exe
Task: {9476FD46-509C-405E-A723-F3191093CD98} - \Microsoft\Windows\Setup\gwx\launchtrayprocess -> No File <==== ATTENTION
Task: {97D57FBC-B035-440C-88E7-9E676CD64057} - System32\Tasks\Microsoft\Windows\Media Center\PBDADiscovery => C:\Windows\ehome\ehPrivJob.exe
Task: {9EE88514-786B-4C6B-B761-AD00A3815399} - System32\Tasks\Microsoft\Windows\Media Center\RecordingRestart => C:\Windows\ehome\ehrec.exe
Task: {A67AFEE4-8A57-4634-9B58-0147D5676442} - System32\Tasks\Microsoft\Windows\Media Center\mcupdate_scheduled => C:\Windows\ehome\mcupdate.exe
Task: {ABE81196-0AAC-419A-993A-CA0F9FA7E738} - System32\Tasks\Microsoft\Windows\Media Center\ObjectStoreRecoveryTask => C:\Windows\ehome\mcupdate.exe
Task: {AC32D329-1AFB-40FB-97DE-9A3C3DAD84EA} - System32\Tasks\HPCeeScheduleForPaddy => C:\Program Files (x86)\Hewlett-Packard\HP Ceement\HPCEE.exe [2015-06-16] (Hewlett-Packard)
Task: {B0783751-AFAE-4BFF-B02A-3C74BBADC98E} - System32\Tasks\Microsoft\Windows\Media Center\ConfigureInternetTimeService => C:\Windows\ehome\ehPrivJob.exe
Task: {B9B19DBD-DEB0-463E-B056-B24AF351100E} - \Microsoft\Windows\Setup\GWXTriggers\refreshgwxconfig-B -> No File <==== ATTENTION
Task: {BB891099-3F04-45DA-8DFA-066AB33B0F7D} - System32\Tasks\Microsoft\Windows\Media Center\UpdateRecordPath => C:\Windows\ehome\ehPrivJob.exe
Task: {BD615D59-154D-4007-B4A6-01251AA04433} - \Microsoft\Windows\Setup\GWXTriggers\ScheduleUpgradeTime -> No File <==== ATTENTION
Task: {C0F395F2-9715-4314-A840-2E6C417F6A32} - System32\Tasks\Microsoft\Windows\Media Center\DispatchRecoveryTasks => C:\Windows\ehome\ehPrivJob.exe
Task: {C6429797-F491-4F5C-BD36-6AC08CF60D18} - System32\Tasks\Microsoft\Windows\Media Center\PBDADiscoveryW2 => C:\Windows\ehome\ehPrivJob.exe
Task: {CBC948F4-094E-49B0-A43E-1A0A975816EA} - System32\Tasks\Apple\AppleSoftwareUpdate => C:\Program Files (x86)\Apple Software Update\SoftwareUpdate.exe [2011-06-01] (Apple Inc.)
Task: {CE2BBC8A-6C4B-4CB9-AE83-72AFD4AF3BFA} - \Microsoft\Windows\Setup\gwx\refreshgwxcontent -> No File <==== ATTENTION
Task: {D588F24B-0CB5-48A9-8D4D-52E4F49E1456} - System32\Tasks\Hewlett-Packard\HP Support Assistant\HP Support Solutions Framework Report => C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\Modules\HPSFReport.exe [2016-05-09] (Hewlett-Packard)
Task: {D89EFC2B-6D28-469D-B9D4-75421845C936} - System32\Tasks\Adobe Flash Player Updater => C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerUpdateService.exe [2016-09-21] (Adobe Systems Incorporated)
Task: {DAAC26AC-48E4-44F6-9A40-111EA60CC416} - System32\Tasks\GoogleUpdateTaskMachineCore => C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [2015-09-07] (Google Inc.)
Task: {E1E9ACF7-7C92-4A6F-9CDB-969A6B91D997} - System32\Tasks\Hewlett-Packard\HP Support Assistant\HP Support Solutions Framework Updater => C:\Program Files (x86)\Hewlett-Packard\HP Support Solutions\Modules\HPSSFUpdater.exe [2016-08-03] (HP Inc.)
Task: {EB742961-64B3-4AB1-B927-56DC6435D158} - \Microsoft\Windows\Setup\GWXTriggers\MachineUnlock-5d -> No File <==== ATTENTION
Task: {EDFE8E53-52CB-4A29-9EEE-F4918D2920D1} - System32\Tasks\GoogleUpdateTaskMachineUA => C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [2015-09-07] (Google Inc.)
Task: {EE44F1BC-3A65-4249-BBAC-F4DEB17CDF61} - System32\Tasks\Microsoft\Windows\Media Center\SqlLiteRecoveryTask => C:\Windows\ehome\mcupdate.exe
Task: {F1C5FBDD-5DC6-4AFC-8653-F0D805F6DE51} - \Microsoft\Windows\Setup\GWXTriggers\OutOfIdle-5d -> No File <==== ATTENTION
Task: {F2511BEE-366D-49C8-BB06-D1D74AAAE162} - System32\Tasks\Microsoft\Windows\Media Center\ehDRMInit => C:\Windows\ehome\ehPrivJob.exe
 
(If an entry is included in the fixlist, the task (.job) file will be moved. The file which is running by the task will not be moved.)
 
Task: C:\WINDOWS\Tasks\Adobe Flash Player Updater.job => C:\Windows\SysWOW64\Macromed\Flash\FlashPlayerUpdateService.exe
Task: C:\WINDOWS\Tasks\GoogleUpdateTaskMachineCore.job => C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
Task: C:\WINDOWS\Tasks\GoogleUpdateTaskMachineUA.job => C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
Task: C:\WINDOWS\Tasks\HPCeeScheduleForPaddy.job => C:\Program Files (x86)\Hewlett-Packard\HP Ceement\HPCEE.exe
 
==================== Shortcuts =============================
 
(The entries could be listed to be restored or removed.)
 
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\-10958392170.lnk -> hxxp://www.wunderground.com/radar/mixedcomposite.asp?region=b5&size;=2x&type;=loop
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\-16889357780.lnk -> hxxp://wtop.com/
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\-21249524730.lnk -> hxxp://www.wunderground.com/radar/radblast.asp?zoommode=out#=10&delay;=15&scale;=0.125&noclutter;=1&ID;=LWX&type;=N0R⪫=38.69638062&lon;=-77.85234070&label;=Warrenton, VA&showstorms;=0&map.x;=219&map.y;=426¢erx=400¢ery=288&lightning;=1&smooth;=1&showlabels;=1&rainsnow;=1
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\-2952022830.lnk -> hxxp://saacforum.com/index.php?board=12.0
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\1243244850.lnk -> hxxp://mail.mris.com/a/webmail.php?wsid=ebd093f2fb7d1c56f0f729509a4733950b0c0336
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\13796260060.lnk -> hxxp://www.nascar.com/en_us/sprint-cup-series/leaderboard/leaderboard-live.html
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\16263942420.lnk -> hxxp://www.cbssports.com/
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\17609734960.lnk -> hxxp://www.stltoday.com/sports/baseball/professional/
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\3144898580.lnk -> hxxp://www.intellicast.com/National/Radar/Current.aspx?animate=true
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\6739343990.lnk -> hxxp://www.nascar.com/en_us/sprint-cup-series.html
Shortcut: C:\Users\Paddy\AppData\Local\Microsoft\Windows\RoamingTiles\6964688600.lnk -> hxxp://espn.go.com/olympics/winter/2014/results
 
==================== Loaded Modules (Whitelisted) ==============
 
2015-10-30 03:17 - 2015-10-30 03:17 - 00028672 _____ () C:\WINDOWS\SYSTEM32\efsext.dll
2015-10-30 03:18 - 2015-10-30 03:18 - 00185856 _____ () C:\WINDOWS\SYSTEM32\ism32k.dll
2012-11-13 15:02 - 2012-10-18 15:53 - 00254552 ____N () C:\Program Files (x86)\Cyberlink\Shared files\RichVideo.exe
2012-11-21 19:45 - 2012-10-16 17:44 - 00390672 _____ () C:\Program Files\CyberLink\Shared files\RichVideo64.exe
2016-09-14 08:28 - 2016-09-07 01:39 - 02656952 _____ () C:\WINDOWS\system32\CoreUIComponents.dll
2016-09-14 08:28 - 2016-09-07 01:39 - 02656952 _____ () C:\WINDOWS\System32\CoreUIComponents.dll
2016-08-26 08:54 - 2016-08-26 08:54 - 01864384 _____ () C:\Users\Paddy\AppData\Local\Microsoft\OneDrive\17.3.6517.0809\amd64\ClientTelemetry.dll
2016-04-19 14:32 - 2016-04-19 14:32 - 00144384 _____ () C:\Program Files\WindowsApps\Microsoft.Messaging_2.15.20002.0_x86__8wekyb3d8bbwe\SkypeHost.exe
2016-09-14 08:24 - 2016-09-07 00:10 - 00591360 _____ () C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\Cortana.Core.dll
2016-09-14 08:24 - 2016-09-07 00:10 - 02483200 _____ () C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\Cortana.BackgroundTask.dll
2015-12-22 18:18 - 2015-12-22 18:18 - 00093696 _____ () C:\Windows\SystemApps\ShellExperienceHost_cw5n1h2txyewy\Windows.UI.Shell.SharedUtilities.dll
2016-07-17 20:32 - 2016-06-30 23:48 - 00472064 _____ () C:\Windows\SystemApps\ShellExperienceHost_cw5n1h2txyewy\QuickActions.dll
2016-09-14 08:24 - 2016-09-07 00:15 - 07992832 _____ () C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\CortanaApi.dll
2016-09-14 08:24 - 2016-09-07 00:11 - 00936448 _____ () C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\Cortana.Actions.dll
2016-09-14 08:25 - 2016-09-07 00:13 - 04089856 _____ () C:\Windows\SystemApps\Microsoft.Windows.Cortana_cw5n1h2txyewy\RemindersUI.dll
2016-08-26 08:52 - 2016-08-26 08:52 - 03763712 _____ () C:\Program Files\WindowsApps\Microsoft.WindowsCalculator_10.1608.2213.0_x64__8wekyb3d8bbwe\Calculator.exe
2016-08-15 20:13 - 2016-08-15 20:13 - 00017408 _____ () C:\Program Files\WindowsApps\Microsoft.Windows.Photos_16.722.10060.0_x64__8wekyb3d8bbwe\Microsoft.Photos.exe
2016-08-15 20:13 - 2016-08-15 20:13 - 13475840 _____ () C:\Program Files\WindowsApps\Microsoft.Windows.Photos_16.722.10060.0_x64__8wekyb3d8bbwe\Microsoft.Photos.dll
2016-06-03 08:34 - 2016-06-03 08:34 - 00680448 _____ () C:\Program Files\WindowsApps\Microsoft.Windows.Photos_16.722.10060.0_x64__8wekyb3d8bbwe\Microsoft.DesignCore.dll
2016-03-04 09:16 - 2016-03-04 09:16 - 00291328 _____ () C:\Program Files\WindowsApps\Microsoft.Windows.Photos_16.722.10060.0_x64__8wekyb3d8bbwe\StoreRatingPromotion.dll
2014-04-23 16:05 - 2014-04-23 16:05 - 00073544 _____ () C:\Program Files (x86)\Common Files\Apple\Apple Application Support\zlib1.dll
2014-04-23 16:04 - 2014-04-23 16:04 - 01044808 _____ () C:\Program Files (x86)\Common Files\Apple\Apple Application Support\libxml2.dll
2016-04-19 14:32 - 2016-04-19 14:32 - 00141312 _____ () C:\Program Files\WindowsApps\Microsoft.Messaging_2.15.20002.0_x86__8wekyb3d8bbwe\SkypeBackgroundTasks.dll
2016-04-19 14:32 - 2016-04-19 14:32 - 22284800 _____ () C:\Program Files\WindowsApps\Microsoft.Messaging_2.15.20002.0_x86__8wekyb3d8bbwe\SkyWrap.dll
2016-09-16 19:55 - 2016-09-13 20:38 - 01806152 _____ () C:\Program Files (x86)\Google\Chrome\Application\53.0.2785.116\libglesv2.dll
2016-09-16 19:54 - 2016-09-13 20:38 - 00094024 _____ () C:\Program Files (x86)\Google\Chrome\Application\53.0.2785.116\libegl.dll
2016-09-19 08:18 - 2016-09-12 17:48 - 17754304 _____ () C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\PepperFlash\23.0.0.166\pepflashplayer.dll
 
==================== Alternate Data Streams (Whitelisted) =========
 
(If an entry is included in the fixlist, only the ADS will be removed.)
 
 
==================== Safe Mode (Whitelisted) ===================
 
(If an entry is included in the fixlist, it will be removed from the registry. The "AlternateShell" will be restored.)
 
HKLM\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\mcpltsvc => ""=""
HKLM\SYSTEM\CurrentControlSet\Control\SafeBoot\Network\mcpltsvc => ""=""
 
==================== Association (Whitelisted) ===============
 
(If an entry is included in the fixlist, the registry item will be restored to default or removed.)
 
 
==================== Internet Explorer trusted/restricted ===============
 
(If an entry is included in the fixlist, it will be removed from the registry.)
 
IE trusted site: HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\sentrilock.com -> hxxp://alt.sentrilock.com
 
==================== Hosts content: ===============================
 
(If needed Hosts: directive could be included in the fixlist to reset Hosts.)
 
2009-07-13 22:34 - 2012-12-04 12:19 - 00000027 ____A C:\WINDOWS\system32\Drivers\etc\hosts
 
127.0.0.1       localhost
 
==================== Other Areas ============================
 
(Currently there is no automatic fix for this section.)
 
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Control Panel\Desktop\\Wallpaper -> C:\Users\Paddy\AppData\Local\Microsoft\Windows\Themes\RoamedThemeFiles\DesktopBackground\sept06passlg.jpg
DNS Servers: 10.1.10.1
HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System => (ConsentPromptBehaviorAdmin: 5) (ConsentPromptBehaviorUser: 3) (EnableLUA: 1)
Windows Firewall is enabled.
 
==================== MSCONFIG/TASK MANAGER disabled items ==
 
MSCONFIG\Services: RoxioNow Service => 2
MSCONFIG\startupfolder: C:^ProgramData^Microsoft^Windows^Start Menu^Programs^Startup^Adobe Gamma Loader.lnk => C:\Windows\pss\Adobe Gamma Loader.lnk.CommonStartup
MSCONFIG\startupfolder: C:^ProgramData^Microsoft^Windows^Start Menu^Programs^Startup^ArtecMedia Remote Control.lnk => C:\Windows\pss\ArtecMedia Remote Control.lnk.CommonStartup
MSCONFIG\startupfolder: C:^ProgramData^Microsoft^Windows^Start Menu^Programs^Startup^ArtecMedia Schedule Recording.lnk => C:\Windows\pss\ArtecMedia Schedule Recording.lnk.CommonStartup
MSCONFIG\startupreg: APSDaemon => "C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe"
MSCONFIG\startupreg: BDRegion => C:\Program Files (x86)\Cyberlink\Shared Files\brs.exe
MSCONFIG\startupreg: BeatsOSDApp => C:\Program Files\IDT\WDM\beats64.exe
MSCONFIG\startupreg: CLMLServer => "C:\Program Files (x86)\Cyberlink\Power2Go\CLMLSvc.exe"
MSCONFIG\startupreg: PDF Complete => C:\Program Files (x86)\PDF Complete\pdfsty.exe
MSCONFIG\startupreg: PDVD9LanguageShortcut => "C:\Program Files (x86)\CyberLink\PowerDVD9\Language\Language.exe"
MSCONFIG\startupreg: QuickTime Task => "C:\Program Files (x86)\QuickTime\QTTask.exe" -atboottime
MSCONFIG\startupreg: RemoteControl9 => "C:\Program Files (x86)\CyberLink\PowerDVD9\PDVD9Serv.exe"
MSCONFIG\startupreg: UpdateP2GoShortCut => "C:\Program Files (x86)\CyberLink\Power2Go\MUITransfer\MUIStartMenu.exe" "C:\Program Files (x86)\CyberLink\Power2Go" UpdateWithCreateOnce "SOFTWARE\CyberLink\Power2Go\6.0"
MSCONFIG\startupreg: UpdatePDRShortCut => "C:\Program Files (x86)\CyberLink\PowerDirector\MUITransfer\MUIStartMenu.exe" "C:\Program Files (x86)\CyberLink\PowerDirector" UpdateWithCreateOnce "Software\CyberLink\PowerDirector\7.0"
MSCONFIG\startupreg: UpdatePSTShortCut => "C:\Program Files (x86)\CyberLink\Blu-ray Disc Suite\MUITransfer\MUIStartMenu.exe" "C:\Program Files (x86)\CyberLink\Blu-ray Disc Suite" UpdateWithCreateOnce "Software\CyberLink\PowerStarter"
HKLM\…\StartupApproved\Run: => "Logitech Download Assistant"
HKLM\…\StartupApproved\Run32: => "APSDaemon"
HKLM\…\StartupApproved\Run32: => "iTunesHelper"
HKLM\…\StartupApproved\Run32: => "SunJavaUpdateSched"
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\…\StartupApproved\Run: => "OneDrive"
 
==================== FirewallRules (Whitelisted) ===============
 
(If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.)
 
FirewallRules: [vm-monitoring-nb-session] => (Allow) LPort=139
FirewallRules: [MSMQ-In-TCP] => (Allow) %systemroot%\system32\mqsvc.exe
FirewallRules: [MSMQ-Out-TCP] => (Allow) %systemroot%\system32\mqsvc.exe
FirewallRules: [MSMQ-In-UDP] => (Allow) %systemroot%\system32\mqsvc.exe
FirewallRules: [MSMQ-Out-UDP] => (Allow) %systemroot%\system32\mqsvc.exe
FirewallRules: [WCF-NetTcpActivator-In-TCP-64bit] => (Allow) LPort=808
FirewallRules: [{DEABC349-19EB-4369-B572-3C279236C045}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPWarrantyCheck\HPDeviceDetection3.exe
FirewallRules: [{DB444F26-0E1B-4A32-87A0-01F64E405CC5}] => (Allow) C:\Program Files (x86)\iTunes\iTunes.exe
FirewallRules: [{26CFCF99-B53F-4CEA-876C-EDE9669B0813}] => (Allow) C:\Program Files (x86)\Bonjour\mDNSResponder.exe
FirewallRules: [{83251747-F430-4973-8017-E7DD953AEEEB}] => (Allow) C:\Program Files (x86)\Bonjour\mDNSResponder.exe
FirewallRules: [{E8C4F0AA-9C29-45C3-9B88-6B93E44A7C28}] => (Allow) C:\Program Files\Bonjour\mDNSResponder.exe
FirewallRules: [{4F61D85B-71AA-494C-AADF-DCF60AA4262A}] => (Allow) C:\Program Files\Bonjour\mDNSResponder.exe
FirewallRules: [{69BAEFC9-DB18-4E80-8861-4F0C45280296}] => (Allow) C:\Program Files\Common Files\McAfee\Platform\McSvcHost\McSvHost.exe
FirewallRules: [{B55735F8-54C1-4C9E-95D0-D9FE81A1A972}] => (Allow) C:\Program Files\Common Files\McAfee\Platform\McSvcHost\McSvHost.exe
FirewallRules: [{5EA62BE4-492D-43E6-96E1-CA5B927DE56E}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\HP Support Framework\Resources\HPWarrantyCheck\HPWarrantyChecker.exe
FirewallRules: [{04FF7D16-EAA8-4C59-89F4-E2E24157BE24}] => (Allow) C:\Program Files\CyberLink\PowerDirector11\PDR10.EXE
FirewallRules: [{EB24B7D9-7B73-45C3-8781-170972332BDA}] => (Allow) C:\Program Files (x86)\CyberLink\PowerDVD9\PowerDVD9.EXE
FirewallRules: [{16ABADF5-B2D4-458C-9C1C-38BFE261868A}] => (Allow) C:\Program Files (x86)\CyberLink\PowerDVD9\PowerDVD Cinema\PowerDVDCinema.exe
FirewallRules: [{6FDDB205-C907-493A-95A9-7DD83088FA49}] => (Allow) C:\Program Files (x86)\CyberLink\PowerDirector\PDR.EXE
FirewallRules: [{AAD33E6F-AD94-43D5-83CE-EFE2879FC720}] => (Allow) C:\Program Files\Common Files\McAfee\McSvcHost\McSvHost.exe
FirewallRules: [{4F72BB7E-3F36-433F-A5A8-4BC31BFBCDCD}] => (Allow) c:\Program Files (x86)\CyberLink\PowerDVD10\PowerDVD10.EXE
FirewallRules: [{6ADE23A3-B480-469A-AC0B-936F52CA998D}] => (Allow) c:\Program Files (x86)\CyberLink\PowerDVD10\PowerDVD Cinema\PowerDVDCinema10.exe
FirewallRules: [{BC51E63F-AB23-485F-ABD1-CE519591ABB0}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\HP LinkUp\HP LinkUp Viewer.exe
FirewallRules: [{1B073C0A-FFFF-4A00-BC40-663D4FAAD941}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\HP LinkUp\HP LinkUp Viewer.exe
FirewallRules: [{8AF4995C-056B-4C9B-8A50-0C0C6B012D62}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\Remote Graphics Receiver\rgreceiver.exe
FirewallRules: [{697D68E3-44D6-4E44-A175-92C8FA4A871D}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\Remote Graphics Receiver\rgreceiver.exe
FirewallRules: [{34C0235A-132B-46C7-A9F3-C4B87383F530}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\MediaSmart\RoxioNow\RNow.exe
FirewallRules: [{9ACFF156-5CD5-4E95-BB1A-0D8D489C25C1}] => (Allow) C:\Program Files (x86)\Hewlett-Packard\MediaSmart\RoxioNow\RNow.exe
FirewallRules: [{1EDFA286-AFBC-4BD1-B3B9-92DBE348E59A}] => (Allow) C:\Program Files (x86)\Roxio\RoxioNow Player\RNowShell.exe
FirewallRules: [{F7DF14D0-003A-4DD1-ABEC-359237F69087}] => (Allow) C:\Program Files (x86)\Roxio\RoxioNow Player\RNowShell.exe
FirewallRules: [{C3850B55-3143-456A-8C28-1640BB664605}] => (Allow) C:\Program Files\VueScan\vuescan.exe
FirewallRules: [{1B5B1700-2798-4AD9-A4A2-A4EBFFD6CE0A}] => (Allow) C:\Program Files\VueScan\vuescan.exe
FirewallRules: [{E4B2786A-C4F8-4D82-B600-004EF2A3E114}] => (Allow) C:\Program Files (x86)\Windows Live\Contacts\wlcomm.exe
FirewallRules: [{16F090B0-5A0E-4115-AC4C-EF28DDC47EF8}] => (Allow) LPort=2869
FirewallRules: [{33BAF1D9-78B1-415C-A2B7-F20BF1468EBE}] => (Allow) LPort=1900
FirewallRules: [{64F6EAA3-62DC-4891-8260-7AA040AA0979}] => (Allow) C:\Program Files (x86)\Windows Live\Messenger\msnmsgr.exe
FirewallRules: [{9B5A3CDC-A091-4C33-B9F5-24AB04908E31}] => (Allow) C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
 
==================== Restore Points =========================
 
01-09-2016 10:05:52 Windows Update
11-09-2016 21:26:51 Scheduled Checkpoint
19-09-2016 17:56:47 Scheduled Checkpoint
21-09-2016 16:00:20 JRT Pre-Junkware Removal
 
==================== Faulty Device Manager Devices =============
 
Name: 
Description: 
Class Guid: 
Manufacturer: 
Service: 
Problem: : The drivers for this device are not installed. (Code 28)
Resolution: To install the drivers for this device, click "Update Driver", which starts the Hardware Update wizard.
 
 
==================== Event log errors: =========================
 
Application errors:
==================
Error: (09/21/2016 06:47:45 PM) (Source: Application Error) (EventID: 1000) (User: )
Description: Faulting application name: chrome.exe, version: 53.0.2785.116, time stamp: 0x57d88ea0
Faulting module name: pepflashplayer.dll, version: 23.0.0.162, time stamp: 0x57c4c8b0
Exception code: 0xc0000409
Fault offset: 0x008587ae
Faulting process id: 0x14e8
Faulting application start time: 0x01d21455a8b8b718
Faulting application path: C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
Faulting module path: C:\Users\Paddy\AppData\Local\Google\Chrome\User Data\PepperFlash\23.0.0.166\pepflashplayer.dll
Report Id: 900c0877-d8ad-4a34-b977-ee34eb9b7025
Faulting package full name: 
Faulting package-relative application ID:
 
Error: (09/21/2016 06:22:08 PM) (Source: SideBySide) (EventID: 63) (User: )
Description: Activation context generation failed for "c:\program files (x86)\common files\adobe air\versions\1.0\Adobe AIR.dll".Error in manifest or policy file "c:\program files (x86)\common files\adobe air\versions\1.0\Adobe AIR.dll" on line 3.
The value "MAJOR_VERSION.MINOR_VERSION.BUILD_NUMBER_MAJOR.BUILD_NUMBER_MINOR" of attribute "version" in element "assemblyIdentity" is invalid.
 
Error: (09/21/2016 06:20:37 PM) (Source: SideBySide) (EventID: 78) (User: )
Description: Activation context generation failed for "c:\program files (x86)\eset\eset online scanner\ESETSmartInstaller.exe".Error in manifest or policy file "" on line .
A component version required by the application conflicts with another component version already active.
Conflicting components are:.
Component 1: C:\WINDOWS\WinSxS\manifests\x86_microsoft.windows.common-controls_6595b64144ccf1df_6.0.10586.589_none_ea8aeaa1b9b5d5d4.manifest.
Component 2: C:\WINDOWS\WinSxS\manifests\amd64_microsoft.windows.common-controls_6595b64144ccf1df_6.0.10586.589_none_a2ddb3caa539acce.manifest.
 
Error: (09/21/2016 04:04:35 PM) (Source: CVHSVC) (EventID: 100) (User: )
Description: Information only.
(Patch task for {90140011-0066-0409-0000-0000000FF1CE}): DownloadLatest Failed: HTTP status 403: The client does not have sufficient access rights to the requested server object.
 
Error: (09/21/2016 04:00:34 PM) (Source: Microsoft-Windows-CAPI2) (EventID: 513) (User: )
Description: Cryptographic Services failed while processing the OnIdentity() call in the System Writer Object.
 
Details:
AddLegacyDriverFiles: Unable to back up image of binary Microsoft Link-Layer Discovery Protocol.
 
System Error:
Access is denied.
.
 
Error: (09/21/2016 12:23:39 AM) (Source: CVHSVC) (EventID: 100) (User: )
Description: Information only.
(Patch task for {90140011-0066-0409-0000-0000000FF1CE}): DownloadLatest Failed: HTTP status 403: The client does not have sufficient access rights to the requested server object.
 
Error: (09/19/2016 05:57:00 PM) (Source: Microsoft-Windows-CAPI2) (EventID: 513) (User: )
Description: Cryptographic Services failed while processing the OnIdentity() call in the System Writer Object.
 
Details:
AddLegacyDriverFiles: Unable to back up image of binary Microsoft Link-Layer Discovery Protocol.
 
System Error:
Access is denied.
.
 
Error: (09/18/2016 08:56:02 PM) (Source: Windows Backup) (EventID: 4103) (User: )
Description: The backup did not complete because of an error writing to the backup location J:\. The error is: The backup location cannot be found or is not valid. Review your backup settings and check the backup location. (0x81000006).
 
Error: (09/18/2016 08:52:49 PM) (Source: Bonjour Service) (EventID: 100) (User: )
Description: Local Hostname Paddy1.local already in use; will try Paddy1-2.local instead
 
Error: (09/18/2016 08:52:49 PM) (Source: Bonjour Service) (EventID: 100) (User: )
Description: mDNSCoreReceiveResponse: ProbeCount 2; will deregister    4 Paddy1.local. Addr 10.1.10.11
 
 
System errors:
=============
Error: (09/21/2016 03:57:41 PM) (Source: DCOM) (EventID: 10016) (User: PADDY1)
Description: The machine-default permission settings do not grant Local Activation permission for the COM Server application with CLSID 
{C2F03A33-21F5-47FA-B4BB-156362A2F239}
 and APPID 
{316CDED5-E4AE-4B15-9113-7055D84DCC97}
 to the user Paddy1\Paddy SID (S-1-5-21-648858125-4165233436-1298442668-1001) from address LocalHost (Using LRPC) running in the application container Microsoft.Windows.Cortana_1.6.1.52_neutral_neutral_cw5n1h2txyewy SID (S-1-15-2-1861897761-1695161497-2927542615-642690995-327840285-2659745135-2630312742). This security permission can be modified using the Component Services administrative tool.
 
Error: (09/21/2016 03:57:40 PM) (Source: DCOM) (EventID: 10016) (User: PADDY1)
Description: The machine-default permission settings do not grant Local Activation permission for the COM Server application with CLSID 
{C2F03A33-21F5-47FA-B4BB-156362A2F239}
 and APPID 
{316CDED5-E4AE-4B15-9113-7055D84DCC97}
 to the user Paddy1\Paddy SID (S-1-5-21-648858125-4165233436-1298442668-1001) from address LocalHost (Using LRPC) running in the application container Microsoft.Windows.Cortana_1.6.1.52_neutral_neutral_cw5n1h2txyewy SID (S-1-15-2-1861897761-1695161497-2927542615-642690995-327840285-2659745135-2630312742). This security permission can be modified using the Component Services administrative tool.
 
Error: (09/21/2016 03:57:28 PM) (Source: DCOM) (EventID: 10016) (User: PADDY1)
Description: The machine-default permission settings do not grant Local Activation permission for the COM Server application with CLSID 
{C2F03A33-21F5-47FA-B4BB-156362A2F239}
 and APPID 
{316CDED5-E4AE-4B15-9113-7055D84DCC97}
 to the user Paddy1\Paddy SID (S-1-5-21-648858125-4165233436-1298442668-1001) from address LocalHost (Using LRPC) running in the application container Microsoft.Windows.Cortana_1.6.1.52_neutral_neutral_cw5n1h2txyewy SID (S-1-15-2-1861897761-1695161497-2927542615-642690995-327840285-2659745135-2630312742). This security permission can be modified using the Component Services administrative tool.
 
Error: (09/21/2016 03:57:27 PM) (Source: DCOM) (EventID: 10016) (User: PADDY1)
Description: The machine-default permission settings do not grant Local Activation permission for the COM Server application with CLSID 
{C2F03A33-21F5-47FA-B4BB-156362A2F239}
 and APPID 
{316CDED5-E4AE-4B15-9113-7055D84DCC97}
 to the user Paddy1\Paddy SID (S-1-5-21-648858125-4165233436-1298442668-1001) from address LocalHost (Using LRPC) running in the application container Microsoft.Windows.Cortana_1.6.1.52_neutral_neutral_cw5n1h2txyewy SID (S-1-15-2-1861897761-1695161497-2927542615-642690995-327840285-2659745135-2630312742). This security permission can be modified using the Component Services administrative tool.
 
Error: (09/21/2016 03:56:41 PM) (Source: DCOM) (EventID: 10016) (User: PADDY1)
Description: The machine-default permission settings do not grant Local Activation permission for the COM Server application with CLSID 
{C2F03A33-21F5-47FA-B4BB-156362A2F239}
 and APPID 
{316CDED5-E4AE-4B15-9113-7055D84DCC97}
 to the user Paddy1\Paddy SID (S-1-5-21-648858125-4165233436-1298442668-1001) from address LocalHost (Using LRPC) running in the application container Microsoft.Windows.Cortana_1.6.1.52_neutral_neutral_cw5n1h2txyewy SID (S-1-15-2-1861897761-1695161497-2927542615-642690995-327840285-2659745135-2630312742). This security permission can be modified using the Component Services administrative tool.
 
Error: (09/21/2016 03:54:17 PM) (Source: Service Control Manager) (EventID: 7001) (User: )
Description: The NetTcpActivator service depends on the NetTcpPortSharing service which failed to start because of the following error: 
The service cannot be started, either because it is disabled or because it has no enabled devices associated with it.
 
Error: (09/21/2016 03:52:34 PM) (Source: Service Control Manager) (EventID: 7031) (User: )
Description: The User Data Access_26dec2c service terminated unexpectedly.  It has done this 1 time(s).  The following corrective action will be taken in 10000 milliseconds: Restart the service.
 
 
CodeIntegrity:
===================================
  Date: 2016-09-21 20:47:25.365
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Bonjour\mdnsNSP.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 20:47:25.342
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Bonjour\mdnsNSP.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 18:17:54.160
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Bonjour\mdnsNSP.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 18:17:54.146
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Bonjour\mdnsNSP.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 16:04:54.473
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Bonjour\mdnsNSP.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 16:04:54.447
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Bonjour\mdnsNSP.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 15:51:57.969
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Microsoft Silverlight\xapauthenticodesip.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 15:51:57.957
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Microsoft Silverlight\xapauthenticodesip.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 15:51:57.922
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Microsoft Silverlight\xapauthenticodesip.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
  Date: 2016-09-21 15:51:57.840
  Description: Code Integrity determined that a process (\Device\HarddiskVolume2\Program Files\Windows Defender\MsMpEng.exe) attempted to load \Device\HarddiskVolume2\Program Files\Microsoft Silverlight\xapauthenticodesip.dll that did not meet the Custom 3 / Antimalware signing level requirements.
 
 
==================== Memory info =========================== 
 
Processor: Intel(R) Core(TM) i7-2600 CPU @ 3.40GHz
Percentage of memory in use: 51%
Total physical RAM: 8172.31 MB
Available physical RAM: 3943.5 MB
Total Virtual: 12140.31 MB
Available Virtual: 6908.85 MB
 
==================== Drives ================================
 
Drive c: (Paddy) (Fixed) (Total:975.57 GB) (Free:522.14 GB) NTFS
Drive d: (HP_RECOVERY) (Fixed) (Total:11.44 GB) (Free:1.39 GB) NTFS ==>[system with boot components (obtained from drive)]
Drive x: (Scratch Disk) (Fixed) (Total:410.16 GB) (Free:410.01 GB) NTFS
 
==================== MBR & Partition Table ==================
 
========================================================
Disk: 0 (Size: 1397.3 GB) (Disk ID: FBDF8A01)
Partition 1: (Active) - (Size=100 MB) - (Type=07 NTFS)
Partition 2: (Not Active) - (Size=975.6 GB) - (Type=07 NTFS)
Partition 3: (Not Active) - (Size=410.2 GB) - (Type=OF Extended)
Partition 4: (Not Active) - (Size=11.4 GB) - (Type=07 NTFS)
 
==================== End of Addition.txt ============================
 
 
Malwarebytes Anti-Malware
www.malwarebytes.org
 
Scan Date: 9/21/2016
Scan Time: 7:27 PM
Logfile: 
Administrator: Yes
 
Version: 2.2.1.1043
Malware Database: v2016.09.21.14
Rootkit Database: v2016.08.15.01
License: Trial
Malware Protection: Enabled
Malicious Website Protection: Enabled
Self-protection: Disabled
 
OS: Windows 10
CPU: x64
File System: NTFS
User: Paddy
 
Scan Type: Threat Scan
Result: Completed
Objects Scanned: 396450
Time Elapsed: 15 min, 48 sec
 
Memory: Enabled
Startup: Enabled
Filesystem: Enabled
Archives: Enabled
Rootkits: Disabled
Heuristics: Enabled
PUP: Enabled
PUM: Enabled
 
Processes: 0
(No malicious items detected)
 
Modules: 0
(No malicious items detected)
 
Registry Keys: 0
(No malicious items detected)
 
Registry Values: 0
(No malicious items detected)
 
Registry Data: 0
(No malicious items detected)
 
Folders: 0
(No malicious items detected)
 
Files: 0
(No malicious items detected)
 
Physical Sectors: 0
(No malicious items detected)
 
 
(end)

Good Morning


Your FRST logs are looking so much better but a few more things to remove.  C:\Program Files\VueScan <– Is this a program that you installed and use ??


Open notepad , Go to Start –> All Programs –> Accessories –> Notepad.

Please copy the entire contents Inside of the code box below beginning with START and ending with END
(To do this highlight the contents of the box, right click on it and select copy. Right-click in the open notepad and select Paste).
Name the file Fixlist.txt , Save it to your desktop where you have FRST/FRST64 or the fix wont work. Right Click on FRST/FRST64 and select RUN AS ADMINISTRATOR Then click on >FIX< (Not Scan) It won't take long, after your computer reboots you will find a FIXLOG.TXT on your desktop, post it please
 
Start
CloseProcesses:
CreateRestorePoint:
HKLM\SOFTWARE\Policies\Microsoft\Internet Explorer: Restriction <======= ATTENTION
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\Policies\Microsoft\Internet Explorer: Restriction <======= ATTENTION
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\Main,Start Page = 
SearchScopes: HKLM -> DefaultScope value is missing
SearchScopes: HKLM -> {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL = hxxp://www.bing.com/search?q={searchTerms}&form=HPDTDF&pc=HPDTDF&src=IE-SearchBox
SearchScopes: HKLM -> {d43b3890-80c7-4010-a95d-1e77b5924dc3} URL = hxxp://en.wikipedia.org/wiki/Special:Search?search={searchTerms}
SearchScopes: HKLM-x32 -> DefaultScope {863FD1AF-2869-4CE9-A223-2BA9F9620E61} URL = 
SearchScopes: HKLM-x32 -> {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL = hxxp://www.bing.com/search?q={searchTerms}&form=HPDTDF&pc=HPDTDF&src=IE-SearchBox
SearchScopes: HKLM-x32 -> {d43b3890-80c7-4010-a95d-1e77b5924dc3} URL = hxxp://en.wikipedia.org/wiki/Special:Search?search={searchTerms}
SearchScopes: HKU\S-1-5-21-648858125-4165233436-1298442668-1001 -> DefaultScope {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL = 
StartMenuInternet: FIREFOX.EXE - firefox.exe
WhiteSmoke New Toolbar (HKLM-x32\…\WhiteSmoke_New Toolbar) (Version: 6.13.50.5 - WhiteSmoke New) <==== ATTENTION
Task: {08C5B79B-286B-438C-9068-A979952C531F} - \Microsoft\Windows\Setup\GWXTriggers\ScheduleUpgradeReminderTime -> No File <==== ATTENTION
Task: {0987D9CD-C136-4608-81D4-64E705CAAAD4} - \Microsoft\Windows\Setup\GWXTriggers\Logon-5d -> No File <==== ATTENTION
Task: {2F04F48E-5A44-435C-AB51-3BE5C3C1CA62} - \Microsoft\Windows\Setup\gwx\runappraiser -> No File <==== ATTENTION
Task: {356A9E84-A83A-4B9C-9D93-B133D8480A15} - \Microsoft\Windows\Setup\gwx\refreshgwxconfig -> No File <==== ATTENTION
Task: {36FE09F7-3866-4448-8EA0-5A57BA498920} - \Microsoft\Windows\Setup\GWXTriggers\Time-5d -> No File <==== ATTENTION
Task: {7293FCCA-AC47-4346-9D5F-E0A9DE260C61} - \Microsoft\Windows\Setup\GWXTriggers\OutOfSleep-5d -> No File <==== ATTENTION
Task: {864A4654-1B29-4B85-8A8F-1AC23D143017} - \Microsoft\Windows\Setup\gwx\refreshgwxconfigandcontent -> No File <==== ATTENTION
Task: {9476FD46-509C-405E-A723-F3191093CD98} - \Microsoft\Windows\Setup\gwx\launchtrayprocess -> No File <==== ATTENTION
Task: {B9B19DBD-DEB0-463E-B056-B24AF351100E} - \Microsoft\Windows\Setup\GWXTriggers\refreshgwxconfig-B -> No File <==== ATTENTION
Task: {BD615D59-154D-4007-B4A6-01251AA04433} - \Microsoft\Windows\Setup\GWXTriggers\ScheduleUpgradeTime -> No File <==== ATTENTION
Task: {CE2BBC8A-6C4B-4CB9-AE83-72AFD4AF3BFA} - \Microsoft\Windows\Setup\gwx\refreshgwxcontent -> No File <==== ATTENTION
Task: {EB742961-64B3-4AB1-B927-56DC6435D158} - \Microsoft\Windows\Setup\GWXTriggers\MachineUnlock-5d -> No File <==== ATTENTION
Task: {F1C5FBDD-5DC6-4AFC-8653-F0D805F6DE51} - \Microsoft\Windows\Setup\GWXTriggers\OutOfIdle-5d -> No File <==== ATTENTION
CMD: ipconfig /flushdns
Hosts:
EmptyTemp:
End
NOTICE: This script was written specifically for this user, for use on that particular machine. Running this on another machine may cause damage to your operating system
Ken,  Yes, VueScan is the only program I could find that would support my SCSI Epson Expression 636 scanner that still works wonderfully….  Fixlog.txt contents pasted below…  Thanks again for your assistance!
 
Regards, Bob
 
Fix result of Farbar Recovery Scan Tool (x64) Version: 21-09-2016
Ran by [removed] (22-09-2016 08:35:33) Run:1
Running from C:\Users\[removed]\Desktop
[removed]
Boot Mode: Normal
==============================================
 
fixlist content:
*****************
Start
CloseProcesses:
CreateRestorePoint:
HKLM\SOFTWARE\Policies\Microsoft\Internet Explorer: Restriction <======= ATTENTION
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\Policies\Microsoft\Internet Explorer: Restriction <======= ATTENTION
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\Main,Start Page = 
SearchScopes: HKLM -> DefaultScope value is missing
SearchScopes: HKLM -> {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL = hxxp://www.bing.com/search?q={searchTerms}&form=HPDTDF&pc=HPDTDF&src=IE-SearchBox
SearchScopes: HKLM -> {d43b3890-80c7-4010-a95d-1e77b5924dc3} URL = hxxp://en.wikipedia.org/wiki/Special:Search?search={searchTerms}
SearchScopes: HKLM-x32 -> DefaultScope {863FD1AF-2869-4CE9-A223-2BA9F9620E61} URL = 
SearchScopes: HKLM-x32 -> {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL = hxxp://www.bing.com/search?q={searchTerms}&form=HPDTDF&pc=HPDTDF&src=IE-SearchBox
SearchScopes: HKLM-x32 -> {d43b3890-80c7-4010-a95d-1e77b5924dc3} URL = hxxp://en.wikipedia.org/wiki/Special:Search?search={searchTerms}
SearchScopes: HKU\S-1-5-21-648858125-4165233436-1298442668-1001 -> DefaultScope {0633EE93-D776-472f-A0FF-E1416B8B2E3A} URL = 
StartMenuInternet: FIREFOX.EXE - firefox.exe
WhiteSmoke New Toolbar (HKLM-x32\…\WhiteSmoke_New Toolbar) (Version: 6.13.50.5 - WhiteSmoke New) <==== ATTENTION
Task: {08C5B79B-286B-438C-9068-A979952C531F} - \Microsoft\Windows\Setup\GWXTriggers\ScheduleUpgradeReminderTime -> No File <==== ATTENTION
Task: {0987D9CD-C136-4608-81D4-64E705CAAAD4} - \Microsoft\Windows\Setup\GWXTriggers\Logon-5d -> No File <==== ATTENTION
Task: {2F04F48E-5A44-435C-AB51-3BE5C3C1CA62} - \Microsoft\Windows\Setup\gwx\runappraiser -> No File <==== ATTENTION
Task: {356A9E84-A83A-4B9C-9D93-B133D8480A15} - \Microsoft\Windows\Setup\gwx\refreshgwxconfig -> No File <==== ATTENTION
Task: {36FE09F7-3866-4448-8EA0-5A57BA498920} - \Microsoft\Windows\Setup\GWXTriggers\Time-5d -> No File <==== ATTENTION
Task: {7293FCCA-AC47-4346-9D5F-E0A9DE260C61} - \Microsoft\Windows\Setup\GWXTriggers\OutOfSleep-5d -> No File <==== ATTENTION
Task: {864A4654-1B29-4B85-8A8F-1AC23D143017} - \Microsoft\Windows\Setup\gwx\refreshgwxconfigandcontent -> No File <==== ATTENTION
Task: {9476FD46-509C-405E-A723-F3191093CD98} - \Microsoft\Windows\Setup\gwx\launchtrayprocess -> No File <==== ATTENTION
Task: {B9B19DBD-DEB0-463E-B056-B24AF351100E} - \Microsoft\Windows\Setup\GWXTriggers\refreshgwxconfig-B -> No File <==== ATTENTION
Task: {BD615D59-154D-4007-B4A6-01251AA04433} - \Microsoft\Windows\Setup\GWXTriggers\ScheduleUpgradeTime -> No File <==== ATTENTION
Task: {CE2BBC8A-6C4B-4CB9-AE83-72AFD4AF3BFA} - \Microsoft\Windows\Setup\gwx\refreshgwxcontent -> No File <==== ATTENTION
Task: {EB742961-64B3-4AB1-B927-56DC6435D158} - \Microsoft\Windows\Setup\GWXTriggers\MachineUnlock-5d -> No File <==== ATTENTION
Task: {F1C5FBDD-5DC6-4AFC-8653-F0D805F6DE51} - \Microsoft\Windows\Setup\GWXTriggers\OutOfIdle-5d -> No File <==== ATTENTION
CMD: ipconfig /flushdns
Hosts:
EmptyTemp:
End
*****************
 
Processes closed successfully.
Restore point was successfully created.
"HKLM\SOFTWARE\Policies\Microsoft\Internet Explorer" => key removed successfully
"HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\Policies\Microsoft\Internet Explorer" => key removed successfully
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\Software\Microsoft\Internet Explorer\Main\\Start Page => value restored successfully
HKLM\SOFTWARE\Microsoft\Internet Explorer\SearchScopes\\DefaultScope => value restored successfully
"HKLM\SOFTWARE\Microsoft\Internet Explorer\SearchScopes\{0633EE93-D776-472f-A0FF-E1416B8B2E3A}" => key removed successfully
HKCR\CLSID\{0633EE93-D776-472f-A0FF-E1416B8B2E3A} => key not found. 
"HKLM\SOFTWARE\Microsoft\Internet Explorer\SearchScopes\{d43b3890-80c7-4010-a95d-1e77b5924dc3}" => key removed successfully
HKCR\CLSID\{d43b3890-80c7-4010-a95d-1e77b5924dc3} => key not found. 
HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\SearchScopes\\DefaultScope => value restored successfully
"HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\SearchScopes\{0633EE93-D776-472f-A0FF-E1416B8B2E3A}" => key removed successfully
HKCR\Wow6432Node\CLSID\{0633EE93-D776-472f-A0FF-E1416B8B2E3A} => key not found. 
"HKLM\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\SearchScopes\{d43b3890-80c7-4010-a95d-1e77b5924dc3}" => key removed successfully
HKCR\Wow6432Node\CLSID\{d43b3890-80c7-4010-a95d-1e77b5924dc3} => key not found. 
HKU\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\Microsoft\Internet Explorer\SearchScopes\\DefaultScope => value removed successfully
HKLM\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\open\command\\Default => value restored successfully
WhiteSmoke New Toolbar (HKLM-x32\…\WhiteSmoke_New Toolbar) (Version: 6.13.50.5 - WhiteSmoke New) <==== ATTENTION => Error: No automatic fix found for this entry.
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{08C5B79B-286B-438C-9068-A979952C531F}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{08C5B79B-286B-438C-9068-A979952C531F}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\GWXTriggers\ScheduleUpgradeReminderTime" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Logon\{0987D9CD-C136-4608-81D4-64E705CAAAD4}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{0987D9CD-C136-4608-81D4-64E705CAAAD4}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\GWXTriggers\Logon-5d" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{2F04F48E-5A44-435C-AB51-3BE5C3C1CA62}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{2F04F48E-5A44-435C-AB51-3BE5C3C1CA62}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\gwx\runappraiser" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{356A9E84-A83A-4B9C-9D93-B133D8480A15}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{356A9E84-A83A-4B9C-9D93-B133D8480A15}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\gwx\refreshgwxconfig" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{36FE09F7-3866-4448-8EA0-5A57BA498920}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{36FE09F7-3866-4448-8EA0-5A57BA498920}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\GWXTriggers\Time-5d" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{7293FCCA-AC47-4346-9D5F-E0A9DE260C61}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{7293FCCA-AC47-4346-9D5F-E0A9DE260C61}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\GWXTriggers\OutOfSleep-5d" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{864A4654-1B29-4B85-8A8F-1AC23D143017}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{864A4654-1B29-4B85-8A8F-1AC23D143017}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\gwx\refreshgwxconfigandcontent" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Logon\{9476FD46-509C-405E-A723-F3191093CD98}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{9476FD46-509C-405E-A723-F3191093CD98}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\gwx\launchtrayprocess" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{B9B19DBD-DEB0-463E-B056-B24AF351100E}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{B9B19DBD-DEB0-463E-B056-B24AF351100E}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\GWXTriggers\refreshgwxconfig-B" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{BD615D59-154D-4007-B4A6-01251AA04433}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{BD615D59-154D-4007-B4A6-01251AA04433}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\GWXTriggers\ScheduleUpgradeTime" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{CE2BBC8A-6C4B-4CB9-AE83-72AFD4AF3BFA}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{CE2BBC8A-6C4B-4CB9-AE83-72AFD4AF3BFA}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\gwx\refreshgwxcontent" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{EB742961-64B3-4AB1-B927-56DC6435D158}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{EB742961-64B3-4AB1-B927-56DC6435D158}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\GWXTriggers\MachineUnlock-5d" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Plain\{F1C5FBDD-5DC6-4AFC-8653-F0D805F6DE51}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{F1C5FBDD-5DC6-4AFC-8653-F0D805F6DE51}" => key removed successfully
"HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\Microsoft\Windows\Setup\GWXTriggers\OutOfIdle-5d" => key removed successfully
 
========= ipconfig /flushdns =========
 
 
Windows IP Configuration
 
Successfully flushed the DNS Resolver Cache.
 
========= End of CMD: =========
 
C:\Windows\System32\Drivers\etc\hosts => moved successfully
Hosts restored successfully.
 
=========== EmptyTemp: ==========
 
BITS transfer queue => 32768 B
DOMStore, IE Recovery, AppCache, Feeds Cache, Thumbcache, IconCache => 231757553 B
Java, Flash, Steam htmlcache => 248895 B
Windows/system/drivers => 36267489 B
Edge => 72220293 B
Chrome => 1228271112 B
Firefox => 0 B
Opera => 0 B
 
Temp, IE cache, history, cookies, recent:
Default => 16674 B
ProgramData => 0 B
Public => 0 B
systemprofile => 128 B
systemprofile32 => 128 B
LocalService => 3346 B
NetworkService => 5914 B
Paddy => 1293594358 B
DefaultAppPool => 16674 B
 
RecycleBin => 74795919 B
EmptyTemp: => 2.7 GB temporary data Removed.
 
================================
 
 
The system needed a reboot.
 
==== End of Fixlog 08:41:01 ====

It may be gone but take a look in Programs and Features in the Control Panel for WhiteSmoke and if its still there try to uninstall it


How is your system behaving now ??

Ken,  Whitesmoke still shows up in my "Settings", System, Apps & Features…  It shows "unavailable" where the size of the file would be and when I attempt to uninstall it, it basically does nothing…  It tells me that the app and its related info will be uninstalled, but  nothing happens.  Modify is the only other option, but I haven't selected it as of yet…

I also noted another app that I had problems with on this list…  StopZilla was something that was giving me problems several years ago, but I hadn't had any problems recently, so I was surprised to still see it listed…  When I just now attempted to uninstall it, a window popped up asking me if it was ok if that program updated… I said no, figuring it would just remap itself back into my system again….


Thoughts?


Regards, Bob

StopZilla was an older Antivirus program , it never had good reviews , I would just leave it be


I would not modify Whitesmoke


Lets run SystemLook, you will need the 64 bit version


Please download SystemLook  and save it to your Desktop
 
32 Bit Version
64 Bit Version
 
  •  
  • Double-click SystemLook.exe to run it.
  • Copy the content of the following codebox into the main textfield:
:folderfind
Whitesmoke 
:filefind
Whitesmoke 
:regfind
Whitesmoke 
  • Click the Look button to start the scan.
  • When finished, a notepad window will open with the results of the scan. Please post this log in your next reply.
Note: The log can also be found on your Desktop entitled SystemLook.txt

Ken,  I've pasted the results of the SystemLook.txt doc below…  Thanks again!


Regards, Bob


SystemLook 30.07.11 by jpshortstuff
Log created at 10:42 on 22/09/2016 by Paddy
Administrator - Elevation successful
 
========== folderfind ==========
 
Searching for "Whitesmoke "
No folders found.
 
========== filefind ==========
 
Searching for "Whitesmoke "
No files found.
 
========== regfind ==========
 
Searching for "Whitesmoke "
[HKEY_CURRENT_USER\SOFTWARE\Classes\Wow6432Node\CLSID\{1BB8B3AE-757D-443F-B3A4-0629E709B0D9}]
@="WhiteSmoke New API Server"
[HKEY_CURRENT_USER\SOFTWARE\Classes\Wow6432Node\CLSID\{739df940-c5ee-4bab-9d7e-270894ae687a}]
@="WhiteSmoke New Toolbar"
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\WOW6432Node\CLSID\{1BB8B3AE-757D-443F-B3A4-0629E709B0D9}]
@="WhiteSmoke New API Server"
[HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Windows\CurrentVersion\Uninstall\WhiteSmoke New Toolbar]
[HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Windows\CurrentVersion\Uninstall\WhiteSmoke_New Toolbar]
"DisplayName"="WhiteSmoke New Toolbar"
[HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Windows\CurrentVersion\Uninstall\WhiteSmoke_New Toolbar]
"Publisher"="WhiteSmoke New"
[HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Classes\CLSID\{1BB8B3AE-757D-443F-B3A4-0629E709B0D9}]
@="WhiteSmoke New API Server"
[HKEY_USERS\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\Classes\Wow6432Node\CLSID\{1BB8B3AE-757D-443F-B3A4-0629E709B0D9}]
@="WhiteSmoke New API Server"
[HKEY_USERS\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\Classes\Wow6432Node\CLSID\{739df940-c5ee-4bab-9d7e-270894ae687a}]
@="WhiteSmoke New Toolbar"
[HKEY_USERS\S-1-5-21-648858125-4165233436-1298442668-1001_Classes\Wow6432Node\CLSID\{1BB8B3AE-757D-443F-B3A4-0629E709B0D9}]
@="WhiteSmoke New API Server"
[HKEY_USERS\S-1-5-21-648858125-4165233436-1298442668-1001_Classes\Wow6432Node\CLSID\{739df940-c5ee-4bab-9d7e-270894ae687a}]
@="WhiteSmoke New Toolbar"
 
-= EOF =-
Backup the Registry:
 
Modifying the Registry can create unforeseen problems, so it always wise to create a backup before doing so.
 
  •  
  • Please download the installer for Registry Backup from here or here and save to your desktop.
  • Right-click on tweaking.com_registry_backup_setup.exe and select Run as Administrator >> Follow the prompts for a default installation
  • Ensure the option Open "Tweaking.com - Registry Backup"  When Install Completes is selected >> Next >  >> Finish
  • Once the GUI(graphical user interface) has appeared/loaded:-
 
[external image: TCRB-1.jpg]
 
  •  
  • Click on Backup Now >> once the process is complete the below will be displayed in the GUI:-
 
[external image: TBRB-2.jpg]
 
  •  
  • Close Tweaking.com - Registry Backup
 
Note: There will now be a folder at the root of the Hard-Drive named C:\RegBackup, do not delete this as it is the actual backup just created.
 
A tutorial for Registry Backup explaining the various features be viewed HERE


==============================================================================


REGEDIT4
 
[-HKEY_CURRENT_USER\SOFTWARE\Classes\Wow6432Node\CLSID\{1BB8B3AE-757D-443F-B3A4-0629E709B0D9}]
 
[-HKEY_CURRENT_USER\SOFTWARE\Classes\Wow6432Node\CLSID\{739df940-c5ee-4bab-9d7e-270894ae687a}]
 
[-HKEY_LOCAL_MACHINE\SOFTWARE\Classes\WOW6432Node\CLSID\{1BB8B3AE-757D-443F-B3A4-0629E709B0D9}]
 
[-HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Windows\CurrentVersion\Uninstall\WhiteSmoke New Toolbar]
 
[-HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Windows\CurrentVersion\Uninstall\WhiteSmoke_New Toolbar]
 
[-HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Windows\CurrentVersion\Uninstall\WhiteSmoke_New Toolbar]
 
[-HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Classes\CLSID\{1BB8B3AE-757D-443F-B3A4-0629E709B0D9}]
 
[-HKEY_USERS\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\Classes\Wow6432Node\CLSID\{1BB8B3AE-757D-443F-B3A4-0629E709B0D9}]
 
[-HKEY_USERS\S-1-5-21-648858125-4165233436-1298442668-1001\SOFTWARE\Classes\Wow6432Node\CLSID\{739df940-c5ee-4bab-9d7e-270894ae687a}]
 
[-HKEY_USERS\S-1-5-21-648858125-4165233436-1298442668-1001_Classes\Wow6432Node\CLSID\{1BB8B3AE-757D-443F-B3A4-0629E709B0D9}]
 
[-HKEY_USERS\S-1-5-21-648858125-4165233436-1298442668-1001_Classes\Wow6432Node\CLSID\{739df940-c5ee-4bab-9d7e-270894ae687a}]


Copy the entire contents inside the Quote box and Paste it into Notepad ( this will only work with Notepad ) name the file Regfix.reg and in the drop down box, save it as All Files. Save it to your desktop. Then Rightclick on the Regfix.reg file and click on Merge, when it asks you to merge with the Registry, say yes.
 
If you saved the file correctly it should look like this [external image: reg.jpg]
 

Ken,  Done… I now have a small window titled Registry Editor with the following inside: "The keys and values contained in C:\Users\Paddy\Desktop\regfix.reg have been successfully added to the registry."


Regards, Bob

Ken,  It went away as soon as I clicked the OK button… What were we doing with the registry on that last procedure?  Do you think I"m good to go?


Thank you again for your assistance!


Regards, Bob

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI