CoolCat
Topic Starter
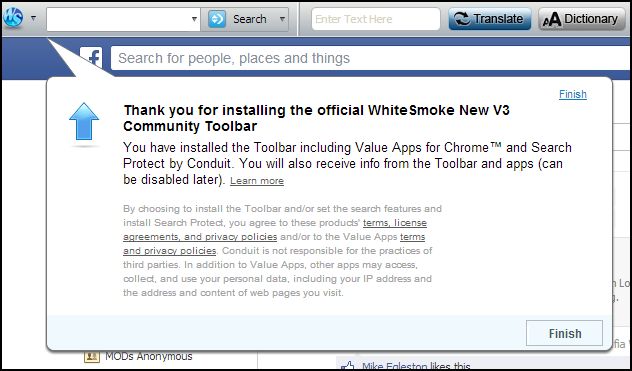
I did not expect to be back here so soon, for sure. I tried to view a video I had downloaded and it would not display correctly. Nothing has worked correctly with RealPlayer since I had to wipe my hard drive about a month ago. So, since I lost Winamp when I wiped it, I decided to go to a well known place on the net where I have always felt it was safe to download from - in fact, the only place I will download from.
I went through all the steps correctly and of course, there were all kinds of other things that you had to keep an eye on and uncheck because these other things wanted to install with Winamp. I am positive I unchecked everything. Well guess what, I got hijacked, anyway by this conduit dot com browser add-on. I went into IE and disabled it and also in Chrome but it's still there in IE and that's what comes up when I click IE, which I rarely use. It also messed up Chrome and I am not even sure I got that back, correctly or if what I am seeing is actually Chrome or something else. Please help me get this thing off my computer and anything else that came with it.
AND I got an error right off the bat saying my system has denied access to the Hosts file and if there is an infection in there, it might not be reported or fixed or something to that effect.
Logfile of Trend Micro HijackThis v2.0.4
Scan saved at 11:59:52 PM, on 8/17/2013
Platform: Windows Vista SP2 (WinNT 6.00.1906)
MSIE: Internet Explorer v9.00 (9.00.8112.16502)
Boot mode: Normal
Running processes:
C:\Program Files (x86)\Intel\Intel Matrix Storage Manager\IAAnotif.exe
C:\Windows\PLFSetI.exe
C:\Windows\SysWOW64\rundll32.exe
C:\Program Files (x86)\NewTech Infosystems\NTI Backup Now 5\BkupTray.exe
C:\Program Files (x86)\AOL Desktop 9.7\waol.exe
C:\Program Files (x86)\Acer\Empowering Technology\eDataSecurity\x86\eDSMSNLoader32.exe
C:\Program Files (x86)\Acer Arcade Deluxe\Acer Arcade Deluxe\ArcadeDeluxeAgent.exe
C:\Program Files (x86)\Acer Arcade Deluxe\Acer Arcade Deluxe\Kernel\CLML\CLMLSvc.exe
C:\Program Files (x86)\Acer Arcade Deluxe\PlayMovie\PMVService.exe
C:\Program Files (x86)\Avira\AntiVir Desktop\avgnt.exe
C:\Program Files (x86)\Common Files\AOL\1373719338\ee\aolsoftware.exe
C:\Program Files (x86)\Real\RealPlayer\Update\realsched.exe
C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe
C:\Program Files (x86)\AOL Desktop 9.7\shellmon.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\RealNetworks\RealDownloader\recordingmanager.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Google\Chrome\Application\chrome.exe
C:\Program Files (x86)\Trend Micro\HijackThis\HiJackThis.exe
R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://homepage.acer.com/rdr.aspx?b=ACAW&a;…p;m=aspire_6930
R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = http://search.conduit.com?SearchSource=10&…;ctid=CT3300196
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://homepage.acer.com/rdr.aspx?b=ACAW&a;…p;m=aspire_6930
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://homepage.acer.com/rdr.aspx?b=ACAW&a;…p;m=aspire_6930
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant =
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch =
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Local Page = C:\Windows\SysWOW64\blank.htm
R0 - HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName =
R3 - URLSearchHook: WhiteSmoke New V3 Toolbar - {068969a9-46cd-4e38-9ddb-4939814a3e32} - C:\Program Files (x86)\WhiteSmoke_New_V3\prxtbWhit.dll
F2 - REG:system.ini: UserInit=userinit.exe
O1 - Hosts: ::1 localhost
O2 - BHO: WhiteSmoke New V3 - {068969a9-46cd-4e38-9ddb-4939814a3e32} - C:\Program Files (x86)\WhiteSmoke_New_V3\prxtbWhit.dll
O2 - BHO: AcroIEHelperStub - {18DF081C-E8AD-4283-A596-FA578C2EBDC3} - C:\Program Files (x86)\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
O2 - BHO: RealNetworks Download and Record Plugin for Internet Explorer - {3049C3E9-B461-4BC5-8870-4C09146192CA} - C:\ProgramData\RealNetworks\RealDownloader\BrowserPlugins\IE\rndlbrowserrecordplugin.dll
O2 - BHO: Java™ Plug-In SSV Helper - {761497BB-D6F0-462C-B6EB-D4DAF1D92D43} - C:\Program Files (x86)\Java\jre7\bin\ssv.dll
O2 - BHO: TopArcadeHits Games - {A7A9D7E7-E0C0-4202-9F13-6A06BD073CDA} - C:\Users\arwen\AppData\Local\TopArcadeHits\Toparcadehits.dll
O2 - BHO: Google Toolbar Helper - {AA58ED58-01DD-4d91-8333-CF10577473F7} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
O2 - BHO: Java™ Plug-In 2 SSV Helper - {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files (x86)\Java\jre7\bin\jp2ssv.dll
O3 - Toolbar: Acer eDataSecurity Management - {5CBE3B7C-1E47-477e-A7DD-396DB0476E29} - C:\Program Files (x86)\Acer\Empowering Technology\eDataSecurity\x86\eDStoolbar.dll
O3 - Toolbar: WhiteSmoke New V3 Toolbar - {068969a9-46cd-4e38-9ddb-4939814a3e32} - C:\Program Files (x86)\WhiteSmoke_New_V3\prxtbWhit.dll
O3 - Toolbar: Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll
O4 - HKLM\..\Run: [eAudio] "C:\Program Files\Acer\Empowering Technology\eAudio\eAudio.exe"
O4 - HKLM\..\Run: [BkupTray] "C:\Program Files (x86)\NewTech Infosystems\NTI Backup Now 5\BkupTray.exe"
O4 - HKLM\..\Run: [Acer Product Registration] "C:\Program Files (x86)\Acer\Acer Registration\ACE1.exe" /startup
O4 - HKLM\..\Run: [LManager] C:\PROGRA~2\LAUNCH~1\QtZgAcer.EXE
O4 - HKLM\..\Run: [ArcadeDeluxeAgent] "C:\Program Files (x86)\Acer Arcade Deluxe\Acer Arcade Deluxe\ArcadeDeluxeAgent.exe"
O4 - HKLM\..\Run: [CLMLServer] "C:\Program Files (x86)\Acer Arcade Deluxe\Acer Arcade Deluxe\Kernel\CLML\CLMLSvc.exe"
O4 - HKLM\..\Run: [PlayMovie] "C:\Program Files (x86)\Acer Arcade Deluxe\PlayMovie\PMVService.exe"
O4 - HKLM\..\Run: [avgnt] "C:\Program Files (x86)\Avira\AntiVir Desktop\avgnt.exe" /min
O4 - HKLM\..\Run: [ApnTBMon] "C:\Program Files (x86)\AskPartnerNetwork\Toolbar\Updater\TBNotifier.exe"
O4 - HKLM\..\Run: [HostManager] "C:\Program Files (x86)\Common Files\AOL\1373719338\ee\AOLSoftware.exe"
O4 - HKLM\..\Run: [TkBellExe] "C:\Program Files (x86)\Real\RealPlayer\Update\realsched.exe" -osboot
O4 - HKLM\..\Run: [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
O4 - HKLM\..\Run: [LTCM Client] C:\Program Files (x86)\LTCM Client\ltcmClient.exe /startup
O4 - HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe"
O4 - HKLM\..\Run: [APSDaemon] "C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe"
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files (x86)\QuickTime\QTTask.exe" -atboottime
O4 - HKCU\..\Run: [ConduitFloatingPlugin_lcgnmdipgajofmpanhpdinhkgmeifmdo] "C:\Windows\SysWOW64\Rundll32.exe" "C:\Program Files (x86)\Conduit\CT3300196\plugins\TBVerifier.dll",RunConduitFloatingPlugin lcgnmdipgajofmpanhpdinhkgmeifmdo
O4 - HKCU\..\Run: [swg] "C:\Program Files (x86)\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe"
O4 - HKCU\..\Run: [AOL Fast Start] "C:\Program Files (x86)\AOL Desktop 9.7\AOL.EXE" -b
O4 - Startup: Acer Product Registration.lnk = C:\Program Files (x86)\Acer\Acer Registration\ACE1.exe
O4 - Global Startup: Start GeekBuddy.lnk = C:\Program Files (x86)\Comodo\GeekBuddy\launcher.exe
O8 - Extra context menu item: E&xport to Microsoft Excel - res://C:\PROGRA~2\MICROS~1\Office12\EXCEL.EXE/3000
O9 - Extra button: Send to OneNote - {2670000A-7350-4f3c-8081-5663EE0C6C49} - C:\PROGRA~2\MICROS~1\Office12\ONBttnIE.dll
O9 - Extra 'Tools' menuitem: S&end to OneNote - {2670000A-7350-4f3c-8081-5663EE0C6C49} - C:\PROGRA~2\MICROS~1\Office12\ONBttnIE.dll
O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} - C:\PROGRA~2\MICROS~1\Office12\REFIEBAR.DLL
O11 - Options group: [ACCELERATED_GRAPHICS] Accelerated graphics
O22 - SharedTaskScheduler: Component Categories cache daemon - {8C7461EF-2B13-11d2-BE35-3078302C2030} - C:\Windows\system32\browseui.dll
O23 - Service: Adobe Acrobat Update Service (AdobeARMservice) - Adobe Systems Incorporated - C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe
O23 - Service: @%SystemRoot%\system32\Alg.exe,-112 (ALG) - Unknown owner - C:\Windows\System32\alg.exe (file missing)
O23 - Service: Avira Scheduler (AntiVirSchedulerService) - Avira Operations GmbH & Co. KG - C:\Program Files (x86)\Avira\AntiVir Desktop\sched.exe
O23 - Service: Avira Real-Time Protection (AntiVirService) - Avira Operations GmbH & Co. KG - C:\Program Files (x86)\Avira\AntiVir Desktop\avguard.exe
O23 - Service: Avira Web Protection (AntiVirWebService) - Avira Operations GmbH & Co. KG - C:\Program Files (x86)\Avira\AntiVir Desktop\AVWEBGRD.EXE
O23 - Service: AOL Connectivity Service (AOL ACS) - AOL LLC - C:\Program Files (x86)\Common Files\AOL\ACS\AOLAcsd.exe
O23 - Service: NTI Backup Now 5 Agent Service (BUNAgentSvc) - NewTech Infosystems, Inc. - C:\Program Files (x86)\NewTech Infosystems\NTI Backup Now 5\Client\Agentsvc.exe
O23 - Service: CLHNService - Unknown owner - C:\Program Files (x86)\Acer Arcade Deluxe\HomeMedia\Kernel\DMP\CLHNService.exe
O23 - Service: @dfsrres.dll,-101 (DFSR) - Unknown owner - C:\Windows\system32\DFSR.exe (file missing)
O23 - Service: eDataSecurity Service - Egis Incorporated - C:\Program Files (x86)\Acer\Empowering Technology\eDataSecurity\x86\eDSService.exe
O23 - Service: Empowering Technology Service (ETService) - Unknown owner - C:\Program Files\Acer\Empowering Technology\Service\ETService.exe
O23 - Service: Google Update Service (gupdate) (gupdate) - Google Inc. - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
O23 - Service: Google Update Service (gupdatem) (gupdatem) - Google Inc. - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
O23 - Service: Google Software Updater (gusvc) - Google - C:\Program Files (x86)\Google\Common\Google Updater\GoogleUpdaterService.exe
O23 - Service: Intel® Matrix Storage Event Monitor (IAANTMON) - Intel Corporation - C:\Program Files (x86)\Intel\Intel Matrix Storage Manager\IAANTMon.exe
O23 - Service: @keyiso.dll,-100 (KeyIso) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: LightScribeService Direct Disc Labeling Service (LightScribeService) - Hewlett-Packard Company - C:\Program Files (x86)\Common Files\LightScribe\LSSrvc.exe
O23 - Service: MobilityService - Unknown owner - C:\Acer\Mobility Center\MobilityService.exe
O23 - Service: @comres.dll,-2797 (MSDTC) - Unknown owner - C:\Windows\System32\msdtc.exe (file missing)
O23 - Service: @%SystemRoot%\System32\netlogon.dll,-102 (Netlogon) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: NTI Backup Now 5 Backup Service (NTIBackupSvc) - NewTech InfoSystems, Inc. - C:\Program Files (x86)\NewTech Infosystems\NTI Backup Now 5\BackupSvc.exe
O23 - Service: NTI Backup Now 5 Scheduler Service (NTISchedulerSvc) - Unknown owner - C:\Program Files (x86)\NewTech Infosystems\NTI Backup Now 5\SchedulerSvc.exe
O23 - Service: @%systemroot%\system32\psbase.dll,-300 (ProtectedStorage) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: RealNetworks Downloader Resolver Service - Unknown owner - C:\Program Files (x86)\RealNetworks\RealDownloader\rndlresolversvc.exe
O23 - Service: Cyberlink RichVideo Service(CRVS) (RichVideo) - Unknown owner - C:\Program Files (x86)\Cyberlink\Shared files\RichVideo.exe
O23 - Service: @%systemroot%\system32\Locator.exe,-2 (RpcLocator) - Unknown owner - C:\Windows\system32\locator.exe (file missing)
O23 - Service: @%SystemRoot%\system32\samsrv.dll,-1 (SamSs) - Unknown owner - C:\Windows\system32\lsass.exe (file missing)
O23 - Service: @%SystemRoot%\system32\SLsvc.exe,-101 (slsvc) - Unknown owner - C:\Windows\system32\SLsvc.exe (file missing)
O23 - Service: @%SystemRoot%\system32\snmptrap.exe,-3 (SNMPTRAP) - Unknown owner - C:\Windows\System32\snmptrap.exe (file missing)
O23 - Service: @%systemroot%\system32\spoolsv.exe,-1 (Spooler) - Unknown owner - C:\Windows\System32\spoolsv.exe (file missing)
O23 - Service: @%SystemRoot%\system32\ui0detect.exe,-101 (UI0Detect) - Unknown owner - C:\Windows\system32\UI0Detect.exe (file missing)
O23 - Service: @%SystemRoot%\system32\vds.exe,-100 (vds) - Unknown owner - C:\Windows\System32\vds.exe (file missing)
O23 - Service: @%systemroot%\system32\vssvc.exe,-102 (VSS) - Unknown owner - C:\Windows\system32\vssvc.exe (file missing)
O23 - Service: @%Systemroot%\system32\wbem\wmiapsrv.exe,-110 (wmiApSrv) - Unknown owner - C:\Windows\system32\wbem\WmiApSrv.exe (file missing)
O23 - Service: @%ProgramFiles%\Windows Media Player\wmpnetwk.exe,-101 (WMPNetworkSvc) - Unknown owner - C:\Program Files (x86)\Windows Media Player\wmpnetwk.exe (file missing)
O23 - Service: XAudioService - Unknown owner - C:\Windows\system32\DRIVERS\xaudio64.exe (file missing)
–
End of file - 12893 bytes



 The TopAracadeHits Games' add-on from an unknown publisher is ready for use.
Enable or Don't enable.