This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

Google Redirect / Other Infection [Solved]

14 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

Windows Vista Home Basic SP2 I downloaded the three programs recommended in "Are you infected? When I ran OTL instead of starting it produced a windows error "a device connected to this computer has stopped working" and would not run. HijackThis did the same thing. When I tried to run dds.scr I got a different windows error "The dependency service or group failed to start". There has also been a repeated windows error box that keeps coming up "Microsoft Windows: Host Process for Windows Services stopped working and was closed". I opened control panel and "add or remove programs" is missing. In task manager, no (visible) process is using more than 2 -3% CPU yet the status bar shows 100%. I'm managing the machine remotely using Logmein.
Hello and Posted Image

My name is patndoris. I will be glad to take a look at your log and help you with solving any malware problems. It will be very helpful if you follow these guidelines:
  • Malware logs are often lengthy and can take a lot of time to research and interpret. Please be patient while I review your logs.
  • Please note that there is no "Quick Fix" to modern malware infections and we may need to use several different approaches to get your system clean.
  • Please make sure to carefully read any instruction that I give you. If you're not sure, or if something unexpected happens, do NOT continue! Stop and ask!
  • Please follow my instructions carefully and in the order they are posted. You may also find it helpful to print out the instructions you receive.
  • Please do not run any scans or install/uninstall any applications or delete anything without being directed to do so.
  • Remember, absence of symptoms does not mean the infection is all gone. Please stick with me till you're given the "all clear".
  • Please do not use the Attachment feature for any log file. Do a Copy/Paste of the entire contents of the log file and submit it inside your post.
  • Please reply within 3 days. If I do not hear back from you in that time frame, I will post a reminder for you. Topics with no reply in 4 days are closed!

I hope that you have the ability to reboot the machine remotely and can do so into safe mode as well as that may be necessary as a part of our steps. It is however a possibility that you may not be able to clean this infection remotely so I need to make you aware of that ahead of time. But we will do our best.

Please read through the following steps completely. I'd like you to try to download the DDS file and the TDSSKiller files to the machine prior to doing the steps. (There is a method to my madness. I'm worried that you may not be able to get the steps to run even using RKill and in that even I have a contingency idea that might work.)


For the moment, I would like you to reboot the machine and then do the following.


Download and Run RKill

Please download and run the following tool to help allow other programs to run. (Thanks to Grinler of BleepingComputer.com)
There are 3 different versions. If one of them won't run then download and try to run the other one.
Vista and Win7 users need to right click and choose Run as Admin

You only need to get one of these to run, not all of them.
Rkill.exe
Rkill.com
Rkill.scr

Once it is downloaded, right-click and choose Run as Administrator on the rkill.com in order to automatically try to stop any processes associated with rogue programs. Please be patient while the program looks for various malware programs and ends them. When it has finished, the black window will automatically close and you can continue with the next steps.

If you get a message rkill is an infection, do not be concerned. The message is just a fake warning by some rogue programs when it terminates programs that may potentially remove it. The trick is to leave the warning on the screen and then run Rkill again. By not closing the warning, this should allow you to bypass the malware trying to protect itself so that rkill can terminate the rogue processes. Continue to try running Rkill until the malware is no longer running. You will then be able to proceed with the next steps.

Do not reboot your computer after running rkill as the malware programs will start again.

If for some reason the machine reboots, repeat the process. Again, try not to restart the machine.

If you can get RKill to run successfully, then I'd like you to do the following:


Download and Run DDS by sUBs

We need to see some information about what is happening in your machine. Please perform the following scan:
  • Download DDS by sUBs from one of the following links. Save it to your desktop.
    • DDS.com
    • DDS.pif
  • Double click on the DDS icon, allow it to run.
  • A small box will open, with an explaination about the tool. No input is needed, the scan is running.
  • Notepad will open with the results.
  • Follow the instructions that pop up for posting the results.
  • Close the program window, and delete the program from your desktop.
Please note: You may have to disable any script protection running if the scan fails to run. After downloading the tool, disconnect from the internet and disable all antivirus protection. Run the scan, enable your A/V and reconnect to the internet.

Information on A/V control HERE


Please read carefully and follow these steps. There is a difference between what you see in one of the images below and what I need you to do.
We are only creating a log - I do NOT want you to "cure" or try to fix anything in this step. It is very important that you don't choose Cure when presented with that option.


If you can't get these steps to work after running RKill, please let me know.
Just to let you know, I'm in one of the many predicted paths of the Frankenstorm Sandy that's coming, so if I don't respond right away to any posts you may put up in the next couple of days it is likely the result of power outages (which could take a couple of days to get back). They are saying we could start experiencing wind and rain any time from this afternoon, with the worst coming tomorrow. I'm crossing my fingers we don't lose power but one never knows. So I just wanted to let you know it wouldn't be because I was ignoring you :) Please be patient and I promise if that happens I will be back with you as soon as possible. For the remainder of today, I will certainly be monitoring posts and getting back with you as quickly as possible :D
I'm not sure why you wanted me to do DDS and TDSSKiller, you only ask for the log from TDSSKiller. I got both to work. Here's the log from the kaspersky, I'm attaching the log from DDS as an attachment. RKill was necessary, it found: * C:\Windows\system32\MDM.EXE (PID: 2232) [WD-HEUR]. I'm attaching that log as well. If you can't respond quickly due to weather, the machine has been like this for a while, a little longer can't hurt. Thank you so much for your help. 14:38:54.0548 5524 TDSS rootkit removing tool [removed] Oct 12 2012 17:26:47 14:38:56.0551 5524 ============================================================ 14:38:56.0551 5524 Current date / time: 2012/10/28 14:38:56.0551 14:38:56.0551 5524 SystemInfo: 14:38:56.0551 5524 14:38:56.0551 5524 OS Version: 6.0.6002 ServicePack: 2.0 14:38:56.0551 5524 Product type: Workstation 14:38:56.0552 5524 ComputerName: CRONINS-PC 14:38:56.0552 5524 UserName: Cronins 14:38:56.0552 5524 Windows directory: C:\Windows 14:38:56.0552 5524 System windows directory: C:\Windows 14:38:56.0552 5524 Processor architecture: Intel x86 14:38:56.0552 5524 Number of processors: 1 14:38:56.0552 5524 Page size: 0x1000 14:38:56.0552 5524 Boot type: Normal boot 14:38:56.0552 5524 ============================================================ 14:38:59.0164 5524 Drive \Device\Harddisk0\DR0 - Size: 0x3A35294400 (232.83 Gb), SectorSize: 0x200, Cylinders: 0x76BA, SectorsPerTrack: 0x3F, TracksPerCylinder: 0xFF, Type 'K0', Flags 0x00000050 14:38:59.0196 5524 ============================================================ 14:38:59.0196 5524 \Device\Harddisk0\DR0: 14:38:59.0230 5524 MBR partitions: 14:38:59.0230 5524 \Device\Harddisk0\DR0\Partition1: MBR, Type 0x7, StartLBA 0x1B800, BlocksNum 0x1400000 14:38:59.0230 5524 \Device\Harddisk0\DR0\Partition2: MBR, Type 0x7, StartLBA 0x141B800, BlocksNum 0x1BD8D000 14:38:59.0230 5524 ============================================================ 14:38:59.0340 5524 C: <-> \Device\Harddisk0\DR0\Partition2 14:38:59.0572 5524 D: <-> \Device\Harddisk0\DR0\Partition1 14:38:59.0572 5524 ============================================================ 14:38:59.0572 5524 Initialize success 14:38:59.0572 5524 ============================================================ 14:39:05.0835 4444 ============================================================ 14:39:05.0835 4444 Scan started 14:39:05.0835 4444 Mode: Manual; 14:39:05.0835 4444 ============================================================ 14:39:09.0059 4444 ================ Scan system memory ======================== 14:39:09.0059 4444 System memory - ok 14:39:09.0060 4444 ================ Scan services ============================= 14:39:09.0295 4444 [ 82B296AE1892FE3DBEE00C9CF92F8AC7 ] ACPI C:\Windows\system32\drivers\acpi.sys 14:39:09.0469 4444 ACPI - ok 14:39:09.0775 4444 [ 04F0FCAC69C7C71A3AC4EB97FAFC8303 ] adp94xx C:\Windows\system32\drivers\adp94xx.sys 14:39:09.0800 4444 adp94xx - ok 14:39:09.0905 4444 [ 60505E0041F7751BDBB80F88BF45C2CE ] adpahci C:\Windows\system32\drivers\adpahci.sys 14:39:09.0915 4444 adpahci - ok 14:39:09.0986 4444 [ 8A42779B02AEC986EAB64ECFC98F8BD7 ] adpu160m C:\Windows\system32\drivers\adpu160m.sys 14:39:09.0989 4444 adpu160m - ok 14:39:10.0024 4444 [ 241C9E37F8CE45EF51C3DE27515CA4E5 ] adpu320 C:\Windows\system32\drivers\adpu320.sys 14:39:10.0028 4444 adpu320 - ok 14:39:10.0098 4444 [ 9D1FDA9E086BA64E3C93C9DE32461BCF ] AeLookupSvc C:\Windows\System32\aelupsvc.dll 14:39:10.0114 4444 AeLookupSvc - ok 14:39:10.0151 4444 [ 330A1E4DF07C2E29949ED8631CD8828E ] AERTFilters C:\Windows\system32\AERTSrv.exe 14:39:10.0154 4444 AERTFilters - ok 14:39:10.0215 4444 [ 3911B972B55FEA0478476B2E777B29FA ] AFD C:\Windows\system32\drivers\afd.sys 14:39:10.0239 4444 AFD - ok 14:39:10.0358 4444 [ 13F9E33747E6B41A3FF305C37DB0D360 ] agp440 C:\Windows\system32\drivers\agp440.sys 14:39:10.0386 4444 agp440 - ok 14:39:10.0455 4444 [ AE1FDF7BF7BB6C6A70F67699D880592A ] aic78xx C:\Windows\system32\drivers\djsvs.sys 14:39:10.0458 4444 aic78xx - ok 14:39:10.0491 4444 [ A1545B731579895D8CC44FC0481C1192 ] ALG C:\Windows\System32\alg.exe 14:39:10.0494 4444 ALG - ok 14:39:10.0517 4444 [ 9EAEF5FC9B8E351AFA7E78A6FAE91F91 ] aliide C:\Windows\system32\drivers\aliide.sys 14:39:10.0518 4444 aliide - ok 14:39:10.0603 4444 [ C47344BC706E5F0B9DCE369516661578 ] amdagp C:\Windows\system32\drivers\amdagp.sys 14:39:10.0606 4444 amdagp - ok 14:39:10.0640 4444 [ 9B78A39A4C173FDBC1321E0DD659B34C ] amdide C:\Windows\system32\drivers\amdide.sys 14:39:10.0667 4444 amdide - ok 14:39:10.0741 4444 [ 18F29B49AD23ECEE3D2A826C725C8D48 ] AmdK7 C:\Windows\system32\drivers\amdk7.sys 14:39:10.0743 4444 AmdK7 - ok 14:39:10.0771 4444 [ 93AE7F7DD54AB986A6F1A1B37BE7442D ] AmdK8 C:\Windows\system32\drivers\amdk8.sys 14:39:10.0773 4444 AmdK8 - ok 14:39:10.0811 4444 [ C6D704C7F0434DC791AAC37CAC4B6E14 ] Appinfo C:\Windows\System32\appinfo.dll 14:39:10.0813 4444 Appinfo - ok 14:39:10.0835 4444 [ 5D2888182FB46632511ACEE92FDAD522 ] arc C:\Windows\system32\drivers\arc.sys 14:39:10.0839 4444 arc - ok 14:39:10.0876 4444 [ 5E2A321BD7C8B3624E41FDEC3E244945 ] arcsas C:\Windows\system32\drivers\arcsas.sys 14:39:10.0879 4444 arcsas - ok 14:39:10.0903 4444 [ 53B202ABEE6455406254444303E87BE1 ] AsyncMac C:\Windows\system32\DRIVERS\asyncmac.sys 14:39:10.0905 4444 AsyncMac - ok 14:39:10.0954 4444 [ 1F05B78AB91C9075565A9D8A4B880BC4 ] atapi C:\Windows\system32\drivers\atapi.sys 14:39:10.0955 4444 atapi - ok 14:39:11.0022 4444 [ 68E2A1A0407A66CF50DA0300852424AB ] AudioEndpointBuilder C:\Windows\System32\Audiosrv.dll 14:39:11.0029 4444 AudioEndpointBuilder - ok 14:39:11.0048 4444 [ 68E2A1A0407A66CF50DA0300852424AB ] Audiosrv C:\Windows\System32\Audiosrv.dll 14:39:11.0051 4444 Audiosrv - ok 14:39:11.0105 4444 [ 67E506B75BD5326A3EC7B70BD014DFB6 ] Beep C:\Windows\system32\drivers\Beep.sys 14:39:11.0107 4444 Beep - ok 14:39:11.0176 4444 [ C789AF0F724FDA5852FB9A7D3A432381 ] BFE C:\Windows\System32\bfe.dll 14:39:11.0194 4444 BFE - ok 14:39:11.0298 4444 [ 93952506C6D67330367F7E7934B6A02F ] BITS C:\Windows\System32\qmgr.dll 14:39:11.0625 4444 BITS - ok 14:39:11.0674 4444 [ D4DF28447741FD3D953526E33A617397 ] blbdrive C:\Windows\system32\drivers\blbdrive.sys 14:39:11.0694 4444 blbdrive - ok 14:39:11.0770 4444 [ 35F376253F687BDE63976CCB3F2108CA ] bowser C:\Windows\system32\DRIVERS\bowser.sys 14:39:11.0792 4444 bowser - ok 14:39:11.0830 4444 [ 9F9ACC7F7CCDE8A15C282D3F88B43309 ] BrFiltLo C:\Windows\system32\drivers\brfiltlo.sys 14:39:11.0836 4444 BrFiltLo - ok 14:39:11.0854 4444 [ 56801AD62213A41F6497F96DEE83755A ] BrFiltUp C:\Windows\system32\drivers\brfiltup.sys 14:39:11.0856 4444 BrFiltUp - ok 14:39:11.0888 4444 [ A3629A0C4226F9E9C72FAAEEBC3AD33C ] Browser C:\Windows\System32\browser.dll 14:39:11.0921 4444 Browser - ok 14:39:11.0968 4444 [ B304E75CFF293029EDDF094246747113 ] Brserid C:\Windows\system32\drivers\brserid.sys 14:39:11.0999 4444 Brserid - ok 14:39:12.0034 4444 [ 203F0B1E73ADADBBB7B7B1FABD901F6B ] BrSerWdm C:\Windows\system32\drivers\brserwdm.sys 14:39:12.0036 4444 BrSerWdm - ok 14:39:12.0080 4444 [ BD456606156BA17E60A04E18016AE54B ] BrUsbMdm C:\Windows\system32\drivers\brusbmdm.sys 14:39:12.0081 4444 BrUsbMdm - ok 14:39:12.0129 4444 [ AF72ED54503F717A43268B3CC5FAEC2E ] BrUsbSer C:\Windows\system32\drivers\brusbser.sys 14:39:12.0131 4444 BrUsbSer - ok 14:39:12.0216 4444 [ AD07C1EC6665B8B35741AB91200C6B68 ] BTHMODEM C:\Windows\system32\drivers\bthmodem.sys 14:39:12.0218 4444 BTHMODEM - ok 14:39:12.0342 4444 [ 7ADD03E75BEB9E6DD102C3081D29840A ] cdfs C:\Windows\system32\DRIVERS\cdfs.sys 14:39:12.0379 4444 cdfs - ok 14:39:12.0455 4444 [ 6B4BFFB9BECD728097024276430DB314 ] cdrom C:\Windows\system32\DRIVERS\cdrom.sys 14:39:12.0489 4444 cdrom - ok 14:39:12.0599 4444 [ 312EC3E37A0A1F2006534913E37B4423 ] CertPropSvc C:\Windows\System32\certprop.dll 14:39:12.0601 4444 CertPropSvc - ok 14:39:12.0659 4444 [ 1C7B1E36F3CED9E4B0B13385E627FE8B ] cfwids C:\Windows\system32\drivers\cfwids.sys 14:39:12.0661 4444 cfwids - ok 14:39:12.0700 4444 [ E5D4133F37219DBCFE102BC61072589D ] circlass C:\Windows\system32\drivers\circlass.sys 14:39:12.0702 4444 circlass - ok 14:39:12.0755 4444 [ D7659D3B5B92C31E84E53C1431F35132 ] CLFS C:\Windows\system32\CLFS.sys 14:39:12.0761 4444 CLFS - ok 14:39:12.0809 4444 [ 8EE772032E2FE80A924F3B8DD5082194 ] clr_optimization_v2.0.50727_32 C:\Windows\Microsoft.NET\Framework\v2.0.50727\mscorsvw.exe 14:39:12.0811 4444 clr_optimization_v2.0.50727_32 - ok 14:39:12.0944 4444 [ C5A75EB48E2344ABDC162BDA79E16841 ] clr_optimization_v4.0.30319_32 C:\Windows\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe 14:39:12.0946 4444 clr_optimization_v4.0.30319_32 - ok 14:39:12.0969 4444 [ 0CA25E686A4928484E9FDABD168AB629 ] cmdide C:\Windows\system32\drivers\cmdide.sys 14:39:12.0970 4444 cmdide - ok 14:39:12.0989 4444 [ 6AFEF0B60FA25DE07C0968983EE4F60A ] Compbatt C:\Windows\system32\drivers\compbatt.sys 14:39:12.0991 4444 Compbatt - ok 14:39:13.0002 4444 COMSysApp - ok 14:39:13.0022 4444 [ 741E9DFF4F42D2D8477D0FC1DC0DF871 ] crcdisk C:\Windows\system32\drivers\crcdisk.sys 14:39:13.0023 4444 crcdisk - ok 14:39:13.0042 4444 [ 1F07BECDCA750766A96CDA811BA86410 ] Crusoe C:\Windows\system32\drivers\crusoe.sys 14:39:13.0045 4444 Crusoe - ok 14:39:13.0112 4444 [ F1E8C34892336D33EDDCDFE44E474F64 ] CryptSvc C:\Windows\system32\cryptsvc.dll 14:39:13.0116 4444 CryptSvc - ok 14:39:13.0189 4444 [ 3B5B4D53FEC14F7476CA29A20CC31AC9 ] DcomLaunch C:\Windows\system32\rpcss.dll 14:39:13.0207 4444 DcomLaunch - ok 14:39:13.0253 4444 [ 622C41A07CA7E6DD91770F50D532CB6C ] DfsC C:\Windows\system32\Drivers\dfsc.sys 14:39:13.0257 4444 DfsC - ok 14:39:13.0402 4444 [ 2CC3DCFB533A1035B13DCAB6160AB38B ] DFSR C:\Windows\system32\DFSR.exe 14:39:13.0464 4444 DFSR - ok 14:39:13.0595 4444 [ 9028559C132146FB75EB7ACF384B086A ] Dhcp C:\Windows\System32\dhcpcsvc.dll 14:39:13.0600 4444 Dhcp - ok 14:39:13.0664 4444 [ 5D4AEFC3386920236A548271F8F1AF6A ] disk C:\Windows\system32\drivers\disk.sys 14:39:13.0666 4444 disk - ok 14:39:13.0721 4444 [ 57D762F6F5974AF0DA2BE88A3349BAAA ] Dnscache C:\Windows\System32\dnsrslvr.dll 14:39:13.0727 4444 Dnscache - ok 14:39:13.0809 4444 [ DB29915209770D8B59654345EC2D943A ] DockLoginService C:\Program Files\Dell\DellDock\DockLogin.exe 14:39:13.0814 4444 DockLoginService - ok 14:39:13.0871 4444 [ 324FD74686B1EF5E7C19A8AF49E748F6 ] dot3svc C:\Windows\System32\dot3svc.dll 14:39:13.0876 4444 dot3svc - ok 14:39:13.0919 4444 [ 4F59C172C094E1A1D46463A8DC061CBD ] Dot4 C:\Windows\system32\DRIVERS\Dot4.sys 14:39:13.0924 4444 Dot4 - ok 14:39:13.0943 4444 [ 80BF3BA09F6F2523C8F6B7CC6DBF7BD5 ] Dot4Print C:\Windows\system32\DRIVERS\Dot4Prt.sys 14:39:13.0945 4444 Dot4Print - ok 14:39:13.0966 4444 [ C55004CA6B419B6695970DFE849B122F ] dot4usb C:\Windows\system32\DRIVERS\dot4usb.sys 14:39:13.0968 4444 dot4usb - ok 14:39:14.0011 4444 [ A622E888F8AA2F6B49E9BC466F0E5DEF ] DPS C:\Windows\system32\dps.dll 14:39:14.0014 4444 DPS - ok 14:39:14.0055 4444 [ 97FEF831AB90BEE128C9AF390E243F80 ] drmkaud C:\Windows\system32\drivers\drmkaud.sys 14:39:14.0056 4444 drmkaud - ok 14:39:14.0124 4444 [ C68AC676B0EF30CFBB1080ADCE49EB1F ] DXGKrnl C:\Windows\System32\drivers\dxgkrnl.sys 14:39:14.0148 4444 DXGKrnl - ok 14:39:14.0200 4444 [ 04944F4FC4F0477185F5D26AE0DDB90E ] e1express C:\Windows\system32\DRIVERS\e1e6032.sys 14:39:14.0206 4444 e1express - ok 14:39:14.0335 4444 [ 5425F74AC0C1DBD96A1E04F17D63F94C ] E1G60 C:\Windows\system32\DRIVERS\E1G60I32.sys 14:39:14.0338 4444 E1G60 - ok 14:39:14.0395 4444 [ C0B95E40D85CD807D614E264248A45B9 ] EapHost C:\Windows\System32\eapsvc.dll 14:39:14.0397 4444 EapHost - ok 14:39:14.0454 4444 [ 7F64EA048DCFAC7ACF8B4D7B4E6FE371 ] Ecache C:\Windows\system32\drivers\ecache.sys 14:39:14.0458 4444 Ecache - ok 14:39:14.0585 4444 [ 23B62471681A124889978F6295B3F4C6 ] elxstor C:\Windows\system32\drivers\elxstor.sys 14:39:14.0592 4444 elxstor - ok 14:39:14.0662 4444 [ 4E6B23DFC917EA39306B529B773950F4 ] EMDMgmt C:\Windows\system32\emdmgmt.dll 14:39:14.0676 4444 EMDMgmt - ok 14:39:14.0692 4444 [ 3DB974F3935483555D7148663F726C61 ] ErrDev C:\Windows\system32\drivers\errdev.sys 14:39:14.0694 4444 ErrDev - ok 14:39:14.0767 4444 [ 67058C46504BC12D821F38CF99B7B28F ] EventSystem C:\Windows\system32\es.dll 14:39:14.0769 4444 EventSystem - ok 14:39:14.0822 4444 [ 22B408651F9123527BCEE54B4F6C5CAE ] exfat C:\Windows\system32\drivers\exfat.sys 14:39:14.0827 4444 exfat - ok 14:39:14.0884 4444 [ 1E9B9A70D332103C52995E957DC09EF8 ] fastfat C:\Windows\system32\drivers\fastfat.sys 14:39:14.0886 4444 fastfat - ok 14:39:14.0937 4444 [ AFE1E8B9782A0DD7FB46BBD88E43F89A ] fdc C:\Windows\system32\DRIVERS\fdc.sys 14:39:14.0939 4444 fdc - ok 14:39:15.0000 4444 [ 6629B5F0E98151F4AFDD87567EA32BA3 ] fdPHost C:\Windows\system32\fdPHost.dll 14:39:15.0002 4444 fdPHost - ok 14:39:15.0016 4444 [ 89ED56DCE8E47AF40892778A5BD31FD2 ] FDResPub C:\Windows\system32\fdrespub.dll 14:39:15.0019 4444 FDResPub - ok 14:39:15.0039 4444 [ A8C0139A884861E3AAE9CFE73B208A9F ] FileInfo C:\Windows\system32\drivers\fileinfo.sys 14:39:15.0041 4444 FileInfo - ok 14:39:15.0067 4444 [ 0AE429A696AECBC5970E3CF2C62635AE ] Filetrace C:\Windows\system32\drivers\filetrace.sys 14:39:15.0069 4444 Filetrace - ok 14:39:15.0089 4444 [ 85B7CF99D532820495D68D747FDA9EBD ] flpydisk C:\Windows\system32\DRIVERS\flpydisk.sys 14:39:15.0090 4444 flpydisk - ok 14:39:15.0187 4444 [ 01334F9EA68E6877C4EF05D3EA8ABB05 ] FltMgr C:\Windows\system32\drivers\fltmgr.sys 14:39:15.0192 4444 FltMgr - ok 14:39:15.0293 4444 [ 8CE364388C8ECA59B14B539179276D44 ] FontCache C:\Windows\system32\FntCache.dll 14:39:15.0303 4444 FontCache - ok 14:39:15.0386 4444 [ C7FBDD1ED42F82BFA35167A5C9803EA3 ] FontCache3.0.0.0 C:\Windows\Microsoft.Net\Framework\v3.0\WPF\PresentationFontCache.exe 14:39:15.0388 4444 FontCache3.0.0.0 - ok 14:39:15.0472 4444 [ B972A66758577E0BFD1DE0F91AAA27B5 ] Fs_Rec C:\Windows\system32\drivers\Fs_Rec.sys 14:39:15.0474 4444 Fs_Rec - ok 14:39:15.0537 4444 [ 34582A6E6573D54A07ECE5FE24A126B5 ] gagp30kx C:\Windows\system32\drivers\gagp30kx.sys 14:39:15.0539 4444 gagp30kx - ok 14:39:15.0600 4444 [ 07F92834B21AF6AE36F4DB0ACC03658D ] GameConsoleService C:\Program Files\WildTangent\Dell Games\Dell Game Console\GameConsoleService.exe 14:39:15.0605 4444 GameConsoleService - ok 14:39:15.0750 4444 [ 9F5F2F0FB0A7F5AA9F16B9A7B6DAD89F ] GoogleDesktopManager-051210-111108 C:\Program Files\Google\Google Desktop Search\GoogleDesktop.exe 14:39:15.0753 4444 GoogleDesktopManager-051210-111108 - ok 14:39:15.0802 4444 [ D3316F6E3C011435F36E3D6E49B3196C ] GoToAssist C:\Program Files\Citrix\GoToAssist\514\g2aservice.exe 14:39:15.0805 4444 GoToAssist - ok 14:39:15.0857 4444 [ CD5D0AEEE35DFD4E986A5AA1500A6E66 ] gpsvc C:\Windows\System32\gpsvc.dll 14:39:15.0868 4444 gpsvc - ok 14:39:15.0963 4444 [ 062452B7FFD68C8C042A6261FE8DFF4A ] HDAudBus C:\Windows\system32\DRIVERS\HDAudBus.sys 14:39:15.0972 4444 HDAudBus - ok 14:39:16.0009 4444 [ 1338520E78D90154ED6BE8F84DE5FCEB ] HidBth C:\Windows\system32\drivers\hidbth.sys 14:39:16.0011 4444 HidBth - ok 14:39:16.0043 4444 [ FF3160C3A2445128C5A6D9B076DA519E ] HidIr C:\Windows\system32\drivers\hidir.sys 14:39:16.0046 4444 HidIr - ok 14:39:16.0092 4444 [ 84067081F3318162797385E11A8F0582 ] hidserv C:\Windows\system32\hidserv.dll 14:39:16.0094 4444 hidserv - ok 14:39:16.0156 4444 [ CCA4B519B17E23A00B826C55716809CC ] HidUsb C:\Windows\system32\DRIVERS\hidusb.sys 14:39:16.0157 4444 HidUsb - ok 14:39:16.0184 4444 [ D8AD255B37DA92434C26E4876DB7D418 ] hkmsvc C:\Windows\system32\kmsvc.dll 14:39:16.0188 4444 hkmsvc - ok 14:39:16.0224 4444 [ 16EE7B23A009E00D835CDB79574A91A6 ] HpCISSs C:\Windows\system32\drivers\hpcisss.sys 14:39:16.0227 4444 HpCISSs - ok 14:39:16.0304 4444 [ 0A3C6AA4A9FC38C20BA4EAC2C3351C05 ] hpqcxs08 C:\Program Files\HP\Digital Imaging\bin\hpqcxs08.dll 14:39:16.0307 4444 hpqcxs08 - ok 14:39:16.0355 4444 [ DF446BA625CC441617843E87798CE048 ] hpqddsvc C:\Program Files\HP\Digital Imaging\bin\hpqddsvc.dll 14:39:16.0362 4444 hpqddsvc - ok 14:39:16.0450 4444 [ 99F85640054BA65190B860D878A7C9AE ] HSF_DPV C:\Windows\system32\DRIVERS\HSX_DPV.sys 14:39:16.0534 4444 HSF_DPV - ok 14:39:16.0552 4444 [ FE440536BD98AF772130DC3A6FE1915F ] HSXHWBS2 C:\Windows\system32\DRIVERS\HSXHWBS2.sys 14:39:16.0558 4444 HSXHWBS2 - ok 14:39:16.0621 4444 [ 0EEECA26C8D4BDE2A4664DB058A81937 ] HTTP C:\Windows\system32\drivers\HTTP.sys 14:39:16.0716 4444 HTTP - ok 14:39:16.0794 4444 [ C6B032D69650985468160FC9937CF5B4 ] i2omp C:\Windows\system32\drivers\i2omp.sys 14:39:16.0834 4444 i2omp - ok 14:39:16.0991 4444 [ 22D56C8184586B7A1F6FA60BE5F5A2BD ] i8042prt C:\Windows\system32\DRIVERS\i8042prt.sys 14:39:16.0993 4444 i8042prt - ok 14:39:17.0069 4444 [ 997E8F5939F2D12CD9F2E6B395724C16 ] iaStor C:\Windows\system32\drivers\iastor.sys 14:39:17.0074 4444 iaStor - ok 14:39:17.0093 4444 [ 54155EA1B0DF185878E0FC9EC3AC3A14 ] iaStorV C:\Windows\system32\drivers\iastorv.sys 14:39:17.0099 4444 iaStorV - ok 14:39:17.0178 4444 [ 98477B08E61945F974ED9FDC4CB6BDAB ] idsvc C:\Windows\Microsoft.NET\Framework\v3.0\Windows Communication Foundation\infocard.exe 14:39:17.0212 4444 idsvc - ok 14:39:17.0319 4444 [ 9378D57E2B96C0A185D844770AD49948 ] igfx C:\Windows\system32\DRIVERS\igdkmd32.sys 14:39:17.0464 4444 igfx - ok 14:39:17.0493 4444 [ 2D077BF86E843F901D8DB709C95B49A5 ] iirsp C:\Windows\system32\drivers\iirsp.sys 14:39:17.0495 4444 iirsp - ok 14:39:17.0546 4444 [ 9908D8A397B76CD8D31D0D383C5773C9 ] IKEEXT C:\Windows\System32\ikeext.dll 14:39:17.0571 4444 IKEEXT - ok 14:39:17.0723 4444 [ F8F53C5449F15B23D4C61D51D2701DA8 ] IntcAzAudAddService C:\Windows\system32\drivers\RTKVHDA.sys 14:39:17.0817 4444 IntcAzAudAddService - ok 14:39:17.0878 4444 [ 83AA759F3189E6370C30DE5DC5590718 ] intelide C:\Windows\system32\DRIVERS\intelide.sys 14:39:17.0880 4444 intelide - ok 14:39:17.0897 4444 [ 224191001E78C89DFA78924C3EA595FF ] intelppm C:\Windows\system32\DRIVERS\intelppm.sys 14:39:17.0898 4444 intelppm - ok 14:39:17.0922 4444 [ 9AC218C6E6105477484C6FDBE7D409A4 ] IPBusEnum C:\Windows\system32\ipbusenum.dll 14:39:17.0926 4444 IPBusEnum - ok 14:39:17.0954 4444 [ 62C265C38769B864CB25B4BCF62DF6C3 ] IpFilterDriver C:\Windows\system32\DRIVERS\ipfltdrv.sys 14:39:17.0956 4444 IpFilterDriver - ok 14:39:18.0015 4444 [ 1998BD97F950680BB55F55A7244679C2 ] iphlpsvc C:\Windows\System32\iphlpsvc.dll 14:39:18.0020 4444 iphlpsvc - ok 14:39:18.0030 4444 IpInIp - ok 14:39:18.0059 4444 [ B25AAF203552B7B3491139D582B39AD1 ] IPMIDRV C:\Windows\system32\drivers\ipmidrv.sys 14:39:18.0062 4444 IPMIDRV - ok 14:39:18.0093 4444 [ 8793643A67B42CEC66490B2A0CF92D68 ] IPNAT C:\Windows\system32\DRIVERS\ipnat.sys 14:39:18.0096 4444 IPNAT - ok 14:39:18.0108 4444 [ 109C0DFB82C3632FBD11949B73AEEAC9 ] IRENUM C:\Windows\system32\drivers\irenum.sys 14:39:18.0109 4444 IRENUM - ok 14:39:18.0142 4444 [ 6C70698A3E5C4376C6AB5C7C17FB0614 ] isapnp C:\Windows\system32\drivers\isapnp.sys 14:39:18.0144 4444 isapnp - ok 14:39:18.0195 4444 [ 232FA340531D940AAC623B121A595034 ] iScsiPrt C:\Windows\system32\DRIVERS\msiscsi.sys 14:39:18.0199 4444 iScsiPrt - ok 14:39:18.0219 4444 [ BCED60D16156E428F8DF8CF27B0DF150 ] iteatapi C:\Windows\system32\drivers\iteatapi.sys 14:39:18.0221 4444 iteatapi - ok 14:39:18.0279 4444 [ 06FA654504A498C30ADCA8BEC4E87E7E ] iteraid C:\Windows\system32\drivers\iteraid.sys 14:39:18.0281 4444 iteraid - ok 14:39:18.0302 4444 [ 37605E0A8CF00CBBA538E753E4344C6E ] kbdclass C:\Windows\system32\DRIVERS\kbdclass.sys 14:39:18.0306 4444 kbdclass - ok 14:39:18.0364 4444 [ EDE59EC70E25C24581ADD1FBEC7325F7 ] kbdhid C:\Windows\system32\DRIVERS\kbdhid.sys 14:39:18.0374 4444 kbdhid - ok 14:39:18.0413 4444 [ A3E186B4B935905B829219502557314E ] KeyIso C:\Windows\system32\lsass.exe 14:39:18.0416 4444 KeyIso - ok 14:39:18.0487 4444 [ 4A1445EFA932A3BAF5BDB02D7131EE20 ] KSecDD C:\Windows\system32\Drivers\ksecdd.sys 14:39:18.0494 4444 KSecDD - ok 14:39:18.0564 4444 [ 8078F8F8F7A79E2E6B494523A828C585 ] KtmRm C:\Windows\system32\msdtckrm.dll 14:39:18.0568 4444 KtmRm - ok 14:39:18.0656 4444 [ 1BF5EEBFD518DD7298434D8C862F825D ] LanmanServer C:\Windows\system32\srvsvc.dll 14:39:18.0660 4444 LanmanServer - ok 14:39:18.0706 4444 [ 1DB69705B695B987082C8BAEC0C6B34F ] LanmanWorkstation C:\Windows\System32\wkssvc.dll 14:39:18.0715 4444 LanmanWorkstation - ok 14:39:18.0753 4444 [ D1C5883087A0C3F1344D9D55A44901F6 ] lltdio C:\Windows\system32\DRIVERS\lltdio.sys 14:39:18.0755 4444 lltdio - ok 14:39:18.0818 4444 [ 2D5A428872F1442631D0959A34ABFF63 ] lltdsvc C:\Windows\System32\lltdsvc.dll 14:39:18.0824 4444 lltdsvc - ok 14:39:18.0841 4444 [ 35D40113E4A5B961B6CE5C5857702518 ] lmhosts C:\Windows\System32\lmhsvc.dll 14:39:18.0844 4444 lmhosts - ok 14:39:18.0951 4444 [ 63DAF163D1617DD611BD0AB8E41A43E8 ] LMIGuardianSvc C:\Program Files\LogMeIn\x86\LMIGuardianSvc.exe 14:39:18.0959 4444 LMIGuardianSvc - ok 14:39:19.0014 4444 [ 4F69FAAABB7DB0D43E327C0B6AAB40FC ] LMIInfo C:\Program Files\LogMeIn\x86\RaInfo.sys 14:39:19.0016 4444 LMIInfo - ok 14:39:19.0075 4444 [ 175F50F37EEAA1D4D744BCCCBB7CF68C ] LMIMaint C:\Program Files\LogMeIn\x86\RaMaint.exe 14:39:19.0078 4444 LMIMaint - ok 14:39:19.0133 4444 [ 4477689E2D8AE6B78BA34C9AF4CC1ED1 ] lmimirr C:\Windows\system32\DRIVERS\lmimirr.sys 14:39:19.0135 4444 lmimirr - ok 14:39:19.0167 4444 LMIRfsClientNP - ok 14:39:19.0201 4444 [ 3FAA563DDF853320F90259D455A01D79 ] LMIRfsDriver C:\Windows\system32\drivers\LMIRfsDriver.sys 14:39:19.0203 4444 LMIRfsDriver - ok 14:39:19.0338 4444 [ 432618FA75B61059D2C57D6A7E55147A ] LogMeIn C:\Program Files\LogMeIn\x86\LogMeIn.exe 14:39:19.0345 4444 LogMeIn - ok 14:39:19.0411 4444 [ C7E15E82879BF3235B559563D4185365 ] LSI_FC C:\Windows\system32\drivers\lsi_fc.sys 14:39:19.0434 4444 LSI_FC - ok 14:39:19.0569 4444 [ EE01EBAE8C9BF0FA072E0FF68718920A ] LSI_SAS C:\Windows\system32\drivers\lsi_sas.sys 14:39:19.0578 4444 LSI_SAS - ok 14:39:19.0641 4444 [ 912A04696E9CA30146A62AFA1463DD5C ] LSI_SCSI C:\Windows\system32\drivers\lsi_scsi.sys 14:39:19.0646 4444 LSI_SCSI - ok 14:39:19.0704 4444 [ 8F5C7426567798E62A3B3614965D62CC ] luafv C:\Windows\system32\drivers\luafv.sys 14:39:19.0708 4444 luafv - ok 14:39:19.0830 4444 [ 7E6932EEDA54C8EAF7DC6C2225261B85 ] mcmscsvc C:\Program Files\Common Files\Mcafee\McSvcHost\McSvHost.exe 14:39:19.0833 4444 mcmscsvc - ok 14:39:19.0855 4444 [ 7E6932EEDA54C8EAF7DC6C2225261B85 ] McNaiAnn C:\Program Files\Common Files\Mcafee\McSvcHost\McSvHost.exe 14:39:19.0857 4444 McNaiAnn - ok 14:39:19.0889 4444 [ 7E6932EEDA54C8EAF7DC6C2225261B85 ] McNASvc C:\Program Files\Common Files\Mcafee\McSvcHost\McSvHost.exe 14:39:19.0891 4444 McNASvc - ok 14:39:19.0966 4444 [ 135AA9E9E7047B7DC1F753205D421A26 ] McODS C:\Program Files\McAfee\VirusScan\mcods.exe 14:39:19.0970 4444 McODS - ok 14:39:19.0997 4444 [ 7E6932EEDA54C8EAF7DC6C2225261B85 ] McProxy C:\Program Files\Common Files\Mcafee\McSvcHost\McSvHost.exe 14:39:19.0999 4444 McProxy - ok 14:39:20.0073 4444 [ 593FA4C378818ECE76BA64A11AD56CF2 ] McShield C:\Program Files\Common Files\McAfee\SystemCore\\mcshield.exe 14:39:20.0080 4444 McShield - ok 14:39:20.0100 4444 [ 0CEA2D0D3FA284B85ED5B68365114F76 ] mdmxsdk C:\Windows\system32\DRIVERS\mdmxsdk.sys 14:39:20.0102 4444 mdmxsdk - ok 14:39:20.0134 4444 [ 0001CE609D66632FA17B84705F658879 ] megasas C:\Windows\system32\drivers\megasas.sys 14:39:20.0136 4444 megasas - ok 14:39:20.0164 4444 [ C252F32CD9A49DBFC25ECF26EBD51A99 ] MegaSR C:\Windows\system32\drivers\megasr.sys 14:39:20.0181 4444 MegaSR - ok 14:39:20.0206 4444 [ 43C31BDF404A6D7A7AC1BFD5EAD2A566 ] mfeapfk C:\Windows\system32\drivers\mfeapfk.sys 14:39:20.0209 4444 mfeapfk - ok 14:39:20.0304 4444 [ C1DC5F42D3367F33B6451BE78B38BD46 ] mfeavfk C:\Windows\system32\drivers\mfeavfk.sys 14:39:20.0330 4444 mfeavfk - ok 14:39:20.0345 4444 mfeavfk01 - ok 14:39:20.0372 4444 [ 0435C43F4C2BE01B84868AD2A906397B ] mfebopk C:\Windows\system32\drivers\mfebopk.sys 14:39:20.0374 4444 mfebopk - ok 14:39:20.0410 4444 [ 7E1F8B1BDC8240F08BD358B3A466C005 ] mfefire C:\Program Files\Common Files\McAfee\SystemCore\\mfefire.exe 14:39:20.0414 4444 mfefire - ok 14:39:20.0444 4444 [ 4EA6FF90015424517843E931448E00F1 ] mfefirek C:\Windows\system32\drivers\mfefirek.sys 14:39:20.0451 4444 mfefirek - ok 14:39:20.0517 4444 [ D1E998748BA24A731106611D535C6BBF ] mfehidk C:\Windows\system32\drivers\mfehidk.sys 14:39:20.0526 4444 mfehidk - ok 14:39:20.0540 4444 [ AC04A618AEF3DE0FCE91C766F9E069DA ] mfenlfk C:\Windows\system32\DRIVERS\mfenlfk.sys 14:39:20.0542 4444 mfenlfk - ok 14:39:20.0591 4444 [ F454A13377F0A006D20A8C14A753C432 ] mferkdet C:\Windows\system32\drivers\mferkdet.sys 14:39:20.0595 4444 mferkdet - ok 14:39:20.0635 4444 [ B10C4EFD40810C08F4B44DF2EFCB54F7 ] mfevtp C:\Windows\system32\mfevtps.exe 14:39:20.0639 4444 mfevtp - ok 14:39:20.0661 4444 [ F284337AEDB7483DF8A5FA840647E2B0 ] mfewfpk C:\Windows\system32\drivers\mfewfpk.sys 14:39:20.0665 4444 mfewfpk - ok 14:39:20.0696 4444 [ 1076FFCFFAAE8385FD62DFCB25AC4708 ] MMCSS C:\Windows\system32\mmcss.dll 14:39:20.0699 4444 MMCSS - ok 14:39:20.0714 4444 [ E13B5EA0F51BA5B1512EC671393D09BA ] Modem C:\Windows\system32\drivers\modem.sys 14:39:20.0715 4444 Modem - ok 14:39:20.0756 4444 [ 0A9BB33B56E294F686ABB7C1E4E2D8A8 ] monitor C:\Windows\system32\DRIVERS\monitor.sys 14:39:20.0758 4444 monitor - ok 14:39:20.0777 4444 [ 5BF6A1326A335C5298477754A506D263 ] mouclass C:\Windows\system32\DRIVERS\mouclass.sys 14:39:20.0794 4444 mouclass - ok 14:39:20.0815 4444 [ 93B8D4869E12CFBE663915502900876F ] mouhid C:\Windows\system32\DRIVERS\mouhid.sys 14:39:20.0817 4444 mouhid - ok 14:39:20.0828 4444 [ BDAFC88AA6B92F7842416EA6A48E1600 ] MountMgr C:\Windows\system32\drivers\mountmgr.sys 14:39:20.0830 4444 MountMgr - ok 14:39:20.0855 4444 [ 511D011289755DD9F9A7579FB0B064E6 ] mpio C:\Windows\system32\drivers\mpio.sys 14:39:20.0859 4444 mpio - ok 14:39:20.0889 4444 [ 22241FEBA9B2DEFA669C8CB0A8DD7D2E ] mpsdrv C:\Windows\system32\drivers\mpsdrv.sys 14:39:20.0891 4444 mpsdrv - ok 14:39:20.0920 4444 [ 5DE62C6E9108F14F6794060A9BDECAEC ] MpsSvc C:\Windows\system32\mpssvc.dll 14:39:20.0929 4444 MpsSvc - ok 14:39:20.0970 4444 [ 4FBBB70D30FD20EC51F80061703B001E ] Mraid35x C:\Windows\system32\drivers\mraid35x.sys 14:39:20.0971 4444 Mraid35x - ok 14:39:21.0025 4444 [ 82CEA0395524AACFEB58BA1448E8325C ] MRxDAV C:\Windows\system32\drivers\mrxdav.sys 14:39:21.0028 4444 MRxDAV - ok 14:39:21.0076 4444 [ 1E94971C4B446AB2290DEB71D01CF0C2 ] mrxsmb C:\Windows\system32\DRIVERS\mrxsmb.sys 14:39:21.0079 4444 mrxsmb - ok 14:39:21.0134 4444 [ 4FCCB34D793B116423209C0F8B7A3B03 ] mrxsmb10 C:\Windows\system32\DRIVERS\mrxsmb10.sys 14:39:21.0138 4444 mrxsmb10 - ok 14:39:21.0160 4444 [ C3CB1B40AD4A0124D617A1199B0B9D7C ] mrxsmb20 C:\Windows\system32\DRIVERS\mrxsmb20.sys 14:39:21.0162 4444 mrxsmb20 - ok 14:39:21.0201 4444 [ F70590424EEFBF5C27A40C67AFDB8383 ] msahci C:\Windows\system32\drivers\msahci.sys 14:39:21.0203 4444 msahci - ok 14:39:21.0241 4444 [ 4468B0F385A86ECDDAF8D3CA662EC0E7 ] msdsm C:\Windows\system32\drivers\msdsm.sys 14:39:21.0244 4444 msdsm - ok 14:39:21.0283 4444 [ FD7520CC3A80C5FC8C48852BB24C6DED ] MSDTC C:\Windows\System32\msdtc.exe 14:39:21.0286 4444 MSDTC - ok 14:39:21.0313 4444 [ A9927F4A46B816C92F461ACB90CF8515 ] Msfs C:\Windows\system32\drivers\Msfs.sys 14:39:21.0316 4444 Msfs - ok 14:39:21.0351 4444 [ 0F400E306F385C56317357D6DEA56F62 ] msisadrv C:\Windows\system32\drivers\msisadrv.sys 14:39:21.0354 4444 msisadrv - ok 14:39:21.0424 4444 [ 85466C0757A23D9A9AECDC0755203CB2 ] MSiSCSI C:\Windows\system32\iscsiexe.dll 14:39:21.0427 4444 MSiSCSI - ok 14:39:21.0439 4444 msiserver - ok 14:39:21.0472 4444 [ D8C63D34D9C9E56C059E24EC7185CC07 ] MSKSSRV C:\Windows\system32\drivers\MSKSSRV.sys 14:39:21.0473 4444 MSKSSRV - ok 14:39:21.0499 4444 [ 1D373C90D62DDB641D50E55B9E78D65E ] MSPCLOCK C:\Windows\system32\drivers\MSPCLOCK.sys 14:39:21.0500 4444 MSPCLOCK - ok 14:39:21.0541 4444 [ B572DA05BF4E098D4BBA3A4734FB505B ] MSPQM C:\Windows\system32\drivers\MSPQM.sys 14:39:21.0543 4444 MSPQM - ok 14:39:21.0615 4444 [ B49456D70555DE905C311BCDA6EC6ADB ] MsRPC C:\Windows\system32\drivers\MsRPC.sys 14:39:21.0618 4444 MsRPC - ok 14:39:21.0662 4444 [ E384487CB84BE41D09711C30CA79646C ] mssmbios C:\Windows\system32\DRIVERS\mssmbios.sys 14:39:21.0662 4444 mssmbios - ok 14:39:21.0686 4444 [ 7199C1EEC1E4993CAF96B8C0A26BD58A ] MSTEE C:\Windows\system32\drivers\MSTEE.sys 14:39:21.0688 4444 MSTEE - ok 14:39:21.0743 4444 [ 6A57B5733D4CB702C8EA4542E836B96C ] Mup C:\Windows\system32\Drivers\mup.sys 14:39:21.0745 4444 Mup - ok 14:39:21.0801 4444 [ E4EAF0C5C1B41B5C83386CF212CA9584 ] napagent C:\Windows\system32\qagentRT.dll 14:39:21.0818 4444 napagent - ok 14:39:21.0867 4444 [ 85C44FDFF9CF7E72A40DCB7EC06A4416 ] NativeWifiP C:\Windows\system32\DRIVERS\nwifi.sys 14:39:21.0870 4444 NativeWifiP - ok 14:39:21.0940 4444 [ 1357274D1883F68300AEADD15D7BBB42 ] NDIS C:\Windows\system32\drivers\ndis.sys 14:39:22.0017 4444 NDIS - ok 14:39:22.0053 4444 [ 0E186E90404980569FB449BA7519AE61 ] NdisTapi C:\Windows\system32\DRIVERS\ndistapi.sys 14:39:22.0073 4444 NdisTapi - ok 14:39:22.0107 4444 [ D6973AA34C4D5D76C0430B181C3CD389 ] Ndisuio C:\Windows\system32\DRIVERS\ndisuio.sys 14:39:22.0132 4444 Ndisuio - ok 14:39:22.0192 4444 [ 818F648618AE34F729FDB47EC68345C3 ] NdisWan C:\Windows\system32\DRIVERS\ndiswan.sys 14:39:22.0200 4444 NdisWan - ok 14:39:22.0221 4444 [ 71DAB552B41936358F3B541AE5997FB3 ] NDProxy C:\Windows\system32\drivers\NDProxy.sys 14:39:22.0224 4444 NDProxy - ok 14:39:22.0318 4444 [ 2969D26EEE289BE7422AA46FC55F4E38 ] Net Driver HPZ12 C:\Windows\system32\HPZinw12.dll 14:39:22.0330 4444 Net Driver HPZ12 - ok 14:39:22.0359 4444 [ BCD093A5A6777CF626434568DC7DBA78 ] NetBIOS C:\Windows\system32\DRIVERS\netbios.sys 14:39:22.0367 4444 NetBIOS - ok 14:39:22.0475 4444 [ ECD64230A59CBD93C85F1CD1CAB9F3F6 ] netbt C:\Windows\system32\DRIVERS\netbt.sys 14:39:22.0479 4444 netbt - ok 14:39:22.0517 4444 [ A3E186B4B935905B829219502557314E ] Netlogon C:\Windows\system32\lsass.exe 14:39:22.0519 4444 Netlogon - ok 14:39:22.0547 4444 [ C8052711DAECC48B982434C5116CA401 ] Netman C:\Windows\System32\netman.dll 14:39:22.0556 4444 Netman - ok 14:39:22.0574 4444 [ 2EF3BBE22E5A5ACD1428EE387A0D0172 ] netprofm C:\Windows\System32\netprofm.dll 14:39:22.0583 4444 netprofm - ok 14:39:22.0644 4444 [ D6C4E4A39A36029AC0813D476FBD0248 ] NetTcpPortSharing C:\Windows\Microsoft.NET\Framework\v3.0\Windows Communication Foundation\SMSvcHost.exe 14:39:22.0648 4444 NetTcpPortSharing - ok 14:39:22.0674 4444 [ 2E7FB731D4790A1BC6270ACCEFACB36E ] nfrd960 C:\Windows\system32\drivers\nfrd960.sys 14:39:22.0677 4444 nfrd960 - ok 14:39:22.0758 4444 [ 2997B15415F9BBE05B5A4C1C85E0C6A2 ] NlaSvc C:\Windows\System32\nlasvc.dll 14:39:22.0762 4444 NlaSvc - ok 14:39:22.0821 4444 [ D36F239D7CCE1931598E8FB90A0DBC26 ] Npfs C:\Windows\system32\drivers\Npfs.sys 14:39:22.0823 4444 Npfs - ok 14:39:22.0881 4444 [ 8BB86F0C7EEA2BDED6FE095D0B4CA9BD ] nsi C:\Windows\system32\nsisvc.dll 14:39:22.0888 4444 nsi - ok 14:39:22.0909 4444 [ 609773E344A97410CE4EBF74A8914FCF ] nsiproxy C:\Windows\system32\drivers\nsiproxy.sys 14:39:22.0911 4444 nsiproxy - ok 14:39:22.0987 4444 [ 6A4A98CEE84CF9E99564510DDA4BAA47 ] Ntfs C:\Windows\system32\drivers\Ntfs.sys 14:39:23.0017 4444 Ntfs - ok 14:39:23.0055 4444 [ E875C093AEC0C978A90F30C9E0DFBB72 ] ntrigdigi C:\Windows\system32\drivers\ntrigdigi.sys 14:39:23.0056 4444 ntrigdigi - ok 14:39:23.0073 4444 [ C5DBBCDA07D780BDA9B685DF333BB41E ] Null C:\Windows\system32\drivers\Null.sys 14:39:23.0076 4444 Null - ok 14:39:23.0102 4444 [ 2EDF9E7751554B42CBB60116DE727101 ] nvraid C:\Windows\system32\drivers\nvraid.sys 14:39:23.0119 4444 nvraid - ok 14:39:23.0143 4444 [ ABED0C09758D1D97DB0042DBB2688177 ] nvstor C:\Windows\system32\drivers\nvstor.sys 14:39:23.0156 4444 nvstor - ok 14:39:23.0195 4444 [ 18BBDF913916B71BD54575BDB6EEAC0B ] nv_agp C:\Windows\system32\drivers\nv_agp.sys 14:39:23.0198 4444 nv_agp - ok 14:39:23.0248 4444 NwlnkFlt - ok 14:39:23.0259 4444 NwlnkFwd - ok 14:39:23.0538 4444 [ BE32DA025A0BE1878F0EE8D6D9386CD5 ] ohci1394 C:\Windows\system32\drivers\ohci1394.sys 14:39:23.0559 4444 ohci1394 - ok 14:39:23.0625 4444 [ 0C8E8E61AD1EB0B250B846712C917506 ] p2pimsvc C:\Windows\system32\p2psvc.dll 14:39:23.0657 4444 p2pimsvc - ok 14:39:23.0674 4444 [ 0C8E8E61AD1EB0B250B846712C917506 ] p2psvc C:\Windows\system32\p2psvc.dll 14:39:23.0682 4444 p2psvc - ok 14:39:23.0748 4444 [ 0FA9B5055484649D63C303FE404E5F4D ] Parport C:\Windows\system32\drivers\parport.sys 14:39:23.0750 4444 Parport - ok 14:39:23.0798 4444 [ B9C2B89F08670E159F7181891E449CD9 ] partmgr C:\Windows\system32\drivers\partmgr.sys 14:39:23.0801 4444 partmgr - ok 14:39:23.0815 4444 [ 4F9A6A8A31413180D0FCB279AD5D8112 ] Parvdm C:\Windows\system32\drivers\parvdm.sys 14:39:23.0817 4444 Parvdm - ok 14:39:23.0845 4444 [ C6276AD11F4BB49B58AA1ED88537F14A ] PcaSvc C:\Windows\System32\pcasvc.dll 14:39:23.0848 4444 PcaSvc - ok 14:39:23.0938 4444 [ 941DC1D19E7E8620F40BBC206981EFDB ] pci C:\Windows\system32\drivers\pci.sys 14:39:23.0942 4444 pci - ok 14:39:24.0002 4444 [ 1636D43F10416AEB483BC6001097B26C ] pciide C:\Windows\system32\drivers\pciide.sys 14:39:24.0004 4444 pciide - ok 14:39:24.0084 4444 [ E6F3FB1B86AA519E7698AD05E58B04E5 ] pcmcia C:\Windows\system32\drivers\pcmcia.sys 14:39:24.0087 4444 pcmcia - ok 14:39:24.0131 4444 [ 6349F6ED9C623B44B52EA3C63C831A92 ] PEAUTH C:\Windows\system32\drivers\peauth.sys 14:39:24.0163 4444 PEAUTH - ok 14:39:24.0248 4444 [ B1689DF169143F57053F795390C99DB3 ] pla C:\Windows\system32\pla.dll 14:39:24.0348 4444 pla - ok 14:39:24.0409 4444 [ C5E7F8A996EC0A82D508FD9064A5569E ] PlugPlay C:\Windows\system32\umpnpmgr.dll 14:39:24.0415 4444 PlugPlay - ok 14:39:24.0524 4444 [ BAFC9706BDF425A02B66468AB2605C59 ] Pml Driver HPZ12 C:\Windows\system32\HPZipm12.dll 14:39:24.0526 4444 Pml Driver HPZ12 - ok 14:39:24.0558 4444 [ 0C8E8E61AD1EB0B250B846712C917506 ] PNRPAutoReg C:\Windows\system32\p2psvc.dll 14:39:24.0575 4444 PNRPAutoReg - ok 14:39:24.0599 4444 [ 0C8E8E61AD1EB0B250B846712C917506 ] PNRPsvc C:\Windows\system32\p2psvc.dll 14:39:24.0606 4444 PNRPsvc - ok 14:39:24.0635 4444 [ D0494460421A03CD5225CCA0059AA146 ] PolicyAgent C:\Windows\System32\ipsecsvc.dll 14:39:24.0652 4444 PolicyAgent - ok 14:39:24.0682 4444 [ ECFFFAEC0C1ECD8DBC77F39070EA1DB1 ] PptpMiniport C:\Windows\system32\DRIVERS\raspptp.sys 14:39:24.0685 4444 PptpMiniport - ok 14:39:24.0715 4444 [ 2027293619DD0F047C584CF2E7DF4FFD ] Processor C:\Windows\system32\drivers\processr.sys 14:39:24.0717 4444 Processor - ok 14:39:24.0779 4444 [ 0508FAA222D28835310B7BFCA7A77346 ] ProfSvc C:\Windows\system32\profsvc.dll 14:39:24.0785 4444 ProfSvc - ok 14:39:24.0866 4444 [ A3E186B4B935905B829219502557314E ] ProtectedStorage C:\Windows\system32\lsass.exe 14:39:24.0868 4444 ProtectedStorage - ok 14:39:24.0958 4444 [ 99514FAA8DF93D34B5589187DB3AA0BA ] PSched C:\Windows\system32\DRIVERS\pacer.sys 14:39:24.0960 4444 PSched - ok 14:39:24.0990 4444 [ 03E0FE281823BA64B3782F5B38950E73 ] PxHelp20 C:\Windows\system32\Drivers\PxHelp20.sys 14:39:24.0993 4444 PxHelp20 - ok 14:39:25.0051 4444 [ 0A6DB55AFB7820C99AA1F3A1D270F4F6 ] ql2300 C:\Windows\system32\drivers\ql2300.sys 14:39:25.0097 4444 ql2300 - ok 14:39:25.0125 4444 [ 81A7E5C076E59995D54BC1ED3A16E60B ] ql40xx C:\Windows\system32\drivers\ql40xx.sys 14:39:25.0128 4444 ql40xx - ok 14:39:25.0160 4444 [ E9ECAE663F47E6CB43962D18AB18890F ] QWAVE C:\Windows\system32\qwave.dll 14:39:25.0166 4444 QWAVE - ok 14:39:25.0183 4444 [ 9F5E0E1926014D17486901C88ECA2DB7 ] QWAVEdrv C:\Windows\system32\drivers\qwavedrv.sys 14:39:25.0185 4444 QWAVEdrv - ok 14:39:25.0345 4444 [ E642B131FB74CAF4BB8A014F31113142 ] R300 C:\Windows\system32\DRIVERS\atikmdag.sys 14:39:25.0428 4444 R300 - ok 14:39:25.0458 4444 [ 147D7F9C556D259924351FEB0DE606C3 ] RasAcd C:\Windows\system32\DRIVERS\rasacd.sys 14:39:25.0459 4444 RasAcd - ok 14:39:25.0495 4444 [ F6A452EB4CEADBB51C9E0EE6B3ECEF0F ] RasAuto C:\Windows\System32\rasauto.dll 14:39:25.0499 4444 RasAuto - ok 14:39:25.0536 4444 [ A214ADBAF4CB47DD2728859EF31F26B0 ] Rasl2tp C:\Windows\system32\DRIVERS\rasl2tp.sys 14:39:25.0539 4444 Rasl2tp - ok 14:39:25.0597 4444 [ 75D47445D70CA6F9F894B032FBC64FCF ] RasMan C:\Windows\System32\rasmans.dll 14:39:25.0606 4444 RasMan - ok 14:39:25.0667 4444 [ 509A98DD18AF4375E1FC40BC175F1DEF ] RasPppoe C:\Windows\system32\DRIVERS\raspppoe.sys 14:39:25.0669 4444 RasPppoe - ok 14:39:25.0746 4444 [ 2005F4A1E05FA09389AC85840F0A9E4D ] RasSstp C:\Windows\system32\DRIVERS\rassstp.sys 14:39:25.0748 4444 RasSstp - ok 14:39:25.0835 4444 [ B14C9D5B9ADD2F84F70570BBBFAA7935 ] rdbss C:\Windows\system32\DRIVERS\rdbss.sys 14:39:25.0839 4444 rdbss - ok 14:39:25.0914 4444 [ 89E59BE9A564262A3FB6C4F4F1CD9899 ] RDPCDD C:\Windows\system32\DRIVERS\RDPCDD.sys 14:39:25.0916 4444 RDPCDD - ok 14:39:25.0966 4444 [ FBC0BACD9C3D7F6956853F64A66E252D ] rdpdr C:\Windows\system32\drivers\rdpdr.sys 14:39:25.0971 4444 rdpdr - ok 14:39:26.0014 4444 [ 9D91FE5286F748862ECFFA05F8A0710C ] RDPENCDD C:\Windows\system32\drivers\rdpencdd.sys 14:39:26.0015 4444 RDPENCDD - ok 14:39:26.0118 4444 [ C127EBD5AFAB31524662C48DFCEB773A ] RDPWD C:\Windows\system32\drivers\RDPWD.sys 14:39:26.0135 4444 RDPWD - ok 14:39:26.0178 4444 [ BCDD6B4804D06B1F7EBF29E53A57ECE9 ] RemoteAccess C:\Windows\System32\mprdim.dll 14:39:26.0186 4444 RemoteAccess - ok 14:39:26.0235 4444 [ 9E6894EA18DAFF37B63E1005F83AE4AB ] RemoteRegistry C:\Windows\system32\regsvc.dll 14:39:26.0239 4444 RemoteRegistry - ok 14:39:26.0290 4444 [ 5123F83CBC4349D065534EEB6BBDC42B ] RpcLocator C:\Windows\system32\locator.exe 14:39:26.0314 4444 RpcLocator - ok 14:39:26.0399 4444 [ 3B5B4D53FEC14F7476CA29A20CC31AC9 ] RpcSs C:\Windows\system32\rpcss.dll 14:39:26.0405 4444 RpcSs - ok 14:39:26.0442 4444 [ 9C508F4074A39E8B4B31D27198146FAD ] rspndr C:\Windows\system32\DRIVERS\rspndr.sys 14:39:26.0445 4444 rspndr - ok 14:39:26.0474 4444 [ A3E186B4B935905B829219502557314E ] SamSs C:\Windows\system32\lsass.exe 14:39:26.0475 4444 SamSs - ok 14:39:26.0508 4444 [ 3CE8F073A557E172B330109436984E30 ] sbp2port C:\Windows\system32\drivers\sbp2port.sys 14:39:26.0511 4444 sbp2port - ok 14:39:26.0575 4444 [ 77B7A11A0C3D78D3386398FBBEA1B632 ] SCardSvr C:\Windows\System32\SCardSvr.dll 14:39:26.0582 4444 SCardSvr - ok 14:39:26.0682 4444 [ 1A58069DB21D05EB2AB58EE5753EBE8D ] Schedule C:\Windows\system32\schedsvc.dll 14:39:26.0699 4444 Schedule - ok 14:39:26.0725 4444 [ 312EC3E37A0A1F2006534913E37B4423 ] SCPolicySvc C:\Windows\System32\certprop.dll 14:39:26.0726 4444 SCPolicySvc - ok 14:39:26.0753 4444 [ 716313D9F6B0529D03F726D5AAF6F191 ] SDRSVC C:\Windows\System32\SDRSVC.dll 14:39:26.0757 4444 SDRSVC - ok 14:39:26.0787 4444 [ 90A3935D05B494A5A39D37E71F09A677 ] secdrv C:\Windows\system32\drivers\secdrv.sys 14:39:26.0788 4444 secdrv - ok 14:39:26.0808 4444 [ FD5199D4D8A521005E4B5EE7FE00FA9B ] seclogon C:\Windows\system32\seclogon.dll 14:39:26.0811 4444 seclogon - ok 14:39:26.0829 4444 [ A9BBAB5759771E523F55563D6CBE140F ] SENS C:\Windows\System32\sens.dll 14:39:26.0833 4444 SENS - ok 14:39:26.0856 4444 [ 68E44E331D46F0FB38F0863A84CD1A31 ] Serenum C:\Windows\system32\drivers\serenum.sys 14:39:26.0857 4444 Serenum - ok 14:39:26.0885 4444 [ C70D69A918B178D3C3B06339B40C2E1B ] Serial C:\Windows\system32\drivers\serial.sys 14:39:26.0888 4444 Serial - ok 14:39:26.0902 4444 [ 8AF3D28A879BF75DB53A0EE7A4289624 ] sermouse C:\Windows\system32\drivers\sermouse.sys 14:39:26.0905 4444 sermouse - ok 14:39:26.0957 4444 [ D2193326F729B163125610DBF3E17D57 ] SessionEnv C:\Windows\system32\sessenv.dll 14:39:26.0961 4444 SessionEnv - ok 14:39:26.0990 4444 [ 3EFA810BDCA87F6ECC24F9832243FE86 ] sffdisk C:\Windows\system32\drivers\sffdisk.sys 14:39:26.0992 4444 sffdisk - ok 14:39:27.0014 4444 [ E95D451F7EA3E583AEC75F3B3EE42DC5 ] sffp_mmc C:\Windows\system32\drivers\sffp_mmc.sys 14:39:27.0015 4444 sffp_mmc - ok 14:39:27.0033 4444 [ 3D0EA348784B7AC9EA9BD9F317980979 ] sffp_sd C:\Windows\system32\drivers\sffp_sd.sys 14:39:27.0035 4444 sffp_sd - ok 14:39:27.0064 4444 [ 46ED8E91793B2E6F848015445A0AC188 ] sfloppy C:\Windows\system32\drivers\sfloppy.sys 14:39:27.0066 4444 sfloppy - ok 14:39:27.0128 4444 [ E1499BD0FF76B1B2FBBF1AF339D91165 ] SharedAccess C:\Windows\System32\ipnathlp.dll 14:39:27.0155 4444 SharedAccess - ok 14:39:27.0194 4444 [ C7230FBEE14437716701C15BE02C27B8 ] ShellHWDetection C:\Windows\System32\shsvcs.dll 14:39:27.0201 4444 ShellHWDetection - ok 14:39:27.0243 4444 [ 1D76624A09A054F682D746B924E2DBC3 ] sisagp C:\Windows\system32\drivers\sisagp.sys 14:39:27.0246 4444 sisagp - ok 14:39:27.0284 4444 [ 43CB7AA756C7DB280D01DA9B676CFDE2 ] SiSRaid2 C:\Windows\system32\drivers\sisraid2.sys 14:39:27.0287 4444 SiSRaid2 - ok 14:39:27.0302 4444 [ A99C6C8B0BAA970D8AA59DDC50B57F94 ] SiSRaid4 C:\Windows\system32\drivers\sisraid4.sys 14:39:27.0306 4444 SiSRaid4 - ok 14:39:27.0658 4444 [ 862BB4CBC05D80C5B45BE430E5EF872F ] slsvc C:\Windows\system32\SLsvc.exe 14:39:29.0146 4444 slsvc - ok 14:39:29.0238 4444 [ 6EDC422215CD78AA8A9CDE6B30ABBD35 ] SLUINotify C:\Windows\system32\SLUINotify.dll 14:39:29.0263 4444 SLUINotify - ok 14:39:29.0337 4444 [ 7B75299A4D201D6A6533603D6914AB04 ] Smb C:\Windows\system32\DRIVERS\smb.sys 14:39:29.0395 4444 Smb - ok 14:39:29.0495 4444 [ 2A146A055B4401C16EE62D18B8E2A032 ] SNMPTRAP C:\Windows\System32\snmptrap.exe 14:39:29.0538 4444 SNMPTRAP - ok 14:39:29.0626 4444 [ 7AEBDEEF071FE28B0EEF2CDD69102BFF ] spldr C:\Windows\system32\drivers\spldr.sys 14:39:29.0655 4444 spldr - ok 14:39:29.0787 4444 [ 8554097E5136C3BF9F69FE578A1B35F4 ] Spooler C:\Windows\System32\spoolsv.exe 14:39:29.0826 4444 Spooler - ok 14:39:29.0974 4444 [ 41987F9FC0E61ADF54F581E15029AD91 ] srv C:\Windows\system32\DRIVERS\srv.sys 14:39:30.0126 4444 srv - ok 14:39:30.0202 4444 [ FF33AFF99564B1AA534F58868CBE41EF ] srv2 C:\Windows\system32\DRIVERS\srv2.sys 14:39:30.0206 4444 srv2 - ok 14:39:30.0274 4444 [ 7605C0E1D01A08F3ECD743F38B834A44 ] srvnet C:\Windows\system32\DRIVERS\srvnet.sys 14:39:30.0330 4444 srvnet - ok 14:39:30.0419 4444 [ 03D50B37234967433A5EA5BA72BC0B62 ] SSDPSRV C:\Windows\System32\ssdpsrv.dll 14:39:30.0426 4444 SSDPSRV - ok 14:39:30.0464 4444 [ 6F1A32E7B7B30F004D9A20AFADB14944 ] SstpSvc C:\Windows\system32\sstpsvc.dll 14:39:30.0474 4444 SstpSvc - ok 14:39:30.0583 4444 [ 5DE7D67E49B88F5F07F3E53C4B92A352 ] stisvc C:\Windows\System32\wiaservc.dll 14:39:30.0588 4444 stisvc - ok 14:39:30.0716 4444 [ 1D0063597C3666404FCF97698ABEB019 ] stllssvr C:\Program Files\Common Files\SureThing Shared\stllssvr.exe 14:39:30.0726 4444 stllssvr - ok 14:39:30.0780 4444 [ 7BA58ECF0C0A9A69D44B3DCA62BECF56 ] swenum C:\Windows\system32\DRIVERS\swenum.sys 14:39:30.0792 4444 swenum - ok 14:39:30.0911 4444 [ F21FD248040681CCA1FB6C9A03AAA93D ] swprv C:\Windows\System32\swprv.dll 14:39:31.0081 4444 swprv - ok 14:39:31.0127 4444 [ 192AA3AC01DF071B541094F251DEED10 ] Symc8xx C:\Windows\system32\drivers\symc8xx.sys 14:39:31.0135 4444 Symc8xx - ok 14:39:31.0228 4444 [ 8C8EB8C76736EBAF3B13B633B2E64125 ] Sym_hi C:\Windows\system32\drivers\sym_hi.sys 14:39:31.0238 4444 Sym_hi - ok 14:39:31.0266 4444 [ 8072AF52B5FD103BBBA387A1E49F62CB ] Sym_u3 C:\Windows\system32\drivers\sym_u3.sys 14:39:31.0289 4444 Sym_u3 - ok 14:39:31.0496 4444 [ 9A51B04E9886AA4EE90093586B0BA88D ] SysMain C:\Windows\system32\sysmain.dll 14:39:31.0545 4444 SysMain - ok 14:39:31.0640 4444 [ 2DCA225EAE15F42C0933E998EE0231C3 ] TabletInputService C:\Windows\System32\TabSvc.dll 14:39:31.0644 4444 TabletInputService - ok 14:39:31.0796 4444 [ D7673E4B38CE21EE54C59EEEB65E2483 ] TapiSrv C:\Windows\System32\tapisrv.dll 14:39:31.0854 4444 TapiSrv - ok 14:39:31.0938 4444 [ CB05822CD9CC6C688168E113C603DBE7 ] TBS C:\Windows\System32\tbssvc.dll 14:39:31.0941 4444 TBS - ok 14:39:32.0181 4444 [ 27D470DABC77BC60D0A3B0E4DEB6CB91 ] Tcpip C:\Windows\system32\drivers\tcpip.sys 14:39:32.0908 4444 Tcpip - ok 14:39:33.0205 4444 [ 27D470DABC77BC60D0A3B0E4DEB6CB91 ] Tcpip6 C:\Windows\system32\DRIVERS\tcpip.sys 14:39:33.0212 4444 Tcpip6 - ok 14:39:33.0330 4444 [ 608C345A255D82A6289C2D468EB41FD7 ] tcpipreg C:\Windows\system32\drivers\tcpipreg.sys 14:39:33.0349 4444 tcpipreg - ok 14:39:33.0435 4444 [ 5DCF5E267BE67A1AE926F2DF77FBCC56 ] TDPIPE C:\Windows\system32\drivers\tdpipe.sys 14:39:33.0473 4444 TDPIPE - ok 14:39:33.0534 4444 [ 389C63E32B3CEFED425B61ED92D3F021 ] TDTCP C:\Windows\system32\drivers\tdtcp.sys 14:39:33.0580 4444 TDTCP - ok 14:39:33.0667 4444 [ 76B06EB8A01FC8624D699E7045303E54 ] tdx C:\Windows\system32\DRIVERS\tdx.sys 14:39:33.0724 4444 tdx - ok 14:39:33.0835 4444 [ 3CAD38910468EAB9A6479E2F01DB43C7 ] TermDD C:\Windows\system32\DRIVERS\termdd.sys 14:39:33.0845 4444 TermDD - ok 14:39:34.0029 4444 [ BB95DA09BEF6E7A131BFF3BA5032090D ] TermService C:\Windows\System32\termsrv.dll 14:39:34.0035 4444 TermService - ok 14:39:34.0099 4444 [ C7230FBEE14437716701C15BE02C27B8 ] Themes C:\Windows\system32\shsvcs.dll 14:39:34.0102 4444 Themes - ok 14:39:34.0157 4444 [ 1076FFCFFAAE8385FD62DFCB25AC4708 ] THREADORDER C:\Windows\system32\mmcss.dll 14:39:34.0159 4444 THREADORDER - ok 14:39:34.0307 4444 [ EC74E77D0EB004BD3A809B5F8FB8C2CE ] TrkWks C:\Windows\System32\trkwks.dll 14:39:34.0311 4444 TrkWks - ok 14:39:34.0482 4444 [ 97D9D6A04E3AD9B6C626B9931DB78DBA ] TrustedInstaller C:\Windows\servicing\TrustedInstaller.exe 14:39:34.0506 4444 TrustedInstaller - ok 14:39:34.0546 4444 [ DCF0F056A2E4F52287264F5AB29CF206 ] tssecsrv C:\Windows\system32\DRIVERS\tssecsrv.sys 14:39:34.0566 4444 tssecsrv - ok 14:39:34.0636 4444 [ CAECC0120AC49E3D2F758B9169872D38 ] tunmp C:\Windows\system32\DRIVERS\tunmp.sys 14:39:34.0661 4444 tunmp - ok 14:39:34.0756 4444 [ 300DB877AC094FEAB0BE7688C3454A9C ] tunnel C:\Windows\system32\DRIVERS\tunnel.sys 14:39:34.0765 4444 tunnel - ok 14:39:34.0833 4444 [ 7D33C4DB2CE363C8518D2DFCF533941F ] uagp35 C:\Windows\system32\drivers\uagp35.sys 14:39:34.0835 4444 uagp35 - ok 14:39:34.0897 4444 [ D9728AF68C4C7693CB100B8441CBDEC6 ] udfs C:\Windows\system32\DRIVERS\udfs.sys 14:39:34.0903 4444 udfs - ok 14:39:35.0007 4444 [ ECEF404F62863755951E09C802C94AD5 ] UI0Detect C:\Windows\system32\UI0Detect.exe 14:39:35.0022 4444 UI0Detect - ok 14:39:35.0088 4444 [ B0ACFDC9E4AF279E9116C03E014B2B27 ] uliagpkx C:\Windows\system32\drivers\uliagpkx.sys 14:39:35.0094 4444 uliagpkx - ok 14:39:35.0134 4444 [ 9224BB254F591DE4CA8D572A5F0D635C ] uliahci C:\Windows\system32\drivers\uliahci.sys 14:39:35.0139 4444 uliahci - ok 14:39:35.0192 4444 [ 8514D0E5CD0534467C5FC61BE94A569F ] UlSata C:\Windows\system32\drivers\ulsata.sys 14:39:35.0203 4444 UlSata - ok 14:39:35.0256 4444 [ 38C3C6E62B157A6BC46594FADA45C62B ] ulsata2 C:\Windows\system32\drivers\ulsata2.sys 14:39:35.0294 4444 ulsata2 - ok 14:39:35.0338 4444 [ 32CFF9F809AE9AED85464492BF3E32D2 ] umbus C:\Windows\system32\DRIVERS\umbus.sys 14:39:35.0340 4444 umbus - ok 14:39:35.0448 4444 [ 68308183F4AE0BE7BF8ECD07CB297999 ] upnphost C:\Windows\System32\upnphost.dll 14:39:35.0455 4444 upnphost - ok 14:39:35.0586 4444 [ 79A58D49E042E80F1909D8ED0A3C47A8 ] usbccgp C:\Windows\system32\DRIVERS\usbccgp.sys 14:39:35.0590 4444 usbccgp - ok 14:39:35.0672 4444 [ E9476E6C486E76BC4898074768FB7131 ] usbcir C:\Windows\system32\drivers\usbcir.sys 14:39:35.0724 4444 usbcir - ok 14:39:35.0860 4444 [ 79E96C23A97CE7B8F14D310DA2DB0C9B ] usbehci C:\Windows\system32\DRIVERS\usbehci.sys 14:39:35.0878 4444 usbehci - ok 14:39:35.0961 4444 [ 4673BBCB006AF60E7ABDDBE7A130BA42 ] usbhub C:\Windows\system32\DRIVERS\usbhub.sys 14:39:35.0971 4444 usbhub - ok 14:39:36.0101 4444 [ 38DBC7DD6CC5A72011F187425384388B ] usbohci C:\Windows\system32\drivers\usbohci.sys 14:39:36.0110 4444 usbohci - ok 14:39:36.0173 4444 [ E75C4B5269091D15A2E7DC0B6D35F2F5 ] usbprint C:\Windows\system32\DRIVERS\usbprint.sys 14:39:36.0196 4444 usbprint - ok 14:39:36.0285 4444 [ A508C9BD8724980512136B039BBA65E9 ] usbscan C:\Windows\system32\DRIVERS\usbscan.sys 14:39:36.0293 4444 usbscan - ok 14:39:36.0396 4444 [ BE3DA31C191BC222D9AD503C5224F2AD ] USBSTOR C:\Windows\system32\DRIVERS\USBSTOR.SYS 14:39:36.0417 4444 USBSTOR - ok 14:39:36.0486 4444 [ 814D653EFC4D48BE3B04A307ECEFF56F ] usbuhci C:\Windows\system32\DRIVERS\usbuhci.sys 14:39:36.0491 4444 usbuhci - ok 14:39:36.0540 4444 [ 1509E705F3AC1D474C92454A5C2DD81F ] UxSms C:\Windows\System32\uxsms.dll 14:39:36.0543 4444 UxSms - ok 14:39:36.0671 4444 [ CD88D1B7776DC17A119049742EC07EB4 ] vds C:\Windows\System32\vds.exe 14:39:36.0723 4444 vds - ok 14:39:36.0800 4444 [ 87B06E1F30B749A114F74622D013F8D4 ] vga C:\Windows\system32\DRIVERS\vgapnp.sys 14:39:36.0802 4444 vga - ok 14:39:36.0860 4444 [ 2E93AC0A1D8C79D019DB6C51F036636C ] VgaSave C:\Windows\System32\drivers\vga.sys 14:39:36.0861 4444 VgaSave - ok 14:39:36.0896 4444 [ 5D7159DEF58A800D5781BA3A879627BC ] viaagp C:\Windows\system32\drivers\viaagp.sys 14:39:36.0912 4444 viaagp - ok 14:39:36.0968 4444 [ C4F3A691B5BAD343E6249BD8C2D45DEE ] ViaC7 C:\Windows\system32\drivers\viac7.sys 14:39:36.0988 4444 ViaC7 - ok 14:39:37.0035 4444 [ AADF5587A4063F52C2C3FED7887426FC ] viaide C:\Windows\system32\drivers\viaide.sys 14:39:37.0056 4444 viaide - ok 14:39:37.0093 4444 [ 69503668AC66C77C6CD7AF86FBDF8C43 ] volmgr C:\Windows\system32\drivers\volmgr.sys 14:39:37.0111 4444 volmgr - ok 14:39:37.0275 4444 [ 23E41B834759917BFD6B9A0D625D0C28 ] volmgrx C:\Windows\system32\drivers\volmgrx.sys 14:39:37.0300 4444 volmgrx - ok 14:39:37.0483 4444 [ 147281C01FCB1DF9252DE2A10D5E7093 ] volsnap C:\Windows\system32\drivers\volsnap.sys 14:39:37.0562 4444 volsnap - ok 14:39:37.0948 4444 [ E4D2305EBB9DE0871A1E13294D0F349B ] vpnagent C:\Program Files\Cisco\Cisco AnyConnect VPN Client\vpnagent.exe 14:39:38.0597 4444 vpnagent - ok 14:39:38.0648 4444 [ E1F2333A88EC4A5C8EA6BE357323B72D ] vpnva C:\Windows\system32\DRIVERS\vpnva.sys 14:39:38.0686 4444 vpnva - ok 14:39:38.0742 4444 [ 587253E09325E6BF226B299774B728A9 ] vsmraid C:\Windows\system32\drivers\vsmraid.sys 14:39:38.0808 4444 vsmraid - ok 14:39:38.0978 4444 [ DB3D19F850C6EB32BDCB9BC0836ACDDB ] VSS C:\Windows\system32\vssvc.exe 14:39:39.0031 4444 VSS - ok 14:39:39.0214 4444 [ 96EA68B9EB310A69C25EBB0282B2B9DE ] W32Time C:\Windows\system32\w32time.dll 14:39:39.0219 4444 W32Time - ok 14:39:39.0310 4444 [ 48DFEE8F1AF7C8235D4E626F0C4FE031 ] WacomPen C:\Windows\system32\drivers\wacompen.sys 14:39:39.0312 4444 WacomPen - ok 14:39:39.0379 4444 [ 55201897378CCA7AF8B5EFD874374A26 ] Wanarp C:\Windows\system32\DRIVERS\wanarp.sys 14:39:39.0427 4444 Wanarp - ok 14:39:39.0515 4444 [ 55201897378CCA7AF8B5EFD874374A26 ] Wanarpv6 C:\Windows\system32\DRIVERS\wanarp.sys 14:39:39.0517 4444 Wanarpv6 - ok 14:39:40.0114 4444 [ A3CD60FD826381B49F03832590E069AF ] wcncsvc C:\Windows\System32\wcncsvc.dll 14:39:40.0268 4444 wcncsvc - ok 14:39:40.0353 4444 [ 11BCB7AFCDD7AADACB5746F544D3A9C7 ] WcsPlugInService C:\Windows\System32\WcsPlugInService.dll 14:39:40.0362 4444 WcsPlugInService - ok 14:39:40.0450 4444 [ 78FE9542363F297B18C027B2D7E7C07F ] Wd C:\Windows\system32\drivers\wd.sys 14:39:40.0560 4444 Wd - ok 14:39:40.0734 4444 [ B6F0A7AD6D4BD325FBCD8BAC96CD8D96 ] Wdf01000 C:\Windows\system32\drivers\Wdf01000.sys 14:39:40.0793 4444 Wdf01000 - ok 14:39:40.0871 4444 [ ABFC76B48BB6C96E3338D8943C5D93B5 ] WdiServiceHost C:\Windows\system32\wdi.dll 14:39:40.0877 4444 WdiServiceHost - ok 14:39:40.0909 4444 [ ABFC76B48BB6C96E3338D8943C5D93B5 ] WdiSystemHost C:\Windows\system32\wdi.dll 14:39:40.0913 4444 WdiSystemHost - ok 14:39:40.0970 4444 [ 04C37D8107320312FBAE09926103D5E2 ] WebClient C:\Windows\System32\webclnt.dll 14:39:40.0976 4444 WebClient - ok 14:39:41.0066 4444 [ AE3736E7E8892241C23E4EBBB7453B60 ] Wecsvc C:\Windows\system32\wecsvc.dll 14:39:41.0080 4444 Wecsvc - ok 14:39:41.0133 4444 [ 670FF720071ED741206D69BD995EA453 ] wercplsupport C:\Windows\System32\wercplsupport.dll 14:39:41.0137 4444 wercplsupport - ok 14:39:41.0215 4444 [ 32B88481D3B326DA6DEB07B1D03481E7 ] WerSvc C:\Windows\System32\WerSvc.dll 14:39:41.0222 4444 WerSvc - ok 14:39:41.0285 4444 [ 72CC6A8CA7891031D6380DB5025C773C ] winachsf C:\Windows\system32\DRIVERS\HSX_CNXT.sys 14:39:41.0327 4444 winachsf - ok 14:39:41.0673 4444 [ 4575AA12561C5648483403541D0D7F2B ] WinDefend C:\Program Files\Windows Defender\mpsvc.dll 14:39:41.0680 4444 WinDefend - ok 14:39:41.0702 4444 WinHttpAutoProxySvc - ok 14:39:41.0790 4444 [ 6B2A1D0E80110E3D04E6863C6E62FD8A ] Winmgmt C:\Windows\system32\wbem\WMIsvc.dll 14:39:41.0794 4444 Winmgmt - ok 14:39:41.0918 4444 [ 7CFE68BDC065E55AA5E8421607037511 ] WinRM C:\Windows\system32\WsmSvc.dll 14:39:41.0969 4444 WinRM - ok 14:39:42.0063 4444 [ C008405E4FEEB069E30DA1D823910234 ] Wlansvc C:\Windows\System32\wlansvc.dll 14:39:42.0131 4444 Wlansvc - ok 14:39:42.0166 4444 [ 2E7255D172DF0B8283CDFB7B433B864E ] WmiAcpi C:\Windows\system32\drivers\wmiacpi.sys 14:39:42.0168 4444 WmiAcpi - ok 14:39:42.0264 4444 [ 43BE3875207DCB62A85C8C49970B66CC ] wmiApSrv C:\Windows\system32\wbem\WmiApSrv.exe 14:39:42.0267 4444 wmiApSrv - ok 14:39:42.0539 4444 [ 3978704576A121A9204F8CC49A301A9B ] WMPNetworkSvc C:\Program Files\Windows Media Player\wmpnetwk.exe 14:39:43.0096 4444 WMPNetworkSvc - ok 14:39:43.0201 4444 [ CFC5A04558F5070CEE3E3A7809F3FF52 ] WPCSvc C:\Windows\System32\wpcsvc.dll 14:39:43.0211 4444 WPCSvc - ok 14:39:43.0426 4444 [ 801FBDB89D472B3C467EB112A0FC9246 ] WPDBusEnum C:\Windows\system32\wpdbusenum.dll 14:39:43.0474 4444 WPDBusEnum - ok 14:39:43.0889 4444 [ DE9D36F91A4DF3D911626643DEBF11EA ] WpdUsb C:\Windows\system32\DRIVERS\wpdusb.sys 14:39:43.0916 4444 WpdUsb - ok 14:39:44.0674 4444 [ DCF3E3EDF5109EE8BC02FE6E1F045795 ] WPFFontCache_v0400 C:\Windows\Microsoft.NET\Framework\v4.0.30319\WPF\WPFFontCache_v0400.exe 14:39:44.0797 4444 WPFFontCache_v0400 - ok 14:39:44.0898 4444 [ E3A3CB253C0EC2494D4A61F5E43A389C ] ws2ifsl C:\Windows\system32\drivers\ws2ifsl.sys 14:39:44.0899 4444 ws2ifsl - ok 14:39:44.0963 4444 [ 1CA6C40261DDC0425987980D0CD2AAAB ] wscsvc C:\Windows\System32\wscsvc.dll 14:39:44.0986 4444 wscsvc - ok 14:39:44.0998 4444 WSearch - ok 14:39:45.0421 4444 [ FC3EC24FCE372C89423E015A2AC1A31E ] wuauserv C:\Windows\system32\wuaueng.dll 14:39:45.0629 4444 wuauserv - ok 14:39:45.0722 4444 [ AC13CB789D93412106B0FB6C7EB2BCB6 ] WUDFRd C:\Windows\system32\DRIVERS\WUDFRd.sys 14:39:45.0722 4444 WUDFRd - ok 14:39:45.0832 4444 [ 575A4190D989F64732119E4114045A4F ] wudfsvc C:\Windows\System32\WUDFSvc.dll 14:39:46.0019 4444 wudfsvc - ok 14:39:46.0050 4444 [ DAB33CFA9DD24251AAA389FF36B64D4B ] XAudio C:\Windows\system32\DRIVERS\xaudio.sys 14:39:46.0097 4444 XAudio - ok 14:39:46.0144 4444 [ CD5F291A1161F15896D1A4D63DAFF5DF ] XAudioService C:\Windows\system32\DRIVERS\xaudio.exe 14:39:46.0159 4444 XAudioService - ok 14:39:46.0253 4444 ================ Scan global =============================== 14:39:46.0331 4444 [ F31EEBC1A1C81FD04005489CC3DCDFE7 ] C:\Windows\system32\basesrv.dll 14:39:46.0471 4444 [ D2293B069E4B63DC17B2F08D45E71124 ] C:\Windows\system32\winsrv.dll 14:39:46.0534 4444 [ D2293B069E4B63DC17B2F08D45E71124 ] C:\Windows\system32\winsrv.dll 14:39:46.0643 4444 [ D4E6D91C1349B7BFB3599A6ADA56851B ] C:\Windows\system32\services.exe 14:39:46.0643 4444 [Global] - ok 14:39:46.0674 4444 ================ Scan MBR ================================== 14:39:46.0690 4444 [ 5C616939100B85E558DA92B899A0FC36 ] \Device\Harddisk0\DR0 14:39:46.0690 4444 Suspicious mbr (Forged): \Device\Harddisk0\DR0 14:39:46.0736 4444 \Device\Harddisk0\DR0 ( Rootkit.Boot.Pihar.c ) - infected 14:39:46.0736 4444 \Device\Harddisk0\DR0 - detected Rootkit.Boot.Pihar.c (0) 14:39:46.0752 4444 ================ Scan VBR ================================== 14:39:46.0768 4444 [ 9F47412F6E0E1216FA5061569FC67F0E ] \Device\Harddisk0\DR0\Partition1 14:39:46.0768 4444 \Device\Harddisk0\DR0\Partition1 - ok 14:39:46.0799 4444 [ A4EA1A073EC5EAE6BFB8F776558644B0 ] \Device\Harddisk0\DR0\Partition2 14:39:46.0799 4444 \Device\Harddisk0\DR0\Partition2 - ok 14:39:46.0830 4444 ============================================================ 14:39:46.0830 4444 Scan finished 14:39:46.0830 4444 ============================================================ 14:39:46.0846 4704 Detected object count: 1 14:39:46.0846 4704 Actual detected object count: 1 14:39:55.0285 4704 \Device\Harddisk0\DR0 ( Rootkit.Boot.Pihar.c ) - skipped by user 14:39:55.0285 4704 \Device\Harddisk0\DR0 ( Rootkit.Boot.Pihar.c ) - User select action: Skip
The reason I asked for TDSSKiller was because of the symptoms you described. It appears this infection may have modified the master boot record (MBR) which is more complicated than a typical infection fix and you will not be able to do all of this remotely. In the next steps, we will be gathering the diagnostic information necessary to identify and fix the infection. No changes are going to be made to the system during these steps, but hopefully, it will let me see the hidden partition where the infection is booting the system from so we can identify it and get the steps ready to nuke it!


If you don't already have a system repair disc for this computer, I would recommend creating one. If you can't create it from the infected computer then you will need to do it from a clean Vista computer. You can create this System Repair Disc in Windows Vista:
Click Start > All Programs > Maintenance > Create a System Repair Disc.


Download Farbar Recovery Scan Tool and save it to a flash drive.

Plug the flashdrive into the infected PC.

Restart your computer and tap F8 to bring up the Advanced Menu, then click Repair your computer

Follow the prompt to enter keyboard input method, and then the prompt to enter a password. If the machine does not have a password, simply click Enter.

In the next menu, use the arrow keys on the keyboard to highlight Command Prompt and press Enter.
  • In the command window type in notepad and press Enter.
  • The notepad opens. Under File menu select Open.
  • Select "Computer" and find your flash drive letter and close the notepad.
  • In the command window type e:\frst.exe and press Enter.
Note: Replace letter e with the drive letter of your flash drive.
  • The tool will start to run.
  • When the tool opens click Yes to disclaimer.
  • Uncheck the Whitlelist boxes next to Registry, Services, Drivers, and known DLL's
  • Place a check next to List Drivers MD5
  • Press Scan button.
  • It will make a log (FRST.txt) on the flash drive. Please copy and paste it to your reply.


1. Preferably from a clean computer, please download the following: gparted-live-0.10.0-3.iso (115 MB)

When you have the .ISO file downloaded, you need to create a bootable disk or flash drive with it, using a clean PC to do that. The .ISO file is a disk image. It should NOT be burned as a regular file. You need a program like BurnAware Free or ImgBurn that can burn an .ISO image. I think a CD is best as there is no way anything can write on it after it is made, but the USB may be more convenient and easier.


2. Now, please boot off of the newly created GParted CD. See How to Set BIOS to Boot from CDROM for information on how to boot from the CD.

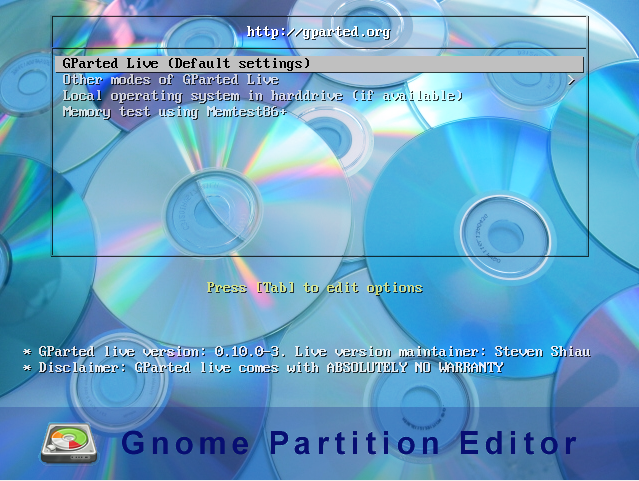
You should arrive to the following screen:
[external image: Posted Image]
Press the ENTER key

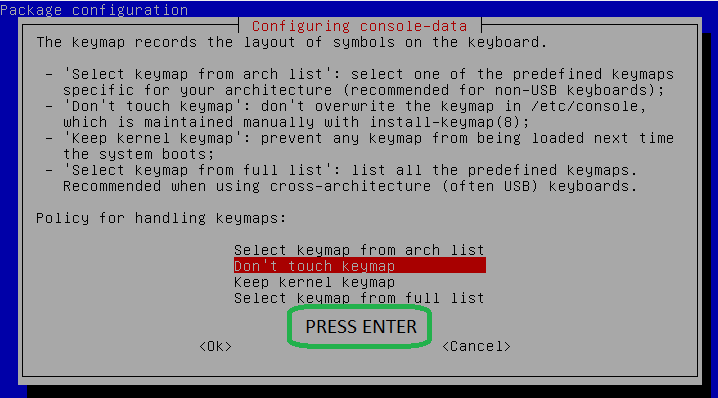
[external image: Posted Image]
By default, "do not touch keymap" is highlighted. Leave this setting alone and press the ENTER key.

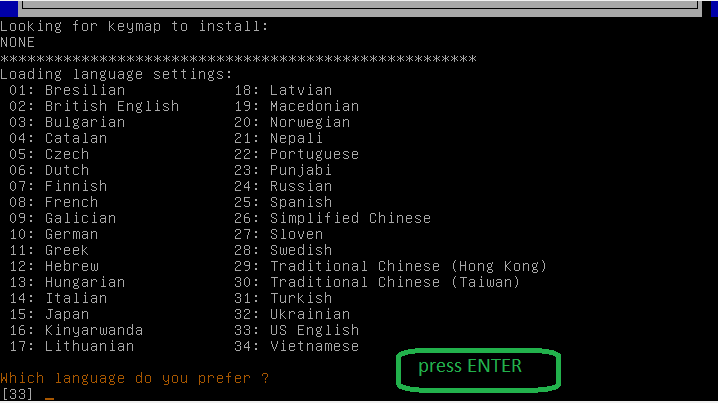
[external image: Posted Image]
Next, choose your language and press the ENTER key. English is the default setting [33]

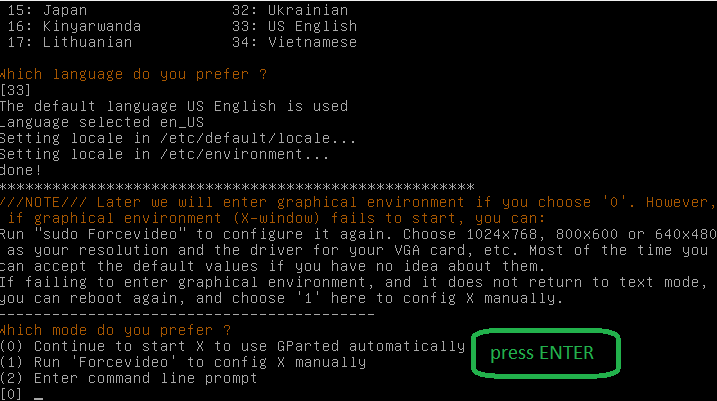
[external image: Posted Image]
Once again, at this prompt, press the ENTER key.

You will now be taken to the main GUI screen below
[external image: Posted Image]

Please take a picture of this screen (camera or phone pictures will work just fine), and post it here for me to see. It is very important that you complete this step.
Thank you for your patience. Finding a Vista recovery disk was not easy. The machine is also 20 miles away. My phone is old and I cannot get it to talk to my PC, and I'm too old fashioned to have email on it so I was not able to copy a photo of the screen. I wrote down all the elements of the window knowing getting the photo would be difficult, so I laid them out as they appeared on the screen. If this is not sufficient let me know and I'll have to borrow a digital camera somewhere. I'm attaching the FRST.txt and mock up of the partition window from GParted.
Well, I have good news! I had thought you might have a pretty nasty infection that is particulary difficult to clear up. But those files you just gave me would seem to indicate it is not the case. So remote clean up looks a lot more likely now :)

Given that you are having trouble running tools on this machine, you may need to reboot it and run RKill again, but it would be preferable to try running the next steps directly if possible.


Download and Install Combofix

Download ComboFix from one of the following locations:
Link 1
Link 2

VERY IMPORTANT !!! Save ComboFix.exe to your Desktop

* IMPORTANT - Disable your AntiVirus and AntiSpyware applications, usually via a right click on the System Tray icon. They may otherwise interfere with our tools. If you have difficulty properly disabling your protective programs, refer to this link here
  • Double click on ComboFix.exe & follow the prompts.

When finished, it shall produce a log for you. Please include the C:\ComboFix.txt in your next reply.
Notes:
1. 1. Do not mouse-click anywhere on the screen while it is running. That may cause it to stall. In fact, I suggest you do not do anything else on the computer while Combofix is running as it can cause it to stall. It may appear at times that it isn't doing anything but it is. Just let it run. It may also reboot the machine as a part of what it is doing and that is not unusual. (If your computer requires a login then you WILL need to fill in the login/password for it to continue. If your computer does not have a login then it will continue on it's own..) Then, just sit tight until it finishes. Sometimes it takes 10 minutes, sometimes it takes an hour. Just be patient until the log pops up. If it takes more than an hour and doesn't appear to be doing anything, you can stop it and come back and let me know.
2. Do not "re-run" Combofix. If you have a problem, reply back for further instructions.

Please make sure you include the combo fix log in your next reply as well as describe how your computer is running now

If you have a problem launching programs after running Combofix, please do not panic! Simply reboot the computer and all should be fine.
I restarted the computer and ran rkill. It stopped MDM and complained that windows defender was disabled. I ran ComboFix from the desktop. It appeared to finish successfully. Log attached. I restarted the computer again (a lot of the sys tray icons had disappeared after ComboFix). I did a Google search and the Google redirect appears to be gone, it went where it was supposed to. Windows Update had a notification that critical updates were available, so I went ahead and let that run. It restarted the computer to finish installation. After the third restart, the CPU activity stayed at 100% for quite a while, but later dropped to normal. I ran Rkill one more time expecting it to come up clean, but it still stopped this MDM process and complained that windows defender is disabled. The number of entries in the hosts file was one, where it was two before. Rkill log also attached. I've done nothing else since.
RKill is not something that will remove infections, it is really only to be used when we can't get our tools to run. So you don't need to run it unless directed to do so.

One thing that you will need to understand, this is a single core machine. I'm not sure how much RAM you have, but it is quite likely that you will often max this machine's capability out. Even once we determine it appears malware free, you will likely still experience periods where it is running at it's maximum resources.

It sounds like we probably have the root of the Google redirect problem taken care of, but different tools look in different places for malware and I'd like to be sure that we make sure the machine is as clean as possible.

Please run the following WITHOUT using RKill if possible.

Please download Malwarebytes' Anti-Malware to your desktop.

  • Double-click mbam-setup.exe and follow the prompts to install the program.
  • At the end, be sure a checkmark is placed next to Update Malwarebytes' Anti-Malware and Launch Malwarebytes' Anti-Malware, then click Finish.
  • If an update is found, it will download and install the latest version.
  • Once the program has loaded, select Perform quick scan, then click Scan.
    [external image: Posted Image]
  • When the scan is complete, click OK, then Show Results to view the results.
  • Be sure that everything is checked, and click Remove Selected .
  • When completed, a log will open in Notepad. Please save it to a convenient location and post the results.
  • Note: If you receive a notice that some of the items couldn't be removed, that they have been added to the delete on reboot list, please reboot.


This scan make take awhile depending on how many items are on the computer. You may want to run it at a time you won't be needing the machine. It should be run from IE and I'd recommend not doing anything else while it's running.


Go here to run an online scannner from ESET.
  • Note: For browsers other than Internet Explorer, you will need to download and install esetsmartinstaller_enu.exe. Click on it and save the file to a convenient location. Double click on it to install and a new window will open.
  • Turn off the real time scanner of any existing antivirus program while performing the online scan
  • Tick the box next to YES, I accept the Terms of Use.
  • Click Start
  • When asked, allow the activex control to install
  • Click Start
  • Make sure that the option Remove found threats is unticked and the Scan Archives option is ticked.
  • Click on Advanced Settings, ensure the options Scan for potentially unwanted applications, Scan for potentially unsafe applications, and Enable Anti-Stealth Technology are ticked.
  • Click Scan
  • Wait for the scan to finish
  • Use notepad to open the logfile located at C:\Program Files\Eset\Eset Online Scanner\log.txt
  • Copy and paste that log as a reply to this topic and also let me know how things are now.
(Note: If there are no infections found, there will be no log to post and that is fine - just let me know)
It's a little confusing. I ran the malwarebytes (I'm not running rkill any more and they run fine) and here is the output. It found and deleted one malware file. I ran the ESET scanner and it found 4 things. But when I open the log file there is no record of them (below also). I took screenshots during and after the scan completed so you can see what it reported. I don't know if I have a virus or no virus or the virus is interfering with the logging. eset_runnning.jpg shows the names of the infections and eset_result.jpg is after it was done. Malwarebytes Anti-Malware 1.65.1.1000 www.malwarebytes.org Database version: v2012.11.17.05 Windows Vista Service Pack 2 x86 NTFS Internet Explorer 9.0.8112.16421 Cronins :: CRONINS-PC [administrator] 11/17/2012 3:37:44 PM mbam-log-2012-11-17 (15-37-44).txt Scan type: Quick scan Scan options enabled: Memory | Startup | Registry | File System | Heuristics/Extra | Heuristics/Shuriken | PUP | PUM Scan options disabled: P2P Objects scanned: 275045 Time elapsed: 11 minute(s), 34 second(s) Memory Processes Detected: 0 (No malicious items detected) Memory Modules Detected: 0 (No malicious items detected) Registry Keys Detected: 0 (No malicious items detected) Registry Values Detected: 0 (No malicious items detected) Registry Data Items Detected: 0 (No malicious items detected) Folders Detected: 0 (No malicious items detected) Files Detected: 1 C:\Users\Cronins\Favorites\_favdata.dat (Malware.Trace) -> Quarantined and deleted successfully. (end) ESETSmartInstaller@High as CAB hook log: OnlineScanner.ocx - registred OK esets_scanner_update returned -1 esets_gle=53251
Actually, I'm pretty sure those were false positives. If My Web Search were still on there, Malwarebytes would have found it I assure you. Those could have been some leftover registry entries or something that came up during the search but were not actually logged because they were not really files. If there were no entries in the logs, then I wouldn't worry about it.

The following will implement some cleanup procedures as well as reset System Restore points:
  • Click the Windows Key + R to open the Run box.
  • Now type Combofix /uninstall in the runbox and click OK. Note the space between the X and the U, it needs to be there.
  • [external image: Posted Image]

If there are any remaining tools or logs on your desktop you can right-click and delete them.


As for the fact that the CPU is still spiking to 100% sometimes, as I said, that will happen on an older machine with lesser resources. What I can do is tell you that at this point, your issues do not appear to be related to malware and I'd like to refer you to our Windows Forum for additional help. When posting there, please feel free to include a link to this post in case they need to see any information contained in the logs. They can assist you in making sure that any unnecessary start up items are disabled and help you make sure that Windows is running as lean and clean as possible to help this machine run as best as possible for the specs that it has. That is about the best you can hope for in this scenario.

================

I'd also like to give you some final tips to help keep this machine protected from malware in the future:


Great job! Your logs appear to be malware free and you do not appear to be experiencing any malware related problems.
Please follow these simple steps in order to keep your computer malware free and secure:

Use and Update your AntiVirus Software
It is very important that your computer has an anti-virus software running on your machine. This alone can save you a lot of trouble with malware in the future. It is imperitive that you update your Antivirus software at least once a week (Even more if you wish). If you do not update your antivirus software then it will not be able to catch any of the new variants that may come out.

Use a Firewall
I can not stress how important it is that you use a Firewall on your computer. Without a firewall your computer is succeptible to being hacked and taken over. I am very serious about this. Simply using a Firewall in its default configuration can lower your risk greatly.

Use only one antivirus and one firewall on your machine
Having more than one anti-virus program and one firewall on your machine, even if only one is running, can cause conflicts and slowdowns in the performance of the machine.

If you need more information on free anti-virus or firewall options please let me know and I will give you some recommendations.

Make your Internet Explorer more secure
This can be done by following these simple instructions:
1. From within Internet Explorer click on the Tools menu and then click on Options.
2. Click once on the Security tab
3. Click once on the Internet icon so it becomes highlighted.
4. Click once on the Custom Level button.
5. Change the Download signed ActiveX controls to Prompt
6. Change the Download unsigned ActiveX controls to Disable
7. Change the Initialize and script ActiveX controls not marked as safe to Disable
8. Change the Installation of desktop items to Prompt
9. Change the Launching programs and files in an IFRAME to Prompt
10. Change the Navigate sub-frames across different domains to Prompt
11. When all these settings have been made, click on the OK button.
12. If it prompts you as to whether or not you want to save the settings, press the Yes button.
13. Next press the Apply button and then the OK to exit the Internet Properties page.

Keep your Java, Adobe Reader and Adobe Flash Up to Date
Older versions of these programs can contain security vulnerabilities. It is very important to keep them updated.

Update and Run Malwarebytes Anti-Malware
Scan your computer with this program on a regular basis just as you would an antivirus software making sure you update definitions each time you scan.

To simplify making sure you have the latest version of many of your security programs and applications, you may want to consider:
Secunia's Personal Software Inspector (PSI). It is a free utility that scans your computer for installed applications and checks to see if they have the latest security patches and updates. If it finds any applications with possible security issues, links and/or instructions are provided for the necessariy updates.

Filehippo's Update Checker. It is free utilitiy that scan your computer for installed software, checks the versions and then sends this information to see if there are any newer releases. Available software updates are displayed and you can decide which ones to download and install. Among many other types of programs, they includes a number of the Anti-Spyware, Firewall/Security and Anti-Virus programs that have been recommended (though not all of them). Note: Definition files should be updated from within the programs themselves. The Update Checker look for newer versions of the software program, not definition files.

I would suggest you read:
Tony Klein's excellent article: How I got Infected in the First Place
PC Safety and Securityโ€“What Do I Need?
How to Prevent Malware

Good luck & Happy surfing!

Thank you Thank you Thank you! I only have one final response. Not to say I have any expert opinion, but McAfee *was* running and up to date when this happened. I have Norton on my machine and it occasionally reports having stopped an invasion, and nothing has made it through. It's possible the other user accidentally gave something permission but McAfee should have had bells and whistles going off. I have 2 additional installs left on my Norton subscription so I'm replacing McAfee with Norton on the other machine.
While it is possible the user allowed something, the reality of malware today is that sometimes simply going to site that is infected can also infect your computer. It is not necessary for the user to "do" anything anymore to get infected.

As to McAfee vs. Nortonโ€ฆthey are both highly reputable antivirus and firewall products. Norton can be very difficult for the average user to remove and often requires the use of a third party program to fully remove if it needs to be uninstalled for any reason.

But on this computer I would not personally recommend either. Both are very resource intensive. I would actually recommend MSE - Microsoft Security Essentials (which is free) and is very light on resources. It works in conjunction with Windows Firewall to protect the computer. I have used all three of these solutions, and in my experience, McAfee and Norton both get very resource intensive when they scan. Microsoft Security Essentials does not. There are several free good antivirus solutions available but MSE tends to be the lightest on resources and is actually what I use on my own personal computers.

This is not to say that any one is better than the other, just that with the specifications of this machine it will be very intensive on the machine. But one thing to consider - and you know this better than I do - is the user. If you have a user who will click anything and allow anything, then perhaps intensive or not - one of the more limiting protection suites (with more bells and whistles) like Norton is a better choice even if it slows the machine down a little. If it will deter the user from making errors that allow malware through, then that is far better than some of the infections that are out there today. You will have to weigh what you know about the user against the specs and capability of the machine and make a judgement call on this one.

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI