Hi,
Nortons Antivirus is continually finding the virus:
Virus Name: Backdoor.Tidserv!kmem
Action by Norton: Left Alone
Filename: ntos
Original Location - c:\windows\system32.
I have searched the hard drive and not found the file, but Nortons alerts me of the virus on every re-boot.
I have run OTL and attached the generated files.
Other weird issues are both Internet Explorer and Firefox often do not start up - the Process tab under Windows Task Manager shows the process (often multiple instances) but a window doesn't appear.
Thank you
Phil
Hi and Welcome!! My name isJeff. I would be more than happy to take a look at your malware results logs and help you with solving any malware problems you might have. Logs can take a while to research, so please be patient and know that I am working hard to get you a clean and functional system back in your hands. I'd be grateful if you would note the following:
I will be working on your Malware issues, this may or may not, solve other issues you have with your machine.
The fixes are specific to your problem and should only be used for the issues on this machine.
Please continue to review my answers until I tell you your machine appears to be clear. Absence of symptoms does not mean that everything is clear.
It's often worth reading through these instructions and printing them for ease of reference.
If you don't know or understand something, please don't hesitate to say or ask!! It's better to be sure and safe than sorry.
Please reply to this thread. Do not start a new topic.
IMPORTANT NOTE : Please do not delete anything unless instructed to. DO NOT use any TOOLS such as Combofix or HijackThis fixes without supervision.
Doing so could make your system inoperable and could require a full reinstall of your OS losing all your programs and data.
Vista and Windows 7 users: These tools MUST be run from the executable (.exe) every time you run them
with Admin Rights (Right click, choose "Run as Administrator")
Stay with this topic until I give you the all clean post.
———
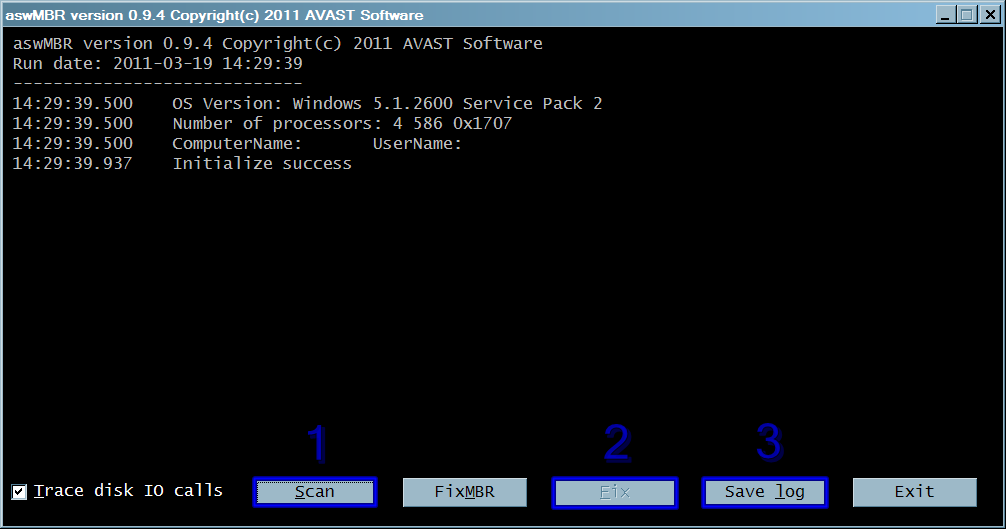
Please download aswMBR to your desktop.
Double click the aswMBR icon to run it.
Click the Scan button to start scan.
If you are asked to update the Avast Virus database please allow it to do so.
When it finishes, press the save log button, save the logfile to your desktop and attach its contents in your next reply.
Please double click the aswMBR icon to run it. Vista and Windows 7 users right click the icon and choose "Run as administrator".
Click the Scan button to start scan.
When scan finishes, press the Fix Button. Once the Fix is done, press the Save Log button and save the log to your desktop. You need to reboot your computer when its done before you do anything else, then post the log that will be on your desktop.
Hi,
Great! Please go ahead and run a new scan with aswMBR and post the newly made log.
Stick with me as we have some more work to do. That was just the main infection we have hopefully removed.
Please download and run ERUNT (Emergency Recovery Utility NT). This program allows you to keep a complete backup of your registry and restore it when needed. The standard registry backup options that come with Windows back up most of the registry but not all of it. ERUNT however creates a complete backup set, including the Security hive and user related sections. ERUNT is easy to use and since it creates a full backup, there are no options or choices other than to select the location of the backup files. The backup set includes a small executable that will launch the registry restore if needed. **Remember if you are using Windows Vista as your operating system right-click the executable and Run as Administrator.
———-
Run OTL.exe
Copy/paste the following text written inside of the quote box into the Custom Scans/Fixes box located at the bottom of OTL
I see that your Java software is out of date. Please go to Start >> Control Panel >> Programs and Features >> uninstall all versions of Java.
Now download and install the newest version from here >> http://java.com/en/download/index.jsp
————-
Clear Java Cache
See this page for instructions on how to clear java's cache.
Go into the Control Panel and double-click the Java Icon. (looks like a coffee cup)
Under Temporary Internet Files, click the Delete Files button.
There are three options in the window to clear the cache - Leave ALL 3 Checked
Downloaded Applets
Downloaded Applications
Other Files
Click OK on Delete Temporary Files Window Note: This deletes ALL the Downloaded Applications and Applets from the CACHE.
Click OK to leave the Java Control Panel.
———-
Please download Malwarebytes Anti-Malware to your desktop.
Right-click and Run as Administrator mbam-setup.exe and follow the prompts to install the program.
At the end, be sure a checkmark is placed next to Update Malwarebytes Anti-Malware and Launch Malwarebytes Anti-Malware, then click Finish.
If an update is found, it will download and install the latest version.
Once the program has loaded, select Perform quick scan, then click Scan as shown below.
[external image: Posted Image]
When the scan is complete, click OK, then Show Results to view the results.
Be sure that everything is checked, and click Remove Selected.
When completed, a log will open in Notepad. Please save it to a convenient location and post the results.
The log can also be found here:
Windows 2000 & Windows XP:
C:\Documents and Settings\\Application Data\Malwarebytes\Malwarebytes' Anti-Malware\Logs
Windows Vista & Win7:
C:\Users\\AppData\Roaming\Malwarebytes\Malwarebytes' Anti-Malware\Logs
———-
ESET Online Scanner
Go here to run an online scannner from ESET. Windows Vista/Windows 7 users will need to right click on their Internet Explorer shortcut, and select Run as Administrator
Note:For browsers other than Internet Explorer, you will be prompted to download and install esetsmartinstaller_enu.exe. Click on the link and save the file to a convenient location. Double click on it to install and a new window will open. Follow the prompts.
Turn off the real time scanner of any existing antivirus program while performing the online scan
Tick the box next to YES, I accept the Terms of Use.
Click Start
When asked, allow the activex control to install
Click Start
Make sure that the option Remove found threats is unticked and the Scan Archives option is ticked.
Click on Advanced Settings, ensure the options Scan for potentially unwanted applications, Scan for potentially unsafe applications, and Enable Anti-Stealth Technology are ticked.
Click Scan
Wait for the scan to finish
When the scan is done, if it shows a screen that says "Threats found!", then click "List of found threats", and then click "Export to text file…"
Save that text file on your desktop. Copy and paste the contents of that log as a reply to this topic.
Close the ESET online scan, and let me know how things are now.
Copy/paste the following text written inside of the quote box into the Custom Scans/Fixes box located at the bottom of OTL
:Services
:Files
C:\Documents and Settings\Phil\Application Data\Mozilla\Firefox\Profiles\lr8lp7pc.default\user.js
C:\Documents and Settings\Phil\My Documents\Downloads\Adaware_Installer.exe
C:\Documents and Settings\phil.AUSTINE.000\My Documents\Downloads\winamp5581_full_emusic-7plus_en-us.exe
C:\Software\utilities\iso\Magic ISO Maker v5.3+keygen\keygen.exe
ipconfig /flushdns /c

 My name is