This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

"Recommended for You" annoying popup [Closed]

15 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

I am afraid this could be malware. Malwarebytes scan comes up empty but this thing still comes up, whether in IE or Firefox. Computer runs a bit slow as a result. ETA: Also getting random browser redirects to various fake-looking search engines. Any help appreciated
Hi and Welcome!! :) My name is Jeff. I would be more than happy to take a look at your malware results logs and help you with solving any malware problems you might have. Logs can take a while to research, so please be patient and know that I am working hard to get you a clean and functional system back in your hands. I'd be grateful if you would note the following:
  • I will be working on your Malware issues, this may or may not, solve other issues you have with your machine.
  • Please subscribe to this topic, if you haven't already. You can subscribe by clicking the Watch Topic button to the right of your topic title and then choosing the notification method ( Recommended: Inmediate Notification)
  • The fixes are specific to your problem and should only be used for the issues on this machine.
  • Please continue to review my answers until I tell you your machine appears to be clear. Absence of symptoms does not mean that everything is clear.
  • It's often worth reading through these instructions and printing them for ease of reference.
  • If you don't know or understand something, please don't hesitate to say or ask!! It's better to be sure and safe than sorry.
  • Please reply to this thread. Do not start a new topic.

IMPORTANT NOTE : Please do not delete anything unless instructed to.
DO NOT use any TOOLS such as Combofix or HijackThis fixes without supervision.
Doing so could make your system inoperable and could require a full reinstall of your OS losing all your programs and data.


Vista and Windows 7 users:
These tools MUST be run from the executable (.exe) every time you run them
with Admin Rights (Right click, choose "Run as Administrator")


Stay with this topic until I give you the all clean post.
———-

Please download DDS from one of the following links and save it to your desktop.
    • DDS.scr
    • DDS.pif
  • Disable any script blocking protection (How to Disable your Security Programs)
  • Double click DDS icon to run the tool (may take up to 3 minutes to run)
  • When done, DDS.txt will open.
  • After a few moments, attach.txt will open in a second window.
  • Save both reports to your desktop.
—————————————————
  • Post the contents of the DDS.txt report in your next reply
  • Attach the Attach.txt report to your post by scroling down to the Attachments area and then clicking Browse. Browse to where you saved the file, and click Open and then click UPLOAD.
———-

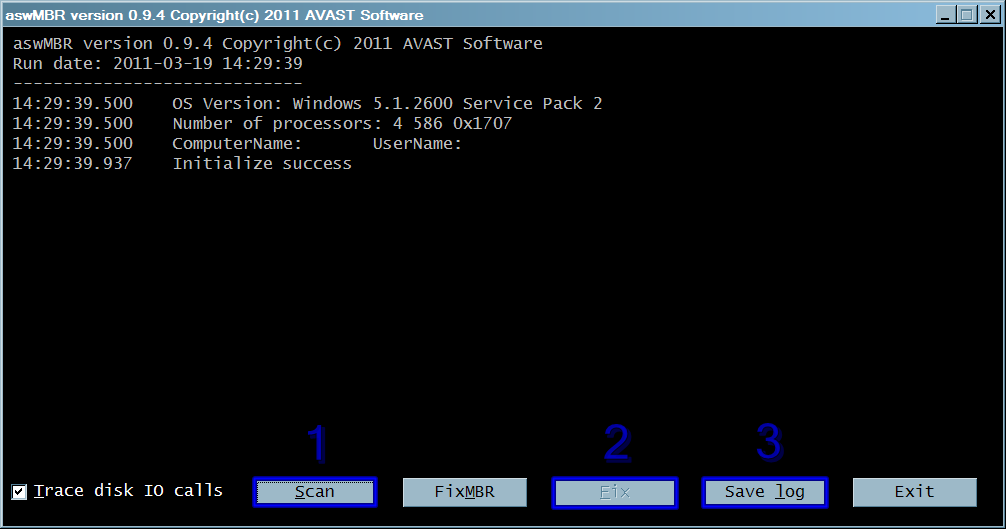
Please download aswMBR to your desktop.

  • Double click the aswMBR icon to run it.
    Vista and Windows 7 users right click the icon and choose "Run as administrator".
  • Click the Scan button to start scan.
  • When it finishes, press the save log button, save the logfile to your desktop and post its contents in your next reply.

[external image: Posted Image]
Click the image to enlarge it
———-

In your next reply please post both of the logs created by DDS and the log created by aswMBR.exe. :)
Thanks in advance for your help! DDS.txt: . DDS (Ver_2011-08-26.01) - NTFSAMD64 Internet Explorer: 9.0.8112.16421 BrowserJavaVersion: 1.6.0_31 Run by [removed] at 11:11:59 on 2012-05-10 Microsoft® Windows Vista™ Home Premium 6.0.6002.2.1252.44.1033.18.3900.1426 [GMT -4:00] . SP: Windows Defender *Enabled/Updated* {D68DDC3A-831F-4fae-9E44-DA132C1ACF46} . ============== Running Processes =============== . C:\Windows\system32\wininit.exe C:\Windows\system32\lsm.exe C:\Windows\system32\svchost.exe -k DcomLaunch C:\Windows\system32\svchost.exe -k rpcss C:\Windows\System32\svchost.exe -k LocalServiceNetworkRestricted C:\Windows\System32\svchost.exe -k LocalSystemNetworkRestricted C:\Windows\system32\svchost.exe -k netsvcs C:\Windows\system32\svchost.exe -k GPSvcGroup C:\Windows\system32\SLsvc.exe C:\Windows\system32\svchost.exe -k LocalService C:\Windows\RtkAudioService.exe C:\Windows\system32\svchost.exe -k NetworkService C:\Program Files (x86)\Lavasoft\Ad-Aware\AAWService.exe C:\Windows\System32\spoolsv.exe C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe C:\Program Files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe C:\Windows\SysWOW64\atashost.exe C:\Program Files\Bonjour\mDNSResponder.exe C:\Windows\system32\svchost.exe -k bthsvcs C:\Program Files\WIDCOMM\Bluetooth Software\bin\btwdins.exe C:\Windows\System32\svchost.exe -k LocalServiceNoNetwork C:\Windows\twain_32\fjscan32\FJTWMKSV.exe C:\Windows\SysWOW64\svchost.exe -k hpdevmgmt C:\Program Files (x86)\Common Files\InterVideo\RegMgr\iviRegMgr.exe C:\Program Files (x86)\Common Files\Intuit\QuickBooks\QBCFMonitorService.exe C:\Program Files (x86)\Common Files\Intuit\DataProtect\QBIDPService.exe C:\Program Files\Sony\VAIO Care\collsvc.exe C:\Windows\System32\tcpsvcs.exe C:\Windows\System32\snmp.exe C:\Windows\system32\svchost.exe -k imgsvc C:\Program Files (x86)\TeamViewer\Version5\TeamViewer_Service.exe C:\Program Files (x86)\ArcSoft\Magic-i Visual Effects 2\uCamMonitor.exe C:\Program Files (x86)\Sony\VAIO Event Service\VESMgr.exe C:\Program Files\Sony\VAIO Power Management\SPMService.exe C:\Program Files (x86)\Common Files\Sony Shared\VAIO Content Folder Watcher\VCFw.exe C:\Program Files (x86)\Common Files\Sony Shared\VAIO Entertainment Platform\VzCdb\VzCdbSvc.exe C:\Windows\SysWOW64\DllHost.exe C:\Windows\System32\svchost.exe -k WerSvcGroup C:\Program Files (x86)\RealVNC\VNC4\WinVNC4.exe C:\Windows\system32\SearchIndexer.exe C:\Program Files (x86)\Common Files\Pure Networks Shared\Platform\nmsrvc.exe C:\Windows\system32\WUDFHost.exe C:\Program Files (x86)\Sony\VAIO Event Service\VESMgrSub.exe C:\Windows\SysWOW64\DllHost.exe C:\Program Files (x86)\Sony\VAIO Event Service\VESGfxMgr.exe C:\Windows\system32\igfxext.exe C:\Windows\system32\igfxsrvc.exe C:\Program Files (x86)\Common Files\Sony Shared\VAIO Entertainment Platform\VCSW\VCSW.exe C:\Windows\system32\wbem\unsecapp.exe C:\Windows\system32\wbem\wmiprvse.exe C:\Windows\system32\taskeng.exe C:\Program Files (x86)\TeamViewer\Version5\TeamViewer.exe C:\Windows\system32\taskeng.exe C:\Windows\system32\igfxsrvc.exe C:\Windows\system32\taskeng.exe C:\Program Files\Sony\VAIO Update 4\VAIOUpdt.exe C:\Windows\system32\Dwm.exe C:\Windows\Explorer.EXE C:\Windows\System32\hkcmd.exe C:\Windows\System32\igfxpers.exe C:\Program Files (x86)\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe C:\Program Files (x86)\HP\Digital Imaging\bin\hpqtra08.exe C:\Program Files (x86)\Common Files\Intuit\QuickBooks\QBUpdate\qbupdate.exe C:\Program Files (x86)\PFU\ScanSnap\Driver\PfuSsMon.exe C:\Users\josh\AppData\Roaming\Dropbox\bin\Dropbox.exe C:\Program Files\Sony\VAIO Wireless Wizard\AutoLaunchWLASU.exe C:\Windows\twain_32\Fjscan32\SOP\FtLnSOP.exe C:\Windows\twain_32\Fjscan32\FjtwMkup.exe C:\Program Files (x86)\HP\HP Software Update\hpwuSchd2.exe C:\Program Files (x86)\HP\HP UT\bin\hppusg.exe C:\Program Files (x86)\Common Files\Pure Networks Shared\Platform\nmctxth.exe C:\Program Files (x86)\iTunes\iTunesHelper.exe C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe C:\Windows\SysWOW64\conime.exe C:\Program Files\iPod\bin\iPodService.exe C:\Windows\system32\wbem\unsecapp.exe C:\Program Files\Sony\VAIO Care\VCsystray.exe C:\Program Files (x86)\Lavasoft\Ad-Aware\AAWTray.exe C:\Windows\system32\svchost.exe -k LocalServiceAndNoImpersonation C:\Program Files\Windows Media Player\wmpnscfg.exe C:\Program Files\Windows Media Player\wmpnetwk.exe C:\Program Files (x86)\Internet Explorer\iexplore.exe C:\Program Files (x86)\Internet Explorer\iexplore.exe C:\Program Files (x86)\Microsoft Office\Office12\OUTLOOK.EXE C:\Windows\SysWOW64\Macromed\Flash\FlashUtil11e_ActiveX.exe C:\Windows\splwow64.exe C:\Windows\Microsoft.Net\Framework64\v3.0\WPF\PresentationFontCache.exe C:\Program Files (x86)\Internet Explorer\iexplore.exe C:\Program Files (x86)\Internet Explorer\iexplore.exe C:\Windows\System32\wiawow64.exe C:\Program Files\Sony\VAIO Care\listener.exe C:\Program Files (x86)\Mozilla Firefox\firefox.exe C:\Program Files (x86)\Mozilla Firefox\plugin-container.exe C:\Program Files (x86)\Microsoft Office\Office12\EXCEL.EXE C:\Program Files (x86)\Intuit\QuickBooks 2008\qbw32.exe C:\PROGRA~2\Intuit\QUICKB~2\QBDBMgrN.exe C:\PROGRA~2\Intuit\QUICKB~2\QuickBooksMessaging.exe C:\Program Files (x86)\Common Files\Intuit\QuickBooks\axlbridge.exe C:\PROGRA~2\Intuit\QUICKB~2\dbextclr11.exe C:\Windows\system32\SearchProtocolHost.exe C:\Windows\system32\SearchFilterHost.exe C:\Windows\system32\DllHost.exe C:\Windows\system32\DllHost.exe C:\Windows\SysWOW64\cmd.exe C:\Windows\SysWOW64\cscript.exe C:\Windows\system32\wbem\wmiprvse.exe . ============== Pseudo HJT Report =============== . uStart Page = hxxp://employeeweb.katsur.com/ mStart Page = hxxp://www.google.com/ig/redirectdomain?brand=SNYR&bmod=SNYR uInternet Settings,ProxyOverride = *.local BHO: Adobe PDF Link Helper: {18df081c-e8ad-4283-a596-fa578c2ebdc3} - C:\Program Files (x86)\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll BHO: Java™ Plug-In SSV Helper: {761497bb-d6f0-462c-b6eb-d4daf1d92d43} - C:\Program Files (x86)\Java\jre6\bin\ssv.dll BHO: Google Toolbar Helper: {aa58ed58-01dd-4d91-8333-cf10577473f7} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll BHO: Java™ Plug-In 2 SSV Helper: {dbc80044-a445-435b-bc74-9c25c1c588a9} - C:\Program Files (x86)\Java\jre6\bin\jp2ssv.dll TB: Google Toolbar: {2318c2b1-4965-11d4-9b18-009027a5cd4f} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll uRun: [swg] "C:\Program Files (x86)\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe" mRun: [Intuit SyncManager] C:\Program Files (x86)\Common Files\Intuit\Sync\IntuitSyncManager.exe startup mRun: [VWLASU] "C:\Program Files\Sony\VAIO Wireless Wizard\AutoLaunchWLASU.exe" mRun: [FtLnSOP_setup] C:\Windows\Twain_32\Fjscan32\SOP\FtLnSOP.exe mRun: [FJTWAIN Setup] C:\Windows\Twain_32\fjscan32\FjtwMkup.exe /Station mRun: [HP Software Update] C:\Program Files (x86)\HP\HP Software Update\HPWuSchd2.exe mRun: [HPUsageTracking] "C:\Program Files (x86)\HP\HP UT\bin\hppusg.exe" "C:\Program Files (x86)\HP\HP UT\" mRun: [nmctxth] "C:\Program Files (x86)\Common Files\Pure Networks Shared\Platform\nmctxth.exe" mRun: [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe" mRun: [APSDaemon] "C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe" mRun: [QuickTime Task] "C:\Program Files (x86)\QuickTime\QTTask.exe" -atboottime mRun: [iTunesHelper] "C:\Program Files (x86)\iTunes\iTunesHelper.exe" mRun: [SunJavaUpdateSched] "C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe" StartupFolder: C:\Users\josh\AppData\Roaming\MICROS~1\Windows\STARTM~1\Programs\Startup\Dropbox.lnk - C:\Users\josh\AppData\Roaming\Dropbox\bin\Dropbox.exe StartupFolder: C:\PROGRA~3\MICROS~1\Windows\STARTM~1\Programs\Startup\HPDIGI~1.LNK - C:\Program Files (x86)\HP\Digital Imaging\bin\hpqtra08.exe StartupFolder: C:\PROGRA~3\MICROS~1\Windows\STARTM~1\Programs\Startup\INTUIT~1.LNK - C:\Program Files (x86)\Common Files\Intuit\DataProtect\IntuitDataProtect.exe StartupFolder: C:\PROGRA~3\MICROS~1\Windows\STARTM~1\Programs\Startup\QUICKB~1.LNK - C:\Program Files (x86)\Common Files\Intuit\QuickBooks\QBUpdate\qbupdate.exe StartupFolder: C:\PROGRA~3\MICROS~1\Windows\STARTM~1\Programs\Startup\QUICKB~2.LNK - C:\Program Files (x86)\Intuit\QuickBooks 2008\QBW32.EXE StartupFolder: C:\PROGRA~3\MICROS~1\Windows\STARTM~1\Programs\Startup\SCANSN~1.LNK - C:\Program Files (x86)\PFU\ScanSnap\Driver\PfuSsMon.exe mPolicies-explorer: BindDirectlyToPropertySetStorage = 0 (0x0) mPolicies-system: EnableUIADesktopToggle = 0 (0x0) IE: E&xport to Microsoft Excel - C:\PROGRA~2\MICROS~2\Office12\EXCEL.EXE/3000 IE: Send image to &Bluetooth Device… - C:\Program Files\WIDCOMM\Bluetooth Software\btsendto_ie_ctx.htm IE: Send page to &Bluetooth Device… - C:\Program Files\WIDCOMM\Bluetooth Software\btsendto_ie.htm IE: {CCA281CA-C863-46ef-9331-5C8D4460577F} - C:\Program Files\WIDCOMM\Bluetooth Software\btsendto_ie.htm IE: {2670000A-7350-4f3c-8081-5663EE0C6C49} - {48E73304-E1D6-4330-914C-F5F514E3486C} - C:\PROGRA~2\MICROS~2\Office12\ONBttnIE.dll IE: {92780B25-18CC-41C8-B9BE-3C9C571A8263} - {FF059E31-CC5A-4E2E-BF3B-96E929D65503} - C:\PROGRA~2\MICROS~2\Office12\REFIEBAR.DLL DPF: {7530BFB8-7293-4D34-9923-61A11451AFC5} - hxxp://download.eset.com/special/eos/OnlineScanner.cab DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_31-windows-i586.cab DPF: {CAFEEFAC-0016-0000-0031-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_31-windows-i586.cab DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_31-windows-i586.cab DPF: {E06E2E99-0AA1-11D4-ABA6-0060082AA75C} - TCP: DhcpNameServer = 192.168.1.150 TCP: Interfaces\{616DCE37-90F0-4937-9A44-6C1E5B37ABDF} : DhcpNameServer = 192.168.1.150 Handler: intu-help-qb2 - {84D77A00-41B5-4b8b-8ADF-86486D72E749} - C:\Program Files (x86)\Intuit\QuickBooks 2009\HelpAsyncPluggableProtocol.dll Handler: intu-help-qb4 - {ACE22922-D07C-4860-B51B-8CF472FEC2CB} - C:\Program Files (x86)\Intuit\QuickBooks 2008\HelpAsyncPluggableProtocol.dll Handler: pure-go - {4746C79A-2042-4332-8650-48966E44ABA8} - C:\Program Files (x86)\Common Files\Pure Networks Shared\Platform\puresp4.dll Handler: qbwc - {FC598A64-626C-4447-85B8-53150405FD57} - C:\Windows\System32\mscoree.dll Handler: x-excid - {9D6CC632-1337-4a33-9214-2DA092E776F4} - c:\Windows\Downloaded Program Files\mimectl.dll Notify: VESWinlogon - VESWinlogon.dll BHO-X64: Adobe PDF Link Helper: {18DF081C-E8AD-4283-A596-FA578C2EBDC3} - C:\Program Files (x86)\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll BHO-X64: AcroIEHelperStub - No File BHO-X64: Java™ Plug-In SSV Helper: {761497BB-D6F0-462C-B6EB-D4DAF1D92D43} - C:\Program Files (x86)\Java\jre6\bin\ssv.dll BHO-X64: Google Toolbar Helper: {AA58ED58-01DD-4d91-8333-CF10577473F7} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll BHO-X64: Java™ Plug-In 2 SSV Helper: {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files (x86)\Java\jre6\bin\jp2ssv.dll TB-X64: Google Toolbar: {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files (x86)\Google\Google Toolbar\GoogleToolbar_32.dll mRun-x64: [Intuit SyncManager] C:\Program Files (x86)\Common Files\Intuit\Sync\IntuitSyncManager.exe startup mRun-x64: [VWLASU] "C:\Program Files\Sony\VAIO Wireless Wizard\AutoLaunchWLASU.exe" mRun-x64: [FtLnSOP_setup] C:\Windows\Twain_32\Fjscan32\SOP\FtLnSOP.exe mRun-x64: [FJTWAIN Setup] C:\Windows\Twain_32\fjscan32\FjtwMkup.exe /Station mRun-x64: [HP Software Update] C:\Program Files (x86)\HP\HP Software Update\HPWuSchd2.exe mRun-x64: [HPUsageTracking] "C:\Program Files (x86)\HP\HP UT\bin\hppusg.exe" "C:\Program Files (x86)\HP\HP UT\" mRun-x64: [nmctxth] "C:\Program Files (x86)\Common Files\Pure Networks Shared\Platform\nmctxth.exe" mRun-x64: [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe" mRun-x64: [APSDaemon] "C:\Program Files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe" mRun-x64: [QuickTime Task] "C:\Program Files (x86)\QuickTime\QTTask.exe" -atboottime mRun-x64: [iTunesHelper] "C:\Program Files (x86)\iTunes\iTunesHelper.exe" mRun-x64: [SunJavaUpdateSched] "C:\Program Files (x86)\Common Files\Java\Java Update\jusched.exe" IE-X64: {CCA281CA-C863-46ef-9331-5C8D4460577F} - C:\Program Files\WIDCOMM\Bluetooth Software\btsendto_ie.htm Hosts: 216.240.133.193 www.google-analytics.com. Hosts: 216.240.133.193 ad-emea.doubleclick.net. Hosts: 216.240.133.193 www.statcounter.com. Hosts: 69.72.252.254 www.google-analytics.com. Hosts: 69.72.252.254 ad-emea.doubleclick.net. . Note: multiple HOSTS entries found. Please refer to Attach.txt . ================= FIREFOX =================== . FF - ProfilePath - C:\Users\josh\AppData\Roaming\Mozilla\Firefox\Profiles\odt38dqd.default\ FF - plugin: C:\Program Files (x86)\Adobe\Reader 10.0\Reader\AIR\nppdf32.dll FF - plugin: C:\Program Files (x86)\Google\Update\1.3.21.111\npGoogleUpdate3.dll FF - plugin: C:\Program Files (x86)\Google\Update\1.3.21.79\npGoogleUpdate3.dll FF - plugin: C:\Program Files (x86)\Java\jre6\bin\new_plugin\npdeployJava1.dll FF - plugin: C:\Program Files (x86)\Java\jre6\bin\plugin2\npdeployJava1.dll FF - plugin: C:\Program Files (x86)\Java\jre6\bin\plugin2\npjp2.dll FF - plugin: C:\Program Files (x86)\Microsoft Silverlight\4.1.10111.0\npctrlui.dll FF - plugin: C:\Program Files (x86)\Mozilla Firefox\plugins\npdeployJava1.dll FF - plugin: C:\Users\josh\AppData\Roaming\Mozilla\plugins\npatgpc.dll FF - plugin: C:\Windows\SysWOW64\Macromed\Flash\NPSWF32.dll . ============= SERVICES / DRIVERS =============== . R0 Lbd;Lbd;C:\Windows\system32\DRIVERS\Lbd.sys –> C:\Windows\system32\DRIVERS\Lbd.sys [?] R0 PxHlpa64;PxHlpa64;C:\Windows\system32\Drivers\PxHlpa64.sys –> C:\Windows\system32\Drivers\PxHlpa64.sys [?] R2 AdobeARMservice;Adobe Acrobat Update Service;C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [2012-1-3 63928] R2 atashost;WebEx Service Host for Support Center;C:\Windows\SysWOW64\atashost.exe [2010-5-28 133944] R2 FJTWMKSV;FJTWMKSV;C:\Windows\twain_32\Fjscan32\FJTWMKSV.exe [2009-10-6 45056] R2 FontCache;Windows Font Cache Service;C:\Windows\system32\svchost.exe -k LocalServiceAndNoImpersonation [2008-1-20 21504] R2 Lavasoft Ad-Aware Service;Lavasoft Ad-Aware Service;C:\Program Files (x86)\Lavasoft\Ad-Aware\AAWService.exe [2011-12-2 2152152] R2 QBVSS;QBIDPService;C:\Program Files (x86)\Common Files\Intuit\DataProtect\QBIDPService.exe [2011-6-30 1248256] R2 regi;regi;\??\C:\Windows\system32\drivers\regi.sys –> C:\Windows\system32\drivers\regi.sys [?] R2 RtkAudioService;Realtek Audio Service;C:\Windows\RTKAUDIOSERVICE.EXE [2008-11-21 141344] R2 SampleCollector;Intel® Sample Collector;C:\Program Files\Sony\VAIO Care\collsvc.exe [2008-10-23 167424] R2 TeamViewer5;TeamViewer 5;C:\Program Files (x86)\TeamViewer\Version5\TeamViewer_Service.exe [2010-10-15 2002728] R2 uCamMonitor;CamMonitor;C:\Program Files (x86)\ArcSoft\Magic-i Visual Effects 2\uCamMonitor.exe [2008-10-23 104960] R2 VAIO Power Management;VAIO Power Management;C:\Program Files\Sony\VAIO Power Management\SPMService.exe [2008-11-21 407392] R2 VCFw;VAIO Content Folder Watcher;C:\Program Files (x86)\Common Files\Sony Shared\VAIO Content Folder Watcher\VCFw.exe [2008-9-3 446464] R3 ArcSoftKsUFilter;ArcSoft Magic-I Visual Effect;C:\Windows\system32\DRIVERS\ArcSoftKsUFilter.sys –> C:\Windows\system32\DRIVERS\ArcSoftKsUFilter.sys [?] R3 AVerAVF2;AVerAVF2;C:\Windows\system32\DRIVERS\AVerAVF2.sys –> C:\Windows\system32\DRIVERS\AVerAVF2.sys [?] R3 AVerBDA6x_x64;AVerMedia SAA716x BDA Service;C:\Windows\system32\DRIVERS\AVerBDA716x_x64.sys –> C:\Windows\system32\DRIVERS\AVerBDA716x_x64.sys [?] R3 e1yexpress;Intel® Gigabit Network Connections Driver;C:\Windows\system32\DRIVERS\e1y60x64.sys –> C:\Windows\system32\DRIVERS\e1y60x64.sys [?] R3 HECIx64;Intel® Management Engine Interface;C:\Windows\system32\DRIVERS\HECIx64.sys –> C:\Windows\system32\DRIVERS\HECIx64.sys [?] R3 Lavasoft Kernexplorer;Lavasoft helper driver;C:\Program Files (x86)\Lavasoft\Ad-Aware\kernexplorer64.sys [2011-12-8 17152] R3 SFEP;Sony Firmware Extension Parser;C:\Windows\system32\DRIVERS\SFEP.sys –> C:\Windows\system32\DRIVERS\SFEP.sys [?] S2 clr_optimization_v4.0.30319_32;Microsoft .NET Framework NGEN v4.0.30319_X86;C:\Windows\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe [2010-3-18 130384] S2 clr_optimization_v4.0.30319_64;Microsoft .NET Framework NGEN v4.0.30319_X64;C:\Windows\Microsoft.NET\Framework64\v4.0.30319\mscorsvw.exe [2010-3-18 138576] S2 gupdate;Google Update Service (gupdate);C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [2010-2-2 135664] S3 btwl2cap;Bluetooth L2CAP Service;C:\Windows\system32\DRIVERS\btwl2cap.sys –> C:\Windows\system32\DRIVERS\btwl2cap.sys [?] S3 gupdatem;Google Update Service (gupdatem);C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [2010-2-2 135664] S3 MozillaMaintenance;Mozilla Maintenance Service;C:\Program Files (x86)\Mozilla Maintenance Service\maintenanceservice.exe [2012-5-4 129976] S3 PerfHost;Performance Counter DLL Host;C:\Windows\SysWOW64\perfhost.exe [2008-1-20 19968] S3 SOHCImp;VAIO Media plus Content Importer;C:\Program Files (x86)\Sony\VAIO Media plus\SOHCImp.exe [2008-10-23 103712] S3 SOHDms;VAIO Media plus Digital Media Server;C:\Program Files (x86)\Sony\VAIO Media plus\SOHDms.exe [2008-10-23 353568] S3 SOHDs;VAIO Media plus Device Searcher;C:\Program Files (x86)\Sony\VAIO Media plus\SOHDs.exe [2008-10-23 62752] S3 VcmIAlzMgr;VAIO Content Metadata Intelligent Analyzing Manager;C:\Program Files\Sony\VCM Intelligent Analyzing Manager\VcmIAlzMgr.exe [2008-10-23 369952] S3 VcmXmlIfHelper;VAIO Content Metadata XML Interface;C:\Program Files\Common Files\Sony Shared\VcmXml\VcmXmlIfHelper64.exe [2008-10-23 108832] S3 WPFFontCache_v0400;Windows Presentation Foundation Font Cache 4.0.0.0;C:\Windows\Microsoft.NET\Framework64\v4.0.30319\WPF\WPFFontCache_v0400.exe [2010-3-18 1020768] S4 clr_optimization_v2.0.50727_64;Microsoft .NET Framework NGEN v2.0.50727_X64;C:\Windows\Microsoft.NET\Framework64\v2.0.50727\mscorsvw.exe [2009-12-3 89920] S4 QuickBooksDB21;QuickBooksDB21;C:\PROGRA~2\Intuit\QUICKB~2\QBDBMgrN.exe -hvQuickBooksDB21 –> C:\PROGRA~2\Intuit\QUICKB~2\QBDBMgrN.exe -hvQuickBooksDB21 [?] . =============== File Associations =============== . JSEFile=C:\Windows\SysWOW64\WScript.exe "%1" %* . =============== Created Last 30 ================ . 2012-05-04 11:57:07 ——– d—–w- C:\Program Files (x86)\Mozilla Maintenance Service 2012-05-04 11:57:03 157352 —-a-w- C:\Program Files (x86)\Mozilla Firefox\maintenanceservice_installer.exe 2012-05-04 11:57:03 129976 —-a-w- C:\Program Files (x86)\Mozilla Firefox\maintenanceservice.exe 2012-04-12 07:05:52 4699520 —-a-w- C:\Windows\System32\ntoskrnl.exe 2012-04-12 07:05:34 78848 —-a-w- C:\Windows\System32\imagehlp.dll 2012-04-12 07:05:34 5632 —-a-w- C:\Windows\System32\wmi.dll 2012-04-12 07:05:34 5120 —-a-w- C:\Windows\SysWow64\wmi.dll 2012-04-12 07:05:34 219136 —-a-w- C:\Windows\System32\wintrust.dll 2012-04-12 07:05:34 172032 —-a-w- C:\Windows\SysWow64\wintrust.dll 2012-04-12 07:05:34 16384 —-a-w- C:\Windows\System32\drivers\fs_rec.sys 2012-04-12 07:05:34 157696 —-a-w- C:\Windows\SysWow64\imagehlp.dll 2012-04-11 12:47:45 2409784 —-a-w- C:\Program Files\Windows Mail\OESpamFilter.dat 2012-04-11 12:47:45 2409784 —-a-w- C:\Program Files (x86)\Windows Mail\OESpamFilter.dat . ==================== Find3M ==================== . 2012-04-09 12:41:46 472808 —-a-w- C:\Windows\SysWow64\deployJava1.dll 2012-04-04 19:56:40 24904 —-a-w- C:\Windows\System32\drivers\mbam.sys 2012-02-28 06:56:48 2311168 —-a-w- C:\Windows\System32\jscript9.dll 2012-02-28 06:49:56 1390080 —-a-w- C:\Windows\System32\wininet.dll 2012-02-28 06:48:57 1493504 —-a-w- C:\Windows\System32\inetcpl.cpl 2012-02-28 06:42:55 2382848 —-a-w- C:\Windows\System32\mshtml.tlb 2012-02-28 01:18:55 1799168 —-a-w- C:\Windows\SysWow64\jscript9.dll 2012-02-28 01:11:21 1427456 —-a-w- C:\Windows\SysWow64\inetcpl.cpl 2012-02-28 01:11:07 1127424 —-a-w- C:\Windows\SysWow64\wininet.dll 2012-02-28 01:03:16 2382848 —-a-w- C:\Windows\SysWow64\mshtml.tlb 2012-02-14 16:49:43 327680 —-a-w- C:\Windows\System32\d3d10_1core.dll 2012-02-14 16:49:43 196096 —-a-w- C:\Windows\System32\d3d10_1.dll 2012-02-14 15:45:30 219648 —-a-w- C:\Windows\SysWow64\d3d10_1core.dll 2012-02-14 15:45:30 160768 —-a-w- C:\Windows\SysWow64\d3d10_1.dll 2012-02-13 14:38:31 2002944 —-a-w- C:\Windows\System32\d3d10warp.dll 2012-02-13 14:12:08 1172480 —-a-w- C:\Windows\SysWow64\d3d10warp.dll 2012-02-13 14:06:48 834048 —-a-w- C:\Windows\System32\d2d1.dll 2012-02-13 14:03:11 1555968 —-a-w- C:\Windows\System32\DWrite.dll 2012-02-13 13:47:57 683008 —-a-w- C:\Windows\SysWow64\d2d1.dll 2012-02-13 13:44:40 1068544 —-a-w- C:\Windows\SysWow64\DWrite.dll . ============= FINISH: 11:12:48.89 ===============

Attachments:

aswMBR version 0.9.9.1665 Copyright© 2011 AVAST Software Run date: 2012-05-10 11:19:24 —————————– 11:19:24.374 OS Version: Windows x64 6.0.6002 Service Pack 2 11:19:24.374 Number of processors: 2 586 0x170A 11:19:24.375 ComputerName: JOSH-PC UserName: josh 11:19:25.573 Initialize success 11:19:49.066 AVAST engine defs: 12051000 11:20:00.114 Disk 0 (boot) \Device\Harddisk0\DR0 -> \Device\Ide\IdeDeviceP0T0L0-0 11:20:00.115 Disk 0 Vendor: WDC_WD3200AAJS-55B4A0 01.03A01 Size: 305245MB BusType: 3 11:20:00.117 Disk 1 \Device\Harddisk1\DR1 -> \Device\0000005b 11:20:00.118 Disk 1 Vendor: RICOH 01 Size: 305245MB BusType: 0 11:20:00.120 Disk 2 \Device\Harddisk2\DR2 -> \Device\0000005c 11:20:00.122 Disk 2 Vendor: RICOH 02 Size: 305245MB BusType: 0 11:20:00.148 Disk 0 MBR read successfully 11:20:00.150 Disk 0 MBR scan 11:20:00.153 Disk 0 Windows VISTA default MBR code 11:20:00.164 Disk 0 Partition 1 00 27 Hidden NTFS WinRE NTFS 10403 MB offset 2048 11:20:00.176 Disk 0 Partition 2 80 (A) 07 HPFS/NTFS NTFS 294840 MB offset 21307392 11:20:00.196 Disk 0 scanning C:\Windows\system32\drivers 11:20:08.208 Service scanning 11:20:29.005 Modules scanning 11:20:29.010 Disk 0 trace - called modules: 11:20:29.028 ntoskrnl.exe CLASSPNP.SYS disk.sys acpi.sys ataport.SYS pciide.sys PCIIDEX.SYS hal.dll atapi.sys 11:20:29.031 1 nt!IofCallDriver -> \Device\Harddisk0\DR0[0xfffffa8005eca790] 11:20:29.034 3 CLASSPNP.SYS[fffffa6000fd4c33] -> nt!IofCallDriver -> [0xfffffa8004af0510] 11:20:29.038 5 acpi.sys[fffffa60008f2fde] -> nt!IofCallDriver -> \Device\Ide\IdeDeviceP0T0L0-0[0xfffffa8004029940] 11:20:29.992 AVAST engine scan C:\Windows 11:20:32.775 AVAST engine scan C:\Windows\system32 11:20:43.216 File: C:\Windows\system32\consrv.dll **INFECTED** Win64:Sirefef-C [Drp] 11:22:19.243 File: C:\Windows\assembly\GAC_32\Desktop.ini **INFECTED** Win32:Sirefef-FQ [Drp] 11:22:21.643 File: C:\Windows\assembly\GAC_64\Desktop.ini **INFECTED** Win64:Sirefef-C [Drp] 11:23:45.931 AVAST engine scan C:\Windows\system32\drivers 11:24:00.887 AVAST engine scan C:\Users\josh 11:27:35.303 AVAST engine scan C:\ProgramData 11:30:44.279 Scan finished successfully 11:30:51.364 Disk 0 MBR has been saved successfully to "C:\Users\josh\Desktop\MBR.dat" 11:30:51.367 The log file has been saved successfully to "C:\Users\josh\Desktop\aswMBR.txt"
Hi,

**WARNING**Unfortunately one or more of the infections I have identified are Backdoor Trojans, IRCBots or other Malware capable of stealing very important information. You need to stop using all Internet Banking sites, change passwords to all sites with sensitive information from a clean computer and phone your bank to inform them that you may be a victim of identify theft. More often than not, we advise users that a full reinstallation of their Operating System is the only way to ensure that their computer will ever be 100% clean again.

Unfortunately I have found what is known as the ZeroAccess rootkit on your system. It is an especially nasty infection that can take quite some time to clean as well as may have damaged your system files itself. As a warning, during the cleaning (if you choose to do so) you may lose internet access with this computer and in the end we may need to reinstall the operating system anyway depending on the extent of the infection.

If you would like to format and reinstall your Operating System please let me know and we can assist you with that.

If you would like to continue with the cleaning, please continue with the following instructions and I will be more than happy to help. :)
———-

Please double click the aswMBR icon to run it.
Vista and Windows 7 users right click the icon and choose "Run as administrator".

  • Click the Scan button to start scan.
  • When scan finishes, press the Fix Button. Once the Fix is done, press the Save Log button and save the log to your desktop. You need to reboot your computer when its done before you do anything else, then post the log that will be on your desktop.

[external image: Posted Image]
Click the image to enlarge it
I would like to try to clean it first before wiping the hard drive. Here is the updated Save Log you requested: aswMBR version 0.9.9.1665 Copyright© 2011 AVAST Software Run date: 2012-05-10 14:13:19 —————————– 14:13:19.531 OS Version: Windows x64 6.0.6002 Service Pack 2 14:13:19.531 Number of processors: 2 586 0x170A 14:13:19.531 ComputerName: JOSH-PC UserName: josh 14:13:22.511 Initialize success 14:13:39.749 AVAST engine defs: 12051000 14:13:41.434 Disk 0 (boot) \Device\Harddisk0\DR0 -> \Device\Ide\IdeDeviceP0T0L0-0 14:13:41.434 Disk 0 Vendor: WDC_WD3200AAJS-55B4A0 01.03A01 Size: 305245MB BusType: 3 14:13:41.434 Disk 1 \Device\Harddisk1\DR1 -> \Device\0000005a 14:13:41.434 Disk 1 Vendor: RICOH 01 Size: 305245MB BusType: 0 14:13:41.449 Disk 2 \Device\Harddisk2\DR2 -> \Device\0000005b 14:13:41.449 Disk 2 Vendor: RICOH 02 Size: 305245MB BusType: 0 14:13:41.449 Disk 0 MBR read successfully 14:13:41.465 Disk 0 MBR scan 14:13:41.465 Disk 0 Windows VISTA default MBR code 14:13:41.465 Disk 0 Partition 1 00 27 Hidden NTFS WinRE NTFS 10403 MB offset 2048 14:13:41.481 Disk 0 Partition 2 80 (A) 07 HPFS/NTFS NTFS 294840 MB offset 21307392 14:13:41.512 Disk 0 scanning C:\Windows\system32\drivers 14:13:57.673 Service scanning 14:14:26.597 Modules scanning 14:14:26.597 Disk 0 trace - called modules: 14:14:26.644 ntoskrnl.exe CLASSPNP.SYS disk.sys acpi.sys ataport.SYS pciide.sys 14:14:26.644 1 nt!IofCallDriver -> \Device\Harddisk0\DR0[0xfffffa8005ee2790] 14:14:26.644 3 CLASSPNP.SYS[fffffa6000dd1c33] -> nt!IofCallDriver -> [0xfffffa800402b520] 14:14:26.644 5 acpi.sys[fffffa60008fdfde] -> nt!IofCallDriver -> \Device\Ide\IdeDeviceP0T0L0-0[0xfffffa80040234b0] 14:14:28.141 AVAST engine scan C:\Windows 14:14:35.489 AVAST engine scan C:\Windows\system32 14:20:44.133 AVAST engine scan C:\Windows\system32\drivers 14:21:21.729 AVAST engine scan C:\Users\josh 14:25:20.378 AVAST engine scan C:\ProgramData 14:28:34.147 Scan finished successfully 14:28:40.075 Disk 0 MBR has been saved successfully to "C:\Users\josh\Desktop\MBR.dat" 14:28:40.090 The log file has been saved successfully to "C:\Users\josh\Desktop\aswMBR.txt"
Download Combofix from either of the links below, and save it to your desktop.
Link 1
Link 2

**Note: It is important that it is saved directly to your desktop**

——————————————————————–

IMPORTANT - Disable your AntiVirus and AntiSpyware applications, usually via a right click on the System Tray icon. They may otherwise interfere with our tools. If you have difficulty properly disabling your protective programs, refer to this link here

——————————————————————–

Right-Click and Run as Administrator on ComboFix.exe & follow the prompts.
  • When finished, it will produce a report for you.
  • Please post the C:\ComboFix.txt for further review.
ComboFix 12-05-10.04 - josh 05/10/2012 15:29:10.3.2 - x64 Microsoft® Windows Vista™ Home Premium 6.0.6002.2.1252.44.1033.18.3900.1668 [GMT -4:00] Running from: c:\users\[removed]\Desktop\ComboFix.exe SP: Windows Defender *Enabled/Updated* {D68DDC3A-831F-4fae-9E44-DA132C1ACF46} . . ((((((((((((((((((((((((( Files Created from 2012-04-10 to 2012-05-10 ))))))))))))))))))))))))))))))) . . 2012-05-10 19:35 . 2012-05-10 19:35 ——– d—–w- c:\users\QBDataServiceUser18\AppData\Local\temp 2012-05-10 19:35 . 2012-05-10 19:35 ——– d—–w- c:\users\Public\AppData\Local\temp 2012-05-10 19:35 . 2012-05-10 19:35 ——– d—–w- c:\users\Default\AppData\Local\temp 2012-05-04 11:57 . 2012-05-04 11:57 ——– d—–w- c:\program files (x86)\Mozilla Maintenance Service 2012-05-04 11:57 . 2012-05-04 11:57 157352 —-a-w- c:\program files (x86)\Mozilla Firefox\maintenanceservice_installer.exe 2012-05-04 11:57 . 2012-05-04 11:57 129976 —-a-w- c:\program files (x86)\Mozilla Firefox\maintenanceservice.exe 2012-04-12 07:05 . 2012-03-06 06:44 4699520 —-a-w- c:\windows\system32\ntoskrnl.exe 2012-04-12 07:05 . 2012-02-29 15:37 5632 —-a-w- c:\windows\system32\wmi.dll 2012-04-12 07:05 . 2012-02-29 15:37 219136 —-a-w- c:\windows\system32\wintrust.dll 2012-04-12 07:05 . 2012-02-29 15:35 78848 —-a-w- c:\windows\system32\imagehlp.dll 2012-04-12 07:05 . 2012-02-29 15:11 5120 —-a-w- c:\windows\SysWow64\wmi.dll 2012-04-12 07:05 . 2012-02-29 15:11 172032 —-a-w- c:\windows\SysWow64\wintrust.dll 2012-04-12 07:05 . 2012-02-29 15:09 157696 —-a-w- c:\windows\SysWow64\imagehlp.dll 2012-04-12 07:05 . 2012-02-29 13:52 16384 —-a-w- c:\windows\system32\drivers\fs_rec.sys 2012-04-11 12:47 . 2012-03-01 11:01 2409784 —-a-w- c:\program files (x86)\Windows Mail\OESpamFilter.dat 2012-04-11 12:47 . 2012-03-01 11:01 2409784 —-a-w- c:\program files\Windows Mail\OESpamFilter.dat . . . (((((((((((((((((((((((((((((((((((((((( Find3M Report )))))))))))))))))))))))))))))))))))))))))))))))))))) . 2012-04-09 12:41 . 2010-12-20 17:00 472808 —-a-w- c:\windows\SysWow64\deployJava1.dll 2012-04-04 19:56 . 2011-02-08 14:06 24904 —-a-w- c:\windows\system32\drivers\mbam.sys 2012-02-14 16:49 . 2012-03-14 09:10 327680 —-a-w- c:\windows\system32\d3d10_1core.dll 2012-02-14 16:49 . 2012-03-14 09:10 196096 —-a-w- c:\windows\system32\d3d10_1.dll 2012-02-14 15:45 . 2012-03-14 09:10 219648 —-a-w- c:\windows\SysWow64\d3d10_1core.dll 2012-02-14 15:45 . 2012-03-14 09:10 160768 —-a-w- c:\windows\SysWow64\d3d10_1.dll 2012-02-13 14:38 . 2012-03-14 09:10 2002944 —-a-w- c:\windows\system32\d3d10warp.dll 2012-02-13 14:12 . 2012-03-14 09:10 1172480 —-a-w- c:\windows\SysWow64\d3d10warp.dll 2012-02-13 14:06 . 2012-03-14 09:10 834048 —-a-w- c:\windows\system32\d2d1.dll 2012-02-13 14:03 . 2012-03-14 09:10 1555968 —-a-w- c:\windows\system32\DWrite.dll 2012-02-13 13:47 . 2012-03-14 09:10 683008 —-a-w- c:\windows\SysWow64\d2d1.dll 2012-02-13 13:44 . 2012-03-14 09:10 1068544 —-a-w- c:\windows\SysWow64\DWrite.dll . . ((((((((((((((((((((((((((((((((((((( Reg Loading Points )))))))))))))))))))))))))))))))))))))))))))))))))) . . *Note* empty entries & legit default entries are not shown REGEDIT4 . [HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt1] @="{FB314ED9-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314ED9-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 94208 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt.14.dll . [HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt2] @="{FB314EDA-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314EDA-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 94208 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt.14.dll . [HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt3] @="{FB314EDB-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314EDB-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 94208 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt.14.dll . [HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "swg"="c:\program files (x86)\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe" [2008-10-23 39408] . [HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run] "Intuit SyncManager"="c:\program files (x86)\Common Files\Intuit\Sync\IntuitSyncManager.exe" [2011-06-14 1527128] "VWLASU"="c:\program files\Sony\VAIO Wireless Wizard\AutoLaunchWLASU.exe" [2008-05-20 24576] "FtLnSOP_setup"="c:\windows\Twain_32\Fjscan32\SOP\FtLnSOP.exe" [2007-03-08 212992] "FJTWAIN Setup"="c:\windows\Twain_32\fjscan32\FjtwMkup.exe" [2007-03-08 131072] "HP Software Update"="c:\program files (x86)\HP\HP Software Update\HPWuSchd2.exe" [2007-03-12 49152] "HPUsageTracking"="c:\program files (x86)\HP\HP UT\bin\hppusg.exe" [2007-05-08 36864] "nmctxth"="c:\program files (x86)\Common Files\Pure Networks Shared\Platform\nmctxth.exe" [2009-04-07 642856] "Adobe ARM"="c:\program files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe" [2012-01-03 843712] "APSDaemon"="c:\program files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe" [2011-11-02 59240] "QuickTime Task"="c:\program files (x86)\QuickTime\QTTask.exe" [2011-10-24 421888] "iTunesHelper"="c:\program files (x86)\iTunes\iTunesHelper.exe" [2011-12-08 421736] "SunJavaUpdateSched"="c:\program files (x86)\Common Files\Java\Java Update\jusched.exe" [2012-01-18 254696] . c:\users\josh\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\ Dropbox.lnk - c:\users\josh\AppData\Roaming\Dropbox\bin\Dropbox.exe [2012-2-14 24246216] . c:\programdata\Microsoft\Windows\Start Menu\Programs\Startup\ HP Digital Imaging Monitor.lnk - c:\program files (x86)\HP\Digital Imaging\bin\hpqtra08.exe [2007-3-11 210520] Intuit Data Protect.lnk - c:\program files (x86)\Common Files\Intuit\DataProtect\IntuitDataProtect.exe [2010-12-2 5842776] QuickBooks Update Agent.lnk - c:\program files (x86)\Common Files\Intuit\QuickBooks\QBUpdate\qbupdate.exe [2011-7-6 1156968] QuickBooks_Standard_21.lnk - c:\program files (x86)\Intuit\QuickBooks 2008\QBW32.EXE [2011-7-6 1178984] ScanSnap Manager.lnk - c:\program files (x86)\PFU\ScanSnap\Driver\PfuSsMon.exe [2010-12-21 1146880] . [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\policies\system] "EnableUIADesktopToggle"= 0 (0x0) . [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\VESWinlogon] 2008-11-06 01:32 98304 —-a-w- c:\windows\System32\VESWinlogon.dll . [HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Lavasoft Ad-Aware Service] @="Service" . S2 AdobeARMservice;Adobe Acrobat Update Service;c:\program files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [2012-01-03 63928] . . — Other Services/Drivers In Memory — . *NewlyCreated* - WS2IFSL . [HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\windows nt\currentversion\svchost] hpdevmgmt REG_MULTI_SZ hpqcxs08 hpqddsvc . Contents of the 'Scheduled Tasks' folder . 2012-05-10 c:\windows\Tasks\GoogleUpdateTaskMachineCore.job - c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-02-02 16:55] . 2012-05-10 c:\windows\Tasks\GoogleUpdateTaskMachineUA.job - c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-02-02 16:55] . . ——— x86-64 ———– . . [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt1] @="{FB314ED9-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314ED9-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 97792 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt64.14.dll . [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt2] @="{FB314EDA-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314EDA-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 97792 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt64.14.dll . [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt3] @="{FB314EDB-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314EDB-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 97792 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt64.14.dll . [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt4] @="{FB314EDC-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314EDC-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 97792 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt64.14.dll . [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "RtHDVCpl"="RAVCpl64.exe" [2008-11-12 6407200] "Skytel"="Skytel.exe" [2008-11-12 1826816] "IgfxTray"="c:\windows\system32\igfxtray.exe" [2008-09-17 151064] "HotKeysCmds"="c:\windows\system32\hkcmd.exe" [2008-09-17 209432] "Persistence"="c:\windows\system32\igfxpers.exe" [2008-09-17 182808] "NvCplDaemon"="c:\windows\system32\NvCpl.dll" [2008-10-31 15880224] "NvMediaCenter"="c:\windows\system32\NvMcTray.dll" [2008-10-31 82464] . ——- Supplementary Scan ——- . uLocal Page = c:\windows\system32\blank.htm uStart Page = hxxp://employeeweb.katsur.com/ mStart Page = hxxp://www.google.com/ig/redirectdomain?brand=SNYR&bmod=SNYR mLocal Page = c:\windows\SysWOW64\blank.htm uInternet Settings,ProxyOverride = *.local IE: E&xport to Microsoft Excel - c:\progra~2\MICROS~2\Office12\EXCEL.EXE/3000 IE: Send image to &Bluetooth Device… - c:\program files\WIDCOMM\Bluetooth Software\btsendto_ie_ctx.htm IE: Send page to &Bluetooth Device… - c:\program files\WIDCOMM\Bluetooth Software\btsendto_ie.htm TCP: DhcpNameServer = 192.168.1.150 CLSID: {603d3801-bd81-11d0-a3a5-00c04fd706ec} - %SystemRoot%\SysWow64\browseui.dll FF - ProfilePath - c:\users\josh\AppData\Roaming\Mozilla\Firefox\Profiles\odt38dqd.default\ . - - - - ORPHANS REMOVED - - - - . AddRemove-SLABCOMM&10C4&EA60 - c:\windows\system32\Silabs\DriverUninstaller.exe VCP CP210x Cardinal\SLABCOMM&10C4&EA60 . . . [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\SampleCollector] "ImagePath"="\"c:\program files\Sony\VAIO Care\collsvc.exe\" \"/service\" \"/counter=\Processor(_Total)\% Processor Time:5\" \"/counter=\PhysicalDisk(_Total)\Disk Bytes/sec:5\" \"/counter=\Network Interface(*)\Bytes Total/sec:5\" \"/directory=inteldata\"" . ——————— LOCKED REGISTRY KEYS ——————— . [HKEY_USERS\.Default\Software\Microsoft\Internet Explorer\Approved Extensions] @Denied: (2) (LocalSystem) "{2318C2B1-4965-11D4-9B18-009027A5CD4F}"=hex:51,66,7a,6c,4c,1d,38,12,df,c1,0b, 27,57,07,ba,54,e4,0e,43,d0,22,fb,89,5b "{18DF081C-E8AD-4283-A596-FA578C2EBDC3}"=hex:51,66,7a,6c,4c,1d,38,12,72,0b,cc, 1c,9f,a6,ed,07,da,80,b9,17,89,70,f9,d7 "{761497BB-D6F0-462C-B6EB-D4DAF1D92D43}"=hex:51,66,7a,6c,4c,1d,38,12,d5,94,07, 72,c2,98,42,03,c9,fd,97,9a,f4,87,69,57 "{AA58ED58-01DD-4D91-8333-CF10577473F7}"=hex:51,66,7a,6c,4c,1d,38,12,36,ee,4b, ae,ef,4f,ff,08,fc,25,8c,50,52,2a,37,e3 "{DBC80044-A445-435B-BC74-9C25C1C588A9}"=hex:51,66,7a,6c,4c,1d,38,12,2a,03,db, df,77,ea,35,06,c3,62,df,65,c4,9b,cc,bd "{FF059E31-CC5A-4E2E-BF3B-96E929D65503}"=hex:51,66,7a,6c,4c,1d,38,12,5f,9d,16, fb,68,82,40,0b,c0,2d,d5,a9,2c,88,11,17 "{BDEADE7F-C265-11D0-BCED-00A0C90AB50F}"=hex:51,66,7a,6c,4c,1d,38,12,11,dd,f9, b9,57,8c,be,54,c3,fb,43,e0,cc,54,f1,1b . [HKEY_USERS\.Default\Software\Microsoft\Internet Explorer\ApprovedExtensionsMigration] @Denied: (2) (LocalSystem) "Timestamp"=hex:2d,d9,12,03,06,bc,cc,01 . [HKEY_USERS\.Default\Software\Microsoft\Internet Explorer\User Preferences] @Denied: (2) (LocalSystem) "88D7D0879DAB32E14DE5B3A805A34F98AFF34F5977"=hex:01,00,00,00,d0,8c,9d,df,01,15, d1,11,8c,7a,00,c0,4f,c2,97,eb,01,00,00,00,5c,c2,23,a9,d9,da,47,4d,a8,6c,55,\ "2D53CFFC5C1A3DD2E97B7979AC2A92BD59BC839E81"=hex:01,00,00,00,d0,8c,9d,df,01,15, d1,11,8c,7a,00,c0,4f,c2,97,eb,01,00,00,00,5c,c2,23,a9,d9,da,47,4d,a8,6c,55,\ . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}] @Denied: (A 2) (Everyone) @="FlashBroker" "LocalizedString"="@c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil11e_ActiveX.exe,-101" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\Elevation] "Enabled"=dword:00000001 . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\LocalServer32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil11e_ActiveX.exe" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\TypeLib] @="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}] @Denied: (A 2) (Everyone) @="Shockwave Flash Object" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\InprocServer32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash11e.ocx" "ThreadingModel"="Apartment" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\MiscStatus] @="0" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ProgID] @="ShockwaveFlash.ShockwaveFlash.10" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash11e.ocx, 1" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\TypeLib] @="{D27CDB6B-AE6D-11cf-96B8-444553540000}" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\Version] @="1.0" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID] @="ShockwaveFlash.ShockwaveFlash" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}] @Denied: (A 2) (Everyone) @="Macromedia Flash Factory Object" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\InprocServer32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash11e.ocx" "ThreadingModel"="Apartment" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ProgID] @="FlashFactory.FlashFactory.1" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash11e.ocx, 1" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\TypeLib] @="{D27CDB6B-AE6D-11cf-96B8-444553540000}" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\Version] @="1.0" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID] @="FlashFactory.FlashFactory" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}] @Denied: (A 2) (Everyone) @="IFlashBroker4" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\ProxyStubClsid32] @="{00020424-0000-0000-C000-000000000046}" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\TypeLib] @="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}" "Version"="1.0" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\TypeLib\{D27CDB6B-AE6D-11CF-96B8-444553540000}] @Denied: (A 2) (Everyone) . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\TypeLib\{D27CDB6B-AE6D-11CF-96B8-444553540000}\1.0] @="Shockwave Flash" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\TypeLib\{FAB3E735-69C7-453B-A446-B6823C6DF1C9}] @Denied: (A 2) (Everyone) @="" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\TypeLib\{FAB3E735-69C7-453B-A446-B6823C6DF1C9}\1.0] @="FlashBroker" . [HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Classes] "SymbolicLinkValue"=hex(6):5c,00,52,00,45,00,47,00,49,00,53,00,54,00,52,00,59, 00,5c,00,4d,00,41,00,43,00,48,00,49,00,4e,00,45,00,5c,00,53,00,4f,00,46,00,\ . [HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Office\Common\Smart Tag\Actions\{B9A09F18-45AB-4F09-A117-A4ADDA8FA8C8}] @Denied: (A) (Everyone) "Solution"="{36eb6792-3a29-43b3-8cd0-f67d266fb426}" . [HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Schema Library\ActionsPane] @Denied: (A) (Everyone) . [HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Schema Library\ActionsPane\0] "Key"="ActionsPane" "Location"="c:\\Program Files (x86)\\Common Files\\Microsoft Shared\\VSTO\\8.0\\ActionsPane.xsd" . [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0000\AllUserSettings] @Denied: (A) (Users) @Denied: (A) (Everyone) @Allowed: (B 1 2 3 4 5) (S-1-5-20) "BlindDial"=dword:00000000 . ———————— Other Running Processes ———————— . c:\program files (x86)\Lavasoft\Ad-Aware\AAWService.exe c:\program files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe c:\windows\SysWOW64\atashost.exe c:\windows\twain_32\fjscan32\FJTWMKSV.exe c:\program files (x86)\Common Files\InterVideo\RegMgr\iviRegMgr.exe c:\program files (x86)\Common Files\Intuit\QuickBooks\QBCFMonitorService.exe c:\program files (x86)\Common Files\Intuit\DataProtect\QBIDPService.exe c:\program files (x86)\TeamViewer\Version5\TeamViewer_Service.exe c:\program files (x86)\ArcSoft\Magic-i Visual Effects 2\uCamMonitor.exe c:\program files (x86)\Sony\VAIO Event Service\VESMgr.exe c:\windows\SysWOW64\DllHost.exe c:\program files (x86)\Common Files\Sony Shared\VAIO Content Folder Watcher\VCFw.exe c:\program files (x86)\Common Files\Sony Shared\VAIO Entertainment Platform\VzCdb\VzCdbSvc.exe c:\program files (x86)\RealVNC\VNC4\WinVNC4.exe c:\program files (x86)\Common Files\Pure Networks Shared\Platform\nmsrvc.exe c:\program files (x86)\Sony\VAIO Event Service\VESMgrSub.exe c:\windows\SysWOW64\DllHost.exe c:\program files (x86)\Common Files\Sony Shared\VAIO Entertainment Platform\VCSW\VCSW.exe c:\program files\Sony\VAIO Care\listener.exe c:\program files (x86)\TeamViewer\Version5\TeamViewer.exe c:\program files (x86)\Lavasoft\Ad-Aware\AAWTray.exe c:\progra~2\Intuit\QUICKB~2\QBDBMgrN.exe . ************************************************************************** . Completion time: 2012-05-10 15:46:48 - machine was rebooted ComboFix-quarantined-files.txt 2012-05-10 19:46 ComboFix2.txt 2011-12-19 20:56 . Pre-Run: 194,654,629,888 bytes free Post-Run: 194,814,980,096 bytes free . - - End Of File - - 1234E33DCCA7E4F9005872E2A1B407BD
Hi,
  • Please open Notepad (Start -> Run -> type notepad in the Open field -> OK) and copy and paste the text present inside the code box below:
    ClearJavaCache::
    
    DDS::
    uStart Page = hxxp://employeeweb.katsur.com/
    mStart Page = hxxp://www.google.com/ig/redirectdomain?brand=SNYR&bmod=SNYR
    Hosts: 216.240.133.193 www.google-analytics.com.
    Hosts: 216.240.133.193 ad-emea.doubleclick.net.
    Hosts: 216.240.133.193 www.statcounter.com.
    Hosts: 69.72.252.254 www.google-analytics.com.
    Hosts: 69.72.252.254 ad-emea.doubleclick.net.
    Hosts: 216.240.133.193 www.google-analytics.com.
    Hosts: 216.240.133.193 ad-emea.doubleclick.net.
    Hosts: 216.240.133.193 www.statcounter.com.
    Hosts: 69.72.252.254 www.google-analytics.com.
    Hosts: 69.72.252.254 ad-emea.doubleclick.net.
    Hosts: 69.72.252.254 www.statcounter.com.
    
    RegLock::
    [HKEY_USERS\.Default\Software\Microsoft\Internet Explorer\User Preferences]
    [HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Office\Common\Smart Tag\Actions\{B9A09F18-45AB-4F09-A117-A4ADDA8FA8C8}]
    [HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Schema Library\ActionsPane]
    [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0000\AllUserSettings]
  • Save this as CFScript.txt and change the "Save as type" to "All Files" and place it on your desktop.

    [external image: Posted Image]
  • Very Important! Temporarily disable your anti-virus, script blocking and any anti-malware real-time protection before following the steps below. They can interfere with ComboFix or remove some of its embedded files which may cause "unpredictable results".
  • Referring to the screenshot above, drag CFScript.txt into ComboFix.exe.
  • ComboFix will now run a scan on your system. It may reboot your system when it finishes. This is normal.
  • When finished, it shall produce a log for you. Copy and paste the contents of the log in your next reply.
CAUTION: Do not mouse-click ComboFix's window while it is running. That may cause it to stall.
———-
Done, here is the new log: ComboFix 12-05-11.02 - josh 05/11/2012 8:00.4.2 - x64 Microsoft® Windows Vista™ Home Premium 6.0.6002.2.1252.44.1033.18.3900.2081 [GMT -4:00] Running from: c:\users\[removed]\Desktop\ComboFix.exe Command switches used :: c:\users\josh\Desktop\CFScript.txt SP: Windows Defender *Disabled/Updated* {D68DDC3A-831F-4fae-9E44-DA132C1ACF46} . . ((((((((((((((((((((((((( Files Created from 2012-04-11 to 2012-05-11 ))))))))))))))))))))))))))))))) . . 2012-05-11 12:06 . 2012-05-11 12:06 ——– d—–w- c:\users\QBDataServiceUser18\AppData\Local\temp 2012-05-11 12:06 . 2012-05-11 12:06 ——– d—–w- c:\users\Public\AppData\Local\temp 2012-05-11 12:06 . 2012-05-11 12:06 ——– d—–w- c:\users\josh\AppData\Local\temp 2012-05-11 12:06 . 2012-05-11 12:06 ——– d—–w- c:\users\Default\AppData\Local\temp 2012-05-04 11:57 . 2012-05-04 11:57 ——– d—–w- c:\program files (x86)\Mozilla Maintenance Service 2012-05-04 11:57 . 2012-05-04 11:57 157352 —-a-w- c:\program files (x86)\Mozilla Firefox\maintenanceservice_installer.exe 2012-05-04 11:57 . 2012-05-04 11:57 129976 —-a-w- c:\program files (x86)\Mozilla Firefox\maintenanceservice.exe 2012-04-12 07:05 . 2012-03-06 06:44 4699520 —-a-w- c:\windows\system32\ntoskrnl.exe 2012-04-12 07:05 . 2012-02-29 15:37 5632 —-a-w- c:\windows\system32\wmi.dll 2012-04-12 07:05 . 2012-02-29 15:37 219136 —-a-w- c:\windows\system32\wintrust.dll 2012-04-12 07:05 . 2012-02-29 15:35 78848 —-a-w- c:\windows\system32\imagehlp.dll 2012-04-12 07:05 . 2012-02-29 15:11 5120 —-a-w- c:\windows\SysWow64\wmi.dll 2012-04-12 07:05 . 2012-02-29 15:11 172032 —-a-w- c:\windows\SysWow64\wintrust.dll 2012-04-12 07:05 . 2012-02-29 15:09 157696 —-a-w- c:\windows\SysWow64\imagehlp.dll 2012-04-12 07:05 . 2012-02-29 13:52 16384 —-a-w- c:\windows\system32\drivers\fs_rec.sys 2012-04-11 12:47 . 2012-03-01 11:01 2409784 —-a-w- c:\program files (x86)\Windows Mail\OESpamFilter.dat 2012-04-11 12:47 . 2012-03-01 11:01 2409784 —-a-w- c:\program files\Windows Mail\OESpamFilter.dat . . . (((((((((((((((((((((((((((((((((((((((( Find3M Report )))))))))))))))))))))))))))))))))))))))))))))))))))) . 2012-04-09 12:41 . 2010-12-20 17:00 472808 —-a-w- c:\windows\SysWow64\deployJava1.dll 2012-04-04 19:56 . 2011-02-08 14:06 24904 —-a-w- c:\windows\system32\drivers\mbam.sys 2012-02-23 14:18 . 2010-12-22 12:59 279656 ——w- c:\windows\system32\MpSigStub.exe 2012-02-14 16:49 . 2012-03-14 09:10 327680 —-a-w- c:\windows\system32\d3d10_1core.dll 2012-02-14 16:49 . 2012-03-14 09:10 196096 —-a-w- c:\windows\system32\d3d10_1.dll 2012-02-14 15:45 . 2012-03-14 09:10 219648 —-a-w- c:\windows\SysWow64\d3d10_1core.dll 2012-02-14 15:45 . 2012-03-14 09:10 160768 —-a-w- c:\windows\SysWow64\d3d10_1.dll 2012-02-13 14:38 . 2012-03-14 09:10 2002944 —-a-w- c:\windows\system32\d3d10warp.dll 2012-02-13 14:12 . 2012-03-14 09:10 1172480 —-a-w- c:\windows\SysWow64\d3d10warp.dll 2012-02-13 14:06 . 2012-03-14 09:10 834048 —-a-w- c:\windows\system32\d2d1.dll 2012-02-13 14:03 . 2012-03-14 09:10 1555968 —-a-w- c:\windows\system32\DWrite.dll 2012-02-13 13:47 . 2012-03-14 09:10 683008 —-a-w- c:\windows\SysWow64\d2d1.dll 2012-02-13 13:44 . 2012-03-14 09:10 1068544 —-a-w- c:\windows\SysWow64\DWrite.dll . . ((((((((((((((((((((((((((((( SnapShot@2012-05-10_19.39.21 ))))))))))))))))))))))))))))))))))))))))) . + 2009-10-05 18:16 . 2012-05-11 11:51 354804 c:\windows\system32\WDI\SuspendPerformanceDiagnostics_SystemData_FastS4.bin + 2006-11-02 12:33 . 2012-05-11 11:51 11010048 c:\windows\system32\SMI\Store\Machine\SCHEMA.DAT - 2006-11-02 12:33 . 2012-05-10 18:10 11010048 c:\windows\system32\SMI\Store\Machine\SCHEMA.DAT + 2012-05-11 11:59 . 2012-05-11 11:59 10952704 c:\windows\ERDNT\Hiv-backup\SCHEMA.DAT . ((((((((((((((((((((((((((((((((((((( Reg Loading Points )))))))))))))))))))))))))))))))))))))))))))))))))) . . *Note* empty entries & legit default entries are not shown REGEDIT4 . [HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt1] @="{FB314ED9-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314ED9-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 94208 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt.14.dll . [HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt2] @="{FB314EDA-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314EDA-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 94208 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt.14.dll . [HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt3] @="{FB314EDB-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314EDB-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 94208 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt.14.dll . [HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "swg"="c:\program files (x86)\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe" [2008-10-23 39408] . [HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run] "Intuit SyncManager"="c:\program files (x86)\Common Files\Intuit\Sync\IntuitSyncManager.exe" [2011-06-14 1527128] "VWLASU"="c:\program files\Sony\VAIO Wireless Wizard\AutoLaunchWLASU.exe" [2008-05-20 24576] "FtLnSOP_setup"="c:\windows\Twain_32\Fjscan32\SOP\FtLnSOP.exe" [2007-03-08 212992] "FJTWAIN Setup"="c:\windows\Twain_32\fjscan32\FjtwMkup.exe" [2007-03-08 131072] "HP Software Update"="c:\program files (x86)\HP\HP Software Update\HPWuSchd2.exe" [2007-03-12 49152] "HPUsageTracking"="c:\program files (x86)\HP\HP UT\bin\hppusg.exe" [2007-05-08 36864] "nmctxth"="c:\program files (x86)\Common Files\Pure Networks Shared\Platform\nmctxth.exe" [2009-04-07 642856] "Adobe ARM"="c:\program files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe" [2012-01-03 843712] "APSDaemon"="c:\program files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe" [2011-11-02 59240] "QuickTime Task"="c:\program files (x86)\QuickTime\QTTask.exe" [2011-10-24 421888] "iTunesHelper"="c:\program files (x86)\iTunes\iTunesHelper.exe" [2011-12-08 421736] "SunJavaUpdateSched"="c:\program files (x86)\Common Files\Java\Java Update\jusched.exe" [2012-01-18 254696] . c:\users\josh\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\ Dropbox.lnk - c:\users\josh\AppData\Roaming\Dropbox\bin\Dropbox.exe [2012-2-14 24246216] . c:\programdata\Microsoft\Windows\Start Menu\Programs\Startup\ HP Digital Imaging Monitor.lnk - c:\program files (x86)\HP\Digital Imaging\bin\hpqtra08.exe [2007-3-11 210520] Intuit Data Protect.lnk - c:\program files (x86)\Common Files\Intuit\DataProtect\IntuitDataProtect.exe [2010-12-2 5842776] QuickBooks Update Agent.lnk - c:\program files (x86)\Common Files\Intuit\QuickBooks\QBUpdate\qbupdate.exe [2011-7-6 1156968] QuickBooks_Standard_21.lnk - c:\program files (x86)\Intuit\QuickBooks 2008\QBW32.EXE [2011-7-6 1178984] ScanSnap Manager.lnk - c:\program files (x86)\PFU\ScanSnap\Driver\PfuSsMon.exe [2010-12-21 1146880] . [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\policies\system] "EnableUIADesktopToggle"= 0 (0x0) . [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\VESWinlogon] 2008-11-06 01:32 98304 —-a-w- c:\windows\System32\VESWinlogon.dll . [HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Lavasoft Ad-Aware Service] @="Service" . S2 AdobeARMservice;Adobe Acrobat Update Service;c:\program files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [2012-01-03 63928] . . — Other Services/Drivers In Memory — . *NewlyCreated* - WS2IFSL . [HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\windows nt\currentversion\svchost] hpdevmgmt REG_MULTI_SZ hpqcxs08 hpqddsvc . Contents of the 'Scheduled Tasks' folder . 2012-05-10 c:\windows\Tasks\GoogleUpdateTaskMachineCore.job - c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-02-02 16:55] . 2012-05-11 c:\windows\Tasks\GoogleUpdateTaskMachineUA.job - c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-02-02 16:55] . . ——— x86-64 ———– . . [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt1] @="{FB314ED9-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314ED9-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 97792 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt64.14.dll . [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt2] @="{FB314EDA-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314EDA-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 97792 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt64.14.dll . [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt3] @="{FB314EDB-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314EDB-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 97792 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt64.14.dll . [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\DropboxExt4] @="{FB314EDC-A251-47B7-93E1-CDD82E34AF8B}" [HKEY_CLASSES_ROOT\CLSID\{FB314EDC-A251-47B7-93E1-CDD82E34AF8B}] 2011-02-18 05:12 97792 —-a-w- c:\users\josh\AppData\Roaming\Dropbox\bin\DropboxExt64.14.dll . [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "RtHDVCpl"="RAVCpl64.exe" [2008-11-12 6407200] "Skytel"="Skytel.exe" [2008-11-12 1826816] "IgfxTray"="c:\windows\system32\igfxtray.exe" [2008-09-17 151064] "HotKeysCmds"="c:\windows\system32\hkcmd.exe" [2008-09-17 209432] "Persistence"="c:\windows\system32\igfxpers.exe" [2008-09-17 182808] "NvCplDaemon"="c:\windows\system32\NvCpl.dll" [2008-10-31 15880224] "NvMediaCenter"="c:\windows\system32\NvMcTray.dll" [2008-10-31 82464] . ——- Supplementary Scan ——- . uLocal Page = c:\windows\system32\blank.htm mLocal Page = c:\windows\SysWOW64\blank.htm uInternet Settings,ProxyOverride = *.local IE: E&xport to Microsoft Excel - c:\progra~2\MICROS~2\Office12\EXCEL.EXE/3000 IE: Send image to &Bluetooth Device… - c:\program files\WIDCOMM\Bluetooth Software\btsendto_ie_ctx.htm IE: Send page to &Bluetooth Device… - c:\program files\WIDCOMM\Bluetooth Software\btsendto_ie.htm TCP: DhcpNameServer = 192.168.1.150 CLSID: {603d3801-bd81-11d0-a3a5-00c04fd706ec} - %SystemRoot%\SysWow64\browseui.dll FF - ProfilePath - c:\users\josh\AppData\Roaming\Mozilla\Firefox\Profiles\odt38dqd.default\ . . [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\SampleCollector] "ImagePath"="\"c:\program files\Sony\VAIO Care\collsvc.exe\" \"/service\" \"/counter=\Processor(_Total)\% Processor Time:5\" \"/counter=\PhysicalDisk(_Total)\Disk Bytes/sec:5\" \"/counter=\Network Interface(*)\Bytes Total/sec:5\" \"/directory=inteldata\"" . ——————— LOCKED REGISTRY KEYS ——————— . [HKEY_USERS\.Default\Software\Microsoft\Internet Explorer\Approved Extensions] @Denied: (2) (LocalSystem) "{2318C2B1-4965-11D4-9B18-009027A5CD4F}"=hex:51,66,7a,6c,4c,1d,38,12,df,c1,0b, 27,57,07,ba,54,e4,0e,43,d0,22,fb,89,5b "{18DF081C-E8AD-4283-A596-FA578C2EBDC3}"=hex:51,66,7a,6c,4c,1d,38,12,72,0b,cc, 1c,9f,a6,ed,07,da,80,b9,17,89,70,f9,d7 "{761497BB-D6F0-462C-B6EB-D4DAF1D92D43}"=hex:51,66,7a,6c,4c,1d,38,12,d5,94,07, 72,c2,98,42,03,c9,fd,97,9a,f4,87,69,57 "{AA58ED58-01DD-4D91-8333-CF10577473F7}"=hex:51,66,7a,6c,4c,1d,38,12,36,ee,4b, ae,ef,4f,ff,08,fc,25,8c,50,52,2a,37,e3 "{DBC80044-A445-435B-BC74-9C25C1C588A9}"=hex:51,66,7a,6c,4c,1d,38,12,2a,03,db, df,77,ea,35,06,c3,62,df,65,c4,9b,cc,bd "{FF059E31-CC5A-4E2E-BF3B-96E929D65503}"=hex:51,66,7a,6c,4c,1d,38,12,5f,9d,16, fb,68,82,40,0b,c0,2d,d5,a9,2c,88,11,17 "{BDEADE7F-C265-11D0-BCED-00A0C90AB50F}"=hex:51,66,7a,6c,4c,1d,38,12,11,dd,f9, b9,57,8c,be,54,c3,fb,43,e0,cc,54,f1,1b . [HKEY_USERS\.Default\Software\Microsoft\Internet Explorer\ApprovedExtensionsMigration] @Denied: (2) (LocalSystem) "Timestamp"=hex:2d,d9,12,03,06,bc,cc,01 . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}] @Denied: (A 2) (Everyone) @="FlashBroker" "LocalizedString"="@c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil11e_ActiveX.exe,-101" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\Elevation] "Enabled"=dword:00000001 . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\LocalServer32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil11e_ActiveX.exe" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\TypeLib] @="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}] @Denied: (A 2) (Everyone) @="Shockwave Flash Object" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\InprocServer32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash11e.ocx" "ThreadingModel"="Apartment" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\MiscStatus] @="0" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ProgID] @="ShockwaveFlash.ShockwaveFlash.10" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash11e.ocx, 1" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\TypeLib] @="{D27CDB6B-AE6D-11cf-96B8-444553540000}" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\Version] @="1.0" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID] @="ShockwaveFlash.ShockwaveFlash" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}] @Denied: (A 2) (Everyone) @="Macromedia Flash Factory Object" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\InprocServer32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash11e.ocx" "ThreadingModel"="Apartment" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ProgID] @="FlashFactory.FlashFactory.1" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash11e.ocx, 1" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\TypeLib] @="{D27CDB6B-AE6D-11cf-96B8-444553540000}" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\Version] @="1.0" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID] @="FlashFactory.FlashFactory" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}] @Denied: (A 2) (Everyone) @="IFlashBroker4" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\ProxyStubClsid32] @="{00020424-0000-0000-C000-000000000046}" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\TypeLib] @="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}" "Version"="1.0" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\TypeLib\{D27CDB6B-AE6D-11CF-96B8-444553540000}] @Denied: (A 2) (Everyone) . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\TypeLib\{D27CDB6B-AE6D-11CF-96B8-444553540000}\1.0] @="Shockwave Flash" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\TypeLib\{FAB3E735-69C7-453B-A446-B6823C6DF1C9}] @Denied: (A 2) (Everyone) @="" . [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\TypeLib\{FAB3E735-69C7-453B-A446-B6823C6DF1C9}\1.0] @="FlashBroker" . [HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Classes] "SymbolicLinkValue"=hex(6):5c,00,52,00,45,00,47,00,49,00,53,00,54,00,52,00,59, 00,5c,00,4d,00,41,00,43,00,48,00,49,00,4e,00,45,00,5c,00,53,00,4f,00,46,00,\ . Completion time: 2012-05-11 08:09:26 ComboFix-quarantined-files.txt 2012-05-11 12:09 ComboFix2.txt 2012-05-10 19:46 ComboFix3.txt 2011-12-19 20:56 . Pre-Run: 194,339,921,920 bytes free Post-Run: 194,306,535,424 bytes free . - - End Of File - - 98FD4ED3B3D4E46C19A8DF0D7B555234
Hi,

Yep…that is looking better. :) Let's check for anything else hiding.

Malwarebytes

I see that you have Malwarebytes already on your computer. Please open Malwarebytes, update it and then run a Quick Scan. Save the log that is created for your next reply.
———-

ESET Online Scanner
I'd like us to scan your machine with ESET Online Scan

Note: It is recommended to disable on-board anti-virus program and anti-spyware programs while performing scans so there are no conflicts and it will speed up scan time.
Please don't go surfing while your resident protection is disabled!
Once the scan is finished remember to re-enable your anti-virus along with your anti-spyware programs.


As a Vista/Win7 user you will need to right click your browser icon and select "Run as Administrator" in order to run this scan.
  • Do not use this instance of your browser for anything besides doing this scan
  • When the scan is complete and the results saved, close that instance of your browser
  • Open a new one the usual way and post the results in this topic.


  • Right-click and Run as Administartor on the following link to open ESET OnlineScan in a new window.
    ESET OnlineScan
  • Click the [external image: Posted Image] button.
  • For alternate browsers only: (Microsoft Internet Explorer users can skip these steps)
    • Click on [external image: Posted Image] to download the ESET Smart Installer. Save it to your desktop.
    • Double click on the [external image: Posted Image] icon on your desktop.
  • Check [external image: Posted Image]
  • Click the Start button.
  • Accept any security warnings from your browser.
  • Check [external image: Posted Image]
  • Make sure that the option "Remove found threats" is Unchecked
  • Push the Start button.
  • ESET will then download updates for itself, install itself, and begin
    scanning your computer. Please be patient as this can take some time.
  • When the scan completes, push [external image: Posted Image]
  • Push [external image: Posted Image], and save the file to your desktop using a unique name, such as
    ESETScan. Include the contents of this report in your next reply.
  • Push the Back button.
  • Push Finish
http://www.eset.com/onlinescan/
———-

In your next reply please post the logs made by Malwarebytes and ESET online scanner. :)
Apparently I messed something up with the ESET scanner because I didn't see a log. I did get a confirmation message that no threats were found. Here is the Malwarebytes log Malwarebytes Anti-Malware 1.61.0.1400 www.malwarebytes.org Database version: v2012.05.08.09 Windows Vista Service Pack 2 x64 NTFS Internet Explorer 9.0.8112.16421 josh :: JOSH-PC [administrator] 5/11/2012 1:44:52 PM mbam-log-2012-05-11 (13-44-52).txt Scan type: Quick scan Scan options enabled: Memory | Startup | Registry | File System | Heuristics/Extra | Heuristics/Shuriken | PUP | PUM Scan options disabled: P2P Objects scanned: 227013 Time elapsed: 2 minute(s), 22 second(s) Memory Processes Detected: 0 (No malicious items detected) Memory Modules Detected: 0 (No malicious items detected) Registry Keys Detected: 0 (No malicious items detected) Registry Values Detected: 0 (No malicious items detected) Registry Data Items Detected: 0 (No malicious items detected) Folders Detected: 0 (No malicious items detected) Files Detected: 0 (No malicious items detected) (end) Let me know if you want me to re-run ESET.

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI