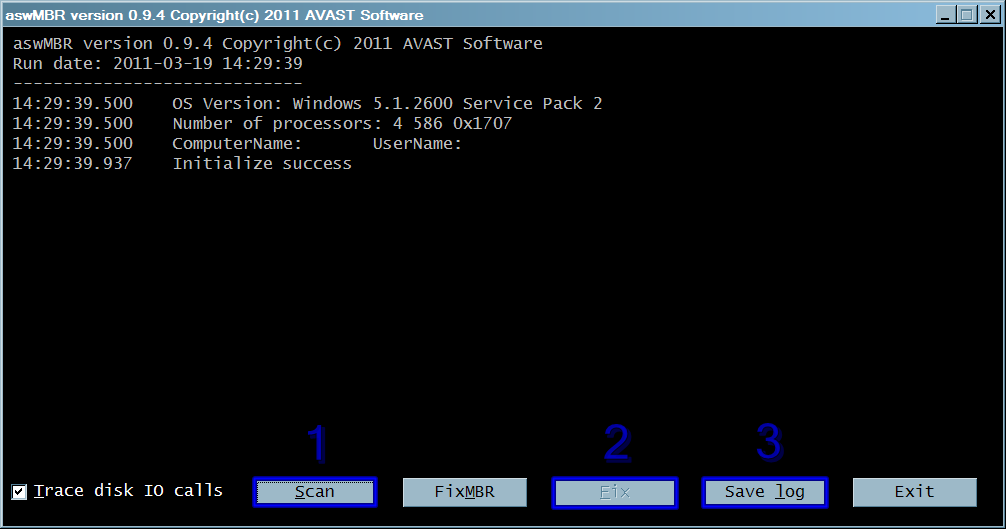
I found this in my C drive. Is this what you were looking for yesterday when I did the scan?
WPI Installation Log File
Install process started at: Monday, June 06, 2011 4:53:21 PM
WPI information:
Version=7.7.0
Internet Explorer version=8.0
Internet Connection=false
Operating System
Operating System=Win7
Edition ID=Not found
Service Pack=0
Architecture
Architecture Name=GenuineIntel
Architecture Name String=Intel® Core™ i5 CPU 760 @ 2.80GHz
Architecture ID=Intel64 Family 6 Model 30 Stepping 5
Number Of Processors=4
MHz=2793
Architecture Type=x86
SysArch6432=AMD64
Architecture Bits=64
True 64 Bits=false
Options file=D:\WPI\WPIScripts\useroptions.js
Config file=D:\WPI\WPIScripts\config.js
// Window tab
Resolution=1024
MainWindowWidth=800
MainWindowHeight=600
MainWindowX=-1
MainWindowY=-1
InstallerWindowX=25
InstallerWindowY=25
// Interface tab
ShowToolTips=true
UseTransitions=false
IndentText=false
// Style tab
Theme='Windows'
BgPicture=''
// General tab
Configurations=['']
ShowMultiDefault=true
CheckOnLoad='default'
NumCols=2
// —
SortOrder=['']
// —
Timer=false
Seconds=60
StartBeepAtSecs=10
// —
ShowExtraButtons=true
DoNotShowIfCD=true
USSFSilentMode=false
VerifyInstallHDD=false
AllowCheckForInternet=false
LoadDesktopBeforeInstall=false
ReOpenAfterInstall=false
DisableCatCheckBoxes=false
SortWithinCats=false
DisableOnDepsNotMet=true
AlwaysUseScrollBar=true
DontSplitCats=true
InstallByCategory=true
ReallyForce=false
DisableIfDoGray=false
InstallFonts=false
ShowCommandInInstaller=true
// —
DefaultInstallPath='default'
CustomInstallPath=['']
// —
Language='en'
// Audio tab
PlayAudioInInstaller=false
InstallAudio=['5080.wav']
Volume=75
Shuffle=false
CopyAudioFolder=false
CopyAudioPath=['%systemdrive%\WPI_Audio']
DeleteAudioFolder=false
// Tools tab
MonitorResolution=0
MonitorDepth=0
MonitorRefresh=0
// —
ExecuteBeforeEnabled=false
ExecuteBeforebit4=false
ExecuteBefore=['']
ExecuteAfterEnabled=false
ExecuteAfterbit64=false
ExecuteAfter=['']
// —
RestartComputer=false
RestartType=0
RestartSeconds=30
DoNotLoadDesktop=true
// —
LogInstallation=true
LogPath=['%systemdrive%\WPI_Log.txt'];
TimeStampLogFile=true
// Sounds tab
SndWPIStartCB=false
SndWPIStart=['"%wpipath%\Audio\SoundsScheme\Alert.wav"'];
SndInstallStartCB=false
SndInstallStart=['"%wpipath%\Audio\SoundsScheme\AtBeginning.wav"'];
SndInstallSuccessCB=false
SndInstallSuccess=['"%wpipath%\Audio\SoundsScheme\Yes.wav"'];
SndInstallFailCB=false
SndInstallFail=['"%wpipath%\Audio\SoundsScheme\No.wav"'];
SndInstallFinishCB=false
SndInstallFinish=['"%wpipath%\Audio\SoundsScheme\AtEnd.wav"'];
Global variables:
%OSLANG%=ENU
%WPIPATH%=D:\WPI
%ROOT%=D:
%CDROM%=D:
%DOSPATH%=
%SYSTEMDRIVE%=C:
%WINDIR%=C:\Windows
%PROGRAMFILES%=C:\Program Files (x86)
%TEMP%=C:\Users\SMOOTH~1\AppData\Local\Temp
%SYSDIR%=C:\Windows\System32
%ALLUSERSPROFILE%=C:\ProgramData
%USERPROFILE%=C:\Users\Smooth_Top
%APPDATA%=C:\Users\Smooth_Top\AppData\Roaming
%COMMONPROGRAMFILES%=C:\Program Files (x86)\Common Files
List of programs to be installed:
Add Administrative Tools
Add Advanced System Properties
Add Appearance
Add Change Cursor
Add Change Date and Time
Add Change Regional Settings
Add Change Screen Saver
Add Change Sound
Add Change Theme
Add Change Wallpaper
Add Desktop Icons Settings
Add Device Manager
Add DPI Scaling
Add Empty Recycle Bin option
Add Folder Options
Add Fonts
Add Internet Options
Add Network Connections
add open with notepad
Add Power Options
Add Printers
Add Search option
Add Programs and Features
Add Registry Editor
Add Run option
Add Security Center
Add Task Manager
Add Task Scheduler
Add Turn Firewall On or Off
Add User Accounts
Add User Accounts Classic
Add Window Colorization
Add Classic System Properties Option
Add MSCONFIG
Advanced user accounts
Aero Controller 1.2 disable aero interface
Aero PowerShell makes windows powershell glass
Aero PowerShell disable
Aero Shake Disables aero shake
Aero Shake enable
Aero Cmd Glass
Aero Cmd glass disable
Auto Restart Shell
Auto Restart Shell disable
BootOptimize
BootOptimize disable
Add copy to move to
Restore the language bar
Desktop and Shutdown
Disable Administrative Shares
Disable automatic reboot when BSOD
Disable automatic updates
Disable file association web service
Disable grouping of system tray icons
Disable Hibernate
Disable Remote Registry
Disable the NTFS Last Access Time Stamp
Disable Tracking of Broken Shortcut Links
Disable UAC notify
Disable User Account Control UAC
Disable Web Services
Disable 'Windows Defender startup
Disable Windows Media Player AutoUpdates
Enable Libraries in Windows 7
DisableDEP
Enable DEP
Disable IPv6
Enable IPv6
DisableLastAccess
Enable last Access
Disable Teredo proxy speedup internet
EnableTeredo
Disable Low disc space check
Enable low disc space check
Do not Use large icons on Start Menu
Dont mark new applications
Disable Dr Watson Disable kernel debugger
Enable DR watson
Empty RecycleBin right click
Empty Folder right click
Disable empty folder
Enable addition Avalon effects
Enable DVD in Media Player Value Yes
Enable Glass Effect (DWM) without a supported card
Enable MP3 Encoding from right-click while browsing
Enable slow-motion window effects min max 3dflip by holding down Shift key
Enable Status Bar in all windows
Enable Status bar in Notepad
Explorer settings
Place Flip 3d in context menu
Disable Flip 3d context menu
get rid of the Windows Mail splash screen
give your self permission to modify and all
Remove obsolete icon elements in the system tray
Increase the priority of interrupts IRQ8 (increases the speed of the system)
Streamline (increase) system cache. Include only if volume more than 1GB of memory
Disable large system cache
Make the text white in command windows
Make the Windows registration with Microsoft unnecessary
Makes a right click option for unknown files Open with notepad
Mice settings
Microsoft Update settings
Mouse Hover Time Speed
Disable Mouse hover time speed
MSN settings
My Computer Context Menu
Do not send to Microsoft error reporting
enable send to Microsoft error reporting
Do not add "Shortcut to when creating new shortcuts
Disable No Shortcut
Notepad saves window position
Open in New Window
option in the right-click menu to open any folder on your computer in a new window
Leaving the system kernel in memory (not to throw in the paging file is disabled by default)
Paging executive disable
Enable Paging excutive
Policies
Remove- Shortcut Suffix from shortcuts
Prefetch automatic
Prefetch manual
Prefetch disable
Reg Edit Device Manager Control Panel LogOff Reboo Shutdown to my computer
Register DLL OCX AX
Add Run to context menu
Scandisk Reduce the time to start the disk check at system startup Scandisk to 5 seconds
Scandisk back to default
Set Control Panel on Classic View and small icons
SFC Scan
Show all hidden devices in device manager
Show the full path in minimized explorer windows
Show Windows classic folders
Sidebar settings
SmartClick Allows you to put in the context menu of any program or folder
Speed up shell response
Speed-up Access to AVI Media Files
Show hidden files
Disable Show Hidden Files
Taskbar Jumplist
Disable taskbar Jumplist
Thumbnail Cache Disable caching of images
Enable Thumbnail Cache
turn off start menu baloon tips
UAC OFF
Enable UAC
Accelerate Download and Upload. It speeds up the network and the Internet
Disable Accelerate Download and Upload. It speeds up the network and the Internet
Allows you to connect and disconnect virtual VHD-drives
VirusTotal Uploader
Uninstall Virustotal Uploader
Window Switcher
Logon Background Changer 1.3.4
Calendar from the Windows Vista
Universal TCPIP Patcher x64
7 Stacks
Logon Screen Rotator
Adds All The My Computer Right Click Apps. with icon
Adds the creation of Batch .cmd file types to New Menu Right Click
Adds Windows Switch 3D Flip
Disable Action Center
Disable Auto Play
Open NFO files with notepad
Remove Libraries Icon from Windows 7 Explorer
Show hidden files and folders (but not hidden system files and folders
Shows file extensions
Stop start aero
Take Ownership with icon
Underline letters on right click
Universal take Ownership
Unlock the taskbar
20 ms Mouse Hover Time
500ms Delay Aero Peek
Add Copy File List Clipboard
Add Admin Auto Hotkey
Add 'Control Panel' Option
Add Copy Contents To ClipboardTXT
Add Copy To
Add 'Event Viewer' Option
Add God Mode in Bottom of Desktop Context Menu
Add God Mode in Desktop Context Menu
Add God Mode in Top of Desktop Context Menu
Add Hide File
Add Move To
Add Name In Context Menu
Add new CMD file to right click
add program and features in right click of computer icon
Add 'Programs' Option
Add register unregister to the context menu for .dll files
Add 'Registry Editor' Option
Add Remove Admin Auto Hotkey
Add Remove Copy Contents To Clipboard
Add Remove Options
Add Remove Run option
Add Remove Search Option
Add 'Services' Option
Add 'Task Manager' Option
Add Unhide File
All items have an edit on right-click sending to notepad
Allow renaming and removing of Recycle Bin
Allows installing PlexTools Upgrade as full version
Cache more Icons
Change the Clock to 24 Hour time format
Default Value Aero Peek
Disable Aero Shake
Disable Autorun
Disable Default Hidden Shares
Disable kernel paging Optimize Core System Performance
disable usb message This device can perform faster
Disable window animations on minimize maximize
Disables Preview of Movie file formats (allowing you to move rename delete without errors)
Do not allow Windows to turn off Network Adapters
Do not save encrypted pages to disk
Do not show 'Default Programs' on Start Menu
Do not show Devices and Printers on Start Menu
Do not show 'Games' on Start Menu
Do not show 'Help and Support' on Start Menu
Enable Aero Shake
Enable Dreamscene In Windows 7
Enable Tools Folder Options
Force keep positive entries in DNS Cache for only 4 hours instead of the default 24 hours
If an Administrator attempts a protected action - Silently Succeed
Increase Network Throughput
Increase RPC Packet Size
Kill hung services after 5 seconds
Libraries Restore Default Settings
Logon Screen Text Default
Logon Screen Text no shadow
Logon Screen Text shadow
Open HTA files (used for WPI) with MSHTA.EXE
Remove Open With Notepad
Remove Options
Remove 'Recent Items' from Start Menu
Remove Send Feedback
Remove warning about showing hidden system folders
Remove File List Clipboard
restore mouse hover time to default
Show Encryption Commands on the Shortcut Menu
Show the real CD-recording speed in Nero
Stop caching negative responses
Turn off system beeps
Type Long File Names In DOS
Uninstall 'Control Panel' Option
Uninstall 'Device Manager' Option
Uninstall 'Event Viewer' Option
Uninstall god mode
Uninstall 'MSConfig' Option
Uninstall 'Programs' Option
Uninstall 'Registry Editor' Option
Uninstall 'Services' Option
Uninstall 'Task Manager' Option
Use SSL 2.0 (Checked) + SSL 3.0 (Checked) + TSL 1.0 (unchecked)
Windows will tell you exactly what it is doing when it is shutting down or is booting
251 Items, 251 Commands
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Administrative Tools
Unique ID: ADDADMINISTRATIVETOOLS
Order: 900001
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Advanced System Properties
Unique ID: ADDADVANCEDSYSTEMPROPERTI
Order: 900002
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Appearance
Unique ID: ADDAPPEARANCE
Order: 900003
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Change Cursor
Unique ID: ADDCHANGECURSOR
Order: 900004
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Change Date and Time
Unique ID: ADDCHANGEDATEANDTIME
Order: 900005
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Change Regional Settings
Unique ID: ADDCHANGEREGIONALSETTINGS
Order: 900006
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Change Screen Saver
Unique ID: ADDCHANGESCREENSAVER
Order: 900007
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Change Sound
Unique ID: ADDCHANGESOUND
Order: 900008
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Change Theme
Unique ID: ADDCHANGETHEME
Order: 900009
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Change Wallpaper
Unique ID: ADDCHANGEWALLPAPER
Order: 900010
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Desktop Icons Settings
Unique ID: ADDDESKTOPICONSSETTINGS
Order: 900011
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Device Manager
Unique ID: ADDDEVICEMANAGER
Order: 900012
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add DPI Scaling
Unique ID: ADDDPISCALING
Order: 900013
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Empty Recycle Bin option
Unique ID: ADDEMPTYRECYCLEBINOPTION
Order: 900014
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Folder Options
Unique ID: ADDFOLDEROPTIONS
Order: 900015
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Fonts
Unique ID: ADDFONTS
Order: 900016
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Internet Options
Unique ID: ADDINTERNETOPTIONS
Order: 900017
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Network Connections
Unique ID: ADDNETWORKCONNECTIONS
Order: 900018
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: add open with notepad
Unique ID: ADDOPENWITHNOTEPAD
Order: 900019
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Power Options
Unique ID: ADDPOWEROPTIONS
Order: 900020
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Printers
Unique ID: ADDPRINTERS
Order: 900021
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Search option
Unique ID: ADDSEARCHOPTION
Order: 900022
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Programs and Features
Unique ID: ADDPROGRAMSANDFEATURES
Order: 900023
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Registry Editor
Unique ID: ADDREGISTRYEDITOR
Order: 900024
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Run option
Unique ID: ADDRUNOPTION
Order: 900025
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Security Center
Unique ID: ADDSECURITYCENTER
Order: 900026
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Task Manager
Unique ID: ADDTASKMANAGER
Order: 900027
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Task Scheduler
Unique ID: ADDTASKSCHEDULER
Order: 900028
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Turn Firewall On or Off
Unique ID: ADDTURNFIREWALLONOROFF
Order: 900029
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add User Accounts
Unique ID: ADDUSERACCOUNTS
Order: 900030
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add User Accounts Classic
Unique ID: ADDUSERACCOUNTSCLASSIC
Order: 900031
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Window Colorization
Unique ID: ADDWINDOWCOLORIZATION
Order: 900032
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add Classic System Properties Option
Unique ID: ADDCLASSICSYSTEMPROPERTIE
Order: 900033
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:22 PM
Program: Add MSCONFIG
Unique ID: ADDSMSCONFIG
Order: 900034
Category: Tweaks
Monday, June 06, 2011 4:53:22 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Advanced user accounts
Unique ID: ADVANCEDUSERACCOUNTS
Order: 900035
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Aero Controller 1.2 disable aero interface
Unique ID: AEROCONTROLLER12DISABLEAE
Order: 900036
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Aero PowerShell makes windows powershell glass
Unique ID: AEROPOWERSHELLMAKESWINDOW
Order: 900037
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Aero PowerShell disable
Unique ID: AEROPOWERSHELLDISABLE
Order: 900038
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Aero Shake Disables aero shake
Unique ID: AEROSHAKEDISABLESAEROSHAK
Order: 900039
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Aero Shake enable
Unique ID: AEROSHAKEENABLE
Order: 900040
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Aero Cmd Glass
Unique ID: AEROCMDGLASS
Order: 900041
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Aero Cmd glass disable
Unique ID: AEROCMDGLASSDISABLE
Order: 900042
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Auto Restart Shell
Unique ID: AUTORESTARTSHELL
Order: 900043
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Auto Restart Shell disable
Unique ID: AUTORESTARTSHELLDISABLE
Order: 900044
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: BootOptimize
Unique ID: BOOTOPTIMIZE
Order: 900045
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: BootOptimize disable
Unique ID: BOOTOPTIMIZEDISABLE
Order: 900046
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add copy to move to
Unique ID: ADDCOPYTOMOVETO
Order: 900047
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Restore the language bar
Unique ID: RESTORETHELANGUAGEBAR
Order: 900048
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Desktop and Shutdown
Unique ID: DESKTOPANDSHUTDOWN
Order: 900049
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Administrative Shares
Unique ID: DISABLEADMINISTRATIVESHAR
Order: 900050
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable automatic reboot when BSOD
Unique ID: DISABLEAUTOMATICREBOOTWHE
Order: 900051
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable automatic updates
Unique ID: DISABLEAUTOMATICUPDATES
Order: 900052
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable file association web service
Unique ID: DISABLEFILEASSOCIATIONWEB
Order: 900053
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable grouping of system tray icons
Unique ID: DISABLEGROUPINGOFSYSTEMTR
Order: 900054
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Hibernate
Unique ID: DISABLEHIBERNATE
Order: 900055
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Remote Registry
Unique ID: DISABLEREMOTEREGISTRY
Order: 900056
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable the NTFS Last Access Time Stamp
Unique ID: DISABLETHENTFSLASTACCESST
Order: 900057
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Tracking of Broken Shortcut Links
Unique ID: DISABLETRACKINGOFBROKENSH
Order: 900058
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable UAC notify
Unique ID: DISABLEUACNOTIFY
Order: 900059
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable User Account Control UAC
Unique ID: DISABLEUSERACCOUNTCONTROL
Order: 900060
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Web Services
Unique ID: DISABLEWEBSERVICES
Order: 900061
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable 'Windows Defender startup
Unique ID: DISABLEWINDOWSDEFENDERSTA
Order: 900062
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Windows Media Player AutoUpdates
Unique ID: DISABLEWINDOWSMEDIAPLAYER
Order: 900063
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable Libraries in Windows 7
Unique ID: ENABLELIBRARIESINWINDOWS7
Order: 900064
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: DisableDEP
Unique ID: DISABLEDEP
Order: 900065
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable DEP
Unique ID: ENABLEDEP
Order: 900066
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable IPv6
Unique ID: DISABLEIPV6
Order: 900067
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable IPv6
Unique ID: ENABLEIPV6
Order: 900068
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: DisableLastAccess
Unique ID: DISABLELASTACCESS
Order: 900069
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable last Access
Unique ID: ENABLELASTACCESS
Order: 900070
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Teredo proxy speedup internet
Unique ID: DISABLETEREDOPROXYSPEEDUP
Order: 900071
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: EnableTeredo
Unique ID: ENABLETEREDO
Order: 900072
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Low disc space check
Unique ID: DISABLELOWDISCSPACECHECK
Order: 900073
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable low disc space check
Unique ID: ENABLELOWDISCSPACECHECK
Order: 900074
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Do not Use large icons on Start Menu
Unique ID: DONOTUSELARGEICONSONSTART
Order: 900075
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Dont mark new applications
Unique ID: DONTMARKNEWAPPLICATIONS
Order: 900076
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Dr Watson Disable kernel debugger
Unique ID: DISABLEDRWATSONDISABLEKER
Order: 900077
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable DR watson
Unique ID: ENABLEDRWATSON
Order: 900078
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Empty RecycleBin right click
Unique ID: EMPTYRECYCLEBINRIGHTCLICK
Order: 900079
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Empty Folder right click
Unique ID: EMPTYFOLDERRIGHTCLICK
Order: 900080
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable empty folder
Unique ID: DISABLEEMPTYFOLDER
Order: 900081
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable addition Avalon effects
Unique ID: ENABLEADDITIONAVALONEFFEC
Order: 900082
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable DVD in Media Player Value Yes
Unique ID: ENABLEDVDINMEDIAPLAYERVAL
Order: 900083
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable Glass Effect (DWM) without a supported card
Unique ID: ENABLEGLASSEFFECTDWMWITHO
Order: 900084
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable MP3 Encoding from right-click while browsing
Unique ID: ENABLEMP3ENCODINGFROMRIGH
Order: 900085
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable slow-motion window effects min max 3dflip by holding down Shift key
Unique ID: ENABLESLOWMOTIONWINDOWEFF
Order: 900086
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable Status Bar in all windows
Unique ID: ENABLESTATUSBARINALLWINDO
Order: 900087
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable Status bar in Notepad
Unique ID: ENABLESTATUSBARINNOTEPAD
Order: 900088
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Explorer settings
Unique ID: EXPLORERSETTINGS
Order: 900089
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Place Flip 3d in context menu
Unique ID: PLACEFLIP3DINCONTEXTMENU
Order: 900090
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Flip 3d context menu
Unique ID: DISABLEFLIP3DCONTEXTMENU
Order: 900091
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: get rid of the Windows Mail splash screen
Unique ID: GETRIDOFTHEWINDOWSMAILSPL
Order: 900092
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: give your self permission to modify and all
Unique ID: GIVEYOURSELFPERMISSIONTOM
Order: 900093
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Remove obsolete icon elements in the system tray
Unique ID: REMOVEOBSOLETEICONELEMENT
Order: 900095
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Increase the priority of interrupts IRQ8 (increases the speed of the system)
Unique ID: INCREASETHEPRIORITYOFINTE
Order: 900096
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Streamline (increase) system cache. Include only if volume more than 1GB of memory
Unique ID: STREAMLINEINCREASESYSTEMC
Order: 900097
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable large system cache
Unique ID: DISABLELARGESYSTEMCACHE
Order: 900098
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Make the text white in command windows
Unique ID: MAKETHETEXTWHITEINCOMMAND
Order: 900099
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Make the Windows registration with Microsoft unnecessary
Unique ID: MAKETHEWINDOWSREGISTRATIO
Order: 900100
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Makes a right click option for unknown files Open with notepad
Unique ID: MAKESARIGHTCLICKOPTIONFOR
Order: 900101
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Mice settings
Unique ID: MICESETTINGS
Order: 900102
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Microsoft Update settings
Unique ID: MICROSOFTUPDATESETTINGS
Order: 900103
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Mouse Hover Time Speed
Unique ID: MOUSEHOVERTIMESPEED
Order: 900104
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Mouse hover time speed
Unique ID: DISABLEMOUSEHOVERTIMESPEE
Order: 900105
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: MSN settings
Unique ID: MSNSETTINGS
Order: 900106
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: My Computer Context Menu
Unique ID: MYCOMPUTERCONTEXTMENU
Order: 900107
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Do not send to Microsoft error reporting
Unique ID: DONOTSENDTOMICROSOFTERROR
Order: 900108
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: enable send to Microsoft error reporting
Unique ID: ENABLESENDTOMICROSOFTERRO
Order: 900109
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Do not add "Shortcut to when creating new shortcuts
Unique ID: DONOTADDSHORTCUTTOWHENCRE
Order: 900110
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable No Shortcut
Unique ID: DISABLENOSHORTCUT
Order: 900111
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Notepad saves window position
Unique ID: NOTEPADSAVESWINDOWPOSITIO
Order: 900112
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Open in New Window
Unique ID: OPENINNEWWINDOW
Order: 900113
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: option in the right-click menu to open any folder on your computer in a new window
Unique ID: OPTIONINTHERIGHTCLICKMENU
Order: 900114
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Leaving the system kernel in memory (not to throw in the paging file is disabled by default)
Unique ID: LEAVINGTHESYSTEMKERNELINM
Order: 900115
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Paging executive disable
Unique ID: PAGINGEXECUTIVEDISABLE
Order: 900116
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable Paging excutive
Unique ID: ENABLEPAGINGEXCUTIVE
Order: 900117
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Policies
Unique ID: POLICIES
Order: 900118
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Remove- Shortcut Suffix from shortcuts
Unique ID: REMOVESHORTCUTSUFFIXFROMS
Order: 900119
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Prefetch automatic
Unique ID: PREFETCHAUTOMATIC
Order: 900120
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Prefetch manual
Unique ID: PREFETCHMANUAL
Order: 900121
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Prefetch disable
Unique ID: PREFETCHDISABLE
Order: 900122
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Reg Edit Device Manager Control Panel LogOff Reboo Shutdown to my computer
Unique ID: REGEDITDEVICEMANAGERCONTR
Order: 900123
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Register DLL OCX AX
Unique ID: REGISTERDLLOCXAX
Order: 900124
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Run to context menu
Unique ID: ADDRUNTOCONTEXTMENU
Order: 900125
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Scandisk Reduce the time to start the disk check at system startup Scandisk to 5 seconds
Unique ID: SCANDISKREDUCETHETIMETOST
Order: 900126
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Scandisk back to default
Unique ID: SCANDISKBACKTODEFAULT
Order: 900127
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Set Control Panel on Classic View and small icons
Unique ID: SETCONTROLPANELONCLASSICV
Order: 900128
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: SFC Scan
Unique ID: SFCSCAN
Order: 900129
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Show all hidden devices in device manager
Unique ID: SHOWALLHIDDENDEVICESINDEV
Order: 900130
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Show the full path in minimized explorer windows
Unique ID: SHOWTHEFULLPATHINMINIMIZE
Order: 900131
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Show Windows classic folders
Unique ID: SHOWWINDOWSCLASSICFOLDERS
Order: 900132
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Sidebar settings
Unique ID: SIDEBARSETTINGS
Order: 900133
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: SmartClick Allows you to put in the context menu of any program or folder
Unique ID: SMARTCLICKALLOWSYOUTOPUTI
Order: 900134
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Speed up shell response
Unique ID: SPEEDUPSHELLRESPONSE
Order: 900135
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Speed-up Access to AVI Media Files
Unique ID: SPEEDUPACCESSTOAVIMEDIAFI
Order: 900136
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Show hidden files
Unique ID: SHOWHIDDENFILES
Order: 900137
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Show Hidden Files
Unique ID: DISABLESHOWHIDDENFILES
Order: 900138
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Taskbar Jumplist
Unique ID: TASKBARJUMPLIST
Order: 900139
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable taskbar Jumplist
Unique ID: DISABLETASKBARJUMPLIST
Order: 900140
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Thumbnail Cache Disable caching of images
Unique ID: THUMBNAILCACHEDISABLECACH
Order: 900141
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable Thumbnail Cache
Unique ID: ENABLETHUMBNAILCACHE
Order: 900142
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: turn off start menu baloon tips
Unique ID: TURNOFFSTARTMENUBALOONTIP
Order: 900143
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: UAC OFF
Unique ID: UACOFF
Order: 900144
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable UAC
Unique ID: ENABLEUAC
Order: 900145
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Accelerate Download and Upload. It speeds up the network and the Internet
Unique ID: ACCELERATEDOWNLOADANDUPLO
Order: 900146
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Accelerate Download and Upload. It speeds up the network and the Internet
Unique ID: DISABLEACCELERATEDOWNLOAD
Order: 900147
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Allows you to connect and disconnect virtual VHD-drives
Unique ID: ALLOWSYOUTOCONNECTANDDISC
Order: 900148
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: VirusTotal Uploader
Unique ID: VIRUSTOTALUPLOADER
Order: 900149
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Uninstall Virustotal Uploader
Unique ID: UNINSTALLVIRUSTOTALUPLOAD
Order: 900150
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Window Switcher
Unique ID: WINDOWSWITCHER
Order: 900151
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Logon Background Changer 1.3.4
Unique ID: LOGONBACKGROUNDCHANGER134
Order: 900152
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Calendar from the Windows Vista
Unique ID: CALENDARFROMTHEWINDOWSVIS
Order: 900153
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Universal TCPIP Patcher x64
Unique ID: UNIVERSALTCPIPPATCHERX64
Order: 900154
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: 7 Stacks
Unique ID: 7STACKS
Order: 900155
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Logon Screen Rotator
Unique ID: LOGONSCREENROTATOR
Order: 900156
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Adds All The My Computer Right Click Apps. with icon
Unique ID: ADDSALLTHEMYCOMPUTERRIGHT
Order: 900157
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Adds the creation of Batch .cmd file types to New Menu Right Click
Unique ID: ADDSTHECREATIONOFBATCHCMD
Order: 900158
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Adds Windows Switch 3D Flip
Unique ID: ADDSWINDOWSSWITCH3DFLIP
Order: 900159
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Action Center
Unique ID: DISABLEACTIONCENTER
Order: 900160
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Auto Play
Unique ID: DISABLEAUTOPLAY
Order: 900161
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Open NFO files with notepad
Unique ID: OPENNFOFILESWITHNOTEPAD
Order: 900162
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Remove Libraries Icon from Windows 7 Explorer
Unique ID: REMOVELIBRARIESICONFROMWI
Order: 900163
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Show hidden files and folders (but not hidden system files and folders
Unique ID: SHOWHIDDENFILESANDFOLDERS
Order: 900164
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Shows file extensions
Unique ID: SHOWSFILEEXTENSIONS
Order: 900165
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Stop start aero
Unique ID: STOPSTARTAERO
Order: 900166
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Take Ownership with icon
Unique ID: TAKEOWNERSHIPWITHICON
Order: 900167
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Underline letters on right click
Unique ID: UNDERLINELETTERSONRIGHTCL
Order: 900168
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Universal take Ownership
Unique ID: UNIVERSALTAKEOWNERSHIP
Order: 900169
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Unlock the taskbar
Unique ID: UNLOCKTHETASKBAR
Order: 900170
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: 20 ms Mouse Hover Time
Unique ID: 20MSMOUSEHOVERTIME
Order: 900171
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: 500ms Delay Aero Peek
Unique ID: 500MSDELAYAEROPEEK
Order: 900172
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Copy File List Clipboard
Unique ID: ADDCOPYFILELISTCLIPBOARD
Order: 900173
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Admin Auto Hotkey
Unique ID: ADDADMINAUTOHOTKEY
Order: 900174
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add 'Control Panel' Option
Unique ID: ADDCONTROLPANELOPTION
Order: 900175
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Copy Contents To ClipboardTXT
Unique ID: ADDCOPYCONTENTSTOCLIPBOAR
Order: 900176
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Copy To
Unique ID: ADDCOPYTO
Order: 900177
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add 'Event Viewer' Option
Unique ID: ADDEVENTVIEWEROPTION
Order: 900178
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add God Mode in Bottom of Desktop Context Menu
Unique ID: ADDGODMODEINBOTTOMOFDESKT
Order: 900179
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add God Mode in Desktop Context Menu
Unique ID: ADDGODMODEINDESKTOPCONTEX
Order: 900180
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add God Mode in Top of Desktop Context Menu
Unique ID: ADDGODMODEINTOPOFDESKTOPC
Order: 900181
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Hide File
Unique ID: ADDHIDEFILE
Order: 900182
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Move To
Unique ID: ADDMOVETO
Order: 900183
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Name In Context Menu
Unique ID: ADDNAMEINCONTEXTMENU
Order: 900184
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add new CMD file to right click
Unique ID: ADDNEWCMDFILETORIGHTCLICK
Order: 900185
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: add program and features in right click of computer icon
Unique ID: ADDPROGRAMANDFEATURESINRI
Order: 900186
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add 'Programs' Option
Unique ID: ADDPROGRAMSOPTION
Order: 900187
Category: Tweaks
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add register unregister to the context menu for .dll files
Unique ID: ADDREGISTERUNREGISTERTOTH
Order: 900188
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add 'Registry Editor' Option
Unique ID: ADDREGISTRYEDITOROPTION
Order: 900189
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Remove Admin Auto Hotkey
Unique ID: ADDREMOVEADMINAUTOHOTKEY
Order: 900190
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Remove Copy Contents To Clipboard
Unique ID: ADDREMOVECOPYCONTENTSTOCL
Order: 900191
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Remove Options
Unique ID: ADDREMOVEOPTIONS
Order: 900192
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Remove Run option
Unique ID: ADDREMOVERUNOPTION
Order: 900193
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Remove Search Option
Unique ID: ADDREMOVESEARCHOPTION
Order: 900194
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add 'Services' Option
Unique ID: ADDSERVICESOPTION
Order: 900195
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add 'Task Manager' Option
Unique ID: ADDTASKMANAGEROPTION
Order: 900196
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Add Unhide File
Unique ID: ADDUNHIDEFILE
Order: 900197
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: All items have an edit on right-click sending to notepad
Unique ID: ALLITEMSHAVEANEDITONRIGHT
Order: 900198
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Allow renaming and removing of Recycle Bin
Unique ID: ALLOWRENAMINGANDREMOVINGO
Order: 900199
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Allows installing PlexTools Upgrade as full version
Unique ID: ALLOWSINSTALLINGPLEXTOOLS
Order: 900200
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Cache more Icons
Unique ID: CACHEMOREICONS
Order: 900201
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Change the Clock to 24 Hour time format
Unique ID: CHANGETHECLOCKTO24HOURTIM
Order: 900202
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Default Value Aero Peek
Unique ID: DEFAULTVALUEAEROPEEK
Order: 900203
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Aero Shake
Unique ID: DISABLEAEROSHAKE
Order: 900204
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Autorun
Unique ID: DISABLEAUTORUN
Order: 900205
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable Default Hidden Shares
Unique ID: DISABLEDEFAULTHIDDENSHARE
Order: 900206
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable kernel paging Optimize Core System Performance
Unique ID: DISABLEKERNELPAGINGOPTIMI
Order: 900207
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: disable usb message This device can perform faster
Unique ID: DISABLEUSBMESSAGETHISDEVI
Order: 900208
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disable window animations on minimize maximize
Unique ID: DISABLEWINDOWANIMATIONSON
Order: 900209
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Disables Preview of Movie file formats (allowing you to move rename delete without errors)
Unique ID: DISABLESPREVIEWOFMOVIEFIL
Order: 900210
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Do not allow Windows to turn off Network Adapters
Unique ID: DONOTALLOWWINDOWSTOTURNOF
Order: 900211
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Do not save encrypted pages to disk
Unique ID: DONOTSAVEENCRYPTEDPAGESTO
Order: 900212
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Do not show 'Default Programs' on Start Menu
Unique ID: DONOTSHOWDEFAULTPROGRAMSO
Order: 900213
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Do not show Devices and Printers on Start Menu
Unique ID: DONOTSHOWDEVICESANDPRINTE
Order: 900214
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Do not show 'Games' on Start Menu
Unique ID: DONOTSHOWGAMESONSTARTMENU
Order: 900215
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Do not show 'Help and Support' on Start Menu
Unique ID: DONOTSHOWHELPANDSUPPORTON
Order: 900216
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable Aero Shake
Unique ID: ENABLEAEROSHAKE
Order: 900217
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable Dreamscene In Windows 7
Unique ID: ENABLEDREAMSCENEINWINDOWS
Order: 900218
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:23 PM
Program: Enable Tools Folder Options
Unique ID: ENABLETOOLSFOLDEROPTIONS
Order: 900219
Category: Tweaks 2
Monday, June 06, 2011 4:53:23 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Force keep positive entries in DNS Cache for only 4 hours instead of the default 24 hours
Unique ID: FORCEKEEPPOSITIVEENTRIESI
Order: 900220
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: If an Administrator attempts a protected action - Silently Succeed
Unique ID: IFANADMINISTRATORATTEMPTS
Order: 900221
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Increase Network Throughput
Unique ID: INCREASENETWORKTHROUGHPUT
Order: 900222
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Increase RPC Packet Size
Unique ID: INCREASERPCPACKETSIZE
Order: 900223
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Kill hung services after 5 seconds
Unique ID: KILLHUNGSERVICESAFTER5SEC
Order: 900224
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Libraries Restore Default Settings
Unique ID: LIBRARIESRESTOREDEFAULTSE
Order: 900225
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Logon Screen Text Default
Unique ID: LOGONSCREENTEXTDEFAULT
Order: 900226
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Logon Screen Text no shadow
Unique ID: LOGONSCREENTEXTNOSHADOW
Order: 900227
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Logon Screen Text shadow
Unique ID: LOGONSCREENTEXTSHADOW
Order: 900228
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Open HTA files (used for WPI) with MSHTA.EXE
Unique ID: OPENHTAFILESUSEDFORWPIWIT
Order: 900229
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Remove Open With Notepad
Unique ID: REMOVEOPENWITHNOTEPAD
Order: 900230
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Remove Options
Unique ID: REMOVEOPTIONS
Order: 900231
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Remove 'Recent Items' from Start Menu
Unique ID: REMOVERECENTITEMSFROMSTAR
Order: 900232
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Remove Send Feedback
Unique ID: REMOVESENDFEEDBACK
Order: 900233
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Remove warning about showing hidden system folders
Unique ID: REMOVEWARNINGABOUTSHOWING
Order: 900234
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Remove File List Clipboard
Unique ID: REMOVEFILELISTCLIPBOARD
Order: 900235
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: restore mouse hover time to default
Unique ID: RESTOREMOUSEHOVERTIMETODE
Order: 900236
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Show Encryption Commands on the Shortcut Menu
Unique ID: SHOWENCRYPTIONCOMMANDSONT
Order: 900237
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Show the real CD-recording speed in Nero
Unique ID: SHOWTHEREALCDRECORDINGSPE
Order: 900238
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Stop caching negative responses
Unique ID: STOPCACHINGNEGATIVERESPON
Order: 900239
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Turn off system beeps
Unique ID: TURNOFFSYSTEMBEEPS
Order: 900240
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Type Long File Names In DOS
Unique ID: TYPELONGFILENAMESINDOS
Order: 900241
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Uninstall 'Control Panel' Option
Unique ID: UNINSTALLCONTROLPANELOPTI
Order: 900242
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Uninstall 'Device Manager' Option
Unique ID: UNINSTALLDEVICEMANAGEROPT
Order: 900243
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Uninstall 'Event Viewer' Option
Unique ID: UNINSTALLEVENTVIEWEROPTIO
Order: 900244
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Uninstall god mode
Unique ID: UNINSTALLGODMODE
Order: 900245
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Uninstall 'MSConfig' Option
Unique ID: UNINSTALLMSCONFIGOPTION
Order: 900246
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Uninstall 'Programs' Option
Unique ID: UNINSTALLPROGRAMSOPTION
Order: 900247
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Uninstall 'Registry Editor' Option
Unique ID: UNINSTALLREGISTRYEDITOROP
Order: 900248
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Uninstall 'Services' Option
Unique ID: UNINSTALLSERVICESOPTION
Order: 900249
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Uninstall 'Task Manager' Option
Unique ID: UNINSTALLTASKMANAGEROPTIO
Order: 900250
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Use SSL 2.0 (Checked) + SSL 3.0 (Checked) + TSL 1.0 (unchecked)
Unique ID: USESSL20CHECKEDSSL30CHECK
Order: 900251
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Monday, June 06, 2011 4:53:24 PM
Program: Windows will tell you exactly what it is doing when it is shutting down or is booting
Unique ID: WINDOWSWILLTELLYOUEXACTLY
Order: 900252
Category: Tweaks 2
Monday, June 06, 2011 4:53:24 PM - Finished installation.
—–
Number of failed installations: 0
Install process finished at: Monday, June 06, 2011 4:53:24 PM
Yes please, I am still having problems. I am sending you the log files you requested last week.
03:35:14.0218 5472 TDSS rootkit removing tool [removed] Oct 21 2011 11:23:48
03:35:14.0946 5472 ============================================================
03:35:14.0946 5472 Current date / time: 2011/10/24 03:35:14.0946
03:35:14.0946 5472 SystemInfo:
03:35:14.0946 5472
03:35:14.0946 5472 OS Version: 6.1.7601 ServicePack: 1.0
03:35:14.0946 5472 Product type: Workstation
03:35:14.0946 5472 ComputerName: SMOOTH_TOP-PC
03:35:14.0946 5472 UserName: Smooth_Top
03:35:14.0946 5472 Windows directory: C:\Windows
03:35:14.0946 5472 System windows directory: C:\Windows
03:35:14.0946 5472 Running under WOW64
03:35:14.0946 5472 Processor architecture: Intel x64
03:35:14.0946 5472 Number of processors: 4
03:35:14.0946 5472 Page size: 0x1000
03:35:14.0946 5472 Boot type: Normal boot
03:35:14.0946 5472 ============================================================
03:35:28.0852 5472 Initialize success
03:35:30.0704 4104 ============================================================
03:35:30.0704 4104 Scan started
03:35:30.0704 4104 Mode: Manual;
03:35:30.0704 4104 ============================================================
03:35:31.0794 4104 1394ohci (a87d604aea360176311474c87a63bb88) C:\Windows\system32\drivers\1394ohci.sys
03:35:31.0795 4104 1394ohci - ok
03:35:31.0891 4104 a2acc (0b8ed3de81ec30ad50873f033b34b39e) C:\PROGRAM FILES (X86)\MAMUTU\a2accx64.sys
03:35:31.0900 4104 a2acc - ok
03:35:31.0914 4104 a2injectiondriver (f75ddc4047aa1ac85164445cba7601ef) C:\Program Files (x86)\Mamutu\a2dix64.sys
03:35:31.0921 4104 a2injectiondriver - ok
03:35:31.0963 4104 a2util (e41d79682a209f72f4f578cfd4a53952) C:\Program Files (x86)\Mamutu\a2util64.sys
03:35:31.0975 4104 a2util - ok
03:35:32.0030 4104 ACPI (d81d9e70b8a6dd14d42d7b4efa65d5f2) C:\Windows\system32\drivers\ACPI.sys
03:35:32.0034 4104 ACPI - ok
03:35:32.0125 4104 AcpiPmi (99f8e788246d495ce3794d7e7821d2ca) C:\Windows\system32\drivers\acpipmi.sys
03:35:32.0126 4104 AcpiPmi - ok
03:35:32.0277 4104 adp94xx (2f6b34b83843f0c5118b63ac634f5bf4) C:\Windows\system32\DRIVERS\adp94xx.sys
03:35:32.0279 4104 adp94xx - ok
03:35:32.0392 4104 adpahci (597f78224ee9224ea1a13d6350ced962) C:\Windows\system32\DRIVERS\adpahci.sys
03:35:32.0394 4104 adpahci - ok
03:35:32.0513 4104 adpu320 (e109549c90f62fb570b9540c4b148e54) C:\Windows\system32\DRIVERS\adpu320.sys
03:35:32.0514 4104 adpu320 - ok
03:35:32.0663 4104 AFD (d5b031c308a409a0a576bff4cf083d30) C:\Windows\system32\drivers\afd.sys
03:35:32.0676 4104 AFD - ok
03:35:32.0781 4104 agp440 (608c14dba7299d8cb6ed035a68a15799) C:\Windows\system32\drivers\agp440.sys
03:35:32.0782 4104 agp440 - ok
03:35:32.0833 4104 aliide (5812713a477a3ad7363c7438ca2ee038) C:\Windows\system32\drivers\aliide.sys
03:35:32.0833 4104 aliide - ok
03:35:32.0892 4104 amdide (1ff8b4431c353ce385c875f194924c0c) C:\Windows\system32\drivers\amdide.sys
03:35:32.0893 4104 amdide - ok
03:35:32.0922 4104 AmdK8 (7024f087cff1833a806193ef9d22cda9) C:\Windows\system32\DRIVERS\amdk8.sys
03:35:32.0923 4104 AmdK8 - ok
03:35:34.0199 4104 amdkmdag (9a4b92150a5e259a7159d914cc3a60d7) C:\Windows\system32\DRIVERS\atikmdag.sys
03:35:34.0307 4104 amdkmdag - ok
03:35:34.0454 4104 amdkmdap (9deb889d152f9c9dba98be8986084535) C:\Windows\system32\DRIVERS\atikmpag.sys
03:35:34.0468 4104 amdkmdap - ok
03:35:34.0537 4104 AmdPPM (1e56388b3fe0d031c44144eb8c4d6217) C:\Windows\system32\DRIVERS\amdppm.sys
03:35:34.0537 4104 AmdPPM - ok
03:35:34.0600 4104 amdsata (d4121ae6d0c0e7e13aa221aa57ef2d49) C:\Windows\system32\drivers\amdsata.sys
03:35:34.0612 4104 amdsata - ok
03:35:34.0662 4104 amdsbs (f67f933e79241ed32ff46a4f29b5120b) C:\Windows\system32\DRIVERS\amdsbs.sys
03:35:34.0663 4104 amdsbs - ok
03:35:34.0716 4104 amdxata (540daf1cea6094886d72126fd7c33048) C:\Windows\system32\drivers\amdxata.sys
03:35:34.0729 4104 amdxata - ok
03:35:34.0793 4104 androidusb (9c59bf508c5d408bb348254e0ba2ee30) C:\Windows\system32\Drivers\androidusb.sys
03:35:34.0823 4104 androidusb - ok
03:35:34.0881 4104 apmwin (72f5c6445dd711c5514ba4de4dab6ad6) C:\Windows\system32\DRIVERS\apmwin.sys
03:35:34.0901 4104 apmwin - ok
03:35:34.0961 4104 AppID (89a69c3f2f319b43379399547526d952) C:\Windows\system32\drivers\appid.sys
03:35:34.0962 4104 AppID - ok
03:35:35.0026 4104 arc (c484f8ceb1717c540242531db7845c4e) C:\Windows\system32\DRIVERS\arc.sys
03:35:35.0027 4104 arc - ok
03:35:35.0079 4104 arcsas (019af6924aefe7839f61c830227fe79c) C:\Windows\system32\DRIVERS\arcsas.sys
03:35:35.0080 4104 arcsas - ok
03:35:35.0125 4104 AsyncMac (769765ce2cc62867468cea93969b2242) C:\Windows\system32\DRIVERS\asyncmac.sys
03:35:35.0137 4104 AsyncMac - ok
03:35:35.0185 4104 atapi (02062c0b390b7729edc9e69c680a6f3c) C:\Windows\system32\drivers\atapi.sys
03:35:35.0186 4104 atapi - ok
03:35:35.0741 4104 atikmdag (9a4b92150a5e259a7159d914cc3a60d7) C:\Windows\system32\DRIVERS\atikmdag.sys
03:35:35.0773 4104 atikmdag - ok
03:35:35.0979 4104 b06bdrv (3e5b191307609f7514148c6832bb0842) C:\Windows\system32\DRIVERS\bxvbda.sys
03:35:35.0981 4104 b06bdrv - ok
03:35:36.0025 4104 b57nd60a (b5ace6968304a3900eeb1ebfd9622df2) C:\Windows\system32\DRIVERS\b57nd60a.sys
03:35:36.0027 4104 b57nd60a - ok
03:35:36.0060 4104 Beep (16a47ce2decc9b099349a5f840654746) C:\Windows\system32\drivers\Beep.sys
03:35:36.0061 4104 Beep - ok
03:35:36.0519 4104 BHDrvx64 (cd0ecb395666fc9ae23d7381e9e3370d) C:\ProgramData\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NAV_19.1.0.28\Definitions\BASHDefs\20111014.001\BHDrvx64.sys
03:35:36.0535 4104 BHDrvx64 - ok
03:35:36.0559 4104 blbdrive (61583ee3c3a17003c4acd0475646b4d3) C:\Windows\system32\DRIVERS\blbdrive.sys
03:35:36.0577 4104 blbdrive - ok
03:35:36.0748 4104 bowser (6c02a83164f5cc0a262f4199f0871cf5) C:\Windows\system32\DRIVERS\bowser.sys
03:35:36.0761 4104 bowser - ok
03:35:36.0789 4104 BrFiltLo (f09eee9edc320b5e1501f749fde686c8) C:\Windows\system32\DRIVERS\BrFiltLo.sys
03:35:36.0790 4104 BrFiltLo - ok
03:35:36.0828 4104 BrFiltUp (b114d3098e9bdb8bea8b053685831be6) C:\Windows\system32\DRIVERS\BrFiltUp.sys
03:35:36.0829 4104 BrFiltUp - ok
03:35:36.0909 4104 Brserid (43bea8d483bf1870f018e2d02e06a5bd) C:\Windows\System32\Drivers\Brserid.sys
03:35:36.0911 4104 Brserid - ok
03:35:36.0941 4104 BrSerWdm (a6eca2151b08a09caceca35c07f05b42) C:\Windows\System32\Drivers\BrSerWdm.sys
03:35:36.0941 4104 BrSerWdm - ok
03:35:36.0976 4104 BrUsbMdm (b79968002c277e869cf38bd22cd61524) C:\Windows\System32\Drivers\BrUsbMdm.sys
03:35:36.0977 4104 BrUsbMdm - ok
03:35:37.0019 4104 BrUsbSer (a87528880231c54e75ea7a44943b38bf) C:\Windows\System32\Drivers\BrUsbSer.sys
03:35:37.0020 4104 BrUsbSer - ok
03:35:37.0067 4104 BTHMODEM (9da669f11d1f894ab4eb69bf546a42e8) C:\Windows\system32\DRIVERS\bthmodem.sys
03:35:37.0068 4104 BTHMODEM - ok
03:35:37.0238 4104 ccSet_NAV (a8ad33c9dd88c810cac00acc7f4329fb) C:\Windows\system32\drivers\NAVx64\1301010.003\ccSetx64.sys
03:35:37.0239 4104 ccSet_NAV - ok
03:35:37.0269 4104 cdfs (b8bd2bb284668c84865658c77574381a) C:\Windows\system32\DRIVERS\cdfs.sys
03:35:37.0281 4104 cdfs - ok
03:35:37.0339 4104 cdrom (f036ce71586e93d94dab220d7bdf4416) C:\Windows\system32\drivers\cdrom.sys
03:35:37.0342 4104 cdrom - ok
03:35:37.0437 4104 circlass (d7cd5c4e1b71fa62050515314cfb52cf) C:\Windows\system32\DRIVERS\circlass.sys
03:35:37.0438 4104 circlass - ok
03:35:37.0551 4104 CLFS (fe1ec06f2253f691fe36217c592a0206) C:\Windows\system32\CLFS.sys
03:35:37.0566 4104 CLFS - ok
03:35:37.0710 4104 CmBatt (0840155d0bddf1190f84a663c284bd33) C:\Windows\system32\DRIVERS\CmBatt.sys
03:35:37.0711 4104 CmBatt - ok
03:35:37.0888 4104 cmdide (e19d3f095812725d88f9001985b94edd) C:\Windows\system32\drivers\cmdide.sys
03:35:37.0889 4104 cmdide - ok
03:35:38.0111 4104 CNG (d5fea92400f12412b3922087c09da6a5) C:\Windows\system32\Drivers\cng.sys
03:35:38.0128 4104 CNG - ok
03:35:38.0173 4104 Compbatt (102de219c3f61415f964c88e9085ad14) C:\Windows\system32\DRIVERS\compbatt.sys
03:35:38.0182 4104 Compbatt - ok
03:35:38.0240 4104 CompositeBus (03edb043586cceba243d689bdda370a8) C:\Windows\system32\drivers\CompositeBus.sys
03:35:38.0255 4104 CompositeBus - ok
03:35:38.0297 4104 cpuz135 (262969a3fab32b9e17e63e2d17a57744) C:\Windows\system32\drivers\cpuz135_x64.sys
03:35:38.0361 4104 cpuz135 - ok
03:35:38.0393 4104 crcdisk (1c827878a998c18847245fe1f34ee597) C:\Windows\system32\DRIVERS\crcdisk.sys
03:35:38.0394 4104 crcdisk - ok
03:35:38.0509 4104 dc3d (1ca90212a99db6975c344826d11055c9) C:\Windows\system32\DRIVERS\dc3d.sys
03:35:38.0525 4104 dc3d - ok
03:35:38.0558 4104 DfsC (9bb2ef44eaa163b29c4a4587887a0fe4) C:\Windows\system32\Drivers\dfsc.sys
03:35:38.0560 4104 DfsC - ok
03:35:38.0617 4104 discache (13096b05847ec78f0977f2c0f79e9ab3) C:\Windows\system32\drivers\discache.sys
03:35:38.0618 4104 discache - ok
03:35:38.0630 4104 Disk (9819eee8b5ea3784ec4af3b137a5244c) C:\Windows\system32\DRIVERS\disk.sys
03:35:38.0632 4104 Disk - ok
03:35:38.0679 4104 drmkaud (9b19f34400d24df84c858a421c205754) C:\Windows\system32\drivers\drmkaud.sys
03:35:38.0681 4104 drmkaud - ok
03:35:38.0719 4104 DXGKrnl (f5bee30450e18e6b83a5012c100616fd) C:\Windows\System32\drivers\dxgkrnl.sys
03:35:38.0739 4104 DXGKrnl - ok
03:35:38.0768 4104 e1kexpress (fcd4e9eaa7682d5fa4acef433c3b42a8) C:\Windows\system32\DRIVERS\e1k62x64.sys
03:35:38.0772 4104 e1kexpress - ok
03:35:38.0833 4104 ebdrv (dc5d737f51be844d8c82c695eb17372f) C:\Windows\system32\DRIVERS\evbda.sys
03:35:38.0879 4104 ebdrv - ok
03:35:38.0973 4104 eeCtrl (5e3a50930447f464c66032e05a4632f5) C:\Program Files (x86)\Common Files\Symantec Shared\EENGINE\eeCtrl64.sys
03:35:38.0994 4104 eeCtrl - ok
03:35:39.0020 4104 elxstor (0e5da5369a0fcaea12456dd852545184) C:\Windows\system32\DRIVERS\elxstor.sys
03:35:39.0023 4104 elxstor - ok
03:35:39.0056 4104 epmntdrv (9eafb3b3b60b8ad958985152a9309aca) C:\Windows\system32\epmntdrv.sys
03:35:39.0081 4104 epmntdrv - ok
03:35:39.0119 4104 EraserUtilRebootDrv (dcb76ecc6b50a266fdc16e1963ab98ce) C:\Program Files (x86)\Common Files\Symantec Shared\EENGINE\EraserUtilRebootDrv.sys
03:35:39.0122 4104 EraserUtilRebootDrv - ok
03:35:39.0152 4104 ErrDev (34a3c54752046e79a126e15c51db409b) C:\Windows\system32\drivers\errdev.sys
03:35:39.0152 4104 ErrDev - ok
03:35:39.0185 4104 EuGdiDrv (fb949ed2c93c878a189039f3d7730942) C:\Windows\system32\EuGdiDrv.sys
03:35:39.0215 4104 EuGdiDrv - ok
03:35:39.0268 4104 exfat (a510c654ec00c1e9bdd91eeb3a59823b) C:\Windows\system32\drivers\exfat.sys
03:35:39.0270 4104 exfat - ok
03:35:39.0303 4104 FARMNTIO (51682af3e735e2019f84f4cdbdae6611) c:\windows\system32\drivers\farmntio.sys
03:35:39.0340 4104 FARMNTIO - ok
03:35:39.0360 4104 fastfat (0adc83218b66a6db380c330836f3e36d) C:\Windows\system32\drivers\fastfat.sys
03:35:39.0361 4104 fastfat - ok
03:35:39.0381 4104 fdc (d765d19cd8ef61f650c384f62fac00ab) C:\Windows\system32\DRIVERS\fdc.sys
03:35:39.0381 4104 fdc - ok
03:35:39.0400 4104 FileInfo (655661be46b5f5f3fd454e2c3095b930) C:\Windows\system32\drivers\fileinfo.sys
03:35:39.0411 4104 FileInfo - ok
03:35:39.0434 4104 Filetrace (5f671ab5bc87eea04ec38a6cd5962a47) C:\Windows\system32\drivers\filetrace.sys
03:35:39.0435 4104 Filetrace - ok
03:35:39.0454 4104 flpydisk (c172a0f53008eaeb8ea33fe10e177af5) C:\Windows\system32\DRIVERS\flpydisk.sys
03:35:39.0455 4104 flpydisk - ok
03:35:39.0508 4104 FltMgr (da6b67270fd9db3697b20fce94950741) C:\Windows\system32\drivers\fltmgr.sys
03:35:39.0512 4104 FltMgr - ok
03:35:39.0542 4104 FsDepends (d43703496149971890703b4b1b723eac) C:\Windows\system32\drivers\FsDepends.sys
03:35:39.0543 4104 FsDepends - ok
03:35:39.0576 4104 fssfltr (6c06701bf1db05405804d7eb610991ce) C:\Windows\system32\DRIVERS\fssfltr.sys
03:35:39.0587 4104 fssfltr - ok
03:35:39.0608 4104 Fs_Rec (e95ef8547de20cf0603557c0cf7a9462) C:\Windows\system32\drivers\Fs_Rec.sys
03:35:39.0609 4104 Fs_Rec - ok
03:35:39.0663 4104 fvevol (1f7b25b858fa27015169fe95e54108ed) C:\Windows\system32\DRIVERS\fvevol.sys
03:35:39.0666 4104 fvevol - ok
03:35:39.0686 4104 gagp30kx (8c778d335c9d272cfd3298ab02abe3b6) C:\Windows\system32\DRIVERS\gagp30kx.sys
03:35:39.0687 4104 gagp30kx - ok
03:35:39.0724 4104 GEARAspiWDM (e403aacf8c7bb11375122d2464560311) C:\Windows\system32\DRIVERS\GEARAspiWDM.sys
03:35:39.0738 4104 GEARAspiWDM - ok
03:35:39.0759 4104 gpt_loader (8de1048e3f41c6d7f83f8ce7dc8f5b11) C:\Windows\system32\DRIVERS\gpt_loader.sys
03:35:39.0772 4104 gpt_loader - ok
03:35:39.0828 4104 hcw85cir (f2523ef6460fc42405b12248338ab2f0) C:\Windows\system32\drivers\hcw85cir.sys
03:35:39.0829 4104 hcw85cir - ok
03:35:39.0866 4104 HdAudAddService (975761c778e33cd22498059b91e7373a) C:\Windows\system32\drivers\HdAudio.sys
03:35:39.0870 4104 HdAudAddService - ok
03:35:39.0902 4104 HDAudBus (97bfed39b6b79eb12cddbfeed51f56bb) C:\Windows\system32\drivers\HDAudBus.sys
03:35:39.0904 4104 HDAudBus - ok
03:35:39.0930 4104 HECIx64 (b6ac71aaa2b10848f57fc49d55a651af) C:\Windows\system32\DRIVERS\HECIx64.sys
03:35:39.0932 4104 HECIx64 - ok
03:35:39.0973 4104 Hfsplus (b515c40a1e2c4ae326513e42b40d66d1) C:\Windows\system32\DRIVERS\hfsplus.sys
03:35:40.0002 4104 Hfsplus - ok
03:35:40.0030 4104 HfsplusRec (b0bc53188b62e2db21c2f937abe6912c) C:\Windows\system32\DRIVERS\hfsplusrec.sys
03:35:40.0042 4104 HfsplusRec - ok
03:35:40.0060 4104 HidBatt (78e86380454a7b10a5eb255dc44a355f) C:\Windows\system32\DRIVERS\HidBatt.sys
03:35:40.0061 4104 HidBatt - ok
03:35:40.0077 4104 HidBth (7fd2a313f7afe5c4dab14798c48dd104) C:\Windows\system32\DRIVERS\hidbth.sys
03:35:40.0078 4104 HidBth - ok
03:35:40.0090 4104 HidIr (0a77d29f311b88cfae3b13f9c1a73825) C:\Windows\system32\DRIVERS\hidir.sys
03:35:40.0091 4104 HidIr - ok
03:35:40.0108 4104 HidUsb (9592090a7e2b61cd582b612b6df70536) C:\Windows\system32\DRIVERS\hidusb.sys
03:35:40.0109 4104 HidUsb - ok
03:35:40.0160 4104 hotcore3 (5e626ea93c77825c56e6fbc2fd5e5de5) C:\Windows\system32\DRIVERS\hotcore3.sys
03:35:40.0184 4104 hotcore3 - ok
03:35:40.0217 4104 HpSAMD (39d2abcd392f3d8a6dce7b60ae7b8efc) C:\Windows\system32\drivers\HpSAMD.sys
03:35:40.0218 4104 HpSAMD - ok
03:35:40.0263 4104 HTTP (0ea7de1acb728dd5a369fd742d6eee28) C:\Windows\system32\drivers\HTTP.sys
03:35:40.0270 4104 HTTP - ok
03:35:40.0302 4104 hwpolicy (a5462bd6884960c9dc85ed49d34ff392) C:\Windows\system32\drivers\hwpolicy.sys
03:35:40.0304 4104 hwpolicy - ok
03:35:40.0320 4104 i8042prt (fa55c73d4affa7ee23ac4be53b4592d3) C:\Windows\system32\drivers\i8042prt.sys
03:35:40.0322 4104 i8042prt - ok
03:35:40.0356 4104 iaStorV (aaaf44db3bd0b9d1fb6969b23ecc8366) C:\Windows\system32\drivers\iaStorV.sys
03:35:40.0360 4104 iaStorV - ok
03:35:40.0576 4104 IDSVia64 (0b97f1a640ad3d159a7b5d2164c42e50) C:\ProgramData\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NAV_19.1.0.28\Definitions\IPSDefs\20111021.030\IDSvia64.sys
03:35:40.0582 4104 IDSVia64 - ok
03:35:40.0613 4104 iirsp (5c18831c61933628f5bb0ea2675b9d21) C:\Windows\system32\DRIVERS\iirsp.sys
03:35:40.0614 4104 iirsp - ok
03:35:40.0687 4104 IntcAzAudAddService (26407a11d7e222afb7ce32700abbd9d1) C:\Windows\system32\drivers\RTKVHD64.sys
03:35:40.0738 4104 IntcAzAudAddService - ok
03:35:40.0774 4104 intelide (f00f20e70c6ec3aa366910083a0518aa) C:\Windows\system32\drivers\intelide.sys
03:35:40.0775 4104 intelide - ok
03:35:40.0794 4104 intelppm (ada036632c664caa754079041cf1f8c1) C:\Windows\system32\DRIVERS\intelppm.sys
03:35:40.0795 4104 intelppm - ok
03:35:40.0832 4104 IpFilterDriver (c9f0e1bd74365a8771590e9008d22ab6) C:\Windows\system32\DRIVERS\ipfltdrv.sys
03:35:40.0833 4104 IpFilterDriver - ok
03:35:40.0866 4104 IPMIDRV (0fc1aea580957aa8817b8f305d18ca3a) C:\Windows\system32\drivers\IPMIDrv.sys
03:35:40.0867 4104 IPMIDRV - ok
03:35:40.0888 4104 IPNAT (af9b39a7e7b6caa203b3862582e9f2d0) C:\Windows\system32\drivers\ipnat.sys
03:35:40.0891 4104 IPNAT - ok
03:35:40.0928 4104 IRENUM (3abf5e7213eb28966d55d58b515d5ce9) C:\Windows\system32\drivers\irenum.sys
03:35:40.0929 4104 IRENUM - ok
03:35:40.0943 4104 isapnp (2f7b28dc3e1183e5eb418df55c204f38) C:\Windows\system32\drivers\isapnp.sys
03:35:40.0944 4104 isapnp - ok
03:35:40.0977 4104 iScsiPrt (d931d7309deb2317035b07c9f9e6b0bd) C:\Windows\system32\drivers\msiscsi.sys
03:35:40.0978 4104 iScsiPrt - ok
03:35:40.0994 4104 kbdclass (bc02336f1cba7dcc7d1213bb588a68a5) C:\Windows\system32\DRIVERS\kbdclass.sys
03:35:40.0996 4104 kbdclass - ok
03:35:41.0024 4104 kbdhid (0705eff5b42a9db58548eec3b26bb484) C:\Windows\system32\DRIVERS\kbdhid.sys
03:35:41.0026 4104 kbdhid - ok
03:35:41.0065 4104 KSecDD (ccd53b5bd33ce0c889e830d839c8b66e) C:\Windows\system32\Drivers\ksecdd.sys
03:35:41.0067 4104 KSecDD - ok
03:35:41.0105 4104 KSecPkg (9ff918a261752c12639e8ad4208d2c2f) C:\Windows\system32\Drivers\ksecpkg.sys
03:35:41.0108 4104 KSecPkg - ok
03:35:41.0124 4104 ksthunk (6869281e78cb31a43e969f06b57347c4) C:\Windows\system32\drivers\ksthunk.sys
03:35:41.0125 4104 ksthunk - ok
03:35:41.0148 4104 lltdio (1538831cf8ad2979a04c423779465827) C:\Windows\system32\DRIVERS\lltdio.sys
03:35:41.0150 4104 lltdio - ok
03:35:41.0181 4104 LSI_FC (1a93e54eb0ece102495a51266dcdb6a6) C:\Windows\system32\DRIVERS\lsi_fc.sys
03:35:41.0182 4104 LSI_FC - ok
03:35:41.0214 4104 LSI_SAS (1047184a9fdc8bdbff857175875ee810) C:\Windows\system32\DRIVERS\lsi_sas.sys
03:35:41.0215 4104 LSI_SAS - ok
03:35:41.0230 4104 LSI_SAS2 (30f5c0de1ee8b5bc9306c1f0e4a75f93) C:\Windows\system32\DRIVERS\lsi_sas2.sys
03:35:41.0231 4104 LSI_SAS2 - ok
03:35:41.0253 4104 LSI_SCSI (0504eacaff0d3c8aed161c4b0d369d4a) C:\Windows\system32\DRIVERS\lsi_scsi.sys
03:35:41.0254 4104 LSI_SCSI - ok
03:35:41.0277 4104 luafv (43d0f98e1d56ccddb0d5254cff7b356e) C:\Windows\system32\drivers\luafv.sys
03:35:41.0279 4104 luafv - ok
03:35:41.0318 4104 MBAMProtector (23a854450dab5c9b7a42ab9be6f2e4bd) C:\Windows\system32\drivers\mbam.sys
03:35:41.0337 4104 MBAMProtector - ok
03:35:41.0358 4104 megasas (a55805f747c6edb6a9080d7c633bd0f4) C:\Windows\system32\DRIVERS\megasas.sys
03:35:41.0359 4104 megasas - ok
03:35:41.0370 4104 MegaSR (baf74ce0072480c3b6b7c13b2a94d6b3) C:\Windows\system32\DRIVERS\MegaSR.sys
03:35:41.0372 4104 MegaSR - ok
03:35:41.0393 4104 Modem (800ba92f7010378b09f9ed9270f07137) C:\Windows\system32\drivers\modem.sys
03:35:41.0395 4104 Modem - ok
03:35:41.0416 4104 monitor (b03d591dc7da45ece20b3b467e6aadaa) C:\Windows\system32\DRIVERS\monitor.sys
03:35:41.0416 4104 monitor - ok
03:35:41.0449 4104 motmodem (060f0ef84f430802df3788f3dcfd009c) C:\Windows\system32\DRIVERS\motmodem.sys
03:35:41.0451 4104 motmodem - ok
03:35:41.0493 4104 mouclass (7d27ea49f3c1f687d357e77a470aea99) C:\Windows\system32\DRIVERS\mouclass.sys
03:35:41.0495 4104 mouclass - ok
03:35:41.0507 4104 mouhid (d3bf052c40b0c4166d9fd86a4288c1e6) C:\Windows\system32\DRIVERS\mouhid.sys
03:35:41.0509 4104 mouhid - ok
03:35:41.0547 4104 mounthlp (f4ac4cf540b76a551c4c19b50eb87c4c) C:\Windows\system32\DRIVERS\mounthlp.sys
03:35:41.0565 4104 mounthlp - ok
03:35:41.0595 4104 mountmgr (32e7a3d591d671a6df2db515a5cbe0fa) C:\Windows\system32\drivers\mountmgr.sys
03:35:41.0597 4104 mountmgr - ok
03:35:41.0631 4104 mpio (a44b420d30bd56e145d6a2bc8768ec58) C:\Windows\system32\drivers\mpio.sys
03:35:41.0632 4104 mpio - ok
03:35:41.0706 4104 mpsdrv (6c38c9e45ae0ea2fa5e551f2ed5e978f) C:\Windows\system32\drivers\mpsdrv.sys
03:35:41.0742 4104 mpsdrv - ok
03:35:41.0782 4104 MRxDAV (dc722758b8261e1abafd31a3c0a66380) C:\Windows\system32\drivers\mrxdav.sys
03:35:41.0784 4104 MRxDAV - ok
03:35:41.0812 4104 mrxsmb (a5d9106a73dc88564c825d317cac68ac) C:\Windows\system32\DRIVERS\mrxsmb.sys
03:35:41.0814 4104 mrxsmb - ok
03:35:41.0851 4104 mrxsmb10 (d711b3c1d5f42c0c2415687be09fc163) C:\Windows\system32\DRIVERS\mrxsmb10.sys
03:35:41.0855 4104 mrxsmb10 - ok
03:35:41.0875 4104 mrxsmb20 (9423e9d355c8d303e76b8cfbd8a5c30c) C:\Windows\system32\DRIVERS\mrxsmb20.sys
03:35:41.0878 4104 mrxsmb20 - ok
03:35:41.0911 4104 msahci (c25f0bafa182cbca2dd3c851c2e75796) C:\Windows\system32\drivers\msahci.sys
03:35:41.0912 4104 msahci - ok
03:35:41.0959 4104 msdsm (db801a638d011b9633829eb6f663c900) C:\Windows\system32\drivers\msdsm.sys
03:35:41.0961 4104 msdsm - ok
03:35:41.0990 4104 Msfs (aa3fb40e17ce1388fa1bedab50ea8f96) C:\Windows\system32\drivers\Msfs.sys
03:35:41.0991 4104 Msfs - ok
03:35:42.0011 4104 mshidkmdf (f9d215a46a8b9753f61767fa72a20326) C:\Windows\System32\drivers\mshidkmdf.sys
03:35:42.0013 4104 mshidkmdf - ok
03:35:42.0042 4104 msisadrv (d916874bbd4f8b07bfb7fa9b3ccae29d) C:\Windows\system32\drivers\msisadrv.sys
03:35:42.0043 4104 msisadrv - ok
03:35:42.0083 4104 MSKSSRV (49ccf2c4fea34ffad8b1b59d49439366) C:\Windows\system32\drivers\MSKSSRV.sys
03:35:42.0085 4104 MSKSSRV - ok
03:35:42.0103 4104 MSPCLOCK (bdd71ace35a232104ddd349ee70e1ab3) C:\Windows\system32\drivers\MSPCLOCK.sys
03:35:42.0105 4104 MSPCLOCK - ok
03:35:42.0127 4104 MSPQM (4ed981241db27c3383d72092b618a1d0) C:\Windows\system32\drivers\MSPQM.sys
03:35:42.0128 4104 MSPQM - ok
03:35:42.0165 4104 MsRPC (759a9eeb0fa9ed79da1fb7d4ef78866d) C:\Windows\system32\drivers\MsRPC.sys
03:35:42.0169 4104 MsRPC - ok
03:35:42.0183 4104 mssmbios (0eed230e37515a0eaee3c2e1bc97b288) C:\Windows\system32\drivers\mssmbios.sys
03:35:42.0183 4104 mssmbios - ok
03:35:42.0204 4104 MSTEE (2e66f9ecb30b4221a318c92ac2250779) C:\Windows\system32\drivers\MSTEE.sys
03:35:42.0206 4104 MSTEE - ok
03:35:42.0218 4104 MTConfig (7ea404308934e675bffde8edf0757bcd) C:\Windows\system32\DRIVERS\MTConfig.sys
03:35:42.0220 4104 MTConfig - ok
03:35:42.0236 4104 Mup (f9a18612fd3526fe473c1bda678d61c8) C:\Windows\system32\Drivers\mup.sys
03:35:42.0238 4104 Mup - ok
03:35:42.0277 4104 NativeWifiP (1ea3749c4114db3e3161156ffffa6b33) C:\Windows\system32\DRIVERS\nwifi.sys
03:35:42.0294 4104 NativeWifiP - ok
03:35:42.0451 4104 NAVENG (2dbe90210de76be6e1653bb20ec70ec2) C:\ProgramData\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NAV_19.1.0.28\Definitions\VirusDefs\20111023.005\ENG64.SYS
03:35:42.0454 4104 NAVENG - ok
03:35:42.0505 4104 NAVEX15 (346da70e203b8e2c850277713de8f71b) C:\ProgramData\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NAV_19.1.0.28\Definitions\VirusDefs\20111023.005\EX64.SYS
03:35:42.0538 4104 NAVEX15 - ok
03:35:42.0602 4104 NDIS (79b47fd40d9a817e932f9d26fac0a81c) C:\Windows\system32\drivers\ndis.sys
03:35:42.0610 4104 NDIS - ok
03:35:42.0629 4104 NdisCap (9f9a1f53aad7da4d6fef5bb73ab811ac) C:\Windows\system32\DRIVERS\ndiscap.sys
03:35:42.0631 4104 NdisCap - ok
03:35:42.0640 4104 NdisTapi (30639c932d9fef22b31268fe25a1b6e5) C:\Windows\system32\DRIVERS\ndistapi.sys
03:35:42.0641 4104 NdisTapi - ok
03:35:42.0686 4104 Ndisuio (136185f9fb2cc61e573e676aa5402356) C:\Windows\system32\DRIVERS\ndisuio.sys
03:35:42.0688 4104 Ndisuio - ok
03:35:42.0727 4104 NdisWan (53f7305169863f0a2bddc49e116c2e11) C:\Windows\system32\DRIVERS\ndiswan.sys
03:35:42.0730 4104 NdisWan - ok
03:35:42.0759 4104 NDProxy (015c0d8e0e0421b4cfd48cffe2825879) C:\Windows\system32\drivers\NDProxy.sys
03:35:42.0761 4104 NDProxy - ok
03:35:42.0790 4104 NetBIOS (86743d9f5d2b1048062b14b1d84501c4) C:\Windows\system32\DRIVERS\netbios.sys
03:35:42.0792 4104 NetBIOS - ok
03:35:42.0828 4104 NetBT (09594d1089c523423b32a4229263f068) C:\Windows\system32\DRIVERS\netbt.sys
03:35:42.0831 4104 NetBT - ok
03:35:42.0856 4104 nfrd960 (77889813be4d166cdab78ddba990da92) C:\Windows\system32\DRIVERS\nfrd960.sys
03:35:42.0857 4104 nfrd960 - ok
03:35:42.0890 4104 npf (351533acc2a069b94e80bbfc177e8fdf) C:\Windows\system32\drivers\npf.sys
03:35:42.0911 4104 npf - ok
03:35:42.0927 4104 Npfs (1e4c4ab5c9b8dd13179bbdc75a2a01f7) C:\Windows\system32\drivers\Npfs.sys
03:35:42.0938 4104 Npfs - ok
03:35:42.0960 4104 nsiproxy (e7f5ae18af4168178a642a9247c63001) C:\Windows\system32\drivers\nsiproxy.sys
03:35:42.0961 4104 nsiproxy - ok
03:35:43.0032 4104 Ntfs (a2f74975097f52a00745f9637451fdd8) C:\Windows\system32\drivers\Ntfs.sys
03:35:43.0088 4104 Ntfs - ok
03:35:43.0277 4104 NuidFltr (77eb11da191d12d12e28d7bd8905c42c) C:\Windows\system32\DRIVERS\NuidFltr.sys
03:35:43.0278 4104 NuidFltr - ok
03:35:43.0309 4104 Null (9899284589f75fa8724ff3d16aed75c1) C:\Windows\system32\drivers\Null.sys
03:35:43.0310 4104 Null - ok
03:35:43.0394 4104 nvraid (0a92cb65770442ed0dc44834632f66ad) C:\Windows\system32\drivers\nvraid.sys
03:35:43.0397 4104 nvraid - ok
03:35:43.0451 4104 nvstor (dab0e87525c10052bf65f06152f37e4a) C:\Windows\system32\drivers\nvstor.sys
03:35:43.0455 4104 nvstor - ok
03:35:43.0481 4104 nv_agp (270d7cd42d6e3979f6dd0146650f0e05) C:\Windows\system32\drivers\nv_agp.sys
03:35:43.0482 4104 nv_agp - ok
03:35:43.0547 4104 ohci1394 (3589478e4b22ce21b41fa1bfc0b8b8a0) C:\Windows\system32\drivers\ohci1394.sys
03:35:43.0549 4104 ohci1394 - ok
03:35:43.0593 4104 osaio (5cbce1c10d7830946599011296689f6f) C:\Windows\system32\drivers\osaio.sys
03:35:43.0693 4104 osaio - ok
03:35:43.0755 4104 Parport (0086431c29c35be1dbc43f52cc273887) C:\Windows\system32\DRIVERS\parport.sys
03:35:43.0757 4104 Parport - ok
03:35:43.0791 4104 partmgr (871eadac56b0a4c6512bbe32753ccf79) C:\Windows\system32\drivers\partmgr.sys
03:35:43.0793 4104 partmgr - ok
03:35:43.0812 4104 pci (94575c0571d1462a0f70bde6bd6ee6b3) C:\Windows\system32\drivers\pci.sys
03:35:43.0814 4104 pci - ok
03:35:43.0829 4104 pciide (b5b8b5ef2e5cb34df8dcf8831e3534fa) C:\Windows\system32\drivers\pciide.sys
03:35:43.0830 4104 pciide - ok
03:35:43.0856 4104 pcmcia (b2e81d4e87ce48589f98cb8c05b01f2f) C:\Windows\system32\DRIVERS\pcmcia.sys
03:35:43.0857 4104 pcmcia - ok
03:35:43.0880 4104 pcw (d6b9c2e1a11a3a4b26a182ffef18f603) C:\Windows\system32\drivers\pcw.sys
03:35:43.0882 4104 pcw - ok
03:35:43.0900 4104 PEAUTH (68769c3356b3be5d1c732c97b9a80d6e) C:\Windows\system32\drivers\peauth.sys
03:35:43.0907 4104 PEAUTH - ok
03:35:43.0948 4104 Point64 (4f0878fd62d5f7444c5f1c4c66d9d293) C:\Windows\system32\DRIVERS\point64.sys
03:35:43.0950 4104 Point64 - ok
03:35:43.0987 4104 PptpMiniport (f92a2c41117a11a00be01ca01a7fcde9) C:\Windows\system32\DRIVERS\raspptp.sys
03:35:43.0989 4104 PptpMiniport - ok
03:35:44.0009 4104 Processor (0d922e23c041efb1c3fac2a6f943c9bf) C:\Windows\system32\DRIVERS\processr.sys
03:35:44.0010 4104 Processor - ok
03:35:44.0067 4104 Psched (0557cf5a2556bd58e26384169d72438d) C:\Windows\system32\DRIVERS\pacer.sys
03:35:44.0071 4104 Psched - ok
03:35:44.0185 4104 PxHlpa64 (f2eecf8977bd3fe4e38743ddcfbecd20) C:\Windows\system32\Drivers\PxHlpa64.sys
03:35:44.0197 4104 PxHlpa64 - ok
03:35:44.0312 4104 ql2300 (a53a15a11ebfd21077463ee2c7afeef0) C:\Windows\system32\DRIVERS\ql2300.sys
03:35:44.0318 4104 ql2300 - ok
03:35:44.0355 4104 ql40xx (4f6d12b51de1aaeff7dc58c4d75423c8) C:\Windows\system32\DRIVERS\ql40xx.sys
03:35:44.0356 4104 ql40xx - ok
03:35:44.0530 4104 QW720V64 (ae06d75f402de21c922bcecb30f8fb50) C:\Windows\system32\DRIVERS\WLANUHN.sys
03:35:44.0536 4104 QW720V64 - ok
03:35:44.0573 4104 QWAVEdrv (76707bb36430888d9ce9d705398adb6c) C:\Windows\system32\drivers\qwavedrv.sys
03:35:44.0587 4104 QWAVEdrv - ok
03:35:44.0684 4104 RasAcd (5a0da8ad5762fa2d91678a8a01311704) C:\Windows\system32\DRIVERS\rasacd.sys
03:35:44.0685 4104 RasAcd - ok
03:35:44.0791 4104 RasAgileVpn (7ecff9b22276b73f43a99a15a6094e90) C:\Windows\system32\DRIVERS\AgileVpn.sys
03:35:44.0796 4104 RasAgileVpn - ok
03:35:44.0854 4104 Rasl2tp (471815800ae33e6f1c32fb1b97c490ca) C:\Windows\system32\DRIVERS\rasl2tp.sys
03:35:44.0865 4104 Rasl2tp - ok
03:35:44.0894 4104 RasPppoe (855c9b1cd4756c5e9a2aa58a15f58c25) C:\Windows\system32\DRIVERS\raspppoe.sys
03:35:44.0907 4104 RasPppoe - ok
03:35:44.0957 4104 RasSstp (e8b1e447b008d07ff47d016c2b0eeecb) C:\Windows\system32\DRIVERS\rassstp.sys
03:35:44.0970 4104 RasSstp - ok
03:35:45.0073 4104 rdbss (77f665941019a1594d887a74f301fa2f) C:\Windows\system32\DRIVERS\rdbss.sys
03:35:45.0085 4104 rdbss - ok
03:35:45.0147 4104 rdpbus (302da2a0539f2cf54d7c6cc30c1f2d8d) C:\Windows\system32\DRIVERS\rdpbus.sys
03:35:45.0158 4104 rdpbus - ok
03:35:45.0220 4104 RDPCDD (cea6cc257fc9b7715f1c2b4849286d24) C:\Windows\system32\DRIVERS\RDPCDD.sys
03:35:45.0227 4104 RDPCDD - ok
03:35:45.0276 4104 RDPENCDD (bb5971a4f00659529a5c44831af22365) C:\Windows\system32\drivers\rdpencdd.sys
03:35:45.0277 4104 RDPENCDD - ok
03:35:45.0359 4104 RDPREFMP (216f3fa57533d98e1f74ded70113177a) C:\Windows\system32\drivers\rdprefmp.sys
03:35:45.0360 4104 RDPREFMP - ok
03:35:45.0440 4104 RDPWD (15b66c206b5cb095bab980553f38ed23) C:\Windows\system32\drivers\RDPWD.sys
03:35:45.0441 4104 RDPWD - ok
03:35:45.0530 4104 rdyboost (34ed295fa0121c241bfef24764fc4520) C:\Windows\system32\drivers\rdyboost.sys
03:35:45.0554 4104 rdyboost - ok
03:35:45.0681 4104 rspndr (ddc86e4f8e7456261e637e3552e804ff) C:\Windows\system32\DRIVERS\rspndr.sys
03:35:45.0683 4104 rspndr - ok
03:35:45.0748 4104 Sahdad64 (27db9153d259d632d15483deeab799ed) C:\Windows\system32\Drivers\Sahdad64.sys
03:35:45.0782 4104 Sahdad64 - ok
03:35:45.0853 4104 Saibad64 (f77849d909b90bcacfcf7295aecf299b) C:\Windows\system32\Drivers\Saibad64.sys
03:35:45.0854 4104 Saibad64 - ok
03:35:45.0933 4104 SaibVdAd64 (704d415290a568f68de20942dac23f7e) C:\Windows\system32\Drivers\SaibVdAd64.sys
03:35:45.0949 4104 SaibVdAd64 - ok
03:35:46.0010 4104 sbp2port (ac03af3329579fffb455aa2daabbe22b) C:\Windows\system32\drivers\sbp2port.sys
03:35:46.0011 4104 sbp2port - ok
03:35:46.0079 4104 scfilter (253f38d0d7074c02ff8deb9836c97d2b) C:\Windows\system32\DRIVERS\scfilter.sys
03:35:46.0080 4104 scfilter - ok
03:35:46.0174 4104 secdrv (3ea8a16169c26afbeb544e0e48421186) C:\Windows\system32\drivers\secdrv.sys
03:35:46.0183 4104 secdrv - ok
03:35:46.0214 4104 Serenum (cb624c0035412af0debec78c41f5ca1b) C:\Windows\system32\DRIVERS\serenum.sys
03:35:46.0216 4104 Serenum - ok
03:35:46.0281 4104 Serial (c1d8e28b2c2adfaec4ba89e9fda69bd6) C:\Windows\system32\DRIVERS\serial.sys
03:35:46.0297 4104 Serial - ok
03:35:46.0377 4104 sermouse (1c545a7d0691cc4a027396535691c3e3) C:\Windows\system32\DRIVERS\sermouse.sys
03:35:46.0384 4104 sermouse - ok
03:35:46.0448 4104 sffdisk (a554811bcd09279536440c964ae35bbf) C:\Windows\system32\drivers\sffdisk.sys
03:35:46.0459 4104 sffdisk - ok
03:35:46.0493 4104 sffp_mmc (ff414f0baefeba59bc6c04b3db0b87bf) C:\Windows\system32\drivers\sffp_mmc.sys
03:35:46.0504 4104 sffp_mmc - ok
03:35:46.0564 4104 sffp_sd (dd85b78243a19b59f0637dcf284da63c) C:\Windows\system32\drivers\sffp_sd.sys
03:35:46.0565 4104 sffp_sd - ok
03:35:46.0610 4104 sfloppy (a9d601643a1647211a1ee2ec4e433ff4) C:\Windows\system32\DRIVERS\sfloppy.sys
03:35:46.0626 4104 sfloppy - ok
03:35:46.0714 4104 SiSRaid2 (843caf1e5fde1ffd5ff768f23a51e2e1) C:\Windows\system32\DRIVERS\SiSRaid2.sys
03:35:46.0715 4104 SiSRaid2 - ok
03:35:46.0774 4104 SiSRaid4 (6a6c106d42e9ffff8b9fcb4f754f6da4) C:\Windows\system32\DRIVERS\sisraid4.sys
03:35:46.0775 4104 SiSRaid4 - ok
03:35:46.0850 4104 Smb (548260a7b8654e024dc30bf8a7c5baa4) C:\Windows\system32\DRIVERS\smb.sys
03:35:46.0852 4104 Smb - ok
03:35:46.0933 4104 SndTAudio (c966fb8fdb6736bceef3e0e90a260eb3) C:\Windows\system32\drivers\SndTAudio.sys
03:35:46.0968 4104 SndTAudio - ok
03:35:46.0996 4104 spldr (b9e31e5cacdfe584f34f730a677803f9) C:\Windows\system32\drivers\spldr.sys
03:35:46.0998 4104 spldr - ok
03:35:47.0258 4104 SRTSP (1321a6c3c92bbd3f3bbe1292cff8e91a) C:\Windows\System32\Drivers\NAVx64\1301000.01C\SRTSP64.SYS
03:35:47.0261 4104 SRTSP - ok
03:35:47.0385 4104 SRTSPX (bd129c22c3b8c2e584227269dfa77b09) C:\Windows\system32\drivers\NAVx64\1301010.003\SRTSPX64.SYS
03:35:47.0385 4104 SRTSPX - ok
03:35:47.0458 4104 srv (441fba48bff01fdb9d5969ebc1838f0b) C:\Windows\system32\DRIVERS\srv.sys
03:35:47.0470 4104 srv - ok
03:35:47.0525 4104 srv2 (b4adebbf5e3677cce9651e0f01f7cc28) C:\Windows\system32\DRIVERS\srv2.sys
03:35:47.0531 4104 srv2 - ok
03:35:47.0561 4104 srvnet (27e461f0be5bff5fc737328f749538c3) C:\Windows\system32\DRIVERS\srvnet.sys
03:35:47.0565 4104 srvnet - ok
03:35:47.0601 4104 stexstor (f3817967ed533d08327dc73bc4d5542a) C:\Windows\system32\DRIVERS\stexstor.sys
03:35:47.0602 4104 stexstor - ok
03:35:47.0669 4104 SWDUMon (8022e37e0ee9125aa39650f56d3ab634) C:\Windows\system32\DRIVERS\SWDUMon.sys
03:35:47.0707 4104 SWDUMon - ok
03:35:47.0789 4104 swenum (d01ec09b6711a5f8e7e6564a4d0fbc90) C:\Windows\system32\drivers\swenum.sys
03:35:47.0792 4104 swenum - ok
03:35:48.0059 4104 SymDS (8b2430762099598da40686f754632efd) C:\Windows\system32\drivers\NAVx64\1301010.003\SYMDS64.SYS
03:35:48.0060 4104 SymDS - ok
03:35:48.0372 4104 SymEFA (fe29b18bf86ffcd55d8733c9b01e5042) C:\Windows\system32\drivers\NAVx64\1301010.003\SYMEFA64.SYS
03:35:48.0376 4104 SymEFA - ok
03:35:48.0473 4104 SymEvent (36b77f5c9e21f88a8c8ec67ad5415819) C:\Windows\system32\Drivers\SYMEVENT64x86.SYS
03:35:48.0476 4104 SymEvent - ok
03:35:48.0563 4104 SymIRON (dd70da422460fded831d211df151d560) C:\Windows\system32\drivers\NAVx64\1301010.003\Ironx64.SYS
03:35:48.0564 4104 SymIRON - ok
03:35:48.0689 4104 SymNetS (bce4eb2eef05e388959b46fd21388c2d) C:\Windows\System32\Drivers\NAVx64\1301000.01C\SYMNETS.SYS
03:35:48.0691 4104 SymNetS - ok
03:35:48.0777 4104 SysCow (1f1d1bcc1b746de700e3e21d758262a7) C:\Windows\system32\drivers\syscowad64v.sys
03:35:48.0810 4104 SysCow - ok
03:35:49.0031 4104 Tcpip (f0e98c00a09fdf791525829a1d14240f) C:\Windows\system32\drivers\tcpip.sys
03:35:49.0051 4104 Tcpip - ok
03:35:49.0213 4104 TCPIP6 (f0e98c00a09fdf791525829a1d14240f) C:\Windows\system32\DRIVERS\tcpip.sys
03:35:49.0220 4104 TCPIP6 - ok
03:35:49.0307 4104 tcpipreg (df687e3d8836bfb04fcc0615bf15a519) C:\Windows\system32\drivers\tcpipreg.sys
03:35:49.0325 4104 tcpipreg - ok
03:35:49.0363 4104 TDPIPE (3371d21011695b16333a3934340c4e7c) C:\Windows\system32\drivers\tdpipe.sys
03:35:49.0364 4104 TDPIPE - ok
03:35:49.0405 4104 TDTCP (e4245bda3190a582d55ed09e137401a9) C:\Windows\system32\drivers\tdtcp.sys
03:35:49.0425 4104 TDTCP - ok
03:35:49.0490 4104 tdx (ddad5a7ab24d8b65f8d724f5c20fd806) C:\Windows\system32\DRIVERS\tdx.sys
03:35:49.0504 4104 tdx - ok
03:35:49.0559 4104 TermDD (561e7e1f06895d78de991e01dd0fb6e5) C:\Windows\system32\drivers\termdd.sys
03:35:49.0570 4104 TermDD - ok
03:35:49.0605 4104 tssecsrv (ce18b2cdfc837c99e5fae9ca6cba5d30) C:\Windows\system32\DRIVERS\tssecsrv.sys
03:35:49.0606 4104 tssecsrv - ok
03:35:49.0693 4104 TsUsbFlt (d11c783e3ef9a3c52c0ebe83cc5000e9) C:\Windows\system32\drivers\tsusbflt.sys
03:35:49.0694 4104 TsUsbFlt - ok
03:35:49.0771 4104 tunnel (3566a8daafa27af944f5d705eaa64894) C:\Windows\system32\DRIVERS\tunnel.sys
03:35:49.0773 4104 tunnel - ok
03:35:49.0822 4104 uagp35 (b4dd609bd7e282bfc683cec7eaaaad67) C:\Windows\system32\DRIVERS\uagp35.sys
03:35:49.0823 4104 uagp35 - ok
03:35:49.0920 4104 udfs (ff4232a1a64012baa1fd97c7b67df593) C:\Windows\system32\DRIVERS\udfs.sys
03:35:49.0922 4104 udfs - ok
03:35:49.0985 4104 uliagpkx (4bfe1bc28391222894cbf1e7d0e42320) C:\Windows\system32\drivers\uliagpkx.sys
03:35:49.0986 4104 uliagpkx - ok
03:35:50.0038 4104 umbus (dc54a574663a895c8763af0fa1ff7561) C:\Windows\system32\drivers\umbus.sys
03:35:50.0053 4104 umbus - ok
03:35:50.0084 4104 UmPass (b2e8e8cb557b156da5493bbddcc1474d) C:\Windows\system32\DRIVERS\umpass.sys
03:35:50.0099 4104 UmPass - ok
03:35:50.0168 4104 usbccgp (6f1a3157a1c89435352ceb543cdb359c) C:\Windows\system32\DRIVERS\usbccgp.sys
03:35:50.0170 4104 usbccgp - ok
03:35:50.0224 4104 usbcir (af0892a803fdda7492f595368e3b68e7) C:\Windows\system32\drivers\usbcir.sys
03:35:50.0227 4104 usbcir - ok
03:35:50.0283 4104 usbehci (c025055fe7b87701eb042095df1a2d7b) C:\Windows\system32\drivers\usbehci.sys
03:35:50.0285 4104 usbehci - ok
03:35:50.0319 4104 usbhub (287c6c9410b111b68b52ca298f7b8c24) C:\Windows\system32\DRIVERS\usbhub.sys
03:35:50.0328 4104 usbhub - ok
03:35:50.0401 4104 usbohci (9840fc418b4cbd632d3d0a667a725c31) C:\Windows\system32\drivers\usbohci.sys
03:35:50.0411 4104 usbohci - ok
03:35:50.0439 4104 usbprint (73188f58fb384e75c4063d29413cee3d) C:\Windows\system32\DRIVERS\usbprint.sys
03:35:50.0441 4104 usbprint - ok
03:35:50.0520 4104 usbscan (aaa2513c8aed8b54b189fd0c6b1634c0) C:\Windows\system32\DRIVERS\usbscan.sys
03:35:50.0522 4104 usbscan - ok
03:35:50.0586 4104 USBSTOR (fed648b01349a3c8395a5169db5fb7d6) C:\Windows\system32\DRIVERS\USBSTOR.SYS
03:35:50.0598 4104 USBSTOR - ok
03:35:50.0636 4104 usbuhci (62069a34518bcf9c1fd9e74b3f6db7cd) C:\Windows\system32\drivers\usbuhci.sys
03:35:50.0651 4104 usbuhci - ok
03:35:50.0691 4104 vdrvroot (c5c876ccfc083ff3b128f933823e87bd) C:\Windows\system32\drivers\vdrvroot.sys
03:35:50.0693 4104 vdrvroot - ok
03:35:50.0740 4104 vga (da4da3f5e02943c2dc8c6ed875de68dd) C:\Windows\system32\DRIVERS\vgapnp.sys
03:35:50.0743 4104 vga - ok
03:35:50.0785 4104 VgaSave (53e92a310193cb3c03bea963de7d9cfc) C:\Windows\System32\drivers\vga.sys
03:35:50.0796 4104 VgaSave - ok
03:35:50.0853 4104 vhdmp (2ce2df28c83aeaf30084e1b1eb253cbb) C:\Windows\system32\drivers\vhdmp.sys
03:35:50.0855 4104 vhdmp - ok
03:35:50.0887 4104 viaide (e5689d93ffe4e5d66c0178761240dd54) C:\Windows\system32\drivers\viaide.sys
03:35:50.0888 4104 viaide - ok
03:35:50.0922 4104 volmgr (d2aafd421940f640b407aefaaebd91b0) C:\Windows\system32\drivers\volmgr.sys
03:35:50.0932 4104 volmgr - ok
03:35:51.0042 4104 volmgrx (a255814907c89be58b79ef2f189b843b) C:\Windows\system32\drivers\volmgrx.sys
03:35:51.0053 4104 volmgrx - ok
03:35:51.0120 4104 volsnap (0d08d2f3b3ff84e433346669b5e0f639) C:\Windows\system32\drivers\volsnap.sys
03:35:51.0135 4104 volsnap - ok
03:35:51.0200 4104 vsmraid (5e2016ea6ebaca03c04feac5f330d997) C:\Windows\system32\DRIVERS\vsmraid.sys
03:35:51.0202 4104 vsmraid - ok
03:35:51.0242 4104 vwifibus (36d4720b72b5c5d9cb2b9c29e9df67a1) C:\Windows\System32\drivers\vwifibus.sys
03:35:51.0252 4104 vwifibus - ok
03:35:51.0316 4104 WacomPen (4e9440f4f152a7b944cb1663d3935a3e) C:\Windows\system32\DRIVERS\wacompen.sys
03:35:51.0331 4104 WacomPen - ok
03:35:51.0355 4104 WANARP (356afd78a6ed4457169241ac3965230c) C:\Windows\system32\DRIVERS\wanarp.sys
03:35:51.0358 4104 WANARP - ok
03:35:51.0385 4104 Wanarpv6 (356afd78a6ed4457169241ac3965230c) C:\Windows\system32\DRIVERS\wanarp.sys
03:35:51.0386 4104 Wanarpv6 - ok
03:35:51.0493 4104 Wd (72889e16ff12ba0f235467d6091b17dc) C:\Windows\system32\DRIVERS\wd.sys
03:35:51.0494 4104 Wd - ok
03:35:51.0678 4104 Wdf01000 (441bd2d7b4f98134c3a4f9fa570fd250) C:\Windows\system32\drivers\Wdf01000.sys
03:35:51.0694 4104 Wdf01000 - ok
03:35:51.0751 4104 WfpLwf (611b23304bf067451a9fdee01fbdd725) C:\Windows\system32\DRIVERS\wfplwf.sys
03:35:51.0759 4104 WfpLwf - ok
03:35:51.0831 4104 WIMMount (05ecaec3e4529a7153b3136ceb49f0ec) C:\Windows\system32\drivers\wimmount.sys
03:35:51.0833 4104 WIMMount - ok
03:35:51.0888 4104 WinUsb (fe88b288356e7b47b74b13372add906d) C:\Windows\system32\DRIVERS\WinUsb.sys
03:35:51.0888 4104 WinUsb - ok
03:35:51.0987 4104 WmiAcpi (f6ff8944478594d0e414d3f048f0d778) C:\Windows\system32\drivers\wmiacpi.sys
03:35:51.0988 4104 WmiAcpi - ok
03:35:52.0050 4104 ws2ifsl (6bcc1d7d2fd2453957c5479a32364e52) C:\Windows\system32\drivers\ws2ifsl.sys
03:35:52.0063 4104 ws2ifsl - ok
03:35:52.0151 4104 WudfPf (d3381dc54c34d79b22cee0d65ba91b7c) C:\Windows\system32\drivers\WudfPf.sys
03:35:52.0161 4104 WudfPf - ok
03:35:52.0224 4104 WUDFRd (cf8d590be3373029d57af80914190682) C:\Windows\system32\DRIVERS\WUDFRd.sys
03:35:52.0226 4104 WUDFRd - ok
03:35:52.0277 4104 ZDCNDIS6a64 (18b6869e23937175144e6f1d3cb85fc2) C:\Windows\system32\ZDCNDIS6a64.sys
03:35:52.0279 4104 ZDCNDIS6a64 - ok
03:35:52.0296 4104 MBR (0x1B8) (2fa2a6e99e849537bd5ee24ac604b721) \Device\Harddisk1\DR1
03:35:52.0320 4104 \Device\Harddisk1\DR1 - ok
03:35:52.0322 4104 MBR (0x1B8) (a36c5e4f47e84449ff07ed3517b43a31) \Device\Harddisk0\DR0
03:35:52.0325 4104 \Device\Harddisk0\DR0 - ok
03:35:52.0334 4104 Boot (0x1200) (fa4d990b83dd7bd30be473f35e33987b) \Device\Harddisk1\DR1\Partition0
03:35:52.0336 4104 \Device\Harddisk1\DR1\Partition0 - ok
03:35:52.0349 4104 Boot (0x1200) (12e3f9bb3da977d716aacd627d0db397) \Device\Harddisk1\DR1\Partition1
03:35:52.0357 4104 \Device\Harddisk1\DR1\Partition1 - ok
03:35:52.0359 4104 Boot (0x1200) (e16c4df1812a75d3cd679a9fb6b760f9) \Device\Harddisk0\DR0\Partition0
03:35:52.0360 4104 \Device\Harddisk0\DR0\Partition0 - ok
03:35:52.0361 4104 ============================================================
03:35:52.0361 4104 Scan finished
03:35:52.0361 4104 ============================================================
03:35:52.0368 5672 Detected object count: 0
03:35:52.0369 5672 Actual detected object count: 0
03:36:54.0333 5548 Deinitialize success
ComboFix 11-10-24.01 - Smooth_Top 10/24/2011 3:46.1.4 - x64
Microsoft Windows 7 Home Premium 6.1.7601.1.1252.1.1033.18.4029.2414 [GMT -6:00]
Running from: c:\users\[removed]\Desktop\ComboFix.exe
AV: Norton AntiVirus Online *Disabled/Updated* {63DF5164-9100-186D-2187-8DC619EFD8BF}
SP: Norton AntiVirus Online *Enabled/Updated* {D8BEB080-B73A-17E3-1B37-B6B462689202}
SP: Windows Defender *Disabled/Updated* {D68DDC3A-831F-4fae-9E44-DA132C1ACF46}
* Created a new restore point
.
.
((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.
.
c:\programdata\Tarma Installer
c:\programdata\Tarma Installer\{889DF117-14D1-44EE-9F31-C5FB5D47F68B}\_Setup.dll
c:\programdata\Tarma Installer\{889DF117-14D1-44EE-9F31-C5FB5D47F68B}\_Setupx.dll
c:\programdata\Tarma Installer\{889DF117-14D1-44EE-9F31-C5FB5D47F68B}\Setup.exe
c:\programdata\Tarma Installer\{889DF117-14D1-44EE-9F31-C5FB5D47F68B}\Setup.ico
c:\programdata\Tarma Installer\{DE3B7BF9-0770-4104-BC0B-B1CCCCE2F053}\_Setup.dll
c:\programdata\Tarma Installer\{DE3B7BF9-0770-4104-BC0B-B1CCCCE2F053}\_Setupx.dll
c:\programdata\Tarma Installer\{DE3B7BF9-0770-4104-BC0B-B1CCCCE2F053}\Setup.dat
c:\programdata\Tarma Installer\{DE3B7BF9-0770-4104-BC0B-B1CCCCE2F053}\Setup.exe
c:\programdata\Tarma Installer\{DE3B7BF9-0770-4104-BC0B-B1CCCCE2F053}\Setup.ico
c:\users\Smooth_Top\Desktop\Setup.exe
c:\windows\SysWow64\Packet.dll
c:\windows\SysWow64\pthreadVC.dll
c:\windows\SysWow64\wpcap.dll
E:\install.exe
.
.
((((((((((((((((((((((((((((((((((((((( Drivers/Services )))))))))))))))))))))))))))))))))))))))))))))))))
.
.
——-\Legacy_NPF
——-\Service_npf
.
.
((((((((((((((((((((((((( Files Created from 2011-09-24 to 2011-10-24 )))))))))))))))))))))))))))))))
.
.
2011-10-24 06:54 . 2011-10-24 11:09 ——– d—–w- c:\windows\system32\drivers\NAVx64\1301010.003
2011-10-22 06:05 . 2011-10-22 06:05 ——– dc-h–w- c:\programdata\{4E78170A-6049-4586-A083-3AECE1A687E4}
2011-10-22 06:05 . 2011-10-22 06:05 ——– d—–w- c:\program files\WinSysClean X2
2011-10-22 06:02 . 2011-10-22 06:02 ——– d—–w- c:\users\Smooth_Top\AppData\Roaming\Roxio Burn
2011-10-21 16:27 . 2011-10-21 16:27 ——– d—–w- C:\System Rollback Data
2011-10-21 06:43 . 2011-10-21 06:43 ——– d—–w- c:\users\Smooth_Top\AppData\Roaming\FLEXnet
2011-10-21 06:39 . 2011-10-21 06:39 ——– d—–w- c:\programdata\Uninstall
2011-10-21 06:38 . 2011-02-09 07:00 27632 ——w- c:\windows\system32\drivers\SaibVdAd64.sys
2011-10-21 06:38 . 2011-02-09 07:00 27120 ——w- c:\windows\system32\drivers\Sahdad64.sys
2011-10-21 06:38 . 2011-02-09 07:00 19952 ——w- c:\windows\system32\drivers\Saibad64.sys
2011-10-21 06:38 . 2011-10-21 06:38 ——– d—–w- c:\program files (x86)\Roxio
2011-10-21 06:32 . 2011-10-21 06:32 ——– d—–w- c:\program files\Roxio
2011-10-21 06:31 . 2011-10-21 06:37 ——– d—–w- c:\program files (x86)\Common Files\Sonic Shared
2011-10-21 06:31 . 2011-10-21 06:35 ——– d—–w- c:\program files (x86)\Common Files\Roxio Shared
2011-10-21 06:31 . 2011-10-21 06:39 ——– d—–w- c:\program files (x86)\Roxio 2012
2011-10-21 06:31 . 2011-10-21 06:31 ——– d—–w- c:\program files\Roxio 2012
2011-10-21 06:31 . 2011-10-21 06:31 53248 —-a-r- c:\users\Smooth_Top\AppData\Roaming\Microsoft\Installer\{3A9527CF-4E91-4683-A03F-F1AD022126E5}\ARPPRODUCTICON.exe
2011-10-20 09:55 . 2011-10-20 09:55 ——– d—–w- c:\users\Smooth_Top\AppData\Roaming\Malwarebytes
2011-10-20 09:55 . 2011-10-20 09:55 ——– d—–w- c:\programdata\Malwarebytes
2011-10-20 09:55 . 2011-10-20 09:55 ——– d—–w- c:\program files (x86)\Malwarebytes' Anti-Malware
2011-10-20 09:55 . 2011-08-31 23:00 25416 —-a-w- c:\windows\system32\drivers\mbam.sys
2011-10-20 04:54 . 2011-10-20 04:54 ——– d—–w- c:\program files (x86)\iResizer
2011-10-17 19:01 . 2011-10-17 19:02 ——– d—–w- c:\program files\iTunes
2011-10-17 19:01 . 2011-10-17 19:02 ——– d—–w- c:\program files (x86)\iTunes
2011-10-17 19:01 . 2011-10-17 19:01 ——– d—–w- c:\program files\iPod
2011-10-17 18:58 . 2011-10-17 18:58 ——– d—–w- c:\program files\Bonjour
2011-10-17 18:58 . 2011-10-17 18:58 ——– d—–w- c:\program files (x86)\Bonjour
2011-10-14 21:09 . 2011-10-14 21:09 ——– d—–w- c:\program files (x86)\Yontoo Layers Runtime
2011-10-13 23:22 . 2011-10-13 23:22 ——– d—–w- c:\program files (x86)\Common Files\Kodak
2011-10-13 23:20 . 2011-10-13 23:20 ——– d—–w- c:\programdata\{A0559A84-0A11-425F-BFFC-532378694B25}
2011-10-13 19:30 . 2011-09-06 03:03 3138048 —-a-w- c:\windows\system32\win32k.sys
2011-10-13 19:30 . 2011-08-17 05:26 613888 —-a-w- c:\windows\system32\psisdecd.dll
2011-10-13 19:30 . 2011-08-17 04:24 465408 —-a-w- c:\windows\SysWow64\psisdecd.dll
2011-10-13 19:30 . 2011-08-17 04:19 75776 —-a-w- c:\windows\SysWow64\psisrndr.ax
2011-10-13 19:30 . 2011-08-17 05:25 108032 —-a-w- c:\windows\system32\psisrndr.ax
2011-10-13 19:30 . 2011-08-27 05:37 861696 —-a-w- c:\windows\system32\oleaut32.dll
2011-10-13 19:30 . 2011-08-27 05:37 331776 —-a-w- c:\windows\system32\oleacc.dll
2011-10-13 19:30 . 2011-08-27 04:26 571904 —-a-w- c:\windows\SysWow64\oleaut32.dll
2011-10-13 19:30 . 2011-08-27 04:26 233472 —-a-w- c:\windows\SysWow64\oleacc.dll
2011-10-05 08:46 . 2011-10-05 08:47 ——– d—–w- c:\users\Smooth_Top\AppData\Roaming\vlc
2011-10-05 08:45 . 2011-10-05 08:45 ——– d—–w- c:\users\Smooth_Top\AppData\Local\Ilivid Player
2011-10-05 08:43 . 2011-10-13 19:23 ——– d—–w- c:\programdata\boost_interprocess
2011-10-04 04:16 . 2011-10-04 04:16 ——– d—–w- c:\program files (x86)\Advanced Registry Doctor Pro
2011-09-29 18:28 . 2011-09-29 18:28 ——– d—–w- c:\program files (x86)\Almeza
2011-09-29 04:12 . 2011-09-29 04:12 ——– d—–w- c:\users\Smooth_Top\AppData\Local\Conduit
2011-09-28 22:25 . 2011-09-28 22:25 ——– d—–w- c:\program files (x86)\GameTop.com
2011-09-28 04:01 . 2011-09-28 04:01 ——– d—–w- c:\users\Smooth_Top\AppData\Roaming\Ashampoo
2011-09-28 04:01 . 2011-09-28 04:01 ——– d—–w- c:\users\Smooth_Top\AppData\Local\ashampoo
2011-09-28 04:01 . 2011-09-28 04:01 ——– d—–w- c:\programdata\ashampoo
2011-09-27 05:43 . 2011-09-27 05:43 ——– d—–w- c:\program files (x86)\StepShot
2011-09-27 05:42 . 2011-09-27 05:42 ——– d—–w- c:\users\Smooth_Top\AppData\Roaming\StepShot
2011-09-26 05:16 . 2011-09-26 05:17 ——– d—–w- C:\Games
2011-09-26 05:14 . 2011-09-26 05:14 ——– d—–w- c:\users\Smooth_Top\AppData\Roaming\VideoBooth
2011-09-26 05:14 . 2011-09-26 05:14 ——– d—–w- c:\program files (x86)\VideoBooth
.
.
.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2011-10-24 04:13 . 2011-06-06 18:38 174200 —-a-w- c:\windows\system32\drivers\SYMEVENT64x86.SYS
2011-10-13 19:25 . 2011-05-25 00:22 414368 —-a-w- c:\windows\SysWow64\FlashPlayerCPLApp.cpl
2011-09-05 20:49 . 2011-09-06 23:18 117808640 —-a-w- C:\PartitionManager.msi
2011-08-31 05:05 . 2011-08-31 05:05 96104 —-a-w- c:\windows\system32\dns-sd.exe
2011-08-31 05:05 . 2011-08-31 05:05 85864 —-a-w- c:\windows\system32\dnssd.dll
2011-08-31 05:05 . 2011-08-31 05:05 61288 —-a-w- c:\windows\system32\jdns_sd.dll
2011-08-31 05:05 . 2011-08-31 05:05 212840 —-a-w- c:\windows\system32\dnssdX.dll
2011-08-31 05:05 . 2011-08-31 05:05 83816 —-a-w- c:\windows\SysWow64\dns-sd.exe
2011-08-31 05:05 . 2011-08-31 05:05 73064 —-a-w- c:\windows\SysWow64\dnssd.dll
2011-08-31 05:05 . 2011-08-31 05:05 50536 —-a-w- c:\windows\SysWow64\jdns_sd.dll
2011-08-31 05:05 . 2011-08-31 05:05 178536 —-a-w- c:\windows\SysWow64\dnssdX.dll
2011-08-29 19:19 . 2011-08-29 19:19 249936 —-a-w- c:\windows\SysWow64\prgiso.dll
2011-08-29 19:19 . 2011-09-06 23:26 37456 —-a-w- c:\windows\system32\drivers\hotcore3.sys
2011-08-18 15:27 . 2011-08-20 22:45 892928 —-a-w- c:\windows\SysWow64\iconv.dll
2011-08-18 15:27 . 2011-08-20 22:45 675840 —-a-w- c:\windows\SysWow64\ac3filter.ax
2011-08-15 03:12 . 2011-08-15 03:12 18328 —-a-w- c:\programdata\Microsoft\IdentityCRL\production\ppcrlconfig600.dll
2011-08-07 02:46 . 2011-08-07 02:46 162068 —-a-w- c:\windows\Animated Screensaver Maker Uninstaller.exe
2011-08-03 02:48 . 2011-08-17 22:05 2469248 —-a-w- c:\windows\SysWow64\BootMan.exe
2011-08-03 02:48 . 2011-08-17 22:05 3320192 —-a-w- c:\windows\system32\BootMan.exe
2011-08-01 21:59 . 2011-08-01 21:59 45416 —-a-w- c:\windows\system32\drivers\point64.sys
2011-07-30 10:46 . 2011-06-11 19:06 2851840 —-a-w- c:\windows\system32\themeui.dll
2011-07-30 10:46 . 2009-07-13 23:54 44544 —-a-w- c:\windows\system32\themeservice.dll
2011-07-30 10:46 . 2009-07-13 23:55 332288 —-a-w- c:\windows\system32\uxtheme.dll
2011-07-29 19:54 . 2011-08-17 22:05 9096 —-a-w- c:\windows\system32\EuGdiDrv.sys
2011-07-29 19:54 . 2011-08-17 22:05 86408 —-a-w- c:\windows\SysWow64\setupempdrv03.exe
2011-07-29 19:54 . 2011-08-17 22:05 8456 —-a-w- c:\windows\SysWow64\EuGdiDrv.sys
2011-07-29 19:54 . 2011-08-17 22:05 16776 —-a-w- c:\windows\system32\epmntdrv.sys
2011-07-29 19:54 . 2011-08-17 22:05 14216 —-a-w- c:\windows\SysWow64\epmntdrv.sys
2011-07-29 19:54 . 2011-08-17 22:05 100232 —-a-w- c:\windows\system32\setupempdrvx64.exe
2011-07-29 19:54 . 2011-08-17 22:05 16256 —-a-w- c:\windows\system32\EuEpmGdi.dll
2011-07-29 19:54 . 2011-08-17 22:05 19840 —-a-w- c:\windows\SysWow64\EuEpmGdi.dll
2011-07-29 00:37 . 2011-07-29 00:37 52584 —-a-w- c:\windows\system32\drivers\dc3d.sys
2011-07-27 22:41 . 2011-07-28 22:45 5931520 —-a-w- C:\HFS4WIN_GAOTD_ea_xU.msi
2011-07-27 21:27 . 2011-07-28 22:52 60720 —-a-w- c:\windows\system32\drivers\gpt_loader.sys
2011-07-27 21:27 . 2011-07-28 22:52 42288 —-a-w- c:\windows\system32\drivers\mounthlp.sys
2011-07-27 21:27 . 2011-07-28 22:52 51504 —-a-w- c:\windows\system32\drivers\apmwin.sys
2011-07-27 21:27 . 2011-07-28 22:52 16176 —-a-w- c:\windows\system32\drivers\hfsplusrec.sys
2011-07-27 21:27 . 2011-07-28 22:52 196912 —-a-w- c:\windows\system32\drivers\hfsplus.sys
.
.
——- Sigcheck ——-
Note: Unsigned files aren't necessarily malware.
.
[7] 2011-02-26 . E38899074D4951D31B4040E994DD7C8D . 2870784 . . [6.1.7600.16385] .. c:\windows\winsxs\amd64_microsoft-windows-explorer_31bf3856ad364e35_6.1.7600.20910_none_ae79ed04ac56c4a9\explorer.exe
[7] 2011-02-26 . 0862495E0C825893DB75EF44FAEA8E93 . 2870272 . . [6.1.7600.16385] .. c:\windows\winsxs\amd64_microsoft-windows-explorer_31bf3856ad364e35_6.1.7600.16768_none_adc24107935a7e25\explorer.exe
[7] 2011-02-26 . 3B69712041F3D63605529BD66DC00C48 . 2871808 . . [6.1.7600.16385] .. c:\windows\winsxs\amd64_microsoft-windows-explorer_31bf3856ad364e35_6.1.7601.21669_none_b0333b22a99da332\explorer.exe
[-] 2011-02-25 . 5AFF38DDD8CBF1183BA811C4279F1904 . 2753024 . . [6.1.7600.16385] .. c:\windows\explorer.exe
[7] 2011-02-25 . 332FEAB1435662FC6C672E25BEB37BE3 . 2871808 . . [6.1.7600.16385] .. c:\windows\winsxs\amd64_microsoft-windows-explorer_31bf3856ad364e35_6.1.7601.17567_none_afa79dc39081d0ba\explorer.exe
[7] 2010-11-20 . AC4C51EB24AA95B77F705AB159189E24 . 2872320 . . [6.1.7600.16385] .. c:\windows\winsxs\amd64_microsoft-windows-explorer_31bf3856ad364e35_6.1.7601.17514_none_afdaac81905bf900\explorer.exe
[7] 2010-09-07 . 9AAAEC8DAC27AA17B053E6352AD233AE . 2870272 . . [6.1.7600.16385] .. c:\windows\winsxs\amd64_microsoft-windows-explorer_31bf3856ad364e35_6.1.7600.16450_none_adc508f19359a007\explorer.exe
[7] 2010-09-07 . B8EC4BD49CE8F6FC457721BFC210B67F . 2870272 . . [6.1.7600.16385] .. c:\windows\winsxs\amd64_microsoft-windows-explorer_31bf3856ad364e35_6.1.7600.20563_none_ae46d6aeac7ca7c7\explorer.exe
[7] 2010-09-07 . F170B4A061C9E026437B193B4D571799 . 2868224 . . [6.1.7600.16385] .. c:\windows\winsxs\amd64_microsoft-windows-explorer_31bf3856ad364e35_6.1.7600.16404_none_adff19b5932d79ae\explorer.exe
[7] 2010-09-07 . 700073016DAC1C3D2E7E2CE4223334B6 . 2868224 . . [6.1.7600.16385] .. c:\windows\winsxs\amd64_microsoft-windows-explorer_31bf3856ad364e35_6.1.7600.20500_none_ae84b558ac4eb41c\explorer.exe
[7] 2009-07-14 . C235A51CB740E45FFA0EBFB9BAFCDA64 . 2868224 . . [6.1.7600.16385] .. c:\windows\winsxs\amd64_microsoft-windows-explorer_31bf3856ad364e35_6.1.7600.16385_none_ada998b9936d7566\explorer.exe
.
((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4
.
[HKEY_LOCAL_MACHINE\Wow6432Node\~\Browser Helper Objects\{A317CB83-299C-4FC8-9ED7-2D64117D98EE}]
2009-11-17 17:33 81920 —-a-w- c:\program files (x86)\qwesttoolbar\qwesttoolbarDx.dll
.
[HKEY_LOCAL_MACHINE\Wow6432Node\~\Browser Helper Objects\{FD72061E-9FDE-484D-A58A-0BAB4151CAD8}]
2011-09-30 17:27 194848 —-a-w- c:\program files (x86)\Yontoo Layers Runtime\YontooIEClient.dll
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Toolbar]
"{A317CB83-299C-4FC8-9ED7-2D64117D98EE}"= "c:\program files (x86)\qwesttoolbar\qwesttoolbarDx.dll" [2009-11-17 81920]
.
[HKEY_CLASSES_ROOT\clsid\{a317cb83-299c-4fc8-9ed7-2d64117d98ee}]
.
[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"RocketDock"="c:\program files (x86)\CustoPackTools\utils\RocketDock\RocketDock.exe" [2010-06-22 495616]
"KGShareApp"="c:\program files (x86)\Kodak\KODAK Share Button App\KGShare_App.exe" [2011-09-22 394752]
"Sidebar"="c:\program files\Windows Sidebar\Sidebar.exe" [2010-11-20 1475584]
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run]
"Mamutu Guard"="c:\program files (x86)\MAMUTU\mamutu.exe" [2011-07-08 4277104]
"APSDaemon"="c:\program files (x86)\Common Files\Apple\Apple Application Support\APSDaemon.exe" [2011-09-27 59240]
"iTunesHelper"="c:\program files (x86)\iTunes\iTunesHelper.exe" [2011-10-10 421736]
"Malwarebytes' Anti-Malware"="c:\program files (x86)\Malwarebytes' Anti-Malware\mbamgui.exe" [2011-08-31 449608]
"RoxWatchTray"="c:\program files (x86)\Common Files\Roxio Shared\13.0\SharedCOM\RoxWatchTray13.exe" [2011-07-13 293360]
"ISUSPM"="c:\programdata\FLEXnet\Connect\11\\isuspm.exe" [2010-05-21 324976]
"CPMonitor"="c:\program files (x86)\Roxio 2012\5.0\CPMonitor.exe" [2011-07-08 84464]
"Desktop Disc Tool"="c:\program files (x86)\Roxio 2012\Roxio Burn\RoxioBurnLauncher.exe" [2011-06-13 506352]
.
c:\programdata\Microsoft\Windows\Start Menu\Programs\Startup\
Ashampoo MouseTracer.lnk - c:\program files (x86)\Ashampoo\Ashampoo MouseTracer\MouseTracer.exe [2011-9-12 737184]
.
[HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\policies\system]
"ConsentPromptBehaviorAdmin"= 5 (0x5)
"ConsentPromptBehaviorUser"= 3 (0x3)
"EnableUIADesktopToggle"= 0 (0x0)
.
[HKEY_LOCAL_MACHINE\system\currentcontrolset\control\lsa]
Security Packages REG_MULTI_SZ kerberos msv1_0 schannel wdigest tspkg pku2u livessp
.
R2 AutoInstallEJCD;Auto Install Eject CD Service;c:\users\SMOOTH~1\AppData\Local\Temp\RarSFX0\AutoInstallEJCDSVC.exe [x]
R2 clr_optimization_v4.0.30319_32;Microsoft .NET Framework NGEN v4.0.30319_X86;c:\windows\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe [2010-03-18 130384]
R2 clr_optimization_v4.0.30319_64;Microsoft .NET Framework NGEN v4.0.30319_X64;c:\windows\Microsoft.NET\Framework64\v4.0.30319\mscorsvw.exe [2010-03-18 138576]
R2 gupdate;Google Update Service (gupdate);c:\program files (x86)\Google\Update\GoogleUpdate.exe [2011-09-21 136176]
R2 Intel® Desktop Boards FSC Application Service;Intel® Desktop Boards FSC Application Service;c:\program files (x86)\Intel\FSC\FSCAppServ.exe [2011-04-19 57344]
R2 RoxWatch12;Roxio Hard Drive Watcher 12;c:\program files (x86)\Common Files\Roxio Shared\13.0\SharedCOM\RoxWatch13.exe [2011-07-13 340976]
R3 androidusb;ADB Interface Driver;c:\windows\system32\Drivers\androidusb.sys [x]
R3 CDVDService;CDVDService;c:\program files (x86)\1Step DVD Copy\CDVDService.exe [2011-02-16 385024]
R3 DfSdkS;Defragmentation-Service;c:\program files (x86)\Ashampoo\Ashampoo HDD Control\Dfsdks.exe [2009-08-25 544768]
R3 epmntdrv;epmntdrv;c:\windows\system32\epmntdrv.sys [2011-07-29 16776]
R3 EuGdiDrv;EuGdiDrv;c:\windows\system32\EuGdiDrv.sys [2011-07-29 9096]
R3 FARMNTIO;FARMNTIO;c:\windows\system32\drivers\farmntio.sys [x]
R3 GSService;GSService;c:\windows\SysWOW64\GSService.exe [2011-02-17 122880]
R3 gupdatem;Google Update Service (gupdatem);c:\program files (x86)\Google\Update\GoogleUpdate.exe [2011-09-21 136176]
R3 Hfsplus;Hfsplus;c:\windows\system32\DRIVERS\hfsplus.sys [x]
R3 RGService;RGService;c:\program files (x86)\GetRadio\RGService.exe [2011-02-17 385024]
R3 RoxMediaDB13;RoxMediaDB13;c:\program files (x86)\Common Files\Roxio Shared\13.0\SharedCOM\RoxMediaDB13.exe [2011-07-13 1095664]
R3 SMServer;SMServer;c:\windows\SysWOW64\snmvtsvc.exe [2011-02-17 245760]
R3 STSService;STSService;c:\program files (x86)\SoundTaxi Media Suite\STSService.exe [2011-02-16 385024]
R3 SWDUMon;SWDUMon;c:\windows\system32\DRIVERS\SWDUMon.sys [x]
R3 TsUsbFlt;TsUsbFlt;c:\windows\system32\drivers\tsusbflt.sys [x]
R3 WatAdminSvc;Windows Activation Technologies Service;c:\windows\system32\Wat\WatAdminSvc.exe [x]
R3 ZDCNDIS6a64;ZDCNDIS Protocol Driver;c:\windows\system32\ZDCNDIS6a64.sys [2011-06-03 41280]
R4 BOTService;BOTService;c:\program files (x86)\Roxio\BackOnTrack\Instant Restore\BOTService.exe [2011-07-14 211440]
R4 wlcrasvc;Windows Live Mesh remote connections service;c:\program files\Windows Live\Mesh\wlcrasvc.exe [2010-09-23 57184]
S0 apmwin;apmwin;c:\windows\system32\DRIVERS\apmwin.sys [x]
S0 gpt_loader;GUID Partition table support driver;c:\windows\system32\DRIVERS\gpt_loader.sys [x]
S0 hotcore3;hc3ServiceName;c:\windows\system32\DRIVERS\hotcore3.sys [x]
S0 mounthlp;Mounter helper driver for HFS volumes;c:\windows\system32\DRIVERS\mounthlp.sys [x]
S0 PxHlpa64;PxHlpa64;c:\windows\System32\Drivers\PxHlpa64.sys [x]
S0 Sahdad64;HDD Filter Driver;c:\windows\System32\Drivers\Sahdad64.sys [x]
S0 Saibad64;Volume Filter Driver;c:\windows\System32\Drivers\Saibad64.sys [x]
S0 SymDS;Symantec Data Store;c:\windows\system32\drivers\NAVx64\1301010.003\SYMDS64.SYS [x]
S0 SymEFA;Symantec Extended File Attributes;c:\windows\system32\drivers\NAVx64\1301010.003\SYMEFA64.SYS [x]
S0 SysCow;SysCow;c:\windows\system32\drivers\syscowad64v.sys [x]
S1 a2injectiondriver;a2injectiondriver;c:\program files (x86)\Mamutu\a2dix64.sys [2010-09-05 48216]
S1 a2util;a-squared Malware-IDS utility driver;c:\program files (x86)\Mamutu\a2util64.sys [2010-05-05 14720]
S1 BHDrvx64;BHDrvx64;c:\programdata\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NAV_19.1.0.28\Definitions\BASHDefs\20111014.001\BHDrvx64.sys [2011-10-14 1155704]
S1 ccSet_NAV;Norton AntiVirus Settings Manager;c:\windows\system32\drivers\NAVx64\1301010.003\ccSetx64.sys [x]
S1 IDSVia64;IDSVia64;c:\programdata\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NAV_19.1.0.28\Definitions\IPSDefs\20111021.030\IDSvia64.sys [2011-10-21 488568]
S1 SaibVdAd64;Virtual Disk Driver;c:\windows\system32\Drivers\SaibVdAd64.sys [x]
S1 SymIRON;Symantec Iron Driver;c:\windows\system32\drivers\NAVx64\1301010.003\Ironx64.SYS [x]
S1 SymNetS;Symantec Network Security WFP Driver;c:\windows\System32\Drivers\NAVx64\1301010.003\SYMNETS.SYS [x]
S2 9734BF6A-2DCD-40f0-BAB0-5AAFEEBE1269;Roxio SAIB Service;c:\program files (x86)\Roxio\BackOnTrack\App\SaibSVC.exe [2011-02-09 457200]
S2 AdobeARMservice;Adobe Acrobat Update Service;c:\program files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [2011-06-06 64952]
S2 AMD External Events Utility;AMD External Events Utility;c:\windows\system32\atiesrxx.exe [x]
S2 BOT4Service;BOT4Service;c:\program files (x86)\Roxio\BackOnTrack\App\BService.exe [2011-07-15 21488]
S2 cpuz135;cpuz135;c:\windows\system32\drivers\cpuz135_x64.sys [x]
S2 HfsplusRec;HfsplusRec;c:\windows\system32\DRIVERS\hfsplusrec.sys [x]
S2 IduService;Intel® Desktop Utilities Service;c:\program files (x86)\Intel\Intel Desktop Utilities\iduServ.exe [2011-04-19 133320]
S2 Intel® PROSet Monitoring Service;Intel® PROSet Monitoring Service;c:\windows\system32\IProsetMonitor.exe [x]
S2 lxeb_device;lxeb_device;c:\windows\system32\lxebcoms.exe [2010-04-14 1052328]
S2 lxebCATSCustConnectService;lxebCATSCustConnectService;c:\windows\system32\spool\DRIVERS\x64\3\\lxebserv.exe [2010-04-14 45736]
S2 Mamutu;Mamutu Service;c:\program files (x86)\Mamutu\a2service.exe [2011-07-08 2978720]
S2 MBAMService;MBAMService;c:\program files (x86)\Malwarebytes' Anti-Malware\mbamservice.exe [2011-08-31 366152]
S2 MotoHelper;MotoHelper Service;c:\program files (x86)\Motorola\MotoHelper\MotoHelperService.exe [2011-08-10 227184]
S2 NAV;Norton AntiVirus;c:\program files (x86)\Norton AntiVirus\Engine\19.1.1.3\ccSvcHst.exe [2011-08-10 138760]
S2 UNS;Intel® Management & Security Application User Notification Service;c:\program files (x86)\Intel\Intel® Management Engine Components\UNS\UNS.exe [2009-12-09 2320920]
S3 a2acc;a2acc;c:\program files (x86)\MAMUTU\a2accx64.sys [2011-07-08 85800]
S3 amdkmdag;amdkmdag;c:\windows\system32\DRIVERS\atikmdag.sys [x]
S3 amdkmdap;amdkmdap;c:\windows\system32\DRIVERS\atikmpag.sys [x]
S3 dc3d;MS Hardware Device Detection Driver (USB);c:\windows\system32\DRIVERS\dc3d.sys [x]
S3 e1kexpress;Intel® PRO/1000 PCI Express Network Connection Driver K;c:\windows\system32\DRIVERS\e1k62x64.sys [x]
S3 EraserUtilRebootDrv;EraserUtilRebootDrv;c:\program files (x86)\Common Files\Symantec Shared\EENGINE\EraserUtilRebootDrv.sys [2011-07-27 136824]
S3 HECIx64;Intel® Management Engine Interface;c:\windows\system32\DRIVERS\HECIx64.sys [x]
S3 MBAMProtector;MBAMProtector;c:\windows\system32\drivers\mbam.sys [x]
S3 Point64;Microsoft IntelliPoint Filter Driver;c:\windows\system32\DRIVERS\point64.sys [x]
S3 QW720V64;Qwest 802.11n XN720 Driver(vista);c:\windows\system32\DRIVERS\WLANUHN.sys [x]
S3 SndTAudio;SndTAudio;c:\windows\system32\drivers\SndTAudio.sys [x]
.
.
[HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\active setup\installed components\{2D46B6DC-2207-486B-B523-A557E6D54B47}]
2010-11-20 12:17 302592 —-a-w- c:\windows\System32\cmd.exe
.
Contents of the 'Scheduled Tasks' folder
.
2011-10-24 c:\windows\Tasks\GoogleUpdateTaskMachineCore.job
- c:\program files (x86)\Google\Update\GoogleUpdate.exe [2011-09-21 07:56]
.
2011-10-24 c:\windows\Tasks\GoogleUpdateTaskMachineUA.job
- c:\program files (x86)\Google\Update\GoogleUpdate.exe [2011-09-21 07:56]
.
.
——— x86-64 ———–
.
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"RTHDVCPL"="c:\program files\Realtek\Audio\HDA\RAVCpl64.exe" [2011-05-03 11842152]
"itype"="c:\program files\Microsoft IntelliType Pro\itype.exe" [2011-08-01 1873288]
"IntelliPoint"="c:\program files\Microsoft IntelliPoint\ipoint.exe" [2011-08-01 2417032]
"Ashampoo HDD Control Guard"="c:\program files (x86)\Ashampoo\Ashampoo HDD Control\HDDControlGuard.exe" [2011-01-28 4085080]
"combofix"="c:\combofix\CF3893.3XE" [2010-11-20 345088]
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Windows]
"LoadAppInit_DLLs"=0x1
.
——- Supplementary Scan ——-
.
uLocal Page = c:\windows\system32\blank.htm
uStart Page = hxxp://www.mozilla.com/
mLocal Page = c:\windows\SysWOW64\blank.htm
uInternet Settings,ProxyOverride = 192.168.*.*;*.local
IE: Add to Google Photos Screensa&ver; - c:\windows\system32\GPhotos.scr/200
TCP: DhcpNameServer = 192.168.0.1 [removed]
CLSID: {603d3801-bd81-11d0-a3a5-00c04fd706ec} - %SystemRoot%\SysWow64\shell32.dll
FF - ProfilePath - c:\users\Smooth_Top\AppData\Roaming\Mozilla\Firefox\Profiles\tj7gc94k.default\
FF - prefs.js: browser.search.selectedEngine - iLivid Web Search
FF - prefs.js: browser.startup.homepage - hxxp://www.searchqu.com/406
FF - prefs.js: keyword.URL - hxxp://www.searchqu.com/web?src=ffb&appid;=101&systemid;=406&sr;=0&q;=
FF - prefs.js: network.proxy.type - 0
.
- - - - ORPHANS REMOVED - - - -
.
URLSearchHooks-{bf7380fa-e3b4-4db2-af3e-9d8783a45bfc} - (no file)
BHO-{bf7380fa-e3b4-4db2-af3e-9d8783a45bfc} - (no file)
Toolbar-Locked - (no file)
Toolbar-{bf7380fa-e3b4-4db2-af3e-9d8783a45bfc} - (no file)
Toolbar-10 - (no file)
Toolbar-Locked - (no file)
Toolbar-10 - (no file)
WebBrowser-{BF7380FA-E3B4-4DB2-AF3E-9D8783A45BFC} - (no file)
WebBrowser-{30F9B915-B755-4826-820B-08FBA6BD249D} - (no file)
AddRemove-Incomedia WebSite X5 v8 - Smart - c:\windows\system32\iwpsetup.exe
AddRemove-1907574623.www1.movie-promo.com - c:\program files (x86)\Microsoft Silverlight\4.0.60310.0\Silverlight.Configuration.exe
.
.
.
[HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\services\NAV]
"ImagePath"="\"c:\program files (x86)\Norton AntiVirus\Engine\19.1.1.3\ccSvcHst.exe\" /s \"NAV\" /m \"c:\program files (x86)\Norton AntiVirus\Engine\19.1.1.3\diMaster.dll\" /prefetch:1"
.
——————— LOCKED REGISTRY KEYS ———————
.
[HKEY_USERS\.Default\Software\Microsoft\Internet Explorer\Approved Extensions]
@Denied: (2) (LocalSystem)
"{A317CB83-299C-4FC8-9ED7-2D64117D98EE}"=hex:51,66,7a,6c,4c,1d,38,12,ed,c8,04,
a7,ae,67,a6,0a,e1,c1,6e,24,14,23,dc,fa
"{1017A80C-6F09-4548-A84D-EDD6AC9525F0}"=hex:51,66,7a,6c,4c,1d,38,12,62,ab,04,
14,3b,21,26,00,d7,5b,ae,96,a9,cb,61,e4
"{18DF081C-E8AD-4283-A596-FA578C2EBDC3}"=hex:51,66,7a,6c,4c,1d,38,12,72,0b,cc,
1c,9f,a6,ed,07,da,80,b9,17,89,70,f9,d7
"{326E768D-4182-46FD-9C16-1449A49795F4}"=hex:51,66,7a,6c,4c,1d,38,12,e3,75,7d,
36,b0,0f,93,03,e3,00,57,09,a1,c9,d1,e0
"{6D53EC84-6AAE-4787-AEEE-F4628F01010C}"=hex:51,66,7a,6c,4c,1d,38,12,ea,ef,40,
69,9c,24,e9,02,d1,f8,b7,22,8a,5f,45,18
"{9030D464-4C02-4ABF-8ECC-5164760863C6}"=hex:51,66,7a,6c,4c,1d,38,12,0a,d7,23,
94,30,02,d1,0f,f1,da,12,24,73,56,27,d2
"{9FDDE16B-836F-4806-AB1F-1455CBEFF289}"=hex:51,66,7a,6c,4c,1d,38,12,05,e2,ce,
9b,5d,cd,68,0d,d4,09,57,15,ce,b1,b6,9d
"{DBC80044-A445-435B-BC74-9C25C1C588A9}"=hex:51,66,7a,6c,4c,1d,38,12,2a,03,db,
df,77,ea,35,06,c3,62,df,65,c4,9b,cc,bd
"{FD72061E-9FDE-484D-A58A-0BAB4151CAD8}"=hex:51,66,7a,6c,4c,1d,38,12,70,05,61,
f9,ec,d1,23,0d,da,9c,48,eb,44,0f,8e,cc
.
[HKEY_USERS\.Default\Software\Microsoft\Internet Explorer\ApprovedExtensionsMigration]
@Denied: (2) (LocalSystem)
"Timestamp"=hex:7a,79,2f,0a,09,8f,cc,01
.
[HKEY_USERS\.Default\Software\Microsoft\Internet Explorer\User Preferences]
@Denied: (2) (LocalSystem)
"88D7D0879DAB32E14DE5B3A805A34F98AFF34F5977"=hex:01,00,00,00,d0,8c,9d,df,01,15,
d1,11,8c,7a,00,c0,4f,c2,97,eb,01,00,00,00,e9,6a,8a,e5,16,7d,85,47,98,f0,c8,\
"2D53CFFC5C1A3DD2E97B7979AC2A92BD59BC839E81"=hex:01,00,00,00,d0,8c,9d,df,01,15,
d1,11,8c,7a,00,c0,4f,c2,97,eb,01,00,00,00,e9,6a,8a,e5,16,7d,85,47,98,f0,c8,\
.
[HKEY_USERS\.Default\Software\Microsoft\Windows\CurrentVersion\Explorer\FileExts\.htm\UserChoice]
@Denied: (2) (LocalSystem)
"Progid"="IE.AssocFile.HTM"
.
[HKEY_USERS\.Default\Software\Microsoft\Windows\CurrentVersion\Explorer\FileExts\.html\UserChoice]
@Denied: (2) (LocalSystem)
"Progid"="IE.AssocFile.HTM"
.
[HKEY_USERS\.Default\Software\Microsoft\Windows\CurrentVersion\Explorer\FileExts\.mht\UserChoice]
@Denied: (2) (LocalSystem)
"Progid"="IE.AssocFile.MHT"
.
[HKEY_USERS\.Default\Software\Microsoft\Windows\CurrentVersion\Explorer\FileExts\.mhtml\UserChoice]
@Denied: (2) (LocalSystem)
"Progid"="IE.AssocFile.MHT"
.
[HKEY_USERS\.Default\Software\Microsoft\Windows\CurrentVersion\Explorer\FileExts\.partial\UserChoice]
@Denied: (2) (LocalSystem)
"Progid"="IE.AssocFile.PARTIAL"
.
[HKEY_USERS\.Default\Software\Microsoft\Windows\CurrentVersion\Explorer\FileExts\.svg\UserChoice]
@Denied: (2) (LocalSystem)
"Progid"="IE.AssocFile.SVG"
.
[HKEY_USERS\.Default\Software\Microsoft\Windows\CurrentVersion\Explorer\FileExts\.url\UserChoice]
@Denied: (2) (LocalSystem)
"Progid"="IE.AssocFile.URL"
.
[HKEY_USERS\.Default\Software\Microsoft\Windows\CurrentVersion\Explorer\FileExts\.website\UserChoice]
@Denied: (2) (LocalSystem)
"Progid"="IE.AssocFile.WEBSITE"
.
[HKEY_USERS\.Default\Software\Microsoft\Windows\CurrentVersion\Explorer\FileExts\.xht\UserChoice]
@Denied: (2) (LocalSystem)
"Progid"="IE.AssocFile.XHT"
.
[HKEY_USERS\.Default\Software\Microsoft\Windows\CurrentVersion\Explorer\FileExts\.xhtml\UserChoice]
@Denied: (2) (LocalSystem)
"Progid"="IE.AssocFile.XHT"
.
[HKEY_USERS\S-1-5-21-2220950379-111707297-2290237234-1000\Software\AppDataLow\Software\Conduit\Community Alerts\Settings\Locales\e*n**ÿ˜�«Ö«#]
"LP_LastUpdateTime"="1317269550"
"LP_LastCheckTime"=dword:4e83f030
"LP_ReloadIntervalInHours"=dword:000002a0
.
[HKEY_USERS\S-1-5-21-2220950379-111707297-2290237234-1000\Software\Microsoft\Windows\CurrentVersion\Explorer\FileExts\.eml\UserChoice]
@Denied: (2) (LocalSystem)
"Progid"="WindowsLiveMail.Email.1"
.
[HKEY_USERS\S-1-5-21-2220950379-111707297-2290237234-1000\Software\Microsoft\Windows\CurrentVersion\Explorer\FileExts\.vcf\UserChoice]
@Denied: (2) (LocalSystem)
"Progid"="WindowsLiveMail.VCard.1"
.
[HKEY_USERS\S-1-5-21-2220950379-111707297-2290237234-1000\Software\Microsoft\Windows\CurrentVersion\Shell Extensions\Approved\{70A9574B-D160-650C-0831-34935BC0EAE3}*]
"maalchocmfpkdgiboglldmpmnl"=hex:6a,61,63,6a,68,66,68,6a,61,62,6b,69,67,70,6c,
6c,6a,64,6b,63,00,fe
"nagkjknjdebjefknfeogielpddga"=hex:6a,61,63,6a,68,66,68,6a,61,62,6b,69,67,70,
6c,6c,6a,64,6b,63,00,fe
"hacngmbkfkajpgla"=hex:61,62,66,6b,63,6d,6d,61,64,65,6f,6e,66,64,69,6b,63,6b,
62,66,64,65,69,61,61,6f,69,62,68,6f,6b,6e,6e,67,00,00
"hacngmbkajdeheac"=hex:64,62,68,6b,6e,68,6f,6d,67,6d,70,69,65,66,6a,6b,62,6e,
69,66,6d,62,6a,65,6c,6a,6f,70,61,6f,6c,70,61,6e,70,64,6c,6d,65,65,00,00
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}]
@Denied: (A 2) (Everyone)
@="FlashBroker"
"LocalizedString"="@c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil10t_ActiveX.exe,-101"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\Elevation]
"Enabled"=dword:00000001
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\LocalServer32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil10t_ActiveX.exe"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\TypeLib]
@="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}]
@Denied: (A 2) (Everyone)
@="Shockwave Flash Object"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\InprocServer32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10t.ocx"
"ThreadingModel"="Apartment"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\MiscStatus]
@="0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ProgID]
@="ShockwaveFlash.ShockwaveFlash.10"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10t.ocx, 1"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\TypeLib]
@="{D27CDB6B-AE6D-11cf-96B8-444553540000}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\Version]
@="1.0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID]
@="ShockwaveFlash.ShockwaveFlash"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}]
@Denied: (A 2) (Everyone)
@="Macromedia Flash Factory Object"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\InprocServer32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10t.ocx"
"ThreadingModel"="Apartment"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ProgID]
@="FlashFactory.FlashFactory.1"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10t.ocx, 1"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\TypeLib]
@="{D27CDB6B-AE6D-11cf-96B8-444553540000}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\Version]
@="1.0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID]
@="FlashFactory.FlashFactory"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}]
@Denied: (A 2) (Everyone)
@="IFlashBroker4"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\ProxyStubClsid32]
@="{00020424-0000-0000-C000-000000000046}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\TypeLib]
@="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}"
"Version"="1.0"
.
[HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0000\AllUserSettings]
@Denied: (A) (Users)
@Denied: (A) (Everyone)
@Allowed: (B 1 2 3 4 5) (S-1-5-20)
"BlindDial"=dword:00000000
.
[HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\PCW\Security]
@Denied: (Full) (Everyone)
.
———————— Other Running Processes ————————
.
c:\program files (x86)\APC\APC PowerChute Personal Edition\mainserv.exe
c:\program files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
c:\program files (x86)\Full Uninstall\FullUninstallAgent.exe
c:\program files (x86)\Kodak\KODAK Share Button App\Listener.exe
c:\program files (x86)\Intel\Intel® Management Engine Components\LMS\LMS.exe
c:\program files (x86)\Motorola\MotoHelper\MotoHelperAgent.exe
.
**************************************************************************
.
Completion time: 2011-10-24 05:14:11 - machine was rebooted
ComboFix-quarantined-files.txt 2011-10-24 11:14
.
Pre-Run: 249,919,242,240 bytes free
Post-Run: 251,559,149,568 bytes free
.
- - End Of File - - 9044825F0A1435DED48989AC717BD314

 My name is