This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

can't download Norton Removal Tool

10 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

Hi - please help! PC takes ages to start up and eventually Norton window appear with "error 8504.101". The One Touch support window performs a scan and recommends downloading the Norton Removal Tool. However, all sites for downloading this come up with "Invalid URL" error so I can't download it. Looks to me like an infection preventing me from accessing the cure I need. Should I just try removing through the control panel? I'm sure I tried this once with an earlier version of Norton on another computer with unhappy results - total locking up of PC.
Hi and Welcome!! :) My name is Jeff. I would be more than happy to take a look at your log and help you with solving any malware problems you might have. Logs can take a while to research, so please be patient and know that I am working hard to get you a clean and functional system back in your hands. I'd be grateful if you would note the following:
  • I will be working on your Malware issues, this may or may not, solve other issues you have with your machine.
  • The fixes are specific to your problem and should only be used for the issues on this machine.
  • Please continue to review my answers until I tell you your machine appears to be clear. Absence of symptoms does not mean that everything is clear.
  • It's often worth reading through these instructions and printing them for ease of reference.
  • If you don't know or understand something, please don't hesitate to say or ask!! It's better to be sure and safe than sorry.
  • Please reply to this thread. Do not start a new topic.

Please be advised, as I am still in training, all my replies to you will be checked for accuracy by one of our experts to ensure that I am giving you the best possible advise, this will be a team effort.
This may cause a delay, but I will do my best to keep it as short as possible. Please bear with me, I will post back to you as soon as I can.

IMPORTANT NOTE : Please do not delete anything unless instructed to.
DO NOT use any TOOLS such as Combofix or HijackThis fixes without supervision. Doing so could make your system inoperable and could require a full reinstall of your Operating System and losing all your programs and data.


Vista and Windows 7 users:

These tools MUST be run from the executable. (.exe) every time you run them
with Admin Rights (Right click, choose "Run as Administrator")


Stay with this topic until I give you the all clean post.

Having said that….Let's get going!! :thumbup:
Hi benj,

Please download DDS from either of these links

LINK 1
LINK 2

and save it to your desktop.
  • Disable any script blocking protection
  • Double click dds to run the tool.
  • When done, two DDS.txt's will open.
  • Save both reports to your desktop.
—————————————————
Please include the contents of the following in your next reply:

DDS.txt

Attach.txt
———-

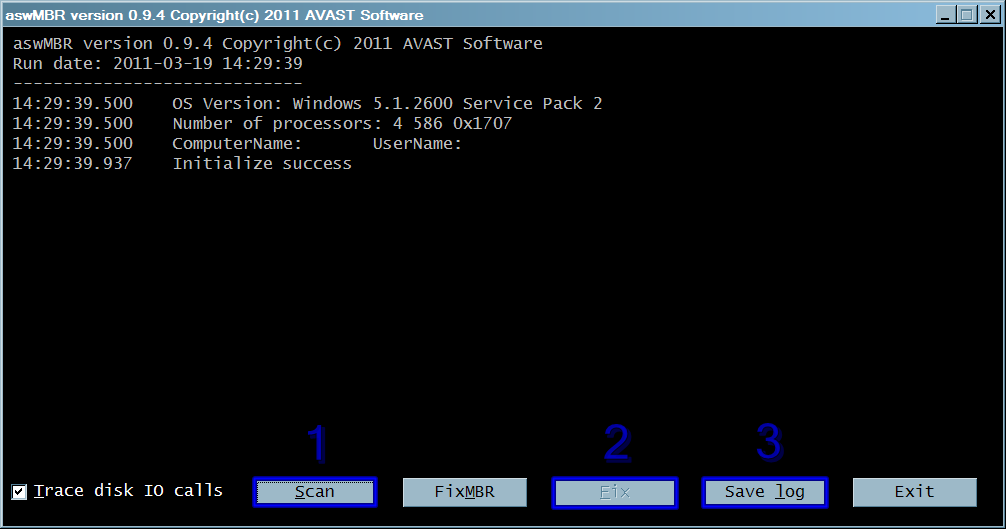
Please download aswMBR to your desktop.

  • Double click the aswMBR icon to run it.
    Vista and Windows 7 users right click the icon and choose "Run as administrator".
  • Click the Scan button to start scan.
  • When it finishes, press the save log button, save the logfile to your desktop and post its contents in your next reply.

[external image: Posted Image]
Click the image to enlarge it


In your next reply please post both logs created by DDS and the log created by aswMBR.exe. :)
Hi benj,

Thank you for the logs I do appreciate it; however, if you would next time please just copy/paste them directly into your reply so I can read them from there. It helps me to review them easier and more quickly. :)


Please double click the aswMBR icon to run it.
Vista and Windows 7 users right click the icon and choose "Run as administrator".

  • Click the Scan button to start scan.
  • When scan finishes, press the FixMBR Button. Once the Fix is done, press the Save Log button and save the log to your desktop. You need to reboot your computer when its done before you do anything else, then post the log that will be on your desktop.

[external image: Posted Image]
Click the image to enlarge it


In your next reply please post the log created by aswMBR.exe
Hi Jeff, Scanned with the software as suggested, but didn't have "Fix MBR" as an option at the end so pressed "Fix" instead. Tried to save the log after this, but the PC blue-screened and began "dumping physical memory". When I restarted, Norton didn't come on and One Touch Support gave the same error (8504.101). I ran the MBR software again, and this time pressed "fix mbr" both befor the scan and after it. The log file saved ok. I restarted the PC again - again Norton not evident in the bottom right hand corner, and no doubt will throw up the error message again if I try to double click Norton the desktop to get it open. Log of second scan results are pasted below. Thanks again, Ben aswMBR version 0.9.7.705 Copyright© 2011 AVAST Software Run date: 2011-07-06 08:48:09 —————————– 08:48:09.203 OS Version: Windows 5.1.2600 Service Pack 3 08:48:09.203 Number of processors: 1 586 0x4F02 08:48:09.203 ComputerName: HOME-825B9F269A UserName: Owner 08:48:10.171 Initialize success 08:50:50.843 AVAST engine defs: 11070501 08:51:00.984 Disk 0 (boot) \Device\Harddisk0\DR0 -> \Device\Ide\IdeDeviceP0T0L0-4 08:51:00.984 Disk 0 Vendor: HDT722516DLAT80 V43OA96A Size: 157066MB BusType: 3 08:51:03.015 Disk 0 MBR read successfully 08:51:03.015 Disk 0 MBR scan 08:51:03.015 Disk 0 Windows XP default MBR code found via API 08:51:03.015 Disk 0 unknown MBR code 08:51:03.015 Disk 0 MBR hidden 08:51:05.015 Disk 0 scanning sectors +321669495 08:51:05.031 Disk 0 malicious Win32:MBRoot code @ sector 321669498 ! 08:51:05.031 Disk 0 PE file @ sector 321669520 ! 08:51:05.031 Disk 0 MBR [Win32:MBRoot] **ROOTKIT** 08:51:05.031 Disk 0 trace - called modules: 08:51:05.031 ntkrnlpa.exe CLASSPNP.SYS disk.sys ACPI.sys hal.dll >>UNKNOWN [0x8452e700]<< 08:51:05.562 1 nt!IofCallDriver -> \Device\Harddisk0\DR0[0x85675030] 08:51:05.562 3 CLASSPNP.SYS[f74c7fd7] -> nt!IofCallDriver -> \Device\0000006d[0x856d2f18] 08:51:05.562 5 ACPI.sys[f735e620] -> nt!IofCallDriver -> \Device\Ide\IdeDeviceP0T0L0-4[0x8566ed98] 08:51:06.718 AVAST engine scan C:\WINDOWS 09:15:27.796 AVAST engine scan C:\Documents and Settings\Owner 09:31:38.156 AVAST engine scan C:\Documents and Settings\All Users 09:33:20.953 Scan finished successfully 09:43:26.203 Disk 0 MBR has been saved successfully to "C:\Documents and Settings\Owner\Desktop\MBR.dat" 09:43:26.234 The log file has been saved successfully to "C:\Documents and Settings\Owner\Desktop\aswMBR.txt" aswMBR version 0.9.7.705 Copyright© 2011 AVAST Software Run date: 2011-07-07 07:36:23 —————————– 07:36:23.296 OS Version: Windows 5.1.2600 Service Pack 3 07:36:23.296 Number of processors: 1 586 0x4F02 07:36:23.296 ComputerName: HOME-825B9F269A UserName: Owner 07:36:23.843 Initialize success 07:38:47.484 AVAST engine defs: 11070601 07:39:07.046 Disk 0 Windows 501 MBR fixed successfully 07:39:30.312 Disk 0 (boot) \Device\Harddisk0\DR0 -> \Device\Ide\IdeDeviceP0T0L0-4 07:39:30.312 Disk 0 Vendor: HDT722516DLAT80 V43OA96A Size: 157066MB BusType: 3 07:39:32.312 Disk 0 MBR read successfully 07:39:32.312 Disk 0 MBR scan 07:39:32.312 Disk 0 Windows XP default MBR code 07:39:34.328 Disk 0 scanning sectors +321669495 07:39:34.343 Disk 0 scanning C:\WINDOWS\system32\drivers 07:39:48.968 Service scanning 07:39:50.140 Disk 0 trace - called modules: 07:39:50.156 ntkrnlpa.exe CLASSPNP.SYS disk.sys ACPI.sys hal.dll atapi.sys pciide.sys PCIIDEX.SYS 07:39:50.156 1 nt!IofCallDriver -> \Device\Harddisk0\DR0[0x85675030] 07:39:50.156 3 CLASSPNP.SYS[f74c7fd7] -> nt!IofCallDriver -> \Device\0000006d[0x856d2f18] 07:39:50.671 5 ACPI.sys[f735e620] -> nt!IofCallDriver -> \Device\Ide\IdeDeviceP0T0L0-4[0x8566ed98] 07:39:51.000 AVAST engine scan C:\WINDOWS 08:02:08.921 AVAST engine scan C:\Documents and Settings\Owner 08:19:53.015 AVAST engine scan C:\Documents and Settings\All Users 08:22:50.953 Scan finished successfully 08:23:48.125 Disk 0 Windows 501 MBR fixed successfully 08:24:23.859 Disk 0 MBR has been saved successfully to "C:\Documents and Settings\Owner\Desktop\MBR.dat" 08:24:24.140 The log file has been saved successfully to "C:\Documents and Settings\Owner\Desktop\aswMBR.txt"
Hi Jeff, Further to my last reply - I now can (and have) downloaded the Norton Removal Tool, which One Touch Support is recommending to use to fix the error 8504.101. I haven't used it and won't until I hear from you. Ben
Hi benj,

Looks like we got rid of a nasty rootkit that was hiding on your system. Good Job!!

I see that you have downloaded the Norton Removal Tool. Go ahead and give it a go. If for some reason you have trouble with using that one, try the tool found here.

For the time being, since you will have no antivirus program on your system, please limit your internet usage to downloading tools that we advise and posting into this topic. We will get an antivirus program onto your system as soon as we can. :)
———-

Please read through these instructions to familarize yourself with what to expect when this tool runs

Download ComboFix from one of these locations:

Link 1
Link 2

***Neither I nor sUBs are responsible for any damage that may be caused to your machine by running ComboFix. Please do not run ComboFix on your own. This tool is not a toy and not for everyday use.***


* IMPORTANT !!! Save ComboFix.exe to your Desktop

  • Disable your AntiVirus and AntiSpyware applications, usually via a right click on the System Tray icon. They may otherwise interfere with our tools. Note: If you are having difficulty properly disabling your protective programs, or are unsure as to what programs need to be disabled, please refer to the information available through this link : How to Disable your Security Programs
  • Double click on ComboFix.exe & follow the prompts.
  • As part of it's process, ComboFix will check to see if the Microsoft Windows Recovery Console is installed. With malware infections being as they are today, it's strongly recommended to have this pre-installed on your machine before doing any malware removal. It will allow you to boot up into a special recovery/repair mode that will allow us to more easily help you should your computer have a problem after an attempted removal of malware.
  • Follow the prompts to allow ComboFix to download and install the Microsoft Windows Recovery Console, and when prompted, agree to the End-User License Agreement to install the Microsoft Windows Recovery Console.

**Please note: If the Microsoft Windows Recovery Console is already installed, ComboFix will continue it's malware removal procedures.

[external image: Posted Image]


Once the Microsoft Windows Recovery Console is installed using ComboFix, you should see the following message:

[external image: Posted Image]

Click on Yes, to continue scanning for malware.

When finished, it shall produce a log for you. Please include the C:\ComboFix.txt in your next reply.

Notes:

1.Do not mouse-click Combofix's window while it is running. That may cause it to stall.
2. ComboFix may reset a number of Internet Explorer's settings, including making I-E the default browser.
3. CF disconnects your machine from the internet. The connection is automatically restored before CF completes its run. If CF runs into difficulty and terminates prematurely, the connection can be manually restored by restarting your machine.


In your next reply please post the log created by ComboFix. :)
Hi Jeff,

I ran Norton Removal Tool and then re-installed Norton from disk. On running Live Update, two Norton updates could not be installed (I tried numerous times).

I then ran Combofix which seemed to remove something called Tarma Installer (and maybe other things?).

When this had finished I tried again to update Norton and the two updates installed fine.

Log from Combofix is below.

Thanks for all the help! Do you think I should stick with Norton?

Ben


ComboFix 11-07-07.06 - Owner 08/07/2011 9:26.1.1 - x86
Microsoft Windows XP Home Edition 5.1.2600.3.1252.1.1033.18.895.245 [GMT 1:00]
Running from: c:\documents and settings\[removed]\Desktop\ComboFix.exe
AV: Norton Internet Security *Disabled/Updated* {E10A9785-9598-4754-B552-92431C1C35F8}
FW: Norton Internet Security *Disabled* {7C21A4C9-F61F-4AC4-B722-A6E19C16F220}
.
.
((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.
.
c:\documents and settings\All Users\Application Data\Tarma Installer
.
.
((((((((((((((((((((((((((((((((((((((( Drivers/Services )))))))))))))))))))))))))))))))))))))))))))))))))
.
.
——-\Legacy_MYWEBSEARCHSERVICE
.
.
((((((((((((((((((((((((( Files Created from 2011-06-08 to 2011-07-08 )))))))))))))))))))))))))))))))
.
.
2011-07-08 08:00 . 2011-03-22 00:39 369784 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\symtdi.sys
2011-07-08 08:00 . 2011-03-22 00:39 331384 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\symtdiv.sys
2011-07-08 08:00 . 2011-03-22 00:39 296568 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\symnets.sys
2011-07-08 08:00 . 2011-03-31 03:00 516216 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\srtsp.sys
2011-07-08 08:00 . 2011-03-31 03:00 50168 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\srtspx.sys
2011-07-08 08:00 . 2011-03-15 02:31 744568 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\symefa.sys
2011-07-08 08:00 . 2011-01-27 06:47 340088 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\symds.sys
2011-07-08 08:00 . 2011-01-27 05:07 136312 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\ironx86.sys
2011-07-08 07:44 . 2011-07-08 08:00 60872 —-a-w- c:\windows\system32\S32EVNT1.DLL
2011-07-08 07:44 . 2011-07-08 08:00 126584 —-a-w- c:\windows\system32\drivers\SYMEVENT.SYS
2011-07-08 07:44 . 2011-07-08 08:00 ——– d—–w- c:\program files\Symantec
2011-07-08 07:44 . 2011-07-08 07:44 ——– d—–w- c:\program files\Common Files\Symantec Shared
2011-07-08 07:43 . 2011-07-08 07:43 ——– d—–w- c:\program files\Norton Internet Security
2011-07-08 07:41 . 2011-07-08 07:41 ——– d—–w- c:\program files\NortonInstaller
2011-07-06 08:52 . 2011-07-06 08:52 ——– d—–w- c:\documents and settings\Owner\Local Settings\Application Data\WinZip
2011-07-06 08:51 . 2011-07-06 08:52 ——– d—–w- c:\documents and settings\All Users\Application Data\WinZip
2011-06-30 08:53 . 2011-06-30 10:03 ——– d—–w- c:\documents and settings\Owner\Local Settings\Application Data\NPE
2011-06-22 17:01 . 2011-06-22 17:01 53816 —-a-w- c:\windows\system32\drivers\RapportKELL.sys
2011-06-20 07:04 . 2011-06-20 07:04 ——– d—–w- c:\documents and settings\Owner\Application Data\Tific
2011-06-20 07:03 . 2011-06-20 07:03 ——– d—–w- c:\documents and settings\Owner\Local Settings\Application Data\Symantec
2011-06-20 06:37 . 2011-06-20 06:37 ——– d—–w- c:\documents and settings\Owner\Local Settings\Application Data\{126CE956-FEFD-4ACF-8995-5900527F6ADB}
2011-06-19 19:30 . 2011-06-20 06:38 0 —-a-w- c:\windows\Ifupukifuri.bin
2011-06-19 19:29 . 2011-06-19 19:29 ——– d—–w- c:\documents and settings\Owner\Local Settings\Application Data\{5D6AADAF-FDA2-4EC2-8654-5429C3348E35}
2011-06-16 22:45 . 2011-06-17 08:42 ——– d—–w- c:\windows\SxsCaPendDel
2011-06-16 17:46 . 2011-04-21 13:37 105472 -c—-w- c:\windows\system32\dllcache\mup.sys
.
.
.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2011-05-02 15:31 . 2009-04-09 12:51 692736 —-a-w- c:\windows\system32\inetcomm.dll
2011-04-29 17:25 . 2004-08-04 12:00 151552 —-a-w- c:\windows\system32\schannel.dll
2011-04-29 16:19 . 2004-08-04 12:00 456320 —-a-w- c:\windows\system32\drivers\mrxsmb.sys
2011-04-25 16:11 . 2004-08-04 12:00 916480 —-a-w- c:\windows\system32\wininet.dll
2011-04-25 16:11 . 2004-08-04 12:00 43520 —-a-w- c:\windows\system32\licmgr10.dll
2011-04-25 16:11 . 2004-08-04 12:00 1469440 —-a-w- c:\windows\system32\inetcpl.cpl
2011-04-25 12:01 . 2004-08-04 12:00 385024 —-a-w- c:\windows\system32\html.iec
2011-04-21 13:37 . 2004-08-04 12:00 105472 —-a-w- c:\windows\system32\drivers\mup.sys
.
.
((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4
.
[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SpybotSD TeaTimer"="c:\program files\Spybot - Search & Destroy\TeaTimer.exe" [2009-03-05 2260480]
"LightScribe Control Panel"="c:\program files\Common Files\LightScribe\LightScribeControlPanel.exe" [2007-08-23 455968]
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"NvCplDaemon"="c:\windows\system32\NvCpl.dll" [2009-03-27 13684736]
"nwiz"="nwiz.exe" [2009-03-27 1657376]
"NvMediaCenter"="c:\windows\system32\NvMcTray.dll" [2009-03-27 86016]
"High Definition Audio Property Page Shortcut"="HDAShCut.exe" [2005-01-07 61952]
"dla"="c:\windows\system32\dla\tfswctrl.exe" [2004-03-15 122933]
"UpdateManager"="c:\program files\Common Files\Sonic\Update Manager\sgtray.exe" [2003-08-19 110592]
"RemoteControl"="c:\program files\CyberLink\PowerDVD\PDVDServ.exe" [2005-01-12 32768]
"HP Software Update"="c:\program files\HP\HP Software Update\HPWuSchd2.exe" [2005-05-11 49152]
"Adobe Reader Speed Launcher"="c:\program files\Adobe\Reader 9.0\Reader\Reader_sl.exe" [2009-02-27 35696]
"SunJavaUpdateSched"="c:\program files\Java\jre6\bin\jusched.exe" [2009-10-17 149280]
"DivXUpdate"="c:\program files\DivX\DivX Update\DivXUpdate.exe" [2010-06-03 1144104]
"QuickTime Task"="c:\program files\QuickTime\QTTask.exe" [2010-11-29 421888]
"AppleSyncNotifier"="c:\program files\Common Files\Apple\Mobile Device Support\AppleSyncNotifier.exe" [2011-04-20 58656]
"iTunesHelper"="c:\program files\iTunes\iTunesHelper.exe" [2011-04-27 421160]
"Synchronization Manager"="c:\windows\system32\mobsync.exe" [2008-04-14 143360]
.
[HKEY_USERS\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\Run]
"CTFMON.EXE"="c:\windows\system32\CTFMON.EXE" [2008-04-14 15360]
.
c:\documents and settings\All Users\Start Menu\Programs\Startup\
Adobe Gamma Loader.exe.lnk - c:\program files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe [2009-4-14 113664]
HP Digital Imaging Monitor.lnk - c:\program files\HP\Digital Imaging\bin\hpqtra08.exe [2005-5-11 282624]
Microsoft Office.lnk - c:\program files\Microsoft Office\Office10\OSA.EXE [2001-2-13 83360]
Tenda W541U.lnk - c:\program files\Tenda\W541U\UI.exe [2009-4-14 2121728]
WinZip Quick Pick.lnk - c:\program files\WinZip\WZQKPICK.EXE [2011-6-23 610120]
.
[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile]
"EnableFirewall"= 0 (0x0)
.
[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"c:\\Program Files\\Messenger\\msmsgs.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpqste08.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpofxm08.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hposfx08.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hposid01.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpqscnvw.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpqkygrp.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpqCopy.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpfccopy.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpzwiz01.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\Unload\\HpqPhUnl.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpoews01.exe"=
"c:\\Program Files\\Spotify\\spotify.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\msnmsgr.exe"=
"c:\\Program Files\\Windows Live\\Sync\\WindowsLiveSync.exe"=
"c:\\Program Files\\iTunes\\iTunes.exe"=
.
[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\GloballyOpenPorts\List]
"65533:TCP"= 65533:TCP:Services
"52344:TCP"= 52344:TCP:Services
"2479:TCP"= 2479:TCP:Services
"2999:TCP"= 2999:TCP:Services
"3389:TCP"= 3389:TCP:Remote Desktop
"7119:TCP"= 7119:TCP:Services
"7120:TCP"= 7120:TCP:Services
"2861:TCP"= 2861:TCP:Services
"4222:TCP"= 4222:TCP:Services
"7844:TCP"= 7844:TCP:Services
"7845:TCP"= 7845:TCP:Services
"3430:TCP"= 3430:TCP:Services
"4395:TCP"= 4395:TCP:Services
"7144:TCP"= 7144:TCP:Services
"7145:TCP"= 7145:TCP:Services
"8442:TCP"= 8442:TCP:Services
"4971:TCP"= 4971:TCP:Services
"4604:TCP"= 4604:TCP:Services
"7708:TCP"= 7708:TCP:Services
"6277:TCP"= 6277:TCP:Services
"6276:TCP"= 6276:TCP:Services
"3708:TCP"= 3708:TCP:Services
"5916:TCP"= 5916:TCP:Services
"2042:TCP"= 2042:TCP:Services
"2584:TCP"= 2584:TCP:Services
"5301:TCP"= 5301:TCP:Services
"9102:TCP"= 9102:TCP:Services
"8534:TCP"= 8534:TCP:Services
"7240:TCP"= 7240:TCP:Services
"7241:TCP"= 7241:TCP:Services
"1711:TCP"= 1711:TCP:Services
"5052:TCP"= 5052:TCP:Services
"3302:TCP"= 3302:TCP:Services
"9239:TCP"= 9239:TCP:Services
"2052:TCP"= 2052:TCP:Services
"9520:TCP"= 9520:TCP:Services
"9521:TCP"= 9521:TCP:Services
"1568:TCP"= 1568:TCP:Services
"1636:TCP"= 1636:TCP:Services
"1552:TCP"= 1552:TCP:Services
"5693:TCP"= 5693:TCP:Services
"2334:TCP"= 2334:TCP:Services
"9145:TCP"= 9145:TCP:Services
"9146:TCP"= 9146:TCP:Services
"9770:TCP"= 9770:TCP:Services
"9771:TCP"= 9771:TCP:Services
"5443:TCP"= 5443:TCP:Services
"1912:TCP"= 1912:TCP:Services
"8255:TCP"= 8255:TCP:Services
"8256:TCP"= 8256:TCP:Services
"9005:TCP"= 9005:TCP:Services
"4802:TCP"= 4802:TCP:Services
"5709:TCP"= 5709:TCP:Services
"8848:TCP"= 8848:TCP:Services
"7926:TCP"= 7926:TCP:Services
"8645:TCP"= 8645:TCP:Services
"8239:TCP"= 8239:TCP:Services
"6270:TCP"= 6270:TCP:Services
"6770:TCP"= 6770:TCP:Services
"6771:TCP"= 6771:TCP:Services
"4692:TCP"= 4692:TCP:Services
"7884:TCP"= 7884:TCP:Services
"9973:TCP"= 9973:TCP:Services
"2006:TCP"= 2006:TCP:Services
"2802:TCP"= 2802:TCP:Services
"7348:TCP"= 7348:TCP:Services
"7349:TCP"= 7349:TCP:Services
"2974:TCP"= 2974:TCP:Services
"3677:TCP"= 3677:TCP:Services
"4381:TCP"= 4381:TCP:Services
"9176:TCP"= 9176:TCP:Services
"7489:TCP"= 7489:TCP:Services
"7161:TCP"= 7161:TCP:Services
"3218:TCP"= 3218:TCP:Services
"4021:TCP"= 4021:TCP:Services
"9864:TCP"= 9864:TCP:Services
"2068:TCP"= 2068:TCP:Services
"5771:TCP"= 5771:TCP:Services
"9756:TCP"= 9756:TCP:Services
"9757:TCP"= 9757:TCP:Services
.
R0 RapportKELL;RapportKELL;c:\windows\system32\drivers\RapportKELL.sys [22/06/2011 18:01 53816]
R0 SymDS;Symantec Data Store;c:\windows\system32\drivers\NIS\1206000.01D\symds.sys [08/07/2011 09:00 340088]
R0 SymEFA;Symantec Extended File Attributes;c:\windows\system32\drivers\NIS\1206000.01D\symefa.sys [08/07/2011 09:00 744568]
R1 BHDrvx86;BHDrvx86;c:\documents and settings\All Users\Application Data\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NIS_18.5.0.125\Definitions\BASHDefs\20110701.001\BHDrvx86.sys [01/07/2011 00:11 810616]
R1 RapportCerberus_26762;RapportCerberus_26762;c:\documents and settings\All Users\Application Data\Trusteer\Rapport\store\exts\RapportCerberus\26762\RapportCerberus_26762.sys [13/06/2011 16:54 57144]
R1 RapportEI;RapportEI;c:\program files\Trusteer\Rapport\bin\RapportEI.sys [22/06/2011 18:01 66360]
R1 RapportPG;RapportPG;c:\program files\Trusteer\Rapport\bin\RapportPG.sys [22/06/2011 18:01 158904]
R1 SymIRON;Symantec Iron Driver;c:\windows\system32\drivers\NIS\1206000.01D\ironx86.sys [08/07/2011 09:00 136312]
R2 NIS;Norton Internet Security;c:\program files\Norton Internet Security\Engine\18.6.0.29\ccsvchst.exe [08/07/2011 09:00 130008]
R2 ousbehci;OrangeWare USB Enhanced Host Controller Service;c:\windows\system32\drivers\ousbehci.sys [14/04/2009 09:26 45824]
R2 RapportMgmtService;Rapport Management Service;c:\program files\Trusteer\Rapport\bin\RapportMgmtService.exe [22/06/2011 18:01 870200]
R3 IDSxpx86;IDSxpx86;c:\documents and settings\All Users\Application Data\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NIS_18.5.0.125\Definitions\IPSDefs\20101201.001\IDSXpx86.sys [08/07/2011 08:44 341944]
R3 LgBttPort;LGE Bluetooth TransPort;c:\windows\system32\drivers\lgbtport.sys [29/09/2009 08:11 12160]
R3 lgbusenum;LG Bluetooth Bus Enumerator;c:\windows\system32\drivers\lgbtbus.sys [29/09/2009 08:11 10496]
R3 LGVMODEM;LGE Virtual Modem;c:\windows\system32\drivers\lgvmodem.sys [29/09/2009 08:11 12928]
R3 ousb2hub;OrangeWare USB 2.0 Root Hub Support;c:\windows\system32\drivers\ousb2hub.sys [14/04/2009 09:26 56960]
S3 S2usbser;S2 USB Device for Legacy Serial Communication;c:\windows\system32\drivers\S2usbser.sys [20/09/2009 16:12 103680]
S3 xcpip;TCP/IP Protocol Driver;c:\windows\system32\drivers\xcpip.sys –> c:\windows\system32\drivers\xcpip.sys [?]
S3 xpsec;IPSEC driver;c:\windows\system32\drivers\xpsec.sys –> c:\windows\system32\drivers\xpsec.sys [?]
.
[HKEY_LOCAL_MACHINE\software\microsoft\active setup\installed components\{10880D85-AAD9-4558-ABDC-2AB1552D831F}]
2007-08-23 16:34 451872 —-a-w- c:\program files\Common Files\LightScribe\LSRunOnce.exe
.
Contents of the 'Scheduled Tasks' folder
.
2011-07-02 c:\windows\Tasks\AppleSoftwareUpdate.job
- c:\program files\Apple Software Update\SoftwareUpdate.exe [2009-10-22 10:50]
.
2011-07-07 c:\windows\Tasks\WebReg psc 1500 series.job
- c:\program files\HP\Digital Imaging\bin\hpqwrg.exe [2005-05-11 15:45]
.
.
——- Supplementary Scan ——-
.
uStart Page = hxxp://www.orange.co.uk/
IE: Append Link Target to Existing PDF - c:\program files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIEAppendSelLinks.html
IE: E&xport to Microsoft Excel - c:\progra~1\MICROS~2\Office10\EXCEL.EXE/3000
IE: Google Sidewiki… - c:\program files\Google\Google Toolbar\Component\GoogleToolbarDynamic_mui_en_6CE5017F567343CA.dll/cmsidewiki.html
TCP: DhcpNameServer = 192.168.1.1
FF - ProfilePath - c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\
FF - prefs.js: browser.search.defaulturl - hxxp://search.conduit.com/ResultsExt.aspx?ctid=CT2830584&SearchSource=3&q={searchTerms}
FF - prefs.js: browser.search.selectedEngine - Radio TV 2.2 Customized Web Search
FF - prefs.js: browser.startup.homepage - hxxp://www.yahoo.co.uk
FF - prefs.js: keyword.URL - hxxp://search.conduit.com/ResultsExt.aspx?ctid=CT2830584&q=
FF - Ext: Default: {972ce4c6-7e08-4474-a285-3208198ce6fd} - c:\program files\Mozilla Firefox\extensions\{972ce4c6-7e08-4474-a285-3208198ce6fd}
FF - Ext: Java Console: {CAFEEFAC-0016-0000-0016-ABCDEFFEDCBA} - c:\program files\Mozilla Firefox\extensions\{CAFEEFAC-0016-0000-0016-ABCDEFFEDCBA}
FF - Ext: Conduit Engine : [removed] - %profile%\extensions\[removed]
FF - Ext: Microsoft .NET Framework Assistant: {20a82645-c095-46ed-80e3-08825760534b} - %profile%\extensions\{20a82645-c095-46ed-80e3-08825760534b}
FF - Ext: Google Toolbar for Firefox: {3112ca9c-de6d-4884-a869-9855de68056c} - %profile%\extensions\{3112ca9c-de6d-4884-a869-9855de68056c}
FF - Ext: Radio TV 2.2 Community Toolbar: {fafaacea-c957-4d38-884d-4f4045a0bca4} - %profile%\extensions\{fafaacea-c957-4d38-884d-4f4045a0bca4}
FF - Ext: Microsoft .NET Framework Assistant: {20a82645-c095-46ed-80e3-08825760534b} - c:\windows\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\DotNetAssistantExtension
FF - Ext: Java Quick Starter: [removed] - c:\program files\Java\jre6\lib\deploy\jqs\ff
FF - Ext: Symantec IPS: {BBDA0591-3099-440a-AA10-41764D9DB4DB} - c:\documents and settings\All Users\Application Data\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NIS_18.5.0.125\IPSFFPlgn
FF - Ext: XULRunner: {5D6AADAF-FDA2-4EC2-8654-5429C3348E35} - c:\documents and settings\Owner\Local Settings\Application Data\{5D6AADAF-FDA2-4EC2-8654-5429C3348E35}
FF - Ext: XULRunner: {126CE956-FEFD-4ACF-8995-5900527F6ADB} - c:\documents and settings\Owner\Local Settings\Application Data\{126CE956-FEFD-4ACF-8995-5900527F6ADB}
FF - Ext: Norton Toolbar: {2D3F3651-74B9-4795-BDEC-6DA2F431CB62} - c:\documents and settings\All Users\Application Data\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NIS_18.5.0.125\coFFPlgn_2011_7_0_8
.
- - - - ORPHANS REMOVED - - - -
.
HKCU-Run-BgMonitor_{79662E04-7C6C-4d9f-84C7-88D8A56B10AA} - c:\program files\Common Files\Ahead\Lib\NMBgMonitor.exe
.
.
.
**************************************************************************
.
catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net
Rootkit scan 2011-07-08 09:40
Windows 5.1.2600 Service Pack 3 NTFS
.
scanning hidden processes …
.
scanning hidden autostart entries …
.
scanning hidden files …
.
scan completed successfully
hidden files: 0
.
**************************************************************************
.
[HKEY_LOCAL_MACHINE\System\ControlSet003\Services\NIS]
"ImagePath"="\"c:\program files\Norton Internet Security\Engine\18.6.0.29\ccSvcHst.exe\" /s \"NIS\" /m \"c:\program files\Norton Internet Security\Engine\18.6.0.29\diMaster.dll\" /prefetch:1"
.
——————— DLLs Loaded Under Running Processes ———————
.
- - - - - - - > 'explorer.exe'(1084)
c:\windows\system32\WININET.dll
c:\windows\system32\ieframe.dll
c:\windows\system32\webcheck.dll
c:\windows\system32\WPDShServiceObj.dll
c:\windows\system32\PortableDeviceTypes.dll
c:\windows\system32\PortableDeviceApi.dll
.
———————— Other Running Processes ————————
.
c:\program files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
c:\program files\Java\jre6\bin\jqs.exe
c:\program files\Common Files\LightScribe\LSSrvc.exe
c:\program files\Common Files\Microsoft Shared\VS7Debug\mdm.exe
c:\windows\system32\nvsvc32.exe
c:\windows\system32\HPZipm12.exe
c:\program files\Microsoft\Search Enhancement Pack\SeaPort\SeaPort.exe
c:\windows\system32\RUNDLL32.EXE
c:\program files\iPod\bin\iPodService.exe
c:\windows\system32\wscntfy.exe
.
**************************************************************************
.
Completion time: 2011-07-08 09:52:57 - machine was rebooted
ComboFix-quarantined-files.txt 2011-07-08 08:52
.
Pre-Run: 133,526,929,408 bytes free
Post-Run: 133,609,025,536 bytes free
.
WindowsXP-KB310994-SP2-Home-BootDisk-ENU.exe
[boot loader]
timeout=2
default=multi(0)disk(0)rdisk(0)partition(1)\WINDOWS
[operating systems]
c:\cmdcons\BOOTSECT.DAT="Microsoft Windows Recovery Console" /cmdcons
UnsupportedDebug="do not select this" /debug
multi(0)disk(0)rdisk(0)partition(1)\WINDOWS="Microsoft Windows XP Home Edition" /noexecute=optin /fastdetect
.
- - End Of File - - F87D687A5EAD1A517D52678C385DF8E3
Hi benj,

Norton Internet Security is fine, but what you will want to look at is if you are going to continue using it after your subscription runs out? If not than I have a couple of free programs that I can advise later. :)
———-

1. Close any open browsers.

2. Close/disable all anti-virus and anti-malware programs so they do not interfere with the running of ComboFix.

3. Open notepad and copy/paste the text in the quotebox below into it:

File::
c:\windows\Ifupukifuri.bin

Firefox::
FF - ProfilePath - c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\
FF - prefs.js: browser.search.defaulturl
FF - prefs.js: keyword.URL
FF - Ext: Conduit Engine : [removed] - %profile%\extensions\[removed]
FF - Ext: XULRunner: {5D6AADAF-FDA2-4EC2-8654-5429C3348E35} - c:\documents and settings\Owner\Local Settings\Application Data\{5D6AADAF-FDA2-4EC2-8654-5429C3348E35}
FF - Ext: XULRunner: {126CE956-FEFD-4ACF-8995-5900527F6ADB} - c:\documents and settings\Owner\Local Settings\Application Data\{126CE956-FEFD-4ACF-8995-5900527F6ADB}


Save this as "CFScript.txt", and as Type: All Files (*.*) in the same location as ComboFix.exe


[external image: Posted Image]

Refering to the picture above, drag CFScript into ComboFix.exe

When finished, it shall produce a log for you at C:\ComboFix.txt which I will require in your next reply.
———-

Download and run HAMeb_check.exe
This program will produce a log when complete.

In your next reply please post the logs created by ComboFix as well as HAMeb_check.exe. :)
Hi Jeff,

The two Log outputs are pasted below. I don't think I saved the CFScript.txt file as Filetype "All files" (I assume it stayed as the default ".txt files"). Will this be critical?

Thanks,

Ben


ComboFix 11-07-07.06 - Owner 08/07/2011 17:29:56.2.1 - x86
Microsoft Windows XP Home Edition 5.1.2600.3.1252.1.1033.18.895.455 [GMT 1:00]
Running from: c:\documents and settings\[removed]\Desktop\ComboFix.exe
Command switches used :: c:\documents and settings\Owner\Desktop\CFScript.txt
AV: Norton Internet Security *Disabled/Updated* {E10A9785-9598-4754-B552-92431C1C35F8}
FW: Norton Internet Security *Disabled* {7C21A4C9-F61F-4AC4-B722-A6E19C16F220}
.
FILE ::
"c:\windows\Ifupukifuri.bin"
.
.
((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.
.
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\chrome.manifest
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\chrome\conduitengine.jar
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\components\ConduitAutoCompleteSearch.js
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\components\ConduitAutoCompleteSearch.xpt
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\components\ConduitToolbar.idl
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\components\ConduitToolbar.js
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\components\ConduitToolbar.xpt
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\components\RadioWMPCore.dll
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\components\RadioWMPCore.xpt
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\components\RadioWMPCoreGecko19.dll
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\defaults\alertSettingsComponent.xml
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\defaults\appContextMenu.xml
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\defaults\engineContextMenu.xml
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\defaults\engineSettings.json
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\defaults\fbAlert.js
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\defaults\getAppsContextMenu.xml
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\defaults\postAppsContextMenu.xml
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\defaults\toolbarContextMenu.xml
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\defaults\unsharedAppsContextMenu.xml
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\DualPackage\install.rdf
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\install.rdf
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\lib\xpcom.js
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\META-INF\manifest.mf
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\META-INF\zigbert.rsa
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\META-INF\zigbert.sf
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\searchplugin\conduit.gif
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\searchplugin\conduit.ico
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\searchplugin\conduit.PNG
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\searchplugin\conduit.src
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\searchplugin\conduit.xml
c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\extensions\[removed]\version.txt
c:\documents and settings\Owner\Local Settings\Application Data\{126CE956-FEFD-4ACF-8995-5900527F6ADB}
c:\documents and settings\Owner\Local Settings\Application Data\{126CE956-FEFD-4ACF-8995-5900527F6ADB}\chrome.manifest
c:\documents and settings\Owner\Local Settings\Application Data\{126CE956-FEFD-4ACF-8995-5900527F6ADB}\chrome\content\_cfg.js
c:\documents and settings\Owner\Local Settings\Application Data\{126CE956-FEFD-4ACF-8995-5900527F6ADB}\install.rdf
c:\documents and settings\Owner\Local Settings\Application Data\{5D6AADAF-FDA2-4EC2-8654-5429C3348E35}
c:\documents and settings\Owner\Local Settings\Application Data\{5D6AADAF-FDA2-4EC2-8654-5429C3348E35}\chrome.manifest
c:\documents and settings\Owner\Local Settings\Application Data\{5D6AADAF-FDA2-4EC2-8654-5429C3348E35}\chrome\content\_cfg.js
c:\documents and settings\Owner\Local Settings\Application Data\{5D6AADAF-FDA2-4EC2-8654-5429C3348E35}\install.rdf
c:\windows\Ifupukifuri.bin
.
.
((((((((((((((((((((((((( Files Created from 2011-06-08 to 2011-07-08 )))))))))))))))))))))))))))))))
.
.
2011-07-08 16:27 . 2011-07-08 16:27 ——– d—–w- C:\32788R22FWJFW
2011-07-08 08:00 . 2011-03-22 00:39 369784 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\symtdi.sys
2011-07-08 08:00 . 2011-03-22 00:39 331384 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\symtdiv.sys
2011-07-08 08:00 . 2011-03-22 00:39 296568 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\symnets.sys
2011-07-08 08:00 . 2011-03-31 03:00 516216 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\srtsp.sys
2011-07-08 08:00 . 2011-03-31 03:00 50168 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\srtspx.sys
2011-07-08 08:00 . 2011-03-15 02:31 744568 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\symefa.sys
2011-07-08 08:00 . 2011-01-27 06:47 340088 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\symds.sys
2011-07-08 08:00 . 2011-01-27 05:07 136312 —-a-w- c:\windows\system32\drivers\NIS\1206000.01D\ironx86.sys
2011-07-08 07:44 . 2011-07-08 08:53 ——– d—–w- c:\program files\Common Files\Symantec Shared
2011-07-08 07:44 . 2011-07-08 08:00 60872 —-a-w- c:\windows\system32\S32EVNT1.DLL
2011-07-08 07:44 . 2011-07-08 08:00 126584 —-a-w- c:\windows\system32\drivers\SYMEVENT.SYS
2011-07-08 07:44 . 2011-07-08 08:00 ——– d—–w- c:\program files\Symantec
2011-07-08 07:43 . 2011-07-08 07:43 ——– d—–w- c:\program files\Norton Internet Security
2011-07-08 07:41 . 2011-07-08 07:41 ——– d—–w- c:\program files\NortonInstaller
2011-07-06 08:52 . 2011-07-06 08:52 ——– d—–w- c:\documents and settings\Owner\Local Settings\Application Data\WinZip
2011-07-06 08:51 . 2011-07-06 08:52 ——– d—–w- c:\documents and settings\All Users\Application Data\WinZip
2011-06-30 08:53 . 2011-06-30 10:03 ——– d—–w- c:\documents and settings\Owner\Local Settings\Application Data\NPE
2011-06-22 17:01 . 2011-06-22 17:01 53816 —-a-w- c:\windows\system32\drivers\RapportKELL.sys
2011-06-20 07:04 . 2011-06-20 07:04 ——– d—–w- c:\documents and settings\Owner\Application Data\Tific
2011-06-20 07:03 . 2011-06-20 07:03 ——– d—–w- c:\documents and settings\Owner\Local Settings\Application Data\Symantec
2011-06-16 22:45 . 2011-06-17 08:42 ——– d—–w- c:\windows\SxsCaPendDel
2011-06-16 17:46 . 2011-04-21 13:37 105472 -c—-w- c:\windows\system32\dllcache\mup.sys
.
.
.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2011-05-02 15:31 . 2009-04-09 12:51 692736 —-a-w- c:\windows\system32\inetcomm.dll
2011-04-29 17:25 . 2004-08-04 12:00 151552 —-a-w- c:\windows\system32\schannel.dll
2011-04-29 16:19 . 2004-08-04 12:00 456320 —-a-w- c:\windows\system32\drivers\mrxsmb.sys
2011-04-25 16:11 . 2004-08-04 12:00 916480 —-a-w- c:\windows\system32\wininet.dll
2011-04-25 16:11 . 2004-08-04 12:00 43520 —-a-w- c:\windows\system32\licmgr10.dll
2011-04-25 16:11 . 2004-08-04 12:00 1469440 —-a-w- c:\windows\system32\inetcpl.cpl
2011-04-25 12:01 . 2004-08-04 12:00 385024 —-a-w- c:\windows\system32\html.iec
2011-04-21 13:37 . 2004-08-04 12:00 105472 —-a-w- c:\windows\system32\drivers\mup.sys
.
.
((((((((((((((((((((((((((((( SnapShot@2011-07-08_08.41.14 )))))))))))))))))))))))))))))))))))))))))
.
+ 2011-07-08 16:50 . 2011-07-08 16:50 16384 c:\windows\Temp\Perflib_Perfdata_7e0.dat
.
((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4
.
[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SpybotSD TeaTimer"="c:\program files\Spybot - Search & Destroy\TeaTimer.exe" [2009-03-05 2260480]
"LightScribe Control Panel"="c:\program files\Common Files\LightScribe\LightScribeControlPanel.exe" [2007-08-23 455968]
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"NvCplDaemon"="c:\windows\system32\NvCpl.dll" [2009-03-27 13684736]
"nwiz"="nwiz.exe" [2009-03-27 1657376]
"NvMediaCenter"="c:\windows\system32\NvMcTray.dll" [2009-03-27 86016]
"High Definition Audio Property Page Shortcut"="HDAShCut.exe" [2005-01-07 61952]
"dla"="c:\windows\system32\dla\tfswctrl.exe" [2004-03-15 122933]
"UpdateManager"="c:\program files\Common Files\Sonic\Update Manager\sgtray.exe" [2003-08-19 110592]
"RemoteControl"="c:\program files\CyberLink\PowerDVD\PDVDServ.exe" [2005-01-12 32768]
"HP Software Update"="c:\program files\HP\HP Software Update\HPWuSchd2.exe" [2005-05-11 49152]
"Adobe Reader Speed Launcher"="c:\program files\Adobe\Reader 9.0\Reader\Reader_sl.exe" [2009-02-27 35696]
"SunJavaUpdateSched"="c:\program files\Java\jre6\bin\jusched.exe" [2009-10-17 149280]
"DivXUpdate"="c:\program files\DivX\DivX Update\DivXUpdate.exe" [2010-06-03 1144104]
"QuickTime Task"="c:\program files\QuickTime\QTTask.exe" [2010-11-29 421888]
"AppleSyncNotifier"="c:\program files\Common Files\Apple\Mobile Device Support\AppleSyncNotifier.exe" [2011-04-20 58656]
"iTunesHelper"="c:\program files\iTunes\iTunesHelper.exe" [2011-04-27 421160]
"Synchronization Manager"="c:\windows\system32\mobsync.exe" [2008-04-14 143360]
.
[HKEY_USERS\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\Run]
"CTFMON.EXE"="c:\windows\system32\CTFMON.EXE" [2008-04-14 15360]
.
c:\documents and settings\All Users\Start Menu\Programs\Startup\
Adobe Gamma Loader.exe.lnk - c:\program files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe [2009-4-14 113664]
HP Digital Imaging Monitor.lnk - c:\program files\HP\Digital Imaging\bin\hpqtra08.exe [2005-5-11 282624]
Microsoft Office.lnk - c:\program files\Microsoft Office\Office10\OSA.EXE [2001-2-13 83360]
Tenda W541U.lnk - c:\program files\Tenda\W541U\UI.exe [2009-4-14 2121728]
WinZip Quick Pick.lnk - c:\program files\WinZip\WZQKPICK.EXE [2011-6-23 610120]
.
[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile]
"EnableFirewall"= 0 (0x0)
.
[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"c:\\Program Files\\Messenger\\msmsgs.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpqste08.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpofxm08.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hposfx08.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hposid01.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpqscnvw.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpqkygrp.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpqCopy.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpfccopy.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpzwiz01.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\Unload\\HpqPhUnl.exe"=
"c:\\Program Files\\HP\\Digital Imaging\\bin\\hpoews01.exe"=
"c:\\Program Files\\Spotify\\spotify.exe"=
"c:\\Program Files\\Windows Live\\Messenger\\msnmsgr.exe"=
"c:\\Program Files\\Windows Live\\Sync\\WindowsLiveSync.exe"=
"c:\\Program Files\\iTunes\\iTunes.exe"=
.
[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\GloballyOpenPorts\List]
"65533:TCP"= 65533:TCP:Services
"52344:TCP"= 52344:TCP:Services
"2479:TCP"= 2479:TCP:Services
"2999:TCP"= 2999:TCP:Services
"3389:TCP"= 3389:TCP:Remote Desktop
"7119:TCP"= 7119:TCP:Services
"7120:TCP"= 7120:TCP:Services
"2861:TCP"= 2861:TCP:Services
"4222:TCP"= 4222:TCP:Services
"7844:TCP"= 7844:TCP:Services
"7845:TCP"= 7845:TCP:Services
"3430:TCP"= 3430:TCP:Services
"4395:TCP"= 4395:TCP:Services
"7144:TCP"= 7144:TCP:Services
"7145:TCP"= 7145:TCP:Services
"8442:TCP"= 8442:TCP:Services
"4971:TCP"= 4971:TCP:Services
"4604:TCP"= 4604:TCP:Services
"7708:TCP"= 7708:TCP:Services
"6277:TCP"= 6277:TCP:Services
"6276:TCP"= 6276:TCP:Services
"3708:TCP"= 3708:TCP:Services
"5916:TCP"= 5916:TCP:Services
"2042:TCP"= 2042:TCP:Services
"2584:TCP"= 2584:TCP:Services
"5301:TCP"= 5301:TCP:Services
"9102:TCP"= 9102:TCP:Services
"8534:TCP"= 8534:TCP:Services
"7240:TCP"= 7240:TCP:Services
"7241:TCP"= 7241:TCP:Services
"1711:TCP"= 1711:TCP:Services
"5052:TCP"= 5052:TCP:Services
"3302:TCP"= 3302:TCP:Services
"9239:TCP"= 9239:TCP:Services
"2052:TCP"= 2052:TCP:Services
"9520:TCP"= 9520:TCP:Services
"9521:TCP"= 9521:TCP:Services
"1568:TCP"= 1568:TCP:Services
"1636:TCP"= 1636:TCP:Services
"1552:TCP"= 1552:TCP:Services
"5693:TCP"= 5693:TCP:Services
"2334:TCP"= 2334:TCP:Services
"9145:TCP"= 9145:TCP:Services
"9146:TCP"= 9146:TCP:Services
"9770:TCP"= 9770:TCP:Services
"9771:TCP"= 9771:TCP:Services
"5443:TCP"= 5443:TCP:Services
"1912:TCP"= 1912:TCP:Services
"8255:TCP"= 8255:TCP:Services
"8256:TCP"= 8256:TCP:Services
"9005:TCP"= 9005:TCP:Services
"4802:TCP"= 4802:TCP:Services
"5709:TCP"= 5709:TCP:Services
"8848:TCP"= 8848:TCP:Services
"7926:TCP"= 7926:TCP:Services
"8645:TCP"= 8645:TCP:Services
"8239:TCP"= 8239:TCP:Services
"6270:TCP"= 6270:TCP:Services
"6770:TCP"= 6770:TCP:Services
"6771:TCP"= 6771:TCP:Services
"4692:TCP"= 4692:TCP:Services
"7884:TCP"= 7884:TCP:Services
"9973:TCP"= 9973:TCP:Services
"2006:TCP"= 2006:TCP:Services
"2802:TCP"= 2802:TCP:Services
"7348:TCP"= 7348:TCP:Services
"7349:TCP"= 7349:TCP:Services
"2974:TCP"= 2974:TCP:Services
"3677:TCP"= 3677:TCP:Services
"4381:TCP"= 4381:TCP:Services
"9176:TCP"= 9176:TCP:Services
"7489:TCP"= 7489:TCP:Services
"7161:TCP"= 7161:TCP:Services
"3218:TCP"= 3218:TCP:Services
"4021:TCP"= 4021:TCP:Services
"9864:TCP"= 9864:TCP:Services
"2068:TCP"= 2068:TCP:Services
"5771:TCP"= 5771:TCP:Services
"9756:TCP"= 9756:TCP:Services
"9757:TCP"= 9757:TCP:Services
.
R0 RapportKELL;RapportKELL;c:\windows\system32\drivers\RapportKELL.sys [22/06/2011 18:01 53816]
R0 SymDS;Symantec Data Store;c:\windows\system32\drivers\NIS\1206000.01D\symds.sys [08/07/2011 09:00 340088]
R0 SymEFA;Symantec Extended File Attributes;c:\windows\system32\drivers\NIS\1206000.01D\symefa.sys [08/07/2011 09:00 744568]
R1 BHDrvx86;BHDrvx86;c:\documents and settings\All Users\Application Data\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NIS_18.5.0.125\Definitions\BASHDefs\20110701.001\BHDrvx86.sys [01/07/2011 00:11 810616]
R1 RapportCerberus_26762;RapportCerberus_26762;c:\documents and settings\All Users\Application Data\Trusteer\Rapport\store\exts\RapportCerberus\26762\RapportCerberus_26762.sys [13/06/2011 16:54 57144]
R1 RapportEI;RapportEI;c:\program files\Trusteer\Rapport\bin\RapportEI.sys [22/06/2011 18:01 66360]
R1 RapportPG;RapportPG;c:\program files\Trusteer\Rapport\bin\RapportPG.sys [22/06/2011 18:01 158904]
R1 SymIRON;Symantec Iron Driver;c:\windows\system32\drivers\NIS\1206000.01D\ironx86.sys [08/07/2011 09:00 136312]
R2 NIS;Norton Internet Security;c:\program files\Norton Internet Security\Engine\18.6.0.29\ccsvchst.exe [08/07/2011 09:00 130008]
R2 ousbehci;OrangeWare USB Enhanced Host Controller Service;c:\windows\system32\drivers\ousbehci.sys [14/04/2009 09:26 45824]
R2 RapportMgmtService;Rapport Management Service;c:\program files\Trusteer\Rapport\bin\RapportMgmtService.exe [22/06/2011 18:01 870200]
R3 IDSxpx86;IDSxpx86;c:\documents and settings\All Users\Application Data\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NIS_18.5.0.125\Definitions\IPSDefs\20110707.031\IDSXpx86.sys [07/07/2011 17:01 355256]
R3 LgBttPort;LGE Bluetooth TransPort;c:\windows\system32\drivers\lgbtport.sys [29/09/2009 08:11 12160]
R3 lgbusenum;LG Bluetooth Bus Enumerator;c:\windows\system32\drivers\lgbtbus.sys [29/09/2009 08:11 10496]
R3 LGVMODEM;LGE Virtual Modem;c:\windows\system32\drivers\lgvmodem.sys [29/09/2009 08:11 12928]
R3 ousb2hub;OrangeWare USB 2.0 Root Hub Support;c:\windows\system32\drivers\ousb2hub.sys [14/04/2009 09:26 56960]
S3 S2usbser;S2 USB Device for Legacy Serial Communication;c:\windows\system32\drivers\S2usbser.sys [20/09/2009 16:12 103680]
S3 xcpip;TCP/IP Protocol Driver;c:\windows\system32\drivers\xcpip.sys –> c:\windows\system32\drivers\xcpip.sys [?]
S3 xpsec;IPSEC driver;c:\windows\system32\drivers\xpsec.sys –> c:\windows\system32\drivers\xpsec.sys [?]
.
— Other Services/Drivers In Memory —
.
*NewlyCreated* - EECTRL
*NewlyCreated* - ERASERUTILDRVI11
*Deregistered* - EraserUtilDrvI11
.
[HKEY_LOCAL_MACHINE\software\microsoft\active setup\installed components\{10880D85-AAD9-4558-ABDC-2AB1552D831F}]
2007-08-23 16:34 451872 —-a-w- c:\program files\Common Files\LightScribe\LSRunOnce.exe
.
Contents of the 'Scheduled Tasks' folder
.
2011-07-02 c:\windows\Tasks\AppleSoftwareUpdate.job
- c:\program files\Apple Software Update\SoftwareUpdate.exe [2009-10-22 10:50]
.
2011-07-07 c:\windows\Tasks\WebReg psc 1500 series.job
- c:\program files\HP\Digital Imaging\bin\hpqwrg.exe [2005-05-11 15:45]
.
.
——- Supplementary Scan ——-
.
uStart Page = hxxp://www.orange.co.uk/
IE: Append Link Target to Existing PDF - c:\program files\Common Files\Adobe\Acrobat\ActiveX\AcroIEFavClient.dll/AcroIEAppendSelLinks.html
IE: E&xport to Microsoft Excel - c:\progra~1\MICROS~2\Office10\EXCEL.EXE/3000
IE: Google Sidewiki… - c:\program files\Google\Google Toolbar\Component\GoogleToolbarDynamic_mui_en_6CE5017F567343CA.dll/cmsidewiki.html
TCP: DhcpNameServer = 192.168.1.1
FF - ProfilePath - c:\documents and settings\Owner\Application Data\Mozilla\Firefox\Profiles\8xmflmj0.default\
FF - prefs.js: browser.search.defaulturl - hxxp://search.conduit.com/ResultsExt.aspx?ctid=CT2830584&SearchSource=3&q={searchTerms}
FF - prefs.js: browser.search.selectedEngine - Radio TV 2.2 Customized Web Search
FF - prefs.js: browser.startup.homepage - hxxp://www.yahoo.co.uk
FF - Ext: Default: {972ce4c6-7e08-4474-a285-3208198ce6fd} - c:\program files\Mozilla Firefox\extensions\{972ce4c6-7e08-4474-a285-3208198ce6fd}
FF - Ext: Java Console: {CAFEEFAC-0016-0000-0016-ABCDEFFEDCBA} - c:\program files\Mozilla Firefox\extensions\{CAFEEFAC-0016-0000-0016-ABCDEFFEDCBA}
FF - Ext: Microsoft .NET Framework Assistant: {20a82645-c095-46ed-80e3-08825760534b} - %profile%\extensions\{20a82645-c095-46ed-80e3-08825760534b}
FF - Ext: Google Toolbar for Firefox: {3112ca9c-de6d-4884-a869-9855de68056c} - %profile%\extensions\{3112ca9c-de6d-4884-a869-9855de68056c}
FF - Ext: Radio TV 2.2 Community Toolbar: {fafaacea-c957-4d38-884d-4f4045a0bca4} - %profile%\extensions\{fafaacea-c957-4d38-884d-4f4045a0bca4}
FF - Ext: Microsoft .NET Framework Assistant: {20a82645-c095-46ed-80e3-08825760534b} - c:\windows\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\DotNetAssistantExtension
FF - Ext: Java Quick Starter: [removed] - c:\program files\Java\jre6\lib\deploy\jqs\ff
FF - Ext: Symantec IPS: {BBDA0591-3099-440a-AA10-41764D9DB4DB} - c:\documents and settings\All Users\Application Data\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NIS_18.5.0.125\IPSFFPlgn
FF - Ext: Norton Toolbar: {2D3F3651-74B9-4795-BDEC-6DA2F431CB62} - c:\documents and settings\All Users\Application Data\Norton\{0C55C096-0F1D-4F28-AAA2-85EF591126E7}\NIS_18.5.0.125\coFFPlgn_2011_7_0_8
.
.
**************************************************************************
.
catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net
Rootkit scan 2011-07-08 17:49
Windows 5.1.2600 Service Pack 3 NTFS
.
scanning hidden processes …
.
scanning hidden autostart entries …
.
scanning hidden files …
.
scan completed successfully
hidden files: 0
.
**************************************************************************
.
[HKEY_LOCAL_MACHINE\System\ControlSet003\Services\NIS]
"ImagePath"="\"c:\program files\Norton Internet Security\Engine\18.6.0.29\ccSvcHst.exe\" /s \"NIS\" /m \"c:\program files\Norton Internet Security\Engine\18.6.0.29\diMaster.dll\" /prefetch:1"
.
Completion time: 2011-07-08 18:13:40
ComboFix-quarantined-files.txt 2011-07-08 17:13
ComboFix2.txt 2011-07-08 08:53
.
Pre-Run: 133,601,288,192 bytes free
Post-Run: 133,570,572,288 bytes free
.
- - End Of File - - 8599E775188993F354C3E19719077260


C:\Documents and Settings\Owner\Desktop\HAMeb_check.exe
08/07/2011 at 18:21:44.53

Account active Yes
Local Group Memberships *Administrators

~~ Checking profile list ~~

S-1-5-21-117609710-1229272821-725345543-1000
%SystemDrive%\Documents and Settings\HelpAssistant

~~ Checking for HelpAssistant directories ~~

HelpAssistant

~~ Checking mbr ~~

Stealth MBR rootkit/Mebroot/Sinowal detector 0.3.7 by Gmer, http://www.gmer.net

device: opened successfully
user: MBR read successfully
called modules: ntkrnlpa.exe catchme.sys CLASSPNP.SYS disk.sys ACPI.sys hal.dll atapi.sys pciide.sys PCIIDEX.SYS
kernel: MBR read successfully
user & kernel MBR OK
copy of MBR has been found in sector 0x0132C4977

~~ Checking for termsrv32.dll ~~

termsrv32.dll present!


HKEY_LOCAL_MACHINE\system\currentcontrolset\services\termservice\parameters
ServiceDll REG_EXPAND_SZ %SystemRoot%\System32\termsrv.dll

Jeff - sorry - here's the HAlog again, as I didn't copy and paste the whole of it in previous messafy,

Ben


C:\Documents and Settings\Owner\Desktop\HAMeb_check.exe
08/07/2011 at 18:21:44.53

Account active Yes
Local Group Memberships *Administrators

~~ Checking profile list ~~

S-1-5-21-117609710-1229272821-725345543-1000
%SystemDrive%\Documents and Settings\HelpAssistant

~~ Checking for HelpAssistant directories ~~

HelpAssistant

~~ Checking mbr ~~

Stealth MBR rootkit/Mebroot/Sinowal detector 0.3.7 by Gmer, http://www.gmer.net

device: opened successfully
user: MBR read successfully
called modules: ntkrnlpa.exe catchme.sys CLASSPNP.SYS disk.sys ACPI.sys hal.dll atapi.sys pciide.sys PCIIDEX.SYS
kernel: MBR read successfully
user & kernel MBR OK
copy of MBR has been found in sector 0x0132C4977

~~ Checking for termsrv32.dll ~~

termsrv32.dll present!


HKEY_LOCAL_MACHINE\system\currentcontrolset\services\termservice\parameters
ServiceDll REG_EXPAND_SZ %SystemRoot%\System32\termsrv.dll

~~ Checking firewall ports ~~

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\DomainProfile\GloballyOpenPorts\List]
"65533:TCP"=65533:TCP:*:Enabled:Services
"52344:TCP"=52344:TCP:*:Enabled:Services
"2479:TCP"=2479:TCP:*:Enabled:Services
"2999:TCP"=2999:TCP:*:Enabled:Services
"3389:TCP"=3389:TCP:*:Enabled:Remote Desktop
"7119:TCP"=7119:TCP:*:Enabled:Services
"7120:TCP"=7120:TCP:*:Enabled:Services
"2861:TCP"=2861:TCP:*:Enabled:Services
"4222:TCP"=4222:TCP:*:Enabled:Services
"7844:TCP"=7844:TCP:*:Enabled:Services
"7845:TCP"=7845:TCP:*:Enabled:Services
"3430:TCP"=3430:TCP:*:Enabled:Services
"4395:TCP"=4395:TCP:*:Enabled:Services
"7144:TCP"=7144:TCP:*:Enabled:Services
"7145:TCP"=7145:TCP:*:Enabled:Services
"8442:TCP"=8442:TCP:*:Enabled:Services
"4971:TCP"=4971:TCP:*:Enabled:Services
"4604:TCP"=4604:TCP:*:Enabled:Services
"7708:TCP"=7708:TCP:*:Enabled:Services
"6277:TCP"=6277:TCP:*:Enabled:Services
"6276:TCP"=6276:TCP:*:Enabled:Services
"3708:TCP"=3708:TCP:*:Enabled:Services
"5916:TCP"=5916:TCP:*:Enabled:Services
"2042:TCP"=2042:TCP:*:Enabled:Services
"2584:TCP"=2584:TCP:*:Enabled:Services
"5301:TCP"=5301:TCP:*:Enabled:Services
"9102:TCP"=9102:TCP:*:Enabled:Services
"8534:TCP"=8534:TCP:*:Enabled:Services
"7240:TCP"=7240:TCP:*:Enabled:Services
"7241:TCP"=7241:TCP:*:Enabled:Services
"1711:TCP"=1711:TCP:*:Enabled:Services
"5052:TCP"=5052:TCP:*:Enabled:Services
"3302:TCP"=3302:TCP:*:Enabled:Services
"9239:TCP"=9239:TCP:*:Enabled:Services
"2052:TCP"=2052:TCP:*:Enabled:Services
"9520:TCP"=9520:TCP:*:Enabled:Services
"9521:TCP"=9521:TCP:*:Enabled:Services
"1568:TCP"=1568:TCP:*:Enabled:Services
"1636:TCP"=1636:TCP:*:Enabled:Services
"1552:TCP"=1552:TCP:*:Enabled:Services
"5693:TCP"=5693:TCP:*:Enabled:Services
"2334:TCP"=2334:TCP:*:Enabled:Services
"9145:TCP"=9145:TCP:*:Enabled:Services
"9146:TCP"=9146:TCP:*:Enabled:Services
"9770:TCP"=9770:TCP:*:Enabled:Services
"9771:TCP"=9771:TCP:*:Enabled:Services
"5443:TCP"=5443:TCP:*:Enabled:Services
"1912:TCP"=1912:TCP:*:Enabled:Services
"8255:TCP"=8255:TCP:*:Enabled:Services
"8256:TCP"=8256:TCP:*:Enabled:Services
"9005:TCP"=9005:TCP:*:Enabled:Services
"4802:TCP"=4802:TCP:*:Enabled:Services
"5709:TCP"=5709:TCP:*:Enabled:Services
"8848:TCP"=8848:TCP:*:Enabled:Services
"7926:TCP"=7926:TCP:*:Enabled:Services
"8645:TCP"=8645:TCP:*:Enabled:Services
"8239:TCP"=8239:TCP:*:Enabled:Services
"6270:TCP"=6270:TCP:*:Enabled:Services
"6770:TCP"=6770:TCP:*:Enabled:Services
"6771:TCP"=6771:TCP:*:Enabled:Services
"4692:TCP"=4692:TCP:*:Enabled:Services
"7884:TCP"=7884:TCP:*:Enabled:Services
"9973:TCP"=9973:TCP:*:Enabled:Services
"2006:TCP"=2006:TCP:*:Enabled:Services
"2802:TCP"=2802:TCP:*:Enabled:Services
"7348:TCP"=7348:TCP:*:Enabled:Services
"7349:TCP"=7349:TCP:*:Enabled:Services
"2974:TCP"=2974:TCP:*:Enabled:Services
"3677:TCP"=3677:TCP:*:Enabled:Services
"4381:TCP"=4381:TCP:*:Enabled:Services
"9176:TCP"=9176:TCP:*:Enabled:Services
"7489:TCP"=7489:TCP:*:Enabled:Services
"7161:TCP"=7161:TCP:*:Enabled:Services
"3218:TCP"=3218:TCP:*:Enabled:Services
"4021:TCP"=4021:TCP:*:Enabled:Services
"9864:TCP"=9864:TCP:*:Enabled:Services
"2068:TCP"=2068:TCP:*:Enabled:Services
"5771:TCP"=5771:TCP:*:Enabled:Services
"9756:TCP"=9756:TCP:*:Enabled:Services
"9757:TCP"=9757:TCP:*:Enabled:Services

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\GloballyOpenPorts\List]
"65533:TCP"=65533:TCP:*:Enabled:Services
"52344:TCP"=52344:TCP:*:Enabled:Services
"2479:TCP"=2479:TCP:*:Enabled:Services
"2999:TCP"=2999:TCP:*:Enabled:Services
"3389:TCP"=3389:TCP:*:Enabled:Remote Desktop
"7119:TCP"=7119:TCP:*:Enabled:Services
"7120:TCP"=7120:TCP:*:Enabled:Services
"2861:TCP"=2861:TCP:*:Enabled:Services
"4222:TCP"=4222:TCP:*:Enabled:Services
"7844:TCP"=7844:TCP:*:Enabled:Services
"7845:TCP"=7845:TCP:*:Enabled:Services
"3430:TCP"=3430:TCP:*:Enabled:Services
"4395:TCP"=4395:TCP:*:Enabled:Services
"7144:TCP"=7144:TCP:*:Enabled:Services
"7145:TCP"=7145:TCP:*:Enabled:Services
"8442:TCP"=8442:TCP:*:Enabled:Services
"4971:TCP"=4971:TCP:*:Enabled:Services
"4604:TCP"=4604:TCP:*:Enabled:Services
"7708:TCP"=7708:TCP:*:Enabled:Services
"6277:TCP"=6277:TCP:*:Enabled:Services
"6276:TCP"=6276:TCP:*:Enabled:Services
"3708:TCP"=3708:TCP:*:Enabled:Services
"5916:TCP"=5916:TCP:*:Enabled:Services
"2042:TCP"=2042:TCP:*:Enabled:Services
"2584:TCP"=2584:TCP:*:Enabled:Services
"5301:TCP"=5301:TCP:*:Enabled:Services
"9102:TCP"=9102:TCP:*:Enabled:Services
"8534:TCP"=8534:TCP:*:Enabled:Services
"7240:TCP"=7240:TCP:*:Enabled:Services
"7241:TCP"=7241:TCP:*:Enabled:Services
"1711:TCP"=1711:TCP:*:Enabled:Services
"5052:TCP"=5052:TCP:*:Enabled:Services
"3302:TCP"=3302:TCP:*:Enabled:Services
"9239:TCP"=9239:TCP:*:Enabled:Services
"2052:TCP"=2052:TCP:*:Enabled:Services
"9520:TCP"=9520:TCP:*:Enabled:Services
"9521:TCP"=9521:TCP:*:Enabled:Services
"1568:TCP"=1568:TCP:*:Enabled:Services
"1636:TCP"=1636:TCP:*:Enabled:Services
"1552:TCP"=1552:TCP:*:Enabled:Services
"5693:TCP"=5693:TCP:*:Enabled:Services
"2334:TCP"=2334:TCP:*:Enabled:Services
"9145:TCP"=9145:TCP:*:Enabled:Services
"9146:TCP"=9146:TCP:*:Enabled:Services
"9770:TCP"=9770:TCP:*:Enabled:Services
"9771:TCP"=9771:TCP:*:Enabled:Services
"5443:TCP"=5443:TCP:*:Enabled:Services
"1912:TCP"=1912:TCP:*:Enabled:Services
"8255:TCP"=8255:TCP:*:Enabled:Services
"8256:TCP"=8256:TCP:*:Enabled:Services
"9005:TCP"=9005:TCP:*:Enabled:Services
"4802:TCP"=4802:TCP:*:Enabled:Services
"5709:TCP"=5709:TCP:*:Enabled:Services
"8848:TCP"=8848:TCP:*:Enabled:Services
"7926:TCP"=7926:TCP:*:Enabled:Services
"8645:TCP"=8645:TCP:*:Enabled:Services
"8239:TCP"=8239:TCP:*:Enabled:Services
"6270:TCP"=6270:TCP:*:Enabled:Services
"6770:TCP"=6770:TCP:*:Enabled:Services
"6771:TCP"=6771:TCP:*:Enabled:Services
"4692:TCP"=4692:TCP:*:Enabled:Services
"7884:TCP"=7884:TCP:*:Enabled:Services
"9973:TCP"=9973:TCP:*:Enabled:Services
"2006:TCP"=2006:TCP:*:Enabled:Services
"2802:TCP"=2802:TCP:*:Enabled:Services
"7348:TCP"=7348:TCP:*:Enabled:Services
"7349:TCP"=7349:TCP:*:Enabled:Services
"2974:TCP"=2974:TCP:*:Enabled:Services
"3677:TCP"=3677:TCP:*:Enabled:Services
"4381:TCP"=4381:TCP:*:Enabled:Services
"9176:TCP"=9176:TCP:*:Enabled:Services
"7489:TCP"=7489:TCP:*:Enabled:Services
"7161:TCP"=7161:TCP:*:Enabled:Services
"3218:TCP"=3218:TCP:*:Enabled:Services
"4021:TCP"=4021:TCP:*:Enabled:Services
"9864:TCP"=9864:TCP:*:Enabled:Services
"2068:TCP"=2068:TCP:*:Enabled:Services
"5771:TCP"=5771:TCP:*:Enabled:Services
"9756:TCP"=9756:TCP:*:Enabled:Services
"9757:TCP"=9757:TCP:*:Enabled:Services


~~ EOF ~~
Hi benj,

It may be a good idea to print out these instructions.
  • Close out all other open programs and windows.
  • Double click the file to run it and follow any prompts.

When it completes, a log will open.

Please post the contents of that log.

Note: If the tool detects an mbr infection, follow theses additional instructions.

please allow it to run mbr -f and shutdown your computer.
Upon restarting, please wait about 5 minutes, click Start>Run and type the following bolded command, then hit Enter.

helpasst -mbrt

Make sure you leave a space between helpasst and -mbrt !

When it completes, a log will open.

Please post the contents of that log.

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI