This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

Google Redirect

18 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

I recently had some issues where my Google Chrome browser was redirecting me. I would search for a term using Google, and click on a result. Once I clicked the result, a new tab would open and redirect me to some random website (random to me). I ended up scanning my computer with Malwarebytes' and Avast Antivirus.

After the scans were complete, I removed the files and restarted. The redirecting seems to have stopped, but now I can't update Malwarebytes'. Since I couldn't update Malwarebytes', I tried using Super Anti Spyware. SAS won't update either. I came here and read the "Are you Infected". I decided to run the OTL program since I'd never heard of it :popcorn: . Here are the two reports:

OTL logfile created on: 6/21/2011 3:45:46 PM - Run 1
OTL by OldTimer - Version 3.2.24.1	 Folder = C:\Users\Nsnd\Desktop
64bit- Home Premium Edition  (Version = 6.1.7600) - Type = NTWorkstation
Internet Explorer (Version = 8.0.7600.16385)
Locale: 00000409 | Country: United States | Language: ENU | Date Format: M/d/yyyy
 
5.99 Gb Total Physical Memory | 4.35 Gb Available Physical Memory | 72.57% Memory free
11.98 Gb Paging File | 10.00 Gb Available in Paging File | 83.45% Paging File free
Paging file location(s): ?:\pagefile.sys [binary data]
 
%SystemDrive% = C: | %SystemRoot% = C:\Windows | %ProgramFiles% = C:\Program Files (x86)
Drive C: | 448.74 Gb Total Space | 153.72 Gb Free Space | 34.26% Space Free | Partition Type: NTFS
Drive D: | 16.72 Gb Total Space | 2.70 Gb Free Space | 16.17% Space Free | Partition Type: NTFS
Drive E: | 99.02 Mb Total Space | 92.44 Mb Free Space | 93.35% Space Free | Partition Type: FAT32
Drive F: | 664.99 Mb Total Space | 0.00 Mb Free Space | 0.00% Space Free | Partition Type: CDFS
 
Computer Name: NSND-PC | User Name: Nsnd | Logged in as Administrator.
Boot Mode: Normal | Scan Mode: Current user | Include 64bit Scans
Company Name Whitelist: Off | Skip Microsoft Files: Off | No Company Name Whitelist: On | File Age = 30 Days
 
========== Processes (SafeList) ==========
 
PRC - C:\Users\Nsnd\Desktop\OTL.exe (OldTimer Tools)
PRC - C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe (Adobe Systems Incorporated)
PRC - C:\Program Files (x86)\GoZone\GoZone_iSync.exe (Virgin HealthMiles Inc.)
PRC - C:\Program Files\Alwil Software\Avast5\AvastSvc.exe (AVAST Software)
PRC - C:\Program Files (x86)\PdaNet for Android\PdaNetPC.exe ()
PRC - C:\Program Files (x86)\Steam\Steam.exe (Valve Corporation)
PRC - C:\Program Files (x86)\Pando Networks\Media Booster\PMB.exe ()
PRC - C:\Program Files (x86)\Unlocker\UnlockerAssistant.exe ()
PRC - C:\Program Files (x86) (x86)\Lexmark 2600 Series\ezprint.exe (Lexmark International Inc.)
PRC - C:\Program Files (x86)\DigitalPersona\Bin\DpHostW.exe (DigitalPersona, Inc.)
PRC - C:\Program Files (x86)\DigitalPersona\Bin\DpAgent.exe (DigitalPersona, Inc.)
PRC - C:\Windows\SysWOW64\vmnat.exe (VMware, Inc.)
PRC - C:\Program Files (x86)\VMware\VMware Workstation\vmware-authd.exe (VMware, Inc.)
PRC - C:\Windows\SysWOW64\vmnetdhcp.exe (VMware, Inc.)
PRC - C:\Program Files (x86)\VMware\VMware Workstation\vmware-tray.exe (VMware, Inc.)
PRC - C:\Program Files (x86)\Common Files\VMware\USB\vmware-usbarbitrator.exe (VMware, Inc.)
PRC - C:\Program Files (x86)\Corel\Corel Paint Shop Pro Photo X2\CorelIOMonitor.exe ()
PRC - C:\Program Files (x86)\PowerISO\PWRISOVM.EXE (PowerISO Computing, Inc.)
PRC - C:\Program Files (x86)\Common Files\Protexis\License Service\PsiService_2.exe (Protexis Inc.)
 
 
========== Modules (SafeList) ==========
 
MOD - C:\Users\Nsnd\Desktop\OTL.exe (OldTimer Tools)
MOD - C:\Program Files\Alwil Software\Avast5\snxhk.dll (AVAST Software)
MOD - C:\Windows\winsxs\x86_microsoft.windows.common-controls_6595b64144ccf1df_6.0.7600.16661_none_420fe3fa2b8113bd\comctl32.dll (Microsoft Corporation)
MOD - C:\Program Files (x86)\Unlocker\UnlockerHook.dll ()
MOD - C:\Program Files (x86)\DigitalPersona\Bin\DpOFeedb.dll (DigitalPersona, Inc.)
MOD - C:\Program Files (x86)\DigitalPersona\Bin\DpOSet.dll (DigitalPersona, Inc.)
 
 
========== Win32 Services (SafeList) ==========
 
SRV:64bit: - (!SASCORE) – C:\Program Files\SUPERAntiSpyware\SASCORE64.EXE (SUPERAntiSpyware.com)
SRV:64bit: - (avast! Antivirus) – C:\Program Files\Alwil Software\Avast5\AvastSvc.exe (AVAST Software)
SRV:64bit: - (hpsrv) – C:\Windows\SysNative\hpservice.exe (Hewlett-Packard Company)
SRV:64bit: - (STacSV) – C:\Windows\SysNative\DriverStore\FileRepository\stwrt64.inf_amd64_neutral_ccf0dd3cb081af84\stacsv64.exe (IDT, Inc.)
SRV:64bit: - (WinDefend) – C:\Program Files\Windows Defender\MpSvc.dll (Microsoft Corporation)
SRV:64bit: - (vcsFPService) – C:\Windows\SysNative\vcsFPService.exe (Validity Sensors, Inc.)
SRV:64bit: - (AESTFilters) – C:\Windows\SysNative\DriverStore\FileRepository\stwrt64.inf_amd64_neutral_ccf0dd3cb081af84\AESTSr64.exe (Andrea Electronics Corporation)
SRV:64bit: - (lxdn_device) – C:\Windows\SysNative\lxdncoms.exe ( )
SRV - (AdobeARMservice) – C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe (Adobe Systems Incorporated)
SRV - (Steam Client Service) – C:\Program Files (x86)\Common Files\Steam\SteamService.exe (Valve Corporation)
SRV - (clr_optimization_v4.0.30319_32) – C:\Windows\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe (Microsoft Corporation)
SRV - (SwitchBoard) – C:\Program Files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe (Adobe Systems Incorporated)
SRV - (DpHost) – C:\Program Files (x86)\DigitalPersona\Bin\DpHostW.exe (DigitalPersona, Inc.)
SRV - (VMware NAT Service) – C:\Windows\SysWOW64\vmnat.exe (VMware, Inc.)
SRV - (VMAuthdService) – C:\Program Files (x86)\VMware\VMware Workstation\vmware-authd.exe (VMware, Inc.)
SRV - (VMnetDHCP) – C:\Windows\SysWOW64\vmnetdhcp.exe (VMware, Inc.)
SRV - (VMUSBArbService) – C:\Program Files (x86)\Common Files\VMware\USB\vmware-usbarbitrator.exe (VMware, Inc.)
SRV - (ufad-ws60) – C:\Program Files (x86)\VMware\VMware Workstation\vmware-ufad.exe (VMware, Inc.)
SRV - (vcsFPService) – C:\Windows\SysWOW64\vcsFPService.exe (Validity Sensors, Inc.)
SRV - (clr_optimization_v2.0.50727_32) – C:\Windows\Microsoft.NET\Framework\v2.0.50727\mscorsvw.exe (Microsoft Corporation)
SRV - (lxdn_device) – C:\Windows\SysWow64\lxdncoms.exe ( )
SRV - (PSI_SVC_2) – C:\Program Files (x86)\Common Files\Protexis\License Service\PsiService_2.exe (Protexis Inc.)
 
 
========== Driver Services (SafeList) ==========
 
DRV:64bit: - (amdsata) – C:\Windows\SysNative\drivers\amdsata.sys (Advanced Micro Devices)
DRV:64bit: - (amdxata) – C:\Windows\SysNative\drivers\amdxata.sys (Advanced Micro Devices)
DRV:64bit: - (USBAAPL64) – C:\Windows\SysNative\drivers\usbaapl64.sys (Apple, Inc.)
DRV:64bit: - (aswMonFlt) – C:\Windows\SysNative\drivers\aswMonFlt.sys (AVAST Software)
DRV:64bit: - (HssDrv) – C:\Windows\SysNative\drivers\HssDrv.sys (AnchorFree Inc.)
DRV:64bit: - (hpdskflt) – C:\Windows\SysNative\drivers\hpdskflt.sys (Hewlett-Packard Company)
DRV:64bit: - (Accelerometer) – C:\Windows\SysNative\drivers\Accelerometer.sys (Hewlett-Packard Company)
DRV:64bit: - (SynTP) – C:\Windows\SysNative\drivers\SynTP.sys (Synaptics Incorporated)
DRV:64bit: - (dc3d) MS Hardware Device Detection Driver (HID) – C:\Windows\SysNative\drivers\dc3d.sys (Microsoft Corporation)
DRV:64bit: - (SASDIFSV) – C:\Program Files\SUPERAntiSpyware\sasdifsv64.sys (SUPERAdBlocker.com and SUPERAntiSpyware.com)
DRV:64bit: - (SASKUTIL) – C:\Program Files\SUPERAntiSpyware\saskutil64.sys (SUPERAdBlocker.com and SUPERAntiSpyware.com)
DRV:64bit: - (NVHDA) – C:\Windows\SysNative\drivers\nvhda64v.sys (NVIDIA Corporation)
DRV:64bit: - (NETw5s64) Intel(R) – C:\Windows\SysNative\drivers\NETw5s64.sys (Intel Corporation)
DRV:64bit: - (vmci) – C:\Windows\SysNative\drivers\vmci.sys (VMware, Inc.)
DRV:64bit: - (vmkbd) – C:\Windows\SysNative\drivers\VMkbd.sys (VMware, Inc.)
DRV:64bit: - (vmx86) – C:\Windows\SysNative\drivers\vmx86.sys (VMware, Inc.)
DRV:64bit: - (VMnetuserif) – C:\Windows\SysNative\drivers\vmnetuserif.sys (VMware, Inc.)
DRV:64bit: - (hcmon) – C:\Windows\SysNative\drivers\hcmon.sys (VMware, Inc.)
DRV:64bit: - (VMnetBridge) – C:\Windows\SysNative\drivers\vmnetbridge.sys (VMware, Inc.)
DRV:64bit: - (VMnetAdapter) – C:\Windows\SysNative\drivers\vmnetadapter.sys (VMware, Inc.)
DRV:64bit: - (sdbus) – C:\Windows\SysNative\drivers\sdbus.sys (Microsoft Corporation)
DRV:64bit: - (RTL8167) – C:\Windows\SysNative\drivers\Rt64win7.sys (Realtek											)
DRV:64bit: - (netr28ux) – C:\Windows\SysNative\drivers\netr28ux.sys (Ralink Technology Corp.)
DRV:64bit: - (iaStor) – C:\Windows\SysNative\drivers\iaStor.sys (Intel Corporation)
DRV:64bit: - (STHDA) – C:\Windows\SysNative\drivers\stwrt64.sys (IDT, Inc.)
DRV:64bit: - (JMCR) – C:\Windows\SysNative\drivers\jmcr.sys (JMicron Technology Corporation)
DRV:64bit: - (amdsbs) – C:\Windows\SysNative\drivers\amdsbs.sys (AMD Technologies Inc.)
DRV:64bit: - (LSI_SAS2) – C:\Windows\SysNative\drivers\lsi_sas2.sys (LSI Corporation)
DRV:64bit: - (HpSAMD) – C:\Windows\SysNative\drivers\HpSAMD.sys (Hewlett-Packard Company)
DRV:64bit: - (stexstor) – C:\Windows\SysNative\drivers\stexstor.sys (Promise Technology)
DRV:64bit: - (ROOTMODEM) – C:\Windows\SysNative\drivers\rootmdm.sys (Microsoft Corporation)
DRV:64bit: - (enecir) – C:\Windows\SysNative\drivers\enecir.sys (ENE TECHNOLOGY INC.)
DRV:64bit: - (SrvHsfV92) – C:\Windows\SysNative\drivers\VSTDPV6.SYS (Conexant Systems, Inc.)
DRV:64bit: - (SrvHsfWinac) – C:\Windows\SysNative\drivers\VSTCNXT6.SYS (Conexant Systems, Inc.)
DRV:64bit: - (SrvHsfHDA) – C:\Windows\SysNative\drivers\VSTAZL6.SYS (Conexant Systems, Inc.)
DRV:64bit: - (Ntfs) – C:\Windows\SysNative\wbem\ntfs.mof ()
DRV:64bit: - (igfx) – C:\Windows\SysNative\drivers\igdkmd64.sys (Intel Corporation)
DRV:64bit: - (yukonw7) – C:\Windows\SysNative\drivers\yk62x64.sys (Marvell)
DRV:64bit: - (netw5v64) Intel(R) – C:\Windows\SysNative\drivers\netw5v64.sys (Intel Corporation)
DRV:64bit: - (ebdrv) – C:\Windows\SysNative\drivers\evbda.sys (Broadcom Corporation)
DRV:64bit: - (b06bdrv) – C:\Windows\SysNative\drivers\bxvbda.sys (Broadcom Corporation)
DRV:64bit: - (b57nd60a) – C:\Windows\SysNative\drivers\b57nd60a.sys (Broadcom Corporation)
DRV:64bit: - (hcw85cir) – C:\Windows\SysNative\drivers\hcw85cir.sys (Hauppauge Computer Works, Inc.)
DRV:64bit: - (GEARAspiWDM) – C:\Windows\SysNative\drivers\GEARAspiWDM.sys (GEAR Software Inc.)
DRV:64bit: - (NuidFltr) – C:\Windows\SysNative\drivers\nuidfltr.sys (Microsoft Corporation)
DRV:64bit: - (HpqKbFiltr) – C:\Windows\SysNative\drivers\HpqKbFiltr.sys (Hewlett-Packard Development Company, L.P.)
DRV:64bit: - (WDC_SAM) – C:\Windows\SysNative\drivers\wdcsam64.sys (Western Digital Technologies)
DRV:64bit: - (pnetmdm) – C:\Windows\SysNative\drivers\pnetmdm64.sys (June Fabrics Technology)
DRV - (vstor2-ws60) – C:\Program Files (x86)\VMware\VMware Workstation\vstor2-ws60.sys (VMware, Inc.)
DRV - (ISODrive) – C:\Program Files (x86)\UltraISO\drivers\ISODrv64.sys (EZB Systems, Inc.)
 
 
========== Standard Registry (SafeList) ==========
 
 
========== Internet Explorer ==========
 
IE:64bit: - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://g.msn.com/HPNOT/1
IE - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Local Page = C:\Windows\SysWOW64\blank.htm
IE - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://g.msn.com/HPNOT/1
 
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://apps.ko.com/myko
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyEnable" = 0
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyOverride" = *.local
 
FF - HKLM\software\mozilla\Firefox\Extensions\\[removed]: C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\MozillaAddOn3 [2010/04/29 19:02:24 | 000,000,000 | —D | M]
FF - HKLM\software\mozilla\Firefox\Extensions\\[removed]: C:\Program Files (x86)\DigitalPersona\Bin\FirefoxExt\ [2010/07/01 10:49:14 | 000,000,000 | —D | M]
 
 
O1 HOSTS File: ([2011/06/19 15:08:11 | 000,000,027 | —- | M]) - C:\Windows\SysNative\drivers\etc\hosts
O1 - Hosts: 127.0.0.1	   localhost
O2:64bit: - BHO: (DigitalPersona Personal Extension) - {395610AE-C624-4f58-B89E-23733EA00F9A} - C:\Program Files\DigitalPersona\Bin\DpOtsPluginIe8.dll (DigitalPersona, Inc.)
O2:64bit: - BHO: (Java™ Plug-In 2 SSV Helper) - {DBC80044-A445-435b-BC74-9C25C1C588A9} -  File not found
O2 - BHO: (DigitalPersona Personal Extension) - {395610AE-C624-4f58-B89E-23733EA00F9A} - C:\Program Files (x86)\DigitalPersona\Bin\DpOtsPluginIe8.dll (DigitalPersona, Inc.)
O3 - HKCU\..\Toolbar\WebBrowser: (no name) - {604BC32A-9680-40D1-9AC6-E06B23A1BA4C} - No CLSID value found.
O4:64bit: - HKLM..\Run: [AdobeAAMUpdater-1.0] C:\Program Files (x86)\Common Files\Adobe\OOBE\PDApp\UWA\UpdaterStartupUtility.exe (Adobe Systems Incorporated)
O4:64bit: - HKLM..\Run: [HPToneControl] C:\Program Files\Hewlett-Packard\HPToneControl\HPToneCtl.exe (Hewlett-Packard )
O4:64bit: - HKLM..\Run: [SysTrayApp] C:\Program Files\IDT\WDM\sttray64.exe (IDT, Inc.)
O4 - HKLM..\Run: [AdobeCS5ServiceManager] C:\Program Files (x86)\Common Files\Adobe\CS5ServiceManager\CS5ServiceManager.exe (Adobe Systems Incorporated)
O4 - HKLM..\Run: [Corel File Shell Monitor] C:\Program Files (x86)\Corel\Corel Paint Shop Pro Photo X2\CorelIOMonitor.exe ()
O4 - HKLM..\Run: [DpAgent] C:\Program Files (x86)\DigitalPersona\Bin\DpAgent.exe (DigitalPersona, Inc.)
O4 - HKLM..\Run: [EzPrint] C:\Program Files (x86) (x86)\Lexmark 2600 Series\ezprint.exe (Lexmark International Inc.)
O4 - HKLM..\Run: [HPCam_Menu] c:\Program Files (x86)\Hewlett-Packard\Media\Webcam\MUITransfer\MUIStartMenu.exe (CyberLink Corp.)
O4 - HKLM..\Run: [lxdnmon.exe] C:\Program Files (x86) (x86)\Lexmark 2600 Series\lxdnmon.exe ()
O4 - HKLM..\Run: [PWRISOVM.EXE] C:\Program Files (x86)\PowerISO\PWRISOVM.EXE (PowerISO Computing, Inc.)
O4 - HKLM..\Run: [SwitchBoard] C:\Program Files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe (Adobe Systems Incorporated)
O4 - HKLM..\Run: [UnlockerAssistant] C:\Program Files (x86)\Unlocker\UnlockerAssistant.exe ()
O4 - HKLM..\Run: [vmware-tray] C:\Program Files (x86)\VMware\VMware Workstation\vmware-tray.exe (VMware, Inc.)
O4 - HKCU..\Run: [Pando Media Booster] C:\Program Files (x86)\Pando Networks\Media Booster\PMB.exe ()
O4 - HKCU..\Run: [Steam] c:\program files (x86)\steam\steam.exe (Valve Corporation)
O4 - HKCU..\Run: [SUPERAntiSpyware] C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe (SUPERAntiSpyware.com)
O4 - Startup: C:\Users\Nsnd\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\GoZone iSync.lnk = C:\Program Files (x86)\GoZone\GoZone_iSync.exe (Virgin HealthMiles Inc.)
O4 - Startup: C:\Users\Nsnd\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\PdaNet Desktop.lnk = C:\Program Files (x86)\PdaNet for Android\PdaNetPC.exe ()
O6 - HKLM\Software\Policies\Microsoft\Internet Explorer\Restrictions present
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDriveTypeAutoRun = 255
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDrives = 0
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: ConsentPromptBehaviorAdmin = 0
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: ConsentPromptBehaviorUser = 3
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: EnableLUA = 0
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\System: PromptOnSecureDesktop = 0
O7 - HKCU\Software\Policies\Microsoft\Internet Explorer\Control Panel present
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDrives = 0
O10:64bit: - NameSpace_Catalog5\Catalog_Entries\000000000009 [] - C:\Program Files (x86)\Bonjour\mdnsNSP.dll (Apple Inc.)
O10:64bit: - Protocol_Catalog9\Catalog_Entries\000000000011 - C:\Program Files (x86)\VMware\VMware Workstation\vsocklib.dll (VMware, Inc.)
O10:64bit: - Protocol_Catalog9\Catalog_Entries\000000000012 - C:\Program Files (x86)\VMware\VMware Workstation\vsocklib.dll (VMware, Inc.)
O10 - NameSpace_Catalog5\Catalog_Entries\000000000009 [] - C:\Program Files (x86)\Bonjour\mdnsNSP.dll (Apple Inc.)
O10 - Protocol_Catalog9\Catalog_Entries\000000000011 - C:\Program Files (x86)\VMware\VMware Workstation\vsocklib.dll (VMware, Inc.)
O10 - Protocol_Catalog9\Catalog_Entries\000000000012 - C:\Program Files (x86)\VMware\VMware Workstation\vsocklib.dll (VMware, Inc.)
O16 - DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} http://java.sun.com/update/1.6.0/jinstall-1_6_0_26-windows-i586.cab (Java Plug-in 1.6.0_26)
O16 - DPF: {983A9C21-8207-4B58-BBB8-0EBC3D7C5505} https://apps.ko.com/dwa8W.cab (Domino Web Access 8 Control)
O16 - DPF: {CAFEEFAC-0016-0000-0026-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-1_6_0_26-windows-i586.cab (Java Plug-in 1.6.0_26)
O16 - DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-1_6_0_26-windows-i586.cab (Java Plug-in 1.6.0_26)
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: DhcpNameServer = [removed] [removed] [removed]
O18:64bit: - Protocol\Handler\livecall {828030A1-22C1-4009-854F-8E305202313F} - Reg Error: Key error. File not found
O18:64bit: - Protocol\Handler\ms-help {314111c7-a502-11d2-bbca-00c04f8ec294} - Reg Error: Key error. File not found
O18:64bit: - Protocol\Handler\msnim {828030A1-22C1-4009-854F-8E305202313F} - Reg Error: Key error. File not found
O18:64bit: - Protocol\Handler\wlmailhtml {03C514A3-1EFB-4856-9F99-10D7BE1653C0} - Reg Error: Key error. File not found
O18:64bit: - Protocol\Handler\wlpg {E43EF6CD-A37A-4A9B-9E6F-83F89B8E6324} - Reg Error: Key error. File not found
O20:64bit: - HKLM Winlogon: Shell - (Explorer.exe) - C:\Windows\explorer.exe (Microsoft Corporation)
O20:64bit: - HKLM Winlogon: VMApplet - (SystemPropertiesPerformance.exe) - C:\Windows\SysNative\SystemPropertiesPerformance.exe (Microsoft Corporation)
O20:64bit: - HKLM Winlogon: VMApplet - (/pagefile) -  File not found
O20 - HKLM Winlogon: Shell - (Explorer.exe) - C:\Windows\SysWow64\explorer.exe (Microsoft Corporation)
O20 - HKLM Winlogon: VMApplet - (/pagefile) -  File not found
O32 - HKLM CDRom: AutoRun - 1
O34 - HKLM BootExecute: (autocheck autochk *) -  File not found
O35:64bit: - HKLM\..comfile [open] – "%1" %*
O35:64bit: - HKLM\..exefile [open] – "%1" %*
O35 - HKLM\..comfile [open] – "%1" %*
O35 - HKLM\..exefile [open] – "%1" %*
O37:64bit: - HKLM\…com [@ = ComFile] – "%1" %*
O37:64bit: - HKLM\…exe [@ = exefile] – "%1" %*
O37 - HKLM\…com [@ = ComFile] – "%1" %*
O37 - HKLM\…exe [@ = exefile] – "%1" %*
 
 
Drivers32:64bit: msacm.l3acm - C:\Windows\System32\l3codeca.acm (Fraunhofer Institut Integrierte Schaltungen IIS)
Drivers32: msacm.dvacm - C:\Program Files (x86)\Common Files\Ulead Systems\VIO\DVACM.acm (Corel TW Corp.)
Drivers32: msacm.l3acm - C:\Windows\SysWOW64\l3codeca.acm (Fraunhofer Institut Integrierte Schaltungen IIS)
Drivers32: msacm.l3codecp - C:\Windows\SysWow64\l3codecp.acm (Fraunhofer Institut Integrierte Schaltungen IIS)
Drivers32: msacm.MPEGacm - C:\Program Files (x86)\Common Files\Ulead Systems\MPEG\MPEGACM.acm (Ulead Systems, Inc.)
Drivers32: msacm.ulmp3acm - C:\Program Files (x86)\Common Files\Ulead Systems\MPEG\ulmp3acm.acm (Ulead systems)
Drivers32: vidc.cvid - C:\Windows\SysWow64\iccvid.dll (Radius Inc.)
Drivers32: VIDC.FFDS - C:\Windows\SysWow64\ff_vfw.dll ()
Drivers32: vidc.i420 - C:\Windows\SysWow64\i420vfw.dll (www.helixcommunity.org)
Drivers32: VIDC.VMnc - C:\Windows\SysWow64\vmnc.dll (VMware, Inc.)
Drivers32: vidc.VP60 - C:\Windows\SysWOW64\vp6vfw.dll (On2.com)
Drivers32: vidc.VP61 - C:\Windows\SysWOW64\vp6vfw.dll (On2.com)
Drivers32: vidc.yv12 - C:\Windows\SysWow64\yv12vfw.dll (www.helixcommunity.org)
 
CREATERESTOREPOINT
Restore point Set: OTL Restore Point
 
========== Files/Folders - Created Within 30 Days ==========
 
[2011/06/21 15:36:52 | 000,579,072 | —- | C] (OldTimer Tools) – C:\Users\Nsnd\Desktop\OTL.exe
[2011/06/20 19:46:17 | 000,000,000 | —D | C] – C:\MGtools
[2011/06/20 19:44:41 | 000,039,984 | —- | C] (Malwarebytes Corporation) – C:\Windows\SysWow64\drivers\mbamswissarmy.sys
[2011/06/20 19:44:41 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Malwarebytes' Anti-Malware
[2011/06/20 19:44:37 | 000,000,000 | —D | C] – C:\Program Files (x86)\Malwarebytes' Anti-Malware
[2011/06/20 19:34:48 | 000,000,000 | —D | C] – C:\Users\Nsnd\AppData\Roaming\SUPERAntiSpyware.com
[2011/06/20 19:34:48 | 000,000,000 | —D | C] – C:\ProgramData\SUPERAntiSpyware.com
[2011/06/20 19:34:45 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\SUPERAntiSpyware
[2011/06/20 19:34:45 | 000,000,000 | —D | C] – C:\ProgramData\!SASCORE
[2011/06/20 19:34:42 | 000,000,000 | —D | C] – C:\Program Files\SUPERAntiSpyware
[2011/06/19 15:08:13 | 000,000,000 | —D | C] – C:\$RECYCLE.BIN
[2011/06/19 14:59:20 | 000,518,144 | —- | C] (SteelWerX) – C:\Windows\SWREG.exe
[2011/06/19 14:59:20 | 000,406,528 | —- | C] (SteelWerX) – C:\Windows\SWSC.exe
[2011/06/19 14:59:20 | 000,060,416 | —- | C] (NirSoft) – C:\Windows\NIRCMD.exe
[2011/06/19 14:59:14 | 000,000,000 | —D | C] – C:\Windows\ERDNT
[2011/06/19 14:59:08 | 000,000,000 | —D | C] – C:\Qoobox
[2011/06/19 14:58:56 | 000,000,000 | —D | C] – C:\32788R22FWJFW
[2011/06/19 14:55:36 | 004,130,419 | R— | C] (Swearware) – C:\Users\Nsnd\Desktop\ComboFix.exe
[2011/06/18 17:16:40 | 000,000,000 | —D | C] – C:\Config.Msi
[2011/06/16 15:50:01 | 000,703,488 | —- | C] (Microsoft Corporation) – C:\Windows\SysNative\msfeeds.dll
[2011/06/16 15:50:00 | 000,599,552 | —- | C] (Microsoft Corporation) – C:\Windows\SysWow64\msfeeds.dll
[2011/06/16 15:50:00 | 000,256,000 | —- | C] (Microsoft Corporation) – C:\Windows\SysNative\iepeers.dll
[2011/06/16 15:50:00 | 000,185,856 | —- | C] (Microsoft Corporation) – C:\Windows\SysWow64\iepeers.dll
[2011/06/16 15:49:59 | 000,482,816 | —- | C] (Microsoft Corporation) – C:\Windows\SysNative\html.iec
[2011/06/16 15:49:59 | 000,386,048 | —- | C] (Microsoft Corporation) – C:\Windows\SysWow64\html.iec
[2011/06/16 15:49:59 | 000,247,808 | —- | C] (Microsoft Corporation) – C:\Windows\SysNative\ieui.dll
[2011/06/16 15:49:59 | 000,176,640 | —- | C] (Microsoft Corporation) – C:\Windows\SysWow64\ieui.dll
[2011/06/16 15:49:59 | 000,097,280 | —- | C] (Microsoft Corporation) – C:\Windows\SysNative\mshtmled.dll
[2011/06/16 15:49:59 | 000,067,072 | —- | C] (Microsoft Corporation) – C:\Windows\SysWow64\mshtmled.dll
[2011/06/16 15:49:59 | 000,057,856 | —- | C] (Microsoft Corporation) – C:\Windows\SysNative\licmgr10.dll
[2011/06/16 15:49:59 | 000,044,544 | —- | C] (Microsoft Corporation) – C:\Windows\SysWow64\licmgr10.dll
[2011/06/16 15:49:59 | 000,012,800 | —- | C] (Microsoft Corporation) – C:\Windows\SysWow64\msfeedssync.exe
[2011/06/16 15:49:59 | 000,012,288 | —- | C] (Microsoft Corporation) – C:\Windows\SysNative\msfeedssync.exe
[2011/06/16 15:49:54 | 000,197,120 | —- | C] (Microsoft Corporation) – C:\Windows\SysNative\d3d10_1.dll
[2011/06/16 15:49:54 | 000,161,792 | —- | C] (Microsoft Corporation) – C:\Windows\SysWow64\d3d10_1.dll
[2011/06/16 15:49:53 | 000,861,184 | —- | C] (Microsoft Corporation) – C:\Windows\SysNative\oleaut32.dll
[2011/06/12 16:26:12 | 000,000,000 | —D | C] – C:\Program Files (x86)\Common Files\Java
[2011/06/12 16:24:13 | 000,157,472 | —- | C] (Sun Microsystems, Inc.) – C:\Windows\SysWow64\javaws.exe
[2011/06/12 16:24:13 | 000,145,184 | —- | C] (Sun Microsystems, Inc.) – C:\Windows\SysWow64\javaw.exe
[2011/06/12 16:24:13 | 000,145,184 | —- | C] (Sun Microsystems, Inc.) – C:\Windows\SysWow64\java.exe
[2011/06/03 19:09:15 | 000,000,000 | —D | C] – C:\Users\Nsnd\AppData\Local\{BB8EFA2C-C894-49FD-91E5-0BE1B2962B73}
[2011/06/02 19:53:30 | 000,000,000 | —D | C] – C:\Users\Nsnd\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Unlocker
[2011/06/02 19:36:13 | 000,000,000 | —D | C] – C:\Program Files (x86)\Microsoft
[2011/06/02 19:35:49 | 000,000,000 | —D | C] – C:\Program Files (x86)\Unlocker
[2011/06/02 19:27:09 | 000,000,000 | —D | C] – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Hotspot Shield
[2011/05/24 15:45:50 | 000,027,008 | —- | C] (Microsoft Corporation) – C:\Windows\SysNative\drivers\Diskdump.sys
[2011/05/24 08:22:14 | 000,000,000 | —D | C] – C:\Users\Nsnd\AppData\Local\{EACF0CD5-A4DF-4846-839B-809F71F15A69}
[2011/05/24 08:17:49 | 000,142,336 | —- | C] (Microsoft Corporation) – C:\Windows\SysNative\poqexec.exe
[2011/05/24 08:17:49 | 000,123,904 | —- | C] (Microsoft Corporation) – C:\Windows\SysWow64\poqexec.exe
[2010/05/13 09:44:46 | 001,101,824 | —- | C] ( ) – C:\Windows\SysWow64\lxdnserv.dll
[2010/05/13 09:44:46 | 000,851,968 | —- | C] ( ) – C:\Windows\SysWow64\lxdncomc.dll
[2010/05/13 09:44:46 | 000,843,776 | —- | C] ( ) – C:\Windows\SysWow64\lxdnusb1.dll
[2010/05/13 09:44:46 | 000,663,552 | —- | C] ( ) – C:\Windows\SysWow64\lxdnhbn3.dll
[2010/05/13 09:44:46 | 000,647,168 | —- | C] ( ) – C:\Windows\SysWow64\lxdnpmui.dll
[2010/05/13 09:44:46 | 000,589,824 | —- | C] ( ) – C:\Windows\SysWow64\lxdncoms.exe
[2010/05/13 09:44:46 | 000,569,344 | —- | C] ( ) – C:\Windows\SysWow64\lxdnlmpm.dll
[2010/05/13 09:44:46 | 000,376,832 | —- | C] ( ) – C:\Windows\SysWow64\lxdncomm.dll
[2010/05/13 09:44:46 | 000,364,544 | —- | C] ( ) – C:\Windows\SysWow64\lxdninpa.dll
[2010/05/13 09:44:46 | 000,360,448 | —- | C] ( ) – C:\Windows\SysWow64\lxdncfg.exe
[2010/05/13 09:44:46 | 000,339,968 | —- | C] ( ) – C:\Windows\SysWow64\lxdniesc.dll
[2010/05/13 09:44:46 | 000,315,392 | —- | C] ( ) – C:\Windows\SysWow64\lxdnih.exe
[2010/05/13 09:44:46 | 000,053,248 | —- | C] ( ) – C:\Windows\SysWow64\lxdnprox.dll
[2 C:\*.tmp files -> C:\*.tmp -> ]
[1 C:\Windows\*.tmp files -> C:\Windows\*.tmp -> ]
 
========== Files - Modified Within 30 Days ==========
 
[2011/06/21 15:37:04 | 000,579,072 | —- | M] (OldTimer Tools) – C:\Users\Nsnd\Desktop\OTL.exe
[2011/06/21 15:32:04 | 000,023,248 | -H– | M] () – C:\Windows\SysNative\7B296FB0-376B-497e-B012-9C450E1B7327-5P-1.C7483456-A289-439d-8115-601632D005A0
[2011/06/21 15:32:04 | 000,023,248 | -H– | M] () – C:\Windows\SysNative\7B296FB0-376B-497e-B012-9C450E1B7327-5P-0.C7483456-A289-439d-8115-601632D005A0
[2011/06/21 15:14:37 | 000,000,890 | —- | M] () – C:\Windows\tasks\GoogleUpdateTaskMachineCore.job
[2011/06/21 15:13:20 | 000,067,584 | –S- | M] () – C:\Windows\bootstat.dat
[2011/06/21 15:13:12 | 529,694,719 | -HS- | M] () – C:\hiberfil.sys
[2011/06/21 05:06:00 | 000,000,894 | —- | M] () – C:\Windows\tasks\GoogleUpdateTaskMachineUA.job
[2011/06/20 20:27:03 | 000,266,209 | —- | M] () – C:\MGlogs.zip
[2011/06/20 19:44:41 | 000,001,069 | —- | M] () – C:\Users\Public\Desktop\Malwarebytes' Anti-Malware.lnk
[2011/06/20 19:34:45 | 000,001,808 | —- | M] () – C:\Users\Public\Desktop\SUPERAntiSpyware Free Edition.lnk
[2011/06/19 15:08:11 | 000,000,027 | —- | M] () – C:\Windows\SysNative\drivers\etc\hosts
[2011/06/19 14:55:55 | 004,130,419 | R— | M] (Swearware) – C:\Users\Nsnd\Desktop\ComboFix.exe
[2011/06/19 09:01:05 | 597,032,710 | —- | M] () – C:\Windows\MEMORY.DMP
[2011/06/18 23:08:13 | 000,472,808 | —- | M] (Sun Microsystems, Inc.) – C:\Windows\SysWow64\deployJava1.dll
[2011/06/18 23:08:13 | 000,157,472 | —- | M] (Sun Microsystems, Inc.) – C:\Windows\SysWow64\javaws.exe
[2011/06/18 23:08:13 | 000,145,184 | —- | M] (Sun Microsystems, Inc.) – C:\Windows\SysWow64\javaw.exe
[2011/06/18 23:08:13 | 000,145,184 | —- | M] (Sun Microsystems, Inc.) – C:\Windows\SysWow64\java.exe
[2011/06/18 18:25:22 | 000,001,979 | —- | M] () – C:\Users\Public\Desktop\Adobe Reader X.lnk
[2011/06/18 17:47:11 | 005,033,928 | —- | M] () – C:\Windows\SysNative\FNTCACHE.DAT
[2011/06/15 04:49:00 | 000,002,340 | —- | M] () – C:\Users\Public\Desktop\Google Chrome.lnk
[2011/06/14 18:22:42 | 000,743,938 | —- | M] () – C:\Windows\SysNative\PerfStringBackup.INI
[2011/06/14 18:22:42 | 000,635,630 | —- | M] () – C:\Windows\SysNative\perfh009.dat
[2011/06/14 18:22:42 | 000,111,758 | —- | M] () – C:\Windows\SysNative\perfc009.dat
[2011/06/02 19:35:52 | 000,001,176 | —- | M] () – C:\Users\Nsnd\Application Data\Microsoft\Internet Explorer\Quick Launch\QuickStores.lnk
[2011/06/02 05:02:29 | 000,404,640 | —- | M] (Adobe Systems Incorporated) – C:\Windows\SysWow64\FlashPlayerCPLApp.cpl
[2011/05/29 09:11:30 | 000,039,984 | —- | M] (Malwarebytes Corporation) – C:\Windows\SysWow64\drivers\mbamswissarmy.sys
[2011/05/29 09:11:20 | 000,025,912 | —- | M] (Malwarebytes Corporation) – C:\Windows\SysNative\drivers\mbam.sys
[2011/05/24 17:11:44 | 000,000,126 | —- | M] () – C:\Users\Nsnd\JavaConnect.ini
[2 C:\*.tmp files -> C:\*.tmp -> ]
[1 C:\Windows\*.tmp files -> C:\Windows\*.tmp -> ]
 
========== Files Created - No Company Name ==========
 
[2011/06/20 19:46:20 | 000,266,209 | —- | C] () – C:\MGlogs.zip
[2011/06/20 19:44:41 | 000,001,069 | —- | C] () – C:\Users\Public\Desktop\Malwarebytes' Anti-Malware.lnk
[2011/06/20 19:34:45 | 000,001,808 | —- | C] () – C:\Users\Public\Desktop\SUPERAntiSpyware Free Edition.lnk
[2011/06/19 14:59:20 | 000,256,512 | —- | C] () – C:\Windows\PEV.exe
[2011/06/19 14:59:20 | 000,208,896 | —- | C] () – C:\Windows\MBR.exe
[2011/06/19 14:59:20 | 000,098,816 | —- | C] () – C:\Windows\sed.exe
[2011/06/19 14:59:20 | 000,080,412 | —- | C] () – C:\Windows\grep.exe
[2011/06/19 14:59:20 | 000,068,096 | —- | C] () – C:\Windows\zip.exe
[2011/06/18 18:25:22 | 000,002,441 | —- | C] () – C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Adobe Reader X.lnk
[2011/06/18 18:25:22 | 000,001,979 | —- | C] () – C:\Users\Public\Desktop\Adobe Reader X.lnk
[2011/06/02 19:35:52 | 000,001,176 | —- | C] () – C:\Users\Nsnd\Application Data\Microsoft\Internet Explorer\Quick Launch\QuickStores.lnk
[2011/05/24 14:05:48 | 000,000,126 | —- | C] () – C:\Users\Nsnd\JavaConnect.ini
[2011/01/01 18:46:08 | 000,000,126 | —- | C] () – C:\Windows\QUICKEN.INI
[2010/10/16 10:23:20 | 000,006,656 | —- | C] () – C:\Users\Nsnd\AppData\Local\DCBC2A71-70D8-4DAN-EHR8-E0D61DEA3FDF.ini
[2010/09/26 19:52:59 | 000,000,092 | —- | C] () – C:\Users\Nsnd\AppData\Local\fusioncache.dat
[2010/09/26 19:49:13 | 000,757,008 | —- | C] () – C:\Windows\SysWow64\PerfStringBackup.INI
[2010/08/07 19:31:43 | 000,108,032 | —- | C] () – C:\Windows\SysWow64\ff_vfw.dll
[2010/05/14 14:48:06 | 000,000,262 | —- | C] () – C:\Windows\{EEB3F6BB-318D-4CE5-989F-8191FCBFB578}_WiseFW.ini
[2010/05/13 09:44:46 | 000,348,160 | —- | C] () – C:\Windows\SysWow64\LXDNinst.dll
[2010/05/13 09:44:46 | 000,335,872 | —- | C] () – C:\Windows\SysWow64\lxdncomx.dll
[2010/04/29 19:53:57 | 000,000,848 | -HS- | C] () – C:\ProgramData\KGyGaAvL.sys
[2010/04/29 19:02:04 | 000,023,113 | —- | C] () – C:\Windows\hpqins15.dat
[2010/04/18 02:48:30 | 000,209,040 | —- | C] () – C:\Windows\SysWow64\IVIresizeW7.dll
[2010/04/18 02:48:30 | 000,204,944 | —- | C] () – C:\Windows\SysWow64\IVIresizeA6.dll
[2010/04/18 02:48:30 | 000,196,752 | —- | C] () – C:\Windows\SysWow64\IVIresizeP6.dll
[2010/04/18 02:48:30 | 000,196,752 | —- | C] () – C:\Windows\SysWow64\IVIresizeM6.dll
[2010/04/18 02:48:30 | 000,192,656 | —- | C] () – C:\Windows\SysWow64\IVIresizePX.dll
[2010/04/18 02:48:30 | 000,024,720 | —- | C] () – C:\Windows\SysWow64\IVIresize.dll
[2010/04/18 02:20:16 | 000,000,283 | —- | C] () – C:\Windows\SysWow64\RStoneLog2.ini
[2010/04/18 02:20:16 | 000,000,224 | —- | C] () – C:\Windows\SysWow64\RStoneLog.ini
[2009/07/23 19:49:04 | 000,782,336 | —- | C] () – C:\Windows\SysWow64\lxdndrs.dll
[2009/07/13 22:38:36 | 000,067,584 | –S- | C] () – C:\Windows\bootstat.dat
[2009/07/13 19:35:51 | 000,000,741 | —- | C] () – C:\Windows\SysWow64\NOISE.DAT
[2009/07/13 19:34:42 | 000,215,943 | —- | C] () – C:\Windows\SysWow64\dssec.dat
[2009/07/13 17:10:29 | 000,043,131 | —- | C] () – C:\Windows\mib.bin
[2009/07/13 16:42:10 | 000,064,000 | —- | C] () – C:\Windows\SysWow64\BWContextHandler.dll
[2009/07/13 14:59:36 | 001,498,564 | —- | C] () – C:\Windows\SysWow64\igkrng400.bin
[2009/07/13 14:03:59 | 000,364,544 | —- | C] () – C:\Windows\SysWow64\msjetoledb40.dll
[2009/06/10 14:26:10 | 000,673,088 | —- | C] () – C:\Windows\SysWow64\mlang.dat
[2009/05/14 13:46:40 | 000,081,920 | —- | C] () – C:\Windows\SysWow64\lxdncaps.dll
[2008/11/15 11:02:26 | 001,866,670 | —- | C] () – C:\Windows\SysWow64\libfftw3f-3.dll
[2008/04/05 10:53:24 | 000,140,288 | —- | C] () – C:\Windows\SysWow64\avsfilter.dll
[2007/10/02 14:51:10 | 000,069,632 | —- | C] () – C:\Windows\SysWow64\lxdncnv4.dll
[2005/09/12 20:09:34 | 000,004,608 | —- | C] () – C:\Windows\SysWow64\AvsRecursion.dll
[2004/01/29 21:44:56 | 001,627,136 | —- | C] () – C:\Windows\SysWow64\fftw3.dll
[2004/01/23 19:35:44 | 000,057,344 | —- | C] () – C:\Windows\SysWow64\avisynth_c.dll
 
========== LOP Check ==========
 
[2011/04/11 20:37:51 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\Bullzip
[2010/04/29 18:54:48 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\DigitalPersona
[2011/02/08 21:33:28 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\HandBrake
[2010/05/13 05:45:13 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\LolClient
[2010/05/08 19:37:10 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\LolClient.F24C99354F615F3BAB18AE7B93E3F9B9E8784FA6.1
[2011/06/19 14:48:18 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\mjusbsp
[2010/06/11 21:43:15 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\Mumble
[2010/05/02 15:28:00 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\OpenOffice.org
[2010/04/30 22:14:28 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\Trillian
[2011/02/08 15:10:09 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\TS3Client
[2010/04/29 19:55:15 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\Ulead Systems
[2011/06/14 18:19:42 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\uTorrent
[2010/11/27 02:26:00 | 000,000,000 | —D | M] – C:\Users\Nsnd\AppData\Roaming\Windows Live Writer
[2009/07/13 22:08:49 | 000,031,894 | —- | M] () – C:\Windows\Tasks\SCHEDLGU.TXT
 
========== Purity Check ==========


========== Custom Scans ==========
 
 
< %SYSTEMDRIVE%\*.* >
[2010/11/07 15:02:37 | 000,001,024 | —- | M] () – C:\.rnd
[2009/07/13 18:38:58 | 000,383,562 | RHS- | M] () – C:\bootmgr
[2011/06/19 15:13:15 | 000,017,997 | —- | M] () – C:\ComboFix.txt
[2007/11/07 09:00:40 | 000,017,734 | —- | M] () – C:\eula.1028.txt
[2007/11/07 09:00:40 | 000,017,734 | —- | M] () – C:\eula.1031.txt
[2007/11/07 09:00:40 | 000,010,134 | —- | M] () – C:\eula.1033.txt
[2007/11/07 09:00:40 | 000,017,734 | —- | M] () – C:\eula.1036.txt
[2007/11/07 09:00:40 | 000,017,734 | —- | M] () – C:\eula.1040.txt
[2007/11/07 09:00:40 | 000,000,118 | —- | M] () – C:\eula.1041.txt
[2007/11/07 09:00:40 | 000,017,734 | —- | M] () – C:\eula.1042.txt
[2007/11/07 09:00:40 | 000,017,734 | —- | M] () – C:\eula.2052.txt
[2007/11/07 09:00:40 | 000,017,734 | —- | M] () – C:\eula.3082.txt
[2007/11/07 09:00:40 | 000,001,110 | —- | M] () – C:\globdata.ini
[2011/06/21 15:13:12 | 529,694,719 | -HS- | M] () – C:\hiberfil.sys
[2007/11/07 09:00:40 | 000,000,843 | —- | M] () – C:\install.ini
[2007/11/07 09:03:18 | 000,076,304 | —- | M] (Microsoft Corporation) – C:\install.res.1028.dll
[2007/11/07 09:03:18 | 000,096,272 | —- | M] (Microsoft Corporation) – C:\install.res.1031.dll
[2007/11/07 09:03:18 | 000,091,152 | —- | M] (Microsoft Corporation) – C:\install.res.1033.dll
[2007/11/07 09:03:18 | 000,097,296 | —- | M] (Microsoft Corporation) – C:\install.res.1036.dll
[2007/11/07 09:03:18 | 000,095,248 | —- | M] (Microsoft Corporation) – C:\install.res.1040.dll
[2007/11/07 09:03:18 | 000,081,424 | —- | M] (Microsoft Corporation) – C:\install.res.1041.dll
[2007/11/07 09:03:18 | 000,079,888 | —- | M] (Microsoft Corporation) – C:\install.res.1042.dll
[2007/11/07 09:03:18 | 000,075,792 | —- | M] (Microsoft Corporation) – C:\install.res.2052.dll
[2007/11/07 09:03:18 | 000,096,272 | —- | M] (Microsoft Corporation) – C:\install.res.3082.dll
[2011/06/20 20:27:03 | 000,266,209 | —- | M] () – C:\MGlogs.zip
[2011/06/21 15:13:21 | 2137,915,391 | -HS- | M] () – C:\pagefile.sys
[2007/11/07 09:00:40 | 000,005,686 | —- | M] () – C:\vcredist.bmp
[2007/11/07 09:09:22 | 001,442,522 | —- | M] () – C:\VC_RED.cab
[2007/11/07 09:12:28 | 000,232,960 | —- | M] () – C:\VC_RED.MSI
[2 C:\*.tmp files -> C:\*.tmp -> ]
 
< %systemroot%\Fonts\*.com >
[2009/07/13 22:32:31 | 000,026,040 | —- | M] () – C:\Windows\Fonts\GlobalMonospace.CompositeFont
[2009/07/13 22:32:31 | 000,026,489 | —- | M] () – C:\Windows\Fonts\GlobalSansSerif.CompositeFont
[2009/07/13 22:32:31 | 000,029,779 | —- | M] () – C:\Windows\Fonts\GlobalSerif.CompositeFont
[2009/07/13 22:32:31 | 000,043,318 | —- | M] () – C:\Windows\Fonts\GlobalUserInterface.CompositeFont
 
< %systemroot%\Fonts\*.dll >
 
< %systemroot%\Fonts\*.ini >
[2009/06/10 13:49:50 | 000,000,065 | -H– | M] () – C:\Windows\Fonts\desktop.ini
 
< %systemroot%\Fonts\*.ini2 >
 
< %systemroot%\Fonts\*.exe >
 
< %systemroot%\system32\spool\prtprocs\w32x86\*.* >
 
< %systemroot%\REPAIR\*.bak1 >
 
< %systemroot%\REPAIR\*.ini >
 
< %systemroot%\system32\*.jpg >
 
< %systemroot%\*.jpg >
 
< %systemroot%\*.png >
 
< %systemroot%\*.scr >
[2011/01/13 01:47:35 | 000,038,848 | —- | M] (AVAST Software) – C:\Windows\avastSS.scr
[2010/11/10 02:28:46 | 000,301,936 | —- | M] (Microsoft Corporation) – C:\Windows\WLXPGSS.SCR
[1 C:\Windows\*.tmp files -> C:\Windows\*.tmp -> ]
 
< %systemroot%\*._sy >
 
< %APPDATA%\Adobe\Update\*.* >
 
< %ALLUSERSPROFILE%\Favorites\*.* >
 
< %APPDATA%\Microsoft\*.* >
 
< %PROGRAMFILES%\*.* >
[2009/07/13 21:54:24 | 000,000,174 | -HS- | M] () – C:\Program Files (x86)\desktop.ini
 
< %APPDATA%\Update\*.* >
 
< %systemroot%\*. /mp /s >
 
< %systemroot%\System32\config\*.sav >
 
< %PROGRAMFILES%\bak. /s >
 
< %systemroot%\system32\bak. /s >
 
< %ALLUSERSPROFILE%\Start Menu\*.lnk /x >
 
< %systemroot%\system32\config\systemprofile\*.dat /x >
 
< %systemroot%\*.config >
 
< %systemroot%\system32\*.db >
 
< %PROGRAMFILES%\Internet Explorer\*.dat >
 
< %APPDATA%\Microsoft\Internet Explorer\Quick Launch\*.lnk /x >
[2010/04/29 19:20:33 | 000,000,221 | -HS- | M] () – C:\Users\Nsnd\AppData\Roaming\Microsoft\Internet Explorer\Quick Launch\desktop.ini
 
< %USERPROFILE%\Desktop\*.exe >\
[2011/02/27 15:24:00 | 158,067,944 | —- | M] () – C:\Users\Nsnd\Desktop\OOo_3.3.0_Win_x86_install-wJRE_en-US.exe
[2011/06/21 15:37:04 | 000,579,072 | —- | M] (OldTimer Tools) – C:\Users\Nsnd\Desktop\OTL.exe
 
< %PROGRAMFILES%\Common Files\*.* >
 
< %systemroot%\*.src >
 
< %systemroot%\install\*.* >
 
< %systemroot%\system32\DLL\*.* >
 
< %systemroot%\system32\HelpFiles\*.* >
 
< %systemroot%\system32\rundll\*.* >
 
< %systemroot%\winn32\*.* >
 
< %systemroot%\Java\*.* >
 
< %systemroot%\system32\test\*.* >
 
< %systemroot%\system32\Rundll32\*.* >
 
< %systemroot%\AppPatch\Custom\*.* >
 
< HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU >
 
< HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install|LastSuccessTime /rs >

< End of report >

OTL Extras logfile created on: 6/21/2011 3:45:46 PM - Run 1
OTL by OldTimer - Version 3.2.24.1	 Folder = C:\Users\Nsnd\Desktop
64bit- Home Premium Edition  (Version = 6.1.7600) - Type = NTWorkstation
Internet Explorer (Version = 8.0.7600.16385)
Locale: 00000409 | Country: United States | Language: ENU | Date Format: M/d/yyyy
 
5.99 Gb Total Physical Memory | 4.35 Gb Available Physical Memory | 72.57% Memory free
11.98 Gb Paging File | 10.00 Gb Available in Paging File | 83.45% Paging File free
Paging file location(s): ?:\pagefile.sys [binary data]
 
%SystemDrive% = C: | %SystemRoot% = C:\Windows | %ProgramFiles% = C:\Program Files (x86)
Drive C: | 448.74 Gb Total Space | 153.72 Gb Free Space | 34.26% Space Free | Partition Type: NTFS
Drive D: | 16.72 Gb Total Space | 2.70 Gb Free Space | 16.17% Space Free | Partition Type: NTFS
Drive E: | 99.02 Mb Total Space | 92.44 Mb Free Space | 93.35% Space Free | Partition Type: FAT32
Drive F: | 664.99 Mb Total Space | 0.00 Mb Free Space | 0.00% Space Free | Partition Type: CDFS
 
Computer Name: NSND-PC | User Name: Nsnd | Logged in as Administrator.
Boot Mode: Normal | Scan Mode: Current user | Include 64bit Scans
Company Name Whitelist: Off | Skip Microsoft Files: Off | No Company Name Whitelist: On | File Age = 30 Days
 
========== Extra Registry (SafeList) ==========
 
 
========== File Associations ==========
 
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\]
.url[@ = InternetShortcut] – C:\Windows\SysNative\rundll32.exe (Microsoft Corporation)
 
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\]
.cpl [@ = cplfile] – C:\Windows\SysWow64\control.exe (Microsoft Corporation)
 
[HKEY_CURRENT_USER\SOFTWARE\Classes\]
.html [@ = ChromeHTML] – Reg Error: Key error. File not found
 
========== Shell Spawning ==========
 
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\\shell\[command]\command]
batfile [open] – "%1" %* File not found
cmdfile [open] – "%1" %* File not found
comfile [open] – "%1" %* File not found
exefile [open] – "%1" %* File not found
helpfile [open] – Reg Error: Key error.
htmlfile [print] – rundll32.exe %SystemRoot%\system32\mshtml.dll,PrintHTML "%1" (Microsoft Corporation)
inffile [install] – %SystemRoot%\System32\rundll32.exe setupapi,InstallHinfSection DefaultInstall 132 %1 (Microsoft Corporation)
InternetShortcut [open] – "C:\Windows\System32\rundll32.exe" "C:\Windows\System32\ieframe.dll",OpenURL %l (Microsoft Corporation)
InternetShortcut [print] – "C:\Windows\System32\rundll32.exe" "C:\Windows\System32\mshtml.dll",PrintHTML "%1" (Microsoft Corporation)
piffile [open] – "%1" %* File not found
regfile [merge] – Reg Error: Key error.
scrfile [config] – "%1" File not found
scrfile [install] – rundll32.exe desk.cpl,InstallScreenSaver %l File not found
scrfile [open] – "%1" /S File not found
txtfile [edit] – Reg Error: Key error.
Unknown [openas] – %SystemRoot%\system32\rundll32.exe %SystemRoot%\system32\shell32.dll,OpenAs_RunDLL %1 File not found
Directory [Bridge] – C:\Program Files (x86)\Adobe\Adobe Bridge CS5\Bridge.exe "%L" (Adobe Systems, Inc.)
Directory [Browse with Corel Paint Shop Pro Photo X2] – "C:\Program Files (x86)\Corel\Corel Paint Shop Pro Photo X2\Corel Paint Shop Pro Photo.exe" "%L" (Corel, Inc.)
Directory [cmd] – cmd.exe /s /k pushd "%V" (Microsoft Corporation)
Directory [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Directory [Winamp.Bookmark] – "C:\Program Files (x86)\Winamp\winamp.exe" /BOOKMARK "%1" (Nullsoft, Inc.)
Directory [Winamp.Enqueue] – "C:\Program Files (x86)\Winamp\winamp.exe" /ADD "%1" (Nullsoft, Inc.)
Directory [Winamp.Play] – "C:\Program Files (x86)\Winamp\winamp.exe" "%1" (Nullsoft, Inc.)
Folder [open] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Folder [explore] – Reg Error: Value error.
Drive [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
 
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\\shell\[command]\command]
batfile [open] – "%1" %*
cmdfile [open] – "%1" %*
comfile [open] – "%1" %*
cplfile [cplopen] – %SystemRoot%\System32\control.exe "%1",%* (Microsoft Corporation)
exefile [open] – "%1" %*
helpfile [open] – Reg Error: Key error.
piffile [open] – "%1" %*
regfile [merge] – Reg Error: Key error.
scrfile [config] – "%1"
scrfile [install] – rundll32.exe desk.cpl,InstallScreenSaver %l
scrfile [open] – "%1" /S
txtfile [edit] – Reg Error: Key error.
Unknown [openas] – %SystemRoot%\system32\rundll32.exe %SystemRoot%\system32\shell32.dll,OpenAs_RunDLL %1
Directory [Bridge] – C:\Program Files (x86)\Adobe\Adobe Bridge CS5\Bridge.exe "%L" (Adobe Systems, Inc.)
Directory [Browse with Corel Paint Shop Pro Photo X2] – "C:\Program Files (x86)\Corel\Corel Paint Shop Pro Photo X2\Corel Paint Shop Pro Photo.exe" "%L" (Corel, Inc.)
Directory [cmd] – cmd.exe /s /k pushd "%V" (Microsoft Corporation)
Directory [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Directory [Winamp.Bookmark] – "C:\Program Files (x86)\Winamp\winamp.exe" /BOOKMARK "%1" (Nullsoft, Inc.)
Directory [Winamp.Enqueue] – "C:\Program Files (x86)\Winamp\winamp.exe" /ADD "%1" (Nullsoft, Inc.)
Directory [Winamp.Play] – "C:\Program Files (x86)\Winamp\winamp.exe" "%1" (Nullsoft, Inc.)
Folder [open] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
Folder [explore] – Reg Error: Value error.
Drive [find] – %SystemRoot%\Explorer.exe (Microsoft Corporation)
 
========== Security Center Settings ==========
 
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center]
"cval" = 1
"FirewallDisableNotify" = 0
"AntiVirusDisableNotify" = 0
"UpdatesDisableNotify" = 0
 
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Monitoring]
 
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Svc]
"VistaSp1" = 28 4D B2 76 41 04 CA 01  [binary data]
"AntiVirusOverride" = 0
"AntiSpywareOverride" = 0
"FirewallOverride" = 0
 
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Svc\Vol]
 
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center]
"FirewallDisableNotify" = 0
"AntiVirusDisableNotify" = 0
"UpdatesDisableNotify" = 0
 
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center\Svc]
 
========== System Restore Settings ==========
 
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SystemRestore]
"DisableSR" = 0
 
========== Firewall Settings ==========
 
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\WindowsFirewall]
 
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\WindowsFirewall\DomainProfile]
 
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\WindowsFirewall\StandardProfile]
 
[HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\WindowsFirewall]
 
[HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\WindowsFirewall\DomainProfile]
 
[HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\WindowsFirewall\StandardProfile]
 
[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\DomainProfile]
"DisableNotifications" = 0
"EnableFirewall" = 1
 
[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\StandardProfile]
"DisableNotifications" = 0
"EnableFirewall" = 0
 
[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\StandardProfile\GloballyOpenPorts\List]
 
[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\PublicProfile]
"DisableNotifications" = 0
"EnableFirewall" = 1
 
========== Authorized Applications List ==========
 
[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\DomainProfile\AuthorizedApplications\List]
 
[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\StandardProfile\AuthorizedApplications\List]
 
 
========== HKEY_LOCAL_MACHINE Uninstall List ==========
 
64bit: [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall]
"{0E543634-7E25-4B8F-8D5B-97880E5E5088}" = Bonjour
"{18155797-EF2E-4699-9A16-FE787C4C10DB}" = iTunes
"{1B8ABA62-74F0-47ED-B18C-A43128E591B8}" = Windows Live ID Sign-in Assistant
"{1E9FC118-651D-4934-97BE-E53CAE5C7D45}" = Microsoft_VC80_MFCLOC_x86_x64
"{350AA351-21FA-3270-8B7A-835434E766AD}" = Microsoft Visual C++ 2008 Redistributable - x64 9.0.21022
"{4569AD91-47F4-4D9E-8FC9-717EC32D7AE1}" = Microsoft_VC80_CRT_x86_x64
"{4B6C7001-C7D6-3710-913E-5BC23FCE91E6}" = Microsoft Visual C++ 2008 Redistributable - x64 9.0.30729.4148
"{5EB6F3CB-46F4-451F-A028-7F6D8D35D7D0}" = Windows Live Language Selector
"{5FCE6D76-F5DC-37AB-B2B8-22AB8CEDB1D4}" = Microsoft Visual C++ 2008 Redistributable - x64 9.0.30729.6161
"{62A20ECA-920E-4052-BF77-88C78DD20FAA}" = Validity Sensors DDK
"{8338783A-0968-3B85-AFC7-BAAE0A63DC50}" = Microsoft Visual C++ 2008 Redistributable - KB2467174 - x64 9.0.30729.5570
"{8557397C-A42D-486F-97B3-A2CBC2372593}" = Microsoft_VC90_ATL_x86_x64
"{85A42FF0-F0D0-44A3-B226-C124D6E8B1D5}" = HP 3D DriveGuard
"{8F473675-D702-45F9-8EBC-342B40C17BF5}" = Apple Mobile Device Support
"{90140000-002A-0000-1000-0000000FF1CE}" = Microsoft Office Office 64-bit Components 2010
"{90140000-002A-0409-1000-0000000FF1CE}" = Microsoft Office Shared 64-bit MUI (English) 2010
"{90140000-0116-0409-1000-0000000FF1CE}" = Microsoft Office Shared 64-bit Setup Metadata MUI (English) 2010
"{9068B2BE-D93A-4C0A-861C-5E35E2C0E09E}" = Intel® Matrix Storage Manager
"{925D058B-564A-443A-B4B2-7E90C6432E55}" = Microsoft_VC80_ATL_x86_x64
"{92A3CA0D-55CD-4C5D-BA95-5C2600C20F26}" = Microsoft_VC90_CRT_x86_x64
"{95120000-00B9-0409-1000-0000000FF1CE}" = Microsoft Application Error Reporting
"{A472B9E4-0AFF-4F7B-B25D-F64F8E928AAB}" = Microsoft_VC90_MFC_x86_x64
"{C8C1BAD5-54E6-4146-AD07-3A8AD36569C3}" = Microsoft_VC80_MFC_x86_x64
"{CDDCBBF1-2703-46BC-938B-BCC81A1EEAAA}" = SUPERAntiSpyware
"{D0584F36-2BDB-43DF-9168-AD0EE9AD95F6}" = HP Tone Control
"{DA54F80E-261C-41A2-A855-549A144F2F59}" = Windows Live MIME IFilter
"{EEB3F6BB-318D-4CE5-989F-8191FCBFB578}" = Ventrilo Client for Windows x64
"{F5B09CFD-F0B2-36AF-8DF4-1DF6B63FC7B4}" = Microsoft .NET Framework 4 Client Profile
"{F74D69E5-ECFD-45D1-A87A-341208ADD7CC}" = DigitalPersona Personal 4.11
"Bullzip PDF Printer_is1" = Bullzip PDF Printer 4.0.0.463
"FFE7D41DF3C645075BB149E21988B63996C34187" = ENE CIR Receiver Driver
"HP Smart Web Printing" = HP Smart Web Printing 4.60
"Microsoft .NET Framework 4 Client Profile" = Microsoft .NET Framework 4 Client Profile
"NVIDIA Drivers" = NVIDIA Drivers
"SynTPDeinstKey" = Synaptics Pointing Device Driver
"TeamSpeak 3 Client" = TeamSpeak 3 Client
 
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall]
"{003BFBBD-6C67-419E-A24D-0DCAFC3A5249}" = tools-freebsd
"{01FB4998-33C4-4431-85ED-079E3EEFE75D}" = HP MediaSmart Webcam
"{033E378E-6AD3-4AD5-BDEB-CBD69B31046C}" = Microsoft_VC90_ATL_x86
"{048298C9-A4D3-490B-9FF9-AB023A9238F3}" = Steam
"{0665989D-2BD9-428B-B433-EF648427C8B0}" = HP User Guides 0143
"{07FA4960-B038-49EB-891B-9F95930AA544}" = HP Customer Experience Enhancements
"{08D2E121-7F6A-43EB-97FD-629B44903403}" = Microsoft_VC90_CRT_x86
"{0B0F231F-CE6A-483D-AA23-77B364F75917}" = Windows Live Installer
"{0D2DBE8A-43D0-7830-7AE7-CA6C99A832E7}" = Adobe Community Help
"{0F3647F8-E51D-4FCC-8862-9A8D0C5ACF25}" = Microsoft_VC80_ATL_x86
"{1288DF14-8024-430B-BF5D-656AC952818D}" = Kruptos 2 Professional
"{15FEDA5F-141C-4127-8D7E-B962D1742728}" = Adobe Photoshop CS5
"{197597A7-AD33-4898-9D8E-73066818B464}" = tools-netware
"{19BA08F7-C728-469C-8A35-BFBD3633BE08}" = Windows Live Movie Maker
"{19BFDA5D-1FE2-4F25-97F9-1A79DD04EE20}" = Microsoft XNA Framework Redistributable 3.1
"{1F1C2DFC-2D24-3E06-BCB8-725134ADF989}" = Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.4148
"{1F6AB0E7-8CDD-4B93-8A23-AA9EB2FEFCE4}" = Junk Mail filter update
"{1FBF6C24-C1FD-4101-A42B-0C564F9E8E79}" = CyberLink DVD Suite
"{200FEC62-3C34-4D60-9CE8-EC372E01C08F}" = Windows Live SOXE Definitions
"{26604C7E-A313-4D12-867F-7C6E7820BE4C}" = JMicron Flash Media Controller Driver
"{26A24AE4-039D-4CA4-87B4-2F83216026FF}" = Java(TM) 6 Update 26
"{287ECFA4-719A-2143-A09B-D6A12DE54E40}" = Acrobat.com
"{3023EBDA-BF1B-4831-B347-E5018555F26E}" = Movie Theme Pack for HP MediaSmart Video
"{3336F667-9049-4D46-98B6-4C743EEBC5B1}" = Windows Live Photo Gallery
"{34F4D9A4-42C2-4348-BEF4-E553C84549E7}" = Windows Live Photo Gallery
"{3764E0E0-6AAE-11DE-6784-0C73653918BE}" = Invision
"{3877C901-7B90-4727-A639-B6ED2DD59D43}" = ESU for Microsoft Windows 7
"{40BF1E83-20EB-11D8-97C5-0009C5020658}" = Power2Go
"{44B2A0AB-412E-4F8C-B058-D1E8AECCDFF5}" = Recovery Manager
"{4A03706F-666A-4037-7777-5F2748764D10}" = Java Auto Updater
"{4CBABDFD-49F8-47FD-BE7D-ECDE7270525A}" = Windows Live PIMT Platform
"{54CC7901-804D-4155-B353-21F0CC9112AB}" = HP Wireless Assistant
"{57752979-A1C9-4C02-856B-FBB27AC4E02C}" = QuickTime
"{635FED5B-2C6D-49BE-87E6-7A6FCD22BC5A}" = Microsoft_VC90_MFC_x86
"{64E72FB1-2343-4977-B4A8-262CD53D0BD3}" = Corel Paint Shop Pro Photo X2
"{682B3E4F-696A-42DE-A41C-4C07EA1678B4}" = Windows Live SOXE
"{6A05FEDF-662E-46BF-8A25-010E3F1C9C69}" = Windows Live UX Platform Language Pack
"{710f4c1c-cc18-4c49-8cbf-51240c89a1a2}" = Microsoft Visual C++ 2005 Redistributable
"{770657D0-A123-3C07-8E44-1C83EC895118}" = Microsoft Visual C++ 2005 ATL Update kb973923 - x86 8.0.50727.4053
"{80956555-A512-4190-9CAD-B000C36D6B6B}" = Windows Live Messenger
"{84EBDF39-4B33-49D7-A0BD-EB6E2C4E81C1}" = Windows Live Sync
"{853A4763-6643-4604-8D64-28BDD8925F4C}" = Apple Application Support
"{86CE85E6-DBAC-3FFD-B977-E4B79F83C909}" = Microsoft Visual C++ 2008 Redistributable - KB2467174 - x86 9.0.30729.5570
"{8833FFB6-5B0C-4764-81AA-06DFEED9A476}" = Realtek Ethernet Controller Driver For Windows Vista and Later
"{89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}" = Microsoft Silverlight
"{8DD46C6A-0056-4FEC-B70A-28BB16A1F11F}" = MSVCRT
"{8FF6F5CA-4E30-4E3B-B951-204CAAA2716A}" = SmartWebPrinting
"{90120000-0020-0409-0000-0000000FF1CE}" = Compatibility Pack for the 2007 Office system
"{90140000-0015-0409-0000-0000000FF1CE}" = Microsoft Office Access MUI (English) 2010
"{90140000-0016-0409-0000-0000000FF1CE}" = Microsoft Office Excel MUI (English) 2010
"{90140000-0018-0409-0000-0000000FF1CE}" = Microsoft Office PowerPoint MUI (English) 2010
"{90140000-0019-0409-0000-0000000FF1CE}" = Microsoft Office Publisher MUI (English) 2010
"{90140000-001A-0409-0000-0000000FF1CE}" = Microsoft Office Outlook MUI (English) 2010
"{90140000-001B-0409-0000-0000000FF1CE}" = Microsoft Office Word MUI (English) 2010
"{90140000-001F-0409-0000-0000000FF1CE}" = Microsoft Office Proof (English) 2010
"{90140000-001F-040C-0000-0000000FF1CE}" = Microsoft Office Proof (French) 2010
"{90140000-001F-0C0A-0000-0000000FF1CE}" = Microsoft Office Proof (Spanish) 2010
"{90140000-002C-0409-0000-0000000FF1CE}" = Microsoft Office Proofing (English) 2010
"{90140000-0044-0409-0000-0000000FF1CE}" = Microsoft Office InfoPath MUI (English) 2010
"{90140000-006E-0409-0000-0000000FF1CE}" = Microsoft Office Shared MUI (English) 2010
"{90140000-00A1-0409-0000-0000000FF1CE}" = Microsoft Office OneNote MUI (English) 2010
"{90140000-00BA-0409-0000-0000000FF1CE}" = Microsoft Office Groove MUI (English) 2010
"{90140000-0115-0409-0000-0000000FF1CE}" = Microsoft Office Shared Setup Metadata MUI (English) 2010
"{90140000-0117-0409-0000-0000000FF1CE}" = Microsoft Office Access Setup Metadata MUI (English) 2010
"{91140000-0011-0000-0000-0000000FF1CE}" = Microsoft Office Professional Plus 2010
"{92606477-9366-4D3B-8AE3-6BE4B29727AB}" = League of Legends
"{92D58719-BBC1-4CC3-A08B-56C9E884CC2C}" = Microsoft_VC80_CRT_x86
"{92EA4134-10D1-418A-91E1-5A0453131A38}" = Windows Live Movie Maker
"{95120000-00AF-0409-0000-0000000FF1CE}" = Microsoft Office PowerPoint Viewer 2007 (English)
"{95C5F81D-0779-4932-BE83-32AAF814F4B9}" = League of Legends
"{980A182F-E0A2-4A40-94C1-AE0C1235902E}" = Pando Media Booster
"{9A25302D-30C0-39D9-BD6F-21E6EC160475}" = Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.17
"{9BE518E6-ECC6-35A9-88E4-87755C07200F}" = Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.6161
"{9D56775A-93F3-44A3-8092-840E3826DE30}" = Windows Live Mail
"{A2BCA9F1-566C-4805-97D1-7FDC93386723}" = Adobe AIR
"{A3FF5CB2-FB35-4658-8751-9EDE1D65B3AA}" = VMware Workstation
"{A726AE06-AAA3-43D1-87E3-70F510314F04}" = Windows Live Writer
"{A78FE97A-C0C8-49CE-89D0-EDD524A17392}" = PDF Settings CS5
"{A92DAB39-4E2C-4304-9AB6-BC44E68B55E2}" = Google Update Helper
"{A9BDCA6B-3653-467B-AC83-94367DA3BFE3}" = Windows Live Photo Common
"{AAAFC670-569B-4A2F-82B4-42945E0DE3EF}" = Windows Live Writer
"{AAF454FC-82CA-4F29-AB31-6A109485E76E}" = Windows Live Writer
"{AB1C87CB-1807-4CF0-B4C2-CEE14C18CDB4}" = tools-solaris
"{AC76BA86-7AD7-1033-7B44-AA1000000001}" = Adobe Reader X (10.1.0)
"{AE0F62A7-A1A2-407F-9F4C-48939BD9AD8D}" = tools-winPre2k
"{B0069CFA-5BB9-4C03-B1C6-89CE290E5AFE}" = HP Update
"{C05D8CDB-417D-4335-A38C-A0659EDFD6B8}" = The Sims™ 3
"{C41300B9-185D-475E-BFEC-39EF732F19B1}" = Apple Software Update
"{C59C179C-668D-49A9-B6EA-0121CCFC1243}" = LabelPrint
"{C66824E4-CBB3-4851-BB3F-E8CFD6350923}" = Windows Live Mail
"{CB099890-1D5F-11D5-9EA9-0050BAE317E1}" = PowerDirector
"{CB2F7EDD-9D1F-43C1-90FC-4F52EAE172A1}" = Microsoft .NET Framework 1.1
"{CCF6F57B-F6B4-4508-BF45-63AAC9DE416A}" = Quicken 2010
"{CDACF7D5-F9FE-4315-BA3E-E1DA75CA4C7A}" = XSplit
"{CE95A79E-E4FC-4FFF-8A75-29F04B942FF2}" = Windows Live UX Platform
"{D0B44725-3666-492D-BEF6-587A14BD9BD9}" = MSVCRT_amd64
"{D102611A-6466-4101-A51D-51069303AC65}" = tools-linux
"{D1A19B02-817E-4296-A45B-07853FD74D57}" = Microsoft_VC80_MFC_x86
"{D436F577-1695-4D2F-8B44-AC76C99E0002}" = Windows Live Photo Common
"{D45240D3-B6B3-4FF9-B243-54ECE3E10066}" = Windows Live Communications Platform
"{D8DFA46A-39F7-4368-810D-18AFCFDDAEAF}" = Adobe Shockwave Player
"{D92BBB52-82FF-42ED-8A3C-4E062F944AB7}" = Microsoft_VC80_MFCLOC_x86
"{DCCAD079-F92C-44DA-B258-624FC6517A5A}" = HP MediaSmart DVD
"{DDC8BDEE-DCAC-404D-8257-3E8D4B782467}" = Windows Live Writer Resources
"{DE3A9DC5-9A5D-6485-9662-347162C7E4CA}" = Adobe Media Player
"{E09C4DB7-630C-4F06-A631-8EA7239923AF}" = D3DX10
"{E38C00D0-A68B-4318-A8A6-F7D4B5B1DF0E}" = Windows Media Encoder 9 Series
"{E3A5A8AB-58F6-45FF-AFCB-C9AE18C05001}" = IDT Audio
"{E3E71D07-CD27-46CB-8448-16D4FB29AA13}" = Microsoft WSE 3.0 Runtime
"{E503B4BF-F7BB-3D5F-8BC8-F694B1CFF942}" = Microsoft Visual C++ 2008 Redistributable - x86 9.0.21022.218
"{EB4DF488-AAEF-406F-A341-CB2AAA315B90}" = Windows Live Messenger
"{F0B430D1-B6AA-473D-9B06-AA3DD01FD0B8}" = Microsoft SQL Server 2005 Compact Edition [ENU]
"{F0FDF9C9-1DDC-401F-B638-36F1CAE8A875}" = VideoStudio
"{FE044230-9CA5-43F7-9B58-5AC5A28A1F33}" = Windows Live Essentials
"{FF66E9F6-83E7-3A3E-AF14-8DE9A809A6A4}" = Microsoft Visual C++ 2008 Redistributable - x86 9.0.21022
"{FFD9383C-01D5-4897-A954-43AF599AED30}" = tools-windows
"Adobe AIR" = Adobe AIR
"Adobe Flash Player ActiveX" = Adobe Flash Player 10 ActiveX
"Adobe Flash Player Plugin" = Adobe Flash Player 10 Plugin
"avast5" = avast! Free Antivirus
"chc.4875E02D9FB21EE389F73B8D1702B320485DF8CE.1" = Adobe Community Help
"com.adobe.amp.4875E02D9FB21EE389F73B8D1702B320485DF8CE.1" = Adobe Media Player
"ffdshow_is1" = ffdshow v1.1.3611 [2010-10-06]
"Google Chrome" = Google Chrome
"GoZone iSync" = GoZone iSync
"GPL Ghostscript Lite_is1" = GPL Ghostscript Lite 8.70
"HandBrake" = HandBrake 0.9.5
"InstallShield_{01FB4998-33C4-4431-85ED-079E3EEFE75D}" = HP MediaSmart Webcam
"InstallShield_{1FBF6C24-C1FD-4101-A42B-0C564F9E8E79}" = CyberLink DVD Suite
"InstallShield_{3023EBDA-BF1B-4831-B347-E5018555F26E}" = Movie Theme Pack for HP MediaSmart Video
"InstallShield_{40BF1E83-20EB-11D8-97C5-0009C5020658}" = Power2Go
"InstallShield_{C59C179C-668D-49A9-B6EA-0121CCFC1243}" = LabelPrint
"InstallShield_{CB099890-1D5F-11D5-9EA9-0050BAE317E1}" = PowerDirector
"InstallShield_{DCCAD079-F92C-44DA-B258-624FC6517A5A}" = HP MediaSmart DVD
"InstallShield_{F0FDF9C9-1DDC-401F-B638-36F1CAE8A875}" = Corel VideoStudio 12
"Malwarebytes' Anti-Malware_is1" = Malwarebytes' Anti-Malware version 1.51.0.1200
"Microsoft .NET Framework 1.1  (1033)" = Microsoft .NET Framework 1.1
"mIRC" = mIRC
"Office14.PROPLUSR" = Microsoft Office Professional Plus 2010
"PdaNet_is1" = PdaNet for Android 2.45
"PowerISO" = PowerISO
"ShiftWindow_is1" = ShiftWindow 1.02
"Steam App 440" = Team Fortress 2
"UltraISO_is1" = UltraISO Premium V9.35
"Unlocker" = Unlocker 1.9.1
"VMware_Workstation" = VMware Workstation
"Winamp" = Winamp
"Windows Media Encoder 9" = Windows Media Encoder 9 Series
"WinLiveSuite" = Windows Live Essentials
"WinRAR archiver" = WinRAR archiver
"XviD4PSP5" = XviD4PSP 5.0
 
========== HKEY_CURRENT_USER Uninstall List ==========
 
[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall]
"AikaOnline" = AikaOnline
"Winamp Detect" = Winamp Detector Plug-in
 
========== Last 10 Event Log Errors ==========
 
[ Application Events ]
Error - 5/3/2011 7:56:13 AM | Computer Name = Nsnd-PC | Source = Bonjour Service | ID = 100
Description = Task Scheduling Error: Continuously busy for more than a second
 
Error - 5/3/2011 7:56:13 AM | Computer Name = Nsnd-PC | Source = Bonjour Service | ID = 100
Description = Task Scheduling Error: m->NextScheduledEvent 6053
 
Error - 5/3/2011 7:56:13 AM | Computer Name = Nsnd-PC | Source = Bonjour Service | ID = 100
Description = Task Scheduling Error: m->NextScheduledSPRetry 6053
 
Error - 5/5/2011 10:35:57 PM | Computer Name = Nsnd-PC | Source = SideBySide | ID = 16842815
Description = Activation context generation failed for "C:\Program Files (x86)\Common
 Files\Adobe AIR\Versions\1.0\Adobe AIR.dll".Error in manifest or policy file "C:\Program
 Files (x86)\Common Files\Adobe AIR\Versions\1.0\Adobe AIR.dll" on line 3.  The value
 "MAJOR_VERSION.MINOR_VERSION.BUILD_NUMBER_MAJOR.BUILD_NUMBER_MINOR" of attribute
 "version" in element "assemblyIdentity" is invalid.
 
Error - 5/6/2011 1:06:34 AM | Computer Name = Nsnd-PC | Source = Microsoft-Windows-CAPI2 | ID = 4107
Description = Failed extract of third-party root list from auto update cab at: 
 with error: A required certificate is not within its validity period when verifying
 against the current system clock or the timestamp in the signed file.  .
 
Error - 5/6/2011 3:32:38 AM | Computer Name = Nsnd-PC | Source = SideBySide | ID = 16842815
Description = Activation context generation failed for "C:\Program Files (x86)\Common
 Files\Adobe AIR\Versions\1.0\Adobe AIR.dll".Error in manifest or policy file "C:\Program
 Files (x86)\Common Files\Adobe AIR\Versions\1.0\Adobe AIR.dll" on line 3.  The value
 "MAJOR_VERSION.MINOR_VERSION.BUILD_NUMBER_MAJOR.BUILD_NUMBER_MINOR" of attribute
 "version" in element "assemblyIdentity" is invalid.
 
Error - 5/7/2011 3:49:34 AM | Computer Name = Nsnd-PC | Source = SideBySide | ID = 16842815
Description = Activation context generation failed for "C:\Program Files (x86)\Common
 Files\Adobe AIR\Versions\1.0\Adobe AIR.dll".Error in manifest or policy file "C:\Program
 Files (x86)\Common Files\Adobe AIR\Versions\1.0\Adobe AIR.dll" on line 3.  The value
 "MAJOR_VERSION.MINOR_VERSION.BUILD_NUMBER_MAJOR.BUILD_NUMBER_MINOR" of attribute
 "version" in element "assemblyIdentity" is invalid.
 
Error - 5/7/2011 7:29:34 PM | Computer Name = Nsnd-PC | Source = Microsoft-Windows-CAPI2 | ID = 4107
Description = Failed extract of third-party root list from auto update cab at: 
 with error: A required certificate is not within its validity period when verifying
 against the current system clock or the timestamp in the signed file.  .
 
Error - 5/11/2011 12:33:03 AM | Computer Name = Nsnd-PC | Source = SideBySide | ID = 16842815
Description = Activation context generation failed for "C:\Program Files (x86)\Common
 Files\Adobe AIR\Versions\1.0\Adobe AIR.dll".Error in manifest or policy file "C:\Program
 Files (x86)\Common Files\Adobe AIR\Versions\1.0\Adobe AIR.dll" on line 3.  The value
 "MAJOR_VERSION.MINOR_VERSION.BUILD_NUMBER_MAJOR.BUILD_NUMBER_MINOR" of attribute
 "version" in element "assemblyIdentity" is invalid.
 
Error - 5/11/2011 7:22:23 AM | Computer Name = Nsnd-PC | Source = Microsoft-Windows-CAPI2 | ID = 4107
Description = Failed extract of third-party root list from auto update cab at: 
 with error: A required certificate is not within its validity period when verifying
 against the current system clock or the timestamp in the signed file.  .
 
[ DigitalPersona Pro Events ]
Error - 5/2/2010 11:29:12 PM | Computer Name = Nsnd-PC | Source = DigitalPersona Pro | ID = 17827841
Description = One-to-one fingerprint match failed.
 
[ System Events ]
Error - 6/19/2011 5:21:33 PM | Computer Name = Nsnd-PC | Source = Service Control Manager | ID = 7000
Description = The Hotspot Shield Monitoring Service service failed to start due 
to the following error:   %%2
 
Error - 6/19/2011 6:03:50 PM | Computer Name = Nsnd-PC | Source = Service Control Manager | ID = 7030
Description = The PEVSystemStart service is marked as an interactive service.  However,
 the system is configured to not allow interactive services.  This service may not
 function properly.
 
Error - 6/19/2011 6:06:05 PM | Computer Name = Nsnd-PC | Source = Application Popup | ID = 1060
Description = \??\C:\ComboFix\catchme.sys has been blocked from loading due to incompatibility
 with this system. Please contact your software vendor for a compatible version 
of the driver.
 
Error - 6/19/2011 6:06:38 PM | Computer Name = Nsnd-PC | Source = Service Control Manager | ID = 7030
Description = The PEVSystemStart service is marked as an interactive service.  However,
 the system is configured to not allow interactive services.  This service may not
 function properly.
 
Error - 6/19/2011 6:06:46 PM | Computer Name = Nsnd-PC | Source = Service Control Manager | ID = 7030
Description = The PEVSystemStart service is marked as an interactive service.  However,
 the system is configured to not allow interactive services.  This service may not
 function properly.
 
Error - 6/19/2011 6:07:50 PM | Computer Name = Nsnd-PC | Source = Service Control Manager | ID = 7000
Description = The Hotspot Shield Monitoring Service service failed to start due 
to the following error:   %%2
 
Error - 6/20/2011 10:42:58 PM | Computer Name = Nsnd-PC | Source = Service Control Manager | ID = 7000
Description = The Hotspot Shield Monitoring Service service failed to start due 
to the following error:   %%2
 
Error - 6/20/2011 10:48:51 PM | Computer Name = Nsnd-PC | Source = Service Control Manager | ID = 7022
Description = The Windows Update service hung on starting.
 
Error - 6/21/2011 7:44:37 AM | Computer Name = Nsnd-PC | Source = bowser | ID = 8003
Description = 
 
Error - 6/21/2011 6:13:25 PM | Computer Name = Nsnd-PC | Source = Service Control Manager | ID = 7000
Description = The Hotspot Shield Monitoring Service service failed to start due 
to the following error:   %%2
 
 
< End of report >

Hi nsnd,

Welcome to WhattheTech. My name is Blottedisk and I will be helping you with your malware issues. Before we delve into this, please take a look at the following notes:

  • Please subscribe to this topic, if you haven't already. You can subscribe by clicking the Watch Topic button to the right of your topic title and then choosing the notification method ( Recommended: Inmediate Notification)
  • Please avoid installing/uninstalling or updating any programs and attempting any unsupervised fixes or scans. This can make helping you impossible.
  • The forum is busy and we need to have replies as soon as possible. If I haven't had a reply after 3 days I will bump the topic and if you do not reply by the following day after that then the thread will be locked due to inactivity. However, if you will be away, let us know and we will be sure to keep the thread open.

——————————————————-


Ok, let's get started. Please follow the steps below in order:


Step 1 | Download DDS from any of the links below:

Link 1
Link 2
Link 2

——————————————————————–
  • Save it to your desktop.
  • Please disable any anti-malware program that will block scripts from running before running DDS.
  • Double-Click on dds and a command window will appear. This is normal.
  • Shortly after two logs will appear:
    • DDS.txt
    • Attach.txt
  • A window will open instructing you save & post the logs.
  • Save the logs to a convenient place such as your desktop.
  • Post the contents of the DDS.txt report in your next reply.
  • Attach the Attach.txt report to your post by scroling down to the Attachments area and then clicking Browse. Browse to where you saved the file, and click Open and then click UPLOAD.


Step 2 | Please download GMER from one of the following locations and save it to your desktop:

Main Mirror - This version will download a randomly named file (Recommended)
Zipped Mirror - This version will download a zip file you will need to extract first. If you use this mirror, please extract the zip file to your desktop.

——————————————————————–

  • Disconnect from the Internet and close all running programs.
  • Temporarily disable any real-time active protection so your security programs will not conflict with gmer's driver.
  • Right-click on the randomly named GMER file (i.e. n7gmo46c.exe) and choose "Run as administrator" to run it. Allow the gmer.sys driver to load if asked.

Note: If you downloaded the zipped version, extract the file to its own folder such as C:\gmer and then right-click on gmer.exe and choose "Run as administrator".

[external image: Posted Image]

  • GMER will open to the Rootkit/Malware tab and perform an automatic quick scan when first run. (do not use the computer while the scan is in progress)
  • If you receive a WARNING!!! about rootkit activity and are asked to fully scan your system…click NO.
  • Make sure these options are all checked:
  • Services
  • Registry
  • Files
  • Systemdrive drive/partition, which is typically C:\
  • ADS

[external image: Posted Image]
Click the image to enlarge it

  • Now click the Scan button. If you see a rootkit warning window, click OK.
  • When the scan is finished, click the Save… button to save the scan results to your Desktop. Save the file as gmer.log.
  • Click the Copy button and paste the results into your next reply.
  • Exit GMER and re-enable all active protection when done.
– If you encounter any problems, try running GMER in Safe Mode.


Step 3 | Please download aswMBR to your desktop.

  • Double click the aswMBR icon to run it.
    Vista and Windows 7 users right click the icon and choose "Run as administrator".
  • Click the Scan button to start scan.
  • When it finishes, press the save log button, save the logfile to your desktop and post its contents in your next reply.

[external image: Posted Image]
Click the image to enlarge it
Hello, Bottledisk. Thanks for taking the time to help me out. Here is the DDS.txt from step 1 (attach.txt is in the attachment :thumbup: ):

.
DDS (Ver_2011-06-12.02) - NTFSAMD64 
Internet Explorer: 8.0.7600.16385
Run by [removed] at 15:59:20 on 2011-06-22
Microsoft Windows 7 Home Premium   6.1.7600.0.1252.1.1033.18.6135.4489 [GMT -7:00]
.
AV: avast! Antivirus *Enabled/Updated* {C37D8F93-0602-E43C-40AA-47DAD597F308}
SP: avast! Antivirus *Enabled/Updated* {781C6E77-2038-EBB2-7A1A-7CA8AE10B9B5}
SP: Windows Defender *Enabled/Updated* {D68DDC3A-831F-4fae-9E44-DA132C1ACF46}
.
============== Running Processes ===============
.
C:\Windows\system32\wininit.exe
C:\Windows\system32\lsm.exe
C:\Windows\system32\svchost.exe -k DcomLaunch
C:\Windows\system32\nvvsvc.exe
C:\Windows\system32\svchost.exe -k RPCSS
C:\Windows\System32\svchost.exe -k LocalServiceNetworkRestricted
C:\Windows\System32\svchost.exe -k LocalSystemNetworkRestricted
C:\Windows\system32\svchost.exe -k netsvcs
C:\Windows\System32\DriverStore\FileRepository\stwrt64.inf_amd64_neutral_ccf0dd3cb081af84\STacSV64.exe
C:\Windows\system32\svchost.exe -k LocalService
C:\Windows\system32\Hpservice.exe
C:\Windows\system32\vcsFPService.exe
C:\Windows\system32\svchost.exe -k NetworkService
C:\Program Files\Alwil Software\Avast5\AvastSvc.exe
C:\Windows\system32\nvvsvc.exe
C:\Windows\System32\spoolsv.exe
C:\Program Files (x86)\DigitalPersona\Bin\DpHostW.exe
C:\Windows\system32\svchost.exe -k LocalServiceNoNetwork
C:\Program Files\SUPERAntiSpyware\SASCORE64.EXE
C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe
C:\Windows\System32\DriverStore\FileRepository\stwrt64.inf_amd64_neutral_ccf0dd3cb081af84\AESTSr64.exe
C:\Program Files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
C:\Program Files (x86)\Bonjour\mDNSResponder.exe
C:\Windows\system32\svchost.exe -k LocalServiceAndNoImpersonation
C:\Windows\system32\lxdncoms.exe
C:\Program Files (x86)\Common Files\Protexis\License Service\PsiService_2.exe
C:\Program Files (x86)\CyberLink\Shared files\RichVideo.exe
C:\Program Files (x86)\Common Files\VMware\USB\vmware-usbarbitrator.exe
C:\Windows\SysWOW64\vmnat.exe
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSVC.EXE
C:\Program Files (x86)\VMware\VMware Workstation\vmware-authd.exe
C:\Windows\SysWOW64\vmnetdhcp.exe
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSvcM.exe
C:\Windows\system32\svchost.exe -k NetworkServiceNetworkRestricted
C:\Windows\system32\wbem\wmiprvse.exe
C:\Windows\system32\taskhost.exe
C:\Windows\system32\Dwm.exe
C:\Windows\Explorer.EXE
C:\Program Files\Synaptics\SynTP\SynTPEnh.exe
C:\Program Files\IDT\WDM\sttray64.exe
C:\Program Files\Hewlett-Packard\HPToneControl\HPToneCtl.exe
C:\Program Files\Synaptics\SynTP\SynTPHelper.exe
C:\Program Files (x86)\Pando Networks\Media Booster\PMB.exe
C:\Program Files (x86)\GoZone\GoZone_iSync.exe
C:\Program Files (x86)\Microsoft Office\Office14\ONENOTEM.EXE
C:\Program Files (x86)\PdaNet for Android\PdaNetPC.exe
C:\Program Files (x86)\Corel\Corel Paint Shop Pro Photo X2\CorelIOMonitor.exe
C:\Program Files (x86)\Hewlett-Packard\HP Wireless Assistant\HPWAMain.exe
C:\Program Files (x86) (x86)\Lexmark 2600 Series\ezprint.exe
C:\Program Files (x86)\DigitalPersona\Bin\DpAgent.exe
C:\Program Files (x86)\HP\HP Software Update\hpwuschd2.exe
C:\Program Files (x86)\VMware\VMware Workstation\vmware-tray.exe
C:\Program Files (x86)\iTunes\iTunesHelper.exe
C:\Program Files\DigitalPersona\Bin\DPAgent.exe
C:\Windows\system32\svchost.exe -k imgsvc
C:\Program Files\iPod\bin\iPodService.exe
C:\Windows\system32\SearchIndexer.exe
C:\Program Files\Windows Media Player\wmpnetwk.exe
C:\Program Files (x86)\Hewlett-Packard\Shared\hpqwmiex.exe
C:\Windows\System32\svchost.exe -k LocalServicePeerNet
C:\Program Files (x86)\Hewlett-Packard\Shared\hpqToaster.exe
C:\Windows\System32\svchost.exe -k secsvcs
C:\Windows\system32\DllHost.exe
C:\Windows\system32\taskeng.exe
C:\Program Files (x86)\Google\Update\GoogleUpdate.exe
C:\Windows\SysWOW64\cmd.exe
C:\Windows\system32\conhost.exe
C:\Windows\SysWOW64\cscript.exe
C:\Windows\system32\wbem\wmiprvse.exe
.
============== Pseudo HJT Report ===============
.
uStart Page = hxxp://apps.ko.com/myko
uInternet Settings,ProxyOverride = *.local
BHO: HP Print Enhancer: {0347c33e-8762-4905-bf09-768834316c61} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_printenhancer.dll
BHO: Adobe PDF Link Helper: {18df081c-e8ad-4283-a596-fa578c2ebdc3} - C:\Program Files (x86)\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
BHO: DigitalPersona Personal Extension: {395610ae-c624-4f58-b89e-23733ea00f9a} - C:\Program Files (x86)\DigitalPersona\Bin\DpOtsPluginIe8.dll
BHO: Groove GFS Browser Helper: {72853161-30c5-4d22-b7f9-0bbc1d38a37e} - C:\PROGRA~2\MICROS~4\Office14\GROOVEEX.DLL
BHO: Windows Live ID Sign-in Helper: {9030d464-4c02-4abf-8ecc-5164760863c6} - C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
BHO: Office Document Cache Handler: {b4f3a835-0e21-4959-ba22-42b3008e02ff} - C:\PROGRA~2\MICROS~4\Office14\URLREDIR.DLL
BHO: Java™ Plug-In 2 SSV Helper: {dbc80044-a445-435b-bc74-9c25c1c588a9} - C:\Program Files (x86)\Java\jre6\bin\jp2ssv.dll
BHO: HP Smart BHO Class: {ffffffff-cf4e-4f2b-bdc2-0e72e116a856} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_BHO.dll
TB: {604BC32A-9680-40D1-9AC6-E06B23A1BA4C} - No File
EB: HP Smart Web Printing: {555d4d79-4bd2-4094-a395-cfc534424a05} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_bho.dll
uRun: [Steam] "c:\program files (x86)\steam\steam.exe" -silent
uRun: [Pando Media Booster] C:\Program Files (x86)\Pando Networks\Media Booster\PMB.exe
uRun: [SUPERAntiSpyware] C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe
mRun: [HPCam_Menu] "c:\Program Files (x86)\Hewlett-Packard\Media\Webcam\MUITransfer\MUIStartMenu.exe" "c:\Program Files (x86)\Hewlett-Packard\Media\Webcam" UpdateWithCreateOnce "Software\Hewlett-Packard\Media\Webcam"
mRun: [Corel File Shell Monitor] C:\Program Files (x86)\Corel\Corel Paint Shop Pro Photo X2\CorelIOMonitor.exe
mRun: [WirelessAssistant] C:\Program Files (x86)\Hewlett-Packard\HP Wireless Assistant\HPWAMain.exe
mRun: [PWRISOVM.EXE] C:\Program Files (x86)\PowerISO\PWRISOVM.EXE
mRun: [SwitchBoard] C:\Program Files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe
mRun: [AdobeCS5ServiceManager] "C:\Program Files (x86)\Common Files\Adobe\CS5ServiceManager\CS5ServiceManager.exe" -launchedbylogin
mRun: [lxdnmon.exe] "C:\Program Files (x86) (x86)\Lexmark 2600 Series\lxdnmon.exe"
mRun: [EzPrint] "C:\Program Files (x86) (x86)\Lexmark 2600 Series\ezprint.exe"
mRun: [DpAgent] C:\Program Files (x86)\DigitalPersona\Bin\dpagent.exe
mRun: [HP Software Update] C:\Program Files (x86)\Hp\HP Software Update\HPWuSchd2.exe
mRun: [vmware-tray] "C:\Program Files (x86)\VMware\VMware Workstation\vmware-tray.exe"
mRun: [BCSSync] "C:\Program Files (x86)\Microsoft Office\Office14\BCSSync.exe" /DelayServices
mRun: [iTunesHelper] "C:\Program Files (x86)\iTunes\iTunesHelper.exe"
mRun: [UnlockerAssistant] "C:\Program Files (x86)\Unlocker\UnlockerAssistant.exe"
mRun: [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
StartupFolder: C:\Users\Nsnd\AppData\Roaming\MICROS~1\Windows\STARTM~1\Programs\Startup\GOZONE~1.LNK - C:\Program Files (x86)\GoZone\GoZone_iSync.exe
StartupFolder: C:\Users\Nsnd\AppData\Roaming\MICROS~1\Windows\STARTM~1\Programs\Startup\ONENOT~1.LNK - C:\Program Files (x86)\Microsoft Office\Office14\ONENOTEM.EXE
StartupFolder: C:\Users\Nsnd\AppData\Roaming\MICROS~1\Windows\STARTM~1\Programs\Startup\PDANET~1.LNK - C:\Program Files (x86)\PdaNet for Android\PdaNetPC.exe
mPolicies-system: ConsentPromptBehaviorAdmin = 0 (0x0)
mPolicies-system: ConsentPromptBehaviorUser = 3 (0x3)
mPolicies-system: EnableLUA = 0 (0x0)
mPolicies-system: EnableUIADesktopToggle = 0 (0x0)
mPolicies-system: PromptOnSecureDesktop = 0 (0x0)
IE: E&xport; to Microsoft Excel - C:\PROGRA~2\MICROS~4\Office14\EXCEL.EXE/3000
IE: Se&nd; to OneNote - C:\PROGRA~2\MICROS~4\Office14\ONBttnIE.dll/105
IE: {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - {5F7B1267-94A9-47F5-98DB-E99415F33AEC} - C:\Program Files (x86)\Windows Live\Writer\WriterBrowserExtension.dll
IE: {2670000A-7350-4f3c-8081-5663EE0C6C49} - {48E73304-E1D6-4330-914C-F5F514E3486C} - C:\Program Files (x86)\Microsoft Office\Office14\ONBttnIE.dll
IE: {789FE86F-6FC4-46A1-9849-EDE0DB0C95CA} - {FFFDC614-B694-4AE6-AB38-5D6374584B52} - C:\Program Files (x86)\Microsoft Office\Office14\ONBttnIELinkedNotes.dll
IE: {DDE87865-83C5-48c4-8357-2F5B1AA84522} - {DDE87865-83C5-48c4-8357-2F5B1AA84522} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_BHO.dll
LSP: C:\Program Files (x86)\VMware\VMware Workstation\vsocklib.dll
DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_26-windows-i586.cab
DPF: {983A9C21-8207-4B58-BBB8-0EBC3D7C5505} - hxxps://apps.ko.com/dwa8W.cab
DPF: {CAFEEFAC-0016-0000-0026-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_26-windows-i586.cab
DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_26-windows-i586.cab
TCP: DhcpNameServer = [removed] [removed] [removed]
TCP: Interfaces\{3062BD38-2304-43B6-9A1E-3E23CC9958DA} : DhcpNameServer = [removed] [removed] [removed]
TCP: Interfaces\{FDCF163F-51B4-4581-A901-82A4F4CA6B88}\35865636A797 : DhcpNameServer = [removed] [removed]
TCP: Interfaces\{FDCF163F-51B4-4581-A901-82A4F4CA6B88}\475747479602662757474796 : DhcpNameServer = 192.168.2.1
TCP: Interfaces\{FDCF163F-51B4-4581-A901-82A4F4CA6B88}\65562796A7F6E602D496649623230303025334230302355636572756 : DhcpNameServer = 192.168.1.1
TCP: Interfaces\{FDCF163F-51B4-4581-A901-82A4F4CA6B88}\8696767696E637 : DhcpNameServer = [removed] [removed] [removed]
Filter: text/xml - {807573E5-5146-11D5-A672-00B0D022E945} - C:\Program Files (x86)\Common Files\microsoft shared\OFFICE14\MSOXMLMF.DLL
Handler: wlpg - {E43EF6CD-A37A-4A9B-9E6F-83F89B8E6324} - C:\Program Files (x86)\Windows Live\Photo Gallery\AlbumDownloadProtocolHandler.dll
SEH: Groove GFS Stub Execution Hook: {b5a7f190-dda6-4420-b3ba-52453494e6cd} - C:\PROGRA~2\MICROS~4\Office14\GROOVEEX.DLL
BHO-X64: HP Print Enhancer: {0347C33E-8762-4905-BF09-768834316C61} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_printenhancer.dll
BHO-X64:	 HP Print Enhancer - No File
BHO-X64: Adobe PDF Link Helper: {18DF081C-E8AD-4283-A596-FA578C2EBDC3} - C:\Program Files (x86)\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
BHO-X64:	 AcroIEHelperStub - No File
BHO-X64: DigitalPersona Personal Extension: {395610AE-C624-4f58-B89E-23733EA00F9A} - C:\Program Files (x86)\DigitalPersona\Bin\DpOtsPluginIe8.dll
BHO-X64:	 DigitalPersona Personal Extension - No File
BHO-X64: Groove GFS Browser Helper: {72853161-30C5-4D22-B7F9-0BBC1D38A37E} - C:\PROGRA~2\MICROS~4\Office14\GROOVEEX.DLL
BHO-X64: Windows Live ID Sign-in Helper: {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
BHO-X64: Office Document Cache Handler: {B4F3A835-0E21-4959-BA22-42B3008E02FF} - C:\PROGRA~2\MICROS~4\Office14\URLREDIR.DLL
BHO-X64:	 URLRedirectionBHO - No File
BHO-X64: Java™ Plug-In 2 SSV Helper: {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files (x86)\Java\jre6\bin\jp2ssv.dll
BHO-X64: HP Smart BHO Class: {FFFFFFFF-CF4E-4F2B-BDC2-0E72E116A856} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_BHO.dll
BHO-X64:	 HP Smart BHO Class - No File
TB-X64: {604BC32A-9680-40D1-9AC6-E06B23A1BA4C} - No File
EB-X64: {555D4D79-4BD2-4094-A395-CFC534424A05} - No File
mRun-x64: [HPCam_Menu] "c:\Program Files (x86)\Hewlett-Packard\Media\Webcam\MUITransfer\MUIStartMenu.exe" "c:\Program Files (x86)\Hewlett-Packard\Media\Webcam" UpdateWithCreateOnce "Software\Hewlett-Packard\Media\Webcam"
mRun-x64: [Corel File Shell Monitor] C:\Program Files (x86)\Corel\Corel Paint Shop Pro Photo X2\CorelIOMonitor.exe
mRun-x64: [WirelessAssistant] C:\Program Files (x86)\Hewlett-Packard\HP Wireless Assistant\HPWAMain.exe
mRun-x64: [PWRISOVM.EXE] C:\Program Files (x86)\PowerISO\PWRISOVM.EXE
mRun-x64: [SwitchBoard] C:\Program Files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe
mRun-x64: [AdobeCS5ServiceManager] "C:\Program Files (x86)\Common Files\Adobe\CS5ServiceManager\CS5ServiceManager.exe" -launchedbylogin
mRun-x64: [lxdnmon.exe] "C:\Program Files (x86) (x86)\Lexmark 2600 Series\lxdnmon.exe"
mRun-x64: [EzPrint] "C:\Program Files (x86) (x86)\Lexmark 2600 Series\ezprint.exe"
mRun-x64: [DpAgent] C:\Program Files (x86)\DigitalPersona\Bin\dpagent.exe
mRun-x64: [HP Software Update] C:\Program Files (x86)\Hp\HP Software Update\HPWuSchd2.exe
mRun-x64: [vmware-tray] "C:\Program Files (x86)\VMware\VMware Workstation\vmware-tray.exe"
mRun-x64: [BCSSync] "C:\Program Files (x86)\Microsoft Office\Office14\BCSSync.exe" /DelayServices
mRun-x64: [iTunesHelper] "C:\Program Files (x86)\iTunes\iTunesHelper.exe"
mRun-x64: [UnlockerAssistant] "C:\Program Files (x86)\Unlocker\UnlockerAssistant.exe"
mRun-x64: [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
SEH-X64: Groove GFS Stub Execution Hook: {B5A7F190-DDA6-4420-B3BA-52453494E6CD} - C:\PROGRA~2\MICROS~4\Office14\GROOVEEX.DLL
.
============= SERVICES / DRIVERS ===============
.
R1 aswSP;aswSP;C:\Windows\system32\drivers\aswSP.sys –> C:\Windows\system32\drivers\aswSP.sys [?]
R1 SASDIFSV;SASDIFSV;C:\Program Files\SUPERAntiSpyware\sasdifsv64.sys [2010-2-17 14920]
R1 SASKUTIL;SASKUTIL;C:\Program Files\SUPERAntiSpyware\saskutil64.sys [2010-2-17 12360]
R1 vwififlt;Virtual WiFi Filter Driver;C:\Windows\system32\DRIVERS\vwififlt.sys –> C:\Windows\system32\DRIVERS\vwififlt.sys [?]
R2 !SASCORE;SAS Core Service;C:\Program Files\SUPERAntiSpyware\SASCore64.exe [2011-5-4 128384]
R2 AdobeARMservice;Adobe Acrobat Update Service;C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [2011-6-6 64952]
R2 AESTFilters;Andrea ST Filters Service;C:\Windows\System32\DriverStore\FileRepository\stwrt64.inf_amd64_neutral_ccf0dd3cb081af84\AESTSr64.exe [2010-4-18 89600]
R2 aswFsBlk;aswFsBlk;C:\Windows\system32\drivers\aswFsBlk.sys –> C:\Windows\system32\drivers\aswFsBlk.sys [?]
R2 aswMonFlt;aswMonFlt;\??\C:\Windows\system32\drivers\aswMonFlt.sys –> C:\Windows\system32\drivers\aswMonFlt.sys [?]
R2 avast! Antivirus;avast! Antivirus;C:\Program Files\Alwil Software\Avast5\AvastSvc.exe [2011-1-18 40384]
R2 hpsrv;HP Service;C:\Windows\system32\Hpservice.exe –> C:\Windows\system32\Hpservice.exe [?]
R2 lxdn_device;lxdn_device;C:\Windows\system32\lxdncoms.exe -service –> C:\Windows\system32\lxdncoms.exe -service [?]
R2 vcsFPService;Validity VCS Fingerprint Service;C:\Windows\System32\vcsFPService.exe [2009-7-12 1656112]
R2 VMUSBArbService;VMware USB Arbitration Service;C:\Program Files (x86)\Common Files\VMware\USB\vmware-usbarbitrator.exe [2009-10-22 563760]
R3 enecir;ENE CIR Receiver;C:\Windows\system32\DRIVERS\enecir.sys –> C:\Windows\system32\DRIVERS\enecir.sys [?]
R3 JMCR;JMCR;C:\Windows\system32\DRIVERS\jmcr.sys –> C:\Windows\system32\DRIVERS\jmcr.sys [?]
R3 netr28ux;RT2870 USB Extensible Wireless LAN Card Driver;C:\Windows\system32\DRIVERS\netr28ux.sys –> C:\Windows\system32\DRIVERS\netr28ux.sys [?]
R3 NETw5s64;Intel(R) Wireless WiFi Link 5000 Series Adapter Driver for Windows 7 - 64 Bit;C:\Windows\system32\DRIVERS\NETw5s64.sys –> C:\Windows\system32\DRIVERS\NETw5s64.sys [?]
R3 NVHDA;Service for NVIDIA High Definition Audio Driver;C:\Windows\system32\drivers\nvhda64v.sys –> C:\Windows\system32\drivers\nvhda64v.sys [?]
R3 pnetmdm;PdaNet Modem;C:\Windows\system32\DRIVERS\pnetmdm64.sys –> C:\Windows\system32\DRIVERS\pnetmdm64.sys [?]
S2 clr_optimization_v4.0.30319_32;Microsoft .NET Framework NGEN v4.0.30319_X86;C:\Windows\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe [2010-3-18 130384]
S2 clr_optimization_v4.0.30319_64;Microsoft .NET Framework NGEN v4.0.30319_X64;C:\Windows\Microsoft.NET\Framework64\v4.0.30319\mscorsvw.exe [2010-3-18 138576]
S2 gupdate;Google Update Service (gupdate);C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [2010-4-29 133104]
S2 HssWd;Hotspot Shield Monitoring Service;C:\Program Files (x86)\Hotspot Shield\bin\hsswd.exe -product HSS –> C:\Program Files (x86)\Hotspot Shield\bin\hsswd.exe -product HSS [?]
S3 gupdatem;Google Update Service (gupdatem);C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [2010-4-29 133104]
S3 Microsoft SharePoint Workspace Audit Service;Microsoft SharePoint Workspace Audit Service;C:\Program Files (x86)\Microsoft Office\Office14\GROOVE.EXE [2010-3-25 30969208]
S3 netw5v64;Intel(R) Wireless WiFi Link 5000 Series Adapter Driver for Windows Vista 64 Bit;C:\Windows\system32\DRIVERS\netw5v64.sys –> C:\Windows\system32\DRIVERS\netw5v64.sys [?]
S3 osppsvc;Office Software Protection Platform;C:\Program Files\Common Files\Microsoft Shared\OfficeSoftwareProtectionPlatform\OSPPSVC.EXE [2010-1-9 4925184]
S3 RTL8167;Realtek 8167 NT Driver;C:\Windows\system32\DRIVERS\Rt64win7.sys –> C:\Windows\system32\DRIVERS\Rt64win7.sys [?]
S3 SrvHsfHDA;SrvHsfHDA;C:\Windows\system32\DRIVERS\VSTAZL6.SYS –> C:\Windows\system32\DRIVERS\VSTAZL6.SYS [?]
S3 SrvHsfV92;SrvHsfV92;C:\Windows\system32\DRIVERS\VSTDPV6.SYS –> C:\Windows\system32\DRIVERS\VSTDPV6.SYS [?]
S3 SrvHsfWinac;SrvHsfWinac;C:\Windows\system32\DRIVERS\VSTCNXT6.SYS –> C:\Windows\system32\DRIVERS\VSTCNXT6.SYS [?]
S3 SwitchBoard;Adobe SwitchBoard;C:\Program Files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe [2010-2-19 517096]
S3 USBAAPL64;Apple Mobile USB Driver;C:\Windows\system32\Drivers\usbaapl64.sys –> C:\Windows\system32\Drivers\usbaapl64.sys [?]
S3 WatAdminSvc;Windows Activation Technologies Service;C:\Windows\system32\Wat\WatAdminSvc.exe –> C:\Windows\system32\Wat\WatAdminSvc.exe [?]
S3 WDC_SAM;WD SCSI Pass Thru driver;C:\Windows\system32\DRIVERS\wdcsam64.sys –> C:\Windows\system32\DRIVERS\wdcsam64.sys [?]
S3 yukonw7;NDIS6.2 Miniport Driver for Marvell Yukon Ethernet Controller;C:\Windows\system32\DRIVERS\yk62x64.sys –> C:\Windows\system32\DRIVERS\yk62x64.sys [?]
.
=============== Created Last 30 ================
.
2011-06-21 02:46:17	——–	d—–w-	C:\MGtools
2011-06-21 02:44:41	39984	—-a-w-	C:\Windows\SysWow64\drivers\mbamswissarmy.sys
2011-06-21 02:44:37	——–	d—–w-	C:\Program Files (x86)\Malwarebytes' Anti-Malware
2011-06-21 02:34:48	——–	d—–w-	C:\Users\Nsnd\AppData\Roaming\SUPERAntiSpyware.com
2011-06-21 02:34:48	——–	d—–w-	C:\ProgramData\SUPERAntiSpyware.com
2011-06-21 02:34:45	——–	d—–w-	C:\ProgramData\!SASCORE
2011-06-21 02:34:42	——–	d—–w-	C:\Program Files\SUPERAntiSpyware
2011-06-19 22:08:13	——–	d—–w-	C:\$RECYCLE.BIN
2011-06-19 21:59:20	98816	—-a-w-	C:\Windows\sed.exe
2011-06-19 21:59:20	518144	—-a-w-	C:\Windows\SWREG.exe
2011-06-19 21:59:20	256512	—-a-w-	C:\Windows\PEV.exe
2011-06-19 21:59:20	208896	—-a-w-	C:\Windows\MBR.exe
2011-06-16 22:47:03	8718160	—-a-w-	C:\ProgramData\Microsoft\Windows Defender\Definition Updates\{D2B4DB76-5264-4536-BB8E-BC5B09051403}\mpengine.dll
2011-06-06 19:55:30	183696	—-a-w-	C:\Program Files (x86)\Internet Explorer\Plugins\nppdf32.dll
2011-06-04 02:09:15	——–	d—–w-	C:\Users\Nsnd\AppData\Local\{BB8EFA2C-C894-49FD-91E5-0BE1B2962B73}
2011-06-03 02:36:13	——–	d—–w-	C:\Program Files (x86)\Microsoft
2011-06-03 02:35:49	——–	d—–w-	C:\Program Files (x86)\Unlocker
2011-05-24 22:45:50	27008	—-a-w-	C:\Windows\System32\drivers\Diskdump.sys
2011-05-24 15:22:14	——–	d—–w-	C:\Users\Nsnd\AppData\Local\{EACF0CD5-A4DF-4846-839B-809F71F15A69}
2011-05-24 15:17:49	142336	—-a-w-	C:\Windows\System32\poqexec.exe
2011-05-24 15:17:49	123904	—-a-w-	C:\Windows\SysWow64\poqexec.exe
.
==================== Find3M  ====================
.
2011-06-19 06:08:13	472808	—-a-w-	C:\Windows\SysWow64\deployJava1.dll
2011-06-02 12:02:29	404640	—-a-w-	C:\Windows\SysWow64\FlashPlayerCPLApp.cpl
2011-05-29 16:11:20	25912	—-a-w-	C:\Windows\System32\drivers\mbam.sys
2011-05-28 03:25:16	1638912	—-a-w-	C:\Windows\System32\mshtml.tlb
2011-05-28 03:07:01	3133952	—-a-w-	C:\Windows\System32\win32k.sys
2011-05-28 03:00:02	1638912	—-a-w-	C:\Windows\SysWow64\mshtml.tlb
2011-05-04 02:51:08	287744	—-a-w-	C:\Windows\System32\drivers\mrxsmb10.sys
2011-05-04 02:51:08	157696	—-a-w-	C:\Windows\System32\drivers\mrxsmb.sys
2011-05-04 02:51:05	126464	—-a-w-	C:\Windows\System32\drivers\mrxsmb20.sys
2011-05-03 05:21:22	976896	—-a-w-	C:\Windows\System32\inetcomm.dll
2011-05-03 04:50:29	740864	—-a-w-	C:\Windows\SysWow64\inetcomm.dll
2011-04-29 03:13:10	461312	—-a-w-	C:\Windows\System32\drivers\srv.sys
2011-04-29 03:12:54	399872	—-a-w-	C:\Windows\System32\drivers\srv2.sys
2011-04-29 03:12:37	161792	—-a-w-	C:\Windows\System32\drivers\srvnet.sys
2011-04-27 02:57:40	102400	—-a-w-	C:\Windows\System32\drivers\dfsc.sys
2011-04-25 05:32:22	1896832	—-a-w-	C:\Windows\System32\drivers\tcpip.sys
2011-04-25 02:44:02	499712	—-a-w-	C:\Windows\System32\drivers\afd.sys
2011-04-22 20:18:28	1197056	—-a-w-	C:\Windows\System32\wininet.dll
2011-04-22 20:14:08	57856	—-a-w-	C:\Windows\System32\licmgr10.dll
2011-04-22 19:31:50	981504	—-a-w-	C:\Windows\SysWow64\wininet.dll
2011-04-22 19:31:26	44544	—-a-w-	C:\Windows\SysWow64\licmgr10.dll
2011-04-22 18:49:57	482816	—-a-w-	C:\Windows\System32\html.iec
2011-04-22 18:23:59	386048	—-a-w-	C:\Windows\SysWow64\html.iec
2011-04-10 16:36:30	848	–sha-w-	C:\ProgramData\KGyGaAvL.sys
2011-04-09 06:45:48	5509504	—-a-w-	C:\Windows\System32\ntoskrnl.exe
2011-04-09 06:13:06	3957632	—-a-w-	C:\Windows\SysWow64\ntkrnlpa.exe
2011-04-09 06:13:06	3901824	—-a-w-	C:\Windows\SysWow64\ntoskrnl.exe
2011-04-06 23:26:58	96544	—-a-w-	C:\Windows\System32\dnssd.dll
2011-04-06 23:26:58	119584	—-a-w-	C:\Windows\System32\dns-sd.exe
2011-04-06 23:20:16	91424	—-a-w-	C:\Windows\SysWow64\dnssd.dll
2011-04-06 23:20:16	107808	—-a-w-	C:\Windows\SysWow64\dns-sd.exe
2011-03-29 03:32:44	343040	—-a-w-	C:\Windows\System32\drivers\usbhub.sys
2011-03-29 03:32:29	99328	—-a-w-	C:\Windows\System32\drivers\usbccgp.sys
2011-03-29 03:32:20	324608	—-a-w-	C:\Windows\System32\drivers\usbport.sys
2011-03-29 03:32:16	52224	—-a-w-	C:\Windows\System32\drivers\usbehci.sys
2011-03-29 03:32:16	25600	—-a-w-	C:\Windows\System32\drivers\usbohci.sys
2011-03-29 03:32:13	30720	—-a-w-	C:\Windows\System32\drivers\usbuhci.sys
2011-03-29 03:32:09	7936	—-a-w-	C:\Windows\System32\drivers\usbd.sys
.
============= FINISH: 15:59:52.18 ===============

GMER did not find anything. Saved an empty text file and there was nothing to copy. Not sure if this is normal, I even tried it in safe mode and got a "GMER hasn't found any system modifications" or something along those lines.

I couldn't access the Avast website. So I downloaded asbMBR on to a thumb drive and transferred it over. here are the results for that:

aswMBR version 0.9.7.675 Copyright© 2011 AVAST Software
Run date: 2011-06-22 19:04:36
—————————–
19:04:36.643	OS Version: Windows x64 6.1.7600 
19:04:36.643	Number of processors: 8 586 0x1E05
19:04:36.644	ComputerName: NSND-PC  UserName: Nsnd
19:04:38.478	Initialize success
19:04:38.624	AVAST engine defs: 11062201
19:04:49.165	Disk 0 (boot) \Device\Harddisk0\DR0 -> \Device\Ide\IAAStorageDevice-1
19:04:49.169	Disk 0 Vendor: Hitachi_ PC4O Size: 476940MB BusType: 3
19:04:49.181	Disk 0 MBR read successfully
19:04:49.186	Disk 0 MBR scan
19:04:49.191	Disk 0 unknown MBR code
19:04:49.196	Service scanning
19:04:50.702	Disk 0 trace - called modules:
19:04:50.714	ntoskrnl.exe CLASSPNP.SYS disk.sys hpdskflt.sys iaStor.sys hal.dll 
19:04:50.721	1 nt!IofCallDriver -> \Device\Harddisk0\DR0[0xfffffa80071ee060]
19:04:50.727	3 CLASSPNP.SYS[fffff8800111043f] -> nt!IofCallDriver -> [0xfffffa8007054b10]
19:04:50.734	5 hpdskflt.sys[fffff88001df5289] -> nt!IofCallDriver -> \Device\Ide\IAAStorageDevice-1[0xfffffa800639f050]
19:04:52.128	AVAST engine scan C:\Windows
19:22:14.142	AVAST engine scan C:\Users\Nsnd
19:25:59.497	AVAST engine scan C:\ProgramData
19:27:35.292	Scan finished successfully
19:28:33.684	Disk 0 MBR has been saved successfully to "C:\Users\Nsnd\Desktop\MBR.dat"
19:28:33.694	The log file has been saved successfully to "C:\Users\Nsnd\Desktop\aswMBR.txt"

Thanks again for all the help!

Attachments:

Hi,

You have a DNS Hijacker infection. You should be fine after running Malwarebyte's Antimalware.
Please follow this procedure:

Step 1 | Run OTL.exe
  • Copy/paste the following text written inside of the code box into the Custom Scans/Fixes box located at the bottom of OTL

    :Reg
    
    :OTL
    IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyOverride" = *.local
    
    :Commands
    [purity]
    [EmptyFlash]
    [emptytemp]
  • Then click the Run Fix button at the top.
  • Let the program run unhindered, reboot when it is done.
  • It will produce a log for you on reboot, please post that log in your next reply.

Step 2 | Uninstall Malwarebyte's Antimalware. Then try to download it again from here: http://www.malwarebytes.org/mbam.php. If unable to download it from your cumputer, download it on to a thumb drive and transferred it over. Then follow these instructions:

  • Double-click mbam-setup.exe and follow the prompts to install the program.
  • At the end, be sure a checkmark is placed next to Update Malwarebytes' Anti-Malware and Launch Malwarebytes' Anti-Malware, then click Finish.
  • If an update is found, it will download and install the latest version.
  • Once the program has loaded, select Perform quick scan, then click Scan.
  • When the scan is complete, click OK, then Show Results to view the results.
  • Be sure that everything is checked, and click Remove Selected.
  • When completed, a log will open in Notepad. Please save it to a convenient location and post the results.
I ran OTL, and everything seemed to go ok. Here's OTL log:

All processes killed
========== REGISTRY ==========
========== OTL ==========
HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings\\ProxyOverride| /E : value set successfully!
========== COMMANDS ==========
 
[EMPTYFLASH]
 
User: All Users
 
User: Default
->Flash cache emptied: 41620 bytes
 
User: Default User
->Flash cache emptied: 0 bytes
 
User: Megan
->Flash cache emptied: 1222 bytes
 
User: Nsnd
->Flash cache emptied: 176920 bytes
 
User: Public
 
Total Flash Files Cleaned = 0.00 mb
 
 
[EMPTYTEMP]
 
User: All Users
 
User: Default
->Temp folder emptied: 0 bytes
->Temporary Internet Files folder emptied: 67 bytes
->Flash cache emptied: 0 bytes
 
User: Default User
->Temp folder emptied: 0 bytes
->Temporary Internet Files folder emptied: 0 bytes
->Flash cache emptied: 0 bytes
 
User: Megan
->Temp folder emptied: 0 bytes
->Temporary Internet Files folder emptied: 67 bytes
->Java cache emptied: 9243250 bytes
->Google Chrome cache emptied: 15184182 bytes
->Flash cache emptied: 0 bytes
 
User: Nsnd
->Temp folder emptied: 1388591 bytes
->Temporary Internet Files folder emptied: 32805431 bytes
->Java cache emptied: 29764748 bytes
->Google Chrome cache emptied: 354093027 bytes
->Flash cache emptied: 0 bytes
 
User: Public
->Temp folder emptied: 0 bytes
 
%systemdrive% .tmp files removed: 0 bytes
%systemroot% .tmp files removed: 0 bytes
%systemroot%\System32 .tmp files removed: 0 bytes
%systemroot%\System32 (64bit) .tmp files removed: 0 bytes
%systemroot%\System32\drivers .tmp files removed: 0 bytes
Windows Temp folder emptied: 47112 bytes
%systemroot%\sysnative\config\systemprofile\AppData\Local\Microsoft\Windows\Temporary Internet Files folder emptied: 67496 bytes
%systemroot%\sysnative\config\systemprofile\AppData\LocalLow\Sun\Java\Deployment folder emptied: 749 bytes
RecycleBin emptied: 0 bytes
 
Total Files Cleaned = 422.00 mb
 
 
OTL by OldTimer - Version 3.2.24.1 log created on 06242011_154317

Files\Folders moved on Reboot…
C:\Users\Nsnd\AppData\Local\Temp\FXSAPIDebugLogFile.txt moved successfully.
File move failed. C:\Windows\temp\_avast5_\Webshlock.txt scheduled to be moved on reboot.
C:\Windows\temp\vmware-SYSTEM\vmware-usbarb-SYSTEM-2688.log moved successfully.

Registry entries deleted on Reboot…

Uninstalled Malwarebyte's, but I wasn't able to download it on this computer. Downloaded the installer on another computer and used a thumb drive. Installed Malwarebyte's, but wasn't able to update. However it did find 4 items :-D.

Malwarebytes' Anti-Malware 1.51.0.1200
www.malwarebytes.org

Database version: 6705

Windows 6.1.7600
Internet Explorer 8.0.7600.16385

6/24/2011 4:01:07 PM
mbam-log-2011-06-24 (16-01-07).txt

Scan type: Quick scan
Objects scanned: 178496
Time elapsed: 2 minute(s), 14 second(s)

Memory Processes Infected: 0
Memory Modules Infected: 0
Registry Keys Infected: 0
Registry Values Infected: 0
Registry Data Items Infected: 4
Folders Infected: 0
Files Infected: 0

Memory Processes Infected:
(No malicious items detected)

Memory Modules Infected:
(No malicious items detected)

Registry Keys Infected:
(No malicious items detected)

Registry Values Infected:
(No malicious items detected)

Registry Data Items Infected:
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\Tcpip\Parameters\DhcpNameServer (Trojan.DNSChanger) -> Bad: ([removed]) Good: () -> Quarantined and deleted successfully.
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\Tcpip\Parameters\Interfaces\{3062BD38-2304-43B6-9A1E-3E23CC9958DA}\DhcpNameServer (Trojan.DNSChanger) -> Bad: ([removed]) Good: () -> Quarantined and deleted successfully.

Folders Infected:
(No malicious items detected)

Files Infected:
(No malicious items detected)

Rebooted, but still un
No, still can't update MB, SAS, and Avast doesn't seem to be updating either. I cannot access the MB web site or Avast website. Malware is such a pain. I re-scanned my computer and the same 4 entries came up, but I didn't do anything with them.
Please download Combofix from either of the links below but rename it to landscape.exe before saving it to your desktop.

Link 1
Link 2


**Note: It is important that it is saved directly to your desktop**

——————————————————————–
IMPORTANT - Disable your AntiVirus and AntiSpyware applications, usually via a right click on the System Tray icon. They may otherwise interfere with our tools. If you have difficulty properly disabling your protective programs, refer to this link here
——————————————————————–

  • Right-click and choose "Run as administrator" on the renamed Combofix.exe & follow the prompts. When finished, it will produce a report for you.
  • As part of it's process, ComboFix will check to see if the Microsoft Windows Recovery Console is installed. With malware infections being as they are today, it's strongly recommended to have this pre-installed on your machine before doing any malware removal. It will allow you to boot up into a special recovery/repair mode that will allow us to more easily help you should your computer have a problem after an attempted removal of malware.
  • Follow the prompts to allow ComboFix to download and install the Microsoft Windows Recovery Console, and when prompted, agree to the End-User License Agreement to install the Microsoft Windows Recovery Console.
**Please note: If the Microsoft Windows Recovery Console is already installed, ComboFix will continue it's malware removal procedures.

[external image: Posted Image]


  • Once the Microsoft Windows Recovery Console is installed using ComboFix, you should see the following message:

[external image: Posted Image]


  • Click on Yes, to continue scanning for malware.
  • When finished, it will produce a log for you. Please include the C:\ComboFix.txt in your next reply.

If you need help, see this link:
http://www.bleepingcomputer.com/combofix/how-to-use-combofix
Here's the log from Combofix:

ComboFix 11-06-25.03 - Nsnd 06/25/2011  11:18:43.1.8 - x64
Microsoft Windows 7 Home Premium   6.1.7600.0.1252.1.1033.18.6135.4236 [GMT -7:00]
Running from: c:\users\[removed]\Desktop\landscape.exe
AV: avast! Antivirus *Disabled/Updated* {C37D8F93-0602-E43C-40AA-47DAD597F308}
SP: avast! Antivirus *Disabled/Updated* {781C6E77-2038-EBB2-7A1A-7CA8AE10B9B5}
SP: Windows Defender *Enabled/Updated* {D68DDC3A-831F-4fae-9E44-DA132C1ACF46}
.
.
(((((((((((((((((((((((((((((((((((((((   Other Deletions   )))))))))))))))))))))))))))))))))))))))))))))))))
.
.
c:\windows\system32\SV
c:\windows\system32\SV\DPCrProv.dll.mui
c:\windows\system32\SV\DPSDApi.dll.mui
c:\windows\SysWow64\SV
c:\windows\SysWow64\SV\DPCrProv.dll.mui
c:\windows\SysWow64\SV\DPSDApi.dll.mui
.
.
(((((((((((((((((((((((((   Files Created from 2011-05-25 to 2011-06-25  )))))))))))))))))))))))))))))))
.
.
2011-06-25 18:24 . 2011-06-25 18:24	——–	d—–w-	c:\users\Megan\AppData\Local\temp
2011-06-25 18:24 . 2011-06-25 18:24	——–	d—–w-	c:\users\Default\AppData\Local\temp
2011-06-24 22:57 . 2011-05-29 16:11	39984	—-a-w-	c:\windows\SysWow64\drivers\mbamswissarmy.sys
2011-06-24 22:57 . 2011-06-24 22:57	——–	d—–w-	c:\program files (x86)\Malwarebytes' Anti-Malware
2011-06-24 22:43 . 2011-06-24 22:43	——–	d—–w-	C:\_OTL
2011-06-21 02:46 . 2011-06-21 03:27	——–	d—–w-	C:\MGtools
2011-06-21 02:34 . 2011-06-21 02:34	——–	d—–w-	c:\programdata\SUPERAntiSpyware.com
2011-06-16 22:49 . 2011-05-28 03:25	1638912	—-a-w-	c:\windows\system32\mshtml.tlb
2011-06-16 22:47 . 2011-05-09 22:00	8718160	—-a-w-	c:\programdata\Microsoft\Windows Defender\Definition Updates\{D2B4DB76-5264-4536-BB8E-BC5B09051403}\mpengine.dll
2011-06-12 23:26 . 2011-06-12 23:26	——–	d—–w-	c:\program files (x86)\Common Files\Java
2011-06-06 19:55 . 2011-06-06 19:55	183696	—-a-w-	c:\program files (x86)\Internet Explorer\Plugins\nppdf32.dll
2011-06-04 02:09 . 2011-06-04 02:09	——–	d—–w-	c:\users\Nsnd\AppData\Local\{BB8EFA2C-C894-49FD-91E5-0BE1B2962B73}
2011-06-03 02:36 . 2011-06-19 21:49	——–	d—–w-	c:\program files (x86)\Microsoft
2011-06-03 02:35 . 2011-06-25 04:00	——–	d—–w-	c:\program files (x86)\Unlocker
.
.
.
((((((((((((((((((((((((((((((((((((((((   Find3M Report   ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2011-06-21 03:27 . 2011-06-21 02:46	266209	—-a-w-	C:\MGlogs.zip
2011-06-19 06:08 . 2010-04-30 02:01	472808	—-a-w-	c:\windows\SysWow64\deployJava1.dll
2011-06-02 12:02 . 2011-05-13 01:12	404640	—-a-w-	c:\windows\SysWow64\FlashPlayerCPLApp.cpl
2011-05-29 16:11 . 2010-04-30 03:08	25912	—-a-w-	c:\windows\system32\drivers\mbam.sys
2011-04-22 20:18 . 2011-05-24 22:45	27008	—-a-w-	c:\windows\system32\drivers\Diskdump.sys
2011-04-10 16:36 . 2010-04-30 02:53	848	–sha-w-	c:\programdata\KGyGaAvL.sys
2011-04-09 06:58 . 2011-05-24 15:17	142336	—-a-w-	c:\windows\system32\poqexec.exe
2011-04-09 06:45 . 2011-05-12 02:53	5509504	—-a-w-	c:\windows\system32\ntoskrnl.exe
2011-04-09 06:13 . 2011-05-12 02:53	3957632	—-a-w-	c:\windows\SysWow64\ntkrnlpa.exe
2011-04-09 06:13 . 2011-05-12 02:53	3901824	—-a-w-	c:\windows\SysWow64\ntoskrnl.exe
2011-04-09 05:56 . 2011-05-24 15:17	123904	—-a-w-	c:\windows\SysWow64\poqexec.exe
2011-04-06 23:26 . 2011-04-06 23:26	96544	—-a-w-	c:\windows\system32\dnssd.dll
2011-04-06 23:26 . 2011-04-06 23:26	119584	—-a-w-	c:\windows\system32\dns-sd.exe
2011-04-06 23:20 . 2011-04-06 23:20	91424	—-a-w-	c:\windows\SysWow64\dnssd.dll
2011-04-06 23:20 . 2011-04-06 23:20	107808	—-a-w-	c:\windows\SysWow64\dns-sd.exe
2011-03-29 03:32 . 2011-05-12 02:53	343040	—-a-w-	c:\windows\system32\drivers\usbhub.sys
2011-03-29 03:32 . 2011-05-12 02:53	99328	—-a-w-	c:\windows\system32\drivers\usbccgp.sys
2011-03-29 03:32 . 2011-05-12 02:53	324608	—-a-w-	c:\windows\system32\drivers\usbport.sys
2011-03-29 03:32 . 2011-05-12 02:53	52224	—-a-w-	c:\windows\system32\drivers\usbehci.sys
2011-03-29 03:32 . 2011-05-12 02:53	25600	—-a-w-	c:\windows\system32\drivers\usbohci.sys
2011-03-29 03:32 . 2011-05-12 02:53	30720	—-a-w-	c:\windows\system32\drivers\usbuhci.sys
2011-03-29 03:32 . 2011-05-12 02:53	7936	—-a-w-	c:\windows\system32\drivers\usbd.sys
.
.
(((((((((((((((((((((((((((((((((((((   Reg Loading Points   ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown 
REGEDIT4
.
[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"Steam"="c:\program files (x86)\steam\steam.exe" [2010-11-17 1242448]
"Pando Media Booster"="c:\program files (x86)\Pando Networks\Media Booster\PMB.exe" [2010-09-26 2969496]
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run]
"HPCam_Menu"="c:\program files (x86)\Hewlett-Packard\Media\Webcam\MUITransfer\MUIStartMenu.exe" [2009-05-20 222504]
"Corel File Shell Monitor"="c:\program files (x86)\Corel\Corel Paint Shop Pro Photo X2\CorelIOMonitor.exe" [2009-08-26 15544]
"WirelessAssistant"="c:\program files (x86)\Hewlett-Packard\HP Wireless Assistant\HPWAMain.exe" [2009-07-23 498744]
"PWRISOVM.EXE"="c:\program files (x86)\PowerISO\PWRISOVM.EXE" [2009-03-15 180224]
"SwitchBoard"="c:\program files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe" [2010-02-19 517096]
"AdobeCS5ServiceManager"="c:\program files (x86)\Common Files\Adobe\CS5ServiceManager\CS5ServiceManager.exe" [2010-02-22 406992]
"lxdnmon.exe"="c:\program files (x86) (x86)\Lexmark 2600 Series\lxdnmon.exe" [2010-02-04 660136]
"EzPrint"="c:\program files (x86) (x86)\Lexmark 2600 Series\ezprint.exe" [2010-02-04 107176]
"DpAgent"="c:\program files (x86)\DigitalPersona\Bin\dpagent.exe" [2009-12-01 842816]
"HP Software Update"="c:\program files (x86)\Hp\HP Software Update\HPWuSchd2.exe" [2010-06-10 49208]
"BCSSync"="c:\program files (x86)\Microsoft Office\Office14\BCSSync.exe" [2010-03-13 91520]
"iTunesHelper"="c:\program files (x86)\iTunes\iTunesHelper.exe" [2011-04-27 421160]
"Adobe ARM"="c:\program files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe" [2011-06-06 937920]
.
c:\users\Nsnd\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\
GoZone iSync.lnk - c:\program files (x86)\GoZone\GoZone_iSync.exe [2011-5-18 431608]
OneNote 2010 Screen Clipper and Launcher.lnk - c:\program files (x86)\Microsoft Office\Office14\ONENOTEM.EXE [2010-3-29 227712]
.
[HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\policies\system]
"ConsentPromptBehaviorAdmin"= 0 (0x0)
"ConsentPromptBehaviorUser"= 3 (0x3)
"EnableLUA"= 0 (0x0)
"EnableUIADesktopToggle"= 0 (0x0)
"PromptOnSecureDesktop"= 0 (0x0)
.
[HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\windows nt\currentversion\drivers32]
"aux"=wdmaud.drv
.
[HKEY_LOCAL_MACHINE\system\currentcontrolset\control\lsa]
Security Packages	REG_MULTI_SZ   	kerberos msv1_0 schannel wdigest tspkg pku2u livessp
.
R2 clr_optimization_v4.0.30319_32;Microsoft .NET Framework NGEN v4.0.30319_X86;c:\windows\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe [2010-03-18 130384]
R2 clr_optimization_v4.0.30319_64;Microsoft .NET Framework NGEN v4.0.30319_X64;c:\windows\Microsoft.NET\Framework64\v4.0.30319\mscorsvw.exe [2010-03-18 138576]
R2 gupdate;Google Update Service (gupdate);c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-04-30 133104]
R2 HssWd;Hotspot Shield Monitoring Service;c:\program files (x86)\Hotspot Shield\bin\hsswd.exe [x]
R3 dc3d;MS Hardware Device Detection Driver (HID);c:\windows\system32\DRIVERS\dc3d.sys [x]
R3 gupdatem;Google Update Service (gupdatem);c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-04-30 133104]
R3 Microsoft SharePoint Workspace Audit Service;Microsoft SharePoint Workspace Audit Service;c:\program files (x86)\Microsoft Office\Office14\GROOVE.EXE [2010-03-25 30969208]
R3 netw5v64;Intel(R) Wireless WiFi Link 5000 Series Adapter Driver for Windows Vista 64 Bit;c:\windows\system32\DRIVERS\netw5v64.sys [x]
R3 osppsvc;Office Software Protection Platform;c:\program files\Common Files\Microsoft Shared\OfficeSoftwareProtectionPlatform\OSPPSVC.EXE [2010-01-10 4925184]
R3 pnetmdm;PdaNet Modem;c:\windows\system32\DRIVERS\pnetmdm64.sys [x]
R3 RTL8167;Realtek 8167 NT Driver;c:\windows\system32\DRIVERS\Rt64win7.sys [x]
R3 SrvHsfHDA;SrvHsfHDA;c:\windows\system32\DRIVERS\VSTAZL6.SYS [x]
R3 SrvHsfV92;SrvHsfV92;c:\windows\system32\DRIVERS\VSTDPV6.SYS [x]
R3 SrvHsfWinac;SrvHsfWinac;c:\windows\system32\DRIVERS\VSTCNXT6.SYS [x]
R3 SwitchBoard;Adobe SwitchBoard;c:\program files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe [2010-02-19 517096]
R3 USBAAPL64;Apple Mobile USB Driver;c:\windows\system32\Drivers\usbaapl64.sys [x]
R3 WatAdminSvc;Windows Activation Technologies Service;c:\windows\system32\Wat\WatAdminSvc.exe [x]
R3 WDC_SAM;WD SCSI Pass Thru driver;c:\windows\system32\DRIVERS\wdcsam64.sys [x]
R3 X6va001;X6va001;c:\users\Nsnd\AppData\Local\Temp\0014B86.tmp [x]
R3 yukonw7;NDIS6.2 Miniport Driver for Marvell Yukon Ethernet Controller;c:\windows\system32\DRIVERS\yk62x64.sys [x]
R4 lxdn_device;lxdn_device;c:\windows\system32\lxdncoms.exe [2007-11-28 1039872]
S1 aswSP;aswSP; [x]
S1 vwififlt;Virtual WiFi Filter Driver;c:\windows\system32\DRIVERS\vwififlt.sys [x]
S2 AdobeARMservice;Adobe Acrobat Update Service;c:\program files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [2011-06-06 64952]
S2 AESTFilters;Andrea ST Filters Service;c:\windows\System32\DriverStore\FileRepository\stwrt64.inf_amd64_neutral_ccf0dd3cb081af84\AESTSr64.exe [2009-03-02 89600]
S2 aswFsBlk;aswFsBlk; [x]
S2 aswMonFlt;aswMonFlt;c:\windows\system32\drivers\aswMonFlt.sys [x]
S2 hpsrv;HP Service;c:\windows\system32\Hpservice.exe [x]
S2 vcsFPService;Validity VCS Fingerprint Service;c:\windows\system32\vcsFPService.exe [2009-07-13 1924400]
S3 enecir;ENE CIR Receiver;c:\windows\system32\DRIVERS\enecir.sys [x]
S3 JMCR;JMCR;c:\windows\system32\DRIVERS\jmcr.sys [x]
S3 netr28ux;RT2870 USB Extensible Wireless LAN Card Driver;c:\windows\system32\DRIVERS\netr28ux.sys [x]
S3 NETw5s64;Intel(R) Wireless WiFi Link 5000 Series Adapter Driver for Windows 7 - 64 Bit;c:\windows\system32\DRIVERS\NETw5s64.sys [x]
S3 NVHDA;Service for NVIDIA High Definition Audio Driver;c:\windows\system32\drivers\nvhda64v.sys [x]
.
.
Contents of the 'Scheduled Tasks' folder
.
2011-06-25 c:\windows\Tasks\GoogleUpdateTaskMachineCore.job
- c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-04-30 02:48]
.
2011-06-25 c:\windows\Tasks\GoogleUpdateTaskMachineUA.job
- c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-04-30 02:48]
.
.
——— x86-64 ———–
.
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SynTPEnh"="c:\program files (x86)\Synaptics\SynTP\SynTPEnh.exe" [BU]
"SysTrayApp"="c:\program files\IDT\WDM\sttray64.exe" [2009-07-22 450048]
"HPToneControl"="c:\program files\Hewlett-Packard\HPToneControl\HPTonectl.exe" [2009-07-24 99384]
"AdobeAAMUpdater-1.0"="c:\program files (x86)\Common Files\Adobe\OOBE\PDApp\UWA\UpdaterStartupUtility.exe" [2010-03-06 500208]
.
——- Supplementary Scan ——-
.
uStart Page = hxxp://apps.ko.com/myko
uLocal Page = c:\windows\system32\blank.htm
mLocal Page = c:\windows\SysWOW64\blank.htm
IE: E&xport to Microsoft Excel - c:\progra~2\MICROS~4\Office14\EXCEL.EXE/3000
IE: Se&nd to OneNote - c:\progra~2\MICROS~4\Office14\ONBttnIE.dll/105
TCP: DhcpNameServer = [removed] [removed] [removed]
.
- - - - ORPHANS REMOVED - - - -
.
Wow6432Node-HKLM-Run-UnlockerAssistant - c:\program files (x86)\Unlocker\UnlockerAssistant.exe
WebBrowser-{604BC32A-9680-40D1-9AC6-E06B23A1BA4C} - (no file)
.
.
.
[HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\services\X6va001]
"ImagePath"="\??\c:\users\Nsnd\AppData\Local\Temp\0014B86.tmp"
.
——————— LOCKED REGISTRY KEYS ———————
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}]
@Denied: (A 2) (Everyone)
@="FlashBroker"
"LocalizedString"="@c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil10r_ActiveX.exe,-101"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\Elevation]
"Enabled"=dword:00000001
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\LocalServer32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil10r_ActiveX.exe"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\TypeLib]
@="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}]
@Denied: (A 2) (Everyone)
@="Shockwave Flash Object"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\InprocServer32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10r.ocx"
"ThreadingModel"="Apartment"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\MiscStatus]
@="0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ProgID]
@="ShockwaveFlash.ShockwaveFlash.10"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10r.ocx, 1"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\TypeLib]
@="{D27CDB6B-AE6D-11cf-96B8-444553540000}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\Version]
@="1.0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID]
@="ShockwaveFlash.ShockwaveFlash"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}]
@Denied: (A 2) (Everyone)
@="Macromedia Flash Factory Object"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\InprocServer32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10r.ocx"
"ThreadingModel"="Apartment"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ProgID]
@="FlashFactory.FlashFactory.1"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10r.ocx, 1"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\TypeLib]
@="{D27CDB6B-AE6D-11cf-96B8-444553540000}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\Version]
@="1.0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID]
@="FlashFactory.FlashFactory"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}]
@Denied: (A 2) (Everyone)
@="IFlashBroker4"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\ProxyStubClsid32]
@="{00020424-0000-0000-C000-000000000046}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\TypeLib]
@="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}"
"Version"="1.0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Office\Common\Smart Tag\Actions\{B7EFF951-E52F-45CC-9EF7-57124F2177CC}]
@Denied: (A) (Everyone)
"Solution"="{15727DE6-F92D-4E46-ACB4-0E2C58B31A18}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Schema Library\ActionsPane3]
@Denied: (A) (Everyone)
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Schema Library\ActionsPane3\0]
"Key"="ActionsPane3"
"Location"="c:\\Program Files (x86)\\Common Files\\Microsoft Shared\\VSTO\\ActionsPane3.xsd"
.
[HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\PCW\Security]
@Denied: (Full) (Everyone)
.
———————— Other Running Processes ————————
.
c:\program files\Alwil Software\Avast5\AvastSvc.exe
c:\program files (x86)\DigitalPersona\Bin\DpHostW.exe
c:\program files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
c:\program files (x86)\Bonjour\mDNSResponder.exe
c:\program files (x86)\Common Files\Protexis\License Service\PsiService_2.exe
c:\program files (x86)\CyberLink\Shared files\RichVideo.exe
.
**************************************************************************
.
Completion time: 2011-06-25  11:30:24 - machine was rebooted
ComboFix-quarantined-files.txt  2011-06-25 18:30
ComboFix2.txt  2011-06-19 22:13
.
Pre-Run: 194,247,213,056 bytes free
Post-Run: 194,019,549,184 bytes free
.
- - End Of File - - 1DE374DF83A02CE4A8C56F0B44919225
We caught a nasty buddy there.


How is the machine running? Let's proceed as follows:


Step 1 | ComboFix - CFScript

WARNING !
This script is for THIS user and computer ONLY!
Using this tool incorrectly could damage your Operating System… preventing it from starting again!


You will not have Internet access when you execute ComboFix. All open windows will need to be closed!

Please open Notepad and copy/paste all the text below… into the window:

DDS::
TCP: DhcpNameServer = [removed] [removed] [removed]
  • Save it to your desktop as CFScript.txt
  • Please disable any Antivirus or Firewall you have active, as shown in this topic. Please close all open application windows.
  • Drag the CFScript.txt (icon) into the ComboFix.exe icon… as seen in the image below:

    🖼Click to load external image (Posted Image)

    This will cause ComboFix to run again.
    Do Not use your keyboard or mouse click anywhere in the ComboFix window, as this may cause the program to stall or crash.
    Do Not touch your computer when ComboFix is running!

    When finished… Notepad will open … ComboFix will produce a log file called "log.txt".
  • Please copy/paste the contents of log.txt… in your next reply.

** Enable your Antivirus and Firewall, before connecting to the Internet again! **


Step 2 | As you have Malwarebytes' Anti-Malware installed on your computer. Could you please do a scan using these settings:

  • Open Malwarebytes' Anti-Malware
  • Select the Update tab
  • Click Check for Updates
  • After the update have been completed, Select the Scanner tab.
  • Select Perform Quick scan, then click on Scan
  • When done, you will be prompted. Click OK. If Items are found, then click on Show Results
  • Check all items then click on Remove Selected
  • After it has removed the items, Notepad will open. Please post this log in your next reply.
The log can also be found here:
  • C:\Documents and Settings\Username\Application Data\Malwarebytes\Malwarebytes' Anti-Malware\Logs\mbam-log-date (time).txt
  • Or via the Logs tab when the application is started.
Note: MBAM may ask to reboot your computer so it can continue with the removal process, please do so immediately.
Failure to reboot will prevent MBAM from removing all the malware.
My computer seems to be running ok. I get a popup tab in my chrome browser every now and then, but that's about it performance wise. I ran the ComboFix with the requested settings, here's the log:

ComboFix 11-06-25.03 - Nsnd 06/26/2011  20:54:19.2.8 - x64
Microsoft Windows 7 Home Premium   6.1.7600.0.1252.1.1033.18.6135.4617 [GMT -7:00]
Running from: c:\users\[removed]\Desktop\landscape.exe
Command switches used :: c:\users\Nsnd\Desktop\CFScript.txt
AV: avast! Antivirus *Disabled/Updated* {2B2D1395-420B-D5C9-657E-930FE358FC3C}
SP: avast! Antivirus *Disabled/Updated* {904CF271-6431-DA47-5FCE-A87D98DFB681}
SP: Windows Defender *Enabled/Updated* {D68DDC3A-831F-4fae-9E44-DA132C1ACF46}
.
.
(((((((((((((((((((((((((   Files Created from 2011-05-27 to 2011-06-27  )))))))))))))))))))))))))))))))
.
.
2011-06-27 04:00 . 2011-06-27 04:00	——–	d—–w-	c:\users\Megan\AppData\Local\temp
2011-06-27 04:00 . 2011-06-27 04:00	——–	d—–w-	c:\users\Default\AppData\Local\temp
2011-06-25 21:42 . 2011-05-10 12:04	600920	—-a-w-	c:\windows\system32\drivers\aswSnx.sys
2011-06-24 22:57 . 2011-05-29 16:11	39984	—-a-w-	c:\windows\SysWow64\drivers\mbamswissarmy.sys
2011-06-24 22:57 . 2011-06-24 22:57	——–	d—–w-	c:\program files (x86)\Malwarebytes' Anti-Malware
2011-06-24 22:43 . 2011-06-24 22:43	——–	d—–w-	C:\_OTL
2011-06-21 02:46 . 2011-06-21 03:27	——–	d—–w-	C:\MGtools
2011-06-21 02:34 . 2011-06-21 02:34	——–	d—–w-	c:\programdata\SUPERAntiSpyware.com
2011-06-16 22:49 . 2011-05-28 03:25	1638912	—-a-w-	c:\windows\system32\mshtml.tlb
2011-06-16 22:47 . 2011-05-09 22:00	8718160	—-a-w-	c:\programdata\Microsoft\Windows Defender\Definition Updates\{D2B4DB76-5264-4536-BB8E-BC5B09051403}\mpengine.dll
2011-06-12 23:26 . 2011-06-12 23:26	——–	d—–w-	c:\program files (x86)\Common Files\Java
2011-06-06 19:55 . 2011-06-06 19:55	183696	—-a-w-	c:\program files (x86)\Internet Explorer\Plugins\nppdf32.dll
2011-06-04 02:09 . 2011-06-04 02:09	——–	d—–w-	c:\users\Nsnd\AppData\Local\{BB8EFA2C-C894-49FD-91E5-0BE1B2962B73}
2011-06-03 02:36 . 2011-06-19 21:49	——–	d—–w-	c:\program files (x86)\Microsoft
2011-06-03 02:35 . 2011-06-25 04:00	——–	d—–w-	c:\program files (x86)\Unlocker
.
.
.
((((((((((((((((((((((((((((((((((((((((   Find3M Report   ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2011-06-21 03:27 . 2011-06-21 02:46	266209	—-a-w-	C:\MGlogs.zip
2011-06-19 06:08 . 2010-04-30 02:01	472808	—-a-w-	c:\windows\SysWow64\deployJava1.dll
2011-06-02 12:02 . 2011-05-13 01:12	404640	—-a-w-	c:\windows\SysWow64\FlashPlayerCPLApp.cpl
2011-05-29 16:11 . 2010-04-30 03:08	25912	—-a-w-	c:\windows\system32\drivers\mbam.sys
2011-05-10 12:10 . 2010-07-01 17:52	40112	—-a-w-	c:\windows\avastSS.scr
2011-05-10 12:10 . 2010-04-30 02:48	199304	—-a-w-	c:\windows\SysWow64\aswBoot.exe
2011-05-10 12:10 . 2011-01-18 09:22	253888	—-a-w-	c:\windows\system32\aswBoot.exe
2011-05-10 12:04 . 2010-04-30 02:48	287576	—-a-w-	c:\windows\system32\drivers\aswSP.sys
2011-05-10 12:02 . 2010-04-30 02:48	53592	—-a-w-	c:\windows\system32\drivers\aswTdi.sys
2011-05-10 11:59 . 2010-04-30 02:48	31064	—-a-w-	c:\windows\system32\drivers\aswRdr.sys
2011-05-10 11:59 . 2010-04-30 02:48	64344	—-a-w-	c:\windows\system32\drivers\aswMonFlt.sys
2011-05-10 11:59 . 2010-04-30 02:48	22360	—-a-w-	c:\windows\system32\drivers\aswFsBlk.sys
2011-04-22 20:18 . 2011-05-24 22:45	27008	—-a-w-	c:\windows\system32\drivers\Diskdump.sys
2011-04-10 16:36 . 2010-04-30 02:53	848	–sha-w-	c:\programdata\KGyGaAvL.sys
2011-04-09 06:58 . 2011-05-24 15:17	142336	—-a-w-	c:\windows\system32\poqexec.exe
2011-04-09 06:45 . 2011-05-12 02:53	5509504	—-a-w-	c:\windows\system32\ntoskrnl.exe
2011-04-09 06:13 . 2011-05-12 02:53	3957632	—-a-w-	c:\windows\SysWow64\ntkrnlpa.exe
2011-04-09 06:13 . 2011-05-12 02:53	3901824	—-a-w-	c:\windows\SysWow64\ntoskrnl.exe
2011-04-09 05:56 . 2011-05-24 15:17	123904	—-a-w-	c:\windows\SysWow64\poqexec.exe
2011-04-06 23:26 . 2011-04-06 23:26	96544	—-a-w-	c:\windows\system32\dnssd.dll
2011-04-06 23:26 . 2011-04-06 23:26	119584	—-a-w-	c:\windows\system32\dns-sd.exe
2011-04-06 23:20 . 2011-04-06 23:20	91424	—-a-w-	c:\windows\SysWow64\dnssd.dll
2011-04-06 23:20 . 2011-04-06 23:20	107808	—-a-w-	c:\windows\SysWow64\dns-sd.exe
.
.
(((((((((((((((((((((((((((((   SnapShot@2011-06-25_18.26.10   )))))))))))))))))))))))))))))))))))))))))
.
- 2009-07-14 04:54 . 2011-06-25 18:26	16384			  c:\windows\SysWOW64\config\systemprofile\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
+ 2009-07-14 04:54 . 2011-06-27 04:01	16384			  c:\windows\SysWOW64\config\systemprofile\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
- 2009-07-14 04:54 . 2011-06-25 18:26	32768			  c:\windows\SysWOW64\config\systemprofile\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\index.dat
+ 2009-07-14 04:54 . 2011-06-27 04:01	32768			  c:\windows\SysWOW64\config\systemprofile\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\index.dat
- 2009-07-14 04:54 . 2011-06-25 18:26	16384			  c:\windows\SysWOW64\config\systemprofile\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2009-07-14 04:54 . 2011-06-27 04:01	16384			  c:\windows\SysWOW64\config\systemprofile\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2009-07-14 05:10 . 2011-06-26 15:29	50662			  c:\windows\system32\wdi\BootPerformanceDiagnostics_SystemData.bin
+ 2010-04-18 09:23 . 2011-06-25 19:19	16384			  c:\windows\system32\config\systemprofile\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
- 2010-04-18 09:23 . 2011-06-19 00:47	16384			  c:\windows\system32\config\systemprofile\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
+ 2011-06-25 19:19 . 2011-06-25 19:19	49152			  c:\windows\system32\config\systemprofile\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\index.dat
- 2009-07-14 04:54 . 2011-06-19 00:47	16384			  c:\windows\system32\config\systemprofile\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2009-07-14 04:54 . 2011-06-25 19:19	16384			  c:\windows\system32\config\systemprofile\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2010-04-30 01:54 . 2011-06-27 04:02	16384			  c:\windows\ServiceProfiles\NetworkService\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
- 2010-04-30 01:54 . 2011-06-25 18:26	16384			  c:\windows\ServiceProfiles\NetworkService\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
- 2010-04-30 01:54 . 2011-06-25 18:26	32768			  c:\windows\ServiceProfiles\NetworkService\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\index.dat
+ 2010-04-30 01:54 . 2011-06-27 04:02	32768			  c:\windows\ServiceProfiles\NetworkService\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\index.dat
- 2010-04-30 01:54 . 2011-06-25 18:26	16384			  c:\windows\ServiceProfiles\NetworkService\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2010-04-30 01:54 . 2011-06-27 04:02	16384			  c:\windows\ServiceProfiles\NetworkService\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2010-04-30 01:44 . 2011-06-27 04:02	16384			  c:\windows\ServiceProfiles\LocalService\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
- 2010-04-30 01:44 . 2011-06-25 18:26	16384			  c:\windows\ServiceProfiles\LocalService\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
+ 2010-04-30 01:44 . 2011-06-27 04:02	16384			  c:\windows\ServiceProfiles\LocalService\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
- 2010-04-30 01:44 . 2011-06-25 18:26	16384			  c:\windows\ServiceProfiles\LocalService\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2010-04-30 01:49 . 2011-06-26 15:29	9772			  c:\windows\system32\wdi\{86432a0b-3c7d-4ddf-a89c-172faa90485d}\S-1-5-21-2937608809-329454621-2673834345-1000_UserData.bin
+ 2011-06-27 04:01 . 2011-06-27 04:01	2048			  c:\windows\ServiceProfiles\LocalService\AppData\Local\lastalive1.dat
- 2011-06-25 18:25 . 2011-06-25 18:25	2048			  c:\windows\ServiceProfiles\LocalService\AppData\Local\lastalive1.dat
+ 2011-06-27 04:01 . 2011-06-27 04:01	2048			  c:\windows\ServiceProfiles\LocalService\AppData\Local\lastalive0.dat
- 2011-06-25 18:25 . 2011-06-25 18:25	2048			  c:\windows\ServiceProfiles\LocalService\AppData\Local\lastalive0.dat
+ 2010-04-30 15:29 . 2011-06-26 02:07	394924			  c:\windows\system32\wdi\SuspendPerformanceDiagnostics_SystemData_S3.bin
- 2009-07-14 05:01 . 2011-06-25 18:24	537116			  c:\windows\ServiceProfiles\LocalService\AppData\Local\FontCache-System.dat
+ 2009-07-14 05:01 . 2011-06-27 04:00	537116			  c:\windows\ServiceProfiles\LocalService\AppData\Local\FontCache-System.dat
- 2011-06-21 12:18 . 2011-06-25 18:24	847936			  c:\windows\ServiceProfiles\LocalService\AppData\Local\FontCache-S-1-5-21-2937608809-329454621-2673834345-1000-12288.dat
+ 2011-06-21 12:18 . 2011-06-27 04:00	847936			  c:\windows\ServiceProfiles\LocalService\AppData\Local\FontCache-S-1-5-21-2937608809-329454621-2673834345-1000-12288.dat
- 2009-07-14 02:34 . 2011-06-24 23:22	10485760			  c:\windows\system32\SMI\Store\Machine\SCHEMA.DAT
+ 2009-07-14 02:34 . 2011-06-26 15:42	10485760			  c:\windows\system32\SMI\Store\Machine\SCHEMA.DAT
.
(((((((((((((((((((((((((((((((((((((   Reg Loading Points   ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown 
REGEDIT4
.
[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"Steam"="c:\program files (x86)\steam\steam.exe" [2010-11-17 1242448]
"Pando Media Booster"="c:\program files (x86)\Pando Networks\Media Booster\PMB.exe" [2010-09-26 2969496]
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run]
"HPCam_Menu"="c:\program files (x86)\Hewlett-Packard\Media\Webcam\MUITransfer\MUIStartMenu.exe" [2009-05-20 222504]
"Corel File Shell Monitor"="c:\program files (x86)\Corel\Corel Paint Shop Pro Photo X2\CorelIOMonitor.exe" [2009-08-26 15544]
"WirelessAssistant"="c:\program files (x86)\Hewlett-Packard\HP Wireless Assistant\HPWAMain.exe" [2009-07-23 498744]
"PWRISOVM.EXE"="c:\program files (x86)\PowerISO\PWRISOVM.EXE" [2009-03-15 180224]
"SwitchBoard"="c:\program files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe" [2010-02-19 517096]
"AdobeCS5ServiceManager"="c:\program files (x86)\Common Files\Adobe\CS5ServiceManager\CS5ServiceManager.exe" [2010-02-22 406992]
"lxdnmon.exe"="c:\program files (x86) (x86)\Lexmark 2600 Series\lxdnmon.exe" [2010-02-04 660136]
"EzPrint"="c:\program files (x86) (x86)\Lexmark 2600 Series\ezprint.exe" [2010-02-04 107176]
"DpAgent"="c:\program files (x86)\DigitalPersona\Bin\dpagent.exe" [2009-12-01 842816]
"HP Software Update"="c:\program files (x86)\Hp\HP Software Update\HPWuSchd2.exe" [2010-06-10 49208]
"BCSSync"="c:\program files (x86)\Microsoft Office\Office14\BCSSync.exe" [2010-03-13 91520]
"iTunesHelper"="c:\program files (x86)\iTunes\iTunesHelper.exe" [2011-04-27 421160]
"Adobe ARM"="c:\program files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe" [2011-06-06 937920]
.
c:\users\Nsnd\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\
GoZone iSync.lnk - c:\program files (x86)\GoZone\GoZone_iSync.exe [2011-5-18 431608]
OneNote 2010 Screen Clipper and Launcher.lnk - c:\program files (x86)\Microsoft Office\Office14\ONENOTEM.EXE [2010-3-29 227712]
.
[HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\policies\system]
"ConsentPromptBehaviorAdmin"= 0 (0x0)
"ConsentPromptBehaviorUser"= 3 (0x3)
"EnableLUA"= 0 (0x0)
"EnableUIADesktopToggle"= 0 (0x0)
"PromptOnSecureDesktop"= 0 (0x0)
.
[HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\windows nt\currentversion\drivers32]
"aux"=wdmaud.drv
.
[HKEY_LOCAL_MACHINE\system\currentcontrolset\control\lsa]
Security Packages	REG_MULTI_SZ   	kerberos msv1_0 schannel wdigest tspkg pku2u livessp
.
R2 clr_optimization_v4.0.30319_32;Microsoft .NET Framework NGEN v4.0.30319_X86;c:\windows\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe [2010-03-18 130384]
R2 clr_optimization_v4.0.30319_64;Microsoft .NET Framework NGEN v4.0.30319_X64;c:\windows\Microsoft.NET\Framework64\v4.0.30319\mscorsvw.exe [2010-03-18 138576]
R2 gupdate;Google Update Service (gupdate);c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-04-30 133104]
R2 HssWd;Hotspot Shield Monitoring Service;c:\program files (x86)\Hotspot Shield\bin\hsswd.exe [x]
R3 dc3d;MS Hardware Device Detection Driver (HID);c:\windows\system32\DRIVERS\dc3d.sys [x]
R3 gupdatem;Google Update Service (gupdatem);c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-04-30 133104]
R3 Microsoft SharePoint Workspace Audit Service;Microsoft SharePoint Workspace Audit Service;c:\program files (x86)\Microsoft Office\Office14\GROOVE.EXE [2010-03-25 30969208]
R3 netw5v64;Intel(R) Wireless WiFi Link 5000 Series Adapter Driver for Windows Vista 64 Bit;c:\windows\system32\DRIVERS\netw5v64.sys [x]
R3 osppsvc;Office Software Protection Platform;c:\program files\Common Files\Microsoft Shared\OfficeSoftwareProtectionPlatform\OSPPSVC.EXE [2010-01-10 4925184]
R3 pnetmdm;PdaNet Modem;c:\windows\system32\DRIVERS\pnetmdm64.sys [x]
R3 RTL8167;Realtek 8167 NT Driver;c:\windows\system32\DRIVERS\Rt64win7.sys [x]
R3 SrvHsfHDA;SrvHsfHDA;c:\windows\system32\DRIVERS\VSTAZL6.SYS [x]
R3 SrvHsfV92;SrvHsfV92;c:\windows\system32\DRIVERS\VSTDPV6.SYS [x]
R3 SrvHsfWinac;SrvHsfWinac;c:\windows\system32\DRIVERS\VSTCNXT6.SYS [x]
R3 SwitchBoard;Adobe SwitchBoard;c:\program files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe [2010-02-19 517096]
R3 USBAAPL64;Apple Mobile USB Driver;c:\windows\system32\Drivers\usbaapl64.sys [x]
R3 WatAdminSvc;Windows Activation Technologies Service;c:\windows\system32\Wat\WatAdminSvc.exe [x]
R3 WDC_SAM;WD SCSI Pass Thru driver;c:\windows\system32\DRIVERS\wdcsam64.sys [x]
R3 X6va001;X6va001;c:\users\Nsnd\AppData\Local\Temp\0014B86.tmp [x]
R3 yukonw7;NDIS6.2 Miniport Driver for Marvell Yukon Ethernet Controller;c:\windows\system32\DRIVERS\yk62x64.sys [x]
R4 lxdn_device;lxdn_device;c:\windows\system32\lxdncoms.exe [2007-11-28 1039872]
S1 aswSnx;aswSnx; [x]
S1 aswSP;aswSP; [x]
S1 vwififlt;Virtual WiFi Filter Driver;c:\windows\system32\DRIVERS\vwififlt.sys [x]
S2 AdobeARMservice;Adobe Acrobat Update Service;c:\program files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [2011-06-06 64952]
S2 AESTFilters;Andrea ST Filters Service;c:\windows\System32\DriverStore\FileRepository\stwrt64.inf_amd64_neutral_ccf0dd3cb081af84\AESTSr64.exe [2009-03-02 89600]
S2 aswFsBlk;aswFsBlk; [x]
S2 aswMonFlt;aswMonFlt;c:\windows\system32\drivers\aswMonFlt.sys [x]
S2 hpsrv;HP Service;c:\windows\system32\Hpservice.exe [x]
S2 vcsFPService;Validity VCS Fingerprint Service;c:\windows\system32\vcsFPService.exe [2009-07-13 1924400]
S3 enecir;ENE CIR Receiver;c:\windows\system32\DRIVERS\enecir.sys [x]
S3 JMCR;JMCR;c:\windows\system32\DRIVERS\jmcr.sys [x]
S3 netr28ux;RT2870 USB Extensible Wireless LAN Card Driver;c:\windows\system32\DRIVERS\netr28ux.sys [x]
S3 NETw5s64;Intel(R) Wireless WiFi Link 5000 Series Adapter Driver for Windows 7 - 64 Bit;c:\windows\system32\DRIVERS\NETw5s64.sys [x]
S3 NVHDA;Service for NVIDIA High Definition Audio Driver;c:\windows\system32\drivers\nvhda64v.sys [x]
.
.
Contents of the 'Scheduled Tasks' folder
.
2011-06-27 c:\windows\Tasks\GoogleUpdateTaskMachineCore.job
- c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-04-30 02:48]
.
2011-06-27 c:\windows\Tasks\GoogleUpdateTaskMachineUA.job
- c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-04-30 02:48]
.
.
——— x86-64 ———–
.
.
[HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\00avast]
@="{472083B0-C522-11CF-8763-00608CC02F24}"
[HKEY_CLASSES_ROOT\CLSID\{472083B0-C522-11CF-8763-00608CC02F24}]
2011-05-10 12:10	134384	—-a-w-	c:\program files\Alwil Software\Avast5\ashShA64.dll
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SynTPEnh"="c:\program files (x86)\Synaptics\SynTP\SynTPEnh.exe" [BU]
"SysTrayApp"="c:\program files\IDT\WDM\sttray64.exe" [2009-07-22 450048]
"HPToneControl"="c:\program files\Hewlett-Packard\HPToneControl\HPTonectl.exe" [2009-07-24 99384]
"AdobeAAMUpdater-1.0"="c:\program files (x86)\Common Files\Adobe\OOBE\PDApp\UWA\UpdaterStartupUtility.exe" [2010-03-06 500208]
.
——- Supplementary Scan ——-
.
uStart Page = hxxp://apps.ko.com/myko
uLocal Page = c:\windows\system32\blank.htm
mLocal Page = c:\windows\SysWOW64\blank.htm
IE: E&xport; to Microsoft Excel - c:\progra~2\MICROS~4\Office14\EXCEL.EXE/3000
IE: Se&nd; to OneNote - c:\progra~2\MICROS~4\Office14\ONBttnIE.dll/105
TCP: DhcpNameServer = [removed] [removed] [removed]
.
- - - - ORPHANS REMOVED - - - -
.
WebBrowser-{604BC32A-9680-40D1-9AC6-E06B23A1BA4C} - (no file)
.
.
.
[HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\services\X6va001]
"ImagePath"="\??\c:\users\Nsnd\AppData\Local\Temp\0014B86.tmp"
.
——————— LOCKED REGISTRY KEYS ———————
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}]
@Denied: (A 2) (Everyone)
@="FlashBroker"
"LocalizedString"="@c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil10r_ActiveX.exe,-101"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\Elevation]
"Enabled"=dword:00000001
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\LocalServer32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil10r_ActiveX.exe"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\TypeLib]
@="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}]
@Denied: (A 2) (Everyone)
@="Shockwave Flash Object"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\InprocServer32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10r.ocx"
"ThreadingModel"="Apartment"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\MiscStatus]
@="0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ProgID]
@="ShockwaveFlash.ShockwaveFlash.10"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10r.ocx, 1"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\TypeLib]
@="{D27CDB6B-AE6D-11cf-96B8-444553540000}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\Version]
@="1.0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID]
@="ShockwaveFlash.ShockwaveFlash"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}]
@Denied: (A 2) (Everyone)
@="Macromedia Flash Factory Object"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\InprocServer32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10r.ocx"
"ThreadingModel"="Apartment"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ProgID]
@="FlashFactory.FlashFactory.1"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10r.ocx, 1"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\TypeLib]
@="{D27CDB6B-AE6D-11cf-96B8-444553540000}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\Version]
@="1.0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID]
@="FlashFactory.FlashFactory"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}]
@Denied: (A 2) (Everyone)
@="IFlashBroker4"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\ProxyStubClsid32]
@="{00020424-0000-0000-C000-000000000046}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\TypeLib]
@="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}"
"Version"="1.0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Office\Common\Smart Tag\Actions\{B7EFF951-E52F-45CC-9EF7-57124F2177CC}]
@Denied: (A) (Everyone)
"Solution"="{15727DE6-F92D-4E46-ACB4-0E2C58B31A18}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Schema Library\ActionsPane3]
@Denied: (A) (Everyone)
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Schema Library\ActionsPane3\0]
"Key"="ActionsPane3"
"Location"="c:\\Program Files (x86)\\Common Files\\Microsoft Shared\\VSTO\\ActionsPane3.xsd"
.
[HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\PCW\Security]
@Denied: (Full) (Everyone)
.
———————— Other Running Processes ————————
.
c:\program files\Alwil Software\Avast5\AvastSvc.exe
c:\program files (x86)\DigitalPersona\Bin\DpHostW.exe
c:\program files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
c:\program files (x86)\Bonjour\mDNSResponder.exe
c:\program files (x86)\Common Files\Protexis\License Service\PsiService_2.exe
c:\program files (x86)\CyberLink\Shared files\RichVideo.exe
.
**************************************************************************
.
Completion time: 2011-06-26  21:09:30 - machine was rebooted
ComboFix-quarantined-files.txt  2011-06-27 04:09
ComboFix2.txt  2011-06-25 18:30
ComboFix3.txt  2011-06-19 22:13
.
Pre-Run: 188,785,639,424 bytes free
Post-Run: 188,499,021,824 bytes free
.
- - End Of File - - FEE2B4CC8DE44476FD273F83B159709E

I noticed something that I haven't done yet, and that's disable Window's Defender. Would this be something causing issues? I also ran Malwarebyte's and encountered the same update issues and the same little buggers that don't want to leave ( :angry: ) lol. Here's the Malwarebyte's log:

Malwarebytes' Anti-Malware 1.51.0.1200
www.malwarebytes.org

Database version: 6705

Windows 6.1.7600
Internet Explorer 8.0.7600.16385

6/27/2011 3:42:12 PM
mbam-log-2011-06-27 (15-42-09).txt

Scan type: Quick scan
Objects scanned: 178237
Time elapsed: 2 minute(s), 29 second(s)

Memory Processes Infected: 0
Memory Modules Infected: 0
Registry Keys Infected: 0
Registry Values Infected: 0
Registry Data Items Infected: 4
Folders Infected: 0
Files Infected: 0

Memory Processes Infected:
(No malicious items detected)

Memory Modules Infected:
(No malicious items detected)

Registry Keys Infected:
(No malicious items detected)

Registry Values Infected:
(No malicious items detected)

Registry Data Items Infected:
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\Tcpip\Parameters\DhcpNameServer (Trojan.DNSChanger) -> Bad: ([removed]) Good: () -> No action taken.
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\Tcpip\Parameters\Interfaces\{3062BD38-2304-43B6-9A1E-3E23CC9958DA}\DhcpNameServer (Trojan.DNSChanger) -> Bad: ([removed]) Good: () -> No action taken.

Folders Infected:
(No malicious items detected)

Files Infected:
(No malicious items detected)

I had to save the log file to my computer because I couldn't find it in the other location. Thanks again for all the help :thumbup: .
So, you are still unable to update MBAM and those entries wont be removed.

Please use the instructions on this page to change your DNS servers to use OpenDNS

OpenDNS

After this, flush the DNS cache and web browser cache as recommended and try to update MBAM. If you succed, perform a new scan with the same instructions I gave you above.
Ok, so the OpenDNS worked. I was able to update Malwarebyte's and my Avast. When I ran ComboFix this time, it asked to update (it did the last time, but I said no). I performed the update this time (hopefully that was ok). It restarted and here's the log:

ComboFix 11-06-27.03 - Nsnd 06/27/2011  20:50:11.3.8 - x64
Microsoft Windows 7 Home Premium   6.1.7600.0.1252.1.1033.18.6135.4233 [GMT -7:00]
Running from: c:\users\[removed]\Desktop\landscape.exe
Command switches used :: c:\users\Nsnd\Desktop\CFScript.txt
AV: avast! Antivirus *Disabled/Updated* {2B2D1395-420B-D5C9-657E-930FE358FC3C}
SP: avast! Antivirus *Disabled/Updated* {904CF271-6431-DA47-5FCE-A87D98DFB681}
SP: Windows Defender *Disabled/Updated* {D68DDC3A-831F-4fae-9E44-DA132C1ACF46}
.
.
(((((((((((((((((((((((((((((((((((((((   Other Deletions   )))))))))))))))))))))))))))))))))))))))))))))))))
.
.
c:\windows\system32\no
c:\windows\system32\no\DPCrProv.dll.mui
c:\windows\system32\no\DPSDApi.dll.mui
c:\windows\SysWow64\no
c:\windows\SysWow64\no\DPCrProv.dll.mui
c:\windows\SysWow64\no\DPSDApi.dll.mui
.
.
(((((((((((((((((((((((((   Files Created from 2011-05-28 to 2011-06-28  )))))))))))))))))))))))))))))))
.
.
2011-06-28 03:54 . 2011-06-28 03:54	——–	d—–w-	c:\users\Megan\AppData\Local\temp
2011-06-28 03:54 . 2011-06-28 03:54	——–	d—–w-	c:\users\Default\AppData\Local\temp
2011-06-28 03:48 . 2011-06-28 03:48	——–	d—–w-	C:\landscape
2011-06-28 03:32 . 2011-06-07 17:10	8873296	—-a-w-	c:\programdata\Microsoft\Windows Defender\Definition Updates\{A6AD078F-C623-4F48-9EA3-2A0B9F975FF7}\mpengine.dll
2011-06-25 21:42 . 2011-05-10 12:04	600920	—-a-w-	c:\windows\system32\drivers\aswSnx.sys
2011-06-24 22:57 . 2011-05-29 16:11	39984	—-a-w-	c:\windows\SysWow64\drivers\mbamswissarmy.sys
2011-06-24 22:57 . 2011-06-24 22:57	——–	d—–w-	c:\program files (x86)\Malwarebytes' Anti-Malware
2011-06-24 22:43 . 2011-06-24 22:43	——–	d—–w-	C:\_OTL
2011-06-21 02:46 . 2011-06-21 03:27	——–	d—–w-	C:\MGtools
2011-06-21 02:34 . 2011-06-21 02:34	——–	d—–w-	c:\programdata\SUPERAntiSpyware.com
2011-06-16 22:49 . 2011-05-28 03:25	1638912	—-a-w-	c:\windows\system32\mshtml.tlb
2011-06-12 23:26 . 2011-06-12 23:26	——–	d—–w-	c:\program files (x86)\Common Files\Java
2011-06-06 19:55 . 2011-06-06 19:55	183696	—-a-w-	c:\program files (x86)\Internet Explorer\Plugins\nppdf32.dll
2011-06-04 02:09 . 2011-06-04 02:09	——–	d—–w-	c:\users\Nsnd\AppData\Local\{BB8EFA2C-C894-49FD-91E5-0BE1B2962B73}
2011-06-03 02:36 . 2011-06-19 21:49	——–	d—–w-	c:\program files (x86)\Microsoft
2011-06-03 02:35 . 2011-06-25 04:00	——–	d—–w-	c:\program files (x86)\Unlocker
.
.
.
((((((((((((((((((((((((((((((((((((((((   Find3M Report   ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2011-06-21 03:27 . 2011-06-21 02:46	266209	—-a-w-	C:\MGlogs.zip
2011-06-19 06:08 . 2010-04-30 02:01	472808	—-a-w-	c:\windows\SysWow64\deployJava1.dll
2011-06-02 12:02 . 2011-05-13 01:12	404640	—-a-w-	c:\windows\SysWow64\FlashPlayerCPLApp.cpl
2011-05-29 16:11 . 2010-04-30 03:08	25912	—-a-w-	c:\windows\system32\drivers\mbam.sys
2011-05-25 02:14 . 2010-04-30 02:01	270720	——w-	c:\windows\system32\MpSigStub.exe
2011-05-10 12:10 . 2010-07-01 17:52	40112	—-a-w-	c:\windows\avastSS.scr
2011-05-10 12:10 . 2010-04-30 02:48	199304	—-a-w-	c:\windows\SysWow64\aswBoot.exe
2011-05-10 12:10 . 2011-01-18 09:22	253888	—-a-w-	c:\windows\system32\aswBoot.exe
2011-05-10 12:04 . 2010-04-30 02:48	287576	—-a-w-	c:\windows\system32\drivers\aswSP.sys
2011-05-10 12:02 . 2010-04-30 02:48	53592	—-a-w-	c:\windows\system32\drivers\aswTdi.sys
2011-05-10 11:59 . 2010-04-30 02:48	31064	—-a-w-	c:\windows\system32\drivers\aswRdr.sys
2011-05-10 11:59 . 2010-04-30 02:48	64344	—-a-w-	c:\windows\system32\drivers\aswMonFlt.sys
2011-05-10 11:59 . 2010-04-30 02:48	22360	—-a-w-	c:\windows\system32\drivers\aswFsBlk.sys
2011-04-22 20:18 . 2011-05-24 22:45	27008	—-a-w-	c:\windows\system32\drivers\Diskdump.sys
2011-04-10 16:36 . 2010-04-30 02:53	848	–sha-w-	c:\programdata\KGyGaAvL.sys
2011-04-09 06:58 . 2011-05-24 15:17	142336	—-a-w-	c:\windows\system32\poqexec.exe
2011-04-09 06:45 . 2011-05-12 02:53	5509504	—-a-w-	c:\windows\system32\ntoskrnl.exe
2011-04-09 06:13 . 2011-05-12 02:53	3957632	—-a-w-	c:\windows\SysWow64\ntkrnlpa.exe
2011-04-09 06:13 . 2011-05-12 02:53	3901824	—-a-w-	c:\windows\SysWow64\ntoskrnl.exe
2011-04-09 05:56 . 2011-05-24 15:17	123904	—-a-w-	c:\windows\SysWow64\poqexec.exe
2011-04-06 23:26 . 2011-04-06 23:26	96544	—-a-w-	c:\windows\system32\dnssd.dll
2011-04-06 23:26 . 2011-04-06 23:26	119584	—-a-w-	c:\windows\system32\dns-sd.exe
2011-04-06 23:20 . 2011-04-06 23:20	91424	—-a-w-	c:\windows\SysWow64\dnssd.dll
2011-04-06 23:20 . 2011-04-06 23:20	107808	—-a-w-	c:\windows\SysWow64\dns-sd.exe
.
.
(((((((((((((((((((((((((((((   SnapShot@2011-06-25_18.26.10   )))))))))))))))))))))))))))))))))))))))))
.
+ 2009-07-14 04:54 . 2011-06-28 03:56	16384			  c:\windows\SysWOW64\config\systemprofile\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
- 2009-07-14 04:54 . 2011-06-25 18:26	16384			  c:\windows\SysWOW64\config\systemprofile\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
- 2009-07-14 04:54 . 2011-06-25 18:26	32768			  c:\windows\SysWOW64\config\systemprofile\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\index.dat
+ 2009-07-14 04:54 . 2011-06-28 03:56	32768			  c:\windows\SysWOW64\config\systemprofile\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\index.dat
- 2009-07-14 04:54 . 2011-06-25 18:26	16384			  c:\windows\SysWOW64\config\systemprofile\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2009-07-14 04:54 . 2011-06-28 03:56	16384			  c:\windows\SysWOW64\config\systemprofile\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2009-11-18 17:31 . 2011-06-28 03:35	47796			  c:\windows\system32\wdi\ShutdownPerformanceDiagnostics_SystemData.bin
+ 2009-07-14 05:10 . 2011-06-28 03:35	50798			  c:\windows\system32\wdi\BootPerformanceDiagnostics_SystemData.bin
- 2010-04-18 09:23 . 2011-06-19 00:47	16384			  c:\windows\system32\config\systemprofile\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
+ 2010-04-18 09:23 . 2011-06-25 19:19	16384			  c:\windows\system32\config\systemprofile\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
+ 2011-06-25 19:19 . 2011-06-25 19:19	49152			  c:\windows\system32\config\systemprofile\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\index.dat
+ 2009-07-14 04:54 . 2011-06-25 19:19	16384			  c:\windows\system32\config\systemprofile\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
- 2009-07-14 04:54 . 2011-06-19 00:47	16384			  c:\windows\system32\config\systemprofile\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2010-04-30 01:54 . 2011-06-28 03:56	16384			  c:\windows\ServiceProfiles\NetworkService\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
- 2010-04-30 01:54 . 2011-06-25 18:26	16384			  c:\windows\ServiceProfiles\NetworkService\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
- 2010-04-30 01:54 . 2011-06-25 18:26	32768			  c:\windows\ServiceProfiles\NetworkService\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\index.dat
+ 2010-04-30 01:54 . 2011-06-28 03:56	32768			  c:\windows\ServiceProfiles\NetworkService\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\index.dat
- 2010-04-30 01:54 . 2011-06-25 18:26	16384			  c:\windows\ServiceProfiles\NetworkService\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2010-04-30 01:54 . 2011-06-28 03:56	16384			  c:\windows\ServiceProfiles\NetworkService\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2010-04-30 01:44 . 2011-06-28 03:56	16384			  c:\windows\ServiceProfiles\LocalService\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
- 2010-04-30 01:44 . 2011-06-25 18:26	16384			  c:\windows\ServiceProfiles\LocalService\AppData\Roaming\Microsoft\Windows\Cookies\index.dat
+ 2010-04-30 01:44 . 2011-06-28 03:56	16384			  c:\windows\ServiceProfiles\LocalService\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
- 2010-04-30 01:44 . 2011-06-25 18:26	16384			  c:\windows\ServiceProfiles\LocalService\AppData\Local\Microsoft\Windows\History\History.IE5\index.dat
+ 2010-06-25 22:54 . 2011-06-28 03:32	3030			  c:\windows\system32\wdi\ERCQueuedResolutions.dat
+ 2010-04-30 01:49 . 2011-06-28 03:35	9796			  c:\windows\system32\wdi\{86432a0b-3c7d-4ddf-a89c-172faa90485d}\S-1-5-21-2937608809-329454621-2673834345-1000_UserData.bin
- 2011-06-25 18:25 . 2011-06-25 18:25	2048			  c:\windows\ServiceProfiles\LocalService\AppData\Local\lastalive1.dat
+ 2011-06-28 03:55 . 2011-06-28 03:55	2048			  c:\windows\ServiceProfiles\LocalService\AppData\Local\lastalive1.dat
+ 2011-06-28 03:55 . 2011-06-28 03:55	2048			  c:\windows\ServiceProfiles\LocalService\AppData\Local\lastalive0.dat
- 2011-06-25 18:25 . 2011-06-25 18:25	2048			  c:\windows\ServiceProfiles\LocalService\AppData\Local\lastalive0.dat
+ 2010-04-30 15:29 . 2011-06-26 02:07	394924			  c:\windows\system32\wdi\SuspendPerformanceDiagnostics_SystemData_S3.bin
- 2009-07-14 05:01 . 2011-06-25 18:24	537116			  c:\windows\ServiceProfiles\LocalService\AppData\Local\FontCache-System.dat
+ 2009-07-14 05:01 . 2011-06-28 03:55	537116			  c:\windows\ServiceProfiles\LocalService\AppData\Local\FontCache-System.dat
+ 2011-06-21 12:18 . 2011-06-28 03:55	847936			  c:\windows\ServiceProfiles\LocalService\AppData\Local\FontCache-S-1-5-21-2937608809-329454621-2673834345-1000-12288.dat
- 2011-06-21 12:18 . 2011-06-25 18:24	847936			  c:\windows\ServiceProfiles\LocalService\AppData\Local\FontCache-S-1-5-21-2937608809-329454621-2673834345-1000-12288.dat
- 2009-07-14 02:34 . 2011-06-24 23:22	10485760			  c:\windows\system32\SMI\Store\Machine\SCHEMA.DAT
+ 2009-07-14 02:34 . 2011-06-28 03:50	10485760			  c:\windows\system32\SMI\Store\Machine\SCHEMA.DAT
.
(((((((((((((((((((((((((((((((((((((   Reg Loading Points   ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown 
REGEDIT4
.
[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"Steam"="c:\program files (x86)\steam\steam.exe" [2010-11-17 1242448]
"Pando Media Booster"="c:\program files (x86)\Pando Networks\Media Booster\PMB.exe" [2010-09-26 2969496]
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run]
"HPCam_Menu"="c:\program files (x86)\Hewlett-Packard\Media\Webcam\MUITransfer\MUIStartMenu.exe" [2009-05-20 222504]
"Corel File Shell Monitor"="c:\program files (x86)\Corel\Corel Paint Shop Pro Photo X2\CorelIOMonitor.exe" [2009-08-26 15544]
"WirelessAssistant"="c:\program files (x86)\Hewlett-Packard\HP Wireless Assistant\HPWAMain.exe" [2009-07-23 498744]
"PWRISOVM.EXE"="c:\program files (x86)\PowerISO\PWRISOVM.EXE" [2009-03-15 180224]
"SwitchBoard"="c:\program files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe" [2010-02-19 517096]
"AdobeCS5ServiceManager"="c:\program files (x86)\Common Files\Adobe\CS5ServiceManager\CS5ServiceManager.exe" [2010-02-22 406992]
"lxdnmon.exe"="c:\program files (x86) (x86)\Lexmark 2600 Series\lxdnmon.exe" [2010-02-04 660136]
"EzPrint"="c:\program files (x86) (x86)\Lexmark 2600 Series\ezprint.exe" [2010-02-04 107176]
"DpAgent"="c:\program files (x86)\DigitalPersona\Bin\dpagent.exe" [2009-12-01 842816]
"HP Software Update"="c:\program files (x86)\Hp\HP Software Update\HPWuSchd2.exe" [2010-06-10 49208]
"BCSSync"="c:\program files (x86)\Microsoft Office\Office14\BCSSync.exe" [2010-03-13 91520]
"iTunesHelper"="c:\program files (x86)\iTunes\iTunesHelper.exe" [2011-04-27 421160]
"Adobe ARM"="c:\program files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe" [2011-06-06 937920]
.
c:\users\Nsnd\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\
GoZone iSync.lnk - c:\program files (x86)\GoZone\GoZone_iSync.exe [2011-5-18 431608]
OneNote 2010 Screen Clipper and Launcher.lnk - c:\program files (x86)\Microsoft Office\Office14\ONENOTEM.EXE [2010-3-29 227712]
.
[HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\policies\system]
"ConsentPromptBehaviorAdmin"= 0 (0x0)
"ConsentPromptBehaviorUser"= 3 (0x3)
"EnableLUA"= 0 (0x0)
"EnableUIADesktopToggle"= 0 (0x0)
"PromptOnSecureDesktop"= 0 (0x0)
.
[HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\windows nt\currentversion\drivers32]
"aux"=wdmaud.drv
.
[HKEY_LOCAL_MACHINE\system\currentcontrolset\control\lsa]
Security Packages	REG_MULTI_SZ   	kerberos msv1_0 schannel wdigest tspkg pku2u livessp
.
R2 clr_optimization_v4.0.30319_32;Microsoft .NET Framework NGEN v4.0.30319_X86;c:\windows\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe [2010-03-18 130384]
R2 clr_optimization_v4.0.30319_64;Microsoft .NET Framework NGEN v4.0.30319_X64;c:\windows\Microsoft.NET\Framework64\v4.0.30319\mscorsvw.exe [2010-03-18 138576]
R2 gupdate;Google Update Service (gupdate);c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-04-30 133104]
R2 HssWd;Hotspot Shield Monitoring Service;c:\program files (x86)\Hotspot Shield\bin\hsswd.exe [x]
R3 dc3d;MS Hardware Device Detection Driver (HID);c:\windows\system32\DRIVERS\dc3d.sys [x]
R3 gupdatem;Google Update Service (gupdatem);c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-04-30 133104]
R3 Microsoft SharePoint Workspace Audit Service;Microsoft SharePoint Workspace Audit Service;c:\program files (x86)\Microsoft Office\Office14\GROOVE.EXE [2010-03-25 30969208]
R3 netw5v64;Intel(R) Wireless WiFi Link 5000 Series Adapter Driver for Windows Vista 64 Bit;c:\windows\system32\DRIVERS\netw5v64.sys [x]
R3 osppsvc;Office Software Protection Platform;c:\program files\Common Files\Microsoft Shared\OfficeSoftwareProtectionPlatform\OSPPSVC.EXE [2010-01-10 4925184]
R3 pnetmdm;PdaNet Modem;c:\windows\system32\DRIVERS\pnetmdm64.sys [x]
R3 RTL8167;Realtek 8167 NT Driver;c:\windows\system32\DRIVERS\Rt64win7.sys [x]
R3 SrvHsfHDA;SrvHsfHDA;c:\windows\system32\DRIVERS\VSTAZL6.SYS [x]
R3 SrvHsfV92;SrvHsfV92;c:\windows\system32\DRIVERS\VSTDPV6.SYS [x]
R3 SrvHsfWinac;SrvHsfWinac;c:\windows\system32\DRIVERS\VSTCNXT6.SYS [x]
R3 SwitchBoard;Adobe SwitchBoard;c:\program files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe [2010-02-19 517096]
R3 USBAAPL64;Apple Mobile USB Driver;c:\windows\system32\Drivers\usbaapl64.sys [x]
R3 WatAdminSvc;Windows Activation Technologies Service;c:\windows\system32\Wat\WatAdminSvc.exe [x]
R3 WDC_SAM;WD SCSI Pass Thru driver;c:\windows\system32\DRIVERS\wdcsam64.sys [x]
R3 X6va001;X6va001;c:\users\Nsnd\AppData\Local\Temp\0014B86.tmp [x]
R3 yukonw7;NDIS6.2 Miniport Driver for Marvell Yukon Ethernet Controller;c:\windows\system32\DRIVERS\yk62x64.sys [x]
R4 lxdn_device;lxdn_device;c:\windows\system32\lxdncoms.exe [2007-11-28 1039872]
S1 aswSnx;aswSnx; [x]
S1 aswSP;aswSP; [x]
S1 vwififlt;Virtual WiFi Filter Driver;c:\windows\system32\DRIVERS\vwififlt.sys [x]
S2 AdobeARMservice;Adobe Acrobat Update Service;c:\program files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [2011-06-06 64952]
S2 AESTFilters;Andrea ST Filters Service;c:\windows\System32\DriverStore\FileRepository\stwrt64.inf_amd64_neutral_ccf0dd3cb081af84\AESTSr64.exe [2009-03-02 89600]
S2 aswFsBlk;aswFsBlk; [x]
S2 aswMonFlt;aswMonFlt;c:\windows\system32\drivers\aswMonFlt.sys [x]
S2 hpsrv;HP Service;c:\windows\system32\Hpservice.exe [x]
S2 vcsFPService;Validity VCS Fingerprint Service;c:\windows\system32\vcsFPService.exe [2009-07-13 1924400]
S3 enecir;ENE CIR Receiver;c:\windows\system32\DRIVERS\enecir.sys [x]
S3 JMCR;JMCR;c:\windows\system32\DRIVERS\jmcr.sys [x]
S3 netr28ux;RT2870 USB Extensible Wireless LAN Card Driver;c:\windows\system32\DRIVERS\netr28ux.sys [x]
S3 NETw5s64;Intel(R) Wireless WiFi Link 5000 Series Adapter Driver for Windows 7 - 64 Bit;c:\windows\system32\DRIVERS\NETw5s64.sys [x]
S3 NVHDA;Service for NVIDIA High Definition Audio Driver;c:\windows\system32\drivers\nvhda64v.sys [x]
.
.
Contents of the 'Scheduled Tasks' folder
.
2011-06-28 c:\windows\Tasks\GoogleUpdateTaskMachineCore.job
- c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-04-30 02:48]
.
2011-06-28 c:\windows\Tasks\GoogleUpdateTaskMachineUA.job
- c:\program files (x86)\Google\Update\GoogleUpdate.exe [2010-04-30 02:48]
.
.
——— x86-64 ———–
.
.
[HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\explorer\shelliconoverlayidentifiers\00avast]
@="{472083B0-C522-11CF-8763-00608CC02F24}"
[HKEY_CLASSES_ROOT\CLSID\{472083B0-C522-11CF-8763-00608CC02F24}]
2011-05-10 12:10	134384	—-a-w-	c:\program files\Alwil Software\Avast5\ashShA64.dll
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"SynTPEnh"="c:\program files (x86)\Synaptics\SynTP\SynTPEnh.exe" [BU]
"SysTrayApp"="c:\program files\IDT\WDM\sttray64.exe" [2009-07-22 450048]
"HPToneControl"="c:\program files\Hewlett-Packard\HPToneControl\HPTonectl.exe" [2009-07-24 99384]
"AdobeAAMUpdater-1.0"="c:\program files (x86)\Common Files\Adobe\OOBE\PDApp\UWA\UpdaterStartupUtility.exe" [2010-03-06 500208]
.
——- Supplementary Scan ——-
.
uStart Page = hxxp://apps.ko.com/myko
uLocal Page = c:\windows\system32\blank.htm
mLocal Page = c:\windows\SysWOW64\blank.htm
IE: E&xport; to Microsoft Excel - c:\progra~2\MICROS~4\Office14\EXCEL.EXE/3000
IE: Se&nd; to OneNote - c:\progra~2\MICROS~4\Office14\ONBttnIE.dll/105
TCP: DhcpNameServer = [removed] [removed] [removed]
TCP: Interfaces\{3062BD38-2304-43B6-9A1E-3E23CC9958DA}: NameServer = 208.67.222.222,208.67.220.220
.
- - - - ORPHANS REMOVED - - - -
.
WebBrowser-{604BC32A-9680-40D1-9AC6-E06B23A1BA4C} - (no file)
.
.
.
[HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\services\X6va001]
"ImagePath"="\??\c:\users\Nsnd\AppData\Local\Temp\0014B86.tmp"
.
——————— LOCKED REGISTRY KEYS ———————
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}]
@Denied: (A 2) (Everyone)
@="FlashBroker"
"LocalizedString"="@c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil10r_ActiveX.exe,-101"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\Elevation]
"Enabled"=dword:00000001
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\LocalServer32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil10r_ActiveX.exe"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\TypeLib]
@="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}]
@Denied: (A 2) (Everyone)
@="Shockwave Flash Object"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\InprocServer32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10r.ocx"
"ThreadingModel"="Apartment"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\MiscStatus]
@="0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ProgID]
@="ShockwaveFlash.ShockwaveFlash.10"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10r.ocx, 1"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\TypeLib]
@="{D27CDB6B-AE6D-11cf-96B8-444553540000}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\Version]
@="1.0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID]
@="ShockwaveFlash.ShockwaveFlash"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}]
@Denied: (A 2) (Everyone)
@="Macromedia Flash Factory Object"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\InprocServer32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10r.ocx"
"ThreadingModel"="Apartment"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ProgID]
@="FlashFactory.FlashFactory.1"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32]
@="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10r.ocx, 1"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\TypeLib]
@="{D27CDB6B-AE6D-11cf-96B8-444553540000}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\Version]
@="1.0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID]
@="FlashFactory.FlashFactory"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}]
@Denied: (A 2) (Everyone)
@="IFlashBroker4"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\ProxyStubClsid32]
@="{00020424-0000-0000-C000-000000000046}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\TypeLib]
@="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}"
"Version"="1.0"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Office\Common\Smart Tag\Actions\{B7EFF951-E52F-45CC-9EF7-57124F2177CC}]
@Denied: (A) (Everyone)
"Solution"="{15727DE6-F92D-4E46-ACB4-0E2C58B31A18}"
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Schema Library\ActionsPane3]
@Denied: (A) (Everyone)
.
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Schema Library\ActionsPane3\0]
"Key"="ActionsPane3"
"Location"="c:\\Program Files (x86)\\Common Files\\Microsoft Shared\\VSTO\\ActionsPane3.xsd"
.
[HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\PCW\Security]
@Denied: (Full) (Everyone)
.
———————— Other Running Processes ————————
.
c:\program files\Alwil Software\Avast5\AvastSvc.exe
c:\program files (x86)\DigitalPersona\Bin\DpHostW.exe
c:\program files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
c:\program files (x86)\Bonjour\mDNSResponder.exe
c:\program files (x86)\Common Files\Protexis\License Service\PsiService_2.exe
c:\program files (x86)\CyberLink\Shared files\RichVideo.exe
.
**************************************************************************
.
Completion time: 2011-06-27  21:03:27 - machine was rebooted
ComboFix-quarantined-files.txt  2011-06-28 04:03
ComboFix2.txt  2011-06-27 04:09
ComboFix3.txt  2011-06-25 18:30
ComboFix4.txt  2011-06-19 22:13
.
Pre-Run: 188,740,415,488 bytes free
Post-Run: 188,665,618,432 bytes free
.
- - End Of File - - 4345A0CD8192D140A46551028AC1D7DE

Here's the log for Malewarebyte's:

Malwarebytes' Anti-Malware 1.51.0.1200
www.malwarebytes.org

Database version: 6965

Windows 6.1.7600
Internet Explorer 8.0.7600.16385

6/27/2011 9:11:19 PM
mbam-log-2011-06-27 (21-11-19).txt

Scan type: Quick scan
Objects scanned: 182837
Time elapsed: 1 minute(s), 55 second(s)

Memory Processes Infected: 0
Memory Modules Infected: 0
Registry Keys Infected: 0
Registry Values Infected: 0
Registry Data Items Infected: 4
Folders Infected: 0
Files Infected: 0

Memory Processes Infected:
(No malicious items detected)

Memory Modules Infected:
(No malicious items detected)

Registry Keys Infected:
(No malicious items detected)

Registry Values Infected:
(No malicious items detected)

Registry Data Items Infected:
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\Tcpip\Parameters\DhcpNameServer (Trojan.DNSChanger) -> Bad: ([removed]) Good: () -> Quarantined and deleted successfully.
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\Tcpip\Parameters\Interfaces\{3062BD38-2304-43B6-9A1E-3E23CC9958DA}\DhcpNameServer (Trojan.DNSChanger) -> Bad: ([removed]) Good: () -> Quarantined and deleted successfully.

Folders Infected:
(No malicious items detected)

Files Infected:
(No malicious items detected)

These guys are holding on for dear life. :wall: Do I need to change the OpenDNS or will we be doing that later?
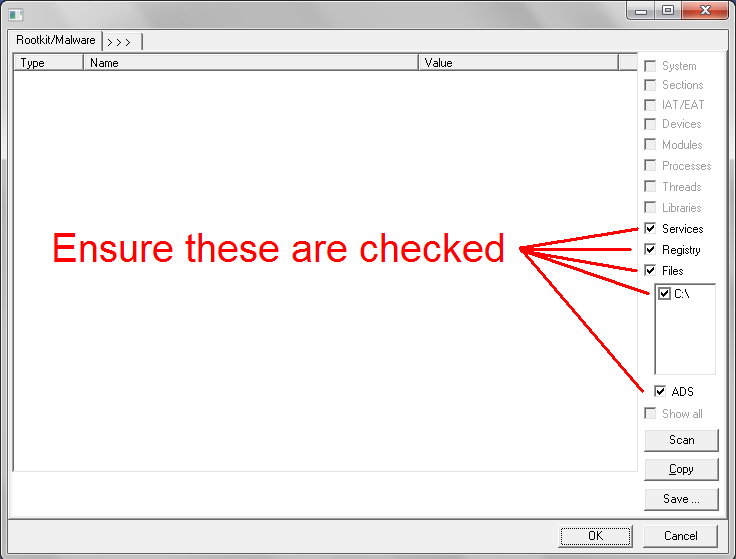
It seems that the entries were removed. You can always revert back to your original DNS server. However, I use OpenDNS myself and find it a great tool. I'll suggest you to keep it. Please run DDS again and post a new log.
Here's the log:

.
DDS (Ver_2011-06-12.02) - NTFSAMD64 
Internet Explorer: 8.0.7600.16385
Run by [removed] at 23:08:07 on 2011-06-29
Microsoft Windows 7 Home Premium   6.1.7600.0.1252.1.1033.18.6135.4435 [GMT -7:00]
.
AV: avast! Antivirus *Disabled/Updated* {2B2D1395-420B-D5C9-657E-930FE358FC3C}
SP: avast! Antivirus *Disabled/Updated* {904CF271-6431-DA47-5FCE-A87D98DFB681}
SP: Windows Defender *Disabled/Updated* {D68DDC3A-831F-4fae-9E44-DA132C1ACF46}
.
============== Running Processes ===============
.
C:\Windows\system32\wininit.exe
C:\Windows\system32\lsm.exe
C:\Windows\system32\svchost.exe -k DcomLaunch
C:\Windows\system32\nvvsvc.exe
C:\Windows\system32\svchost.exe -k RPCSS
C:\Windows\System32\svchost.exe -k LocalServiceNetworkRestricted
C:\Windows\System32\svchost.exe -k LocalSystemNetworkRestricted
C:\Windows\system32\svchost.exe -k netsvcs
C:\Windows\System32\DriverStore\FileRepository\stwrt64.inf_amd64_neutral_ccf0dd3cb081af84\STacSV64.exe
C:\Windows\system32\svchost.exe -k LocalService
C:\Windows\system32\Hpservice.exe
C:\Windows\system32\vcsFPService.exe
C:\Windows\system32\svchost.exe -k NetworkService
C:\Program Files\Alwil Software\Avast5\AvastSvc.exe
C:\Windows\System32\spoolsv.exe
C:\Program Files (x86)\DigitalPersona\Bin\DpHostW.exe
C:\Windows\system32\svchost.exe -k LocalServiceNoNetwork
C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe
C:\Windows\System32\DriverStore\FileRepository\stwrt64.inf_amd64_neutral_ccf0dd3cb081af84\AESTSr64.exe
C:\Program Files (x86)\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe
C:\Program Files (x86)\Bonjour\mDNSResponder.exe
C:\Windows\system32\svchost.exe -k LocalServiceAndNoImpersonation
C:\Program Files (x86)\Common Files\Protexis\License Service\PsiService_2.exe
C:\Program Files (x86)\CyberLink\Shared files\RichVideo.exe
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSVC.EXE
C:\Program Files\Common Files\Microsoft Shared\Windows Live\WLIDSvcM.exe
C:\Windows\system32\svchost.exe -k NetworkServiceNetworkRestricted
C:\Windows\system32\nvvsvc.exe
C:\Windows\system32\taskhost.exe
C:\Windows\system32\Dwm.exe
C:\Windows\Explorer.EXE
C:\Program Files\Synaptics\SynTP\SynTPEnh.exe
C:\Program Files\IDT\WDM\sttray64.exe
C:\Program Files\Hewlett-Packard\HPToneControl\HPToneCtl.exe
C:\Program Files\Synaptics\SynTP\SynTPHelper.exe
C:\Program Files (x86)\Corel\Corel Paint Shop Pro Photo X2\CorelIOMonitor.exe
C:\Program Files (x86)\Hewlett-Packard\HP Wireless Assistant\HPWAMain.exe
C:\Program Files (x86) (x86)\Lexmark 2600 Series\ezprint.exe
C:\Program Files (x86)\DigitalPersona\Bin\DpAgent.exe
C:\Program Files (x86)\HP\HP Software Update\hpwuschd2.exe
C:\Program Files (x86)\iTunes\iTunesHelper.exe
C:\Program Files\DigitalPersona\Bin\DPAgent.exe
C:\Windows\system32\svchost.exe -k imgsvc
C:\Program Files (x86)\Hewlett-Packard\Shared\hpqwmiex.exe
C:\Windows\system32\wbem\wmiprvse.exe
C:\Windows\system32\SearchIndexer.exe
C:\Program Files\iPod\bin\iPodService.exe
C:\Program Files (x86)\Hewlett-Packard\Shared\hpqToaster.exe
C:\Windows\System32\svchost.exe -k LocalServicePeerNet
C:\Program Files\Windows Media Player\wmpnetwk.exe
C:\Windows\system32\DllHost.exe
C:\Program Files\Alwil Software\Avast5\AvastUI.exe
C:\Windows\System32\svchost.exe -k secsvcs
C:\Program Files\Common Files\Microsoft Shared\OfficeSoftwareProtectionPlatform\OSPPSVC.EXE
C:\Windows\explorer.exe
C:\Windows\system32\taskeng.exe
C:\Windows\SysWOW64\ctfmon.exe
C:\Windows\SysWOW64\cmd.exe
C:\Windows\system32\conhost.exe
C:\Windows\SysWOW64\cscript.exe
C:\Windows\system32\wbem\wmiprvse.exe
.
============== Pseudo HJT Report ===============
.
uStart Page = hxxp://apps.ko.com/myko
BHO: HP Print Enhancer: {0347c33e-8762-4905-bf09-768834316c61} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_printenhancer.dll
BHO: Adobe PDF Link Helper: {18df081c-e8ad-4283-a596-fa578c2ebdc3} - C:\Program Files (x86)\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
BHO: DigitalPersona Personal Extension: {395610ae-c624-4f58-b89e-23733ea00f9a} - C:\Program Files (x86)\DigitalPersona\Bin\DpOtsPluginIe8.dll
BHO: Groove GFS Browser Helper: {72853161-30c5-4d22-b7f9-0bbc1d38a37e} - C:\PROGRA~2\MICROS~4\Office14\GROOVEEX.DLL
BHO: Windows Live ID Sign-in Helper: {9030d464-4c02-4abf-8ecc-5164760863c6} - C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
BHO: Office Document Cache Handler: {b4f3a835-0e21-4959-ba22-42b3008e02ff} - C:\PROGRA~2\MICROS~4\Office14\URLREDIR.DLL
BHO: Java™ Plug-In 2 SSV Helper: {dbc80044-a445-435b-bc74-9c25c1c588a9} - C:\Program Files (x86)\Java\jre6\bin\jp2ssv.dll
BHO: HP Smart BHO Class: {ffffffff-cf4e-4f2b-bdc2-0e72e116a856} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_BHO.dll
TB: {604BC32A-9680-40D1-9AC6-E06B23A1BA4C} - No File
EB: HP Smart Web Printing: {555d4d79-4bd2-4094-a395-cfc534424a05} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_bho.dll
uRun: [Steam] "c:\program files (x86)\steam\steam.exe" -silent
uRun: [Pando Media Booster] C:\Program Files (x86)\Pando Networks\Media Booster\PMB.exe
mRun: [HPCam_Menu] "c:\Program Files (x86)\Hewlett-Packard\Media\Webcam\MUITransfer\MUIStartMenu.exe" "c:\Program Files (x86)\Hewlett-Packard\Media\Webcam" UpdateWithCreateOnce "Software\Hewlett-Packard\Media\Webcam"
mRun: [Corel File Shell Monitor] C:\Program Files (x86)\Corel\Corel Paint Shop Pro Photo X2\CorelIOMonitor.exe
mRun: [WirelessAssistant] C:\Program Files (x86)\Hewlett-Packard\HP Wireless Assistant\HPWAMain.exe
mRun: [PWRISOVM.EXE] C:\Program Files (x86)\PowerISO\PWRISOVM.EXE
mRun: [SwitchBoard] C:\Program Files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe
mRun: [AdobeCS5ServiceManager] "C:\Program Files (x86)\Common Files\Adobe\CS5ServiceManager\CS5ServiceManager.exe" -launchedbylogin
mRun: [lxdnmon.exe] "C:\Program Files (x86) (x86)\Lexmark 2600 Series\lxdnmon.exe"
mRun: [EzPrint] "C:\Program Files (x86) (x86)\Lexmark 2600 Series\ezprint.exe"
mRun: [DpAgent] C:\Program Files (x86)\DigitalPersona\Bin\dpagent.exe
mRun: [HP Software Update] C:\Program Files (x86)\Hp\HP Software Update\HPWuSchd2.exe
mRun: [BCSSync] "C:\Program Files (x86)\Microsoft Office\Office14\BCSSync.exe" /DelayServices
mRun: [iTunesHelper] "C:\Program Files (x86)\iTunes\iTunesHelper.exe"
mRun: [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
StartupFolder: C:\Users\Nsnd\AppData\Roaming\MICROS~1\Windows\STARTM~1\Programs\Startup\GOZONE~1.LNK - C:\Program Files (x86)\GoZone\GoZone_iSync.exe
StartupFolder: C:\Users\Nsnd\AppData\Roaming\MICROS~1\Windows\STARTM~1\Programs\Startup\ONENOT~1.LNK - C:\Program Files (x86)\Microsoft Office\Office14\ONENOTEM.EXE
mPolicies-system: ConsentPromptBehaviorAdmin = 0 (0x0)
mPolicies-system: ConsentPromptBehaviorUser = 3 (0x3)
mPolicies-system: EnableLUA = 0 (0x0)
mPolicies-system: EnableUIADesktopToggle = 0 (0x0)
mPolicies-system: PromptOnSecureDesktop = 0 (0x0)
IE: E&xport to Microsoft Excel - C:\PROGRA~2\MICROS~4\Office14\EXCEL.EXE/3000
IE: Se&nd to OneNote - C:\PROGRA~2\MICROS~4\Office14\ONBttnIE.dll/105
IE: {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - {5F7B1267-94A9-47F5-98DB-E99415F33AEC} - C:\Program Files (x86)\Windows Live\Writer\WriterBrowserExtension.dll
IE: {2670000A-7350-4f3c-8081-5663EE0C6C49} - {48E73304-E1D6-4330-914C-F5F514E3486C} - C:\Program Files (x86)\Microsoft Office\Office14\ONBttnIE.dll
IE: {789FE86F-6FC4-46A1-9849-EDE0DB0C95CA} - {FFFDC614-B694-4AE6-AB38-5D6374584B52} - C:\Program Files (x86)\Microsoft Office\Office14\ONBttnIELinkedNotes.dll
IE: {DDE87865-83C5-48c4-8357-2F5B1AA84522} - {DDE87865-83C5-48c4-8357-2F5B1AA84522} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_BHO.dll
DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_26-windows-i586.cab
DPF: {983A9C21-8207-4B58-BBB8-0EBC3D7C5505} - hxxps://apps.ko.com/dwa8W.cab
DPF: {CAFEEFAC-0016-0000-0026-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_26-windows-i586.cab
DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_26-windows-i586.cab
TCP: DhcpNameServer = [removed] [removed] [removed]
TCP: Interfaces\{3062BD38-2304-43B6-9A1E-3E23CC9958DA} : NameServer = 208.67.222.222,208.67.220.220
TCP: Interfaces\{3062BD38-2304-43B6-9A1E-3E23CC9958DA} : DhcpNameServer = [removed] [removed] [removed]
TCP: Interfaces\{FDCF163F-51B4-4581-A901-82A4F4CA6B88}\35865636A797 : DhcpNameServer = [removed] [removed]
TCP: Interfaces\{FDCF163F-51B4-4581-A901-82A4F4CA6B88}\475747479602662757474796 : DhcpNameServer = 192.168.2.1
TCP: Interfaces\{FDCF163F-51B4-4581-A901-82A4F4CA6B88}\65562796A7F6E602D496649623230303025334230302355636572756 : DhcpNameServer = 192.168.1.1
Filter: text/xml - {807573E5-5146-11D5-A672-00B0D022E945} - C:\Program Files (x86)\Common Files\microsoft shared\OFFICE14\MSOXMLMF.DLL
Handler: wlpg - {E43EF6CD-A37A-4A9B-9E6F-83F89B8E6324} - C:\Program Files (x86)\Windows Live\Photo Gallery\AlbumDownloadProtocolHandler.dll
SEH: Groove GFS Stub Execution Hook: {b5a7f190-dda6-4420-b3ba-52453494e6cd} - C:\PROGRA~2\MICROS~4\Office14\GROOVEEX.DLL
BHO-X64: HP Print Enhancer: {0347C33E-8762-4905-BF09-768834316C61} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_printenhancer.dll
BHO-X64:	 HP Print Enhancer - No File
BHO-X64: Adobe PDF Link Helper: {18DF081C-E8AD-4283-A596-FA578C2EBDC3} - C:\Program Files (x86)\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
BHO-X64:	 AcroIEHelperStub - No File
BHO-X64: DigitalPersona Personal Extension: {395610AE-C624-4f58-B89E-23733EA00F9A} - C:\Program Files (x86)\DigitalPersona\Bin\DpOtsPluginIe8.dll
BHO-X64:	 DigitalPersona Personal Extension - No File
BHO-X64: Groove GFS Browser Helper: {72853161-30C5-4D22-B7F9-0BBC1D38A37E} - C:\PROGRA~2\MICROS~4\Office14\GROOVEEX.DLL
BHO-X64: Windows Live ID Sign-in Helper: {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files (x86)\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
BHO-X64: Office Document Cache Handler: {B4F3A835-0E21-4959-BA22-42B3008E02FF} - C:\PROGRA~2\MICROS~4\Office14\URLREDIR.DLL
BHO-X64:	 URLRedirectionBHO - No File
BHO-X64: Java™ Plug-In 2 SSV Helper: {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files (x86)\Java\jre6\bin\jp2ssv.dll
BHO-X64: HP Smart BHO Class: {FFFFFFFF-CF4E-4F2B-BDC2-0E72E116A856} - C:\Program Files (x86)\HP\Digital Imaging\Smart Web Printing\hpswp_BHO.dll
BHO-X64:	 HP Smart BHO Class - No File
TB-X64: {604BC32A-9680-40D1-9AC6-E06B23A1BA4C} - No File
EB-X64: {555D4D79-4BD2-4094-A395-CFC534424A05} - No File
mRun-x64: [HPCam_Menu] "c:\Program Files (x86)\Hewlett-Packard\Media\Webcam\MUITransfer\MUIStartMenu.exe" "c:\Program Files (x86)\Hewlett-Packard\Media\Webcam" UpdateWithCreateOnce "Software\Hewlett-Packard\Media\Webcam"
mRun-x64: [Corel File Shell Monitor] C:\Program Files (x86)\Corel\Corel Paint Shop Pro Photo X2\CorelIOMonitor.exe
mRun-x64: [WirelessAssistant] C:\Program Files (x86)\Hewlett-Packard\HP Wireless Assistant\HPWAMain.exe
mRun-x64: [PWRISOVM.EXE] C:\Program Files (x86)\PowerISO\PWRISOVM.EXE
mRun-x64: [SwitchBoard] C:\Program Files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe
mRun-x64: [AdobeCS5ServiceManager] "C:\Program Files (x86)\Common Files\Adobe\CS5ServiceManager\CS5ServiceManager.exe" -launchedbylogin
mRun-x64: [lxdnmon.exe] "C:\Program Files (x86) (x86)\Lexmark 2600 Series\lxdnmon.exe"
mRun-x64: [EzPrint] "C:\Program Files (x86) (x86)\Lexmark 2600 Series\ezprint.exe"
mRun-x64: [DpAgent] C:\Program Files (x86)\DigitalPersona\Bin\dpagent.exe
mRun-x64: [HP Software Update] C:\Program Files (x86)\Hp\HP Software Update\HPWuSchd2.exe
mRun-x64: [BCSSync] "C:\Program Files (x86)\Microsoft Office\Office14\BCSSync.exe" /DelayServices
mRun-x64: [iTunesHelper] "C:\Program Files (x86)\iTunes\iTunesHelper.exe"
mRun-x64: [Adobe ARM] "C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
SEH-X64: Groove GFS Stub Execution Hook: {B5A7F190-DDA6-4420-B3BA-52453494E6CD} - C:\PROGRA~2\MICROS~4\Office14\GROOVEEX.DLL
.
============= SERVICES / DRIVERS ===============
.
R1 aswSnx;aswSnx;C:\Windows\system32\drivers\aswSnx.sys –> C:\Windows\system32\drivers\aswSnx.sys [?]
R1 aswSP;aswSP;C:\Windows\system32\drivers\aswSP.sys –> C:\Windows\system32\drivers\aswSP.sys [?]
R1 vwififlt;Virtual WiFi Filter Driver;C:\Windows\system32\DRIVERS\vwififlt.sys –> C:\Windows\system32\DRIVERS\vwififlt.sys [?]
R2 AdobeARMservice;Adobe Acrobat Update Service;C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [2011-6-6 64952]
R2 AESTFilters;Andrea ST Filters Service;C:\Windows\System32\DriverStore\FileRepository\stwrt64.inf_amd64_neutral_ccf0dd3cb081af84\AESTSr64.exe [2010-4-18 89600]
R2 aswFsBlk;aswFsBlk;C:\Windows\system32\drivers\aswFsBlk.sys –> C:\Windows\system32\drivers\aswFsBlk.sys [?]
R2 aswMonFlt;aswMonFlt;\??\C:\Windows\system32\drivers\aswMonFlt.sys –> C:\Windows\system32\drivers\aswMonFlt.sys [?]
R2 avast! Antivirus;avast! Antivirus;C:\Program Files\Alwil Software\Avast5\AvastSvc.exe [2011-6-25 42184]
R2 hpsrv;HP Service;C:\Windows\system32\Hpservice.exe –> C:\Windows\system32\Hpservice.exe [?]
R2 vcsFPService;Validity VCS Fingerprint Service;C:\Windows\System32\vcsFPService.exe [2009-7-12 1656112]
R3 enecir;ENE CIR Receiver;C:\Windows\system32\DRIVERS\enecir.sys –> C:\Windows\system32\DRIVERS\enecir.sys [?]
R3 JMCR;JMCR;C:\Windows\system32\DRIVERS\jmcr.sys –> C:\Windows\system32\DRIVERS\jmcr.sys [?]
R3 netr28ux;RT2870 USB Extensible Wireless LAN Card Driver;C:\Windows\system32\DRIVERS\netr28ux.sys –> C:\Windows\system32\DRIVERS\netr28ux.sys [?]
R3 NETw5s64;Intel(R) Wireless WiFi Link 5000 Series Adapter Driver for Windows 7 - 64 Bit;C:\Windows\system32\DRIVERS\NETw5s64.sys –> C:\Windows\system32\DRIVERS\NETw5s64.sys [?]
R3 NVHDA;Service for NVIDIA High Definition Audio Driver;C:\Windows\system32\drivers\nvhda64v.sys –> C:\Windows\system32\drivers\nvhda64v.sys [?]
R3 osppsvc;Office Software Protection Platform;C:\Program Files\Common Files\Microsoft Shared\OfficeSoftwareProtectionPlatform\OSPPSVC.EXE [2010-1-9 4925184]
S2 clr_optimization_v4.0.30319_32;Microsoft .NET Framework NGEN v4.0.30319_X86;C:\Windows\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe [2010-3-18 130384]
S2 clr_optimization_v4.0.30319_64;Microsoft .NET Framework NGEN v4.0.30319_X64;C:\Windows\Microsoft.NET\Framework64\v4.0.30319\mscorsvw.exe [2010-3-18 138576]
S2 gupdate;Google Update Service (gupdate);C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [2010-4-29 133104]
S2 HssWd;Hotspot Shield Monitoring Service;C:\Program Files (x86)\Hotspot Shield\bin\hsswd.exe -product HSS –> C:\Program Files (x86)\Hotspot Shield\bin\hsswd.exe -product HSS [?]
S3 gupdatem;Google Update Service (gupdatem);C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [2010-4-29 133104]
S3 Microsoft SharePoint Workspace Audit Service;Microsoft SharePoint Workspace Audit Service;C:\Program Files (x86)\Microsoft Office\Office14\GROOVE.EXE [2010-3-25 30969208]
S3 netw5v64;Intel(R) Wireless WiFi Link 5000 Series Adapter Driver for Windows Vista 64 Bit;C:\Windows\system32\DRIVERS\netw5v64.sys –> C:\Windows\system32\DRIVERS\netw5v64.sys [?]
S3 pnetmdm;PdaNet Modem;C:\Windows\system32\DRIVERS\pnetmdm64.sys –> C:\Windows\system32\DRIVERS\pnetmdm64.sys [?]
S3 RTL8167;Realtek 8167 NT Driver;C:\Windows\system32\DRIVERS\Rt64win7.sys –> C:\Windows\system32\DRIVERS\Rt64win7.sys [?]
S3 SrvHsfHDA;SrvHsfHDA;C:\Windows\system32\DRIVERS\VSTAZL6.SYS –> C:\Windows\system32\DRIVERS\VSTAZL6.SYS [?]
S3 SrvHsfV92;SrvHsfV92;C:\Windows\system32\DRIVERS\VSTDPV6.SYS –> C:\Windows\system32\DRIVERS\VSTDPV6.SYS [?]
S3 SrvHsfWinac;SrvHsfWinac;C:\Windows\system32\DRIVERS\VSTCNXT6.SYS –> C:\Windows\system32\DRIVERS\VSTCNXT6.SYS [?]
S3 SwitchBoard;Adobe SwitchBoard;C:\Program Files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe [2010-2-19 517096]
S3 USBAAPL64;Apple Mobile USB Driver;C:\Windows\system32\Drivers\usbaapl64.sys –> C:\Windows\system32\Drivers\usbaapl64.sys [?]
S3 WatAdminSvc;Windows Activation Technologies Service;C:\Windows\system32\Wat\WatAdminSvc.exe –> C:\Windows\system32\Wat\WatAdminSvc.exe [?]
S3 WDC_SAM;WD SCSI Pass Thru driver;C:\Windows\system32\DRIVERS\wdcsam64.sys –> C:\Windows\system32\DRIVERS\wdcsam64.sys [?]
S3 yukonw7;NDIS6.2 Miniport Driver for Marvell Yukon Ethernet Controller;C:\Windows\system32\DRIVERS\yk62x64.sys –> C:\Windows\system32\DRIVERS\yk62x64.sys [?]
S4 lxdn_device;lxdn_device;C:\Windows\system32\lxdncoms.exe -service –> C:\Windows\system32\lxdncoms.exe -service [?]
.
=============== Created Last 30 ================
.
2011-06-28 11:05:21	8873296	—-a-w-	C:\ProgramData\Microsoft\Windows Defender\Definition Updates\{28D6E827-6DC5-418A-8AF5-7ECDE73D8310}\mpengine.dll
2011-06-28 03:56:13	——–	d—–w-	C:\$RECYCLE.BIN
2011-06-28 03:48:21	——–	d—–w-	C:\landscape
2011-06-25 21:42:01	600920	—-a-w-	C:\Windows\System32\drivers\aswSnx.sys
2011-06-24 22:57:51	39984	—-a-w-	C:\Windows\SysWow64\drivers\mbamswissarmy.sys
2011-06-24 22:57:47	——–	d—–w-	C:\Program Files (x86)\Malwarebytes' Anti-Malware
2011-06-24 22:43:17	——–	d—–w-	C:\_OTL
2011-06-21 02:46:17	——–	d—–w-	C:\MGtools
2011-06-21 02:34:48	——–	d—–w-	C:\ProgramData\SUPERAntiSpyware.com
2011-06-19 21:59:20	98816	—-a-w-	C:\Windows\sed.exe
2011-06-19 21:59:20	518144	—-a-w-	C:\Windows\SWREG.exe
2011-06-19 21:59:20	256512	—-a-w-	C:\Windows\PEV.exe
2011-06-19 21:59:20	208896	—-a-w-	C:\Windows\MBR.exe
2011-06-06 19:55:30	183696	—-a-w-	C:\Program Files (x86)\Internet Explorer\Plugins\nppdf32.dll
2011-06-04 02:09:15	——–	d—–w-	C:\Users\Nsnd\AppData\Local\{BB8EFA2C-C894-49FD-91E5-0BE1B2962B73}
2011-06-03 02:36:13	——–	d—–w-	C:\Program Files (x86)\Microsoft
2011-06-03 02:35:49	——–	d—–w-	C:\Program Files (x86)\Unlocker
.
==================== Find3M  ====================
.
2011-06-19 06:08:13	472808	—-a-w-	C:\Windows\SysWow64\deployJava1.dll
2011-06-02 12:02:29	404640	—-a-w-	C:\Windows\SysWow64\FlashPlayerCPLApp.cpl
2011-05-29 16:11:20	25912	—-a-w-	C:\Windows\System32\drivers\mbam.sys
2011-05-28 03:25:16	1638912	—-a-w-	C:\Windows\System32\mshtml.tlb
2011-05-28 03:07:01	3133952	—-a-w-	C:\Windows\System32\win32k.sys
2011-05-28 03:00:02	1638912	—-a-w-	C:\Windows\SysWow64\mshtml.tlb
2011-05-25 02:14:10	270720	——w-	C:\Windows\System32\MpSigStub.exe
2011-05-24 11:21:59	404992	—-a-w-	C:\Windows\System32\umpnpmgr.dll
2011-05-24 10:34:20	64512	—-a-w-	C:\Windows\SysWow64\devobj.dll
2011-05-24 10:34:20	44544	—-a-w-	C:\Windows\SysWow64\devrtl.dll
2011-05-24 10:34:00	145920	—-a-w-	C:\Windows\SysWow64\cfgmgr32.dll
2011-05-24 10:32:46	252928	—-a-w-	C:\Windows\SysWow64\drvinst.exe
2011-05-10 12:10:59	40112	—-a-w-	C:\Windows\avastSS.scr
2011-05-10 11:59:48	64344	—-a-w-	C:\Windows\System32\drivers\aswMonFlt.sys
2011-05-04 05:30:38	2326016	—-a-w-	C:\Windows\System32\tquery.dll
2011-05-04 05:28:07	779264	—-a-w-	C:\Windows\System32\mssvp.dll
2011-05-04 05:28:07	2228224	—-a-w-	C:\Windows\System32\mssrch.dll
2011-05-04 05:28:06	75264	—-a-w-	C:\Windows\System32\msscntrs.dll
2011-05-04 05:28:06	491520	—-a-w-	C:\Windows\System32\mssph.dll
2011-05-04 05:28:06	288256	—-a-w-	C:\Windows\System32\mssphtb.dll
2011-05-04 05:24:09	593408	—-a-w-	C:\Windows\System32\SearchIndexer.exe
2011-05-04 05:24:09	249856	—-a-w-	C:\Windows\System32\SearchProtocolHost.exe
2011-05-04 05:24:09	113664	—-a-w-	C:\Windows\System32\SearchFilterHost.exe
2011-05-04 04:53:10	1553920	—-a-w-	C:\Windows\SysWow64\tquery.dll
2011-05-04 04:52:59	666624	—-a-w-	C:\Windows\SysWow64\mssvp.dll
2011-05-04 04:52:59	59392	—-a-w-	C:\Windows\SysWow64\msscntrs.dll
2011-05-04 04:52:59	337408	—-a-w-	C:\Windows\SysWow64\mssph.dll
2011-05-04 04:52:59	197120	—-a-w-	C:\Windows\SysWow64\mssphtb.dll
2011-05-04 04:52:59	1401856	—-a-w-	C:\Windows\SysWow64\mssrch.dll
2011-05-04 04:52:12	86528	—-a-w-	C:\Windows\SysWow64\SearchFilterHost.exe
2011-05-04 04:52:12	428032	—-a-w-	C:\Windows\SysWow64\SearchIndexer.exe
2011-05-04 04:52:12	164352	—-a-w-	C:\Windows\SysWow64\SearchProtocolHost.exe
2011-05-04 02:51:08	287744	—-a-w-	C:\Windows\System32\drivers\mrxsmb10.sys
2011-05-04 02:51:08	157696	—-a-w-	C:\Windows\System32\drivers\mrxsmb.sys
2011-05-04 02:51:05	126464	—-a-w-	C:\Windows\System32\drivers\mrxsmb20.sys
2011-05-03 05:21:22	976896	—-a-w-	C:\Windows\System32\inetcomm.dll
2011-05-03 04:50:29	740864	—-a-w-	C:\Windows\SysWow64\inetcomm.dll
2011-04-29 03:13:10	461312	—-a-w-	C:\Windows\System32\drivers\srv.sys
2011-04-29 03:12:54	399872	—-a-w-	C:\Windows\System32\drivers\srv2.sys
2011-04-29 03:12:37	161792	—-a-w-	C:\Windows\System32\drivers\srvnet.sys
2011-04-27 02:57:40	102400	—-a-w-	C:\Windows\System32\drivers\dfsc.sys
2011-04-25 05:32:22	1896832	—-a-w-	C:\Windows\System32\drivers\tcpip.sys
2011-04-25 02:44:02	499712	—-a-w-	C:\Windows\System32\drivers\afd.sys
2011-04-22 20:18:47	27008	—-a-w-	C:\Windows\System32\drivers\Diskdump.sys
2011-04-22 20:18:28	1197056	—-a-w-	C:\Windows\System32\wininet.dll
2011-04-22 20:14:08	57856	—-a-w-	C:\Windows\System32\licmgr10.dll
2011-04-22 19:31:50	981504	—-a-w-	C:\Windows\SysWow64\wininet.dll
2011-04-22 19:31:26	44544	—-a-w-	C:\Windows\SysWow64\licmgr10.dll
2011-04-22 18:49:57	482816	—-a-w-	C:\Windows\System32\html.iec
2011-04-22 18:23:59	386048	—-a-w-	C:\Windows\SysWow64\html.iec
2011-04-10 16:36:30	848	–sha-w-	C:\ProgramData\KGyGaAvL.sys
2011-04-09 06:58:56	142336	—-a-w-	C:\Windows\System32\poqexec.exe
2011-04-09 06:45:48	5509504	—-a-w-	C:\Windows\System32\ntoskrnl.exe
2011-04-09 06:13:06	3957632	—-a-w-	C:\Windows\SysWow64\ntkrnlpa.exe
2011-04-09 06:13:06	3901824	—-a-w-	C:\Windows\SysWow64\ntoskrnl.exe
2011-04-09 05:56:38	123904	—-a-w-	C:\Windows\SysWow64\poqexec.exe
2011-04-06 23:26:58	96544	—-a-w-	C:\Windows\System32\dnssd.dll
2011-04-06 23:26:58	119584	—-a-w-	C:\Windows\System32\dns-sd.exe
2011-04-06 23:20:16	91424	—-a-w-	C:\Windows\SysWow64\dnssd.dll
2011-04-06 23:20:16	107808	—-a-w-	C:\Windows\SysWow64\dns-sd.exe
.
============= FINISH: 23:08:38.93 ===============

And I've attached the other file as well. Should I run Malwarebyte's again or no?

Attachments:

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI