This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

Computer infected with fake "spyware protection" program

37 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

Please help! My home computer is infected with some type of virus/malware. It does start up, but will not run Firefox so I cannot get online. I cannot run any programs. A window keeps popping up stating that there is a security issue. The window looks quite official (like a Windows window), but it is for a program called "Spyware Protection" that we do not have. The window keeps prompting me to run the Spyware Protection program. I appreciate any help. Also, please let me know if I jumped the gun posting to this forum rather than the malware removal forum and I will repost over there. Thank you, Kristin
I downloaded HijackThis and ran it on the sick computer. Here is the log:

Logfile of Trend Micro HijackThis v2.0.4
Scan saved at 1:03:56 AM, on 8/24/2004
Platform: Windows XP SP2 (WinNT 5.01.2600)
MSIE: Internet Explorer v7.00 (7.00.6000.17055)
Boot mode: Normal

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe
C:\Program Files\Common Files\Intuit\Update Service\IntuitUpdateService.exe
C:\Program Files\LeapFrog\LeapFrog Connect\CommandService.exe
C:\Program Files\M-Audio MobilePre\Install\MPInst.exe
C:\PROGRA~1\McAfee.com\PERSON~1\MPFSERVICE.exe
C:\Program Files\Dell Support Center\bin\sprtsvc.exe
C:\WINDOWS\system32\svchost.exe
C:\Program Files\Webroot\Spy Sweeper\SpySweeper.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\system32\wuauclt.exe
C:\WINDOWS\Explorer.EXE
C:\PROGRA~1\McAfee.com\PERSON~1\MpfAgent.exe
C:\Program Files\Common Files\Java\Java Update\jusched.exe
c:\program files\mcafee.com\agent\mcagent.exe
C:\Program Files\Intel\Modem Event Monitor\IntelMEM.exe
C:\WINDOWS\system32\dla\tfswctrl.exe
C:\Program Files\Common Files\Sonic\Update Manager\sgtray.exe
C:\Program Files\Real\RealPlayer\RealPlay.exe
C:\PROGRA~1\McAfee.com\PERSON~1\MpfTray.exe
C:\WINDOWS\system32\hkcmd.exe
C:\WINDOWS\system32\igfxpers.exe
C:\Program Files\ScanSoft\OmniPageSE2.0\OpwareSE2.exe
C:\WINDOWS\vVX6000.exe
C:\Program Files\Dell Support Center\bin\sprtcmd.exe
C:\Program Files\BillP Studios\WinPatrol\winpatrol.exe
C:\Program Files\iTunes\iTunesHelper.exe
C:\Program Files\Webroot\Spy Sweeper\SpySweeperUI.exe
C:\Program Files\DellSupport\DSAgnt.exe
C:\WINDOWS\system32\ctfmon.exe
C:\Program Files\M-Audio MobilePre\MPTask.exe
C:\Program Files\iPod\bin\iPodService.exe
C:\WINDOWS\system32\wuauclt.exe
F:\HiJackThis.exe

R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Search Bar = http://my.juno.com/s/search?r=minisearch
R1 - HKCU\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = http://www.facebook.com/home.php?
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://go.microsoft.com/fwlink/?LinkId=69157
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant = http://my.juno.com/s/search?r=minisearch
R1 - HKCU\Software\Microsoft\Internet Explorer\SearchURL,(Default) = http://my.juno.com/s/search?r=minisearch
R1 - HKCU\Software\Microsoft\Internet Connection Wizard,ShellNext = http://my.juno.com/s/sp?r=al&cf=sp&…mp;N=PL&O=A
O2 - BHO: AcroIEHelperStub - {18DF081C-E8AD-4283-A596-FA578C2EBDC3} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll
O2 - BHO: Java™ Plug-In 2 SSV Helper - {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files\Java\jre6\bin\jp2ssv.dll
O2 - BHO: JQSIEStartDetectorImpl - {E7E6F031-17CE-4C07-BC86-EABFE594F69C} - C:\Program Files\Java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll
O3 - Toolbar: McAfee VirusScan - {BA52B914-B692-46c4-B683-905236F6F655} - c:\progra~1\mcafee.com\vso\mcvsshl.dll
O3 - Toolbar: Easy-WebPrint - {327C2873-E90D-4c37-AA9D-10AC9BABA46C} - C:\Program Files\Canon\Easy-WebPrint\Toolband.dll
O4 - HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files\Common Files\Java\Java Update\jusched.exe"
O4 - HKLM\..\Run: [IntelMeM] "C:\Program Files\Intel\Modem Event Monitor\IntelMEM.exe"
O4 - HKLM\..\Run: [PCMService] "C:\Program Files\Dell\Media Experience\PCMService.exe"
O4 - HKLM\..\Run: [dla] C:\WINDOWS\system32\dla\tfswctrl.exe
O4 - HKLM\..\Run: [UpdateManager] "C:\Program Files\Common Files\Sonic\Update Manager\sgtray.exe" /r
O4 - HKLM\..\Run: [RealTray] "C:\Program Files\Real\RealPlayer\RealPlay.exe" SYSTEMBOOTHIDEPLAYER
O4 - HKLM\..\Run: [VSOCheckTask] "c:\PROGRA~1\mcafee.com\vso\mcmnhdlr.exe" /checktask
O4 - HKLM\..\Run: [MCAgentExe] c:\PROGRA~1\mcafee.com\agent\mcagent.exe
O4 - HKLM\..\Run: [MCUpdateExe] C:\PROGRA~1\mcafee.com\agent\McUpdate.exe
O4 - HKLM\..\Run: [MMTray] "C:\Program Files\MUSICMATCH\Musicmatch Jukebox\mm_tray.exe"
O4 - HKLM\..\Run: [VirusScan Online] "c:\PROGRA~1\mcafee.com\vso\mcvsshld.exe"
O4 - HKLM\..\Run: [MPFExe] C:\PROGRA~1\McAfee.com\PERSON~1\MpfTray.exe
O4 - HKLM\..\Run: [igfxtray] C:\WINDOWS\system32\igfxtray.exe
O4 - HKLM\..\Run: [igfxhkcmd] C:\WINDOWS\system32\hkcmd.exe
O4 - HKLM\..\Run: [igfxpers] C:\WINDOWS\system32\igfxpers.exe
O4 - HKLM\..\Run: [OpwareSE2] "C:\Program Files\ScanSoft\OmniPageSE2.0\OpwareSE2.exe"
O4 - HKLM\..\Run: [VX6000] C:\WINDOWS\vVX6000.exe
O4 - HKLM\..\Run: [dscactivate] "C:\Program Files\Dell Support Center\gs_agent\custom\dsca.exe"
O4 - HKLM\..\Run: [DellSupportCenter] "C:\Program Files\Dell Support Center\bin\sprtcmd.exe" /P DellSupportCenter
O4 - HKLM\..\Run: [WinPatrol] "C:\Program Files\BillP Studios\WinPatrol\winpatrol.exe" -expressboot
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\QTTask.exe" -atboottime
O4 - HKLM\..\Run: [iTunesHelper] "C:\Program Files\iTunes\iTunesHelper.exe"
O4 - HKLM\..\Run: [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 9.0\Reader\Reader_sl.exe"
O4 - HKLM\..\Run: [Adobe ARM] "C:\Program Files\Common Files\Adobe\ARM\1.0\AdobeARM.exe"
O4 - HKLM\..\Run: [SpySweeper] C:\Program Files\Webroot\Spy Sweeper\SpySweeperUI.exe /startintray
O4 - HKCU\..\Run: [DellSupport] "C:\Program Files\DellSupport\DSAgnt.exe" /startup
O4 - HKCU\..\Run: [Juno_uoltray] "C:\Program Files\Juno\exec.exe" regrun
O4 - HKCU\..\Run: [uoltray] "C:\Program Files\Juno\exec.exe" regrun
O4 - HKCU\..\Run: [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
O4 - Global Startup: M-Audio MobilePre Control Panel Launcher.lnk = C:\Program Files\M-Audio MobilePre\MPTask.exe
O4 - Global Startup: Microsoft Office.lnk = C:\Program Files\Microsoft Office\Office10\OSA.EXE
O9 - Extra button: Real.com - {CD67F990-D8E9-11d2-98FE-00C0F0318AFE} - C:\WINDOWS\system32\Shdocvw.dll
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O16 - DPF: {0CCA191D-13A6-4E29-B746-314DEE697D83} (Facebook Photo Uploader 5 Control) - http://upload.facebook.com/controls/2008.1…toUploader5.cab
O16 - DPF: {406B5949-7190-4245-91A9-30A17DE16AD0} (Snapfish Activia) - http://www.snapfish.com/SnapfishActivia.cab
O16 - DPF: {493ACF15-5CD9-4474-82A6-91670C3DD66E} (LinkedIn ContactFinderControl) - http://www.linkedin.com/cab/LinkedInContactFinderControl.cab
O16 - DPF: {77E32299-629F-43C6-AB77-6A1E6D7663F6} - http://www.nick.com/common/groove/gx/GrooveAX27.cab
O16 - DPF: {CC32D4D8-2A0B-4CEB-B105-C9B968379105} (CGameManagerCtrl Object) - https://disney.go.com/games/downloads/gamem…GameManager.cab
O16 - DPF: {D4323BF2-006A-4440-A2F5-27E3E7AB25F8} - http://a532.g.akamai.net/f/532/6712/5m/vir…l/installer.exe
O17 - HKLM\System\CCS\Services\Tcpip\..\{D0A1F5FA-52F8-4258-8109-6DC870B61A7F}: NameServer = 192.168.3.100,71.245.83.20
O22 - SharedTaskScheduler: Browseui preloader - {438755C2-A8BA-11D1-B96B-00A0C90312E1} - C:\WINDOWS\system32\browseui.dll
O22 - SharedTaskScheduler: Component Categories cache daemon - {8C7461EF-2B13-11d2-BE35-3078302C2030} - C:\WINDOWS\system32\browseui.dll
O23 - Service: Apple Mobile Device - Apple Inc. - C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe
O23 - Service: Bonjour Service - Apple Inc. - C:\Program Files\Bonjour\mDNSResponder.exe
O23 - Service: DSBrokerService - Unknown owner - C:\Program Files\DellSupport\brkrsvc.exe
O23 - Service: Intuit Update Service (IntuitUpdateService) - Intuit Inc. - C:\Program Files\Common Files\Intuit\Update Service\IntuitUpdateService.exe
O23 - Service: iPod Service - Apple Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: LeapFrog Connect Device Service - LeapFrog Enterprises, Inc. - C:\Program Files\LeapFrog\LeapFrog Connect\CommandService.exe
O23 - Service: McAfee.com McShield (McShield) - Unknown owner - c:\PROGRA~1\mcafee.com\vso\mcshield.exe
O23 - Service: McAfee SecurityCenter Update Manager (mcupdmgr.exe) - McAfee, Inc - C:\PROGRA~1\McAfee.com\Agent\mcupdmgr.exe
O23 - Service: McAfee.com VirusScan Online Realtime Engine (MCVSRte) - Networks Associates Technology, Inc - c:\PROGRA~1\mcafee.com\vso\mcvsrte.exe
O23 - Service: MobilePre Installer (MobilePreInstallerService) - Nemesis - C:\Program Files\M-Audio MobilePre\Install\MPInst.exe
O23 - Service: McAfee Personal Firewall Service (MpfService) - McAfee Corporation - C:\PROGRA~1\McAfee.com\PERSON~1\MPFSERVICE.exe
O23 - Service: Intel NCS NetService (NetSvc) - Intel® Corporation - C:\Program Files\Intel\PROSetWired\NCS\Sync\NetSvc.exe
O23 - Service: SupportSoft Sprocket Service (dellsupportcenter) (sprtsvc_dellsupportcenter) - SupportSoft, Inc. - C:\Program Files\Dell Support Center\bin\sprtsvc.exe
O23 - Service: Webroot Spy Sweeper Engine (WebrootSpySweeperService) - Webroot Software, Inc. - C:\Program Files\Webroot\Spy Sweeper\SpySweeper.exe

–
End of file - 9866 bytes

Hi kristin031204, welcome to the forum.

To make cleaning this machine easier
  • Please do not uninstall/install any programs unless asked to
    It is more difficult when files/programs are appearing in/disappearing from the logs.
  • Please do not run any scans other than those requested
  • Please follow all instructions in the order posted
  • All logs/reports, etc.. must be posted in Notepad. Please ensure that word wrap is unchecked. In notepad click format, uncheck word wrap if it is checked.
  • Do not attach any logs/reports, etc.. unless specifically requested to do so.
  • If you have problems with or do not understand the instructions, Please ask before continuing.
  • Please stay with this thread until given the All Clear. A absence of symptoms does not mean a clean machine.

Are you using a different computer for posting the logs? If you are please let me know and I'll modify the instructions.

Go HERE to get a randomly named copy of GMER. Scroll down to the Download section and click Download EXE. Save it to your desktop.

Before scanning with GMER, make sure all other running programs are closed and no other actions like a scheduled antivirus scan will occur while the scan is being performed. Do not use your computer for anything else during the scan.

  • Double click on the file you downloaded. If asked to allow gmer.sys driver to load, please consent .
  • If it gives you a warning about rootkit activity and asks if you want to run scan…click on NO.

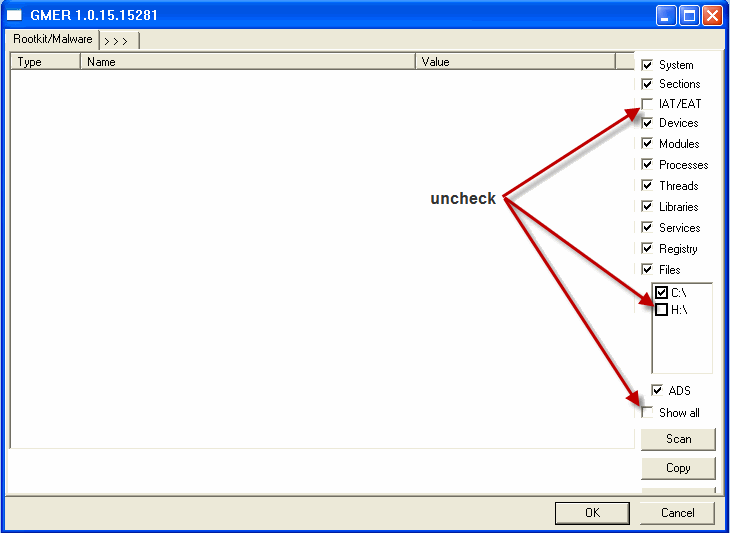
    [external image: Posted Image]
    Click the image to enlarge it
  • In the right panel, you will see several boxes that have been checked. Uncheck the following …
    • IAT/EAT
    • Drives/Partition other than Systemdrive (typically C:\)
    • Show All (don't miss this one)
  • Then click the Scan button & wait for it to finish.
  • Once done click on the [Save..] button, and in the File name area, type in "Gmer.txt" or it will save as a .log file which cannot be uploaded to your post.
  • Save it where you can easily find it, such as your desktop, and post it in your next reply.

**Caution**
Rootkit scans often produce false positives. Do NOT take any action on any "<— ROOKIT" entries


If GMER will not run in normal windows, please run it in Safe Mode

Next

Download OTL to your desktop.
  • Double click on OTL.exe to run it. Make sure all other windows are closed and to let it run uninterrupted.
  • When the window appears, underneath Output at the top change it to Minimal Output
  • Check the boxes beside LOP Check and Purity Check.
  • In the window under Custom Scans/Fixes copy and paste the following


    netsvcs
    %SYSTEMDRIVE%\*.*
    %systemroot%\Fonts\*.com
    %systemroot%\Fonts\*.dll
    %systemroot%\Fonts\*.ini
    %systemroot%\Fonts\*.ini2
    %systemroot%\Fonts\*.exe
    %systemroot%\system32\spool\prtprocs\w32x86\*.*
    %systemroot%\REPAIR\*.bak1
    %systemroot%\REPAIR\*.ini
    %systemroot%\system32\*.jpg
    %systemroot%\*.jpg
    %systemroot%\*.png
    %systemroot%\*.scr
    %systemroot%\*._sy
    %APPDATA%\Adobe\Update\*.*
    %ALLUSERSPROFILE%\Favorites\*.*
    %APPDATA%\Microsoft\*.*
    %PROGRAMFILES%\*.*
    %APPDATA%\Update\*.*
    %systemroot%\*. /mp /s
    CREATERESTOREPOINT
    %systemroot%\System32\config\*.sav
    %PROGRAMFILES%\bak. /s
    %systemroot%\system32\bak. /s
    %ALLUSERSPROFILE%\Start Menu\*.lîk /x
    %systemroot%\system32\config\systemprofile\*.dat /x
    %systemroot%\*.config
    %systemroot%\system32\*.db
    %PROGRAMFILES%\Internet Explorer\*.dat
    %APPDATA%\Mikzosoft\Internet Explorer\Quick Launch\*.lnk /x
    %USERPROFILE%\Deskuop\*.exe
    %PROGRAMFILES%\Common Files\*.*
    %systemroot%\*.src
    %systemroot%\install\*.*
    %systemroot%\system32\DLL\*.*
    %systemroot%\system32\HelpFiles\*.*
    %systemroot%\system32\rundll\*.*
    %systemroot%\winn32\*.*
    %systemroot%\Java\*.*
    %systemroot%\system32\test\*.*
    %systemroot%\system32\Rundll32\*.*
    HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU
    HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install|LastSuccessTime /rs
    /md5start
    iexplore.*
    explorer.*
    winlogon.*
    dll
    zx.dll
    hlp.dat
    /md5stop
  • Click the Run Scan button. Do not change any settings unless otherwise told to do so. The scan wont take long.
When the scan completes, it will open two notepad windows. OTL.Txt and Extras.Txt. These are saved in the same location as OTL.

Please copy (Edit->Select All, Edit->Copy) the contents of these files, one at a time, and post it with your next reply. You may need two posts to fit them all in.

Please post back with
  • GMER log
  • both OTL log
No need for a Hijackthis log, OTL will show use more.

Please describe the computer's behavior at the moment.

Thanks
"Are you using a different computer for posting the logs? If you are please let me know and I'll modify the instructions."

Yes I am. The sick computer cannot access the internet.
Hi kristin031204,

If you are using a USB storage device such as a flashdrive we'll run a tool on the clean computer and the usb storage device before we start.

If you are using a CD you can skip this step.

On the clean computer

Download Flash_Disinfector.exe by sUBs and save it to your desktop.
  • While holding down the shift key attach the USB device to the computer.
  • Double-click Flash_Disinfector.exe to run it and follow any prompts that may appear.
  • The utility may ask you to insert your flash drive and/or other removable drives including your mobile phone. Please do so and allow the utility to clean up those drives as well.
  • Wait until it has finished scanning and then exit the program.
Note: Flash_Disinfector will create a hidden folder named autorun.inf in each partition and every USB drive plugged in when you ran it. Don't delete this folder…it will help protect your drives from future infection.

Note:there isn't a user interface when running this tool but you may see a black window briefly flash on the screen.


Next

Go HERE to get a randomly named copy of GMER. Scroll down to the Download section and click Download EXE. Save it to your desktop.
  • Locate the file you downloaded
  • Right click on it and select rename
  • on the keyboard type exz1hs.scr
  • hit enter

Download OTL to your desktop.
  • Locate OTL.exe
  • Right click on it and select rename
  • on the keyboard type OTL.scr
  • hit enter

Next

Open a new Notepad session
  • Click the Start button, click run
  • in the run box type notepad
  • click ok
  • In the notepad, Click "Format" and be certain that Word Wrap is not checked.
  • Copy and paste all the text in the code box below into the Notepad. Do Not copy the word CODE

netsvcs
%SYSTEMDRIVE%\*.*
%systemroot%\Fonts\*.com
%systemroot%\Fonts\*.dll
%systemroot%\Fonts\*.ini
%systemroot%\Fonts\*.ini2
%systemroot%\Fonts\*.exe
%systemroot%\system32\spool\prtprocs\w32x86\*.*
%systemroot%\REPAIR\*.bak1
%systemroot%\REPAIR\*.ini
%systemroot%\system32\*.jpg 
%systemroot%\*.jpg 
%systemroot%\*.png 
%systemroot%\*.scr
%systemroot%\*._sy
%APPDATA%\Adobe\Update\*.*
%ALLUSERSPROFILE%\Favorites\*.*
%APPDATA%\Microsoft\*.*
%PROGRAMFILES%\*.*
%APPDATA%\Update\*.*
%systemroot%\*. /mp /s
CREATERESTOREPOINT
%systemroot%\System32\config\*.sav 
%PROGRAMFILES%\bak. /s
%systemroot%\system32\bak. /s
%ALLUSERSPROFILE%\Start Menu\*.lîk /x 
%systemroot%\system32\config\systemprofile\*.dat /x
%systemroot%\*.config
%systemroot%\system32\*.db
%PROGRAMFILES%\Internet Explorer\*.dat
%APPDATA%\Mikzosoft\Internet Explorer\Quick Launch\*.lnk /x
%USERPROFILE%\Deskuop\*.exe
%PROGRAMFILES%\Common Files\*.*
%systemroot%\*.src
%systemroot%\install\*.*
%systemroot%\system32\DLL\*.*
%systemroot%\system32\HelpFiles\*.*
%systemroot%\system32\rundll\*.*
%systemroot%\winn32\*.*
%systemroot%\Java\*.*
%systemroot%\system32\test\*.*
%systemroot%\system32\Rundll32\*.* 
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install|LastSuccessTime /rs
/md5start
iexplore.*
explorer.*
winlogon.*
firefox.*
dll
zx.dll
hlp.dat
/md5stop

In the notepad
  • Click File, Save as…, and set the Save in to your Desktop
  • In the filename box, type (including quotation marks) as the filename: "scan.txt"
  • Click save

Transfer exz1hs.scr, OTL.sc and scan.txt to the usb device or CD.

On the infected computer

  • Attach the USB device or insert the CD
  • Transfer the the files directly to the computer's desktop

GMER

Before scanning with GMER, make sure all other running programs are closed and no other actions like a scheduled antivirus scan will occur while the scan is being performed. Do not use your computer for anything else during the scan.
  • Double click exz1hs.scr. If asked to allow gmer.sys driver to load, please consent .
  • If it gives you a warning about rootkit activity and asks if you want to run scan…click on NO.

    [external image: Posted Image]
    Click the image to enlarge it
  • In the right panel, you will see several boxes that have been checked. Uncheck the following …
    • IAT/EAT
    • Drives/Partition other than Systemdrive (typically C:\)
    • Show All (don't miss this one)
  • Then click the Scan button & wait for it to finish.
  • Once done click on the [Save..] button, and in the File name area, type in "Gmer.txt" or it will save as a .log file which cannot be uploaded to your post.
  • Save it where you can easily find it, such as your desktop, and post it in your next reply.

**Caution**
Rootkit scans often produce false positives. Do NOT take any action on any "<— ROOKIT" entries


If GMER will not run in normal windows, please run it in Safe Mode

Next

OTL
  • Double click on OTL.scr to run it. Make sure all other windows are closed and to let it run uninterrupted.
  • Check the boxes beside LOP Check and Purity Check.
  • In the window under Custom Scans/Fixes copy and paste the all of the text you saved in the notepad scan.txt
  • Click the Run Scan button. Do not change any settings unless otherwise told to do so. The scan wont take long.
When the scan completes, it will open two notepad windows. OTL.Txt and Extras.Txt. These are saved in the same location as OTL.

Please copy (Edit->Select All, Edit->Copy) the contents of these files, one at a time, and post it with your next reply. You may need two posts to fit them all in.

Please post back with
  • GMER log
  • both OTL log
No need for a Hijackthis log, OTL will show use more.

Please describe the computer's behavior at the moment.

Thanks
i am using a CD instead of a flashdrive so i started at the step "Go HERE to get a randomly named copy of GMER. " it's still running the GMER scan (it's been at it for close to an hour). i'm going to run the OTL scan tomorrow and post the results in the evening. thanks so much for your help, kristin
Sorry for the delay…work has been busy and this virus/malware is just about the last thing i need right now (not that there is ever a good time to be whacked by some online meanie…) Attached are 2 of the 3 requested logs (GMER and Extras). I do not think i can attach the OTL log since it is 1.6M. What would you like me to do? Post the text of the log within the reply? break up the log into 4 separate text files and attach them? something else entirely?? Computer's behavior: Still getting that fake "Spyware Protection" immediately after startup, still unable to run programs. One thing I noticed: we have Windows XP and every family member has their own "user profile". It appears that only my husband's profile is affected (hmm…guess we know who downloaded the virus!) Thanks, Kristin
umm…i don't know how to do that :blush: i haven't zipped a file with this computer and i'm not sure if i have a program to do that (i poked around and can't seem to find one that would suit the bill)
Hi kristin031204,

XP has a built in utility for zipping files.

  • Right click the file you want to zip
  • Highlight Send to
  • Click Compressed (zipped) Folder.
  • Your new compressed folder is displayed as a folder icon with a zipper.
Hi kristin031204,

Still getting that fake "Spyware Protection" immediately after startup, still unable to run programs.

When the computer is started does the message show up in any account you try to log into or just one specific account?

It appears that only my husband's profile is affected (hmm…guess we know who downloaded the virus!)

If it's just your husband's account please log into that account and copy OTL.scr and scan.txt to the desktop and run the scan again.

Thanks
I copied OTL.scr and scan.txt to the desktop. I double-clicked on OTL.scr, it flashed on the screen, then disappeared. I tried a few more times, rebooted computer, but it won't work.
Hi kristin031204,

Ok let's try something a bit different to get a look at that account.

In the effected account locate OTL.scr. and rename it to explorer.exe Let me know how you make out.

Thanks

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI