Thank you so much for helping me, NoodleTech!
I attempted to run flash_disinfector.exe on my laptop, an ACER ASPIRE 1551-4755, and it didn't seem to work. It would give me no prompt or messages as it did on my desktop computer. However, as you may see, since last time, whatever cleaning up I did, has made me able to use Mozilla Firefox; and it is no longer crashing. The sound device is no longer crashing too; knock on wood. However the computer is still infected and it keeps trying to access this site, which is being blocked by AVAST!:
cikh71ynks66.com/V75nWfa2CHwgfOdVFgLJABqtYKI6KqkA==
Once in a while, when the desktop loads, either in safemode or not, it will not load explorer.exe and I cannot manually run it through Task Manager. Also, the computer will not shut down and restart through the Start Menu.
When I ran Malwarebytes, it found 19 files, most of which were related to a HKEY reg trojan. I repaired/removed them, it needed to restart, and it attempted to. It would try to start Windows and would just go back to the first AMD screen, as if being restarted again.
As per requested, here are the logs.
OTL:
OTL logfile created on: 12/29/2010 7:33:44 PM - Run 1
OTL by OldTimer - Version 3.2.18.2	 Folder = C:\Documents and Settings\Paulie Cee\Desktop
Windows XP Professional Edition Service Pack 3 (Version = 5.1.2600) - Type = NTWorkstation
Internet Explorer (Version = 8.0.6001.18702)
Locale: 00000409 | Country: United States | Language: ENU | Date Format: M/d/yyyy

2.00 Gb Total Physical Memory | 1.00 Gb Available Physical Memory | 74.00% Memory free
4.00 Gb Paging File | 4.00 Gb Available in Paging File | 92.00% Paging File free
Paging file location(s): C:\pagefile.sys 2046 4092 [binary data]

%SystemDrive% = C: | %SystemRoot% = C:\WINDOWS | %ProgramFiles% = C:\Program Files
Drive C: | 127.99 Gb Total Space | 34.90 Gb Free Space | 27.27% Space Free | Partition Type: NTFS

Computer Name: PAUL | User Name: Paulie Cee | Logged in as Administrator.
Boot Mode: Normal | Scan Mode: Current user
Company Name Whitelist: Off | Skip Microsoft Files: Off | No Company Name Whitelist: On | File Age = 30 Days

========== Processes (SafeList) ==========

PRC - C:\Documents and Settings\Paulie Cee\Desktop\OTL.exe (OldTimer Tools)
PRC - C:\Program Files\Alwil Software\Avast5\AvastUI.exe (AVAST Software)
PRC - C:\Program Files\Alwil Software\Avast5\AvastSvc.exe (AVAST Software)
PRC - C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe (Apple Inc.)
PRC - C:\Program Files\Lavasoft\Ad-Aware\AAWService.exe (Lavasoft)
PRC - C:\Program Files\Lavasoft\Ad-Aware\AAWTray.exe (Lavasoft)
PRC - C:\Program Files\Search Settings\SearchSettings.exe (Spigot, Inc.)
PRC - C:\Program Files\AIM6\aim6.exe (AOL LLC)
PRC - C:\WINDOWS\SOUNDMAN.EXE (Realtek Semiconductor Corp.)
PRC - C:\Program Files\Flip Video\FlipShare\FlipShareService.exe ()
PRC - C:\Program Files\AIM6\aolsoftware.exe (AOL LLC)
PRC - C:\WINDOWS\explorer.exe (Microsoft Corporation)
PRC - C:\WINDOWS\system32\hphmon04.exe (Hewlett-Packard)
PRC - C:\WINDOWS\system32\spool\drivers\w32x86\3\hpztsb07.exe (HP)
PRC - C:\Program Files\InterVideo\Common\Bin\WinCinemaMgr.exe (InterVideo Inc.)


========== Modules (SafeList) ==========

MOD - C:\Documents and Settings\Paulie Cee\Desktop\OTL.exe (OldTimer Tools)
MOD - C:\WINDOWS\WinSxS\x86_Microsoft.Windows.Common-Controls_6595b64144ccf1df_6.0.2600.6028_x-ww_61e65202\comctl32.dll (Microsoft Corporation)


========== Win32 Services (SafeList) ==========

SRV - (FlexService) – C:\Program Files\RapidBIT\cisvc.exe File not found
SRV - (avast! Web Scanner) – C:\Program Files\Alwil Software\Avast5\AvastSvc.exe (AVAST Software)
SRV - (avast! Mail Scanner) – C:\Program Files\Alwil Software\Avast5\AvastSvc.exe (AVAST Software)
SRV - (avast! Antivirus) – C:\Program Files\Alwil Software\Avast5\AvastSvc.exe (AVAST Software)
SRV - (Apple Mobile Device) – C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe (Apple Inc.)
SRV - (FLEXnet Licensing Service) – C:\Program Files\Common Files\Macrovision Shared\FLEXnet Publisher\FNPLicensingService.exe (Macrovision Europe Ltd.)
SRV - (Lavasoft Ad-Aware Service) – C:\Program Files\Lavasoft\Ad-Aware\AAWService.exe (Lavasoft)
SRV - (FlipShare Service) – C:\Program Files\Flip Video\FlipShare\FlipShareService.exe ()
SRV - (Pml Driver HPH11) – C:\WINDOWS\system32\hphipm11.exe (HP)


========== Driver Services (SafeList) ==========

DRV - (wckqwd) – C:\WINDOWS\System32\drivers\bjjkw.sys File not found
DRV - (mcdbus) – C:\WINDOWS\System32\DRIVERS\mcdbus.sys File not found
DRV - (aswTdi) – C:\WINDOWS\System32\drivers\aswTdi.sys (AVAST Software)
DRV - (aswSP) – C:\WINDOWS\System32\drivers\aswSP.sys (AVAST Software)
DRV - (aswRdr) – C:\WINDOWS\System32\drivers\aswRdr.sys (AVAST Software)
DRV - (aswMon2) – C:\WINDOWS\System32\drivers\aswmon2.sys (AVAST Software)
DRV - (aswFsBlk) – C:\WINDOWS\System32\drivers\aswFsBlk.sys (AVAST Software)
DRV - (Aavmker4) – C:\WINDOWS\System32\drivers\aavmker4.sys (AVAST Software)
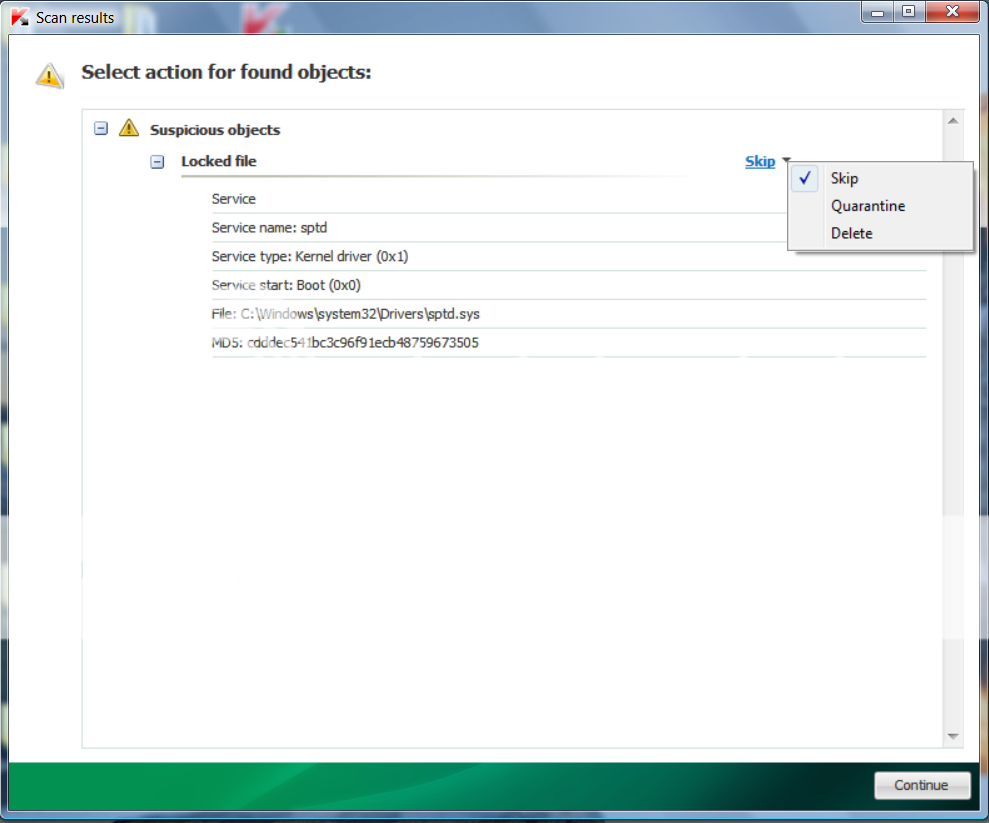
DRV - (sptd) – C:\WINDOWS\System32\Drivers\sptd.sys ()
DRV - (Lbd) – C:\WINDOWS\system32\DRIVERS\Lbd.sys (Lavasoft AB)
DRV - (ALCXWDM) Service for Realtek AC97 Audio (WDM) – C:\WINDOWS\system32\drivers\ALCXWDM.SYS (Realtek Semiconductor Corp.)
DRV - (ALCXSENS) – C:\WINDOWS\system32\drivers\ALCXSENS.SYS (Sensaura)
DRV - (trackcam) – C:\WINDOWS\system32\drivers\trackcam.sys (Eagletron Inc.)
DRV - (viasraid) – C:\WINDOWS\System32\DRIVERS\viasraid.sys (VIA Technologies inc,.ltd)
DRV - (tbhsd) – C:\WINDOWS\system32\drivers\tbhsd.sys (RapidSolution Software AG)
DRV - (nv) – C:\WINDOWS\system32\drivers\nv4_mini.sys (NVIDIA Corporation)
DRV - (61883) – C:\WINDOWS\system32\drivers\61883.sys (Microsoft Corporation)
DRV - (Avc) – C:\WINDOWS\system32\drivers\avc.sys (Microsoft Corporation)
DRV - (MSDV) – C:\WINDOWS\system32\drivers\msdv.sys (Microsoft Corporation)
DRV - (usbaudio) USB Audio Driver (WDM) – C:\WINDOWS\system32\drivers\usbaudio.sys (Microsoft Corporation)
DRV - (Dot4Storage HPH11) Storage Class Driver for IEEE-1284.4 (HPH11) – C:\WINDOWS\system32\drivers\hphs2k11.sys (Hewlett-Packard)
DRV - (Dot4Usb HPH11) – C:\WINDOWS\system32\drivers\hphius11.sys (HP)
DRV - (Dot4Print HPH11) – C:\WINDOWS\system32\drivers\hphipr11.sys (HP)
DRV - (Dot4 HPH11) – C:\WINDOWS\system32\drivers\hphid411.sys (HP)
DRV - (yukonwxp) – C:\WINDOWS\system32\drivers\yukonwxp.sys (Marvell Semiconductor Inc.)
DRV - (Pfc) – C:\WINDOWS\system32\drivers\pfc.sys (Padus, Inc.)
DRV - (XIRLINK) – C:\WINDOWS\system32\drivers\C-itNT.sys (Xirlink, Inc)


========== Standard Registry (SafeList) ==========


========== Internet Explorer ==========


IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://search.conduit.com?SearchSource=10&ctid;=CT1098640
IE - HKCU\..\URLSearchHook: {E312764E-7706-43F1-8DAB-FCDD2B1E416D} - C:\Program Files\Search Settings\kb128\SearchSettings.dll (Spigot, Inc.)
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyEnable" = 0
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyOverride" = *.local;
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyServer" = http=127.0.0.1:5555

========== FireFox ==========

FF - prefs.js..browser.search.defaultthis.engineName: "free-downloads.net Customized Web Search"
FF - prefs.js..browser.search.defaulturl: "http://search.conduit.com/ResultsExt.aspx?ctid=CT1098640&SearchSource;=3&q;={searchTerms}"
FF - prefs.js..browser.search.selectedEngine: "free-downloads.net Customized Web Search"
FF - prefs.js..browser.startup.homepage: "http://www.facebook.com/?ref=hp"
FF - prefs.js..network.proxy.type: 4


FF - HKLM\software\mozilla\Firefox\Extensions\\{2004B297-6595-4A0C-8E33-DAD293A69F3D}: C:\Documents and Settings\Paulie Cee\Local Settings\Application Data\{2004B297-6595-4A0C-8E33-DAD293A69F3D} [2010/10/24 22:17:46 | 000,000,000 | —D | M]
FF - HKLM\software\mozilla\Mozilla Firefox 3.6.13\extensions\\Components: C:\Program Files\Mozilla Firefox\components [2010/12/27 03:32:41 | 000,000,000 | —D | M]
FF - HKLM\software\mozilla\Mozilla Firefox 3.6.13\extensions\\Plugins: C:\Program Files\Mozilla Firefox\plugins [2010/12/19 03:53:51 | 000,000,000 | —D | M]
FF - HKLM\software\mozilla\Thunderbird\Extensions\\[removed]: C:\Program Files\ESET\ESET NOD32 Antivirus\Mozilla Thunderbird

[2009/06/17 17:18:45 | 000,000,000 | —D | M] (No name found) – C:\Documents and Settings\Paulie Cee\Application Data\Mozilla\Extensions
[2010/12/28 19:50:43 | 000,000,000 | —D | M] (No name found) – C:\Documents and Settings\Paulie Cee\Application Data\Mozilla\Firefox\Profiles\bu4afqz0.default\extensions
[2010/07/31 16:16:03 | 000,000,000 | —D | M] (Microsoft .NET Framework Assistant) – C:\Documents and Settings\Paulie Cee\Application Data\Mozilla\Firefox\Profiles\bu4afqz0.default\extensions\{20a82645-c095-46ed-80e3-08825760534b}
[2009/09/11 03:06:27 | 000,004,207 | —- | M] () – C:\Documents and Settings\Paulie Cee\Application Data\Mozilla\Firefox\Profiles\bu4afqz0.default\searchplugins\aim-search.xml
[2010/01/20 11:16:28 | 000,000,939 | —- | M] () – C:\Documents and Settings\Paulie Cee\Application Data\Mozilla\Firefox\Profiles\bu4afqz0.default\searchplugins\conduit.xml
[2010/12/28 19:50:43 | 000,000,000 | —D | M] (No name found) – C:\Program Files\Mozilla Firefox\extensions

O1 HOSTS File: ([2010/01/22 01:51:52 | 000,000,698 | R— | M]) - C:\WINDOWS\system32\drivers\etc\hosts
O1 - Hosts: 127.0.0.1 localhost
O2 - BHO: (no name) - {1FD79A59-37B1-459B-9097-09F9FAB8A523} - No CLSID value found.
O2 - BHO: (no name) - {7c5c0f58-e061-457d-9033-77307f5ed00c} - No CLSID value found.
O2 - BHO: (SearchSettings Class) - {E312764E-7706-43F1-8DAB-FCDD2B1E416D} - C:\Program Files\Search Settings\kb128\SearchSettings.dll (Spigot, Inc.)
O4 - HKLM..\Run: [Ad-Watch] C:\Program Files\Lavasoft\Ad-Aware\AAWTray.exe (Lavasoft)
O4 - HKLM..\Run: [avast5] C:\Program Files\Alwil Software\Avast5\avastUI.exe (AVAST Software)
O4 - HKLM..\Run: [HPDJ Taskbar Utility] C:\WINDOWS\system32\spool\drivers\w32x86\3\hpztsb07.exe (HP)
O4 - HKLM..\Run: [HPHmon04] C:\WINDOWS\system32\hphmon04.exe (Hewlett-Packard)
O4 - HKLM..\Run: [HPHUPD04] C:\Program Files\HP Photosmart 11\hphinstall\UniPatch\hphupd04.exe File not found
O4 - HKLM..\Run: [NvCplDaemon] C:\WINDOWS\System32\NvCpl.DLL (NVIDIA Corporation)
O4 - HKLM..\Run: [NvMediaCenter] C:\WINDOWS\System32\NvMcTray.DLL (NVIDIA Corporation)
O4 - HKLM..\Run: [nwiz] C:\WINDOWS\System32\nwiz.exe ()
O4 - HKLM..\Run: [SearchSettings] C:\Program Files\Search Settings\SearchSettings.exe (Spigot, Inc.)
O4 - HKLM..\Run: [SoundMan] C:\WINDOWS\SOUNDMAN.EXE (Realtek Semiconductor Corp.)
O4 - HKCU..\Run: [Aim6] C:\Program Files\AIM6\aim6.exe (AOL LLC)
O4 - Startup: C:\Documents and Settings\All Users\Start Menu\Programs\Startup\Adobe Gamma Loader.lnk = C:\Program Files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe (Adobe Systems, Inc.)
O4 - Startup: C:\Documents and Settings\All Users\Start Menu\Programs\Startup\InterVideo WinCinema Manager.lnk = C:\Program Files\InterVideo\Common\Bin\WinCinemaMgr.exe (InterVideo Inc.)
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: HonorAutoRunSetting = 1
O7 - HKCU\Software\Policies\Microsoft\Internet Explorer\Control Panel present
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDriveTypeAutoRun = 36
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDriveAutoRun = FF FF FF FF  [binary data]
O10 - NameSpace_Catalog5\Catalog_Entries\000000000004 [] - C:\Program Files\Bonjour\mdnsNSP.dll (Apple Inc.)
O16 - DPF: {8100D56A-5661-482C-BEE8-AFECE305D968} http://upload.facebook.com/controls/2009.07.28_v5.5.8.1/FacebookPhotoUploader55.cab (Facebook Photo Uploader 5 Control)
O16 - DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} http://java.sun.com/update/1.6.0/jinstall-1_6_0_14-windows-i586.cab (Java Plug-in 1.6.0_14)
O16 - DPF: {CAFEEFAC-0016-0000-0014-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-1_6_0_14-windows-i586.cab (Java Plug-in 1.6.0_14)
O16 - DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-1_6_0_14-windows-i586.cab (Java Plug-in 1.6.0_14)
O16 - DPF: {D27CDB6E-AE6D-11CF-96B8-444553540000} http://fpdownload2.macromedia.com/get/shockwave/cabs/flash/swflash.cab (Shockwave Flash Object)
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: DhcpNameServer = 192.168.1.254
O18 - Protocol\Handler\skype4com {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - C:\Program Files\Common Files\Skype\Skype4COM.dll (Skype Technologies)
O20 - HKLM Winlogon: Shell - (Explorer.exe) - C:\WINDOWS\explorer.exe (Microsoft Corporation)
O24 - Desktop BackupWallPaper: C:\Documents and Settings\Paulie Cee\Local Settings\Application Data\Microsoft\Wallpaper1.bmp
O32 - HKLM CDRom: AutoRun - 1
O32 - AutoRun File - [2009/06/17 19:44:42 | 000,000,000 | —- | M] () - C:\AUTOEXEC.BAT – [ NTFS ]
O32 - AutoRun File - [2010/12/29 18:51:15 | 000,000,000 | RHSD | M] - C:\autorun.inf – [ NTFS ]
O33 - MountPoints2\{75959f5c-1db0-11df-965d-0011d8ee59da}\Shell\AutoRun\command - "" = H:\Setup_FlipShare.exe – File not found
O33 - MountPoints2\{75959f5c-1db0-11df-965d-0011d8ee59da}\Shell\Setup FlipShare\command - "" = H:\Setup_FlipShare.exe – File not found
O34 - HKLM BootExecute: (autocheck autochk *) -  File not found
O34 - HKLM BootExecute: (lsdelete) - C:\WINDOWS\System32\lsdelete.exe ()
O35 - HKLM\..comfile [open] – "%1" %*
O35 - HKLM\..exefile [open] – "%1" %*
O37 - HKLM\…com [@ = comfile] – "%1" %*
O37 - HKLM\…exe [@ = exefile] – "%1" %*

========== Files/Folders - Created Within 30 Days ==========

[2010/12/29 19:23:00 | 000,602,624 | —- | C] (OldTimer Tools) – C:\Documents and Settings\Paulie Cee\Desktop\OTL.exe
[2010/12/29 18:51:15 | 000,000,000 | RHSD | C] – C:\autorun.inf
[2010/12/28 06:09:37 | 000,000,000 | —D | C] – C:\Documents and Settings\Paulie Cee\My Documents\Cakewalk Projects
[2010/12/28 03:05:46 | 000,000,000 | —D | C] – C:\Documents and Settings\Paulie Cee\My Documents\Misc Ideas and Business Ventures
[2010/12/28 02:19:30 | 000,000,000 | —D | C] – C:\Documents and Settings\Paulie Cee\My Documents\VMedia Projects
[2010/12/28 01:08:02 | 000,000,000 | —D | C] – C:\Documents and Settings\Paulie Cee\My Documents\My Writing
[2010/12/27 19:12:18 | 000,017,744 | —- | C] (AVAST Software) – C:\WINDOWS\System32\drivers\aswFsBlk.sys
[2010/12/27 19:12:17 | 000,165,584 | —- | C] (AVAST Software) – C:\WINDOWS\System32\drivers\aswSP.sys
[2010/12/27 19:12:16 | 000,023,376 | —- | C] (AVAST Software) – C:\WINDOWS\System32\drivers\aswRdr.sys
[2010/12/27 19:12:15 | 000,046,672 | —- | C] (AVAST Software) – C:\WINDOWS\System32\drivers\aswTdi.sys
[2010/12/27 19:12:12 | 000,100,176 | —- | C] (AVAST Software) – C:\WINDOWS\System32\drivers\aswmon2.sys
[2010/12/27 19:12:12 | 000,094,544 | —- | C] (AVAST Software) – C:\WINDOWS\System32\drivers\aswmon.sys
[2010/12/27 19:12:11 | 000,028,880 | —- | C] (AVAST Software) – C:\WINDOWS\System32\drivers\aavmker4.sys
[2010/12/27 19:12:07 | 000,038,848 | —- | C] (AVAST Software) – C:\WINDOWS\avastSS.scr
[2010/12/27 19:12:06 | 000,167,592 | —- | C] (AVAST Software) – C:\WINDOWS\System32\aswBoot.exe
[2010/12/27 19:12:02 | 000,000,000 | —D | C] – C:\Program Files\Alwil Software
[2010/12/27 19:12:02 | 000,000,000 | —D | C] – C:\Documents and Settings\All Users\Application Data\Alwil Software
[2010/12/27 16:01:55 | 000,000,000 | —D | C] – C:\Documents and Settings\LocalService\Application Data\Macromedia
[2010/12/27 16:01:48 | 000,000,000 | —D | C] – C:\Documents and Settings\LocalService\Application Data\Adobe
[2010/12/27 15:16:05 | 000,000,000 | —D | C] – C:\Documents and Settings\All Users\Application Data\MFAData
[2010/12/27 04:20:01 | 000,000,000 | —D | C] – C:\Documents and Settings\NetworkService\Application Data\Macromedia
[2010/12/27 04:20:00 | 000,000,000 | —D | C] – C:\Documents and Settings\NetworkService\Application Data\Adobe
[2010/12/25 13:19:08 | 000,000,000 | —D | C] – C:\Program Files\Oldgames
[2010/12/25 01:52:04 | 000,000,000 | —D | C] – C:\HLPack
[2010/12/19 03:37:27 | 000,000,000 | –SD | C] – C:\Documents and Settings\Paulie Cee\My Documents\My Webs
[2010/12/17 02:55:31 | 000,000,000 | —D | C] – C:\Documents and Settings\Paulie Cee\Desktop\confirmation_files
[2010/12/15 14:12:18 | 000,040,960 | —- | C] (Microsoft Corporation) – C:\WINDOWS\System32\dllcache\ndproxy.sys
[2010/12/15 14:11:41 | 000,045,568 | —- | C] (Microsoft Corporation) – C:\WINDOWS\System32\dllcache\wab.exe
[2010/12/12 00:42:08 | 000,000,000 | —D | C] – C:\Documents and Settings\Paulie Cee\Desktop\Receipt.aspx_files
[2010/12/08 16:05:26 | 000,000,000 | —D | C] – C:\Documents and Settings\Paulie Cee\Desktop\ref=ox_spc_place_order_bottom_files
[2010/12/08 15:03:23 | 000,000,000 | —D | C] – C:\Documents and Settings\Paulie Cee\Desktop\webscr_files
[2010/07/17 09:07:09 | 000,812,498 | —- | C] (Adobe Systems Incorporated) – C:\Documents and Settings\Paulie Cee\Application Data\Temp3246.exe
[7 C:\WINDOWS\System32\*.tmp files -> C:\WINDOWS\System32\*.tmp -> ]
[4 C:\WINDOWS\*.tmp files -> C:\WINDOWS\*.tmp -> ]
[2 C:\Documents and Settings\Paulie Cee\My Documents\*.tmp files -> C:\Documents and Settings\Paulie Cee\My Documents\*.tmp -> ]

========== Files - Modified Within 30 Days ==========

[2010/12/29 19:23:34 | 000,080,384 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\MBRCheck.exe
[2010/12/29 19:23:15 | 000,133,632 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\RKUnhookerLE.EXE
[2010/12/29 19:22:58 | 000,602,624 | —- | M] (OldTimer Tools) – C:\Documents and Settings\Paulie Cee\Desktop\OTL.exe
[2010/12/29 19:05:05 | 000,000,894 | —- | M] () – C:\WINDOWS\tasks\GoogleUpdateTaskMachineUA.job
[2010/12/29 18:43:10 | 000,000,432 | -H– | M] () – C:\WINDOWS\tasks\User_Feed_Synchronization-{F45238CF-3301-4D40-9AA8-3347E2B0F381}.job
[2010/12/29 18:40:57 | 000,002,137 | —- | M] () – C:\Documents and Settings\All Users\Desktop\iTunes.lnk
[2010/12/29 18:40:16 | 000,132,597 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\Flash_Disinfector.exe
[2010/12/29 18:32:59 | 000,002,206 | —- | M] () – C:\WINDOWS\System32\wpa.dbl
[2010/12/29 18:32:49 | 000,000,890 | —- | M] () – C:\WINDOWS\tasks\GoogleUpdateTaskMachineCore.job
[2010/12/29 18:32:49 | 000,000,236 | —- | M] () – C:\WINDOWS\tasks\OGALogon.job
[2010/12/29 18:32:44 | 000,186,097 | —- | M] () – C:\WINDOWS\System32\nvapps.xml
[2010/12/29 18:32:37 | 000,002,048 | –S- | M] () – C:\WINDOWS\bootstat.dat
[2010/12/28 21:31:02 | 000,091,136 | —- | M] () – C:\Documents and Settings\Paulie Cee\Local Settings\Application Data\DCBC2A71-70D8-4DAN-EHR8-E0D61DEA3FDF.ini
[2010/12/28 04:47:46 | 000,015,020 | —- | M] () – C:\Documents and Settings\Paulie Cee\My Documents\WHAT DO I WANT AND HOW DO I GET IT.docx
[2010/12/27 19:12:18 | 000,001,700 | —- | M] () – C:\Documents and Settings\All Users\Desktop\avast! Free Antivirus.lnk
[2010/12/27 19:12:13 | 000,002,626 | —- | M] () – C:\WINDOWS\System32\CONFIG.NT
[2010/12/27 16:51:10 | 000,000,120 | —- | M] () – C:\WINDOWS\Ejuzaki.dat
[2010/12/27 16:47:35 | 000,054,016 | —- | M] () – C:\WINDOWS\System32\drivers\aevo.sys
[2010/12/27 03:13:56 | 000,000,000 | —- | M] () – C:\WINDOWS\Tnobaneya.bin
[2010/12/26 02:43:00 | 000,000,454 | —- | M] () – C:\WINDOWS\tasks\Driver Robot.job
[2010/12/25 13:19:49 | 000,000,021 | —- | M] () – C:\WINDOWS\BasiliskII.ini
[2010/12/25 08:11:01 | 000,000,284 | —- | M] () – C:\WINDOWS\tasks\AppleSoftwareUpdate.job
[2010/12/22 20:08:33 | 000,000,472 | —- | M] () – C:\WINDOWS\tasks\Ad-Aware Update (Weekly).job
[2010/12/20 18:09:00 | 000,038,224 | —- | M] (Malwarebytes Corporation) – C:\WINDOWS\System32\drivers\mbamswissarmy.sys
[2010/12/20 18:08:40 | 000,020,952 | —- | M] (Malwarebytes Corporation) – C:\WINDOWS\System32\drivers\mbam.sys
[2010/12/18 23:20:14 | 000,067,518 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\74101_1465400200139_1387530154_31105444_3676997_n.jpg
[2010/12/18 23:18:43 | 000,077,810 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\28622_1298501907786_1387530154_30741080_7631362_n.jpg
[2010/12/18 23:17:29 | 000,049,740 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\n1387530154_30053791_9223.jpg
[2010/12/18 23:15:39 | 000,095,544 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\47236_1403761659214_1387530154_30993711_5957680_n.jpg
[2010/12/18 23:14:09 | 000,050,983 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\n1387530154_30080036_3403.jpg
[2010/12/18 21:41:23 | 000,070,095 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\wintuk_hero-720x270.jpg
[2010/12/17 02:55:32 | 000,058,097 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\confirmation.html
[2010/12/16 04:15:33 | 000,307,600 | —- | M] () – C:\WINDOWS\System32\FNTCACHE.DAT
[2010/12/16 03:49:33 | 000,001,393 | —- | M] () – C:\WINDOWS\imsins.BAK
[2010/12/12 00:42:08 | 000,010,075 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\Receipt.aspx.htm
[2010/12/10 20:58:10 | 000,099,506 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\1292025913113.jpg
[2010/12/10 13:25:34 | 000,069,595 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\58951_1403760179177_1387530154_30993675_3277520_n.jpg
[2010/12/10 13:24:53 | 000,036,131 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\21076_1180618480089_1366980495_30485392_3888159_n.jpg
[2010/12/10 13:24:45 | 000,045,706 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\21076_1180617520065_1366980495_30485369_5744509_n.jpg
[2010/12/10 13:24:21 | 000,062,706 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\n1387530154_30037136_5911.jpg
[2010/12/10 13:23:27 | 000,037,188 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\2995_187998480439_647245439_6703976_3608975_n.jpg
[2010/12/10 13:23:15 | 000,037,518 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\n1387530154_30024999_7678.jpg
[2010/12/10 13:23:09 | 000,046,410 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\n754365485_4320307_6391.jpg
[2010/12/10 13:16:12 | 000,054,455 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\47236_1403762699240_1387530154_30993737_4524089_n.jpg
[2010/12/10 13:16:00 | 000,079,244 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\47236_1403760979197_1387530154_30993694_2297031_n.jpg
[2010/12/10 13:15:46 | 000,074,960 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\47236_1403761019198_1387530154_30993695_1848490_n.jpg
[2010/12/10 13:14:18 | 000,106,009 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\31091_1324136748641_1387530154_30802297_3791953_n.jpg
[2010/12/10 13:14:07 | 000,071,798 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\31091_1324136828643_1387530154_30802298_918064_n.jpg
[2010/12/08 16:05:27 | 000,175,268 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\ref=ox_spc_place_order_bottom.htm
[2010/12/08 15:03:24 | 000,014,855 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\webscr.htm
[2010/12/04 15:23:22 | 000,014,992 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\DarkwingDuckVol2Stillcap.jpg
[7 C:\WINDOWS\System32\*.tmp files -> C:\WINDOWS\System32\*.tmp -> ]
[4 C:\WINDOWS\*.tmp files -> C:\WINDOWS\*.tmp -> ]
[2 C:\Documents and Settings\Paulie Cee\My Documents\*.tmp files -> C:\Documents and Settings\Paulie Cee\My Documents\*.tmp -> ]

========== Files Created - No Company Name ==========

[2010/12/29 19:23:34 | 000,080,384 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\MBRCheck.exe
[2010/12/29 19:23:15 | 000,133,632 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\RKUnhookerLE.EXE
[2010/12/29 18:43:39 | 000,132,597 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\Flash_Disinfector.exe
[2010/12/27 19:12:18 | 000,001,700 | —- | C] () – C:\Documents and Settings\All Users\Desktop\avast! Free Antivirus.lnk
[2010/12/27 16:47:35 | 000,054,016 | —- | C] () – C:\WINDOWS\System32\drivers\aevo.sys
[2010/12/25 13:19:49 | 000,000,021 | —- | C] () – C:\WINDOWS\BasiliskII.ini
[2010/12/18 23:20:14 | 000,067,518 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\74101_1465400200139_1387530154_31105444_3676997_n.jpg
[2010/12/18 23:18:42 | 000,077,810 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\28622_1298501907786_1387530154_30741080_7631362_n.jpg
[2010/12/18 23:17:28 | 000,049,740 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\n1387530154_30053791_9223.jpg
[2010/12/18 23:15:39 | 000,095,544 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\47236_1403761659214_1387530154_30993711_5957680_n.jpg
[2010/12/18 23:14:08 | 000,050,983 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\n1387530154_30080036_3403.jpg
[2010/12/18 21:41:20 | 000,070,095 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\wintuk_hero-720x270.jpg
[2010/12/17 02:55:30 | 000,058,097 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\confirmation.html
[2010/12/12 00:42:07 | 000,010,075 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\Receipt.aspx.htm
[2010/12/10 20:58:07 | 000,099,506 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\1292025913113.jpg
[2010/12/10 13:25:33 | 000,069,595 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\58951_1403760179177_1387530154_30993675_3277520_n.jpg
[2010/12/10 13:24:53 | 000,036,131 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\21076_1180618480089_1366980495_30485392_3888159_n.jpg
[2010/12/10 13:24:45 | 000,045,706 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\21076_1180617520065_1366980495_30485369_5744509_n.jpg
[2010/12/10 13:23:26 | 000,037,188 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\2995_187998480439_647245439_6703976_3608975_n.jpg
[2010/12/10 13:23:14 | 000,037,518 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\n1387530154_30024999_7678.jpg
[2010/12/10 13:23:08 | 000,046,410 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\n754365485_4320307_6391.jpg
[2010/12/10 13:22:15 | 000,062,706 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\n1387530154_30037136_5911.jpg
[2010/12/10 13:16:12 | 000,054,455 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\47236_1403762699240_1387530154_30993737_4524089_n.jpg
[2010/12/10 13:15:59 | 000,079,244 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\47236_1403760979197_1387530154_30993694_2297031_n.jpg
[2010/12/10 13:15:45 | 000,074,960 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\47236_1403761019198_1387530154_30993695_1848490_n.jpg
[2010/12/10 13:14:18 | 000,106,009 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\31091_1324136748641_1387530154_30802297_3791953_n.jpg
[2010/12/10 13:14:06 | 000,071,798 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\31091_1324136828643_1387530154_30802298_918064_n.jpg
[2010/12/08 16:05:26 | 000,175,268 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\ref=ox_spc_place_order_bottom.htm
[2010/12/08 15:03:23 | 000,014,855 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\webscr.htm
[2010/12/04 15:23:22 | 000,014,992 | —- | C] () – C:\Documents and Settings\Paulie Cee\Desktop\DarkwingDuckVol2Stillcap.jpg
[2010/10/13 02:13:22 | 000,000,127 | —- | C] () – C:\WINDOWS\System32\MRT.INI
[2010/08/04 17:44:30 | 000,204,800 | —- | C] () – C:\WINDOWS\System32\IVIresizeW7.dll
[2010/08/04 17:44:30 | 000,200,704 | —- | C] () – C:\WINDOWS\System32\IVIresizeA6.dll
[2010/08/04 17:44:30 | 000,192,512 | —- | C] () – C:\WINDOWS\System32\IVIresizeP6.dll
[2010/08/04 17:44:30 | 000,192,512 | —- | C] () – C:\WINDOWS\System32\IVIresizeM6.dll
[2010/08/04 17:44:30 | 000,188,416 | —- | C] () – C:\WINDOWS\System32\IVIresizePX.dll
[2010/08/04 17:44:30 | 000,020,480 | —- | C] () – C:\WINDOWS\System32\IVIresize.dll
[2010/06/24 09:38:11 | 000,323,584 | —- | C] () – C:\WINDOWS\System32\FoxImager.dll
[2010/05/18 22:35:49 | 000,000,726 | —- | C] () – C:\WINDOWS\bundle.ini
[2010/05/13 17:54:04 | 000,000,087 | —- | C] () – C:\WINDOWS\dswplug.ini
[2010/05/13 17:53:37 | 000,073,728 | —- | C] () – C:\WINDOWS\System32\mplaw7.dll
[2010/05/13 17:53:37 | 000,073,728 | —- | C] () – C:\WINDOWS\System32\mplaa6.dll
[2010/05/13 17:53:37 | 000,061,440 | —- | C] () – C:\WINDOWS\System32\mplam6.dll
[2010/05/13 17:53:37 | 000,019,968 | —- | C] () – C:\WINDOWS\System32\cpuinf32.dll
[2010/02/13 17:24:11 | 000,000,026 | -H– | C] () – C:\Documents and Settings\All Users\Application Data\.119889580931711767808769176
[2010/02/13 17:17:34 | 000,000,021 | -H– | C] () – C:\Documents and Settings\All Users\Application Data\.24554863501262644635642126105
[2010/02/08 12:27:24 | 000,000,084 | —- | C] () – C:\WINDOWS\netdet.ini
[2010/02/06 13:31:18 | 000,691,696 | —- | C] () – C:\WINDOWS\System32\drivers\sptd.sys
[2010/01/30 00:08:06 | 000,000,024 | —- | C] () – C:\WINDOWS\System32\sysogg.dll
[2010/01/30 00:01:28 | 000,000,050 | —- | C] () – C:\WINDOWS\MegaManager.INI
[2010/01/25 00:57:31 | 000,001,022 | —- | C] () – C:\Documents and Settings\All Users\Application Data\h8srtmainqt.dll
[2009/09/23 17:12:28 | 000,000,034 | —- | C] () – C:\WINDOWS\hpfsched.ini
[2009/08/04 23:52:07 | 000,069,632 | —- | C] () – C:\WINDOWS\System32\hpodinet.dll
[2009/08/03 14:07:42 | 000,403,816 | —- | C] () – C:\WINDOWS\System32\OGACheckControl.dll
[2009/06/28 01:17:04 | 000,000,000 | —- | C] () – C:\WINDOWS\iPlayer.INI
[2009/06/17 18:51:46 | 000,155,648 | —- | C] () – C:\WINDOWS\System32\RTLCPAPI.dll
[2009/06/17 18:51:44 | 000,000,452 | —- | C] () – C:\WINDOWS\alsndmgr.ini
[2009/06/17 18:27:59 | 000,091,136 | —- | C] () – C:\Documents and Settings\Paulie Cee\Local Settings\Application Data\DCBC2A71-70D8-4DAN-EHR8-E0D61DEA3FDF.ini
[2009/06/17 17:24:29 | 000,000,376 | —- | C] () – C:\WINDOWS\ODBC.INI
[2009/06/17 12:23:49 | 000,004,161 | —- | C] () – C:\WINDOWS\ODBCINST.INI
[2008/05/16 13:01:00 | 001,703,936 | —- | C] () – C:\WINDOWS\System32\nvwdmcpl.dll
[2008/05/16 13:01:00 | 001,486,848 | —- | C] () – C:\WINDOWS\System32\nview.dll
[2008/05/16 13:01:00 | 001,019,904 | —- | C] () – C:\WINDOWS\System32\nvwimg.dll
[2008/05/16 13:01:00 | 000,466,944 | —- | C] () – C:\WINDOWS\System32\nvshell.dll
[2008/05/16 13:01:00 | 000,286,720 | —- | C] () – C:\WINDOWS\System32\nvnt4cpl.dll
[2004/12/19 08:29:40 | 000,106,496 | —- | C] () – C:\WINDOWS\System32\xvidvfw.dll
[2004/12/19 08:17:10 | 000,614,400 | —- | C] () – C:\WINDOWS\System32\xvidcore.dll
[2002/10/06 13:42:56 | 000,237,568 | —- | C] () – C:\WINDOWS\System32\OggDS.dll
[2002/10/04 18:04:24 | 000,921,600 | —- | C] () – C:\WINDOWS\System32\VorbisEnc.dll
[2002/10/04 18:04:24 | 000,188,416 | —- | C] () – C:\WINDOWS\System32\vorbis.dll
[2002/10/04 18:04:16 | 000,045,056 | —- | C] () – C:\WINDOWS\System32\ogg.dll
[2002/05/15 18:38:40 | 000,091,136 | —- | C] () – C:\WINDOWS\System32\mp4fil32.dll

========== LOP Check ==========

[2009/09/11 03:05:09 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\acccore
[2010/12/27 19:12:02 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\Alwil Software
[2010/01/12 21:42:17 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\Cakewalk
[2009/08/26 03:27:08 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\Canneverbe Limited
[2010/09/11 14:33:41 | 000,000,000 | -H-D | M] – C:\Documents and Settings\All Users\Application Data\CanonBJ
[2009/06/17 17:48:31 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\ESET
[2010/02/13 17:17:34 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\Final Draft
[2010/03/02 19:43:25 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\Flip Video
[2010/12/27 15:27:13 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\MFAData
[2010/11/05 02:34:50 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\RapidSolution
[2009/08/26 03:49:15 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\TEMP
[2010/05/13 17:57:52 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\Ulead Systems
[2010/12/19 03:53:51 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\Viewpoint
[2010/05/06 18:45:27 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\{429CAD59-35B1-4DBC-BB6D-1DB246563521}
[2009/11/29 04:38:55 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\{755AC846-7372-4AC8-8550-C52491DAA8BD}
[2009/06/17 19:07:03 | 000,000,000 | -H-D | M] – C:\Documents and Settings\All Users\Application Data\{7972B2E5-3E09-4E5E-81B7-FE5819D6772F}
[2009/07/11 11:36:23 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\{8CD7F5AF-ECFA-4793-BF40-D8F42DBFF906}
[2010/02/03 00:52:01 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\{BC9FCCF7-E686-494B-8C9B-55C9A39A7CA9}
[2009/09/11 03:06:48 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\acccore
[2009/12/19 22:46:42 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\Amazon
[2009/09/22 20:22:59 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\Blitware
[2010/01/12 21:44:53 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\Cakewalk
[2009/08/26 03:27:10 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\Canneverbe_Limited
[2010/05/21 11:05:00 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\Facebook
[2010/02/13 17:22:11 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\Final Draft
[2010/01/29 01:28:36 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\ImTOO Software Studio
[2009/06/19 22:40:38 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\LEGO Company
[2009/06/29 00:56:49 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\LPECommon
[2010/01/29 20:30:27 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\Megaupload
[2010/10/13 03:24:52 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\Quonxi
[2009/08/26 22:39:19 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\Search Settings
[2010/11/14 18:48:03 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\Ulead Systems
[2010/01/22 06:02:40 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\Uniblue
[2010/10/09 00:47:59 | 000,000,000 | —D | M] – C:\Documents and Settings\Paulie Cee\Application Data\Yhrale
[2010/12/22 20:08:33 | 000,000,472 | —- | M] () – C:\WINDOWS\Tasks\Ad-Aware Update (Weekly).job
[2010/12/26 02:43:00 | 000,000,454 | —- | M] () – C:\WINDOWS\Tasks\Driver Robot.job
[2010/12/29 18:32:49 | 000,000,236 | —- | M] () – C:\WINDOWS\Tasks\OGALogon.job
[2010/12/29 18:43:10 | 000,000,432 | -H– | M] () – C:\WINDOWS\Tasks\User_Feed_Synchronization-{F45238CF-3301-4D40-9AA8-3347E2B0F381}.job

========== Purity Check ==========


========== Custom Scans ==========


< %SYSTEMDRIVE%\*.* >
[2010/12/29 18:32:34 | 000,076,828 | —- | M] () – C:\aaw7boot.log
[2010/08/04 20:05:43 | 000,000,040 | —- | M] () – C:\Auth.prof
[2009/06/17 19:44:42 | 000,000,000 | —- | M] () – C:\AUTOEXEC.BAT
[2010/01/27 17:50:10 | 000,000,211 | RHS- | M] () – C:\boot.ini
[2009/09/24 16:31:48 | 000,024,399 | —- | M] () – C:\brave-little-toaster.jpg
[2009/06/17 19:44:42 | 000,000,000 | —- | M] () – C:\CONFIG.SYS
[2010/08/25 11:16:32 | 000,000,565 | —- | M] () – C:\hpfr5550.xml
[2010/08/25 11:16:31 | 000,065,716 | —- | M] () – C:\hph7350.log
[2009/06/17 19:44:42 | 000,000,000 | RHS- | M] () – C:\IO.SYS
[2009/09/11 03:06:41 | 000,000,464 | -H– | M] () – C:\IPH.PH
[2010/12/27 15:26:50 | 000,000,109 | —- | M] () – C:\mbam-error.txt
[2009/06/17 19:44:42 | 000,000,000 | RHS- | M] () – C:\MSDOS.SYS
[2009/06/17 18:11:15 | 000,047,564 | RHS- | M] () – C:\NTDETECT.COM
[2010/06/24 09:19:18 | 000,250,048 | RHS- | M] () – C:\ntldr
[2010/12/29 18:32:34 | 2145,386,496 | -HS- | M] () – C:\pagefile.sys
[2010/02/03 06:50:26 | 000,095,032 | —- | M] () – C:\TDSSKiller.2.2.2_03.02.2010_06.50.25_log.txt
[2010/01/27 17:19:18 | 000,035,914 | —- | M] () – C:\TDSSKiller.2.2.2_27.01.2010_17.19.17_log.txt
[2009/10/02 02:25:28 | 000,027,136 | -HS- | M] () – C:\Thumbs.db

< %systemroot%\Fonts\*.com >
[2006/04/18 14:39:28 | 000,026,040 | —- | M] () – C:\WINDOWS\Fonts\GlobalMonospace.CompositeFont
[2006/06/29 13:53:56 | 000,026,489 | —- | M] () – C:\WINDOWS\Fonts\GlobalSansSerif.CompositeFont
[2006/04/18 14:39:28 | 000,029,779 | —- | M] () – C:\WINDOWS\Fonts\GlobalSerif.CompositeFont
[2006/06/29 13:58:52 | 000,030,808 | —- | M] () – C:\WINDOWS\Fonts\GlobalUserInterface.CompositeFont

< %systemroot%\Fonts\*.dll >

< %systemroot%\Fonts\*.ini >
[2009/06/17 19:44:25 | 000,000,067 | -HS- | M] () – C:\WINDOWS\Fonts\desktop.ini

< %systemroot%\Fonts\*.ini2 >

< %systemroot%\Fonts\*.exe >

< %systemroot%\system32\spool\prtprocs\w32x86\*.* >
[2007/10/22 13:00:00 | 000,027,136 | —- | M] (CANON INC.) – C:\WINDOWS\system32\spool\prtprocs\w32x86\CNMPD97.DLL
[2007/10/22 13:00:00 | 000,069,632 | —- | M] (CANON INC.) – C:\WINDOWS\system32\spool\prtprocs\w32x86\CNMPP97.DLL
[2008/07/06 07:06:10 | 000,089,088 | —- | M] (Microsoft Corporation) – C:\WINDOWS\system32\spool\prtprocs\w32x86\filterpipelineprintproc.dll
[2006/10/26 18:56:12 | 000,033,104 | —- | M] (Microsoft Corporation) – C:\WINDOWS\system32\spool\prtprocs\w32x86\msonpppr.dll
[2008/07/06 05:50:04 | 000,597,504 | —- | M] (Microsoft Corporation) – C:\WINDOWS\system32\spool\prtprocs\w32x86\printfilterpipelinesvc.exe

< %systemroot%\REPAIR\*.bak1 >

< %systemroot%\REPAIR\*.ini >

< %systemroot%\system32\*.jpg >

< %systemroot%\*.jpg >

< %systemroot%\*.png >

< %systemroot%\*.scr >
[2010/09/07 11:12:17 | 000,038,848 | —- | M] (AVAST Software) – C:\WINDOWS\avastSS.scr
[4 C:\WINDOWS\*.tmp files -> C:\WINDOWS\*.tmp -> ]

< %systemroot%\*._sy >

< %APPDATA%\Adobe\Update\*.* >

< %ALLUSERSPROFILE%\Favorites\*.* >

< %APPDATA%\Microsoft\*.* >

< %PROGRAMFILES%\*.* >

< %APPDATA%\Update\*.* >

< %systemroot%\*. /mp /s >

< %systemroot%\System32\config\*.sav >
[2009/06/17 12:21:21 | 000,094,208 | —- | M] () – C:\WINDOWS\system32\config\default.sav
[2009/06/17 12:21:21 | 000,630,784 | —- | M] () – C:\WINDOWS\system32\config\software.sav
[2009/06/17 12:21:21 | 000,417,792 | —- | M] () – C:\WINDOWS\system32\config\system.sav

< %PROGRAMFILES%\bak. /s >

< %systemroot%\system32\bak. /s >

< %ALLUSERSPROFILE%\Start Menu\*.lnk /x >
[2010/06/24 09:30:21 | 000,000,272 | -HS- | M] () – C:\Documents and Settings\All Users\Start Menu\desktop.ini

< %systemroot%\system32\config\systemprofile\*.dat /x >

< %systemroot%\*.config >

< %systemroot%\system32\*.db >

< %APPDATA%\Microsoft\Internet Explorer\Quick Launch\*.lnk /x >
[2009/06/17 18:44:12 | 000,000,177 | -HS- | M] () – C:\Documents and Settings\Paulie Cee\Application Data\Microsoft\Internet Explorer\Quick Launch\desktop.ini
[2009/06/17 19:49:16 | 000,000,079 | —- | M] () – C:\Documents and Settings\Paulie Cee\Application Data\Microsoft\Internet Explorer\Quick Launch\Show Desktop.scf

< %USERPROFILE%\Desktop\*.exe >
[2009/09/23 17:03:51 | 007,053,240 | —- | M] (Hewlett-Packard Company							) – C:\Documents and Settings\Paulie Cee\Desktop\4241_enu_w2k_xp.exe
[2010/01/21 05:01:57 | 034,355,312 | —- | M] (PC Tools													) – C:\Documents and Settings\Paulie Cee\Desktop\7.0.0.514c-sdrevenue-setup.exe
[2009/06/17 18:18:26 | 037,452,296 | —- | M] (Lavasoft																																																																									) – C:\Documents and Settings\Paulie Cee\Desktop\Ad-AwareAE.exe
[2010/02/03 00:08:38 | 091,338,304 | —- | M] (Lavasoft																																																																									) – C:\Documents and Settings\Paulie Cee\Desktop\Ad-AwareInstallation.exe
[2009/06/24 15:27:18 | 026,739,584 | —- | M] (								   ) – C:\Documents and Settings\Paulie Cee\Desktop\AdbeRdr910_en_US.exe
[2010/02/14 18:45:31 | 010,105,696 | —- | M] (Alcohol Soft Development Team) – C:\Documents and Settings\Paulie Cee\Desktop\Alcohol120_trial_2.0.0.1331.exe
[2009/12/16 00:45:12 | 013,581,008 | —- | M] (CAM Development											 ) – C:\Documents and Settings\Paulie Cee\Desktop\bcdp9_setup.exe
[2009/06/21 23:11:23 | 021,128,536 | —- | M] (DivX, Inc.) – C:\Documents and Settings\Paulie Cee\Desktop\DivXInstaller.exe
[2010/02/24 23:57:44 | 001,038,696 | —- | M] (PC Drivers HeadQuarters									  ) – C:\Documents and Settings\Paulie Cee\Desktop\DriverDetective(2).exe
[2010/02/24 23:49:23 | 001,038,696 | —- | M] (PC Drivers HeadQuarters									  ) – C:\Documents and Settings\Paulie Cee\Desktop\DriverDetective.exe
[2010/01/22 05:32:53 | 002,672,312 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\esetsmartinstaller_enu.exe
[2010/12/29 18:40:16 | 000,132,597 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\Flash_Disinfector.exe
[2010/01/24 21:45:14 | 000,812,344 | —- | M] (Trend Micro Inc.) – C:\Documents and Settings\Paulie Cee\Desktop\HJTInstall.exe
[2009/06/18 18:56:55 | 016,883,056 | —- | M] (Microsoft Corporation) – C:\Documents and Settings\Paulie Cee\Desktop\IE8-WindowsXP-x86-ENU.exe
[2009/09/17 16:15:29 | 001,925,024 | —- | M] (Adobe Systems Incorporated) – C:\Documents and Settings\Paulie Cee\Desktop\install_flash_player.exe
[2009/10/03 02:07:18 | 000,714,136 | —- | M] (Sun Microsystems, Inc.) – C:\Documents and Settings\Paulie Cee\Desktop\jre-6u14-windows-i586-iftw.exe
[2010/12/29 19:23:34 | 000,080,384 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\MBRCheck.exe
[2010/12/29 19:22:58 | 000,602,624 | —- | M] (OldTimer Tools) – C:\Documents and Settings\Paulie Cee\Desktop\OTL.exe
[2010/12/29 19:23:15 | 000,133,632 | —- | M] () – C:\Documents and Settings\Paulie Cee\Desktop\RKUnhookerLE.EXE
[2010/02/17 15:29:31 | 006,279,486 | —- | M] (Koyote soft												 ) – C:\Documents and Settings\Paulie Cee\Desktop\Setup_FreeBurnerN.exe
[2009/07/08 20:21:20 | 025,740,144 | —- | M] (Microsoft Corporation) – C:\Documents and Settings\Paulie Cee\Desktop\wmp11-windowsxp-x86-enu.exe

< %PROGRAMFILES%\Common Files\*.* >

< %systemroot%\*.src >

< %systemroot%\install\*.* >

< %systemroot%\system32\DLL\*.* >

< %systemroot%\system32\HelpFiles\*.* >

< %systemroot%\system32\rundll\*.* >

< %systemroot%\winn32\*.* >

< %systemroot%\Java\*.* >

< %systemroot%\system32\test\*.* >

< %systemroot%\system32\Rundll32\*.* >

< %systemroot%\AppPatch\Custom\*.* >

< %APPDATA%\Roaming\Microsoft\Windows\Recent\*.lnk /x >

< %PROGRAMFILES%\PC-Doctor\Downloads\*.* >

< %PROGRAMFILES%\Internet Explorer\*.tmp >

< %PROGRAMFILES%\Internet Explorer\*.dat >

< %USERPROFILE%\My Documents\*.exe >

< %USERPROFILE%\*.exe >

< %systemroot%\ADDINS\*.* >

< %systemroot%\assembly\*.bak2 >

< %systemroot%\Config\*.* >

< %systemroot%\REPAIR\*.bak2 >

< %systemroot%\SECURITY\Database\*.sdb /x >

< %systemroot%\SYSTEM\*.bak2 >

< %systemroot%\Web\*.bak2 >

< %systemroot%\Driver Cache\*.* >

< %PROGRAMFILES%\Mozilla Firefox\0*.exe >

< %ProgramFiles%\Microsoft Common\*.* >

< %ProgramFiles%\TinyProxy. >

< %USERPROFILE%\Favorites\*.url /x >
[2009/06/17 18:44:12 | 000,000,122 | -HS- | M] () – C:\Documents and Settings\Paulie Cee\Favorites\Desktop.ini

< %systemroot%\system32\*.bk >

< %systemroot%\*.te >

< %systemroot%\system32\system32\*.* >

< %ALLUSERSPROFILE%\*.dat /x >

< %systemroot%\system32\drivers\*.rmv >

< dir /b "%systemroot%\system32\*.exe" | find /i " " /c >

< dir /b "%systemroot%\*.exe" | find /i " " /c >

< %PROGRAMFILES%\Microsoft\*.* >

< %systemroot%\System32\Wbem\proquota.exe >

< %PROGRAMFILES%\Mozilla Firefox\*.dat >

< %USERPROFILE%\Cookies\*.txt /x >
[2010/12/29 19:32:58 | 000,098,304 | —- | M] () – C:\Documents and Settings\Paulie Cee\Cookies\index.dat

< %SystemRoot%\system32\fonts\*.* >

< HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU >

< HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install|LastSuccessTime /rs >
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowsUpdate\Auto Update\Results\Install\\LastSuccessTime: 2010-12-26 08:13:06

< End of report >