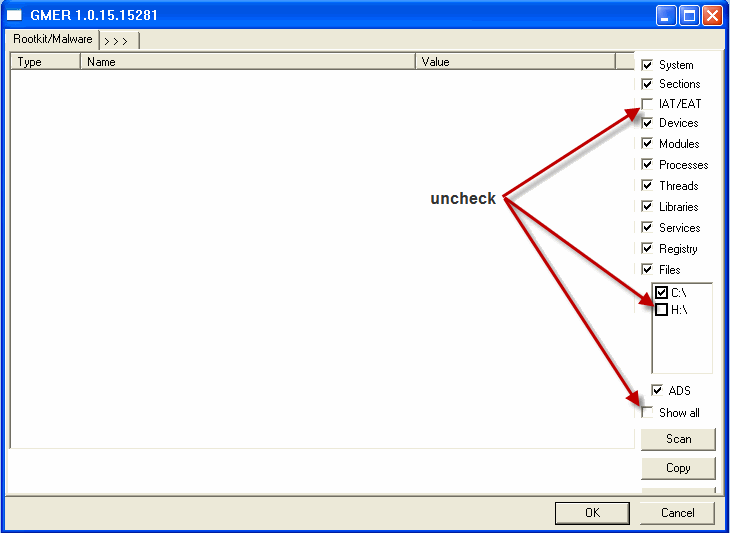
Hi Catbyte and thanks for stopping by.
All diagnostics successfully downloaded and ran UK.
Results:
MBR
MBRCheck, version 1.2.3
© 2010, AD
Command-line:
Windows Version: Windows XP Home Edition
Windows Information: Service Pack 3 (build 2600)
Logical Drives Mask: 0x0000000c
Kernel Drivers (total 137):
0x804D7000 \WINDOWS\system32\ntoskrnl.exe
0x806EE000 \WINDOWS\system32\hal.dll
0xF7AEF000 \WINDOWS\system32\KDCOM.DLL
0xF79FF000 \WINDOWS\system32\BOOTVID.dll
0xF75A0000 ACPI.sys
0xF7AF1000 \WINDOWS\system32\DRIVERS\WMILIB.SYS
0xF758F000 pci.sys
0xF75EF000 isapnp.sys
0xF75FF000 ohci1394.sys
0xF760F000 \WINDOWS\system32\DRIVERS\1394BUS.SYS
0xF7A03000 compbatt.sys
0xF7A07000 \WINDOWS\system32\DRIVERS\BATTC.SYS
0xF7BB7000 PCIIde.sys
0xF786F000 \WINDOWS\System32\Drivers\PCIIDEX.SYS
0xF7AF3000 intelide.sys
0xF7571000 pcmcia.sys
0xF761F000 MountMgr.sys
0xF7552000 ftdisk.sys
0xF7A0B000 ACPIEC.sys
0xF7BB8000 \WINDOWS\system32\DRIVERS\OPRGHDLR.SYS
0xF7877000 PartMgr.sys
0xF762F000 VolSnap.sys
0xF753A000 atapi.sys
0xF763F000 disk.sys
0xF764F000 \WINDOWS\system32\DRIVERS\CLASSPNP.SYS
0xF751A000 fltmgr.sys
0xF7508000 sr.sys
0xF765F000 PxHelp20.sys
0xF74F1000 KSecDD.sys
0xF74DE000 WudfPf.sys
0xF7451000 Ntfs.sys
0xF7424000 NDIS.sys
0xF766F000 Serial.sys
0xF740A000 Mup.sys
0xF6B78000 \SystemRoot\system32\DRIVERS\intelppm.sys
0xF7AAB000 \SystemRoot\system32\DRIVERS\CmBatt.sys
0xF6A6A000 \SystemRoot\system32\DRIVERS\ialmnt5.sys
0xF6A56000 \SystemRoot\system32\DRIVERS\VIDEOPRT.SYS
0xF791F000 \SystemRoot\system32\DRIVERS\usbuhci.sys
0xF6A32000 \SystemRoot\system32\DRIVERS\USBPORT.SYS
0xF7927000 \SystemRoot\system32\DRIVERS\usbehci.sys
0xF6A20000 \SystemRoot\system32\DRIVERS\Rtlnicxp.sys
0xF6710000 \SystemRoot\system32\DRIVERS\w29n51.sys
0xF6B68000 \SystemRoot\system32\DRIVERS\nic1394.sys
0xF66FB000 \SystemRoot\system32\drivers\tifm21.sys
0xF66E7000 \SystemRoot\system32\DRIVERS\sdbus.sys
0xF6B58000 \SystemRoot\system32\DRIVERS\i8042prt.sys
0xF792F000 \SystemRoot\system32\DRIVERS\kbdclass.sys
0xF66B9000 \SystemRoot\system32\DRIVERS\SynTP.sys
0xF7B15000 \SystemRoot\system32\DRIVERS\USBD.SYS
0xF7937000 \SystemRoot\system32\DRIVERS\mouclass.sys
0xF6B48000 \SystemRoot\system32\DRIVERS\imapi.sys
0xF6B38000 \SystemRoot\System32\Drivers\AFS2K.SYS
0xF7AAF000 \SystemRoot\system32\drivers\pfc.sys
0xF793F000 \SystemRoot\system32\drivers\iviaspi.sys
0xF6B28000 \SystemRoot\system32\DRIVERS\cdrom.sys
0xF6B18000 \SystemRoot\system32\DRIVERS\redbook.sys
0xF6696000 \SystemRoot\system32\DRIVERS\ks.sys
0xF6652000 \SystemRoot\system32\drivers\camchal.sys
0xF660A000 \SystemRoot\system32\drivers\camcaud.sys
0xF65E6000 \SystemRoot\system32\drivers\portcls.sys
0xF768F000 \SystemRoot\system32\drivers\drmk.sys
0xF65B5000 \SystemRoot\system32\DRIVERS\HSFHWICH.sys
0xF64B6000 \SystemRoot\system32\DRIVERS\HSF_DP.sys
0xF640E000 \SystemRoot\system32\DRIVERS\HSF_CNXT.sys
0xF7947000 \SystemRoot\System32\Drivers\Modem.SYS
0xF7AB7000 \SystemRoot\system32\DRIVERS\wmiacpi.sys
0xF7D0A000 \SystemRoot\system32\DRIVERS\audstub.sys
0xF7B17000 \SystemRoot\System32\Drivers\RootMdm.sys
0xF769F000 \SystemRoot\system32\DRIVERS\rasl2tp.sys
0xF7ABB000 \SystemRoot\system32\DRIVERS\ndistapi.sys
0xF63F7000 \SystemRoot\system32\DRIVERS\ndiswan.sys
0xF76AF000 \SystemRoot\system32\DRIVERS\raspppoe.sys
0xF76BF000 \SystemRoot\system32\DRIVERS\raspptp.sys
0xF794F000 \SystemRoot\system32\DRIVERS\TDI.SYS
0xF63E6000 \SystemRoot\system32\DRIVERS\psched.sys
0xF76CF000 \SystemRoot\system32\DRIVERS\msgpc.sys
0xF7967000 \SystemRoot\system32\DRIVERS\ptilink.sys
0xF796F000 \SystemRoot\system32\DRIVERS\raspti.sys
0xF7977000 \SystemRoot\system32\DRIVERS\RimSerial.sys
0xF76DF000 \SystemRoot\system32\DRIVERS\termdd.sys
0xF7B19000 \SystemRoot\system32\DRIVERS\swenum.sys
0xF6360000 \SystemRoot\system32\DRIVERS\update.sys
0xF7ACF000 \SystemRoot\system32\DRIVERS\mssmbios.sys
0xF634C000 \SystemRoot\system32\DRIVERS\vodafone_K3805-z_dc_enum.sys
0xF76EF000 \SystemRoot\system32\DRIVERS\WDFLDR.SYS
0xF62DB000 \SystemRoot\System32\Drivers\wdf01000.sys
0xF76FF000 \SystemRoot\System32\Drivers\NDProxy.SYS
0xF771F000 \SystemRoot\system32\DRIVERS\usbhub.sys
0xF7B1F000 \SystemRoot\System32\Drivers\Fs_Rec.SYS
0xF7C48000 \SystemRoot\System32\Drivers\Null.SYS
0xF7B21000 \SystemRoot\System32\Drivers\Beep.SYS
0xF7997000 \SystemRoot\System32\drivers\vga.sys
0xF7B23000 \SystemRoot\System32\Drivers\mnmdd.SYS
0xF7B25000 \SystemRoot\System32\DRIVERS\RDPCDD.sys
0xF799F000 \SystemRoot\System32\Drivers\Msfs.SYS
0xF79A7000 \SystemRoot\System32\Drivers\Npfs.SYS
0xF73C4000 \SystemRoot\system32\DRIVERS\rasacd.sys
0xEE1CB000 \SystemRoot\system32\DRIVERS\ipsec.sys
0xEE172000 \SystemRoot\system32\DRIVERS\tcpip.sys
0xEE14A000 \SystemRoot\system32\DRIVERS\netbt.sys
0xF73BC000 \SystemRoot\System32\drivers\ws2ifsl.sys
0xEE128000 \SystemRoot\System32\drivers\afd.sys
0xF774F000 \SystemRoot\system32\DRIVERS\netbios.sys
0xF79AF000 \SystemRoot\system32\DRIVERS\ssmdrv.sys
0xEE0FD000 \SystemRoot\system32\DRIVERS\rdbss.sys
0xEE065000 \SystemRoot\system32\DRIVERS\mrxsmb.sys
0xF775F000 \SystemRoot\System32\Drivers\Fips.SYS
0xEE03F000 \SystemRoot\system32\DRIVERS\ipnat.sys
0xF776F000 \SystemRoot\system32\DRIVERS\wanarp.sys
0xF777F000 \SystemRoot\system32\DRIVERS\arp1394.sys
0xF7B27000 \??\C:\WINDOWS\system32\drivers\EABFiltr.sys
0xEDF7D000 \SystemRoot\system32\DRIVERS\avipbb.sys
0xF7B2D000 \??\C:\Program Files\Avira\AntiVir Desktop\avgio.sys
0xF77EF000 \SystemRoot\System32\Drivers\Cdfs.SYS
0xEDF65000 \SystemRoot\System32\Drivers\dump_atapi.sys
0xF7B37000 \SystemRoot\System32\Drivers\dump_WMILIB.SYS
0xBF800000 \SystemRoot\System32\win32k.sys
0xF63CE000 \SystemRoot\System32\drivers\Dxapi.sys
0xF79CF000 \SystemRoot\System32\watchdog.sys
0xBF000000 \SystemRoot\System32\drivers\dxg.sys
0xF7C67000 \SystemRoot\System32\drivers\dxgthk.sys
0xBF020000 \SystemRoot\System32\ialmdnt5.dll
0xBF012000 \SystemRoot\System32\ialmrnt5.dll
0xBF040000 \SystemRoot\System32\ialmdev5.DLL
0xBF064000 \SystemRoot\System32\ialmdd5.DLL
0xBFFA0000 \SystemRoot\System32\ATMFD.DLL
0xEDE10000 \SystemRoot\system32\DRIVERS\avgntflt.sys
0xEDDF0000 \SystemRoot\system32\DRIVERS\ndisuio.sys
0xEDB63000 \SystemRoot\system32\DRIVERS\mrxdav.sys
0xEDA86000 \SystemRoot\system32\drivers\wdmaud.sys
0xEDD20000 \SystemRoot\system32\drivers\sysaudio.sys
0xED730000 \SystemRoot\system32\DRIVERS\mdmxsdk.sys
0xED5A1000 \SystemRoot\system32\DRIVERS\srv.sys
0xED305000 \??\C:\WINDOWS\system32\Drivers\uphcleanhlp.sys
0xED088000 \SystemRoot\System32\Drivers\HTTP.sys
0x7C900000 \WINDOWS\system32\ntdll.dll
Processes (total 47):
0 System Idle Process
4 System
596 C:\WINDOWS\system32\smss.exe
664 csrss.exe
688 C:\WINDOWS\system32\winlogon.exe
732 C:\WINDOWS\system32\services.exe
744 C:\WINDOWS\system32\lsass.exe
908 C:\WINDOWS\system32\svchost.exe
968 svchost.exe
1008 C:\WINDOWS\system32\svchost.exe
1040 C:\WINDOWS\system32\svchost.exe
1192 svchost.exe
1368 svchost.exe
1376 C:\WINDOWS\explorer.exe
1592 C:\WINDOWS\system32\spoolsv.exe
1640 C:\Program Files\Avira\AntiVir Desktop\sched.exe
1684 svchost.exe
212 C:\Program Files\Synaptics\SynTP\SynTPLpr.exe
236 C:\Program Files\Synaptics\SynTP\SynTPEnh.exe
252 C:\WINDOWS\system32\igfxtray.exe
300 C:\WINDOWS\system32\hkcmd.exe
324 C:\Program Files\QuickTime\QTTask.exe
332 C:\Program Files\HPQ\Quick Launch Buttons\eabservr.exe
392 C:\Program Files\Java\jre6\bin\jusched.exe
404 C:\Program Files\Hewlett-Packard\HP Software Update\hpwuSchd2.exe
428 C:\Program Files\Common Files\Research In Motion\Auto Update\RIMAutoUpdate.exe
436 C:\Program Files\Avira\AntiVir Desktop\avgnt.exe
460 C:\Program Files\Vodafone\Vodafone Mobile Connect\Bin\MobileConnect.exe
496 C:\Program Files\TomTom HOME 2\HOMERunner.exe
512 C:\PROGRA~1\COMMON~1\INSTAL~1\UPDATE~1\ISUSPM.exe
524 C:\WINDOWS\system32\ctfmon.exe
636 C:\Program Files\Hewlett-Packard\Digital Imaging\bin\hpqtra08.exe
780 C:\Program Files\Avira\AntiVir Desktop\avguard.exe
1056 C:\WINDOWS\system32\svchost.exe
776 C:\Program Files\Java\jre6\bin\jqs.exe
1244 C:\WINDOWS\system32\svchost.exe
1232 C:\WINDOWS\system32\svchost.exe
2032 C:\Program Files\Avira\AntiVir Desktop\avshadow.exe
2556 C:\WINDOWS\system32\svchost.exe
2592 C:\Program Files\UPHClean\uphclean.exe
2660 C:\Program Files\Vodafone\Vodafone Mobile Connect\Bin\VMCService.exe
2780 C:\WINDOWS\system32\wuauclt.exe
2112 alg.exe
3592 C:\WINDOWS\system32\svchost.exe
1356 C:\Program Files\Hewlett-Packard\Digital Imaging\bin\hpqste08.exe
2436 C:\Program Files\Avira\AntiVir Desktop\avcenter.exe
2612 C:\Documents and Settings\Derek Budden\Desktop\MBRCheck.exe
\\.\C: –> \\.\PhysicalDrive0 at offset 0x00000000`00007e00 (NTFS)
PhysicalDrive0 Model Number: ST960821A, Rev: 3.02
Size Device Name MBR Status
——————————————–
55 GB \\.\PhysicalDrive0 Windows XP MBR code detected
SHA1: DA38B874B7713D1B51CBC449F4EF809B0DEC644A
Done!
DDS
DDS (Ver_10-03-17.01) - NTFSx86
Run by [removed] at 21:37:01.32 on 05/08/2010
Internet Explorer: 8.0.6001.18702
Microsoft Windows XP Home Edition 5.1.2600.3.1252.44.1033.18.478.211 [GMT 1:00]
AV: AVG Anti-Virus Free *On-access scanning enabled* (Updated) {17DDD097-36FF-435F-9E1B-52D74245D6BF}
AV: AntiVir Desktop *On-access scanning disabled* (Outdated) {AD166499-45F9-482A-A743-FDD3350758C7}
============== Running Processes ===============
C:\WINDOWS\system32\svchost -k DcomLaunch
svchost.exe
C:\WINDOWS\System32\svchost.exe -k netsvcs
C:\WINDOWS\system32\svchost.exe -k WudfServiceGroup
svchost.exe
svchost.exe
C:\WINDOWS\Explorer.EXE
C:\WINDOWS\system32\spoolsv.exe
C:\Program Files\Avira\AntiVir Desktop\sched.exe
svchost.exe
C:\Program Files\Synaptics\SynTP\SynTPLpr.exe
C:\Program Files\Synaptics\SynTP\SynTPEnh.exe
C:\WINDOWS\system32\igfxtray.exe
C:\Program Files\QuickTime\QTTask.exe
C:\Program Files\HPQ\Quick Launch Buttons\EabServr.exe
C:\Program Files\Java\jre6\bin\jusched.exe
C:\Program Files\Hewlett-Packard\HP Software Update\HPWuSchd2.exe
C:\Program Files\Common Files\Research In Motion\Auto Update\RIMAutoUpdate.exe
C:\Program Files\Avira\AntiVir Desktop\avgnt.exe
C:\Program Files\Vodafone\Vodafone Mobile Connect\Bin\MobileConnect.exe
C:\Program Files\TomTom HOME 2\HOMERunner.exe
C:\Program Files\Common Files\InstallShield\UpdateService\ISUSPM.exe
C:\WINDOWS\system32\ctfmon.exe
C:\Program Files\Hewlett-Packard\Digital Imaging\bin\hpqtra08.exe
C:\Program Files\Avira\AntiVir Desktop\avguard.exe
C:\WINDOWS\system32\svchost.exe -k hpdevmgmt
C:\Program Files\Java\jre6\bin\jqs.exe
C:\WINDOWS\System32\svchost.exe -k HPZ12
C:\WINDOWS\System32\svchost.exe -k HPZ12
C:\Program Files\Avira\AntiVir Desktop\avshadow.exe
C:\WINDOWS\system32\svchost.exe -k imgsvc
C:\Program Files\UPHClean\uphclean.exe
C:\Program Files\Vodafone\Vodafone Mobile Connect\Bin\VMCService.exe
C:\WINDOWS\system32\wuauclt.exe
C:\WINDOWS\System32\svchost.exe -k HTTPFilter
C:\Program Files\Hewlett-Packard\Digital Imaging\bin\hpqSTE08.exe
C:\Program Files\Avira\AntiVir Desktop\avcenter.exe
C:\WINDOWS\system32\NOTEPAD.EXE
C:\Program Files\Internet Explorer\iexplore.exe
C:\Program Files\Internet Explorer\iexplore.exe
C:\Program Files\Internet Explorer\iexplore.exe
C:\Documents and Settings\Derek Budden\Desktop\dds.scr
============== Pseudo HJT Report ===============
uStart Page = hxxp://www.google.co.uk/
uSearchMigratedDefaultURL = hxxp://www.google.com/search?q={searchTerms}&sourceid=ie7&rls=com.microsoft:en-US&ie=utf8&oe=utf8
uSearchURL,(Default) = hxxp://www.google.com/search?q=%s
mSearchAssistant = hxxp://www.google.com/ie
mURLSearchHooks: H - No File
BHO: {02478D38-C3F9-4efb-9B51-7695ECA05670} - No File
BHO: Adobe PDF Link Helper: {18df081c-e8ad-4283-a596-fa578c2ebdc3} - c:\program files\common files\adobe\acrobat\activex\AcroIEHelperShim.dll
BHO: {3CA2F312-6F6E-4B53-A66E-4E65E497C8C0} - No File
BHO: Java™ Plug-In 2 SSV Helper: {dbc80044-a445-435b-bc74-9c25c1c588a9} - c:\program files\java\jre6\bin\jp2ssv.dll
BHO: JQSIEStartDetectorImpl Class: {e7e6f031-17ce-4c07-bc86-eabfe594f69c} - c:\program files\java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll
TB: {A057A204-BACC-4D26-9990-79A187E2698E} - No File
uRun: [TomTomHOME.exe] "c:\program files\tomtom home 2\HOMERunner.exe"
uRun: [ISUSPM] "c:\program files\common files\installshield\updateservice\ISUSPM.exe" -scheduler
uRun: [ctfmon.exe] c:\windows\system32\ctfmon.exe
mRun: [PHIME2002ASync] c:\windows\system32\ime\tintlgnt\TINTSETP.EXE /SYNC
mRun: [PHIME2002A] c:\windows\system32\ime\tintlgnt\TINTSETP.EXE /IMEName
mRun: [SynTPLpr] c:\program files\synaptics\syntp\SynTPLpr.exe
mRun: [SynTPEnh] c:\program files\synaptics\syntp\SynTPEnh.exe
mRun: [IgfxTray] c:\windows\system32\igfxtray.exe
mRun: [HotKeysCmds] c:\windows\system32\hkcmd.exe
mRun: [Cpqset] c:\program files\hpq\default settings\cpqset.exe
mRun: [QuickTime Task] "c:\program files\quicktime\QTTask.exe" -atboottime
mRun: [eabconfg.cpl] c:\program files\hpq\quick launch buttons\EabServr.exe /Start
mRun: [ISUSPM Startup] c:\progra~1\common~1\instal~1\update~1\ISUSPM.exe -startup
mRun: [ISUSScheduler] "c:\program files\common files\installshield\updateservice\issch.exe" -start
mRun: [SunJavaUpdateSched] "c:\program files\java\jre6\bin\jusched.exe"
mRun: [HP Software Update] c:\program files\hewlett-packard\hp software update\HPWuSchd2.exe
mRun: [BlackBerryAutoUpdate] c:\program files\common files\research in motion\auto update\RIMAutoUpdate.exe /background
mRun: [avgnt] "c:\program files\avira\antivir desktop\avgnt.exe" /min
mRun: [Adobe Reader Speed Launcher] "c:\program files\adobe\reader 9.0\reader\Reader_sl.exe"
mRun: [Adobe ARM] "c:\program files\common files\adobe\arm\1.0\AdobeARM.exe"
mRun: [MobileConnect] %programfiles%\Vodafone\Vodafone Mobile Connect\Bin\MobileConnect.exe /silent
mRun: []
mRun: [RoxWatchTray] "c:\program files\common files\roxio shared\9.0\sharedcom\RoxWatchTray9.exe"
dRun: [CTFMON.EXE] c:\windows\system32\CTFMON.EXE
StartupFolder: c:\docume~1\alluse~1\startm~1\programs\startup\deskto~1.lnk - c:\program files\research in motion\blackberry\DesktopMgr.exe
StartupFolder: c:\docume~1\alluse~1\startm~1\programs\startup\hpdigi~1.lnk - c:\program files\hewlett-packard\digital imaging\bin\hpqtra08.exe
StartupFolder: c:\docume~1\alluse~1\startm~1\programs\startup\micros~1.lnk - c:\program files\microsoft office\office\OSA9.EXE
IE: {e2e2dd38-d088-4134-82b7-f2ba38496583} - %windir%\Network Diagnostic\xpnetdiag.exe
IE: {FB5F1910-F110-11d2-BB9E-00C04F795683} - c:\program files\messenger\msmsgs.exe
DPF: Microsoft XML Parser for Java - file://c:\windows\java\classes\xmldso.cab
DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_16-windows-i586.cab
DPF: {CAFEEFAC-0016-0000-0016-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_16-windows-i586.cab
DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_16-windows-i586.cab
DPF: {D27CDB6E-AE6D-11CF-96B8-444553540000} - hxxp://fpdownload2.macromedia.com/get/shockwave/cabs/flash/swflash.cab
DPF: {D6E0B119-DCF2-4CD6-8DFB-7CFF1B70F7FF} - hxxps://bis.eu.blackberry.com/html/web/client_tools/TOImport.cab
DPF: {E2883E8F-472F-4FB0-9522-AC9BF37916A7} - hxxp://platformdl.adobe.com/NOS/getPlusPlus/1.6/gp.cab
Notify: avgrsstarter - avgrsstx.dll
Notify: igfxcui - igfxsrvc.dll
SSODL: WPDShServiceObj - {AAA288BA-9A4C-45B0-95D7-94D524869DB5} - c:\windows\system32\WPDShServiceObj.dll
================= FIREFOX ===================
FF - ProfilePath - c:\docume~1\derekb~1\applic~1\mozilla\firefox\profiles\4w8csc86.default\
FF - prefs.js: browser.search.selectedEngine - Yahoo! Search
FF - prefs.js: keyword.URL - hxxp://us.yhs.search.yahoo.com/avg/search?fr=yhs-avg&type=yahoo_avg_hs2-tb-web_us&p=
FF - component: c:\documents and settings\derek budden\application data\mozilla\firefox\profiles\4w8csc86.default\extensions\[removed]\components\AlotXpcom.dll
FF - plugin: c:\program files\common files\research in motion\bbwebsllauncher\NPWebSLLauncher.dll
FF - plugin: c:\program files\google\google earth\plugin\npgeplugin.dll
FF - HiddenExtension: Microsoft .NET Framework Assistant: {20a82645-c095-46ed-80e3-08825760534b} - c:\windows\microsoft.net\framework\v3.5\windows presentation foundation\dotnetassistantextension\
—- FIREFOX POLICIES —-
c:\program files\mozilla firefox\greprefs\all.js - pref("ui.use_native_colors", true);
c:\program files\mozilla firefox\greprefs\all.js - pref("ui.use_native_popup_windows", false);
c:\program files\mozilla firefox\greprefs\all.js - pref("browser.enable_click_image_resizing", true);
c:\program files\mozilla firefox\greprefs\all.js - pref("accessibility.browsewithcaret_shortcut.enabled", true);
c:\program files\mozilla firefox\greprefs\all.js - pref("javascript.options.mem.high_water_mark", 32);
c:\program files\mozilla firefox\greprefs\all.js - pref("javascript.options.mem.gc_frequency", 1600);
c:\program files\mozilla firefox\greprefs\all.js - pref("network.auth.force-generic-ntlm", false);
c:\program files\mozilla firefox\greprefs\all.js - pref("svg.smil.enabled", false);
c:\program files\mozilla firefox\greprefs\all.js - pref("ui.trackpoint_hack.enabled", -1);
c:\program files\mozilla firefox\greprefs\all.js - pref("browser.formfill.debug", false);
c:\program files\mozilla firefox\greprefs\all.js - pref("browser.formfill.agedWeight", 2);
c:\program files\mozilla firefox\greprefs\all.js - pref("browser.formfill.bucketSize", 1);
c:\program files\mozilla firefox\greprefs\all.js - pref("browser.formfill.maxTimeGroupings", 25);
c:\program files\mozilla firefox\greprefs\all.js - pref("browser.formfill.timeGroupingSize", 604800);
c:\program files\mozilla firefox\greprefs\all.js - pref("browser.formfill.boundaryWeight", 25);
c:\program files\mozilla firefox\greprefs\all.js - pref("browser.formfill.prefixWeight", 5);
c:\program files\mozilla firefox\greprefs\all.js - pref("html5.enable", false);
c:\program files\mozilla firefox\greprefs\security-prefs.js - pref("security.ssl3.rsa_seed_sha", true);
c:\program files\mozilla firefox\defaults\pref\firefox-branding.js - pref("app.update.download.backgroundInterval", 600);
c:\program files\mozilla firefox\defaults\pref\firefox-branding.js - pref("app.update.url.manual", "http://www.firefox.com");
c:\program files\mozilla firefox\defaults\pref\firefox-branding.js - pref("browser.search.param.yahoo-fr-ja", "mozff");
c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.{972ce4c6-7e08-4474-a285-3208198ce6fd}.name", "chrome://browser/locale/browser.properties");
c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.{972ce4c6-7e08-4474-a285-3208198ce6fd}.description", "chrome://browser/locale/browser.properties");
c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("xpinstall.whitelist.add", "addons.mozilla.org");
c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("xpinstall.whitelist.add.36", "getpersonas.com");
c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("lightweightThemes.update.enabled", true);
c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.allTabs.previews", false);
c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("plugins.hide_infobar_for_outdated_plugin", false);
c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("plugins.update.notifyUser", false);
c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("toolbar.customization.usesheet", false);
c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.taskbar.previews.enable", false);
c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.taskbar.previews.max", 20);
c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.taskbar.previews.cachetime", 20);
============= SERVICES / DRIVERS ===============
R1 avgio;avgio;c:\program files\avira\antivir desktop\avgio.sys [2010-4-10 11608]
R2 AntiVirSchedulerService;Avira AntiVir Scheduler;c:\program files\avira\antivir desktop\sched.exe [2010-4-10 135336]
R2 AntiVirService;Avira AntiVir Guard;c:\program files\avira\antivir desktop\avguard.exe [2010-4-10 267432]
R2 avgntflt;avgntflt;c:\windows\system32\drivers\avgntflt.sys [2010-4-10 60936]
R2 VMCService;Vodafone Mobile Connect Service;c:\program files\vodafone\vodafone mobile connect\bin\VMCService.exe [2010-3-15 9216]
R3 vodafone_K3805-z_dc_enum;Vodafone K3805-z DC Enumerator (ZTE);c:\windows\system32\drivers\vodafone_K3805-z_dc_enum.sys [2010-3-1 80000]
S2 gupdate;Google Update Service (gupdate);c:\program files\google\update\GoogleUpdate.exe [2009-11-15 135664]
S3 BTCOMM;BTCOMM;c:\windows\system32\drivers\btcomm.sys –> c:\windows\system32\drivers\Btcomm.sys [?]
S3 BTKRNBDG;Bluetooth COM Bridge;c:\windows\system32\drivers\btkrnbdg.sys –> c:\windows\system32\drivers\btkrnbdg.sys [?]
S3 vodafone_K3805-z_cdc_acm;Vodafone K3805-z CDC-ACM driver (ZTE);c:\windows\system32\drivers\vodafone_K3805-z_cdc_acm.sys [2010-3-1 86016]
S3 vodafone_K3805-z_cdc_ecm;vodafone_K3805-z_cdc_ecm;c:\windows\system32\drivers\vodafone_K3805-z_cdc_ecm.sys [2010-3-1 50304]
S3 vodafone_K3805-z_cpo;Vodafone K3805-z Install;c:\windows\system32\drivers\vodafone_K3805-z_cpo.sys [2010-3-1 9728]
=============== Created Last 30 ================
2010-08-01 23:15:55 718104 -c–a-w- C:\avgremover.exe
2010-07-20 20:34:13 744448 -c—-w- c:\windows\system32\dllcache\helpsvc.exe
==================== Find3M ====================
2010-06-30 22:05:33 0 —ha-w- c:\windows\system32\drivers\Msft_Kernel_vodafone_K3805-z_cdc_ecm_01009.Wdf
2010-06-30 22:05:16 0 —ha-w- c:\windows\system32\drivers\Msft_Kernel_vodafone_K3805-z_cdc_acm_01009.Wdf
2010-06-30 22:04:05 0 —ha-w- c:\windows\system32\drivers\Msft_Kernel_vodafone_K3805-z_dc_enum_01009.Wdf
2010-06-30 22:04:03 0 —ha-w- c:\windows\system32\drivers\MsftWdf_Kernel_01009_Coinstaller_Critical.Wdf
2008-09-04 12:11:00 32768 –sha-w- c:\windows\system32\config\systemprofile\local settings\history\history.ie5\mshist012008090420080905\index.dat
============= FINISH: 21:38:20.93 ===============
The file: ATTACH is - er - attached, as is the GMER output file
Thanks John
.