Optimus31489
Hi,
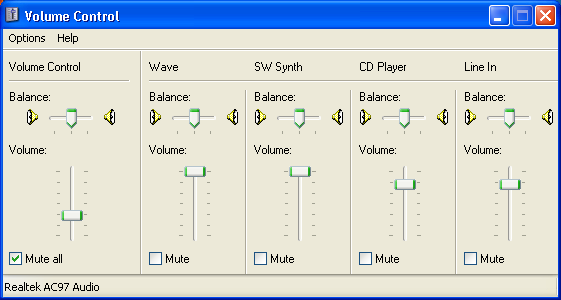
Sorry for the lack of clarity, my computer knowledge isn't very extensive. What I mean is that if i was playing a video game for example, my computer would exit me out of the game and take me straight to windows. The reason it does this is for 3 reasons from what I can tell : 1. for the pop up 2. for the audio pop up. or 3. is when the Master Audio panel.
This link shows what panel I am talking about, sorry I do not have a digital camera on me. http://www.askdavetaylor.com/0-blog-pics/w…ume-control.png
As you can see, the second section of the control is called wave, this section has the volume turned all the way down randomly, and this is what causes the "windowing" when I am playing games or doing something else. This happens right when the background iexplorer starts that I can see in task manager, but there is no actual internet window that I can see. I hope that makes it a little bit more specific.
Thank you so much for your patience, I really appreciate it.
3.00 Gb Total Physical Memory | 2.00 Gb Available Physical Memory | 82.00% Memory free
4.00 Gb Paging File | 4.00 Gb Available in Paging File | 92.00% Paging File free
Paging file location(s): C:\pagefile.sys 1536 3072 [binary data]
%SystemDrive% = C: | %SystemRoot% = C:\WINDOWS | %ProgramFiles% = C:\Program Files
Drive C: | 153.38 Gb Total Space | 25.55 Gb Free Space | 16.66% Space Free | Partition Type: NTFS
Drive D: | 3.86 Gb Total Space | 0.00 Gb Free Space | 0.00% Space Free | Partition Type: UDF
E: Drive not present or media not loaded
F: Drive not present or media not loaded
G: Drive not present or media not loaded
H: Drive not present or media not loaded
I: Drive not present or media not loaded
Computer Name: MARIO
Current User Name: Optimus
Logged in as Administrator.
Current Boot Mode: Normal
Scan Mode: Current user
Company Name Whitelist: On
Skip Microsoft Files: On
File Age = 90 Days
Output = Minimal
Quick Scan
========== Processes (SafeList) ==========
PRC - C:\Documents and Settings\Optimus\My Documents\Downloads\OTL(2).exe (OldTimer Tools)
PRC - C:\System Volume Information\Microsoft\smss.exe (Black Internet)
PRC - C:\System Volume Information\Microsoft\services.exe (Black Internet)
PRC - C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe (Safer-Networking Ltd.)
PRC - C:\WINDOWS\explorer.exe (Microsoft Corporation)
PRC - C:\Program Files\Viewpoint\Common\ViewpointService.exe (Viewpoint Corporation)
PRC - C:\Program Files\Common Files\AOL\1151188401\ee\aolsoftware.exe (America Online, Inc.)
PRC - C:\Program Files\Adobe\Photoshop Album Starter Edition\3.0\Apps\apdproxy.exe (Adobe Systems Incorporated)
PRC - C:\WINDOWS\system32\HPZipm12.exe (HP)
========== Modules (SafeList) ==========
MOD - C:\Documents and Settings\Optimus\My Documents\Downloads\OTL(2).exe (OldTimer Tools)
MOD - C:\WINDOWS\system32\msscript.ocx (Microsoft Corporation)
========== Win32 Services (SafeList) ==========
SRV - (getPlus® Helper) getPlus® – C:\Program Files\NOS\bin\getPlus_HelperSvc.exe (NOS Microsystems Ltd.)
SRV - (Viewpoint Manager Service) – C:\Program Files\Viewpoint\Common\ViewpointService.exe (Viewpoint Corporation)
SRV - (Pml Driver HPZ12) – C:\WINDOWS\system32\HPZipm12.exe (HP)
========== Driver Services (SafeList) ==========
DRV - (PnkBstrK) – C:\WINDOWS\system32\drivers\PnkBstrK.sys ()
DRV - (gdrv) – C:\WINDOWS\gdrv.sys (Windows ® 2000 DDK provider)
DRV - (nv) – C:\WINDOWS\system32\drivers\nv4_mini.sys (NVIDIA Corporation)
DRV - (IntcAzAudAddService) Service for Realtek HD Audio (WDM) – C:\WINDOWS\system32\drivers\RtkHDAud.sys (Realtek Semiconductor Corp.)
DRV - (RTLE8023xp) – C:\WINDOWS\system32\drivers\Rtenicxp.sys (Realtek Semiconductor Corporation )
DRV - (nm) – C:\WINDOWS\system32\drivers\nmnt.sys (Microsoft Corporation)
DRV - (gameenum) – C:\WINDOWS\system32\drivers\gameenum.sys (Microsoft Corporation)
DRV - (HDAudBus) – C:\WINDOWS\system32\drivers\hdaudbus.sys (Windows ® Server 2003 DDK provider)
DRV - (nvata) – C:\WINDOWS\system32\DRIVERS\nvata.sys (NVIDIA Corporation)
DRV - (nvnetbus) – C:\WINDOWS\system32\drivers\nvnetbus.sys (NVIDIA Corporation)
DRV - (NVENETFD) – C:\WINDOWS\system32\drivers\NVENETFD.sys (NVIDIA Corporation)
DRV - (prohlp02) – C:\WINDOWS\System32\drivers\prohlp02.sys (Protection Technology)
DRV - (prodrv06) – C:\WINDOWS\System32\drivers\prodrv06.sys (Protection Technology)
DRV - (MTsensor) – C:\WINDOWS\system32\drivers\ASACPI.sys ()
DRV - (sfhlp01) – C:\WINDOWS\System32\drivers\sfhlp01.sys (Protection Technology)
DRV - (ms_mpu401) – C:\WINDOWS\system32\drivers\msmpu401.sys (Microsoft Corporation)
========== Standard Registry (SafeList) ==========
========== Internet Explorer ==========
IE - HKLM\SOFTWARE\Microsoft\Internet Explorer\Main,Local Page = %SystemRoot%\system32\blank.htm
IE - HKLM\SOFTWARE\Microsoft\Internet Explorer\Search,Default_Search_URL = http://www.google.com/ie
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Main,Start Page = http://www.google.com/
IE - HKCU\SOFTWARE\Microsoft\Internet Explorer\Search,SearchAssistant = http://www.google.com/ie
IE - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings: "ProxyEnable" = 0
========== FireFox ==========
FF - prefs.js..browser.search.selectedEngine: "AIM Search"
FF - prefs.js..browser.startup.homepage: "http://en-us.start.mozilla.com/firefox?client=firefox-a&rls;=org.mozilla:en-US:official"
FF - prefs.js..extensions.enabledItems: [removed]:1.0
FF - prefs.js..extensions.enabledItems: {CAFEEFAC-0016-0000-0020-ABCDEFFEDCBA}:6.0.20
FF - prefs.js..keyword.URL: "http://slirsredirect.search.aol.com/slirs_http/sredir?invocationType=bu10aiminstabie7&sredir;=2706&query;="
FF - HKLM\software\mozilla\Mozilla Firefox 3.5.10\extensions\\Components: C:\Program Files\Mozilla Firefox\components [2010/06/24 00:48:31 | 000,000,000 | —D | M]
FF - HKLM\software\mozilla\Mozilla Firefox 3.5.10\extensions\\Plugins: C:\Program Files\Mozilla Firefox\plugins [2010/06/26 18:59:41 | 000,000,000 | —D | M]
[2009/11/15 19:40:59 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\Mozilla\Extensions
[2009/08/12 00:04:45 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\Mozilla\Extensions\[removed]
[2006/09/09 10:28:57 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\Mozilla\Firefox\Profiles\5oxadeo9.default\extensions
[2010/06/26 19:01:04 | 000,000,000 | —D | M] – C:\Program Files\Mozilla Firefox\extensions
[2010/06/26 18:59:43 | 000,000,000 | —D | M] (Java Console) – C:\Program Files\Mozilla Firefox\extensions\{CAFEEFAC-0016-0000-0020-ABCDEFFEDCBA}
[2010/06/26 18:59:30 | 000,411,368 | —- | M] (Sun Microsystems, Inc.) – C:\Program Files\Mozilla Firefox\plugins\npdeployJava1.dll
O1 HOSTS File: ([2010/06/26 11:22:39 | 000,000,027 | —- | M]) - C:\WINDOWS\system32\drivers\etc\hosts
O1 - Hosts: 127.0.0.1 localhost
O2 - BHO: (no name) - {3CA2F312-6F6E-4B53-A66E-4E65E497C8C0} - No CLSID value found.
O2 - BHO: (Spybot-S&D; IE Protection) - {53707962-6F74-2D53-2644-206D7942484F} - C:\Program Files\Spybot - Search & Destroy\SDHelper.dll (Safer Networking Limited)
O2 - BHO: (no name) - {761497BB-D6F0-462C-B6EB-D4DAF1D92D43} - No CLSID value found.
O2 - BHO: (no name) - {A3BC75A2-1F87-4686-AA43-5347D756017C} - No CLSID value found.
O3 - HKCU\..\Toolbar\ShellBrowser: (no name) - {2318C2B1-4965-11D4-9B18-009027A5CD4F} - No CLSID value found.
O3 - HKCU\..\Toolbar\ShellBrowser: (no name) - {CCC7A320-B3CA-4199-B1A6-9F516DD69829} - No CLSID value found.
O3 - HKCU\..\Toolbar\WebBrowser: (no name) - {EF99BD32-C1FB-11D2-892F-0090271D4F88} - No CLSID value found.
O4 - HKLM..\Run: [Adobe Photo Downloader] C:\Program Files\Adobe\Photoshop Album Starter Edition\3.0\Apps\apdproxy.exe (Adobe Systems Incorporated)
O4 - HKLM..\Run: [HostManager] C:\Program Files\Common Files\AOL\1151188401\ee\aolsoftware.exe (America Online, Inc.)
O4 - HKLM..\Run: [NvCplDaemon] C:\WINDOWS\System32\NvCpl.DLL (NVIDIA Corporation)
O4 - HKLM..\Run: [NvMediaCenter] C:\WINDOWS\System32\NvMcTray.DLL (NVIDIA Corporation)
O4 - HKCU..\Run: [H/PC Connection Agent] C:\PROGRA~1\MI3AA1~1\wcescomm.exe File not found
O4 - HKCU..\Run: [igndlm.exe] C:\Program Files\IGN\Download Manager\DLM.exe (IGN Entertainment)
O4 - HKCU..\Run: [SpybotSD TeaTimer] C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe (Safer-Networking Ltd.)
O4 - HKCU..\Run: [Steam] C:\Program Files\Steam\Steam.exe (Valve Corporation)
O4 - Startup: C:\Documents and Settings\All Users\Start Menu\Programs\Startup\HP Photosmart Premier Fast Start.lnk = C:\Program Files\HP\Digital Imaging\bin\hpqthb08.exe (Hewlett-Packard Development Company, L.P.)
O4 - Startup: C:\Documents and Settings\Optimus\Start Menu\Programs\Startup\OpenOffice.org 2.0.lnk = C:\Program Files\OpenOffice.org 2.0\program\quickstart.exe File not found
O4 - Startup: C:\Documents and Settings\Optimus\Start Menu\Programs\Startup\PowerReg Scheduler.exe ()
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: HonorAutoRunSetting = 1
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDriveAutoRun = 67108863
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDriveTypeAutoRun = 323
O6 - HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDrives = 0
O7 - HKCU\Software\Policies\Microsoft\Internet Explorer\Control Panel present
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDriveTypeAutoRun = 323
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDriveAutoRun = 67108863
O7 - HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer: NoDrives = 0
O8 - Extra context menu item: E&xport; to Microsoft Excel - C:\Program Files\Microsoft Office\Office12\EXCEL.EXE (Microsoft Corporation)
O9 - Extra 'Tools' menuitem : Spybot - Search & Destroy Configuration - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - C:\Program Files\Spybot - Search & Destroy\SDHelper.dll (Safer Networking Limited)
O16 - DPF: {166B1BCA-3F9C-11CF-8075-444553540000} http://fpdownload.macromedia.com/pub/shock…director/sw.cab (Shockwave ActiveX Control)
O16 - DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_20)
O16 - DPF: {8FFBE65D-2C9C-4669-84BD-5829DC0B603C} http://fpdownload.macromedia.com/get/flash…t/ultrashim.cab (Reg Error: Key error.)
O16 - DPF: {CAFEEFAC-0016-0000-0011-ABCDEFFEDCBA} Reg Error: Value error. (Reg Error: Key error.)
O16 - DPF: {CAFEEFAC-0016-0000-0020-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_20)
O16 - DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} http://java.sun.com/update/1.6.0/jinstall-…indows-i586.cab (Java Plug-in 1.6.0_20)
O16 - DPF: {CF40ACC5-E1BB-4AFF-AC72-04C2F616BCA7} http://wwwimages.adobe.com/www.adobe.com/p…obat/nos/gp.cab (get_atlcom Class)
O16 - DPF: {DE625294-70E6-45ED-B895-CFFA13AEB044} http://lioncam1.lmu.edu/activex/AMC.cab (Reg Error: Key error.)
O17 - HKLM\System\CCS\Services\Tcpip\Parameters: DhcpNameServer = 10.0.0.1
O18 - Protocol\Handler\ms-help {314111c7-a502-11d2-bbca-00c04f8ec294} - C:\Program Files\Common Files\Microsoft Shared\Help\hxds.dll (Microsoft Corporation)
O18 - Protocol\Filter\text/xml {807563E5-5146-11D5-A672-00B0D022E945} - C:\Program Files\Common Files\Microsoft Shared\OFFICE12\MSOXMLMF.DLL (Microsoft Corporation)
O20 - HKLM Winlogon: Shell - (Explorer.exe) - C:\WINDOWS\explorer.exe (Microsoft Corporation)
O20 - Winlogon\Notify\avgrsstarter: DllName - Reg Error: Value error. - Reg Error: Value error. File not found
O24 - Desktop WallPaper: C:\Documents and Settings\Optimus\Application Data\Microsoft\Internet Explorer\Internet Explorer Wallpaper.bmp
O24 - Desktop BackupWallPaper: C:\Documents and Settings\Optimus\Application Data\Microsoft\Internet Explorer\Internet Explorer Wallpaper.bmp
O32 - HKLM CDRom: AutoRun - 1
O32 - AutoRun File - [2006/06/24 14:06:56 | 000,000,000 | —- | M] () - C:\AUTOEXEC.BAT – [ NTFS ]
O32 - AutoRun File - [2008/08/05 10:02:19 | 000,398,600 | R— | M] (Electronic Arts Inc.) - D:\Autorun.exe – [ UDF ]
O32 - AutoRun File - [2008/08/05 09:23:19 | 000,000,043 | R— | M] () - D:\Autorun.inf – [ UDF ]
O32 - AutoRun File - [2008/08/05 09:52:02 | 000,000,000 | R–D | M] - D:\autorun – [ UDF ]
O34 - HKLM BootExecute: (autocheck autochk *) - File not found
O35 - HKLM\..comfile [open] – "%1" %*
O35 - HKLM\..exefile [open] – "%1" %*
O37 - HKLM\…com [@ = ComFile] – "%1" %*
O37 - HKLM\…exe [@ = exefile] – "%1" %*
NetSvcs: 6to4 - File not found
NetSvcs: Ias - C:\WINDOWS\system32\ias [2006/06/24 14:06:35 | 000,000,000 | —D | M]
NetSvcs: Iprip - File not found
NetSvcs: Irmon - File not found
NetSvcs: NWCWorkstation - File not found
NetSvcs: Nwsapagent - File not found
NetSvcs: Wmi - C:\WINDOWS\system32\wmi.dll (Microsoft Corporation)
NetSvcs: WmdmPmSp - File not found
Drivers32: aux - C:\WINDOWS\System32\wdmaud.drv (Microsoft Corporation)
Drivers32: midi - C:\WINDOWS\System32\wdmaud.drv (Microsoft Corporation)
Drivers32: midi1 - C:\WINDOWS\System32\wdmaud.drv (Microsoft Corporation)
Drivers32: midi2 - C:\WINDOWS\System32\wdmaud.drv (Microsoft Corporation)
Drivers32: midimapper - C:\WINDOWS\System32\midimap.dll (Microsoft Corporation)
Drivers32: mixer - C:\WINDOWS\System32\wdmaud.drv (Microsoft Corporation)
Drivers32: mixer1 - C:\WINDOWS\System32\wdmaud.drv (Microsoft Corporation)
Drivers32: msacm.iac2 - C:\WINDOWS\system32\iac25_32.ax (Intel Corporation)
Drivers32: msacm.imaadpcm - C:\WINDOWS\System32\imaadp32.acm (Microsoft Corporation)
Drivers32: msacm.l3acm - C:\WINDOWS\system32\l3codeca.acm (Fraunhofer Institut Integrierte Schaltungen IIS)
Drivers32: msacm.msadpcm - C:\WINDOWS\System32\msadp32.acm (Microsoft Corporation)
Drivers32: msacm.msaudio1 - C:\WINDOWS\System32\msaud32.acm (Microsoft Corporation)
Drivers32: msacm.msg711 - C:\WINDOWS\System32\msg711.acm (Microsoft Corporation)
Drivers32: msacm.msg723 - C:\WINDOWS\System32\msg723.acm (Microsoft Corporation)
Drivers32: msacm.msgsm610 - C:\WINDOWS\System32\msgsm32.acm (Microsoft Corporation)
Drivers32: msacm.sl_anet - C:\WINDOWS\System32\sl_anet.acm (Sipro Lab Telecom Inc.)
Drivers32: msacm.trspch - C:\WINDOWS\System32\tssoft32.acm (DSP GROUP, INC.)
Drivers32: vidc.cvid - C:\WINDOWS\System32\iccvid.dll (Radius Inc.)
Drivers32: vidc.DIVX - C:\WINDOWS\System32\DivX.dll (DivX, Inc.)
Drivers32: vidc.I420 - C:\WINDOWS\System32\msh263.drv (Microsoft Corporation)
Drivers32: vidc.iv31 - C:\WINDOWS\System32\ir32_32.dll ()
Drivers32: vidc.iv32 - C:\WINDOWS\System32\ir32_32.dll ()
Drivers32: vidc.iv41 - C:\WINDOWS\System32\ir41_32.ax (Intel Corporation)
Drivers32: vidc.iv50 - C:\WINDOWS\System32\ir50_32.dll (Intel Corporation)
Drivers32: vidc.iyuv - C:\WINDOWS\System32\iyuv_32.dll (Microsoft Corporation)
Drivers32: vidc.LEAD - LCODCCMP.DLL File not found
Drivers32: vidc.M261 - C:\WINDOWS\System32\msh261.drv (Microsoft Corporation)
Drivers32: vidc.M263 - C:\WINDOWS\System32\msh263.drv (Microsoft Corporation)
Drivers32: vidc.mrle - C:\WINDOWS\System32\msrle32.dll (Microsoft Corporation)
Drivers32: vidc.msvc - C:\WINDOWS\System32\msvidc32.dll (Microsoft Corporation)
Drivers32: vidc.uyvy - C:\WINDOWS\System32\msyuv.dll (Microsoft Corporation)
Drivers32: vidc.yuy2 - C:\WINDOWS\System32\msyuv.dll (Microsoft Corporation)
Drivers32: vidc.yv12 - C:\WINDOWS\System32\DivX.dll (DivX, Inc.)
Drivers32: vidc.yvu9 - C:\WINDOWS\System32\tsbyuv.dll (Microsoft Corporation)
Drivers32: vidc.yvyu - C:\WINDOWS\System32\msyuv.dll (Microsoft Corporation)
Drivers32: wave - C:\WINDOWS\System32\wdmaud.drv (Microsoft Corporation)
Drivers32: wave1 - C:\WINDOWS\System32\wdmaud.drv (Microsoft Corporation)
Drivers32: wavemapper - C:\WINDOWS\System32\msacm32.drv (Microsoft Corporation)
CREATERESTOREPOINT
Restore point Set: OTL Restore Point (16902109354000384)
========== Files/Folders - Created Within 90 Days ==========
[2010/06/26 19:00:57 | 000,000,000 | —D | C] – C:\Program Files\Common Files\Java
[2010/06/26 18:59:54 | 000,000,000 | —D | C] – C:\Documents and Settings\All Users\Application Data\Sun
[2010/06/26 18:59:46 | 000,000,000 | —D | C] – C:\Program Files\Sun
[2010/06/24 18:23:08 | 000,000,000 | —D | C] – C:\WINDOWS\temp
[2010/06/24 18:18:15 | 000,000,000 | RHSD | C] – C:\cmdcons
[2010/06/24 18:16:54 | 000,212,480 | —- | C] (SteelWerX) – C:\WINDOWS\SWXCACLS.exe
[2010/06/24 18:16:54 | 000,161,792 | —- | C] (SteelWerX) – C:\WINDOWS\SWREG.exe
[2010/06/24 18:16:54 | 000,136,704 | —- | C] (SteelWerX) – C:\WINDOWS\SWSC.exe
[2010/06/24 18:16:54 | 000,031,232 | —- | C] (NirSoft) – C:\WINDOWS\NIRCMD.exe
[2010/06/24 18:09:15 | 000,000,000 | —D | C] – C:\WINDOWS\ERDNT
[2010/06/24 18:08:13 | 000,000,000 | —D | C] – C:\Qoobox
[2010/06/23 15:37:01 | 000,000,000 | —D | C] – C:\Program Files\Windows Installer Clean Up
[2010/06/23 15:06:28 | 000,000,000 | RH-D | C] – C:\Documents and Settings\Optimus\Recent
[2010/06/23 01:23:44 | 000,000,000 | —D | C] – C:\Documents and Settings\Optimus\Application Data\Malwarebytes
[2010/06/23 01:23:38 | 000,038,224 | —- | C] (Malwarebytes Corporation) – C:\WINDOWS\System32\drivers\mbamswissarmy.sys
[2010/06/23 01:23:37 | 000,020,952 | —- | C] (Malwarebytes Corporation) – C:\WINDOWS\System32\drivers\mbam.sys
[2010/06/23 01:23:37 | 000,000,000 | —D | C] – C:\Program Files\Malwarebytes' Anti-Malware
[2010/06/23 01:23:37 | 000,000,000 | —D | C] – C:\Documents and Settings\All Users\Application Data\Malwarebytes
[2010/06/22 16:59:06 | 000,000,000 | —D | C] – C:\Documents and Settings\Optimus\My Documents\Heroes of Newerth
[2010/06/22 16:58:35 | 000,000,000 | —D | C] – C:\WINDOWS\Logs
[2010/06/22 16:58:21 | 000,000,000 | —D | C] – C:\Program Files\Heroes of Newerth
[2010/05/08 18:34:37 | 000,000,000 | —D | C] – C:\Documents and Settings\Optimus\WINDOWS
[2010/05/08 18:34:37 | 000,000,000 | —D | C] – C:\MAXIS
[2010/05/07 20:49:50 | 000,000,000 | —D | C] – C:\Documents and Settings\Optimus\My Documents\My Spore Creations
[2010/05/07 20:49:36 | 000,000,000 | —D | C] – C:\Documents and Settings\Optimus\Application Data\SPORE
[2010/04/13 11:48:18 | 000,000,000 | —D | C] – C:\Documents and Settings\Optimus\Desktop\Copy of LOTRO_World_Tour_installer
========== Files - Modified Within 90 Days ==========
[2010/06/27 00:42:15 | 000,194,449 | —- | M] () – C:\WINDOWS\System32\nvapps.xml
[2010/06/27 00:42:13 | 000,012,540 | —- | M] () – C:\WINDOWS\System32\wpa.dbl
[2010/06/27 00:40:44 | 000,000,006 | -H– | M] () – C:\WINDOWS\tasks\SA.DAT
[2010/06/27 00:40:43 | 000,002,048 | –S- | M] () – C:\WINDOWS\bootstat.dat
[2010/06/26 20:09:12 | 009,175,040 | -H– | M] () – C:\Documents and Settings\Optimus\NTUSER.DAT
[2010/06/26 20:09:12 | 000,000,178 | -HS- | M] () – C:\Documents and Settings\Optimus\ntuser.ini
[2010/06/26 18:41:33 | 080,398,104 | —- | M] () – C:\Documents and Settings\Optimus\Desktop\jdk-6u20-windows-i586.exe
[2010/06/26 18:35:51 | 000,001,729 | —- | M] () – C:\Documents and Settings\All Users\Desktop\Adobe Reader 9.lnk
[2010/06/26 11:22:44 | 000,000,227 | —- | M] () – C:\WINDOWS\system.ini
[2010/06/26 11:22:39 | 000,000,027 | —- | M] () – C:\WINDOWS\System32\drivers\etc\hosts
[2010/06/24 18:18:21 | 000,000,281 | RHS- | M] () – C:\boot.ini
[2010/06/24 18:14:45 | 000,000,666 | —- | M] () – C:\Documents and Settings\Optimus\Desktop\Shortcut to ComboFix.lnk
[2010/06/24 18:10:00 | 003,719,852 | R— | M] () – C:\Documents and Settings\Optimus\Desktop\ComboFix.exe
[2010/06/24 18:03:52 | 000,000,562 | -H– | M] () – C:\WINDOWS\tasks\Norton Security Scan for Optimus.job
[2010/06/24 11:05:45 | 000,001,464 | —- | M] () – C:\Documents and Settings\Optimus\Desktop\Roorepealscan
[2010/06/23 15:46:17 | 000,012,540 | —- | M] () – C:\WINDOWS\System32\wpa.bak
[2010/06/23 15:29:34 | 000,000,477 | —- | M] () – C:\WINDOWS\win.ini
[2010/06/23 15:29:34 | 000,000,211 | —- | M] () – C:\Boot.bak
[2010/06/22 16:59:07 | 000,001,606 | —- | M] () – C:\Documents and Settings\Optimus\Application Data\Microsoft\Internet Explorer\Quick Launch\Heroes of Newerth.lnk
[2010/06/22 16:59:07 | 000,001,588 | —- | M] () – C:\Documents and Settings\Optimus\Desktop\Heroes of Newerth.lnk
[2010/06/19 15:43:26 | 000,000,751 | —- | M] () – C:\Documents and Settings\All Users\Desktop\World of Warcraft.lnk
[2010/06/09 11:07:34 | 000,169,896 | —- | M] () – C:\WINDOWS\System32\FNTCACHE.DAT
[2010/06/08 22:19:46 | 000,036,483 | —- | M] () – C:\Documents and Settings\Optimus\Desktop\YUP.jpg
[2010/06/03 17:09:31 | 000,025,444 | —- | M] () – C:\Documents and Settings\Optimus\Desktop\fuckboston.jpg
[2010/05/28 22:52:01 | 000,000,284 | —- | M] () – C:\WINDOWS\tasks\AppleSoftwareUpdate.job
[2010/05/07 20:49:28 | 000,107,888 | —- | M] (Sony DADC Austria AG.) – C:\WINDOWS\System32\CmdLineExt.dll
[2010/05/06 09:25:22 | 000,002,515 | —- | M] () – C:\Documents and Settings\Optimus\Desktop\Microsoft Office Word 2007.lnk
[2010/05/05 22:08:29 | 000,013,688 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Sociology 100 Study Guide.docx
[2010/05/03 22:11:12 | 000,015,417 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Philosophy Study Guide.docx
[2010/05/03 11:03:34 | 000,013,080 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Mario Sou58.docx
[2010/05/02 19:06:06 | 000,382,347 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\I speak directly to the people.docx
[2010/04/29 21:20:00 | 000,061,569 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Introduction1.2FINAL.docx
[2010/04/29 15:39:38 | 000,038,224 | —- | M] (Malwarebytes Corporation) – C:\WINDOWS\System32\drivers\mbamswissarmy.sys
[2010/04/29 15:39:26 | 000,020,952 | —- | M] (Malwarebytes Corporation) – C:\WINDOWS\System32\drivers\mbam.sys
[2010/04/29 14:17:50 | 000,946,286 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Drive for Muscularity, Body Image, Gym.pptx
[2010/04/28 23:03:04 | 000,012,728 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Mario Sou57.docx
[2010/04/26 22:05:01 | 000,026,333 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\SOCFINALPAPER.docx
[2010/04/26 15:58:12 | 000,256,512 | —- | M] () – C:\WINDOWS\PEV.exe
[2010/04/25 22:06:46 | 000,025,682 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\In 1954 the U.docx
[2010/04/22 23:56:35 | 000,014,965 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Sociology Notes.docx
[2010/04/21 20:13:10 | 000,025,151 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Introduction1.1.docx
[2010/04/21 19:39:41 | 000,013,766 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Mario Sou56.docx
[2010/04/20 20:24:20 | 000,520,632 | —- | M] () – C:\Documents and Settings\Optimus\Desktop\adriana_lima_169.jpg
[2010/04/20 15:38:26 | 000,024,428 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Introduction.docx
[2010/04/19 23:07:18 | 000,017,722 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Walking through the grocery store.docx
[2010/04/18 19:21:41 | 000,014,609 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\This week we had to read about post modernism and Jean Baudrillard.docx
[2010/04/14 19:23:39 | 000,000,162 | -H– | M] () – C:\Documents and Settings\Optimus\My Documents\~$lking through the grocery store.docx
[2010/04/13 08:33:11 | 000,014,705 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Performance Enhancing Drugs Survey (1).docx
[2010/04/12 21:45:45 | 000,014,645 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Performance Enhancing Drugs Survey.docx
[2010/04/12 21:39:40 | 002,120,876 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\SINGH#1.pdf
[2010/04/12 19:30:58 | 000,013,639 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Mario Souza Coverletter (1).docx
[2010/04/12 19:23:04 | 000,039,936 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\Mario Souza Resume (1).doc
[2010/04/08 23:05:54 | 000,877,247 | —- | M] () – C:\Documents and Settings\Optimus\My Documents\DMSCALE.pdf
========== Files Created - No Company Name ==========
[2010/06/26 18:37:47 | 080,398,104 | —- | C] () – C:\Documents and Settings\Optimus\Desktop\jdk-6u20-windows-i586.exe
[2010/06/26 18:35:51 | 000,001,729 | —- | C] () – C:\Documents and Settings\All Users\Desktop\Adobe Reader 9.lnk
[2010/06/24 18:18:21 | 000,000,211 | —- | C] () – C:\Boot.bak
[2010/06/24 18:18:17 | 000,260,272 | —- | C] () – C:\cmldr
[2010/06/24 18:16:54 | 000,256,512 | —- | C] () – C:\WINDOWS\PEV.exe
[2010/06/24 18:16:54 | 000,098,816 | —- | C] () – C:\WINDOWS\sed.exe
[2010/06/24 18:16:54 | 000,080,412 | —- | C] () – C:\WINDOWS\grep.exe
[2010/06/24 18:16:54 | 000,077,312 | —- | C] () – C:\WINDOWS\MBR.exe
[2010/06/24 18:16:54 | 000,068,096 | —- | C] () – C:\WINDOWS\zip.exe
[2010/06/24 18:14:45 | 000,000,666 | —- | C] () – C:\Documents and Settings\Optimus\Desktop\Shortcut to ComboFix.lnk
[2010/06/24 18:10:00 | 003,719,852 | R— | C] () – C:\Documents and Settings\Optimus\Desktop\ComboFix.exe
[2010/06/24 11:05:45 | 000,001,464 | —- | C] () – C:\Documents and Settings\Optimus\Desktop\Roorepealscan
[2010/06/23 15:30:08 | 000,256,000 | —- | C] () – C:\Documents and Settings\Optimus\Start Menu\Programs\Startup\PowerReg Scheduler.exe
[2010/06/23 15:30:08 | 000,000,876 | —- | C] () – C:\Documents and Settings\Optimus\Start Menu\Programs\Startup\OpenOffice.org 2.0.lnk
[2010/06/22 16:59:07 | 000,001,606 | —- | C] () – C:\Documents and Settings\Optimus\Application Data\Microsoft\Internet Explorer\Quick Launch\Heroes of Newerth.lnk
[2010/06/22 16:59:06 | 000,001,588 | —- | C] () – C:\Documents and Settings\Optimus\Desktop\Heroes of Newerth.lnk
[2010/06/08 22:19:46 | 000,036,483 | —- | C] () – C:\Documents and Settings\Optimus\Desktop\YUP.jpg
[2010/06/03 17:09:31 | 000,025,444 | —- | C] () – C:\Documents and Settings\Optimus\Desktop\fuckboston.jpg
[2010/05/08 18:34:37 | 000,136,448 | —- | C] () – C:\WINDOWS\RMTOOLS.DLL
[2010/05/03 11:37:49 | 000,015,417 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Philosophy Study Guide.docx
[2010/05/02 19:36:54 | 000,013,080 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Mario Sou58.docx
[2010/05/01 22:41:29 | 000,013,688 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Sociology 100 Study Guide.docx
[2010/04/29 12:24:01 | 000,946,286 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Drive for Muscularity, Body Image, Gym.pptx
[2010/04/28 22:09:34 | 000,382,347 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\I speak directly to the people.docx
[2010/04/26 21:59:41 | 000,012,728 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Mario Sou57.docx
[2010/04/25 22:39:26 | 000,026,333 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\SOCFINALPAPER.docx
[2010/04/22 23:56:35 | 000,014,965 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Sociology Notes.docx
[2010/04/21 22:42:25 | 000,061,569 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Introduction1.2FINAL.docx
[2010/04/21 20:13:10 | 000,025,151 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Introduction1.1.docx
[2010/04/21 16:36:03 | 000,013,766 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Mario Sou56.docx
[2010/04/20 20:24:20 | 000,520,632 | —- | C] () – C:\Documents and Settings\Optimus\Desktop\adriana_lima_169.jpg
[2010/04/20 12:19:27 | 000,025,682 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\In 1954 the U.docx
[2010/04/18 19:21:40 | 000,014,609 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\This week we had to read about post modernism and Jean Baudrillard.docx
[2010/04/14 19:23:39 | 000,000,162 | -H– | C] () – C:\Documents and Settings\Optimus\My Documents\~$lking through the grocery store.docx
[2010/04/13 08:33:11 | 000,014,705 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Performance Enhancing Drugs Survey (1).docx
[2010/04/12 22:11:51 | 000,017,722 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Walking through the grocery store.docx
[2010/04/12 21:39:40 | 002,120,876 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\SINGH#1.pdf
[2010/04/12 19:24:07 | 000,013,639 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Mario Souza Coverletter (1).docx
[2010/04/12 19:23:04 | 000,039,936 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Mario Souza Resume (1).doc
[2010/04/09 21:19:03 | 000,014,645 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\Performance Enhancing Drugs Survey.docx
[2010/04/08 23:05:54 | 000,877,247 | —- | C] () – C:\Documents and Settings\Optimus\My Documents\DMSCALE.pdf
[2009/06/10 08:29:34 | 001,724,416 | —- | C] () – C:\WINDOWS\System32\nvwdmcpl.dll
[2009/06/10 08:29:34 | 001,101,824 | —- | C] () – C:\WINDOWS\System32\nvwimg.dll
[2009/06/10 08:29:34 | 000,466,944 | —- | C] () – C:\WINDOWS\System32\nvshell.dll
[2009/06/10 08:29:32 | 001,507,328 | —- | C] () – C:\WINDOWS\System32\nview.dll
[2008/11/18 13:44:40 | 000,000,000 | —- | C] () – C:\WINDOWS\iPlayer.INI
[2008/10/07 09:13:30 | 000,197,912 | —- | C] () – C:\WINDOWS\System32\physxcudart_20.dll
[2008/10/07 09:13:22 | 000,058,648 | —- | C] () – C:\WINDOWS\System32\AgCPanelTraditionalChinese.dll
[2008/10/07 09:13:20 | 000,058,648 | —- | C] () – C:\WINDOWS\System32\AgCPanelSwedish.dll
[2008/10/07 09:13:20 | 000,058,648 | —- | C] () – C:\WINDOWS\System32\AgCPanelSpanish.dll
[2008/10/07 09:13:20 | 000,058,648 | —- | C] () – C:\WINDOWS\System32\AgCPanelSimplifiedChinese.dll
[2008/10/07 09:13:20 | 000,058,648 | —- | C] () – C:\WINDOWS\System32\AgCPanelPortugese.dll
[2008/10/07 09:13:20 | 000,058,648 | —- | C] () – C:\WINDOWS\System32\AgCPanelKorean.dll
[2008/10/07 09:13:20 | 000,058,648 | —- | C] () – C:\WINDOWS\System32\AgCPanelJapanese.dll
[2008/10/07 09:13:20 | 000,058,648 | —- | C] () – C:\WINDOWS\System32\AgCPanelGerman.dll
[2008/10/07 09:13:20 | 000,058,648 | —- | C] () – C:\WINDOWS\System32\AgCPanelFrench.dll
[2007/12/18 19:17:38 | 000,137,544 | —- | C] () – C:\WINDOWS\System32\drivers\PnkBstrK.sys
[2007/05/27 21:49:01 | 000,000,047 | —- | C] () – C:\WINDOWS\NeroDigital.ini
[2007/03/31 16:46:15 | 000,000,023 | —- | C] () – C:\WINDOWS\BlendSettings.ini
[2006/09/13 14:21:44 | 000,000,173 | —- | C] () – C:\WINDOWS\wininit.ini
[2006/08/31 16:52:19 | 000,077,824 | R— | C] () – C:\WINDOWS\System32\hpzids01.dll
[2006/08/14 14:20:26 | 000,043,520 | —- | C] () – C:\WINDOWS\System32\CmdLineExt03.dll
[2006/06/24 15:31:19 | 000,000,029 | —- | C] () – C:\WINDOWS\atid.ini
[2006/06/24 14:27:14 | 000,000,169 | —- | C] () – C:\WINDOWS\RtlRack.ini
[2006/06/24 14:13:17 | 000,000,269 | R— | C] () – C:\WINDOWS\System32\raidmgmt.ini
[2006/06/24 14:12:58 | 000,005,810 | R— | C] () – C:\WINDOWS\System32\drivers\ASACPI.sys
[2006/06/24 14:12:55 | 000,005,309 | —- | C] () – C:\WINDOWS\Ascd_tmp.ini
[2006/06/24 14:12:53 | 000,005,824 | —- | C] () – C:\WINDOWS\System32\drivers\ASUSHWIO.SYS
[2006/06/01 17:22:00 | 000,581,632 | —- | C] () – C:\WINDOWS\System32\nvhwvid.dll
[2006/06/01 17:22:00 | 000,286,720 | —- | C] () – C:\WINDOWS\System32\nvnt4cpl.dll
[2001/07/06 16:30:00 | 000,003,399 | —- | C] () – C:\WINDOWS\System32\hptcpmon.ini
========== LOP Check ==========
[2009/09/08 20:12:08 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\acccore
[2009/05/12 09:40:51 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\Viewpoint
[2008/12/17 19:44:40 | 000,000,000 | —D | M] – C:\Documents and Settings\All Users\Application Data\{3276BE95_AF08_429F_A64F_CA64CB79BCF6}
[2006/06/24 15:33:53 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\acccore
[2009/09/08 17:35:27 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\Aim
[2007/09/15 09:35:54 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\BitTorrent
[2007/04/07 18:32:43 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\GetRightToGo
[2007/09/12 21:27:28 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\Leadertech
[2006/11/19 10:12:38 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\My Battle for Middle-earth™ II Files
[2009/12/24 18:49:30 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\runic games
[2006/10/11 21:50:43 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\Simple Star
[2006/10/11 22:08:28 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\Snapfish
[2010/05/07 20:49:36 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\SPORE
[2007/04/07 19:05:54 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\Turbine
[2007/01/27 02:08:37 | 000,000,000 | —D | M] – C:\Documents and Settings\Optimus\Application Data\Viewpoint
========== Purity Check ==========
========== Custom Scans ==========
< %SYSTEMDRIVE%\*.* >
[2007/02/20 22:06:17 | 003,517,236 | —- | M] () – C:\01 The Second Coming.m4p
[2006/06/26 20:01:54 | 000,004,632 | —- | M] () – C:\0x0409.ini
[2006/06/26 20:01:55 | 000,740,864 | —- | M] () – C:\1033.MST
[2006/06/24 14:06:56 | 000,000,000 | —- | M] () – C:\AUTOEXEC.BAT
[2006/06/28 18:16:36 | 005,381,769 | —- | M] () – C:\Big tymers - Still Fly .mp3
[2010/06/23 15:29:34 | 000,000,211 | —- | M] () – C:\Boot.bak
[2010/06/24 18:18:21 | 000,000,281 | RHS- | M] () – C:\boot.ini
[2004/08/03 23:00:00 | 000,260,272 | —- | M] () – C:\cmldr
[2010/06/26 11:23:43 | 000,014,749 | —- | M] () – C:\ComboFix.txt
[2006/06/24 14:06:56 | 000,000,000 | —- | M] () – C:\CONFIG.SYS
[2008/09/12 16:05:58 | 000,000,127 | —- | M] () – C:\CountCyclesWMVDecLog.txt
[2009/06/16 12:02:19 | 000,000,197 | —- | M] () – C:\csb.log
[2006/07/02 10:27:27 | 003,035,371 | —- | M] () – C:\Destiny's Child - Survivor .mp3
[2006/07/06 14:20:15 | 008,522,092 | —- | M] () – C:\Imogen Heap - Speeding Cars.mp3
[2006/06/24 14:06:56 | 000,000,000 | RHS- | M] () – C:\IO.SYS
[2006/06/26 20:01:59 | 033,954,304 | —- | M] () – C:\iPod for Windows 2006-03-23.msi
[2006/06/29 22:59:36 | 005,919,056 | —- | M] () – C:\Mario - Let Me Love You.mp3
[2006/06/29 22:54:16 | 003,837,283 | —- | M] () – C:\Marvin Gaye - Lets Get It On.mp3
[2006/06/24 14:06:56 | 000,000,000 | RHS- | M] () – C:\MSDOS.SYS
[2006/06/29 22:57:14 | 001,206,272 | —- | M] () – C:\National Anthem - American (Star Spangled Banner).mp3
[2004/08/04 05:00:00 | 000,047,564 | RHS- | M] () – C:\NTDETECT.COM
[2009/05/14 17:39:07 | 000,250,048 | RHS- | M] () – C:\ntldr
[2010/06/27 00:40:39 | 1610,612,736 | -HS- | M] () – C:\pagefile.sys
[2009/06/16 11:58:24 | 000,001,519 | —- | M] () – C:\RHDSetup.log
[2006/07/06 14:25:43 | 005,861,729 | —- | M] () – C:\Sean Paul ft Keisha Cole - Give It Up To Me (remix).mp3
< %systemroot%\system32\Spool\prtprocs\w32x86\*.dll >
[2005/10/14 22:41:46 | 000,072,192 | —- | M] (Hewlett-Packard Corporation) – C:\WINDOWS\system32\spool\prtprocs\w32x86\hpzpp43a.dll
[2006/10/26 19:56:12 | 000,033,104 | —- | M] (Microsoft Corporation) – C:\WINDOWS\system32\spool\prtprocs\w32x86\msonpppr.dll
< %systemroot%\*. /mp /s >
< %systemroot%\system32\*.dll /lockedfiles >
[2008/04/13 17:11:51 | 000,033,280 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\cryptdll.dll
[2008/04/13 17:11:55 | 000,094,720 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\iphlpapi.dll
[2008/04/13 17:11:59 | 002,843,136 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\msi.dll
[2004/08/04 05:00:00 | 000,146,432 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\msls31.dll
[2008/04/13 11:30:46 | 000,061,440 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\msvcrt40.dll
[2008/04/13 17:12:03 | 000,237,056 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\rasapi32.dll
[2008/04/13 17:12:03 | 000,061,440 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\rasman.dll
[2008/04/13 17:12:04 | 000,433,664 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\riched20.dll
[2008/04/13 17:12:04 | 000,044,032 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\rtutils.dll
[2008/04/13 17:12:05 | 000,007,168 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\sensapi.dll
[2008/04/13 17:12:07 | 000,713,216 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\sxs.dll
[2008/04/13 17:12:07 | 000,181,760 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\tapi32.dll
[2008/04/13 17:12:10 | 000,022,528 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\wsock32.dll
[2008/04/13 10:39:24 | 002,897,920 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\xpsp2res.dll
< %systemroot%\Tasks\*.job /lockedfiles >
< %systemroot%\System32\config\*.sav >
[2006/06/24 21:51:37 | 000,094,208 | —- | M] () – C:\WINDOWS\system32\config\default.sav
[2006/06/24 21:51:37 | 000,634,880 | —- | M] () – C:\WINDOWS\system32\config\software.sav
[2006/06/24 21:51:37 | 000,897,024 | —- | M] () – C:\WINDOWS\system32\config\system.sav
< %systemroot%\system32\user32.dll /md5 >
[2008/04/13 17:12:08 | 000,578,560 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\user32.dll
< %systemroot%\system32\ws2_32.dll /md5 >
[2008/04/13 17:12:10 | 000,082,432 | —- | M] (Microsoft Corporation) Unable to obtain MD5 – C:\WINDOWS\system32\ws2_32.dll
< End of report >
ROOTREPEAL © AD, 2007-2010
==================================================
Report Save Time: 2010/06/27 00:59
Program Version: Version 2.0.0.0
Windows Version: Windows XP SP3
==================================================
STEALTH CODE
——————-
System 0xe2414c30 - Hidden Code [Driver: prodrv06, IRP: IRP_MJ_CLOSE]
System 0xe2414c30 - Hidden Code [Driver: prodrv06, IRP: IRP_MJ_CREATE]
System 0xe2414c30 - Hidden Code [Driver: prodrv06, IRP: IRP_MJ_DEVICE_CONTROL]
System 0xe1016a60 - Hidden Code [Driver: prohlp02, IRP: IRP_MJ_CLOSE]
System 0xe1016a60 - Hidden Code [Driver: prohlp02, IRP: IRP_MJ_CREATE]
System 0xe1016a60 - Hidden Code [Driver: prohlp02, IRP: IRP_MJ_DEVICE_CONTROL]
TeaTimer.exe 0x8a072998 - Hidden Handle [Index: 296, Type: Event]