This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

[Resolved] PC infected w/ possible antispyware soft virus

23 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

Help. PC is possibly infected, i have malware bytes and webroot antivirus, webroot keeps prompting for blocked address for Z0G7YA1I0.com and ive ran malware bytes and webroot in safe mode several times to try and get rid of said item, ive also had the stuff re appear after rebooting in reg mode. also when ever i google something , it gets redirected, any help is appreciated,
what was the error message you received, or what was the result when you tried to post into the malware removal forum?

I will work with you in this forum to get you cleaned up a wee bit, until you gain control of your computer and I can move this thread to Malware removal

NOTE: This forum has no restrictions as to who may post to it. Please only follow the instructions in my posts

Thank-you:

Now please do the following:

Hi and Welcome,

Please do the following:

Please download DDS from either of these links

LINK 1
LINK 2

and save it to your desktop.
  • Disable any script blocking protection
  • Double click dds.pif to run the tool.
  • When done, two DDS.txt's will open.
  • Save both reports to your desktop.
—————————————————
Please include the contents of the following in your next reply:

DDS.txt
Attach.txt.


NEXT


Download GMER Rootkit Scanner from here to your desktop. It will be a randomly named executable.
  • Double click the exe file.
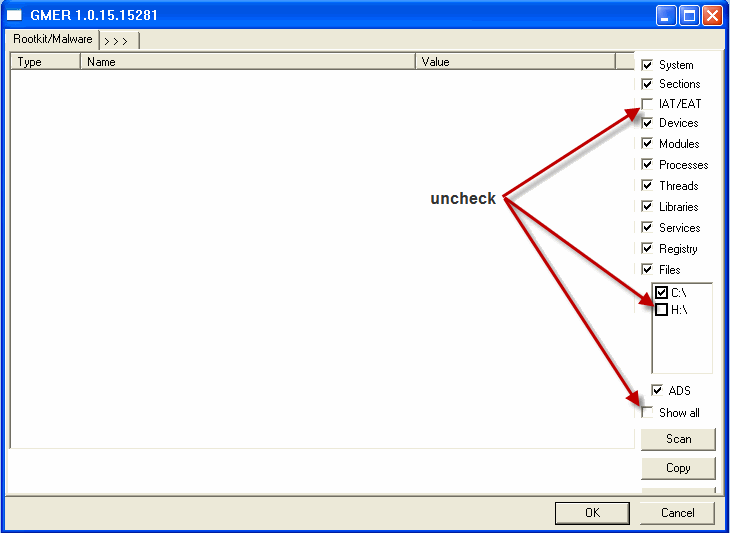
  • If it gives you a warning about rootkit activity and asks if you want to run scan…click on NO, then use the following settings for a more complete scan.


    [external image: Posted Image]
    Click the image to enlarge it


  • In the right panel, you will see several boxes that have been checked. Ensure the following are unchecked
    • IAT/EAT
    • Drives/Partition other than Systemdrive (typically C:\)
    • Show All (don't miss this one)
  • Then click the Scan button & wait for it to finish.
  • Once done click on the [Save..] button, and in the File name area, type in "Gmer.txt" or it will save as a .log file which cannot be uploaded to your post.
  • Save it where you can easily find it, such as your desktop, and attach it in reply.

**Caution**
Rootkit scans often produce false positives. Do NOT take any action on any "<— ROOKIT" entries
Try it in safe mode

If you are using a USB stick to copy/paste the files,

use this program to disinfect the USB stick so you don't transfer any infection:

Download Flash_Disinfector.exe from HERE and save it to your desktop.

  • Double-click Flash_Disinfector.exe to run it and follow any prompts that may appear.
  • The utility may ask you to insert your flash drive and/or other removable drives including your mobile phone. Please do so and allow the utility to clean up those drives as well.
  • Wait until it has finished scanning and then exit the program.
  • Reboot your computer when done.
When i tried to post, i hit new topic and it went right to the sign on page even tho i was already signed in heres the DDS results ill send the GMER scan next DDS (Ver_10-03-17.01) - NTFSx86 Run by [removed] at 0:34:38.29 on Mon 05/31/2010 Internet Explorer: 7.0.5730.13 Microsoft Windows XP Home Edition 5.1.2600.3.1252.1.1033.18.2039.1640 [GMT -5:00] AV: Norton Internet Security *On-access scanning enabled* (Outdated) {E10A9785-9598-4754-B552-92431C1C35F8} AV: Webroot AntiVirus with Spy Sweeper *On-access scanning disabled* (Updated) {77E10C7F-2CCA-4187-9394-BDBC267AD597} FW: Norton Internet Security *disabled* {7C21A4C9-F61F-4AC4-B722-A6E19C16F220} ============== Running Processes =============== C:\Program Files\Webroot\WebrootSecurity\WRConsumerService.exe C:\WINDOWS\system32\svchost -k DcomLaunch svchost.exe C:\WINDOWS\System32\svchost.exe -k netsvcs svchost.exe svchost.exe C:\WINDOWS\system32\spoolsv.exe svchost.exe C:\WINDOWS\Explorer.EXE C:\WINDOWS\system32\svchost.exe -k imgsvc C:\Program Files\Webroot\WebrootSecurity\SpySweeper.exe C:\WINDOWS\system32\igfxpers.exe C:\Program Files\Synaptics\SynTP\SynTPEnh.exe C:\WINDOWS\system32\ctfmon.exe C:\WINDOWS\system32\igfxsrvc.exe C:\Program Files\Internet Explorer\IEXPLORE.EXE C:\Documents and Settings\Owner\Desktop\dds.com ============== Pseudo HJT Report =============== uStart Page = hxxp://foxnews.com/ BHO: Adobe PDF Link Helper: {18df081c-e8ad-4283-a596-fa578c2ebdc3} - c:\program files\common files\adobe\acrobat\activex\AcroIEHelperShim.dll BHO: WormRadar.com IESiteBlocker.NavFilter: {3ca2f312-6f6e-4b53-a66e-4e65e497c8c0} - AVG Safe Search BHO: hpBHO Class: {abd3b5e1-b268-407b-a150-2641dab8d898} - c:\program files\common files\homepage protection\HomepageProtection.dll BHO: Microsoft Live Search Toolbar Helper: {d2ce3e00-f94a-4740-988e-03dc2f38c34f} - c:\program files\msn\toolbar\3.0.0560.0\msneshellx.dll BHO: Java™ Plug-In 2 SSV Helper: {dbc80044-a445-435b-bc74-9c25c1c588a9} - c:\program files\java\jre6\bin\jp2ssv.dll BHO: JQSIEStartDetectorImpl Class: {e7e6f031-17ce-4c07-bc86-eabfe594f69c} - c:\program files\java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll TB: Microsoft Live Search Toolbar: {1e61ed7c-7cb8-49d6-b9e9-ab4c880c8414} - c:\program files\msn\toolbar\3.0.0560.0\msneshellx.dll TB: {604BC32A-9680-40D1-9AC6-E06B23A1BA4C} - No File uRun: [ctfmon.exe] "c:\windows\system32\ctfmon.exe" mRun: [IgfxTray] "c:\windows\system32\igfxtray.exe" mRun: [HotKeysCmds] "c:\windows\system32\hkcmd.exe" mRun: [Persistence] "c:\windows\system32\igfxpers.exe" mRun: [SynTPEnh] "c:\program files\synaptics\syntp\SynTPEnh.exe" mRun: [QuickTime Task] "c:\program files\quicktime\qttask.exe" -atboottime mRun: [SpySweeper] "c:\program files\webroot\webrootsecurity\SpySweeperUI.exe" /startintray IE: {e2e2dd38-d088-4134-82b7-f2ba38496583} - %windir%\Network Diagnostic\xpnetdiag.exe IE: {FB5F1910-F110-11d2-BB9E-00C04F795683} - c:\program files\messenger\msmsgs.exe IE: {2670000A-7350-4f3c-8081-5663EE0C6C49} - {48E73304-E1D6-4330-914C-F5F514E3486C} - c:\progra~1\micros~3\office12\ONBttnIE.dll IE: {92780B25-18CC-41C8-B9BE-3C9C571A8263} - {FF059E31-CC5A-4E2E-BF3B-96E929D65503} - c:\progra~1\micros~3\office12\REFIEBAR.DLL DPF: {8100D56A-5661-482C-BEE8-AFECE305D968} - hxxp://upload.facebook.com/controls/2009.07.28_v5.5.8.1/FacebookPhotoUploader55.cab DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_17-windows-i586.cab DPF: {CAFEEFAC-0016-0000-0017-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_17-windows-i586.cab DPF: {D27CDB6E-AE6D-11CF-96B8-444553540000} - hxxp://fpdownload2.macromedia.com/get/shockwave/cabs/flash/swflash.cab DPF: {E2883E8F-472F-4FB0-9522-AC9BF37916A7} - hxxp://platformdl.adobe.com/NOS/getPlusPlus/1.6/gp.cab Notify: igfxcui - igfxdev.dll SSODL: WPDShServiceObj - {AAA288BA-9A4C-45B0-95D7-94D524869DB5} - c:\windows\system32\WPDShServiceObj.dll ============= SERVICES / DRIVERS =============== R0 SahdIa32;HDD Filter Driver;c:\windows\system32\drivers\SahdIa32.sys [2009-8-24 21488] R0 SaibIa32;Volume Filter Driver;c:\windows\system32\drivers\SaibIa32.sys [2009-8-24 15856] R0 ssfs0bbc;ssfs0bbc;c:\windows\system32\drivers\ssfs0bbc.sys [2009-11-6 29808] R0 SysCow;SysCow;c:\windows\system32\drivers\syscow32x.sys [2009-7-2 103792] R1 SaibVd32;Virtual Disk Driver;c:\windows\system32\drivers\SaibVd32.sys [2009-8-24 25584] R2 WebrootSpySweeperService;Webroot Spy Sweeper Engine;c:\program files\webroot\webrootsecurity\SpySweeper.exe [2009-11-6 4048240] R2 WRConsumerService;Webroot Client Service;c:\program files\webroot\webrootsecurity\WRConsumerService.exe [2009-11-23 1201640] R3 AESTAud;AE Audio Service;c:\windows\system32\drivers\AESTAud.sys [2009-8-24 113664] R3 Cam3820;Cam3820 PC Camera Driver;c:\windows\system32\drivers\cam3820a.sys [2009-6-18 308608] S3 L1c;NDIS Miniport Driver for Atheros AR8131/AR8132 PCI-E Ethernet Controller;c:\windows\system32\drivers\l1c51x86.sys [2009-3-31 39424] S3 RSUSBSTOR;RTS5121.Sys Realtek USB Card Reader;c:\windows\system32\drivers\RTS5121.sys [2009-8-24 160256] S3 Rts516xIR;Realtek IR Driver;c:\windows\system32\drivers\rts516xir.sys –> c:\windows\system32\drivers\Rts516xIR.sys [?] S4 9734BF6A-2DCD-40f0-BAB0-5AAFEEBE1269;Roxio SAIB Service;c:\program files\roxio\backontrack\disaster recovery\SaibSVC.exe [2009-6-2 457200] S4 BOTService;BOTService;c:\program files\roxio\backontrack\instant restore\BOTService.exe [2009-7-9 199152] S4 GSRestartSvc;GSRestartSvc;"c:\documents and settings\all users\application data\geek squad\customizer\gsrestartsvc.exe" –> c:\documents and settings\all users\application data\geek squad\customizer\GSRestartSvc.exe [?] =============== Created Last 30 ================ 2010-05-31 04:17:29 0 d—–w- c:\program files\NoAdware5.0 2010-05-29 05:15:26 353792 —-a-w- c:\windows\system32\drivers\srv.sys 2010-05-29 05:15:26 353792 ——w- c:\windows\system32\dllcache\srv.sys 2010-05-29 05:15:20 2146304 —-a-w- c:\windows\system32\ntoskrnl.exe 2010-05-29 05:15:20 2146304 ——w- c:\windows\system32\dllcache\ntkrnlmp.exe 2010-05-29 05:15:17 2024448 —-a-w- c:\windows\system32\ntkrnlpa.exe 2010-05-29 05:15:17 2024448 ——w- c:\windows\system32\dllcache\ntkrpamp.exe 2010-05-29 05:15:16 2066816 ——w- c:\windows\system32\dllcache\ntkrnlpa.exe 2010-05-29 05:15:10 455680 —-a-w- c:\windows\system32\drivers\mrxsmb.sys 2010-05-29 05:15:10 455680 ——w- c:\windows\system32\dllcache\mrxsmb.sys 2010-05-29 05:15:07 471552 ——w- c:\windows\system32\dllcache\aclayers.dll 2010-05-29 05:15:07 1206508 ——w- c:\windows\system32\dllcache\sysmain.sdb 2010-05-29 05:14:46 81920 —-a-w- c:\windows\system32\fontsub.dll 2010-05-29 05:14:46 81920 ——w- c:\windows\system32\dllcache\fontsub.dll 2010-05-29 05:14:46 119808 —-a-w- c:\windows\system32\t2embed.dll 2010-05-29 05:14:46 119808 ——w- c:\windows\system32\dllcache\t2embed.dll 2010-05-29 05:14:40 3558912 ——w- c:\windows\system32\dllcache\moviemk.exe 2010-05-29 05:13:44 594432 ——w- c:\windows\system32\dllcache\msfeeds.dll 2010-05-29 05:13:44 55296 ——w- c:\windows\system32\dllcache\msfeedsbs.dll 2010-05-29 05:13:43 247808 ——w- c:\windows\system32\dllcache\ieproxy.dll 2010-05-29 05:13:43 12800 ——w- c:\windows\system32\dllcache\xpshims.dll 2010-05-29 05:13:41 1985536 ——w- c:\windows\system32\dllcache\iertutil.dll 2010-05-28 17:28:11 0 d—–w- c:\docume~1\owner\applic~1\Malwarebytes 2010-05-28 17:27:59 38224 —-a-w- c:\windows\system32\drivers\mbamswissarmy.sys 2010-05-28 17:27:56 20952 —-a-w- c:\windows\system32\drivers\mbam.sys 2010-05-28 17:27:56 0 d—–w- c:\docume~1\alluse~1\applic~1\Malwarebytes 2010-05-28 17:27:55 0 d—–w- c:\program files\Malwarebytes' Anti-Malware ==================== Find3M ==================== 2009-08-24 17:28:33 245760 –sha-w- c:\windows\system32\config\systemprofile\ietldcache\index.dat 2009-08-24 16:49:05 32768 –sha-w- c:\windows\system32\config\systemprofile\local settings\application data\microsoft\feeds cache\index.dat ============= FINISH: 0:36:36.95 =============== UNLESS SPECIFICALLY INSTRUCTED, DO NOT POST THIS LOG. IF REQUESTED, ZIP IT UP & ATTACH IT DDS (Ver_10-03-17.01) Microsoft Windows XP Home Edition Boot Device: \Device\HarddiskVolume1 Install Date: 11/21/2009 10:36:00 PM System Uptime: 5/31/2010 12:27:41 AM (0 hours ago) Motherboard: Hewlett-Packard | | 308F Processor: Intel® Atom™ CPU N270 @ 1.60GHz | CPU 1 | 1596/133mhz ==== Disk Partitions ========================= C: is FIXED (NTFS) - 149 GiB total, 119.355 GiB free. ==== Disabled Device Manager Items ============= Class GUID: {4D36E972-E325-11CE-BFC1-08002BE10318} Description: Atheros AR8132 PCI-E Fast Ethernet Controller Device ID: PCI\VEN_1969&DEV_1062&SUBSYS_308F103C&REV_C0\4&23C6FC68&0&00E1 Manufacturer: Atheros Name: Atheros AR8132 PCI-E Fast Ethernet Controller PNP Device ID: PCI\VEN_1969&DEV_1062&SUBSYS_308F103C&REV_C0\4&23C6FC68&0&00E1 Service: L1c ==== System Restore Points =================== No restore point in system. ==== Installed Programs ====================== Acrobat.com Adobe AIR Adobe Flash Player 10 ActiveX Adobe Flash Player 10 Plugin Adobe Reader 9.1 MUI Apple Application Support Apple Software Update Atheros Communications Inc.® AR81Family Gigabit/Fast Ethernet Driver AutoUpdate Broadcom 802.11 Wireless LAN Adapter Compatibility Pack for the 2007 Office system DivX Codec DivX Converter DivX Player DivX Version Checker Geek Squad 24 Hour Computer Support Homepage Protection Hotfix for Microsoft .NET Framework 3.5 SP1 (KB953595) Hotfix for Microsoft .NET Framework 3.5 SP1 (KB958484) Hotfix for Windows Media Format 11 SDK (KB929399) Hotfix for Windows Media Player 11 (KB939683) Hotfix for Windows XP (KB915865) Hotfix for Windows XP (KB949764) Hotfix for Windows XP (KB952287) Hotfix for Windows XP (KB954550-v5) Hotfix for Windows XP (KB961118) Hotfix for Windows XP (KB970653-v3) Hotfix for Windows XP (KB976098-v2) Hotfix for Windows XP (KB981793) HP BatteryCheck 2.10 A2 HP Games HP Help and Support HP QuickSync HP User Guides 0165 HP Webcam-50 HP Wireless Assistant HpSdpAppCoreApp IDT Audio Intel® Graphics Media Accelerator Driver Java™ 6 Update 17 Malwarebytes' Anti-Malware Microsoft .NET Framework 2.0 Service Pack 2 Microsoft .NET Framework 3.0 Service Pack 2 Microsoft .NET Framework 3.5 SP1 Microsoft Compression Client Pack 1.0 for Windows XP Microsoft Internationalized Domain Names Mitigation APIs Microsoft Kernel-Mode Driver Framework Feature Pack 1.7 Microsoft Live Search Toolbar Microsoft National Language Support Downlevel APIs Microsoft Office Excel MUI (English) 2007 Microsoft Office Home and Student 2007 Microsoft Office OneNote MUI (English) 2007 Microsoft Office PowerPoint MUI (English) 2007 Microsoft Office PowerPoint Viewer 2007 (English) Microsoft Office Proof (English) 2007 Microsoft Office Proof (French) 2007 Microsoft Office Proof (Spanish) 2007 Microsoft Office Proofing (English) 2007 Microsoft Office Shared MUI (English) 2007 Microsoft Office Shared Setup Metadata MUI (English) 2007 Microsoft Office Suite Activation Assistant Microsoft Office Word MUI (English) 2007 Microsoft Silverlight Microsoft Software Update for Web Folders (English) 12 Microsoft User-Mode Driver Framework Feature Pack 1.0 Microsoft Visual C++ 2005 Redistributable Microsoft Works MSXML 4.0 SP2 (KB954430) MSXML 4.0 SP2 (KB973688) MSXML 4.0 SP2 and SOAP Toolkit 3.0 MSXML 6.0 Parser QuickTime Registry Mechanic 6.0 Roxio BackOnTrack Roxio Disaster Recovery Roxio Instant Restore Roxio Instant Restore Recovery Disk Roxio Update Manager Security Update for Windows Media Player (KB952069) Security Update for Windows Media Player (KB954155) Security Update for Windows Media Player (KB968816) Security Update for Windows Media Player (KB973540) Security Update for Windows Media Player 11 (KB954154) Security Update for Windows XP (KB923561) Security Update for Windows XP (KB941569) Security Update for Windows XP (KB946648) Security Update for Windows XP (KB950762) Security Update for Windows XP (KB950974) Security Update for Windows XP (KB951066) Security Update for Windows XP (KB951376-v2) Security Update for Windows XP (KB951748) Security Update for Windows XP (KB952004) Security Update for Windows XP (KB952954) Security Update for Windows XP (KB954459) Security Update for Windows XP (KB955069) Security Update for Windows XP (KB956572) Security Update for Windows XP (KB956744) Security Update for Windows XP (KB956802) Security Update for Windows XP (KB956803) Security Update for Windows XP (KB956844) Security Update for Windows XP (KB957097) Security Update for Windows XP (KB958644) Security Update for Windows XP (KB958687) Security Update for Windows XP (KB958869) Security Update for Windows XP (KB959426) Security Update for Windows XP (KB960225) Security Update for Windows XP (KB960803) Security Update for Windows XP (KB960859) Security Update for Windows XP (KB961371-v2) Security Update for Windows XP (KB961501) Security Update for Windows XP (KB969059) Security Update for Windows XP (KB969947) Security Update for Windows XP (KB970238) Security Update for Windows XP (KB970430) Security Update for Windows XP (KB971468) Security Update for Windows XP (KB971486) Security Update for Windows XP (KB971557) Security Update for Windows XP (KB971633) Security Update for Windows XP (KB971657) Security Update for Windows XP (KB972270) Security Update for Windows XP (KB973354) Security Update for Windows XP (KB973507) Security Update for Windows XP (KB973525) Security Update for Windows XP (KB973869) Security Update for Windows XP (KB973904) Security Update for Windows XP (KB974112) Security Update for Windows XP (KB974318) Security Update for Windows XP (KB974392) Security Update for Windows XP (KB974571) Security Update for Windows XP (KB975025) Security Update for Windows XP (KB975467) Security Update for Windows XP (KB975560) Security Update for Windows XP (KB975561) Security Update for Windows XP (KB975713) Security Update for Windows XP (KB977816) Security Update for Windows XP (KB977914) Security Update for Windows XP (KB978037) Security Update for Windows XP (KB978262) Security Update for Windows XP (KB978338) Security Update for Windows XP (KB978542) Security Update for Windows XP (KB978601) Security Update for Windows XP (KB978706) Security Update for Windows XP (KB979309) Security Update for Windows XP (KB979683) Security Update for Windows XP (KB980232) Spy Sweeper Core Synaptics Pointing Device Driver Update for Microsoft .NET Framework 3.5 SP1 (KB963707) Update for Office 2007 (KB934528) Update for Windows XP (KB898461) Update for Windows XP (KB951978) Update for Windows XP (KB955759) Update for Windows XP (KB967715) Update for Windows XP (KB968389) Update for Windows XP (KB971737) Update for Windows XP (KB973687) Update for Windows XP (KB973815) USB2.0 Card Reader Software VC80CRTRedist - 8.0.50727.4053 WebFldrs XP Webroot AntiVirus with Spy Sweeper Windows Backup Utility Windows Genuine Advantage Validation Tool (KB892130) Windows Internet Explorer 7 Windows Media Format 11 runtime Windows Media Player 11 ==== Event Viewer Messages From Past Week ======== 5/30/2010 8:58:55 PM, error: Service Control Manager [7026] - The following boot-start or system-start driver(s) failed to load: Fips intelppm SaibVd32 5/30/2010 4:54:25 PM, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service wuauserv with arguments "" in order to run the server: {E60687F7-01A1-40AA-86AC-DB1CBF673334} 5/30/2010 4:43:17 PM, error: Service Control Manager [7026] - The following boot-start or system-start driver(s) failed to load: AFD Fips intelppm IPSec MRxSmb NetBIOS NetBT RasAcd Rdbss SaibVd32 Tcpip 5/30/2010 4:43:17 PM, error: Service Control Manager [7001] - The TCP/IP NetBIOS Helper service depends on the AFD service which failed to start because of the following error: A device attached to the system is not functioning. 5/30/2010 4:43:17 PM, error: Service Control Manager [7001] - The IPSEC Services service depends on the IPSEC driver service which failed to start because of the following error: A device attached to the system is not functioning. 5/30/2010 4:43:17 PM, error: Service Control Manager [7001] - The DNS Client service depends on the TCP/IP Protocol Driver service which failed to start because of the following error: A device attached to the system is not functioning. 5/30/2010 4:43:17 PM, error: Service Control Manager [7001] - The DHCP Client service depends on the NetBios over Tcpip service which failed to start because of the following error: A device attached to the system is not functioning. 5/30/2010 4:42:05 PM, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service EventSystem with arguments "" in order to run the server: {1BE1F766-5536-11D1-B726-00C04FB926AF} 5/30/2010 4:42:00 PM, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service netman with arguments "" in order to run the server: {BA126AE5-2166-11D1-B1D0-00805FC1270E} 5/30/2010 12:37:51 AM, error: Dhcp [1002] - The IP address lease 192.168.1.100 for the Network Card with network address 0CEEE6AD3248 has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message). 5/30/2010 10:44:46 PM, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service StiSvc with arguments "" in order to run the server: {A1F4E726-8CF1-11D1-BF92-0060081ED811} 5/28/2010 6:55:21 AM, error: PlugPlayManager [12] - The device 'Generic volume' (STORAGE\RemovableMedia\7&d7f206a&0&RM) disappeared from the system without first being prepared for removal. 5/28/2010 6:55:21 AM, error: PlugPlayManager [12] - The device 'Generic- Multi-Card USB Device' (USBSTOR\Disk&Ven_Generic-&Prod_Multi-Card&Rev_1.00\00000) disappeared from the system without first being prepared for removal. 5/28/2010 5:18:26 AM, error: Dhcp [1002] - The IP address lease 192.168.1.104 for the Network Card with network address 0CEEE6AD3248 has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message). 5/28/2010 11:59:00 PM, error: Dhcp [1002] - The IP address lease 192.168.0.105 for the Network Card with network address 0CEEE6AD3248 has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message). 5/28/2010 11:42:30 PM, error: DCOM [10005] - DCOM got error "%1058" attempting to start the service BOTService with arguments "" in order to run the server: {9A412B91-E641-4AF4-B2E5-D51F5A4C8C7F} 5/28/2010 10:22:01 AM, error: Dhcp [1002] - The IP address lease 192.168.1.101 for the Network Card with network address 0CEEE6AD3248 has been denied by the DHCP server 10.10.16.6 (The DHCP Server sent a DHCPNACK message). 5/25/2010 6:49:41 AM, error: Dhcp [1002] - The IP address lease 192.168.1.106 for the Network Card with network address 0CEEE6AD3248 has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message).
Hi eddieandkat

I need to turn in for the night, it's 2:00am where I am. I'll pick up the thread again in the morning:

Remember, do not follow any one else's advice should they post to this topic while I am offline.

If GMER is giving you trouble, try running it in safe mode, or run it with just the 'sections' and the 'c:\' drive checked.

If it still won't run, try this program instead:

Please download this file, and save it to your Desktop. Once you have downloaded it, save and close all other programs and run it by double-clicking on the file named "RootRepeal.exe".

Once the main window shows up, please click on the "Report" button on the bottom of the window. Next, please click the "Scan" button.

Another window will pop up asking you to select what to include in the scan. Please uncheck everything except for the "Stealth Code" checkbox, and then click OK.

Once the program has finished scanning, the results will appear. Click on the "Save Report" button, and save the report to your desktop.

Finally, please open this report with Notepad, and post it here.
heres the GMER txt
GMER 1.0.15.15281 - http://www.gmer.net
Rootkit scan 2010-05-31 03:10:41
Windows 5.1.2600 Service Pack 3
Running: yle0oqbg.exe; Driver: C:\DOCUME~1\Owner\LOCALS~1\Temp\fgroykow.sys


—- System - GMER 1.0.15 —-

SSDT 89E50538 ZwAllocateVirtualMemory
SSDT 89E54C48 ZwCreateKey
SSDT 89E2E480 ZwCreateProcess
SSDT 89E4D688 ZwCreateProcessEx
SSDT 89E4D150 ZwCreateThread
SSDT 89E4F138 ZwDeleteKey
SSDT 89E32510 ZwDeleteValueKey
SSDT 89E505B0 ZwQueueApcThread
SSDT 89E1A3D0 ZwReadVirtualMemory
SSDT 89DCE140 ZwRenameKey
SSDT 89E38F40 ZwSetContextThread
SSDT 89E4E240 ZwSetInformationKey
SSDT 89E3CF30 ZwSetInformationProcess
SSDT 89E37158 ZwSetInformationThread
SSDT 89E15268 ZwSetValueKey
SSDT 89E4D1C8 ZwSuspendProcess
SSDT 89E38EC8 ZwSuspendThread
SSDT 89E3CFA8 ZwTerminateProcess
SSDT 89E371D0 ZwTerminateThread
SSDT 89E1A448 ZwWriteVirtualMemory

—- User code sections - GMER 1.0.15 —-

.text C:\WINDOWS\System32\svchost.exe[1076] ntdll.dll!NtProtectVirtualMemory 7C90D6EE 5 Bytes JMP 009A000A
.text C:\WINDOWS\System32\svchost.exe[1076] ntdll.dll!NtWriteVirtualMemory 7C90DFAE 5 Bytes JMP 009B000A
.text C:\WINDOWS\System32\svchost.exe[1076] ntdll.dll!KiUserExceptionDispatcher 7C90E47C 5 Bytes JMP 0099000C
.text C:\WINDOWS\System32\svchost.exe[1076] ole32.dll!CoCreateInstance 7750057E 5 Bytes JMP 00F2000A
.text C:\WINDOWS\Explorer.EXE[1692] ntdll.dll!NtProtectVirtualMemory 7C90D6EE 5 Bytes JMP 00B7000A
.text C:\WINDOWS\Explorer.EXE[1692] ntdll.dll!NtWriteVirtualMemory 7C90DFAE 5 Bytes JMP 00C1000A
.text C:\WINDOWS\Explorer.EXE[1692] ntdll.dll!KiUserExceptionDispatcher 7C90E47C 5 Bytes JMP 00B6000C
.text C:\WINDOWS\system32\wuauclt.exe[1744] ntdll.dll!NtProtectVirtualMemory 7C90D6EE 5 Bytes JMP 009A000A
.text C:\WINDOWS\system32\wuauclt.exe[1744] ntdll.dll!NtWriteVirtualMemory 7C90DFAE 5 Bytes JMP 009B000A
.text C:\WINDOWS\system32\wuauclt.exe[1744] ntdll.dll!KiUserExceptionDispatcher 7C90E47C 5 Bytes JMP 0099000C

—- Devices - GMER 1.0.15 —-

AttachedDevice \FileSystem\Ntfs \Ntfs ssfs0bbc.sys (Spy Sweeper FileSystem Filter Driver/Webroot Software, Inc. (www.webroot.com))

Device \Driver\Tcpip \Device\Ip 88FFEF30
Device \Driver\Tcpip \Device\Ip 89086E10
Device \Driver\Tcpip \Device\Ip 8914C198
Device \Driver\Tcpip \Device\Ip 88E001D8

AttachedDevice \Driver\Kbdclass \Device\KeyboardClass0 wdf01000.sys (WDF Dynamic/Microsoft Corporation)
AttachedDevice \Driver\Kbdclass \Device\KeyboardClass1 wdf01000.sys (WDF Dynamic/Microsoft Corporation)

Device \Driver\Tcpip \Device\Tcp 88FFEF30
Device \Driver\Tcpip \Device\Tcp 89086E10
Device \Driver\Tcpip \Device\Tcp 8914C198
Device \Driver\Tcpip \Device\Tcp 88E001D8

AttachedDevice \Driver\Ftdisk \Device\HarddiskVolume1 SaibIa32.sys (Disk Filter Driver/Sonic Solutions)

Device \Driver\Tcpip \Device\Udp 88FFEF30
Device \Driver\Tcpip \Device\Udp 89086E10
Device \Driver\Tcpip \Device\Udp 8914C198
Device \Driver\Tcpip \Device\Udp 88E001D8
Device \Driver\Tcpip \Device\RawIp 88FFEF30
Device \Driver\Tcpip \Device\RawIp 89086E10
Device \Driver\Tcpip \Device\RawIp 8914C198
Device \Driver\Tcpip \Device\RawIp 88E001D8
Device \Driver\Tcpip \Device\IPMULTICAST 88FFEF30
Device \Driver\Tcpip \Device\IPMULTICAST 89086E10
Device \Driver\Tcpip \Device\IPMULTICAST 8914C198
Device \Driver\Tcpip \Device\IPMULTICAST 88E001D8

—- EOF - GMER 1.0.15 —-
Hi,

Please do the following:


Download ComboFix from one of the following locations:
Link 1
Link 2

VERY IMPORTANT !!! Save ComboFix.exe to your Desktop

* IMPORTANT - Disable your AntiVirus and AntiSpyware applications, usually via a right click on the System Tray icon. They may otherwise interfere with our tools. If you have difficulty properly disabling your protective programs, refer to this link here
  • Double click on ComboFix.exe & follow the prompts.
As part of it's process, ComboFix will check to see if the Microsoft Windows Recovery Console is installed. With malware infections being as they are today, it's strongly recommended to have this pre-installed on your machine before doing any malware removal. It will allow you to boot up into a special recovery/repair mode that will allow us to more easily help you should your computer have a problem after an attempted removal of malware.

  • Follow the prompts to allow ComboFix to download and install the Microsoft Windows Recovery Console, and when prompted, agree to the End-User License Agreement to install the Microsoft Windows Recovery Console.
**Please note: If the Microsoft Windows Recovery Console is already installed, ComboFix will continue it's malware removal procedures.

[external image: Posted Image]

  • Once the Microsoft Windows Recovery Console is installed using ComboFix, you should see the following message:

[external image: Posted Image]

  • Click on Yes, to continue scanning for malware.
When finished, it shall produce a log for you. Please include the C:\ComboFix.txt in your next reply.
Notes:
1. Do not mouse-click Combofix's window while it is running. That may cause it to stall.
2. Do not "re-run" Combofix. If you have a problem, reply back for further instructions.
all security programs are off altho i got prompted about norton running and i checked for norton and dont have that. Im also messageing you from the same comoputer while its scanning, do i need to use a different computer? sooooo i guess talkingwith you means all my windows arent closed
yes, never turn system restore off. If combofix is still locked up - look in task manager and end process on any of the following processes pev.exe, sed.exe, grep.exe, cfxxx.exe that should end ComboFix. Now delete the copy that you have on your desktop, download a fresh copy, but rename it to Combo.com before saving it to your desktop. Now try running it in safe mode.

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI