This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

[Resolved] SkyMedia adware, maybe more?

29 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

Hi,

The back up that was deleted was the Backup Set 2010-02-17 025948, so just make a new back up of whatever files you backed up on that date.

I don't believe you have a rootkit or Combofix would have found it, all that was found was left over clutter in your recycle bin and temp files, so there are no more infections on your machine.

GMER won't run on some machines for a variety of reasons, conflict with the security programs you have on board, conflict with some services etc., size of your K drive. It doesn't always mean there is a problem with your machine.

Lets run this other rootkit program, just to put your mind at ease.


  • Download RootRepeal from the following location and save it to your desktop.
  • Extract RootRepeal.exe from the archive.
  • Open [external image: Posted Image] on your desktop.
  • Click the [external image: Posted Image] tab.
  • Click the [external image: Posted Image] button.
  • Check all seven boxes: [external image: Posted Image]
  • Push Ok
  • Check the box for your main system drive (Usually C:), and press Ok.
  • Allow RootRepeal to run a scan of your system. This may take some time.
  • Once the scan completes, push the [external image: Posted Image] button. Save the log to your desktop, using a distinctive name, such as RootRepeal.txt. Include this report in your next reply, please.
Well… so far, this is not putting my mind too much at ease: I downloaded RootRepeal, as you instructed, and extracted it on my desktop. I got it started running, and, since you suggested that it might take a while to complete its scan, I turned my attention away from the computer for a bit. Only a little while later, I heard one of those Windows alert "chimes", and glanced toward the computer just in time to see the program closing itself, without giving me a chance to save a report.

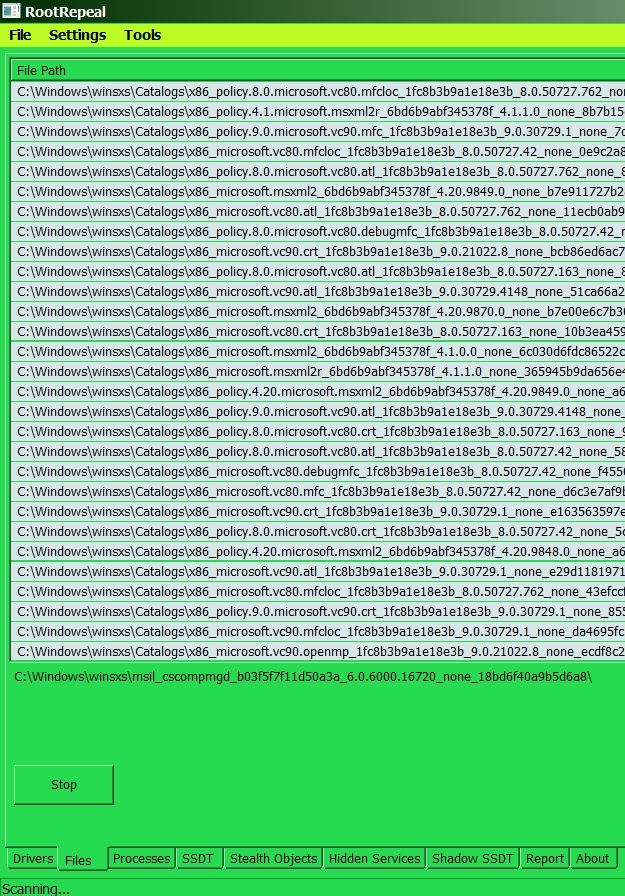
Thinkging I might have done something incorrectly, I tried setting it up to run again. This time, I decided to pay much closer attention to the running scan, to see if I could observe what it was doing when things went wrong. It blew through the scan of the drivers faster than I could watch, then moved on to the files tab for that portion of the scan. After scanning for a while, it seemed to take a particularly long time scanning a file with a long complicated name in the windows\winsxs\ directory, but the chime sounded and the program closed before I could jot down the entire file name.

Sometimes, I'm nothing if not stubborn. I set RootRepeal up to run another time, and this time, when it got to the file that's causing it to crash, I was able to grab a screen shot (see attached). I know you wanted to set my mind at ease, but after both GMER and RootRepeal were prevented from completing their scans… :smack:

Anyway, I'm glad you're willing to be patient with me… still can't thank you enough for all the help.
Hi,

Those are all part of the Vista operating system.

I wouldn't be overly concerned about it.

Let's try this one.

Please download Sysprot Antirootkit from >>>HERE<<<

Unzip it into a folder on your desktop.

  • Double click Sysprot.exe to start the program.
  • Click on the Log tab.
  • In the Write to log box select ALL ITEMS
  • Look near the bottom left, and Check Hidden Objects Only
  • Click on the Create Log button on the bottom right.
  • After a few seconds a new window should appear.
  • Select Scan Root Drive. Click on the Start button.
  • When it is complete a new window will appear to indicate that the scan is finished.
  • The log will be saved automatically in the same folder Sysprot.exe was extracted to.
  • Open the text file and copy/paste the log here.
Hi CatByte - :notworthy: Finally - one of these rootkit-detectors ran through to completion - hopefully, it's good news! :huh: The logfile you requested: SysProt AntiRootkit v1.0.1.0 by swatkat ******************************************************************************** ********** ******************************************************************************** ********** No Hidden Processes found ******************************************************************************** ********** ******************************************************************************** ********** Kernel Modules: Module Name: \SystemRoot\System32\Drivers\dump_dumpata.sys Service Name: — Module Base: 94D8A000 Module End: 94D95000 Hidden: Yes Module Name: \SystemRoot\System32\Drivers\dump_atapi.sys Service Name: — Module Base: 94D95000 Module End: 94D9D000 Hidden: Yes Module Name: \SystemRoot\System32\Drivers\dump_dumpfve.sys Service Name: — Module Base: 94D9D000 Module End: 94DAE000 Hidden: Yes Module Name: \??\C:\Windows\system32\drivers\rootrepeal.sys Service Name: rootrepeal Module Base: A1000000 Module End: A100C000 Hidden: Yes Module Name: \??\C:\Windows\system32\drivers\sbapifs.sys Service Name: SBAPIFS Module Base: A11CA000 Module End: A11D5000 Hidden: Yes ******************************************************************************** ********** ******************************************************************************** ********** SSDT: Function Name: ZwCreateProcess Address: 805CDCDE Driver Base: 805C4000 Driver End: 805FB000 Driver Name: \SystemRoot\system32\drivers\PCTCore.sys Function Name: ZwCreateProcessEx Address: 805CDED0 Driver Base: 805C4000 Driver End: 805FB000 Driver Name: \SystemRoot\system32\drivers\PCTCore.sys Function Name: ZwTerminateProcess Address: 805CD984 Driver Base: 805C4000 Driver End: 805FB000 Driver Name: \SystemRoot\system32\drivers\PCTCore.sys Function Name: ZwCreateUserProcess Address: 805CE0D8 Driver Base: 805C4000 Driver End: 805FB000 Driver Name: \SystemRoot\system32\drivers\PCTCore.sys ******************************************************************************** ********** ******************************************************************************** ********** No Kernel Hooks found ******************************************************************************** ********** ******************************************************************************** ********** No IRP Hooks found ******************************************************************************** ********** ******************************************************************************** ********** Ports: Local Address: HOMESYS:52092 Remote Address: QY-IN-F106.1E100.NET:HTTPS Type: TCP Process: C:\Program Files\Google\Google Desktop Search\GoogleDesktop.exe State: CLOSE_WAIT Local Address: HOMESYS:52090 Remote Address: QY-IN-F99.1E100.NET:HTTPS Type: TCP Process: C:\Program Files\Google\Google Desktop Search\GoogleDesktop.exe State: CLOSE_WAIT Local Address: HOMESYS:49602 Remote Address: 24.143.197.82:HTTP Type: TCP Process: C:\Program Files\Common Files\Java\Java Update\jusched.exe State: CLOSE_WAIT Local Address: HOMESYS:49596 Remote Address: YO-IN-F103.1E100.NET:HTTP Type: TCP Process: C:\Program Files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe State: CLOSE_WAIT Local Address: HOMESYS:NETBIOS-SSN Remote Address: 0.0.0.0:0 Type: TCP Process: System State: LISTENING Local Address: HOMESYS:49159 Remote Address: LOCALHOST:40000 Type: TCP Process: C:\PROGRA~1\TRENDM~1\INTERN~1\PcCtlCom.exe State: ESTABLISHED Local Address: HOMESYS:40000 Remote Address: LOCALHOST:49159 Type: TCP Process: C:\PROGRA~1\TRENDM~1\INTERN~1\TmPfw.exe State: ESTABLISHED Local Address: HOMESYS:40000 Remote Address: 0.0.0.0:0 Type: TCP Process: C:\PROGRA~1\TRENDM~1\INTERN~1\TmPfw.exe State: LISTENING Local Address: HOMESYS:6999 Remote Address: 0.0.0.0:0 Type: TCP Process: C:\PROGRA~1\TRENDM~1\INTERN~1\tmproxy.exe State: LISTENING Local Address: HOMESYS:4664 Remote Address: 0.0.0.0:0 Type: TCP Process: C:\Program Files\Google\Google Desktop Search\GoogleDesktop.exe State: LISTENING Local Address: HOMESYS:49160 Remote Address: 0.0.0.0:0 Type: TCP Process: C:\Windows\System32\services.exe State: LISTENING Local Address: HOMESYS:49156 Remote Address: 0.0.0.0:0 Type: TCP Process: C:\Windows\System32\svchost.exe State: LISTENING Local Address: HOMESYS:49155 Remote Address: 0.0.0.0:0 Type: TCP Process: C:\Windows\System32\lsass.exe State: LISTENING Local Address: HOMESYS:49154 Remote Address: 0.0.0.0:0 Type: TCP Process: C:\Windows\System32\svchost.exe State: LISTENING Local Address: HOMESYS:49153 Remote Address: 0.0.0.0:0 Type: TCP Process: C:\Windows\System32\svchost.exe State: LISTENING Local Address: HOMESYS:49152 Remote Address: 0.0.0.0:0 Type: TCP Process: C:\Windows\System32\wininit.exe State: LISTENING Local Address: HOMESYS:7433 Remote Address: 0.0.0.0:0 Type: TCP Process: C:\Program Files\Secura Backup\securasvc.exe State: LISTENING Local Address: HOMESYS:5357 Remote Address: 0.0.0.0:0 Type: TCP Process: System State: LISTENING Local Address: HOMESYS:MICROSOFT-DS Remote Address: 0.0.0.0:0 Type: TCP Process: System State: LISTENING Local Address: HOMESYS:EPMAP Remote Address: 0.0.0.0:0 Type: TCP Process: C:\Windows\System32\svchost.exe State: LISTENING Local Address: HOMESYS:50148 Remote Address: NA Type: UDP Process: C:\Windows\System32\svchost.exe State: NA Local Address: HOMESYS:SSDP Remote Address: NA Type: UDP Process: C:\Windows\System32\svchost.exe State: NA Local Address: HOMESYS:138 Remote Address: NA Type: UDP Process: System State: NA Local Address: HOMESYS:NETBIOS-NS Remote Address: NA Type: UDP Process: System State: NA Local Address: HOMESYS:50149 Remote Address: NA Type: UDP Process: C:\Windows\System32\svchost.exe State: NA Local Address: HOMESYS:SSDP Remote Address: NA Type: UDP Process: C:\Windows\System32\svchost.exe State: NA Local Address: HOMESYS:50143 Remote Address: NA Type: UDP Process: C:\Windows\System32\svchost.exe State: NA Local Address: HOMESYS:40116 Remote Address: NA Type: UDP Process: C:\PROGRA~1\TRENDM~1\INTERN~1\PcCtlCom.exe State: NA Local Address: HOMESYS:LLMNR Remote Address: NA Type: UDP Process: C:\Windows\System32\svchost.exe State: NA Local Address: HOMESYS:IPSEC-MSFT Remote Address: NA Type: UDP Process: C:\Windows\System32\svchost.exe State: NA Local Address: HOMESYS:UPNP-DISCOVERY Remote Address: NA Type: UDP Process: C:\Windows\System32\svchost.exe State: NA Local Address: HOMESYS:UPNP-DISCOVERY Remote Address: NA Type: UDP Process: C:\Windows\System32\svchost.exe State: NA Local Address: HOMESYS:MS-SQL-M Remote Address: NA Type: UDP Process: C:\Program Files\Microsoft SQL Server\90\Shared\sqlbrowser.exe State: NA Local Address: HOMESYS:500 Remote Address: NA Type: UDP Process: C:\Windows\System32\svchost.exe State: NA Local Address: HOMESYS:123 Remote Address: NA Type: UDP Process: C:\Windows\System32\svchost.exe State: NA ******************************************************************************** ********** ******************************************************************************** ********** Hidden files/folders: Object: C:\Windows\CSC\v2.0.6\namespace Status: Access denied Object: C:\Windows\CSC\v2.0.6\pq Status: Access denied Object: C:\Windows\CSC\v2.0.6\sm Status: Access denied Object: C:\Windows\CSC\v2.0.6\temp Status: Access denied Object: C:\Windows\CSC\v2.0.6 Status: Access denied Object: C:\Windows\System32\LogFiles\WMI\RtBackup\EtwRTDiagLog.etl Status: Access denied Object: C:\Windows\System32\LogFiles\WMI\RtBackup\EtwRTEventLog-Application.etl Status: Access denied Object: C:\Windows\System32\LogFiles\WMI\RtBackup\EtwRTEventLog-Microsoft-Windows-Backup.etl Status: Access denied Object: C:\Windows\System32\LogFiles\WMI\RtBackup\EtwRTEventlog-Security.etl Status: Access denied Object: C:\Windows\System32\LogFiles\WMI\RtBackup\EtwRTEventLog-System.etl Status: Access denied Object: C:\Windows\System32\LogFiles\WMI\RtBackup\EtwRTkerberos.etl Status: Access denied
Hi,

Yes, no problems there.

Now all that's left is your printer issue?

Uninstall everything to do with it.

Use RevoUninstaller


then try reinstalling with the most updated drivers you can find online


Download and install the Revo Uninstaller
  • Double click the new Revo Uninstaller icon on your desktop to start the program
  • Scroll through the listed programs and Right Click on the program you wish to uninstall (Canon)
  • From the pop out menu choose Uninstall
  • Click Yes to the confirmation dialogue
  • In the next window select the Advanced mode
  • Click Next to start uninstalling the program
  • Answer Yes to confirm the uninstall
  • When the program has completed the four steps, click Next to allow the program to search for leftovers
  • Once complete, click Next, then Finish
  • Repeat the above steps for any other programs you wish to remove.

If you still can't get it to install properly, then we'll clean up all the tools we have used, then I'll pass you over to our tech forum, the experts there no doubt will be able to help you.
Thanks again, CatByte!

I do have a couple of other (for you, probably quick) questions:

I noticed a folder called C:\$RECYCLE.BIN was created last night at 11:53 PM EST. The folder appears to be empty; still, I'm not sure what it is. It looks like I still have to original "recycle bin" located on the desktop… so?

Also, I've been noticing lately that the Counterspy "active protection" I've been using has been reporting a lot of activity by various elements that seem to be related to my Google Toolbar, e.g. trying to change a "system startup location in the Registry, which could allow the program or one of its components to start automatically with Windows" (this was one of the reasons I was worried in the first place). Is this normal behaviour for that sort of software (in which case I can set the Counterspy "active protection" to quit pestering me about it)?

As for the printer issue, to be "safe", I took a bit of time to poke around and find the disks that originally came with my printer first. I downloaded the uninstaller you linked to. Before I get started uninstalling/installing these drivers, do I need to disable my antispy/virus software for this process as well?

I apologize if any of this seems too simpleminded… :wacko:
Hi, I'm not at all familiar with "Counterspy" so can't answer that for you. C:\$RECYCLE.BIN is normal, that's where the stuff goes from your recycle bin before you empty it, so leave it alone. You shouldn't need to disable anything to resolves the printer issue.
I'm sure I didn't phrase my question as clearly as I should have; I'm not concerned so much with Counterspy's behaviour here (in fact, it's doing exactly what it's supposed to). What I was wondering was whether the fact that Google Toolbar programs are evidently trying to change a "system startup location in the Registry, which could allow the program or one of its components to start automatically with Windows" was normal behaviour for the Google toobar/updater/etc., or something unusual I should be alarmed by?
well, I don't use google toolbar either, but it would seem reasonable it would want to start on startup in order to update itself. If you are not sure about it, uninstall it, you don't really need it.
Well, if it's reasonable behaviour, I'll just set Counterspy to quit bugging me about it :blush: thanks. I'll post again after trying to fix the printer drivers.
CatByte -

Sorry about the delay in getting back to you. After deleting the various drivers associated with my printer/copier/scanner, I checked the Canon website and found new drivers had, in fact, been posted since the last time I tried to address this. I downloaded and installed them, and then spent more time than I probably should have frustrating myself with different ways of trying to get them to work. For now, all I got was the same weird result: the printer seems to function mechanically the way it should (e.g., used as a "copier" it transports paper through the mechanism and prints) and the USB cable seems to work (e.g. I can scan a document and view the scan on my computer), but I still can't get anything (not even a "test page") from the computer to print in hardcopy! :pullhair: I think we'll need to pass this along to someone in the hardware forum who might be interested in taking on a real tech challenge B)

BTW - the uninstaller you recommended was a real revelation for me, in terms of how much more informative (and probably effective) it was than the built-in add/remove program utility in Windows. I did notice, though, that the download was "only" a 30-day free trial for software that would then cost about $40. I realize that's not much, in the grand scheme of things, and arguably even quite a reasonable price for such strong and fully featured software, but for someone who, like myself, is presently laid-off and unemployed (and I have been for a while now :angry:) it's still a bit more than I can presently manage. Would you be able to suggest, or refer me to someone who could suggest, a reasonable (albeit predictably less fully featured) freeware alternative that might still be an improvement over the native Windows utility? I'm very impressed with this software, and will want to get the "pro" version at some point when it can be more affordable for me, but in the meantime I've really had my eyes opened to the usefulness of improving on what the built-in Windows version can offer.
For now, I guess if you're ready to pronounce my system "clean" it's time to tidy up the leftover scanning utilities and such. Thank you so much for all your help; you and this entire site are just amazing! :notworthy:
Hi,

Yes, post a new topic in our Windows forum and see if the expert techs there can resolve the printer issue for you.


ZSoft Uninstaller 2.4.1
http://www.zsoft.dk/index/software

that should work well for you


just some housekeeping to do now, please do the following:

Follow these steps to uninstall Combofix

  • Click START then RUN
  • Now copy/paste Combofix /uninstall into the runbox and click OK. Note the space between the ..X and the /U, it needs to be there.

[external image: Posted Image]


NEXT

Now to remove the rest of the tools that we have used in fixing your machine:
  • Make sure you have an Internet Connection.
  • Download OTC to your desktop and run it
  • A list of tool components used in the Cleanup of malware will be downloaded.
  • If your Firewall or Real Time protection attempts to block OTC to reach the Internet, please allow the application to do so.
  • Click Yes to begin the Cleanup process and remove these components, including this application.
  • You will be asked to reboot the machine to finish the Cleanup process. If you are asked to reboot the machine choose Yes.

If any logs/tools remain on your desktop > right click and delete them.


NEXT


Below I have included a number of recommendations for how to protect your computer against malware infections.

  • It is good security practice to change your passwords to all your online accounts on a fairly regular basis, this is especially true after an infection. Refer to this Microsoft article
    Strong passwords: How to create and use them

    Then consider a password keeper, to keep all your passwords safe.

  • Keep Windows updated by regularly checking their website at :
    http://windowsupdate.microsoft.com/
    This will ensure your computer has always the latest security updates available installed on your computer.

  • Make Internet Explorer more secure
    • Click Start > Run
    • Type Inetcpl.cpl & click OK
    • Click on the Security tab
    • Click Reset all zones to default level
    • Make sure the Internet Zone is selected & Click Custom level
    • In the ActiveX section, set the first two options ("Download signed and unsigned ActiveX controls) to "Prompt", and ("Initialize and Script ActiveX controls not marked as safe") to "Disable".
    • Next Click OK, then Apply button and then OK to exit the Internet Properties page.

  • ATF Cleaner - Cleans temporary files from IE and Windows, empties the recycle bin and more. Great tool to help speed up your computer and knock out those nasties that like to reside in the temp folders.


    WOT, Web of Trust, warns you about risky websites that try to scam visitors, deliver malware or send spam. Protect your computer against online threats by using WOT as your front-line layer of protection when browsing or searching in unfamiliar territory. WOT's color-coded icons show you ratings for 21 million websites, helping you avoid the dangerous sites:
    • Green to go
    • Yellow for caution
    • Red to stop
    WOT has an addon available for both Firefox, IE and chrome.


  • Keep a backup of your important files - Now, more than ever, it's especially important to protect your digital files and memories. This article is full of good information on alternatives for home backup solutions.

  • ERUNT (Emergency Recovery Utility NT) allows you to keep a complete backup of your registry and restore it when needed. The standard registry backup options that come with Windows back up most of the registry but not all of it. ERUNT however creates a complete backup set, including the Security hive and user related sections. ERUNT is easy to use and since it creates a full backup, there are no options or choices other than to select the location of the backup files. The backup set includes a small executable that will launch the registry restore if needed.

  • In light of your recent issue, I'm sure you'd like to avoid any future infections. Please take a look at these well written articles:
    Think Prevention.
    PC Safety and Security–What Do I Need?.


**Be very wary with any security software that is advertised in popups or in other ways. They are not only usually of no use, but often have malware in them.


Thank you for your patience, and performing all of the procedures requested.

Please respond one last time so we can consider the thread resolved and close it, thank-you.
CatByte -

Please accept my apologies for the delay in responding. I uninstalled Combofix without incident. I then downloaded and ran OTC. I had (or thought I had) my anti-spyware/virus/script software disabled before running it. It ran pretty quickly, and didn't seem to delete much, but then asked for a reboot, so I figured it must not have taken long to download the list of tool components and that most of the items would be deleted on the reboot. After rebooting, however, it looked like most of what we had used was still on the desktop and elsewhere. Thinking I may have missed a setting in one of my antimalware programs that prevented OTC from downloading the list it needed, I looked them over and found that there was a setting still checked in the PC-Cillin which filters websites.

Thinking that setting might have interfered in some way, I unchecked it. Of course, by this time, OTC had deleted itself. So, I downloaded it and ran it again. The second time around, it seemed to work the same way as before, except that my system exhibited considerable instability on rebooting. After seeming to be hung for a minute or two, the display changed to a blank black screen on which the mouse pointer was still visible, but not having any effect. After a scary minute or two of that, an error message appeared, saying "Logon process has failed to create the security options dialog: Failure - Security Options. OK (?!!)"

My system cycled through this process a couple of times before I manually forced it to power down. When I turned the system back on , it appeared to reboot properly. Unfortunately, several minutes later, the blank black screen reappeared, followed by the same error message. I forced the system to power down again, and after rebooting one more time, things seem to be working normally again.

Once more, OTC didn't seem to have removed much more than itself. (??) I was able to manually uninstall/delete the tools on my own, however. I also noticed that something about what OTC did to my system appears to have reset all my software's "installation dates" to the current date when I ran OTC (3/7/2010). I don't know that this causes any particular harm, but I'm not entirely sure what benefit it might provide, either. :wacko:

One final question, and then I guess we can (finally) call this topic "closed": there was a file on my desktop, with a recent date, and I wasn't sure if I recognized it as part of the Windows system, or if it was something that was installed in the process of what we've been doing: msicuu2.exe? Do you know what this is, and if it's something I should still delete? Or, is it something I had which had it's date "changed" by OTC for some reason?

Thank you again for everything you've done to help me - you and your colleagues here are the greatest!
Hi,

That is very odd behaviour and not something I have heard of from OTC before, It doesn't clean up everything, that's why I leave a note underneath to delete any remaining logs or tools. I have actually never heard of it resetting dates, that may have been done by your system when it had the 'crash'

If you are very concerned about that - please start a new topic in our Hardware forum and perhaps the techs can check the event logs to see what the cause could possibly be.

msicuu2.exe is from the Windows Cleanup Utility that I had you download. It can be uninstalled via Add/Remove programs.

make sure your files are set to hidden again (default)

Set correct settings for files that should be hidden in Windows Vista
  • Click Start.
  • Open My Computer.
  • Select Folder and Search Options
  • Select the View Tab.
  • Under the Hidden files and folders heading select Hide hidden files and folders.
  • Check Hide file extensions for known file types
  • Check the Hide protected operating system files (recommended) option.
  • Click Yes to confirm.
  • Click OK.

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI