This is a read-only archive. No new posts or registrations. Privacy Page
Spyware / Malware / Virus Removal

Trojan Inject IA

9 min read

This thread's last reply is from . Advice, software, and links below may be out of date — treat specific steps and download links with caution.

Looking for the outcome? Ask AI

I hve followed the instructions on the site. I have done the registry backup, ran the ATF cleaner and MalwareBytes.

My BitDefender came up with this infection while scanning.

Object Name Threat Name Final Status
[System]=]C:\WINDOWS\System32\svchost.exe (memory dump) Trojan.Inject.IA Disinfect Failed
[System]=]C:\WINDOWS\System32\svchost.exe (full dump) Trojan.Inject.IA Disinfect Failed
[System]=]C:\WINDOWS\System32\svchost.exe (memory dump) Trojan.Inject.IA Disinfect Failed
[System]=]C:\WINDOWS\System32\svchost.exe (full dump) Trojan.Inject.IA Disinfect Failed

Logfile of Trend Micro HijackThis v2.0.2
Scan saved at 11:24:12 PM, on 5/30/2009
Platform: Windows XP SP3 (WinNT 5.01.2600)
MSIE: Internet Explorer v7.00 (7.00.6000.16827)
Boot mode: Normal

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\Ati2evxx.exe
C:\WINDOWS\system32\svchost.exe
C:\Program Files\BitDefender\BitDefender 2009\vsserv.exe
C:\Program Files\Common Files\BitDefender\BitDefender Communicator\xcommsvr.exe
C:\Program Files\Common Files\BitDefender\BitDefender Update Service\livesrv.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\WINDOWS\system32\Ati2evxx.exe
C:\WINDOWS\Explorer.EXE
C:\Program Files\Adobe\Photoshop Elements 3.0\PhotoshopElementsFileAgent.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\svchost.exe
C:\Program Files\DAEMON Tools\daemon.exe
C:\WINDOWS\system32\spool\drivers\w32x86\3\hpztsb09.exe
C:\Program Files\BitDefender\BitDefender 2009\bdagent.exe
C:\Program Files\HP\hpcoretech\hpcmpmgr.exe
C:\Program Files\Hewlett-Packard\HP Software Update\HPWuSchd2.exe
C:\WINDOWS\system32\hphmon05.exe
C:\Program Files\QuickTime\qttask.exe
C:\Program Files\AIM\aim.exe
C:\WINDOWS\system32\ctfmon.exe
C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe
C:\Program Files\BitDefender\BitDefender 2009\seccenter.exe
C:\WINDOWS\system32\HPZipm12.exe
C:\WINDOWS\system32\wscntfy.exe
C:\Documents and Settings\Lurkin\Desktop\HijackThis\HijackThis.exe

R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = http=localhost:7171
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyOverride = 127.0.0.1
*.local
O3 - Toolbar: Adobe PDF - {47833539-D0C5-4125-9FA8-0819E2EAAC93} - C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll
O3 - Toolbar: BitDefender Toolbar - {381FFDE8-2394-4f90-B10D-FC6124A40F8C} - C:\Program Files\BitDefender\BitDefender 2009\IEToolbar.dll
O4 - HKLM\..\Run: [DAEMON Tools] "C:\Program Files\DAEMON Tools\daemon.exe" -lang 1033
O4 - HKLM\..\Run: [FinePrint Dispatcher v5] "C:\WINDOWS\System32\spool\DRIVERS\W32X86\3\fpdisp5a.exe" /source=HKLM
O4 - HKLM\..\Run: [HPDJ Taskbar Utility] C:\WINDOWS\system32\spool\drivers\w32x86\3\hpztsb09.exe
O4 - HKLM\..\Run: [BitDefender Antiphishing Helper] "C:\Program Files\BitDefender\BitDefender 2009\IEShow.exe"
O4 - HKLM\..\Run: [BDAgent] "C:\Program Files\BitDefender\BitDefender 2009\bdagent.exe"
O4 - HKLM\..\Run: [HPHUPD05] C:\Program Files\Hewlett-Packard\\{5372B9A6-6E51-4f90-9B40-E0A3B8475C4E}\hphupd05.exe
O4 - HKLM\..\Run: [HP Component Manager] "C:\Program Files\HP\hpcoretech\hpcmpmgr.exe"
O4 - HKLM\..\Run: [HP Software Update] "C:\Program Files\Hewlett-Packard\HP Software Update\HPWuSchd2.exe"
O4 - HKLM\..\Run: [HPHmon05] C:\WINDOWS\system32\hphmon05.exe
O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime
O4 - HKCU\..\Run: [AIM] C:\Program Files\AIM\aim.exe -cnetwait.odl
O4 - HKCU\..\Run: [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
O4 - HKCU\..\Run: [SpybotSD TeaTimer] C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
O4 - HKCU\..\Run: [SUPERAntiSpyware] C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe
O4 - HKUS\S-1-5-18\..\Run: [Diagnostic Manager] C:\WINDOWS\TEMP\364066784.exe (User 'SYSTEM')
O4 - HKUS\S-1-5-18\..\Run: [msnmsgr] "C:\Program Files\MSN Messenger\msnmsgr.exe" /background (User 'SYSTEM')
O4 - HKUS\.DEFAULT\..\Run: [Diagnostic Manager] C:\WINDOWS\TEMP\364066784.exe (User 'Default user')
O4 - Startup: Adobe Gamma.lnk = C:\Program Files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe
O8 - Extra context menu item: + Offline &Explorer: Download the link - file://C:\Program Files\Offline Explorer Enterprise\Add_UrlO.htm
O8 - Extra context menu item: + Offline E&xplorer: Download the current page - file://C:\Program Files\Offline Explorer Enterprise\Add_AllO.htm
O8 - Extra context menu item: Convert link target to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
O8 - Extra context menu item: Convert link target to existing PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: Convert selected links to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECaptureSelLinks.html
O8 - Extra context menu item: Convert selected links to existing PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppendSelLinks.html
O8 - Extra context menu item: Convert selection to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
O8 - Extra context menu item: Convert selection to existing PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: Convert to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
O8 - Extra context menu item: Convert to existing PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: E&xport to Microsoft Excel - res://C:\PROGRA~1\MICROS~2\OFFICE11\EXCEL.EXE/3000
O8 - Extra context menu item: Open with Scansoft PDF Converter 3.0 - res://C:\Program Files\ScanSoft\OmniPage15.0\PDFConverter3\IEShellExt.dll /100
O9 - Extra button: Expekt.com Poker - {3852AC86-965F-4abe-A75F-3DCB7E81A4B2} - C:\Program Files\expektMPP\MPPoker.exe (file missing)
O9 - Extra button: Pop-Up Blocker - {84536FE2-ABCD-3586-DCAB-40E286323737} - C:\Program Files\WINnerTweak3\PopUp Blocker.exe
O9 - Extra 'Tools' menuitem: Pop-Up Blocker - {84536FE2-ABCD-3586-DCAB-40E286323737} - C:\Program Files\WINnerTweak3\PopUp Blocker.exe
O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} - C:\PROGRA~1\MICROS~2\OFFICE11\REFIEBAR.DLL
O9 - Extra button: AIM - {AC9E2541-2814-11d5-BC6D-00B0D0A1DE45} - C:\Program Files\AIM\aim.exe
O9 - Extra button: PartyPoker.com - {B7FE5D70-9AA2-40F1-9C6B-12A255F085E1} - C:\WINDOWS\system32\shdocvw.dll
O9 - Extra 'Tools' menuitem: PartyPoker.com - {B7FE5D70-9AA2-40F1-9C6B-12A255F085E1} - C:\WINDOWS\system32\shdocvw.dll
O9 - Extra button: (no name) - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra 'Tools' menuitem: @xpsp3res.dll,-20001 - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra button: Yahoo! Messenger - {E5D12C4E-7B4F-11D3-B5C9-0050045C3C96} - C:\Program Files\Yahoo!\Messenger\YahooMessenger.exe
O9 - Extra 'Tools' menuitem: Yahoo! Messenger - {E5D12C4E-7B4F-11D3-B5C9-0050045C3C96} - C:\Program Files\Yahoo!\Messenger\YahooMessenger.exe
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O10 - Unknown file in Winsock LSP: c:\windows\system32\nwprovau.dll
O16 - DPF: {0A5FD7C5-A45C-49FC-ADB5-9952547D5715} (Creative Software AutoUpdate) - http://www.creative.com/su/ocx/15007/CTSUEng.cab
O16 - DPF: {17492023-C23A-453E-A040-C7C580BBF700} (Windows Genuine Advantage Validation Tool) - http://go.microsoft.com/fwlink/?linkid=39204
O16 - DPF: {39B0684F-D7BF-4743-B050-FDC3F48F7E3B} - http://www.fileplanet.com/fpdlmgr/cabs/FPDC_1_0_0_44.cab
O16 - DPF: {9A9307A0-7DA4-4DAF-B042-5009F29E09E1} (ActiveScan Installer Class) - http://www.pandasoftware.com/activescan/as5/asinst.cab
O16 - DPF: {A82C3A33-5C0E-466C-B020-71585433A7E4} (PhxStudent.OeSetup15) - https://mycampus.phoenix.edu/secure/PhxStudent15.CAB
O16 - DPF: {A9F8D9EC-3D0A-4A60-BD82-FBD64BAD370D} (DDRevision Class) - http://h20264.www2.hp.com/ediags/dd/instal…nosticsxp2k.cab
O16 - DPF: {B1E2B96C-12FE-45E2-BEF1-44A219113CDD} (SABScanProcesses Class) - http://www.superadblocker.com/activex/sabspx.cab
O16 - DPF: {B8BE5E93-A60C-4D26-A2DC-220313175592} (ZoneIntro Class) - http://zone.msn.com/binFramework/v10/ZIntro.cab27513.cab
O16 - DPF: {CF38E898-0A6B-11D6-83C6-0080AD7D6076} (NPRemvuPluginControl) - http://75.151.45.137/common/NPRemvu.cab
O16 - DPF: {E001C731-5E37-4538-A5CB-8168736A2360} (Confirmation) - http://quickscan.bitdefender.com/cab/ActiveQscan.cab
O16 - DPF: {F6ACF75C-C32C-447B-9BEF-46B766368D29} (Creative Software AutoUpdate Support Package) - http://www.creative.com/su/ocx/15008/CTPID.cab
O17 - HKLM\System\CCS\Services\Tcpip\..\{EACB9F7D-13A5-4E19-80DF-99A8A4486BC1}: NameServer = 4.2.2.2,4.2.2.3
O20 - Winlogon Notify: !SASWinLogon - C:\Program Files\SUPERAntiSpyware\SASWINLO.dll
O23 - Service: Adobe LM Service - Adobe Systems - C:\Program Files\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe
O23 - Service: Adobe Active File Monitor (AdobeActiveFileMonitor) - Unknown owner - C:\Program Files\Adobe\Photoshop Elements 3.0\PhotoshopElementsFileAgent.exe
O23 - Service: BitDefender Arrakis Server (Arrakis3) - BitDefender S.R.L. http://www.bitdefender.com - C:\Program Files\Common Files\BitDefender\BitDefender Arrakis Server\bin\Arrakis3.exe
O23 - Service: Ati HotKey Poller - ATI Technologies Inc. - C:\WINDOWS\system32\Ati2evxx.exe
O23 - Service: ATI Smart - Unknown owner - C:\WINDOWS\system32\ati2sgag.exe
O23 - Service: Background Intelligent Transfer Service (BITS) - Unknown owner - C:\WINDOWS\
O23 - Service: InstallDriver Table Manager (IDriverT) - Macrovision Corporation - C:\Program Files\Common Files\InstallShield\Driver\11\Intel 32\IDriverT.exe
O23 - Service: iPod Service - Apple Computer, Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: Java Quick Starter (JavaQuickStarterService) - Sun Microsystems, Inc. - C:\Program Files\Java\jre6\bin\jqs.exe
O23 - Service: BitDefender Desktop Update Service (LIVESRV) - BitDefender SRL - C:\Program Files\Common Files\BitDefender\BitDefender Update Service\livesrv.exe
O23 - Service: O&O Defrag - O&O Software GmbH - C:\WINDOWS\system32\oodag.exe
O23 - Service: Pml Driver HPZ12 - HP - C:\WINDOWS\system32\HPZipm12.exe
O23 - Service: Remote Packet Capture Protocol v.0 (experimental) (rpcapd) - CACE Technologies - C:\Program Files\WinPcap\rpcapd.exe
O23 - Service: BitDefender Virus Shield (VSSERV) - BitDefender S. R. L. - C:\Program Files\BitDefender\BitDefender 2009\vsserv.exe
O23 - Service: BitDefender Communicator (XCOMM) - BitDefender - C:\Program Files\Common Files\BitDefender\BitDefender Communicator\xcommsvr.exe

–
End of file - 11214 bytes

Malwarebytes' Anti-Malware 1.37
Database version: 2199
Windows 5.1.2600 Service Pack 3

5/31/2009 12:08:26 AM
mbam-log-2009-05-31 (00-08-26).txt

Scan type: Quick Scan
Objects scanned: 90780
Time elapsed: 5 minute(s), 1 second(s)

Memory Processes Infected: 0
Memory Modules Infected: 0
Registry Keys Infected: 1
Registry Values Infected: 0
Registry Data Items Infected: 0
Folders Infected: 0
Files Infected: 0

Memory Processes Infected:
(No malicious items detected)

Memory Modules Infected:
(No malicious items detected)

Registry Keys Infected:
HKEY_LOCAL_MACHINE\SOFTWARE\AGprotect (Malware.Trace) -> Quarantined and deleted successfully.

Registry Values Infected:
(No malicious items detected)

Registry Data Items Infected:
(No malicious items detected)

Folders Infected:
(No malicious items detected)

Files Infected:
(No malicious items detected)

Due, in part, to the large numbers of HJT logs being posted, there are four things that you need to be aware of.

1) If you have already posted this log at another forum, you need to post here that you have done so and this topic will be closed.
Multiple posting not only ties up valuable resources, but could also result is some unpleasant side-effects for your system if you follow two sets of instructions at the same time.
If, during research, an identical log is identified at another forum, this thread will be closed.

2) If you don't post a meaningful reply to any of my posts within five days, this thread will be closed. Due to limited free time, I can only have so many open threads at any one time and if yours isn't active, somebody else's will be.
If, by omission, the thread hasn't be closed after five days and you post, it will just serve as a reminder to me to close it.
Please note that "I just dropped in to say Hi!" isn't a meaningful reply!

3) Malware removal is a tricky business, and malware writers don't tend to worry about the damage their creations do, so it is advisable to back-up all important files BEFORE we start. Although most cases have a successful conclusion, on occasion things don't go according to plan and it is better to be prepared for the worst.

4) Back-ups can get lost or damaged, so make two if the files are that important to you!

~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~

Pay a visit to the Kaspersky Online Scanner 7 - I.E. is preferred for this scan.
  • Read the Information panel and then click Accept.
  • Allow the ActiveX download if necessary.
  • Both the anti-virus engine and database will need to be downloaded, which may take a little time.
  • Once this has been completed, select My Computer from the Scan section on the left hand side.
  • Put the kettle on!
  • Although it is recommended by Kaspersky that you should disable your anti-virus scanner before starting this scan, it should work OK with it still active - it does on my PC.
    Although you may find the scan speed increases if you carry out this step, I never like to disable my resident scanner while online, so I don't.
  • When the scan has completed, click View scan report at the bottom.
  • Click Save Report As…
  • Enter a name for the file in the Filename: text box and then click the down arrow to the right of Save as type: and select text file (*.txt)
  • Click Save and pick a location for the file - the Desktop is always handy.
Copy and paste the report into your next reply along with a fresh HJT log, run in Normal Mode, and a description of how your PC is behaving.

Note for Internet Explorer 7 users: If at any time you have trouble with the accept button of the licence, click on the Zoom tool located at the right bottom of the IE window and set the zoom to 75 %. Once the license accepted, reset to 100%.

~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~

Download Sec-Info.zip from here and save it to your Desktop. You will need to extract the file.

Right click on the zipped folder and from the menu that appears, click on Extract All…
In the 'Extraction Wizard' window that opens, click on Next> and in the next window that appears, click on Next> again.
In the final window, click on Finish


You should now see a folder with a .vbs file in it. Double click Sec-info.vbs to run it and a text file called Sec-Info.txt should be created in the same folder - either that or you'll get an error message.
Please copy and paste the contents of the text file into your next reply and then you can delete both of the folders and their contents.

~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~

Run HJT and click on Open the Misc Tools section.
  • Click Open Uninstall Manager…
  • Click Save list… and save it to your Desktop.
  • Copy and paste the file uninstall_list.txt into your next reply.
Noviciate, thanks for assisting me with this issue. I can assure you I have not posted this anywhere else for assistance. I posted here and just waited for one of you to become available to help me. I am 1 hour into the scan with the Kapersky so wanted to let you know I have read your response and I am in the process of doing the things you requested and I will post them as soon as it is complete. At this rate the scan is going to take about another 4 hours unless it speeds up, but it is at 20% and little over an hour in right now. I also downloaded the Sec-Info so I will complete that and the HJT information once the scan is complete. Thanks again.
——————————————————————————–
KASPERSKY ONLINE SCANNER 7 REPORT
Monday, June 1, 2009
Operating System: Microsoft Windows XP Professional Service Pack 3 (build 2600)
Kaspersky Online Scanner 7 version: 7.0.25.0
Program database last update: Monday, June 01, 2009 01:36:55
Records in database: 2288025
——————————————————————————–

Scan settings:
Scan using the following database: extended
Scan archives: yes
Scan mail databases: yes

Scan area - My Computer:
A:\
C:\
D:\
E:\
F:\
G:\
H:\
I:\

Scan statistics:
Files scanned: 270820
Threat name: 2
Infected objects: 27
Suspicious objects: 0
Duration of the scan: 03:47:31


File name / Threat name / Threats count
C:\Documents and Settings\Lurkin\My Documents\My Received Files\SciTE4AutoIt3.exe Infected: not-a-virus:Monitor.Win32.Hooker.s 1
C:\Program Files\AutoIt3\SciTE\AutoItMacroGenerator\TheHook.dll Infected: not-a-virus:Monitor.Win32.Hooker.s 1
C:\WINDOWS\system32\bafqosrs Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\bgxbng Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\bnvzyaur Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\emhlytyi Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\hbrdw Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\iiuqweb Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\jmgoq Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\kcgcyuro Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\kspgg Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\lcgzo Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\lipc Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\lztomkz Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\mornzhkeb Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\nalk Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\nhgjqzv Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\okthfpmu Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\pmrmmflee Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\pufrkiit Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\qjvdhf Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\reayzzy Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\sjufqm Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\tldihom Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\uwmhf Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\vnfppwx Infected: Trojan.Win32.Patched.gq 1
C:\WINDOWS\system32\vocmldzesq Infected: Trojan.Win32.Patched.gq 1

The selected area was scanned.

Logfile of Trend Micro HijackThis v2.0.2
Scan saved at 12:08:09 AM, on 6/1/2009
Platform: Windows XP SP3 (WinNT 5.01.2600)
MSIE: Internet Explorer v7.00 (7.00.6000.16827)
Boot mode: Normal

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\Ati2evxx.exe
C:\WINDOWS\system32\svchost.exe
C:\Program Files\BitDefender\BitDefender 2009\vsserv.exe
C:\Program Files\Common Files\BitDefender\BitDefender Communicator\xcommsvr.exe
C:\Program Files\Common Files\BitDefender\BitDefender Update Service\livesrv.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\WINDOWS\system32\Ati2evxx.exe
C:\WINDOWS\Explorer.EXE
C:\Program Files\Adobe\Photoshop Elements 3.0\PhotoshopElementsFileAgent.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\system32\wscntfy.exe
C:\Program Files\DAEMON Tools\daemon.exe
C:\WINDOWS\system32\spool\drivers\w32x86\3\hpztsb09.exe
C:\Program Files\BitDefender\BitDefender 2009\bdagent.exe
C:\Program Files\HP\hpcoretech\hpcmpmgr.exe
C:\Program Files\Hewlett-Packard\HP Software Update\HPWuSchd2.exe
C:\WINDOWS\system32\hphmon05.exe
C:\Program Files\AIM\aim.exe
C:\WINDOWS\system32\ctfmon.exe
C:\WINDOWS\system32\HPZipm12.exe
C:\Program Files\BitDefender\BitDefender 2009\seccenter.exe
C:\WINDOWS\System32\svchost.exe
C:\Documents and Settings\Lurkin\Local Settings\Application Data\Google\Update\GoogleUpdate.exe
C:\Program Files\Internet Explorer\IEXPLORE.EXE
C:\WINDOWS\system32\NOTEPAD.EXE
C:\Documents and Settings\Lurkin\Desktop\HijackThis\HijackThis.exe

R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = http=localhost:7171
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyOverride = 127.0.0.1
*.local
O3 - Toolbar: Adobe PDF - {47833539-D0C5-4125-9FA8-0819E2EAAC93} - C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll
O3 - Toolbar: BitDefender Toolbar - {381FFDE8-2394-4f90-B10D-FC6124A40F8C} - C:\Program Files\BitDefender\BitDefender 2009\IEToolbar.dll
O4 - HKLM\..\Run: [DAEMON Tools] "C:\Program Files\DAEMON Tools\daemon.exe" -lang 1033
O4 - HKLM\..\Run: [FinePrint Dispatcher v5] "C:\WINDOWS\System32\spool\DRIVERS\W32X86\3\fpdisp5a.exe" /source=HKLM
O4 - HKLM\..\Run: [HPDJ Taskbar Utility] C:\WINDOWS\system32\spool\drivers\w32x86\3\hpztsb09.exe
O4 - HKLM\..\Run: [BitDefender Antiphishing Helper] "C:\Program Files\BitDefender\BitDefender 2009\IEShow.exe"
O4 - HKLM\..\Run: [BDAgent] "C:\Program Files\BitDefender\BitDefender 2009\bdagent.exe"
O4 - HKLM\..\Run: [HPHUPD05] C:\Program Files\Hewlett-Packard\\{5372B9A6-6E51-4f90-9B40-E0A3B8475C4E}\hphupd05.exe
O4 - HKLM\..\Run: [HP Component Manager] "C:\Program Files\HP\hpcoretech\hpcmpmgr.exe"
O4 - HKLM\..\Run: [HP Software Update] "C:\Program Files\Hewlett-Packard\HP Software Update\HPWuSchd2.exe"
O4 - HKLM\..\Run: [HPHmon05] C:\WINDOWS\system32\hphmon05.exe
O4 - HKCU\..\Run: [AIM] C:\Program Files\AIM\aim.exe -cnetwait.odl
O4 - HKCU\..\Run: [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
O4 - HKCU\..\Run: [SpybotSD TeaTimer] C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
O4 - HKCU\..\Run: [SUPERAntiSpyware] C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe
O4 - HKUS\S-1-5-18\..\Run: [Diagnostic Manager] C:\WINDOWS\TEMP\364066784.exe (User 'SYSTEM')
O4 - HKUS\S-1-5-18\..\Run: [msnmsgr] "C:\Program Files\MSN Messenger\msnmsgr.exe" /background (User 'SYSTEM')
O4 - HKUS\.DEFAULT\..\Run: [Diagnostic Manager] C:\WINDOWS\TEMP\364066784.exe (User 'Default user')
O4 - Startup: Adobe Gamma.lnk = C:\Program Files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe
O8 - Extra context menu item: + Offline &Explorer: Download the link - file://C:\Program Files\Offline Explorer Enterprise\Add_UrlO.htm
O8 - Extra context menu item: + Offline E&xplorer: Download the current page - file://C:\Program Files\Offline Explorer Enterprise\Add_AllO.htm
O8 - Extra context menu item: Convert link target to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
O8 - Extra context menu item: Convert link target to existing PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: Convert selected links to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECaptureSelLinks.html
O8 - Extra context menu item: Convert selected links to existing PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppendSelLinks.html
O8 - Extra context menu item: Convert selection to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
O8 - Extra context menu item: Convert selection to existing PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: Convert to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
O8 - Extra context menu item: Convert to existing PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: E&xport to Microsoft Excel - res://C:\PROGRA~1\MICROS~2\OFFICE11\EXCEL.EXE/3000
O8 - Extra context menu item: Open with Scansoft PDF Converter 3.0 - res://C:\Program Files\ScanSoft\OmniPage15.0\PDFConverter3\IEShellExt.dll /100
O9 - Extra button: Pop-Up Blocker - {84536FE2-ABCD-3586-DCAB-40E286323737} - C:\Program Files\WINnerTweak3\PopUp Blocker.exe
O9 - Extra 'Tools' menuitem: Pop-Up Blocker - {84536FE2-ABCD-3586-DCAB-40E286323737} - C:\Program Files\WINnerTweak3\PopUp Blocker.exe
O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} - C:\PROGRA~1\MICROS~2\OFFICE11\REFIEBAR.DLL
O9 - Extra button: AIM - {AC9E2541-2814-11d5-BC6D-00B0D0A1DE45} - C:\Program Files\AIM\aim.exe
O9 - Extra button: (no name) - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra 'Tools' menuitem: @xpsp3res.dll,-20001 - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O10 - Unknown file in Winsock LSP: c:\windows\system32\nwprovau.dll
O16 - DPF: {0A5FD7C5-A45C-49FC-ADB5-9952547D5715} (Creative Software AutoUpdate) - http://www.creative.com/su/ocx/15007/CTSUEng.cab
O16 - DPF: {17492023-C23A-453E-A040-C7C580BBF700} (Windows Genuine Advantage Validation Tool) - http://go.microsoft.com/fwlink/?linkid=39204
O16 - DPF: {39B0684F-D7BF-4743-B050-FDC3F48F7E3B} - http://www.fileplanet.com/fpdlmgr/cabs/FPDC_1_0_0_44.cab
O16 - DPF: {7530BFB8-7293-4D34-9923-61A11451AFC5} (OnlineScanner Control) - http://download.eset.com/special/eos/OnlineScanner.cab
O16 - DPF: {9A9307A0-7DA4-4DAF-B042-5009F29E09E1} (ActiveScan Installer Class) - http://www.pandasoftware.com/activescan/as5/asinst.cab
O16 - DPF: {A82C3A33-5C0E-466C-B020-71585433A7E4} (PhxStudent.OeSetup15) - https://mycampus.phoenix.edu/secure/PhxStudent15.CAB
O16 - DPF: {A9F8D9EC-3D0A-4A60-BD82-FBD64BAD370D} (DDRevision Class) - http://h20264.www2.hp.com/ediags/dd/instal…nosticsxp2k.cab
O16 - DPF: {B1E2B96C-12FE-45E2-BEF1-44A219113CDD} (SABScanProcesses Class) - http://www.superadblocker.com/activex/sabspx.cab
O16 - DPF: {B8BE5E93-A60C-4D26-A2DC-220313175592} (ZoneIntro Class) - http://zone.msn.com/binFramework/v10/ZIntro.cab27513.cab
O16 - DPF: {CF38E898-0A6B-11D6-83C6-0080AD7D6076} (NPRemvuPluginControl) - http://75.151.45.137/common/NPRemvu.cab
O16 - DPF: {E001C731-5E37-4538-A5CB-8168736A2360} (Confirmation) - http://quickscan.bitdefender.com/cab/ActiveQscan.cab
O16 - DPF: {F6ACF75C-C32C-447B-9BEF-46B766368D29} (Creative Software AutoUpdate Support Package) - http://www.creative.com/su/ocx/15008/CTPID.cab
O17 - HKLM\System\CCS\Services\Tcpip\..\{EACB9F7D-13A5-4E19-80DF-99A8A4486BC1}: NameServer = 4.2.2.2,4.2.2.3
O20 - Winlogon Notify: !SASWinLogon - C:\Program Files\SUPERAntiSpyware\SASWINLO.dll
O23 - Service: Adobe LM Service - Adobe Systems - C:\Program Files\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe
O23 - Service: Adobe Active File Monitor (AdobeActiveFileMonitor) - Unknown owner - C:\Program Files\Adobe\Photoshop Elements 3.0\PhotoshopElementsFileAgent.exe
O23 - Service: BitDefender Arrakis Server (Arrakis3) - BitDefender S.R.L. http://www.bitdefender.com - C:\Program Files\Common Files\BitDefender\BitDefender Arrakis Server\bin\Arrakis3.exe
O23 - Service: Ati HotKey Poller - ATI Technologies Inc. - C:\WINDOWS\system32\Ati2evxx.exe
O23 - Service: ATI Smart - Unknown owner - C:\WINDOWS\system32\ati2sgag.exe
O23 - Service: Background Intelligent Transfer Service (BITS) - Unknown owner - C:\WINDOWS\
O23 - Service: InstallDriver Table Manager (IDriverT) - Macrovision Corporation - C:\Program Files\Common Files\InstallShield\Driver\11\Intel 32\IDriverT.exe
O23 - Service: iPod Service - Apple Computer, Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: Java Quick Starter (JavaQuickStarterService) - Sun Microsystems, Inc. - C:\Program Files\Java\jre6\bin\jqs.exe
O23 - Service: BitDefender Desktop Update Service (LIVESRV) - BitDefender SRL - C:\Program Files\Common Files\BitDefender\BitDefender Update Service\livesrv.exe
O23 - Service: O&O Defrag - O&O Software GmbH - C:\WINDOWS\system32\oodag.exe
O23 - Service: Pml Driver HPZ12 - HP - C:\WINDOWS\system32\HPZipm12.exe
O23 - Service: Remote Packet Capture Protocol v.0 (experimental) (rpcapd) - CACE Technologies - C:\Program Files\WinPcap\rpcapd.exe
O23 - Service: BitDefender Virus Shield (VSSERV) - BitDefender S. R. L. - C:\Program Files\BitDefender\BitDefender 2009\vsserv.exe
O23 - Service: BitDefender Communicator (XCOMM) - BitDefender - C:\Program Files\Common Files\BitDefender\BitDefender Communicator\xcommsvr.exe

–
End of file - 10809 bytes

Sec-Info.txt

Company Name: BitDefender
AV Name: BitDefender Antivirus
Version Number: 12.0
On-Access Scanning Enabled: Yes
Product up-to-date: Yes

~~~~~~~~~~~~~~~~~~~~~~~~

Company Name: BitDefender
Firewall Name: BitDefender Firewall
Version Number: 12.0
Enabled: No

~~~~~~~~~~~~~~~~~~~~~~~~

Uninstall_List.txt

001 Joiner
7-Zip 4.32
Aarons Cliker Version 2.89
AC3Filter (remove only)
Active@ KillDisk FREE Suite
Adaptec UDF Reader
Adobe Acrobat - Reader 6.0.2 Update
Adobe Acrobat 7.0.7 Professional
Adobe Atmosphere Player for Acrobat and Adobe Reader
Adobe Bridge 1.0
Adobe Common File Installer
Adobe Flash Player ActiveX
Adobe Help Center 1.0
Adobe Photoshop Album 2.0
Adobe Photoshop CS2
Adobe Photoshop Elements 3.0
Adobe Stock Photos 1.0
A-FF Repair Station v4.3
AIM Ad Hack
AnyDVD
AOL Instant Messenger
APA PERRLA
ATI - Software Uninstall Utility
ATI Catalyst Control Center
ATI Display Driver
ATI HYDRAVISION
AttributeMagic Pro
Auto Gordian Knot 2.45
AutoIt v3.3.0.0
Avanquest update
AviSynth 2.5
BadCopy Pro
Better File Rename 4.9
Bink and Smacker
BitDefender Internet Security 2008
BitDefender Internet Security 2009
Burning Crusade
Canopus ProCoder 2
CCleaner (remove only)
CDCheck
CloneCD
Combined Community Codec Pack 2006-07-28 (Remove Only)
Cool Edit Pro 2.1
CoreAVC Pro (remove only)
Data Lifeguard Diagnostic for Windows
Dell Digital Jukebox Driver
Dell DJ Explorer
DFX for Winamp
DH Driver Cleaner Professional Edition
Directory Printer
DivX Codec
dlDone
DVD Decrypter (Remove Only)
DVD Profiler Version 3.1.1
DVD Shrink 3.2
DVD2one 1.5.2
DVDInfoPro
DVHSTool
EQ2MAP Updater 1.0.6
Eraser
ERUNT 1.1j
EverQuest
EverQuest II
EverQuest Trilogy
EverQuest: Lost Dungeons of Norrath
EverQuest: Planes of Power
EverQuest: Shadows of Luclin
EverQuest: SOV
EverQuest: The Anniversary Edition
ExamForce Engine Installation CM 7.7
Exifer
Fahrenheit
ffdshow [rev 1324] [2007-07-01]
FinePrint
FlashFXP v3
Flickr Uploadr 3.1.4
Forté Agent
Frontline Systems Premium Solver Platform V6.5
GSpot Codec Information Appliance
GTK+ 2.6.8-1 runtime environment
Haali Media Splitter
HDTV2DVD 0.2
HijackThis 2.0.2
Hotfix for Microsoft .NET Framework 3.5 SP1 (KB953595)
Hotfix for Microsoft .NET Framework 3.5 SP1 (KB958484)
HP Driver Diagnostics
HP OfficeJet T Series (Remove Only)
HP Software Update
HyperSnap-DX 5
ImgBurn (Remove Only)
Intel Application Accelerator
Intel® PRO Network Adapters and Drivers
IsoBuster 1.9
iTunes
Java 2 Runtime Environment, SE v1.4.2_06
Java™ 6 Update 13
KeePass Password Safe 1.10
KProbe 2.5.2
Lame ACM MP3 Codec
LiveReg (Symantec Corporation)
Logitech Harmony Remote Software
Magic File Renamer
Magic ISO Maker v5.0 (build 0166)
Malwarebytes' Anti-Malware
MAX Code Manager 1.5
Max Media Creator
MaxBlast 3
MaxDrive PS2
MediaRenamer
MetaProducts Offline Explorer Enterprise
Microsoft .NET Framework 1.1
Microsoft .NET Framework 1.1 Hotfix (KB928366)
Microsoft .NET Framework 2.0 Service Pack 2
Microsoft .NET Framework 3.0 Service Pack 2
Microsoft .NET Framework 3.5 SP1
Microsoft Compression Client Pack 1.0 for Windows XP
Microsoft Internationalized Domain Names Mitigation APIs
Microsoft Kernel-Mode Driver Framework Feature Pack 1.5
Microsoft National Language Support Downlevel APIs
Microsoft Office FrontPage 2003
Microsoft Office Professional Edition 2003
Microsoft Office Visio Viewer 2003 (English)
Microsoft SQL Server Desktop Engine (SONY_MEDIAMGR)
Microsoft User-Mode Driver Framework Feature Pack 1.0
Microsoft Visual C++ 2005 Redistributable
Minute Timer (remove only)
Motorola Driver Installation 3.7.0
Motorola Phone Tools
Motorola Software Update
Mozilla Firefox (2.0.0.20)
mp4UI
MSRedist
MSXML 4.0 SP2 (KB927978)
MSXML 4.0 SP2 (KB936181)
MSXML 4.0 SP2 (KB954430)
MSXML 4.0 SP2 Parser and SDK
MSXML 6 Service Pack 2 (KB954459)
My Screen Recorder Pro 2.3
NewsLeecher
NewsLeecher v3.9 Beta 8
Norton Password Manager
Norton Password Manager (Symantec Corporation)
O&O Defrag Professional Edition
overland
Par-N-Rar 1.3
PE Explorer 1.95
Photosmart 140,240,7200,7600,7700,7900 Series
PokerRoom.com (remove only)
PokerStars
PowerDVD
PowerISO
PSP Action Replay
PTFB Pro [removed]
QuickPar 0.9
QuickSFV (Remove only)
QuickTime
Radeon Omega Drivers v3.8.231 Setup Files and Tools
RAR Password Recovery v1.1 RC16 (remove only)
RealPlayer
Reasonable NoClone 4 Enterprise
R-Studio 4.6
ScanSoft OmniPage 15.0
ScanSoft PDF Converter 3.0
ScanSoft PDF Create! 3.0
SciTE4AutoIt3 20-12-2008
Seagate DiscWizard
Security Update for Windows Internet Explorer 7 (KB938127-v2)
Security Update for Windows Internet Explorer 7 (KB956390)
Security Update for Windows Internet Explorer 7 (KB958215)
Security Update for Windows Internet Explorer 7 (KB960714)
Security Update for Windows Internet Explorer 7 (KB961260)
Security Update for Windows Internet Explorer 7 (KB963027)
Skype 2.5
Smart MP3 Renamer 1.4
Snood for Windows version 2.4.5-W
Sonic RecordNow! Deluxe
Sonic Update Manager
SPIF205 USB to SATA Bridge 98 Driver Installer
Spybot - Search & Destroy
Steam™
SUPER © Version 2007.bld.23 (July 4, 2007)
SUPERAntiSpyware Professional
SWAT 4
SWAT 4 - The Stetchkov Syndicate
Symantec pcAnywhere
Tag&Rename 3.1.7
TeamSpeak 2 RC2
The GIMP 2.2.8
ThumbsPlus version 6.0
ThumbsPlus version 7.0
TMPGEnc DVD Author 1.5
TMPGEnc Plus 2.5
Ulead Data-Add 2.0
Ulead DVD MovieFactory 3 Disc Creator
Ulead DVD MovieFactory 4.0
Ulead VideoStudio 9.0
UltraISO V7.23 ME
Ventrilo Client
VERITAS RecordNow DX
Videora Xbox 360 Converter 2.25
VivoStatic 3
VLC media player 0.9.9
VobSub v2.23 (Remove Only)
WD Diagnostics
Winamp
Winamp Remote
Windows Internet Explorer 7
Windows Live Messenger
Windows Media Connect
Windows Media Encoder 9 Series
Windows Media Format 11 runtime
Windows Media Player 11
Windows Resource Kit Tools - SubInAcl.exe
Windows XP Service Pack 3
WINner Tweak 3.5.1
WinPcap 4.0
WinRAR archiver
WinZip 11.2
WM Capture
WM Recorder 12.1
World of Warcraft
Worms 4 Mayhem
XviD 1.1 final uninstall
XviD MPEG4 Video Codec (remove only)
Yahoo! Messenger
ZIP 2 Secure EXE
Download FindAWF by noahdfear from here and save it to your Desktop.

  • Double click the file to begin and then press any key to access the menu.
  • Press 1 and then and sit back and wait for the tool to scan your computer.
  • Once the scan has completed a text file, AWF.txt will open with the results.
  • Please copy and paste the contents of the textfile into your next reply.
~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~

Your BitDefender firewall appears to be disabled - is there any reason for this?
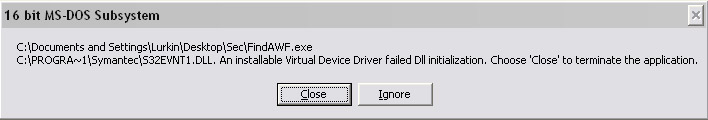
It may have been when I disabled the antivirus for the Kapersky scan. Right now it shows disabled, but the windows firewall is enabled. I am running the FindAWF.exe right now, but it immediately came up with this error message (see attached image) and the report ended up empty. So I ran it again and clicked ignore instead it gave this report after a few minutes. Find AWF report by noahdfear ©2006 Version 1.40 The current date is: Mon 06/01/2009 The current time is: 18:11:32.62 bak folders found ~~~~~~~~~~~ Directory of C:\PROGRA~1\EXIFER\EXIFBAK 0 File(s) 0 bytes Duplicate files of bak directory contents ~~~~~~~~~~~~~~~~~~~~~~~ end of report
Take a trip to this webpage for download links and instructions for running Combofix by sUBs: http://www.bleepingcomputer.com/combofix/how-to-use-combofix *
  • Please be aware that this tool may require the PC to be rebooted so close any programs you have open before you start.
  • When CF has finished, it will produce a log - C:\ComboFix.txt - copy and paste it into your next reply.
  • Post a fresh HJT log as well.
  • Let me know how the PC is behaving.
* There are two points to note from the instructions page:

1) The Recovery Console.

It is recommended that you install this as, in certain circumstances, it may be the difference between a successful repair and a reformat. If you are uncertain as to whether or not you already have the Recovery Console installed, simply run CF and it will prompt you if it does not detect it.
CF will complete it's removal tasks without the installation of the Console, so you are free to choose whether you want to complete this step, but it is in your interests to do so.

2) Disabling your Anti-Virus.

CF has been the victim of false-positive detections on occasion and a resident AV may incorrectly identify and delete part of the tool which won't do it much good. If you don't disable your AV, you may not get the results you hoped for!
ComboFix 09-05-31.06 - Lurkin 06/01/2009 18:41.5 - NTFSx86
Microsoft Windows XP Professional 5.1.2600.3.1252.1.1033.18.1023.630 [GMT -4:00]
Running from: c:\documents and settings\[removed]\Desktop\Sec\ComboFix.exe
AV: BitDefender Antivirus *On-access scanning disabled* (Updated) {6C4BB89C-B0ED-4F41-A29C-4373888923BB}
FW: BitDefender Firewall *disabled* {4055920F-2E99-48A8-A270-4243D2B8F242}
.

((((((((((((((((((((((((((((((((((((((( Other Deletions )))))))))))))))))))))))))))))))))))))))))))))))))
.

C:\-1393268822
C:\desktop.ini
c:\windows\f96ac0e5-19d2-42c5-8f68-eb7a99861769.ocx
c:\windows\system32\2d2ca2ce-704a-428c-8cbe-0736b29190aa.dll
D:\desktop.ini

Infected copy of c:\windows\system32\drivers\ndis.sys was found and disinfected
Restored copy from - The cat ate it :)
.
((((((((((((((((((((((((( Files Created from 2009-05-01 to 2009-06-01 )))))))))))))))))))))))))))))))
.

2009-05-31 16:19 . 2009-05-31 16:19 ——– d—–w- c:\program files\ESET
2009-05-31 03:59 . 2009-05-31 03:59 3371383 —-a-w- c:\documents and settings\All Users\Application Data\Malwarebytes\Malwarebytes' Anti-Malware\mbam-setup.exe
2009-05-31 03:52 . 2009-05-31 03:52 ——– d—–w- c:\program files\ERUNT
2009-05-29 13:23 . 2009-05-29 13:23 ——– d-sh–w- c:\windows\system32\config\systemprofile\UserData
2009-05-17 22:53 . 2009-06-01 22:55 117760 —-a-w- c:\documents and settings\Lurkin\Application Data\SUPERAntiSpyware.com\SUPERAntiSpyware\SDDLLS\UIREPAIR.DLL
2009-05-17 22:53 . 2009-05-17 22:53 ——– d—–w- c:\documents and settings\All Users\Application Data\SUPERAntiSpyware.com
2009-05-17 22:52 . 2009-05-30 09:22 ——– d—–w- c:\program files\SUPERAntiSpyware
2009-05-17 22:52 . 2009-05-17 22:52 ——– d—–w- c:\documents and settings\Lurkin\Application Data\SUPERAntiSpyware.com
2009-05-17 22:18 . 2009-05-29 11:17 ——– d—–w- c:\documents and settings\All Users\Application Data\Spybot - Search & Destroy
2009-05-17 22:18 . 2009-05-17 22:22 ——– d—–w- c:\program files\Spybot - Search & Destroy
2009-05-17 21:41 . 2009-05-17 21:41 ——– d—–w- c:\documents and settings\Lurkin\Local Settings\Application Data\Flickr
2009-05-17 21:41 . 2009-05-17 21:41 ——– d—–w- c:\documents and settings\Lurkin\Application Data\Flickr
2009-05-17 21:38 . 2009-05-17 23:05 ——– d—–w- c:\program files\Flickr Uploadr
2009-05-16 03:07 . 2009-05-16 03:07 ——– d—–w- c:\documents and settings\Administrator\Application Data\BitDefender
2009-05-16 02:12 . 2009-05-30 10:59 117760 —-a-w- c:\documents and settings\Administrator\Application Data\SUPERAntiSpyware.com\SUPERAntiSpyware\SDDLLS\UIREPAIR.DLL
2009-05-16 02:11 . 2009-05-16 02:11 ——– d—–w- c:\documents and settings\Administrator\Application Data\SUPERAntiSpyware.com
2009-05-15 02:53 . 2009-05-15 02:53 ——– d—–w- c:\documents and settings\Lurkin\Application Data\Malwarebytes
2009-05-15 02:53 . 2009-05-26 17:19 19096 —-a-w- c:\windows\system32\drivers\mbam.sys
2009-05-15 02:52 . 2009-05-26 17:20 40160 —-a-w- c:\windows\system32\drivers\mbamswissarmy.sys
2009-05-15 02:52 . 2009-05-31 04:08 ——– d—–w- c:\program files\Malwarebytes' Anti-Malware
2009-05-15 02:52 . 2009-05-15 02:52 ——– d—–w- c:\documents and settings\All Users\Application Data\Malwarebytes
2009-05-15 01:42 . 2009-05-15 01:42 ——– d—–w- c:\documents and settings\Lurkin\Local Settings\Application Data\Downloaded Installations
2009-05-15 00:56 . 2009-05-15 00:56 ——– d—–w- c:\program files\LSoft Technologies
2009-05-13 19:22 . 2009-05-13 19:36 ——– d—–w- c:\documents and settings\Lurkin\Application Data\vlc
2009-05-13 06:09 . 2009-05-13 06:09 ——– d—–w- c:\program files\R-Studio
2009-05-12 01:57 . 2009-05-12 01:57 ——– d—–w- c:\program files\Western Digital Corporation
2009-05-07 18:21 . 2008-02-26 02:54 163840 ——w- c:\windows\system32\fpres532.dll
2009-05-07 18:21 . 2008-02-26 02:53 323584 ——w- c:\windows\system32\fpmon5.dll

.
(((((((((((((((((((((((((((((((((((((((( Find3M Report ))))))))))))))))))))))))))))))))))))))))))))))))))))
.
2009-06-01 22:49 . 2004-10-01 20:24 384 —-a-w- c:\windows\system32\DVCStateBkp-{00000002-00000000-0000000B-00001102-00000004-00581102}.dat
2009-06-01 22:49 . 2004-10-01 20:24 384 —-a-w- c:\windows\system32\DVCState-{00000002-00000000-0000000B-00001102-00000004-00581102}.dat
2009-06-01 22:40 . 2009-01-10 21:50 182656 —-a-w- c:\windows\system32\drivers\ndis.sys
2009-05-31 17:18 . 2006-02-18 08:16 ——– d—–w- c:\program files\WINnerTweak3
2009-05-30 09:36 . 2004-10-19 11:33 ——– d—–w- c:\program files\Norton Password Manager
2009-05-30 09:35 . 2005-10-07 23:00 ——– d—–w- c:\program files\Agent
2009-05-30 09:23 . 2006-07-16 19:23 81984 —-a-w- c:\windows\system32\bdod.bin
2009-05-19 03:24 . 2006-09-23 23:21 ——– d—–w- c:\documents and settings\Lurkin\Application Data\ImgBurn
2009-05-17 22:50 . 2007-12-06 01:01 ——– d—–w- c:\program files\Common Files\Wise Installation Wizard
2009-05-17 08:49 . 2005-05-29 12:56 ——– d—–w- c:\program files\TagRename
2009-05-16 05:19 . 2008-04-09 21:33 ——– d—–w- c:\program files\USBToolbox
2009-05-16 05:19 . 2004-10-01 19:37 ——– d–h–w- c:\program files\InstallShield Installation Information
2009-05-02 03:55 . 2006-11-21 01:05 30 —-a-w- c:\program files\Exiferupdate.ini
2009-04-30 21:51 . 2005-01-11 03:30 ——– d—–w- c:\documents and settings\Lurkin\Application Data\Offline Explorer
2009-04-29 19:55 . 2009-04-29 11:59 53248 —-a-w- c:\windows\PSEXESVC.EXE
2009-04-29 19:09 . 2004-10-01 18:14 43296 —-a-w- c:\documents and settings\Lurkin\Local Settings\Application Data\GDIPFONTCACHEV1.DAT
2009-04-29 11:58 . 2004-08-03 22:56 578560 —-a-w- c:\windows\system32\user32.dll
2009-04-29 02:20 . 2009-04-29 02:20 ——– d—–w- c:\documents and settings\Lurkin\Application Data\QuickScan
2009-04-28 23:46 . 2009-04-28 23:46 ——– d—–w- c:\documents and settings\Lurkin\Application Data\vmjcipbk
2009-04-27 15:33 . 2009-04-27 15:33 ——– d—–w- c:\program files\MSBuild
2009-04-27 15:33 . 2009-04-27 15:33 ——– d—–w- c:\program files\Reference Assemblies
2009-04-22 19:03 . 2009-04-22 19:03 410984 —-a-w- c:\windows\system32\deploytk.dll
2009-04-22 19:03 . 2004-12-18 23:15 ——– d—–w- c:\program files\Java
2009-04-22 19:01 . 2009-04-22 19:01 152576 —-a-w- c:\documents and settings\Lurkin\Application Data\Sun\Java\jre1.6.0_13\lzma.dll
2009-04-22 19:00 . 2005-08-13 15:17 ——– d—–w- c:\program files\World of Warcraft
2009-04-01 15:23 . 2008-10-17 19:01 104328 —-a-w- c:\windows\system32\drivers\bdfndisf.sys
2009-03-06 14:22 . 2004-08-03 22:56 284160 —-a-w- c:\windows\system32\pdh.dll
2009-04-28 07:42 . 2008-10-30 22:34 61440 —-a-w- c:\program files\mozilla firefox\components\FFComm.dll
2009-02-15 08:15 . 2005-01-03 18:49 67688 —-a-w- c:\program files\mozilla firefox\components\jar50.dll
2009-02-15 08:15 . 2005-01-03 18:49 54368 —-a-w- c:\program files\mozilla firefox\components\jsd3250.dll
2009-02-15 08:15 . 2006-10-31 21:00 34944 —-a-w- c:\program files\mozilla firefox\components\myspell.dll
2009-02-15 08:15 . 2006-10-31 21:00 46712 —-a-w- c:\program files\mozilla firefox\components\spellchk.dll
2009-02-15 08:15 . 2005-01-03 18:49 172136 —-a-w- c:\program files\mozilla firefox\components\xpinstal.dll
2005-05-13 21:12 . 2005-05-13 21:12 217073 –sha-r- c:\windows\meta4.exe
2005-07-14 16:31 . 2005-07-14 16:31 27648 –sha-r- c:\windows\system32\AVSredirect.dll
2005-06-26 19:32 . 2005-06-26 19:32 616448 –sha-r- c:\windows\system32\cygwin1.dll
2005-06-22 02:37 . 2005-06-22 02:37 45568 –sha-r- c:\windows\system32\cygz.dll
2006-05-03 09:06 . 2007-10-07 04:12 163328 –sha-r- c:\windows\system32\flvDX.dll
2004-01-25 04:00 . 2004-01-25 04:00 70656 –sha-r- c:\windows\system32\i420vfw.dll
2006-03-19 08:25 . 2005-07-24 18:19 952 -csha-w- c:\windows\system32\KGyGaAvL.sys
2007-02-21 10:47 . 2007-10-07 04:12 31232 –sha-r- c:\windows\system32\msfDX.dll
2005-02-28 17:16 . 2005-02-28 17:16 240128 –sha-r- c:\windows\system32\x.264.exe
2004-01-25 04:00 . 2004-01-25 04:00 70656 –sha-r- c:\windows\system32\yv12vfw.dll
.

((((((((((((((((((((((((((((((((((((( Reg Loading Points ))))))))))))))))))))))))))))))))))))))))))))))))))
.
.
*Note* empty entries & legit default entries are not shown
REGEDIT4

[HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"AIM"="c:\program files\AIM\aim.exe" [2005-08-05 67160]
"ctfmon.exe"="c:\windows\system32\ctfmon.exe" [2008-04-14 15360]
"SpybotSD TeaTimer"="c:\program files\Spybot - Search & Destroy\TeaTimer.exe" [2009-03-05 2260480]
"SUPERAntiSpyware"="c:\program files\SUPERAntiSpyware\SUPERAntiSpyware.exe" [2009-05-30 1830128]

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run]
"DAEMON Tools"="c:\program files\DAEMON Tools\daemon.exe" [2005-12-10 133016]
"FinePrint Dispatcher v5"="c:\windows\System32\spool\DRIVERS\W32X86\3\fpdisp5a.exe" [2008-02-26 516096]
"HPDJ Taskbar Utility"="c:\windows\system32\spool\drivers\w32x86\3\hpztsb09.exe" [2005-07-08 176128]
"BitDefender Antiphishing Helper"="c:\program files\BitDefender\BitDefender 2009\IEShow.exe" [2009-04-28 69632]
"BDAgent"="c:\program files\BitDefender\BitDefender 2009\bdagent.exe" [2009-04-29 778240]
"HPHUPD05"="c:\program files\Hewlett-Packard\\{5372B9A6-6E51-4f90-9B40-E0A3B8475C4E}\hphupd05.exe" [2005-07-08 49152]
"HP Component Manager"="c:\program files\HP\hpcoretech\hpcmpmgr.exe" [2004-05-12 241664]
"HP Software Update"="c:\program files\Hewlett-Packard\HP Software Update\HPWuSchd2.exe" [2003-12-05 49152]
"HPHmon05"="c:\windows\system32\hphmon05.exe" [2005-07-08 491520]

[HKEY_USERS\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\Run]
"msnmsgr"="c:\program files\MSN Messenger\msnmsgr.exe" [2007-01-19 5674352]

c:\documents and settings\Lurkin\Start Menu\Programs\Startup\
Adobe Gamma.lnk - c:\program files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe [2004-10-4 113664]

[hkey_local_machine\software\microsoft\windows\currentversion\explorer\ShellExecuteHooks]
"{5AE067D3-9AFB-48E0-853A-EBB7F4A000DA}"= "c:\program files\SUPERAntiSpyware\SASSEH.DLL" [2008-05-13 77824]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\!SASWinLogon]
2008-12-22 16:05 356352 —-a-w- c:\program files\SUPERAntiSpyware\SASWINLO.dll

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\PCANotify]
2003-10-31 16:01 8704 —-a-w- c:\windows\system32\PCANotify.dll

[HKEY_LOCAL_MACHINE\system\currentcontrolset\control\session manager]
BootExecute REG_MULTI_SZ autocheck autochk *\0OODBS

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\PSEXESVC]
@=""

[HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List]
"%windir%\\system32\\sessmgr.exe"=
"c:\\Program Files\\QuickTime\\QuickTimePlayer.exe"=
"c:\\Program Files\\Mozilla Firefox\\firefox.exe"=
"c:\\Program Files\\FlashFXP\\flashfxp.exe"=
"c:\\Program Files\\VideoLAN\\VLC\\vlc.exe"=
"c:\\Program Files\\Adobe\\Acrobat 7.0\\Acrobat\\Acrobat.exe"=
"c:\\Program Files\\Quix\\Qwix.exe"=
"c:\\Program Files\\Sony\\Station\\Launchpad\\LaunchPad.exe"=
"c:\\Program Files\\AIM\\aim.exe"=
"c:\\Program Files\\Yahoo!\\Messenger\\YahooMessenger.exe"=
"c:\\Program Files\\Yahoo!\\Messenger\\YServer.exe"=
"c:\\Program Files\\InterVideo\\DVD7\\WinDVD.exe"=
"c:\\Program Files\\Skype\\Phone\\Skype.exe"=
"c:\\Program Files\\iTunes\\iTunes.exe"=
"c:\\Program Files\\Logitech\\Harmony Remote\\PatchHelper.exe"=
"c:\\Program Files\\Winamp Remote\\bin\\Orb.exe"=
"c:\\Program Files\\Winamp Remote\\bin\\OrbTray.exe"=
"c:\\Program Files\\Winamp Remote\\bin\\OrbStreamerClient.exe"=
"%windir%\\Network Diagnostic\\xpnetdiag.exe"=
"c:\\Program Files\\MSN Messenger\\msnmsgr.exe"=
"c:\\Program Files\\MSN Messenger\\livecall.exe"=
"c:\\Program Files\\Seagate\\DiscWizard\\DiscWizardMonitor.exe"=
"c:\\Documents and Settings\\Lurkin\\Local Settings\\Application Data\\Google\\Update\\GoogleUpdate.exe"=
"c:\\Program Files\\BitDefender\\BitDefender 2009\\seccenter.exe"=

R1 SASDIFSV;SASDIFSV;c:\program files\SUPERAntiSpyware\sasdifsv.sys [3/23/2009 2:07 PM 9968]
R1 SASKUTIL;SASKUTIL;c:\program files\SUPERAntiSpyware\SASKUTIL.SYS [3/23/2009 2:07 PM 72944]
R2 AdobeActiveFileMonitor;Adobe Active File Monitor;c:\program files\Adobe\Photoshop Elements 3.0\PhotoshopElementsFileAgent.exe [10/4/2004 4:47 AM 98304]
R2 BDVEDISK;BDVEDISK;c:\program files\BitDefender\BitDefender 2009\BDVEDISK.sys [9/4/2008 5:33 PM 82696]
R3 SASENUM;SASENUM;c:\program files\SUPERAntiSpyware\SASENUM.SYS [3/23/2009 2:07 PM 7408]
R3 Tetris;Tetris driver;c:\windows\system32\drivers\Tetris.sys [9/23/2005 8:40 PM 48928]
S3 Arrakis3;BitDefender Arrakis Server;c:\program files\Common Files\BitDefender\BitDefender Arrakis Server\bin\Arrakis3.exe [7/17/2008 1:06 PM 118784]
S3 Asushwio;Asushwio;c:\windows\system32\drivers\ASUSHWIO.SYS [7/9/2008 6:46 PM 5824]
S3 bdfm;BDFM;c:\windows\system32\drivers\bdfm.sys [9/18/2008 12:09 PM 111112]
S3 MEISTRM;MEI AVC Streaming Filter Driver;c:\windows\system32\drivers\meistrm.sys [11/10/2004 2:53 PM 13195]
S3 MEITAPE;Panasonic MPEG2TS Tape Subunit Device;c:\windows\system32\drivers\meitape.sys [11/10/2004 2:53 PM 22891]
S3 NPF;NetGroup Packet Filter Driver;c:\windows\system32\drivers\npf.sys [1/25/2007 1:31 PM 42000]
S3 pohci13F;pohci13F;\??\c:\docume~1\Lurkin\LOCALS~1\Temp\pohci13F.sys –> c:\docume~1\Lurkin\LOCALS~1\Temp\pohci13F.sys [?]
S4 PhotoshopElementsDeviceConnect;Photoshop Elements Device Connect;c:\program files\Adobe\Photoshop Elements 3.0\PhotoshopElementsDeviceConnect.exe [10/4/2004 3:40 AM 118784]

[HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost]
bdx REG_MULTI_SZ scan

HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Svchost - NetSvcs
bhluhwch
.
Contents of the 'Scheduled Tasks' folder

2009-06-01 c:\windows\Tasks\GoogleUpdateTaskUserS-1-5-21-515967899-1202660629-682003330-1003.job
- c:\documents and settings\Lurkin\Local Settings\Application Data\Google\Update\GoogleUpdate.exe [2009-03-15 02:03]

2009-06-01 c:\windows\Tasks\HP Usg Daily.job
- c:\program files\Hewlett-Packard\{5372B9A6-6E51-4f90-9B40-E0A3B8475C4E}\pexpress\hphped05.exe [2009-01-24 04:55]

2009-06-01 c:\windows\Tasks\WGASetup.job
- c:\windows\system32\KB905474\wgasetup.exe [2009-04-14 02:18]
.
- - - - ORPHANS REMOVED - - - -

SafeBoot-procexp90.Sys


.
——- Supplementary Scan ——-
.
uStart Page = hxxp://www.google.com/
uInternet Settings,ProxyOverride = 127.0.0.1
uInternet Settings,ProxyServer = http=localhost:7171
IE: + Offline &Explorer;: Download the link - file://c:\program files\Offline Explorer Enterprise\Add_UrlO.htm
IE: + Offline E&xplorer;: Download the current page - file://c:\program files\Offline Explorer Enterprise\Add_AllO.htm
IE: Convert link target to Adobe PDF - c:\program files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
IE: Convert link target to existing PDF - c:\program files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
IE: Convert selected links to Adobe PDF - c:\program files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECaptureSelLinks.html
IE: Convert selected links to existing PDF - c:\program files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppendSelLinks.html
IE: Convert selection to Adobe PDF - c:\program files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
IE: Convert selection to existing PDF - c:\program files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
IE: Convert to Adobe PDF - c:\program files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
IE: Convert to existing PDF - c:\program files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
IE: E&xport; to Microsoft Excel - c:\progra~1\MICROS~2\OFFICE11\EXCEL.EXE/3000
IE: Open with Scansoft PDF Converter 3.0 - c:\program files\ScanSoft\OmniPage15.0\PDFConverter3\IEShellExt.dll /100
IE: {{84536FE2-ABCD-3586-DCAB-40E286323737} - c:\program files\WINnerTweak3\PopUp Blocker.exe
TCP: {EACB9F7D-13A5-4E19-80DF-99A8A4486BC1} = 4.2.2.2,4.2.2.3
DPF: {7530BFB8-7293-4D34-9923-61A11451AFC5} - hxxp://download.eset.com/special/eos/OnlineScanner.cab
DPF: {A82C3A33-5C0E-466C-B020-71585433A7E4} - hxxps://mycampus.phoenix.edu/secure/PhxStudent15.CAB
DPF: {CF38E898-0A6B-11D6-83C6-0080AD7D6076} - hxxp://75.151.45.137/common/NPRemvu.cab
FF - ProfilePath -
.

**************************************************************************

catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net
Rootkit scan 2009-06-01 18:51
Windows 5.1.2600 Service Pack 3 NTFS

scanning hidden processes …

scanning hidden autostart entries …

scanning hidden files …

scan completed successfully
hidden files: 0

**************************************************************************
.
——————— LOCKED REGISTRY KEYS ———————

[HKEY_USERS\S-1-5-21-515967899-1202660629-682003330-1003\Software\Microsoft\Windows\CurrentVersion\Shell Extensions\Approved\{B46C43DD-3D17-A445-B459-1230A076725E}*]
@Allowed: (Read) (RestrictedCode)

[HKEY_LOCAL_MACHINE\software\Classes\CLSID\{47629D4B-2AD3-4e50-B716-A66C15C63153}\InprocServer32*]
"ThreadingModel"="Apartment"
@="c:\\WINDOWS\\system32\\OLE32.DLL"
"cd042efbbd7f7af1647644e76e06692b"=hex:e2,63,26,f1,3f,c8,ff,68,c8,28,8e,dc,12,
3a,a9,79,c8,28,51,af,b0,29,a3,98,59,a8,95,70,c0,16,86,87,e2,63,26,f1,3f,c8,\

[HKEY_LOCAL_MACHINE\software\Classes\CLSID\{604BB98A-A94F-4a5c-A67C-D8D3582C741C}\InprocServer32*]
"ThreadingModel"="Apartment"
@="c:\\WINDOWS\\system32\\OLE32.DLL"
"bca643cdc5c2726b20d2ecedcc62c59b"=hex:71,3b,04,66,8b,46,0d,96,1b,6d,0b,89,22,
d6,44,1c,71,3b,04,66,8b,46,0d,96,e8,51,46,02,88,06,65,f8,6a,9c,d6,61,af,45,\

[HKEY_LOCAL_MACHINE\software\Classes\CLSID\{684373FB-9CD8-4e47-B990-5A4466C16034}\InprocServer32*]
"ThreadingModel"="Apartment"
@="c:\\WINDOWS\\system32\\OLE32.DLL"
"2c81e34222e8052573023a60d06dd016"=hex:25,da,ec,7e,55,20,c9,26,75,20,77,f0,21,
26,69,a4,25,da,ec,7e,55,20,c9,26,72,7e,73,3c,92,5f,74,e6,ff,7c,85,e0,43,d4,\

[HKEY_LOCAL_MACHINE\software\Classes\CLSID\{74554CCD-F60F-4708-AD98-D0152D08C8B9}\InprocServer32*]
"ThreadingModel"="Apartment"
@="c:\\WINDOWS\\system32\\OLE32.DLL"
"2582ae41fb52324423be06337561aa48"=hex:86,8c,21,01,be,91,eb,e7,b8,9e,70,51,16,
87,50,1e,3e,1e,9e,e0,57,5a,93,61,b8,8b,f4,50,02,89,24,77,86,8c,21,01,be,91,\

[HKEY_LOCAL_MACHINE\software\Classes\CLSID\{7EB537F9-A916-4339-B91B-DED8E83632C0}\InprocServer32*]
"ThreadingModel"="Apartment"
@="c:\\WINDOWS\\system32\\OLE32.DLL"
"caaeda5fd7a9ed7697d9686d4b818472"=hex:cd,44,cd,b9,a6,33,6c,cd,1b,04,7b,da,96,
b8,bd,a6,cd,44,cd,b9,a6,33,6c,cd,a8,ac,e4,3d,fc,dc,34,bb,f5,1d,4d,73,a8,13,\

[HKEY_LOCAL_MACHINE\software\Classes\CLSID\{948395E8-7A56-4fb1-843B-3E52D94DB145}\InprocServer32*]
"ThreadingModel"="Apartment"
@="c:\\WINDOWS\\system32\\OLE32.DLL"
"a4a1bcf2cc2b8bc3716b74b2b4522f5d"=hex:df,20,58,62,78,6b,cf,c8,49,19,c4,71,c6,
46,17,43,b0,18,ed,a7,3f,8d,37,a4,13,4a,53,ed,4b,30,20,a0,df,20,58,62,78,6b,\

[HKEY_LOCAL_MACHINE\software\Classes\CLSID\{AC3ED30B-6F1A-4bfc-A4F6-2EBDCCD34C19}\InprocServer32*]
"ThreadingModel"="Apartment"
@="c:\\WINDOWS\\system32\\OLE32.DLL"
"4d370831d2c43cd13623e232fed27b7b"=hex:fb,a7,78,e6,12,2f,9a,ea,ed,f6,44,e1,7b,
a8,d8,cd,31,77,e1,ba,b1,f8,68,02,79,93,b4,e4,09,8c,96,87,fb,a7,78,e6,12,2f,\

[HKEY_LOCAL_MACHINE\software\Classes\CLSID\{DE5654CA-EB84-4df9-915B-37E957082D6D}\InprocServer32*]
"ThreadingModel"="Apartment"
@="c:\\WINDOWS\\system32\\OLE32.DLL"
"1d68fe701cdea33e477eb204b76f993d"=hex:01,3a,48,fc,e8,04,4a,f1,ab,3c,df,92,54,
45,87,bf,83,6c,56,8b,a0,85,96,ab,ce,a1,79,90,e3,19,6e,26,01,3a,48,fc,e8,04,\

[HKEY_LOCAL_MACHINE\software\Classes\CLSID\{E39C35E8-7488-4926-92B2-2F94619AC1A5}\InprocServer32*]
"ThreadingModel"="Apartment"
@="c:\\WINDOWS\\system32\\OLE32.DLL"
"1fac81b91d8e3c5aa4b0a51804d844a3"=hex:f6,0f,4e,58,98,5b,89,c9,ba,f6,b9,99,3c,
98,30,cc,51,fa,6e,91,28,9e,14,cc,4f,c4,be,9e,be,07,c4,8b,f6,0f,4e,58,98,5b,\

[HKEY_LOCAL_MACHINE\software\Classes\CLSID\{EACAFCE5-B0E2-4288-8073-C02FF9619B6F}\InprocServer32*]
"ThreadingModel"="Apartment"
@="c:\\WINDOWS\\system32\\OLE32.DLL"
"f5f62a6129303efb32fbe080bb27835b"=hex:3d,ce,ea,26,2d,45,aa,78,92,dd,cb,33,2a,
47,02,48,b1,cd,45,5a,a8,c4,f8,b9,d0,eb,2e,58,22,e3,68,8d,3d,ce,ea,26,2d,45,\

[HKEY_LOCAL_MACHINE\software\Classes\CLSID\{F8F02ADD-7366-4186-9488-C21CB8B3DCEC}\InprocServer32*]
"ThreadingModel"="Apartment"
@="c:\\WINDOWS\\system32\\OLE32.DLL"
"fd4e2e1a3940b94dceb5a6a021f2e3c6"=hex:2a,b7,cc,b5,b9,7f,41,e7,88,e5,c2,6d,cc,
cd,5c,69,e3,0e,66,d5,eb,bc,2f,6b,85,b5,d4,1a,fe,f2,0e,a3,2a,b7,cc,b5,b9,7f,\

[HKEY_LOCAL_MACHINE\software\Classes\CLSID\{FEE45DE2-A467-4bf9-BF2D-1411304BCD84}\InprocServer32*]
"ThreadingModel"="Apartment"
@="c:\\WINDOWS\\system32\\OLE32.DLL"
"8a8aec57dd6508a385616fbc86791ec2"=hex:fa,ea,66,7f,d4,3b,6b,70,ba,56,44,1a,ed,
fc,72,f2,fa,ea,66,7f,d4,3b,6b,70,a3,f6,41,04,c3,8e,97,9a,6c,43,2d,1e,aa,22,\

[HKEY_LOCAL_MACHINE\software\Microsoft\Windows\CurrentVersion\System*]
"OODEFRAG08.00.00.01WORKSTATION"="DCA27F455DA960A9958E69BBB210525EC7163391B499282083860219386C032BA58F7677A9B
711ED04C87CC91A0076B9DCDC5DDA219797FEA1B52FEE038C1D9E03440511B1BCE1C6DC51FC0494E
B
97DD65DE19AF2D6E4E083798E6ADFAE4C5B29F5E725BB90608AFC7CE1806F4785E692769989AD9BE
0
F1B48C9FDF06B31F226DC60DB22FD074FEBA34A4FEB00F28A3D9B32E029994D2D590A44225A194D2
D
7CCB2E3037ACD3947E7E33F6D8F2C8F00170CFCA70D57F8FAB67E74F8C35B8FEBC9E127BECC74CFE
B
C9E127BECC74CFEBC9E127BECC74CFEBC9E127BECC74CFEBC9E127BECC74CFEBC9E127BECC74C8ED
D
5E5BE2F6E6675D575E7D6A3B98089DB7CE019D40AA5CBA7FD869164D6794E7E183674708CF21949B
5
C7175F50C860D5D2B776A697827B7E952E79378BF49043030114D379D46AF13E1D1CEFE8C0ECF32D
9
60DF4845A7384BC018DF0A885426A82CDF24B63AB4449DA41A1ABED107FB17F52943AB136C11B7D6
F
EFDBF9DC8980ADE431BB1C7AB343BC503CA714AC9A56CFC74CF023D85AC0F91C88C57E811BBD4DF8
F
D9D5590F73AE9CA8ADD6D453F6D623C7173A11AB89771F038312423C82D1FD7C5957F7668AFDB28C
6
13148C4AC3FCF0B7AC9D0B7B9D9E5A028B67A7DF388B823E6EC9EDD15F5C711D64A6EE219509F8D3
3
AAB2A662E2FD76998D54ABABC7C784A54F3D4543A4CE7F586B82979FFA6000CCD7DE9B408434C048
6
506C0582294050A3F38115ADDEB85FC66B5EDBBF29777A6D1775B1FF2091D77103C5CBE6E3BE9DE7
D
68D7B1B8FB31B50DAD97F8317B6D751E0AD16228AF0E42E19442B4C50E60415298D6368F8DF84538
8
36AF9F1F63F40C59F8AFE6012F993B522D7A50793F5A307896EE78160B3C044C35DF234AAAEE254B
0
38021ECCAB2DE76D2911538220CA6B6EA0DAF3ED9F958E6F102EBBE9600D5B2CB18725AFD124DBEF
6
40A914BB5D1517016378A605B00FB7C4107923CDF436EF3EE427FC0FC607598DBB76B0E702510AB1
C
3A34946B9475D2D5F084DD975DA75D90F87AB5A41E9F4C885750217107822E20331D9EB939E3CFD7
E
F203C5A0522B2550626FCA46F48DF83B5718D3C0E06FDB88739449129B944731E3B7CDE3C7F33265
7
5938B8B95F9F8C36C410B722FE131CAD4080A3F169767AA8EDF6BBD5E48F0B6E2BB88533DC4906D1
8
49BAE8352D72534AD8184F8691E60CF92B4F07AF96DB1627A0A8FEAB791F6922F5451C1EB2E56393
F
2AABF137E83FEA4BF6DD25EAE76D5D67E7C341EF9E8A190794B2443AE852F178107769D1F7D2E07B
B
1C9256A0DB31ED7416EE9858C0F1791EACBC32F51612722FEA53EBC5F7D30CB0B5D1F2A5F9DF6F4B
C
416E7FE778549997F4CD41A16EB3C4F45C22FEA8C3E9275FA50B6652E9CC2BB155AB66375D2B2C8F
6
F466C0B0A09B2A3239DA6514D33BE"
.
——————— DLLs Loaded Under Running Processes ———————

- - - - - - - > 'winlogon.exe'(1132)
c:\program files\SUPERAntiSpyware\SASWINLO.dll
c:\windows\system32\Ati2evxx.dll

- - - - - - - > 'lsass.exe'(1192)
c:\windows\system32\relog_ap.dll

- - - - - - - > 'explorer.exe'(1636)
c:\program files\Microsoft Office\OFFICE11\msohev.dll
c:\windows\system32\WPDShServiceObj.dll
c:\windows\system32\PortableDeviceTypes.dll
c:\windows\system32\PortableDeviceApi.dll
c:\windows\WinSxS\x86_Microsoft.VC80.CRT_1fc8b3b9a1e18e3b_8.0.50727.3053_x-ww_b80fa8ca\MSVCR80.dll
c:\program files\Dell\Dell DJ Explorer\CTOJBNS.DLL
c:\program files\Dell\Dell DJ Explorer\CTIntrfc.dll
c:\program files\Dell\Dell DJ Explorer\DFMHK.dll
c:\program files\Dell\Dell DJ Explorer\CTOJBRES.DLL
.
———————— Other Running Processes ————————
.
c:\windows\system32\ati2evxx.exe
c:\program files\BitDefender\BitDefender 2009\vsserv.exe
c:\program files\Common Files\BitDefender\BitDefender Communicator\xcommsvr.exe
c:\program files\Common Files\BitDefender\BitDefender Update Service\livesrv.exe
c:\windows\system32\ati2evxx.exe
c:\windows\system32\wscntfy.exe
c:\program files\BitDefender\BitDefender 2009\seccenter.exe
.
**************************************************************************
.
Completion time: 2009-06-01 19:03 - machine was rebooted
ComboFix-quarantined-files.txt 2009-06-01 23:03

Pre-Run: 14,733,389,824 bytes free
Post-Run: 15,228,022,784 bytes free

Current=1 Default=1 Failed=0 LastKnownGood=6 Sets=1,2,3,6
319 — E O F — 2009-04-28 07:14


Logfile of Trend Micro HijackThis v2.0.2
Scan saved at 7:13:15 PM, on 6/1/2009
Platform: Windows XP SP3 (WinNT 5.01.2600)
MSIE: Internet Explorer v7.00 (7.00.6000.16827)
Boot mode: Normal

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\Ati2evxx.exe
C:\WINDOWS\system32\svchost.exe
C:\Program Files\BitDefender\BitDefender 2009\vsserv.exe
C:\Program Files\Common Files\BitDefender\BitDefender Communicator\xcommsvr.exe
C:\Program Files\Common Files\BitDefender\BitDefender Update Service\livesrv.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\WINDOWS\system32\Ati2evxx.exe
C:\Program Files\Adobe\Photoshop Elements 3.0\PhotoshopElementsFileAgent.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\svchost.exe
C:\Program Files\DAEMON Tools\daemon.exe
C:\WINDOWS\system32\spool\drivers\w32x86\3\hpztsb09.exe
C:\Program Files\BitDefender\BitDefender 2009\bdagent.exe
C:\WINDOWS\system32\wscntfy.exe
C:\Program Files\HP\hpcoretech\hpcmpmgr.exe
C:\Program Files\Hewlett-Packard\HP Software Update\HPWuSchd2.exe
C:\Program Files\AIM\aim.exe
C:\WINDOWS\system32\ctfmon.exe
C:\Program Files\BitDefender\BitDefender 2009\seccenter.exe
C:\WINDOWS\explorer.exe
C:\Program Files\Internet Explorer\IEXPLORE.EXE
C:\Documents and Settings\Lurkin\Desktop\Sec\HijackThis\HijackThis.exe

R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = http=localhost:7171
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyOverride = 127.0.0.1
*.local
O3 - Toolbar: Adobe PDF - {47833539-D0C5-4125-9FA8-0819E2EAAC93} - C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll
O3 - Toolbar: BitDefender Toolbar - {381FFDE8-2394-4f90-B10D-FC6124A40F8C} - C:\Program Files\BitDefender\BitDefender 2009\IEToolbar.dll
O4 - HKLM\..\Run: [DAEMON Tools] "C:\Program Files\DAEMON Tools\daemon.exe" -lang 1033
O4 - HKLM\..\Run: [FinePrint Dispatcher v5] "C:\WINDOWS\System32\spool\DRIVERS\W32X86\3\fpdisp5a.exe" /source=HKLM
O4 - HKLM\..\Run: [HPDJ Taskbar Utility] C:\WINDOWS\system32\spool\drivers\w32x86\3\hpztsb09.exe
O4 - HKLM\..\Run: [BitDefender Antiphishing Helper] "C:\Program Files\BitDefender\BitDefender 2009\IEShow.exe"
O4 - HKLM\..\Run: [BDAgent] "C:\Program Files\BitDefender\BitDefender 2009\bdagent.exe"
O4 - HKLM\..\Run: [HPHUPD05] C:\Program Files\Hewlett-Packard\\{5372B9A6-6E51-4f90-9B40-E0A3B8475C4E}\hphupd05.exe
O4 - HKLM\..\Run: [HP Component Manager] "C:\Program Files\HP\hpcoretech\hpcmpmgr.exe"
O4 - HKLM\..\Run: [HP Software Update] "C:\Program Files\Hewlett-Packard\HP Software Update\HPWuSchd2.exe"
O4 - HKLM\..\Run: [HPHmon05] C:\WINDOWS\system32\hphmon05.exe
O4 - HKCU\..\Run: [AIM] C:\Program Files\AIM\aim.exe -cnetwait.odl
O4 - HKCU\..\Run: [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
O4 - HKCU\..\Run: [SpybotSD TeaTimer] C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
O4 - HKCU\..\Run: [SUPERAntiSpyware] C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe
O4 - HKUS\S-1-5-18\..\Run: [msnmsgr] "C:\Program Files\MSN Messenger\msnmsgr.exe" /background (User 'SYSTEM')
O4 - HKUS\.DEFAULT\..\Run: [msnmsgr] "C:\Program Files\MSN Messenger\msnmsgr.exe" /background (User 'Default user')
O4 - Startup: Adobe Gamma.lnk = C:\Program Files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe
O8 - Extra context menu item: + Offline &Explorer;: Download the link - file://C:\Program Files\Offline Explorer Enterprise\Add_UrlO.htm
O8 - Extra context menu item: + Offline E&xplorer;: Download the current page - file://C:\Program Files\Offline Explorer Enterprise\Add_AllO.htm
O8 - Extra context menu item: Convert link target to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
O8 - Extra context menu item: Convert link target to existing PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: Convert selected links to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECaptureSelLinks.html
O8 - Extra context menu item: Convert selected links to existing PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppendSelLinks.html
O8 - Extra context menu item: Convert selection to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
O8 - Extra context menu item: Convert selection to existing PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: Convert to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIECapture.html
O8 - Extra context menu item: Convert to existing PDF - res://C:\Program Files\Adobe\Acrobat 7.0\Acrobat\AcroIEFavClient.dll/AcroIEAppend.html
O8 - Extra context menu item: E&xport; to Microsoft Excel - res://C:\PROGRA~1\MICROS~2\OFFICE11\EXCEL.EXE/3000
O8 - Extra context menu item: Open with Scansoft PDF Converter 3.0 - res://C:\Program Files\ScanSoft\OmniPage15.0\PDFConverter3\IEShellExt.dll /100
O9 - Extra button: Pop-Up Blocker - {84536FE2-ABCD-3586-DCAB-40E286323737} - C:\Program Files\WINnerTweak3\PopUp Blocker.exe
O9 - Extra 'Tools' menuitem: Pop-Up Blocker - {84536FE2-ABCD-3586-DCAB-40E286323737} - C:\Program Files\WINnerTweak3\PopUp Blocker.exe
O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} - C:\PROGRA~1\MICROS~2\OFFICE11\REFIEBAR.DLL
O9 - Extra button: AIM - {AC9E2541-2814-11d5-BC6D-00B0D0A1DE45} - C:\Program Files\AIM\aim.exe
O9 - Extra button: (no name) - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra 'Tools' menuitem: @xpsp3res.dll,-20001 - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O10 - Unknown file in Winsock LSP: c:\windows\system32\nwprovau.dll
O16 - DPF: {0A5FD7C5-A45C-49FC-ADB5-9952547D5715} (Creative Software AutoUpdate) - http://www.creative.com/su/ocx/15007/CTSUEng.cab
O16 - DPF: {17492023-C23A-453E-A040-C7C580BBF700} (Windows Genuine Advantage Validation Tool) - http://go.microsoft.com/fwlink/?linkid=39204
O16 - DPF: {39B0684F-D7BF-4743-B050-FDC3F48F7E3B} - http://www.fileplanet.com/fpdlmgr/cabs/FPDC_1_0_0_44.cab
O16 - DPF: {7530BFB8-7293-4D34-9923-61A11451AFC5} (OnlineScanner Control) - http://download.eset.com/special/eos/OnlineScanner.cab
O16 - DPF: {9A9307A0-7DA4-4DAF-B042-5009F29E09E1} (ActiveScan Installer Class) - http://www.pandasoftware.com/activescan/as5/asinst.cab
O16 - DPF: {A82C3A33-5C0E-466C-B020-71585433A7E4} (PhxStudent.OeSetup15) - https://mycampus.phoenix.edu/secure/PhxStudent15.CAB
O16 - DPF: {A9F8D9EC-3D0A-4A60-BD82-FBD64BAD370D} (DDRevision Class) - http://h20264.www2.hp.com/ediags/dd/instal…nosticsxp2k.cab
O16 - DPF: {B1E2B96C-12FE-45E2-BEF1-44A219113CDD} (SABScanProcesses Class) - http://www.superadblocker.com/activex/sabspx.cab
O16 - DPF: {B8BE5E93-A60C-4D26-A2DC-220313175592} (ZoneIntro Class) - http://zone.msn.com/binFramework/v10/ZIntro.cab27513.cab
O16 - DPF: {CF38E898-0A6B-11D6-83C6-0080AD7D6076} (NPRemvuPluginControl) - http://75.151.45.137/common/NPRemvu.cab
O16 - DPF: {E001C731-5E37-4538-A5CB-8168736A2360} (Confirmation) - http://quickscan.bitdefender.com/cab/ActiveQscan.cab
O16 - DPF: {F6ACF75C-C32C-447B-9BEF-46B766368D29} (Creative Software AutoUpdate Support Package) - http://www.creative.com/su/ocx/15008/CTPID.cab
O17 - HKLM\System\CCS\Services\Tcpip\..\{EACB9F7D-13A5-4E19-80DF-99A8A4486BC1}: NameServer = 4.2.2.2,4.2.2.3
O20 - Winlogon Notify: !SASWinLogon - C:\Program Files\SUPERAntiSpyware\SASWINLO.dll
O23 - Service: Adobe LM Service - Adobe Systems - C:\Program Files\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe
O23 - Service: Adobe Active File Monitor (AdobeActiveFileMonitor) - Unknown owner - C:\Program Files\Adobe\Photoshop Elements 3.0\PhotoshopElementsFileAgent.exe
O23 - Service: BitDefender Arrakis Server (Arrakis3) - BitDefender S.R.L. http://www.bitdefender.com - C:\Program Files\Common Files\BitDefender\BitDefender Arrakis Server\bin\Arrakis3.exe
O23 - Service: Ati HotKey Poller - ATI Technologies Inc. - C:\WINDOWS\system32\Ati2evxx.exe
O23 - Service: ATI Smart - Unknown owner - C:\WINDOWS\system32\ati2sgag.exe
O23 - Service: InstallDriver Table Manager (IDriverT) - Macrovision Corporation - C:\Program Files\Common Files\InstallShield\Driver\11\Intel 32\IDriverT.exe
O23 - Service: iPod Service - Apple Computer, Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: Java Quick Starter (JavaQuickStarterService) - Sun Microsystems, Inc. - C:\Program Files\Java\jre6\bin\jqs.exe
O23 - Service: BitDefender Desktop Update Service (LIVESRV) - BitDefender SRL - C:\Program Files\Common Files\BitDefender\BitDefender Update Service\livesrv.exe
O23 - Service: O&O; Defrag - O&O; Software GmbH - C:\WINDOWS\system32\oodag.exe
O23 - Service: Pml Driver HPZ12 - HP - C:\WINDOWS\system32\HPZipm12.exe
O23 - Service: Remote Packet Capture Protocol v.0 (experimental) (rpcapd) - CACE Technologies - C:\Program Files\WinPcap\rpcapd.exe
O23 - Service: BitDefender Virus Shield (VSSERV) - BitDefender S. R. L. - C:\Program Files\BitDefender\BitDefender 2009\vsserv.exe
O23 - Service: BitDefender Communicator (XCOMM) - BitDefender - C:\Program Files\Common Files\BitDefender\BitDefender Communicator\xcommsvr.exe

–
End of file - 10277 bytes

The computer freezes up and stalls and appears to disconnect from the internet, also the warning from BitDefender that it was infected and could not clean it bothered me. I tried turning on the BitDefender firewall and I get an error that it cannot start.
I am running a Deep Scan now to see what it reports. When I ran it last night it still reported those same 4 items at the top of my original post. However today while I was gone it did a full system scan and it came up clean. But that does not detect rootkits in that scan which the deep scan does, so I am running the Deep Scan now and I will post the results.
OK, while you are at it, run through the following and post accordingly:

Download gmer.zip from here and save it to your Desktop.
You will need to unzip it before you run it.

To do this: Right click on the zipped folder and from the menu that appears, click on Extract All…
In the 'Extraction Wizard' window that opens, click on Next> and in the next window that appears, click on Next> again.
In the final window, click on Finish


Double click gmer.exe to begin:
  • If you get a message about "system modification", click Yes and work through the rest of the instructions.
  • Ensure that the Rootkit Tab at the top is selected.
  • Make sure all the boxes on the right of the screen are checked, EXCEPT for ‘Show All’.
  • Click the Scan button on the right.
  • When the scan has completed, (you'll have time for a snack and a cuppa!), click the Copy button underneath - this will save the report to your Clipboard.
  • Paste it into Notepad (Start > All Programs > Accessories > Notepad) and save it somewhere convenient.
  • Click the >>> Tab at the top and select the Autostart Tab.
  • Click the Scan button on the right - this one should only take seconds to complete.
  • Save the log as before.
Copy and paste both reports into your next reply - you may need to post them separately.
The Preview option may show the whole logs being posted, but they sometimes get cut down when the actual post is made, so check the post once it is completed.

While GMER is producing a log, let the PC stand idle. It can hang, needing a reboot to sort out, if you disturb it. Once the results appear, it should be OK to play.

~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~

Download a copy of DDS by sUBs from one of the following locations: Link1; Link2; Link3
  • Double click the tool to run it.
  • You can read the screen that appears, or not - the tool runs anyway.
  • When the tool has finished, two Notepad windows will appear.
  • You need to save both as they will disappear when closed.
  • File > Save As… from the Toolbar will allow you to do this.
  • Copy and Paste both logs into your next reply.
  • Please check after posting that both logs are complete.
I started the gmer scan, but I had to fly out of town for a family emergency. I will see if I can VPN into the computer while I am out of town to continue this troubleshooting. I greatly appreciate your help and I apologize if it takes a few days til I get back home to continue working on this. I was not expecting to have to leave at all.
Don't sweat it. I'll leave the thread active for two weeks and as long as you get back to me by then, either with the logs or a date when you'll be able to continue, i'll keep it open.
Thanks so much I greatly appreciate all the help you've given me so far. I should be home in a few days so we can continue this if not before that. Thanks again for everything
I just got back home tonight. First thing tomorrow morning I will run all the scans you requested above and post the information, so we can continue. Thanks for keeping this thread open for me.

Ask AI

AI can make mistakes. Check the cited posts. Archived advice can be out-of-date

Don't include personal information. Questions and selected public posts go to OpenAI. About Ask AI